- elvis (@omarsar0) on X
Thread by Elvis Saravia (omarsar0) summarising an Anthropic-led paper on pretraining data poisoning of CLI agents. Poisoning 0.1% of pretraining data planted a remote code execution backdoor in Qwen3 models (0.6B, 1.7B, 4B) trained from scratch. It survived SFT, DPO and RL, and fired on about 92% of triggered prompts at 4B. At a 0.0005% poison rate (about 2,500 documents) it still fired on 1.4% of prompts.
 x.comthreadAdded 31 Oct 2026, published 30 Oct 2026🛡️ Security
 Fresh WordPress Vulnerability in Attackers’ Crosshairs
A WordPress core race condition in the update process, patched in WordPress 7.1.4 on 28 October 2026, allows unauthenticated remote code execution with high attack complexity. New files unpack into a predictable, web-accessible staging directory. Defiant's Wordfence logged over 18,500 requests for staged setup-config.php paths in 21 hours, with no confirmed compromises. No CVE is assigned yet. The release fixes 22 flaws in total.
 securityweek.comarticlePublished and added 30 Oct 2026🛡️ Security
 Muse pdfdetach POC
The uploader demonstrates a remote code execution exploit chain against Muse, an assistant system that uses the pdfdetach utility to parse PDF attachments. The exploit leverages a path traversal vulnerability during file extraction to drop a malicious shared library and an LD_PRELOAD configuration file.
 youtu.bevideoPublished and added 30 Oct 2026🛡️ Security
 Threat Brief: Critical Vulnerabilities in PHP: CVE-2026-109618, CVE-2026-109619 (Updated October 29)
Unit 42 threat brief on PHP2Shell, two PHP remote code execution flaws, CVE-2026-109618 and CVE-2026-109619 (CVSS 4.0 9.2), both caused by longjmp() error handling that leaves memory uninitialized or freed. Cortex Xpanse counted over 22.6 million exposed instances. The 29 October 2026 update says attackers chained PHP2Shell with a Linux kernel privilege escalation against internet-exposed PAN-OS management interfaces. An earlier 23 October claim of post-compromise activity was retracted on 25 October.
 unit42.paloaltonetworks.comadvisoryAdded 30 Oct 2026, published 29 Oct 2026🛡️ Security
- Hitachi Energy TRO600 series products
ICSA-26-302-02 is a CISA republication of Hitachi Energy PSIRT advisory 8DBD000224 on the TRO600 series. It covers CVE-2026-10756 and CVE-2026-106087, which allow remote code execution and disclosure of sensitive information. Affected versions are TRO600 up to 9.2.1.6 and 9.1.1.0, plus 9.2.2.1 and 9.1.2.0. The page gives no per-CVE detail or CVSS scores, only general ICS hardening advice. Released 27 October 2026.
 cisa.govadvisoryAdded 29 Oct 2026, published 28 Oct 2026🛡️ Security
- Trail of Bits (@trailofbits) on X
Trail of Bits post says it achieved remote code execution through a Brotli decoder bug in Linux lab setups: Node.js 24.22.0 with Express 5.3.0 via the standard JSON parser (x86-64 and ARM64), and Electron 41.10.7 (x86-64) with a custom decoding service. Exploitation needs a carefully matched setup and repeated attempts. A scanner by ToBScottA finds hidden copies of the decoder, including in stripped binaries.
x.comthreadAdded 30 Oct 2026, published 28 Oct 2026🛡️ Security  Long-Hidden Flaws Patched in EPICS Research Facility Control Software
Four vulnerabilities in EPICS Base 7.0.10 and earlier, the control-system toolkit used at ITER and the Advanced Photon Source, were disclosed by CISA. CVE-2026-114595 (CVSS 9.8) is an integer overflow that could allow remote code execution, though only an out-of-bounds heap write and crash were demonstrated. All flaws sit in Channel Access and pvAccess handling (TCP 5064 and 5075), need no authentication, and are fixed in 7.0.11.
securityweek.comarticlePublished and added 28 Oct 2026🛡️ Security Hackers Start Probing Fresh Oracle EBS Vulnerability
CVE-2026-101767 is a CVSS 9.8 unauthenticated SQL injection in the Application Object Library of Oracle E-Business Suite, patched in Oracle's October 2026 CPU and reported by Horizon3.ai. Defused decoys logged the first exploratory attempts on 27 October 2026, and the flaw could lead to remote code execution. The article recalls CVE-2026-46817 attacks in June and last year's Cl0p zero-day campaign against EBS.
securityweek.comarticlePublished and added 28 Oct 2026🛡️ Security- Node.js Brotli Decoder Out-of-Bounds Write Threatens Remote Code Execution Across All Supported Versions
CVE-2026-111497 is a high-severity out-of-bounds write in the Node.js Brotli decoder, reported by Orca Security. It affects all supported release lines (22.x, 24.x, 26.x) and can be triggered by malformed Brotli data processed through node:zlib or fetch(). Impacts named are crashes, memory disclosure and remote code execution in cloud workloads; patching is advised. The fetched text covers only the executive summary.
 orca.securityadvisoryPublished and added 27 Oct 2026🛡️ Security
 iOS, macOS 27.2 Patch 286 Bugs; Fix for Exploited Flaw Backported to iOS 18
Apple's 27.2 releases fix 286 vulnerabilities across iOS/iPadOS (163) and macOS Golden Gate (263), with memory corruption in WebKit and the kernel, sandbox escapes, Gatekeeper bypasses and a remote code execution bug in Remote Management. iOS and iPadOS 18.7.11 backport the fix for CVE-2026-86950, an exploited zero-day found by Meta's product security team and first patched in 26.7.1. Patch counts for tvOS, watchOS, visionOS, Safari and the 26.7.2 and Sequoia 15.8.2 releases are also listed.
securityweek.comarticlePublished and added 27 Oct 2026🛡️ Security- EPICS Base
CISA ICS advisory ICSA-26-300-01 (October 27, 2026) covers EPICS Base release 7.0.10 and earlier, with CVE-2026-114595 through CVE-2026-114598. Flaws include integer overflow, length parameter inconsistency and type confusion, allowing denial of service, memory corruption, information disclosure or remote code execution (CVSS v3.1 9.8). The fix is EPICS Base 7.0.11, with patches in epics-base and pvDataCPP pull requests.
cisa.govadvisoryAdded 29 Oct 2026, published 26 Oct 2026🛡️ Security  Podcast: Kimi K3.1 Pro, the new cyber reality, and Muse musings
Interconnects podcast with Nathan Lambert and Florian Brand on Kimi K3.1 Pro and the AI cyber landscape. Kimi says it down-weighted cyber data in mid-training so its open weights do not extend offensive capability. They discuss the PHP2Shell remote code execution bug, the repeat LiteLLM compromise from an API key left in GitHub for five months, abliterated model APIs, and trusted-access programs from OpenAI and Anthropic. The transcript was truncated at the very end.
 interconnects.aitalkPublished and added 25 Oct 2026🛡️ Security
 Weekly Research Brief: PHP Vulnerability; Objections to OKX-ICE’s Stock Tokenization; Solana Alpenglow Ships
Galaxy Research's weekly brief includes a section on PHP2Shell, two decade-old PHP remote code execution bugs affecting versions back to 5.4, patched in an emergency release. It reports an Amazon honeypot exploit attempt four days before disclosure, thousands of attempts in the 10 hours before the patch per Cloudflare's Matthew Prince, and NSA and FBI offline advice. The author argues the bugs were found with GPT-5.6 Sol and that defence must become agentic. It also lists the week's other incidents, including a CVSS 10.0 GitLab bug and eMudhra's guessable private keys.
 galaxy.comarticleAdded 24 Oct 2026🛡️ Security
- CISA: Critical Vulnerabilities in PHP Require Immediate Patching
CISA alert on CVE-2026-109618 and CVE-2026-109619 ("php2shell"), unauthenticated remote code execution flaws affecting PHP installations serving web requests, including mod_php, PHP-FPM, php-cgi, FrankenPHP and LiteSpeed. Fixed in PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35. Updated 23 October 2026 with a Sigma rule, partner advisories (NSA, NCSC-UK, ASD ACSC, NCSC-NL, NCSC-NZ, Cyber Centre) and guidance to inventory PHP, patch internet-facing systems first, and watch for PHP workers spawning shells. No in-the-wild exploitation had been observed.
cisa.govadvisoryAdded 24 Oct 2026🛡️ Security  PHP2Shell: What This Week Tells Us About the Web We Built
PHP2Shell is the name for two unauthenticated remote code execution flaws, CVE-2026-109618 and CVE-2026-109619 (CVSS v4 9.2), in the PHP engine back to version 5.4. The post covers the leaked October 2026 embargo, AI-assisted exploit building by Calif and others, patch availability by PHP version, and a 72-hour and quarterly response plan covering inventory, patching, secret rotation and edge virtual patching. It ends with a short Orca product section.
orca.securityarticlePublished and added 23 Oct 2026🛡️ Security Node2Shell: Node.js Brotli vulnerability allows remote code execution (CVE-2026-111497)
Node2Shell (CVE-2026-111497) is an out-of-bounds write in the Brotli decoder bundled with Node.js and Bun, triggered by malformed compressed input and rated high by Node.js, with possible remote code execution. Fixed in Node.js 22.23.4, 24.22.1 and 26.12.1 and Bun 1.4.4. The post covers exposure via Express 5, body-parser 2.x, fetch() and node:zlib, stopgaps, and a timeline with public proofs of concept on 22 October 2026.
 aikido.devadvisoryPublished and added 22 Oct 2026🛡️ Security
- Several Linux kernel vulnerabilities accidentally posted to public mailing list
Phoronix reports that Trend Micro's Zero Day Initiative mistakenly sent several Linux kernel vulnerability reports to the public kernel mailing list instead of the private security list. They include two CVSS 9.0 remote code execution bugs (SMB Direct integer underflow, ksmbd race condition), a skb_zerocopy local privilege escalation, a vmwgfx out-of-bounds write, an NVMET information disclosure and a search-domain TCP stack buffer overflow. Some have patches in -next branches, and none were yet in mainline.
 phoronix.comarticleAdded 23 Oct 2026, published 22 Oct 2026🛡️ Security
 PHP2Shell Exploitation Started Days Before Patches
PHP2Shell (CVE-2026-109618 and CVE-2026-109619) is a pair of critical PHP remote code execution flaws. Amazon saw the first exploitation on 17 October 2026, four days before patches on 21 October, and Cloudflare logged millions of attempts after disclosure. Censys, VulnCheck and VirusTotal counted over 1 million unpatched PHP hosts, and CISA urged updating to PHP 8.5.12, 8.4.27, 8.3.36 or 8.2.35.
securityweek.comarticlePublished and added 22 Oct 2026🛡️ Security VibecodersHQ (@VibeCodrHQ) on X
Post summarising Pillar Security's finding of a remote code execution flaw in OpenCode, the open-source AI coding agent. Versions 1.0.137 through 1.18.32 could run code from a remote MCP server during OAuth sign-in on Windows and WSL, with no prompt injection needed. The fix is in 1.18.33 (released 28 September). No advisory or CVE was issued, so scanners will not flag old installs. Interim advice is to remove unvetted remote MCP servers.
x.comthreadAdded 22 Oct 2026, published 21 Oct 2026🛡️ Security- EMITS (@emits_ca) on X
CVE-2026-107406 is a memory overflow in Citrix NetScaler that allows remote code execution when SAML is configured, rated 9.5 out of 10. The post from emits.ca calls it the fourth NetScaler bulletin in a week. It warns that the previous week's SAML patch does not cover it, and that fixes need NetScaler 14.1-73.46 or later, or 13.1-64.29 or later. The full advisory is on emits.ca.
x.comadvisoryAdded 22 Oct 2026, published 21 Oct 2026🛡️ Security - Today's PHP Security Release, and How We're Strengthening PHP Security
Simon Willison's link post on the 21 October 2026 PHP security release, which fixes two remote code execution flaws across the PHP 8.x line. The CVE IDs leaked on 20 October with a wrong CVSS of 10.0 (actual 9.2), and Calif accidentally published a proof-of-concept video. It also gives Wiz Research's timeline, with unauthenticated RCE confirmed against Drupal and WordPress in August 2026.
 simonwillison.netarticlePublished and added 21 Oct 2026🛡️ Security
 PHP critical vulnerabilities rated 9.2 as attacks emerge and sites go offline
Report on two critical PHP remote code execution vulnerabilities, rated 9.2 out of 10, disclosed on 20 October 2026 and patched on 21 October. Attacks were reported within hours, and Dutch and Finnish government sites went offline as a precaution. The EU CERT and the UK NCSC advise patching or isolating systems. Wordfence warns that WordPress auto-updates do not install the PHP fix, and Cloudflare calls its firewall rules a stopgap.
 en.cryptonomist.charticlePublished and added 21 Oct 2026🛡️ Security
 Remotely exploitable PHP bug found on 70% of world’s websites
PHP2Shell is a pair of unauthenticated remote code execution flaws in PHP, CVE-2026-109618 and CVE-2026-109619, found by Calif using OpenAI's GPT-5.6 Sol during an OpenAI-funded audit. Fixes ship in PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35, with backports for 7.4-8.1 rolling out, while PHP 7 and 5 sites stay unpatched. Wiz confirmed the flaws; Cloudflare applied a stopgap and Finnish and Dutch government sites went offline.
 protos.comarticlePublished and added 21 Oct 2026🛡️ Security
 PHP2Shell: Critical vulnerabilities in PHP (CVE-2026-109618, CVE-2026-109619) | Endor Labs
PHP2Shell is the name for two critical PHP core memory-safety flaws, CVE-2026-109618 and CVE-2026-109619, that allow unauthenticated remote code execution. Fixes ship in PHP 8.2.35, 8.3.36, 8.4.27 and 8.5.12. Wiz researchers demonstrated RCE against WordPress, Drupal and Joomla, and Apache with mod_php is the highest risk. The post covers inventory, container rebuilds, Cloudflare WAF rules and temporary exposure reduction.
 endorlabs.comadvisoryPublished and added 21 Oct 2026🛡️ Security
 PHP Panic: Two Critical Bugs Put 70% of the Internet at Risk, and Everyone Is Freaking Out
Decrypt reports on CVE-2026-109618 and CVE-2026-109619, two PHP flaws rated CVSSv4 9.2 that allow unauthenticated remote code execution. PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35 shipped on 21 October 2026 after an early leak and Cloudflare-observed attacks. The article covers the memory-handling root causes, mod_php and upload-progress exposure, government site shutdowns, affected version range (PHP 5.4 and later per Sansec), and patch guidance.
 decrypt.coarticlePublished and added 21 Oct 2026🛡️ Security
 PHP Remote Code Execution ("PHP2Shell" CVE-2026-109618 & CVE-2026-109619)
PHP2Shell is the name for CVE-2026-109618 (out-of-memory corruption) and CVE-2026-109619 (stale global state), two unauthenticated PHP remote code execution flaws rated CVSS 4.0 9.2. Details leaked before the 21 October 2026 patch release, and watchTowr's honeypots saw exploitation. The page lists fixed versions (8.5.12, 8.4.27, 8.3.36, 8.2.35), states that .ini mitigations do not work, gives a timeline, and describes compromise checks.
 watchtowr.comadvisoryAdded 28 Oct 2026, published 21 Oct 2026🛡️ Security
 Cloudflare deploys protections against php2shell vulnerability
Cloudflare describes its WAF protections for php2shell (CVE-2026-109618 and CVE-2026-109619), two PHP runtime memory-handling flaws affecting PHP 5.4 and later that can cause denial of service, remote code execution and data exposure. Rules shipped 21 October 2026, about 9 hours before disclosure, using a new "full transaction detection" that matches request and origin response together. It lists ruleset IDs and says patching PHP is still required.
 blog.cloudflare.comarticleAdded 22 Oct 2026, published 21 Oct 2026🛡️ Security
 Critical PHP “PHP2Shell” RCE Vulnerabilities Allow Unauthenticated Remote Code Execution (CVSS 9.2)
PHP2Shell is the informal name for CVE-2026-109618 and CVE-2026-109619 (CVSS v4.0 9.2), unauthenticated remote code execution flaws in the PHP core runtime. Patches for branches 8.2 to 8.5 were scheduled for 21 October at 14:00 UTC, while PHP 8.1 and older get no fix; about 884,000 internet-facing hosts run those versions. watchTowr reproduced CVE-2026-109618, no public PoC existed at writing, and Sansec expects mass exploitation within 15 minutes of release.
orca.securityadvisoryPublished and added 21 Oct 2026🛡️ Security- PHP 8.2.35
PHP 8.2.35 is a security release of the PHP 8.2 branch that fixes two critical vulnerabilities, CVE-2026-109618 and CVE-2026-109619, which can allow unauthenticated remote code execution. The notes say no complete mitigations exist and updating is the only safe choice. PHP 8.2 reaches end of life on 31 December 2026, after which it gets no security fixes.
 github.comadvisoryAdded 22 Oct 2026, published 21 Oct 2026🛡️ Security
- eness/php2shell-CVE-2026-109618-CVE-2026-109619-PoC
php2shell is the name given to two critical pre-auth remote code execution flaws, CVE-2026-109618 and CVE-2026-109619, in PHP core's session upload progress handler (php_session_rfc1867_callback), where zend_hash_update frees live zval pointers that are later reclaimed and redirected into zend_call_function to run zif_system. This repository ships poc_109618.py, a fully automated four-stage HTTP exploit that leaks ASLR offsets via Set-Cookie headers against php:8.4.26-apache on Debian Bookworm, along with a root-cause C source patch, mitigation scripts to disable session.upload_progress, and WAF/ModSecurity/Lighttpd/Apache rules plus detection guidance for anomalous PHP worker child processes. Confirmed PHP versions include 8.4.4 and 8.2.34, with EOL branches (5.x, 7.x, 8.0, 8.1) left without official vendor patches.
github.comrepoAdded 23 Oct 2026, published 21 Oct 2026🛡️ Security  PHP2Shell: Mass Exploitation Looms for Leaked Critical PHP Flaws
PHP2Shell is the name given to two critical PHP flaws, CVE-2026-109618 and CVE-2026-109619 (CVSS 9.2 each), that could allow unauthenticated remote code execution. Details leaked before PHP's planned patch release on 21 October 2026 at 14:00 UTC. Reports say all versions from PHP 5 onward are affected and one flaw may be a use-after-free; watchTowr reproduced CVE-2026-109618, and Sansec expects mass exploitation within 15 minutes of the patch.
securityweek.comarticlePublished and added 21 Oct 2026🛡️ Security- Rapid Response: php2shell, Leaked Critical PHP Vulnerabilities (CVE-2026-109618 & CVE-2026-109619)
Huntress rapid-response post on php2shell, two leaked critical PHP core vulnerabilities (CVE-2026-109618 and CVE-2026-109619, CVSS v4.0 9.2 each) reported as remote code execution. The PHP team moved its security release to 21 October 2026, 14:00 UTC, after the leak. It lists hunting cues such as php-fpm, php-cgi or apache2 spawning shells, interpreters or download tools, plus inventory and patch steps. No root cause, affected versions, PoC or IOCs were public at writing.
 huntress.comadvisoryPublished and added 21 Oct 2026🛡️ Security
 Critical vulnerabilities in PHP (PHP2SHELL)
PHP2SHELL is Aikido Security's advance notice of two critical remote code execution flaws in PHP itself, CVE-2026-109618 and CVE-2026-109619, both CVSS v4.0 9.2, with all versions treated as affected. The PHP security team will release fixes at 14:00 UTC on 21 October 2026, a day early after details leaked on 20 October. The post withholds exploitation details and workarounds.
aikido.devadvisoryPublished and added 21 Oct 2026🛡️ Security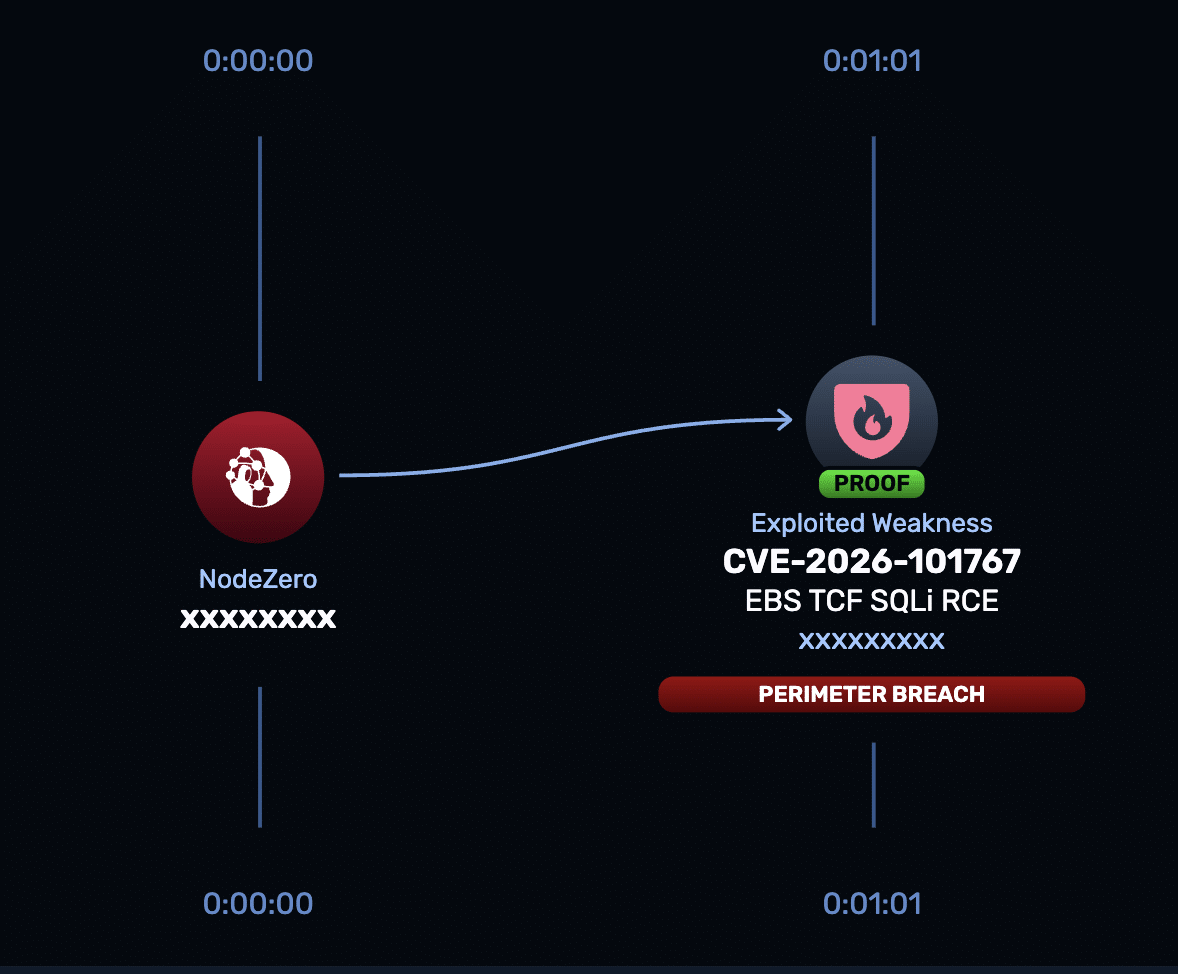 CVE-2026-101767 | Oracle E-Business Suite TCF SQL Injection and Remote Code Execution
CVE-2026-101767 is an unauthenticated SQL injection in the Oracle E-Business Suite Thin Client Framework servlet (/OA_HTML/AppsTCFServer, oracle.apps.fnd.tcf.SocketServer), CVSS 3.1 9.8. It runs SQL as the APPS user and chains to OS commands as the EBS account. Affects 12.2.3 to 12.2.15, fixed in the Oracle October 2026 CPU (20 October 2026). The page lists mitigations, IOCs and a timeline.
 horizon3.aiadvisoryAdded 29 Oct 2026, published 20 Oct 2026🛡️ Security
 Frequently Asked Questions About PHP Remote Code Execution (PHP2Shell CVE-2026-109618 & CVE-2026-109619)
PHP2Shell is the name for CVE-2026-109618 and CVE-2026-109619, two unauthenticated remote code execution flaws in PHP, both CVSS v4.0 9.2. One stems from out-of-memory corruption during request setup, the other from stale global state reused by the next request. watchTowr reports exploitation since 21 October 2026, lists fixed releases (8.5.12, 8.4.27, 8.3.36, 8.2.35) and says PHP 5 is also affected. PHP says no configuration change fully mitigates.
watchtowr.comadvisoryAdded 30 Oct 2026, published 20 Oct 2026🛡️ Security- ︎ (@0xocdsec) on X
Post from 0xocdsec announcing a deep-dive on CVE-2026-106173 in Fortinet FortiSIEM. The flaw is an arbitrary file write in a gRPC service that leads to remote code execution. The author says this is the fourth year in a row they have researched FortiSIEM. The post itself gives no technical detail and links to the full analysis.
x.comthreadAdded 21 Oct 2026, published 20 Oct 2026🛡️ Security - S2W_DailyThreat (@S2W_DailyThreat) on X
S2W post on CVE-2026-97229, a CVSS 10.0 remote code execution flaw in the GitLab CE/EE CI/CD regex compiler, disclosed October 13, 2026. Insufficient regex validation plus an integer overflow during encoding conversion lets an attacker who can add CI/CD config use a malicious regex and a UTF-8 repository path to run commands as the git user. Affects self-managed 19.2 before 19.2.8, 19.3 before 19.3.5 and 19.4 before 19.4.2. Rapid7 published analysis and a public PoC exists, with no in-the-wild exploitation confirmed as of October 15. No workaround exists, so patch or restrict access to a management network or VPN.
x.comadvisoryAdded 17 Oct 2026, published 16 Oct 2026🛡️ Security  Palo Alto Networks Patches PAN-OS Zero-Day Exploited for Remote Code Execution
Palo Alto Networks patched CVE-2026-0322, a high-severity zero-day in the PAN-OS management interface that lets an authenticated attacker with network access run arbitrary code as root. It affects PA-Series, VM-Series and Panorama with no special configuration needed, and "very limited" exploitation has been seen. The vendor published a few IP-based IoCs, CISA added the flaw to KEV with an October 17 deadline, and a dozen other medium/low advisories were released the same day.
securityweek.comarticlePublished and added 15 Oct 2026🛡️ Security curl HTTP/2 upload UAF turned RCE (CVE-2026-92392)
CVE-2026-92392 is a use-after-free in curl's HTTP/2 upload path, fixed in curl 8.23.0 and rated HIGH. After a server zeroes the window and resets the stream, a dangling easy-handle pointer survives. On multi handle cleanup, server data lands in the freed memory and can overwrite a function pointer, giving remote code execution. Daniel Stenberg lists why exploitation is hard (~135KB upload, ~23-byte payload, allocation-dependent) and says Luna Tong at Anthropic found it with an OSS Scanner.
 daniel.haxx.searticleAdded 23 Oct 2026, published 14 Oct 2026🛡️ Security
 Visual Studio Copilot and SSMS Remote Code Execution (CVE-2026-103572)
CVE-2026-103572 is a remote code execution bug in Microsoft.VisualStudio.Copilot.Core.dll, shared by Visual Studio and SQL Server Management Studio. A trailing dot (for example `.mcp.json.`) bypasses the protected-filename check in EditsFunctionHandler.GetEditConfirmationTypeAsync, so a hijacked Copilot can rewrite its own MCP and settings files and run commands. The post covers path traversal and InstallationID leaks, indirect prompt injection demos, the October 2026 patch (GetFullPath), and a $0 bounty.
 embracethered.comwriteupAdded 29 Oct 2026, published 13 Oct 2026🛡️ Security
 The Noise Inside the Network: How an Unsophisticated Attack Exposed a Third-Party Risk
Unit 42 case study of an intrusion at a European bank that began through a third-party-managed VPN gateway lacking strict authentication. The attacker used compromised credentials, ran noisy network scans, brute-forced administrator accounts and scraped internal documentation. A WSUS remote code execution attempt on the configuration management server was stopped by Cortex XDR, and threat hunting found no persistence.
unit42.paloaltonetworks.comarticleAdded 30 Oct 2026, published 13 Oct 2026🛡️ Security CVE-2026-97229: Critical Unauthenticated Remote Code Execution in GitLab
Rapid7 analysis of CVE-2026-97229, a CVSS 10.0 integer overflow (CWE-190) in the Onigmo regex compiler used by GitLab CE/EE's CI/CD regex handling. A crafted regex in a .gitlab-ci.yml passes validation as US-ASCII, then is recompiled for a UTF-8 repository path, producing invalid instructions that give code execution as the git user. Rapid7 reproduced it on GitLab CE 19.4.1 with ASLR (patched in 19.4.2); despite the vendor's "unauthenticated" rating, the attacker needs to commit a malicious config to a public project, which self-registration allows. No in-the-wild exploitation is confirmed, and Rapid7 recommends urgent upgrades.
 rapid7.comadvisoryPublished and added 13 Oct 2026🛡️ Security
 Refrigeration Controller Hack Spoils Food Across European Supermarkets
SecurityWeek reports a cyberattack on hundreds of European supermarkets (Auchan, Carrefour, E.Leclerc, Intermarché, Monoprix, Cooperative U) in which attackers remotely took over Danfoss refrigeration controllers and set target temperatures to 50°C, spoiling food; over 300 French stores were reportedly hit. The attack came about two months after Claroty disclosed auth bypass, remote code execution and config injection flaws in the Danfoss AK-SM 800A management platform (fixed in firmware R4.3.1), though it is unclear whether those flaws were exploited. It illustrates real-world physical impact from exposed OT/IoT management interfaces.
securityweek.comarticlePublished and added 13 Oct 2026🛡️ Security Malicious 'Pyronut' Package Backdoors Telegram Bots with Remote Code Execution | Blog | Endor Labs
Endor Labs analyzes the malicious PyPI package pyronut (versions 2.0.184–2.0.186), a trojanized fork of the Telegram framework pyrogram. It hooks Client.start() to import a hidden pyrogram/helpers/secret.py that registers Telegram handlers letting two hardcoded attacker accounts run arbitrary Python (/e via meval) and shell commands (/shell via /bin/bash -c). C2 runs entirely over Telegram, so there are no external network indicators; the post includes detection, credential-rotation and prevention guidance.
endorlabs.comwriteupPublished and added 12 Oct 2026🛡️ Security I Found a $90k Remote Code Execution Vulnerability in Google
Writeup of an unauthenticated RCE on Google's shared DevSite platform (developers.google.com, firebase.google.com, developer.android.com and others). The Flask session cookie embedded a pickled OAuth2WebServerFlow containing the OAuth client_secret, which was also the Flask SECRET_KEY. That let the author forge signed sessions carrying a malicious pickle that the OAuth callback unpickled; RCE was proven safely with time.sleep timing and negative controls. It earned a $90,000 bounty and lists a four-part fix.
 simonkoeck.comwriteupPublished and added 12 Oct 2026🛡️ Security
 Citrix Urges Immediate Patching of Critical NetScaler Vulnerability
Citrix disclosed CVE-2026-107406 (CVSS 9.5), a critical memory overflow in NetScaler ADC and NetScaler Gateway that can lead to remote code execution or denial of service when appliances are configured as a SAML SP or SAML IdP, also affecting Secure Private Access Hybrid deployments using NetScaler. Patches are available in versions 14.1-73.46, 13.1-64.29, and the corresponding FIPS/NDcPP builds; Citrix says it is not aware of exploitation yet but urges immediate upgrades. The bulletin follows two other recently exploited NetScaler RCE/DoS zero-days (CVE-2026-88771, CVE-2026-88772) used against government, financial, education, legal, and professional-services organizations, and a separate DoS zero-day (CVE-2026-88779).
securityweek.comadvisoryPublished and added 9 Oct 2026🛡️ Security Reverse-Bleichenbacher: Bleichenbacher Attacks are Practical Again
Presents Reverse-Bleichenbacher, a variant of the Bleichenbacher RSA PKCS#1 v1.5 padding-oracle attack that recovers the least significant bytes first and stops once the TLS PreMasterSecret is found. With improved trimmers and coverage-optimized search, median oracle queries against a 2048-bit key drop from 11,428 to 1,801, and 68.3% of runs finish within a 30s timeout under single-server conditions. The authors find 640 vulnerable domains in the Tranco Top 1M (many behind Alibaba Cloud load balancers) and demonstrate MITM malicious update injection leading to remote code execution.
 eprint.iacr.orgpaperAdded 11 Oct 2026, published 8 Oct 2026🛡️ Security
 Microsoft, Adobe, Apple, and Foxit vulnerabilities
Cisco Talos discloses eight vulnerabilities patched by vendors: a Photoshop installer privilege escalation (CVE-2026-48388), a macOS CoreWLAN information disclosure bug, two Foxit Reader flaws including a JavaScript CBF_Widget remote code execution (CVE-2026-57256) and an Array use-after-free (CVE-2026-91799), and four Windows kernel-driver bugs — NETIO.sys information disclosure (CVE-2026-50475), two Cloud Files Mini Filter Driver issues (use-after-free CVE-2026-58613 and type confusion CVE-2026-80093), and a tcpip.sys out-of-bounds read (CVE-2026-49177). Each advisory gives the affected version and trigger mechanism, and Talos notes Snort coverage is available for detection.
 blog.talosintelligence.comadvisoryPublished and added 7 Oct 2026🛡️ Security
- lee1981 (@lee1981b) on X
Analysis of CVE-2026-105844, a CWE-1321 prototype-pollution vulnerability in @payloadcms/plugin-import-export that the vendor says can lead to unauthenticated remote code execution. It covers affected ranges (stable 3.0.0–3.87.x, canary 4.0.0-canary.0–canary.26), the fix (3.88.0 / 4.0.0-canary.27), the patched field-path guard against __proto__/constructor/prototype segments, and a six-step SOC hunting/triage playbook with two offline Python scripts for inspecting npm package trees and triaging request field-paths for prototype-sensitive values.
x.comadvisoryAdded 8 Oct 2026, published 7 Oct 2026🛡️ Security  Ayyaz (@ayyazdev) on X
A security researcher's thread breaks down CVE-2026-105135, an unpatched critical (CVSS 10.0) remote code execution vulnerability in InternLM's MindSearch agent with a public PoC. The flaw is in ExecutionAction.run in mindsearch/agent/graph.py, which passes the planner LLM's output directly to Python's exec() — if the model's reply lacks a code fence, the entire response is executed, and a crafted query to the /solve endpoint can get the model to emit attacker-controlled code that runs as root inside the shipped Docker container (which binds 0.0.0.0:8002). The author notes prompt filtering cannot fix this since the attacker only needs the model's output to contain code, and recommends running any agent that executes model-written code in a network-isolated, non-root sandbox kept off public ports.
x.comthreadAdded 7 Oct 2026, published 5 Oct 2026🛡️ Security- Dark Web Informer (@DarkWebInformer) on X
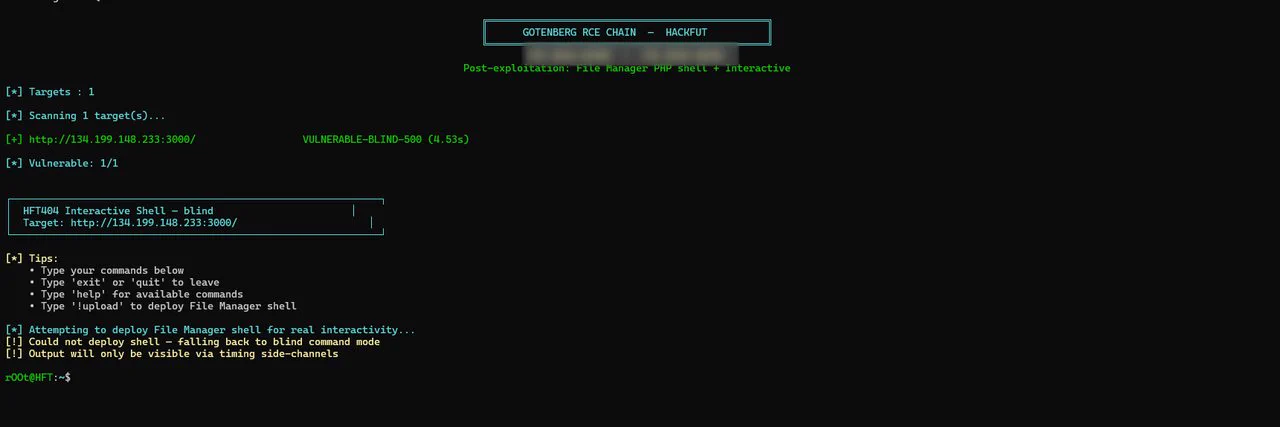
A public PoC chains CVE-2026-42589 and CVE-2026-40281 to achieve unauthenticated remote code execution against Gotenberg (a document/PDF-conversion microservice), abusing metadata injection flaws in the /forms/pdfengines/metadata/write endpoint. The tool supports vulnerability detection, interactive command execution, reverse shell delivery, and multi-target scanning against Gotenberg versions ≤8.30.1 (patched in 8.31.0).
x.comrepoPublished and added 5 Oct 2026🛡️ Security 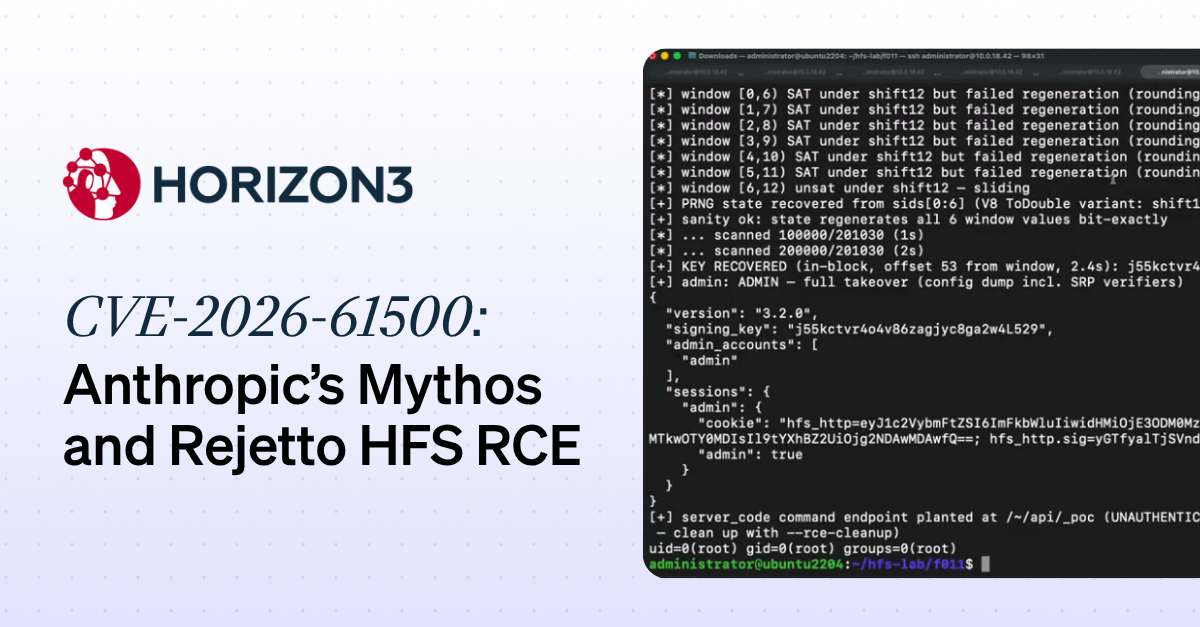 CVE-2026-61500: Rejetto HFS Session Forgery Vulnerability (found via Anthropic Mythos)
Horizon3.ai discloses CVE-2026-61500, a session-forgery vulnerability in Rejetto HTTP File Server (HFS) 3.x found using Anthropic's Mythos model. HFS seeds Koa's keygrip session-signing key with V8's insecure, invertible Math.random() PRNG and separately leaks raw Math.random() outputs through an unauthenticated login endpoint; by sampling a dozen leaked outputs and feeding them to the Z3 SMT solver, an attacker can recover the xorshift128+ internal state, step it backwards to the process-start signing key, and forge an admin session cookie that leads to remote code execution via HFS's built-in admin JavaScript execution feature. The piece walks through the full exploit chain and argues that Mythos independently chained the crypto weakness and the leak, built the Z3-based key-recovery solver, and produced a working PoC without additional prompting.
horizon3.aiwriteupAdded 7 Oct 2026, published 30 Sep 2026🛡️ Security Vulnerability Discovery and Exploitation Trends in the AI Era (Google Cloud)
Google Threat Intelligence Group analyzes vulnerability disclosure and exploitation trends from January 2025 to August 2026, finding disclosures doubled, exploitation nearly doubled, and AI-assisted discovery surfaces proportionally more Medium and High-risk flaws, with 50 percent leading to remote code execution versus 26 percent baseline. It documents real-world exploitation of an AI-discovered CVE in BeyondTrust PRA and a surge in vulnerabilities targeting the AI/LLM operational stack, especially agent orchestration frameworks like Langflow and Flowise and inference gateways like LiteLLM and vLLM, citing specific CVEs in those products.
 cloud.google.comarticleAdded 8 Oct 2026, published 30 Sep 2026🛡️ Security
- Critical Zero-Day Vulnerabilities Exploited in Citrix NetScaler ADC, Gateway
CISA alert amplifying Citrix's disclosure of ten NetScaler ADC and Gateway vulnerabilities (CVE-2026-88771 to CVE-2026-88779 and CVE-2026-107406). CVE-2026-88771 and CVE-2026-88772 are critical zero-days enabling independent remote code execution and are exploited globally; CVE-2026-88779 is a SAML SP/IdP denial-of-service that can force a reboot to trigger code injected via CVE-2026-88771. It advises checking for compromise before patching, preserving forensic evidence, forwarding logs to a SIEM, restoring a pre-compromise backup and rotating all secrets, and links a CISA SIGMA detection rule.
cisa.govadvisoryAdded 28 Sep 2026🛡️ Security - Vulnerability Database - OSV
CVE-2026-91931 is a critical remote code execution vulnerability in Flowise versions before 3.1.4, triggered through the platform's Custom MCP feature which invokes npx to run Model Context Protocol servers. A fix is available in 3.1.4; the flaw scores 9.0 (Critical) on CVSS, indicating an attacker can achieve arbitrary code execution likely via unsanitized input to the npx invocation path.
 osv.devadvisoryAdded 26 Sep 2026🛡️ Security
- Flowise MCP Security Bypass Enables RCE
GHSA advisory detailing three bypasses in Flowise's Custom MCP Server security controls (validateCommandFlags and validateArgsForLocalFileAccess in packages/components/nodes/tools/MCP/core.ts) that combine to achieve remote code execution: an unblocked `docker build` subcommand that pulls and runs a remote Dockerfile, a missing `--yes` long-flag alias on the npx blocklist (only `-y` was blocked) enabling arbitrary npm package execution, and a Unix absolute-path regex that fails to catch double-leading-slash paths (`//root/...`), allowing `node` to execute an uploaded local file. Any authenticated Flowise user (or an API key with chatflow view/update rights) can chain these to fully compromise the host via a prediction API call.
github.comadvisoryAdded 26 Sep 2026🛡️ Security  Discovering and exploiting a remote code execution vulnerability in OpenCode (GHSA-632h-h47v-g4x4)
GHSA-632h-h47v-g4x4 is an RCE in OpenCode's /global/upgrade endpoint, fixed in 1.18.22. The target value reached `npm install -g opencode-ai@TARGET`, so an attacker could supply a malicious tarball URL with a preinstall script. A text/plain HTML form bypassed CORS through top-level navigation because the handler parsed JSON without checking Content-Type. Affects 1.14.30 to 1.18.21 installed via npm, pnpm or Bun.
 securitylabs.datadoghq.comwriteupAdded 29 Oct 2026, published 24 Sep 2026🛡️ Security
- CVE-2026-94127: Critical Unauthenticated RCE in F5 BIG-IP APM
Rapid7's ETR writeup covers CVE-2026-94127, a critical heap-based buffer overflow (CVSS 9.8) in F5 BIG-IP Access Policy Manager that allows unauthenticated remote code execution via crafted traffic. Exploitation requires a virtual server with both an APM access policy and an OAuth profile configured, affects the data plane (including Appliance mode), and has been added to CISA KEV; F5 provides hotfixes for the 21.1.0, 17.5.0, and 17.1.0 release trains plus an iRule workaround for those unable to patch immediately.
rapid7.comadvisoryAdded 7 Oct 2026, published 23 Sep 2026🛡️ Security  WordPress 7.1.2 Release (CVE-2026-87902 path-traversal RCE fix)
WordPress 7.1.2 patches CVE-2026-87902 (GHSA-7hp8-65ch-5whp), a critical unauthenticated path-traversal flaw where page template resolution can be manipulated to include an attacker-chosen readable local PHP file outside the active theme directory. Under certain server and active-theme preconditions this local file inclusion escalates to remote code execution. The security fix was backported to all WordPress branches back to 4.7; discovery credited to researcher Robert Ressl.
 wordpress.orgadvisoryAdded 28 Sep 2026, published 22 Sep 2026🛡️ Security
 Graphalgo campaign spreads to Terraform providers and Go Modules
Aikido documents the Graphalgo malware campaign's expansion beyond NPM into two malicious Terraform providers (gocommunity-io/dockerd and the kreuzwerker/docker typosquat kreuzwenker/docker) and two Go modules (gocommunity.io/orderedbtree, gogets.dev/btreex), marking the first observed systematic Terraform provider malware distribution. The payload is a Go port of Graphalgo sharing blockchain infrastructure, Slack C2, and a public key with prior JS/NPM samples; it activates only under specific hash-gated runtime conditions (targeted attack indicator), then deploys a Go RAT with dual C2 channels — an Ethereum (Arbitrum Sepolia) smart-contract dead drop and Slack bot messaging — plus self-delete and remote code execution capabilities. The threat actor also stood up two fake Go package ecosystem websites (gocommunity.io, gogets.dev) to socially engineer developers and backdated Git commits to obscure module publication timing.
aikido.devwriteupPublished and added 22 Sep 2026🛡️ Security ToolLeak: Tool-Invocation Attacks on Coding Agents
This arXiv paper red-teams six popular coding agents (Cursor, Claude Code, GitHub Copilot, Windsurf, Cline, Trae) from a tool-invocation angle, discovering ToolLeak — a general vulnerability that exfiltrates system prompts via benign argument retrieval during tool calls. Building on leaked security info, the authors craft a two-channel prompt injection (hidden in tool descriptions and tool return values) that hijacks agent tool invocation to achieve remote code execution, succeeding on 19 of 25 agent-LLM pairs for prompt leakage and on every tested pair for RCE across backends including Claude Sonnet 4/4.5, Grok-4, and GPT-5.
 arxiv.orgpaperAdded 22 Sep 2026, published 21 Sep 2026🛡️ Security
 Hackers breach OpenAI using Claude tools, gaining access to employee accounts and the company
Hacktron AI researchers chained a heap overflow in an outdated libheif library (triggered via a malicious HEIF profile-picture upload on OpenAI's Discourse forum) into remote code execution, then pivoted through an SSO session-isolation flaw to hijack an OpenAI employee's ChatGPT/Codex account and its linked GitHub, Slack, and email access, proving impact with an internal pull request. The exploit code for the heap overflow was generated by Claude Opus 5 (an 'authorized, cybersecurity-configured' variant) after the model was fed raw server data describing the bug, illustrating AI-assisted vulnerability exploitation in a real bug bounty. OpenAI patched within 14 hours and paid a $6,500 bounty; full resolution took 72 hours.
 tomshardware.comarticleAdded 26 Sep 2026, published 18 Sep 2026🛡️ Security
 The Apple Security Update Review for September 2026
Zero Day Initiative's monthly Apple patch review covers the September 2026 release (macOS 27/Sequoia 15.8/Tahoe 26.7, iOS/iPadOS 27 & 26.7, visionOS, watchOS, tvOS, Safari, Xcode), totaling 273 CVEs. It highlights CVE-2026-65400 (Screen Sharing Server authentication bypass, 9.8 CRITICAL, actively exploited per CISA KEV), CVE-2026-65414 (Bluetooth remote code execution, 9.8 CRITICAL, affecting all eight platforms), and CVE-2026-65346 (ImageIO arbitrary code execution via malicious image, 8.8 HIGH), plus a full CVE-by-component-by-platform table with CVSS scores where NVD/CISA-ADP has assigned them.
 zerodayinitiative.comarticleAdded 28 Sep 2026, published 16 Sep 2026🛡️ Security
 StyleSmuggler fix: patch the Magento and Adobe Commerce RCE
Aikido Security's writeup on "StyleSmuggler," a remote code execution vulnerability in Magento and Adobe Commerce, covering the fix/patch for the flaw. Page content was not retrieved, so specifics of the exploitation technique and affected versions could not be confirmed directly.
aikido.devadvisoryPublished and added 7 Sep 2026🛡️ Security Breaking Claude Code Opus 5 Auto Mode · Embrace The Red
Embrace The Red (Johann Rehberger) demonstrates an indirect prompt injection attack chain that achieves 60-80% success rates hijacking Claude Code Opus 5 Auto Mode into remote code execution, contrasting with a vendor-run benchmark that reported 0.00% attack success. The chain nudges Claude from WebFetch to curl, delivers a malicious ZIP archive, and exploits Python module shadowing (a poisoned struct.py) when Claude writes its own decoder script, ultimately downloading and executing a payload that establishes C2 and even spawns a nested headless Claude Code instance. Anthropic closed the report as "Informative, working as designed," framing Auto Mode as a best-effort classifier rather than a security boundary, reinforcing that sandboxing and egress control remain necessary mitigations.
embracethered.comwriteupAdded 31 Aug 2026🛡️ Security- PaperCut Zero-Day: Active Exploitation and Pre-Auth RCE
Huntress details active exploitation of an authorization-bypass flaw in PaperCut NG/MF (CVE-2026-81578) chained with an unsafe dynamic class-loading vulnerability in the database connection utilities (CVE-2026-82078) to achieve unauthenticated remote code execution in the PaperCut Application Server. The writeup covers Huntress's own observed intrusions (base64-encoded recon commands, dropped Java .class payloads decompiled with Fernflower, log-wiping behavior, and an Apache Derby pwn database indicator), a reproduced PoC achieving SYSTEM-level code execution via pc-app.exe, and detailed patching, evidence-preservation, and hunting guidance across PaperCut's staged emergency patches.
huntress.comadvisoryAdded 3 Sep 2026, published 28 Aug 2026🛡️ Security  How AI orchestration platforms ship RCE by design | Ebook/Report | Endor Labs
Endor Labs research audits seven AI orchestration and workflow-automation platforms — NocoBase, Flowise, Langflow, Dify, Activepieces, Kestra, and Apache Airflow — across four languages, documenting fourteen findings that range from an accidental sandbox escape to remote code execution that is architecturally built in. The core argument is that these tools inherited a single-user developer-tool trust model (anyone who can touch a workflow is trusted to run code on the host) while being deployed as multi-tenant HTTP services with webhooks and credentials to cloud, databases, and internal APIs, so the threat model never caught up to how they're actually run in CI/CD and agentic AI stacks.
endorlabs.compaperAdded 3 Sep 2026, published 26 Aug 2026🛡️ Security Critical Elementor Pro File Upload Flaw Enables Unauthenticated Remote Code Execution on WordPress Sites
CVE-2026-32475 (CVSS 9.0) is an unauthenticated arbitrary file upload leading to RCE in Elementor Pro's Forms module (versions up to 4.2.1), caused by the extension-blocklist check and the file-move step running in two separate loops with different empty-file handling, letting a two-part file submission bypass the blocklist and drop a PHP webshell into the public wp-content/uploads/elementor/forms/ directory. The post also flags related WordPress core CVE-2026-65640 (CVSS 8.8, fixed in 7.0.4), an Author-level RCE via malicious PostScript upload requiring Imagick and Ghostscript. Fix: upgrade Elementor Pro to 4.2.2+ and WordPress core to 7.0.4, and audit the uploads/elementor/forms directory for planted PHP files.
orca.securityadvisoryAdded 3 Sep 2026, published 20 Aug 2026🛡️ Security Yet another RCE in Gogs, but it's fixed this time!
Aikido researchers detail how an AI pentesting agent found a path traversal in Gogs' organization name handling (CVE-2026-52813), which they manually escalated to full Remote Code Execution by planting a bare git repository inside a worktree and overwriting its hooks/update file to trigger command execution on push. The post also covers a git-receive-pack/git-upload-pack service parameter confusion causing an authorization bypass allowing writes to private repos by read-only users (CVE-2026-52810, with an unpatched case-sensitivity bypass and manual code fix provided), and a stored XSS in Gogs' Jupyter notebook rendering via an outdated notebookjs library that bypasses bluemonday sanitization via onerror handlers set during innerHTML assignment.
aikido.devwriteupAdded 3 Sep 2026, published 19 Aug 2026🛡️ Security You’re Back In The Room (Citrix NetScaler Pre-Auth RCE CVE-2026-8452(?))
watchTowr Labs analyzes a pre-authentication remote code execution flaw in Citrix NetScaler ADC and Gateway, likely CVE-2026-8452, patched in versions 14.1-72.61 and 13.1-63.18. The bug is a heap overflow during SAML SignedInfo canonicalization, triggered by an oversized PrefixList attribute, which the researchers chain into a write-what-where primitive and full RIP control on non-PIE, no-ASLR builds. They describe dropping a PHP webshell, disabling crash signal handlers to survive without a full device reboot, and escalating from the nobody web server user to root via SUID on /bin/sh.
 labs.watchtowr.comwriteupAdded 30 Oct 2026, published 14 Aug 2026🛡️ Security
 Potential for Remote Code Execution in Microsoft SCCM via Newly-Discovered Exploit Chain
XM Cyber researchers detail a four-stage exploit chain in Microsoft SCCM (Configuration Manager) that lets any unprivileged domain user achieve SYSTEM-level remote code execution on the primary site server: a missing authorization check on the AdminService UploadExtensionInChunks endpoint (CVE-2026-47301), a weak code-signing check that accepts any commercial certificate, a "CabSlip" Zip-Slip-style path traversal in CAB extraction giving arbitrary file write, and DLL hijacking of adsource.dll loaded by the SYSTEM-level SMS Executive service. Microsoft patched the RBAC bypass in July 2026, but the rest of the chain remains exploitable via the built-in Operations Administrator role until a full fix in ConfigMgr 2609 (October 2026); the article also gives log-based detection guidance (AdminService.log DirectoryNotFoundException/HTTP 500 patterns) and interim mitigations.
 xmcyber.comwriteupAdded 3 Sep 2026, published 13 Aug 2026🛡️ Security
- From Screen Share to Root Access: Breaking Down CVE-2026-43760 and CVE-2026-65400 on macOS
Huntress breaks down two macOS Screen Sharing (screensharingd/RFB) vulnerabilities patched by Apple: CVE-2026-43760, an authenticated confused-context bug letting legacy-VNC users read/write arbitrary files as root, and CVE-2026-65400, a pre-authentication bug in the SRP handshake that lets an unauthenticated remote attacker read/write any filesystem artifact as root and achieve remote code execution via LaunchDaemons or shell startup file persistence. The post details the SSFileCopySender/SSFileCopyReceiver helper processes, their kTCCServiceSystemPolicyAllFiles entitlement, TCC/SIP interactions, exposure via hosted bare-metal Mac providers, and how to detect exploitation using Apple's Endpoint Security framework (ES_EVENT_TYPE_NOTIFY_SCREENSHARING_ATTACH, authentication_type, UID/GID anomalies).
huntress.comwriteupAdded 3 Sep 2026, published 7 Aug 2026🛡️ Security  MCP Configuration Poisoning: Owning Your Machine With Just A Text File
Explains how a malicious mcp.json in a repository, with attacker-controlled "command" and "args" fields, gives remote code execution when an IDE, scanner, CI/CD pipeline or agent loads it automatically. Walks through a PoC where running Snyk's Agent Scan (snyk-agent-scan) on a poisoned config executes arbitrary commands; Snyk fixed it in 0.5.0 after a duplicate report. Offers mitigations for tool builders (sandboxing, pattern blocking, human-in-the-loop prompts hardened against "Lies in the Loop" dialog forging) and for users (sandbox untrusted repos).
 checkmarx.comwriteupAdded 10 Sep 2026, published 23 Jul 2026🛡️ Security
 AWS Kiro RCE: Prompt Injection to Code Execution | Kodem
Kodem and Intezer disclose a remote code execution flaw in AWS's agentic IDE Kiro (CVE-2026-10591). ~/.kiro/settings/mcp.json was writable by the agent via fsWrite without approval and auto-reloaded, so hidden prompt-injection text on a fetched web page could register a malicious MCP server that runs attacker code. The post gives a PoC using white 1px text and a Node.js callback server, tested on Kiro 0.9.2 and 0.10.16, the fix confirmed in 0.11.130, and the disclosure timeline. It shows how human-in-the-loop approval fails as a security boundary when the agent can edit its own trust configuration.
 kodemsecurity.comwriteupAdded 23 Jul 2026, published 19 Jul 2026🛡️ Security
 Unauthenticated RCE in WordPress core (wp2shell), via SQL injection
WordPress core versions 6.9.0-6.9.4 and 7.0.0-7.0.1 (plus 7.1 beta) contained an unauthenticated remote code execution flaw stemming from REST API batch-route confusion at /wp-json/batch/v1 that chains into SQL injection, exploitable against a stock install with no plugins. WordPress shipped emergency fixes (6.9.5, 7.0.2, 7.1 beta2) and enabled forced auto-updates given the scale of exposure (500M+ WordPress sites); a separate SQLi patched in the same round affects 6.8.x, fixed in 6.8.6. Researcher Adam Kues (Searchlight Cyber) reported the flaw and released a checker tool at wp2shell.com; the post also covers interim mitigations (blocking the batch route via WAF/plugin) for sites that can't patch immediately.
aikido.devwriteupAdded 3 Sep 2026, published 17 Jul 2026🛡️ Security AI Security Briefing
GHSA-3pvh-63gf-j9mw discloses an authenticated remote code execution vulnerability in LangBot, an open-source AI chatbot/agent framework, caused by its MCP Server Configuration feature. Because LangBot's mcp.py uses Anthropic's StdioServerParameters to launch MCP servers, any authenticated user can add a "STDIO" MCP entry with an arbitrary shell command and have it executed on the server, enabling data exfiltration, reverse shells, or full host compromise (CWE-78 OS command injection).
github.comadvisoryPublished and added 17 Jul 2026🛡️ Security The Cursor deeplink vulnerability that turns a “review this PR” click into remote code execution
Adversa AI researchers show how a crafted cursor:// deeplink, disguised as a GitHub "review this PR" notification, nests a double-URL-encoded mcp/install URI inside a pr-review link to silently trigger Cursor's MCP server install dialog. A second variant pads the install dialog's single-line arguments field with tab characters so a malicious command tail (launching cmd.exe and exfiltrating via curl) scrolls off-screen while the user approves what looks like a harmless "calc" command, giving unsandboxed code execution as the victim. Both bugs were reported to Cursor, closed as duplicates, and remain exploitable on the latest build (3.9.8) months after the related CVE-2025-54133 fix was supposed to surface install arguments; the researchers name this bug class "DeepJack" and note most mainstream coding agents register similarly under-scrutinized URL handlers.
 adversa.aiwriteupAdded 7 Oct 2026, published 15 Jul 2026🛡️ Security
- Orca Security: Maximum-Severity Adobe ColdFusion RCE
Orca Security writeup covering CVE-2026-48282, a maximum-severity remote code execution vulnerability in Adobe ColdFusion. The page content could not be retrieved, so technical details (root cause, exploitation vector, affected versions) are unconfirmed beyond the title.
orca.securityadvisoryPublished and added 15 Jul 2026🛡️ Security - CVE-2026-61447
CVE-2026-61447 describes a critical (CVSS 4.0 score 10.0) remote code execution vulnerability in PraisonAI versions before 1.6.78, rooted in CodeAgent._execute_python(), which runs LLM-generated Python code with no AST validation, import restrictions, or sandbox enforcement. An attacker who can influence the LLM's output via prompt injection can exfiltrate environment secrets and achieve arbitrary code execution on the host, making it a textbook agentic-code-execution flaw (CWE-94).
 nvd.nist.govadvisoryPublished and added 12 Jul 2026🛡️ Security
- Lateral Movement Attack: Techniques, Detection & Prevention
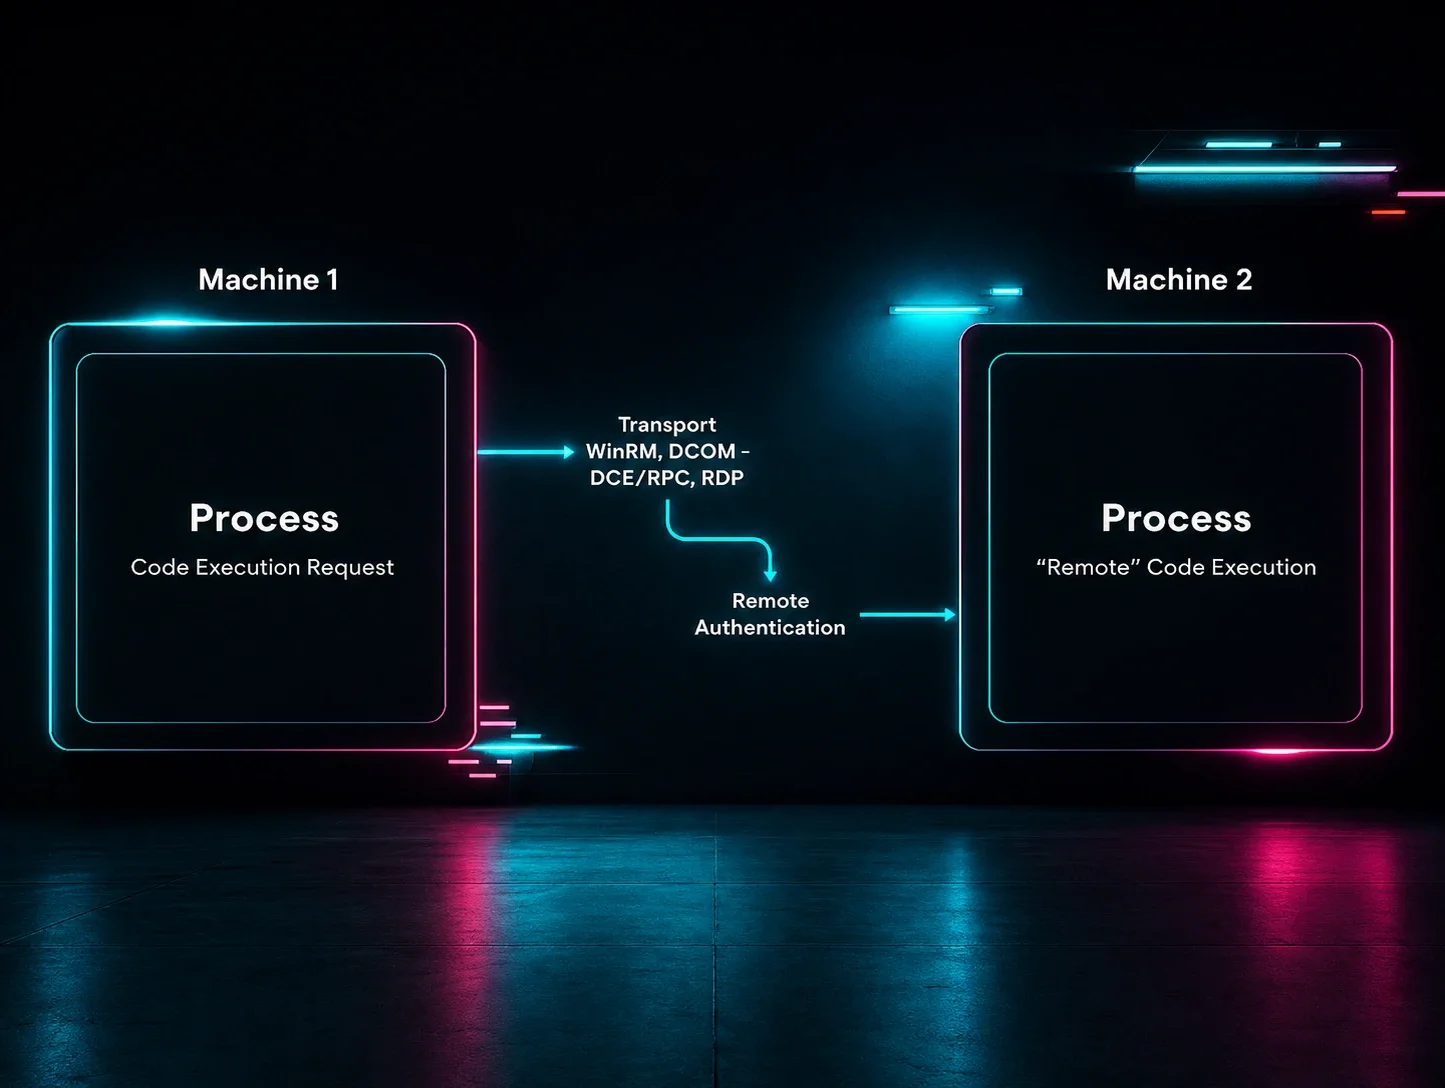
Huntress details how its Managed EDR and ITDR products detect lateral movement by correlating remote authentication events with subsequent process execution (action pillars: initial code execution, transport, remote authentication, remote code execution) rather than tracking source-side network connections. The piece walks through real-world scenarios including MMC20.Application DCOM abuse, LSASS credential dumping via rundll32/comsvcs.dll (as used by Impacket dcomexec.py and NetExec mmcexec.py), SQL Admin account abuse to enable RDP, and ransomware-precursor activity (shadow copy deletion, ntds.dit exfiltration) caught before payload deployment.
huntress.comwriteupAdded 3 Sep 2026, published 1 Jul 2026🛡️ Security  JFrog: PixelSmash
JFrog Security Research discloses CVE-2026-8461 ("PixelSmash"), a critical heap out-of-bounds write in FFmpeg's MagicYUV decoder caused by a rounding mismatch between chroma-plane allocation and slice-height calculation. The team escalates the OOB write into reliable remote code execution by hijacking the AVBuffer.free function pointer to call system(), demonstrating full RCE via a 50KB crafted AVI against a Jellyfin media server (through automatic library/ffprobe scanning) and a Nextcloud instance (via video thumbnail preview generation), plus DoS crashes across mpv, Kodi, OBS Studio, Immich, PhotoPrism and vLLM. The post frames the bug as a software supply-chain issue since libavcodec is a silent transitive dependency in hundreds of downstream media applications, and covers detection, patching, and build-time workarounds.
 jfrog.comwriteupPublished and added 22 Jun 2026🛡️ Security
 watchTowr Labs: Splunk Enterprise CVE-2026-20253 Pre-Auth RCE via PostgreSQL Sidecar
watchTowr Labs analyzes CVE-2026-20253, a pre-authentication vulnerability in the PostgreSQL sidecar service of Splunk Enterprise 10 and later. The sidecar's backup and restore API lacks authentication and is reachable through the main web interface. The write-up explains the root cause and which deployments are vulnerable by default, notably Splunk Enterprise on AWS, and shows how the flaw escalates to remote code execution. It also releases a non-exploitative detection script that tells vulnerable hosts from patched ones.
labs.watchtowr.comwriteupAdded 6 Sep 2026, published 12 Jun 2026🛡️ Security Orca Security: Critical Pre-Auth RCE in ChromaDB Threatens AI Infrastructure
CVE-2026-45829 (CVSS 10.0) is a pre-authentication remote code execution flaw in ChromaDB's Python FastAPI server, versions 1.0.0 through 1.5.8. The server processes user-controlled embedding function configuration before authentication checks, letting an attacker send a crafted collection-creation request referencing a malicious HuggingFace model with trust_remote_code enabled to force arbitrary Python code execution pre-auth. Discovered by researcher Azraelxuemo and later HiddenLayer (dubbed "ChromaToast Served Pre-Auth"); Shodan-based scanning found roughly 73% of internet-exposed ChromaDB instances still vulnerable, with fixes shipped in 1.5.9.
orca.securityadvisoryPublished and added 22 May 2026🛡️ Security Orca Security: CVE-2026-9082
Orca Security breaks down CVE-2026-9082, a critical unauthenticated SQL injection in Drupal core's database abstraction API affecting PostgreSQL-backed sites running versions 8.9.0 through 11.3.9. The flaw stems from insufficient query sanitization and can lead to full data exposure, privilege escalation, and in some configurations remote code execution; Drupal has shipped patched releases (e.g. 11.3.10, 10.6.9) and MySQL/MariaDB sites are unaffected by the SQLi itself but should still update for bundled Symfony/Twig fixes.
orca.securityadvisoryPublished and added 22 May 2026🛡️ Security Orca Security: Critical Apache HTTP Server HTTP/2 Vulnerability Could Enable Remote Code Execution
Orca Security's write-up of CVE-2026-23918 (CVSS 8.8), a double-free memory corruption bug in Apache HTTP Server's mod_http2 stream cleanup logic. An unauthenticated attacker can trigger it by sending crafted HTTP/2 HEADERS frames followed by an early RST_STREAM with a non-zero error code. This causes heap corruption, crashes, and possibly remote code execution. Version 2.4.66 is affected and 2.4.67 fixes it. Public PoC details exist, but no in-the-wild exploitation had been reported. Disabling HTTP/2 is given as a temporary workaround.
orca.securityadvisoryPublished and added 8 May 2026🛡️ Security Zero-Click RCE in MCP
Lakera researchers demonstrate a zero-click exploit chain against Cursor IDE configured with a Google Docs MCP server: an attacker silently shares a malicious document via the Google Docs API, which Cursor's agent retrieves and treats as trusted context, leading to prompt injection that abuses Cursor's command allow-list to achieve persistent remote code execution and credential/data exfiltration. The attack requires no victim interaction and exploits intended MCP/agentic IDE functionality rather than a patchable bug, showing that even "safe" MCP servers become dangerous when combined with implicit trust in external data and permission-fatigue-driven allow-listing.
 lakera.aiwriteupPublished and added 6 May 2026🛡️ Security
 Critical Buffer Overflow Vulnerability in PAN-OS Exploited in-the-Wild | Wiz Blog
Wiz details CVE-2026-0300, a CVSS 9.3 buffer overflow in PAN-OS's User-ID Authentication Portal (Captive Portal, ports 6081/6082) that lets unauthenticated attackers trigger an out-of-bounds write and achieve remote code execution with root privileges. Palo Alto Networks has confirmed limited in-the-wild exploitation against internet-exposed instances; Wiz reports 7% of environments have publicly exposed PAN-OS and Shodan shows 67 exposed servers on port 6081. Guidance includes patching once fixes ship, restricting the Authentication Portal to trusted networks, and disabling it if unused.
 wiz.ioadvisoryAdded 5 Sep 2026, published 6 May 2026🛡️ Security
 GitHub RCE Vulnerability: CVE-2026-3854 Breakdown | Wiz Blog
Wiz Research's technical breakdown of CVE-2026-3854, a critical vulnerability in GitHub's internal git push pipeline (babeld, gitauth, gitrpcd, pre-receive hook) that let any authenticated user achieve unsandboxed remote code execution with a single `git push -o` command. The root cause is a semicolon-delimiter injection into the internal X-Stat header, chained through unsanitized push options to override security fields (rails_env, custom_hooks_dir, repo_pre_receive_hooks) and escape the custom-hooks sandbox, ultimately giving RCE as the shared git user on GitHub.com's multi-tenant storage nodes and full compromise on GitHub Enterprise Server. Wiz also highlights using AI-augmented reverse engineering (IDA MCP) to rapidly analyze GitHub's closed-source compiled binaries and reconstruct the internal protocol, which enabled the discovery.
wiz.iowriteupAdded 5 Sep 2026, published 28 Apr 2026🛡️ Security MCPJam Inspector RCE (CVE-2026-23744)
CVE-2026-23744 describes an unauthenticated remote code execution vulnerability in MCPJam Inspector (versions ≤1.4.2), a debugging/testing tool for MCP servers. The tool's HTTP server binds to 0.0.0.0 by default and exposes a server-management endpoint with no authentication, letting any network-adjacent (or internet-facing) attacker install a malicious MCP server and execute arbitrary code on the developer's host with no user interaction, CVSS 9.8. Fixed in v1.4.3, which restricts the bind address and adds endpoint authentication.
 vulnerablemcp.infoadvisoryAdded 30 Sep 2026, published 1 Feb 2026🛡️ Security
- Ni8mare and N8scape flaws among multiple critical vulnerabilities affecting n8n
Rapid7's ETR write-up on "Ni8mare," an exploit chain against n8n automation software anchored by CVE-2026-21858 (CVSS 10.0), an unauthenticated file read flaw triggered by improper content-type validation on custom webhook file-upload forms that lets an attacker overwrite internal JSON to read arbitrary files and forge admin session tokens. That access can be chained with four authenticated CVEs — CVE-2025-68613 (expression language injection RCE), CVE-2025-68668 (Pyodide Python node command execution), CVE-2025-68697 (legacy Code node file read/write), and CVE-2026-21877 (arbitrary file write RCE, CVSS 9.9) — for full remote code execution. Cyera and researcher Valentin Lobstein published separate technical analyses and PoCs on the same day; Rapid7 lists affected version ranges for each CVE and recommends upgrading self-hosted n8n to 1.121.0+.
rapid7.comadvisoryAdded 26 Sep 2026, published 8 Jan 2026🛡️ Security






Showing 90 of 91
Show more