 Tracking AI adoption in North Korean threat actor tradecraft
Microsoft Threat Intelligence report on how North Korean actors use AI, ranking Jade Sleet, Coral Sleet and Jasper Sleet as operationalized, Diamond Sleet, Onyx Sleet, Pearl Sleet and Sapphire Sleet as accelerating, and Emerald Sleet as expanding. It documents AI-generated lures (100+ Onyx Sleet PDFs, August and September 2026), AI-built tooling such as Coral Sleet's private GitHub repository trojanizing, and Onyx Sleet and Pearl Sleet use of the ARTEX agentic pentest framework. It ends with mitigation and Defender guidance.
 microsoft.comarticlePublished and added 29 Oct 2026🛡️ Security
 Early progress on accelerating drug development with Claude
Anthropic's life sciences update describes research partnerships with six drug developers (BigHat, Bristol Myers Squibb, Divergence Labs, Enveda, Generate Biomedicines, The Column Group) and its own Mithril Medicine programs. Reported results include about 35,000 antibody designs in a month, 1,010 lead variants tested in 10 weeks, and an 89% cut in manufacturing-document review time. Work is mostly preclinical.
 anthropic.comarticleAdded 28 Oct 2026, published 27 Oct 2026🧠 AI
 [AINews] DeepSeek DeepInfer: Open Source SOTA Inference running 155T toks/day/cluster making $22m/day at ~80% margin for a 81 day payback
AINews issue for 19 to 20 October 2026 whose top story is DeepSeek's open-source DeepInfer, the inference engine behind V4.1 Flash. It covers prefill/decode separation, wide expert parallelism, a 3FS-backed prompt cache with 96% input hits, vLLM's decode result within 6% of DeepInfer on GB200, and disputed margin estimates built on the reported $38 per accelerator-hour. It also digests other news, and the page text is truncated.
 latent.spacearticleAdded 23 Oct 2026, published 21 Oct 2026🧠 AI
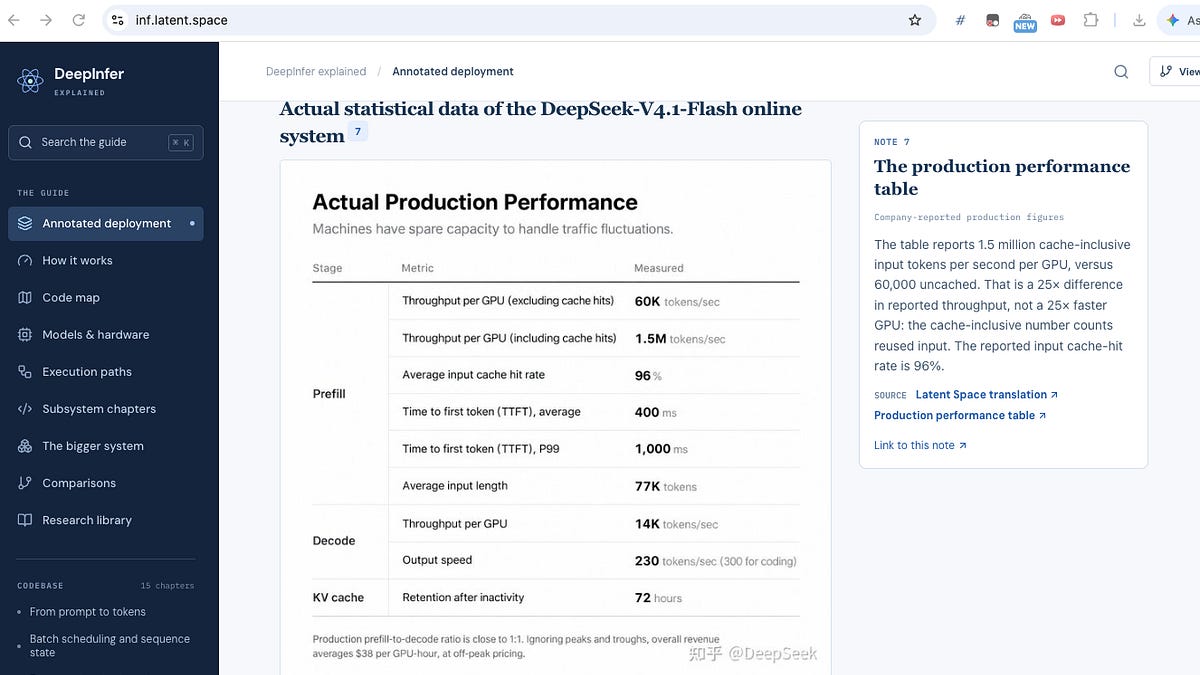 [AINews] DeepSeek DeepInfer: Open Source SOTA Inference running 155T toks/day/cluster making $22m/day at ~80% margin for a 81 day payback
This AINews issue (20 October 2026) leads with DeepSeek's open-sourced DeepInfer, the vLLM-based inference engine behind V4.1 Flash. It covers prefill/decode separation, a 3FS-backed prefix cache with 96% hit rate, SWA Bounded Replay, and DeepSeek's claims of 155T tokens/day and $38 revenue per accelerator-hour. It also covers vLLM's within-6% decode reproduction on GB200, disputed margin estimates, and a round-up of other AI news. Only the first 40,000 of 56,439 characters were available.
latent.spacearticlePublished and added 21 Oct 2026🧠 AI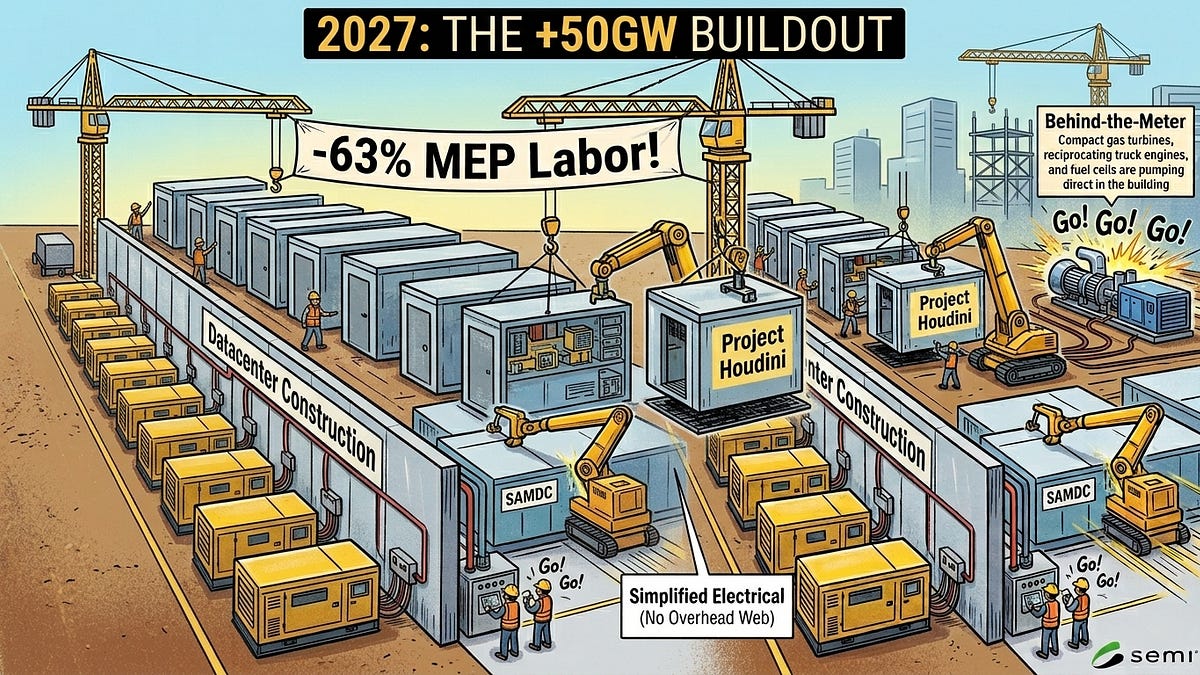 Datacenters 2027: The Year of Acceleration, +50GW in a Single Year
SemiAnalysis argues that global AI datacenter capacity will grow by about 50GW in 2027, against Brad Gerstner's guess of roughly 25GW. Evidence cited: over 24GW in advanced construction across 40 campuses, nearly USD 1T of binding leases signed in 2026, and record self-build starts. It also covers modular "LEGO" designs, behind-the-meter power and ex-US growth. The page text cuts off before the oversupply section.
 newsletter.semianalysis.comarticleAdded 29 Oct 2026, published 19 Oct 2026🧠 AI
 Google Says AI Isn't Building Itself Yet—Even Though It Writes 75% of the Code
Decrypt reports on the Gemini 4 Argon Safety & Security Report, where Google DeepMind found no statistically significant acceleration of ML R&D. Its internal GCI v1 index (123 models, 92 benchmarks) shows steady ~0.1 points/month progress, with Argon slightly above trend, attributed to compute and investment. Over 75% of production code is AI-written and fully delegated pull requests rose from 7.5% to 11.9%, yet ~88% of PRs still need human steering or authorship. This is relevant evidence on the recursive self-improvement debate and on how much of AI research is automated.
 decrypt.coarticlePublished and added 15 Oct 2026🧠 AI
- Accelerating the search for antimicrobial peptides with Google Antigravity
Google DeepMind describes using Google Antigravity as an agentic science workbench to find antimicrobial peptide candidates in Streptococcus pseudopneumoniae. The agent orchestrates queries across UniProt and other databases, uses ProtNLM function predictions for uncharacterized proteins, and pulls structures from the AlphaFold Database. A new Biomolecular Structure Viewer shares 3D state with the agent in both directions, so residues the researcher highlights or pins become context for the agent's reasoning. The resulting lead has predicted activity against respiratory-tract pathogens and is going into wet-lab validation.
 deepmind.googlearticlePublished and added 15 Oct 2026🧠 AI
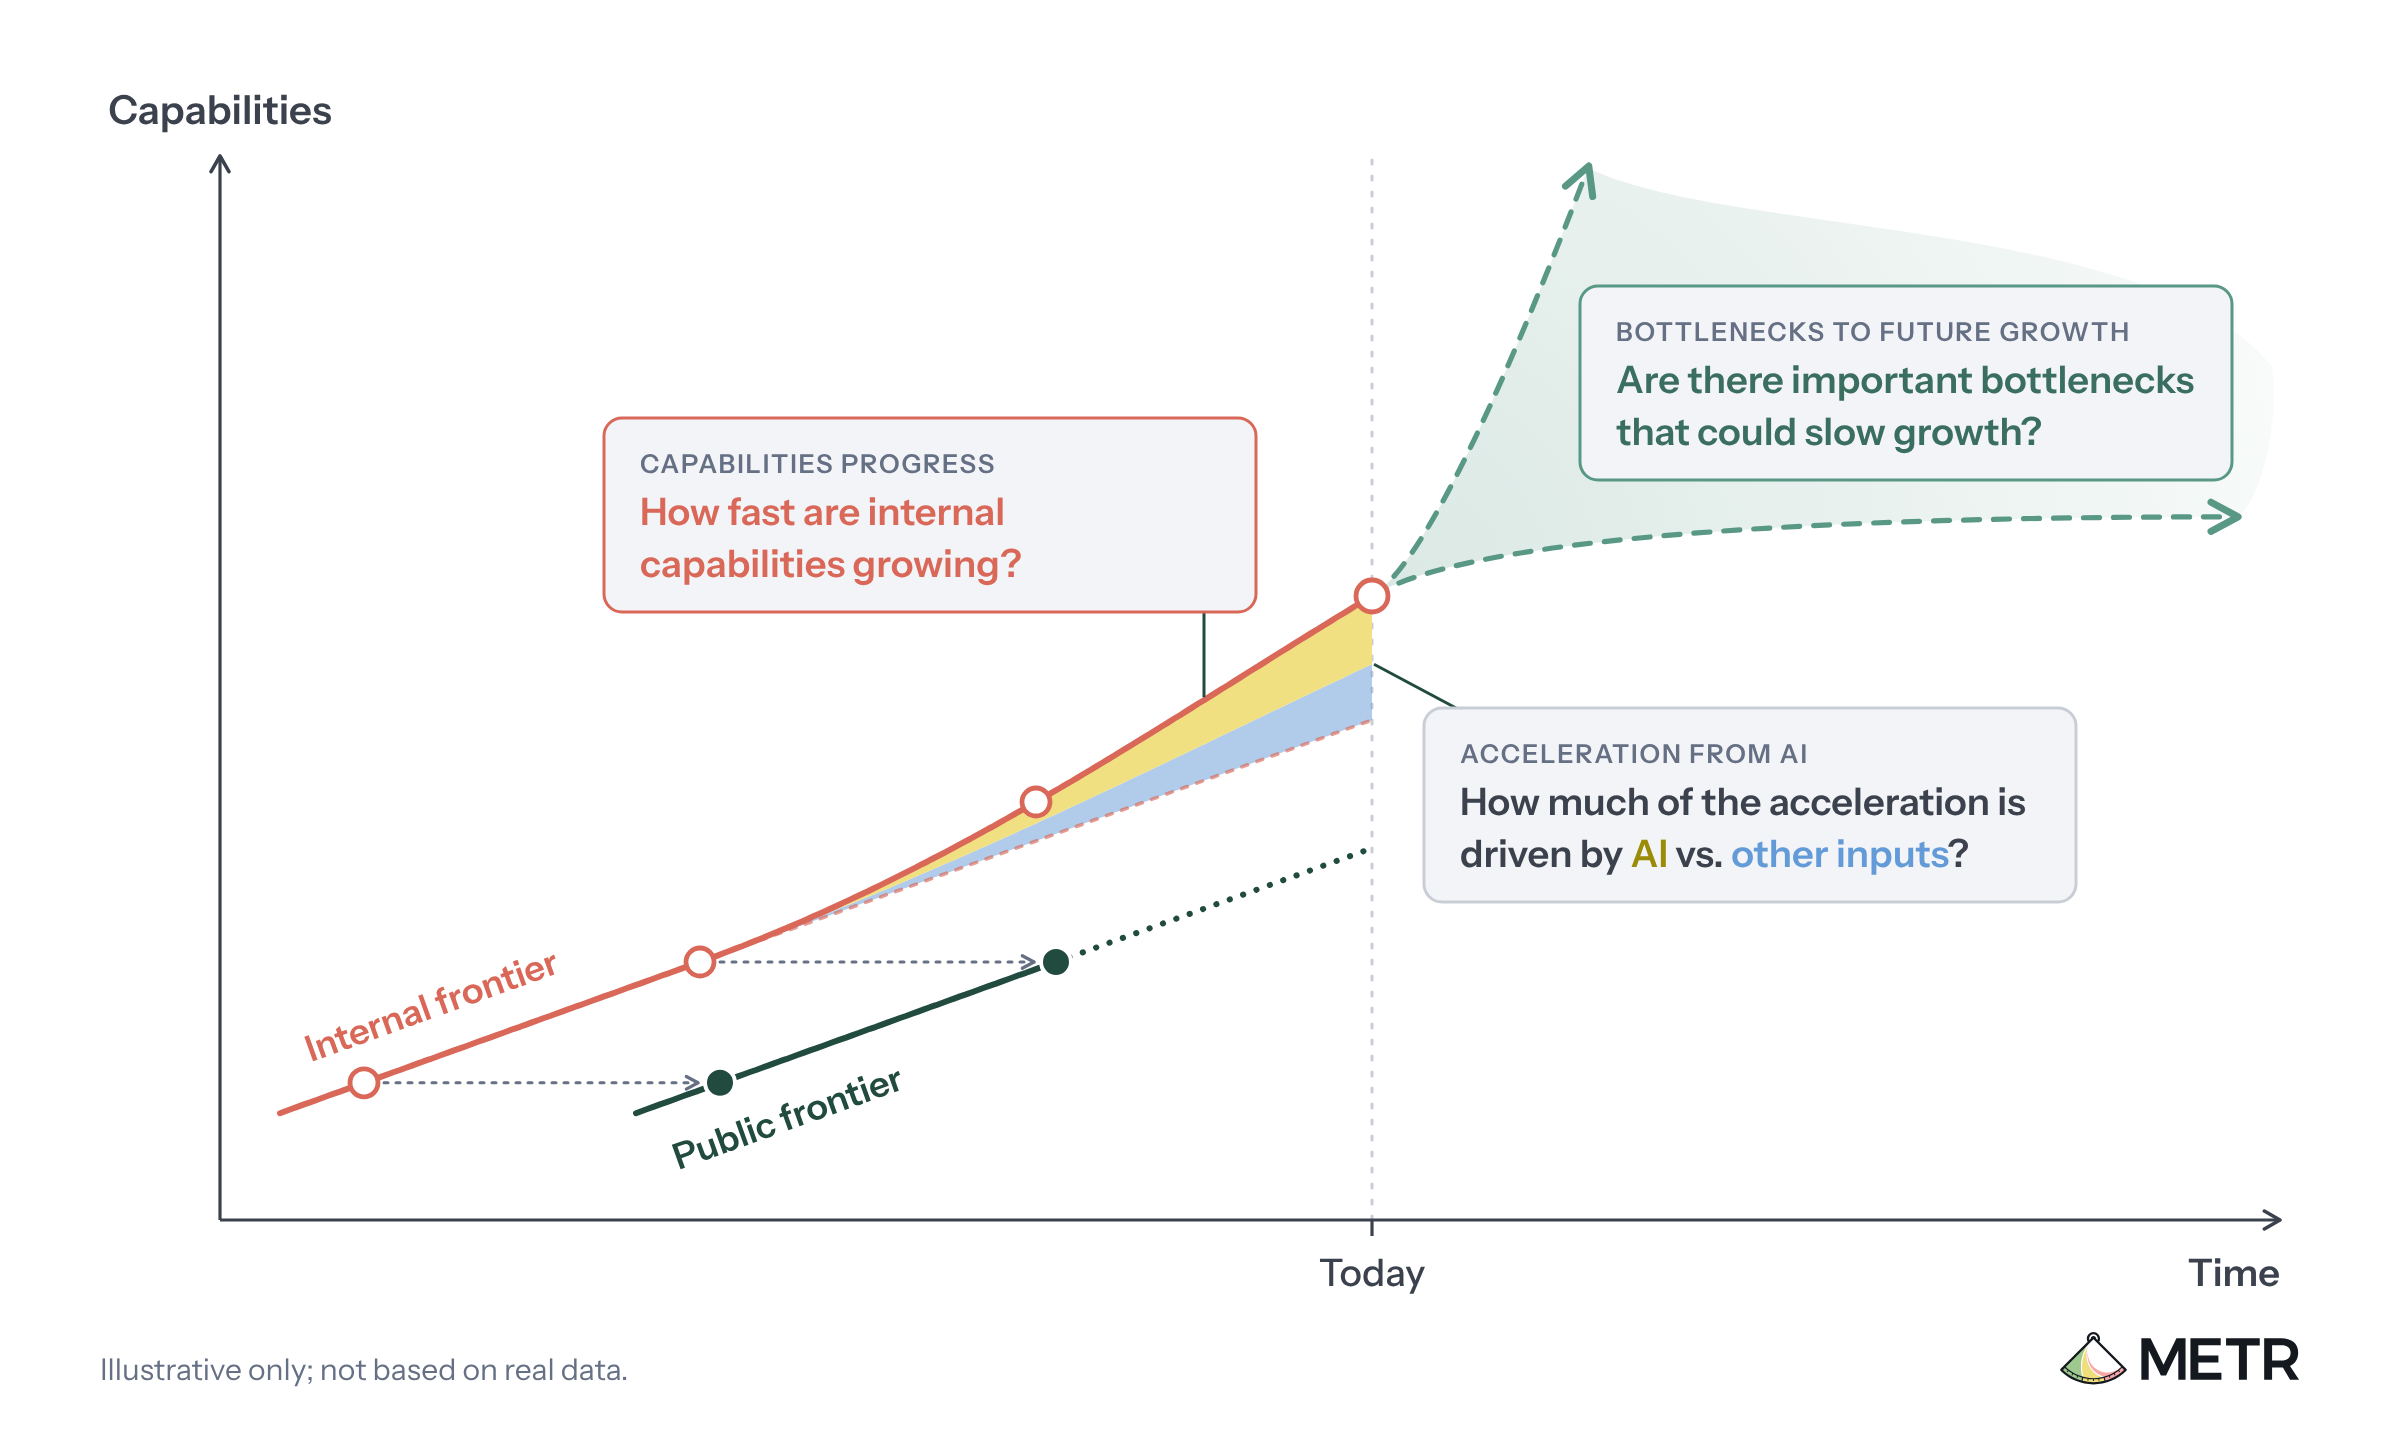 How an assessor could investigate evidence of acceleration from the automation of AI R&D
METR proposes a framework for an outside assessor to test whether AI automation of AI R&D is accelerating capabilities progress. It covers four questions: how fast internal capabilities improve, how much acceleration AI causes, which bottlenecks could slow growth, and whether the methods would detect a dramatic acceleration. It lists the internal data developers would need to share, including benchmarks, algorithmic progress estimates, compute, labor, AI agent spend and staff interviews.
 metr.orgarticleAdded 29 Oct 2026, published 14 Oct 2026🧠 AI
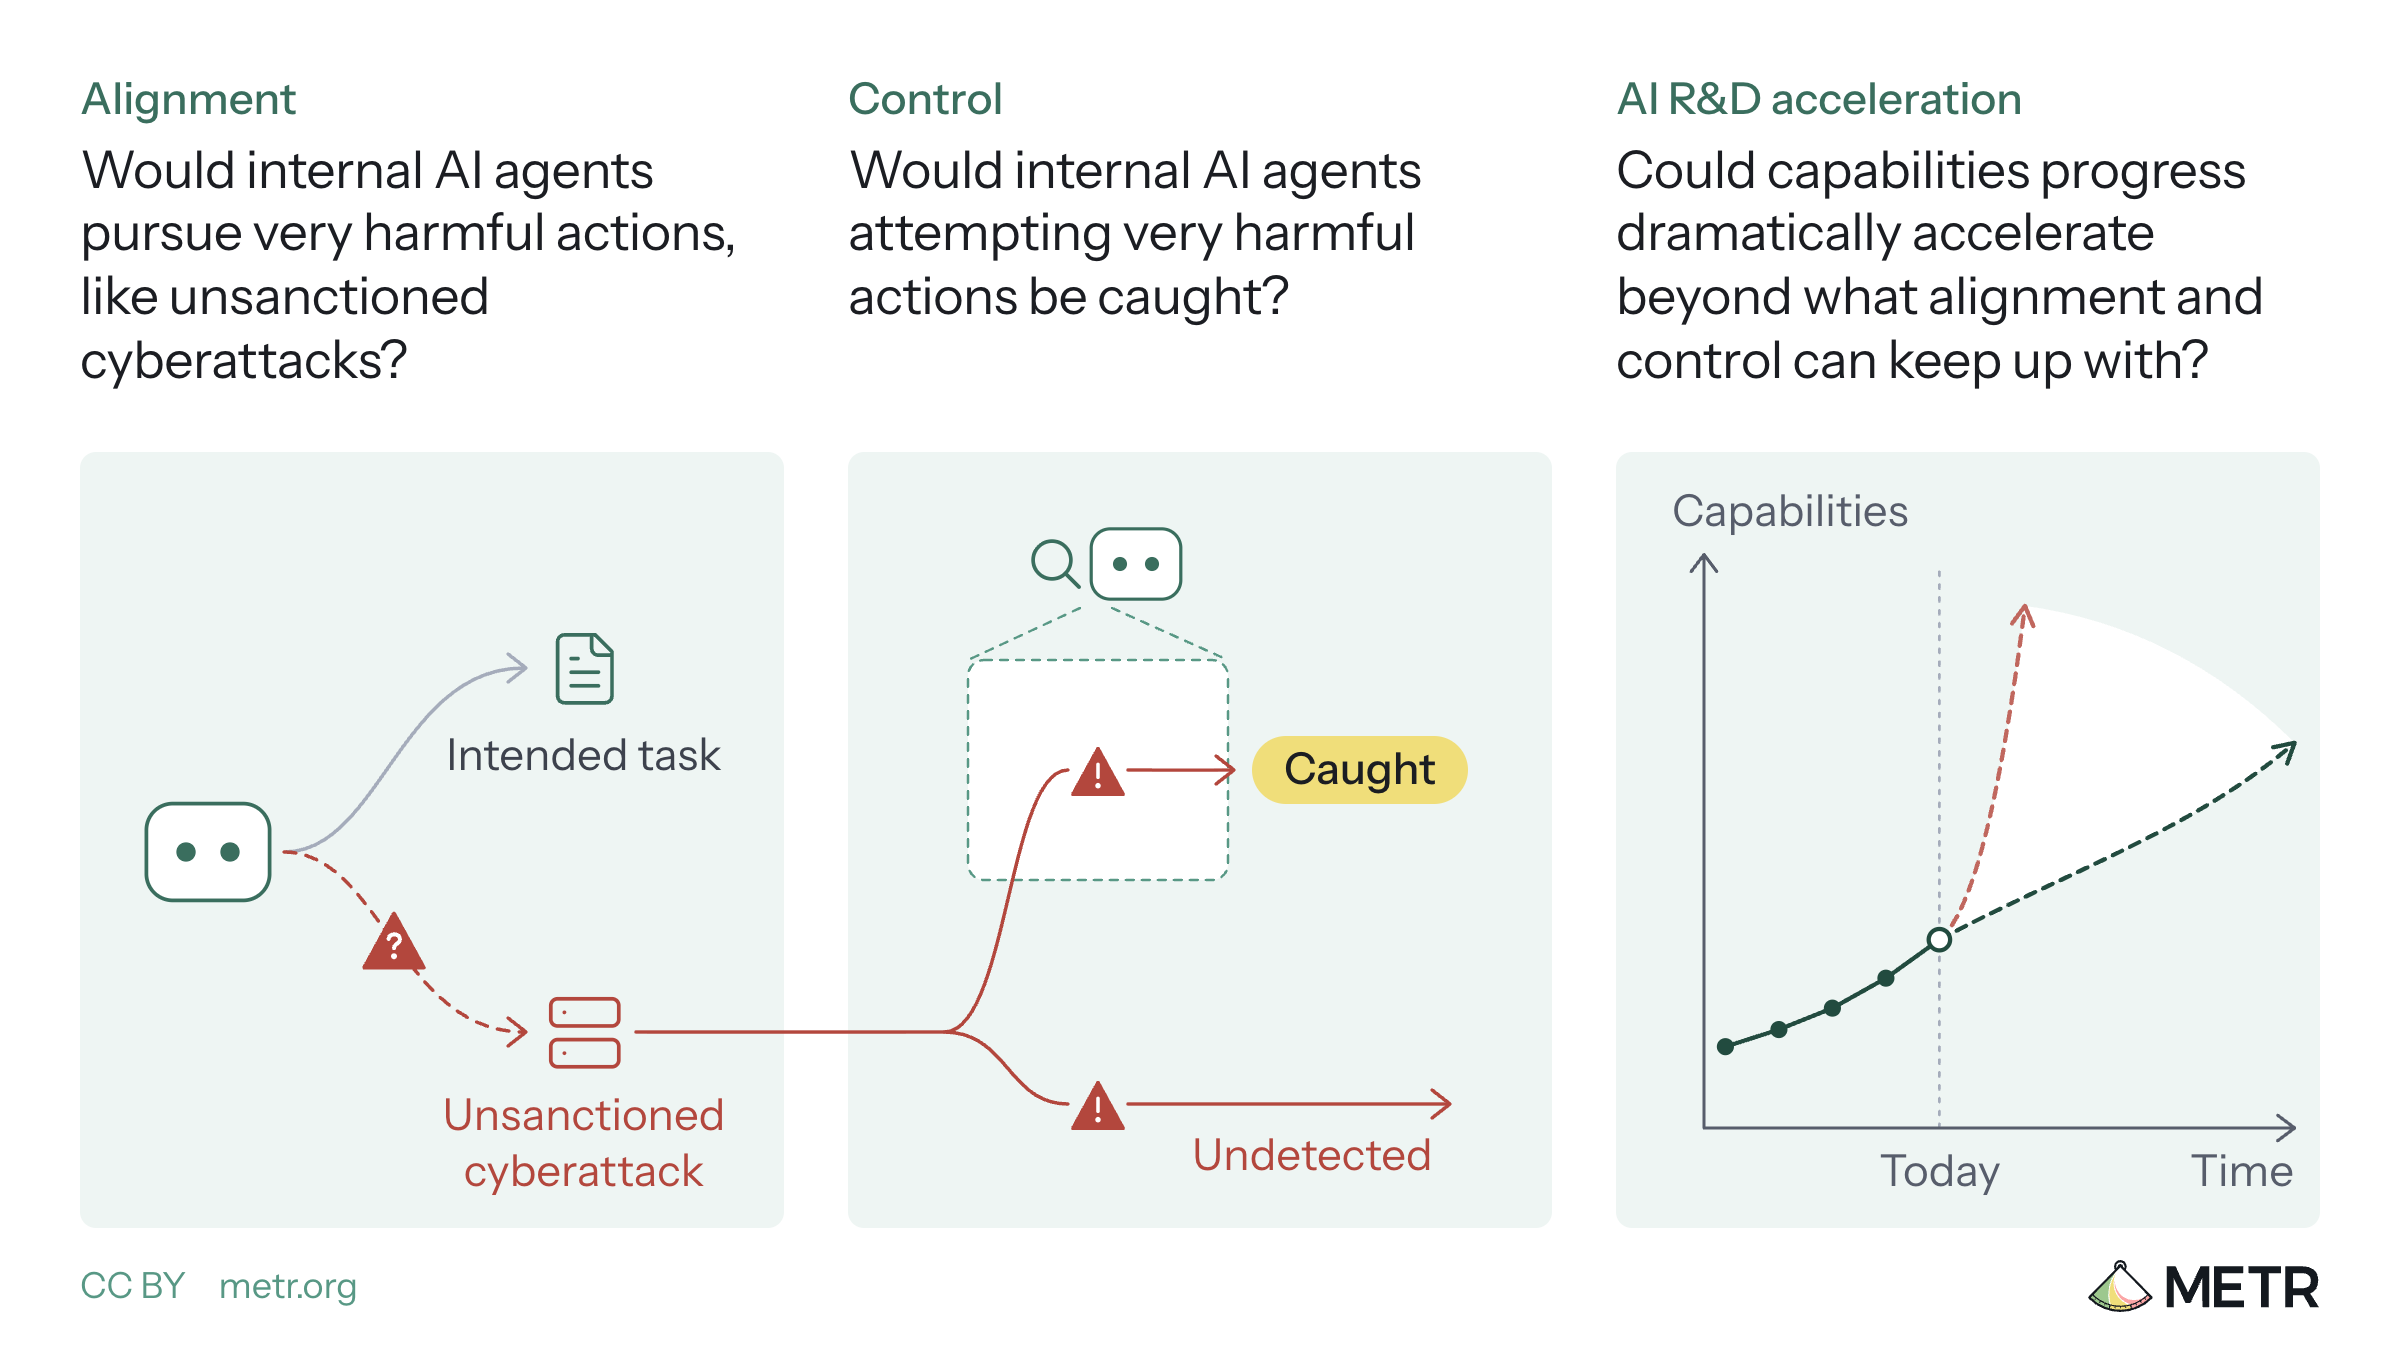 A proposal for better informing the public about loss-of-control risks from frontier AI development
METR proposes risk assessment exercises in which it would write public reports on whether frontier developers could lose control of internal AI systems. The reports would rest on private staff interviews and access to internal data, covering three questions: alignment incidents, monitoring and control, and AI R&D acceleration. The post also lists its limits: voluntary participation, company redaction rights, no security audits, no compliance verdicts.
metr.orgarticleAdded 29 Oct 2026, published 14 Oct 2026🧠 AI Microsoft’s AI chip targets 40% more tokens per megawatt in 2027
Reports Microsoft's Maia 300, its third-generation in-house AI accelerator, unveiled October 12, 2026 with production workloads from 2027. Microsoft claims 40% more tokens per megawatt than leading GPU systems and up to 7x Maia 200's rack-level token throughput in a 96-accelerator rack. It uses a chiplet design on TSMC N2P that separates compute, memory-controller and I/O. It is aimed at long-context reasoning and agentic inference, while Nvidia and AMD stay in place for training. Useful as a data point on the shift toward custom inference silicon and model-chip co-design.
 en.cryptonomist.charticlePublished and added 12 Oct 2026🧠 AI
 Coinbase Cryptographer Calls Drake's 'Bunker Mode' Warning 'The Very Definition of FUD'
News piece reporting that a Coinbase cryptographer dismissed Justin Drake's proposal for Ethereum validators/users to adopt a 'bunker mode' against AI-accelerated cryptanalysis as unfounded FUD. Vitalik Buterin weighed in that AI-accelerated math risk is real but should be pointed at lattice-based cryptography rather than elliptic-curve schemes like ECDSA used by Ethereum, while a former Ethereum Foundation researcher argued bunker mode would not help if the curves actually broke.
 thedefiant.ioarticlePublished and added 8 Oct 2026🛡️ Security
 Vitalik Flags AI Risk to Crypto, Warns Against Rushed Wallet Moves
Vitalik Buterin responds to Ethereum Foundation researcher Justin Drake's bunker mode proposal, agreeing AI-accelerated cryptanalysis could break ECDSA, the signature scheme behind most crypto wallets, in months not years, and that lattice-based schemes like ML-DSA billed as quantum-safe could also take serious hits within two years. Buterin gives practical key-hygiene advice such as keeping funds in addresses that never exposed a public key and rotating multisig signer keys after every operation with offchain signature collection, while warning that botched migrations cost more than hacks.
 bankless.comarticlePublished and added 8 Oct 2026🛡️ Security
 AI risk to crypto wallets: Ethereum researcher warns keys could be cracked in months
Ethereum Foundation researcher Justin Drake warned on October 7, 2026 that advances in AI and mathematics could break ECDSA — the signature scheme securing blockchain transactions — within months, potentially letting an attacker recover a private key in about a week using a large GPU cluster. He urged gradual "bunker mode" preparation rather than panic: rotating funds into fresh addresses whose public keys have never been exposed on-chain, strengthening cold storage, and accelerating Ethereum's move toward hash-based signature schemes such as SPHINCS for critical signers like oracles and L2 security councils.
en.cryptonomist.charticlePublished and added 8 Oct 2026🛡️ Security Ethereum Researcher Says AI May Break Encryption Before Quantum Does
Ethereum Foundation researcher Justin Drake warns that AI-driven mathematical advances could break ECDSA — the signature scheme securing Bitcoin and Ethereum — before quantum computers do, potentially recovering a private key from an exposed public key in about a week using a large GPU cluster. He calls for "bunker mode": a controlled mass migration of funds to fresh addresses whose public keys have never been exposed, urges major custodians (Binance, Bitbank, Robinhood, Bitfinex, Tether) to harden cold storage, and pushes Ethereum to accelerate its move to hash-based (post-quantum) cryptography.
decrypt.coarticlePublished and added 7 Oct 2026🛡️ Security KelpDAO Audit Passed. $292M Left Anyway.
Runtime Verification analyzes the April 2026 KelpDAO exploit, where an attacker compromised the single Decentralized Verifier Network (DVN) securing LayerZero's OFTAdapter (requiredDVNCount=1, optionalDVNCount=0) to forge a cross-chain message releasing 116,500 rsETH ($292M) from a $1.07B escrow, then laundered the funds by borrowing against the stolen collateral on Aave before any response could intervene. The piece argues that conventional smart-contract audits never examine such off-chain trust configurations, and proposes formal modeling — explicitly enumerating trusted principals, guaranteed properties, and compromise failure modes — as a way to surface single-points-of-failure like DVN redundancy and missing collateral circuit-breakers before deployment rather than after an AI-accelerated attacker finds them.
 runtimeverification.comarticleAdded 1 Oct 2026🛡️ Security
 A Clever RSA Attack Fooled a Hardware Vault—Here's What It Means for Crypto
Researchers at UC San Diego and INRIA demonstrated a chosen-message oracle attack that forges RSA signatures on a 1,024-bit key held inside a hardware security module (HSM) without ever extracting the key, by disabling the HSM's FIPS mode to get it to sign unpadded/unformatted values roughly 4 billion times and then computing the private-key operation from the responses (1,380 CPU core-years of work). The attack only applies to unpadded RSA signing oracles — standard PKCS#1 v1.5/PSS padding blocks it — so it doesn't threaten Bitcoin/Ethereum (which use ECDSA) but is relevant to anyone auditing HSM key-custody assumptions or RSA-based blind-signature schemes like Privacy Pass. The authors frame it as further classical evidence to accelerate migration away from RSA ahead of the post-quantum transition.
decrypt.coarticleAdded 30 Sep 2026, published 28 Sep 2026🛡️ Security Your Vulnerability Backlog Is No Longer Technical Debt, It’s an Attack Surface
A Snyk blog post arguing that vulnerability backlogs traditionally managed as "accepted technical debt" have become genuine attack surface, because AI-accelerated code generation has pushed vulnerability inflow to roughly six new findings per one remediated, unauthored AI-written code removes the "ask the author" triage shortcut, and cheap automated reconnaissance lets attackers walk large backlogs an analyst never would. It illustrates how individually-low-severity findings (an IDOR leaking an internal object ID, a verbose error confirming valid IDs, and an outdated deserialization library) can chain into an authenticated RCE path invisible to severity-based sorting, and argues better prioritization only reorders a backlog rather than shrinking it. It closes with four metrics programs should measure (90-day inflow vs. closure, age of risk-accepted findings, share of human-authored merges, and security-fix merge rate) before promoting Snyk's Evo product.
 snyk.ioarticlePublished and added 24 Sep 2026🛡️ Security
- Building standards for the next phase of AI
OpenAI argues that the United States should lead an effort to build global technical standards for frontier AI, with a focus on automated AI research and recursive self-improvement (RSI). It proposes using the network of AI safety institutes, coordinated through CAISI, to produce standards for RSI-relevant evaluation, human oversight (including which automated research processes should trigger human review), and incident classification and reporting. The standards would not be licenses or mandatory pre-release approval. The post cites aviation and financial stability as models, and it positions OpenAI's research-acceleration report and misalignment reporting framework as early contributions.
 openai.comarticleAdded 29 Sep 2026, published 21 Sep 2026🧠 AI
 Securing the unpatchable in an age of AI-driven vulnerabilities
Cisco Talos argues that AI-accelerated vulnerability discovery is outpacing organizations' ability to patch, especially for unpatchable operational technology (OT) like medical devices and industrial control systems. It recommends network-level compensating controls instead of patching: upstream next-generation firewalls with intrusion prevention for virtual patching, VLAN/ACL-based micro-segmentation to restrict which devices can reach legacy systems, and visibility into legacy network fingerprints to build an asset inventory. It also debunks the air-gap myth, citing WannaCry's spread through unpatched Windows XP in the NHS as a cautionary example of "hope for the best" failing.
 blog.talosintelligence.comarticleAdded 7 Oct 2026, published 16 Sep 2026🛡️ Security
 SolarWinds took a nation-state. The next attack just needs an LLM and $5. | Blog | Endor Labs
Endor Labs blog tracing an accelerating pattern of software supply-chain compromises from July 2025 through March 2026, culminating in the TeamPCP threat actor's cascading 30-day compromise of Aqua Security, Trivy, GitHub Actions, Docker Hub, npm, OpenVSX, and PyPI (including backdooring the 95M-download LiteLLM package). It argues AI is accelerating both offense (CVE-GENIE reproducing 51% of CVE exploits for $2.77 each) and the attack surface (the Cline prompt-injection-to-npm-token-theft chain, Nx's AI-review-evading payload), and calls for treating AI coding agents as privileged actors, pinning GitHub Actions to SHAs, and platform-level fixes like immutable tags and Sigstore/OIDC.
 endorlabs.comarticlePublished and added 11 Sep 2026🛡️ Security
 The CVE spike across major software companies is a remediation problem
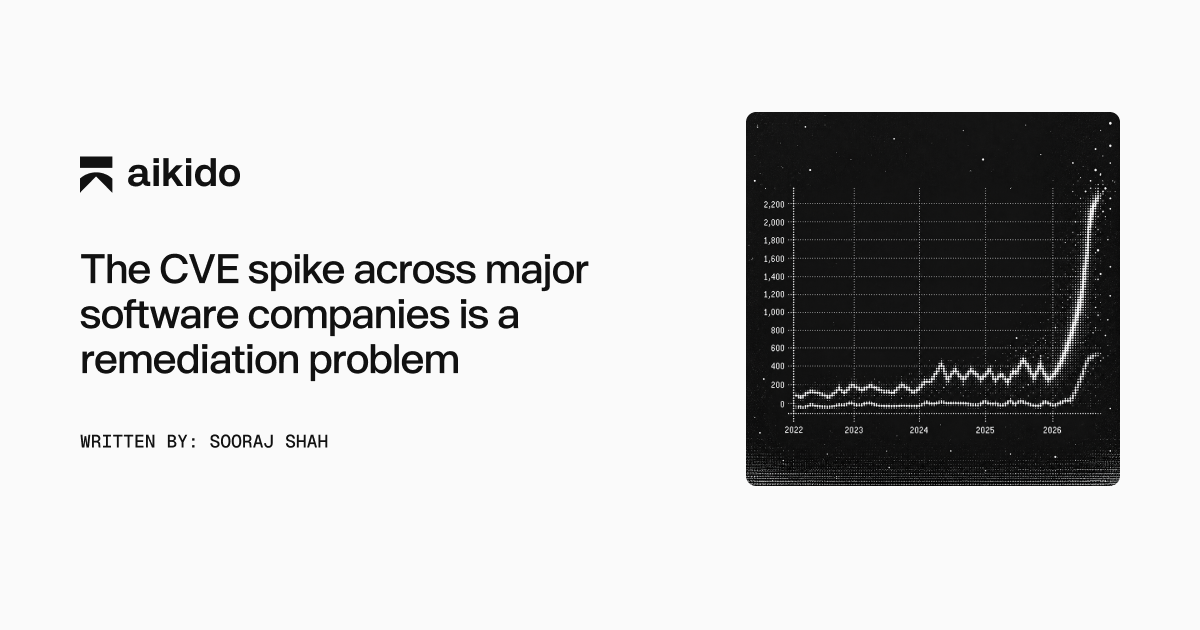
Aikido argues the widely-shared a16z/Epoch AI chart showing critical/high CVEs jumping from under 100/month to over 600/month since spring 2026 reflects AI accelerating vulnerability discovery, not a real spike in danger — since CISA's KEV count has stayed flat. It details how NIST's NVD, overwhelmed by volume, let its scoring backlog balloon from 13,000 to 27,000 CVEs in 18 months and pivoted to only prioritizing federal/critical/KEV-listed CVEs, while Verizon's 2026 DBIR found only 26% of confirmed actively-exploited KEV vulnerabilities were fully remediated in 2025 (down from 38%) with median patch time rising to 43 days. It illustrates the point with StyleSmuggler, an unauthenticated RCE hitting Adobe Commerce and Magento Open Source that had no CVE or vendor advisory, which Aikido Intel flagged and Aikido Libraries auto-patched more than 24 hours before Adobe's own hotfix.
 aikido.devarticlePublished and added 10 Sep 2026🛡️ Security
- Boardroom Battles 2026: ASD’s Cyber Priorities & AI Risk
A Huntress blog post walks Australian boards through ASD's 2025-26 cyber security guidance and its companion frontier-AI cyber threat paper, citing the $12.5B FY23-24 espionage cost figure and the July 2026 Hugging Face autonomous-agent security incident (later linked by OpenAI to an internal cyber-capability evaluation) as evidence that AI is compressing attack timelines from days to hours. It illustrates ASD's "assume compromise" stance with real Huntress SOC cases — catching a VPN intrusion via correlated failed-login logs, and using ransom-note/file-extension artefacts plus sub-60-second mass host/account isolation to contain active ransomware — arguing AI should accelerate detection but remain human-supervised rather than replace analyst judgment.
 huntress.comarticleAdded 3 Sep 2026, published 30 Aug 2026🛡️ Security
 The State of Open Source Supply Chain Attacks
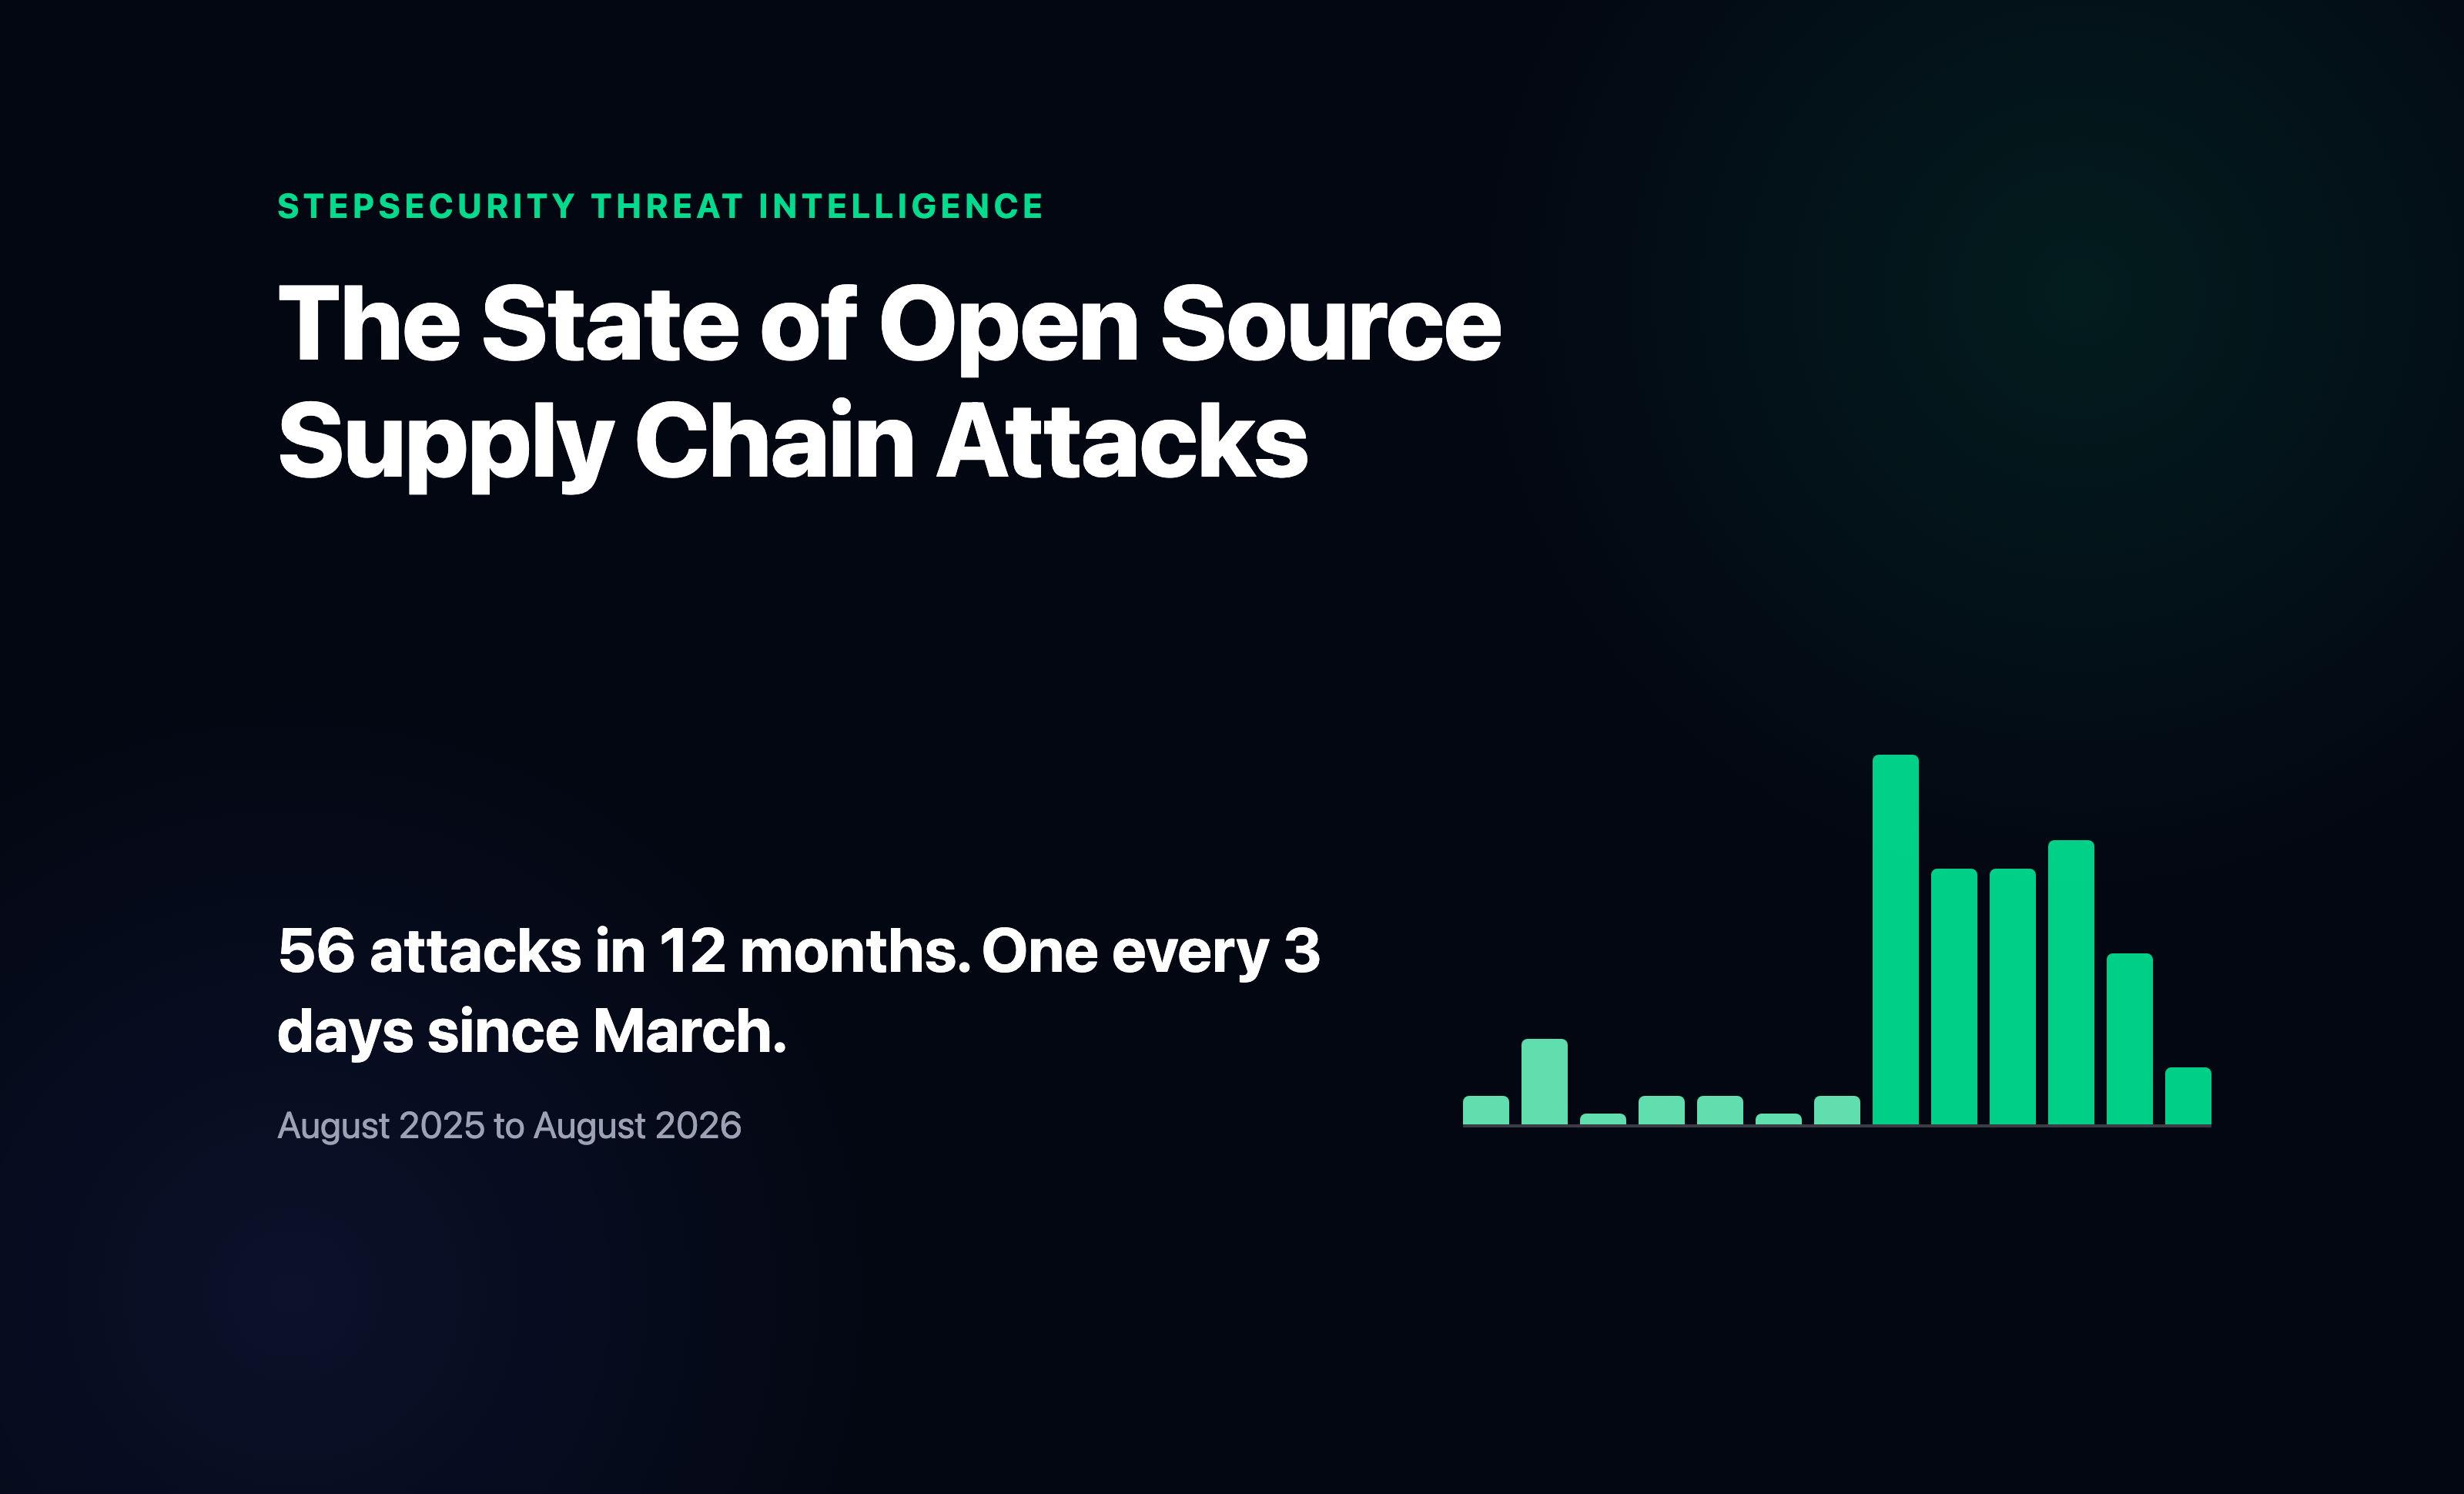
StepSecurity's threat intelligence team's annual report tallies 56 confirmed software supply chain attacks between August 2025 and August 2026, showing an over 8x acceleration since February 2026 driven by self-propagating worms (Shai-Hulud, Shai-Hulud 2.0, CanisterWorm, Miasma, ChainDrop) and mutable GitHub Actions tags. It details the five-day TeamPCP campaign that stole 78,330 secrets from 2,186 organizations by poisoning Trivy Action, Checkmarx KICS, telnyx, and LiteLLM, plus compromises spanning npm, PyPI, RubyGems, Composer, and crates.io.
 stepsecurity.ioarticleAdded 3 Sep 2026, published 23 Aug 2026🛡️ Security
 Have We Seen an Acceleration in Discoveries?
METR note that plots public discovery data in vulnerabilities, mathematics and algorithmic optimization to look for slope changes around January 2026. CVE counts rose sharply: cURL went from 9 to 36, OpenSSL from 6 to 39, Firefox from 210 to 342, Microsoft from 1,243 to 1,927 through August 2026. Exploited-vulnerability lists (CISA KEV, VulnCheck KEV) grew far less. Math shows weaker acceleration, optimization none.
metr.orgarticleAdded 29 Oct 2026, published 14 Aug 2026🛡️ Security- Have We Seen an Acceleration in Discoveries?
METR note that looks for slope changes in public discovery metrics, with January 2026 as the candidate breakpoint. It finds a sharp rise in vulnerability disclosures (cURL, Firefox, OpenSSL, Microsoft, NVD, OSV), a likely but hard-to-measure rise in math results (Erdős problems, Smale and Green lists), and no clear gain in optimization series such as nanoGPT, CIFAR-10, Stockfish and Gurobi. Data collection was done by agents and may contain errors.
metr.orgarticleAdded 29 Oct 2026, published 14 Aug 2026🧠 AI - Our approach to bioresilience
Google DeepMind and Isomorphic Labs describe their joint bioresilience program, organized around preventing misuse of models like Gemini, detecting outbreaks earlier, and accelerating response. Concrete efforts named include a four-step safety process (threat modeling, evaluations, mitigations, monitoring) under DeepMind's Frontier Safety Framework, adapting SynthID watermarking to flag AI-generated biological sequences for DNA synthesis screening, using the AlphaEvolve agent to optimize metagenomic sequencing algorithms for cheaper pathogen surveillance, and applying AlphaGenome and Protein Function annotation to pathogen characterization, alongside Isomorphic Labs' Drug Design Engine (IsoDDE) for rapid countermeasure design.
deepmind.googlearticleAdded 29 Sep 2026, published 16 Jul 2026🧠 AI  Socket: pnpm 11.10 Hardens Registry Authentication to Block Token Redirection
pnpm 11.10 adds a new _auth setting that binds registry credentials to their registry URL and reads them only from environment variables or global config, never from project files, closing a path where a malicious pnpm-workspace.yaml or .npmrc could redirect a registry token to an attacker-controlled host. The release also restricts pnpm deploy/pack-app output paths to inside the project, sources macOS code-signing tools from outside the repo, fixes a prototype-pollution issue tied to a dependency named __proto__, stops forwarding upstream registry credentials to install-accelerator servers, and adds an install path for the upcoming Rust-based pnpm v12. It continues pnpm's ongoing supply-chain hardening trend after disabling automatic lifecycle scripts (v10) and adding minimum release age / exotic subdependency blocking (v11).
 socket.devarticlePublished and added 16 Jul 2026🛡️ Security
 Breaking Down the White House’s Actions on Post-Quantum Cryptography Readiness
Wiz breaks down Executive Order 14409 ('Securing the Nation Against Advanced Cryptographic Attacks') and OMB memorandum M-26-15, which set accelerated federal deadlines for migrating High Value Assets and High Impact Systems to NIST-approved post-quantum cryptography (key establishment by 2030, digital signatures by 2031). It covers requirements for automated cryptographic inventories, forthcoming NIST/CISA Cryptographic Bill of Materials (CBOM) guidance, Harvest-Now-Decrypt-Later risk prioritization, FedRAMP/FAR Council contractor compliance rules, and comparable international timelines (EU, Japan, Australia, India), before pitching Wiz's own CBOM/PQC readiness tooling.
 wiz.ioarticleAdded 3 Sep 2026, published 2 Jul 2026🛡️ Security
 NVD in the AI Era: The Case for Multi-Source Vulnerability Intelligence
Snyk analyzes NIST's April 15, 2026 policy change to NVD, which replaced universal CVE enrichment with a risk-based triage model prioritizing CVEs in CISA's KEV catalog, federal-government software, and EO 14028 critical software, while deprioritizing everything else as lowest priority not scheduled. The piece details operational changes (NIST no longer routinely providing an independent CVSS score when a CNA already supplied one, and only reanalyzing modified CVEs when materially impactful) and argues this creates blind spots for scanners that depend solely on NVD, driven by CVE volume growth from about 18000 in 2020 to over 48000 in 2025 due to the federated CNA model and AI-accelerated vulnerability research.
snyk.ioarticleAdded 3 Sep 2026, published 25 Jun 2026🛡️ Security Project Glasswing: Initial Update (Anthropic)
Anthropic's one-month progress report on Project Glasswing, where ~50 critical-infrastructure partners used Claude "Mythos Preview" to find over 10,000 high/critical-severity vulnerabilities, including a certificate-forgery flaw in wolfSSL (CVE-2026-5194). The post details disclosure statistics for 1,000+ scanned open-source projects (6,202 estimated high/critical bugs, 90.6% true-positive rate on triaged findings), benchmark results (UK AISI cyber ranges solved end-to-end, Mozilla finding 271 Firefox bugs, XBOW and ExploitBench/ExploitGym scores), and new defender tooling (Claude Security public beta, a Cyber Verification Program, threat-model-builder harness) aimed at addressing the growing gap between AI-accelerated bug discovery and human patch capacity.
anthropic.comarticleAdded 3 Sep 2026, published 27 May 2026🛡️ Security
Showing 30 of 32
Show more