- huiwenhan (@huiwenhan) on X
PRAXO-CORE 2.5.0 is a Go agent kernel that owns model calls, tool authorization, context, checkpoints, events and human-in-the-loop decisions, and leaves graph execution, memory storage and tenant policy to RHEOVELA or the host product. The release adds pkg/conformance, with checks for VFS, memory, sandbox, event, policy, model and tool contracts. It also adds stricter Windows path rejection and a plugin trust/SBOM handoff, and it states which adapters are only offline-tested.
 x.comarticleAdded 27 Oct 2026, published 25 Oct 2026🧠 AI
 Everything, everywhere, all at once… the week software broke | Endor Labs
Endor Labs roundup of the 20 to 21 October 2026 patch wave: eMudhra certificate authority keys that anyone can recover, PHP2Shell (CVE-2026-109618, CVE-2026-109619), Node2Shell (CVE-2026-111497) and malware in LiteLLM 1.107.0. It lists fixed versions (PHP 8.2.35 to 8.5.12, Node.js 22.23.4, 24.22.1, 26.12.1, LiteLLM back to 1.106.2) and explains why many separate trust-store copies each need updating. It closes with advice on triage, remediation and SBOM/VEX reporting.
 endorlabs.comarticlePublished and added 24 Oct 2026🛡️ Security
 Software supply chain security best practices for 2026
Aikido's guide to software supply chain security controls for 2026, tied to real incidents. It covers a 48-hour package cooldown, ignore-scripts, lockfile enforcement, SHA and digest pinning, scoped tokens, FIDO2, developer endpoint protection, extension allowlists, agent sandboxing, MCP server vetting, slopsquatting, signed SBOMs and rotation drills. Examples include the March 2026 axios compromise and the March 2025 tj-actions/changed-files attack.
 aikido.devarticleAdded 22 Oct 2026, published 21 Oct 2026🛡️ Security
 Why Your SCA is Always Wrong | Endor Labs
Explains why traditional SCA tools are inaccurate: they parse package-manager manifests and assume those match what the code actually uses. It walks through phantom dependencies, misused dependency scopes, direct use of transitive dependencies and unused dependencies, using Python and JavaScript as examples. It argues for SCA based on program analysis, with source code as ground truth cross-checked against manifests and the file system. Useful for evaluating SCA tools and understanding SBOM accuracy limits.
endorlabs.comarticlePublished and added 16 Oct 2026🛡️ Security SBOMs are Just a Means to an End | Endor Labs
A critique of the state of SBOM adoption, written by a CISSP product manager at Endor Labs. It argues that the NTIA minimum elements and the SPDX and CycloneDX specs don't require a package URL (purl), so name and version alone can't tell a Maven log4j-core from an npm or cargo package of the same name. It also notes that no spec defines build time, which makes transitive dependency resolution unreliable, and that generation tools place the same data in different fields. It adds that vendors have mixed incentives to ship SBOMs and that practices are immature, and it calls on standards bodies to define required data per prioritized use case.
endorlabs.comarticlePublished and added 16 Oct 2026🛡️ Security EU Cyber Resilience Act: Preparing for December 11, 2027 | Endor Labs
Explains what applies on 11 December 2027 under the EU Cyber Resilience Act: Annex I Part I and II, Article 13 manufacturer duties, conformity assessment and CE marking. It covers classification by core functionality, the conformity routes per tier, and how "known exploitable vulnerability" is defined, including findings from your own tooling and AI analysis. It also covers the engineering obligations (per-build SBOMs with VEX, CVD policy, security.txt, signed updates, CSAF disclosure), the 10-year retention and support-period rules, and the product-family and legacy-modification reliefs. It closes with a checklist, and the Endor Labs product claims are vendor-sourced.
endorlabs.comarticlePublished and added 14 Oct 2026🛡️ Security- Executive Order 14028 SBOM Requirements: What to Comply With and How | Endor Labs
Explains what Executive Order 14028 requires for SBOMs. It covers the NTIA Minimum Elements (seven data fields, automation support, practices and processes) and the SPDX, CycloneDX and SWID formats. It also covers who must comply and how OMB M-26-05 (January 2026) rescinded the standardized self-attestation mandate while agencies can still require SBOMs by contract. It then argues an SBOM is only a starting point and recommends adding reachability analysis, EPSS, VEX and safe-upgrade remediation. The last part promotes Endor Labs.
endorlabs.comarticlePublished and added 12 Oct 2026🛡️ Security  Quantum-resistant signing on AWS, Part 1: Build a software supply chain with ML-DSA
Part 1 of an AWS series showing how to build a quantum-resistant software supply chain with ML-DSA: ML-DSA keys in AWS KMS, an ML-DSA root/subordinate CA hierarchy in AWS Private CA, and IAM Roles Anywhere trust anchors for external build agents. It covers signing binaries (EXTERNAL_MU with OpenSSL 3.5), container images as OCI referrers via ORAS, and SBOMs wrapped in in-toto Statements bound to the artifact digest, plus verification, admission control, trust-store distribution, revocation and SCP guardrails. It frames the "forge later" threat and maps CNSA 2.0 (ML-DSA-87 only for NSS) and EU CRA deadlines to actions.
 aws.amazon.comarticlePublished and added 12 Oct 2026🛡️ Security
 Guide to Implementing Software Supply Chain Security | Endor Labs
Vendor-authored guide that defines a software supply chain as developers, code, dependencies, AI models, containers and CI/CD pipelines. It walks through program components: OSS governance, SAST vs reachability-based SCA, AI model security, SBOM/VEX (NTIA minimum elements, SPDX vs CycloneDX), secrets scanning, CI/CD hardening, and signing/attestation with Cosign/Sigstore. It cites figures such as 95% of vulnerabilities sitting in transitive dependencies and only 1% of SBOMs being fully NTIA-conformant. Each section closes with an Endor Labs product pitch, so treat the framing as vendor-flavoured. The fetched text was truncated, so the final attestation/provenance section was not seen.
endorlabs.comarticlePublished and added 12 Oct 2026🛡️ Security Identifying and Tracking FedRAMP False Positives | Endor Labs
Explains how FedRAMP treats false-positive SCA findings, which still have to be tracked in the POA&M and ConMon. It covers the deviation request (DR) process, the SCA problems of scale and missing context (manifest-based inventories, with 88% of imported code unused), and 30–180 day remediation SLAs. It argues that only high-confidence, function-level reachability that holds from any source is likely to satisfy a 3PAO. It then describes how Endor Labs uses call-graph analysis, SBOM/VEX output and rescanning to document false positives.
endorlabs.comarticlePublished and added 12 Oct 2026🛡️ Security Generating and Managing C and C++ SBOMs
A FOSSA blog post explaining why C/C++ SBOMs built from manifest-parsing alone are incomplete, since the ecosystem lacks a centralized package manager and relies heavily on vendored (copy-pasted) source and code snippets. It covers concrete generation paths: Conan's built-in conan.tools.sbom CycloneDX generator, Yocto/OpenEmbedded's native SPDX output via the create-spdx class, process-based tracking for vendored code (third_party/vendor path flagging, manual audits), and the differing snippet-support capabilities of SPDX versus CycloneDX.
 fossa.comarticleAdded 1 Oct 2026, published 29 Sep 2026🛡️ Security
 Proactive Defense: Hardening Code Pipelines and CI/CD Infrastructure
Mandiant's guidance for hardening the software supply chain across five pillars: endpoint, code repositories, artifact management, CI/CD and deployment. It covers a seven-day dependency cooldown, pinning images and actions by digest or commit SHA, ephemeral runners, OIDC short-lived tokens, build cache isolation, signed SBOMs, SLSA provenance and admission-time signature checks. It responds to campaigns using cache poisoning, OIDC token theft and mutable action tags.
 cloud.google.comarticleAdded 29 Oct 2026, published 24 Sep 2026🛡️ Security
 The UK Software Security Code of Practice through a Software Supply Chain Lens | Blog | Endor Labs
Endor Labs analyzes the UK's Software Security Code of Practice, a government-issued framework for software vendors, through the lens of software supply chain security. It breaks down how the Code's requirements map to practices like SBOM generation, dependency/component management, and vendor accountability for third-party code.
endorlabs.comarticlePublished and added 11 Sep 2026🛡️ Security Key Questions for Your SBOM Program | Blog | Endor Labs
Endor Labs blog post outlining six practical questions organizations should answer before standing up an SBOM program: how to send/receive/store SBOMs, which vendors must provide them (via business impact analysis), delivery frequency and SLAs, how to analyze them for exploitability (reachability analysis vs. simple CVE counting), remediation/risk-acceptance policy, and using SBOMs plus VEX during incident response (e.g., Log4Shell-style disclosures). It closes with a pitch for Endor Labs' source-code-based SBOM/VEX generation.
endorlabs.comarticlePublished and added 11 Sep 2026🛡️ Security Next-Gen SCA for C/C++: Closing the Detection Gap | Blog | Endor Labs
Endor Labs announces C/C++ language support for its SCA product, addressing the long-standing difficulty of tracking OSS dependencies in ecosystems with no central package registry. Because C/C++ developers commonly vendor (copy and modify) library source directly into their repos, Endor Labs builds a fingerprint index of known OSS libraries using cryptographic hashes for exact-match segments (functions, license blocks, etc.) and ML-generated code embeddings to catch renamed, reformatted, or lightly modified copies. The company reports customer benchmarks showing 81% fewer false negatives and 143% more true positives versus prior tooling for building SBOMs and detecting vulnerable/license-non-compliant code in C/C++ codebases.
endorlabs.comarticlePublished and added 11 Sep 2026🛡️ Security OSS Vulnerabilities And The Digital Operational Resilience… | Blog | Endor Labs
Endor Labs breaks down the EU Digital Operational Resilience Act (DORA), applicable to financial entities from January 2025, focusing on Article 9 (patch management) and Article 25 (open source analysis/source code review), plus the January 2024 Regulatory Technical Standards Articles 10 (tracking third-party/OSS libraries) and 16 (source code review, security testing before production). It then maps these compliance requirements to concrete AppSec practices: SBOM/SCA for component inventory, proactive OSS risk scoring, vulnerability scanning, and function-level reachability analysis to prioritize remediation and generate VEX documents, noting overlap with PCI DSS requirements 6.3/11.3.
endorlabs.comarticlePublished and added 11 Sep 2026🛡️ Security How CycloneDX VEX Makes Your SBOM Useful | Blog | Endor Labs
Endor Labs explains how the CycloneDX Vulnerability Exploitability eXchange (VEX) format's analysis sub-field (state, justification, response, detail) lets software publishers communicate real exploitability of SBOM-listed CVEs, cutting through the noise of scanners that flag thousands of largely non-exploitable findings. It walks through each state value (resolved, resolved_with_pedigree, exploitable, in_triage, false_positive) as a machine-readable alternative to ad hoc spreadsheets/portals for vulnerability disclosure, referencing log4shell (CVE-2021-44228) as a case where faster communication would help.
endorlabs.comarticlePublished and added 11 Sep 2026🛡️ Security SSDF Compliance and Attestation: A Practical Guide | Blog | Endor Labs
Endor Labs breaks down CISA's finalized Secure Software Development Attestation Form, which requires federal software suppliers to attest compliance with NIST's Secure Software Development Framework (SSDF) under EO 14028, with critical software due June 8, 2024 and other software due September 8, 2024. It covers the form's scope (excluding federal-developed, open source, and freely available software), flags ambiguous language and gaps (no explicit SBOM/threat-modeling/memory-safety mandate), and maps the four required practice areas — secure environments, trusted source code supply chains, code/artifact provenance, and vulnerability scanning/remediation — to Endor Labs' supply chain security platform features.
endorlabs.comarticlePublished and added 11 Sep 2026🛡️ Security Demystifying Transitive Dependency Vulnerabilities | Blog | Endor Labs
Endor Labs blog post demystifying transitive dependencies — libraries pulled in indirectly through direct dependencies — and explaining why they complicate software composition analysis: multiple versions of the same transitive dependency can coexist in a project, it's harder to see what's actually used, and manually forcing an update is risky. It argues reachability analysis (statically stitching first-party call paths through to transitive library code) is the key tool for determining exploitability and for satisfying auditors under PCI DSS, FedRAMP, and EO 14028 SBOM requirements, and walks through a real example where langchain4j pulls a vulnerable JSON library transitively via Redis's jedis client, with the fix being to bump jedis rather than the JSON library directly.
endorlabs.comarticlePublished and added 11 Sep 2026🛡️ Security What is VEX and Why Should I Care? | Blog | Endor Labs
Endor Labs explains VEX (Vulnerability Exploitability eXchange), the CISA-backed machine-readable format that lets software producers assert whether a vulnerability in a component actually affects their product, complementing SBOMs which only list components and versions. It walks through how VEX documents annotate exploitability (e.g., unreachable code), and describes how Endor Labs automates this by building a dependency callgraph via static analysis to determine reachability and auto-generate SBOM/VEX documents.
endorlabs.comarticlePublished and added 11 Sep 2026🛡️ Security Securing Docker images
Aikido Security's guide to hardening Docker images explains where container vulnerabilities come from (base OS layers like Debian/glibc that ship far more than an app needs), citing CVE-2023-4911 (Looney Tunables in glibc) and the xz-utils backdoor as cautionary examples for version-pinning decisions. It lays out hardening steps such as multi-stage builds, removing unused packages, non-root users, read-only filesystems, dropping Linux capabilities, pinning base images by digest, generating SBOMs, and signing/verifying images, then pitches Aikido Images, which backports CVE patches onto the same pinned base image version instead of forcing a migration to a new hardened distro.
aikido.devarticleAdded 3 Sep 2026, published 28 Aug 2026🛡️ Security Software supply chain security requires decisions rather than defaults
Aikido Security argues that supply-chain security should be driven by deliberate decisions rather than defaulting to "always upgrade," using the xz-utils backdoor (versions 5.6.0/5.6.1, where CISA advised downgrading rather than patching) and the 2026 lodash 4.18.0 release (which broke the _.template code path within a day of shipping a fix for an arbitrary code injection vulnerability, forcing a deprecation back to 4.17.21 before the real fix landed in 4.18.1) as evidence that neither blind pinning nor blind upgrading is inherently safe. It advocates backporting specific CVE fixes onto already-running versions instead of forcing full upgrades, and treating SBOMs as continuously maintained baselines rather than one-time compliance artifacts, closing with a promotion of Aikido Libraries' backporting capability.
aikido.devarticleAdded 3 Sep 2026, published 26 Aug 2026🛡️ Security FOSSA: EU CRA Compliance Timeline
A FOSSA blog post laying out the EU Cyber Resilience Act's (Regulation (EU) 2024/2847) phased compliance timeline: it entered into force 10 December 2024, vulnerability/incident reporting obligations to ENISA and national CSIRTs (including a 24-hour early warning) begin 11 September 2026, and full Annex I conformity with CE marking is required by 11 December 2027. It details what manufacturers should prioritize at each stage — CVD policy, incident-response workflows, SBOM automation, secure-by-design defaults, and conformity assessment — and promotes FOSSA's free CRA Readiness Assessment tool.
fossa.comarticlePublished and added 7 Aug 2026🛡️ Security FOSSA: CISA Releases the 2026 SBOM Minimum Elements
FOSSA breaks down CISA's 2026 Minimum Elements for a Software Bill of Materials, the first major revision since NTIA's original 2021 baseline, produced with NSA, FBI, and 15 international agencies. The update roughly doubles required data fields, adding 10 new elements (SBOM Author Signature, SBOM Data Format Name/Version, Generation Context, Tool Name/Version, SBOM Version, Component Hash Value/Algorithm, and Component License) while renaming and clarifying existing fields (e.g., Supplier Name → Component Producer) and mandating full transitive-dependency coverage with no minimum depth, RFC 9557 timestamps, and dropping SWID in favor of SPDX/CycloneDX.
fossa.comarticlePublished and added 31 Jul 2026🛡️ Security Best SBOM Tools in 2026, Compared | Blog | Endor Labs
Endor Labs' 2026 SBOM tooling comparison sorts five tools into three functional layers: open-source generators (Syft, cdxgen, Microsoft SBOM Tool) that produce SPDX/CycloneDX inventories, OWASP Dependency-Track for centralized SBOM storage and continuous monitoring, and Endor Labs' own SBOM Hub which adds function-level reachability analysis to cut CVE alert noise by a claimed 95%. It breaks down each tool's ecosystem coverage, format support, and trade-offs (e.g., Syft's lack of reachability, cdxgen's CycloneDX-only output, Dependency-Track's need for a database) and gives a decision framework for picking a tool by stack and maturity level.
endorlabs.comarticleAdded 3 Sep 2026, published 29 Jul 2026🛡️ Security- wolfBoot 2.9.0
wolfSSL's release announcement for wolfBoot 2.9.0, an open-source secure bootloader for embedded systems, covering new hardware targets (STM32N6/U3/C5/G4/WBA, NXP LPC54S018M-EVK, Kinetis KL26, Xilinx Zynq-7000), new crypto features (RSA-PSS image signatures, hardware crypto-callback interface, multi-root-CA verification, pre-computed IDevID/DICE attestation), and continued security hardening from Fenrir fuzzing including bounded unauthenticated image sizes, memory-copy limits during updates, and fault-injection resistant integrity verification. It also adds an sbom Makefile target producing CycloneDX and SPDX output for CRA-readiness.
 wolfssl.comarticlePublished and added 25 Jul 2026🛡️ Security
 FOSSA: Allan Friedman
Allan Friedman, former NTIA/CISA SBOM and VEX program lead, lays out practical VEX workflows for both software producers and consumers: tracking exposure via SBOM plus CVE/OSV feeds, doing reachability-based impact analysis, documenting and publishing determinations, and closing the loop as status changes. He compares the four VEX formats (CSAF, CycloneDX, SPDX 3.0, OpenVEX), ranks the five standard "not affected" justifications by how verifiable/trustworthy they are, and ties adoption to emerging regulatory pressure from the EU Cyber Resilience Act and FDA medical-device SBOM review.
fossa.comarticlePublished and added 27 Jun 2026🛡️ Security SBOMs in 2026: Everyone's generating them, no one's using them
Aikido Security's blog post recaps ENISA's SBOM Adoption State of Play 2026 report, a survey of 334 organizations (65% EU-based, 80% impacted by the Cyber Resilience Act). Key findings: most orgs now generate SBOMs at build time but rarely consume them for security (only 7% have closed the generation-to-usage gap), 39% never receive SBOMs from suppliers, 28% still use proprietary/non-standard formats instead of CycloneDX (44%) or SPDX (29%), and coverage of transitive dependencies remains weak even though most real-world vulnerabilities hide there. The piece then pitches Aikido's Syft-based SBOM generation, CycloneDX/SPDX export, supplier SBOM import, and Device Protection as ways to close these gaps ahead of the CRA's December 2027 deadline.
aikido.devarticleAdded 3 Sep 2026, published 10 Jun 2026🛡️ Security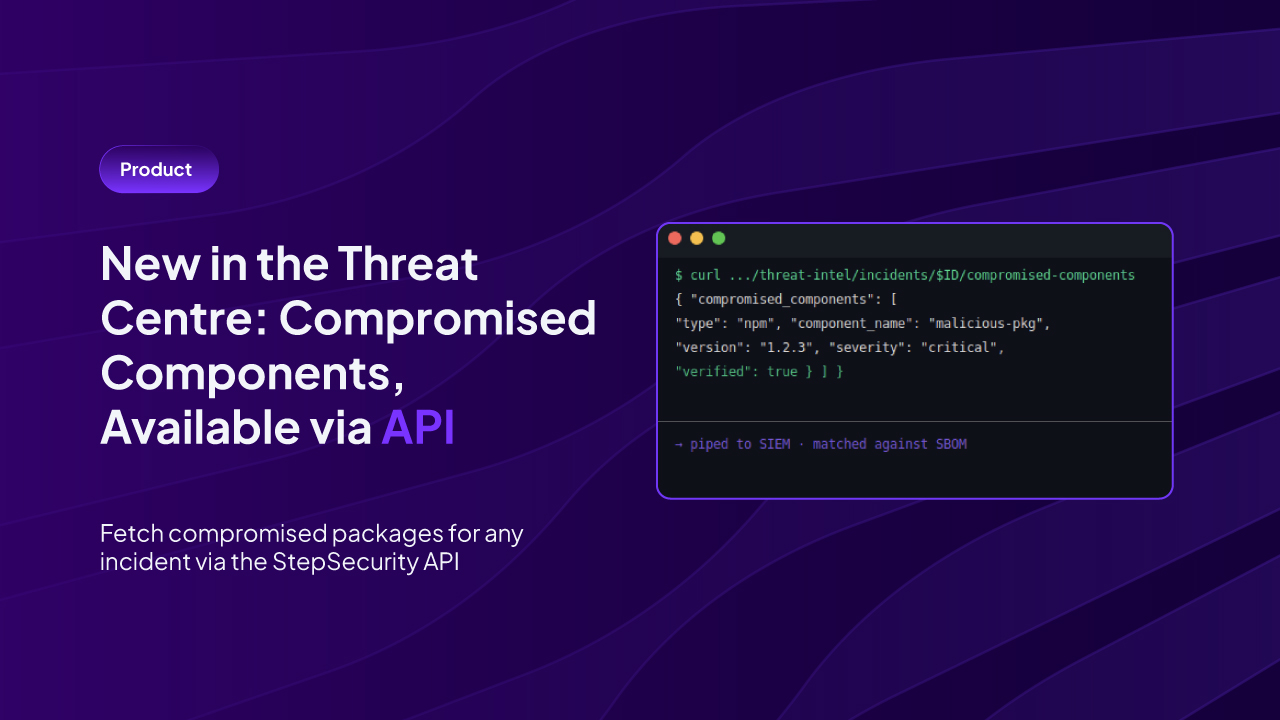 New in the Threat Center: Compromised Components, Now Available via API
StepSecurity added a GET /github/{owner}/threat-intel/incidents/{incidentId}/compromised-components API endpoint to its Threat Center, returning structured data (package ecosystem, version, severity, verified status) for OSS components tied to a detected supply-chain compromise incident. It's positioned as the automatable counterpart to existing Threat-Intelligence detection events (SIEM/Slack/webhook alerts), PR-level compromised-package checks, and the Secure Registry, letting teams pull exact affected packages/versions on demand to drive incident response and cross-check against their SBOM or lockfiles.
 stepsecurity.ioarticleAdded 3 Sep 2026, published 9 Jun 2026🛡️ Security
 Updating the taxonomy of failure modes in agentic AI systems: What a year of red teaming taught us | Microsoft Security Blog
Microsoft's AI Red Team releases v2.0 of its Taxonomy of Failure Modes in Agentic AI Systems, adding seven new categories — agentic supply chain compromise, goal hijacking, inter-agent trust escalation, computer-use-agent visual attacks, session context contamination, MCP/plugin abuse, and capability/architecture disclosure — drawn from 12 months of red team engagements against deployed agents. The post details operational findings (HitL bypass via consent fatigue was the most exploited failure mode, with several zero-click end-to-end exfiltration chains observed) and new mitigations spanning supply chain SBOMs for agent components, zero-trust cryptographic inter-agent identity, and hardened human-in-the-loop consent architecture. It also cites context driving the update, including OpenClaw's 512-vulnerability audit and CVE-2026-25253, and 99 MCP-related CVEs published in 2025.
 microsoft.comarticleAdded 1 Jul 2026, published 4 Jun 2026🛡️ Security

Showing 30 of 33
Show more