- Show HN: I Turned DOOM into a Transformer
Doomformer compiles integer neural networks into ZDoom maps that run in ViZDoom. Voodoo dolls do the arithmetic, and sector light levels and plane heights hold the values. Python reads every value back and compares it with a NumPy integer reference at tolerance 0. It runs MNIST (97.16 % on all 10,000 digits, every pass exact), small transformers, a learning perceptron and a SUBLEQ machine. It is about 23,000 times slower than NumPy on a small MLP.
 github.comrepoAdded 30 Oct 2026, published 29 Oct 2026🧠 AI
- Show HN: Farol – A risk map of a pull request for the person who approves it
farol is a free, MIT-licensed CLI and GitHub Action that runs after an AI code review and gives the human approver a risk verdict (fast track, quick review, careful review) and a 0-100 score for a pull request. It uses the TypeScript type checker, go/types and Python ast to trace which pages, APIs and jobs a change reaches, and it adds diff coverage, security findings and contract breaks. It never executes or sends code.
github.comrepoAdded 26 Oct 2026, published 25 Oct 2026🧠 AI - alirezarezvani/claude-skills
claude-skills is an MIT-licensed library of about 398 Claude Code skills, agents, personas and plugins across 20 domains, including engineering, marketing, compliance and C-level advisory. Each skill is a SKILL.md with stdlib-only Python CLI tools and reference docs. Install scripts and convert.sh adapt it to Codex, Gemini CLI, Cursor, Aider, Windsurf and other coding agents, and it includes a skill-security-auditor scanner.
github.comrepoAdded 25 Oct 2026🧠 AI - alirezarezvani/claude-skills
claude-skills is an open-source MIT library of about 398 Claude Code skills, agents and plugins that also installs into Codex, Gemini CLI, Cursor and 9 other coding agents. The security-relevant parts are skill-security-auditor, a stdlib-only Python scanner that checks skills for command injection, data exfiltration, prompt injection and dependency supply-chain risks before install, plus a security-guidance PreToolUse hook, a security suite and compliance skills (ISO 27001, SOC 2, GDPR).
github.comrepoAdded 25 Oct 2026🛡️ Security  affaan-m/ECC | RepoDir
ECC (affaan-m/ECC) is an open-source performance optimization system for AI coding agents. It packages 261+ skills, 64+ agents and 84+ commands that tune Claude Code, Codex, Cursor and other agent harnesses for speed, memory and security. Practitioners can use it as a ready-made skills and harness configuration set. The RepoDir page gives only this short description, with no install steps or benchmarks.
 repodir.comrepoAdded 24 Oct 2026🧠 AI
- Spectrmachina/Ztrust
ZTrust is a Python supply-chain scanner that checks manifests, lockfiles, source and GitHub workflows for vulnerable or malicious dependencies (via OSV.dev), typosquats, leaked secrets, unsafe lockfiles and risky CI patterns such as pwn requests and script injection. It outputs console, JSON and SARIF 2.1.0 and ships as a GitHub Action. It also includes a FastAPI bounty service using commit-reveal and shielded Zcash payouts for researchers.
github.comrepoAdded 27 Oct 2026, published 22 Oct 2026🛡️ Security - SnailSploit/Claude-Red
claude-red is an MIT-licensed library of offensive security skills for the Claude Skills system, planned at about 130 skills across 23+ categories (web, Active Directory, cloud, exploit development, EDR evasion and others). Each skill is a SKILL.md file that loads on conversational triggers, so unused skills cost no context. It installs by git clone, sparse checkout per category, install.sh or pasting into a system prompt.
github.comrepoAdded 22 Oct 2026🧠 AI - SnailSploit/Claude-Red
claude-red is a library of offensive security skills for the Claude Skills system, each a SKILL.md file that loads on conversational triggers (for example, mentioning SQL injection loads offensive-sqli). Categories include web, Active Directory, cloud, mobile, exploit development, fuzzing, privilege escalation, post-exploitation and AI. It targets about 130 skills across 23+ categories, with an install script and sparse-checkout install per category. Built on Sahar Shlichov's offensive checklists, MIT licensed.
github.comrepoAdded 22 Oct 2026🛡️ Security - Cyber Detective💙💛 (@cyb_detective) on X
Python Cybersecurity Libraries is a curated GitHub list by Yogsec, shared in a post by cyb_detective. It groups Python libraries by task: network analysis, penetration testing, threat intelligence, reverse engineering and malware analysis, forensics and investigation, web application security, CTF, and machine learning for security. The tweet shows only the category names, not the individual libraries.
 x.comrepoAdded 24 Oct 2026, published 21 Oct 2026🛡️ Security
- eness/php2shell-CVE-2026-109618-CVE-2026-109619-PoC
php2shell is the name given to two critical pre-auth remote code execution flaws, CVE-2026-109618 and CVE-2026-109619, in PHP core's session upload progress handler (php_session_rfc1867_callback), where zend_hash_update frees live zval pointers that are later reclaimed and redirected into zend_call_function to run zif_system. This repository ships poc_109618.py, a fully automated four-stage HTTP exploit that leaks ASLR offsets via Set-Cookie headers against php:8.4.26-apache on Debian Bookworm, along with a root-cause C source patch, mitigation scripts to disable session.upload_progress, and WAF/ModSecurity/Lighttpd/Apache rules plus detection guidance for anomalous PHP worker child processes. Confirmed PHP versions include 8.4.4 and 8.2.34, with EOL branches (5.x, 7.x, 8.0, 8.1) left without official vendor patches.
github.comrepoAdded 23 Oct 2026, published 21 Oct 2026🛡️ Security - ikow/php2shell-poc
php2shell-poc is a proof-of-concept and detection toolkit for CVE-2026-109618 and CVE-2026-109619, two PHP vulnerabilities tied to session.upload_progress handling and a Zend engine out-of-memory bailout path affecting PHP 5.4.0 through 8.5.11. The repository includes three working exploit chains, a Docker-based lab (PHP-FPM, nginx, Apache mod_php) for reproduction, and pre-built Suricata, Sigma, ModSecurity, and Lua detection rules. The author recommends disabling session.upload_progress as an interim mitigation, noting the underlying memory corruption requires a full PHP patch to fix.
github.comrepoAdded 23 Oct 2026, published 21 Oct 2026🛡️ Security - Show HN: VoidAccess – open-source dark web OSINT, from query to a graph
VoidAccess is a self-hosted, MIT-licensed dark web OSINT platform that runs a 13-step pipeline from a research query to a relationship graph. It collects from Tor indexes, paste sites, code forges, security feeds and .onion seeds, applies content-safety filters, and exports STIX 2.1, MISP, Sigma, YARA, Snort, Suricata, CSV and JSON. It runs as a CLI with SQLite or as a Docker Compose stack with PostgreSQL, FastAPI and Next.js.
github.comrepoAdded 21 Oct 2026, published 20 Oct 2026🛡️ Security  Abhinav Singwal (@yogsec) on X
GetSubDomains is an open-source tool by yogsec that enumerates subdomains by querying crt.sh certificate transparency logs. It is aimed at the reconnaissance step of penetration tests and bug bounty work. The source is a short tweet pointing to a GitHub repository, so usage details and options are not given.
x.comrepoAdded 21 Oct 2026, published 19 Oct 2026🛡️ Security- DietrichGebert/ponytail
Ponytail is a single skill prompt (skills/ponytail/SKILL.md, with a compact AGENTS.md) that makes coding agents write only the code a task needs, reusing existing components while keeping validation, error handling, security and accessibility. The author benchmarked it in Claude Code with Opus 5.5 over 39 tasks, 5 runs each, including a real FastAPI + React repo. They report -53% code, -41% time, -26% cost and -45% tokens, and 98% of risky logic shipping with a test versus 68% without. It adds /ponytail-review and /ponytail-audit commands, a Claude Code cost/token band with a local board, and installs through Claude Code and Codex plugin marketplaces or as a rules file for Cursor, Copilot, Gemini, OpenCode and others.
github.comrepoAdded 17 Oct 2026🧠 AI - OWASP/MCP-Security-Testing-Guide
OWASP MCP Security Testing Guide is a living, GPL-3.0 collection treating the Model Context Protocol as a security boundary from user through model, MCP client, MCP server and tool to the target system. It covers threats, secure development, host/client controls, supply chain, enterprise gateways, detection, incident response, taxonomy, public incidents, case studies and review checklists, with 79 tests in Chapter 3 (sections 3.1–3.19). It includes a finding template, and it links the MCP Goat lab for safe practice. It is useful to AppSec, red team and SOC people assessing MCP deployments.
github.comrepoAdded 17 Oct 2026🛡️ Security - alex09x/kyb
KYB (Know Your Business) is a Rust/axum server that stores agent-written knowledge, incident reports and tasks as Markdown files in Git, one commit per change. Search is hybrid: Tantivy BM25 fused by reciprocal rank with local multilingual-e5-small ONNX vectors, and it can query historical versions or "as of" a date. It ships a kyb CLI, a native MCP endpoint (Claude Code, Codex, Antigravity, Gemini CLI), an installable agent skill, token auth with per-write attribution trailers, secret scanning on writes, and a web console. It targets persistent shared operational memory for multi-agent, multi-machine fleets.
github.comrepoAdded 17 Oct 2026🧠 AI - enisaeu/enisa-sbd-playbook
ENISA repository of 22 Secure by Design and Secure by Default playbooks for SMEs building products with digital elements. Each playbook has a principle, objective, checklist, minimum evidence and release gate, covering design, build, deployment, maintenance and decommissioning. It supports progressive adoption and CRA readiness without replacing legal obligations.
github.comrepoAdded 17 Oct 2026🛡️ Security - AikidoSec/safe-chain
Aikido Safe Chain is an open-source local proxy and shell-alias wrapper for npm, yarn, pnpm, bun, pip, uv, poetry, pipx and pdm. It checks every package download, including deep dependencies, against the Aikido Intel malware feed and blocks malicious packages before install. It also enforces a configurable 48-hour minimum package age by suppressing too-new versions in registry metadata. It supports custom registries and a self-hosted malware-list mirror, and has CI/CD install recipes for GitHub Actions, Azure Pipelines, CircleCI, Jenkins, Bitbucket and GitLab.
github.comrepoAdded 17 Oct 2026🛡️ Security - santosomar/AI-agents-for-cybersecurity
Companion repository for Omar Santos's Pearson and O'Reilly trainings and books. It has eight parts of runnable Python labs: chat models, embeddings, prompt templates, LCEL prompt chaining, Chroma-based RAG, ReAct/LangGraph/CrewAI/DeepAgents agents, and FastMCP servers (nmap, CISA KEV, Shodan). It also includes guides to six agentic frameworks (OpenClaw, Hermes, Agent Zero, OpenHands, Paperclip, Buzz), a tokenomics module on agent cost (context compounding, prompt caching, model routing, token budget guards, batch API, cost per accepted outcome), and a vendor-neutral design spec for a human-gated multi-agent assessment harness. It is a current, practical curriculum for building and operating agents. Some examples act on real systems and should only be run in an authorized lab.
github.comrepoAdded 13 Oct 2026🧠 AI - santosomar/AI-agents-for-cybersecurity
Omar Santos's companion repo for his Pearson/O'Reilly trainings and books, organised in eight parts. They cover LangChain prompts, chains and RAG (Chroma), and agents (LangGraph, CrewAI, DeepAgents). They also cover FastMCP security servers (nmap, CISA KEV, Shodan) and attack-surface-management and SOC agent examples. Later parts have security guides to six agentic frameworks (OpenClaw, Hermes, Agent Zero, OpenHands, Paperclip, Buzz) with hardening notes and 2026 CVE mapping, agent cost/tokenomics scripts including denial-of-wallet budget guards, and a vendor-neutral spec for a human-gated multi-agent security-assessment harness (scope manifest, approval gates, kill switch). Useful as a hands-on path into AI-agent security tooling, with warnings that some examples act on real systems.
github.comrepoAdded 13 Oct 2026🛡️ Security - Dan Kornas (@DanKornas) on X
Arcjet JS SDK is an Apache-2.0 JavaScript monorepo that adds runtime security checks to AI apps, agents and HTTP endpoints. It ships framework SDKs (Next.js, Node.js, Bun, Deno, Fastify, NestJS) plus a Guard API for agent tool calls, MCP handlers, queue workers and background jobs that have no HTTP request object. Features include prompt injection detection, sensitive-information detection (PII, credit cards, custom patterns) and token-bucket, fixed-window and sliding-window rate limiting.
x.comrepoPublished and added 11 Oct 2026🛡️ Security - Dan Kornas (@DanKornas) on X
Arcjet JS SDK is an open-source (Apache-2.0) JavaScript monorepo that adds runtime security to AI apps, agents and HTTP endpoints. It ships request SDKs for Next.js, Node.js, Bun, Deno, Fastify and NestJS. It also has a Guard API for places with no HTTP request object, such as agent tool calls, MCP handlers, queue workers and background jobs. Built-in checks cover prompt-injection detection, sensitive-information detection (PII, credit cards, custom patterns) and token-bucket, fixed-window or sliding-window rate limits, including token budgets.
x.comrepoPublished and added 11 Oct 2026🧠 AI - bilawalsidhu/gods-eye-view
God's Eye View is an open-source, vanilla-JavaScript CesiumJS and Vite client that puts live aircraft, ships, satellites (SGP4), earthquakes, fires, public CCTV and mapped ALPR cameras on one photorealistic 3D globe. It adds cockpit tracking, FLIR/NVG sensor shaders and a voice agent built on the OpenAI Realtime API. It works without API keys, and the docs cover server-side key brokering with SSRF protection, localhost binding and a SECURITY.md threat model. For OSINT/GEOINT practitioners it is a hackable base for fusing public signals, with an explicit rule against person-tracking features.
github.comrepoAdded 11 Oct 2026🛡️ Security - argoproj-labs/mcp-for-argocd
TypeScript MCP server for Argo CD that lets MCP clients (Cursor, VS Code, Claude Desktop) list, inspect, create, update, delete and sync applications, read logs and events, and run resource actions through natural language. It supports stdio and HTTP stream transports, with a stateless mode for multi-replica Kubernetes deployments. The security design is detailed: API tokens are read only from env vars or headers and never from tool arguments, the default token is bound to the default base URL, a per-host token registry covers extra instances, a read-only mode disables write tools, and the HTTP listener binds loopback by default and requires an inbound auth token if exposed.
github.comrepoAdded 10 Oct 2026🧠 AI - Show HN: Edi Life OS – self-hosted life dashboard with an MCP server for AI
Edi Life OS is a self-hosted dashboard (PHP 8.1+, MySQL, vanilla JavaScript) that combines focus timer, habits, goals, Kanban tasks, finances and notes in ten workspaces. It includes an optional Node.js MCP server that exposes 15 tools over stdio. The tools let Claude Desktop, Claude Code or Codex read the dashboard, create goals and tasks, log habits and record expenses. The MCP server calls only the app's bearer-token /api/v1 HTTP API and never touches the database or credentials. The README is candid about limits: the token has no scopes, there is no app-level rate limiting, and the secret-note flag is only a visibility setting, not encryption.
github.comrepoPublished and added 9 Oct 2026🧠 AI  The Vulnerable MCP Project — MCP vulnerability database
The Vulnerable MCP Project is a curated, continuously growing database of security vulnerabilities and attack techniques specific to the Model Context Protocol ecosystem. Entries cover concrete CVEs (e.g. CVE-2025-68143/68144/68145 in Anthropic's mcp-server-git), transport-layer SDK flaws (cross-client response leakage, missing DNS rebinding protection in the official TypeScript/Python SDKs), unauthenticated/0.0.0.0-bound servers enabling RCE (MCPJam inspector, MCP Inspector, Grafana MCP), command/path injection in dozens of third-party servers (gemini-mcp-tool, mcp-server-kubernetes, Framelink Figma MCP, Zen MCP, filesystem-mcp), SSRF chains reaching cloud metadata (MarkItDown MCP, mcp-fetch-server), and a large set of AI-specific attacks: tool poisoning, trigger-phrase data exfiltration, prompt injection via GitHub issues, Jira and Google Docs, rug-pull tool mutation, and cross-server tool-name collisions. It functions as the de facto vulnerability registry for the MCP ecosystem, useful for tracking disclosed issues before patching or adopting third-party MCP servers.
 vulnerablemcp.inforepoAdded 6 Oct 2026🛡️ Security
- the_OSINT_rack (@the_OSINT_rack) on X
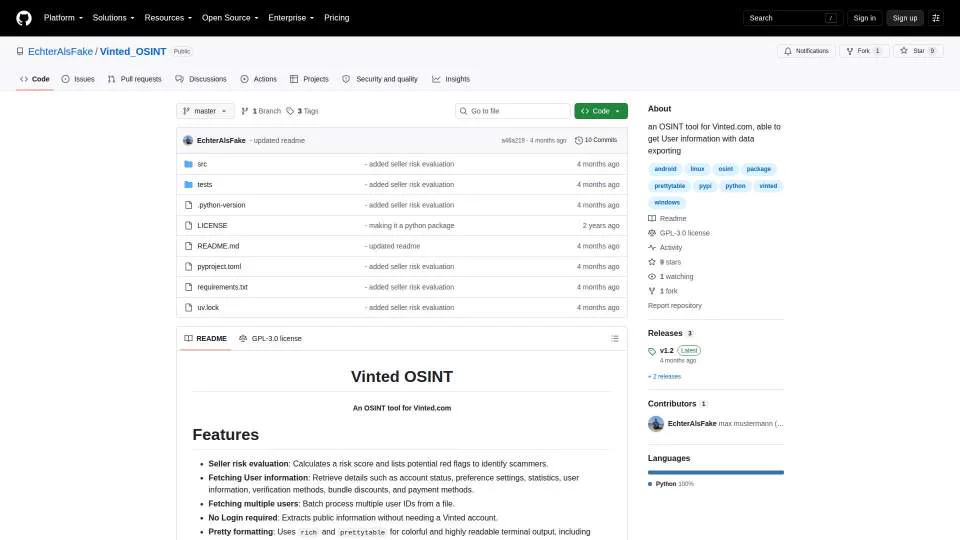
Vinted_OSINT is a GitHub tool by EchterAlsFake that performs open-source intelligence gathering against Vinted.com user profiles, pulling seller/buyer account information and computing a risk score to flag accounts likely run by scammers. It's aimed at buyers wanting to vet sellers before transacting on the second-hand marketplace.
x.comrepoPublished and added 4 Oct 2026🛡️ Security - Microsoft Agent Framework — python-1.20.0 release
Release notes for Microsoft's Agent Framework (Python and .NET SDKs), covering versions python-1.16 through python-1.20 and dotnet-1.19 through dotnet-1.23. Changes span native vector-store connectors (MongoDB, Qdrant, PostgreSQL/pgvector, DuckDB, SQL Server, Azure Cosmos DB, Azure AI Search), Foundry hosting redesigns around request-scoped agent factories and durable Invocations, MCP skill/session security hardening (approval binding, security labels, ZIP-only skill archives), Magentic multi-agent orchestration and handoff routing, and checkpoint/replay correctness fixes across workflows.
github.comrepoAdded 2 Oct 2026🧠 AI - Bifrost (Maxim AI) — open-source LLM gateway
Bifrost is an open-source, high-performance LLM gateway (by Maxim AI) that exposes a single OpenAI-compatible API across 23+ providers including OpenAI, Anthropic, AWS Bedrock, Google Vertex, Azure, Cohere, Mistral, and Ollama. It provides automatic failover, load balancing, semantic caching, Model Context Protocol (MCP) tool integration, budget and governance controls, OIDC user provisioning, and Prometheus-based observability, deployable via npx or Docker with claimed sub-15 microsecond overhead at 5,000 RPS. It is positioned as a drop-in replacement requiring only a base-URL change for existing OpenAI, Anthropic, or GenAI SDK code.
github.comrepoAdded 2 Oct 2026🧠 AI - NuvexNetwork/nuvex
Nuvex is a Solana-native verifiable compute and oracle protocol, still pre-mainnet, whose own README documents unresolved security gaps instead of hiding them: its VRF proof verification relies on solana-ecvrf 0.0.1 (RFC 9381 ECVRF-Edwards25519-SHA512-TAI) which has no known audit, max_fee is stored but never actually charged, and VRF fulfillment is first-come among any node meeting the configured stake/heartbeat threshold — meaning an operator who funds several keys at a low minimum stake can selectively pick which randomness output gets used. The deploy-mainnet script is stubbed to exit before any transaction, and unresolved design questions (fee shares, challenge/reject state transitions) are tracked as explicitly blocked ADRs rather than quietly shipped.
github.comrepoPublished and added 2 Oct 2026🛡️ Security


Showing 30 of 252
Show more