- alex09x/kyb
KYB (Know Your Business) is a Rust/axum server that stores agent-written knowledge, incident reports and tasks as Markdown files in Git, one commit per change. Search is hybrid: Tantivy BM25 fused by reciprocal rank with local multilingual-e5-small ONNX vectors, and it can query historical versions or "as of" a date. It ships a kyb CLI, a native MCP endpoint (Claude Code, Codex, Antigravity, Gemini CLI), an installable agent skill, token auth with per-write attribution trailers, secret scanning on writes, and a web console. It targets persistent shared operational memory for multi-agent, multi-machine fleets.
 github.comrepoAdded 17 Oct 2026🧠 AI
- sakidekin/CVE-2026-41940-PoC
This repository hosts a proof-of-concept for CVE-2026-41940, described as a CVSS 10.0 unauthenticated authentication bypass in cPanel and WHM caused by CRLF injection into server-side session files via the Authorization header. The accompanying Python tool (cve.py) can detect vulnerable cPanel/WHM instances, retrieve system and account information, and perform post-exploitation actions such as running OS commands, changing the root password, and opening an interactive WHM shell. It also supports bulk scanning workflows piped from subfinder, httpx, and Shodan.
github.comrepoAdded 23 Oct 2026, published 11 Oct 2026🛡️ Security - Dark Web Informer (@DarkWebInformer) on X
Infoooze is an open-source command-line OSINT reconnaissance toolkit (github.com/devxprite/infoooze) that consolidates common footprinting tasks into one CLI: username enumeration across platforms, email discovery, subdomain enumeration, port scanning, WHOIS/DNS lookups, IP/HTTP header analysis, EXIF metadata extraction, GitHub recon, and URL scanning/expansion. It automatically saves results, making it a lightweight all-in-one alternative to running several separate recon tools.
 x.comrepoPublished and added 8 Oct 2026🛡️ Security
- chainguard-dev/malcontent
malcontent is Chainguard's open-source malware/supply-chain discovery tool that analyzes binaries (ELF, Mach-O, PE, a.out) and scripting-language source across Linux, macOS and Windows using 14,500+ YARA rules (including third-party rules from Avast, Elastic, FireEye, Mandiant, Nextron and ReversingLabs). Its standout feature is differential analysis ("mal diff"), which compares two versions of a build artifact or OCI image against a known-good baseline to surface newly introduced risky behaviors — the technique the project demonstrates on the 3CX supply-chain compromise by flagging unexpected high-risk changes to libffmpeg. It also supports threshold-based scanning ("mal scan") and unfiltered capability enumeration ("mal analyze"), and is designed to run inside CI/CD pipelines, including air-gapped environments via embedded rules.
github.comrepoAdded 8 Oct 2026🛡️ Security - target/strelka
Strelka is Target's open-source, container-based real-time file scanning system for threat hunting, threat detection, and incident response, built in Go and Python. It runs 50+ scanners (YARA, PE parsing, encrypted ZIP cracking, entropy analysis, etc.) to extract metadata and content from files at enterprise scale, which can feed a SIEM for alerting on suspicious artifacts like an Emotet-laden encrypted ZIP payload.
github.comrepoAdded 8 Oct 2026🛡️ Security - deepfence/YaraHunter
YaraHunter is Deepfence's open-source scanner that applies YARA rulesets against container images, running Docker containers, and filesystems to detect indicators of compromise such as malware and cryptominers. It supports CI/CD build-time scanning, at-rest image scanning, and runtime container scanning, with JSON output for automation, and is designed to eventually integrate into the Deepfence ThreatMapper platform. The README walks through detecting the XMRig cryptominer inside a container image as a worked example.
github.comrepoAdded 8 Oct 2026🛡️ Security - Dark Web Informer (@DarkWebInformer) on X
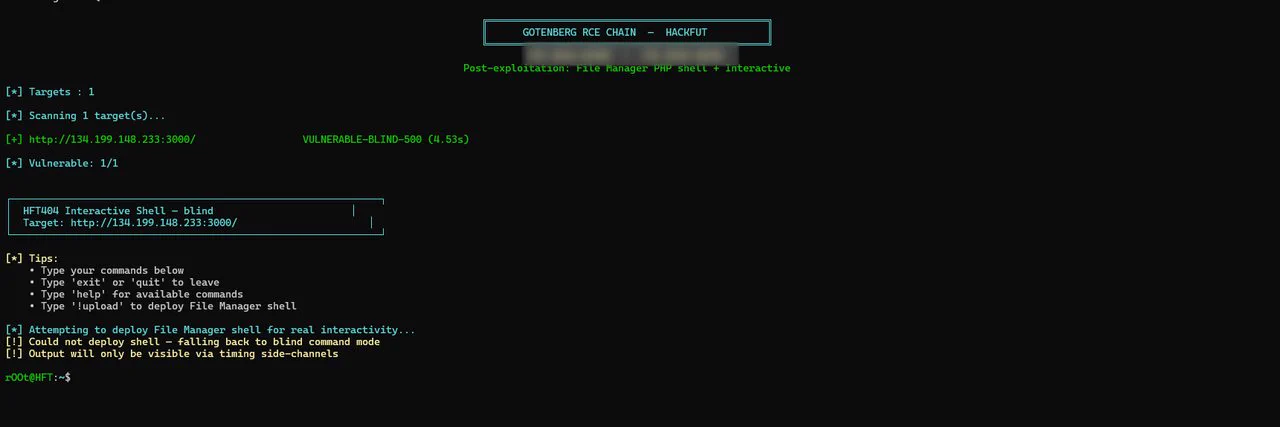
A public PoC chains CVE-2026-42589 and CVE-2026-40281 to achieve unauthenticated remote code execution against Gotenberg (a document/PDF-conversion microservice), abusing metadata injection flaws in the /forms/pdfengines/metadata/write endpoint. The tool supports vulnerability detection, interactive command execution, reverse shell delivery, and multi-target scanning against Gotenberg versions ≤8.30.1 (patched in 8.31.0).
x.comrepoPublished and added 5 Oct 2026🛡️ Security - DeepZero
DeepZero is an open-source orchestration engine that lets researchers define vulnerability-research pipelines declaratively in YAML, handling parallel execution (ThreadPoolExecutor), resumable/fault-tolerant state, and LLM-assessment stages via LiteLLM/Jinja2 prompts. It ships example processors for Ghidra headless decompilation, LOLDrivers.io hash exclusion filtering, PE header/driver metadata extraction, and batch Semgrep scanning, with a dedicated pipeline for BYOVD kernel driver vulnerability research. An extensibility model lets users plug in custom Python processors referenced by path in the YAML config.
github.comrepoAdded 3 Oct 2026🛡️ Security - AI-Infra-Guard (A.I.G) — Tencent Zhuque Lab
AI-Infra-Guard (A.I.G) is Tencent Zhuque Lab's open-source AI red-teaming platform combining AI infrastructure vulnerability scanning (2000+ CVE rules covering vLLM, llama.cpp, LangFlow, n8n, MLflow and 145+ other AI components), MCP server/skill security scanning, LLM API poisoning detection, and multi-turn jailbreak evaluation (Many-Shot, PAIR, GOAT, ActorAttack). It ships CLI tools (skill-scan, mcp-scan, agent-scan), a Docker-deployed web UI, and has produced original research including FORGE-Bench (loss-of-control benchmark), RogueHandoff-20, and SkillJack (persistent skill backdoors), with talks at Black Hat Europe 2025 on MCP security.
github.comrepoAdded 30 Sep 2026🛡️ Security - SpecterOps/Blacklight — local AI agent attack surface mapping toolkit
Blacklight is a SpecterOps toolkit for endpoint forensics on AI coding agents, split into Scout (bounded metadata/filesystem triage across Codex, Claude Code, Cursor, Antigravity CLI, and Grok that finds candidate session artifacts without reading their contents) and Session Analysis (a Python CLI that parses selected JSONL/SQLite session downloads from Codex, Claude Code, Cursor, and Antigravity CLI into ranked, redacted local reports). It's built for investigators who need to identify and review AI agent session history on a host — surfacing config, auth metadata, and high-value indicators — while explicitly leaving secret scanning to external tooling; paths are informed by SpecterOps' Endpoint AI Agent Abuse (EAA) technique catalog.
github.comrepoAdded 27 Sep 2026🛡️ Security - graygnatconsole/mcp-audit-tool
mcp-audit-tool is a dependency-light Python CLI that statically scans Claude Desktop, Cursor, Windsurf, Cline, Zed, and VS Code MCP configuration files for security issues, including hardcoded secrets, unpinned/rug-pull packages, pipe-to-shell installers, tool-poisoning via hidden instructions in tool descriptions, filesystem servers rooted at '/', and unauthenticated plaintext HTTP MCP endpoints. It auto-discovers configs across macOS/Linux/Windows, produces a security score/grade plus SARIF 2.1.0 output for GitHub Code Scanning, and is built around the OWASP MCP Top 10 categories with a CI/CD example that fails builds on severity thresholds. The roadmap adds live server probing over stdio/SSE for runtime rug-pull detection and an ML-based prompt-injection classifier for tool descriptions.
github.comrepoPublished and added 26 Sep 2026🛡️ Security - git-pkgs — dependency history & supply-chain analysis for git repos
git-pkgs is a Go rewrite of a Ruby tool that adds a git subcommand for tracking dependency changes across a repository's history, indexing manifests/lockfiles from 36+ package managers (npm, RubyGems, Cargo, PyPI, Maven, Composer, Go modules, etc.) into a local SQLite database. Beyond history/blame/diff, it offers supply-chain security commands: `vulns` (OSV-based CVE scanning with SARIF output for GitHub code scanning, plus blame/praise/exposure for remediation metrics), `licenses` (with drift detection and CI-friendly exit codes), `deprecated`, `provenance` (trusted-publishing/attestation checks), `integrity` (lockfile hash drift detection), `maintainers`/`health` (via ecosyste.ms metadata), and `sbom` export in CycloneDX/SPDX. It also supports a dependency-aware `bisect` to find when a vulnerability, license change, or capability (e.g. network access) was introduced, and ships GitHub Actions for CI integration.
github.comrepoAdded 25 Sep 2026🛡️ Security - shai-hulud-detect: multi-ecosystem npm/PyPI/Composer/Crates/Go/Hex/RubyGems supply-chain worm scanner
shai-hulud-detect is a dependency-free Bash scanner that checks projects against a 5,782-entry list of compromised npm, PyPI, Composer, Crates, Go, Hex, and RubyGems package versions, plus content-pattern indicators of compromise (malicious file hashes, C2 domains, dead-man's-switch artifacts, forged commits, suspicious lifecycle hooks) tied to the Shai-Hulud supply-chain attack waves. It supports single-project and bulk scanning, CI-friendly exit codes, JSON/log output for pipeline gating, and a --check-host mode to detect the May 2026 gh-token-monitor/kitty-monitor persistence daemons that wipe hosts if their monitored GitHub token is revoked (with a documented safe remediation order). Detection is read-only; new package entries are sourced from named threat-research firms (Socket, StepSecurity, Aikido, Snyk, JFrog, Wiz, Semgrep, SafeDep, GitGuardian, OX Security) and cited in PRs.
github.comrepoAdded 23 Sep 2026🛡️ Security - nealbridges/VulnHunter
A maintained, harness-portable fork of Capital One's open-source VulnHunter — an agentic AI tool that performs attacker-first forward analysis on source code to find exploitable vulnerabilities, falsify weak findings, and produce evidence-backed PoCs rather than pattern-matched SAST alerts. This fork adds containerized (Docker-based) exploit validation, measured-impact PoCs (rows leaked, amplification factor, etc.), and portability across agent harnesses (Claude Code, Codex, Grok, etc.) via environment-contract prompt files, plus an unattended operator (vulnhunter-run) and batch-scanning/benchmark harness tested against OWASP NodeGoat, Juice Shop, and WebGoat.
github.comrepoAdded 6 Oct 2026, published 22 Sep 2026🛡️ Security - StellarFoundry/soroban-security-scanner
soroban-scan is an open-source, deterministic static analyzer for Stellar Soroban smart contracts and Rust projects. It ships 19 Soroban-aware detectors (SS-001 to SS-033) covering missing authorization, re-initialization, cross-contract call ordering, unchecked arithmetic and storage or resource misuse. Output includes JSON, SARIF 2.1.0 and GitHub annotations, with baselines and a PR-scanning Action. The project describes itself as early development.
github.comrepoAdded 28 Oct 2026, published 21 Sep 2026🛡️ Security - Betterleaks — secrets scanner from the Gitleaks creator
Betterleaks is a configurable, fast secrets scanner maintained by the original Gitleaks author and team, capable of scanning git history, local filesystems, stdin, GitHub/GitLab orgs and specific PRs/MRs, Hugging Face models/datasets, and public S3/R2 buckets. Detection rules use regex plus an Expr (with legacy CEL compatibility) based prefilter/filter/validate pipeline, allowing entropy checks, keyword gating, and live API validation of found credentials (e.g. checking a GitHub PAT against api.github.com). It's used in production by projects like Aikido Security and shipped inside MegaLinter.
github.comrepoAdded 18 Sep 2026🛡️ Security - sage — Agent Detection & Response (ADR) for AI coding agents
Sage is an "Agent Detection & Response" (ADR) security layer that intercepts tool calls made by AI coding agents — shell commands, URL fetches, file writes — and screens them through multiple detection layers before execution. It combines cloud URL reputation, 300+ YAML local heuristics, a two-tier (heuristic + fine-tuned ML) prompt-injection detector for fetched content, npm/PyPI package supply-chain checks (registry existence, file reputation, age), installed-plugin scanning at session start, and Windows AMSI integration. It ships as a plugin for Claude Code, Cursor, VS Code, OpenClaw, and OpenCode, and is published by Gen Digital (also distributed under the Norton/Avast Sage branding).
github.comrepoAdded 10 Sep 2026🛡️ Security - mukul975/cve-mcp-server
cve-mcp-server is a Model Context Protocol server that gives Claude direct access to 28 security tools spanning 24 APIs (NVD, EPSS, CISA KEV, OSV.dev, GitHub GHSA, MITRE ATT&CK, AbuseIPDB, GreyNoise, Shodan, VirusTotal, MalwareBazaar, ThreatFox, Ransomwhere, and more), fronted by a one-call triage_cve orchestrator. It computes a composite 0-100 risk score from CVSS, EPSS, KEV status, and PoC availability (with a hard CISA KEV override forcing CRITICAL/≥76), supports dependency scanning via OSV, IP/domain reputation lookups with private-IP blocking, and ships an SSVC v2 gated decision mode plus audit logging and XML-bomb protections via defusedxml.
github.comrepoPublished and added 7 Sep 2026🛡️ Security - eldarshiraliyev/BugScanner
BugScanner is an asyncio/httpx Python framework for recon and automated web vulnerability scanning, with a React and FastAPI dashboard. It covers subdomain enumeration (crt.sh, DNS brute force), TCP port scanning, fingerprinting, and modules for XSS, SQLi, CORS, SSRF, open redirect, JWT, IDOR and business logic, plus a Nuclei wrapper. A 5-rule false-positive filter with SPA detection, adaptive rate limiting, WAF detection and SARIF export are included.
github.comrepoAdded 20 Oct 2026, published 5 Sep 2026🛡️ Security - PackageGuard
PackageGuard is an open-source .NET CLI tool that scans NuGet, npm, pnpm and Yarn dependencies (direct and transitive) across a codebase, enforcing hierarchically-configured allow- and deny-lists for licenses, packages and versions. It scores each package's Legal, Security and Operational risk using signals like OSV vulnerability data, maintainer activity, package signing and release cadence, and can emit a CycloneDX or SPDX SBOM enriched with OSV vulnerability data, plus console, HTML and SARIF output for CI/GitHub code scanning. It's positioned as a free alternative to commercial supply-chain tools like Black Duck and Snyk.
github.comrepoPublished and added 31 Aug 2026🛡️ Security - Rekono
Rekono is an open-source pentesting automation platform that chains 19 hacking tools (Nmap, Nuclei, Metasploit, OWASP ZAP, Nikto, Gitleaks, SearchSploit, etc.) so that output from one tool feeds the next, automatically covering recon, service enumeration, vulnerability scanning, and exploit correlation. It deduplicates findings into a single attack-surface inventory per host/port, enriches CVEs with community context for prioritization, tracks fixed/reopened vulnerabilities, and supports team collaboration, scheduled scans, Telegram/email alerts, and report generation for engagements.
github.comrepoAdded 3 Sep 2026, published 27 Aug 2026🛡️ Security - Ashmmmm/crockTail
crockTail is a passive OSINT tool that, given a domain, aggregates DNS records, IP/ASN ownership, TLS certificate details, WHOIS data, and crt.sh certificate-transparency history into a single report. It layers analysis on top of the raw data: plain-language warning/info observations (near-expiry or expired certs, recently registered domains, unusual reissuance, historical subdomains from CT logs), multi-resolver (Google vs Cloudflare) DNS cross-verification to flag possible tampering, and a 0-100 confidence score per scan based on module success and cross-check agreement. It supports batch domain queries and query logging, and is explicitly limited to passive lookups and a standard TLS handshake, no port scanning or active probing.
github.comrepoAdded 30 Sep 2026, published 25 Aug 2026🛡️ Security - duty1g/x64dbg-mcp-server
x64dbg-MCP Server is a native, dependency-free Zig plugin for the x64dbg debugger that exposes 84 MCP tools and 22 event callbacks over Streamable HTTP and SSE transports, letting any MCP-compatible AI assistant drive breakpoints, stepping, memory reads/writes, register and stack inspection, pattern scanning, PE analysis, and module dumping. It implements the MCP 2024-11-05 spec with JSON-RPC 2.0, mandatory bearer-token auth, a Win32 config dialog, and cross-compiles to both x32 and x64 from a single codebase. The project targets AI-assisted reverse engineering and malware-analysis workflows, turning a traditional interactive debugger into an agent-controllable backend.
github.comrepoAdded 2 Oct 2026, published 22 Aug 2026🧠 AI - duty1g/x64dbg-mcp-server
x64dbg-MCP Server is a native, zero-dependency MCP plugin (built in Zig) for the x64dbg Windows debugger that exposes its full API — breakpoints, stepping, memory allocation/read/write, registers, modules, threads, call stack, pattern scanning, xrefs, symbols, PE/OEP analysis and module dumping — as 84 MCP tools plus 22 event callbacks over Streamable HTTP and SSE transports with mandatory bearer-token auth. It lets any MCP-compatible AI assistant drive an interactive reverse-engineering session against a running process (e.g. load a binary, set a breakpoint, dump registers, step and inspect the stack) directly from inside x64dbg's address space, with no polling or external process required.
github.comrepoAdded 2 Oct 2026, published 22 Aug 2026🛡️ Security - vscan
vscan is an open-source, lightweight, cross-platform website vulnerability scanner built for authorized security assessments. It combines port scanning and fingerprint identification (using a merged database of ~6,832 fingerprints from eHole, wappalyzergo, and local rules), login credential brute-forcing, sensitive file detection, and vulnerability PoC checks compatible with both Xray and Nuclei PoC formats. It supports flexible input (STDIN/host/IP/CIDR/URL/TXT) and output formats (JSON/TXT/CSV/STDOUT).
github.comrepoPublished and added 15 Aug 2026🛡️ Security - ops-engineering-skills
ops-engineering-skills is an open-source library of 296 Agent Skills covering DevOps, DevSecOps, cloud, Kubernetes, CI/CD, GitOps, security scanning, SRE, compliance, databases, messaging, service mesh, serverless, internal developer platforms, MLOps and AgentOps. Each skill is written once to the open SKILL.md standard with machine-checkable frontmatter and eight required sections (prerequisites, steps, pitfalls with fixes, worked example), and works natively across Claude Code, GitHub Copilot, OpenAI Codex, Cursor and Gemini CLI without a translation layer. It ships an automated validator, cross-reference integrity checks, a marketplace/plugin structure for Claude Code, and a generic install.sh/npx installer for any Agent-Skills-compliant agent.
github.comrepoAdded 22 Sep 2026, published 1 Aug 2026🧠 AI - Slither
Slither, developed by Trail of Bits, is a Python3-based static analysis framework for Solidity and Vyper smart contracts that runs a suite of vulnerability detectors, visualizes contract internals via 'printers', and exposes an API for writing custom analyses using its SlithIR intermediate representation. It integrates into Hardhat/Foundry/Brownie builds and CI (including GitHub code scanning), claims 99.9% parse coverage of public Solidity code and sub-second average analysis time per contract, and ships companion tools like slither-check-upgradeability, slither-prop, and slither-read-storage.
github.comrepoPublished and added 31 Jul 2026🛡️ Security - thewhiteh4t/FinalRecon
FinalRecon is a Python-based OSINT/reconnaissance tool for web targets, gathering header info, whois data, SSL certificate details, crawling, DNS enumeration, subdomain discovery, port scanning, and directory search in a single utility. It's commonly used during the recon phase of web application pentests to consolidate multiple footprinting techniques into one CLI tool.
github.comrepoPublished and added 31 Jul 2026🛡️ Security - Beetle
Beetle is an offline-first mobile application security platform that statically analyzes Android APKs and iOS IPAs (including Flutter and React Native apps), combining decompilation, taint analysis, secret/endpoint extraction, certificate and native-binary hardening checks, and CVE enrichment with explainable 'intelligence engines' (ownership, confidence, evidence selection, finding fusion) that correlate findings into evidence-backed attack chains. It maps results to OWASP MASVS/Mobile Top 10, provides source-level navigation, and exports SARIF, CycloneDX SBOM, and PDF reports, with optional (non-scanning) AI assistance via Claude, OpenAI, Gemini, DeepSeek, or local Ollama for explaining findings.
github.comrepoPublished and added 31 Jul 2026🛡️ Security - Talaria
Talaria is a single-binary, pure-Go Linux privilege escalation scanner that enumerates misconfigurations (SUID/SGID, sudoers, capabilities, cron, Polkit JS rules, systemd EnvironmentFile overrides) and links them into confirmed multi-stage root-escalation chains using an embedded Dijkstra pathfinder. It runs read-only with no disk writes, executes in milliseconds, detects backport-aware 2026 Linux kernel vulnerabilities (Dirty Frag, Fragnesia, Copy Fail, DirtyClone, CIFSwitch, PinTheft, pedit COW), and exports JSON/SARIF for SIEM and GitHub Code Scanning integration.
github.comrepoAdded 3 Sep 2026, published 31 Jul 2026🛡️ Security

Showing 30 of 56
Show more