Skip to content

109 results for “certifi”

What you seeeverything
bleepingcomputer.comarticle🛡️ Security

Google disrupts million-device XCPE Android malware botnet, bans TV box maker

XCPE is an Android TV box botnet of more than 1.3 million devices, which Google's Threat Intelligence Group attributes with high confidence to manufacturer Videostrong Technology, who preinstalled a system-level backdoor in firmware. The backdoor (x.cpe, com.oemservice) used an MQTT broker for commands and loaded ad fraud and residential proxy modules. Google took down C2 servers tied to 10 million more devices and banned Videostrong from certified Android devices.

AndroidAndroid TVMQTT+2
XCPEVideostrong TechnologyGoogle Threat Intelligence Group+17

Threat Intel, Mobile Security, Hardware & RF· Published and added 2 Nov 2026

status.bunny.netadvisory🛡️ Security

Bunny CDN Security Incident

Bunny CDN status-page notice, posted 28 October 2026, about unauthorized access at an infrastructure provider that hosted one bunny.net CDN node in Armenia. Traffic was stopped within 20 minutes and the server wiped. No access to the node was found, but cached content, Pull Zone configs and TLS certificates could have been exposed, so all platform certificates were reissued. Customers with their own certificates should rotate them with new private keys.

Bunny CDNTLS
bunny.netb-cdn.netbunny.run

Threat Intel, Cloud & Infra· Added 31 Oct 2026, published 30 Oct 2026

blog.cloudflare.comwriteup🛡️ Security

4 real? Tracking exploitation and patching of eMudhra’s weak keys

Cloudflare's follow-up on eMudhra's eight trivially recoverable intermediate CA keys (such as 4, 56 and 66), disclosed 19 October 2026. Pingora logging showed about 22,000 handshakes with the weak keys, including about 160 forged certificates made within hours of disclosure. Probes on 50 million challenge pages show many bots, old browsers and Android WebView still trust the chain.

CloudflarePingoraAndroid WebView+2
eMudhraMozillaDennis Jackson+6

Threat Intel, Blue Team & Detection· Published and added 30 Oct 2026

microsoft.comwriteup🛡️ Security

From help desk impersonation to AD CS abuse: Investigating ESC1 and ESC8 intrusion paths

Microsoft Threat Intelligence analysis of two human-operated intrusions that began with Teams help desk impersonation and Quick Assist sessions, then diverged at AD CS. Case 1 abused an ESC1 template for privileged certificates and DCSync, with an excluded account later used for Rclone exfiltration. Case 2 used PetitPotam and ESC8 relay to get a domain controller certificate and PKINIT. Includes investigation steps, AD CS hardening and KQL hunting queries.

Active Directory Certificate ServicesMicrosoft TeamsQuick Assist+3
ESC1ESC8PetitPotam+12

Blue Team & Detection, Threat Intel, Offensive Security· Published and added 30 Oct 2026

github.comcourse🧠 AI

rohitg00/ai-engineering-from-scratch

ai-engineering-from-scratch is a free, MIT-licensed curriculum of 542 lessons in 20 phases, from math and deep learning through transformers, LLM engineering, MCP, agents and capstones. Code is in Python, TypeScript, Rust and Julia. It includes three graded projects (retrieval evaluation, agent trace debugger, tool call firewall), installable tutor skills for Claude Code and Codex, and certification prep tracks.

PythonTypeScriptRust+13
Rohit GhumareOpenClawHermes+6

· Added 29 Oct 2026
securityweek.comarticle🛡️ Security

How Secure Are US Elections? Voting Machine Risks and the Growing Threat of AI

SecurityWeek article examining US election security through a cybersecurity lens. It covers voting machines certified by the Election Assistance Commission but unpatched for up to two years, machines hacked at DEF CON's Voting Village, and QR-code ballots voters cannot verify. Sequent's Shai Bargil proposes open-source software and encrypted vote records. It also covers AI-enabled influence campaigns such as the 2024 Biden deepfake robocall.

Microsoft ElectionGuard
Election Assistance CommissionVoting VillageDEF CON+9

Threat Intel, AI Security· Published and added 29 Oct 2026

securityweek.comarticle🛡️ Security

TLS Flaws Found in GoAhead Web Server Used in Hundreds of Millions of Devices

FoxIO disclosed three TLS flaws in the GoAhead embedded web server from EmbedThis, used on hundreds of millions of IoT, OT and network devices. CVE-2026-115881 (CVSS 9.1) leaves revoked client certificates accepted under mTLS with OpenSSL; CVE-2026-115884 (7.4) bypasses chain-length limits with LibreSSL; a third Mbed TLS bug (5.9, no CVE) weakens TLS 1.2 DHE. GoAhead 6.1.1 fixes the OpenSSL and Mbed TLS issues, and FoxIO released PoC code and fingerprints.

GoAheadOpenSSLMbed TLS+2
CVE-2026-115881CVE-2026-115884FoxIO+4

Hardware & RF, AppSec· Published and added 28 Oct 2026

decrypt.coarticle🧠 AI

OpenAI Proves ETH Is False, and Crypto Twitter Has Questions

Decrypt reports that OpenAI published a 67-page paper (dated 17 October 2026, revised 25 October) claiming its AI found a deterministic subexponential-time algorithm for counting 3-SAT solutions, which would refute the Exponential Time Hypothesis. The proof was formalized in Lean. Impagliazzo, Paturi and Ryan Williams are reviewing it independently and say this is not certification. Anthropic posted a Claude-credited 3-SAT paper on 26 October.

LeanGitHubClaude
OpenAIAnthropicDecrypt+7

research, models· Published and added 27 Oct 2026

github.comcourse🛡️ Security

cks/tasks/cks/course/README.md at master · ViktorUJ/cks

The ViktorUJ/cks course is an open-source, community-maintained preparation course for the CKS (Certified Kubernetes Security Specialist) exam. It has 33 chapters grouped by CKS domain: cluster setup, hardening, system hardening, microservice vulnerabilities, supply chain, and runtime security. It also has 15 labs with automatic checks (labs 101-114), mock exams and Killer.sh guidance. Core labs target Kubernetes v1.36.

KubernetesFalcoTrivy+3
CKSCertified Kubernetes Security SpecialistCNCF Kubestronaut+3

Learning, Cloud & Infra· Added 27 Oct 2026

ethresear.chthread🛡️ Security

Proof of One: one-person-one-identity polling with encrypted ballots — design and reference code, requesting critical review

Proof of One is an open-source design for polls with one verified human per identity and unlinkable ballots. Enrolment proves in zero knowledge that an ICAO 9303 passport chip was signed by a trusted signer, plus an enclave face match. Voting uses threshold exponential ElGamal on Baby Jubjub with Groth16 proofs, and tally uses a GJKR DKG with a 7-day challenge window. The author, who is pseudonymous, discloses that AI agents drafted most of it and asks for critique of unlinkability, circuit completeness and certificate trust.

Groth16Baby JubjubDAVINCI+1
Proof of OneNemo UnusICAO 9303+4

Identity & Access· Published and added 27 Oct 2026

ethresear.charticle🛡️ Security

Inventory of PQ P2P Migrations in the Consensus Layer

Inventory of post-quantum migration work for Ethereum consensus-layer networking, by adust09 of Nyx Foundation. It maps three targets: Discovery v5/ENR signatures and key exchange, TLS 1.3 key agreement in QUIC, and libp2p TLS identity binding and CertificateVerify. It covers the 300-byte ENR and 1,280-byte packet limits, why hybrid KEMs do not authenticate peers, and downgrade and DoS concerns. It selects no algorithm or schedule.

Ethereumlibp2pQUIC+3
ML-KEMECDSAFIPS 203+8

other· Published and added 27 Oct 2026

eprint.iacr.orgpaper🛡️ Security

Poly2MsgLeaks: Certified Key Recovery from Polynomial-to-Message Leakage

Poly2MsgLeaks is a profiled chosen-ciphertext power-analysis attack on the SMAUG-T (TiMER parameter set) post-quantum KEM that recovers the full 512-coefficient PKE secret from six traces on an STM32F415. It recovers 999 of 1,000 unseen secrets and proves an incorrect key is released with probability at most 2^-2095.6. Single-write message assembly and a two-share masked P2M resisted the evaluated six-execution attack.

SMAUG-TSTM32F415
Poly2MsgLeakschosen-ciphertext attackpolynomial-to-message leakage+1

Hardware & RF· Added 28 Oct 2026, published 27 Oct 2026

socket.devarticle🛡️ Security

eMudhra, Brotli, and the Long Tail of a Security Fix

Socket post on why fixing the eMudhra weak-key intermediate CA incident (October 2026) and Brotli memory corruption CVE-2026-111497 takes more than updating Node.js. Bundled Brotli copies in Bun, Python Requests and .NET, Go binaries needing rebuilds, and per-program certificate stores all leave stale copies. It lists steps: track bundled components, keep a rebuild path, use workarounds, and verify the shipped artifact.

Node.jsBrotliBun+6
CVE-2026-111497eMudhraOneCRL+6

Supply Chain, AppSec· Published and added 26 Oct 2026

eprint.iacr.orgpaper🛡️ Security

Chosen Commitments and Certified Decoding Regions in the Adaptive Threshold Schnorr Attack

This IACR ePrint 2026/2632 paper by Demirtaş and Yayla analyses the Crites–Stewart adaptive forgery attack on threshold Schnorr signatures, which needs one call to a sparse linear search oracle (bounded distance decoding of a scaled Reed–Solomon code). It shows that choosing the commitment coefficient vector does not help much: a wrapper adversary with Q challenges succeeds with probability at most QM/p, even if its solvers decode every witness for free. For the six original (N, τ) pairs, M stays below 2^24, so the bound is under 2^-100 after 2^128 challenges at p = 2^252.

Schnorr signaturesReed–Solomon codesfolded Reed–Solomon codes
Crites and Stewart attackGuruswami–WangAshvinkumar–Habib–Srivastava+2

other· Added 26 Oct 2026, published 24 Oct 2026

arxiv.orgpaper🧠 AI

Intervention-Certified Amplification: A Validity Gate for $σ$-Weighted Post-Training

Intervention-Certified Amplification (ICA) is a validity gate for sigma-weighted hybrid SFT/RL post-training. The paper shows that DIAA, a per-sample sigma-weighted hybrid, emits unexecuted tool-integrated reasoning on 29% of MATH-500 prompts (three times vanilla GRPO) even with Python fences removed from its anchor. ICA gates sigma with paired-rollout evidence, cutting TIR to 13.8% (frozen) and 11.2% (online) and raising accuracy from 47.5% to 48.7% and 49.3%. It transfers to GSM8K.

GRPOPython
DIAAIntervention-Certified AmplificationMATH-500+2

training, research· Added 27 Oct 2026, published 24 Oct 2026

eprint.iacr.orgpaper🛡️ Security

When Elliptic-Curve Semiprimality Certificates Reveal Factors

The paper formalizes elliptic-curve semiprimality certificates by adapting the Goldwasser-Kilian primality criterion. For certificates built with complex multiplication, a norm-lattice reconstruction factors N from (N, S, D) alone in expected polynomial time. The author uses it, plus public-point and quadratic-twist attacks, to factor Reble's 1084-digit and Broadhurst's 5061-digit moduli, and shows that hidden-cofactor, withheld-CM-map and private-isogeny repairs also fail.

Goldwasser-Kilian primality criterionReble modulusBroadhurst modulus+4

other· Added 26 Oct 2026, published 24 Oct 2026

endorlabs.comarticle🛡️ Security

Everything, everywhere, all at once… the week software broke | Endor Labs

Endor Labs roundup of the 20 to 21 October 2026 patch wave: eMudhra certificate authority keys that anyone can recover, PHP2Shell (CVE-2026-109618, CVE-2026-109619), Node2Shell (CVE-2026-111497) and malware in LiteLLM 1.107.0. It lists fixed versions (PHP 8.2.35 to 8.5.12, Node.js 22.23.4, 24.22.1, 26.12.1, LiteLLM back to 1.106.2) and explains why many separate trust-store copies each need updating. It closes with advice on triage, remediation and SBOM/VEX reporting.

PHPNode.jsLiteLLM+3
CVE-2026-109618CVE-2026-109619CVE-2026-111497+3

Supply Chain, AppSec· Published and added 24 Oct 2026

stepsecurity.ioarticle🛡️ Security

eMudhra / emSign CA Compromise: What Python, pip, and CI/CD Users Need to Update

Guidance on the October 2026 eMudhra / emSign CA incident, where eight intermediate CA certificates had private keys generated with insufficient randomness. It explains why updating certifi alone does not fix pip's vendored bundle, and lists fixed versions (certifi 2026.10.19, pip 26.2.2, Python 3.15.1, 3.14.9, 3.13.17). StepSecurity's OpenSSL 4.0.3 tests showed the older bundle accepted seven emSign paths, while both corrected bundles rejected all fourteen.

pipPythoncertifi+3
eMudhraemSigncertificate authority compromise+3

Supply Chain, DevSecOps· Published and added 22 Oct 2026

eprint.iacr.orgpaper🛡️ Security

Balsamic: One-round Threshold UOV from GPU-Accelerated FHE

Balsamic is a complete homomorphic Unbalanced Oil and Vinegar (UOV) signer, used to build one-round threshold UOV signatures from a packed discrete-CKKS FHE circuit. A paired-pivot linear solver and pivot-success certificates allow encrypted retry selection. In 2-out-of-3 semihonest signing, each online partial signature takes 10.7 s on an RTX 6000 Ada and 7.77 s on a GB300, with 5.25 MB per response.

UOVCKKSFHE+2
Balsamicuniversal thresholdizerspaired-pivot solver+1

other· Added 24 Oct 2026, published 22 Oct 2026

unit42.paloaltonetworks.comadvisory🛡️ Security

EMudhra Intermediate CA Certificates Compromised

Unit 42 advisory on the compromise of eight intermediate CA private keys belonging to Indian CA eMudhra Limited. The keys were generated with insufficient randomness, so attackers could derive them from the public certificates and sign rogue TLS certificates for MitM attacks. eMudhra has revoked the certificates and browser and OS vendors have untrusted them. Interim guidance covers PKI and trust store audits, reissuance, strict CRL/OCSP checking, log hunting, CT monitoring and CAA records.

Prisma BrowserJavaDocker+2
eMudhraUnit 42Palo Alto Networks Next-Gen Trust Security+1

Threat Intel, Blue Team & Detection· Added 30 Oct 2026, published 22 Oct 2026

blog.cloudflare.comarticle🛡️ Security

Localizing compliance at scale: achieving South Korea’s ISMS certification

Cloudflare's account of obtaining South Korea's ISMS-P certification after a ten-day KISA audit of 80 controls and a preparation period of about a year and a half. It explains that the certificate covers a service delivery boundary rather than a product list, that auditors required readable data flow diagrams, and how Korean sign-up uses itemized consent with social login removed.

CloudflareCloudflare Workers
ISMS-PKISAPersonal Information Protection Act+5

GRC· Added 29 Oct 2026, published 22 Oct 2026

aikido.devarticle🛡️ Security

eMudhra CA compromise: eight private keys, and one of them is 4

eMudhra's eight intermediate CA certificates, chaining to emSign ECC Root CA - G3, had private keys below 256 (one is 4), disclosed on 17 October 2026 by a researcher known as Wayne. Browsers and Microsoft blocked them via revocation pushes, but curl, git, containers, language runtimes and IoT may still trust them. The post gives patched ca-certificates versions, test commands and the timeline.

cURLDockermacOS+3
eMudhraemSign ECC Root CA - G3Wayne+6

Supply Chain, DevSecOps· Published and added 22 Oct 2026

x.comadvisory🛡️ Security

lee1981 (@lee1981b) on X

CyberForge CVE of the Day #084 analyses CVE-2026-76466, a CVSS 9.8 flaw in clustered Cisco Expressway-C and Expressway-E. Persistent database cookies and weak client-certificate validation allow root OS command execution over the network. The fix is X15.5.20 (X14 and earlier must migrate), with no workaround. It adds a per-peer SOC investigation trail, reachability checks and exposure status from CISA SSVC, KEV and EPSS.

Cisco ExpresswayCVSSNVD+2
CVE-2026-76466CWE-798cisco-sa-vcs-static-cred-hr7EWZ8t+2

Blue Team & Detection, Cloud & Infra· Added 24 Oct 2026, published 22 Oct 2026

oracle.comadvisory🛡️ Security

Oracle Security Alert Advisory – CVE-2026-91403 (eMudhra cert revocation)

Oracle Security Alert for CVE-2026-91403 ships Java SE updates that distrust a set of intermediate CA certificates tied to eMudhra. It contains one new patch for Oracle Java SE, described as remotely exploitable without authentication. Customers are told to update Java or apply mitigations listed at ops.java/emudhra and in the Patch Availability Document. No reporter is credited and the page gives no CVSS score or technical detail.

JavaCVSS
CVE-2026-91403eMudhra

Cloud & Infra, AppSec· Added 23 Oct 2026, published 21 Oct 2026

endorlabs.comarticle🛡️ Security

eMudhra CA Compromise: The Trust Stores You Didn't Patch | Endor Labs

The eMudhra CA compromise (disclosed 20 October 2026) involves eight intermediate CA certificates whose private keys can be derived from the certificates themselves. They chain to AAA Certificate Services and three other roots. Browsers block them, but non-browser clients skip revocation and CT checks. Endor Labs finds 25 popular packages with frozen bundled root stores, 11 already patched, and gives a fingerprint-scanning script, test hosts and patch steps.

Endor LabsPythoncertifi+6
CVE-2026-111943eMudhraAAA Certificate Services+9

Supply Chain, AppSec, DevSecOps· Published and added 21 Oct 2026

blog.talosintelligence.comadvisory🛡️ Security

Compromised eMudhra intermediate certificates

Cisco Talos describes eight eMudhra intermediate CA certificates (six TLS, two code signing) whose P-384 private keys were trivially recoverable because a flaw in an April 30, 2025 key generation ceremony produced weak keys with only 3 to 8 bytes of entropy. The post lists certificate SHA-256 hashes and serials, browser and Microsoft blocks, and the Go fix (CVE-2026-111943, Go 1.27.3 and 1.26.10) that filters chains by SPKI hash. It covers impact on VPNs, CI/CD and embedded devices, and Snort SIDs 67363 to 67374.

GoChromeVPN+3
CVE-2026-111943eMudhraemSign Root TLS CA - G3+8

Threat Intel, Cloud & Infra· Published and added 21 Oct 2026

aws.amazon.comarticle🛡️ Security

Best practices for integrating IAM Roles Anywhere with your PKI

Best practices for integrating AWS IAM Roles Anywhere with an external PKI so non-AWS workloads get temporary credentials via X.509 certificates. Covers trust anchor placement, certificate attributes (CN, issuer, SAN) in trust policy conditions, short-lived versus just-in-time certificates, and private key protection with PKCS #11, TPM 2.0 and OS certificate stores. Includes credential helper modes (serve, update), expiry monitoring, blue/green trust anchor rotation and a sample CloudFormation template.

AWS IAM Roles AnywhereAWS IAMAWS Private CA+3
X.509trust anchorPKCS #11+5

Identity & Access, Cloud & Infra· Published and added 21 Oct 2026

danielmangum.comarticle🛡️ Security

Your MCU likely escaped the eMudhra intermediate CA compromise

Analysis of the eMudhra intermediate CA compromise disclosed 20 October 2026, in which eight intermediate CA private keys were weak P-384 keys (top 376 bits zero, one key equal to 4) and publicly accessible. It explains web PKI chains and why browsers enforcing Certificate Transparency were not exposed. It argues MCU firmware that bundles only the single root it needs, as in Zephyr's HTTP GET sample, is likely safe unless it trusts an eMudhra or Sectigo cross-signing root.

ZephyrOpenSSLFirefox+1
eMudhraSectigoCertificate Transparency+6

Hardware & RF, other· Added 22 Oct 2026, published 21 Oct 2026

securityweek.comarticle🛡️ Security

Browsers Block eMudhra Intermediate CAs Over Recoverable Private Keys

Eight intermediate CA certificates issued by Indian CA eMudhra in April 2025 had private keys generated with weak entropy, effectively all zeroes except the last byte, so they could be recovered almost instantly with baby-step giant-step. Mozilla and Google blocked them on 17 October 2026, Apple on 19 October and Microsoft on 20 October. eMudhra blamed a key ceremony script flaw that created a second, weaker key pair.

ChromeFirefoxCloudflare
eMudhraDennis Jacksonbaby-step giant-step+5

other· Published and added 21 Oct 2026

arxiv.orgpaper🛡️ Security

PQ-Vault: Provably Quantum-Safe Asset Custody for Unmodified Ethereum

PQ-Vault is a custody design for unmodified Ethereum against quantum key recovery. It combines a quantum-safe vault contract, a proof-of-stake sidechain with compact certificates, and an optimistic dispute protocol. The paper proves that compact certificates with classically chosen parameters fall from 128 to about 60 bits against quantum attackers, and bounds a seed-update stake-steering attack. For 65,536 validators a certificate is 0.8 MB and verifies in about 20 ms, and the vault accepts a checkpoint for about 420,000 gas.

Ethereum
compact certificatesstake steering

Blockchain· Added 24 Oct 2026, published 21 Oct 2026

coindesk.comarticle🛡️ Security

A company that vouches for websites had secret keys so weak that 8 of them were cracked

eMudhra, an Indian certificate authority with over 60 million issued certificates, had eight CA private keys that were tiny integers such as 4, 56 and 237. Researcher Scott Helme recovered all eight from public certificates in under a second, and the keys were exposed from April 2025. Mozilla, Chrome, Apple and Microsoft blocked them between 17 and 20 October 2026, but curl, Python, Node.js, Go and Java accepted a forged Stripe API certificate because they skip revocation checks.

cURLPythonNode.js+3
eMudhraSectigoScott Helme+5

other· Published and added 21 Oct 2026

simonwillison.netarticle🛡️ Security

eMudhra Intermediate CA Compromise

eMudhra Intermediate CA Compromise is a 20 October 2026 link-blog post reporting that private keys of eight eMudhra intermediate CA certificates were compromised. They chain to roots trusted by the Mozilla, Microsoft, Apple and Chrome programs. Software bundling trust lists needs updating: Linux distros must update ca-certificates, and uv 0.13.4, pip 26.2.2 and certifi 2026.10.19 ship new lists. The post does not describe how the keys were compromised.

Pythonpipuv+2
eMudhra

other· Added 21 Oct 2026, published 20 Oct 2026

blog.cloudflare.comwriteup🛡️ Security

8 eMudhra certificates are compromised. Here's what you need to know

Cloudflare's incident post on the compromise of private keys for eight eMudhra intermediate certificates, disclosed 19 October 2026. The weak keys let an attacker forge certificates for any domain. It describes Cloudflare's patching of trust stores, WARP and cloudflared, tells developers to update the underlying TLS verifier and not disable verification, and points to Dennis Jackson's test site and revocation systems such as CRLSets and upki.

CloudflareCloudflare TunnelWARP+2
eMudhraDennis Jacksonupki+1

Cloud & Infra, Blue Team & Detection· Added 29 Oct 2026, published 20 Oct 2026

x.comrepo🛡️ Security

Abhinav Singwal (@yogsec) on X

GetSubDomains is an open-source tool by yogsec that enumerates subdomains by querying crt.sh certificate transparency logs. It is aimed at the reconnaissance step of penetration tests and bug bounty work. The source is a short tweet pointing to a GitHub repository, so usage details and options are not given.

crt.shGitHub
GetSubDomainsyogseccertificate transparency

OSINT, Offensive Security· Added 21 Oct 2026, published 19 Oct 2026

securityweek.comarticle🛡️ Security

Novel Android RAT ‘Hirudo’ Replaces Banking Apps With Trojanized Copies

SecurityWeek covers ThreatFabric's findings on Hirudo, an Android banking trojan/RAT delivered via droppers hidden in fake shopping, adult video and short drama apps. It replaces eight Indonesian banking apps with modified copies containing a hooking engine that spoofs signing certificates and hides Accessibility services, screen capture and Play Integrity checks, while providing WebRTC screen viewing, camera access and SMS theft. ThreatFabric advises banks to enforce Play Integrity server-side, use behavioral analytics, treat Accessibility signals as risk inputs, and keep backend transaction-risk controls.

Android
HirudoThreatFabricPlay Integrity+2

Mobile Security, Threat Intel, Malware & RE· Published and added 15 Oct 2026

eprint.iacr.orgpaper🛡️ Security

Post-Quantum Certificate-Based PSK Provisioning for WireGuard via Mutual TLS, DTLS, and QUIC: Design and Performance Study

The paper proposes a post-quantum architecture for WireGuard that leaves the core protocol unchanged. A mutually authenticated TLS 1.3 control channel runs over TCP, UDP (DTLS) or QUIC and uses ML-KEM key establishment, with X.509 certificates from a PKI signed with ML-DSA. A shared secret derived from the session's exported keying material is injected into WireGuard's native PSK interface. A Tamarin model of the TLS–WireGuard composition layer checks secrecy, binding and provisioning-order properties and identifies the conditions needed for secure deployment. The authors benchmark handshake latency and CPU time for classical, pure-PQ and hybrid key establishment across the three transports, and compare against the Rosenpass PQ WireGuard baseline.

WireGuardVPN
ML-KEMML-DSARosenpass+5

other· Added 15 Oct 2026, published 14 Oct 2026

token.securitycourse🛡️ Security

Agentic Universe | Token Security

Token Security's "Agentic Universe" is a free learning hub for security and identity teams securing AI agents. It sits between shallow video-only overviews and long certifications, with short concept videos, technical deep dives written by practitioners, checklists to run against your own environment, and free tools. The fetched page is a landing blurb that doesn't list the modules or the specific tools, so the depth of the content is unconfirmed.

Token SecurityAgentic Universe

Learning, AI Security· Added 14 Oct 2026

eprint.iacr.orgpaper🛡️ Security

edaBits in the Exponent (edaBitE) and Issuer-Hiding Blind Signatures from ML-DSA and VOLE-in-the-Head

Presents the first blind signature in which the issuer runs unmodified NIST-standardized ML-DSA, so it works with certified secure elements. Issuance is an ML-DSA signature on a commitment. The blind signature is a VOLE-in-the-head zero-knowledge proof of knowledge of that signature, about 1 MB, under 1 s to produce and 0.5 s to verify. Security reduces to ML-DSA EUF-CMA and the proof system. Issuer-hiding and selective disclosure add a few tens of KB. The paper also introduces edaBitE, a batch consistency check between binary and prime-field commitments that replaces the costly edaBits checks.

ML-DSAVOLE-in-the-Head
edaBitEedaBitsNIST+1

Identity & Access· Published and added 14 Oct 2026

aws.amazon.comarticle🛡️ Security

Quantum-resistant signing on AWS, Part 2: Enforce your ML-DSA algorithm policy with SCPs and IAM

Explains how to turn a cryptographic algorithm policy (approve ML-DSA-65/87, exclude ML-DSA-44) into enforceable AWS controls using SCPs, IAM policies, permission boundaries and KMS key policies. The key lever is the kms:KeySpec condition key (kms:SigningAlgorithm can't distinguish variants, since all use ML_DSA_SHAKE_256), applied to CreateKey, ReplicateKey, Sign, Verify and GetPublicKey. It also covers surfaces without algorithm condition keys (AWS Private CA, ACM import, IAM server certificate upload, ELB TLS) via provisioning pipelines plus CloudTrail and AWS Config drift detection, and the default-allow risk of deny-lists.

AWSAWS KMSAWS IAM+3
ML-DSAFIPS 204NIST+2

Cloud & Infra, GRC· Published and added 12 Oct 2026

eprint.iacr.orgpaper🛡️ Security

Revisiting Witness-Succinct UC-lifting Compilers

The paper introduces verifiable reconstructible straightline codes (VRSCs) as an abstraction for compiling zkSNARKs into Universally Composable (UC) secure protocols. It shows that the witness-succinct UC compiler of Ganesh et al. (EUROCRYPT 2023) is missing a security requirement: permuting previously revealed evaluation openings yields a fresh accepting proof, which invalidates the claimed simulation argument. The fix uses verifier-enforced disjoint evaluation domains and a pairing-based Fischlin-style instantiation with structured Reed-Solomon codes and jointly computed KZG openings. This brings certificate generation to O(n log n) with constant extra proof size and verification work.

zkSNARKKZGReed-Solomon codes
Universal Composabilityverifiable reconstructible straightline codesGanesh et al.+3

other· Added 14 Oct 2026, published 12 Oct 2026

securityweek.comarticle🛡️ Security

Let’s Encrypt Cuts Default Certificate Validity to 64 Days Ahead of 45-Day Switch

Let's Encrypt will issue 64-day certificates by default from February 10, 2027, as a step toward 45-day lifetimes planned for 2028, in line with CA/Browser Forum Baseline Requirements. The last 90-day certificate is expected to expire May 11, 2027, and 64-day certificates are available in staging for testing. Automated clients that support ACME Renewal Info (ARI) need no change. Hardcoded renewal schedules should renew at about two-thirds of the lifetime. Authorization reuse drops to 10 days next year and 7 hours in 2028, which removes the need for CAA rechecking.

Let's EncryptACME
CA/Browser Forum Baseline RequirementsACME Renewal InfoCAA rechecking+1

other, GRC· Published and added 12 Oct 2026

securityweek.comarticle🛡️ Security

Google Domains Impacted by Recent ccTLD Hijacks

Google disclosed that attackers hijacked the authoritative DNS of three ccTLDs (.gh for Ghana, .sl for Sierra Leone, .as for American Samoa) and used control of those domains to obtain unauthorized HTTPS certificates covering several Google domains and domains of other organizations. Google blocked the fraudulent certificates in Chrome, worked with issuing CAs to revoke them, and used Certificate Transparency log analysis to find other affected brands, some of which it proactively notified. Google is urging domain owners to monitor CT logs and publish restrictive CAA records after regaining DNS control, since CAs may cache and reuse prior domain-control-validation checks, letting attackers mint new certs even after the hijack ends.

Chrome
.gh ccTLD.sl ccTLD.as ccTLD+3

Threat Intel· Published and added 9 Oct 2026

microsoft.comarticle🛡️ Security

Post-quantum authentication: Why organizations should start testing certificate ecosystems now

Microsoft Security Blog post arguing that post-quantum cryptography planning must extend beyond encrypted-data confidentiality to authentication and certificate ecosystems, since larger PQC certificate chains and new algorithms like ML-DSA-87 can break PKI workflows, HSMs, and legacy infrastructure. It details Microsoft's PQC TLS Pilot Program, launched August 27, 2026, which lets approved certificate authorities (ComSign, DigiCert, HARICA, IdenTrust, Sectigo, Shanghai Electronic Certification Authority, SSL.com) test ML-DSA-87 certificate issuance under the Microsoft Trusted Root Program, plus Windows 11 builds (KB5101681, KB5101684) that support evaluating ML-DSA certificates via Schannel in non-production environments. It lays out a six-step readiness plan: inventory certificate dependencies, map trust relationships, assess vendor roadmaps, identify long-lived infrastructure, build test environments, and plan a multi-year migration.

WindowsSchannelTLS
ML-DSAML-DSA-87PQC TLS Pilot Program+8

Identity & Access, GRC· Published and added 8 Oct 2026

unchained.comarticle🛡️ Security

The randomness question at the heart of your hardware wallet

Unchained explains how hardware wallets generate entropy for bitcoin keys, covering PRNG vs TRNG theory, physical TRNG mechanisms (ring oscillator jitter, diode avalanche noise, radio static reuse), and NIST SP 800-90B / BSI AIS-31 certification. It compares entropy sourcing and secure-element chip suppliers (STMicroelectronics, Microchip, Infineon, Espressif, Silicon Labs) across Trezor, Ledger, Coldcard, BitBox02, Foundation Passport, Blockstream Jade and Block Bitkey, and walks through the July 2026 Coldcard firmware bug that silently bypassed its hardware TRNG for five years, causing real bitcoin losses. It also covers manual dice/coin entropy generation for BIP39 seed phrases, the Dark Skippy nonce-leakage attack, and multisig as the primary mitigation against single-device key-generation failures.

BitcoinColdcardTrezor+3
Coldcard firmware vulnerability (2026)Dark SkippyMilk Sad+6

Hardware & RF, Blockchain· Added 8 Oct 2026, published 7 Oct 2026

aws.amazon.comarticle🛡️ Security

Improving SPIRE security and resiliency with AWS managed services

AWS Security Blog walkthrough on hardening SPIRE (the SPIFFE Runtime Environment) in production by replacing its default self-managed components with AWS managed services: AWS KMS for SVID signing keys, Amazon Aurora PostgreSQL as the datastore, AWS Private CA as the upstream certificate authority, Amazon S3/CloudFront for trust bundle distribution, AWS Secrets Manager for delivering SVIDs to serverless/container workloads, and Amazon Verified Permissions (Cedar policies) for fine-grained SPIFFE-ID-based authorization. It addresses operational concerns like key custody, datastore resiliency, PKI integration, and offline identity validation, and links to a GitHub reference deployment and a SPIFFE/SPIRE-on-AWS workshop.

AWSKubernetesPostgreSQL+2

Cloud & Infra, Identity & Access· Added 7 Oct 2026, published 6 Oct 2026

blog.googlearticle🛡️ Security

Chrome's Response to Recent ccTLD Registry Hijacks

Google describes a series of registry-level hijacks affecting the .gh (Ghana), .sl (Sierra Leone), and .as (American Samoa) ccTLDs, in which attackers modified authoritative DNS records to obtain unauthorized HTTPS certificates for Google domains and, via Certificate Transparency monitoring, several other major organizations. Chrome mitigated impact by blocking the fraudulent certificates through CRLSets and coordinating revocation with issuing CAs, then urges domain owners to continuously monitor CT logs and publish restrictive CAA records with ACME account bindings, since cached domain-control-validation state can let attackers mint new certs even after DNS control is restored.

Chrome

Threat Intel, Blue Team & Detection· Added 7 Oct 2026, published 6 Oct 2026

eprint.iacr.orgpaper🛡️ Security

PoP! Goes the VOLE: Shorter Proofs of Possession for KEM Certificates

This IACR ePrint paper proposes and benchmarks a non-interactive Proof of Possession (PoP) for the code-based post-quantum KEM HQC, built using the VOLE-in-the-Head (VOLEitH) zero-knowledge paradigm, to solve the practical problem of issuing KEM-based certificates needed by protocols like KEMTLS. The authors integrate their HQC PoP into the ACME certificate-issuance protocol and compare it against existing PoP schemes for Kyber and FrodoKEM, showing Kyber issues certificates faster but at the cost of protocol or NIST-standard compatibility, while their HQC-based PoP keeps compatibility and achieves smaller proof sizes, which matters under unstable-network conditions due to larger KEM-based CSRs.

ACMEHQCKyber+2

Identity & Access· Added 8 Oct 2026, published 6 Oct 2026

eprint.iacr.orgpaper🛡️ Security

Role-Specific Signature Placement in TLS 1.3: Cost Propagation and PQC Migration

An IACR eprint paper evaluating all 13-cubed ways to assign 13 post-quantum/traditional signature parameter sets across the Root, Intermediate and Leaf roles of a TLS 1.3 certificate chain, holding the algorithm set fixed and varying only placement. Across 286 three-algorithm groups, median max/min ratios reach 2.085x for TLS handshake latency, 4.310x for certificate body size and 4.551x for path-validation cost purely from role order, with Leaf placement mattering far more than Root/Intermediate swaps. It also shows that looking only at Certificate-message size can misrank candidates such as ML-DSA-65 versus SLH-DSA-SHAKE-192s once the Leaf signature in CertificateVerify and full authentication-path cost are included, arguing PQC certificate-chain design must account for role-specific cost under real network/load conditions.

TLS 1.3X.509ML-DSA
ML-DSA-65SLH-DSA-SHAKE-192s

AppSec· Added 8 Oct 2026, published 5 Oct 2026

github.comwriteup🛡️ Security

Xray-core concealed a certificate verification bypass vulnerability

A security researcher's first-person disclosure describing a certificate verification bypass in Xray-core (a popular censorship-circumvention proxy): when its pinnedPeerCertSha256 option skips regular TLS verification, a MITM attacker can insert a leaf certificate anywhere in the certificate chain and have the custom pinning logic incorrectly validate it, effectively eliminating certificate verification. The writeup also documents how the vulnerability was silently fixed with a misleading "simplify the code" commit message and left undisclosed to users for nearly half a year until the reporter filed a GitHub Security Advisory.

Xray-core
pinnedPeerCertificateChainSha256pinnedPeerCertSha256allowInsecure+1

AppSec· Added 5 Oct 2026, published 4 Oct 2026

orca.securityadvisory🛡️ Security

Critical Citrix NetScaler Zero-Days Under Active Exploitation

Analysis of two CVSS 9.5 Citrix NetScaler ADC/Gateway zero-days, CVE-2026-88771 (unauthenticated RCE through improper input validation in the management interface, affecting default deployments) and CVE-2026-88772 (memory overflow in DTLS, enabled by default on VPN virtual servers). It lists six more high-severity flaws patched in advisory CTX697096, the affected and fixed versions, and the CISA KEV listing with a federal deadline of 2026-09-30. It advises checking for compromise before patching, since patching can destroy forensic evidence, and gives response steps: isolate, revoke credentials, rebuild firmware, rotate keys and certificates.

Citrix NetScalerVPN
CVE-2026-88771CVE-2026-88772CVE-2026-88773+7

Cloud & Infra, Threat Intel· Published and added 29 Sep 2026

arxiv.orgpaper🛡️ Security

Certified Multi-Source Integrity for Structured Agent Actions

This arXiv paper proposes a certifier for structured, privileged agent actions such as paying an invoice, assembled from potentially corrupted documents and tool outputs, formalizing when multi-source corroboration can be trusted under indirect prompt injection. It uses a corruption-radius rule counted via minimum hitting sets over corruption-distinct evidence classes so laundered or re-published copies cannot fake a quorum, plus deterministic reconciliation and trusted anchors for single-sourced fields. Evaluated on 70,966 sanctions entities and 450 software-supply-chain provenance records, and against five LLM agents where a realistic injection fools all but one model and existing action-gating or provenance baselines are broken while the certifier admits no unsafe action.

LLM

AI Security· Added 2 Oct 2026, published 28 Sep 2026

cisa.govadvisory🛡️ Security

CISA KEV Catalog Additions — Check Point, Arista VeloCloud, F5 BIG-IP (Sept 22, 2026)

CISA added four vulnerabilities to the Known Exploited Vulnerabilities catalog on 2026-09-22 based on evidence of active exploitation: two Check Point multi-product flaws (improper certificate validation CVE-2026-85102, path traversal CVE-2026-93616), an Arista VeloCloud Orchestrator improper input validation bug (CVE-2026-93952), and an F5 BIG-IP APM heap-based buffer overflow (CVE-2026-94127). The alert ties the additions to BOD 26-04, which has FCEB agencies prioritize remediation of KEV CVEs on publicly exposed assets that give total control, and to checking for prior compromise before patching.

CISA KEVCheck PointArista VeloCloud Orchestrator+1
CVE-2026-85102CVE-2026-93616CVE-2026-93952+4

Threat Intel, GRC· Added 26 Sep 2026

arxiv.orgpaper🧠 AI

Scope Before You Persist: Preventing Cross-Family Interference in Agent Memory

This arXiv paper studies persistent memory for frozen-model LLM agents, showing that matching retrieval scope to certification scope prevents locally-valid skill edits from interfering with unrelated task families. Using ORC (Orthogonal Regression Control), an execution-grounded gate for accepting persistent skill edits, on a 12-round code-repair benchmark (ProcStream-RSI), the authors show Scoped-ORC raises mean trajectory utility from 0.713 (global memory) to 0.816 and eliminates harmful deployments (from 6/8 to 0), while accepting far more updates (63 vs 12) with zero harmful acceptances across 27 paired streams.

ProcStream-RSIOrthogonal Regression Control

agents, research· Added 26 Sep 2026

nextgov.comarticle🧠 AI

Tech bills of the week: Creating an AI-focused agency, reviewing AI-assisted cyber attacks and more

A weekly congressional tracker detailing multiple new AI bills: a Casar/Sanders proposal to create a Department of Artificial Intelligence and pause advanced AI development pending a ban on artificial superintelligence; Markey's Cybersecurity and AI Board of Investigations modeled on the NTSB to probe AI-driven cyberattacks (citing an OpenAI system breaching Hugging Face and an Australian health database); Bennet/Welch's Federal Digital Commission expansion for frontier model pre-certification and civil penalties; AI 'kill switch' mandates from Kean and Kennedy; Kelly's AI Horizon Fund taxing tech profits to fund worker transition programs; a bipartisan FTC transparency bill from Coons, Britt, Schatz and Lankford; Bonamici's education/workforce AI framework; and two Barrett bills on VA AI transparency and human review of AI-assisted disability claims.

OpenAIHugging FaceSen. Ed Markey+16

ai-policy· Added 26 Sep 2026, published 25 Sep 2026

arxiv.orgpaper🛡️ Security

Resource-Optimized and Energy-Aware Agentic AI Framework Anchored on Blockchain for Secure Software Supply Chains

This arXiv paper proposes a blockchain-anchored agentic AI framework for securing the software development lifecycle: specialized LLM-backed agents handle source integrity, SBOM/dependency analysis, CI configuration auditing, artifact verification, and runtime policy evaluation, each producing a cryptographically signed attestation recorded on a permissioned blockchain via smart contracts (agent registry, immutable attestation log, release-policy module). Agent-to-agent and agent-to-blockchain communication is secured through a consortium-operated certificate authority, and a sequence flow illustrates a source-code security agent anchoring its attestation on-chain to trigger an allow/block deployment decision. It's a conceptual architecture paper rather than an evaluated deployment, aiming to give decentralized, tamper-resistant provenance for agentic AI monitoring the software supply chain.

SBOMLLM

Supply Chain, AI Security, DevSecOps· Added 2 Oct 2026, published 25 Sep 2026

aws.amazon.comarticle🛡️ Security

Architecting a secure landing zone in the AWS European Sovereign Cloud

AWS Security Blog walkthrough of building a secure, production-ready landing zone in the new AWS European Sovereign Cloud (aws-eusc partition), covering multi-account governance via AWS Control Tower/AFT, IAM Identity Center federation as Terraform code, centralized logging into a Log Archive and Security Tooling account, network perimeter design with dedicated Direct Connect PoPs and VPC endpoints, KMS/External Key Store data protection, and partition-aware CI/CD for pushing container images, AMIs, and artifacts across the partition boundary. It maps design decisions to the AWS Security Reference Architecture and Well-Architected Framework, distinguishes hard partition boundaries from configurable choices, and references BSI C5:2020, SOC 2, and ISO 27001/27017/27018/27701 certifications for EUSC.

AWSAWS European Sovereign CloudAWS IAM+3
BSI C5:2020SOC 2ISO 27001+3

Cloud & Infra, GRC, Identity & Access· Added 7 Oct 2026, published 16 Sep 2026

latent.spacewriteup🧠 AI

Underwriting Superintelligence: Backing Agents you can Sue — Rune Kvist, AIUC

Latent Space interview with Rune Kvist, cofounder of AIUC (AI Underwriting Company), on its $40M Series A and AIUC-1 — a quarterly-updated standard for agent security, safety and reliability that pairs technical controls with third-party testing (jailbreak resistance, hallucination rates, data leakage) and real Lloyd's of London-backed insurance. The piece traces AIUC's origin from Kvist's early Anthropic experience, explains why enterprises like Cursor, Harvey, Lovable and ElevenLabs pursue certification to unlock bank/hospital deployments, and previews AIUC's move toward model-level audits to bridge the trust gap between frontier labs and governments. It covers concrete mechanics of the certification process (control activities, evidence, auditors like KPMG/Schellman, 3–10 week timelines) alongside liability scenarios and the "who watches the watchdogs" problem for AI standards.

Model Context ProtocolOpenClaw
Rune KvistAIUCAIUC-1+23

ai-policy, evals· Added 29 Sep 2026, published 16 Sep 2026

ethresear.charticle🛡️ Security

Post-Quantum: Lattice or Hash-Based (one question, two right answers)

A deep-dive field guide to choosing between lattice-based (ML-DSA/FN-DSA) and hash-based (SLH-DSA) post-quantum signatures, built from interviews with the designers and implementers behind both NIST standards and their deployments. It walks through Mosca's-inequality-style migration timing, CNSA 2.0's split between lattice signatures and stateful hash-based LMS/XMSS for firmware, the stateful-signature "footgun," and why the broader internet (TLS/WebPKI, via Merkle Tree Certificates) is converging on lattices while Ethereum's post-quantum consensus roadmap (leanXMSS, EIP-8292, EIP-8288 aggregation) and Algorand's live Falcon-1024 state proofs lean hash-based or scheme-neutral because of aggregation and on-chain storage constraints. It closes with a decision framework and a rundown of NIST's round-3 "onramp" signature candidates (MAYO, SQIsign, HAWK, etc.).

EthereumBitcoinAlgorand+3
ML-DSASLH-DSAFN-DSA+16

Blockchain, other· Added 3 Oct 2026, published 15 Sep 2026

huntress.comwriteup🛡️ Security

Google Doc Sidebar Sends Mac and Windows Users Down Different Paths to Malware

Huntress SOC analysts Ryan Dowd and Jon Semon tore apart a live social-engineering campaign that began with a fake CoinDesk marketing exec DMing a researcher a Google Doc containing a container-bound Apps Script sidebar. The script ran client-side without OAuth consent, exfiltrated victim IP/geolocation/wallet presence via the Telegram API, then routed macOS users to a piped zsh/DMG AMOS stealer chain and Windows users through ClickOnce and PowerShell loaders using three stolen or fraudulent code-signing certificates (a Norwegian company, Discord, and Lenovo). The Windows chain culminated in NetSupport Manager RMM abuse, a Ledger wallet implant, and a self-generated rogue root certificate authority (spoofing Google Trust Services) installed via MsBuild.exe hollowing to silently intercept HTTPS traffic, which the authors flag as the artifact most likely to survive incident remediation short of full reimaging.

WindowsmacOSGoogle Workspace+3
AMOS stealerClickFixMacSync+6

Threat Intel, Malware & RE· Added 11 Sep 2026, published 15 Sep 2026

huntress.comwriteup🛡️ Security

AD Rights Management Service (Part 2): Extraction, Offline Decryption, and the Unrotatable Key

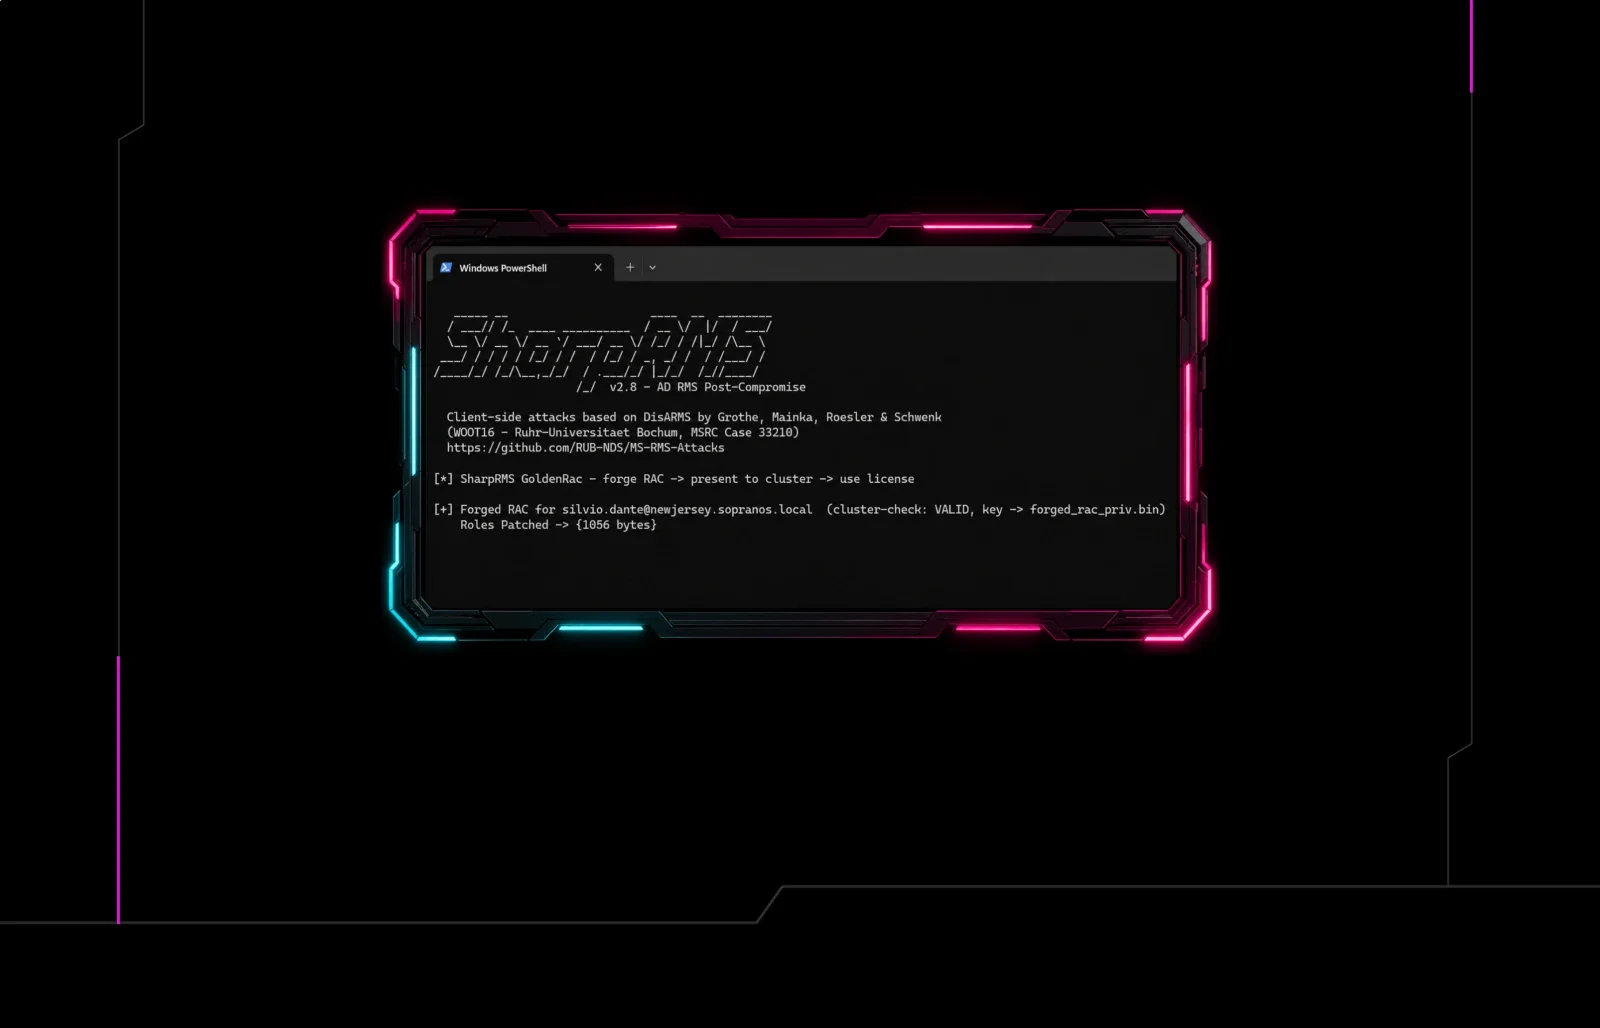
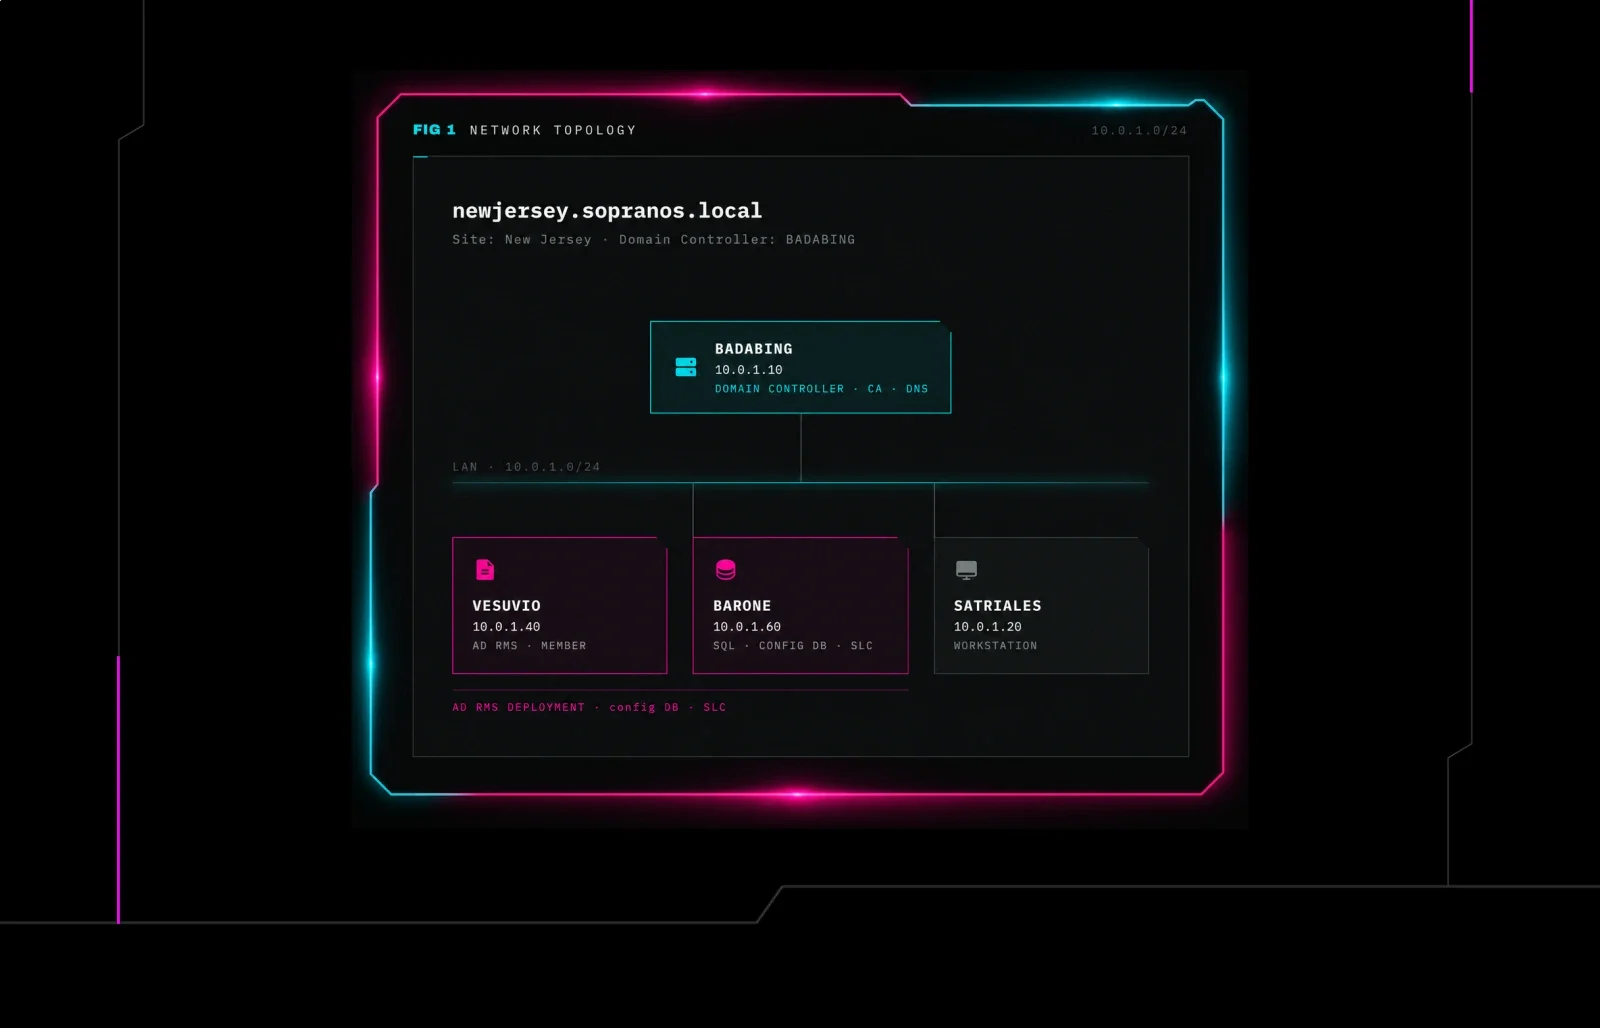
Part 2 of a Huntress series on AD RMS shows how any Service Group member can export the deployment's root SLC private key via the admin SOAP surface's Trusted Publishing Domain (TPD) operation, then use it to offline-decrypt any document the cluster has ever protected — no server contact required. The author goes further, forging XrML Rights Account Certificates signed with the stolen SLC key to trick a live AD RMS server into issuing genuine use licenses for arbitrary/impersonated identities (a "hybrid" of a Golden Ticket and Silver Ticket), and releases the SharpRMS tool that implements extraction, decryption, and RAC forgery. Because the SLC key has a 255-year certificate and no rotation mechanism, the compromise is permanent for all previously protected content, unlike KRBTGT which can be reset to invalidate forged Kerberos tickets.

Active DirectoryAD RMSSharpRMS+3
DisARMSXrMLServer Licensor Certificate+8

Offensive Security, Identity & Access· Added 11 Sep 2026, published 10 Sep 2026

huntress.comarticle🛡️ Security

AD Rights Management Service (Part 1): Architecture, Deprecation, and Reconnaissance

Part 1 of a Huntress research series on Active Directory Rights Management Services (AD RMS), explaining its PKI-based trust model (Server Licensor Certificate signing content keys), why it's still deployed despite Microsoft's deprecation push toward Azure Information Protection, and how to fingerprint and enumerate a cluster from an unprivileged domain account. It introduces SharpRMS, a custom C# tool that speaks the AD RMS SOAP protocol to enumerate clusters and rights-policy templates, and shows how local AD RMS Service Group membership (not Domain Admin) gates the administrative surface where the SLC private key can eventually be reached — setting up Part 2's key extraction and offline decryption.

Active DirectoryWindows.NET+1
DisARMSMSRC Case 33210Sean Metcalf+1

Offensive Security, Identity & Access· Published and added 8 Sep 2026

huntress.comarticle🛡️ Security

CMMC Hit Pause, the FAR Council Hit Play

Huntress blog post clarifying that DoD's July 13 "strategic pause" only suspended CMMC Phase 2 third-party certification requirements (for solicitations after Nov 2026), while Phase 1 self-assessments, SPRS scoring, and DFARS 252.204-7012's 72-hour CUI incident reporting remain fully in force and now face closer DIBCAC/DOJ False Claims Act scrutiny. It also flags the FAR Council's June 23 proposed CUI rule (part of the Revolutionary FAR Overhaul), which would extend 72-hour breach reporting and a NIST 800-171 Rev 3 baseline to all FAR-based federal contractors, not just the defense industrial base, creating a temporary split between CMMC's Rev 2 and the FAR's Rev 3. It closes with a breakdown of 32 CFR 170.21's strict POA&M limits (no POA&M at Level 1, minimum 88/110 score and only 1-point requirements eligible at Level 2) and practical questions MSPs should ask clients about federal contract exposure.

Huntress
CMMCDFARS 252.204-7012DFARS 252.204-7021+12

GRC· Added 8 Sep 2026, published 2 Sep 2026

blackpointcyber.comwriteup🛡️ Security

Built to Blend: Miraak's Modular Post-Exploitation Framework

Blackpoint's Adversary Pursuit Group details Miraak, a novel modular post-exploitation framework discovered through proactive hunting of exposed open web directories. The writeup covers trojanized hostfxr.dll loaders that masquerade as legitimate .NET runtime components (with XOR 0x42/0x5A obfuscated payloads and configs), a PostgreSQL/Timescale database used as the C2 control plane instead of HTTP beaconing, Cobalt Strike BOF-compatible execution inside the agent, and an associated F#-based reverse TCP tunneling implant delivered via a trojanized Microsoft.DocAsCode.Common.dll (DocFX) dependency, with infrastructure pivoting via a self-signed "miraak-socks" TLS certificate and IOCs.

PostgreSQL.NETCobalt Strike+2
MiraakBlackpoint Adversary Pursuit Groupmiraak-socks+4

Malware & RE, Offensive Security, Threat Intel· Added 26 Sep 2026, published 26 Aug 2026

github.comrepo🛡️ Security

Ashmmmm/crockTail

crockTail is a passive OSINT tool that, given a domain, aggregates DNS records, IP/ASN ownership, TLS certificate details, WHOIS data, and crt.sh certificate-transparency history into a single report. It layers analysis on top of the raw data: plain-language warning/info observations (near-expiry or expired certs, recently registered domains, unusual reissuance, historical subdomains from CT logs), multi-resolver (Google vs Cloudflare) DNS cross-verification to flag possible tampering, and a 0-100 confidence score per scan based on module success and cross-check agreement. It supports batch domain queries and query logging, and is explicitly limited to passive lookups and a standard TLS handshake, no port scanning or active probing.

JavaMavenVue+1

OSINT· Added 30 Sep 2026, published 25 Aug 2026

crt.nametool🛡️ Security

crt.name

crt.name is a free subdomain index and API that returns every subdomain on file for a given apex domain plus first-seen dates, built by continuously parsing SAN hostnames from Certificate Transparency logs (Static CT sources like Let's Encrypt Sunlight, Geomys, Cloudflare Raio, plus legacy RFC 6962 logs like Google Argon, Sectigo, DigiCert), supplemented by Internet Archive CT replays, Common Crawl, ICANN CZDS zone files, ProjectDiscovery Chaos, HaGeZi DNS blocklists, and an active hostname prober. It offers a no-token REST API (100 req/IP/day), a Streamable HTTP MCP server exposing a single search tool for agent clients, and is the default crt source in the subfaster CLI subdomain enumerator.

Model Context Protocol
Let's Encrypt SunlightGeomysCloudflare Raio+8

OSINT· Added 3 Sep 2026, published 21 Aug 2026

github.comrepo🛡️ Security

CarterPerez-dev/Cybersecurity-Projects

A GitHub repo of hands-on cybersecurity build projects with full source code, organized into Foundations (pre-beginner, heavily commented single-file Python teaching projects), Beginner, Intermediate, and Advanced tiers, including a work-in-progress DDoS mitigation tool. It also bundles 10 certification/career roadmaps (SOC Analyst, Pentester, Security Engineer, GRC Analyst, etc.) and a curated list of learning tools, courses, and communities, cross-promoting the author's CertGames platform for guided versions of the same projects.

Python
CertGames

Learning· Published and added 21 Aug 2026

huntress.comwriteup🛡️ Security

Post-DEF CON Phishing Uses Malicious Google Doc to Deliver Malware

Huntress researchers document a phishing campaign targeting Black Hat/DEF CON attendees via X DMs impersonating a CoinDesk exec, luring victims into opening a weaponized Google Doc with a custom Google Apps Script sidebar that runs a fake "decryption" flow before delivering ClickFix-style commands or a manual "update" that drops malware. On macOS this delivers AMOS infostealer plus a LaunchDaemon-based polling backdoor with SOCKS5 proxy capability; a follow-up fake DocSend/Dropbox installer delivers a ClickOnce/NSIS loader chain on Windows that installs NetSupport RAT, a process-hollowed rogue Certificate Authority that MITMs VirusTotal traffic, and an incomplete Ledger wallet-targeting implant. The piece includes deep technical detail on the loader's C2 protocol, stolen/fraudulent code-signing certificates, and infrastructure patterns (multi-branded loader domains), plus mitigation guidance and a link to published IOCs.

Google WorkspacePowerShellNetSupport Manager+3
AMOS stealerClickFixSleestak+1

Threat Intel, Malware & RE· Added 3 Sep 2026, published 19 Aug 2026

fossa.comarticle🛡️ Security

FOSSA: CRA Product Classification Explained

FOSSA blog post breaking down how the EU Cyber Resilience Act (Regulation 2024/2847) classifies products with digital elements into four risk tiers — Default, Important Class I, Important Class II, and Critical — each with different conformity assessment paths (self-assessment vs. notified-body third-party assessment vs. European cybersecurity certification). It enumerates the specific product categories named in Annex III (e.g. password managers, VPNs, routers, operating systems, SIEM, browsers) and Annex IV (secure cryptoprocessing hardware, smart meter gateways, smartcards), explains scope exclusions (pure SaaS under NIS2, medical devices, defense products, non-commercial OSS), and gives a four-question decision process for classifying a product ahead of the December 2027 full-compliance deadline.

FOSSA
EU Cyber Resilience ActNIS2Regulation (EU) 2024/2847

GRC· Published and added 18 Aug 2026

xmcyber.comwriteup🛡️ Security

Potential for Remote Code Execution in Microsoft SCCM via Newly-Discovered Exploit Chain

XM Cyber researchers detail a four-stage exploit chain in Microsoft SCCM (Configuration Manager) that lets any unprivileged domain user achieve SYSTEM-level remote code execution on the primary site server: a missing authorization check on the AdminService UploadExtensionInChunks endpoint (CVE-2026-47301), a weak code-signing check that accepts any commercial certificate, a "CabSlip" Zip-Slip-style path traversal in CAB extraction giving arbitrary file write, and DLL hijacking of adsource.dll loaded by the SYSTEM-level SMS Executive service. Microsoft patched the RBAC bypass in July 2026, but the rest of the chain remains exploitable via the built-in Operations Administrator role until a full fix in ConfigMgr 2609 (October 2026); the article also gives log-based detection guidance (AdminService.log DirectoryNotFoundException/HTTP 500 patterns) and interim mitigations.

Microsoft SCCMWindowsActive Directory+1
CVE-2026-47301CabSlip

Offensive Security, AppSec· Added 3 Sep 2026, published 13 Aug 2026

github.comrepo🛡️ Security

SiberKapan

SiberKapan is a Turkey-focused, community-driven open-source threat intelligence platform that aggregates data from FortiGate webhooks, an 11-service honeypot (HoneypotKapan), nginx/Fail2ban log watchers, and external feeds, publishing it as STIX 2.1/TAXII 2.1, a MISP default feed, Sigma/Suricata/Wazuh exports, and REST blocklists. It also runs a real-time phishing/domain-squatting detector via Certificate Transparency log monitoring with fuzzy typosquat and Punycode/IDN decoding, and safely fingerprints SSH-honeypot malware downloads with SSRF-protected, never-executed hashing enriched via MalwareBazaar. The write-up details concrete anti-abuse safeguards: time-based IP score decay, CDN/cloud-proxy allowlisting, UDP-spoofing exclusion, RFC1918 rejection, and manual review gating for weak phishing signals.

MISPFortiGateSuricata+3
CISA KEVAbuseIPDBMalwareBazaar+1

Threat Intel, Blue Team & Detection· Published and added 8 Aug 2026

kuwaitist.github.ioarticle🛡️ Security

ARTOC by White Knight Labs - Review

A reviewer's first-person writeup of the Advanced Red Team Operations Certification (ARTOC) by White Knight Labs, covering a full red team engagement curriculum: building C2 infrastructure with Cobalt Strike and Adaptix, cloud redirectors across AWS, Azure and GCP via CDNs and serverless functions, Active Directory and ADCS exploitation, and kernel and user mode EDR evasion, tested against real enterprise EDR products. The exam is a 48-hour infrastructure build and compromise exercise followed by a 48-hour red team report. The post is a positive testimonial encouraging enrollment rather than a technical walkthrough of any attack.

Cobalt StrikeActive DirectoryAWS+3
ADCS exploitation

Offensive Security, Learning· Added 2 Oct 2026, published 6 Aug 2026

github.comrepo🛡️ Security

UseOSINT/Skills

Collection of 28 skill files for coding agents to run OSINT investigations covering domains, emails, usernames, photos, and companies, using techniques like WHOIS, certificate transparency, reverse image search, and breach lookups.

CursorClaudeShodan

OSINT· Added 30 Sep 2026, published 2 Aug 2026

github.comrepo🧠 AI

UseOSINT/Skills

UseOSINT/Skills is a GitHub repo of 28 SKILL.md files that let Cursor, Claude, and other coding agents run open-source-intelligence investigations — 10 end-to-end workflows (e.g. find-anyone, x-ray-a-company, recon-a-domain-passively) built on 18 reusable technique skills (WHOIS, certificate transparency, reverse image search, breach lookups, chronolocation). Each skill ships with reference material (query cookbooks, indicator guides, registry catalogues) and an install script that symlinks the whole set into ~/.cursor/skills, illustrating a chained, workflow-plus-technique pattern for structuring and routing large agent skill libraries. The repo also documents scope/authorization gating and passive-by-default behavior as part of the skill design.

CursorClaudeShodan
DeHashed

coding-agents, prompting· Added 30 Sep 2026, published 2 Aug 2026

github.comrepo🛡️ Security

thewhiteh4t/FinalRecon

FinalRecon is a Python-based OSINT/reconnaissance tool for web targets, gathering header info, whois data, SSL certificate details, crawling, DNS enumeration, subdomain discovery, port scanning, and directory search in a single utility. It's commonly used during the recon phase of web application pentests to consolidate multiple footprinting techniques into one CLI tool.

FinalReconPython

OSINT, Offensive Security· Published and added 31 Jul 2026

github.comrepo🛡️ Security

Beetle

Beetle is an offline-first mobile application security platform that statically analyzes Android APKs and iOS IPAs (including Flutter and React Native apps), combining decompilation, taint analysis, secret/endpoint extraction, certificate and native-binary hardening checks, and CVE enrichment with explainable 'intelligence engines' (ownership, confidence, evidence selection, finding fusion) that correlate findings into evidence-backed attack chains. It maps results to OWASP MASVS/Mobile Top 10, provides source-level navigation, and exports SARIF, CycloneDX SBOM, and PDF reports, with optional (non-scanning) AI assistance via Claude, OpenAI, Gemini, DeepSeek, or local Ollama for explaining findings.

AndroidiOSDocker+3

Mobile Security, AppSec· Published and added 31 Jul 2026

en.fofa.infotool🛡️ Security

FOFA

FOFA (fofa.info) is a Chinese cyberspace search engine that indexes internet-facing hosts, services, and devices by banner, header, certificate, and icon fingerprints, letting researchers query for exposed assets much like Shodan or Censys. It supports a custom query syntax, icon/favicon-hash search, batch search, and an API for programmatic recon, making it a common tool for attack-surface discovery, threat hunting, and OSINT investigations.

FOFA

OSINT· Added 3 Sep 2026, published 31 Jul 2026

github.comrepo🛡️ Security

Mimikatz Missing Manual

A deep-dive, self-paced manual on Mimikatz and Windows identity internals by Carlos Perez (DarkOperator), refined with input from Benjamin Delpy (Mimikatz's author). It covers LSASS credential dumping, Kerberos ticket forgery/roasting/delegation abuse, PKI/smart card and certificate abuse, DCSync/DCShadow domain persistence, and DPAPI secrets, alongside blue team detection strategies and event log signatures.

MimikatzKerberosActive Directory+3
Benjamin DelpyCarlos PerezDarkOperator+3

Offensive Security, Identity & Access, Blue Team & Detection· Added 3 Sep 2026, published 31 Jul 2026

github.comrepo🛡️ Security

DevCop95/shodan_reconsx

recons101x (shodan_reconsx) is a passive-by-default Python CLI that enumerates hostnames published to certificate transparency logs via ctl.shodan.io, requiring no Shodan API key. It supports optional active features — DNS resolution, TCP/HTTP reachability probing on ports 443/80, bounded live scans, and certificate metadata enrichment — with status states (DNS_ONLY, TCP_REACHABLE, HTTP_REACHABLE, STALE), JSON/TXT output, and safeguards like --max-time, --active-only, and explicit warnings to only scan authorized domains.

PythonShodanPowerShell

OSINT· Added 30 Sep 2026, published 29 Jul 2026

socket.devadvisory🛡️ Security

Socket: Free Certified Patches for Nuxt Security Vulnerabilities

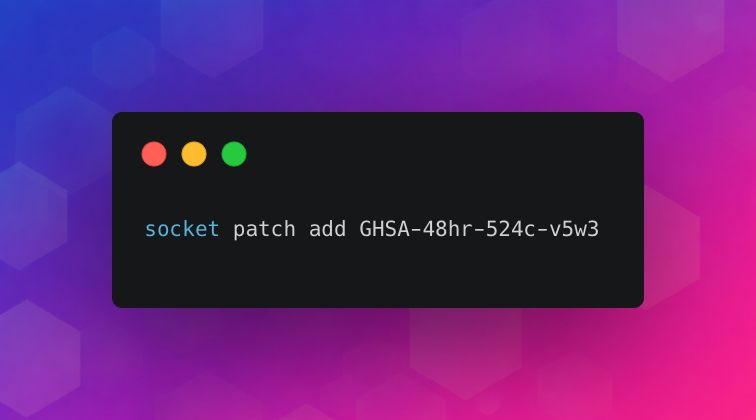
Nuxt 4.5.1/3.21.10 and @nuxt/devtools 3.3.1 patch eight GitHub Security Advisories, the most severe being GHSA-9473-5f9j-94wq, a server-side RCE via server island props reaching Vue's dynamic component resolution when vue.runtimeCompiler is enabled, plus a related unauthorized component instantiation bug (GHSA-48hr-524c-v5w3), a route-rule authz bypass, DoS issues, cross-user payload cache disclosure, and a critical dev-only RCE in Nuxt DevTools. Socket released free Certified Patches for the two highest-severity issues (installable via `socket patch add`) as an interim fix for teams that can't immediately upgrade, and is preparing patches for the rest.

NuxtVue.jsSocket
GHSA-9473-5f9j-94wqGHSA-48hr-524c-v5w3

AppSec, Supply Chain· Published and added 28 Jul 2026

github.comrepo🛡️ Security

aniqfakhrul/CVE-2026-54121

Certighost is a Python PoC for CVE-2026-54121, an Active Directory Certificate Services attack that spins up rogue SMB/LSA and LDAP listeners to intercept the CA's NetLogon-based identity resolution during certificate enrollment. By impersonating a low-privileged computer account and redirecting the CA's lookups to the target Domain Controller's identity, the tool causes the CA to issue a valid certificate for the DC, then uses PKINIT with that certificate to retrieve the DC's Kerberos TGT/ccache and NT hash — a full domain-compromise chain from a single low-privileged account. The repo includes fixes for an in-the-wild NetLogon trust-account error (STATUS_NOLOGON_SERVER_TRUST_ACCOUNT) and a SAN-spoofing bypass for CAs enforcing ESC6-style EDITF_ATTRIBUTESUBJECTALTNAME2 protections.

Active DirectoryImpacketLDAP+2
CVE-2026-54121CertighostESC6+3

Offensive Security, Identity & Access· Added 5 Oct 2026, published 23 Jul 2026

wiz.iowriteup🛡️ Security

Opening the Black Box: Agentless Threat Detection for Virtual Appliances

Wiz details how its Agentless Workload Detection extends EDR-like visibility to FortiGate firewalls by parsing local FortiOS logs (log IDs like 32001/32002/44547/41987) to hunt for credential stuffing, rogue admin account creation, certificate manipulation, NAT/port-forwarding abuse, and FortiManager script abuse. It maps these techniques to real-world campaigns including the FortiBleed credential-compromise campaign, active exploitation of CVE-2026-24858, and UNC3886's use of CVE-2022-41328 to deploy the CASTLETAP backdoor, plus Salt Typhoon's exploitation of CVE-2023-48788 against FortiClient EMS.

FortiGateFortiManagerWiz+3
CVE-2026-24858CVE-2024-55591CVE-2024-23113+8

Blue Team & Detection, Threat Intel, Cloud & Infra· Added 3 Sep 2026, published 22 Jul 2026

github.comrepo🛡️ Security

OSCP & CPTS Study Notes

A GitHub repository (also published as a GitBook) of study notes compiled while pursuing the Hack The Box CPTS certification, structured to double as OSCP prep material. It covers networking fundamentals, enumeration, privilege escalation, Active Directory attacks, and pivoting with hands-on methodologies and tool usage rather than just theory.

Active Directory
OSCPCPTS

Learning, Offensive Security· Added 3 Sep 2026, published 18 Jul 2026

github.comrepo🛡️ Security

0x1ceKing/HTB-Certified-Penetration-Testing-Specialist

A GitHub repository compiling personal study notes and cheatsheets for HackTheBox's CPTS (Certified Penetration Testing Specialist) certification, organized by module: network enumeration (Nmap), web footprinting, file transfers, shells/payloads, Metasploit, password attacks, pivoting/tunnelling, Active Directory enumeration and attacks, web app attacks (SQLi, SQLMap, XSS, LFI, file upload, command injection, Ffuf), and Linux/Windows privilege escalation. It functions as a reference guide mirroring the official HTB Academy course structure rather than original research.

NmapMetasploitsqlmap+2

Learning, Offensive Security· Published and added 18 Jul 2026

github.comrepo🛡️ Security

Trusted-AI/adversarial-robustness-toolbox

Adversarial Robustness Toolbox (ART) is a Python library, hosted by the Linux Foundation AI & Data Foundation, for evaluating and defending machine learning models against adversarial threats: evasion, poisoning, extraction, and inference attacks. It supports major ML frameworks (TensorFlow, Keras, PyTorch, scikit-learn, XGBoost, LightGBM, CatBoost) across data types (images, tables, audio, video) and tasks (classification, object detection, speech recognition, certification), and was developed with DARPA support.

PythonTensorFlowPyTorch+1

AI Security· Published and added 14 Jul 2026

huntress.comwriteup🛡️ Security

Plain Text Passwords: The Risks of Storing Them

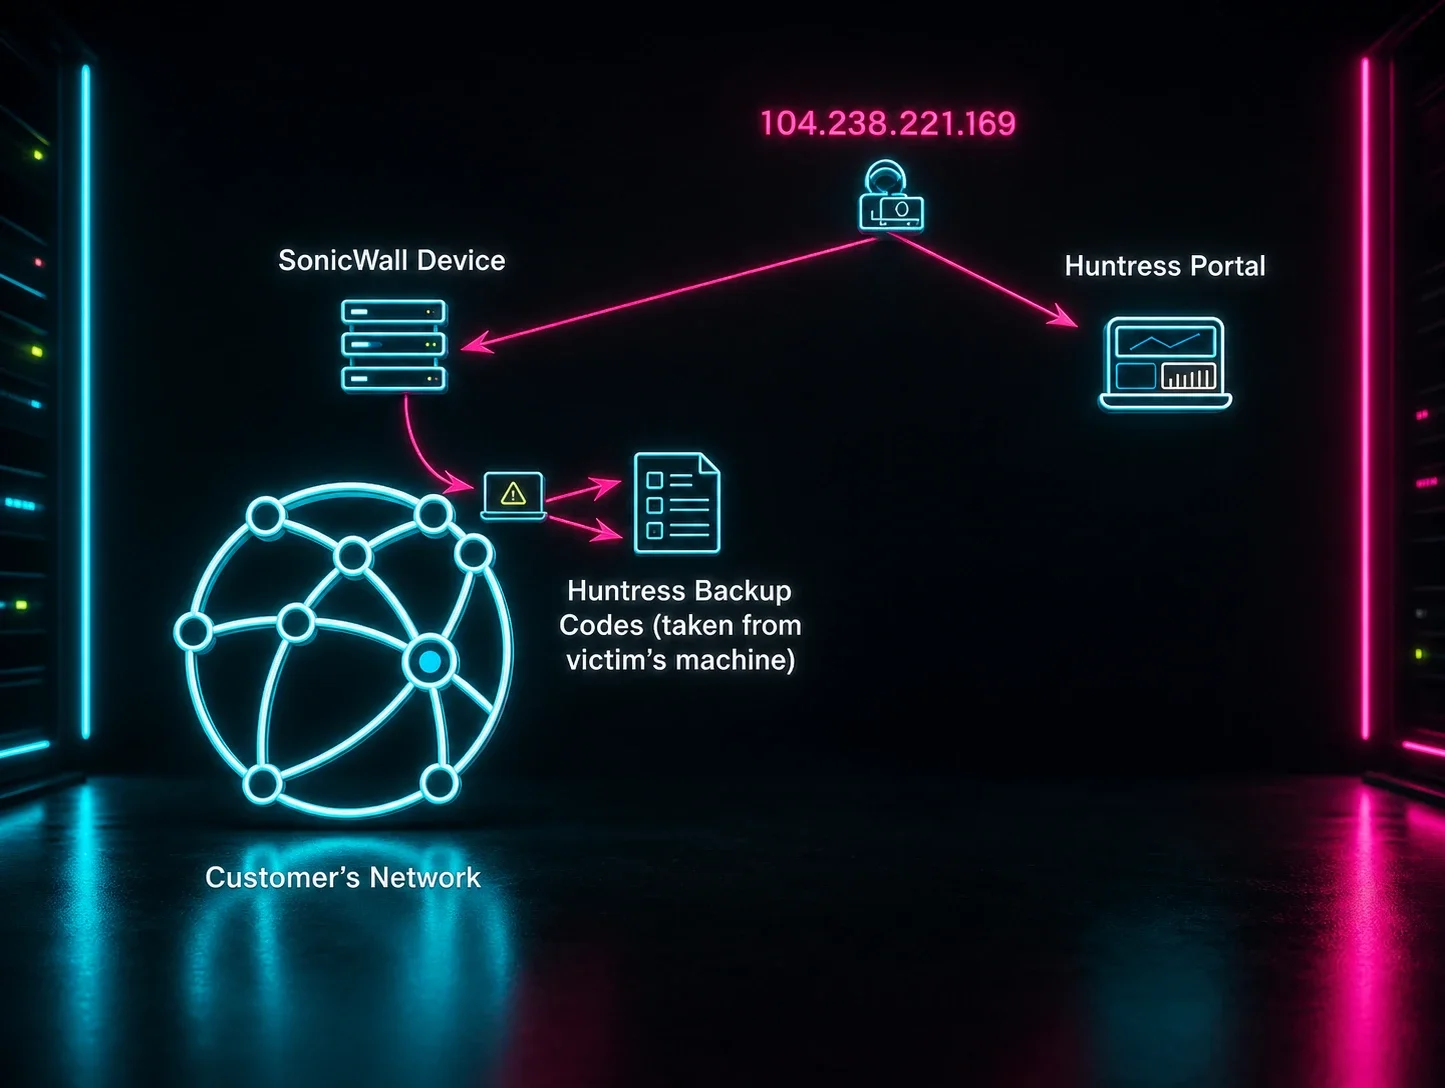
Huntress incident writeup detailing how a threat actor exploited a SonicWall VPN vulnerability to gain initial access, deployed Akira ransomware, and found a plaintext file of Huntress MFA recovery codes on a security engineer's desktop. The attacker used those codes to bypass MFA, log into the victim's Huntress portal from IP 104.238.221.69, close active incident reports, and uninstall EDR agents to blind defenses — while also exporting a certificate via certutil for potential persistence. The piece frames this as a case study for why plaintext password/recovery-code storage is dangerous and recommends hashing (Argon2/bcrypt), salting, and password managers instead.

HuntressSonicWallVPN+2
Akira104.238.221.69

Threat Intel· Added 3 Sep 2026, published 6 Jul 2026

stepsecurity.iowriteup🛡️ Security

15 Malicious JetBrains Plugins Stole AI API Keys from 70,000 Developers

StepSecurity details a coordinated supply chain attack in which 15 fake AI-powered JetBrains plugins (published across 7 vendor accounts from October 2025 to June 2026) exfiltrated developer AI provider API keys in plaintext to a hardcoded Alibaba Cloud C2 server at 39.107.60.51. The plugins genuinely worked (code review, test generation, DeepSeek/OpenAI chat) but their save() methods intercepted valid-looking sk- API keys, disabled TLS certificate validation warnings JVM-wide, and POSTed the keys over unencrypted HTTP; a "donation wall" also resold stolen keys back to other victims. JetBrains banned the accounts and kill-switched the plugins on June 17, 2026, but StepSecurity confirmed the C2 server was still live two days later, and provides code snippets, network IOCs, and remediation/rotation steps.

JetBrainsDeepSeekOpenAI

Supply Chain, Threat Intel· Added 3 Sep 2026, published 1 Jul 2026

huntress.comarticle🛡️ Security

How to Spot a Client in the DoD Industrial Base That Handles CUI

A Huntress blog post (authored by DEFCERT's Ryan Bonner) gives MSPs and MSSPs a concrete methodology for spotting clients that are secretly part of the DoD Industrial Base and subject to DFARS 252.204-7012/-7021, CMMC, and NIST 800-171 obligations. It covers public research signals (USASpending.gov contract lookups, ITAR/DDTC registration, AS9100 certification, Nadcap accreditation, contract vehicles like IDIQ/GWAC/BPA/OTA) and direct screening questions (FAR/DFARS flow-down clauses, DoD distribution-statement-marked technical data, PIEE/SPRS/WAWF account access) to determine whether a company handles Controlled Unclassified Information. It closes with a pitch for Huntress's CMMC Level 2 control coverage.

Huntress
CMMCDFARS 252.204-7012DFARS 252.204-7021+8

GRC· Added 3 Sep 2026, published 25 Jun 2026

academy.8ksec.iocourse🛡️ Security

8kSec AI/LLM Exploitation Labs

8kSec's AI/LLM Exploitation Labs is a set of hands-on CTF-style challenges covering real attack classes against AI systems: prompt-injection to manipulate an LLM essay grader and a workspace assistant into granting admin access, crafting adversarial images to bypass an MNIST-based ML authentication vault, extracting a "secret" encryption key from an n8n/OpenAI chatbot via conversation alone, exploiting a remote MCP server (via Cursor) for path traversal to read /etc/passwd, poisoning a training CSV to backdoor a spam classifier, detecting neural network backdoors in CIFAR-10 models, spotting a malicious MCP skill with a data-exfiltration payload, and identifying "ghost record" membership-inference leakage in a supply-chain-compromised model. Each challenge maps to a distinct AI security technique (prompt injection, adversarial examples, model/data poisoning, MCP tool abuse, membership inference) and offers a free certification on completion.

Model Context ProtocolOpenAICursor

AI Security, Learning· Published and added 21 Jun 2026

snyk.iowriteup🛡️ Security

A Forgotten Contributor Account Compromised the Entire Mastra npm Package Scope

Snyk details how a dormant, never-revoked npm contributor account (ehindero) was used to republish the entire @mastra scope (142+ packages, ~4M monthly downloads for @mastra/core alone) with an injected dependency, easy-day-js, a byte-for-byte dayjs impersonator. The postinstall hook in easy-day-js@1.11.22 disables TLS verification, pulls a second-stage payload from a raw IP, and drops a cross-platform cryptocurrency wallet stealer plus a RAT with OS-specific persistence (LaunchAgent, systemd unit, PowerShell staging) that beacons every 10 minutes over a self-signed wolfSSL certificate. The piece covers detection steps, the Snyk advisory (SNYK-JS-EASYDAYJS-17353313), and draws parallels to the earlier Axios npm compromise attributed by Microsoft to Sapphire Sleet (BlueNoroff).

npmNode.jsSnyk+2
Mastraeasy-day-jsSNYK-JS-EASYDAYJS-17353313+4

Supply Chain, Malware & RE, Blue Team & Detection· Added 3 Sep 2026, published 16 Jun 2026

github.comrepo🛡️ Security

mthcht/awesome-lists

mthcht/awesome-lists is a large, continually updated GitHub collection of threat-hunting IOC lists: suspicious named pipes, Windows services/tasks/firewall rules/ports, user-agents, mutex names, hostnames, MAC addresses, USB IDs, phishing/sinkholed/dyndns domains, HijackLibs, TOR node lists, LOLDrivers hashes, malicious bootloaders and SSL certificates, VPN provider IP ranges, YARA rules, offensive/greyware tool keyword detection patterns, Microsoft Defender/ClamAV signature lists, and RMM detection artifacts. It also links out to DFIR/threat-hunting courses, labs, and CTF-style datasets (SANS FOR500/FOR508, TheDFIRReport labs, Splunk BOTS, Xintra APT emulation) useful for blue teams building detections or hunting.

YARAWindows DefenderClamAV+2
LOLDriversHijackLibs

Blue Team & Detection, Learning· Added 3 Sep 2026, published 10 Jun 2026

Showing 90 of 109

Show more