Skip to content

30 results for โ€œDroidโ€

What you seeeverything
bleepingcomputer.comarticle๐Ÿ›ก๏ธ Security

New Android SMS of Death exploit can remotely crash unpatched phones

CVE-2026-58882, "SMS of Death", is a zero-click Android denial-of-service flaw in WapPushOverSms.decodeWapPdu, where an unchecked header-length value becomes negative and triggers a NegativeArraySizeException that crashes com.android.phone. A malformed eight-byte WAP Push message to port 2948 can drop calls, including emergency calls, and about 20 messages caused reboot loops. A PoC is public. Google patched Android 14 through 17 in October 2026, but Android 12 and 13 remain vulnerable.

AndroidAndroid Debug BridgeGitHub
CVE-2026-58882SMS of DeathGoogle+3

Mobile Security, Offensive Securityยท Published and added 31 Oct 2026

securityweek.comarticle๐Ÿ›ก๏ธ Security

TeamViewer Flaw Could Let Malicious Hosts Take Over Support Techniciansโ€™ Machines

CVE-2026-111585 (CVSS 8.8) is an integer overflow in the remote-control screen processing of TeamViewer clients on Windows, macOS, Linux and Android. A malicious or compromised host can announce an oversized screen surface (for example 32768 by 32768 at 32 bpp), forcing a software decode path and an out-of-bounds write that crashes the viewer or runs code. Remedio's research shows a pointer overwrite routed to WinExec. Version 15.83 fixes it, along with CVE-2026-92372, CVE-2026-92374 and six local privilege escalation bugs.

TeamViewerWindowsmacOS+3
CVE-2026-111585CVE-2026-92372CVE-2026-92374+3

AppSec, Offensive Securityยท Published and added 30 Oct 2026

oversecured.comarticle๐Ÿ›ก๏ธ Security

Android security checklist: theft of arbitrary files | Oversecured Blog

Oversecured's Android security checklist on arbitrary file theft from an app's private storage. It covers implicit intents (PICK, GET_CONTENT) returning file:// or content:// URIs, SEND/SEND_MULTIPLE share activities, exported and non-exported FileProviders, path traversal via Uri.getLastPathSegment, WebView, and local NanoHTTPD servers. Each case has vulnerable code, an attacker PoC and fixes such as /proc/self/fd path checks and narrow files-path entries.

AndroidNanoHTTPDFileProvider+2
Oversecuredpath traversalFileUriExposedException+3

Mobile Security, AppSecยท Added 29 Oct 2026

oversecured.comarticle๐Ÿ›ก๏ธ Security

Content Providers and the potential weak spots they can have | Oversecured Blog

Oversecured's Android security checklist for Content Providers covers insecure FileProvider path configs, path traversal via decoded Uri.getLastPathSegment(), mismatched readPermission/writePermission, proxying requests to more privileged providers, SQL injection across a shared database, and sensitive actions in providers. Each case has vulnerable manifest and Java code, an attacker PoC and remediation. Real cases from Google and Samsung devices are cited. The page text was truncated near the end.

AndroidSQLiteJava
Oversecuredpath traversalSQL injection+5

Mobile Security, AppSecยท Added 29 Oct 2026

oversecured.comarticle๐Ÿ›ก๏ธ Security

Oversecured Apps Care. Part 1: Vulnerability disclosure of 225 Google apps | Oversecured Blog

Oversecured Apps Care, Part 1 (21 March 2024) publishes scanner results for about 224 Google Android apps, drawn from a wider scan of over 6,000 public APKs from 1,000+ companies. Tables per device image (phone, Wear OS, Android Automotive, Android TV) give package names, three finding counts and report links, including android, com.android.settings, gms and Play Store. It invites researchers to report issues to Google for rewards.

AndroidWear OSAndroid Automotive+1
OversecuredOversecured Apps Care

Mobile Security, AppSecยท Added 29 Oct 2026
oversecured.comarticle๐Ÿ›ก๏ธ Security

Inside mobile taint analysis: how source-to-sink tracking finds real data-leak paths | Oversecured Blog

Oversecured explains taint analysis for Android and iOS apps and contrasts it with pattern-matching SAST such as MobSF. It covers source, flow and sink, cross-component tracking over Intents, flag-based sanitizer modeling and implicit intent simulation. The case study is an unsafe Class.forName().newInstance() on a Serializable transportFactoryClassName field in Google's com.google.auth.oauth2 credential classes, which Google fixed with a $3,133.70 bounty.

AndroidiOSOversecured+3
intent redirectionpath traversalSSRF+4

Mobile Security, AppSecยท Added 29 Oct 2026

oversecured.comarticle๐Ÿ›ก๏ธ Security

Android deep link vulnerabilities: how intent filters lead to account takeover | Oversecured Blog

Oversecured's article on Android deep-link vulnerabilities covers five patterns: custom scheme hijacking, open redirect into WebView, limited and full intent redirection, and domain takeover via an expired whitelist entry. It shows bypass payloads, intent selector abuse, and the HierarchicalUri reflection bypass. It also compares what SAST and DAST can find and gives a checklist for pentesters.

AndroidOAuthChrome+1
deep link hijackingcustom scheme hijackingopen redirect+8

Mobile Security, AppSecยท Added 29 Oct 2026
oversecured.comarticle๐Ÿ›ก๏ธ Security

PCI DSS and Mobile Apps: A Simple Guide | Oversecured Blog

Guide to PCI DSS v4.0.1 scope for mobile apps, with a mapping of common Android and iOS finding types to the requirements they break (Req 2, 3, 4, 6, 7). It covers which app behaviors bring an app into scope and gives three anonymized cases: cleartext HTTP in a vendor native library, hardcoded keys in a third-party SDK, and an implicit Intent leaking data. It argues for testing the shipped binary and keeping a current component inventory.

AndroidiOS
PCI DSSPCI Security Standards CouncilQualified Security Assessor+5

Mobile Security, GRCยท Added 29 Oct 2026

securityweek.comarticle๐Ÿ›ก๏ธ Security

Dead Popcorn Time Updater Put Millions of Computers at Risk of Takeover

Time4Popcorn, an abandoned Popcorn Time fork, has an updater (CVE-2026-30612) that fetches updates over HTTP without code signing and runs any executable the domain returns, as System/root. Eye Security registered abandoned update domains, saw millions of Windows, macOS and Android clients, and pushed a fix disabling the updater on about 2 million systems by March 2026. Shadowserver took over the sinkholed domains; Eye Security advises uninstalling the app.

Popcorn TimeWindowsmacOS+2
CVE-2026-30612Eye SecurityShadowserver Foundation+2

Threat Intel, AppSecยท Published and added 27 Oct 2026

decrypt.coarticle๐Ÿง  AI

Google Quietly Updates Privacy Policy to Let Gmail and Photos Data Feed Ads

Google revised its privacy policy, effective 16 October 2026, so that content from Gmail, Drive and Google Photos can personalize ads if users connect it to other Google services, which includes Personal Intelligence in AI Mode and Gemini. The setting is off by default, advertisers do not see the underlying content, and users can opt out under Connected Content apps in Data & privacy settings. Android Authority first spotted the change, and previously collected data may remain in Search history.

GeminiGmailGoogle Photos+1
GoogleDecryptAndroid Authority

ai-policyยท Published and added 24 Oct 2026

decrypt.coarticle๐Ÿง  AI

People Are Vibe Coding the Ads Out of Their Smart TVs: Here's How

Decrypt reports on "vibe coding your TV": owners point Claude Code at Android TVs, which finds the set over Wi-Fi, lists installed apps through Android Debug Bridge, disables ad and telemetry packages, and writes custom launchers. The open-source cleanyourtv project (10,700 GitHub stars, 107 TV models, 37 brands) disables apps reversibly with a restore script. It also covers the dumbtv Fire TV project, a bricked TV, and unencrypted network ADB risks.

Claude CodeAndroidAndroid Debug Bridge+5
Anthropiccleanyourtvdumbtv+5

coding-agentsยท Published and added 20 Oct 2026

en.cryptonomist.charticle๐Ÿ›ก๏ธ Security

Ledgerโ€™s Atom device adds tamper detection after a recovery-phrase breach

News report on a Southeast Asia supply-chain breach in which Ledger devices sold via resellers such as CryptoBilis were modified with hidden chips. The chips read 24-word recovery phrases from the screen signals during setup and sent them out over LTE. Tether froze $10M USDT tied to the theft, and Ledger suspended sales in several Asian markets. It also covers Ledger's Android-based Atom signer, which adds a protective enclosure, screen and back-cover removal sensors with their own battery, tamper-evident packaging, and website-only initial sales.

LedgerAndroid
CryptoBilisTether

Hardware & RF, Blockchainยท Published and added 15 Oct 2026

securityweek.comarticle๐Ÿ›ก๏ธ Security

Novel Android RAT โ€˜Hirudoโ€™ Replaces Banking Apps With Trojanized Copies

SecurityWeek covers ThreatFabric's findings on Hirudo, an Android banking trojan/RAT delivered via droppers hidden in fake shopping, adult video and short drama apps. It replaces eight Indonesian banking apps with modified copies containing a hooking engine that spoofs signing certificates and hides Accessibility services, screen capture and Play Integrity checks, while providing WebRTC screen viewing, camera access and SMS theft. ThreatFabric advises banks to enforce Play Integrity server-side, use behavioral analytics, treat Accessibility signals as risk inputs, and keep backend transaction-risk controls.

Android
HirudoThreatFabricPlay Integrity+2

Mobile Security, Threat Intel, Malware & REยท Published and added 15 Oct 2026

hackers-arise.comarticle๐Ÿ›ก๏ธ Security

SDR (Signals Intelligence) for Hackers: Scanning Wireless Devices Using FieldWatch

Overview of FieldWatch, a free open-source Android app that passively listens to Wi-Fi and Bluetooth with the phone's own radios and matches them against an editable catalog of about 250 device signatures (trackers, drones, cameras, body cams, mesh radios). It supports alerts, recorded sessions, path maps, Remote ID drone and pilot location, GNSS interference/spoofing detection and export to TAK/ATAK. The article also covers its limits (no direction finding, no Bluetooth Classic, cellular or full Wi-Fi traffic, pattern matches only) and sideloading from the official GitHub repo on Android 10+.

FieldWatchAndroidTAK+1
Remote IDGNSS interferenceGPS spoofing+2

Hardware & RF, Mobile Securityยท Published and added 13 Oct 2026

securityweek.comarticle๐Ÿ›ก๏ธ Security

Small AI Models May Soon Be Able to Self-Replicate on IoT Devices, Anthropic Warns

SecurityWeek summarizes Anthropic Frontier Red Team research on AI worms that run small open-weight models directly on compromised IoT devices. A 26B model split across 15 ~$55 Android TV boxes ran at 0.39 tokens/s; a 9B model got inference running on 8 of 9 hardware types, and only GLM-5.2 completed full replication across eight emulated Android devices (4 of 5 runs). Anthropic projects โ‰ค30B models reaching that level by end of 2026, estimates a Kimwolf-sized botnet would host ~133,000 copies worth at most ~40 H100s, and notes defenders can spot large model transfers in ISP traffic and cut the target pool by removing default passwords.

AndroidGLMLLM+1
Anthropic Frontier Red TeamKimwolfMirai+2

AI Security, Hardware & RFยท Published and added 13 Oct 2026

securityweek.comarticle๐Ÿง  AI

Small AI Models May Soon Be Able to Self-Replicate on IoT Devices, Anthropic Warns

SecurityWeek summarizes Anthropic Frontier Red Team research on AI worms that carry their own open-weight model onto compromised IoT devices. A 26B model sharded across 15 cheap Android TV boxes ran at 0.39 tokens/s. A 9B model got inference running on 8 of 9 hardware types. In a closed network of 8 emulated Android devices, only GLM-5.2 completed the full replication cycle, reaching all 8 devices in 4 of 5 runs. Models of 30B or fewer parameters handle individual steps but fail when chaining them. Anthropic projects they reach GLM-5.2's level by end of 2026, and estimates a Kimwolf-sized botnet would offer at most about 40 H100s of compute. Defenders can detect large model transfers and sustained unusual device-to-device traffic, and removing default passwords shrinks the target pool.

GLMAndroidNVIDIA H100
AnthropicFrontier Red TeamGLM-5.2+4

ai-safety, inference, evalsยท Published and added 13 Oct 2026

en.cryptonomist.charticle๐Ÿง  AI

Anthropic tests AI autonomous replication across eight nodes in four of five trials

The article reports Anthropic research (William Zhou and Daniel Freeman) on whether small open models can autonomously replicate onto unfamiliar IoT and consumer hardware. Qwen3.5-9B established inference on eight of nine hardware types using the Memento harness (built on the Pi coding agent). GLM-5.2 completed a simplified end-to-end replication across eight emulated Android nodes in four of five trials, and reached seven nodes in the fifth. Gemma4-26B-A4B was sharded by pipeline parallelism across 15 low-RAM Android TV boxes at 0.39 tokens/s. The authors estimate replication intervals of 1โ€“2 days and a capability threshold around end of 2026, which makes it a concrete capability-evaluation datapoint for AI safety.

PiQwen3.5GLM+6
AnthropicWilliam ZhouDaniel Freeman+7

ai-safety, evals, agentsยท Published and added 12 Oct 2026

en.cryptonomist.charticle๐Ÿ›ก๏ธ Security

Anthropic tests AI autonomous replication across eight nodes in four of five trials

News write-up of an Anthropic research post (William Zhou, Daniel Freeman) testing whether small open-weight models can act as autonomous worms. Qwen3.5-9B established inference on eight of nine hardware types, and GLM-5.2 spread across eight emulated Android nodes via unauthenticated ADB in four of five trials, reaching seven nodes in the fifth. The piece covers sharding a Gemma4-26B-A4B model across 15 low-memory Android TV boxes, projected spread rates, comparison with the Kimwolf botnet, and network signals defenders could watch (large weight transfers, inter-device inference traffic, scanning).

AnthropicAndroidQwen+2
GLM-5.2KimwolfMemento+5

AI Security, Hardware & RFยท Published and added 12 Oct 2026

securityweek.comarticle๐Ÿ›ก๏ธ Security

Pre-Baked Firmware Malware Hits Budget Android Devices in 150+ Countries

SecurityWeek reports on Bitdefender's analysis of 'Midnight Mimosa,' a firmware-level malware campaign preinstalled on budget MediaTek-based Android devices across 150+ countries, giving attackers system-level privileges to silently install/remove apps and run ad fraud and click fraud botnets. The same ad-fraud code family was also found in 13 Google Play apps that temporarily disable Play Protect during malicious installs, showing the campaign spans both a supply-chain firmware vector and an app-store distribution channel.

AndroidMediaTekGoogle Play
Midnight MimosaBitdefender

Mobile Security, Supply Chain, Threat Intelยท Published and added 9 Oct 2026

securityweek.comarticle๐Ÿ›ก๏ธ Security

Androidโ€™s October 2026 Updates Patch 25 Vulnerabilities

SecurityWeek summarizes Google's October 2026 Android Security Bulletin (2026-10-01 patch level), which fixes 25 vulnerabilities โ€” 7 in Framework and 18 in System, including 7 critical bugs. The most severe is a critical local privilege-escalation flaw in System requiring no user interaction or extra execution privileges; the bulletin also covers a System RCE bug, Google Play system updates for Telephonycore/WiFi, and separate Pixel and Android Automotive OS fixes (including critical Bluetooth, GDMC, and GSA issues). Google reports no evidence of in-the-wild exploitation.

Android

Mobile Securityยท Published and added 7 Oct 2026

decrypt.coarticle๐Ÿ›ก๏ธ Security

Someone Scraped 5.6 Billion TikTok Videos and Put the Data on Hugging Face for Free

Decrypt reports that a developer going by "hashfunction," operating under the datasocial account, published a 460GB Parquet dataset of metadata for ~5.6 billion public TikTok videos (captions, hashtags, sound IDs, engagement counts, AI-generated flags) on Hugging Face under CC BY-NC 4.0. The data was obtained by hitting TikTok's private mobile API using generated Android device identities, reverse-engineered request signatures, and a spoofed TLS handshake, bypassing the ToS clause that bars automated scraping; datasocial.ai sells the scraper's source code for $1,699 and offers commercial access, creator profiles, and daily updates. The piece situates this against TikTok's gated official Research Tools and the ongoing Reddit v. Perplexity/SerpApi scraping lawsuit.

TikTokHugging FaceAndroid+1
hashfunctiondatasocial.aiReddit+4

Offensive Securityยท Published and added 6 Oct 2026

blog.jetbrains.comarticle๐Ÿง  AI

Introducing the Kotlin Benchmark for AI coding agents (JetBrains)

JetBrains introduces the Kotlin Benchmark, a SWE-bench-style evaluation suite of 105 repository-level engineering tasks drawn from real open-source Kotlin projects, where agents must read an issue, navigate a codebase, and produce a patch verified by containerized test execution. Built on the open-source Multi-SWE-bench infrastructure, it ships with a public leaderboard and GitHub assets; the first results rank Claude Code with Claude Opus 4.7 (85.71% resolved) ahead of JetBrains Junie with Opus 4.7 and Codex with GPT-5.5, both at 81.9%. JetBrains positions it as complementary to model-level Kotlin evals like Kotlin_HumanEval and Kotlin_QA, and plans to expand coverage to Android/Kotlin Multiplatform tasks and additional metrics beyond pass/fail.

KotlinClaude CodeCodex+1
JetBrainsKotlin BenchmarkClaude Opus 4.7+6

evals, coding-agentsยท Added 4 Oct 2026

github.blogarticle๐Ÿง  AI

How we found 24 Android vulnerabilities using our open source AI security agent

GitHub Security Lab describes the architecture behind its open-source "Taskflow Agent," a set of YAML-defined prompt workflows (e.g. gather_mobile_entry_point_info.yaml, classify_application_local.yaml) that guide an LLM through structured, multi-step code audits rather than a single free-form prompt. Using these taskflows on Android apps via GitHub Copilot, the team found 24 vulnerabilities, including a location-tracking bug in OsmAnd via exported-activity intent extras and a cookie-leaking account-takeover chain in the Wikipedia app via a deeplink hostname-parsing flaw. The post's more durable contribution is its analysis of LLM auditing behavior: strong at recognizing API-level unsafe patterns and generating working PoCs, but unreliable at severity estimation and prone to false positives from mitigating factors the model doesn't account for, requiring human review and repeated/guided runs.

GitHub CopilotSQLiteYAML
GitHub Security LabOsmAndWikipedia

coding-agents, agents, promptingยท Added 8 Oct 2026, published 28 Sep 2026

thehackernews.comarticle๐Ÿ›ก๏ธ Security

OnePlus/OPPO root privilege-escalation chain (AtlasService + olc2)

Researcher Rasmus Moorats disclosed a two-stage local privilege-escalation chain on OnePlus/OPPO Android phones: OnePlus's AtlasService debugging component runs as root and passes unvalidated app input into a system command, granting root but confined to a restricted dumpstate zone; a second flaw in the olc2 hardware-helper service accepts arbitrary shell commands from any root caller, escaping the sandbox to full root with kernel-module-loading privileges. A malicious app requiring zero permissions and showing no prompts can chain both bugs on a stock OnePlus 15 or 12 Pro, and OnePlus said the same flaws affect many other OnePlus and OPPO devices sharing OxygenOS. OnePlus confirmed the bugs in May 2026 but had shipped no fix or CVE by publication (Sept 24), and separately told the researcher it claims sole authority over disclosure timing and threatened legal liability for publishing without consent โ€” a stance he rejected before going public.

Android
Rasmus MooratsAtlasServiceolc2+4

Mobile Security, Offensive Securityยท Added 26 Sep 2026

blog.talosintelligence.comarticle๐Ÿ›ก๏ธ Security

Should you care about an โ€œAI slowdown?โ€

Cisco Talos's weekly Threat Source newsletter opens with commentary arguing that a slowdown in AI development would barely move the needle on cybersecurity, since models already uncover vulnerabilities effectively and defenders still neglect basics like asset inventory, least privilege, and network segmentation. The main threat-intel item covers Japan's ransomware landscape, where incidents rose nearly 5% in H1 2026, driven by "The Gentlemen" (a fast-growing RaaS group using the AdaptixC2 red-team framework for stealthy lateral movement) and "Qilin" (which uses LLMs to generate destructive scripts and speed up attacks), both hitting SMEs with double extortion. It closes with a roundup of other weekly stories: an Android banking-malware campaign abusing Google's Work Profile in Indonesia, Apple's ~200-vulnerability iOS/macOS patch batch, a ClickFix campaign via a compromised HBO Max Reddit account, and the $250/month VectraRAT implant.

AdaptixC2SnortVPN
The GentlemenQilinVectraRAT+2

Threat Intel, AI Securityยท Added 7 Oct 2026, published 17 Sep 2026

developers.googleblog.comarticle๐Ÿง  AI

Announcing ADK for Kotlin 1.0: Building Production-Ready AI Agents in Kotlin, Android, and Beyond

Google announces ADK (Agent Development Kit) for Kotlin 1.0, reaching feature parity with ADK Python/Java and adding Android-first extensions: on-device inference via LiteRT-LM and ML Kit, Firebase AI Logic for hybrid cloud, and persistence through Room and AppSearch. It uses Kotlin Symbol Processing (KSP) to generate type-safe function-calling schemas at compile time from @Tool/@Param annotated methods, and introduces a SkillToolset for progressive-disclosure SOPs (SKILL.md files) plus human-in-the-loop confirmation for sensitive tool calls like bank transfers.

KotlinKotlin MultiplatformKSP+2
GoogleADK for KotlinFirebase AI Logic+4

agents, mcpยท Added 26 Sep 2026, published 9 Sep 2026

deepmind.googlearticle๐Ÿง  AI

Putting sign language AI into usersรขย€ย™ hands

Google DeepMind and Android introduce SL2T, a massively multilingual sign-language-to-text translation model trained on over 100,000 hours of data across 50+ sign languages, now powering ASL-to-English sign dictation in Gboard and Live Transcribe on Pixel 11. Instead of relying on intermediate "gloss" annotations, SL2T translates directly from pose-landmark coordinate sequences (tracked on-device via MediaPipe Holistic for privacy) into text, achieving a zero-shot 70 BLEURT score on the FLEURS-ASL benchmark, reportedly well above prior reported results.

MediaPipe HolisticGboardLive Transcribe+1
Google DeepMindAndroidSL2T+6

multimodalยท Added 29 Sep 2026, published 12 Aug 2026

endorlabs.comarticle๐Ÿง  AI

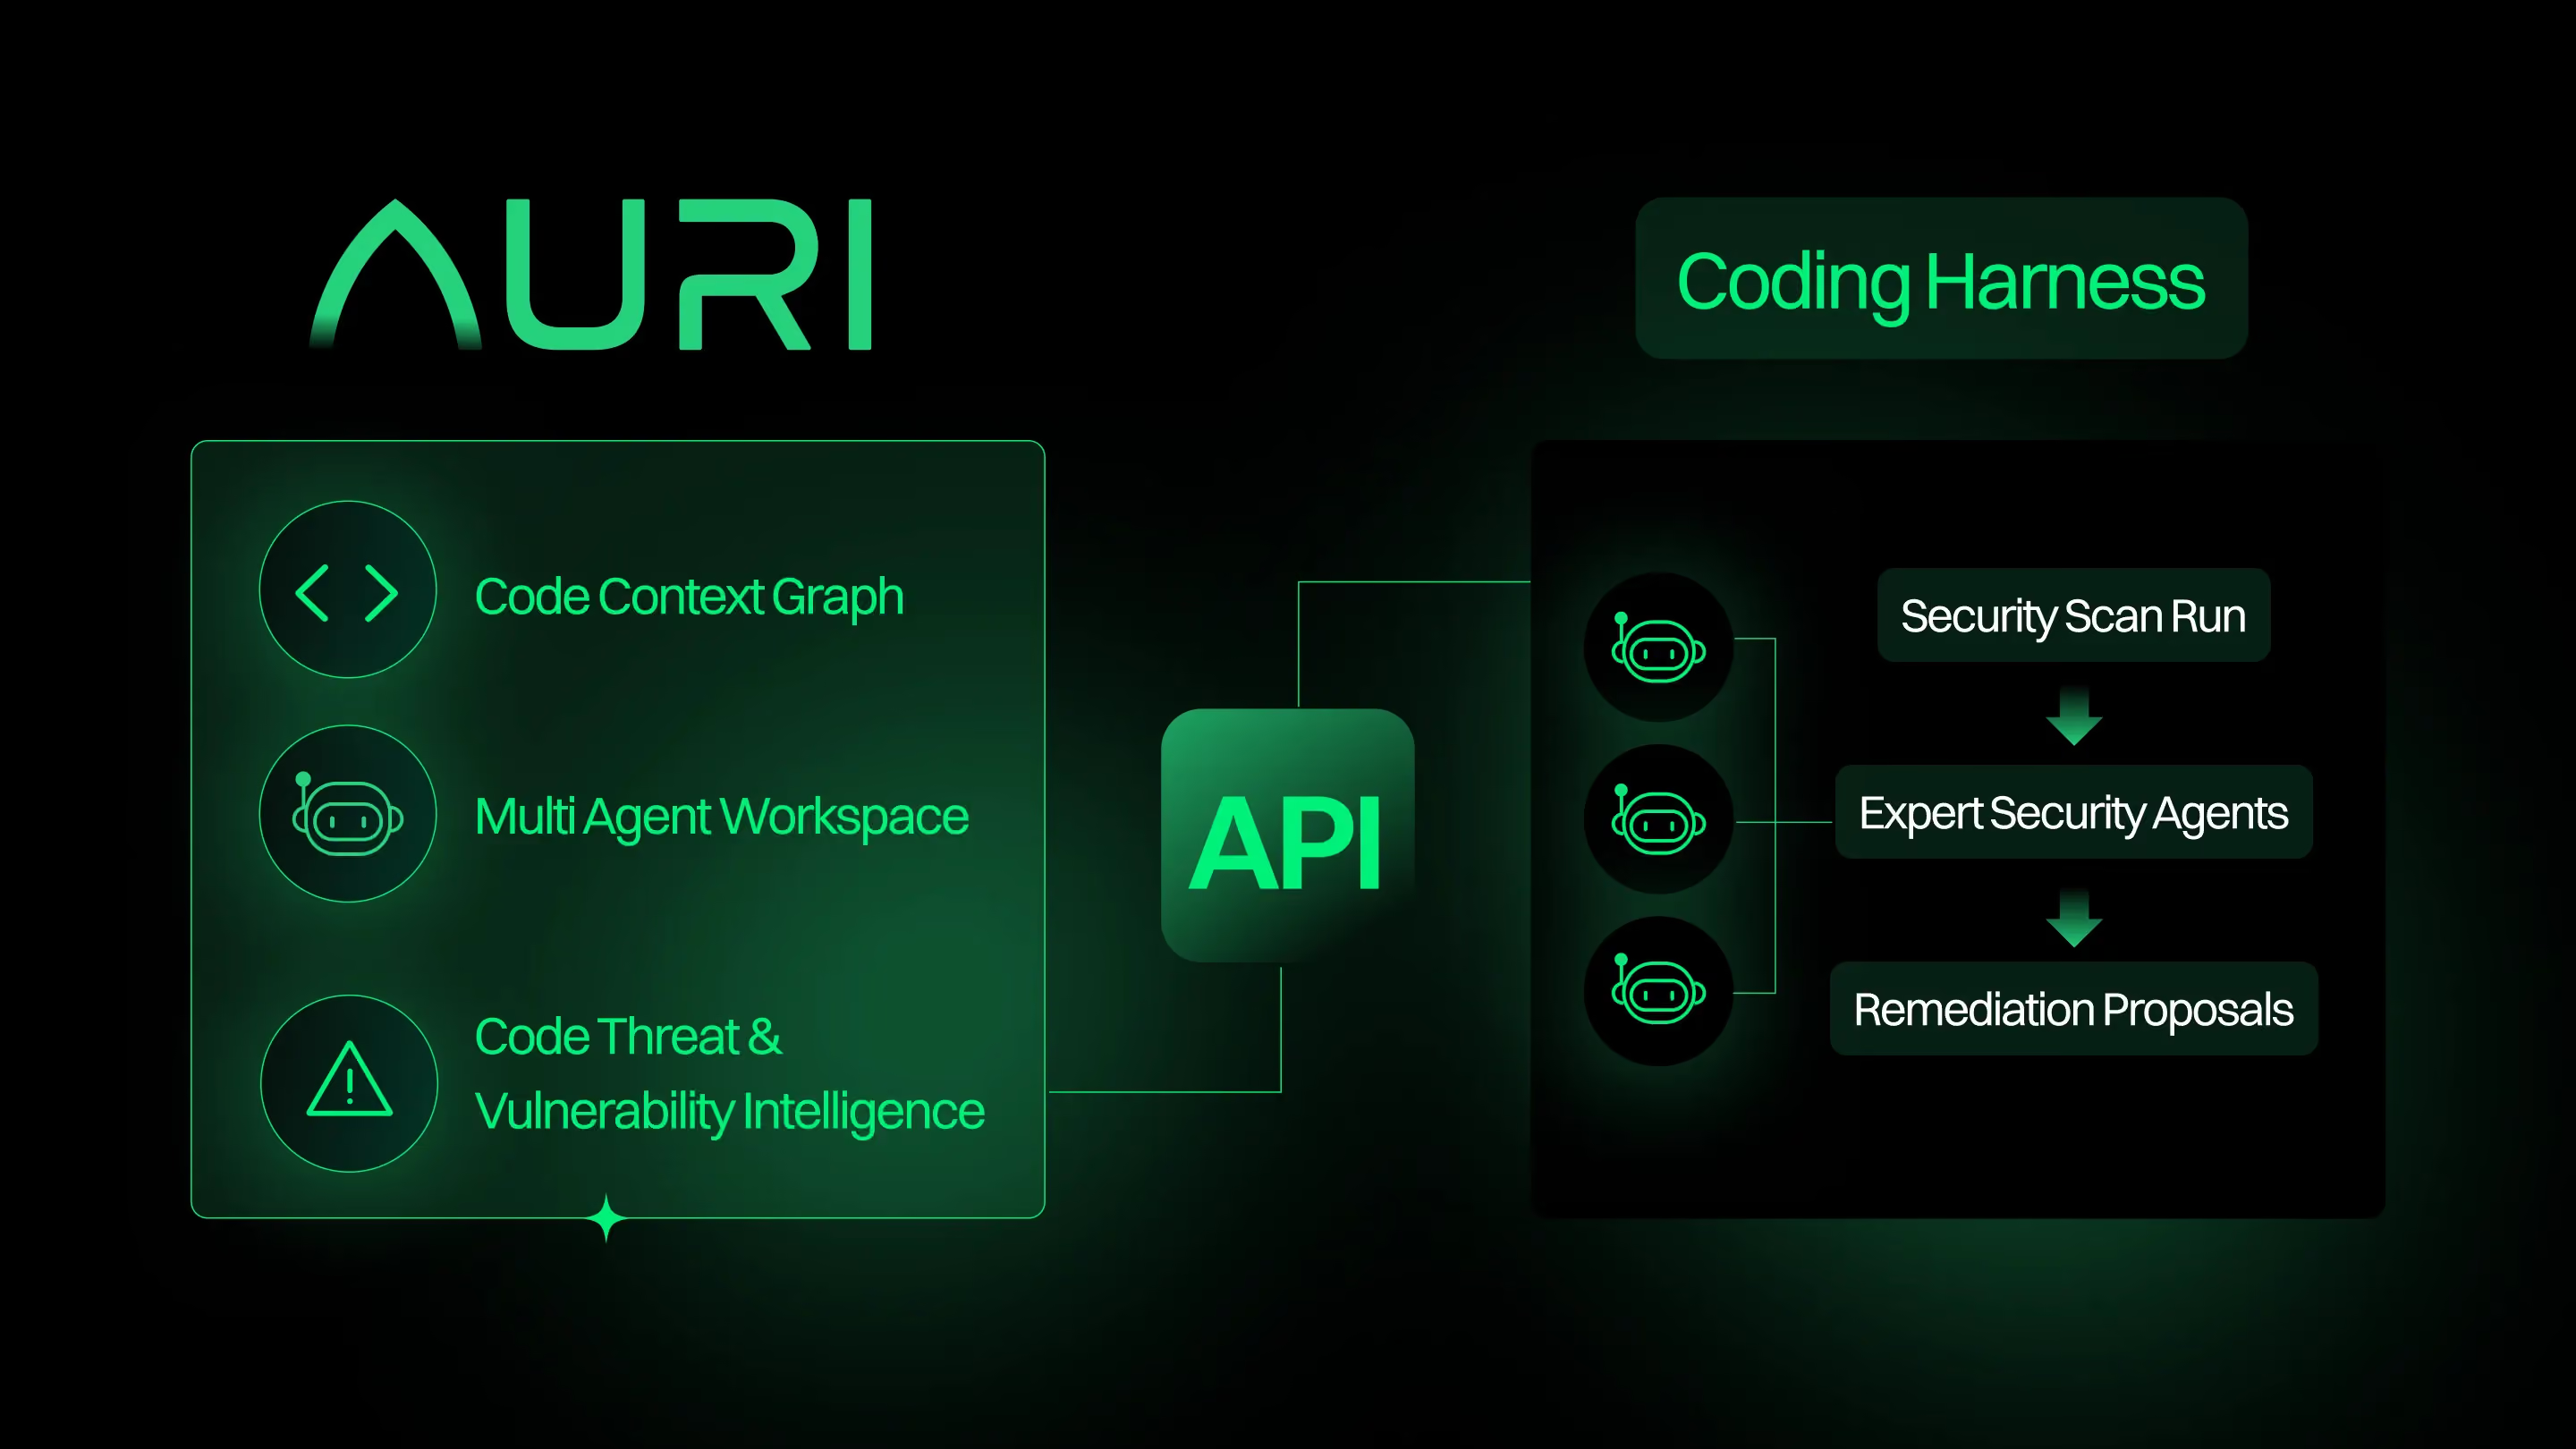
Endor Labs: AURI Agents

Endor Labs announces AURI Agents, a free catalog of pre-configured security agents (SCA Remediation, AI SAST Triage, Probe Droid, Endor Troubleshooter and six more). They run inside Claude Code, Codex, Cursor and similar hosts, using the user's own LLM keys and git credentials (GitHub via gh, GitLab via glab). The open-source Endor Labs Agent Kit defines each agent as a YAML Source Recipe plus markdown instructions, compiles it into per-host artifacts, and ships a skill that helps users author new agents with eval cases. Endor claims expert agents finish tasks 2.8x faster with 92% fewer tokens than an unaugmented agent. Mutating actions require confirmation and most agents are read-only.

Claude CodeCodexCursor+6
Endor LabsGitLab

coding-agents, agentsยท Added 10 Oct 2026, published 17 Jun 2026

endorlabs.comarticle๐Ÿ›ก๏ธ Security

Endor Labs: AURI Agents

Endor Labs announces AURI Agents, twelve pre-configured AI agents (SCA Remediation, AI SAST Triage, Probe Droid, Endor Troubleshooter and others) that use Endor's reachability, upgrade-impact and policy data. They install into Claude Code, Codex, Cursor and similar hosts, and run on the customer's own LLM keys and git credentials (GitHub via gh, GitLab via glab). The open-source Endor Labs Agent Kit defines each agent as a YAML Source Recipe plus markdown instructions, compiled for each host, with a skill for authoring new agents. Most agents are read-only by default, and the ones that mutate state declare their permissions and require confirmation.

Endor LabsAURIClaude Code+3
AURI AgentsEndor Labs Agent KitProbe Droid+1

AI Security, AppSec, Supply Chainยท Published and added 17 Jun 2026

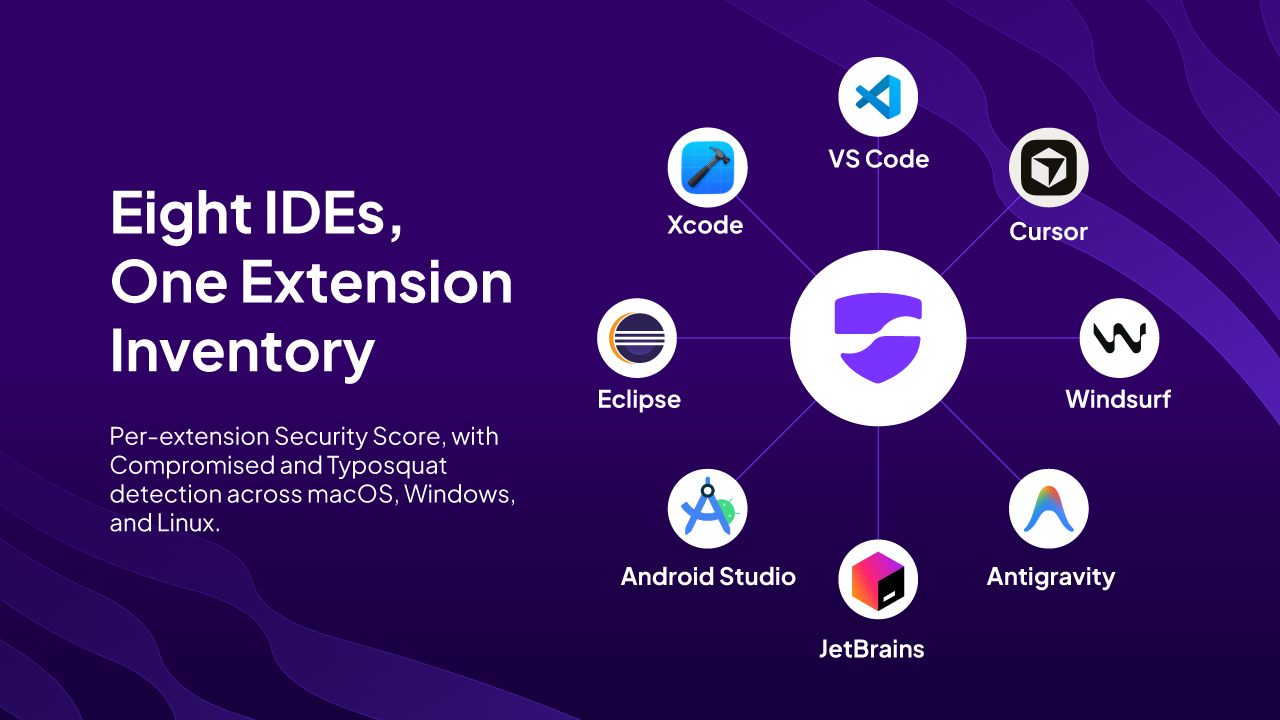
stepsecurity.ioarticle๐Ÿ›ก๏ธ Security

Dev Machine Guard Now Scans Extensions Across Every Modern IDE

StepSecurity's Dev Machine Guard now inventories and scores IDE extensions/plugins across eight IDE families (VS Code, Cursor, Windsurf, Antigravity, JetBrains IDEs, Android Studio, Eclipse-based IDEs, Xcode) on macOS, Windows, and Linux, not just VS Code. It computes a supply-chain Security Score per extension (adoption, publisher verification, license, known vulnerabilities, repo security posture) and flags known-compromised or typosquatted extensions, motivated by incidents like the October 2025 VS Code publisher token leaks, the s1ngularity Nx compromise, and the Shai-Hulud npm worm reaching extensions via transitive dependencies. The scanning engine is open source; enterprise mode feeds a fleet-wide dashboard for incident response and typosquat/compromise hunting.

VS CodeCursorWindsurf+2
Shai-Huluds1ngularityCISA

Supply Chain, DevSecOpsยท Added 3 Sep 2026, published 2 Jun 2026