Skip to content

223 results for β€œIntel”

What you seeeverything
x.comarticle🧠 AI

Lewis - Policifyai (@Policifyai) on X

Policifyai's October 2026 roundup lists model releases by date with prices and benchmark scores: GPT-6.1 Sol and Terra, Claude Sonnet 5.5 and Haiku 5.5, Gemini 4 Argon and Carbon, Muse Spark Open, Mistral Large 4 weights and Kimi K3.1 Pro. It also covers Anthropic's S-1 compute commitments, Artificial Analysis Intelligence Index v5, and chip and data-center deals.

CodexHugging FaceMixture of Experts+6
OpenAIAnthropicGoogle+43

models, ai-infra, evalsΒ· Added 1 Nov 2026, published 31 Oct 2026

x.comthreadπŸ›‘οΈ Security

Dark Web Intelligence (@DailyDarkWeb) on X

CVE-2026-102764 is an unauthenticated RCE in BeyondTrust Remote Support, already exploited and in CISA KEV. Rapid7 published an analysis and opened a Metasploit pull request on 30 October 2026, showing code execution on version 24.1.2 via a forged "local" message origin, the native file-transfer service and a PHP file written to the web root. BT26-05 (CVSS 4.0 9.3) is fixed by patch BT26-05-RS; SaaS was patched by 9 October.

BeyondTrust Remote SupportMetasploitPHP+1
CVE-2026-102764CISA KEVRapid7+2

Offensive Security, Threat Intel, AppSecΒ· Added 1 Nov 2026, published 31 Oct 2026

microsoft.comwriteupπŸ›‘οΈ Security

Inside a malicious Claude Code-branded extension and its persistent SSH backdoor

Microsoft Threat Intelligence analyzes a tampered anthropic.claude-code extension (versions 2.1.312 and 2.1.313) served on the Cursor marketplace on 29 October 2026. The injected JavaScript loader adds an SSH key labeled svc-telemetry, opens a reverse SSH tunnel and sets up persistence on macOS, Linux and Windows. The post gives cleanup steps, IOCs and Defender XDR hunting queries. VS Code Marketplace and npm were not affected.

CursorClaude CodeSSH+3
Protocol Tunneling (T1572)reverse SSH tunnelMicrosoft Threat Intelligence+2

Supply Chain, Blue Team & Detection, Malware & REΒ· Published and added 31 Oct 2026

microsoft.comwriteupπŸ›‘οΈ Security

From help desk impersonation to AD CS abuse: Investigating ESC1 and ESC8 intrusion paths

Microsoft Threat Intelligence analysis of two human-operated intrusions that began with Teams help desk impersonation and Quick Assist sessions, then diverged at AD CS. Case 1 abused an ESC1 template for privileged certificates and DCSync, with an excluded account later used for Rclone exfiltration. Case 2 used PetitPotam and ESC8 relay to get a domain controller certificate and PKINIT. Includes investigation steps, AD CS hardening and KQL hunting queries.

Active Directory Certificate ServicesMicrosoft TeamsQuick Assist+3
ESC1ESC8PetitPotam+12

Blue Team & Detection, Threat Intel, Offensive SecurityΒ· Published and added 30 Oct 2026

x.comthread🧠 AI

Artificial Analysis (@ArtificialAnlys) on X

Artificial Analysis launched an HLE-Diamond leaderboard in v5 of its Intelligence Index, covering the refined 1,000-question Humanity's Last Exam from CAIS and Scale AI. Each question runs once without tools, graded by GPT-5.6 Luna (medium) as pass@1. Gemini 4 Carbon (high) leads at 69%, Claude Opus 5.5 (max) scores 68%, and the top open weights model, Kimi K3.1 Pro, reaches 37%.

Artificial AnalysisArtificial Analysis Intelligence IndexHLE+9

evals, modelsΒ· Published and added 30 Oct 2026

en.cryptonomist.charticleπŸ›‘οΈ Security

Polymarket stolen funds: One account withdrew at least $2.7M across 710 wallets

Polymarket's international exchange suffered unauthorized withdrawals on 29 October 2026 after a compromised third-party provider, reportedly the website monitoring service DebugBear. Betting Intelligence and Polysights found one account withdrew at least $2.7 million across 710 wallets. Polymarket paused trading, referred the case to law enforcement, promised reimbursement, and had a June 2026 vendor breach that cost about $3 million. The attack mechanism is not described.

Polygon
PolymarketDebugBearBetting Intelligence+2

Supply Chain, Threat IntelΒ· Published and added 29 Oct 2026

vulncheck.comtoolπŸ›‘οΈ Security

VulnCheck - Outpace Adversaries

VulnCheck Open Source is an index of VulnCheck's open-source tooling for its vulnerability and exploit intelligence. It lists a Python API client, a CLI, a GitHub Action for CI/CD, go-exploit (a Go exploit framework), an MCP server for delivering intelligence to AI clients, and VulnCheck Insights, a Chrome extension that highlights CVEs, CPEs and PURLs on web pages and enriches them. The page gives only one-line descriptions.

GoPythonGitHub Actions+2
VulnCheckgo-exploitVulnCheck Insights+2

Offensive Security, DevSecOpsΒ· Added 29 Oct 2026

microsoft.comarticleπŸ›‘οΈ Security

Tracking AI adoption in North Korean threat actor tradecraft

Microsoft Threat Intelligence report on how North Korean actors use AI, ranking Jade Sleet, Coral Sleet and Jasper Sleet as operationalized, Diamond Sleet, Onyx Sleet, Pearl Sleet and Sapphire Sleet as accelerating, and Emerald Sleet as expanding. It documents AI-generated lures (100+ Onyx Sleet PDFs, August and September 2026), AI-built tooling such as Coral Sleet's private GitHub repository trojanizing, and Onyx Sleet and Pearl Sleet use of the ARTEX agentic pentest framework. It ends with mitigation and Defender guidance.

CursorGitHubRust+2
Jade SleetOnyx SleetCoral Sleet+9

Threat Intel, AI SecurityΒ· Published and added 29 Oct 2026

artificialanalysis.aiarticle🧠 AI

Gemini 4 Carbon is the new #1 on the Artificial Analysis Intelligence Index v5

Gemini 4 Carbon scores 59 on Artificial Analysis Intelligence Index v5 (published 28 October 2026), the top score, with #1 on 4 of 9 evaluations including HLE-Diamond and AA-Omniscience. On the Coding Agent Index it scores 59 with Antigravity CLI, 3 points behind Claude Code with Claude Opus 5.5 (62). Cost is $7.76 per task, versus $10.04 for Opus 5.5. Rollout is limited to selected users.

GeminiClaude CodeGoogle Antigravity+2
Artificial AnalysisArtificial Analysis Intelligence IndexGemini 4 Carbon+10

evals, models, coding-agentsΒ· Added 30 Oct 2026, published 29 Oct 2026

latent.spacearticle🧠 AI

[AINews] Gemini 4 Carbon tops leaderboards, launches for cyber defenders

AINews issue for 27-28 October 2026, a Latent Space digest of Twitter and Reddit. It leads with Google DeepMind's Gemini 4 Carbon: claimed cyber scores (SEC-bench Pro 88.2%, ExploitGym 54.8%, CWE-bench 71.0%), #1 on Artificial Analysis Intelligence Index v5 at 59, and access limited to cyber defenders through the Fairwind Program. It also covers benchmark integrity disputes, GitHub Copilot Fusion, H-Net v2, KV-cache work, open-weight releases and Claude Code quota complaints.

GeminiClaude CodeGoogle Antigravity+12
Gemini 4 CarbonGemini 4 ArgonGoogle DeepMind+39

models, evals, coding-agentsΒ· Published and added 29 Oct 2026

x.comthreadπŸ›‘οΈ Security

Dark Web Intelligence (@DailyDarkWeb) on X

DailyDarkWeb post summarising Anthropic Frontier Red Team research published 27 October 2026. An unreleased internal Claude research model built five attack chains: Chrome sandbox escape (V8 heap bug, CacheStorage race, FedCM use-after-free), a Safari same-origin policy bypass, data extraction from a locked Pixel 9 over USB, a Windows QUIC kernel crash (CVE-2026-33096) and zero-click Linux root via multipath TCP (CVE-2026-98432). Anthropic says all flaws are fixed, including 62 Chrome CVEs as of Chrome 156. The post notes the chains are not independently reproduced.

ClaudeChromeSafari+3
CVE-2026-33096CVE-2026-98432Anthropic Frontier Red Team+8

AI Security, Offensive SecurityΒ· Added 30 Oct 2026, published 29 Oct 2026

x.comthread🧠 AI

Laban (@lunkertw) on X

An X post summarising five AI items: Google DeepMind's Gemini 4 Carbon (88.2% SEC-bench Pro, 54.8% ExploitGym, 71.0% CWE-bench, 59 on Artificial Analysis Intelligence Index v5.0), Ed Zitron's critique of Anthropic's S-1, a Utah Claude Code pilot, and the repos beenuar/AiSOC and expo/skills. In the Utah pilot, 34 developers in 10 agencies took part over four weeks, 80% had a working setup within 30 minutes, and 71% saved over 20 hours. It gives short summaries and links, not primary analysis.

Claude CodeModel Context ProtocolPython+6
Google DeepMindGemini 4 CarbonSEC-bench Pro+9

models, coding-agents, ai-policyΒ· Added 29 Oct 2026, published 28 Oct 2026

x.comthread🧠 AI

Niko (@nikolayxyz) on X

Gemini 4 Carbon is Google's new frontier model, announced in a post by nikolayxyz that quotes Google's launch text. It ranks #1 on v5.0 of the Artificial Analysis Intelligence Index with 59 points, ahead of Opus 5.5 and GPT-6 Astra. Intro pricing is $2 input and $10 output per million tokens. Access starts for cyber defenders first, as Gemini 4 Argon's did. The captured text is cut off before the rollout details.

Gemini
Gemini 4 CarbonGemini 4 ArgonGoogle+4

models, evalsΒ· Added 29 Oct 2026, published 28 Oct 2026

blog.googlearticle🧠 AI

Gemini 4 Carbon

Gemini 4 Carbon is Google's frontier model, announced two weeks after Gemini 4 Argon. It scores 59 on Artificial Analysis Intelligence Index v5.0, 88.2% on SEC-bench Pro, 54.8% on ExploitGym and 71.0% on CWE-bench. Pricing is $2 per million input and $10 per million output tokens. Access starts with a subset of cyber defenders through the Fairwind Program.

Gemini
Gemini 4 CarbonGemini 4 ArgonGoogle+10

models, evals, ai-safetyΒ· Added 29 Oct 2026, published 28 Oct 2026

deepmind.googlearticle🧠 AI

Gemini 4 Carbon: Our next frontier model

Gemini 4 Carbon is Google DeepMind's new frontier model, announced two weeks after Gemini 4 Argon. It ranks #1 on Artificial Analysis Intelligence Index v5.0 at 59 and scores 88.2% on SEC-bench Pro, 54.8% on ExploitGym and 71.0% on CWE-bench. Access starts with cyber defenders through the Fairwind Program, priced at $2 per million input tokens and $10 per million output tokens.

Gemini
Gemini 4 CarbonGemini 4 ArgonGoogle DeepMind+12

models, evals, ai-safetyΒ· Published and added 28 Oct 2026

huggingface.coarticle🧠 AI

NVIDIA Nemotron 3.5 Transcribe and Granary v2: Intelligent Multilingual Transcription You Can Prompt and Adapt

Nemotron 3.5 Transcribe is an open-weight, promptable speech model that handles transcription in 40 languages, translation, diarization for up to eight speakers, and audio Q&A. It has about 4B active of 30B parameters and tops open-weight ASR and diarization leaderboards. The post also covers the Granary v2 curation pipeline (463,062 hours, 48 languages) and a medical fine-tuning case study that cut held-out WER by 45.8%.

NeMo SpeechNeMo CuratorvLLM+11
NVIDIANemotron 3.5 TranscribeGranary v2+16

models, multimodal, training, evalsΒ· Published and added 28 Oct 2026

decrypt.coarticle🧠 AI

House Oversight Chair Comer Probes Delaware Plan for AI-Run Companies

House Oversight Chairman James Comer opened an investigation on 26 October 2026 into Delaware's proposed Artificial Intelligence Company (AIC), a legal entity run day-to-day by an AI agent. His letter to Gov. Matt Meyer requests documents, including internal AI chat logs, by 9 November. The AIC would run in a 30-month sandbox with a single member shielded from debts, and Delaware's draft legislation is expected in January 2027.

James ComerHouse Oversight CommitteeMatt Meyer+8

ai-policyΒ· Published and added 28 Oct 2026

chainalysis.comarticleπŸ›‘οΈ Security

International Law Enforcement Seizes Domain of Virtualine Bulletproof Hosting Service

Virtualine is a bulletproof hosting provider whose domain virtualine.net was seized on 27 October 2026 by the FBI Washington Field Office and the Eastern District of Virginia, with German, Dutch and UK police support. Chainalysis and OverRIPE gave intelligence support. The post lists aliases (Secury, Massgod, Spamhouse, Lanedo, Omegatech), forum advertising on Exploit.in and HackForums, and unhosted bitcoin payments tied to ransomware, infostealers and scam infrastructure.

BitcoinChainalysis Reactor
VirtualineSecuryMassgod+13

Threat IntelΒ· Published and added 27 Oct 2026

arxiv.orgpaper🧠 AI

Perceiving and Predicting Dynamic Sports: Spatiotemporal Intelligence in Vision Models for Egocentric Tennis Video

This paper presents an annotated egocentric tennis dataset (egocentric video synced with five allocentric views, global positions, contact times, stroke types) and evaluates image encoders, video encoders and vision-language models on seven prediction tasks. Best models reach 0.14 m player and 0.54 m ball localization error and 0.14 s contact-time error. Depth input helps 3D ball localization, and longer histories do not help forecasting. A conditional diffusion model generates whole-body tennis motion in real time.

vision-language modeldiffusion modelTransformer
arXiv

research, multimodal, evalsΒ· Added 28 Oct 2026, published 27 Oct 2026

liquid.aiarticle🧠 AI

Introducing LFM3: Every Modality for Specialized Intelligence

LFM3 is Liquid AI's new family of open-weight multimodal models, six models of about 2B parameters branched from LFM3-1.7B-Base (22T pre-training tokens, 256K context). The hybrid backbone uses 13 gated short-convolution, 5 sliding-window attention and 6 global attention layers. Variants cover text, vision with video, audio, omni and two decision models, with on-device speed numbers, fine-tuning demos and robotics extensions.

llama.cppMLXvLLM+17
Liquid AILFM3LFM3-1.7B+32

models, multimodal, inference, trainingΒ· Added 28 Oct 2026, published 27 Oct 2026

x.comthread🧠 AI

Muzammil Shah (@Muzammil_OX) on X

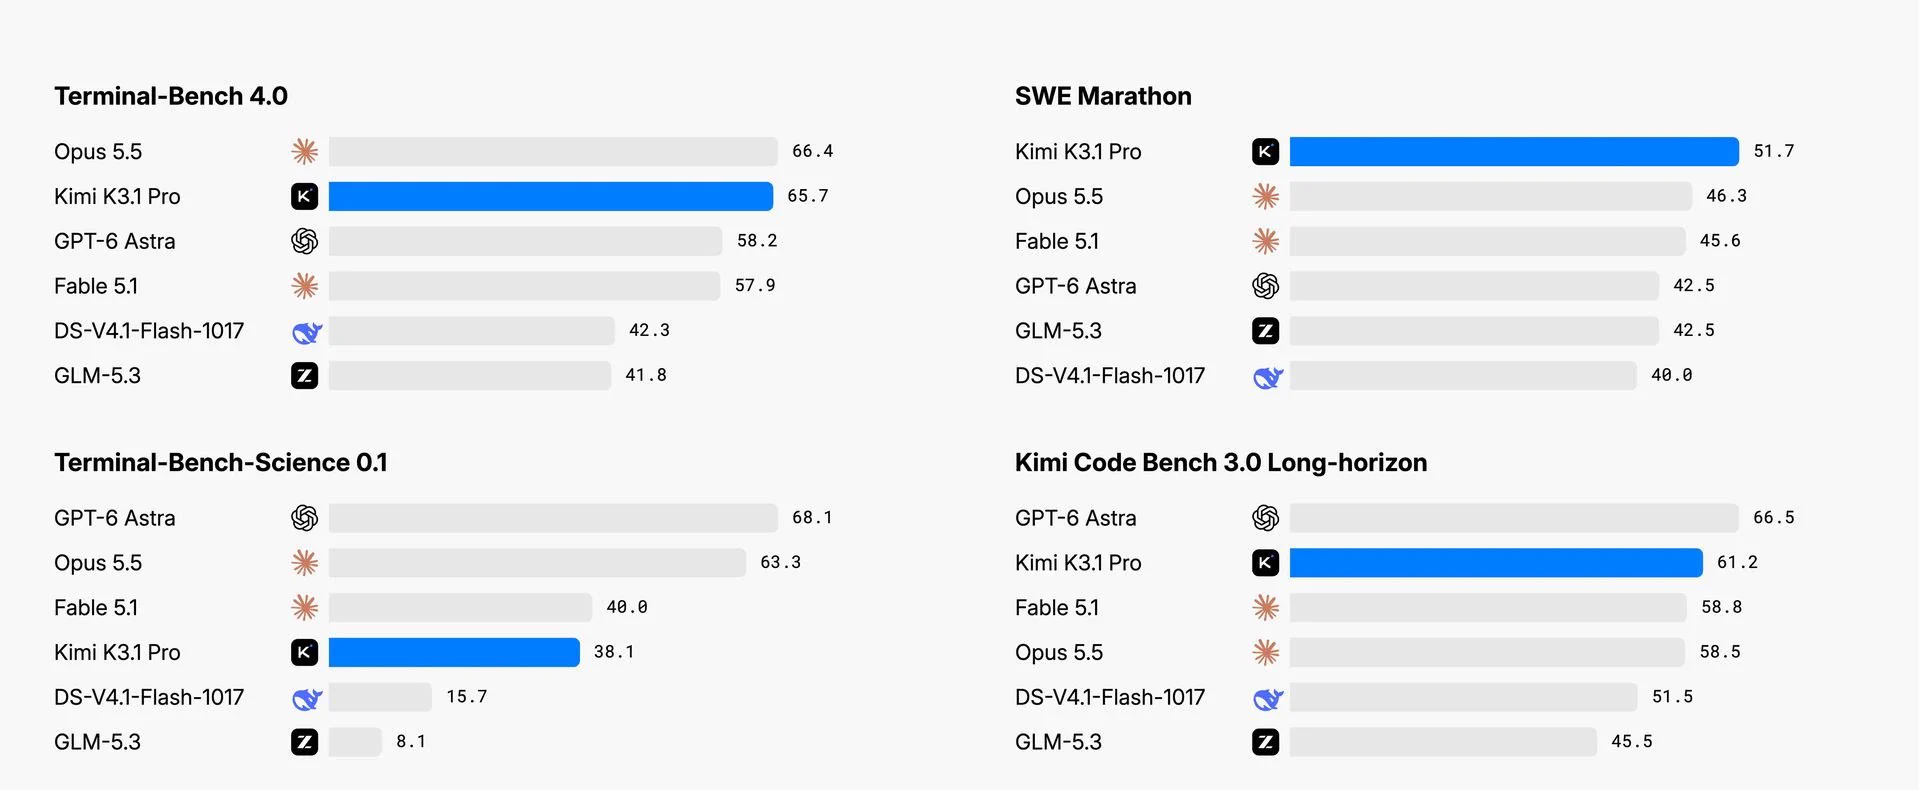
Kimi K3.1 Pro is a new model from Moonshot AI that scores 55 on the Artificial Analysis Intelligence Index, up 11 points from its predecessor, and ranks 4th overall. It has a 1M-token context window and API pricing of $2 per million input tokens and $10 per million output tokens. Weights are due by November 4. Moonshot removed cyber-related training data, which cut its internal vulnerability research score from 90.5% to 81%.

UnityUnreal EngineGodot
Moonshot AIKimi K3.1 ProKimi+2

models, evalsΒ· Added 28 Oct 2026, published 27 Oct 2026

bankless.comarticle🧠 AI

The Rise of Onchain Inference Markets

Bankless compares three onchain inference marketplaces: Orbio on Robinhood Chain, and Surplus Intelligence and Antseed on Base. Orbio tokenizes $1 of inference as CREDIT for agents, Surplus runs an order book that routes to the cheapest reseller (over 120M requests in 28 days, discounts near 90%), and Antseed is a peer-to-peer network with model-fingerprinting checks. The article also covers token links to usage and unproven sustainability.

BaseOpenRouterx402+2
OrbioSurplus IntelligenceAntseed+9

ai-infra, agentsΒ· Added 30 Oct 2026, published 26 Oct 2026

hackers-arise.comarticleπŸ›‘οΈ Security

Artificial Intelligence (AI) in Cybersecurity, Part 30: Shannon – AI Pentester for Web Apps and APIs

Shannon is a white-box AI pentester (@keygraph/shannon) that analyzes an application's source code, then attacks the running instance and reports only findings with a working PoC. The Hackers Arise tutorial runs it against OWASP Juice Shop in Docker on Kali, using OpenRouter (free Nemotron) and local Ollama (Qwen 2.5 Coder 7B) via a models.json file. Output includes PDF, Markdown, JSON and SARIF reports.

ShannonOpenRouterOllama+3
Juice ShopNemotronKeygraph

AI Security, AppSec, Offensive SecurityΒ· Published and added 26 Oct 2026

arxiv.orgpaperπŸ›‘οΈ Security

The Policies of Programming Language Ecosystems: A "Qualitative" Analysis

The Policies of Programming Language Ecosystems is an October 2026 arXiv paper (cs.SE) that compares the policies of eight programming language ecosystems, including CRAN for R, across 38 policy categories. Three authors coded the policies with moderate agreement. Malware, intellectual property and content removal are covered everywhere, while package size limits, metric manipulation, typosquatting and binary uploads diverge.

CRAN
typosquatting

Supply Chain, GRCΒ· Added 28 Oct 2026, published 25 Oct 2026

decrypt.coarticle🧠 AI

Google Quietly Updates Privacy Policy to Let Gmail and Photos Data Feed Ads

Google revised its privacy policy, effective 16 October 2026, so that content from Gmail, Drive and Google Photos can personalize ads if users connect it to other Google services, which includes Personal Intelligence in AI Mode and Gemini. The setting is off by default, advertisers do not see the underlying content, and users can opt out under Connected Content apps in Data & privacy settings. Android Authority first spotted the change, and previously collected data may remain in Search history.

GeminiGmailGoogle Photos+1
GoogleDecryptAndroid Authority

ai-policyΒ· Published and added 24 Oct 2026

latent.spacearticle🧠 AI

[AINews] Kimi 3.1 Pro 104BA-2.8T: Fable-5.1-Class Open Weights narrows Closed-AI lead to 1 month... and Pro Highspeed API with 2-3Γ— speed

AINews issue for 22 to 23 October 2026 centred on Moonshot's Kimi K3.1 Pro, a multimodal mixture-of-experts model with 2.8T total and 104B active parameters and 1M context. Weights are promised for 4 November 2026. Artificial Analysis scored it 55 on its Intelligence Index (fourth place), and Arena ranked it #8 in WebDev. Standard pricing is $2/$10 per million tokens. The issue also covers a cyber-data removal approach, serving-cost objections, and paid-promotion allegations. Shorter items follow on agents, evals and inference.

Mixture of ExpertsClaude CodeCursor+7
Kimi K3Moonshot AIKimi+29

models, evalsΒ· Published and added 24 Oct 2026

x.comadvisoryπŸ›‘οΈ Security

Dark Web Intelligence (@DailyDarkWeb) on X

CVE-2026-114625 is a critical (CVSS 3.1 9.9) SQL injection in on-prem Arista VeloCloud Orchestrator, the SD-WAN management portal, covered in Arista Security Advisory 0199 of 22 October 2026. Any authenticated user, even the lowest Enterprise Read Only tenant role, can become a local superuser operator, and Arista says it is exploited in the wild. On-prem fixes are 5.2.3.18, 6.1.3.10 and 6.4.2.12; two attacker IPs are listed.

Arista VeloCloud OrchestratorCVSS
CVE-2026-114625CWE-8974.82.197.86+2

Threat Intel, AppSecΒ· Added 24 Oct 2026, published 22 Oct 2026

x.comthreadπŸ›‘οΈ Security

Dark Web Intelligence (@DailyDarkWeb) on X

LiteLLM suspects its October 21 release compromise began with Claude Code responses containing GitHub CLI OAuth tokens that were written to logs of an internet-facing internal LiteLLM gateway. Attackers allegedly stole those tokens, used an organization-owner token to disable branch protections, and pushed poisoned artifacts from a lookalike repository. How they entered the gateway is unconfirmed, and this is not a proven Claude Code vulnerability.

LiteLLMClaude CodeGitHub+1
LiteLLM release compromiselookalike repositorybranch protection bypass

Supply Chain, DevSecOps, AI SecurityΒ· Added 25 Oct 2026, published 22 Oct 2026

latent.spacetalk🧠 AI

You are the Team β€” Anekha Sokhal, Moshi

Latent Space interview with Anekha Sokhal, CEO of Moshi, recorded at AI Engineer New York. Moshi is a market-intelligence product for commodity and energy traders. It ingests structured and unstructured data, builds an ontology and graph, and pushes recommendations to each trader's book. She covers confidence scoring across divergent sources, an in-house vision-language model for messy PDFs, and build-versus-buy tradeoffs.

LLMvision-language modelClaude
MoshiAnekha Sokhalswyx+10

llm-apps, ai-policyΒ· Added 23 Oct 2026, published 22 Oct 2026

aws.amazon.comarticleπŸ›‘οΈ Security

Amazon Threat Intelligence identifies PHP2Shell exploitation prior to public disclosure in MadPot

Amazon Threat Intelligence reports PHP2Shell exploitation (CVE-2026-109618, CVE-2026-109619) seen in MadPot honeypot telemetry on 17 October 2026, four days before the 21 October disclosure, from anonymization-network IPs. Multiple actors and PoCs appeared within hours of the patch. It recommends upgrading PHP, hunting for PHP_SESSION_UPLOAD_PROGRESS in multipart POSTs, and investigating from the earliest exploitation date, with patch SLAs measured in hours.

PHPAWS
CVE-2026-109618CVE-2026-109619PHP2Shell+2

Threat Intel, AppSec, Blue Team & DetectionΒ· Published and added 21 Oct 2026

Showing 30 of 223

Show more