Skip to content

121 results for β€œOSI”

What you seeeverything
github.comrepo🧠 AI

Show HN: Hob - Open-source, on device alternative to Claude Cowork and ChatGPT

Hob is an MIT-licensed desktop app from Frigade that runs open-weight models such as Gemma and gpt-oss locally on Mac, Windows and Linux. It picks the best open-weight model that fits the user's computer and sets it up. It is positioned as a free, private, offline alternative to Claude and ChatGPT for tasks like filling out PDFs and working through documents. The page gives no technical detail on its runtime.

GemmaClaudeChatGPT+4
FrigadeHobgpt-oss

inference, llm-appsΒ· Added 27 Oct 2026, published 26 Oct 2026

github.comrepoπŸ›‘οΈ Security

devploit/php2shell

PHP2Shell is a research toolkit by devploit that reproduces a pre-auth remote code execution issue in PHP, tracked as CVE-2026-109618 and CVE-2026-109619, affecting the Apache mod_php and PHP-FPM SAPIs. The repository includes version-matched profiles for many PHP 7.4 through 8.5 builds, reproducible Docker and nginx test labs, a technical write-up of the vulnerability, and mitigation and detection recommendations for defenders.

PHPApachenginx+2
CVE-2026-109618CVE-2026-109619PHP2Shell+7

Offensive Security, AppSecΒ· Added 2 Nov 2026, published 21 Oct 2026

github.comrepoπŸ›‘οΈ Security

eness/php2shell-CVE-2026-109618-CVE-2026-109619-PoC

php2shell is the name given to two critical pre-auth remote code execution flaws, CVE-2026-109618 and CVE-2026-109619, in PHP core's session upload progress handler (php_session_rfc1867_callback), where zend_hash_update frees live zval pointers that are later reclaimed and redirected into zend_call_function to run zif_system. This repository ships poc_109618.py, a fully automated four-stage HTTP exploit that leaks ASLR offsets via Set-Cookie headers against php:8.4.26-apache on Debian Bookworm, along with a root-cause C source patch, mitigation scripts to disable session.upload_progress, and WAF/ModSecurity/Lighttpd/Apache rules plus detection guidance for anomalous PHP worker child processes. Confirmed PHP versions include 8.4.4 and 8.2.34, with EOL branches (5.x, 7.x, 8.0, 8.1) left without official vendor patches.

PHPDockerCloudflare+1
CVE-2026-109618CVE-2026-109619PHP2Shell+6

Offensive Security, AppSec, Blue Team & DetectionΒ· Added 23 Oct 2026, published 21 Oct 2026

github.comrepoπŸ›‘οΈ Security

ikow/php2shell-poc

php2shell-poc is a proof-of-concept and detection toolkit for CVE-2026-109618 and CVE-2026-109619, two PHP vulnerabilities tied to session.upload_progress handling and a Zend engine out-of-memory bailout path affecting PHP 5.4.0 through 8.5.11. The repository includes three working exploit chains, a Docker-based lab (PHP-FPM, nginx, Apache mod_php) for reproduction, and pre-built Suricata, Sigma, ModSecurity, and Lua detection rules. The author recommends disabling session.upload_progress as an interim mitigation, noting the underlying memory corruption requires a full PHP patch to fix.

PHPWordPressDocker+3
CVE-2026-109618CVE-2026-109619GHSA-w8hw-w9fx-j79w+3

AppSec, Offensive Security, Blue Team & DetectionΒ· Added 23 Oct 2026, published 21 Oct 2026

github.comrepoπŸ›‘οΈ Security

Show HN: VoidAccess – open-source dark web OSINT, from query to a graph

VoidAccess is a self-hosted, MIT-licensed dark web OSINT platform that runs a 13-step pipeline from a research query to a relationship graph. It collects from Tor indexes, paste sites, code forges, security feeds and .onion seeds, applies content-safety filters, and exports STIX 2.1, MISP, Sigma, YARA, Snort, Suricata, CSV and JSON. It runs as a CLI with SQLite or as a Docker Compose stack with PostgreSQL, FastAPI and Next.js.

TorPythonDocker+3
LockBitSTIX 2.1MISP+6

OSINT, Threat IntelΒ· Added 21 Oct 2026, published 20 Oct 2026

x.comrepoπŸ›‘οΈ Security

☣ KitPloit - Hacker Tools (@KitPloit) on X

DidierStevensSuite is a collection of Python scripts for malware analysis, file format parsing, hashing and forensic triage. It includes utilities for analysing PDF and OLE documents and for XOR-obfuscated data. The post is a short KitPloit announcement that links to the repository and gives no usage detail.

Python
Didier Stevens

Malware & RE, Blue Team & DetectionΒ· Added 21 Oct 2026, published 20 Oct 2026

x.comrepoπŸ›‘οΈ Security

Abhinav Singwal (@yogsec) on X

GetSubDomains is an open-source tool by yogsec that enumerates subdomains by querying crt.sh certificate transparency logs. It is aimed at the reconnaissance step of penetration tests and bug bounty work. The source is a short tweet pointing to a GitHub repository, so usage details and options are not given.

crt.shGitHub
GetSubDomainsyogseccertificate transparency

OSINT, Offensive SecurityΒ· Added 21 Oct 2026, published 19 Oct 2026

github.comrepo🧠 AI

ralphtradesz/trading-hub

Trading Hub is a free macOS desktop trading platform built with C#/.NET 10 and Avalonia. It uses the user's Claude Code subscription: a chat writes and fixes C# strategies, an in-app MCP server lets Claude run backtests, optimizations and walk-forwards and write reports, and a risk agent proposes position sizes. Install and a Windows port are both driven by Claude Code prompts. License is MIT with Commons Clause.

Claude CodeModel Context Protocol.NET+6
ClaudeATASDatabento+11

mcp, coding-agentsΒ· Added 19 Oct 2026, published 17 Oct 2026

github.comrepoπŸ›‘οΈ Security

enisaeu/enisa-sbd-playbook

ENISA repository of 22 Secure by Design and Secure by Default playbooks for SMEs building products with digital elements. Each playbook has a principle, objective, checklist, minimum evidence and release gate, covering design, build, deployment, maintenance and decommissioning. It supports progressive adoption and CRA readiness without replacing legal obligations.

ENISAEU Cyber Resilience Act

GRC, AppSecΒ· Added 17 Oct 2026

github.comrepo🧠 AI

Show HN: Graphicle, a Rust port of Graphify with memory for coding agents

Graphicle is a local-first Rust program that parses a repository into a tree-sitter code graph (a port of Graphify) and adds project memory: docs, reviewed decisions and captured Claude Code/Codex sessions. It serves cited file-and-line excerpts within a token budget via one MCP server, CLI and browser app, backed by a single SQLite file, with no API key or telemetry. The README reports a code-only extract on Kubernetes (31k files) in 3m18s versus 26m38s for Graphify 0.9.88, and a memory comparison against seven systems. Agent-proposed memories need user approval and go stale when the code they reference changes.

RustModel Context ProtocolSQLite+12
GraphicleGraphifyKarLex AI+2

coding-agents, mcp, llm-appsΒ· Published and added 14 Oct 2026

github.comrepo🧠 AI

santosomar/AI-agents-for-cybersecurity

Companion repository for Omar Santos's Pearson and O'Reilly trainings and books. It has eight parts of runnable Python labs: chat models, embeddings, prompt templates, LCEL prompt chaining, Chroma-based RAG, ReAct/LangGraph/CrewAI/DeepAgents agents, and FastMCP servers (nmap, CISA KEV, Shodan). It also includes guides to six agentic frameworks (OpenClaw, Hermes, Agent Zero, OpenHands, Paperclip, Buzz), a tokenomics module on agent cost (context compounding, prompt caching, model routing, token budget guards, batch API, cost per accepted outcome), and a vendor-neutral design spec for a human-gated multi-agent assessment harness. It is a current, practical curriculum for building and operating agents. Some examples act on real systems and should only be run in an authorized lab.

PythonuvLangChain+17
Omar SantosPearsonO'Reilly+15

agents, llm-apps, mcpΒ· Added 13 Oct 2026

github.comrepoπŸ›‘οΈ Security

sakidekin/CVE-2026-41940-PoC

This repository hosts a proof-of-concept for CVE-2026-41940, described as a CVSS 10.0 unauthenticated authentication bypass in cPanel and WHM caused by CRLF injection into server-side session files via the Authorization header. The accompanying Python tool (cve.py) can detect vulnerable cPanel/WHM instances, retrieve system and account information, and perform post-exploitation actions such as running OS commands, changing the root password, and opening an interactive WHM shell. It also supports bulk scanning workflows piped from subfinder, httpx, and Shodan.

PythonShodan
CVE-2026-41940CRLF injectionauthentication bypass

Offensive SecurityΒ· Added 23 Oct 2026, published 11 Oct 2026

github.comrepoπŸ›‘οΈ Security

bilawalsidhu/gods-eye-view

God's Eye View is an open-source, vanilla-JavaScript CesiumJS and Vite client that puts live aircraft, ships, satellites (SGP4), earthquakes, fires, public CCTV and mapped ALPR cameras on one photorealistic 3D globe. It adds cockpit tracking, FLIR/NVG sensor shaders and a voice agent built on the OpenAI Realtime API. It works without API keys, and the docs cover server-side key brokering with SSRF protection, localhost binding and a SECURITY.md threat model. For OSINT/GEOINT practitioners it is a hackable base for fusing public signals, with an explicit rule against person-tracking features.

CesiumJSOpenAIPinokio+3
SGP4ADS-BAIS+4

OSINTΒ· Added 11 Oct 2026

github.comrepo🧠 AI

mattpocock/skills β€” agent skills for engineers

mattpocock/skills is a collection of small, composable "agent skills" for software engineering that install into Claude Code, Codex, GitHub Copilot, Gemini CLI, Cursor, OpenCode, Devin, Windsurf, Amp and Pi via plugin managers or the `npx skills` CLI. It packages practices like interview-driven requirement gathering (/grill-me, /grill-with-docs), domain-model/glossary building, test-driven development with red-green-refactor (/tdd), bug diagnosis loops, codebase architecture improvement, ticket triage and spec-to-implementation workflows (/to-spec, /to-tickets, /implement, /implement-spec), splitting skills into user-invoked orchestrators and model-invoked reusable disciplines. It's built by Matt Pocock as an alternative to heavier process-owning frameworks like GSD, BMAD and Spec-Kit, aiming to keep engineers in control while giving coding agents better feedback loops and shared vocabulary.

Claude CodeCodexGitHub Copilot+5
Matt PocockDevinWindsurf+5

coding-agents, promptingΒ· Added 8 Oct 2026

x.comrepoπŸ›‘οΈ Security

Dark Web Informer (@DarkWebInformer) on X

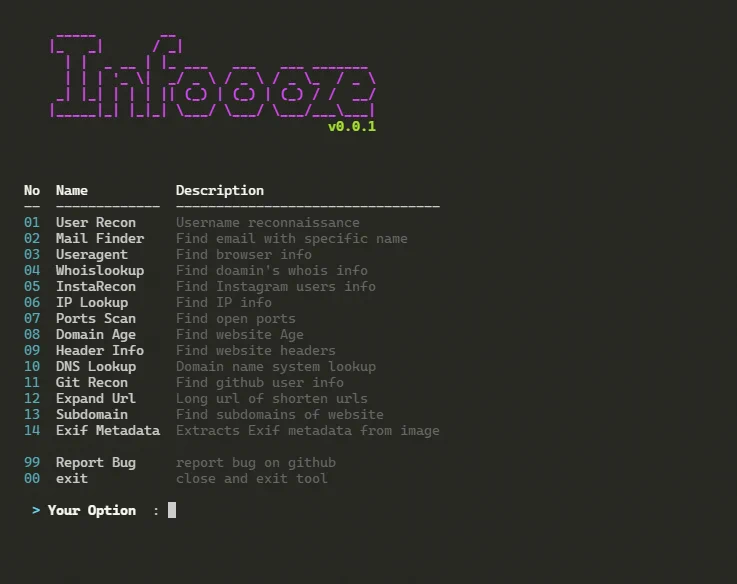
Infoooze is an open-source command-line OSINT reconnaissance toolkit (github.com/devxprite/infoooze) that consolidates common footprinting tasks into one CLI: username enumeration across platforms, email discovery, subdomain enumeration, port scanning, WHOIS/DNS lookups, IP/HTTP header analysis, EXIF metadata extraction, GitHub recon, and URL scanning/expansion. It automatically saves results, making it a lightweight all-in-one alternative to running several separate recon tools.

GitHub

OSINTΒ· Published and added 8 Oct 2026

github.comrepo🧠 AI

overmind-core/overmind

Overmind is an open-source platform (MIT SDK/CLI, AGPL-3.0 platform, self-hostable) that instruments an agent's code via OpenTelemetry tracing, turns the resulting production traces (or any dataset) into a fine-tuned model benchmarked against user-defined eval metrics, and serves it through one unified API with downloadable/retrainable weights. It ships an SDK, CLI, REST API, Console, and an MCP server exposing project tools and workflows (investigate-capability, finetune-capability, ship-model) for Cursor, Claude Code, OpenCode and Codex, and can sync traces from Langfuse, LangSmith, Braintrust or Galileo; self-hosting runs via Docker Compose with Postgres, Redis, Celery workers and Modal-based GPU workers for fine-tuning/serving (vLLM).

PythonDockerPostgreSQL+9
OvermindModalLangfuse+4

training, ai-infraΒ· Added 6 Oct 2026

x.comrepoπŸ›‘οΈ Security

the_OSINT_rack (@the_OSINT_rack) on X

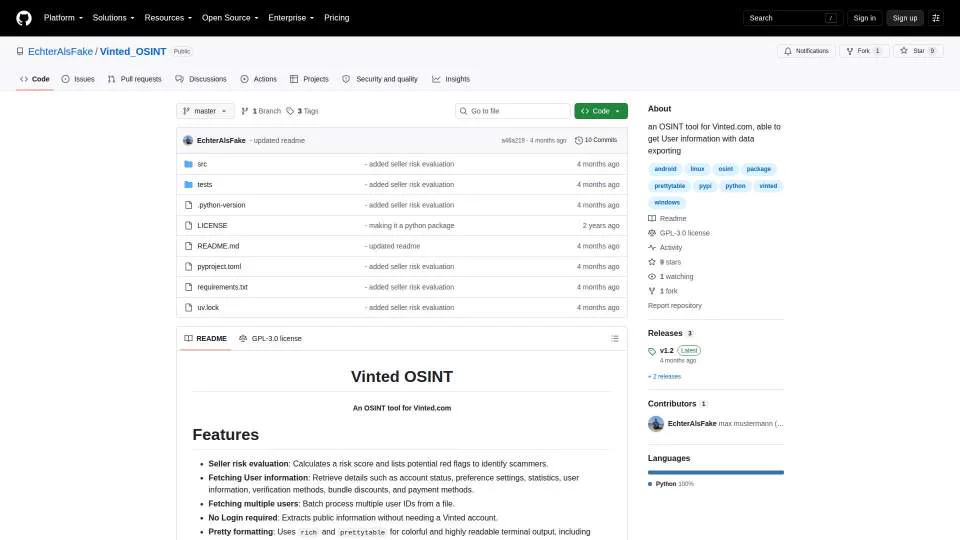
Vinted_OSINT is a GitHub tool by EchterAlsFake that performs open-source intelligence gathering against Vinted.com user profiles, pulling seller/buyer account information and computing a risk score to flag accounts likely run by scammers. It's aimed at buyers wanting to vet sellers before transacting on the second-hand marketplace.

EchterAlsFakeVinted

OSINTΒ· Published and added 4 Oct 2026

github.comrepoπŸ›‘οΈ Security

Sigma r2026-07-01 β€” 20 new detection rules

GitHub release notes for Sigma r2026-07-01, the open-source detection-rule repository, adding 20 new rules (e.g. LSASS crash via Netlogon buffer overflow CVE-2026-41089, TanStack supply-chain attack indicators for Windows/Linux, RedTail cryptominer user-agent detection, AF_ALG kernel crypto API exploit indicator) and updating/fixing dozens of existing rules for ARM64 binary variants, file-sharing domain IOCs, and WMI-based reconnaissance/persistence detection. It's a routine but substantive update to a widely-used blue-team detection content pack.

SigmaWMISysmon+3
CVE-2026-41089RedTail

Blue Team & Detection, Supply ChainΒ· Added 3 Oct 2026

github.comrepo🧠 AI

Bifrost (Maxim AI) β€” open-source LLM gateway

Bifrost is an open-source, high-performance LLM gateway (by Maxim AI) that exposes a single OpenAI-compatible API across 23+ providers including OpenAI, Anthropic, AWS Bedrock, Google Vertex, Azure, Cohere, Mistral, and Ollama. It provides automatic failover, load balancing, semantic caching, Model Context Protocol (MCP) tool integration, budget and governance controls, OIDC user provisioning, and Prometheus-based observability, deployable via npx or Docker with claimed sub-15 microsecond overhead at 5,000 RPS. It is positioned as a drop-in replacement requiring only a base-URL change for existing OpenAI, Anthropic, or GenAI SDK code.

DockerGoModel Context Protocol+4
Maxim AI

ai-infra, mcpΒ· Added 2 Oct 2026

github.comrepo🧠 AI

https://github.com/Panniantong/Agent-Reach

Agent-Reach is a CLI and agent-"skill" layer that equips coding agents (Claude Code, Cursor, OpenClaw) with ready-made web-reading tool use: fetching arbitrary pages via Jina Reader, YouTube transcripts via yt-dlp, GitHub repos via gh CLI, Bilibili search, RSS via feedparser, and semantic web search via Exa through mcporter, with login-gated platforms (Twitter/X, Reddit, Xiaohongshu, Facebook, Instagram) added on request via cookies or OpenCLI browser sessions. Each platform module probes an ordered list of candidate backends and falls back automatically when one breaks (e.g. yt-dlp being blocked by Bilibili's anti-scraping), and an `agent-reach doctor` command reports which backend each channel is currently using. It positions itself as a "capability layer" that selects, installs and health-checks the right upstream tool for an agent rather than wrapping the reads itself.

Model Context ProtocolClaude CodeCursor+4
OpenCLItwitter-clirdt-cli+9

agents, coding-agents, mcpΒ· Added 2 Oct 2026, published 1 Oct 2026

github.comrepoπŸ›‘οΈ Security

Sift β€” Open-Source Secrets/Credential Scanner

Sift is Stratus Security's open-source successor to Snaffler: a Native AOT credential/secrets scanner for pentesters that crawls local drives, SMB shares/subnets, Active Directory, SharePoint/OneDrive/Teams, Slack, and Jira/Confluence for exposed secrets. It supports Kerberos/NTLM/pass-the-hash authentication, resumable checkpointed scans, a JSON rule/ignore-rule system compatible with Snaffler's detection catalogue, and optional local-LLM (Ollama) validation to cut false positives without sending sensitive findings to a cloud API.

.NETActive DirectoryMicrosoft 365+3
Snaffler

Offensive SecurityΒ· Added 30 Sep 2026

x.comrepoπŸ›‘οΈ Security

Andrea (Drego) Draghetti πŸ‘¨πŸ»β€πŸ’» 🎣 (@AndreaDraghetti) on X

Tosint v1.0.0 is an open-source Telegram OSINT tool for analyzing bots and chats, exporting message history and media. The new release adds richer JSONL metadata output, optional SHA-256 hashing of exported media, bot/user authentication support, and an automatic fallback from MTProto-based history retrieval to ID-scan mode when dealing with restricted chats.

TelegramTosint
Andrea Draghetti

OSINTΒ· Added 2 Oct 2026, published 30 Sep 2026

x.comrepo🧠 AI

AI News | AI Tools (@AI_News100x) on X

Open-Dots is an open-source reimplementation of OpenAI's 'Dots' computer-use agent, giving any LLM the ability to control a browser, terminal and filesystem plus connectors to personal apps. It is framework-agnostic (works with any LLM) and free, positioned as a self-hostable alternative to OpenAI's proprietary computer-use offering.

OpenAI

agentsΒ· Published and added 30 Sep 2026

huggingface.corepo🧠 AI

MiMo-V2.6 (Xiaomi): Pro/Flash/9B-distill open-weight release, MIT license, 1M context

Hugging Face collection for Xiaomi's MiMo-V2.6 model family, comprising five open-weight checkpoints: MiMo-V2.6-Pro-RL (1T params), MiMo-V2.6-Flash-RL (311B params), a MiMo-V2.6-Distill-Qwen-9B distillation (vision-language capable), and Pro/Flash MOPD variants. The title claims MIT licensing and a 1M-token context window, positioning this as a large open-weight release spanning full-scale RL-trained models down to a 9B distilled variant usable on consumer hardware.

Hugging FaceQwen
XiaomiMiMo-V2.6-Pro

modelsΒ· Added 29 Sep 2026

github.comrepo🧠 AI

StartLuxLabs/StartLux-Decision

StartLux-Decision is a family of open decision models (0.8B to 27B, plus a 35B-A3B mixture of experts) that return probabilities for every option of typed choice, yes/no and score questions. The repository holds the inference engine and HTTP server (vLLM plugin, /v1/systemone API), with Instant one-pass and AutoThink gated-reasoning variants. Reports first place of 174 entries on Decision Index 0.3.2 (69.12). Code is Apache 2.0; weights are CC BY-NC 4.0.

vLLMPythonHugging Face+3
StartLuxStartLux-DecisionStartLux-Decision-v1-27B+10

models, inference, evalsΒ· Added 23 Oct 2026, published 29 Sep 2026

github.comrepo🧠 AI

Paper2Agent: research papers as interactive AI agents

Paper2Agent is a multi-agent AI system that coordinates parallel specialist agents to transform a research paper and its code repository into a tested MCP server exposing the paper's methods as callable tools ('agentified' papers). It ships as a skill for coding agents like Claude Code and Codex, and the project demonstrates the pipeline on real papers (TISSUE for spatial transcriptomics, Scanpy for single-cell analysis, AlphaGenome for genomic variant interpretation), each producing a hosted MCP server that a chat agent can call to run the paper's actual scientific workflows.

Model Context ProtocolClaude CodeCodex+3
Paper2AgentTISSUEScanpy+9

agents, coding-agents, mcpΒ· Added 27 Sep 2026

github.comrepo🧠 AI

zhuyansen/awesome-claude-video-skills

Awesome-list repository cataloguing 183 open-source 'skills' and toolkits that let Claude Code, Codex and other coding agents generate or edit video: rendering frameworks like HyperFrames and Remotion, motion graphics, explainer/promo video generators, short-form editors, digital avatars and music videos. Each entry is read and security-graded by a companion service (Agent Skills Hub / agentskillshub.top), with a machine-readable JSON feed and category breakdowns (frameworks, promos, explainers, editing, shorts, avatars, animation, motion graphics, scripts, music videos).

Claude CodeCodexModel Context Protocol+10
Claude Opus 5.5

coding-agents, multimodalΒ· Added 29 Sep 2026, published 27 Sep 2026

github.comrepoπŸ›‘οΈ Security

Agent Threat Rules (ATR) β€” open detection-rule standard for AI agent threats

Agent Threat Rules (ATR) is an open, versioned YAML rule format (ATR-YYYY-NNNNN scheme) for detecting AI-agent runtime threats β€” prompt injection, tool-poisoning, malicious SKILL.md content, and MCP exchange abuse β€” evaluated by a reference TypeScript engine (with a Python wrapper) shipped as an npm/pip package, CLI, GitHub Action, and Docker scanner with SARIF output. The project positions itself as "Sigma for agent threats," maps rules to OWASP Agentic/LLM Top 10, MITRE ATLAS, and NIST AI RMF, and publishes an extensive (and unusually self-critical) benchmark suite against corpora like garak, PromptBench, and PromptInject, including documented harness bugs and withdrawn recall figures.

Model Context ProtocolnpmTypeScript+3
CVE-2026-26030CVE-2026-25592OWASP Top 10 for Agentic Applications+2

AI SecurityΒ· Added 26 Sep 2026

github.comrepoπŸ›‘οΈ Security

MITRE ATLAS v2026.09 data release

Release changelog for MITRE ATLAS's atlas-data repository, the structured YAML/STIX dataset behind the ATLAS knowledge base of adversary tactics and techniques targeting AI-enabled systems (prompt injection, model/data poisoning, AI agent tool abuse, AI supply chain compromise). The v2026.09 release brings the matrix to 120 techniques, 88 sub-techniques, 40 mitigations, and 73 case studies, and recent versions introduced a new v6 YAML data format with Pydantic/SQLAlchemy/FastAPI tooling, platform tagging (Predictive AI, Generative AI, Agentic AI, Enterprise), and renamed/generalized techniques like "AI Agent Tool Poisoning," "Manipulate AI Model," and "Enterprise Resource Discovery." It's the canonical, actively-maintained taxonomy practitioners use for AI red-teaming, threat modeling, and mapping real-world AI attack case studies.

MITRE ATLAS
AML.T0019AML.T0058AML.T0104

AI SecurityΒ· Added 26 Sep 2026

github.comrepo🧠 AI

dzhng/jevgrep

Jevgrep (the `jg` CLI) lets a coding agent ask a natural-language question about a repository and get back relevant files, reading leads, and verbatim source excerpts in one response, using an LLM (Jev) to judge relevance across folders, files, and declarations instead of relying on grep/ripgrep alone. It ships an installable "skill" for Claude Code, Codex, OpenCode and other agents that teaches them when to call jg versus their normal tools, and requires a key for Vercel AI Gateway, TypeSafe, OpenRouter, or OpenCode Zen. A reported ten-task SWE-bench repeat found ~40% lower coding-agent cost ($7.62 to $4.52) but a lower solve rate (7/10 vs 8/10 baseline), explicitly framed as a cost/quality tradeoff rather than a win.

Node.jsTypeScriptBun+4
JevTypeSafeVercel AI Gateway+7

coding-agentsΒ· Added 27 Sep 2026, published 26 Sep 2026

Showing 30 of 121

Show more