Skip to content

44 results for β€œTelegram”

What you seeeverything
socket.devwriteupπŸ›‘οΈ Security

Malicious Firefox Extensions Impersonate Phantom, Jupiter, and Bitget to Steal Wallet Secrets

Socket analysis of three malicious Firefox add-ons impersonating Phantom, Jupiter and Bitget wallets, using Unicode homoglyph names. They steal seed phrases and private keys and send them to brand-named subdomains of bonto[.]io. The Phantom fake adds a runtime loader that fetches and evals a second stage, and bundles a drainer backend with Telegram forwarding. Includes IOCs, hashes and wallet addresses.

FirefoxTelegramCloudflare+3
bonto.ioPhantomJupiter+14

Threat Intel, Malware & RE, BlockchainΒ· Published and added 27 Oct 2026
securityweek.comarticleπŸ›‘οΈ Security

Iran’s Prince of Persia APT Hosts C&C in US for First Time Since 2016

Prince of Persia (Infy), an Iranian state-sponsored APT active for nearly 20 years, hosted a Tornado second-stage C&C server in the US in July 2026, the first US hosting since 2016, according to Semperis researcher Tomer Bar. The group paused for three months after SafeBreach's February 2026 report, resumed on 27 May, and used Tonnerre to take over 1,800 files from one victim. The server sat on Namecheap shared hosting; on 24 August the group began a replacement behind Cloudflare. Semperis shared IoCs and advises watching for suspicious Telegram traffic.

TelegramCloudflareNamecheap
Prince of PersiaInfyTonnerre+4

Threat IntelΒ· Published and added 23 Oct 2026

microsoft.comarticleπŸ›‘οΈ Security

The hidden network: Inside the phishing infrastructure ecosystem powering global cybercrime

Microsoft Threat Intelligence maps a Chinese-language cybercrime ecosystem: the YAM Store (Storm-3119), an initial access broker that hijacks Microsoft 365/Azure Education tenants and resells accounts, licenses and SharePoint/OneDrive storage, and the Storm-2990 phishing kits (CoGUI, Haozi, Iron Man System) sold via Telegram. It details the five-stage broker pipeline (app-only client-secret abuse, PnP Management Shell service principal, Graph permissions, Cloudflare DNS management), kit evasion features (geofencing, fake CAPTCHA, WebSocket/Telegram live interaction, 2,335+ templates), downstream device-code phishing and card fraud, and lists mitigations such as passkeys, phishing-resistant MFA and Conditional Access. Microsoft's DCU facilitated a disruption with law enforcement; kits sent over one billion messages since January 2026.

Microsoft 365AzureMicrosoft Entra ID+3
Storm-3119Storm-2990YAM Store+10

Threat Intel, Identity & AccessΒ· Published and added 14 Oct 2026

endorlabs.comwriteupπŸ›‘οΈ Security

Malicious 'Pyronut' Package Backdoors Telegram Bots with Remote Code Execution | Blog | Endor Labs

Endor Labs analyzes the malicious PyPI package pyronut (versions 2.0.184–2.0.186), a trojanized fork of the Telegram framework pyrogram. It hooks Client.start() to import a hidden pyrogram/helpers/secret.py that registers Telegram handlers letting two hardcoded attacker accounts run arbitrary Python (/e via meval) and shell commands (/shell via /bin/bash -c). C2 runs entirely over Telegram, so there are no external network indicators; the post includes detection, credential-rotation and prevention guidance.

PyPIPythonTelegram+1
pyronutpyrogrammeval+4

Supply Chain, Malware & REΒ· Published and added 12 Oct 2026

beaksec.github.iowriteupπŸ›‘οΈ Security

Telegram Desktop vulnerability allowed any user's file to be stolen

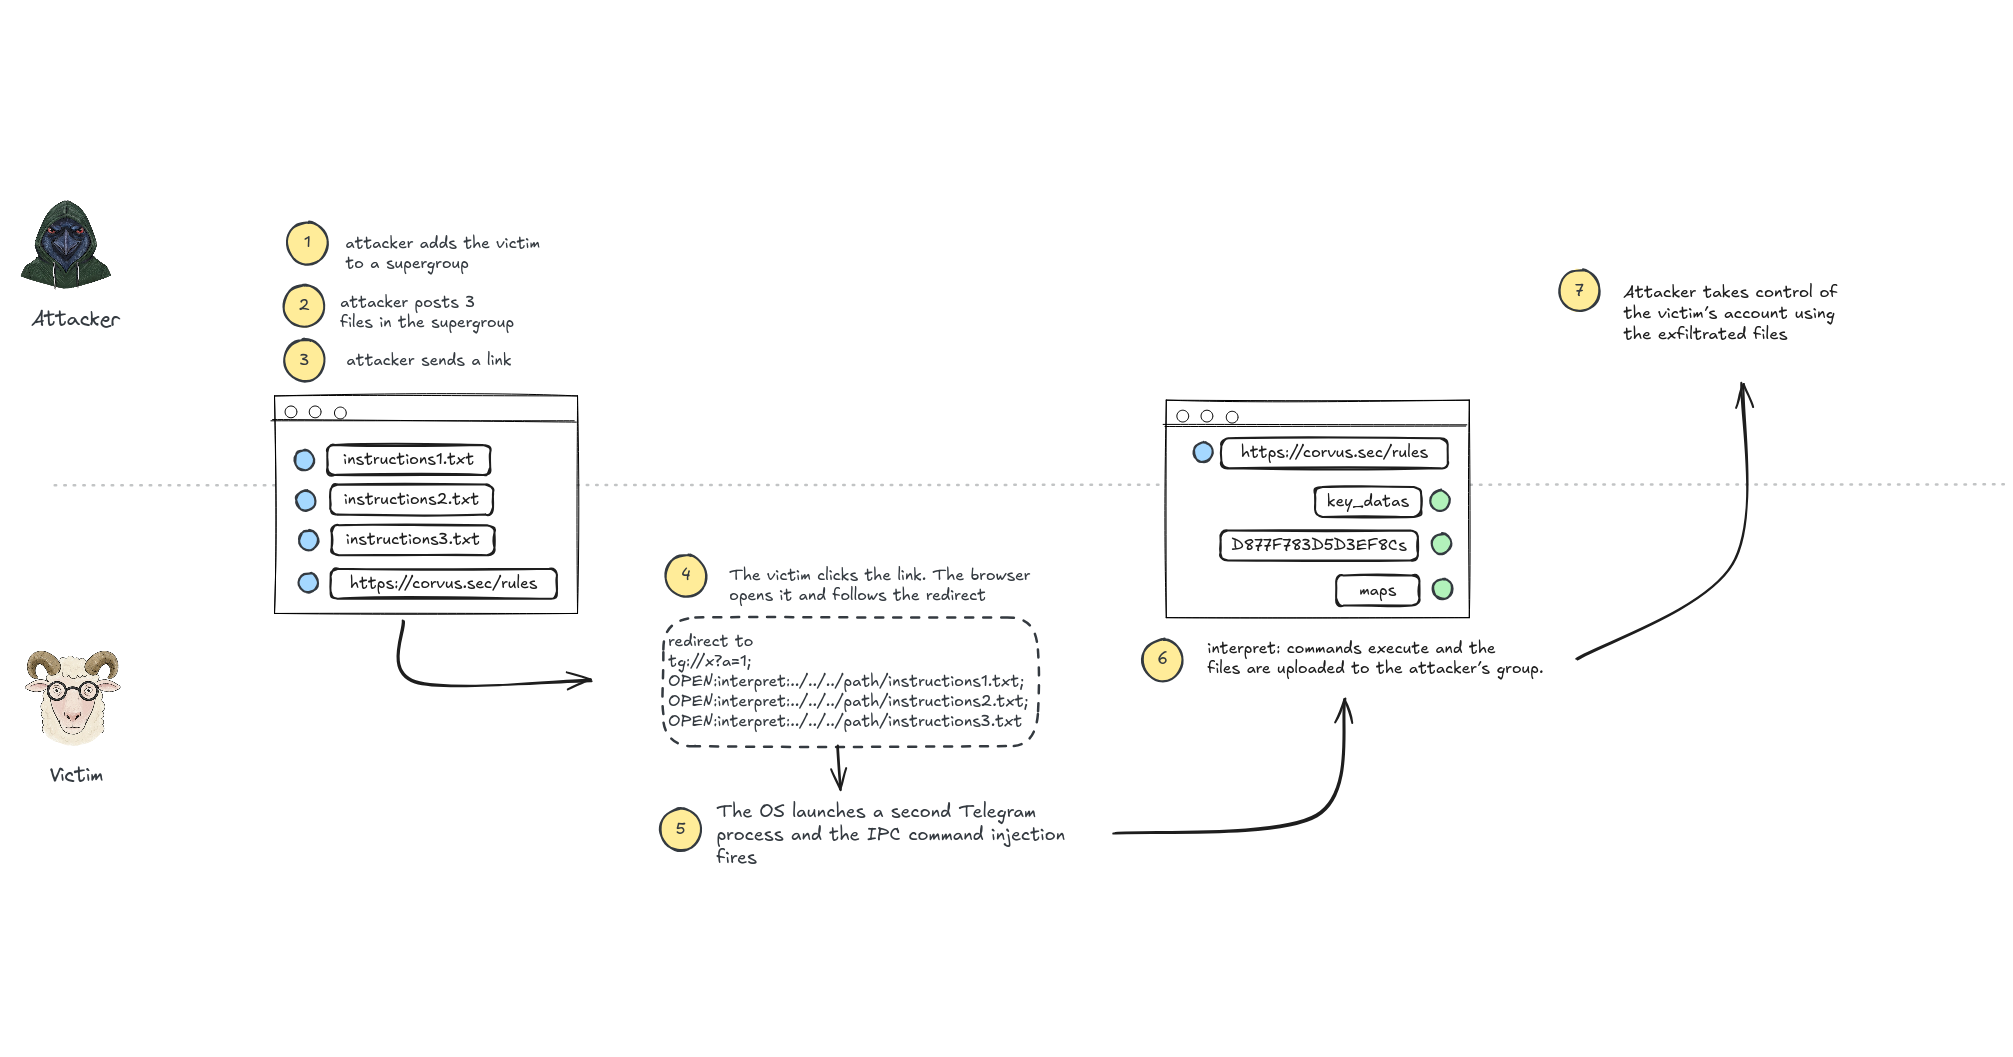
Writeup of a two-bug chain in Telegram Desktop: the single-instance local-socket IPC does not escape the semicolon record separator, so a clicked tg:// link injects extra OPEN: commands, which reach the internal interpret: scheme (InterpretSendPath) that reads an arbitrary file and sends it to a chat with no authorization or confirmation. The author plants instruction files via auto-download in a group, then exfiltrates tdata/key_datas and session files (no local passcode means an empty-password KEK) to take over the account. Fixed in 7.2.9 by removing interpret: and escaping separators; the post lists mitigations such as a local passcode and restricting who can add you to groups.

TelegramWindows
db3405699finterpret:InterpretSendPath+4

AppSec, Offensive SecurityΒ· Published and added 10 Oct 2026

x.comthreadπŸ›‘οΈ Security

Dark Web Informer (@DarkWebInformer) on X

Social post announcing a PoC for CVE-2026-107181 in Telegram Desktop before 7.2.9. A crafted tg:// link abuses Telegram's IPC handler to exfiltrate local files, including session keys, which lets an attacker hijack the account without the password. Rated CVSS 8.1 (v3.1) / 8.6 (v4.0), fixed in 7.2.9, with a linked writeup on beaksec.github.io.

TelegramCVSS
CVE-2026-107181tg:// URI handlersession hijacking

AppSec, Offensive SecurityΒ· Added 10 Oct 2026, published 9 Oct 2026

en.cryptonomist.charticleπŸ›‘οΈ Security

Ledger investigates hardware wallet theft reports; losses estimated above $86M

News report on a suspected supply-chain attack on Ledger hardware wallets sold by the Southeast Asian reseller CryptoBilis. Ledger asked the reseller to suspend sales and shipments, and told buyers from the last 90 days not to initialize devices. Customers who already set up a device should move funds to a new signer with a fresh seed. Onchain investigator Specter estimated more than $86M stolen from hundreds of wallets across Ethereum, TRON and Bitcoin, with 10 addresses listed. The figure is unconfirmed, and there is no evidence that Ledger's hardware or core infrastructure was compromised. The Security Alliance directs victims to its SEAL 911 Telegram bot.

LedgerEthereumTron+1
CryptoBilisSpecterSEAL 911+3

Supply Chain, BlockchainΒ· Published and added 9 Oct 2026

github.comrepo🧠 AI

Tracer-Cloud/opensre

OpenSRE is an open-source framework for building AI SRE agents that resolve production incidents by correlating logs, metrics, traces, deploys and runbooks across 60+ connected tools (observability, cloud infra, incident management, MCP). Beyond the agent runtime (CLI, Python API, Slack/PagerDuty/Telegram integrations), the project's stated mission is to build an RL training and evaluation environment β€” explicitly modeled on SWE-bench's role for coding agents β€” to scale realistic infrastructure-failure scenarios as a benchmark for AI SRE.

DockerPythonPostgreSQL+3
OpenSRETracer-CloudSWE-bench

agents, evals, ai-infraΒ· Added 8 Oct 2026

huntress.comwriteupπŸ›‘οΈ Security

Phishing Campaign Abuses Microsoft Power BI to Deploy Rogue RMMs

Huntress details a phishing campaign that abuses legitimate Microsoft Power BI dashboards (app.powerbi.com) to host a fake "Download Reference" lure that bypasses mail filters trusting the Microsoft domain. Clicking the lure triggers browser/environment fingerprinting and Telegram-bot-based victim telemetry exfiltration via attacker domains (dailylifeproject.site, burnsworth.site, etc.), then silently downloads rogue ScreenConnect installers; a chained CMD/PowerShell script (SCAutoFix.ps1) deploys a second ScreenConnect instance, uninstalls the first for evasion, drops the defense-evasion tool HideUL_x64.exe, and sets a recurring scheduled task before Huntress's SOC intervened.

Power BIScreenConnectTelegram+3
HideUL_x64.exeSCAutoFix.ps1SCAutoRepairEvery2Min

Threat Intel, Blue Team & DetectionΒ· Published and added 7 Oct 2026

rapid7.comarticleπŸ›‘οΈ Security

The ASOS Incident: When Attackers Use the Channels Customers Trust

Rapid7 analyzes the ASOS incident, in which attackers sent a hostile push notification through ASOS's own mobile app claiming its Snowflake environment was compromised and directing customers to a Telegram channel; ASOS confirmed unauthorized access to third-party customer-communication platforms and possible exposure of names/contact details, while Snowflake denied any platform compromise. The piece argues that abusing a legitimate, trusted app/channel defeats typical phishing-awareness heuristics (odd sender, wrong domain) and makes the case for MDR that correlates identity, SaaS, and cloud-integration activity across providers to catch misuse of legitimate access rather than relying on known-bad indicators.

SnowflakeTelegram
ASOS

Threat Intel, Blue Team & DetectionΒ· Published and added 7 Oct 2026
securityweek.comarticleπŸ›‘οΈ Security

ASOS Confirms Cyberattack, Data Breach

ASOS confirmed attackers compromised a third-party platform used for customer communications, sending UK users rogue mobile notifications claiming "we have fully compromised the Snowflake instance" and threatening to leak data unless engaged. ASOS says only basic user info (names, contact details) may have been exposed, with no impact to payment cards or passwords. A newly surfaced group calling itself Xuanye Group claimed the attack on Telegram; researchers note the extortion-via-direct-notification tactic and possible Snowflake angle mirror the 2024 ShinyHunters mass-extortion campaign against Snowflake customers.

Snowflake
Xuanye GroupShinyHunters

Threat IntelΒ· Published and added 7 Oct 2026

decrypt.coarticleπŸ›‘οΈ Security

Crypto Sleuth ZachXBT Fronted $350K to Pose as a Client of Lazarus' Chinese Launderers

Decrypt reports on ZachXBT's account of infiltrating a Chinese money-laundering syndicate working for North Korea's Lazarus Group, by posing as a client ("fronted" $349.7K USDC) to a contact named "Jimmy Green" to gather intelligence on how Bybit's $1.5B hack proceeds were being laundered. The piece details the on-chain corroboration methods used (matching Telegram screenshots to Thorchain swap timing, wallet clustering across BTC/ETH/SOL/Tron) that exposed a $12M+ cluster of Bybit exploit funds, led to a 442K USDT Tether freeze, and separately traced $3M in fraud proceeds to Huione Guarantee, a Cambodian marketplace later targeted by FinCEN and shut down by Telegram.

EthereumSolanaTron+3
ZachXBTLazarus GroupDPRK+12

Threat Intel, OSINT, BlockchainΒ· Published and added 5 Oct 2026

protos.comarticleπŸ›‘οΈ Security

ZachXBT poses as money launderer to infiltrate Lazarus network

Crypto investigator ZachXBT details how he posed as a money-laundering client (contacting a launderer known as "Jimmy Green" over Telegram/Discord) to infiltrate a Chinese organized-crime network laundering funds for North Korea's Lazarus Group. He fronted roughly 350,000 dollars across transactions, collected addresses and bridging methods via THORSwap, and used the intel to link the launderer to the 1.5 billion dollar Bybit hack, the 100 million dollar Poloniex hack, and sanctioned conglomerate Huione Guarantee; findings also contributed to freezing funds tied to the Bybit theft.

Telegram
ZachXBTLazarus GroupBitget+5

Threat Intel, OSINT, BlockchainΒ· Published and added 5 Oct 2026

checkmarx.comwriteupπŸ›‘οΈ Security

MALFEX npm Malware Campaign: Three Payloads And An Adversary That Signs Their Work

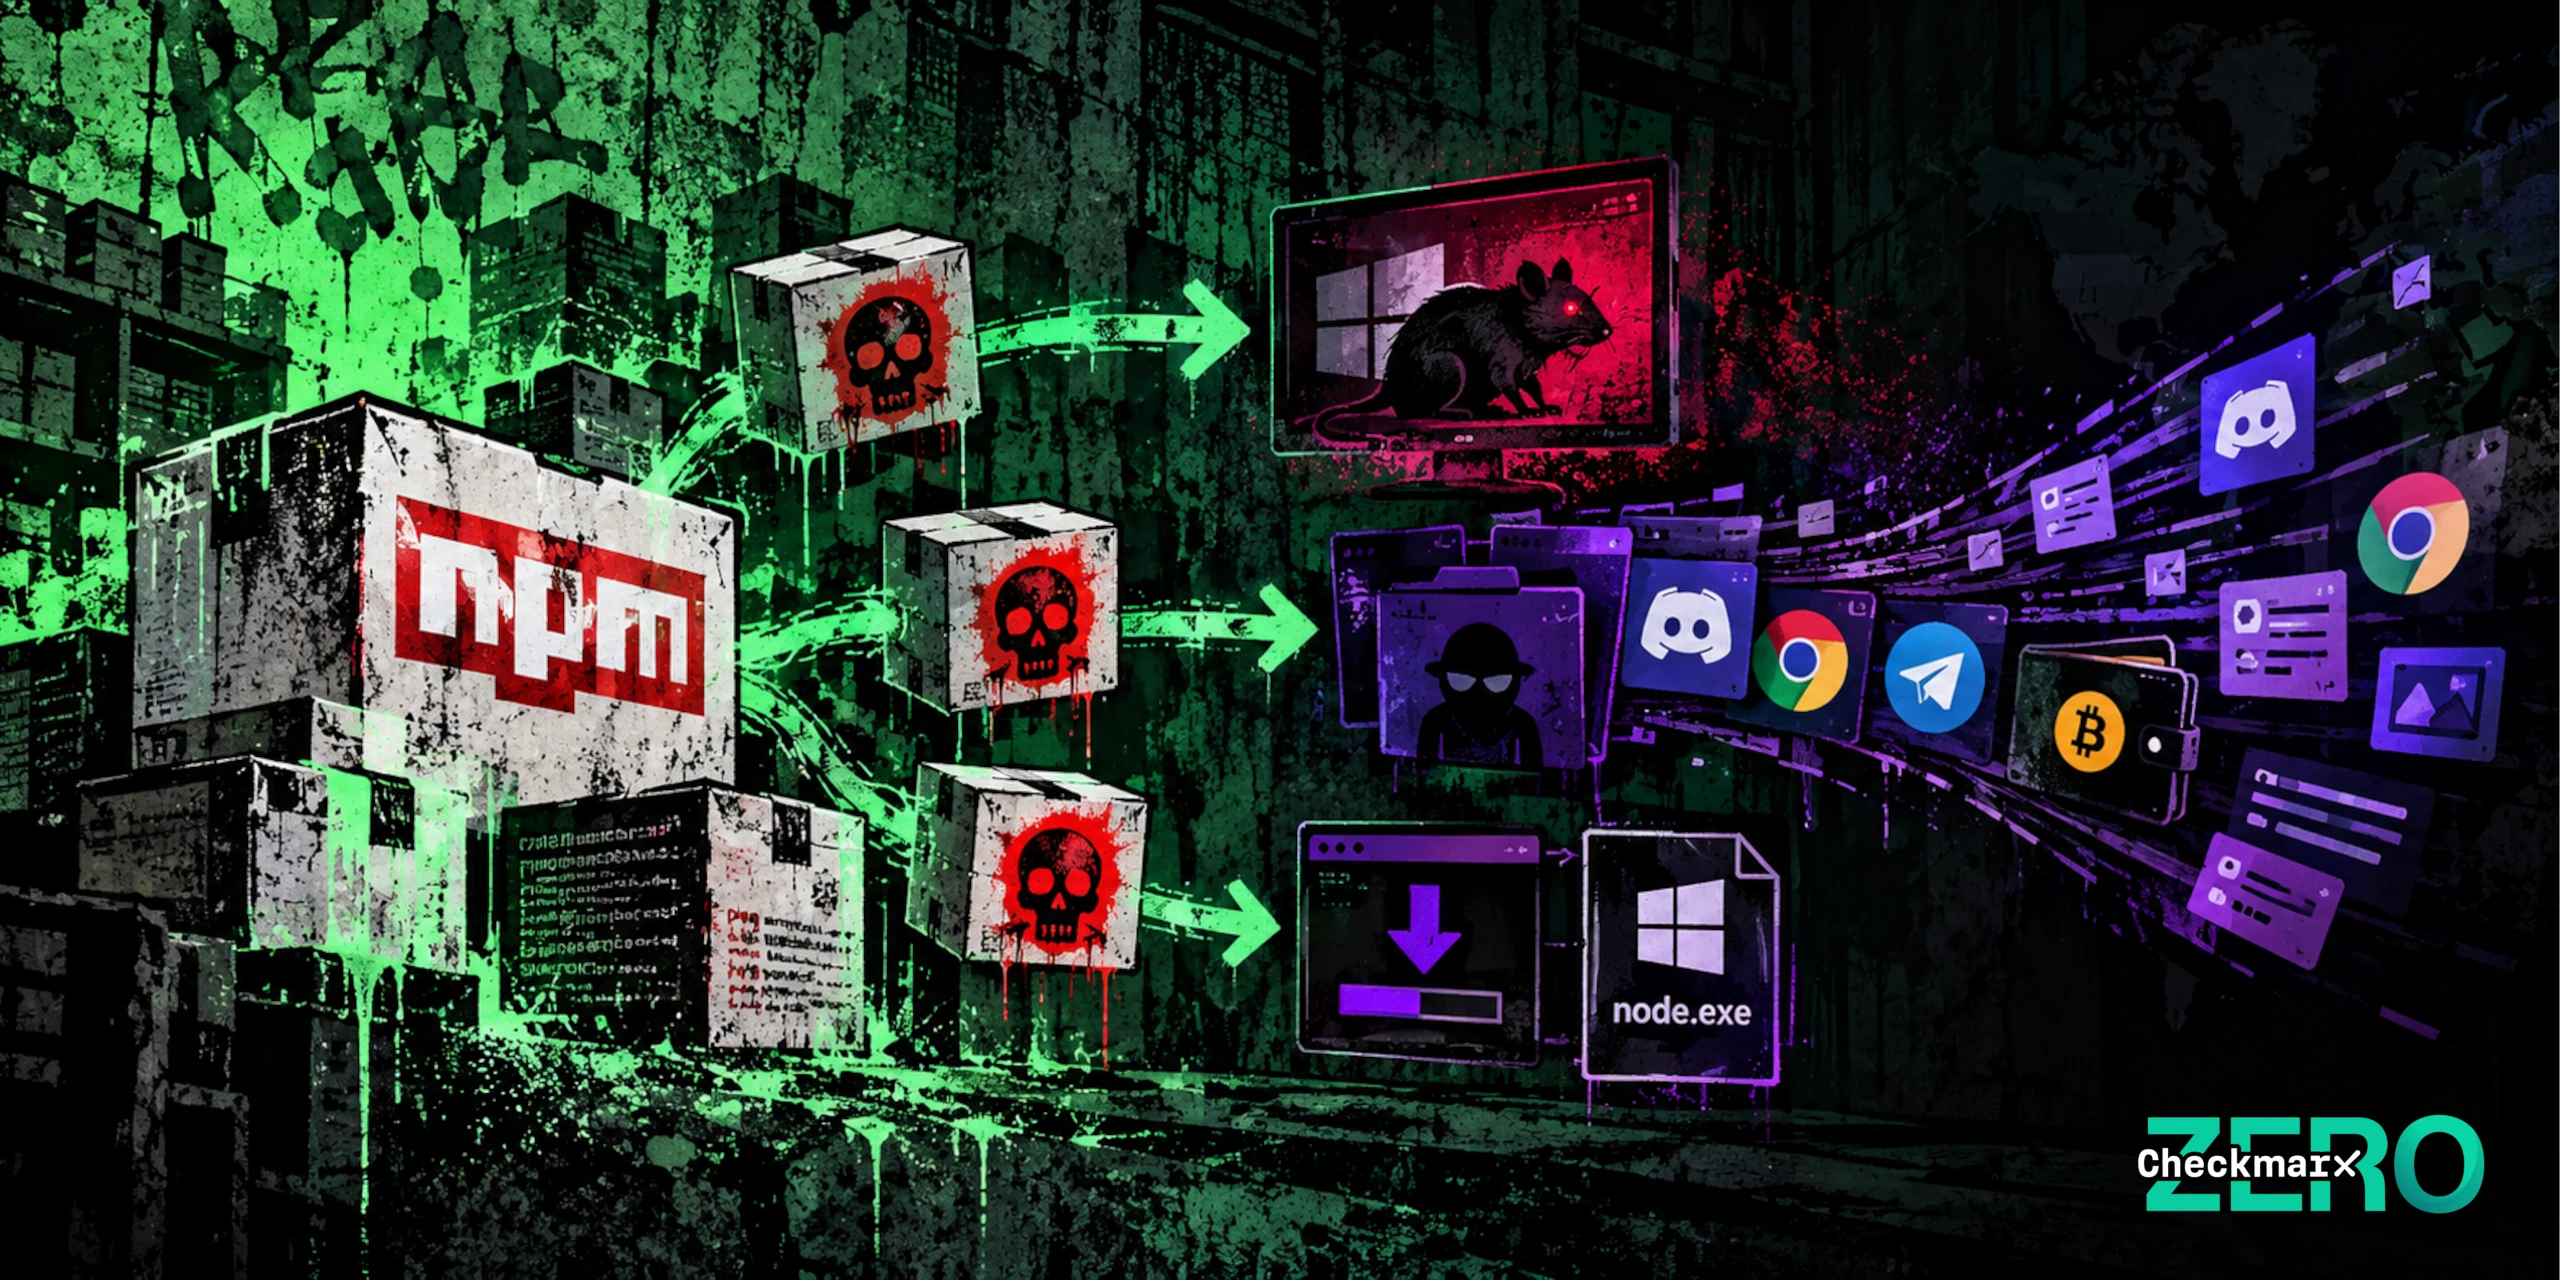
Checkmarx's research team documents MALFEX, an npm supply-chain malware campaign run by a single operator ("Murizada") publishing since August 2023, with 12 packages (8 malicious), three still live as of late September/October 2026. The campaign delivers three distinct Windows payloads: Overlord RAT (a Go-based C2 that reads its server address from encrypted Solana blockchain transactions and uses process hollowing into TapiUnattend.exe), the movinlike Node.js stealer (targeting Discord, browser credentials, Telegram, and crypto wallets, exfiltrating via Discord webhook), and a long-running downloader hidden in function-flag's postinstall script. The writeup includes full IOCs, file hashes, host artifacts, detection commands, and remediation guidance for compromised Windows hosts.

npmNode.jsWindows+3
MALFEXOverlord RATmovinlike+10

Supply Chain, Malware & RE, Threat IntelΒ· Added 7 Oct 2026, published 5 Oct 2026

solana.comtoolπŸ›‘οΈ Security

Introducing Solana Microscope: Program Monitoring and Alerts

Microscope is an open-source, self-hosted monitoring and alerting tool for Solana programs that decodes a program's instructions and events using its IDL, then renders that activity as Grafana dashboards backed by Loki (logs) and Prometheus (metrics). It can also watch a Squads multisig controlling the program, firing precise alerts on specific instructions, events, field values, or multisig proposal approvals to Slack, Telegram, or PagerDuty. A distinguishing feature is built-in health alerting for the monitoring pipeline itself (stalled gRPC/RPC streams, corrupt checkpoints, records decoded but not reaching Loki), so teams can distinguish "program is quiet" from "monitoring is broken." It deploys via Docker Compose, Terraform (AWS/GCP), or Kubernetes manifests, and the code is MIT-licensed on GitHub.

SolanaGrafanaPrometheus+3
Squads

Blue Team & DetectionΒ· Added 8 Oct 2026, published 5 Oct 2026
x.comthread🧠 AI

duyet (@_duyet) on X

AI;DR is an open-source automated pipeline that scrapes AI news from 20+ sources daily, then uses an LLM (routed through AnyRouter) to rank and summarize the stories into a single edition, publishing it to a website, email newsletter, and Telegram channel. It's hosted on Cloudflare and the creator notes it was largely built and is maintained by AI agents. The tool is a concrete example of using LLM-based ranking/summarization to turn a noisy multi-source feed into one curated digest.

Cloudflare
AI;DRAnyRouterJev

llm-appsΒ· Published and added 1 Oct 2026

hackread.comarticleπŸ›‘οΈ Security

MALFEX npm Attack Spreads Windows RAT, Steals Discord and Browser Data

CloudSEK's Global Threat Intelligence team uncovered MALFEX, a supply-chain campaign active since August 2023 that uses malicious npm packages (including tlxbnhd, tldriver, mxdriver, img-to-native, cdn-img-fetch, function-flag, function-color) to deliver malware on Windows. One chain disguises a Windows executable as a PNG to load Overlord RAT, an open-source Go-based RAT that uses the Solana blockchain to resolve C2 addresses; a second chain fetches a 64MB Node.js bundle that steals Discord tokens, browser cookies/credentials, crypto wallets and Telegram session data, exfiltrating via a Discord webhook. Some malicious packages stayed live for over a year even after related packages were pulled or flagged.

npmNode.jsSolana+3
MALFEXOverlord RATcavecrew+8

Supply Chain, Threat Intel, Malware & REΒ· Added 3 Oct 2026, published 30 Sep 2026
x.comrepoπŸ›‘οΈ Security

Andrea (Drego) Draghetti πŸ‘¨πŸ»β€πŸ’» 🎣 (@AndreaDraghetti) on X

Tosint v1.0.0 is an open-source Telegram OSINT tool for analyzing bots and chats, exporting message history and media. The new release adds richer JSONL metadata output, optional SHA-256 hashing of exported media, bot/user authentication support, and an automatic fallback from MTProto-based history retrieval to ID-scan mode when dealing with restricted chats.

TelegramTosint
Andrea Draghetti

OSINTΒ· Added 2 Oct 2026, published 30 Sep 2026

group-ib.comwriteupπŸ›‘οΈ Security

HEAVYGRAM: A Telegram-based Surveillance Backdoor Linked to Handala Hack

Group-IB documents previously undocumented samples of HEAVYGRAM, a Python/PyInstaller-based Windows backdoor that uses the Telegram bot API for command-and-control, screen/audio capture, data exfiltration, and DLL side-loading, alongside the related CRUDEEXCLUDE loader that adds Windows Defender exclusions. The research corroborates and extends a March 2026 US DOJ affidavit and FBI FLASH report, attributing the malware with moderate confidence to the Handala Hack persona β€” assessed as a false-flag "hacktivist" front for Void Manticore (aka Storm-0842/Banished Kitten), operating on behalf of Iran's MOIS β€” used since Fall 2023 against Iranian dissidents, journalists, and critics of the Iranian government via Telegram-delivered, Delphi-packaged lures (fake KeePass, Telegram, Pictory apps). It details four infection-chain variants (WSF/VBS downloaders, HTA Telegram-polling scripts, Delphi droppers with embedded archives), the implant's command prefixes (@@/**/##) and attachment handlers, dual-bot C2 configurations, and provides IOCs and detection/hardening recommendations.

TelegramPowerShellPython+3
Handala HackVoid ManticoreStorm-0842+12

Threat Intel, Malware & REΒ· Added 1 Oct 2026, published 17 Sep 2026

huntress.comwriteupπŸ›‘οΈ Security

Google Doc Sidebar Sends Mac and Windows Users Down Different Paths to Malware

Huntress SOC analysts Ryan Dowd and Jon Semon tore apart a live social-engineering campaign that began with a fake CoinDesk marketing exec DMing a researcher a Google Doc containing a container-bound Apps Script sidebar. The script ran client-side without OAuth consent, exfiltrated victim IP/geolocation/wallet presence via the Telegram API, then routed macOS users to a piped zsh/DMG AMOS stealer chain and Windows users through ClickOnce and PowerShell loaders using three stolen or fraudulent code-signing certificates (a Norwegian company, Discord, and Lenovo). The Windows chain culminated in NetSupport Manager RMM abuse, a Ledger wallet implant, and a self-generated rogue root certificate authority (spoofing Google Trust Services) installed via MsBuild.exe hollowing to silently intercept HTTPS traffic, which the authors flag as the artifact most likely to survive incident remediation short of full reimaging.

WindowsmacOSGoogle Workspace+3
AMOS stealerClickFixMacSync+6

Threat Intel, Malware & REΒ· Added 11 Sep 2026, published 15 Sep 2026

chainalysis.comarticleπŸ›‘οΈ Security

OFAC and DOJ Strike Xinbi, a Multibillion-Dollar Marketplace for Cybercriminals

Chainalysis details the OFAC/DOJ sanctioning and seizure action against Xinbi Guarantee, a $24B Chinese-language Telegram-based marketplace connecting money laundering, scam infrastructure, stolen data, and KYC-bypass vendors. The piece maps Xinbi's escrow model and vendor ecosystem, and traces how DPRK-linked actors used specialized 'Black U' launderers to swap traceable stolen funds from the Bybit ($1.5B) and WazirX ($235M) hacks for cleaner stablecoins sourced from pig-butchering and romance-scam proceeds, ultimately leading to $52M in restrained cryptocurrency across 49 wallets.

Telegram
DPRKXinbi GuaranteeSafeW Technology+4

Threat Intel, BlockchainΒ· Added 30 Sep 2026, published 9 Sep 2026

aikido.devwriteupπŸ›‘οΈ Security

Compromised Flutter package on pub.dev contains XCSSET malware

Aikido Security discovered a variant of the XCSSET macOS worm hidden in universal_file_viewer, a Flutter file-preview package on pub.dev (~500 downloads) β€” the first compromised package found on that registry. The infection was not a targeted supply-chain attack but resulted from the maintainer's machine being infected with XCSSET, which auto-injects malicious build hooks into every Gradle, Xcode, and git project it finds; the poisoned example/ directory (Android Gradle build, iOS/macOS Xcode project files) shipped in the package tarball. The writeup details XCSSET's four-stage infection chain, its android_finder/git_finder/replicator_finder propagation modules, Launchpad-tile persistence, and theft modules targeting Chrome, Safari, Firefox, Telegram, Notes, and clipboard data, plus C2 domain and file-artifact IOCs.

Flutterpub.devmacOS+3
XCSSETuniversal_file_viewer

Supply Chain, Malware & REΒ· Published and added 8 Sep 2026

github.comrepoπŸ›‘οΈ Security

kaandemir993/DarkTortilla-RAT-Telegram-Exfiltration-Payload-Extraction-Analysis

A hands-on reverse-engineering writeup dissecting a DarkTortilla RAT sample (pulled from MalwareBazaar) using Process Hacker, Binary Ninja and x64dbg. It documents the malware's credit-card theft (card_number_encrypted strings for Visa, Mastercard, Amex, Diners Club, etc.), browser credential theft via SQLite queries against Login Data files and app_bound_encrypted_key/os_crypt decryption, and three parallel exfiltration channels β€” a Telegram bot, SMTP mail, and FTP upload β€” with the C2 domain showip.net used for IP detection.

SQLiteTelegramWindows+3
DarkTortilla RATMalwareBazaar

Malware & RE, Threat IntelΒ· Added 30 Sep 2026, published 5 Sep 2026

github.comrepoπŸ›‘οΈ Security

Rekono

Rekono is an open-source pentesting automation platform that chains 19 hacking tools (Nmap, Nuclei, Metasploit, OWASP ZAP, Nikto, Gitleaks, SearchSploit, etc.) so that output from one tool feeds the next, automatically covering recon, service enumeration, vulnerability scanning, and exploit correlation. It deduplicates findings into a single attack-surface inventory per host/port, enriches CVEs with community context for prioritization, tracks fixed/reopened vulnerabilities, and supports team collaboration, scheduled scans, Telegram/email alerts, and report generation for engagements.

NmapMetasploitNuclei+3

Offensive SecurityΒ· Added 3 Sep 2026, published 27 Aug 2026

opensourcemalware.comwriteupπŸ›‘οΈ Security

Windows Infostealer Hits npm and Ruby

Follow-up analysis showing that the RubyGems StubMaker typosquatting campaign and a separately-discovered 40-package npm typosquatting campaign (targeting chalk, commander, lodash, typescript, react, axios) are run by the same threat actor: both use install-time hooks (extconf.rb vs postinstall.js) to fetch a Rust loader from the same GitHub release, which decrypts a byte-for-byte identical Go infostealer confirmed by matching SHA-256 hashes. The stealer harvests browser credentials (bypassing Chromium app-bound encryption), crypto wallets/seed phrases, and Telegram data, exfiltrating via Gofile to a webhook at dresslee.com, and includes WSL-to-Windows sandbox escape logic. The post publishes full network/file IOCs and hashes and argues network-layer blocking (C2 IP and webhook domain) is more durable than package-name blocklisting.

npmRubyGemsRust+3
StubMakerdresslee.comOpenHack

Supply Chain, Threat IntelΒ· Added 3 Sep 2026, published 19 Aug 2026

huntress.comwriteupπŸ›‘οΈ Security

MacSync Stealer: How a Google Search for Claude Led to a macOS Infostealer

Huntress SOC analysts reverse-engineer MacSync, a macOS infostealer/RAT distributed via a sponsored Google Ads link to a fake "Apple Support"-branded claude.ai shared conversation that uses ClickFix to trick victims into pasting a curl/zsh loader into Terminal. The six-stage chain runs a polymorphic gzip/Base64 loader, an in-memory AppleScript stealer that harvests Chromium Safe Storage keys, keychain secrets, Telegram/SSH/cloud credentials, abuses TCC (Full Disk Access and Screen Recording) prompts, drops a Mach-O RAT with WebSocket/TLS C2 and an XOR-obfuscated fallback domain, and trojanizes 84 crypto wallet extensions/apps to phish seed phrases. The piece also compares it to prior AMOS Stealer and SectopRAT ClickFix campaigns and offers behavior-based detection guidance.

macOSAppleScriptzsh+3
MacSyncClickFixSectopRAT+2

Malware & RE, Threat Intel, Blue Team & DetectionΒ· Added 3 Sep 2026, published 17 Aug 2026

opensourcemalware.comwriteupπŸ›‘οΈ Security

StubMaker RubyGems Campaign Delivers a Windows Infostealer

Researchers identified "StubMaker," a RubyGems typosquat campaign (brumdler, brundlef, and 15 packages typosquatting bundler/i18n/rake/activesupport) that abuses the extconf.rb native-extension hook to fake a successful build while beaconing victim OS info and, on Windows, downloading a Rust loader (main.exe) from a GitHub release. The loader decrypts an embedded 11MB Go infostealer entirely in memory, which injects an embedded DLL (abe_payload.dll) into Chromium browsers via the elevation-service COM object to defeat Application-Bound Encryption and steal passwords, cookies, payment cards, crypto wallets/seed phrases, and Telegram data, exfiltrating via Gofile and a webhook at dresslee.com. The piece also details how RubyGems.org's namespace-reclaim behavior let a different account (mod8rz41mje) take over the yanked "brumdler" name to relaunch the campaign, and includes full IOCs and hashes.

RubyGemsGoRust+4
gemlewqqhu1mod8rz41mjerbq95bwt6q+7

Supply Chain, Malware & RE, Threat IntelΒ· Added 3 Sep 2026, published 16 Aug 2026

socket.devwriteupπŸ›‘οΈ Security

Socket: 737 Malicious VPN/Proxy Chrome Extensions Impersonate 66 Brands

Socket's Threat Research Team documents a 737-extension Chrome Web Store campaign ('Myxa VPN' / ΠœΡƒΡ…Π° VPN) that impersonates 66 legitimate VPN/privacy brands (Proton VPN, NordVPN, AmneziaVPN, AntiZapret, Cloudflare 1.1.1.1, etc.) to lure Russian-speaking users seeking censorship circumvention. The extensions force all browser traffic through a shared SOCKS5 proxy pool via chrome.proxy.settings, evade DNS-based blocklists using DNS-over-HTTPS to resolve proxy hosts, sell non-existent premium server locations, ship fake license checks, add remote-configuration code post-approval, and submit false 'no data collection' justifications to Chrome reviewers. The report ties the operation to a single Russian self-employed-registered VPN business via shared Yandex Metrika counters, build-path leakage, bulk domain registration, and a Telegram-based billing dashboard, and notes 516 of the 737 extensions remain live despite prior Palo Alto Networks disclosure.

ChromeChrome Web StoreTelegram+2
T1176.001T1557T1090.002+15

Threat Intel, Supply ChainΒ· Published and added 12 Aug 2026

hackers-arise.comarticleπŸ›‘οΈ Security

Python OSINT Toolkit for Telegram

A Hackers-Arise walkthrough for building a custom Telegram OSINT toolkit in Python using Telethon's MTProto API instead of the limited Bot API, enabling full message-history access, group member enumeration (up to 200/request), and message/engagement metadata collection. The toolkit also extracts EXIF/GPS metadata from downloaded media (via Pillow/piexif) to geolocate targets, persists results in SQLite via aiosqlite, and exposes everything through a Click CLI with modules for profile, members, messages, and media lookups.

PythonTelegramKali Linux+2

OSINTΒ· Added 3 Sep 2026, published 31 Jul 2026

bbradar.iotoolπŸ›‘οΈ Security

BBRadar

BBRadar is a dashboard that aggregates and compares public bug bounty programs across multiple platforms by reward, scope, and listing date, covering web, mobile, source code, and smart contract targets with links to official program policies. It also tracks scope changes and pushes rule-matched alerts to Telegram, with additional shared updates for Pro users in Discord, letting bounty hunters spot newly in-scope targets quickly.

Telegram

Offensive SecurityΒ· Added 3 Sep 2026, published 18 Jul 2026

Showing 30 of 44

Show more