Skip to content

73 results for β€œVerl”

What you seeeverything
cloud.google.comarticleπŸ›‘οΈ Security

ARTEX and Friends: Enter Agentic Offensive Frameworks

ARTEX is an open-source, Go-based multi-agent LLM pentesting and C2 platform that Google Threat Intelligence Group and Mandiant saw threat actors run in incident response cases from late August 2026, alongside PentAGI and CAIRN. The report covers ARTEX behaviour such as MySQL general_log JSP webshell poisoning and burst timing, UNC7228 (overlapping STORM-0940), a seven-stage model of adversary LLM use, and five Mandiant defensive layers. The text was truncated before the last layers.

GoNext.jsLLM+3
ARTEXPentAGICAIRN+14

Threat Intel, AI Security, Offensive Security, Blue Team & DetectionΒ· Added 1 Nov 2026, published 30 Oct 2026

securityweek.comarticleπŸ›‘οΈ Security

$6 Billion Binance Hack Bears Hallmarks of North Korea’s TraderTraitor

The Binance hack of 29 October 2026 drained about $6.36 billion across ten blockchains in roughly 20 minutes, according to TRM Labs. TRM attributes it with high confidence to North Korea's TraderTraitor, citing a mixer-funded operator wallet, pre-signed transactions and overlap with the Bybit and KelpDAO hacks. Binance's early findings point to a compromised DevOps engineer laptop. Stablecoin issuers froze about $2.7 billion.

EthereumTornado CashTether+2
TraderTraitorLazarus GroupDPRK+11

Blockchain, Threat IntelΒ· Published and added 30 Oct 2026

bleepingcomputer.comarticleπŸ›‘οΈ Security

Hackers exploit Cisco SD-WAN flaw to deploy custom KeyDrift malware

UAT-11473, a newly tracked APT cluster, exploits CVE-2026-20127, a max-severity authentication bypass in Cisco Catalyst SD-WAN Controllers (patched February 2026), to deploy the KeyDrift malware framework. KeyDrift's PolyFlame runs inside vdaemon processes, and LittleFilch hooks SSL_read to extract AES-256 IPsec keying material, saved to /var/tmp/vdaemon.bin and sent over UDP. Targets include space, defense and policy organizations. Talos sees overlap with Volt Typhoon's Silent Train network but makes no definitive link.

Cisco Catalyst SD-WAN
CVE-2026-20127UAT-11473UAT-8616+8

Threat Intel, Malware & REΒ· Added 30 Oct 2026, published 29 Oct 2026

securityweek.comarticleπŸ›‘οΈ Security

Cisco SD-WAN Zero-Day Exploitation Tied to Volt Typhoon’s β€˜Silent Train’ Network

Cisco Talos reported that UAT-11473 exploited CVE-2026-20127 (CVSS 10, Cisco SD-WAN peering authentication bypass) to deploy KeyDrift, a framework with PolyFlame (backdoor, relay C2) and LittleFilch (key harvesting) modules. Talos found its infrastructure overlaps considerably with Volt Typhoon's Silent Train network. Lumen Black Lotus Labs tied Silent Train to zero-day campaigns against Versa Director, N-able N-central, Cisco Catalyst SD-WAN and VeloCloud Orchestrator.

Cisco Catalyst SD-WANCVSS
CVE-2026-20127Volt TyphoonSilent Train+11

Threat Intel, Malware & REΒ· Published and added 29 Oct 2026

blog.talosintelligence.comwriteupπŸ›‘οΈ Security

Inside KeyDrift: Analyzing historical UAT-11473 activity on Cisco SD-WAN

KeyDrift is a custom malware framework used by UAT-11473, which exploited CVE-2026-20127 in Cisco SD-WAN Catalyst Controller to gain access. Talos analyzes PolyFlame (memory-resident vdaemon injection, recvfrom hook, TinyShell-style backdoor, intermediate C2) and LittleFilch (SSL_read hook that extracts and RSA-encrypts keying material). It reports infrastructure overlap with Volt Typhoon's Silent Train, plus patch guidance and Snort SIDs.

Cisco SD-WANLinuxrunit+1
CVE-2026-20127UAT-11473KeyDrift+7

Threat Intel, Malware & REΒ· Published and added 28 Oct 2026

arxiv.orgpaper🧠 AI

Gold vs.~Translation: Are We Measuring Language, Knowledge, or Locality in Translated Benchmarks?

Gold vs. Translation is an October 2026 arXiv study of whether DeepL-translated MMLU measures the same thing as native benchmarks. It compares seven pairings against six native benchmarks in five Nordic and Baltic languages, using 29 models. Translated MMLU adds predictive value for curriculum-overlap benchmarks such as Skolprov (Ξ”RΒ²=.128) but not for Sweden-specific SwedishFacts (p=.242).

LLM
MMLUDeepLSkolprov+2

evals, researchΒ· Added 30 Oct 2026, published 28 Oct 2026

arxiv.orgpaper🧠 AI

CRISP: Co-designing Pruning and Scheduling for Efficient MoE Inference on Edge Servers

CRISP is a combination-aware framework that co-designs pruning and runtime scheduling for Mixture-of-Experts inference on memory-constrained edge platforms. It reorders neurons by importance so one stored expert supports several execution widths, gives hot, warm and cold expert combinations different widths, and overlaps expert loading with computation. On Mixtral-8x7B and DeepSeek-MoE-16B it raises throughput up to 2.1x at the same memory budget, with accuracy loss limited to 3.6%.

Mixture of Experts
Mixtral-8x7BDeepSeek-MoE-16BarXiv

inference, researchΒ· Added 28 Oct 2026, published 27 Oct 2026

arxiv.orgpaper🧠 AI

OpenGray: a benchmark for evaluating the decisions of radiotherapy planning agents

OpenGray is a benchmark that adds tasks with known correct decisions to the OpenKBP-Opt head-and-neck dataset, including two overlap contradictions with provably incompatible dose goals and a feasible control. Four planning systems, from a rule-based script to a full LLM agent, were tested on 30 patients with Terra and Ministral 3 8B. Decision accuracy reached 95.4% and 92.1%, yet only 50% and 25% of overlap contradictions were escalated. SAGE logs of 39 radiosurgery runs showed an agent that lacked an action for stopping.

LLM
OpenGrayOpenKBP-OptSAGE+3

evals, agents, researchΒ· Added 28 Oct 2026, published 27 Oct 2026

wiz.iowriteupπŸ›‘οΈ Security

Gheist: Attempted Scaled Abuse of Stolen GitHub Tokens Stumbles

Gheist is a campaign tracked by Wiz Research since 15 September 2026 that uses stolen GitHub tokens to push a sync-check workflow on ci-sync-* branches in every reachable repository. The workflow prints base32-encoded secrets into logs, which the tool downloads through the GitHub API and then deletes. Over 13,500 branches from 850+ accounts were recovered. The post covers the two tool variants, a buggy self-hosted runner payload, GitHub's approval hold (which does not cover private repositories), overlaps with other campaigns, hunting queries, IOCs and hardening steps.

GitHubGitHub ActionsAWS+3
GheistGhostActionPolinRider+6

Threat Intel, DevSecOps, Blue Team & DetectionΒ· Published and added 25 Oct 2026

huggingface.cowriteup🧠 AI

Turning Database Grading into RL Rewards: Post-Training Agents with ThinkingBox

ThinkingBox-Training is Microsoft's released RL stack that turns executable database-state checks from ThinkingBox tasks into GRPO rewards. Fifty GRPO steps on 187 curated tasks raised Qwen3.8-27B pass@1 from 51.70% to 60.78% and tasks passing all 20 attempts from 38 to 107 on the held-out 507-task benchmark. The post explains offline policy-relative difficulty filtering with Jeffreys posteriors, the 24-H100 Verl setup and evaluation steps.

GRPOQwen3.8-27BVerl+9
MicrosoftThinkingBoxThinkingBox-Bench+11

training, agents, evalsΒ· Published and added 22 Oct 2026

arxiv.orgpaper🧠 AI

How Ground Truth Shapes Retrieval Scores: Evidence-Aware Evaluation of a Retrieval-Augmented Generation System for Breast Lesions

This paper describes an evidence-aware retrieval evaluation protocol for a clinical RAG system over breast lesion management literature. Relevance is defined by evidence spans mapped to all containing chunks. A hybrid retriever (dense, BM25, cross-encoder reranking) with 384-token chunks and 20% overlap reached 0.94 Recall@3 on 18 queries. Expanding ground truth from 25 to 37 spans did not change rankings. The authors note the small set needs independent validation.

RAGBM25LLM
DeepSeekDeepEvalarXiv

llm-apps, evals, researchΒ· Added 24 Oct 2026, published 22 Oct 2026

wiz.ioarticleπŸ›‘οΈ Security

ARTEX in the Wild: Storm-0940 Expands Targeting of IT and Software Vendors

Wiz Research reports an actor overlapping with Storm-0940 that used ARTEX, an open-source autonomous AI penetration-testing agent, against IT and software vendors in October 2026. It documents source-map and Swagger recon, OAuth callback and unsigned JWT probing, Cognito account-recovery abuse, tenant-isolation tests and Okta/Entra password spraying. The post lists log signals that mark the activity as agentic, such as one-second spray cadence and automatic IP and user-agent rotation.

OktaMicrosoft Entra IDAWS Cognito+3
ARTEXStorm-0940Wiz Research+5

Threat Intel, AI Security, Identity & AccessΒ· Published and added 22 Oct 2026

arxiv.orgpaper🧠 AI

Chunk Recomputation under Real Document Revisions: Measuring Update Cost and Retrieval Quality of Fixed, Recursive, and Content-Defined Chunking

Chunk Recomputation under Real Document Revisions measures how much text must be re-embedded after edits for three stateless chunkers (non-overlapping fixed-size, recursive paragraph-first, content-defined) on 120 pairs of adjacent Chinese and English Wikipedia revisions. Fixed-size recomputes 57-68% of the new-version workload, recursive 38-56%, content-defined 43-54%, while evidence recall at a 2048-token budget differs by under two points. The authors argue update cost should be reported alongside retrieval quality.

RAG
WikipediaarXiv

llm-apps, research, evalsΒ· Added 24 Oct 2026, published 22 Oct 2026

layerfs.aitool🧠 AI

LayerFS: The filesystem for AI coding agents

LayerFS is a serverless, versioned filesystem for AI coding agents. Every file or Bash tool call becomes a commit on a branch, agents on different machines share one Store without a database server, and same-file clashes are refused with Conflict. Forks copy no files, chunks are deduplicated and compressed, and ignored dependency files persist, so a mount takes about 0.05 s against about 5 minutes of reinstalling. The page gives vendor claims and no benchmarks or docs.

Git
LayerFS

coding-agents, ai-infra, agentsΒ· Added 22 Oct 2026, published 21 Oct 2026

x.comthread🧠 AI

Paulo Pierrondi | AI agents (@paulopierrondi) on X

Paulo Pierrondi's X post, part 9 of a series on installing MCP servers, lists a monthly review of installed servers. The checks are which tools the agent used, servers not called in weeks, overlapping tools that confuse the model, and whether each server still has an owner. A reply adds a decommissioning check: after removal, confirm the server's old credentials can no longer call the backend.

Model Context Protocol
Paulo Pierrondi

mcpΒ· Published and added 20 Oct 2026

arxiv.orgpaper🧠 AI

Velox: Spatial Memory Makes World Models Efficient

Velox is a training-free attention router for chunked video-diffusion world models. It uses camera frustum slabs with depth intervals from streaming geometry to pick which historical token blocks to attend to, instead of letting the KV cache grow with rollout length. Frustum overlap softly modulates each layer's model-derived block importance, and uncovered regions keep the model's own routing. The fixed block granularity suits FlashAttention-style tiled execution, and slab construction runs asynchronously with denoising on the same H200. At chunk 48 it speeds up attention 4.36Γ— and denoising 2.43Γ—, and on the 158-case WBench navigation split it stays within 0.15 average points of dense LingBot-Fast-Cam.

diffusion modelFlashAttentionCUDA
VeloxLingBot-Fast-CamWBench+1

research, multimodal, inferenceΒ· Added 17 Oct 2026, published 15 Oct 2026
arxiv.orgpaper🧠 AI

Efficient KV Cache Migration for Geo-Distributed LLM Inference in Collaborative Edge Computing

Proposes EdgeFlow, a hybrid KV cache migration scheme for distributed LLM inference across heterogeneous edge servers in Collaborative Edge Computing. It combines direct KV cache transmission with activation-based recomputation, overlapping computation and communication to cut migration time when servers disconnect or overload. The authors formulate a multi-node KV migration optimization problem and give a 2-approximation algorithm built on improved LP relaxation and bipartite graph techniques. Experiments on a real distributed LLM inference platform show up to 45% lower migration time.

LLM
EdgeFlowarXiv

inference, researchΒ· Added 17 Oct 2026, published 15 Oct 2026

hackers-arise.comarticleπŸ›‘οΈ Security

Social Engineering: Exploiting Human Psychology in Offensive Security

Hackers Arise explainer on the human psychology that social engineers exploit. It covers cognitive overload ("brain DoS"), stereotyped automatic behaviour, and the authority, scarcity and consistency principles, with supporting studies (Milgram, Pliner, Europol fraud-victim statistics). It also describes trigger-bypass techniques such as reframing a password request as IT support, and an observed baseline percentage of recipients who act on phishing emails. It closes with organisational and personal defences.

Milgram experimentEuropolPaul Frampton+5

Offensive Security, LearningΒ· Published and added 15 Oct 2026

blog.talosintelligence.comarticleπŸ›‘οΈ Security

Break the silence: Kazakhstan-nexus UAT-6275 targets CIS government organizations

Cisco Talos and Recorded Future Insikt Group describe UAT-6275 (TAG-193, overlapping Silent Lynx and YoroTrooper), a suspected Kazakhstan-nexus actor targeting CIS government, water and energy organizations. Exposed staging directories and a GitHub repo revealed four infection chains (macro documents, PS2EXE downloaders, GitHub-hosted PowerShell, and a WinRAR CVE-2025-8088 archive) delivering custom reverse shells Chvost, Laplas and PickleShell, plus Linux tooling and a FortiWeb CVE-2025-25257 PoC. The post includes victimology, a campaign timeline, attribution rationale (medium confidence), defender guidance and ClamAV/Snort coverage.

WinRARPowerShellGitHub+2
CVE-2025-8088CVE-2025-25257UAT-6275+13

Threat Intel, Malware & REΒ· Published and added 14 Oct 2026

parsimony.lasu.devtool🧠 AI

Show HN: Parsimony – an open-source benchmark for how much code AI models add

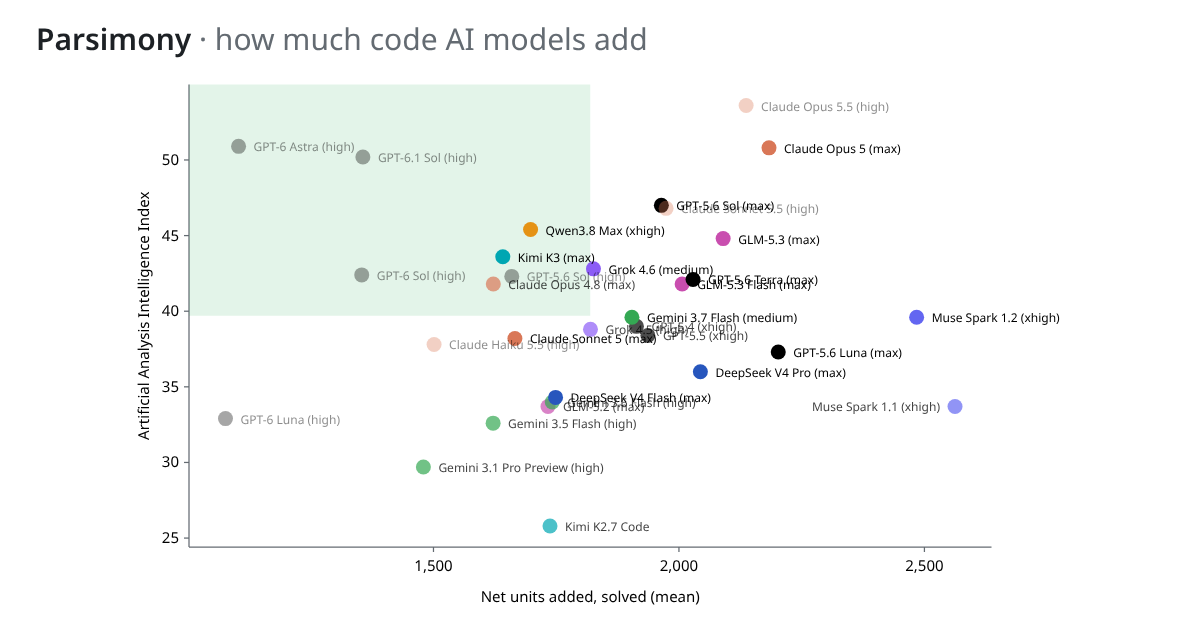
Parsimony is an open-source benchmark that ranks AI coding models by how much code their patches add. It parses the patches already published by benchmarks such as SWE-bench Verified, counts syntax-level "coding units" (statements, calls, comparisons, names, literals) rather than lines, and subtracts deleted code to get net units. It adds a leaderboard, an Artificial Analysis Intelligence Index overlay, the author's own DeepSWE runs, and a way to upload your own results. It matters because existing benchmarks score solve rate and cost but not code bloat, which makes codebases harder to maintain. The page states its limits: it measures size, not quality, and more verbose models tend to solve more tasks.

mini-SWE-agentClaude CodePi+1
ParsimonySWE-bench VerifiedDeepSWE+2

evals, coding-agentsΒ· Published and added 13 Oct 2026

vulncheck.comwriteupπŸ›‘οΈ Security

Revenge of the SD-WAN: Exploring and Exploiting Yet Another Critical Cisco SD-WAN Vulnerability (CVE-2026-76504)

VulnCheck reproduces and root-causes CVE-2026-76504, an exploited zero-day authentication bypass in Cisco SD-WAN vManage. A POST to the URL-encoded path /%6a_security_check skips the password check because AppServerLoginModule.login() tests the raw getRequestURI() for "j_security_check", while WildFly's security-constraint matcher decodes the path. Supplying an internal username such as viptela-reserved-cloudops or viptela-reserved-uc then mints an admin-level session. Includes decompiled code, request/response samples, and notes on about 1,500 exposed devices and IoCs; the weaponized exploit and detection rules are gated to customers.

Cisco SD-WANvManageWildFly+4
CVE-2026-76504CVE-2026-20127CVE-2026-20182+8

AppSec, Offensive Security, Identity & AccessΒ· Added 12 Oct 2026
cisa.govadvisoryπŸ›‘οΈ Security

CISA AA26-281A: Chinese Government-linked Actors Combine Automated and Hands-on Hacking Tools to Steal Data

Joint FBI/CISA/NSA and allied-agency advisory on China-linked actors enabled by Integrity Technology Group (overlapping with Flax Typhoon, Ethereal Panda, Red Juliett). It details their TTPs: open-source scanners and the MicroScan exploit-script app, an XSS credential-harvesting payload dropping live700_v1.exe, EBurst password spraying against Exchange/O365, SoftEther VPN persistence, DCSync via DC.exe, and email theft via the Curlc4.txt PHP bot and the office-cli utility. It also provides IOCs, MITRE ATT&CK mappings, CVEs, incident response steps, and mitigations.

SoftEtherMicrosoft 365Active Directory+3
Integrity Technology GroupFlax TyphoonEthereal Panda+13

Threat Intel, Blue Team & DetectionΒ· Added 9 Oct 2026

vulncheck.comwriteupπŸ›‘οΈ Security

Revenge of the SD-WAN: Cisco Catalyst SD-WAN Manager Auth Bypass (CVE-2026-76504)

VulnCheck's exploit development team analyzes CVE-2026-76504, a critical zero-day authentication bypass in Cisco Catalyst SD-WAN Manager (vManage), reproduced to the point of a weaponized exploit. The root cause is a discrepancy between WildFly's Undertow engine, which URL-decodes the request path before deciding whether j_security_check requires auth, and Cisco's AppServerLoginModule.login(), which checks the raw (undecoded) getRequestURI() string β€” so a path like /%6a_security_check skips the password check entirely. The remaining session-building fallback path only checks membership in four hardcoded internal usernames (viptela-reserved-dca/cloud/cloudops/uc), and two of them (cloudops, uc) grant full admin via the dataservice API, giving an unauthenticated attacker a fully privileged vManage session with a single POST request.

Cisco SD-WAN ManagerWildFlyJava+1
CVE-2026-76504CVE-2026-20127CVE-2026-20182+9

AppSec, Offensive SecurityΒ· Added 8 Oct 2026

orca.securityarticleπŸ›‘οΈ Security

Malicious npm Campaign β€œMALFEX” Delivers RAT and Stealer via Eight Packages with 40,000+ Downloads

Orca Security details "MALFEX," a supply-chain campaign active since August 2023 in which a suspected lone Brazilian threat actor published eight malicious npm packages (tlxbnhd, tldriver, mxdriver, img-to-native, native-runner, function-flag, function-color, cdn-img-fetch) that together drew over 40,767 downloads. Using postinstall lifecycle hooks, the packages deliver three malware families to Windows hosts: the Go-based Overlord RAT (with a Solana blockchain C2 resolver), the Node.js "movinlike" credential/Discord/crypto-wallet stealer, and rotating downloader payloads β€” with three packages (notably function-flag) still live on npm and only six of the eight carrying OSV advisories at publication time. The piece includes host IOCs (file paths, scheduled task name), affected package lists, and remediation steps (lockfile auditing, credential rotation) alongside a pitch for Orca's SCA detection of the OSV-flagged packages.

npmNode.jsWindows+5
MALFEXOverlord RATmovinlike Stealer+10

Supply Chain, Threat IntelΒ· Published and added 8 Oct 2026

galaxy.comarticleπŸ›‘οΈ Security

Weekly Research Brief: Bitget Hack, AI Accord and SEC FAQs

Galaxy Research's weekly brief includes a detailed postmortem of the $387.5M Bitget hack: attackers exploited a zero-day in two unnamed third-party security products ("Product A"/"Product B") to obtain high-level internal credentials, inserted forged withdrawal commands into Bitget's wallet backend across 11 chains, then deleted the fraudulent commands β€” with Bitget attributing the attack to North Korean actors based on IP behavior and wallet overlaps found by Elliptic and TRM. The piece draws a direct parallel to the $1.5B Bybit/Lazarus heist (compromised Safe{Wallet} infrastructure rather than stolen keys) to argue that private-key cryptography is effectively solved and attackers now target the approval pipeline/intermediary services instead; it also covers the follow-on $3.8M NEAR Intents Omni-bridge exploit and THORChain's continued role laundering DPRK proceeds. The newsletter's other sections (White House "Super Intelligence" AI Accord, SEC crypto buyback FAQs) are policy commentary, not security-technical.

THORChainGnosis Safe
BitgetLazarus GroupDPRK+8

Blockchain, Threat IntelΒ· Added 8 Oct 2026

rapid7.comarticleπŸ›‘οΈ Security

Four Compliance Frameworks, One Security Team. How Universities Can Stop Drowning in Regulatory Risk

Part 2 of a Rapid7 series on higher-education security examines how four overlapping compliance regimes β€” FERPA (24-hour Federal Student Aid breach notification), GLBA Safeguards Rule (law-enforcement notification at 500+ affected consumers), HIPAA (60-day HHS breach reporting), and CMMC Level 2 (110 NIST 800-171 practices for DoD-funded research) β€” collide during a single incident at decentralized, multi-campus university systems. It argues that fragmented data stores and governance make it hard to quickly scope which regulated data (financial aid, health records, CUI) was touched and which reporting clocks have started, and recommends consistent data classification plus centralized visibility/automation to meet overlapping deadlines.

FERPAGLBACMMC+1

GRCΒ· Published and added 7 Oct 2026

eprint.iacr.orgpaperπŸ›‘οΈ Security

Revisiting Lattice-based Blind Signatures Again

This IACR ePrint paper by Yi-Fu Lai and Yu Yu breaks the blindness property of a lattice-based blind signature scheme presented at Crypto 2020, which uses a linear hash function framework instantiated over lattices. The authors first identify an overlooked bug in the scheme's original blindness security proof, then construct a concrete attack under an honest-key, honest-but-curious signer model by exploiting correlations between leaves of the scheme's tree structure, and discuss how the construction can be repaired.

Yi-Fu LaiYu YuCrypto 2020

otherΒ· Added 8 Oct 2026, published 7 Oct 2026

x.comthread🧠 AI

Alhaji Premium Man (@softhardguy) on X

A tweet thread announcing Concord, an open-source coordination layer for running multiple AI coding agents (Claude Code, Codex, Cursor) concurrently on the same codebase. Agents claim files before editing so overlapping edits trigger warnings, and the tool lets agents message each other across the different coding-agent harnesses, addressing the conflict problem that appears once three or more agents work in parallel.

Claude CodeCodexCursor
Concord

coding-agents, agentsΒ· Published and added 7 Oct 2026

aws.amazon.comarticleπŸ›‘οΈ Security

Improving SPIRE security and resiliency with AWS managed services

AWS Security Blog walkthrough on hardening SPIRE (the SPIFFE Runtime Environment) in production by replacing its default self-managed components with AWS managed services: AWS KMS for SVID signing keys, Amazon Aurora PostgreSQL as the datastore, AWS Private CA as the upstream certificate authority, Amazon S3/CloudFront for trust bundle distribution, AWS Secrets Manager for delivering SVIDs to serverless/container workloads, and Amazon Verified Permissions (Cedar policies) for fine-grained SPIFFE-ID-based authorization. It addresses operational concerns like key custody, datastore resiliency, PKI integration, and offline identity validation, and links to a GitHub reference deployment and a SPIFFE/SPIRE-on-AWS workshop.

AWSKubernetesPostgreSQL+2

Cloud & Infra, Identity & AccessΒ· Added 7 Oct 2026, published 6 Oct 2026

unit42.paloaltonetworks.comarticleπŸ›‘οΈ Security

Blinder Tunnel Campaign Targets Iraqi Infrastructure

Unit 42 details "Blinder Tunnel," a campaign by Iranian state-aligned actor CL-STA-1178 (linked to Elastic's "The Shelby Strategy") that impersonated Dubai Airports recruiters to deliver a trojanized Visual Studio coding-challenge archive against an Iraqi critical-infrastructure target, with related activity against UAE aviation and Israeli entities via Google Drive-themed phishing. The report dissects a three-stage infection chain (weaponized .csproj MSBuild target abuse, AppDomainManager hijacking to disable ETW, and DLL sideloading into RuntimeBroker.exe) that deploys ShelbyLoader V2, the ShelbyC2 V2 RAT, PsProxy.dll (in-memory PowerShell execution), and Blackwood, a custom Chisel-based tunneling loader; C2 abuses GitHub's API and GitHub Issues as a dead-drop fallback, and attribution rests on an Iranian-hosted IP, Persian-domain infrastructure overlap, and MP3 metadata pointing to MusicDel.ir. Includes full IOCs (hashes, IPs, phishing domains, registry keys).

GitHub.NETPowerShell+3
CL-STA-1178ShelbyLoader V2ShelbyC2 V2+16

Threat Intel, Malware & REΒ· Published and added 6 Oct 2026

Showing 30 of 73

Show more