 Mets Muse Wonder. evaluated against the Endor Labs Agent Security League | Endor Labs
Endor Labs adds Meta's Muse Code with the Muse Wonder model to its Agent Security League. It scores 91.6% FuncPass (first) but 25.1% SecPass (seventh), a 27.4% SecPass-to-FuncPass ratio. A manual spot check exposed a blind spot in the anti-cheating pipeline. Endor Labs closed it with two other extensions, then re-scored all entries. The top twelve places held, and the changes sat in the bottom half.
 endorlabs.comarticlePublished and added 3 Nov 2026🛡️ Security
 WorkOS says attacker used ARTEX AI to breach internal sales app
WorkOS disclosed that on 30 October 2026 an attacker accessed an internal sales application and exposed CRM contacts, account histories and summaries of customer communications. Founder Michael Grinich said the attacker used the ARTEX AI pentesting framework, seen in user agents 'artex-enrich/1.0' and 'norma/0.4'. WorkOS says no production services or app data were affected. The article links ARTEX AI to Vapor Panda (CrowdStrike) and a DIVD intrusion.
 bleepingcomputer.comarticlePublished and added 3 Nov 2026🛡️ Security
- CISA Adds One Known Exploited Vulnerability to Catalog
CISA added CVE-2026-119977, a WordPress Core time-of-check time-of-use (TOCTOU) race condition, to its Known Exploited Vulnerabilities Catalog on 3 November 2026, citing evidence of active exploitation. The alert restates BOD 26-04, which requires Federal Civilian Executive Branch agencies to prioritise fast remediation of KEV entries on exposed assets and to check for prior compromise. It also links the KEV nomination form.
 cisa.govadvisoryPublished and added 3 Nov 2026🛡️ Security
 Crypto Docs Host GitBook Hit by AI Agent Security Breach, Urges Users to Rotate Keys
GitBook disclosed an attack it calls "sophisticated, highly targeted" and AI-agent-assisted. The attacker gained unauthorized access to infrastructure credentials at 7 p.m. CET on 2 November 2026. Potentially exposed data includes API tokens, integration secrets, Git Sync secrets and AI assistant questions. GitBook revoked personal API tokens and told customers to rotate credentials and re-authenticate MCP. PancakeSwap moved its docs off GitBook. GitBook has not said how the agents were used.
 decrypt.coarticlePublished and added 3 Nov 2026🛡️ Security
 Google: LLMjacking attacks rack up $1 million in cloud AI charges
LLMjacking is the abuse of stolen API keys and exposed LLM endpoints to run fraudulent model calls. Google's GTIG and Mandiant report charges above $100,000 per day and up to $1,000,000 cumulatively at some victims. Attackers resell access through "LLM mixers" such as Jet Night and newapi[.]pro; cluster UNC6993 and LiteLLM CVE-2026-40217 exploitation are noted, with IAM, MFA, spending-limit and logging advice.
bleepingcomputer.comarticlePublished and added 3 Nov 2026🛡️ Security GitBook Revokes All Personal API Tokens After Breach
GitBook revoked all personal API tokens after a breach of its documentation platform. The company says the attack used AI agents and may have exposed integration credentials and questions submitted by documentation visitors. The fetched page held only the headline and subhead, so the intrusion method, timeline and scope are not available.
 thedefiant.ioarticlePublished and added 3 Nov 2026🛡️ Security
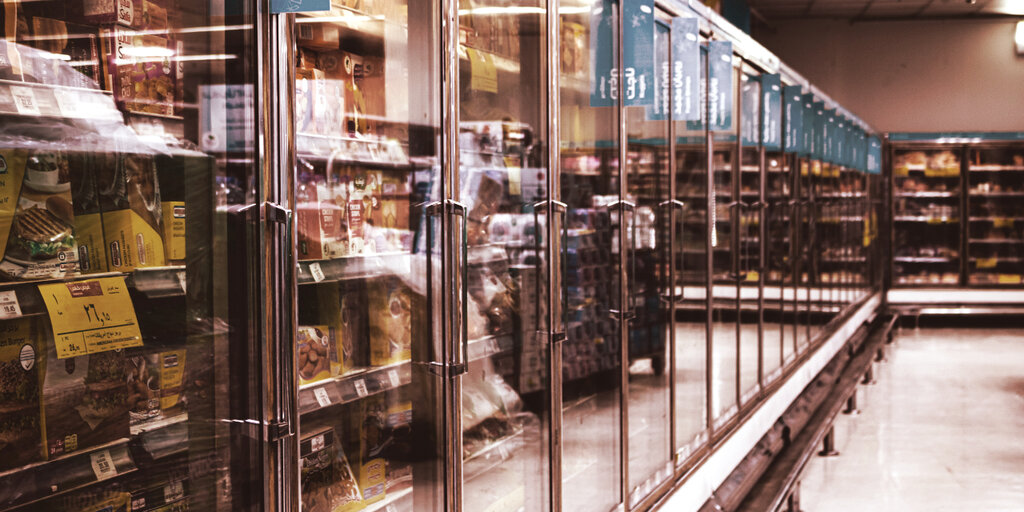 Epidemic of Hacked Freezers Spreads Across Europe
Decrypt reports that about 700 of France's 10,000 supermarkets were hit in October 2026 and that stores in nine more countries saw freezers heat up overnight, with Estonian units pushed to 50°C. CERT-FR links the compromises to Danfoss and Copeland remote control modules and says attackers forced continuous defrost cycles. Claroty found 2,765 Danfoss AK-SM 800A controllers exposed online in August; the exploited weakness is still unknown.
decrypt.coarticlePublished and added 3 Nov 2026🛡️ Security UK Says AI-Powered Ransomware Attack on Critical Infrastructure 'Highly Likely' by 2028
Decrypt reports the UK NCSC's State of the Cyber Nation report of 3 November 2026. It says critical infrastructure should expect a ransomware attack involving AI-powered malware by 2028. NCSC chief Richard Horne argues AI exposes long-tolerated vulnerabilities at scale. The piece lists UK funding (£60 million Cyber Shield, £70 million exposure centre) and cites Google's May 2026 AI-assisted zero-day finding and a Cambridge forum study.
decrypt.coarticlePublished and added 3 Nov 2026🛡️ Security- Binance says hackers used fake job interview, internal AI tool in $6.3 billion breach
The Block reports Binance's initial incident report, published 3 November 2026, on a theft of more than $6.3 billion. Binance says a fake job interview compromised an employee and an internal AI tool exposed wallet-signing systems. Binance says it froze or intercepted about $2.85 billion and replenished 98% of impacted assets. Withdrawals reopened in phases from 4 a.m. UTC across BSC, Ethereum, Solana and other networks. The FBI links the attack to North Korea, which denies it. The available text gives no deeper technical detail.
 theblock.coarticlePublished and added 3 Nov 2026🛡️ Security
 Open-Source Intelligence (OSINT): Doing GeoOSINT and Finding Locations with Azimut
Azimut is a local, open-source GeoOSINT tool (v0.3.3, Linux, Windows, macOS) that keeps case evidence in one folder and runs in the browser at 127.0.0.1:8477. The walkthrough tests a Yosemite photo from Wikimedia using the Horizon 3D skyline overlay, the beta Find mode (hand-drawn skyline, search area up to 10,000 km2), sun path display and exportable proof collages. Results need manual verification.
 hackers-arise.comarticlePublished and added 3 Nov 2026🛡️ Security
- Introducing Zero Wire, a hub for investigating critical Internet vulnerabilities
Zero Wire is a public vulnerability intelligence feed in the security section of Cloudflare Radar. Each briefing covers one critical CVE in Internet-facing software: who should investigate, what to do, evidence links such as the CISA Known Exploited Vulnerabilities catalog, and WAF context. Briefings include a prompt for an AI agent to run a read-only exposure assessment; the first example covers php2shell.
 blog.cloudflare.comarticlePublished and added 3 Nov 2026🛡️ Security
 The cryptography behind electronic voting (and why paper ballots are still essential)
Explains how Helios and ElectionGuard use threshold-shared exponential ElGamal, zero-knowledge proofs, Benaloh challenges and hash-chained ballot commitments to protect voter privacy and give end-to-end verifiability. It covers compromised voting clients and backends, software independence, and the 2018 National Academies report against internet voting. It concludes that cryptography supplements, but cannot replace, paper ballots in general elections.
 blog.trailofbits.comarticlePublished and added 3 Nov 2026🛡️ Security
 Harvard University data breach exposed info of 851,000 accounts
Harvard University's Alumni Affairs and Development systems were breached in November 2025, and Have I Been Pwned confirmed 850,500 accounts exposed. ShinyHunters claimed the attack and leaked a 1.1GB archive in February 2026 after Harvard refused to pay. Exposed data includes names, emails, birth dates, phone numbers, addresses and donation details, but no SSNs, passwords or payment data. The article also notes a separate Clop claim using an Oracle E-Business Suite zero-day.
bleepingcomputer.comarticlePublished and added 3 Nov 2026🛡️ Security Over 100 European Stores Hit as Supermarket Fridge Attacks Return
Over 100 stores in Belgium, Estonia, Ireland, Luxembourg, the Netherlands and Sweden had fridges forced into defrost mode overnight on 2 to 3 November 2026, after about 700 French supermarkets were hit on 11 to 12 October. Targets were internet-exposed, often end-of-life Danfoss AK-SM/AK-SC and Copeland controllers. Censys counted about 1,000 exposed StoreView interfaces. Lupovis saw default-credential probing from 20 October.
 securityweek.comarticlePublished and added 3 Nov 2026🛡️ Security
- Md Ismail Šojal 🕷️ (@0x0SojalSec) on X
An x64dbg MCP server, published on GitHub by duty1g and shared in an X post by @0x0SojalSec, lets Claude drive the x64dbg Windows debugger. It exposes breakpoints, memory dumps and code stepping as tools for reverse engineering and malware analysis. A reply warns that debugging a sample executes it, so the agent should run in a snapshotted VM with no shared folders or host route, and every command should be logged.
 x.comrepoAdded 3 Nov 2026🧠 AI
- Training activation classifiers for safety and alignment
Training activation classifiers for safety and alignment describes how OpenAI trains lightweight probes on a model's residual stream activations to flag misaligned or policy-violating completions. Probes use an MLP plus QV-attention architecture with an exponential moving average and a rolling softmax objective. They run in streaming mode on the inference engine, have run on all assistant completions since GPT-5.6, and transfer well across post-training checkpoints but less across pre-training checkpoints.
 alignment.openai.comarticlePublished and added 2 Nov 2026🧠 AI
 BTCPay Server warns of hot wallet thefts targeting outdated instances
BTCPay Server, an open-source self-hosted cryptocurrency payment processor, reports attackers draining hot wallets on instances running version 2.4.1 (July 23, 2026) or earlier. Attackers logged in as administrators on versions older than 2.4.2. Users should update to 2.4.7; the exploited flaw is not disclosed. An October 29 critical vulnerability found by Anthropic's Frontier OSS scanner prompted 2.4.7. The August 7 release 2.4.2 had already warned of an exploited LND credential exposure.
bleepingcomputer.comarticlePublished and added 2 Nov 2026🛡️ Security Florida Student Aid Website Hack Puts Data of 4.9 Million People at Risk
The Florida Department of Education (FLDOE) disclosed a breach of its Florida Student Financial Aid website (FloridaStudentFinancialAidSG.org), discovered on 19 October and potentially affecting about 4.9 million people. Exposed data may include names, Social Security numbers, dates of birth, addresses, phone numbers and emails. The entry vector and actor are undisclosed. The article links it to the September FLHSMV driver database breach, which came from compromised police credentials.
securityweek.comarticlePublished and added 2 Nov 2026🛡️ Security Over 1,000 GitLab servers vulnerable to ongoing RCE attacks
CVE-2026-97229 is a maximum-severity integer overflow in GitLab's CI/CD Regular Expression Compiler that lets an unauthenticated attacker run code via a crafted regex in pipeline configuration. GitLab patched it on 12 October 2026 in versions 19.4.2, 19.3.5 and 19.2.8. CISA added it to KEV, and Shadowserver tracks over 1,000 unpatched servers, plus 11,300 exposed to the related CVE-2026-110264.
bleepingcomputer.comarticlePublished and added 2 Nov 2026🛡️ Security Supermarket freezers across Europe hit by second suspected cyber-attack
Guardian report from 2 November 2026 on a second suspected cyber-attack on supermarket refrigeration in Belgium, Estonia, Ireland, Finland, Luxembourg, the Netherlands and Sweden, with temperatures set to 50C. It recaps the earlier French attack on up to 700 shops, which hit mostly Danfoss controllers. SentinelOne and Tributech say the attacks point to sabotage and that many controllers remain internet-exposed and unpatched.
 theguardian.comarticleAdded 3 Nov 2026, published 2 Nov 2026🛡️ Security
 Synology warns of C3RB3R ransomware attacks targeting NAS devices
C3RB3R (Cerber) ransomware is encrypting Synology NAS devices running outdated DiskStation Manager, and Synology issued an advisory urging immediate updates. The attacks exploit a vulnerability patched in December 2024, likely among CVE-2024-10441, CVE-2024-50629 and CVE-2024-10445 from a November 2024 advisory. Victims get a read-me3.txt note and .L0CK3D extension. Shadowserver tracks over 380,000 exposed Synology NAS devices.
bleepingcomputer.comarticlePublished and added 2 Nov 2026🛡️ Security Chainalysis Discloses Data Breach Following AI-Driven Cyberattack
Chainalysis disclosed a data breach in which an external actor used offensive agentic techniques to access its systems and internal tools. Exposed data was non-sensitive customer data: user IDs, full names, email addresses and organization role labels. Investigation content, query results and credentials were not compromised. The company says the incident is unrelated to the $6.36 billion Binance heist, and advises users to enable MFA and watch for password reset prompts. Scope and victim count are undisclosed.
securityweek.comarticlePublished and added 2 Nov 2026🛡️ Security Ivanti patches two more Connect Secure zero-days chained in attacks
Ivanti patched two more Connect Secure zero-days, CVE-2026-111357 (privilege escalation) and CVE-2026-118527 (authenticated file upload), chained with authentication bypass CVE-2026-104935 since at least 1 October 2026. Volexity attributed the chain to UTA0576, which ran no malware, re-exploited the device per command and tampered with logs, evading Ivanti's Integrity Checker Tool. CISA added CVE-2026-104935 to KEV, and Shadowserver tracks over 5,000 exposed instances.
bleepingcomputer.comarticlePublished and added 2 Nov 2026🛡️ Security- Luke The Dev (@iamlukethedev) on X
Hermes, the Nous Research agent framework, shipped 130 merged PRs in October 2026, according to this X recap by Luke The Dev. Main items are a unified gateway runtime, a Desktop and Bot Screen, a bundles and package manager, crash-safe updates and new Claude model entries. Ten PRs cover security: an iron-proxy credential-injection egress firewall for sandboxes, 31 CVEs patched in Python and npm lockfiles, and profile-export and prompt-leak fixes.
x.comthreadAdded 2 Nov 2026🧠 AI  Smarthouse (@localyzapp) on X
A reply by Smarthouse (@localyzapp) on X to a question about the best harness for connecting local models to a Minecraft server. It suggests an MCP server that wraps RCON plus a small agent loop. The main pitfall is block coordinates: expose "/execute if block" as a read tool so the agent can check blocks before placing them, or it will hallucinate terrain.
x.comthreadAdded 2 Nov 2026, published 1 Nov 2026🧠 AI- Chainalysis security breach exposed customer data and raised phishing risk
Chainalysis confirmed on 30 October 2026 that an external actor accessed its systems and internal tools earlier in October, using what it called "offensive agentic techniques". Exposed data covers some customers' names, emails, job titles, user IDs and role labels. Chainalysis says it has found no access to passwords, session tokens or investigation content so far, and customers should expect targeted phishing. Affected-customer counts and the exploited vulnerabilities are not disclosed.
 en.cryptonomist.charticlePublished and added 31 Oct 2026🛡️ Security
 Chainalysis discloses data breach from "offensive agentic techniques"
Chainalysis disclosed a security incident in which an external actor used "offensive agentic techniques" to access internal systems and tools earlier in the month. Exposed customer data includes user IDs, names, email addresses and organizational role labels. The company reports no evidence of access to investigation content, credentials or session tokens, and has shared no details on the vulnerabilities, tools or dwell time. The article also lists other incidents from the same week.
bleepingcomputer.comarticlePublished and added 31 Oct 2026🛡️ Security- Bunny CDN Security Incident
Bunny CDN status-page notice, posted 28 October 2026, about unauthorized access at an infrastructure provider that hosted one bunny.net CDN node in Armenia. Traffic was stopped within 20 minutes and the server wiped. No access to the node was found, but cached content, Pull Zone configs and TLS certificates could have been exposed, so all platform certificates were reissued. Customers with their own certificates should rotate them with new private keys.
 status.bunny.netadvisoryAdded 31 Oct 2026, published 30 Oct 2026🛡️ Security
- CISA Adds Two Known Exploited Vulnerabilities to Catalog
CISA added two Ivanti Connect Secure vulnerabilities to its Known Exploited Vulnerabilities (KEV) Catalog on 30 October 2026, citing evidence of active exploitation: CVE-2026-111357 (missing authentication for a critical function) and CVE-2026-118527 (generation of predictable numbers or identifiers). The alert restates BOD 26-04, which requires federal civilian agencies to remediate KEV-listed flaws on exposed assets and check for prior compromise. It also links the KEV nomination form.
cisa.govadvisoryPublished and added 30 Oct 2026🛡️ Security - PHP2Shell Attacks Root Palo Alto Firewalls but Fail Against WordPress
PHP2Shell (CVE-2026-109618 and CVE-2026-109619) has been exploited for over a week. A China-linked group chained it with the Fragnesia Linux kernel privilege escalation to root at least 25 Palo Alto Networks PAN-OS firewalls with exposed management interfaces. Defiant had seen no confirmed WordPress compromise by 28 October 2026 despite 77,000 requests, and Cato and watchTowr report few successful attackers.
securityweek.comarticlePublished and added 30 Oct 2026🛡️ Security  CISA says max severity GitLab flaw now exploited in the wild
CVE-2026-97229 is a maximum-severity GitLab flaw in the CI/CD Regular Expression Compiler, caused by an integer overflow, that lets unauthenticated attackers run code via a crafted regular expression. CISA added it to the KEV Catalog and ordered federal agencies to patch under BOD 26-04. GitLab fixed it in CE/EE 19.4.2, 19.3.5 and 19.2.8, and Shadowserver tracks about 2,800 exposed CE instances.
bleepingcomputer.comarticlePublished and added 30 Oct 2026🛡️ Security- lee1981 (@lee1981b) on X
CyberForge CVE of the Day #091 covers Progress WS_FTP Server CVE-2026-84295 (unauthenticated administrator-credential exposure, CVSS 10.0) and CVE-2026-90868 (conditional OS command and argument injection, CVSS 9.9, low privileges). Fixed floors are 2024.0.7/9.0.7 and 2025.0.4/10.0.4; 2024.0.6/2025.0.3 fix only the first. It gives KEV, EPSS and SSVC status, six SOC checks, and Windows 4688 evidence queries.
x.comadvisoryAdded 2 Nov 2026, published 30 Oct 2026🛡️ Security  Anthropic security breach exposed salaries and messages, not model weights
Anthropic security incident in which researchers from the startup Cathedral reached Anthropic's commercial, HR and IT systems through vulnerable third-party administrative applications. Exposed data included salaries, job offers, meeting transcripts and Slack messages; Anthropic says customer prompts, source code and model weights were not accessed. Anthropic cut access the same day and kept the apps disabled until vendors patched. The companies dispute whether Cathedral reported all its activity.
en.cryptonomist.charticlePublished and added 30 Oct 2026🛡️ Security Japan Airlines suffers third-party data breach exposing passenger info
Japan Airlines disclosed that unauthorized access to Amadeus's Passenger Service System, between 10 August 2023 and 23 September 2026, exposed data on about 92,000 customers. Roughly 2,000 also had emails, phone and passport numbers exposed. ANA, Asiana Airlines and Korean Air are also reported as affected. Amadeus had announced a booking display vulnerability on 1 October 2026 and has not given the full scope.
bleepingcomputer.comarticleAdded 30 Oct 2026, published 29 Oct 2026🛡️ Security Rekt - SingularityNET - Rekt
SingularityNET exploit (19 September 2026): attackers with signing authority exposed through a cloud infrastructure breach drained 8.72M FET from the Ethereum bridge converter, then minted about 2.3 billion AGIX, NTX, WMTX and CGV. Rekt's transaction-level reconstruction puts gross liquid proceeds near $2.29M, not the $16.77M headline, and traces laundering via Chainflip, Baltex and THORChain. It notes conversionIn() skipped checkLimits() and trusted a single EOA signature.
 rekt.newswriteupAdded 29 Oct 2026🛡️ Security
 Android security checklist: theft of arbitrary files | Oversecured Blog
Oversecured's Android security checklist on arbitrary file theft from an app's private storage. It covers implicit intents (PICK, GET_CONTENT) returning file:// or content:// URIs, SEND/SEND_MULTIPLE share activities, exported and non-exported FileProviders, path traversal via Uri.getLastPathSegment, WebView, and local NanoHTTPD servers. Each case has vulnerable code, an attacker PoC and fixes such as /proc/self/fd path checks and narrow files-path entries.
 oversecured.comarticleAdded 29 Oct 2026🛡️ Security
 SDK security in mobile apps: the attack surface your team didn
Oversecured guide to SDK security in mobile apps, built around Microsoft's April 2026 disclosure of an intent redirection flaw in EngageLab's EngageSDK (50 million installs, fixed in 5.2.1). It covers SDK attack surfaces (exported components, WebViews, deep links, hardcoded secrets, payment crypto), a canhub image cropper file-overwrite example, why source-only SAST misses SDK code, and MASVS and PCI DSS expectations.
oversecured.comarticleAdded 29 Oct 2026🛡️ Security What changed when mobile security stopped being theoretical
An Oversecured Head of Engineering, coming from 20 years of web work, describes four mobile security risks that became concrete after seeing real production apps. These are old vulnerable binaries that stay installed after a fix, secrets embedded in client code, Keychain/Keystore guarantees that are weaker than assumed with tokens leaking via logs, and deep links or exported components acting as public endpoints. It ends with advice: test the shipped artifact, verify the full data lifecycle, and build server-side containment.
oversecured.comarticleAdded 29 Oct 2026🛡️ Security What are shell vulnerabilities? PHP2Shell, Node2Shell (HTTP2Shell), React2Shell and Log4Shell explained
Explainer on "shell" vulnerabilities, the -Shell naming for RCE flaws that began with Log4Shell (CVE-2021-44228). It compares memory-corruption bugs (PHP2Shell, CVE-2026-109618 and CVE-2026-109619; Node2Shell, CVE-2026-111497, in the Brotli decoder) with design-flaw bugs (Log4Shell, React2Shell, CVE-2025-55182). It covers shared traits, exposure through inherited components, and Brotli patch status across runtimes and distributions.
 aikido.devarticleAdded 30 Oct 2026, published 29 Oct 2026🛡️ Security
 Threat Brief: Critical Vulnerabilities in PHP: CVE-2026-109618, CVE-2026-109619 (Updated October 29)
Unit 42 threat brief on PHP2Shell, two PHP remote code execution flaws, CVE-2026-109618 and CVE-2026-109619 (CVSS 4.0 9.2), both caused by longjmp() error handling that leaves memory uninitialized or freed. Cortex Xpanse counted over 22.6 million exposed instances. The 29 October 2026 update says attackers chained PHP2Shell with a Linux kernel privilege escalation against internet-exposed PAN-OS management interfaces. An earlier 23 October claim of post-compromise activity was retracted on 25 October.
 unit42.paloaltonetworks.comadvisoryAdded 30 Oct 2026, published 29 Oct 2026🛡️ Security
 TextSeal2: Distortion-Free LLM Watermarking with Copula Mixing and Memoryless Races
TextSeal2 is a distortion-free LLM text watermark that merges two or more keys into one virtual key and couples it to fresh noise through AutoMark's Gaussian copula. Under speculative decoding it verifies keyed drafts with an extra exponential race, so output matches the target model and acceptance rate is unchanged. On three LLMs at a 10^-3 false-positive rate, it detects 8 to 22 points more 100-token answers than TextSeal.
 arxiv.orgpaperAdded 31 Oct 2026, published 29 Oct 2026🛡️ Security
- TextSeal2: Distortion-Free LLM Watermarking with Copula Mixing and Memoryless Races
TextSeal2 is a distortion-free watermark for LLM output that keeps its signal under speculative decoding. It merges two or more keys into one virtual key coupled to fresh noise through AutoMark's Gaussian copula, and verifies drafts with an extra exponential race. On three LLMs it detects 8 to 22 points more 100-token answers than TextSeal at a 10^-3 false-positive rate.
arxiv.orgpaperAdded 31 Oct 2026, published 29 Oct 2026🧠 AI - Quasi-polynomial time algorithms for block basis reduction of linear codes
Kolesnikov and Novoselov give block basis reduction (BKZ) algorithms for linear codes that need polynomial or quasi-polynomial numbers of calls to a minimum weight codeword oracle at fixed block size. The earlier Ghentiyala and Stephens-Davidowitz bounds are exponential. The paper adds a truncated BKZ and a DeepBKZ variant, with an implementation for block sizes 2 to 24 and approximation-factor estimates on random codes.
 eprint.iacr.orgpaperAdded 31 Oct 2026, published 29 Oct 2026🛡️ Security
 New Cisco firewall zero-day exploited to crash SSL VPN devices
CVE-2026-76418 is a high-severity denial-of-service zero-day in Cisco ASA and Threat Defense (FTD) software, exploited in the wild in October 2026. Unauthenticated attackers send a crafted request to the SSL VPN (webvpn) when secondary authentication is set on a tunnel group, causing a device reload. Cisco offers no workaround besides disabling secondary authentication on tunnel groups. Shadowserver sees over 51,000 exposed ASA SSL VPN devices.
bleepingcomputer.comarticleAdded 30 Oct 2026, published 29 Oct 2026🛡️ Security Wagyu Confirms Data Leak Exposing Monero Swap Records
Wagyu, a Monero swap service, confirmed a data leak after Hudson Rock found 4,580 orders in exposed records. The records link public-chain deposit transactions to Monero destination addresses and client IP addresses, which undoes the privacy a swap into Monero is meant to give. The fetched page held only the headline and subhead, so the cause, timeline and remediation are not covered.
thedefiant.ioarticlePublished and added 29 Oct 2026🛡️ Security- REALM: Identifying Minimal Task Assets for LLM Agents
REALM (Required Execution Assets Linked to a Mission) is an approach to applying least privilege to LLM agents by identifying the assets a task needs, including ones discovered at runtime. It models assets as Dependency Graph nodes, separates discovering an asset from authorizing it, and exposes resource-bound Partial APIs inside a Task Container. On AgentDyn with qwen3.5-flash, attack success rate falls from 16.6% to 0.2%, with 40.0% task completion on clean tasks and 36.4% on injected cases.
arxiv.orgpaperAdded 31 Oct 2026, published 29 Oct 2026🛡️ Security  Node2Shell: Reproducing CVE-2026-111497 in the Node.js Brotli decoder
Node2Shell is Datadog Security Labs' analysis of CVE-2026-111497, an out-of-bounds write in the Google Brotli 1.2.0 decoder, fixed in Node.js 22.23.4, 24.22.1 and 26.12.1 on 21 October 2026. It explains the unchecked return value in DecodeBlockTypeAndLength(), the read and write primitives, and why code execution is still engineering effort. It lists inbound and outbound exposure paths, behavioral detections and what WAFs miss.
 securitylabs.datadoghq.comwriteupPublished and added 29 Oct 2026🛡️ Security
 Leak Exposes 41,000 Homeland Security Workers–Including Undercover ICE Agents
Icepick is a leaked archive of records on more than 41,000 Department of Homeland Security employees and contractors, published by Distributed Denial of Secrets in 2026 and said to come from DHS's Okta login system. WIRED's analysis covers CBP, ICE, HSI, USCIS and CISA staff, plus over 55,000 permission groups that reference undercover programs, Palantir Falcon, PenLink, Signal and Mobile Fortify. Okta says it has no evidence of compromise.
 wired.comarticleAdded 29 Oct 2026, published 28 Oct 2026🛡️ Security
 Eddy (@ieddysun) on X
Expo's official skills package gives AI coding agents scoped instructions for building Expo apps. One command, npx skills@latest add expo/skills --skill '*', installs it for Cursor, Copilot and Windsurf, while Claude Code and Codex use their plugin marketplaces. Skills include expo-router, expo-animation, expo-upgrade and eas-update. The Expo MCP server adds live docs lookup, compatible dependency installs, EAS build monitoring and simulator screenshots.
x.comthreadAdded 29 Oct 2026, published 28 Oct 2026🧠 AI- CISA Adds Two Known Exploited Vulnerabilities to Catalog
CISA alert of 28 October 2026 adding two vulnerabilities to the Known Exploited Vulnerabilities Catalog on evidence of active exploitation: CVE-2026-41709 (Broadcom VMware ESX insufficient logging) and CVE-2026-46300 (Linux kernel missing variable initialization). It restates BOD 26-04, which requires federal civilian agencies to prioritize fast remediation of KEV CVEs on exposed assets and to check for prior compromise. It also links the KEV nomination form.
cisa.govadvisoryAdded 29 Oct 2026, published 28 Oct 2026🛡️ Security - Laban (@lunkertw) on X
An X post summarising five AI items: Google DeepMind's Gemini 4 Carbon (88.2% SEC-bench Pro, 54.8% ExploitGym, 71.0% CWE-bench, 59 on Artificial Analysis Intelligence Index v5.0), Ed Zitron's critique of Anthropic's S-1, a Utah Claude Code pilot, and the repos beenuar/AiSOC and expo/skills. In the Utah pilot, 34 developers in 10 agencies took part over four weeks, 80% had a working setup within 30 minutes, and 71% saved over 20 hours. It gives short summaries and links, not primary analysis.
x.comthreadAdded 29 Oct 2026, published 28 Oct 2026🧠 AI  Bithumb Says Hackers Accessed Internal System, Leaking Personal Data
Bithumb, South Korea's second-largest crypto exchange, said an outside party accessed its internal mobile groupware system and leaked personal data. Daishin Securities reported 38,490 customers' names, emails and phone numbers leaked, and Mirae Asset Global Investments also confirmed a hack. Coinbase vendor Amplitude exposed contact data the same day. Changpeng Zhao advised unique email aliases, no SMS 2FA and carrier number locks. The access method is not disclosed.
decrypt.coarticlePublished and added 28 Oct 2026🛡️ Security Coinbase Customer Data Hit in Analytics Vendor Breach, Funds ‘Not Impacted’
Coinbase said on 28 October 2026 that a security incident at analytics vendor Amplitude exposed contact data of a "small subset" of its customers. Coinbase reports no unauthorized access to its own systems and no impact on funds. It gave no counts, data types or dates. The article recalls the May 2025 bribed-support-agent breach (69,461 customers) and the 2025 Trezor/ShipMonk exposure.
decrypt.coarticlePublished and added 28 Oct 2026🛡️ Security- Session-Bound Behavioral Watermarking for Autonomous LLM Agents
AgentAnchor is a session-keyed behavioral watermark for attributing LLM agent trajectory logs to an owner. It derives per-step keys from a secret key, a fresh public session ID and semantic observation states, and embeds parity evidence through a KL-bounded exponential tilt. The paper formalizes learned cross-session forgery, and a trusted verifier checks disputed logs using wrong-key calibration and abstention.
arxiv.orgpaperAdded 30 Oct 2026, published 28 Oct 2026🛡️ Security - Session-Bound Behavioral Watermarking for Autonomous LLM Agents
AgentAnchor is a session-keyed behavioral watermark that lets an agent owner prove ownership of a trajectory log. Each step key comes from a secret key, a fresh public session identifier and semantic states of recent observations. Parity evidence is embedded through a KL-bounded exponential tilt of action choices. A trusted verifier checks disputed logs without rerunning the agent, using wrong-key calibration and abstention. The paper also formulates a learned cross-session forgery threat.
arxiv.orgpaperAdded 30 Oct 2026, published 28 Oct 2026🧠 AI - CISA Adds Two Known Exploited Vulnerabilities to Catalog
CISA alert of 27 October 2026 adding two vulnerabilities to the Known Exploited Vulnerabilities (KEV) Catalog on evidence of active exploitation: CVE-2026-48356, an unrestricted upload of a dangerous file type in Adobe Commerce and Magento, and CVE-2026-111497, an unchecked return value in Google Brotli. It restates BOD 26-04, which makes federal civilian agencies prioritise KEV flaws on exposed assets and check for prior compromise. No technical detail or IOCs are given.
cisa.govadvisoryAdded 29 Oct 2026, published 27 Oct 2026🛡️ Security  Bitcoin Wallet Maker Keystone Pulls Devices as Stolen Key Opens Door to Fakes
Keystone, a Bitcoin hardware wallet maker, will destroy 18,835 unsold devices and has halted shipping after an attacker obtained the permanent WebAuth factory key used to verify genuine hardware, detected October 20, 2026. The key could let counterfeit wallets pass authentication. The breach also exposed 25,964 Shopify buyer records (2024 to 2026) that should have been erased under a 180-day policy; recovery phrases and private keys were not involved.
decrypt.coarticlePublished and added 27 Oct 2026🛡️ Security- Pentesting: Twelve Caesars – Community Tools for Offensive Security
Hackers Arise walks through four tools from Praetorian's "12 Caesars" open-source release: Titus (secret scanner with 487 rules and credential validation), Nerva (fingerprints 170 protocols), Brutus (Hydra alternative covering 40+ protocols) and Julius (fingerprints 60+ LLM services such as Ollama). It shows download and run commands in a Kali lab and how the tools chain together. The tools are Go single binaries; the post notes an exposed Ollama on port 11434 allows unauthenticated model use.
hackers-arise.comarticlePublished and added 27 Oct 2026🛡️ Security  OpenAI Proves ETH Is False, and Crypto Twitter Has Questions
Decrypt reports that OpenAI published a 67-page paper (dated 17 October 2026, revised 25 October) claiming its AI found a deterministic subexponential-time algorithm for counting 3-SAT solutions, which would refute the Exponential Time Hypothesis. The proof was formalized in Lean. Impagliazzo, Paturi and Ryan Williams are reviewing it independently and say this is not certification. Anthropic posted a Claude-credited 3-SAT paper on 26 October.
decrypt.coarticlePublished and added 27 Oct 2026🧠 AI PHP2Shell: Exploitation Attempts and Remediation Trends
Wiz Research follow-up on PHP2Shell (CVE-2026-109618, CVE-2026-109619) after the 21 October 2026 disclosure. Honeypot data shows two variants of an open source exploit kit, one stopped by post_max_size and the other by failed memory leaks and worker pinning, plus PHP2Shell-branded tools that rely on session poisoning and LFI. Daily exposed vulnerable machines fell about 67%.
 wiz.ioarticlePublished and added 27 Oct 2026🛡️ Security
 Crypto wallet maker Keystone to destroy almost 19,000 devices after security breach
Keystone, a hardware wallet maker, will destroy 18,835 unsold devices after an attacker used a flaw in a third-party data monitoring tool to breach its website on 20 October 2026. The breach exposed 25,964 buyer records and a factory-set authenticity key that cannot be changed, so counterfeit wallets could pass checks. An automated deletion tool had failed unnoticed against the 180-day retention policy. The report also covers a Foundation breach with 23,000 phishing attempts.
 coindesk.comarticlePublished and added 27 Oct 2026🛡️ Security
 Proof of One: one-person-one-identity polling with encrypted ballots — design and reference code, requesting critical review
Proof of One is an open-source design for polls with one verified human per identity and unlinkable ballots. Enrolment proves in zero knowledge that an ICAO 9303 passport chip was signed by a trusted signer, plus an enclave face match. Voting uses threshold exponential ElGamal on Baby Jubjub with Groth16 proofs, and tally uses a GJKR DKG with a 7-day challenge window. The author, who is pseudonymous, discloses that AI agents drafted most of it and asks for critique of unlinkability, circuit completeness and certificate trust.
 ethresear.chthreadPublished and added 27 Oct 2026🛡️ Security
 Falcon Key Recovery from Joint Sampler Leakages
 is an ePrint paper presenting a power side-channel attack on Falcon and FN-DSA that fuses three SamplerZ leakages (exponent class of the center, sign bit, proposal magnitude). It turns them into slab and halfspace constraints solved by softplus interval regression, with no LLL or BKZ. On PQClean Falcon-512 (ARM Cortex-M4) it recovered all 50 keys with at most 34 signatures; on c-fn-dsa it recovered 38 of 50 keys within 200 signatures.
eprint.iacr.orgpaperAdded 28 Oct 2026, published 27 Oct 2026🛡️ Security- AGTP (@AGTPinsights) on X
AGTP's X thread summarizes Meta's Muse Spark 1.3 Evaluation Report. Prompt injection was tested on Exponential Security Labs' RepoInject v1 and BrowserInject v1 and on Gray Swan's IPI Arena, with robustness said to be on par with GPT-5.6 Sol. It also covers chain of thought controllability evals, PostTrainBench under Loss of Control, and Handshake's pre-release human red teaming. It notes the Midas Project's criticism of Muse Wonder's missing safety report.
x.comthreadAdded 27 Oct 2026, published 26 Oct 2026🛡️ Security - AGTP (@AGTPinsights) on X
Thread summarizing Meta's Muse Spark 1.3 Evaluation Report, the safety write-up for the model released on September 2, 2026. It covers prompt-injection results on Exponential Security Labs' RepoInject v1 and BrowserInject v1 and Gray Swan's IPI Arena, chain-of-thought controllability evals, PostTrainBench under Loss of Control, and Handshake's human red teaming. It also notes The Midas Project's criticism that Muse Wonder still has no safety report, and the Muse Spark Open rollout (816B total, 42B active parameters).
x.comthreadAdded 27 Oct 2026, published 26 Oct 2026🧠 AI  Cross-request KV cache exposure in the GLM-5.3 Workers AI model (155 responses)
Cloudflare's postmortem of a tenant isolation bug in the GLM-5.3 model on Workers AI, active 27 August to 9 September 2026. Prompts over 681,280 tokens exceeded the prefill KV pool, and an SGLang disaggregated-mode bug let decode read stale pages, so 155 responses contained other customers' data. It covers the timeline, config and engine fixes (SGLang v0.5.22), and recommendations for operators.
blog.cloudflare.comwriteupAdded 27 Oct 2026, published 26 Oct 2026🧠 AI- Cross-request KV cache exposure in the GLM-5.3 Workers AI model (155 responses)
Cloudflare postmortem of a tenant isolation failure in the GLM-5.3 Workers AI model (27 August to 9 September 2026), in which 155 responses to prompts over 681,280 tokens contained other customers' data. Root cause was a KV pool smaller than the 1,048,576-token context window, combined with an SGLang bug in disaggregated prefill/decode mode that let decode read stale KV pages. It lists the fixes (SGLang v0.5.22 patches), hardening steps and operator recommendations.
blog.cloudflare.comwriteupAdded 27 Oct 2026, published 26 Oct 2026🛡️ Security - CISA Adds Two Known Exploited Vulnerabilities to Catalog
CISA added two PHP vulnerabilities to its Known Exploited Vulnerabilities Catalog on 26 October 2026: CVE-2026-109618 (memory corruption) and CVE-2026-109619 (stale internal request state). It also updated its PHP alert on critical vulnerabilities requiring immediate patching. The alert restates BOD 26-04, which requires federal civilian agencies to prioritize fast remediation of KEV CVEs on exposed assets and to check for prior compromise.
cisa.govadvisoryAdded 29 Oct 2026, published 26 Oct 2026🛡️ Security  Keystone Breach Widens as Attacker Grabs Its Device Authentication Key
Keystone, a hardware wallet maker, disclosed on 26 October 2026 that the attacker behind its 20 October store breach also took the WebAuth device authentication key. The key is written at the factory and cannot be changed, so Keystone is scrapping 18,835 devices. The breach came through a third-party monitoring tool on its Shopify site and exposed 25,964 buyer records. Old-key units received after 20 October may be counterfeit.
 bankless.comarticlePublished and added 26 Oct 2026🛡️ Security
 Genesys Hack Exposes Customer Data From Internal Systems
Genesys, a customer experience and call center software provider, disclosed on October 19, 2026 that attackers accessed internal business systems, including a learning management system and a CRM environment. Exposed data likely includes names, phone numbers, business emails, job titles and account details. Genesys Cloud, Engage and Engage Cloud were not affected. The recently emerged ScarlettGroup claimed the attack on its leak site, and Genesys declared the incident contained on October 23.
securityweek.comarticlePublished and added 26 Oct 2026🛡️ Security- Then there is prompt injection, a malicious email, ...: The Wild Wide West of OpenClaw Agentic System Security
An empirical study of security concerns in the OpenClaw AI personal assistant framework, using 25K+ posts from 13 subreddits (162 security-relevant) and 358 security-tagged GitHub issues (180 retained). It maps 521 CWE instances across 59 weakness types, concentrated in access control, sensitive-data exposure, injection and unsafe execution. It extracts 543 practitioner mitigations into seven strategies and reconstructs a sensitive-data exposure path with dummy secrets.
arxiv.orgpaperAdded 28 Oct 2026, published 26 Oct 2026🛡️ Security  Keystone wallet breach exposes order data, not wallet credentials
Keystone, a hardware-wallet maker, disclosed on 24 October 2026 that customer order data was stolen from its Shopify-backed store. Names, contact details, delivery addresses and purchase records were exposed, but not payment data, recovery phrases or keys. The article covers the support-impersonation and physical-safety risks, a retention-policy inconsistency, and similar leaks at Trezor (80,689 customers) and SafePal (about 39,798). Keystone has not given the number affected or the vulnerability.
en.cryptonomist.charticlePublished and added 26 Oct 2026🛡️ Security Bitcoin wallet bug let rogue servers steal funds when users tried to speed up payments
Electrum, a Bitcoin software wallet, disclosed on 24 October 2026 a flaw where malicious servers swapped pending transactions for fake ones with invalid signatures that the wallet did not check. When users chose Replace-by-Fee to raise the fee, Electrum signed a valid replacement paying the attacker, and at least one user lost funds. Version 4.8.3 adds signature checks; users of only trusted or self-run servers were not exposed.
coindesk.comarticlePublished and added 26 Oct 2026🛡️ Security- Subexponential Algorithms for LWE via Rejection Sampling on Superlattices
Subexponential Algorithms for LWE via Rejection Sampling on Superlattices is an ePrint paper by Ligeng Fan, Changpeng Shao, Hongbo Li and Dingkang Wang. It extends the Ducas, Engelberts and Loyer superlattice framework to give a provable classical search-LWE algorithm for prime q in [n^2, 2n^2], using m=4n samples and time and space exp(O(n/ln ln n)). A second variant runs in 2^((1/2+o(1))n/ln R) for general parameters. It resolves a gap left by Kirchner and Fouque.
eprint.iacr.orgpaperPublished and added 26 Oct 2026🛡️ Security - Working with academic communities to build scientific understanding
OpenAI describes three results its models produced in October 2026: a proof of the local smoothing conjecture in all dimensions, a disproof of the Exponential Time Hypothesis, and an existence proof for four-dimensional Yang–Mills and QCD. Each is shepherded by external expert groups under four principles (transparency, no academic credit, recognition, independence). Lean proofs and AI writeups for two results are on GitHub. All claims are OpenAI's.
 openai.comarticlePublished and added 26 Oct 2026🧠 AI
 Proton Flock Camera Map
 is a ZIP-code search map of Flock license plate reader locations. Its data comes from researcher Joshua Michael, who found in November 2025 that Flock's servers exposed an access token to anyone without login, and published his map in December. His inventory lists over 170,000 cameras and 130,000 other devices, about 40% above Flock's cited 120,000 cameras. The page also covers what Flock records and cites a Washington Post review of officer misuse.
 proton.metoolAdded 26 Oct 2026, published 25 Oct 2026🛡️ Security
- Dan Kornas (@DanKornas) on X
jshook is an open-source (AGPL-3.0) search-first reverse-engineering workspace for AI agents, exposed over MCP. It drives Chromium or Camoufox through CDP, captures WebSocket traffic, offers HTTP, GraphQL and Burp Suite helpers, deobfuscates JavaScript, rebuilds source maps and disassembles WebAssembly. Tool profiles start small and expand to workflow or full sets; hot-reload plugins and declarative workflows extend it.
x.comtoolAdded 28 Oct 2026, published 25 Oct 2026🛡️ Security - Keystone customers say breach exposed data the hardware wallet maker promised to delete
Keystone, a hardware wallet maker, disclosed on 25 October 2026 that an attacker accessed its Shopify-based store, detected 20 October and confirmed 23 October. Customer names, contact details, shipping addresses and order details were taken. Keystone says no payment data, recovery phrases or keys were exposed. Customers on X say their data was held despite a 180-day deletion pledge. The piece lists 2026 leaks at Trezor, SafePal and Ledger.
theblock.coarticlePublished and added 25 Oct 2026🛡️ Security  OVHcloud CLI Compromised via GitHub Release Swap: Detonating the Real GlassWorm Loader and What We Found
Analysis of the 19 October 2026 swap of binaries on five ovh/ovhcloud-cli GitHub releases (v0.11.0 to v0.15.0), live 94 minutes. StepSecurity rebuilt the attacker's binary, detonated the recovered GlassWorm preinstall.js loader against a controlled Solana dead drop, and found install.sh never exposed arm64 Linux, Homebrew was safe, and `ovhcloud version` showing "undefined" identifies the swapped build. Includes IOCs and recovery steps.
 stepsecurity.iowriteupPublished and added 24 Oct 2026🛡️ Security
- Faster Matrix Multiplication Leads to Faster Lattice Sieving
Gao and Hu's IACR ePrint 2026/2622 shows that if the matrix multiplication exponent satisfies ω ≤ 9/4 − η, heuristic lattice sieving runs in (3/2 − δ)^(n/2+o(n)) time under the spherical heuristic from the BDGL analysis. It builds on OpenAI's recent result that ω ≤ 9/4. With known matrix multiplication algorithms, the method already gives subquadratic search inside BDGL buckets. Only the abstract is available, so concrete parameters are not shown.
eprint.iacr.orgpaperAdded 26 Oct 2026, published 24 Oct 2026🛡️ Security  New Evidence Shows LiteLLM Secret-Stealing Workflows Ran 11 Days Before Supply Chain Attack
Socket's Threat Research team reports that malicious cache.yml workflows ran in the BerriAI/litellm repository on 10 and 12 October 2026, eleven days before the 21 October release attack that published litellm==1.107.0. Each commit pushed to a short-lived ci-tmp-<hex> branch, then deleted it, sending base64-encoded CI secrets to webhook.site. Evidence comes from Actions metrics and environment deployment records; 20 secret names were exposed.
 socket.devwriteupPublished and added 23 Oct 2026🛡️ Security
 Rafter (@RafterSecurity) on X
Railway security incident update of 23 October 2026, posted by Rafter Security, summarising Railway's preliminary report on the 20-22 October breach. Up to 1.85% of workspaces (about 100,000) may have had environment variables exposed. Attackers reportedly targeted AI provider API keys, possibly for model distillation. Some encrypted secrets were accessed and a subset decrypted. Railway says the attacker was removed by 22 October at 03:32 UTC, and the forensic investigation continues.
x.comthreadAdded 25 Oct 2026, published 23 Oct 2026🛡️ Security CVE-2026-109618 / CVE-2026-109619 | NodeZero Rapid Response Check Now Available
PHP2Shell is the name for CVE-2026-109618 and CVE-2026-109619, critical unauthenticated RCE flaws in PHP core fixed on 21 October 2026 in PHP 8.2.35, 8.3.36, 8.4.27 and 8.5.12. The page explains the out-of-memory corruption and stale global state causes, mod_php and PHP-FPM exposure, interim mitigations, hunting guidance, exploitation reports from October 2026, and the 23 October CVE-2026-115560 upload-progress advisory. Horizon3 also announced a non-exploiting NodeZero check.
 horizon3.aiadvisoryAdded 29 Oct 2026, published 23 Oct 2026🛡️ Security
 Mirai Botnet Operators Join PHP2Shell Attacks as ASLR Bypass Exploits Emerge
PHP2Shell (CVE-2026-109618 and CVE-2026-109619, CVSS v4.0 9.2) are unauthenticated RCE bugs in PHP, patched on 21 October 2026. Sophos, Arctic Wolf and Hunt.io tie exploitation attempts to the Potassium Mirai variant, and VulnCheck built an ASLR-bypassing exploit. SOCRadar and Hunt.io found an exposed attacker server, and Qualys data shows about 110 million instances on end-of-life PHP. No confirmed compromise exists.
securityweek.comarticlePublished and added 23 Oct 2026🛡️ Security Xavier Rivera (@XavierRiveraX) on X
CVE-2026-115560 is a PHP code execution bug reported two days after the PHP2Shell emergency patches. The post says those releases do not fix it and no emergency fix is planned. Only apps that switch session.serialize_handler to php via ini_set() before session_start() are exposed. The mitigation is session.upload_progress.enabled=0, which also covers anyone who applied it for the 21 October advisory. The post gives no technical root-cause detail.
x.comadvisoryAdded 25 Oct 2026, published 23 Oct 2026🛡️ Security- Tight Post-Quantum Multi-Key Security of the FX Construction
Rentaro Shiba and Tetsu Iwata prove a tight multi-key security bound for the FX construction (the DESX generalization) in the quantum ideal cipher model. Security holds up to about 2^((n+κ)/3) total classical and quantum oracle queries against fully adaptive adversaries, for any number of keyed instances μ≥1. This improves their ToSC 2026 bound and matches the offline Simon's algorithm attack in the exponent.
eprint.iacr.orgpaperAdded 24 Oct 2026, published 23 Oct 2026🛡️ Security  11 Million Impacted by Capcom Data Breach
Capcom disclosed a breach of CAPCOM ID, its shared login service for online games, discovered on 19 October. Attackers took 11,774,247 email addresses plus account metadata (creation date, last login, login count, last IP). For 43 users dates of birth, gender, country and nicknames were also exposed, and passwords were changed on 196 accounts. Capcom says no passwords were stolen, reset the affected accounts, and warns of impersonation emails. The root cause is not stated.
securityweek.comarticlePublished and added 23 Oct 2026🛡️ Security- How Much Do You Trust A Dog? Quantifying Hint-Following in Reasoning Language Models
This paper measures how hints such as "[Source] thinks the answer is (X)" shift LLM answers on MMLU questions, varying the source between a professor, a friend and a dog across Qwen, Gemma and SmolLM models. The shift fits an exponential tilt: a roughly constant mean change in the hinted answer's log-odds, with susceptibility largely shared across sources. The shift persists when the source is declared inaccurate or the prompt warns against trusting it. Synthetic experiments show how KL-regularized reward training could produce this pattern.
arxiv.orgpaperAdded 26 Oct 2026, published 23 Oct 2026🧠 AI - PHP2Shell Exposure Depends on More Than Whether You Use PHP
Horizon3.ai post on assessing exposure to PHP2Shell (CVE-2026-109618, CVE-2026-109619), two memory-handling flaws in PHP. It says affected PHP may be bundled in third-party products, containers or managed hosting, and that finding it shows a remediation need, not proven exploitability. It lists questions to ask hosting providers and says Horizon3.ai has validated exploitation under specific preconditions that are still being characterized.
horizon3.aiarticleAdded 29 Oct 2026, published 22 Oct 2026🛡️ Security  Node2Shell: Node.js Brotli vulnerability allows remote code execution (CVE-2026-111497)
Node2Shell (CVE-2026-111497) is an out-of-bounds write in the Brotli decoder bundled with Node.js and Bun, triggered by malformed compressed input and rated high by Node.js, with possible remote code execution. Fixed in Node.js 22.23.4, 24.22.1 and 26.12.1 and Bun 1.4.4. The post covers exposure via Express 5, body-parser 2.x, fetch() and node:zlib, stopgaps, and a timeline with public proofs of concept on 22 October 2026.
aikido.devadvisoryPublished and added 22 Oct 2026🛡️ Security- Integer Coordinate Families and Threshold RSA Signatures for Any Prime Exponent
Paper by Shivansh Jaiswal and Somitra Sanadhya (IACR ePrint 2026/2601) on integer coordinate families for threshold RSA signatures with prime exponent e. It shows the CT-RSA 2026 Ng-Lau scheme admits trivial forgeries and has a flawed proof. It proposes repaired scheme PiIC and integer secret-sharing scheme PiZ for any prime e and any (t,n), both proven TS-UF-CMA secure under the standard RSA assumption. It also gives super-polynomial coordinate lower bounds for pairwise families.
eprint.iacr.orgpaperAdded 24 Oct 2026, published 22 Oct 2026🛡️ Security  Tech and Security Companies Respond to PHP2Shell Vulnerabilities
SecurityWeek roundup of responses to PHP2Shell, two critical unauthenticated RCE flaws (CVE-2026-109618, CVE-2026-109619) fixed in PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35 on 21 October 2026. It covers the exploitation timeline (first attempt 17 October), vendor exposure checks, Red Hat's lower 8.1 score against NVD's 9.8, detections from Cisco Talos, CrowdStrike and Corelight, and government alerts.
securityweek.comarticlePublished and added 22 Oct 2026🛡️ Security- Meku_SI (@MEKU_SI) on X
MEKU Human Cloud is an MCP server for agents that need a real person to do a task. It exposes three tools: search humans (read-only), request a human (a human operator reviews every request first), and check status. It is listed in the MCP Registry as farm.meku/human-cloud. The tweet gives no detail on pricing, humans available or request formats; those are in the linked docs.
x.comtoolAdded 23 Oct 2026, published 22 Oct 2026🧠 AI - lee1981 (@lee1981b) on X
CyberForge CVE of the Day #084 analyses CVE-2026-76466, a CVSS 9.8 flaw in clustered Cisco Expressway-C and Expressway-E. Persistent database cookies and weak client-certificate validation allow root OS command execution over the network. The fix is X15.5.20 (X14 and earlier must migrate), with no workaround. It adds a per-peer SOC investigation trail, reachability checks and exposure status from CISA SSVC, KEV and EPSS.
x.comadvisoryAdded 24 Oct 2026, published 22 Oct 2026🛡️ Security - Getting to the right root: radical isogenies of every degree
Thomas Decru's ePrint 2026/2595 proves a corrected version of radical isogeny formulae for every N≥4, odd and even, over fields of characteristic coprime to 2N. It settles the sign choice for even N so that 2-isogeny walks stay on the volcano surface. One radical step costs about 12.5N multiplications and one exponentiation, and the paper shows how to evaluate radical isogenies on points, so a CSIDH class group action needs no torsion point sampling.
eprint.iacr.orgpaperAdded 24 Oct 2026, published 22 Oct 2026🛡️ Security  PHP Patches Two Critical Unauthenticated RCEs (CVE-2026-109618, CVE-2026-109619): Update Now
Snyk's write-up of two critical unauthenticated PHP runtime RCEs, CVE-2026-109618 (out-of-memory corruption) and CVE-2026-109619 (stale global state, cross-request use-after-free), both CVSS v4.0 9.2. Fixed in PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35 on 21 October 2026. It covers the disclosure timeline, affected SAPIs (mod_php most exposed), backports for 8.1 and older, and partial mitigations.
 snyk.ioadvisoryPublished and added 22 Oct 2026🛡️ Security
 Sizing the PHP exposure window for CVE-2026-109618 and CVE-2026-109619 with VirusTotal
VirusTotal sizes the internet-facing PHP footprint around CVE-2026-109618 and CVE-2026-109619 (CVSS v4.0 9.2, session.upload_progress) using Internet Scanning. About 5.1M IPs run PHP, roughly 4 in 5 hide their version, and ~758K disclose an end-of-life branch. It gives queries that use the SSH banner to match leaked LiteSpeed lsphp 8.2.34 builds, plus mitigations.
 blog.virustotal.comarticleAdded 22 Oct 2026🛡️ Security
 Using AWS WAF to apply mitigations for PHP2Shell RCE vulnerabilities (CVE-2026-109618 and CVE-2026-109619)
AWS Security Blog guide to mitigating the PHP2Shell unauthenticated RCE flaws (CVE-2026-109618 and CVE-2026-109619, CVSS v4.0 9.2) with AWS WAFv2 rules. It covers rules for the PHP_SESSION_UPLOAD_PROGRESS trigger, blocking multipart/form-data, body size caps and rate limits, plus body inspection limits. It lists PHP fixes (8.5.12, 8.4.27, 8.3.36, 8.2.35) and server settings, and stresses WAF only reduces exposure.
 aws.amazon.comarticlePublished and added 22 Oct 2026🛡️ Security
- Dan Kornas (@DanKornas) on X
aula-mcp is an open-source (MIT) TypeScript MCP server that connects an AI client to Denmark's Aula school platform. It exposes tools for profiles, calendar events, messages, notifications, posts and weekly plans. MitID credentials and OAuth tokens are stored in macOS Keychain or an AES-256-GCM encrypted file. The HTTP server binds to 127.0.0.1, and the presence write tool stays off until AULA_MCP_WRITE=1 is set.
x.comrepoAdded 23 Oct 2026, published 22 Oct 2026🧠 AI  Train in Simulation, Deploy on a Real Robot: Microduck with Isaac Lab 3.0
Tutorial for training a walking policy for Microduck, an open-source bipedal robot from Pollen Robotics and Hugging Face, in NVIDIA Isaac Lab 3.0 with Newton. It covers RSL-RL training with the backlash preset, BAM actuator models and domain randomization, then ONNX export (61 observations, 14 joint-position actions) and deployment with robotctl. Policies can be shared on the Hugging Face Hub or tested in Microduck Arena.
 huggingface.cowriteupPublished and added 21 Oct 2026🧠 AI
 Coinbase's Plan for a Quantum-Safe Bitcoin
Bankless summary of Coinbase's October 2026 proposal for making Bitcoin quantum-safe. It covers upgradeable address designs (BIP-360 P2MR, P2TRv2, hybrid addresses), four candidate signatures (ML-DSA, SLH-DSA, FN-DSA, SHRINCS) with size and stateful-key-reuse trade-offs, a five-stage migration plan, and a separate track for dormant coins with exposed public keys such as Satoshi's.
bankless.comarticlePublished and added 21 Oct 2026🛡️ Security Your MCU likely escaped the eMudhra intermediate CA compromise
Analysis of the eMudhra intermediate CA compromise disclosed 20 October 2026, in which eight intermediate CA private keys were weak P-384 keys (top 376 bits zero, one key equal to 4) and publicly accessible. It explains web PKI chains and why browsers enforcing Certificate Transparency were not exposed. It argues MCU firmware that bundles only the single root it needs, as in Zephyr's HTTP GET sample, is likely safe unless it trusts an eMudhra or Sectigo cross-signing root.
 danielmangum.comarticleAdded 22 Oct 2026, published 21 Oct 2026🛡️ Security
 PHP2Shell: Critical vulnerabilities in PHP (CVE-2026-109618, CVE-2026-109619) | Endor Labs
PHP2Shell is the name for two critical PHP core memory-safety flaws, CVE-2026-109618 and CVE-2026-109619, that allow unauthenticated remote code execution. Fixes ship in PHP 8.2.35, 8.3.36, 8.4.27 and 8.5.12. Wiz researchers demonstrated RCE against WordPress, Drupal and Joomla, and Apache with mod_php is the highest risk. The post covers inventory, container rebuilds, Cloudflare WAF rules and temporary exposure reduction.
endorlabs.comadvisoryPublished and added 21 Oct 2026🛡️ Security- PHP Panic: Two Critical Bugs Put 70% of the Internet at Risk, and Everyone Is Freaking Out
Decrypt reports on CVE-2026-109618 and CVE-2026-109619, two PHP flaws rated CVSSv4 9.2 that allow unauthenticated remote code execution. PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35 shipped on 21 October 2026 after an early leak and Cloudflare-observed attacks. The article covers the memory-handling root causes, mod_php and upload-progress exposure, government site shutdowns, affected version range (PHP 5.4 and later per Sansec), and patch guidance.
decrypt.coarticlePublished and added 21 Oct 2026🛡️ Security  Cloudflare deploys protections against php2shell vulnerability
Cloudflare describes its WAF protections for php2shell (CVE-2026-109618 and CVE-2026-109619), two PHP runtime memory-handling flaws affecting PHP 5.4 and later that can cause denial of service, remote code execution and data exposure. Rules shipped 21 October 2026, about 9 hours before disclosure, using a new "full transaction detection" that matches request and origin response together. It lists ruleset IDs and says patching PHP is still required.
blog.cloudflare.comarticleAdded 22 Oct 2026, published 21 Oct 2026🛡️ Security How Commerce.com and Cloudflare are getting storefronts ready for AI agents
Cloudflare and Commerce.com describe enabling WebMCP, Google's proposed browser standard for exposing structured tools to AI agents, across almost 100,000 storefronts. Cloudflare injects a bridge script at the edge that proxies tools from Commerce.com's backend MCP server. Per-merchant opt-out uses Configuration Rules and custom hostname metadata, and a configurable MCP URL (/api/mcp) was added.
blog.cloudflare.comarticleAdded 29 Oct 2026, published 21 Oct 2026🧠 AI A company that vouches for websites had secret keys so weak that 8 of them were cracked
eMudhra, an Indian certificate authority with over 60 million issued certificates, had eight CA private keys that were tiny integers such as 4, 56 and 237. Researcher Scott Helme recovered all eight from public certificates in under a second, and the keys were exposed from April 2025. Mozilla, Chrome, Apple and Microsoft blocked them between 17 and 20 October 2026, but curl, Python, Node.js, Go and Java accepted a forged Stripe API certificate because they skip revocation checks.
coindesk.comarticlePublished and added 21 Oct 2026🛡️ Security Threat Brief: Active Exploitation of PAN-OS CVE-2026-0257 (Updated Oct 20)
Unit 42 threat brief on active exploitation of CVE-2026-0257, a PAN-OS GlobalProtect authentication bypass added to CISA KEV on May 13, 2026. It lists IP addresses, host IDs and PoC-derived client values to hunt in GlobalProtect logs. The October 2026 updates cover Qilin and Inc ransomware operators, MFA bypass, pivots to vCenter and ESXi with offline VMDK credential dumping, and management interface exposure on ports 4443 and 3879.
unit42.paloaltonetworks.comadvisoryAdded 21 Oct 2026, published 20 Oct 2026🛡️ Security- A Spectral Theory of Local-to-Global Leakage
A Spectral Theory of Local-to-Global Leakage is an IACR ePrint paper (2026/2571) by Rei Ueno on additive secret sharing over finite abelian groups. It gives an exact leakage decomposition into local leakage magnitude and spectral alignment across shares. Two channels with identical local mutual information can have exponentially different global leakage. Automorphism-weighted sharing can cancel leakage perfectly with finitely many shares, which ordinary additive sharing cannot do.
eprint.iacr.orgpaperAdded 21 Oct 2026, published 20 Oct 2026🛡️ Security - DeclineCraft: A RAG Abstention Benchmark for Jointly Measuring Combined Retrieval and Parametric Knowledge
DeclineCraft is a dynamic RAG abstention benchmark whose unanswerable questions target Minecraft feature additions made after a corpus cut-off, with audits for parametric exposure. Across 27 LLMs, single-shot retrieval raises Correct Abstention Rate in 38 of 40 configurations, while iterative RAG lowers it in 30 of 40. Enabling thinking without retrieval lowers abstention for 8 of 13 models, shifting responses to premise denial.
arxiv.orgpaperAdded 22 Oct 2026, published 20 Oct 2026🧠 AI - Show HN: VoidAccess – open-source dark web OSINT, from query to a graph
VoidAccess is a self-hosted, MIT-licensed dark web OSINT platform that runs a 13-step pipeline from a research query to a relationship graph. It collects from Tor indexes, paste sites, code forges, security feeds and .onion seeds, applies content-safety filters, and exports STIX 2.1, MISP, Sigma, YARA, Snort, Suricata, CSV and JSON. It runs as a CLI with SQLite or as a Docker Compose stack with PostgreSQL, FastAPI and Next.js.
 github.comrepoAdded 21 Oct 2026, published 20 Oct 2026🛡️ Security
 AI Platform Cairn Abused to Hack Over 100 Organizations
Cairn is an open source AI platform that coordinates agents as an autonomous penetration testing engine. Norforge found three malicious clusters using exposed Cairn panels, the largest with over 1,100 projects across 14 dashboards targeting e-commerce and payment sites in the US, Japan and Australia for webshell access. Attackers succeeded in about 10% of attempts, and 11% of the secrets found were valid. Reuters reports over 100 victims, including John Deere and SharkNinja.
securityweek.comarticlePublished and added 20 Oct 2026🛡️ Security 970,000 Medi-Cal Members Affected by Paradigm Healthcare Data Breach
Paradigm Healthcare Services, a Medi-Cal billing processor, told HHS that a breach affected more than 970,000 people. Attackers accessed its network between October 8 and 15, 2025, and exposed names, dates of birth, gender and Medi-Cal member IDs. The article also covers breaches at law firm Tarter Krinsky & Drogin (196,000 people) and Ridgeway Pharmacy (258,000). No threat actor or intrusion method is named.
securityweek.comarticlePublished and added 20 Oct 2026🛡️ Security SlowMist Says Qubic Wallet Keys Could Be Recovered From Six Network Samples
SlowMist says Qubic wallet private keys could be recovered from six samples observed on the network. Qubic patch 4.26.4 separates new account seeds from the exposed random stream, but leaves header generation unchanged. The page text holds only the headline and subhead, so the attack mechanics, affected versions and any CVE are not stated.
thedefiant.ioarticlePublished and added 20 Oct 2026🛡️ Security- LinuxSecurity (@lnxsec) on X
A post from lnxsec on CI runners that accept outside pull requests while also holding registry credentials, cache write access, signing material or deployment tokens. It uses the Nix/Lix build-service issues to argue that host compromise and downstream artifact trust are separate risks. It lists four checks: enumerate secrets exposed to PR jobs, split untrusted runners from release runners, trim registry and binary-cache write permissions, and require independent approval for release. It links a linuxsecurity.com feature; CVE details are not in the post.
x.comthreadAdded 20 Oct 2026, published 19 Oct 2026🛡️ Security - Can It Actually Work? Synthesizing Functional CAD Mechanisms
FunCAD-Harness is a framework in which LLM agents design CAD mechanisms and revise them using physical simulation feedback. It turns abstract functional requirements into candidate-specific physical tests. The paper also introduces FunCADBench, a benchmark of 46 mechanism families with interdependent, multi-step operations. Experiments on frontier LLM agents show it exposes mechanical failures that visual inspection misses and raises functional success over standard simulation-augmented baselines.
arxiv.orgpaperAdded 21 Oct 2026, published 19 Oct 2026🧠 AI  Rank Math PRO WordPress Plugin Compromised in Supply Chain Attack
Rank Math PRO version 3.0.123, a WordPress SEO plugin, shipped malicious packages between 15 October 2026 20:02 UTC and 16 October 2026 07:12 UTC. The malware gives persistent backdoor access, can expose credentials and API keys, and uses .htaccess rules to run .cache files as PHP. Rank Math released clean v3.0.124 and advises restoring from backup, blocking rank1cdn[.]com, and checking SSH keys and crontabs.
securityweek.comarticlePublished and added 19 Oct 2026🛡️ Security A hacker broke into John Deere and SharkNinja with an army of AI agents
The Verge reports Norforge findings that one hacker used autonomous AI agents on the open-source Cairn platform to breach more than 100 websites in the US, Canada, Australia and Japan. Reuters named John Deere, SharkNinja and Cummins as victims. Norforge found over 20 likely malicious exposed Cairn instances, with breaches taking about 23 hours; the attacker's tactics were written in under 100 Chinese characters. Cairn's creator says misuse is a human decision.
 theverge.comarticleAdded 20 Oct 2026, published 19 Oct 2026🛡️ Security
- One Compromised Login Exposed Millions of California Students’ Records
Breach report on Educational Testing Service (ETS), whose SFTP site was accessed with a compromised login credential between 22 May and 18 September 2026, exposing California student records. The data covers at least three school years of students, over 5.7 million enrolled, and leavers back to 2006. Files included names, birth dates, addresses, ID numbers, disability and English learner status. No Social Security numbers were involved, and the credential's origin and the attacker are unknown.
securityweek.comarticlePublished and added 19 Oct 2026🛡️ Security  Loud, Fast, and Everywhere: Anatomy of a Real AI-Driven Cloud Attack
Wiz CIRT write-up of an AI agent-run intrusion against a multi-cloud organization (GCP, AWS, Kubernetes, CI/CD, GitOps, identity provider). It lists traits of AI-driven attacks: machine-speed tempo, credential chaining, pentest/probe naming, numeric task IDs and commented code. Initial access was a Java RCE in an exposed Kafka UI. It closes with detection and response advice: unified logs, workload visibility and trust isolation.
wiz.iowriteupPublished and added 19 Oct 2026🛡️ Security


Showing 120 of 551
Show more