 VulnCheck - Outpace Adversaries
VulnCheck Open Source is an index of VulnCheck's open-source tooling for its vulnerability and exploit intelligence. It lists a Python API client, a CLI, a GitHub Action for CI/CD, go-exploit (a Go exploit framework), an MCP server for delivering intelligence to AI clients, and VulnCheck Insights, a Chrome extension that highlights CVEs, CPEs and PURLs on web pages and enriches them. The page gives only one-line descriptions.
 vulncheck.comtoolAdded 29 Oct 2026🛡️ Security
 Survival LLM: AI assistant and emergency library that runs on your own computer
Survival LLM is a free, open-source desktop app for macOS (Apple Silicon) and 64-bit Windows that runs an AI model and an offline emergency library on the user's computer. It checks the machine's memory, downloads a fitting model, and answers from sources such as Wikipedia, WikiMed, Ready.gov and CDC guidance, citing each article. Users can add their own files; version 0.3.2 is dated October 2026.
 brangus.iotoolAdded 28 Oct 2026, published 27 Oct 2026🧠 AI
- Search Search results for "security" | MCP Market
MCP Market search results for "security" in its skills category, listing about 20 installable AI agent skills. Entries cover OWASP Top 10 audits, secure PHP coding, STRIDE threat modeling, CVE remediation, security header analysis, misconfiguration finding, bug bounty triage and AgentShield scans of Claude Code configurations. One is a paid D365FO security-role XML skill. Each entry has only a one-line description and a category label.
 mcpmarket.comtoolAdded 25 Oct 2026🧠 AI
 Argus – a free, open-source agentic security operations platform – MIT
Argus is a free, MIT-licensed, self-hosted security operations platform that maps cloud, identity, code, device, network and Kubernetes assets into one evidence graph and detects fast, AI-driven attacks. Read-only AI agents investigate and only propose actions. Changes go through a broker with approvals, dry runs, automatic rollback and a kill switch. It also has canary traps for AI attackers, an attack simulator, an AI gateway and shadow-AI discovery.
 thomasunise.comtoolAdded 25 Oct 2026, published 24 Oct 2026🛡️ Security
- Show HN: Sphinx – A hook that quizzes you on your AI's code before shipping
Sphinx is a free, open-source Git hook (npm package sphinx-understand) that pauses pushes on protected branches and asks the developer a question about what the diff does when things go wrong. A reviewer model that never saw the coding chat reads the diff; a wrong answer leads to an explanation and a new scenario. It works with Codex, Claude Code, Cursor, OpenCode and Pi, or plain Git. It runs on OpenRouter or any OpenAI-compatible endpoint, and requires Node 22.19+.
 sphinx-six-theta.vercel.apptoolAdded 19 Oct 2026, published 18 Oct 2026🧠 AI
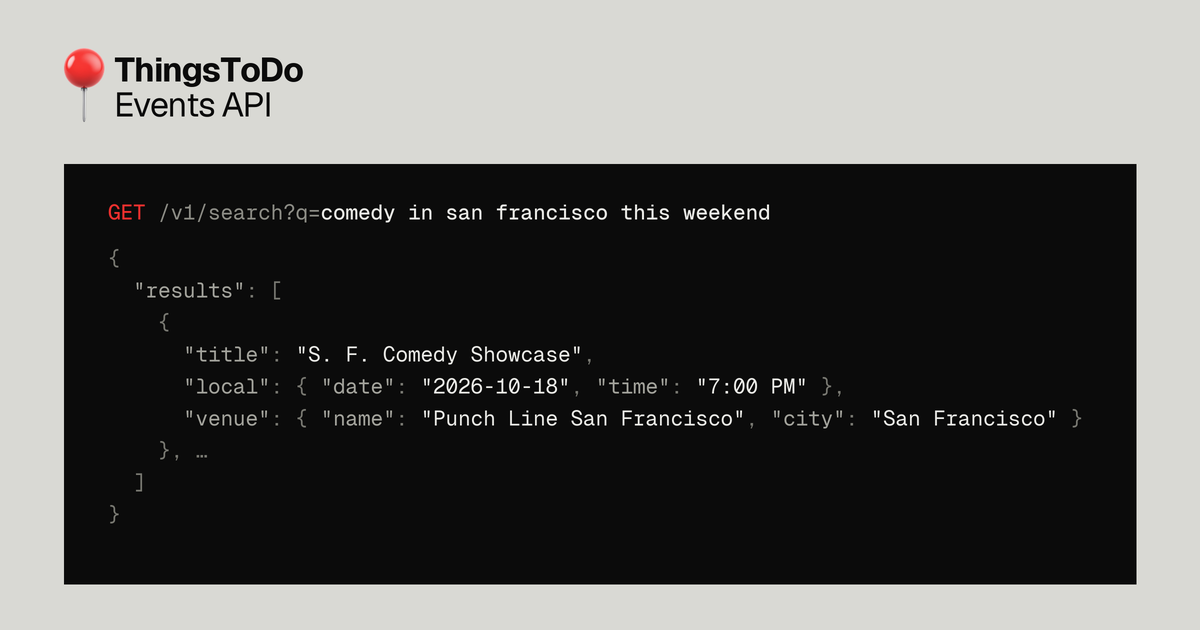 Show HN: Things to Do API
Things to Do API is a hosted knowledge base of local events (shows, talks, pop-ups, markets, festivals) that you query in natural language, for example `/v1/search?q=comedy+in+san+francisco+this+weekend`. It returns structured JSON with title, category, local start time, venue and ticket and source links. It also exposes an HTTP MCP endpoint, added with `claude mcp add --transport http thingstodo https://api.thingstodoapi.com/mcp`, so agents can use it as a tool. Coverage is live for the San Francisco Bay Area, with New York City and Los Angeles coming. Pricing is pay-as-you-go from $5 per 1,000 calls, the first 1,000 a month are free, and there is a 300 calls/min limit.
 thingstodoapi.comtoolAdded 18 Oct 2026, published 16 Oct 2026🧠 AI
 EveryDev.ai (@EveryDevAi) on X
magpie, by @yetone, is an open-source local gateway and desktop app that lets any coding agent use any model or provider. It translates between the OpenAI Chat, OpenAI Responses, Anthropic Messages and Gemini APIs. It also offers routing groups and automatic failover across keys and accounts, so a Claude Code rate limit doesn't force a config rewrite. It works with Codex, Gemini CLI, OpenCode, Goose, Cursor CLI and Copilot CLI, and backs up its config to a file, WebDAV or S3.
 x.comtoolAdded 16 Oct 2026, published 15 Oct 2026🧠 AI
- 44er (@44errrr) on X
hexvero is a Node-only, zero-dependency MCP server that gives coding agents a static first-look triage of binaries and app bundles across 18 formats (ELF, PE, Mach-O, APK, .NET, Go, Wasm, Electron, SQLite). Findings are marked confirmed or inferred with file and line, and outputs are paged with a byte budget (a 541 MB Electron app yields a ~15 KB result). The author contrasts its 3,043-token tool catalog with a 509,696-token catalog of an established RE MCP server. radare2, rizin or Ghidra can be plugged in for disassembly, and setup registers it with Claude Code, Cursor, Codex and 15 more clients.
x.comtoolAdded 15 Oct 2026, published 14 Oct 2026🛡️ Security  Show HN: Use your OpenAI subscription to create audiobooks
PDF TO MP3 is a hosted MCP server (Streamable HTTP, account authentication) that turns PDFs into audiobooks. The user's existing AI subscription, such as Codex, handles document processing through the MCP connection. Speech generation is billed separately through the user's own OpenAI or Google text-to-speech API key. The setup is three steps: add the MCP server, add a speech key, then attach a PDF and ask the assistant to use the MCP. It shows a "bring your own subscription" pattern that keeps the vendor's compute costs low.
 pdftomp3.comtoolPublished and added 13 Oct 2026🧠 AI
- derailed/popeye
Popeye is a read-only Go utility that scans live Kubernetes clusters and reports misconfigurations, stale or unused resources, port mismatches, probe and image issues, RBAC problems, and resource over/under-allocation when a metrics-server is present. It is configurable with a spinach.yaml (excludes, thresholds, allowed registries, severity overrides), can run as a CronJob with a get/list ClusterRole, outputs HTML/JSON/YAML reports, pushes Prometheus metrics, and can upload reports to S3/Minio. It lints what is actually deployed rather than manifests on disk.
 github.comtoolAdded 12 Oct 2026🛡️ Security
- Trail of Bits (@trailofbits) on X
Trail of Bits announces SequenceHash, a library for hashing several inputs without concatenation ambiguity. Plain concatenation lets different input sequences produce the same SHA-256 digest. SequenceHash appends each input's length as a fixed 128-bit integer so every sequence has a single encoding. It ships for Rust, Go and Python, and removes a recurring bug class in crypto and appsec code.
x.comtoolAdded 11 Oct 2026, published 9 Oct 2026🛡️ Security - Agent Game Forge (@agentgameforge) on X
Agent Sprite Forge v0.4.0 is an open-source skill/plugin for Claude Code, Codex and Grok CLI that takes a single character image and generates a full game-ready animated sprite set — idle, walk, run, attack, jump and hurt — all derived from that one master still. It adds official API support for OpenAI, Gemini, xAI, ModelArk and fal.ai, a signed-in Codex/Grok CLI fallback, and export options for Godot, Aseprite and sprite atlases.
x.comtoolPublished and added 6 Oct 2026🧠 AI  texas actual (@texasactualUA) on X
A tweet highlights osinteuropetracker.com, an OSINT tracker built to map known and suspected Russian sabotage operations across the European Union. The tool is shared as a practical way for analysts to monitor and visualize ongoing hybrid-threat incidents attributed to Russia in EU countries.
x.comtoolAdded 3 Oct 2026, published 1 Oct 2026🛡️ Security- Photo Scrubber — local face blur & metadata removal
Simon Willison built an experimental local-only photo tool that detects faces and automatically blurs them to protect the identity of strangers (e.g. protesters) photographed in public, also stripping metadata. It runs entirely client-side using Google's MediaPipe compiled to WebAssembly via @mediapipe/tasks-vision, with the BlazeFace model for face detection, and was built with help from GPT-6 Astra.
 simonwillison.nettoolAdded 2 Oct 2026, published 29 Sep 2026🧠 AI
 Manny M. (Vicente Traditor Mancebo) 💀 (@sargexd) on X
AKCA is an open-source Dynamic Application Security Testing (DAST) scanner written in Go, aimed at evidence-oriented web security testing. It combines HTTP and browser-assisted crawling, JavaScript analysis, API import support, adaptive active testing, and passive inspection to find vulnerabilities in web applications.
x.comtoolAdded 30 Sep 2026, published 27 Sep 2026🛡️ Security- Gemini 3.8 TTS Playground
Simon Willison built a bring-your-own-key playground for Google's newly released gemini-3.8-flash-tts and gemini-3.8-flash-lite-tts text-to-speech models, which offer a library of over 2,000 voices plus custom voice cloning from a 30-second sample. The tool exploits the Gemini API's open CORS policy to run entirely client-side, and supports defining full multi-character conversations with per-character voices and style instructions; a demo generated 1m18s of two-pelican dialogue audio in about 20 seconds for 2.74 cents.
simonwillison.nettoolAdded 29 Sep 2026, published 23 Sep 2026🧠 AI - llm-typesafe 0.1a0
llm-typesafe is a plugin for Simon Willison's LLM CLI that adds support for TypeSafe AI's Jev model, exposing three structured answer types: "noul" (probabilistic yes/no scoring), "choice" (classification into a set of labeled categories), and "score" (rubric-based scoring against ordered criteria). It lets users pipe text into the CLI with a system prompt and get back structured JSON judgments, useful for tasks like routing support messages or triaging bug reports by severity.
simonwillison.nettoolAdded 29 Sep 2026, published 22 Sep 2026🧠 AI  crt.name
 is a free subdomain index and API that returns every subdomain on file for a given apex domain plus first-seen dates, built by continuously parsing SAN hostnames from Certificate Transparency logs (Static CT sources like Let's Encrypt Sunlight, Geomys, Cloudflare Raio, plus legacy RFC 6962 logs like Google Argon, Sectigo, DigiCert), supplemented by Internet Archive CT replays, Common Crawl, ICANN CZDS zone files, ProjectDiscovery Chaos, HaGeZi DNS blocklists, and an active hostname prober. It offers a no-token REST API (100 req/IP/day), a Streamable HTTP MCP server exposing a single search tool for agent clients, and is the default crt source in the subfaster CLI subdomain enumerator.
 crt.nametoolAdded 3 Sep 2026, published 21 Aug 2026🛡️ Security
- IntelTechniques OSINT Tools Hub
IntelTechniques Search Tools is Michael Bazzell and Jason Edison's free companion toolset to their OSINT Techniques book, offering a collection of browser-based query generators and lookup tools for open-source intelligence investigations. Queries run client-side in the user's browser with no data collected or stored by the site, covering username/email/phone lookups, social media search, and other recon categories referenced in the book's 11th edition.
 inteltechniques.comtoolAdded 3 Sep 2026, published 31 Jul 2026🛡️ Security
- ShadowHodks
ShadowDorks is a free browser-based tool that generates over 1000 advanced Google dork queries for a target domain, covering categories like exposed admin panels, subdomain enumeration, and API key/credential leaks. It's built for pentest recon and OSINT reconnaissance workflows, letting a user paste a domain and copy ready-to-search dork strings.
 shadohdorks.vercel.apptoolAdded 3 Sep 2026, published 31 Jul 2026🛡️ Security
- OSINT Framework
OSINT Framework is a free, browsable web-based directory that organizes hundreds of open-source intelligence (OSINT) tools and resources into a category tree covering usernames, email addresses, domains, social media, public records, and more. Each entry is tagged to indicate whether it requires local installation (T), is a Google Dork (D), requires registration (R), or needs manual URL editing (M), helping practitioners quickly find the right recon tool for a given task.
 osintframework.comtoolPublished and added 31 Jul 2026🛡️ Security
 Thinkst Package Proxy
Thinkst released Package Proxy, a Cloudflare Workers-based inline proxy for npm, PyPI, pip, uv, and Cargo index/metadata requests that enforces supply-chain safety checks (minimum package age, upload-mechanism regression detection, allow/block lists) without requiring any client-side software or workflow changes. The proxy returns 404 for packages failing policy and logs installs to a D1 database, and Thinkst reports it protected them from the TanStack, Bitwarden, and TeamPCP npm compromises via its 10-day age check and integrity-downgrade detection.
 blog.thinkst.comtoolAdded 3 Sep 2026, published 26 Jun 2026🛡️ Security
 knowledgator/opir-multitask-large-v1.0 · Hugging Face
Opir-multitask-large is an English encoder-based GLiClass zero-shot classifier for real-time LLM safety filtering, supporting binary safe/unsafe decisions, toxicity classification, jailbreak/prompt-injection detection, and categorization over a 996-label hierarchical safety taxonomy (16 top-level, 126 mid-level, 854 leaf labels). It was trained with taxonomy-derived unsafe-prompt generation, evolutionary hard-negative mining against existing safety models, LLM-as-judge annotation (DeepSeek-V3.1, MiniMax-M2.5, Llama-3.3-70B), and replay training on the gliclass-v3-logic-dataset, and is benchmarked against WildGuard, PolyGuard, Nemotron Safety Guard and Qwen3Guard across datasets like Aegis2, HarmBench, WildGuardMix, ToxicChat, and JBB-Behaviors, reporting ~25ms p50 latency at 1024 tokens for real-time deployment as an input/output moderation layer.
 huggingface.cotoolAdded 29 May 2026🛡️ Security
 JFrog: Keep your Agents Under Control with agent-belt
JFrog open-sourced agent-belt, an Apache 2.0 CLI eval framework that black-box tests real coding-agent CLIs (Claude Code, Codex, Cursor, Copilot, Gemini, Goose, OpenCode) as subprocesses against version-controlled JSON scenarios with rule-based checks and separate LLM-judge scoring. It targets the non-determinism problem in agentic coding — model/CLI updates silently breaking tool selection or MCP behavior — by measuring pass^k across repeated trials, phrasing variants, and multi-judge consensus, with CI-gating exit codes, Docker sandboxing for untrusted-agent runs, and manifest file-locking for concurrent eval runs. It's positioned as complementary to agent governance: governance restricts what an agent can touch, agent-belt verifies whether its actions and outputs are actually correct.
 jfrog.comtoolPublished and added 19 May 2026🛡️ Security
- PathSentinel Radar
PathSentinel Radar is a Spanish-language, read-only CTI dashboard that ingests security news (currently drawn from BleepingComputer) and re-presents it with an urgency score, severity label, and a "playbook" category (e.g. cti_triage, endpoint_tpv_support) plus a one-line remediation action. The sample set covers Pwn2Own exploits against Exchange/Windows 11, credential-theft flaws in WordPress plugins Avada Builder and Funnel Builder, the Linux "Fragnesia" root-privesc bug (CVE-2026-46300), Dell SupportAssist BSOD issues, KongTuke's abuse of Microsoft Teams for initial access, a Google Ads phishing campaign spoofing GoDaddy ManageWP, and the arrest/indictment of the alleged Dream Market administrator. The site states the public front end only serves already-processed reports and runs no live AI queries per visitor.
 radar.pathsentinel.eutoolAdded 3 Sep 2026, published 16 May 2026🛡️ Security
- SaaS Event Maturity Matrix
The SaaS Event Maturity Matrix (EMM) is an open framework that catalogs categories of SaaS audit log events (authentication, user/group/role management, security policy changes, resource CRUD, etc.) and rates the depth of visibility each provides, with real-world JSON audit log examples from platforms like Box and Salesforce. It's built for defensive security practitioners to understand what activity is actually captured in vendor audit logs and to guide security monitoring and detection coverage decisions.
 eventmaturitymatrix.comtoolPublished and added 6 May 2026🛡️ Security


