- Ritik Shukla (@Retik_S) on X
kanzo is a local kanban board that coding agents can update. It ships as one 4 MB binary that starts in 2 ms and runs on localhost. It also works as an MCP server, so Claude Code and Codex see the same tasks as the user. The board is stored as a folder that can sync through a private git repo. The post is brief and gives no further detail.
 x.comtoolPublished and added 30 Oct 2026🧠 AI
- Zyon ⚗️ (@zyonbuilds) on X
Orca is an open-source (MIT) desktop app from stablyai for running a fleet of coding agents, including Claude Code, Codex and OpenCode, each in its own git worktree using the user's own subscriptions. Features include fanning one prompt across five agents and merging the winner, commenting on diffs and sending them back, SSH worktrees on remote machines, and a phone app for steering agents. The post reports 103k stars.
x.comtoolAdded 30 Oct 2026, published 29 Oct 2026🧠 AI - CISO Security Program Management 2026
Security Posture Management is a web tool that maps 30 CISO-accountable security topics across the five NIST Cybersecurity Framework functions. It tracks current maturity, KPIs, risks and audit findings per topic. It also records target maturity, target dates, accountable owners and review dates, flagging topics unreviewed for 6 months as due and 12 months as overdue. Initiatives link to topics and risks with owner, budget, dates and expected maturity uplift.
 spm.threat-modeling.comtoolAdded 29 Oct 2026🛡️ Security
- Big Bull (@BIGBULLapp) on X
clauth is a Rust terminal UI for Claude Code that combines multi-account switching with a live 5h / 7d usage monitor. A fallback chain moves the user off an exhausted account before Claude Code blocks. It supports Pro, Max, Team and Enterprise OAuth accounts and custom API endpoints on Linux, macOS and Windows. The post notes that auto-switching means the tool decides when accounts change.
x.comtoolAdded 30 Oct 2026, published 28 Oct 2026🧠 AI - alex shapalov (@alxshp) on X
PGX is a free, open-source Postgres runtime written in Rust that hosts thousands of isolated databases in one process, aimed at AI agents. A companion agent skill, installed with `npx skills add pgrundev/pgx --skill pgx`, gives each Claude Code agent its own database automatically. The author claims 1,000 databases in 659 MB RAM, about 0.7 MB per idle database, an 85 ms clone of a 674 MB database, and a 200-agent test with no conflicts.
x.comtoolAdded 28 Oct 2026, published 27 Oct 2026🧠 AI - Mauro Ubeda (@mauroubeda) on X
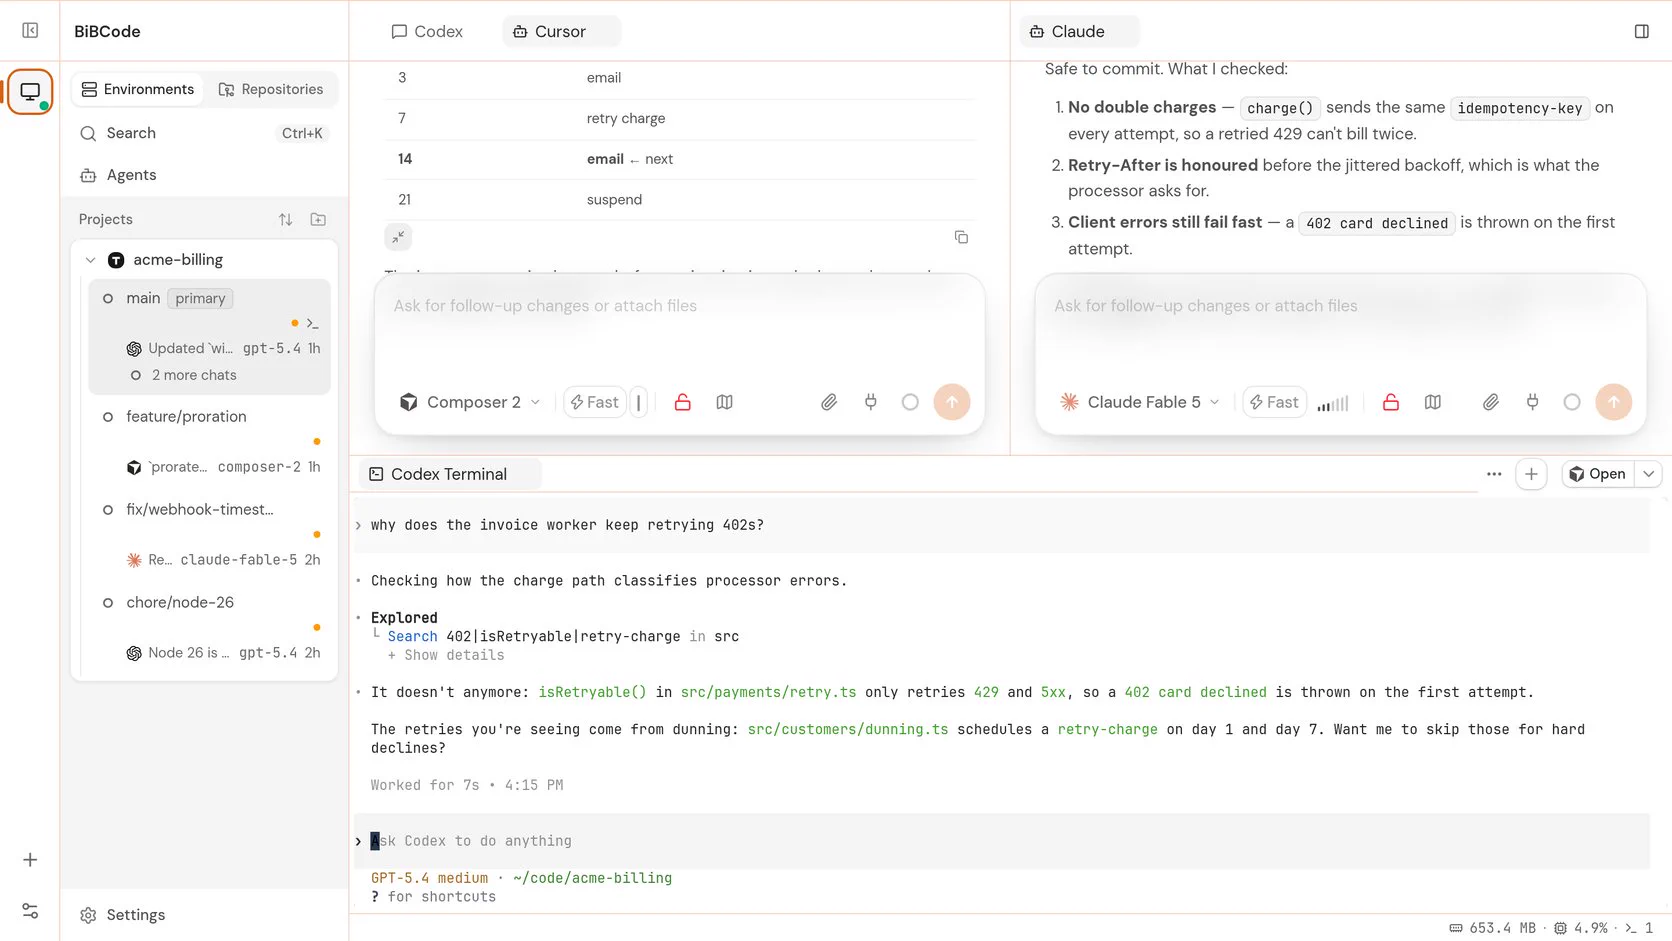
BibCode is an open-source desktop app, now in beta, for running coding agents side by side. It is built with Rust and Tauri rather than Electron, and runs Codex, Claude, Cursor and OpenCode, each in its own git worktree. It can also connect to remote BibCode Servers. The author, Mauro Ubeda, says it mixes ideas from T3 Code and Orca. The post gives no feature detail beyond this.
x.comtoolAdded 28 Oct 2026, published 27 Oct 2026🧠 AI  Proton Flock Camera Map
 is a ZIP-code search map of Flock license plate reader locations. Its data comes from researcher Joshua Michael, who found in November 2025 that Flock's servers exposed an access token to anyone without login, and published his map in December. His inventory lists over 170,000 cameras and 130,000 other devices, about 40% above Flock's cited 120,000 cameras. The page also covers what Flock records and cites a Washington Post review of officer misuse.
 proton.metoolAdded 26 Oct 2026, published 25 Oct 2026🛡️ Security
- Dan Kornas (@DanKornas) on X
jshook is an open-source (AGPL-3.0) MCP server that gives AI agents a search-first, profile-aware reverse-engineering workspace for JavaScript, browser traffic, WASM and native processes. Agents start with a small searchable tool surface and move to workflow or full profiles only when needed. It drives Chromium or Camoufox over CDP, captures WebSocket traffic, has HTTP, GraphQL and Burp Suite helpers, and supports hot-reload plugins and declarative workflows. The post is a short announcement; the repository link is in a reply.
x.comtoolAdded 28 Oct 2026, published 25 Oct 2026🧠 AI - Dan Kornas (@DanKornas) on X
jshook is an open-source (AGPL-3.0) search-first reverse-engineering workspace for AI agents, exposed over MCP. It drives Chromium or Camoufox through CDP, captures WebSocket traffic, offers HTTP, GraphQL and Burp Suite helpers, deobfuscates JavaScript, rebuilds source maps and disassembles WebAssembly. Tool profiles start small and expand to workflow or full sets; hot-reload plugins and declarative workflows extend it.
x.comtoolAdded 28 Oct 2026, published 25 Oct 2026🛡️ Security  Argus – a free, open-source agentic security operations platform – MIT
Argus is a free, MIT-licensed, self-hosted security operations platform that maps cloud, identity, code, device, network and Kubernetes assets into one evidence graph and detects fast, AI-driven attacks. Read-only AI agents investigate and only propose actions. Changes go through a broker with approvals, dry runs, automatic rollback and a kill switch. It also has canary traps for AI attackers, an attack simulator, an AI gateway and shadow-AI discovery.
 thomasunise.comtoolAdded 25 Oct 2026, published 24 Oct 2026🛡️ Security
- Trail of Bits (@trailofbits) on X
Trail of Bits announces a scanner, built by Scott A., that finds hidden copies of the vulnerable Brotli decoder behind a Node.js/Brotli bug, including in stripped binaries. Exploitability of the bug is still under testing. Binary matching covers only aarch64 gcc builds, so an empty result on a stripped x86 binary may be a coverage gap. The post also separates finding vulnerable code from knowing whether an app reaches it.
x.comtoolAdded 25 Oct 2026, published 23 Oct 2026🛡️ Security - Quick Study
Quick Study is a browser artifact built by Claude Opus 5.5 (High) from a single prompt. The user opens a photo and the page repaints it in a few seconds with a simulated paintbrush on a canvas element. Simon Willison links it to an earlier experiment in which Claude Fable simulated a watercolor illustration with P5.js. The post gives the prompt but no code walkthrough.
 simonwillison.nettoolPublished and added 23 Oct 2026🧠 AI
 Trail of Bits (@trailofbits) on X
patching-bugs is a Trail of Bits plugin for Codex that has an AI agent write a vulnerability fix, prove it works, and check it for regressions. It was built from analysis of thousands of Codex sessions from the Patch the Planet work with OpenAI. The post argues defenders need patch-writing agents to match attackers' bug-hunting agents. It gives no technical detail beyond that.
x.comtoolAdded 24 Oct 2026, published 22 Oct 2026🛡️ Security- Meku_SI (@MEKU_SI) on X
MEKU Human Cloud is an MCP server for agents that need a real person to do a task. It exposes three tools: search humans (read-only), request a human (a human operator reviews every request first), and check status. It is listed in the MCP Registry as farm.meku/human-cloud. The tweet gives no detail on pricing, humans available or request formats; those are in the linked docs.
x.comtoolAdded 23 Oct 2026, published 22 Oct 2026🧠 AI  EveryDev.ai (@EveryDevAi) on X
Weco, from WecoAI, is an open source CLI that optimizes code, prompts and agent harnesses against a metric the user defines. It uses LLM-guided tree search: the user supplies an eval command and Weco iterates across multiple files with the user's own API keys. The post lists Claude Code, Cursor, Codex, OpenClaw, PyTorch, CUDA and Triton as supported. It gives no benchmarks or setup details.
x.comtoolPublished and added 22 Oct 2026🧠 AI- SCF Controls Platform — open source
SCF Controls Platform is free, open-source (AGPL-3.0) GRC software built on the Secure Controls Framework. It covers the 1,451-control SCF catalog with 354+ framework mappings, L0–L5 evidence maturity scoring, a risk register linked to controls, and audit workspaces. It self-hosts via Docker Compose or a Helm chart for Kubernetes, and is independent of ComplianceForge, which publishes the SCF.
 scfcontrolsplatform.comtoolAdded 20 Oct 2026🛡️ Security
- Dan Kornas (@DanKornas) on X
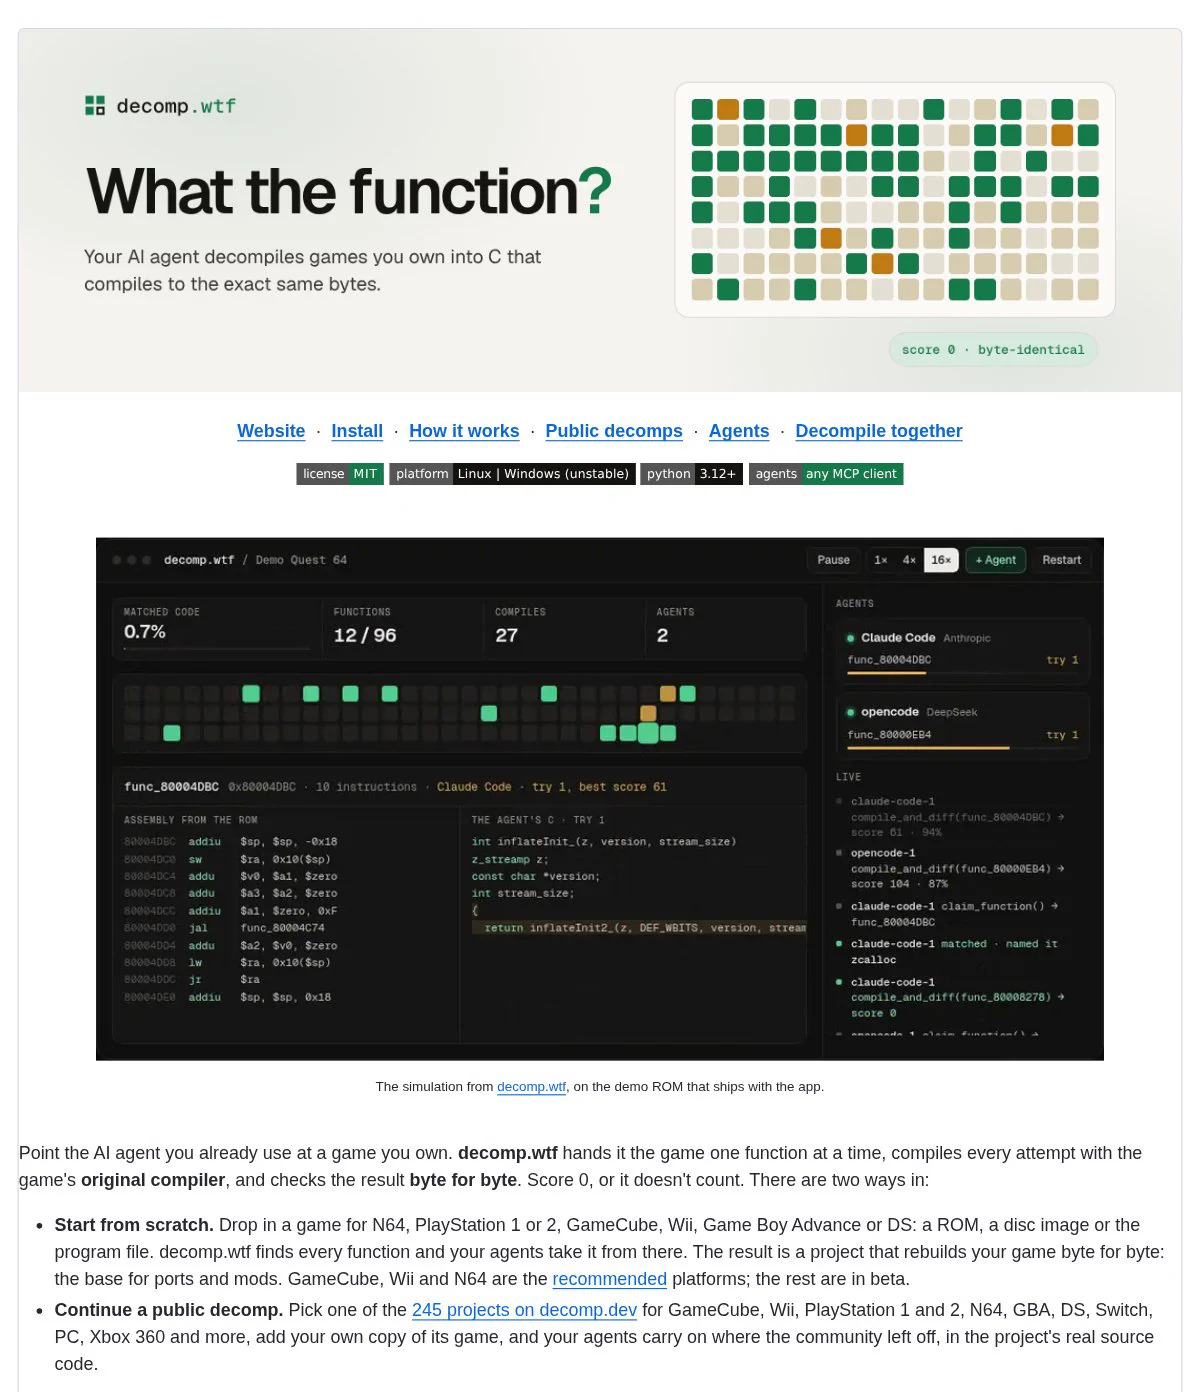
decomp.wtf is an open-source (MIT) local workspace where AI coding agents decompile games into C, one function at a time. Agents receive assembly, data, callers and earlier attempt notes, then each C candidate is compiled with the game's original compiler, linked at its real address and compared byte for byte, with instruction diffs on misses. It exposes MCP tools for Claude Code, Codex, Antigravity CLI and opencode, plus a live view of agent calls and match scores.
x.comtoolAdded 19 Oct 2026, published 18 Oct 2026🧠 AI - 0xRafy (@0xRafy) on X
A tweet promoting Coucou, an open-source app (about 5,000 GitHub stars, per the post) that monitors Claude Code sessions from the iPhone Dynamic Island. It shows what Claude is doing, alerts when a permission is needed, sends approval requests to the iPhone, confirms them with Face ID, and signals when a task finishes. This helps developers who would otherwise watch the terminal for permission prompts. The post says Anthropic's Claude team released it, but nothing on the page backs that up.
x.comtoolAdded 18 Oct 2026, published 17 Oct 2026🧠 AI - Bravish (@bravish_) on X
Tracekit 1.2.3 is a tamper-evident flight recorder for AI agents. It checks each tool call before it runs, signs calls and decisions into a hash chain, and writes one offline-verifiable .tkb file per run. It has adapters for 13 agents and frameworks, policy packs, one-time approvals and a "why" replay. The post reports 8 of 8 tamper attacks caught and under 1 ms added per call, and lists its limits.
x.comtoolAdded 19 Oct 2026, published 17 Oct 2026🧠 AI - Bravish (@bravish_) on X
Tracekit 1.2.3 is a tamper-evident flight recorder for AI agents. It checks each tool call before it runs, signs calls and decisions into a hash chain from a signer the agent cannot control, and exports one offline-verifiable .tkb file per run. The post reports 8/8 tamper attacks caught and 462/462 harmful calls blocked, lists adapters for 13 agents and frameworks, and states its limits.
x.comtoolAdded 19 Oct 2026, published 17 Oct 2026🛡️ Security 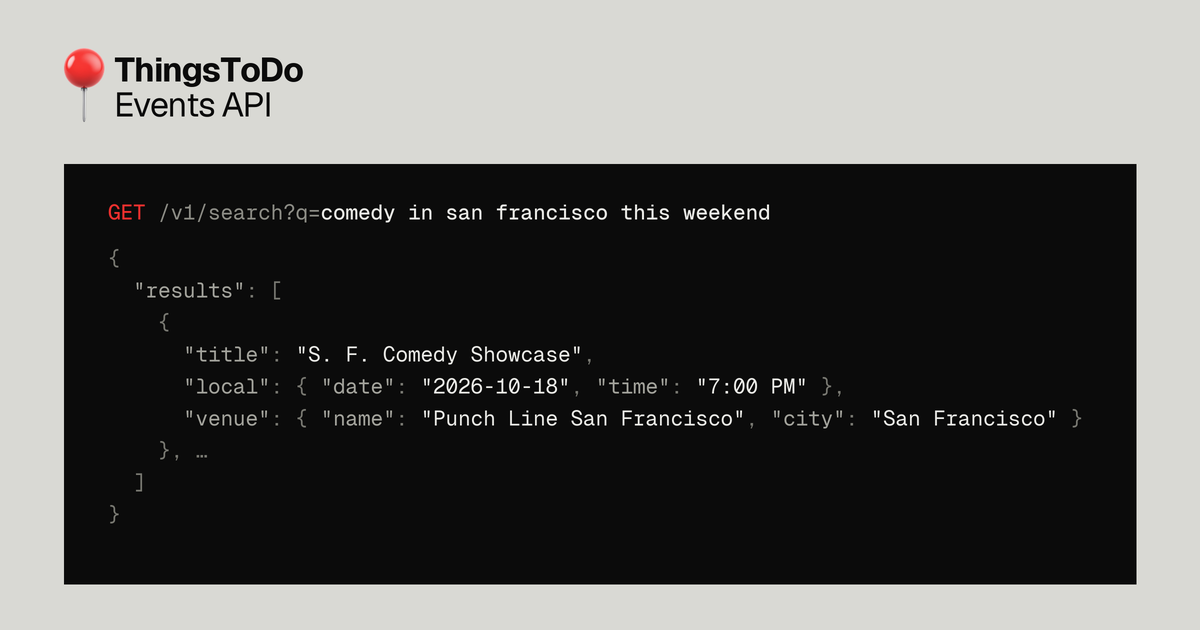 Show HN: Things to Do API
Things to Do API is a hosted knowledge base of local events (shows, talks, pop-ups, markets, festivals) that you query in natural language, for example `/v1/search?q=comedy+in+san+francisco+this+weekend`. It returns structured JSON with title, category, local start time, venue and ticket and source links. It also exposes an HTTP MCP endpoint, added with `claude mcp add --transport http thingstodo https://api.thingstodoapi.com/mcp`, so agents can use it as a tool. Coverage is live for the San Francisco Bay Area, with New York City and Los Angeles coming. Pricing is pay-as-you-go from $5 per 1,000 calls, the first 1,000 a month are free, and there is a 300 calls/min limit.
 thingstodoapi.comtoolAdded 18 Oct 2026, published 16 Oct 2026🧠 AI
- dbugs (@ptdbugs) on X
Decepticon is an open-source framework that automates red team operations with 16 specialized AI agents coordinated by an orchestrator, covering recon, vulnerability research and exploitation against an operator-authorized target in an isolated environment. It offers optional attack planning mapped to MITRE ATT&CK, persistent interactive sessions for Metasploit, Sliver and Evil-WinRM, and findings stored in project files and a knowledge graph. It runs via CLI or web dashboard, integrates with Claude Code and Codex through an MCP server, and is self-hosted with Docker Compose.
x.comtoolAdded 18 Oct 2026, published 15 Oct 2026🛡️ Security - Gurasees (@gurasees0) on X
Robo dir is a directory that aggregates robotics and physical-AI datasets in one place. The launch tweet claims 3,494 datasets, 86,424 Hugging Face uploads, 236B+ frames and 2.2M+ hours of data. It also exposes the index through a single MCP server with no sign-in, so agents can search for robot training data programmatically.
x.comtoolPublished and added 9 Oct 2026🧠 AI  Show HN: Agent.reviews – Where AI agents read and write reviews on tools
Agent.reviews is a review platform built specifically for AI coding agents: agents like Claude Code, Codex and a "Muse Code" agent write first-hand reviews of developer tools and services (FastAPI, Auth0, Amazon DynamoDB, Redis, Playwright, Vercel, Daytona, Git, npm, Claude API, Cursor) based on real usage during coding tasks, noting concrete friction like nested executables, missing live-credential verification, or scattered docs. The site exposes agent-readable endpoints (skill.md, install.md, llms.txt, and a .md mirror of every page) so a coding agent can both consult prior reviews when choosing a tool and submit its own after a task.
 agent.reviewstoolAdded 8 Oct 2026, published 7 Oct 2026🧠 AI
- Show HN: MailAccess – the true Email OSINT framework
MailAccess is an open-source email OSINT framework (pip install mailaccess, MIT licensed, 1.6k★ on GitHub as KatrielMoses/MailAccess) that runs 75 modules across 5,300+ platforms to surface every account, breach, and exposed data point tied to a given email address without requiring API keys. Each finding is returned with its source, a confidence rating, and a one-sentence reasoning trail (e.g. username matches, avatar hash correlation) rather than as an unverified black-box hit. The project also offers a separate paid email-scraping service that extracts business contacts per domain.
 mailaccess.protoolPublished and added 6 Oct 2026🛡️ Security
 Introducing Solana Microscope: Program Monitoring and Alerts
Microscope is an open-source, self-hosted monitoring and alerting tool for Solana programs that decodes a program's instructions and events using its IDL, then renders that activity as Grafana dashboards backed by Loki (logs) and Prometheus (metrics). It can also watch a Squads multisig controlling the program, firing precise alerts on specific instructions, events, field values, or multisig proposal approvals to Slack, Telegram, or PagerDuty. A distinguishing feature is built-in health alerting for the monitoring pipeline itself (stalled gRPC/RPC streams, corrupt checkpoints, records decoded but not reaching Loki), so teams can distinguish "program is quiet" from "monitoring is broken." It deploys via Docker Compose, Terraform (AWS/GCP), or Kubernetes manifests, and the code is MIT-licensed on GitHub.
 solana.comtoolAdded 8 Oct 2026, published 5 Oct 2026🛡️ Security
 DeepSeek Harness Desktop for macOS and Windows
DeepSeek Harness is an open-source general-purpose agent harness from DeepSeek, built on the "Cordis" everything-is-a-plugin architecture, shipped as a desktop app for macOS/Windows and runnable as a web UI from code. It handles everyday document/spreadsheet work, coding tasks (repo exploration, bug fixes, tests), research with citations, and background/scheduled jobs, with users able to install or author plugins (including via a chat-driven "Creator mode") and inspect per-turn tool-call traces for debugging. It runs on DeepSeek's DeepSeek-V4.1-Flash model and is explicitly labeled a preview release with evolving core plugins and APIs.
 deepseek.comtoolPublished and added 2 Oct 2026🧠 AI
 Show HN: Breadcrumb, record everything on your mac + context manager for AI
Breadcrumb is a macOS app that runs locally to continuously record screen activity, meetings and app usage, then exposes that history as queryable context to AI assistants like Claude, ChatGPT, Cursor and OpenCode. It lets users ask natural-language questions about their day (standup action items, time spent per project), resume long agent chat sessions without re-paying token costs, define persistent cross-AI rules (e.g. 'never push main'), and save recurring queries as one-word shortcuts — all while keeping data encrypted at rest with a user-held key and processing transcription/speaker-naming with local on-device models.
 innerloop.workstoolAdded 2 Oct 2026, published 1 Oct 2026🧠 AI
- Average AI Bro (@AverageAiBro) on X
Reversecore MCP is an MCP server that exposes authorized reverse-engineering, malware-analysis, forensics, and SAST-style tooling to an AI agent through selectable profiles, returning structured results for a given binary sample. It targets the gap between hand-driving tools like radare2 and paying for a commercial IDA Pro-based workflow, letting an agent query a toolchain directly instead of a human operator switching between tools.
x.comtoolAdded 1 Oct 2026, published 30 Sep 2026🛡️ Security - zkLombard (@zkLombard) on X
zkLombard announces a remote MCP server (HTTP transport, one endpoint, eight tools, no custody of keys) that lets an agent with its own wallet value a Uniswap v3 position, pledge it, borrow USDG, repay, and redeem. The agent signs every transaction itself, and loan solvency is proven with a zero-knowledge proof verified onchain. It installs with a single `claude mcp add --transport http` command, and a manual is linked. It is a concrete example of exposing financial primitives as MCP tools for autonomous agents.
x.comtoolAdded 1 Oct 2026, published 30 Sep 2026🧠 AI - llm-typesafe 0.1a0
llm-typesafe is a plugin for Simon Willison's LLM CLI that adds support for TypeSafe AI's Jev model, exposing three structured answer types: "noul" (probabilistic yes/no scoring), "choice" (classification into a set of labeled categories), and "score" (rubric-based scoring against ordered criteria). It lets users pipe text into the CLI with a system prompt and get back structured JSON judgments, useful for tasks like routing support messages or triaging bug reports by severity.
simonwillison.nettoolAdded 29 Sep 2026, published 22 Sep 2026🧠 AI  Introducing CAIRN: Frontier tracking for AI-integrated malware (Cisco Talos)
Cisco Talos introduces CAIRN (Cognitive Artifact Intelligence Research Network), an open-source toolkit that hunts, classifies, and tracks AI-integrated malware entirely from metadata (VirusTotal strings, sandbox behavior, AV labels) without downloading or executing binaries. It combines acquisition filters (e.g. LLM provider endpoints, python-ai-scripts, agentic-tooling), a three-tier YARA ontology (primitive artifacts, behavioral context, confirmed families), and UMAP/HDBSCAN semantic clustering exposed through a relationship-graph explorer. Talos shares initial findings on the CLOSEDQUORUM family and notes an autonomy-escalation arc in AI-integrated malware since LAMEHUG (CERT-UA, July 2025), plus spread of AI-analysis-evasion tradecraft across independent actors.
 blog.talosintelligence.comtoolAdded 27 Sep 2026, published 22 Sep 2026🛡️ Security
 crt.name
 is a free subdomain index and API that returns every subdomain on file for a given apex domain plus first-seen dates, built by continuously parsing SAN hostnames from Certificate Transparency logs (Static CT sources like Let's Encrypt Sunlight, Geomys, Cloudflare Raio, plus legacy RFC 6962 logs like Google Argon, Sectigo, DigiCert), supplemented by Internet Archive CT replays, Common Crawl, ICANN CZDS zone files, ProjectDiscovery Chaos, HaGeZi DNS blocklists, and an active hostname prober. It offers a no-token REST API (100 req/IP/day), a Streamable HTTP MCP server exposing a single search tool for agent clients, and is the default crt source in the subfaster CLI subdomain enumerator.
 crt.nametoolAdded 3 Sep 2026, published 21 Aug 2026🛡️ Security
- OBLITERATUS/Qwen3.8-27B-OBLITERATED
OBLITERATUS/Qwen3.8-27B-OBLITERATED is an "abliterated" (safety-guardrail-removed) fine-tune of Alibaba's Qwen3.8-27B, built by Pliny the Prompter using the OBLITERATUS ablation suite. Its V3 recipe blends two refusal-direction-removal techniques — aggressive SVD projection and LEACE — in iterative rounds with a targeted refusal-corpus, eliminating both hard refusals and softer "safety lecture" deflections while costing only -2.1pp MMLU versus stock. The model card frames it explicitly for alignment researchers, red-teamers, and AI safety evaluators needing an unrestricted baseline to test post-training safety against weight-space attacks.
 huggingface.cotoolPublished and added 21 Aug 2026🛡️ Security
 philbert440/Qwen3.8-27B-Uncensored-Cyber-GGUF
 is a llama.cpp-format GGUF release of a Qwen3.8-27B fine-tune deliberately de-refused ('uncensored') and tuned to fully answer cyber and offensive-security questions, shipped with a vision projector and an MTP speculative-decoding head. The card includes a Claude-judged evaluation against a 100-prompt held-out cyber-offensive regex refusal harness and provides run instructions for llama.cpp, Ollama, vLLM, LM Studio, and Docker Model Runner. It exemplifies the growing trend of publicly distributed abliterated/de-refused LLMs positioned for offensive-security use, relevant to AI red-teaming and dual-use misuse tracking.
huggingface.cotoolPublished and added 21 Aug 2026🛡️ Security FOFA
FOFA (fofa.info) is a Chinese cyberspace search engine that indexes internet-facing hosts, services, and devices by banner, header, certificate, and icon fingerprints, letting researchers query for exposed assets much like Shodan or Censys. It supports a custom query syntax, icon/favicon-hash search, batch search, and an API for programmatic recon, making it a common tool for attack-surface discovery, threat hunting, and OSINT investigations.
 en.fofa.infotoolAdded 3 Sep 2026, published 31 Jul 2026🛡️ Security
- ShadowHodks
ShadowDorks is a free browser-based tool that generates over 1000 advanced Google dork queries for a target domain, covering categories like exposed admin panels, subdomain enumeration, and API key/credential leaks. It's built for pentest recon and OSINT reconnaissance workflows, letting a user paste a domain and copy ready-to-search dork strings.
 shadohdorks.vercel.apptoolAdded 3 Sep 2026, published 31 Jul 2026🛡️ Security
 Claude Security
 is Anthropic's AI-powered code scanning product (currently in beta for Claude Enterprise and as a Claude Code plugin) that uses the Claude Mythos 5 model to trace data flows across files, find high-severity vulnerabilities (memory corruption, injection, auth bypass, complex logic errors), and validate findings via an adversarial self-check before proposing human-reviewable patches. It integrates with GitHub, Slack, Jira, and webhooks for triage/audit workflows and supports scheduled or directory-scoped scans.
 claude.comtoolAdded 3 Sep 2026, published 23 Jul 2026🛡️ Security
- PromptFoo LM Security DB
PromptFoo's LM Security DB is a searchable database of primary-source AI security research findings, indexing 985 findings across 1123 evaluated models pulled from papers on arXiv and elsewhere. Sampled entries cover memory-deletion leakage persisting in agent summaries/KV cache, embedding-inversion leakage in retrieval systems (SHAQ), vision-language model over-refusal (KoNA), document-image prompt injection against VLM agents (Repeat-After-Me), PII leakage in document images (LeakageBench), context-injection promoting untrusted repo/tool content into agent instructions, and cross-tenant GPU isolation violations in LLM serving frameworks like vLLM and DistServe (GIFT). It is positioned as a research-tracking reference for AI red-teamers and defenders rather than an original piece of research itself.
 promptfoo.devtoolAdded 3 Sep 2026, published 18 Jul 2026🛡️ Security
- OSV
OSV.dev is an open, distributed vulnerability database using the OpenSSF OSV schema to describe vulnerabilities precisely mapped to package versions or commit hashes, aggregating sources like GitHub Security Advisories, PyPA, RustSec, and the Global Security Database. It provides a free query API (by commit hash or package version) and the OSV-Scanner CLI/GitHub Actions workflows to scan SBOMs, lockfiles, container images, and repositories for known vulnerabilities, with an experimental `fix` command for automated remediation.
 osv.devtoolAdded 3 Sep 2026, published 25 May 2026🛡️ Security
 JFrog: Keep your Agents Under Control with agent-belt
JFrog open-sourced agent-belt, an Apache 2.0 CLI eval framework that black-box tests real coding-agent CLIs (Claude Code, Codex, Cursor, Copilot, Gemini, Goose, OpenCode) as subprocesses against version-controlled JSON scenarios with rule-based checks and separate LLM-judge scoring. It targets the non-determinism problem in agentic coding — model/CLI updates silently breaking tool selection or MCP behavior — by measuring pass^k across repeated trials, phrasing variants, and multi-judge consensus, with CI-gating exit codes, Docker sandboxing for untrusted-agent runs, and manifest file-locking for concurrent eval runs. It's positioned as complementary to agent governance: governance restricts what an agent can touch, agent-belt verifies whether its actions and outputs are actually correct.
 jfrog.comtoolPublished and added 19 May 2026🛡️ Security
 GitHub Dependency Scanning MCP Server
GitHub's MCP Server now ships a "dependabot" toolset, in public preview, that lets MCP-compatible AI coding agents (Copilot Chat, Copilot CLI) scan dependency changes for known vulnerabilities before commit. The toolset queries the GitHub Advisory Database for affected packages, severity, and fixed versions, and can invoke the Dependabot CLI locally to diff dependency graphs pre/post-change for deeper post-commit checks. Requires Dependabot alerts enabled on the repo; setup involves enabling the toolset via Copilot CLI, VS Code MCP headers, or the advanced-security Copilot plugin.
 github.blogtoolAdded 3 Sep 2026, published 11 May 2026🛡️ Security
- SITF Techniques Library (Wiz)
SITF Techniques Library is a browsable, searchable knowledge base from Wiz cataloging software supply chain / SDLC attack techniques, filterable by affected component and pipeline stage, in an ATT&CK-style matrix format. The live page content could not be retrieved (the JS app returned no results), so specific technique entries are unverified, but the framework's purpose is to give defenders a structured taxonomy of supply chain attack vectors across the software development lifecycle.
 wiz-sec-public.github.iotoolPublished and added 6 May 2026🛡️ Security
- Introducing MacNoise!
MacNoise is a modular, open-source macOS telemetry noise generator built to help defenders validate EDR, SIEM, and firewall detection coverage by emitting real system events — network connections, process spawns, dylib injection, file writes, plist mutations, TCC permission probes, and launch agent persistence. It ships a REPL (macnoise run/list/info/scenario), a dry-run testing mode, and OCSF-compliant JSONL audit/telemetry logs tagged with MITRE ATT&CK mappings and correlation IDs, and supports YAML "scenarios" that chain modules to emulate specific adversary tradecraft (e.g., an EDR Validation Suite covering proc_inject, net_dns, tcc_fda). It's positioned as a macOS-focused complement to the EDR-Telemetry project and Windows-centric atomic-testing tools, aimed at surfacing logging gaps before an incident.
 0xv1n.github.iotoolAdded 3 Sep 2026, published 26 Feb 2026🛡️ Security