- Md Ismail Šojal 🕷️ (@0x0SojalSec) on X
An x64dbg MCP server, published on GitHub by duty1g and shared in an X post by @0x0SojalSec, lets Claude drive the x64dbg Windows debugger. It exposes breakpoints, memory dumps and code stepping as tools for reverse engineering and malware analysis. A reply warns that debugging a sample executes it, so the agent should run in a snapshotted VM with no shared folders or host route, and every command should be logged.
 x.comrepoAdded 3 Nov 2026🧠 AI
- colibri: pure-C engine for running huge MoE models by streaming experts from disk
colibri is a pure-C, dependency-free inference engine that runs mixture-of-experts models of hundreds of billions of parameters on ordinary machines. It keeps the dense layers in RAM and streams routed experts from disk through a learning cache, with optional CUDA, Vulkan and Metal tiers. It supports GLM-5.2, Kimi K3, DeepSeek V4, Qwen3.6 and GGUF files, and serves OpenAI- and Anthropic-compatible APIs.
 github.comrepoAdded 3 Nov 2026🧠 AI
- rikugan: LLM reverse-engineering agent for IDA Pro and Binary Ninja
Rikugan is a reverse-engineering agent that runs inside IDA Pro and Binary Ninja. It has its own generator-based agent loop, context management, plan mode and 60+ tools, and does not depend on an external MCP server. An orchestrator spawns parallel subagents to analyze a binary. It supports Anthropic, Gemini, MiniMax, Kimi, OpenAI-compatible endpoints and Ollama, with per-model notes.
github.comrepoAdded 30 Oct 2026🧠 AI - rikugan: LLM reverse-engineering agent for IDA Pro and Binary Ninja
Rikugan is an open-source reverse-engineering agent that runs inside IDA Pro 9.0+ and Binary Ninja, with its own agent loop instead of an MCP server. It has 60+ tools (decompiler, xrefs, strings, types, IL/microcode), parallel subagent exploration, an experimental /modify natural-language patching command and an experimental Binary Ninja deobfuscation skill for control flow flattening and opaque predicates. It supports Claude, Gemini, MiniMax, Kimi, OpenAI-compatible endpoints and Ollama.
github.comrepoAdded 30 Oct 2026🛡️ Security - Show HN: I Turned DOOM into a Transformer
Doomformer compiles integer neural networks into ZDoom maps that run in ViZDoom. Voodoo dolls do the arithmetic, and sector light levels and plane heights hold the values. Python reads every value back and compares it with a NumPy integer reference at tolerance 0. It runs MNIST (97.16 % on all 10,000 digits, every pass exact), small transformers, a learning perceptron and a SUBLEQ machine. It is about 23,000 times slower than NumPy on a small MLP.
github.comrepoAdded 30 Oct 2026, published 29 Oct 2026🧠 AI - Show HN: Overtone – Transcribe, correct and cut captions for any screen shape
Overtone is a caption format (.overtone.json), a CLI and a video.js plugin that store each spoken word once and cut captions separately per screen shape (16:9, 9:16 or custom). The transcribe pipeline combines gpt-transcribe, Azure AI Speech and optional ElevenLabs Scribe, resolves disagreements with an LLM vote, and uses an LLM editor for corrections. A small public benchmark reports 5.3% word error rate and $0.023–0.025 per audio minute.
github.comrepoAdded 30 Oct 2026, published 29 Oct 2026🧠 AI - Show HN: Hob - Open-source, on device alternative to Claude Cowork and ChatGPT
Hob is an MIT-licensed desktop app from Frigade that runs open-weight models such as Gemma and gpt-oss locally on Mac, Windows and Linux. It picks the best open-weight model that fits the user's computer and sets it up. It is positioned as a free, private, offline alternative to Claude and ChatGPT for tasks like filling out PDFs and working through documents. The page gives no technical detail on its runtime.
github.comrepoAdded 27 Oct 2026, published 26 Oct 2026🧠 AI - alirezarezvani/claude-skills
claude-skills is an MIT-licensed library of about 398 Claude Code skills, agents, personas and plugins across 20 domains, including engineering, marketing, compliance and C-level advisory. Each skill is a SKILL.md with stdlib-only Python CLI tools and reference docs. Install scripts and convert.sh adapt it to Codex, Gemini CLI, Cursor, Aider, Windsurf and other coding agents, and it includes a skill-security-auditor scanner.
github.comrepoAdded 25 Oct 2026🧠 AI - Show HN: OnKey – I'm a bad singer, so I built an app to show where I'm off-key
OnKey is a free, MIT-licensed singing trainer for Apple Silicon Macs. After a song ends in Spotify, Apple Music or browser YouTube, it separates the lead vocal with UVR's MDX-Net Karaoke 2, tracks pitch with CREPE and turns it into syllable-level notes with the GAME model. On later plays it scrolls the notes, draws the user's live pitch and scores each line. Analysis runs on-device, and the repo explains the build steps and network requests.
github.comrepoAdded 24 Oct 2026, published 22 Oct 2026🧠 AI - OpenAI CLI
OpenAI CLI is OpenAI's official Go command-line client for the REST API. It lets users generate images, upload and download files, create and wait on batches, call the Responses API, and query admin usage endpoints from a terminal or shell script. It supports JSON, JSONL and YAML output, GJSON transforms, shell completion, and install via Homebrew, go install or release binaries.
github.comrepoAdded 23 Oct 2026, published 22 Oct 2026🧠 AI - Show HN: Omnara – Open-source alternative to Claude Managed Agents
Omnara is an open-source, self-hostable managed agent platform, an alternative to Claude Managed Agents and OpenAI's Agents API. It runs agents on any model (OpenAI, Anthropic, OpenRouter, Bedrock, LiteLLM, Ollama) and any machine, with Postgres-backed durable state, stateless workers, per-tool permissions, MCP, skills, memory, subagents, schedules and Slack, Discord and GitHub triggers. It ships a REST API, TypeScript SDK, CLI and Docker Compose setup.
github.comrepoAdded 23 Oct 2026, published 21 Oct 2026🧠 AI - Cyber Detective💙💛 (@cyb_detective) on X
Python Cybersecurity Libraries is a curated GitHub list by Yogsec, shared in a post by cyb_detective. It groups Python libraries by task: network analysis, penetration testing, threat intelligence, reverse engineering and malware analysis, forensics and investigation, web application security, CTF, and machine learning for security. The tweet shows only the category names, not the individual libraries.
x.comrepoAdded 24 Oct 2026, published 21 Oct 2026🛡️ Security - ikow/php2shell-poc
php2shell-poc is a proof-of-concept and detection toolkit for CVE-2026-109618 and CVE-2026-109619, two PHP vulnerabilities tied to session.upload_progress handling and a Zend engine out-of-memory bailout path affecting PHP 5.4.0 through 8.5.11. The repository includes three working exploit chains, a Docker-based lab (PHP-FPM, nginx, Apache mod_php) for reproduction, and pre-built Suricata, Sigma, ModSecurity, and Lua detection rules. The author recommends disabling session.upload_progress as an interim mitigation, noting the underlying memory corruption requires a full PHP patch to fix.
github.comrepoAdded 23 Oct 2026, published 21 Oct 2026🛡️ Security - Show HN: VoidAccess – open-source dark web OSINT, from query to a graph
VoidAccess is a self-hosted, MIT-licensed dark web OSINT platform that runs a 13-step pipeline from a research query to a relationship graph. It collects from Tor indexes, paste sites, code forges, security feeds and .onion seeds, applies content-safety filters, and exports STIX 2.1, MISP, Sigma, YARA, Snort, Suricata, CSV and JSON. It runs as a CLI with SQLite or as a Docker Compose stack with PostgreSQL, FastAPI and Next.js.
github.comrepoAdded 21 Oct 2026, published 20 Oct 2026🛡️ Security - DeepInfer: High-performance inference framework for DeepSeek models
DeepInfer is DeepSeek's open-source inference framework for offline inference of DeepSeek-V4.1-Flash, released under Apache 2.0. It covers attention data parallelism, MoE expert parallelism with load balancing, draft-token decoding with confidence-scheduled verification, batch-invariant inference, deterministic sampling and structured outputs. It runs on NVIDIA SM100 GPUs and Huawei Ascend 950 NPUs. The KV cache system, prefill/decode disaggregation and load balancing are not included.
github.comrepoAdded 21 Oct 2026, published 20 Oct 2026🧠 AI - Saylor (@Kev96790724) on X
G-Krusch is an MIT-licensed, local-first Google Workspace hub built on Node.js 22 and SQLite WAL. It runs a 12-tool MCP server (SSE and Stdio) plus a REST bridge on port 5446 for Drive, Calendar and Gmail. It includes a 1,024-dimension hybrid Drive RAG with an embedding cascade (Ollama bge-large, then Gemini, then offline fallback) and FTS5 BM25. PDF extraction returns page citations. Tokens are kept in an AES-256-GCM vault; 30 of 30 tests pass.
x.comrepoAdded 21 Oct 2026, published 19 Oct 2026🧠 AI - alex09x/kyb
KYB (Know Your Business) is a Rust/axum server that stores agent-written knowledge, incident reports and tasks as Markdown files in Git, one commit per change. Search is hybrid: Tantivy BM25 fused by reciprocal rank with local multilingual-e5-small ONNX vectors, and it can query historical versions or "as of" a date. It ships a kyb CLI, a native MCP endpoint (Claude Code, Codex, Antigravity, Gemini CLI), an installable agent skill, token auth with per-write attribution trailers, secret scanning on writes, and a web console. It targets persistent shared operational memory for multi-agent, multi-machine fleets.
github.comrepoAdded 17 Oct 2026🧠 AI - enisaeu/enisa-sbd-playbook
ENISA repository of 22 Secure by Design and Secure by Default playbooks for SMEs building products with digital elements. Each playbook has a principle, objective, checklist, minimum evidence and release gate, covering design, build, deployment, maintenance and decommissioning. It supports progressive adoption and CRA readiness without replacing legal obligations.
github.comrepoAdded 17 Oct 2026🛡️ Security - AikidoSec/safe-chain
Aikido Safe Chain is an open-source local proxy and shell-alias wrapper for npm, yarn, pnpm, bun, pip, uv, poetry, pipx and pdm. It checks every package download, including deep dependencies, against the Aikido Intel malware feed and blocks malicious packages before install. It also enforces a configurable 48-hour minimum package age by suppressing too-new versions in registry metadata. It supports custom registries and a self-hosted malware-list mirror, and has CI/CD install recipes for GitHub Actions, Azure Pipelines, CircleCI, Jenkins, Bitbucket and GitLab.
github.comrepoAdded 17 Oct 2026🛡️ Security - OpenMOSS/MOSS-Image
MOSS-Image is an open-source text-to-image model family from OpenMOSS with a 5B backbone, released October 2026 as MOSS-Image-Base and MOSS-Image-SFT. It supports JSON layout control with bounding boxes, text rendering inside images, and prompts up to 4K tokens. The repo gives a Diffusers pipeline, a Gradio app, a ComfyUI plugin, LoRA training guidance, a prompt-enhancer skill and day-0 SGLang and vLLM-Omni support.
github.comrepoAdded 20 Oct 2026, published 16 Oct 2026🧠 AI - Show HN: Graphicle, a Rust port of Graphify with memory for coding agents
Graphicle is a local-first Rust program that parses a repository into a tree-sitter code graph (a port of Graphify) and adds project memory: docs, reviewed decisions and captured Claude Code/Codex sessions. It serves cited file-and-line excerpts within a token budget via one MCP server, CLI and browser app, backed by a single SQLite file, with no API key or telemetry. The README reports a code-only extract on Kubernetes (31k files) in 3m18s versus 26m38s for Graphify 0.9.88, and a memory comparison against seven systems. Agent-proposed memories need user approval and go stale when the code they reference changes.
github.comrepoPublished and added 14 Oct 2026🧠 AI - Show HN: SolidCraft – Open-Source Parametric CAD in Rust (With MCP Support)
SolidCraft is an open-source parametric 3D CAD application written in pure Rust. It has constrained sketches with its own solver, a feature timeline, assemblies, sheet metal, and STEP/IGES/3MF/STL export. It runs on desktop (egui+wgpu), in the browser, and as a headless CLI. The built-in MCP server (`solidcraft-cli mcp`) gives agents tools such as execute, batch, inspect_design, measure, set_parameter, screenshot and export. They can model headless or drive the running app over a JSON-lines control channel. A rover with 3,323 timeline steps was built entirely through MCP, which shows agent-driven parametric modelling working at scale.
github.comrepoPublished and added 13 Oct 2026🧠 AI - zero-lab-ai/skills
zero-lab-ai/skills is a collection of 56 portable SKILL.md agent skills in 10 installable plugins from zero-lab.ai. They cover authorized defensive assessment, penetration testing, red teaming, detection engineering, purple teaming and engagement operations. Skills install via the Claude marketplace layout or `npx skills add`, and a make check release gate runs linting and tests.
github.comrepoAdded 23 Oct 2026, published 11 Oct 2026🛡️ Security - sepehr071/iran-mcp
iran-mcp is an open-source catalog of 39 MCP servers (488 tools) that let AI agents query Iranian websites such as Digikala, Torob, Divar, Snappfood, Jabama, Paziresh24, TSETMC and qavanin.ir, with prices normalised to Toman. Most servers are unofficial, read-only Python packages run with uvx; three are official hosted servers. It ships Claude Code plugins, Agent Skills, bundles, proxy lists and a machine-readable servers.json.
github.comrepoAdded 24 Oct 2026, published 11 Oct 2026🧠 AI - Talorys – A self-hosted personal AI agent on Cloudflare's free tier
Talorys is an open-source, single-user personal AI assistant deployed with one command (npx create-talorys) into the user's own Cloudflare account. It uses a Cloudflare Agents SDK Durable Object with SQLite for conversations, memories, tasks, notes and automations, Workers AI (@cf/zai-org/glm-4.7-flash) for streaming chat with tool calling, and Durable Object alarms for reminders and scheduled AI routines. It stays within the Workers Free plan, with a private Worker behind a Pages Function service binding, owner-password auth, per-day AI usage guardrails, and fallback to non-AI features when quota runs out.
github.comrepoPublished and added 10 Oct 2026🧠 AI - morluto/awesome-reverse-engineering
awesome-reverse-engineering is a CC0 curated list of reverse-engineering tools and learning resources, organized by task: triage, native analysis, debuggers, instrumentation, deobfuscation, malware analysis, mobile, firmware, file formats, games, diffing, symbolic execution, lifting and AI agents. Each entry notes licensing, maintenance status and prerequisites. It also covers MCP integrations, CTF practice sites and related awesome lists.
github.comrepoAdded 27 Oct 2026, published 9 Oct 2026🛡️ Security - Show HN: Edi Life OS – self-hosted life dashboard with an MCP server for AI
Edi Life OS is a self-hosted dashboard (PHP 8.1+, MySQL, vanilla JavaScript) that combines focus timer, habits, goals, Kanban tasks, finances and notes in ten workspaces. It includes an optional Node.js MCP server that exposes 15 tools over stdio. The tools let Claude Desktop, Claude Code or Codex read the dashboard, create goals and tasks, log habits and record expenses. The MCP server calls only the app's bearer-token /api/v1 HTTP API and never touches the database or credentials. The README is candid about limits: the token has no scopes, there is no app-level rate limiting, and the secret-note flag is only a visibility setting, not encryption.
github.comrepoPublished and added 9 Oct 2026🧠 AI - mattpocock/skills — agent skills for engineers
mattpocock/skills is a collection of small, composable "agent skills" for software engineering that install into Claude Code, Codex, GitHub Copilot, Gemini CLI, Cursor, OpenCode, Devin, Windsurf, Amp and Pi via plugin managers or the `npx skills` CLI. It packages practices like interview-driven requirement gathering (/grill-me, /grill-with-docs), domain-model/glossary building, test-driven development with red-green-refactor (/tdd), bug diagnosis loops, codebase architecture improvement, ticket triage and spec-to-implementation workflows (/to-spec, /to-tickets, /implement, /implement-spec), splitting skills into user-invoked orchestrators and model-invoked reusable disciplines. It's built by Matt Pocock as an alternative to heavier process-owning frameworks like GSD, BMAD and Spec-Kit, aiming to keep engineers in control while giving coding agents better feedback loops and shared vocabulary.
github.comrepoAdded 8 Oct 2026🧠 AI - Dark Web Informer (@DarkWebInformer) on X
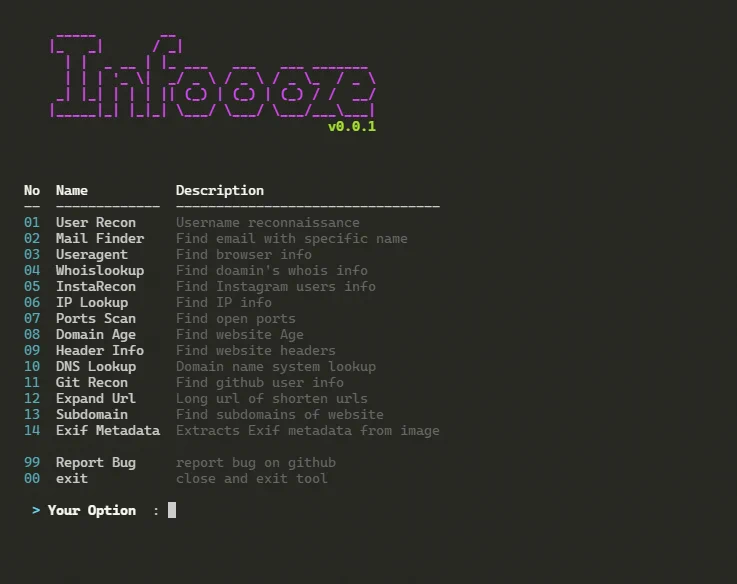
Infoooze is an open-source command-line OSINT reconnaissance toolkit (github.com/devxprite/infoooze) that consolidates common footprinting tasks into one CLI: username enumeration across platforms, email discovery, subdomain enumeration, port scanning, WHOIS/DNS lookups, IP/HTTP header analysis, EXIF metadata extraction, GitHub recon, and URL scanning/expansion. It automatically saves results, making it a lightweight all-in-one alternative to running several separate recon tools.
x.comrepoPublished and added 8 Oct 2026🛡️ Security - microsoft/mxc
MXC is Microsoft's cross-platform sandboxed code execution system for running untrusted workloads — model output, plugins, and tool calls — behind a unified containment model with Rust, .NET, and Node SDKs. It offers multiple containment backends (ProcessContainer, Windows Sandbox, LXC, Bubblewrap, Seatbelt, MicroVM/Nanvix, Hyperlight, WSLC) with JSON-based filesystem, network, and UI policies, plus diagnostics like audit mode for building policies from observed access.
github.comrepoAdded 8 Oct 2026🧠 AI - chainguard-dev/malcontent
malcontent is Chainguard's open-source malware/supply-chain discovery tool that analyzes binaries (ELF, Mach-O, PE, a.out) and scripting-language source across Linux, macOS and Windows using 14,500+ YARA rules (including third-party rules from Avast, Elastic, FireEye, Mandiant, Nextron and ReversingLabs). Its standout feature is differential analysis ("mal diff"), which compares two versions of a build artifact or OCI image against a known-good baseline to surface newly introduced risky behaviors — the technique the project demonstrates on the 3CX supply-chain compromise by flagging unexpected high-risk changes to libffmpeg. It also supports threshold-based scanning ("mal scan") and unfiltered capability enumeration ("mal analyze"), and is designed to run inside CI/CD pipelines, including air-gapped environments via embedded rules.
github.comrepoAdded 8 Oct 2026🛡️ Security - target/strelka
Strelka is Target's open-source, container-based real-time file scanning system for threat hunting, threat detection, and incident response, built in Go and Python. It runs 50+ scanners (YARA, PE parsing, encrypted ZIP cracking, entropy analysis, etc.) to extract metadata and content from files at enterprise scale, which can feed a SIEM for alerting on suspicious artifacts like an Emotet-laden encrypted ZIP payload.
github.comrepoAdded 8 Oct 2026🛡️ Security - deepfence/YaraHunter
YaraHunter is Deepfence's open-source scanner that applies YARA rulesets against container images, running Docker containers, and filesystems to detect indicators of compromise such as malware and cryptominers. It supports CI/CD build-time scanning, at-rest image scanning, and runtime container scanning, with JSON output for automation, and is designed to eventually integrate into the Deepfence ThreatMapper platform. The README walks through detecting the XMRig cryptominer inside a container image as a worked example.
github.comrepoAdded 8 Oct 2026🛡️ Security - Port of the TypeScript compiler, checker and lsp to Rust, by LLM
ts-rust (npm package tsc-rs) is a from-scratch Rust port of Microsoft's TypeScript compiler/checker/language server (typescript-go), produced almost entirely by LLM coding agents rather than hand-written. The author first spent over $400,000 in API tokens running GPT-5.6 Sol and GPT-6 Astra in long agentic '/goal' loops, which wrote 1.3M lines of Rust but plateaued at ~84% compatibility; switching to Claude Opus 5.5 produced a working version in 10 hours and, after ~$24,000 of further API spend over two weeks, reached 100% compatibility on tested real-world projects while passing all 181,711 ported Go baseline tests. Benchmarks show the Rust port running about 1.6x faster than the Go tsc 7 compiler (though slower than Bun's native `bun check`) across dozens of open-source codebases including VS Code, TanStack Query, Sentry and T3 Code.
github.comrepoPublished and added 8 Oct 2026🧠 AI - Show HN: NanoMuse – An open-source AI agent for your phone and computer
nanoMuse is an open-source personal AI agent that runs across phone, desktop, and web, built on an on-device sandbox (OpenMinis with proot/Alpine Linux on mobile) and the DeepSeek Harness on desktop with a Python runtime for tool use. Devices share one account and sync conversations through a relay (self-hostable), while the agent proactively acts, retains memory, and pauses before irreversible actions; it is released GPL-3.0-or-later with documentation on install, self-hosting, connectors, and memory.
github.comrepoPublished and added 7 Oct 2026🧠 AI - Show HN: OpenChart – OSS TradingView alternative with your own AI agent
OpenChart is an open-source TradingView-style desktop charting app (Electron, Node.js/Bun, Effect runtime) that embeds AI agents into statistical/technical analysis, real-time market alerts and agentic opportunity research. It ships a custom DSL called Tea (inspired by TradingView's Pine Script) for writing indicators, and a conversation interface built on assistant-ui and the AG-UI event protocol so users converse with agents while charting.
github.comrepoPublished and added 6 Oct 2026🧠 AI - browser-use/jev-ultrafast
jev-ultrafast is an open-source browser automation agent (from Browser Use) that represents each page as an indexed element table and uses a 'TypeSafe' policy to speculatively predict both the next operation (CLICK, TYPE_TEXT, SELECT, SCROLL, WAIT, DONE, BLOCKED) and its target in a single network round trip, only invoking a small LLM (e.g. inception/mercury-2.5 via OpenRouter) to generate text when the operation is TYPE_TEXT. The repo includes a local inspector UI, Chrome automation via a 'Browser Harness' tool, offline tests, and published before/after benchmarks showing a Google Flights search dropping from a median 9.45s to 7.09s and browser protocol calls from 1,092 to 101 across repeated runs.
github.comrepoAdded 6 Oct 2026🧠 AI - overmind-core/overmind
Overmind is an open-source platform (MIT SDK/CLI, AGPL-3.0 platform, self-hostable) that instruments an agent's code via OpenTelemetry tracing, turns the resulting production traces (or any dataset) into a fine-tuned model benchmarked against user-defined eval metrics, and serves it through one unified API with downloadable/retrainable weights. It ships an SDK, CLI, REST API, Console, and an MCP server exposing project tools and workflows (investigate-capability, finetune-capability, ship-model) for Cursor, Claude Code, OpenCode and Codex, and can sync traces from Langfuse, LangSmith, Braintrust or Galileo; self-hosting runs via Docker Compose with Postgres, Redis, Celery workers and Modal-based GPU workers for fine-tuning/serving (vLLM).
github.comrepoAdded 6 Oct 2026🧠 AI - claude-mem — persistent memory system for Claude Code and other coding agents
Claude-Mem is an open-source persistent memory plugin for Claude Code and other coding agents (Codex, OpenCode, Grok Bot, T3 Code, OpenClaw) that captures tool-usage observations during sessions, compresses them into semantic summaries, and reinjects relevant context into future sessions. It uses five lifecycle hooks (SessionStart, UserPromptSubmit, PostToolUse, Stop, SessionEnd), a local SQLite database, a Chroma vector store for hybrid semantic+keyword search, and exposes three MCP tools (search, timeline, get_observations) that follow a token-efficient layered retrieval pattern to cut context costs roughly 10x. It is Apache-2.0 licensed, built with the Claude Agent SDK and TypeScript, and ships an optional hosted "observer" memory service alongside self-hosted options via OpenRouter/Gemini keys or an Anthropic plan.
github.comrepoAdded 5 Oct 2026🧠 AI - Dark Web Informer (@DarkWebInformer) on X
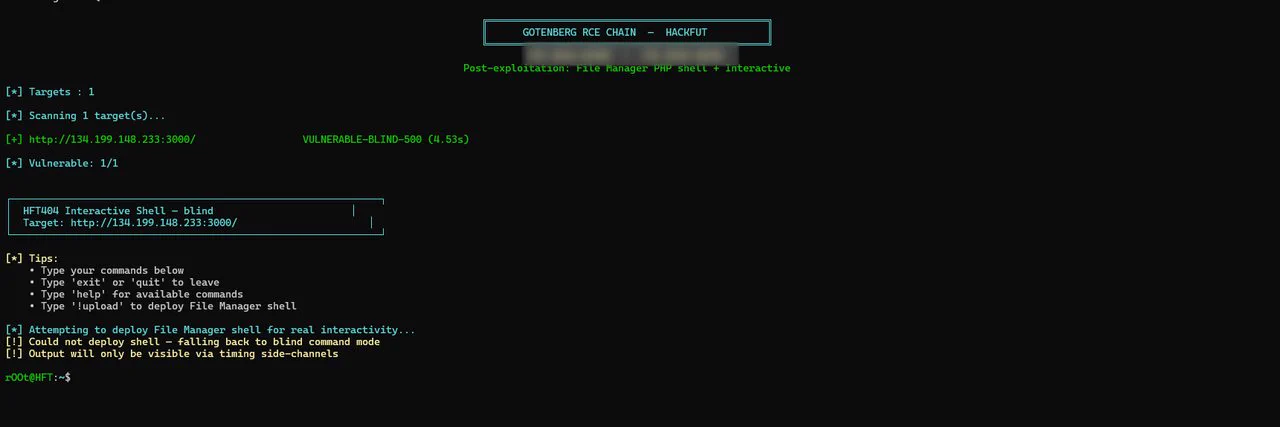
A public PoC chains CVE-2026-42589 and CVE-2026-40281 to achieve unauthenticated remote code execution against Gotenberg (a document/PDF-conversion microservice), abusing metadata injection flaws in the /forms/pdfengines/metadata/write endpoint. The tool supports vulnerability detection, interactive command execution, reverse shell delivery, and multi-target scanning against Gotenberg versions ≤8.30.1 (patched in 8.31.0).
x.comrepoPublished and added 5 Oct 2026🛡️ Security - DeepZero
DeepZero is an open-source orchestration engine that lets researchers define vulnerability-research pipelines declaratively in YAML, handling parallel execution (ThreadPoolExecutor), resumable/fault-tolerant state, and LLM-assessment stages via LiteLLM/Jinja2 prompts. It ships example processors for Ghidra headless decompilation, LOLDrivers.io hash exclusion filtering, PE header/driver metadata extraction, and batch Semgrep scanning, with a dedicated pipeline for BYOVD kernel driver vulnerability research. An extensibility model lets users plug in custom Python processors referenced by path in the YAML config.
github.comrepoAdded 3 Oct 2026🛡️ Security - Sigma r2026-07-01 — 20 new detection rules
GitHub release notes for Sigma r2026-07-01, the open-source detection-rule repository, adding 20 new rules (e.g. LSASS crash via Netlogon buffer overflow CVE-2026-41089, TanStack supply-chain attack indicators for Windows/Linux, RedTail cryptominer user-agent detection, AF_ALG kernel crypto API exploit indicator) and updating/fixing dozens of existing rules for ARM64 binary variants, file-sharing domain IOCs, and WMI-based reconnaissance/persistence detection. It's a routine but substantive update to a widely-used blue-team detection content pack.
github.comrepoAdded 3 Oct 2026🛡️ Security - jiwoochris/artex-global
ARTEX global edition is an English-default fork of the Chinese open-source ARTEX (AGPL-3.0), an autonomous penetration-testing system in which planner and worker LLM agents run real tools and record results in an asset graph and an exploration graph on PostgreSQL. It also ships a defense guide, Sigma and Suricata rules, an ATT&CK Navigator layer, MISP indicators and a host triage script for spotting ARTEX-driven attacks.
github.comrepoAdded 31 Oct 2026, published 3 Oct 2026🛡️ Security - Jakeschincariol/replica-skill
replica-skill is an MIT-licensed set of eleven Claude skills that run an app-cloning pipeline: recon, architect, design, build, backend, test, diff, entrepreneur, brand, launch and deploy. Six standard-library Python tools handle image diffing, parity scoring, review ranking, contrast checks, rebrand sweeps and store-listing lint. It installs as a Claude Code plugin or by copying folders, and states clean-room and rebranding limits.
github.comrepoAdded 29 Oct 2026, published 3 Oct 2026🧠 AI - OKX Agent Trade Kit (okx-trade-mcp / okx-trade-cli)
OKX Agent Trade Kit is an open-source MCP server (okx-trade-mcp) and CLI (okx-trade-cli) that let AI assistants like Claude Desktop, Cursor, Claude Code and VS Code place trades and query account data on the OKX exchange via natural-language commands. It runs locally with API keys never leaving the machine, supports module scoping (market, spot, swap, account, earn), a read-only mode for safe querying, multiple profiles, and includes pre-built skill files for agent frameworks plus structured JSON error reporting for debugging failed tool calls.
github.comrepoAdded 2 Oct 2026🧠 AI - Show HN: Made an open-source Lego AI generator
ldraw-nova is an open-source agentic pipeline where an LLM agent (tested with models like Claude Opus 5.5 and GPT-6 Astra) takes a build prompt, reads LDraw-building instructions, and produces a plan.json describing a model's geometry. From that plan it writes a Python generator script that, when executed, outputs an LDraw (.mpd) 3D CAD source file, viewable in 3D/VR (Meta Quest 3) or exportable to Blender-editable glTF. The agent uses jev-rerank, a semantic search tool with reranking backed by TypeSafe's Jev System One model, to find suitable LEGO parts and example models, falling back to full-text search without an API key; it also uses headless rendering and collision/gap detection to self-inspect and iterate on designs.
github.comrepoAdded 3 Oct 2026, published 2 Oct 2026🧠 AI  Kyutai Pocket TTS
Pocket TTS is a 100M-parameter text-to-speech model from Kyutai designed to run efficiently on CPU, generating audio faster than real-time (~6x on a MacBook Air M4) with ~200ms latency to first audio chunk and voice cloning from short audio samples. It supports English, French, German, Portuguese, Italian, and Spanish, ships a Python library and CLI, and has spawned numerous community ports (WASM, ONNX, Rust/Candle, MLX, C++, C#) and fine-tuned language variants (Czech, Hindi, Korean, Persian, Indonesian, Estonian, Welsh, Polish).
 huggingface.corepoAdded 2 Oct 2026🧠 AI
 Tencent Hy4 preview (open-weight MoE + Sherry quantization)
Hy4 preview is Tencent's new flagship Mixture-of-Experts language model: 770B total parameters with 49B activated per token across 78 layers (256 routed experts + 1 shared expert, top-8 routing), plus a native 10B multi-token-prediction layer for speculative decoding. It introduces Gated DeepSeek Sparse Attention with IndexCache for cross-layer index reuse and identity Hyper-Connections (iHC) on the residual path, and in blind internal evaluations on engineering tasks it edges out GLM-5.3 and Kimi K3. Weights (including an FP8 variant) are released under Apache 2.0 on Hugging Face with vLLM/SGLang deployment recipes and AngelSlim-based quantization/compression tooling.
huggingface.corepoAdded 2 Oct 2026🧠 AI- zzzz7788990213-ops/EvoVLM
EvoVLM searches over prompts, image preprocessing, generation budgets and answer extraction for frozen Qwen3-VL-2B-Instruct and Qwen3-VL-2B-Thinking, without fine-tuning weights. A local Qwen model ranks a catalog of typed mutations, a trusted renderer produces Python programs, and Pareto selection on accuracy and latency drives two small generations on scientific chart understanding (CharXiv subset). Recorded results on Dev128: Evolved Instruct keeps accuracy with 8.9% lower median latency, and Evolved Thinking gains 16.41 points of accuracy with 10.6% lower median latency. CPU-only replay and fail-closed evidence verification are included. The authors state the limits: small sample, overlap with the evolution set, and results tied to the recorded hardware.
github.comrepoAdded 16 Oct 2026, published 2 Oct 2026🧠 AI - CAIRN — Cisco Talos AI-Malware-Hunting Toolkit
CAIRN is a Cisco Talos research toolkit that identifies and attributes AI-integrated malware purely from VirusTotal metadata — no binary downloads or detonation — by running a tiered YARA ontology (T1/T2/T3) over composed scan text (AV strings, PE resources, Sigma/sandbox behavioral data, embedded URLs) and layering on sentence-transformer embeddings with HDBSCAN clustering for semantic family attribution. It has produced confirmed family reports for AI-malware such as PROMPTLOCK, LAMEHUG, PROMPTSTEAL, QUIETVAULT, CLOSEDQUORUM, and FRUITSHELL, each cross-verified by hands-on Talos reverse engineering before publication.
github.comrepoAdded 30 Sep 2026🛡️ Security - Launch HN: Magnitude (YC S25) – Self-optimizing inference engine for agents
Magnitude is an open source local inference engine (Apache 2.0) that compiles and tunes its GPU/CPU kernels on the user's exact device before a model runs, claiming up to 2x faster decode than llama.cpp (92% faster on Metal, 19% on CUDA) with 27% lower memory per agent. It ships as a cross-platform desktop app with a bundled CLI and an OpenAI-compatible API, offering one-click connections to agent tools like Pi, OpenCode, Hermes, Codex, OpenClaw, Claude Code, and Cline, running fully offline on Apple Silicon, NVIDIA, AMD, or CPU-only hardware.
github.comrepoPublished and added 30 Sep 2026🧠 AI - rehan-remade/universal-modder
universal-modder is a set of Agent Skills, a CLI (um) and a shared knowledge base (field notes in knowledge/) that let AI coding agents such as Claude Code, Codex, Gemini CLI, Cursor, GitHub Copilot and OpenCode find a PC game's engine, reverse-engineer its code, build a working mod, generate art/3D/sound assets via the fal MCP server (or a local ComfyUI server), test the mod in the running game, and write a field note for the next agent. It ships worked examples — a weapon/boss pack for Terraria via tModLoader, a new civilization for Age of Empires II DE, and a real-time Minecraft-inside-GTA-V passthrough mod — each documented with a field note of exact versions, routes and gotchas, and agents can open pull requests to grow the shared knowledge base.
github.comrepoAdded 6 Oct 2026, published 30 Sep 2026🧠 AI  Ternary-Bonsai-2-27B: 27B model compressed to ~1.75 bits/weight, 98.2% of FP16 quality retained
Ternary-Bonsai-2-27B is a 27B-parameter reasoning model (built on Qwen3.8-27B) quantized to true ternary weights ({-1,0,+1}) at ~1.72 bits/weight, shrinking it from ~54GB FP16 to ~5.95GB while retaining 98.2% of FP16 benchmark quality (84.78 vs the conventional sub-4-bit IQ2_XXS build's 72.59). It uses a Hadamard-rotated weight basis and ships two GGUF packing formats (PTQ1_0 dense trits, PQ2_0 2-bit slots) that require a custom llama.cpp/MLX kernel fork since stock llama.cpp cannot decode them correctly. The card includes per-category benchmark breakdowns (math, coding, agentic tool calling), cross-platform throughput/power measurements (Apple M5 Pro/Max, RTX 5090, L4, H100/A100/Blackwell), and an "intelligence density" metric comparing capability retained per GB against FP16 and other quantizations.
huggingface.corepoAdded 29 Sep 2026🧠 AI MiMo-V2.6 (Xiaomi): Pro/Flash/9B-distill open-weight release, MIT license, 1M context
Hugging Face collection for Xiaomi's MiMo-V2.6 model family, comprising five open-weight checkpoints: MiMo-V2.6-Pro-RL (1T params), MiMo-V2.6-Flash-RL (311B params), a MiMo-V2.6-Distill-Qwen-9B distillation (vision-language capable), and Pro/Flash MOPD variants. The title claims MIT licensing and a 1M-token context window, positioning this as a large open-weight release spanning full-scale RL-trained models down to a 9B distilled variant usable on consumer hardware.
huggingface.corepoAdded 29 Sep 2026🧠 AI- https://github.com/dmdhrumilmistry/security-harness
security-harness is an open-source Claude Code plugin (also packaged for Gemini CLI, Codex and opencode) that orchestrates subagents — sh-recon, sh-hunter, sh-chainer, sh-verifier, sh-reporter — through a static-analysis pipeline covering 15 vulnerability classes (IDOR/BOLA, SQLi, XSS, SSRF, injection, auth, deserialization, path traversal, secrets, CSRF, XXE, open redirect, crypto, race conditions, file upload), producing README/JSON/SARIF/HTML/PDF reports with PoCs, CVSS and CWE/OWASP mappings. It also ships sh-pr-review, a per-PR merge-gate skill that posts inline findings and a commit status scoped only to code the PR itself introduced or aggravated, with caching, dedup via fingerprints, and a scheduled GitHub Action that keeps its per-class knowledge bases fresh by having one AI agent draft updates from allowlisted sources (OWASP, PortSwigger Research, CWE/CAPEC, HackerOne) while a separate adversarial reviewer agent fails-closed against prompt injection before auto-merge.
github.comrepoAdded 2 Oct 2026, published 29 Sep 2026🛡️ Security - StartLuxLabs/StartLux-Decision
StartLux-Decision is a family of open decision models (0.8B to 27B, plus a 35B-A3B mixture of experts) that return probabilities for every option of typed choice, yes/no and score questions. The repository holds the inference engine and HTTP server (vLLM plugin, /v1/systemone API), with Instant one-pass and AutoThink gated-reasoning variants. Reports first place of 174 entries on Decision Index 0.3.2 (69.12). Code is Apache 2.0; weights are CC BY-NC 4.0.
github.comrepoAdded 23 Oct 2026, published 29 Sep 2026🧠 AI - Uncensored and Offensive Security AI Models Benchmark
A curated GitHub list of open-weight "uncensored" and security-fine-tuned LLMs intended for authorized red teaming, pentesting, and security research, covering models like WhiteRabbitNeo's DeepHat V2, BugTraceAI-CORE, CYBER-FROST, and several abliterated Qwen/GLM/DeepSeek variants. It explains the underlying techniques (abliteration per Arditi et al. 2024, QLoRA/DPO fine-tuning, GGUF/FP8 quantization) and links to Hugging Face model cards, benchmark suites (CyberBench, TrustedSec's LLM Attack Benchmark vs OWASP Juice Shop), and deployment platforms for running these models locally or via API.
github.comrepoAdded 2 Oct 2026, published 29 Sep 2026🛡️ Security - Uncensored and Offensive Security AI Models Benchmark
A GitHub README curating open-weight "uncensored" and security-fine-tuned LLMs (e.g. WhiteRabbitNeo's DeepHat V2, BugTraceAI-CORE, CYBER-FROST, CyberPal2.0, Lily-Cybersecurity-7B, Dolphin-Llama3-8B, Wizard-Vicuna-13B-Uncensored, huihui-ai's abliterated Qwen variants) with HuggingFace download links, quantization formats (GGUF, FP8, Q4_K_M, Q6_K), and training techniques used (SFT, QLoRA, DPO, abliteration, MoE/MTP architectures). It also includes a glossary explaining abliteration (orthogonalizing the refusal direction out of the residual stream, per Arditi et al. 2024) and references benchmarks like CyberBench and TrustedSec's LLM Attack Benchmark, making it a practical reference for anyone sourcing or deploying refusal-removed models.
github.comrepoAdded 2 Oct 2026, published 29 Sep 2026🧠 AI - openrig — multi-agent Claude Code/Codex orchestration
OpenRig is an open-source local daemon/CLI/TUI/MCP server that orchestrates teams of Claude Code and Codex agent sessions (via tmux) defined declaratively in YAML "RigSpecs." Its own docs disclose a significant trust/permission footprint: it writes workspace-trust settings and status-line/activity hooks into ~/.claude.json and .claude/settings.local.json, pre-writes Codex trust hashes and trusted workspace entries into ~/.codex/config.toml, defaults Claude to --permission-mode acceptEdits and Codex to -s workspace-write, and supports an explicit OPENRIG_YOLO=1 mode that enables Claude's --dangerously-skip-permissions or Codex's -s danger-full-access. It also relays session/activity telemetry to a local daemon endpoint.
github.comrepoAdded 28 Sep 2026🛡️ Security - openrig — multi-agent Claude Code/Codex orchestration
OpenRig is an open-source local daemon, CLI, TUI and MCP server (built on tmux + SQLite) that manages teams of Claude Code and Codex agent sessions as a single persistent system rather than a pile of terminal windows. Topologies (pods, seats, edges) are defined declaratively in YAML (RigSpec/AgentSpec), booted with `rig up`, inspected via a topology TUI, and can be snapshotted/restored, discovered from existing tmux sessions, and messaged across agents (`rig send`, `rig broadcast`, `rig chatroom`). It ships starter topologies (first-project, conveyor, product-team, secrets-manager using HashiCorp Vault) and documents in detail what it writes to Claude/Codex config, trust and telemetry state on the host machine.
github.comrepoAdded 28 Sep 2026🧠 AI


Showing 60 of 315
Show more