 David Gutierrez | Eng (@david_x_ai) on X
Thread on two October 2026 npm compromises: @subql/common 5.8.3 (5 October), published through GitHub Actions OIDC Trusted Publishing after the attacker tampered with the publish workflow, and tensorlake 0.5.144 (8 October), published by the project's own release workflow with valid provenance for about 1 hour 40 minutes. Both ran on install and stole cloud, GitHub, Kubernetes, Vault, SSH and .env credentials; tensorlake also took AI tool and MCP config. Its payload installed a gh-token-monitor service that deletes the home directory if the stolen GitHub token is revoked, so remove it before rotating.
 x.comthreadAdded 27 Oct 2026, published 26 Oct 2026🛡️ Security
 Launch HN: Alter (YC S25) – Access control for multi-user agents
Alter is a privileged access management layer for AI agents (YC S25). It stores credentials in a vault, injects them per request through a proxy, gives each agent its own identity and scoped grants, and logs every call to a tamper-evident audit trail. One SDK call covers storage, refresh, policy and audit for 140 API providers, with LangChain, MCP and AWS integrations. Policy is default-deny down to the parameter, with human approval for risky calls.
 alterauth.comtoolAdded 22 Oct 2026, published 21 Oct 2026🧠 AI
 PQ-Vault: Provably Quantum-Safe Asset Custody for Unmodified Ethereum
PQ-Vault is a custody design for unmodified Ethereum against quantum key recovery. It combines a quantum-safe vault contract, a proof-of-stake sidechain with compact certificates, and an optimistic dispute protocol. The paper proves that compact certificates with classically chosen parameters fall from 128 to about 60 bits against quantum attackers, and bounds a seed-update stake-steering attack. For 65,536 validators a certificate is 0.8 MB and verifies in about 20 ms, and the vault accepts a checkpoint for about 420,000 gas.
 arxiv.orgpaperAdded 24 Oct 2026, published 21 Oct 2026🛡️ Security
- DFIR Radar (@DFIR_Radar) on X
DFIR_Radar weekly detection engineering digest covering 23 new and 19 updated rules across 6 GitHub repositories. It lists KQL rules for Azure Key Vault secret retrieval, MCP client User-Agent bulk operations and local Azure token theft, AWS CloudTrail analytics, Sigma rules for firewall and ETW tampering (decimal 17 vs hex 0x11), updated LOLDrivers hashes, and Sublime email rules for OAuth consent phishing and fake IRS W-9 PDFs.
x.comthreadAdded 20 Oct 2026, published 19 Oct 2026🛡️ Security - Saylor (@Kev96790724) on X
G-Krusch is an MIT-licensed, local-first Google Workspace hub built on Node.js 22 and SQLite WAL. It runs a 12-tool MCP server (SSE and Stdio) plus a REST bridge on port 5446 for Drive, Calendar and Gmail. It includes a 1,024-dimension hybrid Drive RAG with an embedding cascade (Ollama bge-large, then Gemini, then offline fallback) and FTS5 BM25. PDF extraction returns page citations. Tokens are kept in an AES-256-GCM vault; 30 of 30 tests pass.
x.comrepoAdded 21 Oct 2026, published 19 Oct 2026🧠 AI  ARMORY CASTLE Exploits BeyondTrust
ARMORY CASTLE (formerly UNC5221), a suspected PRC-nexus actor, exploited BeyondTrust Remote Support zero-day CVE-2026-102764 in August 2026, per Mandiant incident response. The post details the SAWFLY PHP webshell, BARECLAW SOCKS5 WebSocket tunneler, SUID root escalation, sudoers template persistence, vault credential extraction, log deletion and haproxy.conf changes. It adds YARA rules, detection ideas and patch-first remediation (BT26-05).
 cloud.google.comwriteupAdded 29 Oct 2026, published 15 Oct 2026🛡️ Security
- ♫Why♥Not♪ (@Python_s_) on X
Alert summarizing Socket Threat Research's disclosure that a malicious version of the Tensorlake npm SDK (an AI-agent infrastructure package) was published with a preinstall hook delivering Shai-Hulud/ChainDrop credential-stealing malware. The payload targets GitHub, npm, AWS, Kubernetes and Vault credentials, persists via a gh-token-monitor mechanism, and spreads through compromised publishing accounts. It lists IOCs (lib/setup.mjs, lib/Math_Symbol.js) and warns to remove the persistence before revoking stolen GitHub tokens, since revocation triggers a destructive routine. Socket detected the release about 11 minutes after publication.
x.comadvisoryAdded 11 Oct 2026, published 9 Oct 2026🛡️ Security  Tensorlake npm Package Compromised to Spread Shai-Hulud Worm
The tensorlake npm package, version 0.5.144 released 8 October 2026, carried a new Shai-Hulud worm variant, per Aikido's analysis. A preinstall script runs node lib/setup.mjs, downloads Bun and launches lib/Math_Symbol.js, which steals cloud, CI/CD, SSH, Vault, browser and crypto-wallet secrets. It reaches C2 iseekaigogo[.]com or an Ethereum smart-contract dead drop, and has a wipe dead-man's switch tied to a GitHub token.
 cybersecuritynews.comarticleAdded 19 Oct 2026, published 8 Oct 2026🛡️ Security
 Tensorlake npm package compromised by Shai-Hulud in latest software supply chain attack | Blog | Endor Labs
Endor Labs documents the compromise of tensorlake@0.5.144, the official npm TypeScript SDK for Tensorlake, which shipped a Shai-Hulud worm payload via a poisoned preinstall hook (node lib/setup.mjs) after the project's main branch was altered and pushed through a legitimate, provenance-signed GitHub Actions release pipeline. The malware harvests npm, GitHub, SSH, cloud (AWS/GCP/Azure), Kubernetes/Docker and Vault credentials, uses an EtherHiding Ethereum wallet as a durable dead-drop to fetch its rotating C2 domain, and republishes itself into other packages the victim controls. The writeup includes affected package versions, file hashes, C2 indicators, and concrete remediation guidance (pin to 0.5.143, rotate credentials, disable install scripts).
 endorlabs.comadvisoryPublished and added 8 Oct 2026🛡️ Security
 Tensorlake npm Package Compromised: A Worm With a Hostage Token That Wipes Your Machine If You Revoke It
StepSecurity details how tensorlake@0.5.144 was pushed to npm after malicious commits landed directly on the tensorlakeai/tensorlake GitHub repo's main branch under a maintainer's identity, carrying a valid npm provenance attestation despite being malicious. The preinstall hook downloads Bun to run an obfuscated payload that steals GitHub/npm tokens, cloud and Vault/Kubernetes secrets, SSH keys, browser logins, and AI-tool configs (Claude, Cursor, Windsurf), then self-propagates by republishing stolen npm packages and committing persistence files (.claude/settings.json, .vscode/tasks.json) to reachable repos. A "hostage token" mechanism installs a gh-token-monitor service that runs a home-directory wipe if the stolen GitHub token is revoked before the monitor is removed, inverting the normal incident-response order.
 stepsecurity.iowriteupPublished and added 8 Oct 2026🛡️ Security
 SubQuery Ecosystem Compromise: Hidden Credential Theft and Backdoors
StepSecurity's investigation of @subql/common@5.8.3, a malicious npm release in the SubQuery Web3 indexing framework's monorepo, found a heavily obfuscated postinstall/import-time payload (base64+XOR+gzip inside a function constructed via Function()) that spawns a detached worker to steal credentials (.npmrc, .env, AWS, SSH, kubeconfig, Vault, cloud secrets), read GitHub Actions runner memory for CI secrets, inject a camouflaged "Run Copilot" GitHub Actions workflow to exfiltrate repo secrets, and provide a remote shell/PTY over an encrypted channel to ci-artifacts.dev. The release was published via a compromised build pipeline: a workflow modification swapped the real build output for an externally downloaded, unsigned tarball from that same C2 domain immediately before publish, and the authors provide IOCs and remediation steps (credential rotation, host isolation, domain blocking).
stepsecurity.iowriteupPublished and added 5 Oct 2026🛡️ Security Ethereum Now Lets You Pay for AI Without Revealing Who You Are
The Ethereum Foundation and the Open Anonymity Project launched zkAPI on Ethereum mainnet: users deposit ETH/USDC into a vault contract and generate zero-knowledge proofs of sufficient, unspent balance to receive capped, short-lived API keys for AI services (currently routed through OpenRouter), so the AI provider never learns payer identity and the payment layer never learns prompt content. The design follows a February 2026 Ethereum Research proposal by Davide Crapis (Ethereum Foundation dAI team lead) and Vitalik Buterin, who had earlier proposed the ERC-8004 agent-identity standard; the protocol is explicitly labeled experimental with no formal audit, and a companion browser-based client (OA Chat) is open source on GitHub.
 decrypt.coarticleAdded 3 Oct 2026, published 2 Oct 2026🛡️ Security
- Ethereum Now Lets You Pay for AI Without Revealing Who You Are
The Ethereum Foundation and the Open Anonymity Project launched zkAPI on Ethereum mainnet: users deposit ETH or USDC into a vault contract, then generate a zero-knowledge proof of sufficient, unspent funds to obtain a capped, short-lived API key, letting them call AI models through OpenRouter without the provider linking their prompts to a billing identity. The protocol (based on a February 2026 Ethereum Research proposal by Davide Crapis and Vitalik Buterin) issues signed usage receipts after the key expires to settle actual spend, and ships with a browser chatbot (OA Chat) and an open GitHub repo; it is explicitly labeled experimental with no formal audit yet. The same proof-based metering pattern is proposed for other metered services like blockchain data queries, image/video generation, and machine-to-machine payments.
decrypt.coarticlePublished and added 2 Oct 2026🧠 AI  Ethereum Foundation Launches zkAPI for Private AI Payments
The Ethereum Foundation and the Open Anonymity Project launched zkAPI, a system that lets users prepay into an on-chain USDC vault and then generate zero-knowledge proofs to unlock short-lived, spend-capped API keys for AI models (and other metered services) without tying usage back to a billing identity. It ships a local client that mimics the OpenAI and Ollama APIs so existing apps can switch to account-free access with minimal changes, plus an in-browser client called OA Chat; funds remain withdrawable on-chain even if zkAPI's own servers go down. The design, originally sketched by Davide Crapis and Vitalik Buterin on Ethereum Research, still leaves IP address and prompt content visible to providers, so the team recommends Tor for stronger privacy.
 bankless.comarticlePublished and added 2 Oct 2026🧠 AI
- Binary Security: Azure Logic Apps cross-tenant compromises (One Root Case)
Third post in a series on Azure Logic Apps API Connections, describing five critical cross-tenant privilege escalations that let an attacker use any other tenant's connection to reach its backend (Key Vault, Azure SQL, Jira, Salesforce). Techniques include path traversal via ARM DynamicInvoke and undocumented DynamicList endpoints, and abusing the host.api.runtimeUrl parameter in Consumption Logic Apps, including a validation-before-normalization bypass. The author reports $200,000 in bounties; Microsoft fixed all issues.
 binsec.nowriteupAdded 30 Oct 2026, published 2 Oct 2026🛡️ Security
 Introducing zkAPI: private usage credits for any API
zkAPI, built by the Open Anonymity Project with the Ethereum Foundation, separates payment from identity for metered APIs, with AI inference first. Users deposit credits into an Ethereum vault contract and spend them as private notes. Groth16 proofs on BN254, Poseidon hashing, a 32-level Merkle tree and nullifiers authorize spends. The server mints short-lived, dollar-capped API keys, and signed usage receipts settle the metered amount. A local client exposes standard OpenAI and Ollama APIs, so existing apps work unchanged. The post also covers a proxy mode and the limits: network metadata and prompt-content fingerprinting can still link sessions.
 blog.ethereum.orgarticlePublished and added 1 Oct 2026🧠 AI
- Introducing zkAPI: private usage credits for any API
zkAPI, built by the Open Anonymity Project with the Ethereum Foundation, lets users deposit credits into an Ethereum vault contract once and then authorize bounded, metered API usage via zero-knowledge proofs instead of an API key tied to identity. The scheme uses Groth16 proofs over BN254, Poseidon-hashed note commitments in a 32-level Merkle tree, and one-way nullifiers to prevent double-spend while keeping spends unlinkable to deposits; a client mints short-lived, capped API keys locally and the server settles against the private balance via signed usage receipts. The post also candidly documents the system's limits: it doesn't anonymize network metadata/IP (mitigated by Tor) and doesn't prevent re-linking via prompt-content fingerprinting across sessions.
blog.ethereum.orgarticleAdded 7 Oct 2026, published 1 Oct 2026🛡️ Security - CAIRN — Cisco Talos AI-Malware-Hunting Toolkit
CAIRN is a Cisco Talos research toolkit that identifies and attributes AI-integrated malware purely from VirusTotal metadata — no binary downloads or detonation — by running a tiered YARA ontology (T1/T2/T3) over composed scan text (AV strings, PE resources, Sigma/sandbox behavioral data, embedded URLs) and layering on sentence-transformer embeddings with HDBSCAN clustering for semantic family attribution. It has produced confirmed family reports for AI-malware such as PROMPTLOCK, LAMEHUG, PROMPTSTEAL, QUIETVAULT, CLOSEDQUORUM, and FRUITSHELL, each cross-verified by hands-on Talos reverse engineering before publication.
 github.comrepoAdded 30 Sep 2026🛡️ Security
 A Clever RSA Attack Fooled a Hardware Vault—Here's What It Means for Crypto
Researchers at UC San Diego and INRIA demonstrated a chosen-message oracle attack that forges RSA signatures on a 1,024-bit key held inside a hardware security module (HSM) without ever extracting the key, by disabling the HSM's FIPS mode to get it to sign unpadded/unformatted values roughly 4 billion times and then computing the private-key operation from the responses (1,380 CPU core-years of work). The attack only applies to unpadded RSA signing oracles — standard PKCS#1 v1.5/PSS padding blocks it — so it doesn't threaten Bitcoin/Ethereum (which use ECDSA) but is relevant to anyone auditing HSM key-custody assumptions or RSA-based blind-signature schemes like Privacy Pass. The authors frame it as further classical evidence to accelerate migration away from RSA ahead of the post-quantum transition.
decrypt.coarticleAdded 30 Sep 2026, published 28 Sep 2026🛡️ Security- openrig — multi-agent Claude Code/Codex orchestration
OpenRig is an open-source local daemon, CLI, TUI and MCP server (built on tmux + SQLite) that manages teams of Claude Code and Codex agent sessions as a single persistent system rather than a pile of terminal windows. Topologies (pods, seats, edges) are defined declaratively in YAML (RigSpec/AgentSpec), booted with `rig up`, inspected via a topology TUI, and can be snapshotted/restored, discovered from existing tmux sessions, and messaged across agents (`rig send`, `rig broadcast`, `rig chatroom`). It ships starter topologies (first-project, conveyor, product-team, secrets-manager using HashiCorp Vault) and documents in detail what it writes to Claude/Codex config, trust and telemetry state on the host machine.
github.comrepoAdded 28 Sep 2026🧠 AI - 973 MCP Packages, 71% Single-Maintainer: A Practitioner
Suzu Labs guide to securing AI developer workflows across three surfaces: AI-generated code (Veracode 45% vulnerable, a formal-verification study at 55.8%), the MCP supply chain and credential exposure, and prompt injection in the context window. It cites 973 npm MCP packages (71% single-maintainer), 24,008 secrets in MCP configs on public GitHub, and the March 2026 axios hijack by UNC1069 that dropped WAVESHAPER.V2 and tampered with MCP configs. It lists CVEs for Copilot, Cursor and Claude Code, and gives controls: SAST on every commit, env/vault credential references, pinning MCP versions, minimal agent permissions, `.cursorignore`/Claude deny rules, and monitoring IDE DNS traffic.
 securityboulevard.comarticleAdded 26 Sep 2026🛡️ Security
 Inside IMD, Ethereum's New AI Swarm Experiment
Bankless profiles IMD (identity.md), an Ethereum project where holders of 2,000 NFTs register AI agents under the ERC-8004 identity/reputation standard, run a worker client wired to their own Claude or Codex subscription, and receive tasks from a lead orchestrator. Submissions are rebuilt in a sealed container to verify only allowed files changed, reviewed adversarially by other agents, logged onchain as reputation, and (as of the article) can be purchased by outside customers for 0.5 $IMD per job via the x402 payment rail, currently deploying only to Sepolia testnet. The surrounding token design — a Uniswap V4 CappedBurnHook that burns sell pressure, an ERC-4626 staking vault (sIMD), and an $IMD-denominated launchpad — is the article's main focus, framing the agent swarm as the productive backbone of a speculative token economy.
bankless.comarticleAdded 8 Oct 2026, published 25 Sep 2026🧠 AI Storm-3168: Agentic-driven cloud attacks using compromised service principals
Microsoft Security Research documents an Azure-focused campaign by Storm-3168 (aka JADEPUFFER, discovered by Sysdig as the first documented agentic ransomware operation), using two compromised service principals to enumerate an Azure tenant and then execute a seven-minute destructive sequence deleting 100+ Storage Accounts, a Key Vault, a Function App, and attempting (unsuccessfully, due to API version mismatch) to delete Azure SQL databases. Initial access traces to a client ID/secret/tenant ID leaked in a GitHub issue's public edit history even after the secret was redacted; the attacker also harvested storage account keys and targeted Site Recovery/Backup protection locks to impair recovery, consistent with ransomware/extortion tradecraft. The post includes a MITRE ATT&CK mapping (T1190, T1078.004, T1526, T1485, T1490) and mitigation guidance around workload identity hygiene, least privilege, and backup protection.
 microsoft.comwriteupAdded 7 Oct 2026, published 25 Sep 2026🛡️ Security
 Sckit Supply Chain Worm Hits MemTensor npm & PyPi scopes
StepSecurity documents a supply-chain attack against @memtensor/memos-cloud-openclaw-plugin on npm (versions 0.1.21, 0.1.23, 0.1.25) and MemoryOS 2.0.34 on PyPI, which insert a hidden "sckit" launcher into normal plugin/import lifecycle code (no install scripts) to spawn a platform-specific Go binary that harvests the parent process's environment and the user's AI prompt text. The Go payloads contain regex patterns for AWS, GitHub, GitLab, npm, PyPI, Hugging Face, Vault, Slack, Stripe and SendGrid credentials, target the user's home directory as an inventory root, and beacon to skyleen.fr "front" domains; the PyPI variant additionally hides a conditional build-backend/CI bridge that can steal PYPI_API_TOKEN during publishing and pull a hash-pinned, Ed25519-signed secondary payload via GitHub Actions. The writeup includes full IOC/remediation guidance.
stepsecurity.iowriteupPublished and added 23 Sep 2026🛡️ Security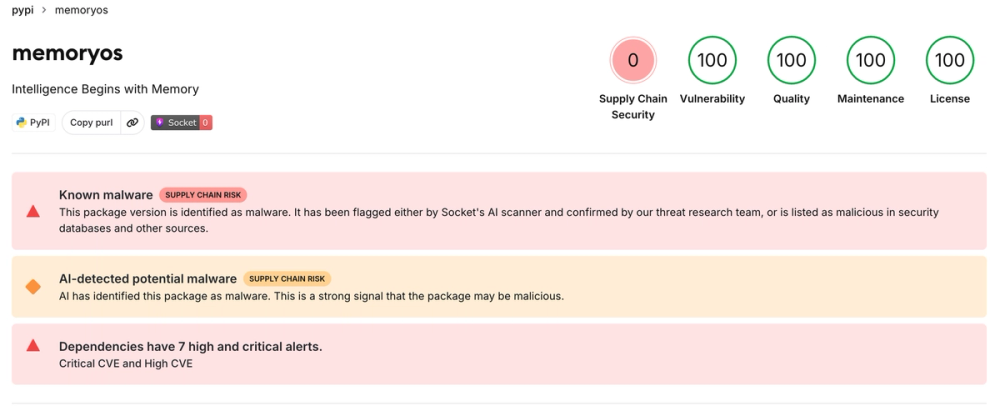 MemTensor npm and PyPI Packages Compromised in Credential-Stealing Supply Chain Attack
Socket details a supply-chain compromise of MemTensor's MemOS packages: npm package @memtensor/memos-cloud-openclaw-plugin (versions 0.1.21, 0.1.23, 0.1.25) and PyPI package MemoryOS (2.0.34), both published as the latest release on their registries. Each malicious release bundles a stripped, statically-linked Go binary called sckit that launches on import/plugin-load, scans $HOME for npm, PyPI, GitHub, GitLab, AWS, Vault and SSH credentials, and exfiltrates them to C2 servers under skyleen[.]fr, with the npm variant also capturing OpenClaw agent prompt text and the code additionally showing potential worm-like republish capability using stolen registry tokens.
 socket.devwriteupPublished and added 23 Sep 2026🛡️ Security
- APort Vault: Benchmarking AI Agent Payment Authorization with the Open Agent Passport
APort Vault is a benchmark that replays 4,371 human-written CTF attacks against a live AI payment agent across 14 models from 8 labs, five policy configurations, and two replay tracks — with and without a deterministic pre-action check implementing the Open Agent Passport (OAP) specification. Across 225,964 evaluations, unauthorized transfers to non-allowlisted recipients occurred 140/76,842 times with the model alone versus 0/69,297 times behind the OAP layer, while the layer still allowed 25,370 legitimate payments through, showing a policy-enforcement layer can materially close the authorization gap in agentic payment flows without just refusing everything. The authors release all evaluations, level passports, scoring code, and analysis scripts.
arxiv.orgpaperAdded 21 Sep 2026, published 18 Sep 2026🛡️ Security  Attacker infrastructure, but vibe-coded: tracking the evolution of credential harvesting platforms
Datadog Security Research analyses two vibe-coded credential harvesting platforms, Loot and UltraVault, monitored since July 2026. Loot catalogs plaintext secrets, including 1,778 AI keys (196 live). UltraVault adds credential validation, exploit chains, a 14-bug LPE matrix and AWS key-pair correlation. The same host probed Amazon Bedrock with GetCallerIdentity, ListFoundationModels and InvokeModel, using kali-cloud Boto3 and Python-urllib user agents.
 securitylabs.datadoghq.comwriteupAdded 29 Oct 2026, published 18 Sep 2026🛡️ Security
- ProjectDXAI/continuous-record-llm-trading-agents
Companion repository for the DXRG paper "What LLM Trading Agents Actually Do in Production" (arXiv:2609.05663), reporting a six-month, population-scale record of two live LLM-agent trading fleets: 3,505 DX Terminal Pro vaults on Base and a 500-599 agent DXAP fleet on Hyperliquid perpetuals (231,638 finalized turns, 14,596 fills). It quantifies how the operating layer — not strategy text — drives behavior: a prompt-rendered leaderboard routes 46.5% of trade entries with a sharp regression discontinuity at the render boundary, agent fixed effects absorb 60% of outcome variance, leverage choice is volatility-blind (median 5.0x across a 5.7x volatility spread) with one posture/slider cell concentrating 62% of liquidations, and discretionary exits underperform a fixed 2%/4% bracket. A 416-scenario paired replay across three frontier models found similar decision quality but sharply different choice-consistency flip rates (35% vs 90%+), and the repo ships the paper, figures, aggregate data extracts, dataset cards and a 17-rule methodology canon distilled from the project's own retracted claims.
github.comrepoAdded 2 Oct 2026, published 1 Sep 2026🧠 AI  LiteLLM
 is an open-source (MIT) AI gateway that puts 140+ LLM providers, agents and MCP servers behind one OpenAI-compatible API. It adds virtual keys, per-team budgets and rate limits, SSO/JWT/RBAC with SCIM, audit logs, leaked-key protection, and guardrails for PII masking and prompt injection (Presidio, Lakera). It self-hosts via Helm, Terraform or Docker, including air-gapped, with Cosign-signed non-root images, Grype and CodeQL scanning, and secrets pulled from Vault or cloud secret managers. A new Rust gateway is benchmarked at 0.66 ms p99 overhead.
 litellm.aitoolAdded 3 Sep 2026, published 31 Aug 2026🛡️ Security
 Dev Machine Guard Now Inventories Where Developer Credentials Live
StepSecurity describes a new Credentials inventory page in Dev Machine Guard that scans developer machines for thirteen well-known credential source types (npm, PyPI, Docker, AWS, GCP, Kubernetes, Vault, GitHub, SSH keys, etc.) across five categories and reports how many devices hold each, how many entries exist, and whether the material is stored in plaintext or protected. It frames the feature against real attacker behavior - the TeamPCP stealer in the xinference PyPI package and the hijacked Bitwarden CLI npm package both enumerated this exact list of well-known dotfile paths - arguing defenders need the same enumeration attackers already have to scope incidents and plan rotations.
stepsecurity.ioarticleAdded 3 Sep 2026, published 28 Aug 2026🛡️ Security- emlai/defi-native-skill
An open-source Agent Skill ("defi-native") that teaches Claude Code, Cursor, Codex and other Agent-Skills-compatible agents capital-markets and DeFi domain knowledge, including yield decomposition, vault/curator anatomy, oracle classes, and stablecoin/RWA taxonomy. It is structured with progressive disclosure (SKILL.md routes to task-specific reference files only when needed), an api-routes.json router that forces live data pulls (vaults.fyi, DefiLlama, Morpho's GraphQL, rwa.xyz, Merkl, 130+ protocol docs) before any numeric claim, and a verified 90+ source manifest. The author describes an eval-gated release process (paired with/without-skill runs graded on structure) and adversarial review by independent models before publishing, making it a useful case study in skill engineering even for readers uninterested in DeFi itself.
github.comrepoAdded 2 Oct 2026, published 28 Aug 2026🧠 AI  The Term Finance Exploit: $8.5M Approved by Silence
A transaction-level forensic reconstruction of the August 23, 2026 Term Finance vault drain ($8.5M), in which an attacker funded a wallet via Tornado Cash, deposited a trivial 0.017% stake, and used it to submit an executable governance proposal through Term's opt-out "veto" voting model. The payload sat publicly visible on-chain for six days with no objection, then disabled the seven-day Zodiac delay-modifier timelock from inside the same proposal it was supposed to be gated by, before draining four ETH sub-vaults and five USDC vaults (including contagion into a RockawayX/Tori Finance curated vault). The piece dissects why the exploit required no leaked key, oracle manipulation, or reentrancy — only an unwatched veto queue and a timelock reachable by the mechanism it was meant to contain.
 defiprime.comwriteupAdded 30 Sep 2026, published 23 Aug 2026🛡️ Security
- archcanary
Archcanary is a read-only, layered detection scanner for Arch Linux (and derivatives like EndeavourOS/Manjaro) that checks installed packages, pacman logs, systemd units, eBPF programs, ld.so.preload, DKMS kernel modules, and npm/bun/yarn/pnpm caches against curated and third-party (aur-audit.wtako.net) threat lists. It was built in direct response to a 2026 AUR supply-chain attack in which commit forgery was used to impersonate maintainers and inject npm/bun install hooks delivering an infostealer (Discord tokens, GitHub PATs, SSH keys, Vault tokens) and a CAP_BPF eBPF rootkit into 1600+ PKGBUILDs, plus a separate Russian-spam PKGBUILD injection campaign. It integrates with yay/paru pre-build hooks, systemd timers, auditd, and Lynis, and originated as a fork/expansion of lenucksi/aur-malware-check.
github.comrepoPublished and added 21 Aug 2026🛡️ Security - VaultKeepR/vaultkeepr-public
vaultkeepr-public is the MIT-licensed repository behind VaultKeepR, a zero-knowledge password manager. It holds 15 SDK packages published to npm under @vaultkeepr and Solidity contracts on Base L2 that anchor vault locations, recovery fragments and digital legacy, tested with Foundry. Encryption is XChaCha20-Poly1305 with Argon2id (t=3, m=64 MiB, p=4), and docs/THREAT_MODEL.md covers assets, adversaries and trust boundaries. Clients stay in a private repository.
github.comrepoAdded 23 Oct 2026, published 12 Aug 2026🛡️ Security - HarnessRouter/harnessrouter
HarnessRouter is a self-hostable (Docker) infrastructure layer that wraps existing agent harnesses such as Codex and Claude Code behind one OpenAI Responses-compatible API, letting a product run tasks, stream progress, manage files/artifacts, and switch harnesses without writing harness-specific integration code. It implements the Unified Harness Protocol (UHP), a versioned, OpenAI Responses-compatible contract with a reference implementation, schemas, and conformance suite, plus features like per-session workspaces, custom harness configuration with tools/skills/MCP servers, and secret redaction via vault references or header-scoped env vars so long-lived tokens never leak through agent output.
github.comrepoAdded 2 Oct 2026, published 9 Aug 2026🧠 AI  The OpenSourceMalware Show #16
Recap episode of The OpenSourceMalware Show covering three incidents: a Shai-Hulud-derived npm worm that compromised maintainer Jared Wray's account and spread to 400+ packages (including Keyv and cacheable, with ServiceTitan losing 100 packages) while harvesting credentials from GitHub, npm, AWS, Kubernetes, Vault, Azure, GCP, Terraform, Docker, and Slack; a "WEL1DROPPER" campaign flooding npm with 1000+ AI-slopsquatted malicious packages that execute on import rather than via install scripts; and "NullReceiver," a DPRK-linked C2 technique that hides C2 IPs inside the recipient address of empty Ethereum transactions, an evolution of EtherHiding found in at least 10 malicious packages.
 opensourcemalware.comtalkAdded 3 Sep 2026, published 8 Aug 2026🛡️ Security
- NPM Malware Compromises keyv and cacheable with 500M+ Weekly Downloads and Spreads to Hundreds of Packages | Blog | Endor Labs
Endor Labs' active-tracking advisory on an npm supply-chain worm that compromised keyv, flat-cache, and file-entry-cache (500M+ combined weekly downloads) via the jaredwray/Cacheable GitHub Actions OIDC trusted-publishing pipeline, injecting a preinstall hook (setup.mjs) that fetches a legitimate Bun binary to run an obfuscated ~727KB stage-2 payload (Math_Symbol.js/math_init.js) stealing AWS, npm, GitHub, and Vault tokens. The stolen tokens were used to self-propagate the same payload to 384+ packages and 1,136+ versions across unrelated maintainer accounts, including scopes belonging to companies like ServiceTitan, Qlik, and Picsart. The post includes IOCs (file hashes), affected package/version lists, and mitigation guidance (lockfile/CI log checks, --ignore-scripts).
endorlabs.comadvisoryAdded 3 Sep 2026, published 4 Aug 2026🛡️ Security  Inside the keyv npm Compromise: preinstall Malware, Trusted Provenance, and IDE Hooks
Snyk Security Research independently verified an active npm supply-chain compromise affecting keyv@6.0.0 and 10 related packages (cacheable family, ecto) published by maintainer jaredwray on August 4, 2026, adding a preinstall hook (setup.mjs) that loads a 727KB obfuscated second-stage payload (Math_Symbol.js) targeting GitHub/npm/cloud credentials, private keys, and Vault/Kubernetes tokens via a gh-token-monitor persistence mechanism. The attack also planted .claude/settings.json and .vscode/tasks.json hooks to trigger execution when developers open the repo in Claude Code or VS Code, and the malicious release was signed by a valid npm trusted-publisher (GitHub Actions) attestation, demonstrating that provenance can faithfully attest a build whose source was already compromised. Snyk provides byte-level tarball diffs, a minute-by-minute incident timeline, and remediation steps including pinning to keyv@5.6.0, hunting for gh-token-monitor persistence, and credential rotation.
 snyk.iowriteupAdded 3 Sep 2026, published 4 Aug 2026🛡️ Security
 'ChainDrop' worm compromises hundreds of popular npm packages
ChainDrop is an npm worm that compromised hundreds of packages on 4 August 2026, some with over 150 million weekly downloads, starting from a malicious commit (174f6a5) in the keyv repository. Datadog dissects the Bun-based loader, the obfuscated second stage, credential theft (files, GitHub Actions runner memory, AWS, Kubernetes, Vault), Ethereum smart-contract C2 discovery, AES/RSA exfiltration, an eval channel, and propagation via stolen npm tokens, GitHub branches and Sigstore provenance. IOCs and a list of affected packages are included.
securitylabs.datadoghq.comwriteupAdded 29 Oct 2026, published 4 Aug 2026🛡️ Security 0xSimao Findings Database
0xSimao's public findings database aggregates smart contract audit results from many independent engagements, cataloging dozens of critical/high/medium/low severity bugs such as ERC4626 vault accounting errors, missing slippage controls, incorrect ICR/debt tracking in leveraged vault "Den" systems, cross-chain state desynchronization via LayerZero in a CDS/borrowing protocol, inflation attacks on ERC4626 shares, and DoS conditions from bad-debt checks. It covers protocols spanning leveraged vaults, lending/liquidation engines, Uniswap-based strategies, Maple/Sky/Aave yield strategies, an IDO launchpad, and a GameFi/DeFi hybrid ("Codeup"), providing concrete real-world examples of DeFi/Solidity vulnerability classes and fixes.
 0xsimao.comwriteupAdded 3 Sep 2026, published 1 Aug 2026🛡️ Security
- Damn Vulnerable DeFi
Damn Vulnerable DeFi is a Foundry-based Solidity smart contract security playground featuring intentionally vulnerable challenges around flashloans, price oracles, governance, NFTs, DEXs, lending pools, smart contract wallets, timelocks, vaults, meta-transactions, and upgradeability. Each challenge presents a prompt and vulnerable contracts; solvers write a Foundry test exploiting the flaw to drain funds or bypass restrictions, making it a benchmark for both human auditors and automated security tooling.
github.comrepoPublished and added 31 Jul 2026🛡️ Security - Flowsint - OSINT Framework
Flowsint is an open-source, self-hosted OSINT investigation platform that lets analysts visually explore relationships between entities (domains, IPs, ASNs, individuals, organizations, crypto wallets, emails, phones) via a graph interface backed by automated enrichers. It integrates recon modules like reverse/forward DNS resolution, WHOIS, subdomain discovery, ASN/CIDR mapping, breach-database checks, Maigret username search, and crypto wallet transaction/NFT lookups, storing all data locally for investigation privacy. The deployment docs also cover hardening steps for network exposure, including rotating AUTH_SECRET and MASTER_VAULT_KEY, binding backend services (PostgreSQL, Redis, Neo4j, API) to localhost, and a host-header allowlist to defend against DNS rebinding.
github.comrepoAdded 3 Sep 2026, published 31 Jul 2026🛡️ Security  Coldcard Security Advisory
Unchained client-facing security advisory responding to Coinkite disclosure that Coldcard hardware wallets (Mk3, Mk4, Mk5, and Q models) generated private keys using a lower-than-expected amount of random bits, weakening key-generation entropy. The advisory details risk to Bitcoin multisig vaults built with Coldcard-generated keys and describes an attack scenario where an attacker holding 2-of-3 compromised keys plus knowledge of a reused address can mount a Replace-By-Fee (RBF) replacement-cycling attack to redirect pending transactions, along with key-replacement remediation steps including Unchained Slipstream as RBF mitigation.
 unchained.comadvisoryAdded 4 Oct 2026, published 31 Jul 2026🛡️ Security
 User Accounts and Privilege Management
Introductory primer on OS user accounts and privilege management. It covers permissions versus privileges, the Principle of Least Privilege, vertical versus horizontal privilege escalation, UAC and sudo, and group-based access. It then moves to enterprise controls: IAM, RBAC, PAM with credential vaulting and session monitoring, Just-In-Time access, Endpoint Privilege Management and Zero Trust. It includes a best-practices list, an FAQ on service-account targeting and why MFA does not replace PAM/JIT, and a tip to start with Azure PIM and forward logs to Splunk for privilege-event alerting.
 asecurityguru.comarticleAdded 13 Oct 2026, published 27 Jul 2026🛡️ Security
- ShortDot Zone Abuse Evidence
PhishDestroy's shortdot-evidence is a daily-updated GitHub investigation into ShortDot SA, the Luxembourg registry operator behind the .icu, .bond, .cyou, .sbs, .cfd, .buzz and .qpon gTLDs, documenting that 51,985+ tracked domains impersonate brands like Chase, Binance, MetaMask and Ledger and that ~70% of registered domains in these zones carry no DNS records (metric-padding rather than legitimate use). It publishes machine-generated IOC/blocklist files and analytics built from a per-TLD zone-file pull cross-referenced against Spamhaus DBL, SURBL, OpenPhish, URLhaus, PhishTank and AlienVault OTX, and ties the zones to concrete criminal cases (FBI's LabHost domain list, Google v. DOES/Yucheng Chang RICO suits, the Revolver Rabbit XLoader/Formbook C2 campaign using 500k+ .bond domains). It also details structural conflicts of interest between ShortDot, its registry infrastructure provider Team Internet Group/CentralNic, registrar partner NameSilo, and the brand-protection vendor NameBlock, backed by Interisle Consulting Group phishing-volume statistics.
github.comrepoPublished and added 25 Jul 2026🛡️ Security - jit
jit is a macOS (Apple Silicon) tool that moves plaintext secrets from .env files, ~/.aws/credentials, shell exports, .npmrc, and MCP configs into a Touch ID-gated local encrypted vault, leaving decoy files on disk and injecting real values only into the specific process that requests them via execve, native credential-helper protocols (AWS credential_process, docker/git credential helpers), or ephemeral named-pipe (FIFO) mounts. It adds per-process consent prompts naming the requesting tool/agent, time-bounded "process grants" for unattended AI agents (e.g. Claude, Codex) to use credentials overnight, and a durable audit log of every credential read, unlock, and denial. It explicitly targets the risk that AI coding agents and CLIs run with full user permissions and can read plaintext secrets, treating agent MCP configs and wrapped AI CLIs as first-class.
github.comrepoPublished and added 18 Jul 2026🛡️ Security - CyberSunil/LLMVault
LLMVault is a self-hosted, deliberately-vulnerable training range modeled on WebGoat but for LLM applications, covering 25 labs across the OWASP Top 10 for LLM Applications (2025) - prompt injection, jailbreaking, data/model poisoning, agent exploitation, model extraction, and insecure downstream output handling. It ships two modes: a scored Play Mode with scripted assistants for repeatable flag capture, and an unscripted Live Mode that points the same attacks at a real local Ollama model (qwen2.5:3b-instruct) with a freshly minted per-session secret, requiring the player to actually talk the model into leaking it. Each lab pairs the attack with a written defense explanation, and an expert tier is shipped AES/Fernet-encrypted and unlocked manually by the maintainer.
github.comrepoPublished and added 18 Jul 2026🛡️ Security  THORChain Exploit Report #2 — GG20 root-cause disclosure
THORChain's second exploit post-mortem details how an attacker who joined as a validator planted a malformed multi-prime Paillier modulus during GG20 threshold-signature key generation, then deliberately failed 864 MTA signing rounds over 2.5 days to leak fragments of other validators' key shares via a combination of three individually low-severity flaws inherited from Binance's tss-lib: an unverified Paillier modulus (the same class documented as BitForge and TSSHOCK), a range proof that didn't bind its two halves together, and an undersized blinding value. Once enough fragments accumulated the attacker reconstructed the full vault private key and drained roughly 10 million dollars in a single transaction before solvency checks could react, since no anomalous fund movement preceded the theft. THORChain is patching the fork, moving from GG20 and Paillier to DKLS and Schnorr based signing, and adding per-validator key-sign failure monitoring as a result.
 blog.thorchain.orgwriteupAdded 29 Sep 2026, published 3 Jul 2026🛡️ Security
 8kSec AI/LLM Exploitation Labs
8kSec's AI/LLM Exploitation Labs is a set of hands-on CTF-style challenges covering real attack classes against AI systems: prompt-injection to manipulate an LLM essay grader and a workspace assistant into granting admin access, crafting adversarial images to bypass an MNIST-based ML authentication vault, extracting a "secret" encryption key from an n8n/OpenAI chatbot via conversation alone, exploiting a remote MCP server (via Cursor) for path traversal to read /etc/passwd, poisoning a training CSV to backdoor a spam classifier, detecting neural network backdoors in CIFAR-10 models, spotting a malicious MCP skill with a data-exfiltration payload, and identifying "ghost record" membership-inference leakage in a supply-chain-compromised model. Each challenge maps to a distinct AI security technique (prompt injection, adversarial examples, model/data poisoning, MCP tool abuse, membership inference) and offers a free certification on completion.
 academy.8ksec.iocoursePublished and added 21 Jun 2026🛡️ Security
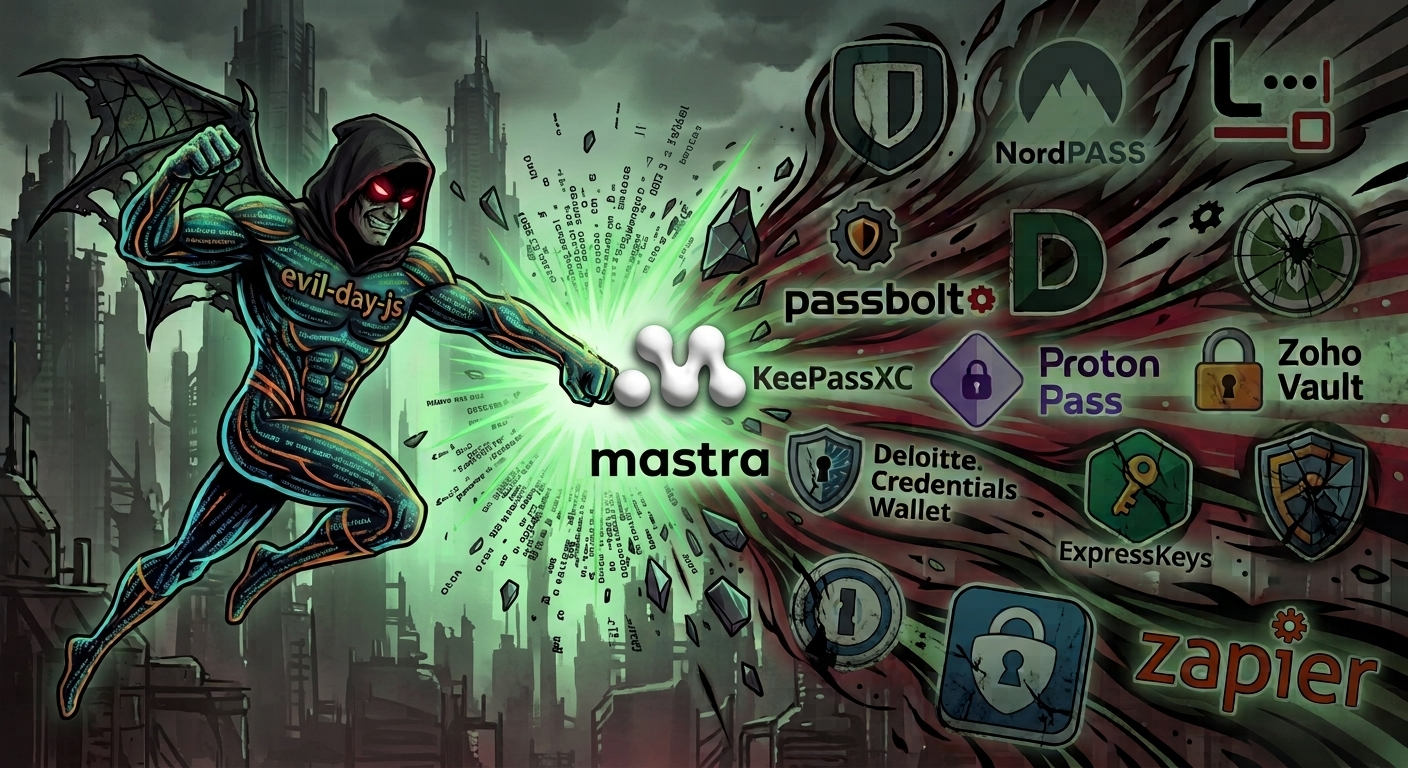 Mastra Attack Targets Crypto, Password Managers, Authenticators, and Zapier
A threat actor took over a dormant maintainer account and republished 140+ packages in the @mastra npm scope (including @mastra/core, ~918K weekly downloads), injecting a typosquat of dayjs called easy-day-js as a new dependency in every manifest. A clean 1.11.21 version was published first, then a weaponized 1.11.22 tagged latest was pulled in via caret-range resolution, delivering a two-stage cross-platform backdoor that disables TLS validation, self-deletes, installs OS-specific persistence disguised as Node/NVM tooling, and steals browser history plus data from 166 crypto-wallet, password-manager (1Password, Bitwarden, LastPass, Dashlane, NordPass, Proton Pass, KeePassXC, Zoho Vault, Kaspersky), MFA-authenticator, and Zapier browser extensions. The report ties the campaign's Hostwinds infrastructure, clean-then-armed typosquat, and TLS-off/detached/self-delete dropper pattern to the same playbook Microsoft attributed to Lazarus Group in the earlier axios npm compromise, and compares its extension targeting to the "HyperHives" ClickFix campaign, noting npm's lack of provenance enforcement (provenance: no on the malicious wave) as the control gap that let it through.
opensourcemalware.comwriteupAdded 3 Sep 2026, published 18 Jun 2026🛡️ Security Microsoft's durabletask PyPI Package Compromised in Supply Chain Attack
StepSecurity documents the compromise of Microsoft's durabletask PyPI package (versions 1.4.1-1.4.3, 400k+ monthly downloads), where an attacker bypassed the GitHub CI/CD pipeline entirely using stolen publishing credentials to inject a dropper for rope.pyz, a modular cloud-intrusion framework with dedicated collectors for AWS, Azure, GCP, Kubernetes, HashiCorp Vault, password managers, and the filesystem. The framework encrypts stolen data with AES-256-GCM/RSA-4096, exfiltrates via HTTPS, GitHub commit beacons, and attacker-created public repos using the victim's own stolen GitHub tokens, propagates via AWS SSM and kubectl exec, and drops a geo-targeted rm -rf wiper for systems matching Israeli locale/timezone markers. The post ties the attack to TeamPCP's Mini Shai-Hulud campaign (same infrastructure as TanStack, Mistral AI, LiteLLM, @antv) and later updates describe a second compromise of the Azure/durabletask GitHub repo that plants payloads triggering in Claude Code, Gemini CLI, Cursor, and VS Code.
stepsecurity.iowriteupAdded 3 Sep 2026, published 9 Jun 2026🛡️ Security Pythagora-io/gpt-pilot Compromised on GitHub - Shai-Hulud Credential Stealer Blocked by Python Linter
StepSecurity documents a June 2026 compromise of the Pythagora-io/gpt-pilot GitHub repo (33.7k stars), where an attacker took over a co-founder's account and force-pushed a Shai-Hulud-variant credential stealer disguised as a "Revert" commit. The malware, a 758KB obfuscated Bun/JavaScript payload delivered via a Python telemetry module, steals AWS/npm/GitHub/Kubernetes/Vault/SSH credentials, uses GitHub commit messages as a covert C2 channel, exfiltrates via newly created GitHub repos, can abuse Sigstore/Fulcio to forge SLSA Build Level 3 attestations, and plants persistence hooks in Claude Code and VS Code. Notably, the attacker's injected code was blocked twice by the project's ruff CI linter/formatter before they gave up, illustrating code-quality tooling as an accidental security control, alongside full IOCs and lessons on branch protection and force-push monitoring.
stepsecurity.iowriteupAdded 3 Sep 2026, published 9 Jun 2026🛡️ Security Node-gyp Supply Chain Compromise: A Self-Propagating npm Worm That Hides in binding.gyp
Snyk documents an active npm supply-chain attack ("Node-gyp Supply Chain Compromise - June 2026") that abuses binding.gyp's GYP command-expansion syntax (<!(...)) to trigger arbitrary code execution via node-gyp during npm install, bypassing detection tools that only monitor preinstall/postinstall scripts. The worm, tracked as "Phantom Gyp"/"Miasma" (a Shai-Hulud descendant) by StepSecurity, has hit 57 packages including autotel-* and @vapi-ai/server-sdk, harvests npm/GitHub/AWS/GCP/Azure/Vault/Kubernetes credentials via a multi-stage obfuscated Bun-based loader, injects GitHub Actions workflows for persistence, and self-propagates by republishing from compromised maintainer accounts.
snyk.iowriteupAdded 3 Sep 2026, published 4 Jun 2026🛡️ Security Why EDR and proxy won’t save you from supply chain malware
Aikido argues that EDR and corporate/remote proxies cannot catch supply chain malware because the malicious code executes with full trust inside legitimate package managers at install time. It walks through two real incidents: the March 2026 hijack of the axios maintainer's npm account (a new dependency's postinstall script dropped a cross-platform RAT and self-deleted, indistinguishable from a normal npm install), and a backdoor added to three versions of Microsoft's Python durabletask package that harvested credentials across AWS, Azure, GCP, Kubernetes, and HashiCorp Vault, propagated via SSM and kubectl exec, and triggered rm -rf / on machines with Israeli/Iranian locale settings. It concludes that this class of attack needs host-based, always-on, install-time protection rather than network-perimeter or behavioral-anomaly tooling — pitching Aikido's Device Protection product.
 aikido.devarticleAdded 3 Sep 2026, published 2 Jun 2026🛡️ Security
 Nx Console VS Code Extension Compromised
StepSecurity's technical teardown of the May 2026 compromise of the Nx Console VS Code extension (nrwl.angular-console v18.95.0, 2.2M+ installs), where a stolen contributor GitHub token was used to push a dangling orphan commit to nrwl/nx and publish a malicious extension via stolen VSCE_PAT credentials. The payload silently ran `npx github:nrwl/nx#<sha>` to fetch a heavily obfuscated 498KB Bun/Node credential stealer that harvests secrets from GitHub, npm, AWS, Vault, Kubernetes, 1Password and Claude Code config, exfiltrates via HTTPS/GitHub API/DNS tunneling, installs a macOS Python backdoor using the GitHub Search API as a C2 dead-drop, and can forge valid Sigstore/SLSA provenance attestations for downstream npm packages. The writeup ties this to a later GitHub breach (3,800 repos, attributed to TeamPCP) and provides detection signals, IOCs, and full recovery steps.
stepsecurity.iowriteupAdded 3 Sep 2026, published 2 Jun 2026🛡️ Security Red Hat npm Packages Compromised to Spread a Credential-Stealing Worm
Aikido details a June 2026 compromise of 96 versions across 32 @redhat-cloud-services npm packages (116,991 weekly downloads) with "Miasma," a new variant of the TeamPCP-authored Mini Shai-Hulud credential-stealing worm whose source was open-sourced in May 2026. Attackers compromised a Red Hat employee's GitHub account to push malicious orphan commits containing a GitHub Actions workflow that abused OIDC id-token: write permissions to authenticate to npm's trusted publishing endpoint and republish backdoored packages; each package's preinstall script then ran a 4.2MB obfuscated payload that swept GitHub Actions, AWS, GCP, Azure, Vault, Kubernetes, npm/PyPI, SSH, Docker, GPG, and .env credentials. The piece also lays out the broader Mini Shai-Hulud campaign timeline (Bitwarden CLI, SAP, PyTorch Lightning, Mistral/TanStack, Microsoft DurableTask) and full IOC package/version list.
aikido.devwriteupAdded 3 Sep 2026, published 1 Jun 2026🛡️ Security Supply Chain Attack Targets Laravel-Lang Packages with Credential Stealer
Aikido Security discovered an active supply chain attack against laravel-lang/lang, laravel-lang/attributes, and laravel-lang/http-statuses (233 compromised versions total), where an attacker used GitHub's cross-fork tag feature to point official-looking version tags at commits in a malicious fork, injecting a src/helpers.php dropper that loads via Composer's autoloader. The dropper fingerprints the host, decodes a hidden C2 domain (flipboxstudio[.]info), and fetches a second-stage PHP credential stealer that harvests cloud credentials, Kubernetes/Vault/Docker configs, SSH keys, browser and password-manager vaults, crypto wallets, and VPN configs, exfiltrating AES-256 encrypted data before self-deleting. Aikido reported it to Packagist, which pulled the malicious versions.
aikido.devwriteupAdded 3 Sep 2026, published 23 May 2026🛡️ Security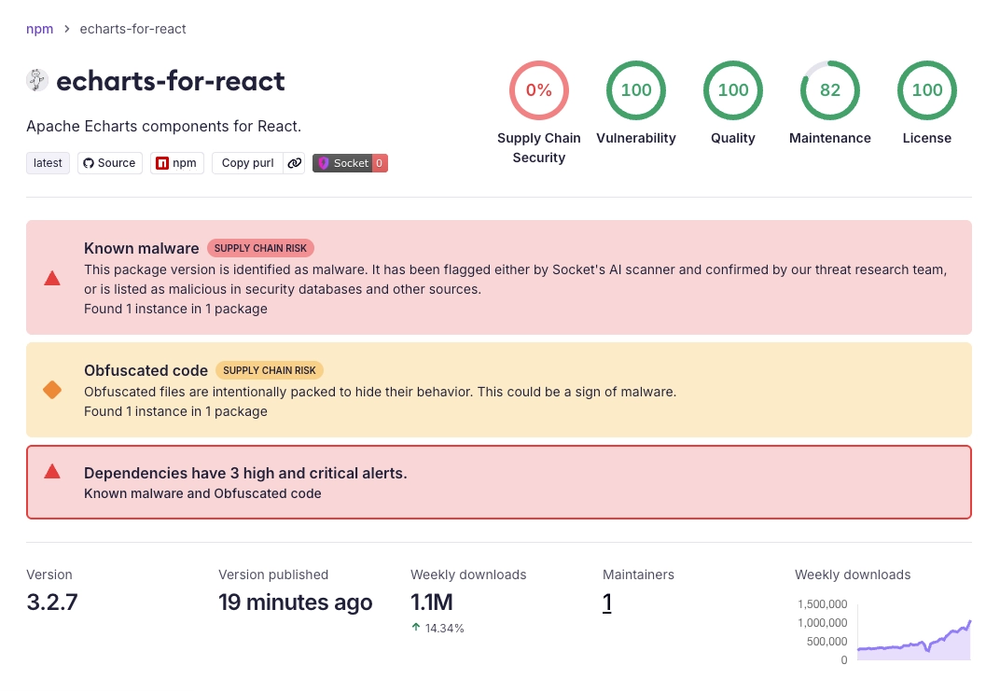 Socket: Mini Shai-Hulud Hits @antv Ecosystem
Socket's Threat Research team documents a Mini Shai-Hulud variant compromising the npm maintainer account "atool," affecting @antv data-visualization packages (g2, g6, x6, l7, s2, f2, graphin) plus echarts-for-react (~1.1M weekly downloads) and others, totaling 639 compromised versions across 323 packages in one wave (1,055 versions/502 packages campaign-wide across npm, PyPI, and Composer). The install-time payload (triggered via a preinstall "bun run index.js" hook) is heavily obfuscated, harvests GitHub/npm/AWS/Kubernetes/Vault/SSH credentials and CI/CD secrets, exfiltrates data via AES-256-GCM+RSA-OAEP encrypted HTTPS to t.m-kosche[.]com and via GitHub repo commits under a reversed "Shai-Hulud: Here We Go Again" marker, and self-propagates by using stolen npm tokens to republish trojanized packages with a malicious @antv/setup GitHub optionalDependency.
socket.devwriteupPublished and added 20 May 2026🛡️ Security StepSecurity + Endor Labs: Mini-Shai-Hulud Wave 2
StepSecurity and Endor Labs document a second wave of the Mini Shai-Hulud npm worm spreading through the compromised 'atool' account, which publishes timeago.js and maintains packages in Alibaba's @antv namespace, hitting echarts-for-react, jest-canvas-mock and dozens of other packages. The payload scrapes GitHub Actions Runner.Worker process memory to steal masked CI/CD secrets, harvests 130+ credential file paths (cloud, SSH, Kubernetes, Vault, crypto wallets, Claude Code/VS Code configs), exfiltrates via a GitHub API dead-drop in antvis/G2 or a fake-OpenTelemetry C2 at t.m-kosche.com, drops persistent backdoors in Claude Code/VS Code, and has already used stolen GitHub tokens to spin up 2,500+ dead-drop repositories. The writeup includes full process/network telemetry from Harden-Runner showing the attack blocked, deobfuscated payload internals, IOCs, and detection/remediation guidance.
stepsecurity.iowriteupPublished and added 19 May 2026🛡️ Security FOSSA: Mini-Shai-Hulud Mass Compromise
FOSSA's technical breakdown of the May 2026 Mini-Shai-Hulud campaign, which compromised at least 235 npm and PyPI packages including @tanstack/*, @uipath/*, mistralai, and @opensearch-project/opensearch. It details the two install-time payload mechanisms (a Git-dependency prepare-hook trick with an orphan commit for @tanstack/*, and direct preinstall scripts for @uipath/*/Mistral AI), a staged PyPI dropper in __init__.py that evades sandbox scanning, the credential-harvesting targets (AWS/GCP/Azure, Kubernetes, Vault, GitHub, npm tokens), exfiltration infrastructure (filev2.getsession.org, git-tanstack.com), and IDE-persistence via modified Claude/VS Code config files.
 fossa.comwriteupPublished and added 18 May 2026🛡️ Security


Showing 60 of 66
Show more