- Cyber Detective💙💛 (@cyb_detective) on X
Python Cybersecurity Libraries is a curated GitHub list by Yogsec, shared in a post by cyb_detective. It groups Python libraries by task: network analysis, penetration testing, threat intelligence, reverse engineering and malware analysis, forensics and investigation, web application security, CTF, and machine learning for security. The tweet shows only the category names, not the individual libraries.
 x.comrepoAdded 24 Oct 2026, published 21 Oct 2026🛡️ Security
- AikidoSec/safe-chain
Aikido Safe Chain is an open-source local proxy and shell-alias wrapper for npm, yarn, pnpm, bun, pip, uv, poetry, pipx and pdm. It checks every package download, including deep dependencies, against the Aikido Intel malware feed and blocks malicious packages before install. It also enforces a configurable 48-hour minimum package age by suppressing too-new versions in registry metadata. It supports custom registries and a self-hosted malware-list mirror, and has CI/CD install recipes for GitHub Actions, Azure Pipelines, CircleCI, Jenkins, Bitbucket and GitLab.
 github.comrepoAdded 17 Oct 2026🛡️ Security
 Meta Muse Spark Open (816B-A42B) open-weights model card
Model card for Meta Superintelligence Labs' Muse Spark Open, an open-weights, natively multimodal model with 816B total and 42B active parameters and a 1M-token context window. It targets coding and agentic work (tool use, long-horizon tasks, multimodal reasoning, synthetic data generation, LLM-as-judge). It ships in BF16 and NVFP4, needs about 700GB VRAM (NVFP4) or 2TB (BF16), runs on SGLang, vLLM, Transformers, TensorRT-LLM, Unsloth, llama.cpp and MLX, and supports a reasoning_effort setting. The Muse Model License requires "Built with Muse Spark Open" attribution and a separate agreement for Model-as-a-Service above $20M revenue. The card reports safety results against Kimi K3 on cyber, chem/bio and loss-of-control evals.
 huggingface.corepoAdded 17 Oct 2026🧠 AI
- the_OSINT_rack (@the_OSINT_rack) on X
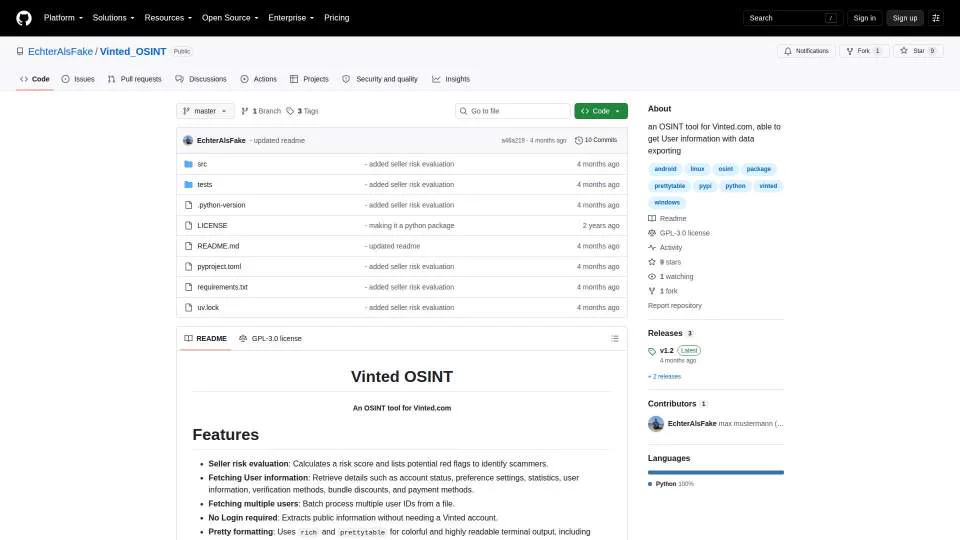
Vinted_OSINT is a GitHub tool by EchterAlsFake that performs open-source intelligence gathering against Vinted.com user profiles, pulling seller/buyer account information and computing a risk score to flag accounts likely run by scammers. It's aimed at buyers wanting to vet sellers before transacting on the second-hand marketplace.
x.comrepoPublished and added 4 Oct 2026🛡️ Security  Ternary-Bonsai-2-27B: 27B model compressed to ~1.75 bits/weight, 98.2% of FP16 quality retained
Ternary-Bonsai-2-27B is a 27B-parameter reasoning model (built on Qwen3.8-27B) quantized to true ternary weights ({-1,0,+1}) at ~1.72 bits/weight, shrinking it from ~54GB FP16 to ~5.95GB while retaining 98.2% of FP16 benchmark quality (84.78 vs the conventional sub-4-bit IQ2_XXS build's 72.59). It uses a Hadamard-rotated weight basis and ships two GGUF packing formats (PTQ1_0 dense trits, PQ2_0 2-bit slots) that require a custom llama.cpp/MLX kernel fork since stock llama.cpp cannot decode them correctly. The card includes per-category benchmark breakdowns (math, coding, agentic tool calling), cross-platform throughput/power measurements (Apple M5 Pro/Max, RTX 5090, L4, H100/A100/Blackwell), and an "intelligence density" metric comparing capability retained per GB against FP16 and other quantizations.
huggingface.corepoAdded 29 Sep 2026🧠 AI- vLLM v0.30.0
Release notes for vLLM v0.30.0, a major update to the open-source LLM inference/serving engine spanning 762 commits. Highlights include new model support (DeepSeek-V4.1-Flash, GLM-5.3-Flash, Kimi K3, Qwen3.8-Flash-Next, K2-Horizon, Cohere Compass and others), a "Fast Start" GPU weight-cache daemon for near-instant engine restarts via CUDA IPC, Gumbel-max watermarking for generated text, a HiSparse host-memory tier for sparse-MLA KV offload, Model Runner V2 improvements (dual-batch overlap, speculative decoding under pipeline parallelism), expanded quantization support (NVFP4, W4A16 DSA, AutoRound), and hardware-specific tuning across NVIDIA, AMD ROCm, Intel XPU and CPU backends.
github.comrepoAdded 28 Sep 2026🧠 AI  Ling-3.0-flash-VL (InclusionAI/Ant Group)
Ling-3.0-flash-VL is InclusionAI/Ant Group's native multimodal model built on Ling-3.0-flash, adding image and video understanding via a ViT encoder, VideoRoPE, and a hybrid MoE backbone (42 layers alternating KDA and Gated MLA at 5:1) with 124B total parameters but only 5.5B activated per token, and a 256K context window. It targets agentic multimodal workflows — understanding, reasoning, and acting on visual interfaces — scoring 42 on Artificial Analysis Intelligence Index v4.1.1, up from 38 for the text-only Ling-3.0-flash. The card includes concrete SGLang and vLLM serving recipes for various GPU configurations.
huggingface.corepoAdded 26 Sep 2026🧠 AI- Outrider Recon
Outrider Recon is an open-source, Claude-native multi-agent OSINT and external attack-surface recon platform for authorized engagements, covering web/API, identity/SSO, cloud, secrets, and people/breach intelligence. It deliberately stops short of exploitation: active enumeration is approval-gated and intrusive validation is a human hand-off, with deterministic Python controls enforcing scope, evidence integrity, workflow state, and finding promotion around Claude skills and optional MCP-based enrichment. Output is ranked, evidence-backed finding cards (confidence/severity/handoff recommendations) meant to feed proxy-assisted testing or pen-testing rather than raw scanner dumps.
github.comrepoAdded 22 Sep 2026, published 19 Sep 2026🛡️ Security - ThreatIntel-Aggregator
ThreatIntel-Aggregator is a self-hosted FastAPI/Next.js platform that polls 60+ tiered security RSS feeds (CISA, Talos, Unit42, etc.), runs AI triage to score severity and tag MITRE ATT&CK TTPs, extracts IOCs/CVEs, and correlates findings against a RunZero asset inventory to surface org-level exposure. Its Detections module goes further: it catalogs AI-generated or locally-imported detection rules (KQL/Sigma/YARA/Suricata/SPL), statically validates them, runs AI-driven MITRE alignment checks against technique coverage, tracks detection "rot," and can sync Hunts/Analytics Rules to a live Microsoft Sentinel workspace. It's designed to run standalone with zero cloud dependency or fully integrated with Azure/Entra/Sentinel, with all storage in Postgres and auth via Entra SSO or a local API key.
github.comrepoAdded 22 Sep 2026, published 17 Sep 2026🛡️ Security - vet (SafeDep)
vet is an open-source CLI (from SafeDep) that scans package manifests, SBOMs, container images, and source repos across npm, PyPI, Maven, Go, RubyGems, Cargo, and Packagist to surface vulnerabilities, malicious packages, and license/quality issues. It cuts through CVE noise by analyzing actual code-usage evidence, queries SafeDep Cloud's threat-intelligence database for real-time malware detection (e.g. flagged packages like express-cookie-parser, eslint-config-airbnb-compat), and lets teams enforce security/license/OpenSSF-Scorecard policies as CEL expressions in CI/CD via SARIF/JSON/Markdown reporting.
github.comrepoPublished and added 7 Sep 2026🛡️ Security - rollroyces/py-idp
py-idp is a Python framework for intelligent document processing with a six-stage pipeline (parse, classify, extract, assess, validate, human review). It supports 23 LLM backends including OpenAI, Anthropic, Ollama, and self-hosted Nanonets-OCR2-3B. It adds Pydantic schema extraction, auto-chunking of oversized documents, an eval harness, and a review-driven policy update for confidence. It is dual-licensed AGPL-3.0 and commercial.
github.comrepoAdded 23 Oct 2026, published 31 Aug 2026🧠 AI - ThreatRadar
ThreatRadar is an open-source, Docker-based threat intelligence pipeline that ingests IOCs from feeds like NVD, OTX, AbuseIPDB, and EmergingThreats, enriches them with MITRE ATT&CK and CVSS data, and scores them via Cortex analyzers (VirusTotal, AbuseIPDB, Maltiverse, IPinfo, Urlscan, HybridAnalysis). Its core focus is feed poisoning detection: a scikit-learn IsolationForest model flags statistically anomalous IOCs, which are then semantically validated by an LLM (GPT-4o via OpenRouter) against eight contradiction classes (e.g., APT-sector mismatches) before enriched, validated intel is pushed to MISP with TLP tagging, and analyst-confirmed sightings feed back into retraining the anomaly model.
github.comrepoPublished and added 27 Aug 2026🛡️ Security - Deep Eye
Deep Eye is an open-source Python pentesting framework that orchestrates 11 AI providers (OpenAI, Claude, Grok, Gemini, Ollama, Groq, Mistral, OpenRouter, LiteLLM, LM Studio, and more) with automatic failover to generate context-aware attack payloads for 50+ vulnerability classes including SQLi, XSS, SSRF, IDOR, JWT and GraphQL flaws. It adds an RAG-indexed CVE intelligence DB built from NVD/MITRE/Exploit-DB, AI-based finding triage and false-positive filtering, Nuclei-style YAML templates, Playwright browser automation, CAPTCHA-solving (reCAPTCHA/hCaptcha/Turnstile/Arkose), mitmproxy interception, and auto-generated HackerOne-style bug bounty reports with PCI-DSS/SOC2/ISO 27001 compliance mapping, SARIF/JUnit export, scan diffing, and retest workflows.
github.comrepoAdded 3 Sep 2026, published 22 Aug 2026🛡️ Security - Teycir/BurpAPISecuritySuite
BurpAPISecuritySuite is a Jython-based Burp Suite extension that consolidates API reconnaissance, intelligent fuzzing (108+ payloads across 15 attack types including BOLA, IDOR, JWT exploitation, GraphQL abuse, SSTI, and WAF bypass), and passive deep-logic checks (counterfactual differentials, sequence invariants, token lineage, cross-interface parity drift) into a single tool covering the OWASP API Top 10. It auto-captures and normalizes API traffic, exports attack campaigns to Burp Intruder/Turbo Intruder/Nuclei, and generates AI-ready bundles (ChatGPT/Claude/Ollama) for LLM-assisted triage, while orchestrating external tools like ApiHunter, Katana, httpx, FFUF, Kiterunner, sqlmap, and Dalfox for verification.
github.comrepoPublished and added 21 Aug 2026🛡️ Security - PrimeIntellect-ai/prime-agent
Prime Agent is an open source coding and research agent built on a persistent Python REPL and subagent architecture. Its documentation explicitly warns that it executes model generated code with full user permissions and is not a security sandbox, advising users to only run trusted repositories, instructions, and skills.
github.comrepoPublished and added 9 Aug 2026🛡️ Security - SiberKapan
SiberKapan is a Turkey-focused, community-driven open-source threat intelligence platform that aggregates data from FortiGate webhooks, an 11-service honeypot (HoneypotKapan), nginx/Fail2ban log watchers, and external feeds, publishing it as STIX 2.1/TAXII 2.1, a MISP default feed, Sigma/Suricata/Wazuh exports, and REST blocklists. It also runs a real-time phishing/domain-squatting detector via Certificate Transparency log monitoring with fuzzy typosquat and Punycode/IDN decoding, and safely fingerprints SSH-honeypot malware downloads with SSRF-protected, never-executed hashing enriched via MalwareBazaar. The write-up details concrete anti-abuse safeguards: time-based IP score decay, CDN/cloud-proxy allowlisting, UDP-spoofing exclusion, RFC1918 rejection, and manual review gating for weak phishing signals.
github.comrepoPublished and added 8 Aug 2026🛡️ Security - CyberSec-Blogs
CyberSec-Blogs is a GitHub-hosted, categorized directory of independent cybersecurity blogs run by practitioners, organized into Red Team (54 entries), Threat Hunting (6), Threat Intelligence, Purple Team, and Detection Engineering sections. The list favors personal blogs publishing original research, tradecraft, and tooling over corporate/vendor content, and is community-maintained via PRs/issues under a CC0 license.
github.comrepoPublished and added 5 Aug 2026🛡️ Security - UseOSINT/Skills
UseOSINT/Skills is a GitHub repo of 28 SKILL.md files that let Cursor, Claude, and other coding agents run open-source-intelligence investigations — 10 end-to-end workflows (e.g. find-anyone, x-ray-a-company, recon-a-domain-passively) built on 18 reusable technique skills (WHOIS, certificate transparency, reverse image search, breach lookups, chronolocation). Each skill ships with reference material (query cookbooks, indicator guides, registry catalogues) and an install script that symlinks the whole set into ~/.cursor/skills, illustrating a chained, workflow-plus-technique pattern for structuring and routing large agent skill libraries. The repo also documents scope/authorization gating and passive-by-default behavior as part of the skill design.
github.comrepoAdded 30 Sep 2026, published 2 Aug 2026🧠 AI - Awesome Offensive AI Agentic Landscape
A comprehensively curated landscape document tracking the offensive AI agent space: ranked open-source pentesting/red-team agent projects (e.g. strix, shannon, VulnBot), uncensored offensive LLMs (Qwythos, WhiteRabbitNeo/DeepHat, BaronLLM) versus security-specialized but aligned models (Foundation-Sec, CyberSecQwen), Claude Code Agent Skills and MCP servers wrapping tools like Metasploit and BloodHound, 116 cross-referenced academic papers on pentest/vuln-discovery agents, capability benchmarks (Cybench, NYU CTF Bench, CyberGym), and a fact-checked Top-20 list of commercial AI pentesting vendors. It also covers competitions like the DARPA AI Cyber Challenge and Tencent's Intelligent Penetration Hackathon, positioning itself as a cross-merge of several other awesome-lists in this niche.
github.comrepoPublished and added 1 Aug 2026🛡️ Security - Awesome Malware Analysis
Awesome Malware Analysis is a curated GitHub list aggregating hundreds of tools and resources across the malware analysis lifecycle: honeypots (Cowrie, Dionaea, Conpot), sample repositories (VirusShare, Malshare, theZoo, VX Underground), IOC/threat-intel platforms (MISP, YARA, ThreatCrowd, URLhaus), online sandboxes (VirusTotal, Cuckoo Sandbox, Hybrid Analysis, any.run), static/dynamic RE tools (IDA Pro, Ghidra, Radare2, x64dbg, angr), deobfuscation utilities, network traffic analyzers (Wireshark, Bro, mitmproxy), and memory forensics frameworks (Volatility, Rekall). It also links essential books, blogs, and training material (Practical Malware Analysis, REMnux, FLARE VM) making it a de facto index for the malware analysis community.
github.comrepoPublished and added 31 Jul 2026🛡️ Security - Beetle
Beetle is an offline-first mobile application security platform that statically analyzes Android APKs and iOS IPAs (including Flutter and React Native apps), combining decompilation, taint analysis, secret/endpoint extraction, certificate and native-binary hardening checks, and CVE enrichment with explainable 'intelligence engines' (ownership, confidence, evidence selection, finding fusion) that correlate findings into evidence-backed attack chains. It maps results to OWASP MASVS/Mobile Top 10, provides source-level navigation, and exports SARIF, CycloneDX SBOM, and PDF reports, with optional (non-scanning) AI assistance via Claude, OpenAI, Gemini, DeepSeek, or local Ollama for explaining findings.
github.comrepoPublished and added 31 Jul 2026🛡️ Security - lockfale/OSINT-Framework
OSINT Framework is a curated, categorized index of free (mostly) open-source intelligence tools and resources, organized by data type (username, domain, IP, email, social media, etc.) and rendered as an interactive tree at osintframework.com. Each entry in the underlying arf.json is tagged with metadata like whether it requires local install (T), a Google dork (D), registration (R), or manual URL editing (M), plus richer fields such as input/output type, pricing, and opsec notes. It's a long-standing community reference for recon and investigation tradecraft across infosec and other fields.
github.comrepoPublished and added 31 Jul 2026🛡️ Security - OpenOSINT
OpenOSINT is a Python OSINT agent that wraps 20 investigation tools (holehe for email enumeration, sherlock for username lookup, sublist3r for subdomain enumeration, phoneinfoga for phone intel, plus HaveIBeenPwned, Shodan, VirusTotal, Censys, AbuseIPDB, IP2Location, DNS/SPF/DMARC checks, GitHub, and Bright Data-powered dorking/scraping) behind a natural-language AI interface that issues deterministic tool calls so findings can't be hallucinated. It ships as a REPL, CLI, MCP server (usable from Claude Code/Desktop, Cursor, Windsurf), or browser web UI, with an optional additive FollowTheMoney entity graph for correlating findings and pivoting between investigation results, plus documented reverse-proxy/credential-handling behavior for remote deployments.
github.comrepoPublished and added 31 Jul 2026🛡️ Security - BountyForge
BountyForge is a Claude Code skill that spins up 8 specialized agents in parallel to hunt for vulnerabilities across web/API, smart contracts (EVM, Move, Solana, TRON), infrastructure, and supply-chain targets, then deduplicates and runs findings through a four-gate validation pipeline (Refutation, Reachability, Trigger, Impact) before CVSS-scoring them into submission-ready HackerOne/Bugcrowd/Intigriti/Immunefi reports. It orchestrates local tools (nmap, ffuf, sqlmap, amass, ZAP, Burp Suite) when Claude Code execution is enabled, integrates with a companion `bug-bounty-intelligence-mcp` MCP server for Solidity scanning via "Al-Mizaan v3" 7-gate deep validation, and also offers a paid Firecracker-microVM cloud version at bountyforge.xyz.
github.comrepoPublished and added 22 Jul 2026🛡️ Security - ailinone/collective-intelligence
Collective Intelligence is an open-source (AGPL-3.0) OpenAI-API-compatible gateway that routes a single request across a continuously-discovered pool of AI models (claimed ~90 provider integrations, 103,224 indexed models) using one of 32 coordination strategies - consensus with convergence floors, blind debate, expert panels, devil's-advocate consensus, cost-cascade, best-of-N with objective verification - instead of sending it to one model. Every response carries an ailin_metadata provenance record (strategy used, models used, cost, dissent), and the repo ships a reproducible benchmark harness with raw per-execution CSVs claiming the coordinated pool beats GPT-5.5-pro, Claude Opus 4.8, Gemini 3.1 Pro and Grok 4.3 on verifiable tasks (97% vs 68-82%). It installs via Docker Compose, exposes an OpenAI SDK-compatible base_url swap, and supports a no-API-key Ollama degraded self-hosted mode.
github.comrepoAdded 2 Oct 2026, published 20 Jul 2026🧠 AI - ZX41R/awesome-reverse-engineering-and-malware-analysis
A curated, upkept "awesome list" for reverse engineering and malware analysis that organizes hundreds of resources into guided learning tracks (Windows malware triage-to-config-extraction, Linux/ELF reversing, exploit development, firmware & embedded, mobile, anti-analysis) plus a full taxonomy covering foundations, RE tooling (IDA, Ghidra, Binary Ninja, radare2, x64dbg), malware analysis/unpacking/YARA/C2 tracking, fuzzing (AFL++, libFuzzer), firmware, mobile, OS internals, LOLBAS/GTFOBins living-off-the-land resources, DFIR, and threat intelligence. It also surfaces niche researcher communities like Kanxue, 52pojie, Tuts4You, the WASM Russian RE forum, 0x00sec, and back.engineering (VTIL/VMProtect devirtualization work), with every link manually vetted and dead links pruned.
github.comrepoAdded 30 Sep 2026, published 6 Jul 2026🛡️ Security - XORCISM-AI/XORCISM
XORCISM is a self-hosted, open-source enterprise risk/exposure management platform (Node.js/TypeScript over SQLite/PostgreSQL/MySQL) that unifies asset inventory, vulnerability management, threat intel (STIX/TAXII), GRC (ISO 27001, NIST CSF/800-53, EBIOS Risk Manager, NIS2, DORA), incident management, and offensive/defensive testing into one continuously recomputed per-asset and enterprise risk score. It chains recon/exploitation tool connectors (nmap, nuclei, Metasploit, sqlmap) into attack-path/choke-point graphs weighted by fusion exploitability (EPSS+CVSS+KEV+public exploits), validates detection coverage via a purple-team loop against 3,750+ Sigma rules and MITRE ATT&CK/D3FEND, and quantifies ransomware impact in dollar terms via a FAIR-style model — with local-only Ollama AI assistants for triage, hunting, and reporting.
github.comrepoPublished and added 1 Jul 2026🛡️ Security - OASIS
OASIS (Open Automated Security Intelligence Scanner) is an AI-powered SAST tool that runs local LLMs via Ollama or any OpenAI-compatible backend (vLLM, LiteLLM, LM Studio, llama.cpp) to detect vulnerabilities like SQLi and XSS in source code. It uses a two-phase scan (lightweight scan model + deep analysis model) orchestrated by a LangGraph pipeline (discover→scan→expand→deep→verify→report), adds a deterministic finding-validation agent that computes exploitability verdicts with confidence, and exports canonical JSON/SARIF/HTML/PDF reports with a web dashboard, RAG-backed chat assistant, --fail-on CI gating, and suppression/inline-ignore support.
github.comrepoPublished and added 28 Jun 2026🛡️ Security - 0x4m4/hexstrike-ai
HexStrike AI is an MCP server that exposes 150+ security tools (Nmap, sqlmap, Ghidra, Metasploit/MSFVenom, Trivy, Nuclei, TruffleHog, etc.) to MCP-compatible AI agents like Claude, GPT, or Copilot, letting them autonomously plan and execute network, web, binary, cloud, and CTF assessments. It ships 12+ specialized agents (BugBounty, CTF Solver, CVE Intelligence, Exploit Generator) that handle tool selection, parameter optimization, and attack-chain discovery, effectively turning an LLM into an autonomous pentest operator. The README includes explicit authorized-use guidance (pentests, bug bounty, CTF, red team) and warnings about the tool's broad system access.
github.comrepoAdded 18 Jun 2026🛡️ Security - tmylla/Awesome-LLM4Cybersecurity
Awesome-LLM4Cybersecurity is a GitHub-hosted, continuously updated literature review (861+ papers as of 2026) organized around three research questions: building domain-specific security LLMs, applying LLMs to cybersecurity tasks (threat intelligence, fuzzing, vulnerability detection, program repair, insecure code generation, LLM-assisted attack and defense), and future directions like security-focused LLM agents. It accompanies the paper "When LLMs Meet Cybersecurity: A Systematic Literature Review" (Zhang et al., Cybersecurity journal, 2025) and serves as an index for researchers tracking the intersection of large language models and security.
github.comrepoPublished and added 10 Jun 2026🛡️ Security


Showing 30 of 35
Show more