 Trojanized Claude Code Extension Plants an SSH Backdoor
Analysis of a trojanized anthropic.claude-code 2.1.313 extension (darwin-arm64), found on Open VSX, with a 66-line loader prepended to extension.js. It adds an svc-telemetry key to authorized_keys, opens a reverse SSH tunnel to 134.209.82.225, sets persistence (LaunchAgent, cron, scheduled task) and sends host recon over HTTP port 8099. Includes IOCs, hashes and response steps; no further payload download was found.
 opensourcemalware.comwriteupPublished and added 30 Oct 2026🛡️ Security
 Trojanized Claude Code Extension Delivered Persistent SSH Backdoor to Developer Machines
The Claude Code VS Code extension anthropic.claude-code 2.1.313 was published on Open VSX on 29 October 2026 with a malicious loader prepended to extension.js. On load it planted an attacker SSH key (svc-telemetry), installed per-OS persistence, opened a reverse SSH tunnel and beaconed host recon over HTTP. Cursor reports at most 5,000 users received it in an 11-hour window. The post gives the timeline, cleanup artifacts and credential rotation steps.
 stepsecurity.iowriteupPublished and added 30 Oct 2026🛡️ Security
 Malicious 'Pyronut' Package Backdoors Telegram Bots with Remote Code Execution | Blog | Endor Labs
Endor Labs analyzes the malicious PyPI package pyronut (versions 2.0.184–2.0.186), a trojanized fork of the Telegram framework pyrogram. It hooks Client.start() to import a hidden pyrogram/helpers/secret.py that registers Telegram handlers letting two hardcoded attacker accounts run arbitrary Python (/e via meval) and shell commands (/shell via /bin/bash -c). C2 runs entirely over Telegram, so there are no external network indicators; the post includes detection, credential-rotation and prevention guidance.
 endorlabs.comwriteupPublished and added 12 Oct 2026🛡️ Security
 Post-Exploitation Analysis & Artifacts – Citrix NetScaler CVE-2026-88771
watchTowr post-exploitation analysis of CVE-2026-88771, an unauthenticated log-poisoning command injection in Citrix NetScaler (advisory CTX697096). Sensors logged thousands of attempts: about 85% were OOB callbacks, the rest Sliver implants, a trojanized Dropbear SSH backdoor, a Perl stager with a PHP webshell, and SSH-key and secret-harvesting sprays. Includes artifacts to hunt (/var/tmp files, ns_helper, ns.conf edits) and IOC repo pointers.
 watchtowr.comwriteupAdded 30 Oct 2026, published 7 Oct 2026🛡️ Security
- Determined Attacker Uploads Malicious Webshells to Parks and Rec Management Platform Servers
Huntress details a four-act intrusion against a shared parks-and-recreation management platform running on IIS, where an attacker first tried noisy unauthenticated exploits (IIS 8.3 tilde enumeration, WebDAV verb abuse, upload-handler bypasses) before simply registering a member account and uploading .aspx webshells via a member-file upload feature across three servers. The attacker enumerated hosts, extracted web.config/connection strings, hunted for cardholder data (Fortis/MXMerchant webhook logs, CVV/card-number strings), then escalated to timestomping, re-deploying known-filename webshells, and finally injecting an AI-generated PowerShell/JS dropper into a trojanized jQuery file to turn site visitors' browsers into WebRTC/WebSocket C2 clients (ririmochii/bubuneeko Cloudflare Workers infrastructure). Includes a zh-CN PowerShell user-agent string used for attribution and full command/IOC listings useful for detection engineering.
 huntress.comwriteupAdded 1 Oct 2026, published 30 Sep 2026🛡️ Security
- DarkMe RAT: A VB6 APT Trojan Turned Conventional Infostealer
Huntress details a 2026 DarkMe RAT campaign that ditches the zero-days (CVE-2023-38831, CVE-2024-21412) previously used by the Water Hydra/EvilNum-linked group in favor of a plain phishing email delivering a disguised .pif file. The writeup reverse-engineers the full chain — msiexec pulling a wrapped MSI, a WSF stager, three obfuscated VB6 loader DLLs (Coconout.dll, Use.dll, Finalized.dll), a novel 329-app "inverted sandbox" gate, process hollowing into a signed clspack.exe, and Locked:// protocol-handler persistence — and corrects prior public reporting by showing the payload's "single-byte XOR" is actually a broken RC4 implementation. It closes with fresh C2 infrastructure (thatawful[.]boutique, port 7712), OSINT on delivery domains (including a related ClickFix/Efimer campaign), and concrete Sigma-style hunting rules and remediation steps.
huntress.comwriteupAdded 23 Sep 2026, published 22 Sep 2026🛡️ Security  Socket: Two Joyfill npm Beta Releases Compromised to Deliver DEV#POPPER Remote Access Trojan
Socket's research team found two beta releases of the @joyfill npm packages (@joyfill/layouts and @joyfill/components) contained an import-time JavaScript implant that resolves encrypted payloads through Tron, Aptos, and BNB Smart Chain transactions, ultimately dropping a 77KB Node.js remote-access trojan matching the DEV#POPPER family and sharing loader fingerprints with the PolinRider blockchain-loader campaign. The RAT establishes a Socket.IO C2 channel, executes arbitrary JS/shell commands, exfiltrates files and clipboard data, and persists by patching files inside VS Code, Cursor, Antigravity, Discord Desktop, GitHub Desktop, and the global npm CLI; a parallel detached-process branch fetches an additional bootstrap that can deploy a Python credential/browser-data stealer assessed as an OmniStealer variant. Because the implant fires on module load (not via npm lifecycle scripts), `--ignore-scripts` provides no protection, and the writeup includes full IOCs, blockchain addresses, C2 infrastructure, and MITRE ATT&CK mappings.
 socket.devwriteupAdded 22 Sep 2026, published 20 Sep 2026🛡️ Security
 ClearFake WebDAV infection chain delivers Amatera stealer, ZigCryptoStealer, and NetSupport Manager
Cisco Talos reconstructs two related WebDAV-based infection chains (tracked actor UAT-10820) that use a ClickFix fake-CAPTCHA lure, EtherHiding on BNB Smart Chain to stage JavaScript via a malicious Cloudflare Worker, and WebDAV-delivered disguised DLLs executed via rundll32 ordinal calls to drop the Amatera stealer. Depending on the C2 configuration, Amatera then deploys either a NativeAOT-loaded ZigCryptoStealer with a BYOVD EDR-killer driver and a Go-based Yamux reverse proxy, or a PowerShell stager that installs a trojanized NetSupport Manager RAT pointed at Russian C2 infrastructure. The post details loader internals, Amatera's dead-drop C2 resolution via Telegraph and Steam, and provides ClamAV signatures plus a full IOC list.
 blog.talosintelligence.comwriteupAdded 7 Oct 2026, published 8 Sep 2026🛡️ Security
- The Crypto Wallet That Never Opened: Tampered Exodus Installer Hides a Modular RAT
Huntress dissects a trojanized Exodus crypto wallet installer (v24.33.4, unsigned MSI built with WiX) that installs a genuine wallet but patches Electron's show()/focus()/center() methods so no window ever appears, then loads a modular RAT via a hand-written reflective PE loader implemented in JavaScript using the Node.js koffi FFI library. The RAT (VNC, SOCKS proxy, browser-credential stealer, recon module) beacons over WebSockets and uses Azure Table Storage as a dead-drop C2 channel to blend into legitimate cloud traffic, while delivery abuses double-extension .pdf.js phishing, ZIP-staged JS files, and an unused search-ms/WebDAV technique; the writeup also covers multi-layer string-array/arithmetic deobfuscation and includes full IOCs and mitigation guidance.
huntress.comwriteupAdded 3 Sep 2026, published 1 Sep 2026🛡️ Security - Mini Shai-Hulud worm hits openapi-react-query-codegen, spreads across npm, RubyGems, and PyPI | Blog | Endor Labs
Endor Labs researchers document a 'Mini Shai-Hulud' worm variant that compromised the openapi-react-query-codegen npm package and self-replicated across npm, expanding into RubyGems and PyPI ecosystems. The writeup traces how the worm trojanized a legitimate package to propagate malicious code cross-registry, illustrating an evolving multi-ecosystem software supply-chain attack pattern.
endorlabs.comwriteupAdded 3 Sep 2026, published 31 Aug 2026🛡️ Security - Teach Yourself to Phish | Huntress
Huntress security team shares their internal strategy for running monthly phishing simulations, including how they rotate lures (payment offers, spoofed conferencing tools), track click rates and report-before-click as success metrics, and use repeat-clicker data to target individualized training. Includes real click-rate trends from their own employees across January-February campaigns showing how difficulty escalation and exposure therapy reduce susceptibility over time.
huntress.comwriteupAdded 3 Sep 2026, published 28 Aug 2026🛡️ Security  Built to Blend: Miraak's Modular Post-Exploitation Framework
Blackpoint's Adversary Pursuit Group details Miraak, a novel modular post-exploitation framework discovered through proactive hunting of exposed open web directories. The writeup covers trojanized hostfxr.dll loaders that masquerade as legitimate .NET runtime components (with XOR 0x42/0x5A obfuscated payloads and configs), a PostgreSQL/Timescale database used as the C2 control plane instead of HTTP beaconing, Cobalt Strike BOF-compatible execution inside the agent, and an associated F#-based reverse TCP tunneling implant delivered via a trojanized Microsoft.DocAsCode.Common.dll (DocFX) dependency, with infrastructure pivoting via a self-signed "miraak-socks" TLS certificate and IOCs.
 blackpointcyber.comwriteupAdded 26 Sep 2026, published 26 Aug 2026🛡️ Security
 Dark Caracal Reloaded: GoCaracal — New Go Malware With Ethereum-Based C2 Fallback
Arctic Wolf Labs documents GoCaracal, a previously undocumented modular Go-based malware framework attributed with medium confidence to Dark Caracal (linked to Lebanon's GDGS), deployed alongside an updated Bandook variant in a June 2026 intrusion against a Venezuelan communications organization. The extended GoCaracal build features a novel Ethereum smart-contract (BulletproofC2) fallback that lets operators update C2 addresses via on-chain transactions without redeploying malware, and analysis of 249 samples traces the framework's four-phase development from January to July 2026. The report includes delivery-chain details (SVG phishing, URL shorteners, Delphi loader), infrastructure analysis (AEZA Group, AlexHost hosting), a YARA rule, and IOCs for detection.
 arcticwolf.comwriteupAdded 26 Sep 2026, published 26 Aug 2026🛡️ Security
 VMs won't contain cyber-capable agents
Trail of Bits gave GPT 5.6-Cyber preview access and tasked it with escaping a QEMU/KVM VM on a Debian 12 host; the agent succeeded three separate times, first via a recently disclosed host kernel bug (Januscape, CVE-2026-53359), then by chaining CVE-2026-9539 in libslirp with an unmarked bug fix, and finally by autonomously discovering and chaining multiple 0-day vulnerabilities in the kernel/QEMU stack over roughly 12 hours of largely unsupervised operation. The author argues off-the-shelf VMs (even hardened stable distros) no longer reliably contain a sufficiently capable AI agent — treat such agents as an APT — though Firecracker's minimal attack surface withstood the same agent's attempts.
 blog.trailofbits.comwriteupAdded 3 Sep 2026, published 26 Aug 2026🛡️ Security
- MacSync Stealer: How a Google Search for Claude Led to a macOS Infostealer
Huntress SOC analysts reverse-engineer MacSync, a macOS infostealer/RAT distributed via a sponsored Google Ads link to a fake "Apple Support"-branded claude.ai shared conversation that uses ClickFix to trick victims into pasting a curl/zsh loader into Terminal. The six-stage chain runs a polymorphic gzip/Base64 loader, an in-memory AppleScript stealer that harvests Chromium Safe Storage keys, keychain secrets, Telegram/SSH/cloud credentials, abuses TCC (Full Disk Access and Screen Recording) prompts, drops a Mach-O RAT with WebSocket/TLS C2 and an XOR-obfuscated fallback domain, and trojanizes 84 crypto wallet extensions/apps to phish seed phrases. The piece also compares it to prior AMOS Stealer and SectopRAT ClickFix campaigns and offers behavior-based detection guidance.
huntress.comwriteupAdded 3 Sep 2026, published 17 Aug 2026🛡️ Security  Cloud Threat Highlights: H1 2026
Wiz's H1 2026 cloud threat report documents a 60% jump in significant incidents driven by a doubling of supply-chain attacks (TeamPCP's npm/PyPI/GitHub Actions credential-harvesting spree, its open-sourced Shai-Hulud worm spawning Miasma/Hades/Megalodon/IronWorm follow-ons, North Korea's axios and @mastra trojanizations) and by growing attacks on AI infrastructure, including exposed unauthenticated MCP servers, LiteLLM/Dify/Langflow/n8n/Ollama vulnerabilities, and cryptominers deployed via a Langflow RCE. It also profiles JINX-0163, a cloud-native extortion group targeting non-human identities (service accounts/IAM roles) across AWS/Azure/GCP/Okta/Snowflake linked to the "FulcrumSec" extortion brand, and closes with concrete detection techniques for stolen access keys, Kubernetes VM Run Command abuse, GCP org-policy tampering, and CloudTrail user-agent/boto3 credential-provenance mismatches.
 wiz.iowriteupAdded 3 Sep 2026, published 6 Aug 2026🛡️ Security
 NullReceiver's Blank Crypto Transfers Solves the Challenges of EtherHiding
Researchers analyzing the DPRK-linked npm packages bianira-ui@1.27.0 and fluid-type-ui@2.0.8 (Contagious Interview campaign, trojanized clones of Tailwind CSS plugins) identified NullReceiver, a new blockchain C2-resolution technique that encodes the C2 IP address directly in the bytes of the recipient address of a zero-value, zero-data Ethereum transfer, rather than in calldata as with EtherHiding. Because it uses a disposable, never-reused destination address and carries no data field, it avoids the fixed "burn address" landmark that let Google's GTIG detect EtherHiding, making it harder to fingerprint. The writeup includes the malware's wallet-lookup logic, a code snippet, and full IOCs (packages, attacker wallet, encoded address, C2 IPs).
opensourcemalware.comwriteupAdded 3 Sep 2026, published 2 Aug 2026🛡️ Security Compromised npm Packages: @joyfill/components and @joyfill/layouts Ship an Obfuscated Remote Access Trojan
StepSecurity dissects malicious beta versions of @joyfill/components and @joyfill/layouts published to npm on July 28, 2026, which inject a five-stage obfuscated payload that executes on import rather than via a postinstall hook, so npm install --ignore-scripts does not stop it. The chain resolves its C2 server by reading a transaction on the Tron blockchain (with Aptos as fallback), decrypts a BNB Smart Chain transaction to find the next stage, and deploys a Socket.IO remote access trojan with worm-like self-propagation that patches the global npm CLI, VS Code/Cursor's @vscode/deviceid module, Discord desktop, and GitHub Desktop, plus a Python credential stealer targeting browser data, wallets, and Git/GitHub tokens. The writeup includes fully deobfuscated source code, IOCs (C2 IPs, Tron addresses, file hashes), and results from detonating the packages under Harden-Runner in a sandbox.
stepsecurity.iowriteupAdded 3 Sep 2026, published 30 Jul 2026🛡️ Security- Reverse Engineering the Six Stages of MacSync Stealer and RAT
Huntress reverse-engineers MacSync, a macOS stealer-and-RAT chain delivered via a weaponised claude.ai share link promoted through Google Ads malvertising, where a victim searching for how to install Claude on a Mac pastes a curl piped to zsh one-liner. The writeup traces all six stages: a polymorphic zsh loader, a server-side AppleScript that social-engineers Full Disk Access and validates the account password via dscl authonly, keychain and browser Safe Storage theft, a statically-linked C++ Mach-O RAT with WebSocket and AES-CBC C2 plus LaunchAgent persistence disguised as legitimate updaters, a signed Screen Recording-badged helper that phishes the TCC screen-capture permission, and trojanised Electron wallet apps (Ledger Live and Ledger Wallet) that inject a fake recovery-phrase phishing flow. It ties the kit to the AMOS and Atomic Stealer lineage via Russian-language code comments and shared infrastructure, and documents concrete IOCs including domains, C2 IP, mutex naming, and plist patterns for defenders.
huntress.comwriteupAdded 3 Sep 2026, published 29 Jul 2026🛡️ Security  Socket: Fake Corepack Site Distributes Infostealer and Proxyware to Developers
Socket's Threat Research team analyzed corepack[.]org, a fake site impersonating the Node.js Corepack tool that exploits its 2025 removal from Node.js bundling to rank in search results and trick developers into downloading a fake VPN installer. The installer drops OpenShield (an infostealer with browser-data/SSH-key theft, PowerShell execution, and run-key persistence) plus a bandwidth-sharing proxyware component that turns victim machines into proxy exit nodes, while a second click path delivers adware/trojan activity via OperaGXSetup.exe. The post includes full IOCs and details community/OpenJS Foundation takedown efforts against the domain.
socket.devwriteupPublished and added 25 Jul 2026🛡️ Security JFrog: NuGet Typosquat Rigs Betting Outcomes at Digitain
JFrog Security Research disclosed Newtonsoftt.Json.Net, a typosquatted NuGet package impersonating Newtonsoft.Json that shipped a fully functional JSON library alongside a trojanized fork targeting Digitain's FG-Crash betting platform. Using HarmonyLib to patch GenerateGameResult, the payload rigs crash-game coefficients on a schedule and, in later versions, exfiltrates rigged results to a C2 server disguised as Seq structured-logging traffic; seven published versions across three generations show escalating obfuscation (Dotfuscator, then ConfuserEx) before an unobfuscated final build exposed the full attack chain and IOCs.
 jfrog.comwriteupPublished and added 21 Jul 2026🛡️ Security
 SleeperGem: Compromised git_credential_manager, Dendreo, and fastlane RubyGems Drop a Persistent Backdoor
StepSecurity analyzes SleeperGem, a coordinated RubyGems supply chain attack that trojanized git_credential_manager, Dendreo, and a fastlane plugin between July 18-19, 2026. The malicious releases act as CI-evading loaders that, on developer machines, download a second-stage native daemon and deploy.sh from an attacker-controlled Forgejo host (git.disroot.org), install dual persistence via systemd and cron, and attempt privilege escalation to plant a setuid backdoor mimicking ping6. The post uses Harden-Runner audit-mode captures to document the full kill chain and provides IOCs and cleanup steps, crediting Aikido Security with the original discovery.
stepsecurity.iowriteupAdded 3 Sep 2026, published 19 Jul 2026🛡️ Security OpenAI Codex with GPT-5.6 Sol: competitive, zero cheating, one unique Django fix | Blog | Endor Labs
Endor Labs benchmarks OpenAI's Codex agent with GPT-5.6 Sol on its Agent Security League, reporting 70.9% FuncPass and 23.5% SecPass (third on security among 23 combos) and steady gains over GPT-5.4 and GPT-5.5. It documents a four-signal anti-cheating pipeline (conversation analysis, patch similarity, memorization detection, strict-test pass) feeding a multi-step LLM adjudicator, which flagged 7 instances and confirmed none as cheating. Case studies include an identical two-line django-rest-registration patch, FastAPI CVE-2021-32677, Django CVE-2024-39329, and a unique Django CVE-2021-44420 solve with a structurally different patch (similarity 0.57).
endorlabs.comwriteupAdded 23 Sep 2026, published 17 Jul 2026🧠 AI Socket: Operation Muck and Load
Socket details "Operation Muck and Load," a campaign starting with a malicious Go module (github.com/kaleidora/dnsub-scanning-tool) that impersonates a DNS scanner but launches hidden PowerShell to fetch and decode a multi-layer, XOR-encrypted loader. The loader resolves encrypted payload locations from public dead drops (Pastebin, GitHub, YouTube, Instagram, Telegram, Google Docs), retrieves a password-protected .7z archive masquerading as Microsoft Photos, and deploys AsyncRAT/Quasar/Remcos-style RATs and Vidar infostealer. Pivoting from the module, Socket uncovered 222 GitHub repositories across 190 accounts using automated force-push workflows tied to a single email (ischhfd83@rambler.ru) to fake activity and credibility, some directly hosting Vidar, XMRig/BitMiner, and trojan loaders.
socket.devwriteupPublished and added 16 Jul 2026🛡️ Security M-Red-Team: AsyncAPI Supply Chain Compromise via GitHub Actions
Wiz Research details how an attacker used 37 decoy pull requests to mask exploitation of a pull_request_target "pwn request" misconfiguration in the asyncapi/generator GitHub Actions workflow, stealing a privileged PAT belonging to the asyncapi-bot service account. The attacker then published four malicious npm packages (five versions) under the @asyncapi namespace with over 3 million weekly downloads, delivering a self-identified "M-RED-TEAM v6.4" multi-stage payload that fetches an 8.25MB encrypted bundle from IPFS and installs a 92,000-line trojan framework with systemd persistence and HTTP/Nostr/Ethereum/libp2p C2 channels, targeting browser credentials, SSH keys, npm/GitHub tokens, AWS credentials, and crypto wallets. The piece also analyzes partial technical overlap with the Miasma malware framework and the unrelated prt-scan campaign without making definitive attribution.
wiz.iowriteupAdded 3 Sep 2026, published 14 Jul 2026🛡️ Security Unauthenticated RCE in ArgoCD
Synacktiv details an unauthenticated arbitrary code execution vulnerability in Argo CD's repo-server gRPC service (GenerateManifest endpoint), found by building custom CodeQL RemoteFlowSource model packs for the Go codebase. The bug abuses the KustomizeOptions.BuildOptions field to inject kustomize CLI flags like --enable-helm --helm-command, achieving RCE and exfiltrating the Redis password; the team then shows how unauthenticated access to Argo CD's Redis cache lets an attacker poison cached manifests and git-ref commit hashes to force deployment of an attacker-controlled Kubernetes manifest even without selfHeal enabled, fully compromising the cluster. Disclosed to Argo CD maintainers in January 2025 and still unpatched at publication; mitigation requires Kubernetes NetworkPolicies (not applied by default in the Helm chart) restricting access to the repo-server and Redis.
 synacktiv.comwriteupPublished and added 11 Jul 2026🛡️ Security
 Socket: GlassWASM
Socket's Threat Research team found two trojanized Open VSX extensions (ExarGD.vsblack, noellee-doc/flint-debug) that impersonate legitimate, verified VS Code Marketplace publishers to exploit a cross-registry trust gap. The extensions ship a TinyGo-compiled WebAssembly payload whose strings are ChaCha20-encrypted and only decrypted in memory at runtime; once running, it polls the Solana blockchain for SPL Memo instructions sent to an attacker wallet to resolve a rotating C2 host (dodod[.]lat) and then executes OS-specific download-and-execute commands via Node's child_process. Socket attributes the campaign with medium confidence to the GlassWorm developer and names this WASM-stager variant "GlassWASM," providing full hashes, wallet/memo IOCs, and detection guidance.
socket.devwriteupPublished and added 16 Jun 2026🛡️ Security OpenSource Malware: Active Malware Campaigns in January-May 2026
OpenSourceMalware's analysis of active malware campaigns from January-May 2026, covering Lazarus Group's Contagious Interview (fake recruiter outreach delivering BeaverTail/InvisibleFerret via npm, PyPI, Go, Cargo, Packagist) and two new campaigns, TasksJacker (malicious .vscode/tasks.json auto-execution, including payloads hidden in .woff2 font files and fake VS Code dictionary files) and PolinRider (weaponizing stolen credentials via malicious PRs merged into projects like VS Code, Apache Superset, Rails, LangFlow, Expo). It also details TeamPCP's supply chain attack on Trivy's GitHub Actions repos using a leaked Aqua Security PAT to force-push malicious commits across 76 version tags.
opensourcemalware.comwriteupPublished and added 12 Jun 2026🛡️ Security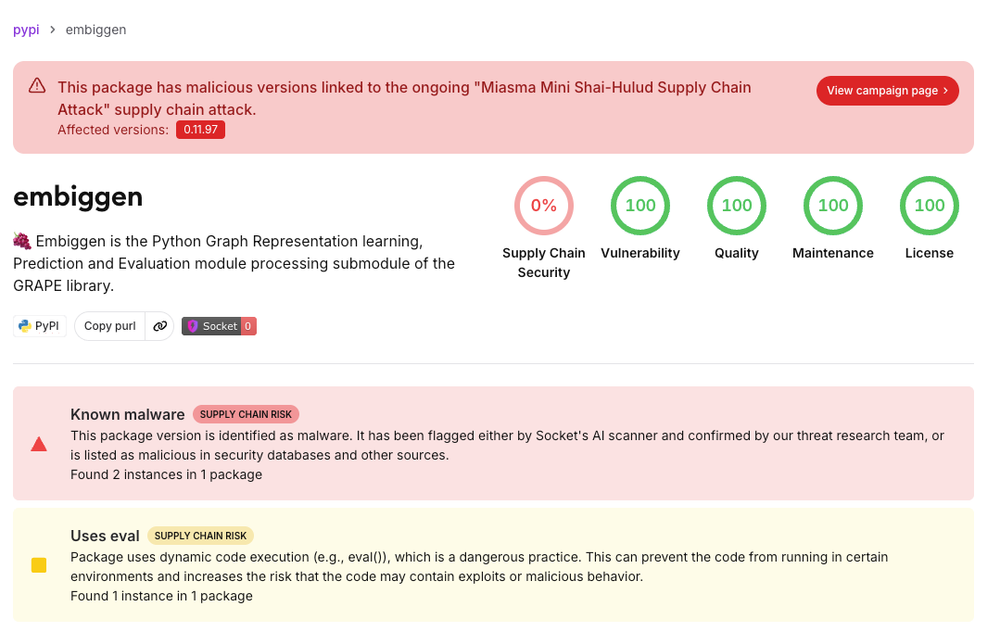 Miasma & Hades Worms
Socket's Threat Research team documents a new wave of 23 malicious PyPI artifacts (bioinformatics packages like embiggen/ensmallen/gpsea/pyphetools, typosquats like rsquests/tlask/rlask, and an MCP-themed langchain-core-mcp package) tied to the ongoing Mini Shai-Hulud/Miasma/Hades supply chain campaign. Unlike earlier .pth-hook wheels that bundled an obfuscated _index.js JavaScript stealer run via Bun, the bioinformatics cluster hides execution inside trojanized .abi3.so native extensions triggered at import time, while langchain-core-mcp ships only a .pth loader that scans sys.path for an external _index.js payload — a loader/payload split designed to evade detection rules. The payload also opens with a fake prompt-injection comment block meant to derail LLM-based static analysis tools before reaching the actual obfuscated stealer code that harvests GitHub, npm, PyPI, cloud, Kubernetes, SSH, and Docker credentials.
socket.devwriteupAdded 3 Sep 2026, published 10 Jun 2026🛡️ Security- Active Malware Campaigns in January-May 2026
OpenSourceMalware's analysis of active malware campaigns from January-May 2026, focused on Lazarus Group and TeamPCP. Details include Contagious Interview's pivot to abusing .vscode/tasks.json files to deploy BeaverTail/InvisibleFerret, the new TasksJacker campaign (multi-blockchain C2 across TRON/Aptos/BSC, hex-encoded JS hidden in .woff2 font files and a fake spellright.dict) that compromised 400+ repos including DataStax, and the follow-on PolinRider campaign that weaponized stolen credentials via malicious pull requests merged into high-profile projects like VS Code, Apache Superset, Rails, and Expo. Also covers TeamPCP's cascading attack via a leaked Aqua Security service-account PAT used to force-push malicious commits across version tags.
opensourcemalware.comwriteupAdded 3 Sep 2026, published 8 Jun 2026🛡️ Security





Showing 30 of 42
Show more