Skip to content

207 results for โ€œMicrosoftโ€

What you seeeverything
microsoft.comwriteup๐Ÿ›ก๏ธ Security

Inside a malicious Claude Code-branded extension and its persistent SSH backdoor

Microsoft Threat Intelligence analyzes a tampered anthropic.claude-code extension (versions 2.1.312 and 2.1.313) served on the Cursor marketplace on 29 October 2026. The injected JavaScript loader adds an SSH key labeled svc-telemetry, opens a reverse SSH tunnel and sets up persistence on macOS, Linux and Windows. The post gives cleanup steps, IOCs and Defender XDR hunting queries. VS Code Marketplace and npm were not affected.

CursorClaude CodeSSH+3
Protocol Tunneling (T1572)reverse SSH tunnelMicrosoft Threat Intelligence+2

Supply Chain, Blue Team & Detection, Malware & REยท Published and added 31 Oct 2026

microsoft.comwriteup๐Ÿ›ก๏ธ Security

From help desk impersonation to AD CS abuse: Investigating ESC1 and ESC8 intrusion paths

Microsoft Threat Intelligence analysis of two human-operated intrusions that began with Teams help desk impersonation and Quick Assist sessions, then diverged at AD CS. Case 1 abused an ESC1 template for privileged certificates and DCSync, with an excluded account later used for Rclone exfiltration. Case 2 used PetitPotam and ESC8 relay to get a domain controller certificate and PKINIT. Includes investigation steps, AD CS hardening and KQL hunting queries.

Active Directory Certificate ServicesMicrosoft TeamsQuick Assist+3
ESC1ESC8PetitPotam+12

Blue Team & Detection, Threat Intel, Offensive Securityยท Published and added 30 Oct 2026

oversecured.comarticle๐Ÿ›ก๏ธ Security

SDK security in mobile apps: the attack surface your team didn

Oversecured guide to SDK security in mobile apps, built around Microsoft's April 2026 disclosure of an intent redirection flaw in EngageLab's EngageSDK (50 million installs, fixed in 5.2.1). It covers SDK attack surfaces (exported components, WebViews, deep links, hardcoded secrets, payment crypto), a canhub image cropper file-overwrite example, why source-only SAST misses SDK code, and MASVS and PCI DSS expectations.

AndroidEngageSDKOversecured+3
intent redirectionEngageSDK intent redirectionMTCommonActivity+11

Mobile Security, Supply Chain, AppSecยท Added 29 Oct 2026

microsoft.comarticle๐Ÿ›ก๏ธ Security

Tracking AI adoption in North Korean threat actor tradecraft

Microsoft Threat Intelligence report on how North Korean actors use AI, ranking Jade Sleet, Coral Sleet and Jasper Sleet as operationalized, Diamond Sleet, Onyx Sleet, Pearl Sleet and Sapphire Sleet as accelerating, and Emerald Sleet as expanding. It documents AI-generated lures (100+ Onyx Sleet PDFs, August and September 2026), AI-built tooling such as Coral Sleet's private GitHub repository trojanizing, and Onyx Sleet and Pearl Sleet use of the ARTEX agentic pentest framework. It ends with mitigation and Defender guidance.

CursorGitHubRust+2
Jade SleetOnyx SleetCoral Sleet+9

Threat Intel, AI Securityยท Published and added 29 Oct 2026

securityweek.comarticle๐Ÿ›ก๏ธ Security

Adobe, Veeam, Juniper Networks Patch Critical Vulnerabilities

SecurityWeek roundup of patches from Adobe, Veeam and Juniper Networks covering over three dozen vulnerabilities. Adobe fixed 12 flaws (eight critical in Campaign Classic), Veeam fixed nine (including a cross-tenant RCE in Backup for Microsoft 365), and Juniper fixed 18 in Session Smart Router and Conductor. None were reported exploited. Juniper said CVE-2026-109618 (PHP2Shell) affects Junos OS but is not exploitable there.

Adobe Campaign ClassicVeeam Backup & ReplicationVeeam Backup for Microsoft 365+2
CVE-2026-109618PHP2Shell

otherยท Published and added 29 Oct 2026

huntress.comwriteup๐Ÿ›ก๏ธ Security

Camera Management Software Compromise Leads to Malware Deployment

Huntress investigation of incidents in September and October 2025 where a compromised camera management application (CMS.exe) was the initial access vector. Attackers dropped rs.win32.exe, a reverse shell, and sideloaded modified zlib DLLs (IPHLPAPI.DLL, samcli.dll) via the legitimate Microsoft WpcMon.exe in AppData, with Run key persistence and beaconing to 144.172.116[.]37. Includes detection pivots and hardening advice.

WindowsHuntress
DLL sideloadingCMS.exers.win32.exe+6

Threat Intel, Blue Team & Detectionยท Added 28 Oct 2026, published 27 Oct 2026

huntress.comwriteup๐Ÿ›ก๏ธ Security

AI, Scripts, Operator: Inside the ConnectWise Attack

Huntress analyzes Entra sign-in and audit logs from the ConnectWise Cloud Backup credential abuse of 15 October 2026 to judge whether a script, a person or an LLM agent drove it. It found a thread-pool spray, trial-and-error credential planting with a retry added within 55 seconds, and pilot-then-batch targeting. Huntress rates LLM involvement low to medium on its own data and medium to high with Microsoft's Storm-0940/ARTEX attribution. It ends with detections for service principal role self-assignment and vendor app baselining.

Microsoft Entra IDMicrosoft 365Microsoft Graph+3
Storm-0940ARTEXConnectWise Cloud Backup credential abuse+7

Threat Intel, Blue Team & Detection, Identity & Access, AI Securityยท Published and added 26 Oct 2026

cisa.govarticle๐Ÿ›ก๏ธ Security

CISA Publishes Significant Updates to ScubaGear and ScubaGoggles

ScubaGear v2.0 and ScubaGoggles v1.1.0 are CISA's updated SCuBA assessment tools for Microsoft 365 and Google Workspace secure configuration baselines. ScubaGear now uses direct REST API calls, adds Power BI coverage, a consolidated Security Suite baseline and app severity scoring. ScubaGoggles adds a GUI, Policy API integration and Gemini controls. The release supports BOD 25-01 compliance.

ScubaGearScubaGogglesMicrosoft 365+3
CISASCuBABOD 25-01+1

Cloud & Infra, GRCยท Added 29 Oct 2026, published 26 Oct 2026

securityweek.comarticle๐Ÿ›ก๏ธ Security

Node2Shell: Brotli Flaw Triggers Patching Across Microsoft, Node.js, Python Packages

CVE-2026-111497 (Node2Shell) is an out-of-bounds write in Google's Brotli decoder, versions 1.0.3 through 1.2.0, rated CVSS v4 9.2. Fixed in Brotli 1.0.10, 1.1.1 and 1.2.1, with patches from Node.js, Microsoft (.NET, Visual Studio, PowerShell on October 25), PyPI Brotli and brotlicffi, Bun, Envoy and Istio. Imperva showed code execution on Node.js 24.22.0 arm64; no in-the-wild exploitation is reported and some researchers say it only enables DoS.

BrotliNode.jsPython+3
CVE-2026-111497Node2ShellHTTP2Shell+5

AppSec, Supply Chainยท Published and added 26 Oct 2026

decrypt.coarticle๐Ÿ›ก๏ธ Security

Sweden's Government Offices Block ChatGPT and Claude, Keep Microsoft Copilot

Sweden's Government Offices will block ChatGPT and Claude on staff computers from 26 October 2026 and leave Microsoft Copilot as the only approved AI tool, citing information security. Digitalisation director Mikael Wettercrantz said unvetted AI use had involved sensitive inputs and poorly handled outputs. The Tax Agency and National Board of Institutional Care have similar bans, and the European Parliament disabled AI features in February 2026. Whether Copilot has Claude models enabled is unconfirmed.

ChatGPTClaudeMicrosoft Copilot
Swedish Government OfficesMikael WettercrantzSveriges Radio+5

GRCยท Published and added 24 Oct 2026

decrypt.coarticle๐Ÿง  AI

Sweden's Government Offices Block ChatGPT and Claude, Keep Microsoft Copilot

Sweden's Government Offices will block ChatGPT and Claude on staff computers from 26 October 2026 and keep Microsoft Copilot as the only approved AI tool, after a security review. Director of digitalisation Mikael Wettercrantz cites sensitive data entered into open services and tools used without a formal contract. The Tax Agency and the National Board of Institutional Care have similar bans. The article notes Copilot can include Claude models, and the Government Offices has not said whether that is enabled.

Microsoft CopilotChatGPTClaude
Sweden's Government OfficesMikael WettercrantzSveriges Radio+7

ai-policyยท Published and added 24 Oct 2026

microsoft.comwriteup๐Ÿ›ก๏ธ Security

Inside the LiteLLM 1.107.0 supply chain compromise: Credential theft through Python startup hooks

Microsoft's analysis of the LiteLLM 1.107.0 compromise, published to PyPI and container images on 21 October 2026. The wheel shipped cook.pth, cook.py and sitecustomize.py, so a credential collector (PRIVCOLLECT) ran whenever Python started, even without importing LiteLLM. It covers AES/RSA-encrypted exfiltration to litellm.dev, a re-armable Unix loader, Defender KQL hunting queries, ATT&CK mapping and rotation guidance.

LiteLLMPythonPyPI+3
cook.pthPRIVCOLLECTT1195.001+4

Supply Chain, Blue Team & Detection, Threat Intelยท Published and added 23 Oct 2026

securityweek.comarticle๐Ÿ›ก๏ธ Security

China APT Uses AI Pentest Tool Artex in ConnectWise Attacks

Storm-0940, a China-linked APT, used the open source AI penetration testing framework Artex to automate a mid-October 2026 campaign against ConnectWise customers, per Microsoft. Artex drove reconnaissance, password spraying and OAuth application abuse at more than 2,900 attempts per minute, with sign-in attempts against over 2,250 tenants. Attackers modified application credentials for persistence, and Microsoft advises correlating service principal sign-ins with Graph activity.

Microsoft Entra IDMicrosoft 365OAuth+3
Storm-0940ArtexConnectWise+4

Threat Intel, AI Security, Identity & Accessยท Published and added 23 Oct 2026

huggingface.cowriteup๐Ÿง  AI

Turning Database Grading into RL Rewards: Post-Training Agents with ThinkingBox

ThinkingBox-Training is Microsoft's released RL stack that turns executable database-state checks from ThinkingBox tasks into GRPO rewards. Fifty GRPO steps on 187 curated tasks raised Qwen3.8-27B pass@1 from 51.70% to 60.78% and tasks passing all 20 attempts from 38 to 107 on the held-out 507-task benchmark. The post explains offline policy-relative difficulty filtering with Jeffreys posteriors, the 24-H100 Verl setup and evaluation steps.

GRPOQwen3.8-27BVerl+9
MicrosoftThinkingBoxThinkingBox-Bench+11

training, agents, evalsยท Published and added 22 Oct 2026

unit42.paloaltonetworks.comarticle๐Ÿ›ก๏ธ Security

The Current Landscape of OAuth Attacks

Unit 42 survey of OAuth attacks that steal tokens after MFA, so access survives password resets. It covers account hijacking (device authorization and authorization code misuse), permission hijacking (vague or impersonating app names), and malicious redirects, including the error-triggered redirect campaign Microsoft documented in March 2026. It also describes COSF and OAuth-as-a-service flaws, PhaaS and LLM evasion trends, and defenses such as admin-only consent and redirect_uri audits.

OAuthMicrosoft Entra IDCloudflare Workers+2
Cross-User OAuth Session FixationCross-Tenant Client ID ConfusionCross-Connector OAuth Account Takeover+7

Identity & Access, Threat Intel, Blue Team & Detectionยท Added 30 Oct 2026, published 22 Oct 2026

decrypt.coarticle๐Ÿง  AI

What Is a Neocloud? The GPU Clouds Powering the AI Boom

Decrypt explainer on neoclouds, specialist providers such as CoreWeave and Nebius that rent Nvidia GPU clusters for AI training and inference. It covers the chips, power and debt model, Bitcoin miners turned AI hosts, and customers including Microsoft, AWS, Google and Anthropic. It cites Gartner's 14 October 2026 forecast that over 80% of neoclouds will stop operating independently by 2030.

EthereumBitcoin
CoreWeaveNebiusLambda+22

ai-infra, ai-policyยท Published and added 22 Oct 2026

huntress.comarticle๐Ÿ›ก๏ธ Security

Unboxing Phishing Kits: Huntress Examines 3 Real Kits

Recap of a Huntress Tradecraft Tuesday session (October 2026) on phishing kits that target Microsoft 365 tokens, including EvilTokens (a device-code phishing campaign abusing Railway) and the Kali365 control panel. It explains device-code phishing, adversary-in-the-middle and token replay. It lists detections (unfamiliar cloud sign-ins, device-code auth, new devices) and response steps (revoke refresh tokens, remove rogue devices, block device-code flow).

Microsoft 365Microsoft Entra IDHuntress+1
EvilTokensKali365device-code phishing+4

Threat Intel, Blue Team & Detection, Identity & Accessยท Published and added 22 Oct 2026

huntress.comwriteup๐Ÿ›ก๏ธ Security

M365 Token Spray and Replay Campaign Compromises Business Email Accounts

Huntress analysis of a July to September 2026 token replay ("token spraying") campaign: 497 successful Microsoft 365 sign-ins across 79 organizations, replayed from six addresses in 193.26.115.0/24 (1337 Services GmbH). Tokens came from AiTM relays, device-code phishing and social engineering. It covers four phases, rogue Entra devices, MFA method swaps, hidden inbox rules, hunting queries and Conditional Access guidance.

Microsoft 365Microsoft Entra IDConditional Access+3
token sprayingtoken replayadversary-in-the-middle+9

Threat Intel, Blue Team & Detection, Identity & Accessยท Published and added 22 Oct 2026

aikido.devarticle๐Ÿ›ก๏ธ Security

eMudhra CA compromise: eight private keys, and one of them is 4

eMudhra's eight intermediate CA certificates, chaining to emSign ECC Root CA - G3, had private keys below 256 (one is 4), disclosed on 17 October 2026 by a researcher known as Wayne. Browsers and Microsoft blocked them via revocation pushes, but curl, git, containers, language runtimes and IoT may still trust them. The post gives patched ca-certificates versions, test commands and the timeline.

cURLDockermacOS+3
eMudhraemSign ECC Root CA - G3Wayne+6

Supply Chain, DevSecOpsยท Published and added 22 Oct 2026

blog.talosintelligence.comadvisory๐Ÿ›ก๏ธ Security

Compromised eMudhra intermediate certificates

Cisco Talos describes eight eMudhra intermediate CA certificates (six TLS, two code signing) whose P-384 private keys were trivially recoverable because a flaw in an April 30, 2025 key generation ceremony produced weak keys with only 3 to 8 bytes of entropy. The post lists certificate SHA-256 hashes and serials, browser and Microsoft blocks, and the Go fix (CVE-2026-111943, Go 1.27.3 and 1.26.10) that filters chains by SPKI hash. It covers impact on VPNs, CI/CD and embedded devices, and Snort SIDs 67363 to 67374.

GoChromeVPN+3
CVE-2026-111943eMudhraemSign Root TLS CA - G3+8

Threat Intel, Cloud & Infraยท Published and added 21 Oct 2026

microsoft.comwriteup๐Ÿ›ก๏ธ Security

AI-driven, large-scale nation-state campaign using ARTEX enables supply chain compromise

Microsoft Threat Intelligence report on Storm-0940, a China-state aligned actor that used the open-source agentic AI pentest framework ARTEX from September 2026 to automate attacks on hundreds of organizations. It links the actor to the October 2026 ConnectWise multi-tenant OAuth app compromise (2,250+ tenants, 2,900 sign-ins per minute, privileged access in under 3 hours). It gives IOCs, Defender XDR and Sentinel KQL hunting queries, ATT&CK mapping and mitigations.

Microsoft 365Microsoft Entra IDMicrosoft Defender XDR+3
Storm-0940ARTEXConnectWise Cloud Backup+12

Threat Intel, AI Security, Identity & Access, Blue Team & Detectionยท Published and added 21 Oct 2026

securityweek.comarticle๐Ÿ›ก๏ธ Security

Browsers Block eMudhra Intermediate CAs Over Recoverable Private Keys

Eight intermediate CA certificates issued by Indian CA eMudhra in April 2025 had private keys generated with weak entropy, effectively all zeroes except the last byte, so they could be recovered almost instantly with baby-step giant-step. Mozilla and Google blocked them on 17 October 2026, Apple on 19 October and Microsoft on 20 October. eMudhra blamed a key ceremony script flaw that created a second, weaker key pair.

ChromeFirefoxCloudflare
eMudhraDennis Jacksonbaby-step giant-step+5

otherยท Published and added 21 Oct 2026
coindesk.comarticle๐Ÿ›ก๏ธ Security

A company that vouches for websites had secret keys so weak that 8 of them were cracked

eMudhra, an Indian certificate authority with over 60 million issued certificates, had eight CA private keys that were tiny integers such as 4, 56 and 237. Researcher Scott Helme recovered all eight from public certificates in under a second, and the keys were exposed from April 2025. Mozilla, Chrome, Apple and Microsoft blocked them between 17 and 20 October 2026, but curl, Python, Node.js, Go and Java accepted a forged Stripe API certificate because they skip revocation checks.

cURLPythonNode.js+3
eMudhraSectigoScott Helme+5

otherยท Published and added 21 Oct 2026

simonwillison.netarticle๐Ÿ›ก๏ธ Security

eMudhra Intermediate CA Compromise

eMudhra Intermediate CA Compromise is a 20 October 2026 link-blog post reporting that private keys of eight eMudhra intermediate CA certificates were compromised. They chain to roots trusted by the Mozilla, Microsoft, Apple and Chrome programs. Software bundling trust lists needs updating: Linux distros must update ca-certificates, and uv 0.13.4, pip 26.2.2 and certifi 2026.10.19 ship new lists. The post does not describe how the keys were compromised.

Pythonpipuv+2
eMudhra

otherยท Added 21 Oct 2026, published 20 Oct 2026

blog.talosintelligence.comarticle๐Ÿ›ก๏ธ Security

There's only so much code: the rise in vulnerability numbers

Cisco Talos analysis of why Microsoft Patch Tuesday advisories rose from about 100 a month before June 2026 to 975 in September and 1,415 in October, as frontier models such as Mythos mine old code. CVEs grew 105% year over year while CISA KEV additions grew 37%, and only three September advisories were exploited in the wild. It covers pressure on 90-day coordinated disclosure and open-source maintainers, the format string bug-class precedent, and defender advice.

SnortWindows
CVE-2021-44228MythosCISA KEV+8

AI Security, AppSec, Blue Team & Detectionยท Published and added 20 Oct 2026

securityweek.comarticle๐Ÿ›ก๏ธ Security

Microsoft Targets Rogue AI Agents With Dynamic Permissions, Risk Scoring

Microsoft extended Project Perception to treat internally deployed AI agents as insiders. New controls are Dynamic Permissions (least privilege granted per task, human review for high-impact actions), Dynamic Agent Risk (continuously updated risk score) and Dynamic Conditional Access (scaling back, isolating or halting agents). Guardian Agents run Playbooks for containment, and agent discovery now covers 60 local agent types, including Claude Code, OpenAI Codex and GitHub Copilot.

Project PerceptionMicrosoft Entra IDClaude Code+2
Dynamic PermissionsDynamic Agent RiskDynamic Conditional Access+4

AI Security, Identity & Accessยท Published and added 20 Oct 2026

securityweek.comarticle๐Ÿ›ก๏ธ Security

ConnectWise Suspends Cloud Services in Response to Cyberattack

ConnectWise suspended its Cloud Backup (formerly SkyKick), SaaS Security and Cloud Management services in October 2026 after a compromised application credential was used to access customers' Microsoft 365 tenants. Huntress saw the Cloud Backup identity sign in to 162 tenants on 15 to 16 October and attacker IP 144.172.64[.]128 try nearly 1,000 Entra tenants, with over 300 successful sign-ins. In one tenant, the Cloud Management Teams app added itself to Global Administrator and added client secrets to other apps. No restoration timeline has been given.

Microsoft 365Microsoft Entra IDHuntress+2
ConnectWise Cloud BackupConnectWise Cloud ManagementSkyKick+5

Threat Intel, Identity & Access, Blue Team & Detectionยท Published and added 19 Oct 2026

x.comadvisory๐Ÿ›ก๏ธ Security

Microsoft Threat Intelligence (@MsftSecIntel) on X

ConnectWise Cloud Backup (formerly SkyKick Backup, AppId 506e08f9-6e9a-4da4-942b-a099a03644ae) had its multitenant OAuth app compromised, per Microsoft Threat Intelligence. On 15 October 2026 the actor authenticated broadly as the service principal from 144.172.64[.]128, likely using customer-granted permissions such as Directory.ReadWrite.All, then ran Graph API reconnaissance and tried to add credentials to the service principal as a backdoor. The post lists IOCs, Defender alerts and hunting advice.

OAuthMicrosoft Entra IDMicrosoft Defender+1
ConnectWise Cloud BackupSkyKickDirectory.ReadWrite.All+2

Threat Intel, Identity & Access, Supply Chain, Blue Team & Detectionยท Added 20 Oct 2026, published 17 Oct 2026

huntress.comwriteup๐Ÿ›ก๏ธ Security

ConnectWise (SkyKick) Vendor Credentials Abused in M365 Attacks

Huntress documents abuse of ConnectWise Cloud Backup (formerly SkyKick) vendor app credentials, used on October 15 from 144.172.64[.]128 to obtain Microsoft Graph tokens in at least 162 customer M365 tenants via client assertion. In one tenant, a ConnectWise Cloud Management Teams app self-assigned Global Administrator and added client secrets to an MSP management app and Huntress's own app, a persistence technique. The post lists application IDs, Entra sign-in and audit-log checks, user-agent indicators (kiota-dotnet vs Python-urllib/3.12, curl/7.88.1), and mitigation steps such as disabling (not deleting) the enterprise apps and reviewing added credentials.

Microsoft 365Microsoft Entra IDHuntress+1
ConnectWiseSkyKick144.172.64.128+7

Threat Intel, Identity & Access, Blue Team & Detectionยท Added 17 Oct 2026, published 16 Oct 2026

microsoft.comarticle๐Ÿ›ก๏ธ Security

Managing open-weight model risk in enterprise deployments

Microsoft blog post introducing "Risk Management for Open-Weight Models in Enterprise", a joint Microsoftโ€“NVIDIA paper. It proposes a shared risk taxonomy (Cybersecurity, Data Protection, Content, Human-AI Interaction, Bias) grounded in ISO standards and the NIST AI RMF. The paper maps evaluations to risks as evidence and argues that risk depends on the model, use case, deployment and safeguards, not on weight openness alone. It also covers how responsibility for controls shifts when enterprises self-host models, and points to a joint repository of evaluations. The first paper focuses on the model layer; runtime, harness and application layers are planned for later.

Microsoft FoundryNVIDIA
NIST AI RMFISO

GRC, AI Securityยท Published and added 16 Oct 2026

microsoft.comarticle๐Ÿง  AI

Managing open-weight model risk in enterprise deployments

Microsoft's announcement of "Risk Management for Open-Weight Models in Enterprise", the first paper in a planned joint series with NVIDIA. It proposes a taxonomy of five risk categories (Cybersecurity, Data Protection, Content, Human-AI Interaction, Bias). The approach is grounded in ISO standards and the NIST AI Risk Management Framework. It maps evaluations to risks as evidence, stresses that weight openness alone doesn't determine risk, and explains how self-hosting shifts responsibility for safeguards. A joint repository will collect evaluations, and later work will cover the runtime, harness and application layers.

Microsoft Foundry
MicrosoftNVIDIANIST+7

ai-policy, evalsยท Published and added 16 Oct 2026

arxiv.orgpaper๐Ÿ›ก๏ธ Security

Approve What, Exactly? Effect Binding and Trusted Rendering for Agent Step-Up Authorization

Paper arguing that agent human-approval prompts count as a second factor only if agent compromise cannot forge them and they name exactly what is approved. It defines twelve attacks on the approval path (decoy recipients, amount cancellation, card padding, label spoofing, enrollment squatting, threshold splitting) and tests them against AP2, Microsoft's action-bound approval design and MCP elicitation. An audit of ten agent runtimes found no third-party verifiable approval record and post-approval argument changes in four of eight. The reference defense ASU (Agent Step-Up) renders the card from a canonical effect descriptor, has a phone passkey sign its digest, and executes only the stored call. It is proven in Tamarin (53 lemmas) and evaluated on 27,108 scripted trials and 609 AgentDojo pairs. The trusted card cut forged-narration attack success from 0.54 to 0.03 and raised LLM-approver catch rate from 0.30 to 0.98.

Model Context ProtocolMicrosoft
Agent Payments ProtocolAgent Step-UpASU+6

AI Security, Identity & Accessยท Added 17 Oct 2026, published 15 Oct 2026

decrypt.coarticle๐Ÿง  AI

Developer Who Cloned Photoshop With AI Just Did the Same to Microsoft Office

Decrypt reports that developer Brandon Thomas released WordCraft, GridCraft and DeckCraft, MIT/Apache-2.0 open-source clones of Word, Excel and PowerPoint. They were written in Rust with Anthropic's Claude (Opus 5.5) as a clean-room rebuild and run natively on Windows, macOS, Linux and BSD, and in a browser. Coverage is high (WordCraft 88% of ribbon features, GridCraft 513 of 523 Excel functions), but the authors rate them only about 50โ€“60% ready for real work. Every button is also an MCP command, so agents like Claude can drive the apps. The article is a useful data point on what AI-assisted "vibe coding" can produce in under two weeks, and on where it still falls short (file fidelity, stability).

RustClaudeModel Context Protocol+4
Brandon ThomasWordCraftGridCraft+10

coding-agents, mcpยท Published and added 14 Oct 2026

microsoft.comarticle๐Ÿ›ก๏ธ Security

The hidden network: Inside the phishing infrastructure ecosystem powering global cybercrime

Microsoft Threat Intelligence maps a Chinese-language cybercrime ecosystem: the YAM Store (Storm-3119), an initial access broker that hijacks Microsoft 365/Azure Education tenants and resells accounts, licenses and SharePoint/OneDrive storage, and the Storm-2990 phishing kits (CoGUI, Haozi, Iron Man System) sold via Telegram. It details the five-stage broker pipeline (app-only client-secret abuse, PnP Management Shell service principal, Graph permissions, Cloudflare DNS management), kit evasion features (geofencing, fake CAPTCHA, WebSocket/Telegram live interaction, 2,335+ templates), downstream device-code phishing and card fraud, and lists mitigations such as passkeys, phishing-resistant MFA and Conditional Access. Microsoft's DCU facilitated a disruption with law enforcement; kits sent over one billion messages since January 2026.

Microsoft 365AzureMicrosoft Entra ID+3
Storm-3119Storm-2990YAM Store+10

Threat Intel, Identity & Accessยท Published and added 14 Oct 2026

securityweek.comarticle๐Ÿ›ก๏ธ Security

Microsoft Disrupts Chinese-Language Phishing Market Behind 1B+ Messages

Microsoft and Health-ISAC seized domains tied to YAM Store (Storm-3119), an access broker that hijacks Microsoft 365 and Azure for Education tenants, and to the Storm-2990 phishing kits CoGUI, Haozi and Iron Man, under a Southern District of Florida order. The services sent over 1B malicious messages since January 2026 to 75,000+ organizations in 150+ countries; Microsoft disabled 20,000+ accounts and is blocking 100,000+ domains. Iron Man offers 2,335+ templates and real-time OTP capture, and Resecurity found it needs regular contact with a vendor licensing server, a dependency defenders can exploit.

Microsoft 365AzureCloudflare
YAM StoreStorm-3119Storm-2990+7

Threat Intelยท Published and added 14 Oct 2026

securityweek.comarticle๐Ÿ›ก๏ธ Security

Microsoft Patches Record 1,413 Vulnerabilities, Including Exploited Windows Zero-Day

SecurityWeek reports Microsoft's October 2026 Patch Tuesday fixed a record 1,413 CVEs (1,102 in Windows, 134 Office, 36 SharePoint), more than all of 2025, with the surge attributed largely to AI-driven discovery. The exploited zero-day CVE-2026-96951 is a Windows shell Mark of the Web security feature bypass (CVSS 8.8), added to CISA KEV with an October 16 deadline. Two flaws were publicly disclosed: CVE-2026-108398 (WDAC bypass) and CVE-2026-92707 (MessagePack-CSharp DoS), and Microsoft introduced 'risk cohorts' for patch prioritization.

WindowsWindows Defender.NET+2
CVE-2026-96951CVE-2026-108398CVE-2026-92707+5

Threat Intel, Blue Team & Detectionยท Published and added 14 Oct 2026

dfir.chwriteup๐Ÿ›ก๏ธ Security

Field Notes: EtherRAT Distributed Through a Legitimate Intune Workflow

DFIR case where a malicious MSI impersonating Advanced IP Scanner, sourced from a fake GitHub repo found via Bing, was imported by a customer into Microsoft Intune and deployed to four endpoints, running a Node.js-based EtherRAT chain. It traces the infections by correlating the MSI ProductCode, MDMAppInstaller/omadmclient process ancestry and Intune app inventory (Graph PowerShell query). It also covers renamed node.exe hash-hunting pitfalls, Ethereum RPC dead-drop C2 traffic, a screen-capture script and a second impersonating repo.

Microsoft IntuneNode.jsEthereum+3
EtherRATEtherHidingAtos Threat Research Center+4

Blue Team & Detection, Threat Intel, Malware & REยท Added 14 Oct 2026, published 13 Oct 2026

embracethered.comwriteup๐Ÿ›ก๏ธ Security

Visual Studio Copilot and SSMS Remote Code Execution (CVE-2026-103572)

CVE-2026-103572 is a remote code execution bug in Microsoft.VisualStudio.Copilot.Core.dll, shared by Visual Studio and SQL Server Management Studio. A trailing dot (for example `.mcp.json.`) bypasses the protected-filename check in EditsFunctionHandler.GetEditConfirmationTypeAsync, so a hijacked Copilot can rewrite its own MCP and settings files and run commands. The post covers path traversal and InstallationID leaks, indirect prompt injection demos, the October 2026 patch (GetFullPath), and a $0 bounty.

Visual StudioSQL Server Management StudioGitHub Copilot+3
CVE-2026-103572indirect prompt injectionpath traversal+5

AI Security, AppSec, Offensive Securityยท Added 29 Oct 2026, published 13 Oct 2026

rapid7.comadvisory๐Ÿ›ก๏ธ Security

Patch Tuesday - October 2026

Rapid7's analysis of Microsoft's October 2026 Patch Tuesday, which covers 1,413 vulnerabilities, 1,102 of them in Windows. It highlights the exploited Windows Shell Mark of the Web bypass (CVE-2026-96951) and the publicly disclosed .NET Framework WDAC bypass (CVE-2026-108398). It also covers five no-interaction Outlook preview-pane RCEs, the Edge advisories that list no CVEs, and end-of-support dates for Server 2012/2012 R2, Office 2021, Exchange 2016/2019 and Windows 11 24H2. The page text is truncated, so the later CVE tables are not seen.

Windows.NETMicrosoft Edge+2
CVE-2026-96951CVE-2026-108398CVE-2026-70242+63

Blue Team & Detection, otherยท Published and added 13 Oct 2026

huntress.comwriteup๐Ÿ›ก๏ธ Security

Fake WatchGuard VPN Site Steals Credentials

Huntress analyzes an October incident where an admin searching Bing for a WatchGuard VPN download landed on watchguard-vpn[.]net, a lookalike site whose popup.js harvests Server/Login/Password, deliberately rejects the first submission to get a second set, and posts to watchguard-ssl[.]online. Unlike earlier iterations (Secplicity, Microsoft Storm-2561), the final payload is the genuine, validly signed WatchGuard installer from the official CDN, so no malware is present for endpoint tools to flag. Covers infrastructure timeline, thin VirusTotal detections, and defender guidance (MFA, monitoring VPN logins from hosting ASNs, blocking domains, publishing official download links).

WatchGuardVPNHuntress+2
Storm-2561SEO poisoningwatchguard-vpn[.]net+5

Threat Intel, Blue Team & Detectionยท Added 14 Oct 2026, published 13 Oct 2026

blog.talosintelligence.comadvisory๐Ÿ›ก๏ธ Security

Microsoft Patch Tuesday for October 2026 โ€” Snort rules and prominent vulnerabilities

Talos summarises Microsoft's October 2026 Patch Tuesday, which covers 1415 vulnerabilities, 85 of them critical (67 RCE). One bug is exploited in the wild: CVE-2026-96951, a Windows Shell security feature bypass. The post groups the CVEs by Microsoft's exploitability rating (more likely, less likely, unlikely) with CVSS and CWE for each, covering Windows, Office, Exchange, Hyper-V, DHCP, QUIC, Outlook and Azure. It also lists the Snort 2 and Snort 3 rule ID ranges that detect exploitation attempts.

WindowsSnortMicrosoft Exchange Server+3
CVE-2026-96951CVE-2026-70229CVE-2026-70571+191

Blue Team & Detectionยท Published and added 13 Oct 2026

thezdi.comadvisory๐Ÿ›ก๏ธ Security

ZDI: The October 2026 Security Update Review

ZDI's October 2026 Security Update Review covers Adobe's 11 bulletins (174 CVEs) and Microsoft's record 1,415 CVEs. The only actively exploited bug is CVE-2026-96951, a Windows Shell Mark of the Web bypass. It also flags 59 wormable bugs, Microsoft's new "risk cohorts", and top-priority fixes in ColdFusion, Commerce, Experience Manager, SharePoint, SQL Server and Exchange.

WindowsMicrosoft ExchangeSharePoint+5
CVE-2026-96951CVE-2026-108398CVE-2026-92707+1425

AppSec, Blue Team & Detectionยท Added 27 Oct 2026, published 13 Oct 2026

en.cryptonomist.charticle๐Ÿง  AI

Microsoftโ€™s AI chip targets 40% more tokens per megawatt in 2027

Reports Microsoft's Maia 300, its third-generation in-house AI accelerator, unveiled October 12, 2026 with production workloads from 2027. Microsoft claims 40% more tokens per megawatt than leading GPU systems and up to 7x Maia 200's rack-level token throughput in a 96-accelerator rack. It uses a chiplet design on TSMC N2P that separates compute, memory-controller and I/O. It is aimed at long-context reasoning and agentic inference, while Nvidia and AMD stay in place for training. Useful as a data point on the shift toward custom inference silicon and model-chip co-design.

Maia 300Maia 200Azure+4
MicrosoftNVIDIAAMD+12

inference, ai-infraยท Published and added 12 Oct 2026

en.cryptonomist.charticle๐Ÿง  AI

300 Publishers Press Congress for AI Bot Scraping Disclosure Rules

Reports that about 300 publishers, including Condรฉ Nast and Hearst, are lobbying Congress to pass the bipartisan Stealth Bot Prohibition Act, introduced in the House in July. The bill would make AI scraping bots disclose their identity and purpose to site owners, with FTC civil penalties and state attorney general enforcement. It also lists the publisher AI licensing deals with OpenAI, Google, Microsoft, Meta and Amazon, and Ziff Davis's copyright suit against OpenAI. Useful as a snapshot of the push for scraper-transparency regulation and the licensing-versus-litigation split among publishers.

ChatGPT
Stealth Bot Prohibition ActCondรฉ NastHearst+13

ai-policyยท Published and added 11 Oct 2026

latent.spacearticle๐Ÿง  AI

[AINews] TypeSafe/Jev at >$100M ARR, $7.5B valuation 3 weeks after launch

AINews issue for 10/8โ€“10/9/2026 from Latent Space. It leads with "decision models" (typed single-pass outputs) becoming a product category after Jev, with OpenAI Decisions API, Microsoft-Decision-1, Perplexity pplx-decider, Cloudflare clef, Liquid d1, and Unsloth/Qwen3.5 training recipes. It also covers Claude Managed Agents dynamic workflows (up to 1,000 agents), a Vals AI study of agent teams, Codex updates, model releases (Qwen-Image-2.1-Turbo, StepFun Step 5 Preview, Solar Mini 4, Gemini 4 Argon), and inference/training systems news (vLLM/SGLang on Vera Rubin, TRL v1.15, DeepSeek stride weak spots).

vLLMSGLangTRL+17
Latent SpaceJevTypeSafe+35

models, agents, inferenceยท Published and added 10 Oct 2026

securityweek.comarticle๐Ÿ›ก๏ธ Security

Unpatched AhsayCBS Vulnerabilities Exploited in the Wild

Huntress reports in-the-wild exploitation of two unpatched AhsayCBS vulnerabilities (CVE-2026-105133 and CVE-2026-105134) affecting all versions up to and including the latest 10.3.4. Attackers chain an authentication bypass with OS command injection via the Replication Receiver API to gain unauthenticated RCE with System privileges, drop JSP webshells, deploy XMRig cryptominers disguised as Microsoft Edge, achieve persistence using a modified NSSM binary as a fake Microsoft Edge Update service, and load the vulnerable WinRing0x64.sys driver for kernel-level miner access (BYOVD). At least five organizations were targeted as of October 8; Huntress recommends restricting management-interface access until a patch is released.

HuntressWindowsPowerShell+2
CVE-2026-105133CVE-2026-105134BYOVD

Threat Intel, Offensive Securityยท Published and added 9 Oct 2026

x.comthread๐Ÿ›ก๏ธ Security

Ned Peterson (@NedPeterson99) on X

A post summarizing a joint FBI and six-country advisory on actors tied to Integrity Technology Group (the sanctioned Chinese firm linked to Flax Typhoon and the Raptor Train botnet). They password-sprayed Microsoft 365 and Exchange accounts over EWS, OWA, ActiveSync and PowerShell with EBurst. They then drained mailboxes with a PHP bot over Exchange Web Services and an office-cli utility using stored client ID, tenant ID and secret values, and exposed the stolen email to third parties through a web app, in some cases restricted to Xiamen IP addresses. Victims were in government, law enforcement, healthcare and religious organizations across Southeast Asia, Africa and North America, with activity since at least January 2021. Defensive takeaways: enforce MFA on every legacy path, retire basic auth and EWS, audit OAuth apps and service principals with mail-read rights, and alert on bulk mailbox pulls.

Microsoft 365Microsoft ExchangeEBurst+3
Integrity Technology GroupFlax TyphoonRaptor Train+3

Threat Intel, Identity & Accessยท Added 11 Oct 2026, published 9 Oct 2026

decrypt.coarticle๐Ÿง  AI

Google Wants Gemini to Be Your Next Coworkerโ€”Complete With Its Own Email Address

Decrypt reports on Google Cloud's newly announced Gemini Agent, a long-running AI agent that operates across Gmail, Docs, Sheets, Slides, Drive, Chat, Calendar, Microsoft 365 and Slack, and can run for hours or days on a single goal. The feature allows managers to spin up coworker agents with their own Workspace email address, calendar, Drive storage and directory listing, each given a cryptographically attested identity and a separate audit trail; agents connect to Salesforce, ServiceNow, Jira, Snowflake, BigQuery and any Model Context Protocol server, and are orchestrated across both Gemini and Anthropic's Claude models depending on cost and quality fit. Google pairs the launch with safety infrastructure, an Agent Sandbox, an AI network firewall called Agent Gateway, and real-time token-spend caps, citing a prior Claude Cowork VM-escape finding by Accomplish AI as the kind of containment failure it is designed to prevent.

GeminiClaudeGoogle Cloud+2
AnthropicThomas KurianGrok+9

agents, ai-infraยท Published and added 8 Oct 2026

microsoft.comarticle๐Ÿ›ก๏ธ Security

Post-quantum authentication: Why organizations should start testing certificate ecosystems now

Microsoft Security Blog post arguing that post-quantum cryptography planning must extend beyond encrypted-data confidentiality to authentication and certificate ecosystems, since larger PQC certificate chains and new algorithms like ML-DSA-87 can break PKI workflows, HSMs, and legacy infrastructure. It details Microsoft's PQC TLS Pilot Program, launched August 27, 2026, which lets approved certificate authorities (ComSign, DigiCert, HARICA, IdenTrust, Sectigo, Shanghai Electronic Certification Authority, SSL.com) test ML-DSA-87 certificate issuance under the Microsoft Trusted Root Program, plus Windows 11 builds (KB5101681, KB5101684) that support evaluating ML-DSA certificates via Schannel in non-production environments. It lays out a six-step readiness plan: inventory certificate dependencies, map trust relationships, assess vendor roadmaps, identify long-lived infrastructure, build test environments, and plan a multi-year migration.

WindowsSchannelTLS
ML-DSAML-DSA-87PQC TLS Pilot Program+8

Identity & Access, GRCยท Published and added 8 Oct 2026

x.comthread๐Ÿ›ก๏ธ Security

Dark Web Intelligence (@DailyDarkWeb) on X

A Twitter/X post digests joint advisory AA26-281A from FBI, CISA, NSA and allied agencies (UK, Australia, Canada, Japan, New Zealand, Spain) on China-based Integrity Technology Group enabling threat actors, tracked elsewhere as Flax Typhoon, Ethereal Panda and Red Juliett, to target US critical infrastructure, government, healthcare, education and law enforcement networks worldwide. The actors chain open-source scanners, large botnets, XSS, password spraying against Microsoft Exchange, VPN persistence and credential-harvesting scripts. CISA added five exploited CVEs (ISC BIND, Apache Struts, ProFTPD, ONLYOFFICE Docs, Strapi) to its KEV catalog with an Oct 11 federal remediation deadline, and STIX IOCs accompany the advisory.

ISC BINDApache StrutsProFTPD+3
CVE-2015-5477CVE-2016-3081CVE-2015-3306+7

Threat Intelยท Published and added 8 Oct 2026

securityweek.comarticle๐Ÿ›ก๏ธ Security

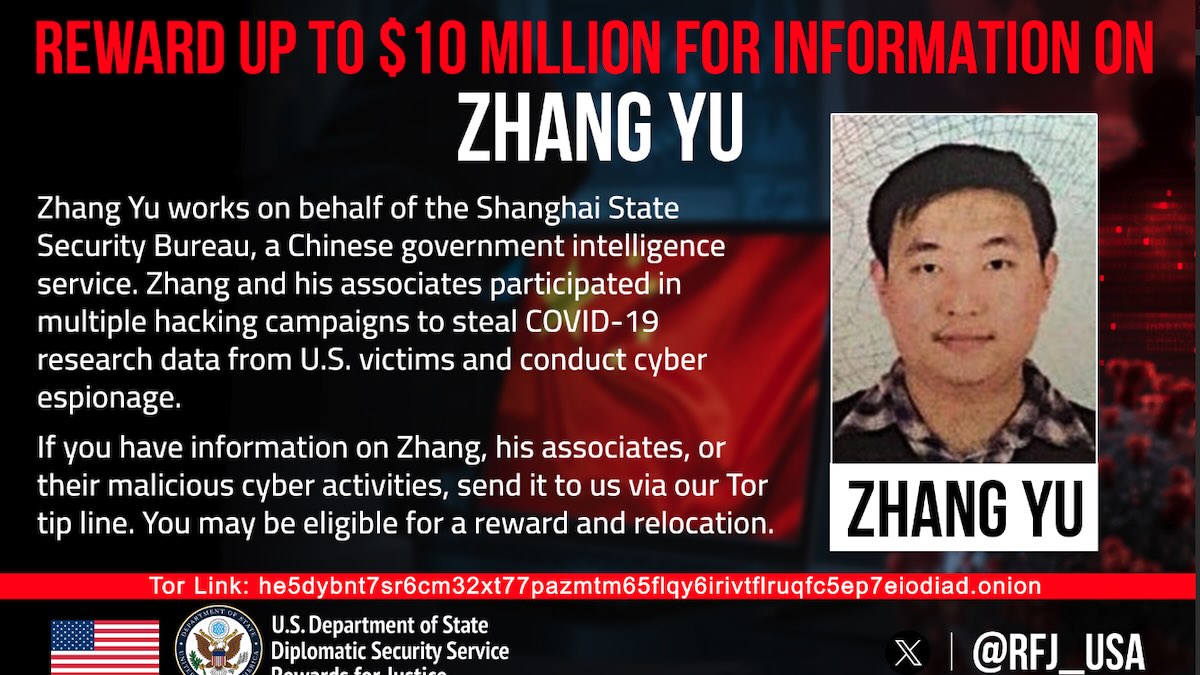
US Seeks Alleged Chinese Hafnium Hacker With $10 Million Reward

The US State Department's Rewards for Justice program is offering up to $10 million for information on Zhang Yu, a Chinese national charged alongside Xu Zewei for the 2021 Hafnium campaign that exploited Microsoft Exchange Server vulnerabilities and for earlier theft of COVID-19 research from US universities and immunologists starting in 2020. Zhang is identified as a director at Shanghai Firetech Information Science and Technology Company allegedly acting for the Shanghai State Security Bureau (part of China's MSS); Xu was extradited from Italy in April 2026 and has appeared in a Houston federal court while Zhang remains at large. Microsoft now tracks the Hafnium activity as Silk Typhoon; the FBI said the campaign compromised more than 12,700 US organizations.

Microsoft Exchange Server
HafniumSilk TyphoonZhang Yu+7

Threat Intelยท Published and added 8 Oct 2026

github.comrepo๐Ÿง  AI

microsoft/mxc

MXC is Microsoft's cross-platform sandboxed code execution system for running untrusted workloads โ€” model output, plugins, and tool calls โ€” behind a unified containment model with Rust, .NET, and Node SDKs. It offers multiple containment backends (ProcessContainer, Windows Sandbox, LXC, Bubblewrap, Seatbelt, MicroVM/Nanvix, Hyperlight, WSLC) with JSON-based filesystem, network, and UI policies, plus diagnostics like audit mode for building policies from observed access.

Rust.NETNode.js+1
Microsoft

ai-infraยท Added 8 Oct 2026

github.comrepo๐Ÿ›ก๏ธ Security

microsoft/mxc

MXC is Microsoft's cross-platform sandboxed code execution system for running untrusted code such as LLM/agent output, plugins, and tools, offering containment backends ranging from OS-native process sandboxes (Windows Sandbox, LXC, Bubblewrap, Seatbelt) to full VMs (Nanvix MicroVM, Hyperlight). It exposes a unified JSON-based policy model for filesystem, network, and UI access controls, with Rust, .NET, and Node SDKs plus diagnostic tooling (audit mode, access-denied logging) to help developers tune containment rules for agentic workloads.

WindowsLinuxmacOS+3

AI Security, Offensive Securityยท Added 8 Oct 2026

github.comrepo๐Ÿง  AI

Port of the TypeScript compiler, checker and lsp to Rust, by LLM

ts-rust (npm package tsc-rs) is a from-scratch Rust port of Microsoft's TypeScript compiler/checker/language server (typescript-go), produced almost entirely by LLM coding agents rather than hand-written. The author first spent over $400,000 in API tokens running GPT-5.6 Sol and GPT-6 Astra in long agentic '/goal' loops, which wrote 1.3M lines of Rust but plateaued at ~84% compatibility; switching to Claude Opus 5.5 produced a working version in 10 hours and, after ~$24,000 of further API spend over two weeks, reached 100% compatibility on tested real-world projects while passing all 181,711 ported Go baseline tests. Benchmarks show the Rust port running about 1.6x faster than the Go tsc 7 compiler (though slower than Bun's native `bun check`) across dozens of open-source codebases including VS Code, TanStack Query, Sentry and T3 Code.

RustTypeScriptGo+5
Claude Opus 5.5GPT-5.6 SolGPT-6 Astra+2

coding-agentsยท Published and added 8 Oct 2026

blog.talosintelligence.comadvisory๐Ÿ›ก๏ธ Security

Microsoft, Adobe, Apple, and Foxit vulnerabilities

Cisco Talos discloses eight vulnerabilities patched by vendors: a Photoshop installer privilege escalation (CVE-2026-48388), a macOS CoreWLAN information disclosure bug, two Foxit Reader flaws including a JavaScript CBF_Widget remote code execution (CVE-2026-57256) and an Array use-after-free (CVE-2026-91799), and four Windows kernel-driver bugs โ€” NETIO.sys information disclosure (CVE-2026-50475), two Cloud Files Mini Filter Driver issues (use-after-free CVE-2026-58613 and type confusion CVE-2026-80093), and a tcpip.sys out-of-bounds read (CVE-2026-49177). Each advisory gives the affected version and trigger mechanism, and Talos notes Snort coverage is available for detection.

Adobe PhotoshopmacOSFoxit Reader+2
CVE-2026-48388CVE-2026-57256CVE-2026-91799+12

AppSec, Offensive Securityยท Published and added 7 Oct 2026

github.blogarticle๐Ÿ›ก๏ธ Security

Secret protection must scale with software

GitHub essay by Secret Protection PM Erin Havens presenting nine quarters of telemetry (Q2 2024โ€“Q2 2026) on secret leaks: pushes with credentials grew 2.59x while developer override rates of push-protection blocks fell from 6.63% to 3.93%, and mean time to manually revoke a leaked secret hovers around 40 days. It introduces a new fine-tuned ModernBERT classifier, built with Microsoft Applied Sciences, that evaluates candidate secrets in context in under 2ms to extend push protection to unstructured secrets (e.g. internal database passwords with no recognizable pattern), rolling out in private preview to GitHub Secret Protection customers and as a /security-review command in Copilot CLI/App.

GitHubGitHub Copilot CLIModernBERT+1
ReviewBench

DevSecOps, AI Securityยท Published and added 7 Oct 2026

microsoft.comwriteup๐Ÿ›ก๏ธ Security

3 lessons from frontier AI vulnerability research

Microsoft Security's FORGE Lab shares results and lessons from four months of AI-agent-driven vulnerability research: 140 Windows CVEs (52 in September 2026's release), 155 internally validated reports across 23 open-source projects, and the first patch merged into the Linux kernel via the Linux Foundation's Akrites coordinated-disclosure initiative. Using their multi-model agentic scanning harness MDASH and GPT-5.5-based validation agents, the team measured automated PoC generation at an average $3.61/21.5 minutes per confirmed crash and local privilege-escalation AEG at $8.56/25.4 minutes, and argues the real bottleneck has shifted from finding bugs to validating and remediating them at matching speed. Specific disclosed CVEs include curl's CVE-2026-9545 and CVE-2026-13608, Node.js's CVE-2026-56848, and Linux kernel's CVE-2026-64563.

MDASHWindowsLinux kernel+3
CVE-2026-9545CVE-2026-13608CVE-2026-56848+6

AI Security, Offensive Security, AppSecยท Published and added 7 Oct 2026

huntress.comwriteup๐Ÿ›ก๏ธ Security

Phishing Campaign Abuses Microsoft Power BI to Deploy Rogue RMMs

Huntress details a phishing campaign that abuses legitimate Microsoft Power BI dashboards (app.powerbi.com) to host a fake "Download Reference" lure that bypasses mail filters trusting the Microsoft domain. Clicking the lure triggers browser/environment fingerprinting and Telegram-bot-based victim telemetry exfiltration via attacker domains (dailylifeproject.site, burnsworth.site, etc.), then silently downloads rogue ScreenConnect installers; a chained CMD/PowerShell script (SCAutoFix.ps1) deploys a second ScreenConnect instance, uninstalls the first for evasion, drops the defense-evasion tool HideUL_x64.exe, and sets a recurring scheduled task before Huntress's SOC intervened.

Power BIScreenConnectTelegram+3
HideUL_x64.exeSCAutoFix.ps1SCAutoRepairEvery2Min

Threat Intel, Blue Team & Detectionยท Published and added 7 Oct 2026

securityweek.comarticle๐Ÿง  AI

Anthropic Introduces 3-Tier Cyber Verification Program for AI Access

Anthropic's revamped Cyber Verification Program merges the original CVP with Project Glasswing into three tiers: Defense Access, Red Team Access and Specialized Access. All tiers cover Opus 5.5, Sonnet 5.5, Mythos 5.1 and future models, with different verification and fewer cyber blocks at higher tiers. Applicants must accept data retention, and availability differs across the Claude Platform, Vertex AI, Microsoft Foundry and Amazon Bedrock.

ClaudeClaude PlatformVertex AI+2
AnthropicClaude Opus 5.5Claude Sonnet 5.5+8

ai-policy, ai-safety, modelsยท Added 30 Oct 2026, published 7 Oct 2026

stepsecurity.ioarticle๐Ÿ›ก๏ธ Security

SubQuery npm package (@subql/common) compromised with credential-stealing payload

StepSecurity recaps a 48-hour (May 18-19, 2026) software supply-chain attack wave that hit every pipeline layer at once: the Nx Console VS Code extension (2.2M installs) stealing tokens from GitHub/npm/AWS/1Password, the trusted GitHub Action actions-cool/issues-helper hijacked via tag replacement, a trojanized Microsoft durabletask PyPI package pulled within a 35-minute discovery window, a self-replicating Shai-Hulud npm worm, and GitHub's own disclosure that ~3,800 internal source repos were exfiltrated. The piece argues traditional SCA/SAST/EDR/CNAPP tooling missed all of it because none monitor CI/CD runner runtime behavior (e.g., attackers reading /proc/pid/mem to extract secrets) or developer-machine IDE extensions, and ties the incidents to StepSecurity's Harden Runner, Dev Machine Guard, Compromised Actions Policy and Secure Registry controls.

GitHub ActionsVS Codenpm+6
Shai-HuludTeamPCPNx Console+3

Supply Chain, DevSecOps, Threat Intelยท Added 6 Oct 2026

Showing 60 of 207

Show more