Skip to content

63 results for β€œICE”

What you seeeverything
status.bunny.netadvisoryπŸ›‘οΈ Security

Bunny CDN Security Incident

Bunny CDN status-page notice, posted 28 October 2026, about unauthorized access at an infrastructure provider that hosted one bunny.net CDN node in Armenia. Traffic was stopped within 20 minutes and the server wiped. No access to the node was found, but cached content, Pull Zone configs and TLS certificates could have been exposed, so all platform certificates were reissued. Customers with their own certificates should rotate them with new private keys.

Bunny CDNTLS
bunny.netb-cdn.netbunny.run

Threat Intel, Cloud & InfraΒ· Added 31 Oct 2026, published 30 Oct 2026

x.comadvisoryπŸ›‘οΈ Security

lee1981 (@lee1981b) on X

CVE-2026-103780 is a stack-based buffer overflow (CWE-121) in Dell PowerProtect Data Domain / DD OS. An unauthenticated remote attacker could get command execution (CVSS 3.1 9.8, Dell DSA-2026-416). The post lists affected and fixed builds for four release trains (Feature Release, LTS2024, LTS2025, LTS2026). It adds KEV, EPSS and SSVC status, plus six defensive checks. The vulnerable service is not public.

Dell PowerProtect Data DomainDD OSCVSS+2
CVE-2026-103780CVE-2026-86400CVE-2026-86397+5

Blue Team & Detection, Cloud & InfraΒ· Added 31 Oct 2026, published 29 Oct 2026

cisa.govadvisoryπŸ›‘οΈ Security

Hitachi Energy TRO600 series products

ICSA-26-302-02 is a CISA republication of Hitachi Energy PSIRT advisory 8DBD000224 on the TRO600 series. It covers CVE-2026-10756 and CVE-2026-106087, which allow remote code execution and disclosure of sensitive information. Affected versions are TRO600 up to 9.2.1.6 and 9.1.1.0, plus 9.2.2.1 and 9.1.2.0. The page gives no per-CVE detail or CVSS scores, only general ICS hardening advice. Released 27 October 2026.

Hitachi Energy TRO600
CVE-2026-10756CVE-2026-106087Hitachi Energy PSIRT 8DBD000224+1

Hardware & RFΒ· Added 29 Oct 2026, published 28 Oct 2026

horizon3.aiadvisoryπŸ›‘οΈ Security

CVE-2026-20362 | Cisco Finesse Server-Side Request Forgery Vulnerability

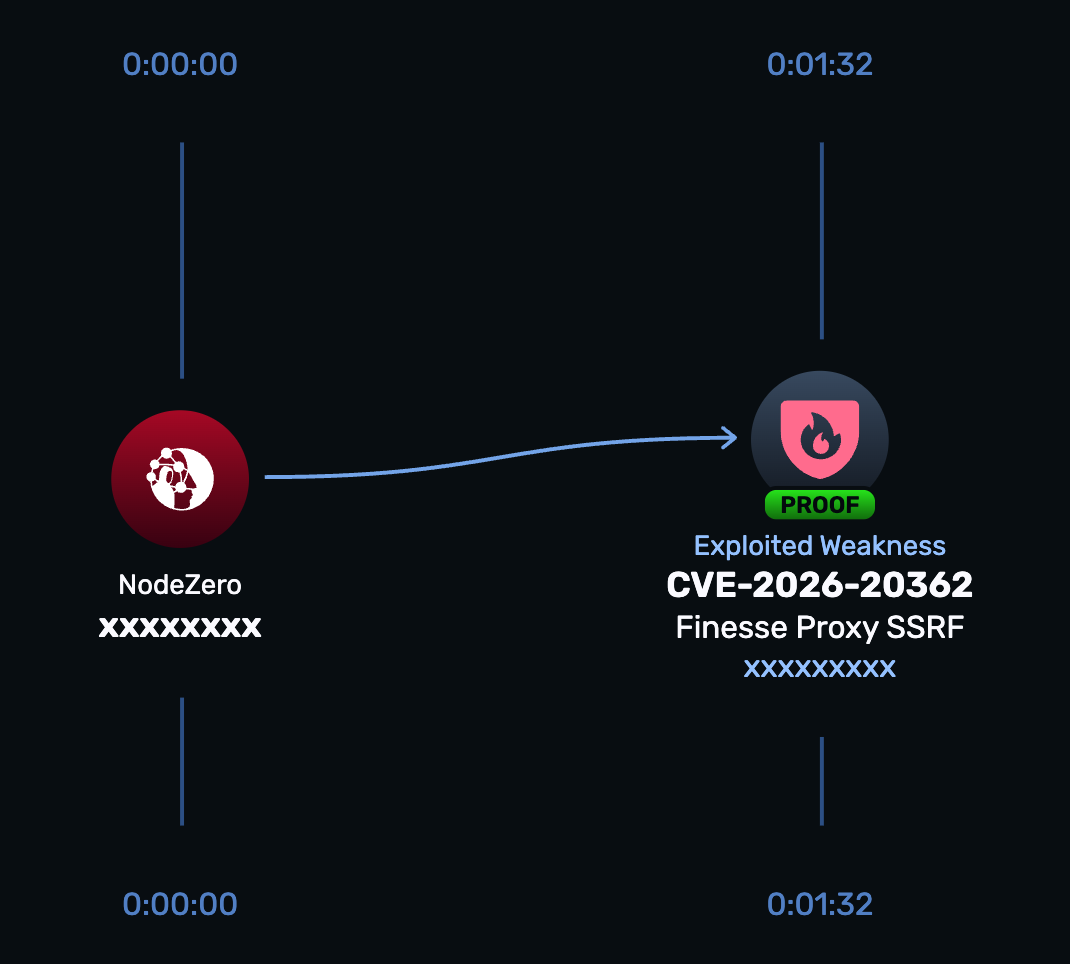
CVE-2026-20362 is an unauthenticated server-side request forgery in Cisco Finesse (CVSS 3.1 score 7.2), found by Horizon3 researchers Noah King and Brandon Peterson. The embedded Apache Shindig content proxy fetches attacker-supplied URLs, including loopback services such as the Finesse REST API at 127.0.0.1:8082, which returns SystemInfo with node hostnames and the XMPP domain. Cisco published its advisory on 7 October 2026. Fixes are planned for January and February 2027, and no workaround exists.

Cisco FinesseApache ShindigNodeZero+1
CVE-2026-20362SSRFCWE-918+3

AppSecΒ· Added 29 Oct 2026, published 28 Oct 2026

x.comadvisoryπŸ›‘οΈ Security

Dark Web Informer (@DarkWebInformer) on X

Veeam patched five vulnerabilities across Backup & Replication, Veeam Agent for Linux and Veeam ONE. The worst is CVE-2026-108142 (CVSS 9.1), an unauthenticated authorization bypass in the CDP Coordinator Service affecting Backup & Replication 13.0 and 13.1. Other fixes cover Linux agent privilege escalation, two path-traversal file writes, and a Veeam ONE MFA bypass; fixed builds are listed.

Veeam Backup & ReplicationVeeam Agent for LinuxVeeam ONE+1
CVE-2026-108142CVE-2026-105477CVE-2026-108140+3

AppSec, Identity & AccessΒ· Added 30 Oct 2026, published 28 Oct 2026

cisa.govadvisoryπŸ›‘οΈ Security

EPICS Base

CISA ICS advisory ICSA-26-300-01 (October 27, 2026) covers EPICS Base release 7.0.10 and earlier, with CVE-2026-114595 through CVE-2026-114598. Flaws include integer overflow, length parameter inconsistency and type confusion, allowing denial of service, memory corruption, information disclosure or remote code execution (CVSS v3.1 9.8). The fix is EPICS Base 7.0.11, with patches in epics-base and pvDataCPP pull requests.

EPICS BaseCVSS
CVE-2026-114595CVE-2026-114596CVE-2026-114597+5

AppSecΒ· Added 29 Oct 2026, published 26 Oct 2026

x.comadvisoryπŸ›‘οΈ Security

dbugs (@ptdbugs) on X

CVE-2026-106173 is a critical (CVSS 9.4) unauthenticated arbitrary file write in FortiSIEM's phQueryMaster gRPC service on port 27918/TCP. The SendQueryResult method builds a path from the query-id parameter without validation, so "../" sequences escape the directory and a null byte drops the appended filename and extension. Overwriting /opt/charting/redishb.sh, which runs every 60 seconds, gives remote command execution. Horizon3.ai published the analysis and a PoC.

FortiSIEMgRPCRedis+1
CVE-2026-106173PT-2026-111783Horizon3.ai+4

Offensive Security, AppSecΒ· Added 27 Oct 2026, published 26 Oct 2026

blog.railway.comadvisoryπŸ›‘οΈ Security

Railway Security Disclosure

Railway's security disclosure of 21 October 2026 says an unauthorized third party may have accessed encrypted customer environment variables and decrypted some of them. Railway links it to a series of attacks on platform companies aimed at compromising AI inference providers, and has asked upstream providers to revoke keys. It tells all users to roll every environment variable, API key and registry credential, and it paused all deployments. The notice gives no technical details of the intrusion.

Railway
Railway security incident October 2026

Threat Intel, DevSecOpsΒ· Added 22 Oct 2026, published 21 Oct 2026

aws.amazon.comadvisoryπŸ›‘οΈ Security

PHP web runtimes (CVE-2026-109618 and CVE-2026-109619)

AWS bulletin 2026-143-AWS covers CVE-2026-109618 and CVE-2026-109619, critical PHP web runtime flaws that let an unauthenticated remote caller run code, read process data or cause denial of service. Fixed in PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35; PHP 5.4 to 8.1 get no fix. It gives status for WorkMail, Elastic Beanstalk, Amazon Linux and Lightsail, plus AWS WAF rules, including a custom "PHP2Shell" rule matching PHP_SESSION_UPLOAD_PROGRESS and PHPSESSID.

PHPAWSAWS WAF+3
CVE-2026-109618CVE-2026-109619PHP2Shell+1

AppSec, Cloud & InfraΒ· Added 22 Oct 2026, published 21 Oct 2026

blog.talosintelligence.comadvisoryπŸ›‘οΈ Security

Compromised eMudhra intermediate certificates

Cisco Talos describes eight eMudhra intermediate CA certificates (six TLS, two code signing) whose P-384 private keys were trivially recoverable because a flaw in an April 30, 2025 key generation ceremony produced weak keys with only 3 to 8 bytes of entropy. The post lists certificate SHA-256 hashes and serials, browser and Microsoft blocks, and the Go fix (CVE-2026-111943, Go 1.27.3 and 1.26.10) that filters chains by SPKI hash. It covers impact on VPNs, CI/CD and embedded devices, and Snort SIDs 67363 to 67374.

GoChromeVPN+3
CVE-2026-111943eMudhraemSign Root TLS CA - G3+8

Threat Intel, Cloud & InfraΒ· Published and added 21 Oct 2026

github.comadvisoryπŸ›‘οΈ Security

PHP 8.2.35

PHP 8.2.35 is a security release of the PHP 8.2 branch that fixes two critical vulnerabilities, CVE-2026-109618 and CVE-2026-109619, which can allow unauthenticated remote code execution. The notes say no complete mitigations exist and updating is the only safe choice. PHP 8.2 reaches end of life on 31 December 2026, after which it gets no security fixes.

PHP
CVE-2026-109618CVE-2026-109619

AppSecΒ· Added 22 Oct 2026, published 21 Oct 2026

aikido.devadvisoryπŸ›‘οΈ Security

Critical vulnerabilities in PHP (PHP2SHELL)

PHP2SHELL is Aikido Security's advance notice of two critical remote code execution flaws in PHP itself, CVE-2026-109618 and CVE-2026-109619, both CVSS v4.0 9.2, with all versions treated as affected. The PHP security team will release fixes at 14:00 UTC on 21 October 2026, a day early after details leaked on 20 October. The post withholds exploitation details and workarounds.

PHPCVSS
CVE-2026-109618CVE-2026-109619PHP2SHELL+1

AppSecΒ· Published and added 21 Oct 2026

cisa.govadvisoryπŸ›‘οΈ Security

#StopRansomware: SafePay Ransomware (AA26-293A)

CISA advisory AA26-293A (20 October 2026) details SafePay ransomware, active since August 2024 with at least 600 victims across critical infrastructure. It covers initial access via Mullvad VPN IPs, phished profiles and edge-device CVEs, LOTL lateral movement with PsExec, WinRM and RDP, exfiltration with RClone and WinSCP, and ChaCha20/RSA encryption. It lists IOCs, MITRE ATT&CK mappings, incident response steps and mitigations.

MITRE ATT&CKRDPAnyDesk+3
CVE-2020-3259CVE-2023-20269SafePay+11

Threat Intel, Blue Team & DetectionΒ· Added 21 Oct 2026

news-web.php.netadvisoryπŸ›‘οΈ Security

Upcoming Critical PHP Security Release

The PHP security team announces an upcoming PHP security release that fixes two critical vulnerabilities, both rated CVSS v4.0 9.2. The release is scheduled for Wednesday, 21 October 2026 at 14:00 UTC. The team says it may release earlier if details become public or exploitation in the wild is seen. The notice gives no CVE IDs, affected versions or technical details.

PHPCVSS
PHP security team

AppSecΒ· Added 21 Oct 2026, published 20 Oct 2026

php.netadvisoryπŸ›‘οΈ Security

Upcoming Critical PHP Security Release

The php.net 2026 news archive opens with the PHP security team's advance notice of a release scheduled for 21 October 2026 at 14:00 UTC. It fixes two critical vulnerabilities, both rated CVSS v4.0 9.2, and may ship earlier if details leak or exploitation appears. Details and fixed versions come with the release. The archive also lists 2026 security releases (8.2.34, 8.3.35, 8.4.26, 8.5.11), PHP 8.6 RC3 and conference announcements.

PHPCVSS
PHP 8.2.34PHP 8.3.35PHP 8.4.26+1

AppSecΒ· Added 21 Oct 2026, published 20 Oct 2026
x.comadvisoryπŸ›‘οΈ Security

Microsoft Threat Intelligence (@MsftSecIntel) on X

ConnectWise Cloud Backup (formerly SkyKick Backup, AppId 506e08f9-6e9a-4da4-942b-a099a03644ae) had its multitenant OAuth app compromised, per Microsoft Threat Intelligence. On 15 October 2026 the actor authenticated broadly as the service principal from 144.172.64[.]128, likely using customer-granted permissions such as Directory.ReadWrite.All, then ran Graph API reconnaissance and tried to add credentials to the service principal as a backdoor. The post lists IOCs, Defender alerts and hunting advice.

OAuthMicrosoft Entra IDMicrosoft Defender+1
ConnectWise Cloud BackupSkyKickDirectory.ReadWrite.All+2

Threat Intel, Identity & Access, Supply Chain, Blue Team & DetectionΒ· Added 20 Oct 2026, published 17 Oct 2026

x.comadvisoryπŸ›‘οΈ Security

Dark Web Intelligence (@DailyDarkWeb) on X

Summary of SAP's October 13, 2026 Security Patch Day (16 new notes, 4 GitHub advisories). It leads with CVE-2026-89111, a CVSS 10.0 OAuth2 SSRF in SAP Cloud SDK for Python before 0.45.2, where an attacker-controlled tenant_subdomain redirects token requests and exfiltrates client credentials. It also lists three other critical flaws: broken access control in NetWeaver Visual Composer, code injection in S/4HANA substitution/validation rules, and a missing authorization check in the Manufacturing Integration and Intelligence (XMII) Configuration Service. It notes that none are in CISA KEV and SAP reports no in-the-wild exploitation.

SAP Cloud SDK for PythonSAP NetWeaverSAP S/4HANA+3
CVE-2026-89111CVE-2026-89110CVE-2026-89107+5

AppSec, Identity & AccessΒ· Added 15 Oct 2026, published 13 Oct 2026
rapid7.comadvisoryπŸ›‘οΈ Security

Patch Tuesday - October 2026

Rapid7's analysis of Microsoft's October 2026 Patch Tuesday, which covers 1,413 vulnerabilities, 1,102 of them in Windows. It highlights the exploited Windows Shell Mark of the Web bypass (CVE-2026-96951) and the publicly disclosed .NET Framework WDAC bypass (CVE-2026-108398). It also covers five no-interaction Outlook preview-pane RCEs, the Edge advisories that list no CVEs, and end-of-support dates for Server 2012/2012 R2, Office 2021, Exchange 2016/2019 and Windows 11 24H2. The page text is truncated, so the later CVE tables are not seen.

Windows.NETMicrosoft Edge+2
CVE-2026-96951CVE-2026-108398CVE-2026-70242+63

Blue Team & Detection, otherΒ· Published and added 13 Oct 2026
blog.talosintelligence.comadvisoryπŸ›‘οΈ Security

Microsoft Patch Tuesday for October 2026 β€” Snort rules and prominent vulnerabilities
Talos summarises Microsoft's October 2026 Patch Tuesday, which covers 1415 vulnerabilities, 85 of them critical (67 RCE). One bug is exploited in the wild: CVE-2026-96951, a Windows Shell security feature bypass. The post groups the CVEs by Microsoft's exploitability rating (more likely, less likely, unlikely) with CVSS and CWE for each, covering Windows, Office, Exchange, Hyper-V, DHCP, QUIC, Outlook and Azure. It also lists the Snort 2 and Snort 3 rule ID ranges that detect exploitation attempts.

WindowsSnortMicrosoft Exchange Server+3
CVE-2026-96951CVE-2026-70229CVE-2026-70571+191

Blue Team & DetectionΒ· Published and added 13 Oct 2026

x.comadvisoryπŸ›‘οΈ Security

lee1981 (@lee1981b) on X

CyberForge CVE of the Day #074 analyses CVE-2026-85097, a CVSS 9.8 unauthenticated file upload to PHP execution flaw (CWE-434) in the Bricksforge WordPress plugin through 3.1.8.9. Wordfence names 3.1.8.10 as the fix, and a separate vendor 4.0.1 Pro Forms upload-security notice has no verified mapping to the CVE. It gives a defender workflow: scope versions, preserve edge/origin logs, inspect resulting files and PHP-FPM handling, and verify the patched version is serving. It also separates KEV (no match), EPSS (0.312%) and SSVC (exploitation none) from compromise evidence.

WordPressPHPCVSS+2
CVE-2026-85097CWE-434Wordfence+4

Blue Team & Detection, AppSecΒ· Added 11 Oct 2026, published 10 Oct 2026

cisa.govadvisoryπŸ›‘οΈ Security

CISA AA26-281A: Chinese Government-linked Actors Combine Automated and Hands-on Hacking Tools to Steal Data

Joint FBI/CISA/NSA and allied-agency advisory on China-linked actors enabled by Integrity Technology Group (overlapping with Flax Typhoon, Ethereal Panda, Red Juliett). It details their TTPs: open-source scanners and the MicroScan exploit-script app, an XSS credential-harvesting payload dropping live700_v1.exe, EBurst password spraying against Exchange/O365, SoftEther VPN persistence, DCSync via DC.exe, and email theft via the Curlc4.txt PHP bot and the office-cli utility. It also provides IOCs, MITRE ATT&CK mappings, CVEs, incident response steps, and mitigations.

SoftEtherMicrosoft 365Active Directory+3
Integrity Technology GroupFlax TyphoonEthereal Panda+13

Threat Intel, Blue Team & DetectionΒ· Added 9 Oct 2026

x.comadvisoryπŸ›‘οΈ Security

lee1981 (@lee1981b) on X

CyberForge's CVE of the Day #073 covers CVE-2026-102255, a critical (CVSS 10.0) pre-authentication SSRF / confused-deputy flaw (CWE-918, CWE-441) in the SonicWall SMA1000 Work Place interface, per advisory SNWLID-2026-0017. It lists affected platform hotfixes (12.4.3-03526 and older, 12.5.0-02952 and older), fixed floors (12.4.3-03670, 12.5.0-03082), no workaround, and the exploitation picture (no known exploitation, not in KEV, EPSS 0.477%, SSVC automatable). It gives a six-step SOC playbook covering appliance scoping, AMC log preservation, hunting appliance-originated internal requests, correlating receiving-service changes, patching, and verifying every node, and it separates exposure, a lead, confirmed compromise and telemetry gaps.

SonicWallSMA1000CVSS+3
CVE-2026-102255CVE-2026-102256CVE-2026-102257+7

Blue Team & Detection, AppSecΒ· Added 12 Oct 2026, published 9 Oct 2026

securityweek.comadvisoryπŸ›‘οΈ Security

Citrix Urges Immediate Patching of Critical NetScaler Vulnerability

Citrix disclosed CVE-2026-107406 (CVSS 9.5), a critical memory overflow in NetScaler ADC and NetScaler Gateway that can lead to remote code execution or denial of service when appliances are configured as a SAML SP or SAML IdP, also affecting Secure Private Access Hybrid deployments using NetScaler. Patches are available in versions 14.1-73.46, 13.1-64.29, and the corresponding FIPS/NDcPP builds; Citrix says it is not aware of exploitation yet but urges immediate upgrades. The bulletin follows two other recently exploited NetScaler RCE/DoS zero-days (CVE-2026-88771, CVE-2026-88772) used against government, financial, education, legal, and professional-services organizations, and a separate DoS zero-day (CVE-2026-88779).

Citrix NetScalerSAML
CVE-2026-107406CVE-2026-88779CVE-2026-88771+1

AppSec, Identity & AccessΒ· Published and added 9 Oct 2026

github.comadvisoryπŸ›‘οΈ Security

go-ethereum v1.17.8 "Protein Sludge Pack"

Security-focused release notes for go-ethereum (Geth) v1.17.8, patching several denial-of-service vulnerabilities in the eth/snap p2p protocol handlers, hardening JUMPDEST analysis caching against post-Amsterdam-fork attacks, requiring IP verification before accepting discovery statements, fixing a rogue-STUN-server crash, and closing a DoS vector tied to BAL accounts. Most issues only become exploitable after the Amsterdam fork activates, and the release also includes RPC correctness fixes (eth_simulateV1, eth_createAccessList) and a Sparse Blobpool (EIP-8070) correctness bug.

go-ethereumEthereum
Amsterdam forkEIP-8070

BlockchainΒ· Added 8 Oct 2026

orca.securityadvisoryπŸ›‘οΈ Security

Critical Atlassian Path Traversal Exposes Sensitive Files Across 8 Products

Orca Security details CVE-2026-21589 (CVSS 9.3), a critical unauthenticated path traversal flaw affecting all versions of eight Atlassian Data Center and Server products: Bitbucket, Confluence, Jira Software, Jira Service Management, Bamboo, Crowd, Crucible, and Fisheye. Insufficient path validation lets remote attackers read arbitrary files within the web application root without authentication, and in Crowd SSO deployments this can expose plaintext credentials usable to create administrative accounts and take over the entire Atlassian ecosystem. The advisory lists fixed versions for each product and recommends WAF rules and log review for organizations unable to patch immediately.

JiraConfluenceBitbucket+3
CVE-2026-21589path traversal

AppSec, Identity & AccessΒ· Published and added 7 Oct 2026

securityweek.comadvisoryπŸ›‘οΈ Security

Atlassian Patches Critical Vulnerability Affecting 8 Products

Atlassian patched CVE-2026-21589 (CVSS 9.3), an unauthenticated arbitrary file access flaw affecting all versions of Bitbucket, Bamboo, Crowd, Crucible, Confluence, Fisheye, Jira Service Management, and Jira Software Data Center. WatchTowr researcher Yordan Ganchev notes that organizations using Crowd for SSO are especially at risk because authentication details are stored in plaintext at a predictable path, letting attackers mint admin accounts if Crowd endpoints are internet-reachable. Fixed versions are listed for each product; Atlassian recommends immediate patching or disconnecting internet-facing instances, with WAF rules as a stopgap.

BitbucketConfluenceJira+2
CVE-2026-21589watchTowrYordan Ganchev

AppSec, Identity & AccessΒ· Published and added 7 Oct 2026

watchtowr.comadvisoryπŸ›‘οΈ Security

Atlassian Jira, Confluence (and more) Arbitrary File Read Vulnerability (CVE-2026-21589)

CVE-2026-21589 is an unauthenticated arbitrary file read (path traversal) in eight Atlassian Data Center and Server products: Bitbucket, Confluence, Jira, Jira Service Management, Bamboo, Crowd, Crucible and Fisheye. Atlassian fixed it on 5 October 2026, and CISA added it to the KEV catalog on 15 October 2026. The page lists patching, WAF regex, Tomcat RewriteValve and urlrewrite.xml mitigations, and a log check for ".." sequences after up to two rounds of URL decoding.

JiraConfluenceBitbucket+3
CVE-2026-21589CISA KEVpath traversal+3

AppSec, Blue Team & DetectionΒ· Added 30 Oct 2026, published 6 Oct 2026

watchtowr.comadvisoryπŸ›‘οΈ Security

Frequently Asked Questions About the Atlassian Jira & Confluence Arbitrary File Read Vulnerability (CVE-2026-21589)

CVE-2026-21589 is an unauthenticated arbitrary file read in eight self-hosted Atlassian products: Bitbucket, Confluence, Jira Service Management, Jira Software, Bamboo, Crowd, Crucible and Fisheye Data Center. Attackers must know the exact file path, and watchTowr Intel observed exploitation by 6 October 2026. The FAQ covers the timeline (Atlassian advisory 5 October 2026), upgrade and WAF mitigations, and log searches for two dots next to a slash, backslash or double colon.

JiraConfluenceBitbucket+2
CVE-2026-21589path traversalCISA KEV+1

AppSec, Blue Team & DetectionΒ· Added 30 Oct 2026, published 6 Oct 2026

x.comadvisoryπŸ›‘οΈ Security

Dark Web Intelligence (@DailyDarkWeb) on X

Atlassian disclosed CVE-2026-21589, a critical (CVSS 9.3) unauthenticated path traversal flaw allowing remote attackers to read specific files within the web application root across its self-managed Data Center/Server products β€” Jira Software, Jira Service Management, Confluence, Bitbucket, Bamboo, Crowd, Crucible, and Fisheye. Fixed versions are listed for each product (e.g. Jira 9.12.40/10.3.26/11.3.12, Confluence 9.2.26/10.2.19), and Atlassian Cloud is already patched; WAF/URL-rewrite mitigations are available for those who can't upgrade immediately. The post's analyst note clarifies exploitation requires knowing the exact target file path (no directory listing), and as of Oct 5, 2026 it is not yet in CISA KEV with no public exploit reported.

JiraConfluenceBitbucket+3
CVE-2026-21589path traversal

AppSecΒ· Added 7 Oct 2026, published 6 Oct 2026

orca.securityadvisoryπŸ›‘οΈ Security

Citrix NetScaler Zero-Day Exploited in the Wild Crashes SAML Authentication Services

Analysis of CVE-2026-88779 (CVSS v4.0 8.7), an unauthenticated memory-overflow flaw in the nsaaad SAML authentication handler on Citrix NetScaler ADC/Gateway that lets attackers crash the SAML service and lock out VPN/SSO access indefinitely through repeated triggering. Affects NetScaler 14.1 before 14.1-73.41 and 13.1 before 13.1-64.28 (plus FIPS/NDcPP builds); watchTowr Labs reproduced it via honeypot activity, Citrix confirmed targeted in-the-wild exploitation from IP 213.209.159.55, and CISA added it to KEV on 2026-10-04 with an Oct 7 federal remediation deadline. Some researchers suspect the overflow could extend to RCE beyond the documented DoS, though Citrix hasn't confirmed this.

Citrix NetScalerSAMLCVSS+1
CVE-2026-88779CWE-119watchTowr Labs+1

Identity & Access, Threat IntelΒ· Published and added 5 Oct 2026

Showing 30 of 63

Show more