Skip to content

109 results for β€œINE”

What you seeeverything
x.comthread🧠 AI

🚨 AI News | TestingCatalog (@testingcatalog) on X

Drex for Finance is a multimodal decision model from Nace AI, post-trained for sub-second financial decisions such as card-payment fraud checks. It takes a document or transaction log plus a fixed set of answers and returns a probability for each. On 3,361 decisions from 48 held-out finance benchmarks it scored 85.7%, against 70.9% for GPT-6 Luna and 77.7% for Drex Max v1.1. It is available on the Nace Console.

Drex for FinanceNace Console
Nace AIDrex Max v1.1GPT-6 Luna+1

models, evalsΒ· Added 3 Nov 2026, published 2 Nov 2026
x.comthread🧠 AI

CuteGuy☣️ (@cutetoxicguy) on X

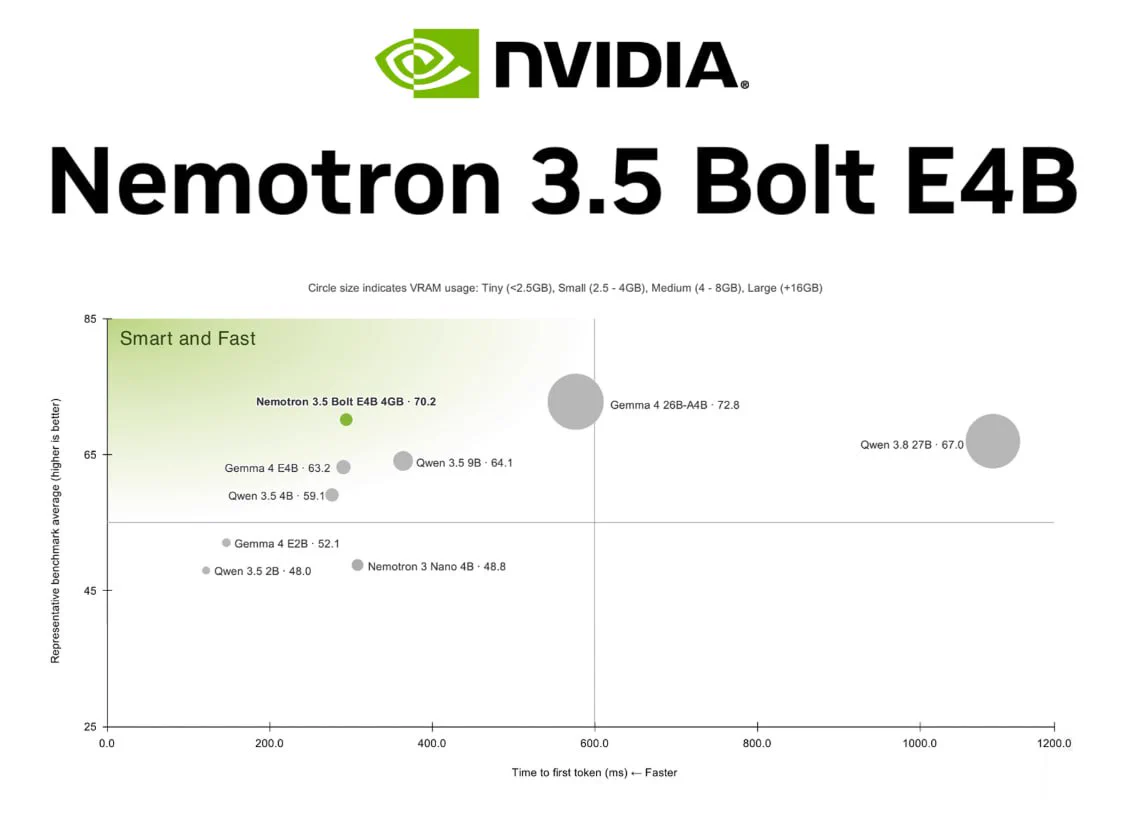
Nemotron 3.5 Bolt E4B is an NVIDIA open-weights model with 8B total and 4B active parameters, built on Gemma 4 E4B and post-trained with NeMo RL and NeMo Gym. It targets local agents in about 4GB of GPU memory, with 64K context, 35 languages, multi-step tool calling and configurable reasoning. NVIDIA's llama.cpp tests show 133.4 tokens/sec on an RTX 5070 and 15.5 on a Jetson Orin Nano. Benchmarks are NVIDIA's own.

llama.cppOllamaLM Studio+9
NVIDIANemotronGemma 4+8

models, inference, agentsΒ· Added 3 Nov 2026, published 2 Nov 2026

x.comthread🧠 AI

Smarthouse (@localyzapp) on X

A reply by Smarthouse (@localyzapp) on X to a question about the best harness for connecting local models to a Minecraft server. It suggests an MCP server that wraps RCON plus a small agent loop. The main pitfall is block coordinates: expose "/execute if block" as a read tool so the agent can check blocks before placing them, or it will hallucinate terrain.

Model Context ProtocolMinecraftRCON

mcp, agentsΒ· Added 2 Nov 2026, published 1 Nov 2026

x.comthreadπŸ›‘οΈ Security

lee1981 (@lee1981b) on X

CyberForge Weekly CVE Rundown #008 covers seven CVEs from 26 to 31 October 2026: Wasmtime/Cranelift miscompilation, Rust zip cloaking, Qode Membership account takeover, Dell PowerProtect Data Domain stack overflow, two Progress WS_FTP Server flaws and Kubeflow Pipelines log reads. Each entry gives fixed versions and defender actions. A 1 November check adds EPSS values dated 31 October and notes none of the IDs were in CISA's 30 October catalogue.

WasmtimeKubeflow PipelinesWS_FTP Server+3
CVE-2026-115889CVE-2026-115905CVE-2026-92885+11

AppSec, Cloud & InfraΒ· Added 3 Nov 2026, published 1 Nov 2026

x.comthreadπŸ›‘οΈ Security

lee1981 (@lee1981b) on X

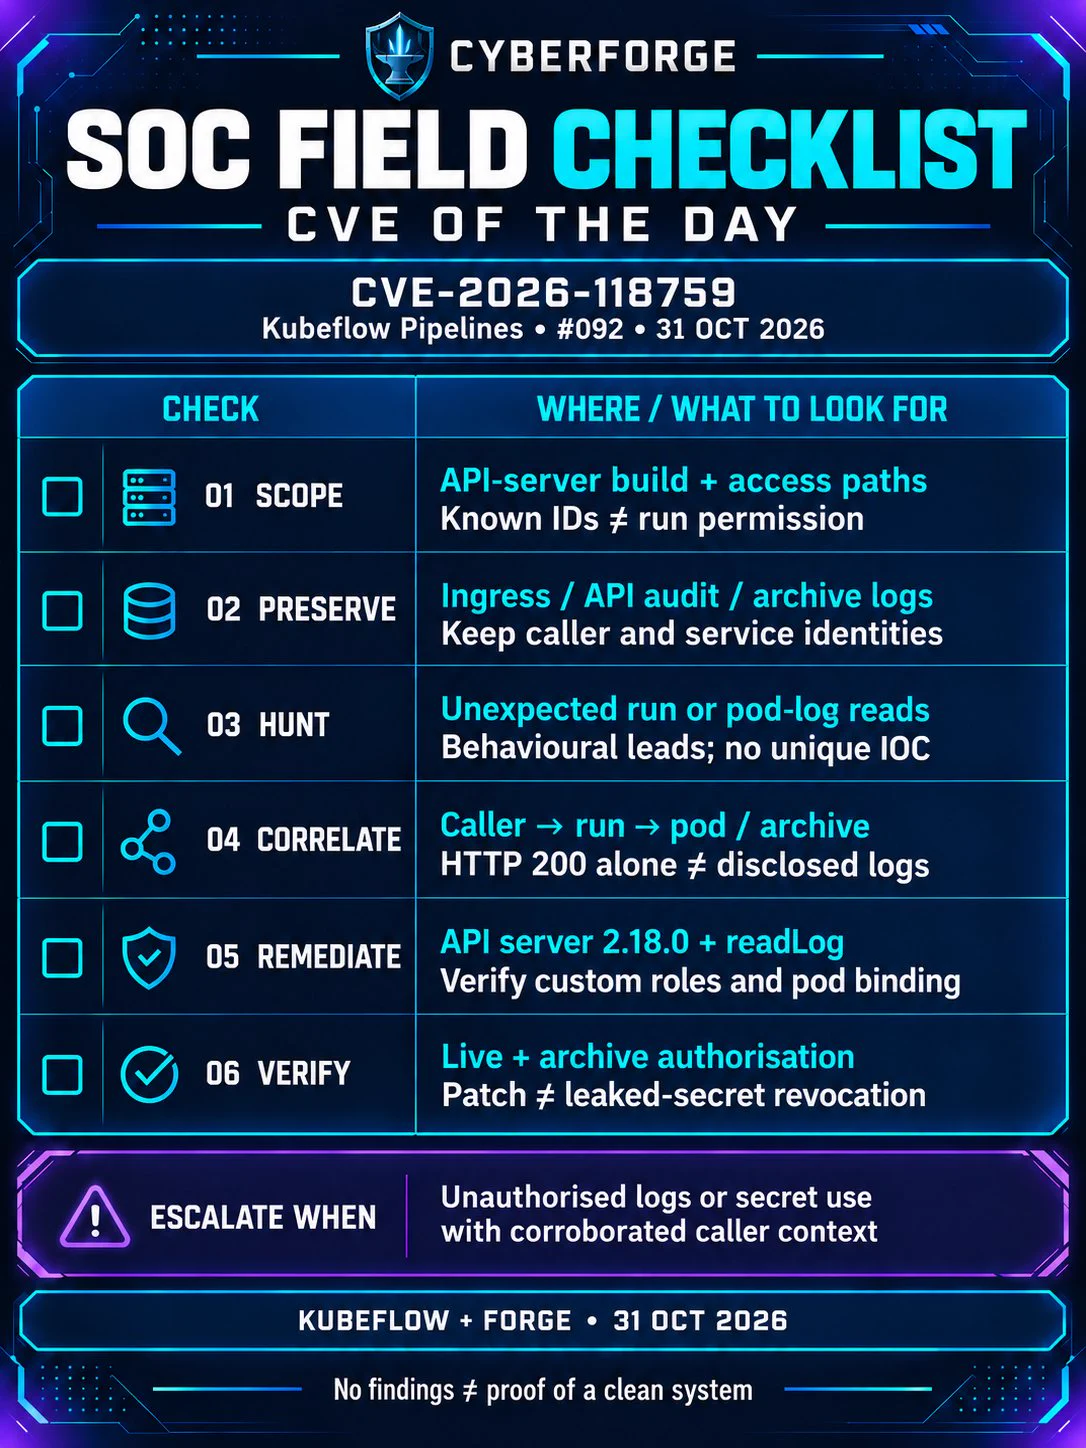
CyberForge "CVE of the Day" #092 covers CVE-2026-118759 in Kubeflow Pipelines. The post says a run-log request must carry permission, not just a run ID: knowing the identifier does not authorize reading that workload's output. It points to Kubeflow's advisory, but the fetched text is cut off before any affected versions, fix or exploit details.

Kubeflow Pipelines
CVE-2026-118759CyberForgeIDOR

AppSec, Cloud & InfraΒ· Added 3 Nov 2026, published 31 Oct 2026

ethresear.chthreadπŸ›‘οΈ Security

ERC draft: Independent Simulation Result for (STVA)

ERC draft "Independent Simulation Result" (STVA) defines a canonical, content-addressed SimulationResult (success, gasUsed, returnData, stateDiffHash, logsHash, snapshotId, resultHash) that any wallet, hardware device or verifier can recompute from the same VerificationPayload and state snapshot. It targets compromised-frontend and UI/calldata-mismatch attacks, and defines Basic, Standard and Strict compliance levels. Open questions are stateDiff encoding, prestate proofs and binding to capability tokens.

EthereumrevmSafe
ERC-7730EIP-712ERC-4337+3

BlockchainΒ· Published and added 30 Oct 2026

x.comthreadπŸ›‘οΈ Security

elvis (@omarsar0) on X

Thread by Elvis Saravia (omarsar0) summarising an Anthropic-led paper on pretraining data poisoning of CLI agents. Poisoning 0.1% of pretraining data planted a remote code execution backdoor in Qwen3 models (0.6B, 1.7B, 4B) trained from scratch. It survived SFT, DPO and RL, and fired on about 92% of triggered prompts at 4B. At a 0.0005% poison rate (about 2,500 documents) it still fired on 1.4% of prompts.

QwenLLM
Anthropicremote code executiondata poisoning+1

AI SecurityΒ· Added 31 Oct 2026, published 30 Oct 2026

x.comthreadπŸ›‘οΈ Security

Trail of Bits (@trailofbits) on X

Trail of Bits post on X summarising Binance's initial investigation into a security incident. Binance suggests a compromised DevOps engineer's laptop let an attacker reach a service container and submit unauthorized withdrawal transactions. The text says no evidence has been found of wallet private key compromise. The fetched text is truncated and gives no further detail.

BinanceTrail of Bits

Threat Intel, BlockchainΒ· Published and added 30 Oct 2026

x.comthread🧠 AI

Artificial Analysis (@ArtificialAnlys) on X

Artificial Analysis launched an HLE-Diamond leaderboard in v5 of its Intelligence Index, covering the refined 1,000-question Humanity's Last Exam from CAIS and Scale AI. Each question runs once without tools, graded by GPT-5.6 Luna (medium) as pass@1. Gemini 4 Carbon (high) leads at 69%, Claude Opus 5.5 (max) scores 68%, and the top open weights model, Kimi K3.1 Pro, reaches 37%.

Artificial AnalysisArtificial Analysis Intelligence IndexHLE+9

evals, modelsΒ· Published and added 30 Oct 2026

x.comthread🧠 AI

Prasenjit Sarkar (@stretchcloud) on X

A thread on Cloudflare's agent-readiness scan and the AgentReady.org open spec for "Agent Experience", developed with Vercel, Stripe, Auth0, Mintlify, Google, Netlify and Elementor. The scan grades whether agents can find a site (robots.txt, DNS), read clean Markdown, pass bot rules, and discover an MCP server or API catalog. One quoted example raised a score from 20 to 67 by shipping an API catalog with Link headers, an MCP server card, a skills index and an AI catalog file.

Model Context ProtocolCloudflareMarkdown
AgentReady.orgOraNick Launches+7

mcp, agentsΒ· Added 30 Oct 2026, published 29 Oct 2026

x.comthread🧠 AI

SGLang (@sgl_project) on X

SGLang announces Day-0 support for Mistral Large 4 ("Le Chonk"), saying it is the first engine to serve the model on NVIDIA Vera Rubin. The post describes the model as Mistral's largest to date: a natively multimodal 1T-parameter mixture-of-experts model covering instruct, reasoning, coding and agentic workflows. The fetched text is truncated, so benchmark claims and launch commands are not visible.

SGLangMixture of Experts
MistralMistral Large 4NVIDIA

inference, modelsΒ· Added 30 Oct 2026, published 29 Oct 2026

x.comthread🧠 AI

TENSA Engineering (@TENSAEng) on X

A post by TENSAEng describing a workflow for staying within coding-tool usage limits. ChatGPT chat sits outside those limits, while Claude and Grok chats share a pool with Claude Code, Codex and Grok Build. Architecture, file layout, step order and acceptance checks are planned in ChatGPT and saved as repo docs. Claude Code or Codex then implements one small chunk per fresh session.

ChatGPTClaude CodeCodex+2

coding-agents, ai-policyΒ· Added 29 Oct 2026, published 28 Oct 2026

x.comthreadπŸ›‘οΈ Security

JFrog Security (@JFrogSecurity) on X

JFrog Security announces research on CVE-2026-102479 in Vert.x, which skips validating the letter 'L' in header names and so accepts `Content-Xength` as `Content-Length`. JFrog Research chained this with a dangling-byte primitive to bypass reverse proxy socket validation. They demonstrate end-to-end response poisoning and session fixation behind real reverse proxies. The post links to a full writeup; the tweet itself gives no exploit detail.

Vert.xJFrog
CVE-2026-102479response poisoningsession fixation+2

AppSec, Offensive SecurityΒ· Added 30 Oct 2026, published 28 Oct 2026

x.comthreadπŸ›‘οΈ Security

Christiaan Stoudt (@cstoudt) on X

Thread on CVE-2026-97631, a critical (9.5) flaw in TianoCore EDK II UEFI firmware, found by Alex Matrosov and Dan Holmes-Mitra. It is exploitable only while a machine is PXE network booting and the attacker sends an oversized ICMP error from the same network. Code execution also needs the exact firmware build, and Secure Boot does not help. The fix landed in EDK II main on 15 October but is not in a stable release. No known exploitation, and not in CISA KEV.

EDK IIUEFITianoCore+2
CVE-2026-97631Alex MatrosovDan Holmes-Mitra+3

Hardware & RFΒ· Added 30 Oct 2026, published 28 Oct 2026

x.comthreadπŸ›‘οΈ Security

Hakimi Eiqbal (@hakimieiqbal) on X

A practical reverse-engineering map by hakimieiqbal on X that picks tools by target: native binaries, .NET, Electron, iOS, firmware, WebAssembly and network protocols. It introduces REA (morluto/rea), which connects coding agents to RE tools, and lists MCP bridges for IDA Pro, Ghidra and radare2. It adds an evidence-first workflow and free courses such as pwn.college and OpenSecurityTraining2.

GhidraIDA Proradare2+3
REAFlare-OnOpenSecurityTraining2+5

Malware & RE, LearningΒ· Added 29 Oct 2026, published 28 Oct 2026

x.comthread🧠 AI

Hakimi Eiqbal (@hakimieiqbal) on X

A thread by Hakimi Eiqbal that maps reverse-engineering tools by target type: native binaries, Electron, .NET, iOS, firmware, WebAssembly and network protocols. Its AI sections cover REA (an open-source layer connecting coding agents to analysis tools) and MCP bridges for IDA Pro, Ghidra and radare2. It argues for an evidence-first workflow and gives a prompt that separates verified facts from hypotheses.

Model Context ProtocolClaude CodeCodex+8
REAIDA Pro MCPGhidrAssistMCP+3

coding-agents, mcpΒ· Added 29 Oct 2026, published 28 Oct 2026

x.comthreadπŸ›‘οΈ Security

Kizuno18 (@Kizuno18) on X

Thread by Kizuno18 on the move from local stdio/Docker Model Context Protocol servers to remote HTTP/SSE endpoints in enterprise infrastructure. It names three trade-offs: credential boundary inversion (short-lived OAuth/JWT tokens instead of long-lived admin tokens on workstations), tool schema bloat solved by deferred discovery, and governance via HCP Terraform policy-as-code (Sentinel/OPA), audit trails and approvals. It is opinion, with no data or implementation detail.

Model Context ProtocolTerraformDocker+2
Sentinelblast radiuspolicy-as-code+1

AI Security, Identity & Access, DevSecOpsΒ· Added 29 Oct 2026, published 27 Oct 2026

x.comthread🧠 AI

Kizuno18 (@Kizuno18) on X

Kizuno18's X post argues that the move from local stdio and Docker MCP servers to remote HTTP/SSE endpoints matures the Model Context Protocol in enterprise infrastructure. It lists three trade-offs: short-lived OAuth/JWT bearer tokens replace mounted admin credentials, deferred tool discovery avoids roughly 20k tokens of eager schema loading, and HCP Terraform enforces Sentinel/OPA policy, audit trails and approvals server-side. Opinion post with no benchmarks or code.

Model Context ProtocolDockerTerraform+5
Kizuno18HCP TerraformOPA

mcpΒ· Added 29 Oct 2026, published 27 Oct 2026

x.comthreadπŸ›‘οΈ Security

Buchi Reddy B (@buchireddy) on X

Buchi Reddy B's X thread comments on Forever Security's research (Gal Weizman, Omer Samet) on coding agents. A web page silently writes a fake AGENTS.md or CLAUDE.md into a Downloads folder, and Codex and Claude Code follow it as project rules. Codex then wrote an attacker's MCP server into the machine-wide config, so one injection becomes a standing connection for every session. It asks whether teams inventory runtime MCP connections against approved lists.

CodexClaude CodeModel Context Protocol
Forever SecurityGal WeizmanOmer Samet+3

AI SecurityΒ· Added 28 Oct 2026, published 27 Oct 2026

x.comthreadπŸ›‘οΈ Security

Prasenjit Sarkar (@stretchcloud) on X

Campfire is a self-hosted tool that runs Claude Code, Codex, Goose, Aider and OpenHands in one tab. Risky actions need permission voting (majority approves, any single deny blocks, 30 second timeout), and session replay traces which file or tool call triggered an action. The post cites Forever Security's finding that Codex followed a planted AGENTS.md instruction over 90% of the time and Claude Code about half the time. It also cites the February Cline release compromise via a poisoned GitHub Actions cache.

CampfireClaude CodeCodex+3
Forever SecurityAGENTS.mdprompt injection+1

AI SecurityΒ· Added 28 Oct 2026, published 27 Oct 2026

x.comthreadπŸ›‘οΈ Security

BenjaminπŸ‘¨β€πŸ’» (@Hislordship_9) on X

Thread on Forever Security's finding that a planted Markdown "Engineering Work Guidelines" file in ~/Downloads made Codex add a "project-tools" MCP server to ~/.codex/config.toml. The server ran npm install function-color, a known malicious package, and started a child session with --dangerously-bypass-approvals-and-sandbox. Codex complied in over 90% of the firm's tests; Claude Code, via a CLAUDE.md setting ANTHROPIC_BASE_URL, about half. Advice: don't start agents in Downloads, review instruction files, and diff agent config.

CodexClaude CodeModel Context Protocol+1
Forever Securityfunction-colorAGENTS.md+4

AI Security, Supply ChainΒ· Added 27 Oct 2026, published 26 Oct 2026

x.comthreadπŸ›‘οΈ Security

TechNadu (@TechNadu) on X

TechNadu's post reports a hacker's claim of leaking 6 million records linked to CONAPE, the Dominican Republic's pension body. The alleged dataset includes national IDs, addresses, medical details and pension records. TechNadu notes that neither the records nor their link to CONAPE has been independently verified. The post gives no technical details on how the data was obtained.

CONAPEDominican Republic

Threat IntelΒ· Added 27 Oct 2026, published 26 Oct 2026

x.comthreadπŸ›‘οΈ Security

Ricardo Arguello (@RicardoIQSource) on X

Post by RicardoIQSource on breaches of developer platforms aimed at AI provider keys. It reports OpenCode (17 October, provider keys in its Console) and Zeabur (14-15 October, 3.2M environment variable records, admin tokens stored in plaintext since January 2024) as following the Railway incident. It claims three platforms were hit in eight days and links a blog with a timeline and remediation steps.

OpenCodeZeabur
RailwayZeabur breachplaintext admin tokens

Threat Intel, DevSecOpsΒ· Added 29 Oct 2026, published 26 Oct 2026

x.comthread🧠 AI

SemiAnalysis (@SemiAnalysis_) on X

SemiAnalysis claims AMD chips running vLLM can earn up to $3 per chip-hour in profit serving the open-source Kimi K3 model, even after higher chip rental prices following Claude Code's rise. Kimi K3 has over 2.8 trillion parameters and fits AMD's 288GB per chip, while B200 cannot hold it in one server. B200 must then use tensor or pipeline parallelism over 400Gbit/s InfiniBand or Ethernet, which SemiAnalysis says is 18x slower than NVLink. The post gives no methodology.

vLLMClaude CodeNVLink+1
SemiAnalysisAMDKimi K3+1

inferenceΒ· Added 26 Oct 2026, published 25 Oct 2026

ethereum-magicians.orgthreadπŸ›‘οΈ Security

Draft ERC: Agent Safety Framework (ASF) β€” attributable adoption of versioned safety specifications

Draft ERC "Agent Safety Framework (ASF)" on Ethereum Magicians (ethereum/ERCs PR #2113). It defines versioned, content-addressed Safety Specifications and on-chain Safety Bindings. A binding records which adopter accepted which pinned spec version for a subject and scope, with named interveners who can suspend, resume or terminate. A pure-registry check() returns Satisfied, NotSatisfied or Unknown, and Unknown never counts as satisfied. Reference consumers ASFGuardedAccount and ASFTaskTenderAdapter come with 73 tests, 47 of them negative.

Ethereum
Agent Safety FrameworkASFGuardedAccountASFTaskTenderAdapter+3

AI Security, Identity & AccessΒ· Published and added 25 Oct 2026

ethereum-magicians.orgthread🧠 AI

Draft ERC: Agent Safety Framework (ASF) β€” a registry of versioned safety specifications and of the scoped, attributable adoption relations that bind agents to them

Agent Safety Framework (ASF) is a draft ERC on Ethereum Magicians that defines two on-chain objects: a versioned, content-addressed Safety Specification and a Safety Binding, in which an adopter pins one spec version for a subject and scope. A registry check() returns Satisfied, NotSatisfied or Unknown. Bindings support derived delegation, and suspensions come in five graded restrictions. Reference consumers are ASFGuardedAccount and ASFTaskTenderAdapter, with 73 tests, 47 of them negative.

EthereumERC-165Anvil+2
Agent Safety FrameworkASFGuardedAccountASFTaskTenderAdapter

agents, ai-policyΒ· Published and added 25 Oct 2026

ethereum-magicians.orgthreadπŸ›‘οΈ Security

ERC-8468: Agent Safety Framework (ASF)

ERC-8468 (Agent Safety Framework, ASF) is a draft Ethereum standard, now at revision 6, for recording which participants accepted which safety requirements for an AI agent, in which version, enforced where, and whether that acceptance is in force now. It defines a versioned Safety Specification, an on-chain Safety Binding with interveners holding suspend, resume and terminate rights, and a check() that returns Satisfied, NotSatisfied or Unknown. The reference guarded account and task-tender adapter passed 90 tests (64 negative) and a Sepolia run of 36 transactions.

Ethereum
ERC-8468ERC-165TASK-KERNEL+4

AI Security, Identity & AccessΒ· Added 27 Oct 2026, published 25 Oct 2026

ethereum-magicians.orgthread🧠 AI

Draft ERC: Agent Safety Framework (ASF) β€” attributable adoption of versioned safety specifications

Agent Safety Framework (ASF) is a draft ERC (ethereum/ERCs pull request #2113) for an on-chain registry that records which participants adopted which versioned safety specification, for what subject and scope, and where it is enforced. It defines two objects (Safety Specification, Safety Binding) and a registry check returning Satisfied, NotSatisfied or Unknown. Two reference consumers and 73 tests (47 negative) are reported, and the post asks the community four design questions.

EthereumERC-165Anvil+2
ethereum/ERCsASFGuardedAccountASFTaskTenderAdapter+1

agents, ai-policyΒ· Published and added 25 Oct 2026

x.comthread🧠 AI

Prasenjit Sarkar (@stretchcloud) on X

Post explaining Claude's new support for MCP Tasks and Elicitations. A server returns a durable task handle instead of blocking. The client polls tasks/get every 250 ms to 30 s, and states are working, input_required, completed, failed or cancelled. Elicitations pause a task at input_required for human approval. It also notes Cloudflare's stateless MCP servers and Code Mode, and Sentry and Linear adoption.

Model Context ProtocolClaude CodeGitHub Actions+3
AnthropicClaudeAWS+4

mcp, agentsΒ· Added 25 Oct 2026, published 24 Oct 2026

x.comthread🧠 AI

HajrΓ« Hyseni | AI for Business (@hajra) on X

Kimi K3.1 Pro is a new model from Moonshot AI. According to a post by hajra, Artificial Analysis ranks it 4th in the world, 3 points behind Claude Opus 5.5. The API price is down by a third, and full open weights are promised by 4 November. The post gives no benchmark breakdown, licence or architecture details.

LLM
Moonshot AIKimi K3Artificial Analysis+1

models, evalsΒ· Published and added 24 Oct 2026

Showing 30 of 109

Show more