simonwillison.netwriteup🧠 AI
The October inflection point for vibe game development
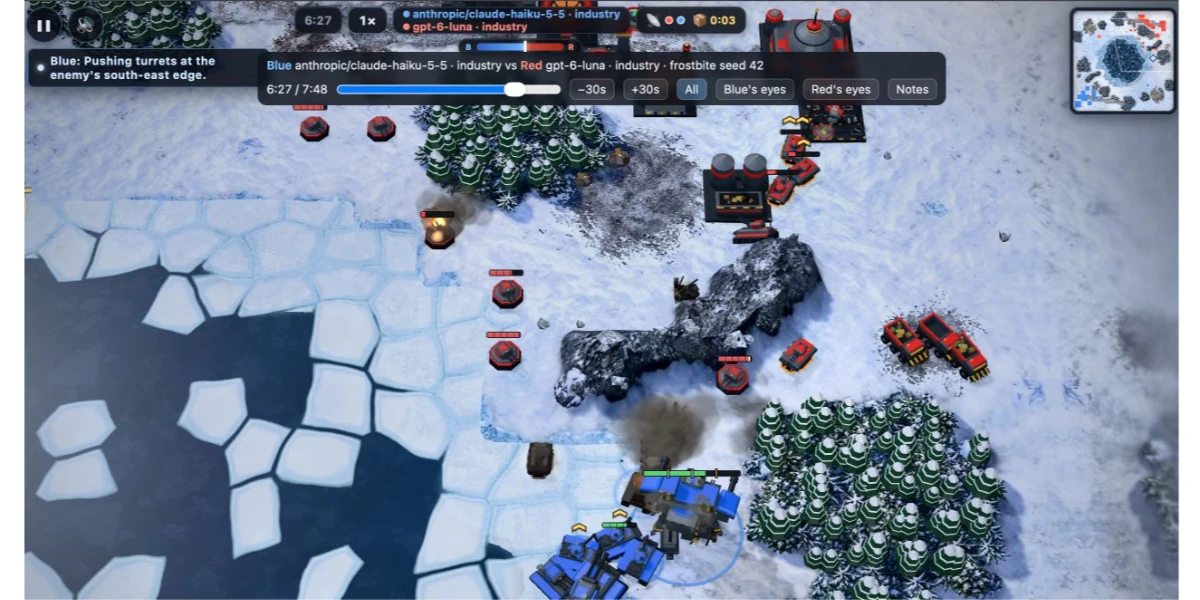
Simon Willison argues October 2026 is an inflection point for vibe coding games, because Claude Opus 5.5 can now handle 3D modeling, music and game design. He describes four browser games built with three.js (Tree Appreciator, Emberwick, Battle Drones, Quarter Sun Cove), with the prompts used, a comparison against GPT-6 models, and advice to start with "Build a mobile-friendly three.js game where...".
three.jsPhaserClaude+7
Simon WillisonClaude Opus 5.5Claude Fable 5+6
coding-agents, prompting, models· Published and added 28 Oct 2026