Skip to content

110 results for β€œPoS”

What you seeeverything
atlasum.netadvisoryπŸ›‘οΈ Security

TCP Use-After-Free: CVE-2026-98432 / CVSS 9.8

CVE-2026-98432 is a use-after-free in the Linux IPv4 TCP handshake, rated CVSS 3.1 9.8 and reachable by a remote unauthenticated peer on kernels back to 4.4. The post lists fixed stable releases (October 2026) and distribution patch status as of 31 October 2026, plus kernel and MPTCP listener checks. It gives interim nftables and iptables rules that drop IPv4 packets carrying options, and notes Anthropic's claim that Claude wrote a working exploit.

Linux kernelnftablesiptables+3
CVE-2026-98432use-after-freeAnthropic

Blue Team & Detection, Cloud & InfraΒ· Added 1 Nov 2026, published 31 Oct 2026

x.comadvisoryπŸ›‘οΈ Security

ClioBitcoinBank πŸ΄β€β˜ οΈ (@ClioBitcoinBank) on X

lnd v0.20.7 and v0.21.6 are Lightning Network Daemon releases announced by Clio Bitcoin Bank. They include a Go-specific mitigation, with the MPTCP flag turned off, for CVE-2026-98432, a use-after-free in the Linux kernel's IPv4 TCP code. The post recommends all users update. It gives no exploit or impact detail.

lndLinux kernelGo+2
CVE-2026-98432use-after-freeClio Bitcoin Bank

Cloud & InfraΒ· Published and added 31 Oct 2026

status.bunny.netadvisoryπŸ›‘οΈ Security

Bunny CDN Security Incident

Bunny CDN status-page notice, posted 28 October 2026, about unauthorized access at an infrastructure provider that hosted one bunny.net CDN node in Armenia. Traffic was stopped within 20 minutes and the server wiped. No access to the node was found, but cached content, Pull Zone configs and TLS certificates could have been exposed, so all platform certificates were reissued. Customers with their own certificates should rotate them with new private keys.

Bunny CDNTLS
bunny.netb-cdn.netbunny.run

Threat Intel, Cloud & InfraΒ· Added 31 Oct 2026, published 30 Oct 2026

cisa.govadvisoryπŸ›‘οΈ Security

CISA Adds Two Known Exploited Vulnerabilities to Catalog

CISA added two Ivanti Connect Secure vulnerabilities to its Known Exploited Vulnerabilities (KEV) Catalog on 30 October 2026, citing evidence of active exploitation: CVE-2026-111357 (missing authentication for a critical function) and CVE-2026-118527 (generation of predictable numbers or identifiers). The alert restates BOD 26-04, which requires federal civilian agencies to remediate KEV-listed flaws on exposed assets and check for prior compromise. It also links the KEV nomination form.

Ivanti Connect SecureCISA KEVVPN
CVE-2026-111357CVE-2026-118527BOD 26-04+1

Threat Intel, GRCΒ· Published and added 30 Oct 2026

unit42.paloaltonetworks.comadvisoryπŸ›‘οΈ Security

Threat Brief: Critical Vulnerabilities in PHP: CVE-2026-109618, CVE-2026-109619 (Updated October 29)

Unit 42 threat brief on PHP2Shell, two PHP remote code execution flaws, CVE-2026-109618 and CVE-2026-109619 (CVSS 4.0 9.2), both caused by longjmp() error handling that leaves memory uninitialized or freed. Cortex Xpanse counted over 22.6 million exposed instances. The 29 October 2026 update says attackers chained PHP2Shell with a Linux kernel privilege escalation against internet-exposed PAN-OS management interfaces. An earlier 23 October claim of post-compromise activity was retracted on 25 October.

PHPPAN-OSLinux kernel+2
CVE-2026-109618CVE-2026-109619PHP2Shell+2

Threat Intel, AppSecΒ· Added 30 Oct 2026, published 29 Oct 2026

x.comadvisoryπŸ›‘οΈ Security

lee1981 (@lee1981b) on X

CVE-2026-103780 is a stack-based buffer overflow (CWE-121) in Dell PowerProtect Data Domain / DD OS. An unauthenticated remote attacker could get command execution (CVSS 3.1 9.8, Dell DSA-2026-416). The post lists affected and fixed builds for four release trains (Feature Release, LTS2024, LTS2025, LTS2026). It adds KEV, EPSS and SSVC status, plus six defensive checks. The vulnerable service is not public.

Dell PowerProtect Data DomainDD OSCVSS+2
CVE-2026-103780CVE-2026-86400CVE-2026-86397+5

Blue Team & Detection, Cloud & InfraΒ· Added 31 Oct 2026, published 29 Oct 2026

cisa.govadvisoryπŸ›‘οΈ Security

CISA Adds Two Known Exploited Vulnerabilities to Catalog

CISA alert of 28 October 2026 adding two vulnerabilities to the Known Exploited Vulnerabilities Catalog on evidence of active exploitation: CVE-2026-41709 (Broadcom VMware ESX insufficient logging) and CVE-2026-46300 (Linux kernel missing variable initialization). It restates BOD 26-04, which requires federal civilian agencies to prioritize fast remediation of KEV CVEs on exposed assets and to check for prior compromise. It also links the KEV nomination form.

CISA KEVVMware ESXLinux kernel
CVE-2026-41709CVE-2026-46300BOD 26-04+1

Threat Intel, GRCΒ· Added 29 Oct 2026, published 28 Oct 2026

x.comadvisoryπŸ›‘οΈ Security

lee1981 (@lee1981b) on X

CVE-2026-92885 is a critical (CVSS 3.1 9.8, CWE-287) authentication bypass in the Qode Membership WordPress plugin, versions through 2.0.6.2. A misspelled variable in the Facebook token-verification guard skips provider checks, so an unauthenticated attacker with a public nonce can get a session cookie for an existing account, including an administrator. The post gives the fix (2.0.6.3, bundled in Bridge 30.9), KEV/EPSS/SSVC status, and a SOC log-correlation and remediation plan.

WordPressQode MembershipBridge+3
CVE-2026-92885CWE-287Wordfence+4

AppSec, Identity & Access, Blue Team & DetectionΒ· Added 31 Oct 2026, published 28 Oct 2026

cisa.govadvisoryπŸ›‘οΈ Security

CISA Adds Two Known Exploited Vulnerabilities to Catalog

CISA alert of 27 October 2026 adding two vulnerabilities to the Known Exploited Vulnerabilities (KEV) Catalog on evidence of active exploitation: CVE-2026-48356, an unrestricted upload of a dangerous file type in Adobe Commerce and Magento, and CVE-2026-111497, an unchecked return value in Google Brotli. It restates BOD 26-04, which makes federal civilian agencies prioritise KEV flaws on exposed assets and check for prior compromise. No technical detail or IOCs are given.

Adobe CommerceMagentoBrotli
CVE-2026-48356CVE-2026-111497CISA KEV+2

AppSec, GRCΒ· Added 29 Oct 2026, published 27 Oct 2026

x.comadvisoryπŸ›‘οΈ Security

lee1981 (@lee1981b) on X

CVE-2026-115905 is a ZIP cloaking flaw in the Rust zip crate (zip-rs/zip2), rated CVSS v4.0 10.0 and affecting versions below 9.0.5. ZipArchive reads central-directory metadata while ZipStreamReader reads local headers, so a crafted archive can pass filename inspection and then overwrite a different file during streaming extraction. Version 9.0.5 adds consistency checks, but ZipStreamReader::new leaves them off by default, and extraction is not atomic, so files can be written before an error is raised. The post covers CWE-20 and CWE-436, KEV and EPSS status, Debian status and a six-step investigation trail.

Rustzip crateCargo+3
CVE-2026-115905CWE-20CWE-436+3

AppSec, Blue Team & DetectionΒ· Added 29 Oct 2026, published 27 Oct 2026

cisa.govadvisoryπŸ›‘οΈ Security

CISA Adds Two Known Exploited Vulnerabilities to Catalog

CISA added two PHP vulnerabilities to its Known Exploited Vulnerabilities Catalog on 26 October 2026: CVE-2026-109618 (memory corruption) and CVE-2026-109619 (stale internal request state). It also updated its PHP alert on critical vulnerabilities requiring immediate patching. The alert restates BOD 26-04, which requires federal civilian agencies to prioritize fast remediation of KEV CVEs on exposed assets and to check for prior compromise.

PHPCISA KEV
CVE-2026-109618CVE-2026-109619BOD 26-04+1

AppSec, GRCΒ· Added 29 Oct 2026, published 26 Oct 2026

wiz.ioadvisoryπŸ›‘οΈ Security

Broccoli2shell: Everything You Need To Know About The Critical Brotli Decoder Vulnerability

CVE-2026-111497 (Broccoli2Shell, also Node2Shell and HTTP2Shell) is an out-of-bounds write in the upstream Brotli C decoder. It affects Node.js, Bun, Envoy Proxy, Istio and Python packages, and can lead to memory corruption, information disclosure, crashes or RCE when untrusted Brotli data is decompressed. Wiz reports 91% of cloud environments have vulnerable resources. The post lists patching, inventory, rebuild and temporary mitigation steps.

BrotliNode.jsBun+3
CVE-2026-111497Broccoli2ShellNode2Shell+8

AppSec, Cloud & InfraΒ· Published and added 25 Oct 2026

aikido.devadvisoryπŸ›‘οΈ Security

Python packages are also vulnerable to the Node2Shell Brotli flaw (CVE-2026-111497)

Python2Shell is the Python-side impact of CVE-2026-111497 (Node2Shell), a Brotli decoder flaw (CVSS 4.0 9.2) in DecodeBlockTypeAndLength() that mixes an unchecked return value with an out-of-bounds write. Brotli 1.2.0 and earlier, and brotlicffi 1.2.0.x, are affected through urllib3, requests, httpx, aiohttp and Scrapy. Fixes are Brotli 1.2.1 and brotlicffi 1.2.1.0; as of 23 October 2026 advisory databases do not map the CVE to either package. The post lists checks and workarounds.

BrotlibrotlicffiPyPI+3
CVE-2026-111497Node2ShellPython2Shell+4

AppSec, Supply ChainΒ· Published and added 23 Oct 2026

horizon3.aiadvisoryπŸ›‘οΈ Security

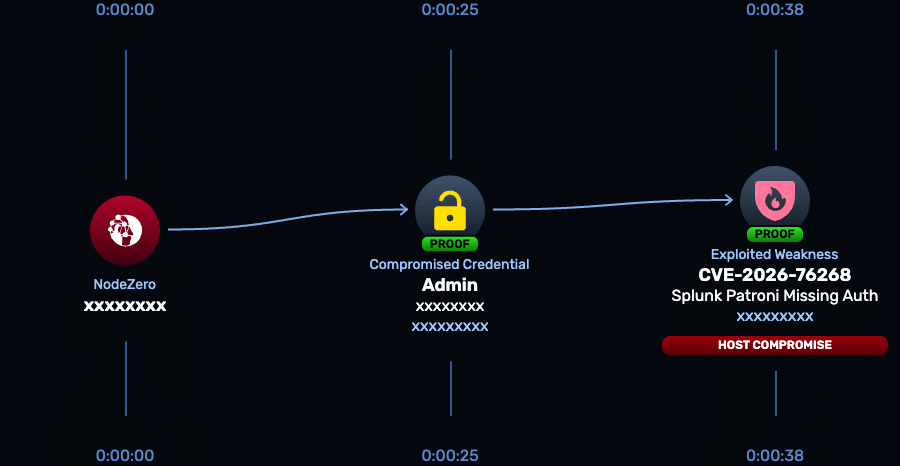
CVE-2026-109618 / CVE-2026-109619 | NodeZero Rapid Response Check Now Available

PHP2Shell is the name for CVE-2026-109618 and CVE-2026-109619, critical unauthenticated RCE flaws in PHP core fixed on 21 October 2026 in PHP 8.2.35, 8.3.36, 8.4.27 and 8.5.12. The page explains the out-of-memory corruption and stale global state causes, mod_php and PHP-FPM exposure, interim mitigations, hunting guidance, exploitation reports from October 2026, and the 23 October CVE-2026-115560 upload-progress advisory. Horizon3 also announced a non-exploiting NodeZero check.

PHPPHP-FPMApache+3
CVE-2026-109618CVE-2026-109619CVE-2026-115560+5

AppSec, Blue Team & DetectionΒ· Added 29 Oct 2026, published 23 Oct 2026

x.comadvisoryπŸ›‘οΈ Security

Xavier Rivera (@XavierRiveraX) on X

CVE-2026-115560 is a PHP code execution bug reported two days after the PHP2Shell emergency patches. The post says those releases do not fix it and no emergency fix is planned. Only apps that switch session.serialize_handler to php via ini_set() before session_start() are exposed. The mitigation is session.upload_progress.enabled=0, which also covers anyone who applied it for the 21 October advisory. The post gives no technical root-cause detail.

PHP
CVE-2026-115560PHP2Shell

AppSecΒ· Added 25 Oct 2026, published 23 Oct 2026

github.comadvisoryπŸ›‘οΈ Security

Brotli vulnerability affects curl and Git

GHSA-9v8h-qqgm-4m35 is a critical buffer overflow (CVSS v4 9.2) in the Google Brotli decoder (c/dec/decode.c), affecting versions 1.0.3 through 1.2.0 on all platforms. A crafted compressed stream lets an unauthenticated remote attacker corrupt adjacent decoder state, leak memory, crash the process, or possibly execute code. Fixed in 1.0.10, 1.1.1 and 1.2.1. The page does not mention curl or Git, despite the title.

BrotliCVSSNVD
GHSA-9v8h-qqgm-4m35buffer overflow

AppSecΒ· Added 25 Oct 2026, published 23 Oct 2026

x.comadvisoryπŸ›‘οΈ Security

lee1981 (@lee1981b) on X

CVE-2026-111497 is an out-of-bounds write in the Brotli decoder bundled with Node.js (CWE-787, CWE-252), rated CVSS v4.0 9.2 by the Google CNA and High by the Node.js project. Fixes are Node 22.23.4, 24.22.1 and 26.12.1, and 24.22.1 still labels Brotli 1.2.0 because the fix was cherry-picked. The post gives a SOC trail from input to worker, with remediation and verification steps. It notes no KEV match, CISA SSVC exploitation none, and only unverified public lab claims.

Node.jsBrotliCVSS+3
CVE-2026-111497CWE-787CWE-252+3

Blue Team & Detection, AppSecΒ· Added 26 Oct 2026, published 23 Oct 2026

horizon3.aiadvisoryπŸ›‘οΈ Security

CVE-2026-76268 | Splunk Enterprise Patroni REST API Missing Authentication Vulnerability

CVE-2026-76268 is a critical (CVSS 9.8) missing authentication flaw (CWE-306) in the Patroni REST API on Splunk Enterprise search head cluster members. An unauthenticated attacker with network access can run operating-system commands. Affected: 10.4.0 to 10.4.2 and 10.2.0 to 10.2.6. Fixed in 10.4.3 and 10.2.7. Splunk (SVD-2026-1001, 7 October 2026) suggests disabling the PostgreSQL sidecar as a workaround.

SplunkPatroniPostgreSQL+1
CVE-2026-76268CWE-306SVD-2026-1001+1

Offensive Security, Cloud & InfraΒ· Added 29 Oct 2026, published 22 Oct 2026

aikido.devadvisoryπŸ›‘οΈ Security

Node2Shell: Node.js Brotli vulnerability allows remote code execution (CVE-2026-111497)

Node2Shell (CVE-2026-111497) is an out-of-bounds write in the Brotli decoder bundled with Node.js and Bun, triggered by malformed compressed input and rated high by Node.js, with possible remote code execution. Fixed in Node.js 22.23.4, 24.22.1 and 26.12.1 and Bun 1.4.4. The post covers exposure via Express 5, body-parser 2.x, fetch() and node:zlib, stopgaps, and a timeline with public proofs of concept on 22 October 2026.

Node.jsBunExpress+3
CVE-2026-111497Node2ShellCWE-787+1

AppSecΒ· Published and added 22 Oct 2026

x.comadvisoryπŸ›‘οΈ Security

lee1981 (@lee1981b) on X

CyberForge CVE of the Day #084 analyses CVE-2026-76466, a CVSS 9.8 flaw in clustered Cisco Expressway-C and Expressway-E. Persistent database cookies and weak client-certificate validation allow root OS command execution over the network. The fix is X15.5.20 (X14 and earlier must migrate), with no workaround. It adds a per-peer SOC investigation trail, reachability checks and exposure status from CISA SSVC, KEV and EPSS.

Cisco ExpresswayCVSSNVD+2
CVE-2026-76466CWE-798cisco-sa-vcs-static-cred-hr7EWZ8t+2

Blue Team & Detection, Cloud & InfraΒ· Added 24 Oct 2026, published 22 Oct 2026

snyk.ioadvisoryπŸ›‘οΈ Security

PHP Patches Two Critical Unauthenticated RCEs (CVE-2026-109618, CVE-2026-109619): Update Now

Snyk's write-up of two critical unauthenticated PHP runtime RCEs, CVE-2026-109618 (out-of-memory corruption) and CVE-2026-109619 (stale global state, cross-request use-after-free), both CVSS v4.0 9.2. Fixed in PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35 on 21 October 2026. It covers the disclosure timeline, affected SAPIs (mod_php most exposed), backports for 8.1 and older, and partial mitigations.

PHPApacheFrankenPHP+3
CVE-2026-109618CVE-2026-109619SNYK-UNMANAGED-PHP-21347795+2

AppSecΒ· Published and added 22 Oct 2026

blog.talosintelligence.comadvisoryπŸ›‘οΈ Security

Compromised eMudhra intermediate certificates

Cisco Talos describes eight eMudhra intermediate CA certificates (six TLS, two code signing) whose P-384 private keys were trivially recoverable because a flaw in an April 30, 2025 key generation ceremony produced weak keys with only 3 to 8 bytes of entropy. The post lists certificate SHA-256 hashes and serials, browser and Microsoft blocks, and the Go fix (CVE-2026-111943, Go 1.27.3 and 1.26.10) that filters chains by SPKI hash. It covers impact on VPNs, CI/CD and embedded devices, and Snort SIDs 67363 to 67374.

GoChromeVPN+3
CVE-2026-111943eMudhraemSign Root TLS CA - G3+8

Threat Intel, Cloud & InfraΒ· Published and added 21 Oct 2026

x.comadvisoryπŸ›‘οΈ Security

EMITS (@emits_ca) on X

CVE-2026-107406 is a memory overflow in Citrix NetScaler that allows remote code execution when SAML is configured, rated 9.5 out of 10. The post from emits.ca calls it the fourth NetScaler bulletin in a week. It warns that the previous week's SAML patch does not cover it, and that fixes need NetScaler 14.1-73.46 or later, or 13.1-64.29 or later. The full advisory is on emits.ca.

Citrix NetScaler
CVE-2026-107406

Cloud & Infra, Identity & AccessΒ· Added 22 Oct 2026, published 21 Oct 2026

endorlabs.comadvisoryπŸ›‘οΈ Security

PHP2Shell: Critical vulnerabilities in PHP (CVE-2026-109618, CVE-2026-109619) | Endor Labs

PHP2Shell is the name for two critical PHP core memory-safety flaws, CVE-2026-109618 and CVE-2026-109619, that allow unauthenticated remote code execution. Fixes ship in PHP 8.2.35, 8.3.36, 8.4.27 and 8.5.12. Wiz researchers demonstrated RCE against WordPress, Drupal and Joomla, and Apache with mod_php is the highest risk. The post covers inventory, container rebuilds, Cloudflare WAF rules and temporary exposure reduction.

PHPWordPressDrupal+3
CVE-2026-109618CVE-2026-109619PHP2Shell+4

AppSec, DevSecOpsΒ· Published and added 21 Oct 2026

x.comadvisoryπŸ›‘οΈ Security

JFrog Security (@JFrogSecurity) on X

JFrog Security Research warns that the LiteLLM 1.107.0 release on PyPI contains malicious code, as part of a supply-chain attack. It advises avoiding that version and investigating any environment where it was installed or executed. The post gives no technical detail, payload description or IOCs, and says a blog post will follow.

LiteLLMPyPIPython+1

Supply ChainΒ· Added 23 Oct 2026, published 21 Oct 2026
huntress.comadvisoryπŸ›‘οΈ Security

Rapid Response: php2shell, Leaked Critical PHP Vulnerabilities (CVE-2026-109618 & CVE-2026-109619)

Huntress rapid-response post on php2shell, two leaked critical PHP core vulnerabilities (CVE-2026-109618 and CVE-2026-109619, CVSS v4.0 9.2 each) reported as remote code execution. The PHP team moved its security release to 21 October 2026, 14:00 UTC, after the leak. It lists hunting cues such as php-fpm, php-cgi or apache2 spawning shells, interpreters or download tools, plus inventory and patch steps. No root cause, affected versions, PoC or IOCs were public at writing.

PHPHuntressWordPress+2
CVE-2026-109618CVE-2026-109619php2shell+4

Blue Team & Detection, Threat Intel, AppSecΒ· Published and added 21 Oct 2026

aikido.devadvisoryπŸ›‘οΈ Security

Critical vulnerabilities in PHP (PHP2SHELL)

PHP2SHELL is Aikido Security's advance notice of two critical remote code execution flaws in PHP itself, CVE-2026-109618 and CVE-2026-109619, both CVSS v4.0 9.2, with all versions treated as affected. The PHP security team will release fixes at 14:00 UTC on 21 October 2026, a day early after details leaked on 20 October. The post withholds exploitation details and workarounds.

PHPCVSS
CVE-2026-109618CVE-2026-109619PHP2SHELL+1

AppSecΒ· Published and added 21 Oct 2026

unit42.paloaltonetworks.comadvisoryπŸ›‘οΈ Security

Threat Brief: Active Exploitation of PAN-OS CVE-2026-0257 (Updated Oct 20)

Unit 42 threat brief on active exploitation of CVE-2026-0257, a PAN-OS GlobalProtect authentication bypass added to CISA KEV on May 13, 2026. It lists IP addresses, host IDs and PoC-derived client values to hunt in GlobalProtect logs. The October 2026 updates cover Qilin and Inc ransomware operators, MFA bypass, pivots to vCenter and ESXi with offline VMDK credential dumping, and management interface exposure on ports 4443 and 3879.

PAN-OSGlobalProtectVPN+3
CVE-2026-0257CVE-2023-27532Spikey Scorpius+10

Threat Intel, Blue Team & Detection, Identity & AccessΒ· Added 21 Oct 2026, published 20 Oct 2026

x.comadvisoryπŸ›‘οΈ Security

lee1981 (@lee1981b) on X

CVE-2026-77932 affects DB-GPT through 0.8.2 (dbgpt-app). The /api/v1/chat/react-agent route accepts unauthenticated requests because get_user_from_headers returns an admin-role user, and the ReAct agent can reach unsandboxed Python and shell tools. Lasso reported root in the webserver container in a lab. The post gives CVSS 9.8 and 9.3, no verified fix (0.8.2 is still the latest release), no KEV match, no EPSS data, and a SOC hunting trail.

DB-GPTPythonDocker+3
CVE-2026-77932CWE-306Lasso+4

AI Security, AppSec, Blue Team & DetectionΒ· Added 23 Oct 2026, published 20 Oct 2026

x.comadvisoryπŸ›‘οΈ Security

lee1981 (@lee1981b) on X

CVE-2026-106931 is an OS command injection (CWE-78) in the statistics processing of EG Secure Solutions SiteGuard Server Edition, a host-based WAF. It can give root or SYSTEM command execution. The vendor and JVN confirm exploitation on 14 October 2026. The post lists fixed builds (Ver8.00 Update 5, Ver7.00 Update 6 on FreeBSD), the IIS exclusion, the workaround of disabling statistics, and a SOC trail starting with diagnostic preservation before patching.

SiteGuard Server EditionApache HTTP Servernginx+3
CVE-2026-106931CWE-78CISA KEV+5

Blue Team & Detection, AppSecΒ· Added 21 Oct 2026, published 19 Oct 2026

Showing 30 of 110

Show more