Skip to content

210 results for β€œTRON”

What you seeeverything
blog.trailofbits.comarticleπŸ›‘οΈ Security

The cryptography behind electronic voting (and why paper ballots are still essential)

Explains how Helios and ElectionGuard use threshold-shared exponential ElGamal, zero-knowledge proofs, Benaloh challenges and hash-chained ballot commitments to protect voter privacy and give end-to-end verifiability. It covers compromised voting clients and backends, software independence, and the 2018 National Academies report against internet voting. It concludes that cryptography supplements, but cannot replace, paper ballots in general elections.

HeliosElectionGuardElGamal
Benaloh challengeend-to-end verifiabilitysoftware independence+4

other, LearningΒ· Published and added 3 Nov 2026

securityweek.comarticleπŸ›‘οΈ Security

Google Dismantles XCPE Botnet of 1.3 Million Android Devices

XCPE (X.CPE) is a backdoor and botnet of more than 1.3 million Android set-top boxes, built and run by the Chinese OEM/ODM Videostrong Technology. Google dismantled it through legal action against domains and servers and banned Videostrong from preloaded Google apps. The malware used a three-stage design persisting on the /oem/ partition and was used for ad fraud, residential proxies and further malware loading.

AndroidAndroid TV
XCPEVideostrong TechnologyGoogle+8

Threat Intel, Mobile Security, Supply ChainΒ· Published and added 3 Nov 2026

bankless.comarticleπŸ›‘οΈ Security

Binance Reopens Withdrawals as FBI Pins $6B Hack on North Korea

Bankless news report on Binance reopening withdrawals in phases on 1 November 2026 after a record $6B+ hack. The FBI named North Korea's TraderTraitor group on 31 October, listed 628 addresses tied to the theft and asked THORChain node operators, instant exchanges and DeFi services to block them. Chainalysis says $500M moved out of TRON wallets and funds are shifting to Solana. Binance published a new proof of reserves covering 10 tokens.

THORChainTronSolana
TraderTraitorDPRKBinance+2

Blockchain, Threat IntelΒ· Published and added 2 Nov 2026

bleepingcomputer.comarticleπŸ›‘οΈ Security

Google disrupts million-device XCPE Android malware botnet, bans TV box maker

XCPE is an Android TV box botnet of more than 1.3 million devices, which Google's Threat Intelligence Group attributes with high confidence to manufacturer Videostrong Technology, who preinstalled a system-level backdoor in firmware. The backdoor (x.cpe, com.oemservice) used an MQTT broker for commands and loaded ad fraud and residential proxy modules. Google took down C2 servers tied to 10 million more devices and banned Videostrong from certified Android devices.

AndroidAndroid TVMQTT+2
XCPEVideostrong TechnologyGoogle Threat Intelligence Group+17

Threat Intel, Mobile Security, Hardware & RFΒ· Published and added 2 Nov 2026

cloud.google.comwriteupπŸ›‘οΈ Security

Shutting the Door on the XCPE Botnet

XCPE is an Android firmware backdoor (x.cpe, com.oemservice) preloaded by OEM Videostrong Technology on more than 1.3 million set-top boxes. Google Threat Intelligence Group details the three-stage architecture, the MQTT C2 (mqtt.szbboys[.]com), Play Protect disabling, persistence, and affiliate modules for residential proxies and ad fraud. It also lists the legal takedowns, the Videostrong ban and the partners involved.

AndroidAndroid TVMQTT+3
XCPEVideostrong TechnologyBadBox+18

Threat Intel, Malware & RE, Mobile SecurityΒ· Published and added 2 Nov 2026

en.cryptonomist.charticleπŸ›‘οΈ Security

Elliptic traces $2.2M of Binance hack funds through Bitcoin mixing

Elliptic's 2 November 2026 analysis reports the first laundering of proceeds from the 29 October 2026 Binance hack. By 1:02 a.m. ET it counted 18 WabiSabi coinjoin transactions, funded by bitcoin routed out of Tron and bitcoin bought with swapped ETH. The 18,270 BTC stolen directly had not moved. Elliptic names stablecoins and centralized cashout platforms as the remaining chokepoints. The page gives no addresses, transaction IDs or tracing method.

BitcoinEthereumTron+1
EllipticBinanceFBI+2

Blockchain, Threat IntelΒ· Published and added 2 Nov 2026

decrypt.coarticleπŸ›‘οΈ Security

FBI Blames North Korea for $6B Binance Hack as Exchange Reopens Withdrawals

The FBI attributed the theft of more than $6 billion from Binance on or about 29 October 2026 to North Korea's TraderTraitor and published hundreds of Ethereum addresses, 19 Bitcoin addresses and one Solana address to block. Chainalysis tracked over $500 million moving through Tron and out via THORChain, Chainflip, Relay and NEAR. Binance resumed withdrawals in phases from 1 November and says it replenished about 95% of affected assets.

EthereumBitcoinSolana+3
TraderTraitorDPRKFBI+11

Blockchain, Threat IntelΒ· Published and added 2 Nov 2026

x.comthread🧠 AI

CuteGuy☣️ (@cutetoxicguy) on X

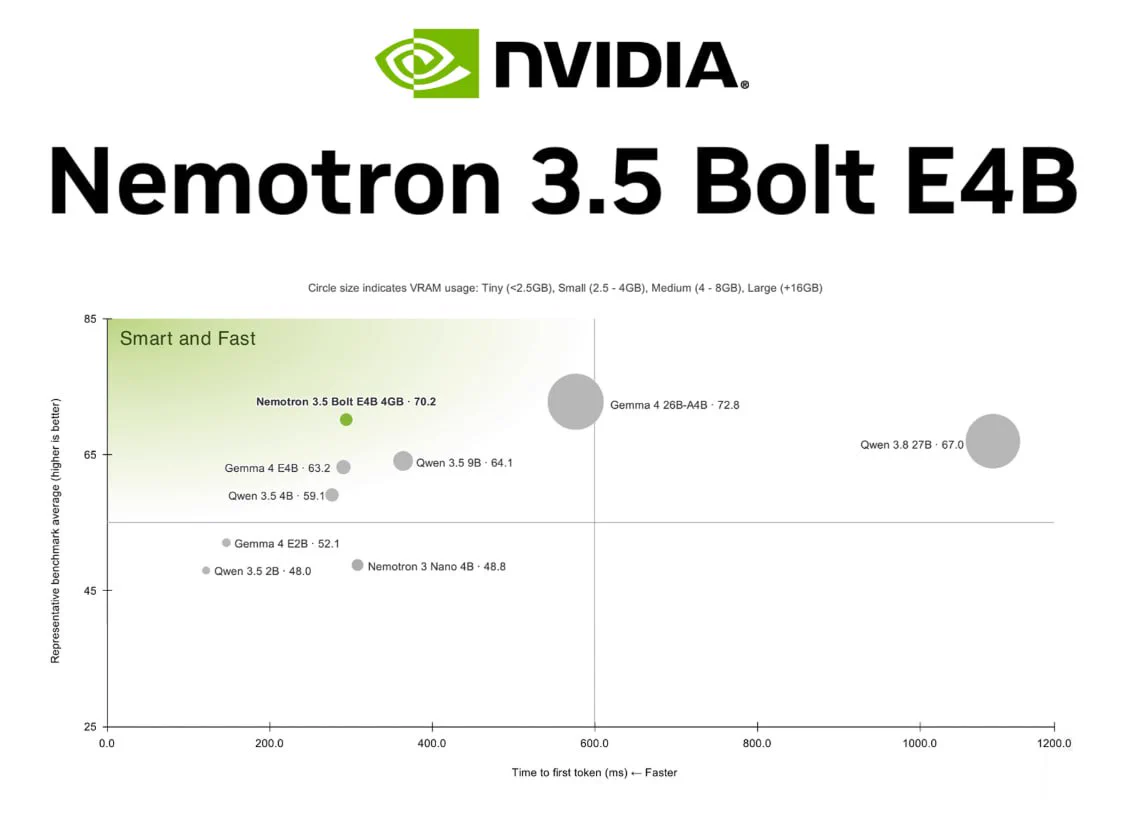
Nemotron 3.5 Bolt E4B is an NVIDIA open-weights model with 8B total and 4B active parameters, built on Gemma 4 E4B and post-trained with NeMo RL and NeMo Gym. It targets local agents in about 4GB of GPU memory, with 64K context, 35 languages, multi-step tool calling and configurable reasoning. NVIDIA's llama.cpp tests show 133.4 tokens/sec on an RTX 5070 and 15.5 on a Jetson Orin Nano. Benchmarks are NVIDIA's own.

llama.cppOllamaLM Studio+9
NVIDIANemotronGemma 4+8

models, inference, agentsΒ· Added 3 Nov 2026, published 2 Nov 2026

theblock.coarticleπŸ›‘οΈ Security

North Korean hackers launder $242 million of Binance loot via Tron as FBI presses THORChain: analyst

The Block reports that North Korean hackers (TraderTraitor) laundered about $242 million of funds stolen from Binance through Tron in two days, according to analyst SomaXBT. Relay, THORChain, Chainflip and Symbiosis moved about $140 million off Tron. Elliptic counts $2.85 billion frozen or seized, 44% of $6.43 billion stolen, and $3.25 billion in assets no issuer can freeze. The FBI urged THORChain and others to block listed addresses.

TronTHORChain
TraderTraitorDPRKBinance+6

Blockchain, Threat IntelΒ· Published and added 1 Nov 2026

theblock.coarticleπŸ›‘οΈ Security

Chainalysis says hacker using β€˜offensive agentic techniques’ accessed its customers’ names and emails

Chainalysis disclosed on 30 October 2026 that an attacker using "offensive agentic techniques" accessed customer names, emails, user IDs and role labels, but no investigation content, passwords or session tokens. The report also covers the Binance hack (about $6.3-6.4 billion, attributed to North Korea), where funds loop through addresses and JustLend lending on Tron is used to dodge stablecoin freezes. About $2.8 billion is frozen.

TronJustLend
ChainalysisBinanceDPRK

Threat Intel, Blockchain, AI SecurityΒ· Published and added 31 Oct 2026

securityweek.comarticleπŸ›‘οΈ Security

Syrian Hacker Gets Prison Time in US After Over a Decade on the Run

Ahmad Umar Agha (Th3Pr0), a Syrian Electronic Army member, received a 42-month US sentence in the Eastern District of Virginia, over 12 years after he was first charged in June 2014. He compromised about 47 Western media, company, NGO and government targets, including the 2013 Associated Press Twitter takeover that caused a flash crash. Accomplice Firas Dardar remains at large.

Twitter
Syrian Electronic ArmyAhmad Umar AghaTh3Pr0+5

Threat IntelΒ· Published and added 31 Oct 2026

latent.spacearticle🧠 AI

[AINews] Google admits AI Mode hurts Search revenue; -15% $500B drop worst since 2004 IPO. AI Bear Market coming?

AINews issue for 29 to 30 October 2026 from Latent Space. It opens on Google's admission that AI Mode monetises worse than classic Search, which preceded a roughly 15% share drop. It then recaps Claude Ultra dropping the 5-hour limit, Gemini 4 Carbon, Mistral Large 4, Nemotron 3.5, Artificial Analysis Index v5, Unsloth GGUF disputes, and the Anthropic S-1 filing.

Claude CodeClaudeGemini+17
GoogleAnthropicOpenAI+46

ai-policy, models, evalsΒ· Published and added 31 Oct 2026

arxiv.orgpaper🧠 AI

From Small to Large: Assessing Medical Reasoning, Benchmark Contamination, and Model Size in Language Models

This paper evaluates fourteen LLMs from six providers on 3,076 questions from MedQA-USMLE, MedMCQA, PubMedQA and MedBullets. It tests standard multiple choice, questions with answer choices withheld, and reconstruction of hidden questions from choices alone. Mean accuracy falls from 82.3% to 50.9% without choices, smaller models trail larger ones by 8.7 points, and the strongest models reconstruct about one question in four.

LLM
MedQA-USMLEMedMCQAPubMedQA+2

evals, researchΒ· Added 3 Nov 2026, published 30 Oct 2026

huggingface.cowriteup🧠 AI

nemotron-halloween

MonsterHouse is a Halloween interactive projection built on the NVIDIA Nemotron Voice Agent: Nemotron Speech ASR, Nemotron 3.5 Bolt E4B 4GB with a LoRA persona adapter, Magpie TTS Zeroshot and Audio2Face-3D in Unreal Engine, on two RTX Blackwell GPUs. Median end-of-speech-to-audio is 1.70 seconds live and 0.72 seconds with cached responses. The post gives a build path and tips on caching and state handling.

Nemotron Voice AgentNemotron Speech ASRNemotron 3.5 Bolt E4B 4GB+11
NVIDIANemotronQwen3 30B-A3B+3

multimodal, agents, trainingΒ· Published and added 30 Oct 2026

arxiv.orgpaperπŸ›‘οΈ Security

SecPO: Principled Adversarial Training for Prompt Injection Security

SecPO is a prompt injection defense that combines a new preference-optimization loss with adversarial training. It replaces the insecure DPO reference model with an approximated injection-invariant oracle, and trains on strong injections synthesized at best@240. Against Meta-SecAlign, AT cuts attack success rates 1.5-14.5x, and on Qwen3.6-27B AgentDojo ASR@800 falls to 8.8% from 78.8%, with no noticeable utility loss across nine benchmarks. Code, training data and model are released.

QwenHugging FaceLLM
prompt injectionAgentDojoMeta-SecAlign+3

AI SecurityΒ· Added 3 Nov 2026, published 30 Oct 2026

decrypt.coarticleπŸ›‘οΈ Security

Binance Sets Aside $6.34B to Cover Hack Losses, CEO Says 'Your Assets Are Safe'

Decrypt reports on the October 2026 Binance hot-wallet hack, about $6.3 billion, which Binance CEO Richard Teng says the company will cover with over $6.34 billion of its own funds. Teng says the attacker used an EIP-7702 delegation that skipped Binance's approval controls, a self-destruct mechanism to wipe tooling, and more than one breach point beyond a compromised laptop. TRM Labs and Chainalysis attribute the theft to TraderTraitor, and the attacker is still moving funds on Tron.

EthereumTronAave+1
TraderTraitorEIP-7702Binance+5

Blockchain, Threat IntelΒ· Published and added 30 Oct 2026

github.comrepo🧠 AI

Show HN: I Turned DOOM into a Transformer

Doomformer compiles integer neural networks into ZDoom maps that run in ViZDoom. Voodoo dolls do the arithmetic, and sector light levels and plane heights hold the values. Python reads every value back and compares it with a NumPy integer reference at tolerance 0. It runs MNIST (97.16 % on all 10,000 digits, every pass exact), small transformers, a learning perceptron and a SUBLEQ machine. It is about 23,000 times slower than NumPy on a small MLP.

ViZDoomZDoomACS+10
DoomformerDOOMFreedoom+6

research, inferenceΒ· Added 30 Oct 2026, published 29 Oct 2026

decrypt.coarticleπŸ›‘οΈ Security

Binance Drained of $5.5 Billion in Suspected Hack, Tether and Circle Freeze $1.8 Billion

Decrypt reports that at least $5.57 billion left Binance-linked hot wallets on Ethereum, Bitcoin and Tron on 29 October 2026, which would be the largest crypto hack on record. On-chain analysts point to an EIP-7702 delegation, installed from a Tornado Cash-funded address minutes before the first sweep. Tether and Circle froze about $1.8 billion. Binance has not confirmed the hack, and how the attacker obtained the signature is unknown.

EthereumBitcoinTron+2
BinanceEIP-7702Circle+4

Blockchain, Threat IntelΒ· Published and added 29 Oct 2026

rekt.newswriteupπŸ›‘οΈ Security

Rekt - Duelbits - Rekt

Duelbits is a crypto casino that lost an estimated $6.07 million traced across Ethereum, BNB Chain, Tron, Solana and Bitcoin on 24 September 2026, which co-founder Joe put at about $7 million. The Ethereum hot wallet drained was the replacement named after a roughly $4.6 million theft in February 2024. Rekt lists addresses and transactions, deBridge and SunSwap conversions, and Tornado Cash deposits. Duelbits has not published a root cause.

EthereumBitcoinSolana+3
Duelbitsprivate key compromiseScam Sniffer+8

Blockchain, Threat IntelΒ· Added 29 Oct 2026

eprint.iacr.orgpaperπŸ›‘οΈ Security

A Quantitative Evaluation of Constant-Time Analysis Tools

AutoBench-CT is a modular benchmark for constant-time analysis tools, with manually verified per-violation ground truth across 64 cryptographic tasks. It scores seven tools on operational performance, detection quality and usability. The authors explain why CT-grind (2010) is still the most used tool, list recurring limitations across tools, and propose a composite pipeline for stronger constant-time guarantees. Accepted at ACSAC 2026.

AutoBench-CTCT-grind
ACSAC

Hardware & RF, AppSecΒ· Added 31 Oct 2026, published 29 Oct 2026

x.comthread🧠 AI

Muhammad Waris (@WarisCodes) on X

Nemotron 3.5 Transcribe is a free open-weight speech-to-text model from NVIDIA covering 40 languages, including mixed-language speech. The post says it ties for first among open models with a 2.8% error rate. It says the model needs a large GPU such as an H100 or RTX 5090, so it will not run on a laptop. The post gives no benchmark name or model card link.

Nemotron 3.5 Transcribe
NVIDIANemotron

models, multimodalΒ· Added 30 Oct 2026, published 29 Oct 2026

decrypt.coarticleπŸ›‘οΈ Security

Treasury Sanctions 11 Over North Korean IT Worker Scheme That Moved Millions in Crypto

Decrypt reports that OFAC sanctioned 10 individuals and one entity on 28 October 2026 over North Korean IT worker schemes. Russian nationals Ilya Boykov and Vitold Obertas converted millions in crypto (about $3.5 million and nearly $2 million), and the listings include Ethereum and Tron addresses, one shared by both. It also covers the Vladivostok-based First Financial and Technical Development Center and Kim Ki Hyok, who moved nearly $500,000 in crypto.

EthereumTron
OFACDPRKIlya Boykov+7

Threat Intel, BlockchainΒ· Published and added 29 Oct 2026

x.comthread🧠 AI

🚨 AI News | TestingCatalog (@testingcatalog) on X

Nemotron 3.5 Transcribe is an open-weight, promptable NVIDIA mixture-of-experts model with 30B total and about 4B active parameters. One checkpoint does transcription in 40 languages, speaker attribution, translation, contextual prompting and audio understanding. The post says it ranked first in VoiceArena's comparison of 14 diarization plus ASR systems. The fetched text is cut off and gives no license or download details.

Mixture of Experts
NVIDIANemotronNemotron 3.5 Transcribe+1

models, multimodalΒ· Added 30 Oct 2026, published 29 Oct 2026

eprint.iacr.orgpaperπŸ›‘οΈ Security

High Precision Noise Cleaning for CKKS with Application to Asynchronous Threshold CKKS

High Precision Noise Cleaning for CKKS is an IACR ePrint preprint (2026/2675) by Zhihao Li, Cheng Hong and Tao Wei. It composes lower-degree Hermite polynomials to reach output noise bounds such as 2^-300 for noise flooding, and uses this to build an asynchronous threshold CKKS scheme with strong simulation security in the random oracle model. In OpenFHE, binary-message cleaning falls from 9.63 s to 1.54 s.

CKKSOpenFHE
noise floodingHermite interpolationfunctional bootstrapping+2

otherΒ· Added 31 Oct 2026, published 29 Oct 2026

x.comthreadπŸ›‘οΈ Security

Trail of Bits (@trailofbits) on X

Trail of Bits post says it achieved remote code execution through a Brotli decoder bug in Linux lab setups: Node.js 24.22.0 with Express 5.3.0 via the standard JSON parser (x86-64 and ARM64), and Electron 41.10.7 (x86-64) with a custom decoding service. Exploitation needs a carefully matched setup and repeated attempts. A scanner by ToBScottA finds hidden copies of the decoder, including in stripped binaries.

BrotliNode.jsExpress+1
Trail of BitsToBScottA

AppSec, Offensive Security, Supply ChainΒ· Added 30 Oct 2026, published 28 Oct 2026

x.comthread🧠 AI

Laban (@lunkertw) on X

An X post summarising five AI items: Google DeepMind's Gemini 4 Carbon (88.2% SEC-bench Pro, 54.8% ExploitGym, 71.0% CWE-bench, 59 on Artificial Analysis Intelligence Index v5.0), Ed Zitron's critique of Anthropic's S-1, a Utah Claude Code pilot, and the repos beenuar/AiSOC and expo/skills. In the Utah pilot, 34 developers in 10 agencies took part over four weeks, 80% had a working setup within 30 minutes, and 71% saved over 20 hours. It gives short summaries and links, not primary analysis.

Claude CodeModel Context ProtocolPython+6
Google DeepMindGemini 4 CarbonSEC-bench Pro+9

models, coding-agents, ai-policyΒ· Added 29 Oct 2026, published 28 Oct 2026

arxiv.orgpaper🧠 AI

AskStream: When and What to Ask Proactively under Uncertainty in Streaming Video Understanding

AskStream is a multi-turn benchmark for streaming video understanding that adds a third proactive action, ask, alongside wait and answer, for cases where video or user information is incomplete. It has 438 videos, 2,714 manually annotated frame-level time windows (wait, ask, answer), four task categories and eight subtasks. The strongest model reaches only 52.18% on the proposed Ask-F1 metric, in both multiple-choice and open-ended settings.

multimodal large language model
AskStreamAsk-F1arXiv

evals, multimodal, researchΒ· Added 30 Oct 2026, published 28 Oct 2026

x.comthread🧠 AI

John Rood (@johnroodepic) on X

Nemotron 3.5 Transcribe is an open-weight, promptable 30B mixture-of-experts model from NVIDIA with about 4B active parameters, built for recorded audio. One checkpoint transcribes 40 languages, handles recordings up to an hour, labels up to eight speakers, translates, and answers questions about English audio. Weights and a demo are on Hugging Face. The post gives no benchmarks.

Mixture of ExpertsHugging Face
NVIDIANemotronNemotron 3.5 Transcribe+1

models, multimodalΒ· Added 29 Oct 2026, published 28 Oct 2026

huggingface.coarticle🧠 AI

NVIDIA Nemotron 3.5 Transcribe and Granary v2: Intelligent Multilingual Transcription You Can Prompt and Adapt

Nemotron 3.5 Transcribe is an open-weight, promptable speech model that handles transcription in 40 languages, translation, diarization for up to eight speakers, and audio Q&A. It has about 4B active of 30B parameters and tops open-weight ASR and diarization leaderboards. The post also covers the Granary v2 curation pipeline (463,062 hours, 48 languages) and a medical fine-tuning case study that cut held-out WER by 45.8%.

NeMo SpeechNeMo CuratorvLLM+11
NVIDIANemotron 3.5 TranscribeGranary v2+16

models, multimodal, training, evalsΒ· Published and added 28 Oct 2026

arxiv.orgpaper🧠 AI

Repairs for Whom? Evaluator-Executor Mismatch in Selecting Repairs for Failed LLM Agents

Repairs for Whom? studies single-step repairs of failed LLM agent trajectories and asks whether common evaluators (greedy replay, stronger models, oracles, log-reading judges) pick repairs that help the deployed agent. Using independent rollouts in ALFWorld and WebShop, greedy replay loses 0.06-0.13 in expected gain, and Qwen2.5-14B rollouts misselect repairs for Qwen2.5-7B. The authors recommend verifying repairs with the executor that will run them.

LLMQwen
ALFWorldWebShopQwen2.5-7B+2

research, agents, evalsΒ· Added 30 Oct 2026, published 28 Oct 2026

Showing 30 of 210

Show more