- colibri: pure-C engine for running huge MoE models by streaming experts from disk
colibri is a pure-C, dependency-free inference engine that runs mixture-of-experts models of hundreds of billions of parameters on ordinary machines. It keeps the dense layers in RAM and streams routed experts from disk through a learning cache, with optional CUDA, Vulkan and Metal tiers. It supports GLM-5.2, Kimi K3, DeepSeek V4, Qwen3.6 and GGUF files, and serves OpenAI- and Anthropic-compatible APIs.
 github.comrepoAdded 3 Nov 2026🧠 AI
- llm-trails: What LLMs reach for inside a breached AWS account
llm-trails is an open study of what LLMs choose to do next inside a breached AWS account. It puts 14 models in 13 post-compromise situations, records only a single-turn plan with nothing executed, and codes each answer to CloudTrail events. The repo has the llmtrials harness, prompts, codebook, processed dataset (viz_data.json) and an interactive dashboard, so the study can be rerun or extended.
github.comrepoAdded 30 Oct 2026🧠 AI - rikugan: LLM reverse-engineering agent for IDA Pro and Binary Ninja
Rikugan is a reverse-engineering agent that runs inside IDA Pro and Binary Ninja. It has its own generator-based agent loop, context management, plan mode and 60+ tools, and does not depend on an external MCP server. An orchestrator spawns parallel subagents to analyze a binary. It supports Anthropic, Gemini, MiniMax, Kimi, OpenAI-compatible endpoints and Ollama, with per-model notes.
github.comrepoAdded 30 Oct 2026🧠 AI - rikugan: LLM reverse-engineering agent for IDA Pro and Binary Ninja
Rikugan is an open-source reverse-engineering agent that runs inside IDA Pro 9.0+ and Binary Ninja, with its own agent loop instead of an MCP server. It has 60+ tools (decompiler, xrefs, strings, types, IL/microcode), parallel subagent exploration, an experimental /modify natural-language patching command and an experimental Binary Ninja deobfuscation skill for control flow flattening and opaque predicates. It supports Claude, Gemini, MiniMax, Kimi, OpenAI-compatible endpoints and Ollama.
github.comrepoAdded 30 Oct 2026🛡️ Security - Show HN: Hob - Open-source, on device alternative to Claude Cowork and ChatGPT
Hob is an MIT-licensed desktop app from Frigade that runs open-weight models such as Gemma and gpt-oss locally on Mac, Windows and Linux. It picks the best open-weight model that fits the user's computer and sets it up. It is positioned as a free, private, offline alternative to Claude and ChatGPT for tasks like filling out PDFs and working through documents. The page gives no technical detail on its runtime.
github.comrepoAdded 27 Oct 2026, published 26 Oct 2026🧠 AI - alirezarezvani/claude-skills
claude-skills is an open-source MIT library of about 398 Claude Code skills, agents and plugins that also installs into Codex, Gemini CLI, Cursor and 9 other coding agents. The security-relevant parts are skill-security-auditor, a stdlib-only Python scanner that checks skills for command injection, data exfiltration, prompt injection and dependency supply-chain risks before install, plus a security-guidance PreToolUse hook, a security suite and compliance skills (ISO 27001, SOC 2, GDPR).
github.comrepoAdded 25 Oct 2026🛡️ Security  affaan-m/ECC | RepoDir
ECC (affaan-m/ECC) is an open-source performance optimization system for AI coding agents. It packages 261+ skills, 64+ agents and 84+ commands that tune Claude Code, Codex, Cursor and other agent harnesses for speed, memory and security. Practitioners can use it as a ready-made skills and harness configuration set. The RepoDir page gives only this short description, with no install steps or benchmarks.
 repodir.comrepoAdded 24 Oct 2026🧠 AI
- Sadra Majidi (@SadraMajidi04) on X
Impeccable is an open-source skill for AI coding agents that steers them away from generic UI output such as purple gradients and nested cards. It provides 24 commands (critique, audit, polish, typeset) and 61 detector rules that run without an LLM. It works with Claude Code, Cursor and Codex, and the repo is pbakaus/impeccable on GitHub. The source is a short tweet and gives no further detail.
 x.comrepoAdded 23 Oct 2026, published 22 Oct 2026🧠 AI
- OpenAI CLI
OpenAI CLI is OpenAI's official Go command-line client for the REST API. It lets users generate images, upload and download files, create and wait on batches, call the Responses API, and query admin usage endpoints from a terminal or shell script. It supports JSON, JSONL and YAML output, GJSON transforms, shell completion, and install via Homebrew, go install or release binaries.
github.comrepoAdded 23 Oct 2026, published 22 Oct 2026🧠 AI - Dan Kornas (@DanKornas) on X
aula-mcp is an open-source (MIT) TypeScript MCP server that connects an AI client to Denmark's Aula school platform. It exposes tools for profiles, calendar events, messages, notifications, posts and weekly plans. MitID credentials and OAuth tokens are stored in macOS Keychain or an AES-256-GCM encrypted file. The HTTP server binds to 127.0.0.1, and the presence write tool stays off until AULA_MCP_WRITE=1 is set.
x.comrepoAdded 23 Oct 2026, published 22 Oct 2026🧠 AI - Show HN: Omnara – Open-source alternative to Claude Managed Agents
Omnara is an open-source, self-hostable managed agent platform, an alternative to Claude Managed Agents and OpenAI's Agents API. It runs agents on any model (OpenAI, Anthropic, OpenRouter, Bedrock, LiteLLM, Ollama) and any machine, with Postgres-backed durable state, stateless workers, per-tool permissions, MCP, skills, memory, subagents, schedules and Slack, Discord and GitHub triggers. It ships a REST API, TypeScript SDK, CLI and Docker Compose setup.
github.comrepoAdded 23 Oct 2026, published 21 Oct 2026🧠 AI - vxcontrol/pentagi
PentAGI is an open-source, self-hosted multi-agent system that uses LLM agents to carry out penetration testing tasks autonomously. The MIT-licensed repo has a Go backend, a React frontend and GraphQL. It ships Docker Compose files for Langfuse tracing, Graphiti knowledge-graph memory and an observability stack. Topics list OpenAI and Anthropic as model backends.
github.comrepoAdded 20 Oct 2026🧠 AI - Show HN: VoidAccess – open-source dark web OSINT, from query to a graph
VoidAccess is a self-hosted, MIT-licensed dark web OSINT platform that runs a 13-step pipeline from a research query to a relationship graph. It collects from Tor indexes, paste sites, code forges, security feeds and .onion seeds, applies content-safety filters, and exports STIX 2.1, MISP, Sigma, YARA, Snort, Suricata, CSV and JSON. It runs as a CLI with SQLite or as a Docker Compose stack with PostgreSQL, FastAPI and Next.js.
github.comrepoAdded 21 Oct 2026, published 20 Oct 2026🛡️ Security - DeepInfer: High-performance inference framework for DeepSeek models
DeepInfer is DeepSeek's open-source inference framework for offline inference of DeepSeek-V4.1-Flash, released under Apache 2.0. It covers attention data parallelism, MoE expert parallelism with load balancing, draft-token decoding with confidence-scheduled verification, batch-invariant inference, deterministic sampling and structured outputs. It runs on NVIDIA SM100 GPUs and Huawei Ascend 950 NPUs. The KV cache system, prefill/decode disaggregation and load balancing are not included.
github.comrepoAdded 21 Oct 2026, published 20 Oct 2026🧠 AI  Abhinav Singwal (@yogsec) on X
GetSubDomains is an open-source tool by yogsec that enumerates subdomains by querying crt.sh certificate transparency logs. It is aimed at the reconnaissance step of penetration tests and bug bounty work. The source is a short tweet pointing to a GitHub repository, so usage details and options are not given.
x.comrepoAdded 21 Oct 2026, published 19 Oct 2026🛡️ Security- eliasbiondo/antirion
Antirion is an open-source AI gateway shipped as one Rust binary with a built-in admin console. It sits between apps and providers such as OpenAI, Anthropic, Bedrock, Vertex and vLLM, translating between OpenAI, Anthropic, Gemini and Bedrock dialects. It covers routing with fallbacks and circuit breakers, budgets, guardrails, caching, MCP and A2A gateways, SSO, and a benchmark against Bifrost 2.2.4 and LiteLLM 1.103.1.
github.comrepoAdded 21 Oct 2026, published 17 Oct 2026🧠 AI - DietrichGebert/ponytail
Ponytail is a single skill prompt (skills/ponytail/SKILL.md, with a compact AGENTS.md) that makes coding agents write only the code a task needs, reusing existing components while keeping validation, error handling, security and accessibility. The author benchmarked it in Claude Code with Opus 5.5 over 39 tasks, 5 runs each, including a real FastAPI + React repo. They report -53% code, -41% time, -26% cost and -45% tokens, and 98% of risky logic shipping with a test versus 68% without. It adds /ponytail-review and /ponytail-audit commands, a Claude Code cost/token band with a local board, and installs through Claude Code and Codex plugin marketplaces or as a rules file for Cursor, Copilot, Gemini, OpenCode and others.
github.comrepoAdded 17 Oct 2026🧠 AI - AikidoSec/safe-chain
Aikido Safe Chain is an open-source local proxy and shell-alias wrapper for npm, yarn, pnpm, bun, pip, uv, poetry, pipx and pdm. It checks every package download, including deep dependencies, against the Aikido Intel malware feed and blocks malicious packages before install. It also enforces a configurable 48-hour minimum package age by suppressing too-new versions in registry metadata. It supports custom registries and a self-hosted malware-list mirror, and has CI/CD install recipes for GitHub Actions, Azure Pipelines, CircleCI, Jenkins, Bitbucket and GitLab.
github.comrepoAdded 17 Oct 2026🛡️ Security  Meta Muse Spark Open (816B-A42B) open-weights model card
Model card for Meta Superintelligence Labs' Muse Spark Open, an open-weights, natively multimodal model with 816B total and 42B active parameters and a 1M-token context window. It targets coding and agentic work (tool use, long-horizon tasks, multimodal reasoning, synthetic data generation, LLM-as-judge). It ships in BF16 and NVFP4, needs about 700GB VRAM (NVFP4) or 2TB (BF16), runs on SGLang, vLLM, Transformers, TensorRT-LLM, Unsloth, llama.cpp and MLX, and supports a reasoning_effort setting. The Muse Model License requires "Built with Muse Spark Open" attribution and a separate agreement for Model-as-a-Service above $20M revenue. The card reports safety results against Kimi K3 on cyber, chem/bio and loss-of-control evals.
 huggingface.corepoAdded 17 Oct 2026🧠 AI
- Llama.cpp on a jailbroken PS5: run any GGUF model natively on the console
PS5LM is a homebrew app for jailbroken PS5s (firmware 7.00–13.60). It runs llama.cpp with the ggml-vulkan backend on the console's RDNA 2 GPU, using 11.4 GB of shared memory, and loads any GGUF model. It serves OpenAI /v1/chat/completions, Anthropic /v1/messages (usable from Claude Code, Codex and opencode) and a browser chat page on port 8081. It also supports image-projector vision models and TypeSafe-style decision models through a /v1/systemone endpoint. A planner picks the longest context and best cache that fit the free memory, and the app downloads models from Hugging Face.
github.comrepoAdded 17 Oct 2026, published 16 Oct 2026🧠 AI - OpenMOSS/MOSS-Image
MOSS-Image is an open-source text-to-image model family from OpenMOSS with a 5B backbone, released October 2026 as MOSS-Image-Base and MOSS-Image-SFT. It supports JSON layout control with bounding boxes, text rendering inside images, and prompts up to 4K tokens. The repo gives a Diffusers pipeline, a Gradio app, a ComfyUI plugin, LoRA training guidance, a prompt-enhancer skill and day-0 SGLang and vLLM-Omni support.
github.comrepoAdded 20 Oct 2026, published 16 Oct 2026🧠 AI - BijectiveLabs/trading-research-agents
Open-source Python CLI (`tra`) for autonomous trading desks in which LLM analysts (technical, macro, on-chain, sentiment) and validators only give opinions on figures the system computed. Fixed rules do the arithmetic: pricing the round-trip cost, applying risk limits, sizing, cost gates, and sending a single order with stop attached via ccxt (Bybit and OKX demo accounts tested). It supports multiple model providers with per-role models, effort settings and fallbacks. Every answer is parsed against a closed schema, every refusal is logged with the figure behind it, and models can tighten but never loosen controls. This makes it a concrete reference for keeping LLM agents away from arithmetic and money.
github.comrepoAdded 18 Oct 2026, published 13 Oct 2026🧠 AI - santosomar/AI-agents-for-cybersecurity
Companion repository for Omar Santos's Pearson and O'Reilly trainings and books. It has eight parts of runnable Python labs: chat models, embeddings, prompt templates, LCEL prompt chaining, Chroma-based RAG, ReAct/LangGraph/CrewAI/DeepAgents agents, and FastMCP servers (nmap, CISA KEV, Shodan). It also includes guides to six agentic frameworks (OpenClaw, Hermes, Agent Zero, OpenHands, Paperclip, Buzz), a tokenomics module on agent cost (context compounding, prompt caching, model routing, token budget guards, batch API, cost per accepted outcome), and a vendor-neutral design spec for a human-gated multi-agent assessment harness. It is a current, practical curriculum for building and operating agents. Some examples act on real systems and should only be run in an authorized lab.
github.comrepoAdded 13 Oct 2026🧠 AI - santosomar/AI-agents-for-cybersecurity
Omar Santos's companion repo for his Pearson/O'Reilly trainings and books, organised in eight parts. They cover LangChain prompts, chains and RAG (Chroma), and agents (LangGraph, CrewAI, DeepAgents). They also cover FastMCP security servers (nmap, CISA KEV, Shodan) and attack-surface-management and SOC agent examples. Later parts have security guides to six agentic frameworks (OpenClaw, Hermes, Agent Zero, OpenHands, Paperclip, Buzz) with hardening notes and 2026 CVE mapping, agent cost/tokenomics scripts including denial-of-wallet budget guards, and a vendor-neutral spec for a human-gated multi-agent security-assessment harness (scope manifest, approval gates, kill switch). Useful as a hands-on path into AI-agent security tooling, with warnings that some examples act on real systems.
github.comrepoAdded 13 Oct 2026🛡️ Security - Show HN: SolidCraft – Open-Source Parametric CAD in Rust (With MCP Support)
SolidCraft is an open-source parametric 3D CAD application written in pure Rust. It has constrained sketches with its own solver, a feature timeline, assemblies, sheet metal, and STEP/IGES/3MF/STL export. It runs on desktop (egui+wgpu), in the browser, and as a headless CLI. The built-in MCP server (`solidcraft-cli mcp`) gives agents tools such as execute, batch, inspect_design, measure, set_parameter, screenshot and export. They can model headless or drive the running app over a JSON-lines control channel. A rover with 3,323 timeline steps was built entirely through MCP, which shows agent-driven parametric modelling working at scale.
github.comrepoPublished and added 13 Oct 2026🧠 AI  google/embeddinggemma-2
Model card for EmbeddingGemma 2, an open (Apache 2.0) 740M-parameter multimodal embedding model from Google DeepMind built on Gemma 4. It maps text, code, images, video and audio into one 768-d space, with a 270M text backbone and optionally loadable 170M vision and 300M audio encoders, an 8K context, and Matryoshka truncation to 128/256/512/768 dims. The card gives practical guidance: task instruction prefixes, re-normalising after truncation, avoiding float16 (NaN or degraded embeddings), interleaved multimodal inputs with placeholder tokens, and vision token budgets. It targets on-device search, RAG, classification and clustering.
huggingface.corepoAdded 12 Oct 2026🧠 AI- Show HN: Atticus – Hold-to-talk voice assistant for macOS that runs on Claude -p
Atticus is an MIT-licensed macOS 26+ hold-to-talk voice assistant that uses Apple's on-device speech transcription and runs AI requests through Claude Code on an existing Claude Pro/Max plan, so no API key is needed. Simple commands skip the model entirely (apps open in 0.08 s), actions it has seen once are learned as zero-cost shortcuts, and a "remember…" memory persists across asks. It also sets up no-AI background watchers (polling every 5 s) and holds itself to a budget of a median under $0.002 and 6 s per AI ask, with a system prompt under 10,000 characters.
github.comrepoPublished and added 12 Oct 2026🧠 AI - sepehr071/iran-mcp
iran-mcp is an open-source catalog of 39 MCP servers (488 tools) that let AI agents query Iranian websites such as Digikala, Torob, Divar, Snappfood, Jabama, Paziresh24, TSETMC and qavanin.ir, with prices normalised to Toman. Most servers are unofficial, read-only Python packages run with uvx; three are official hosted servers. It ships Claude Code plugins, Agent Skills, bundles, proxy lists and a machine-readable servers.json.
github.comrepoAdded 24 Oct 2026, published 11 Oct 2026🧠 AI - Dan Kornas (@DanKornas) on X
Arcjet JS SDK is an open-source (Apache-2.0) JavaScript monorepo that adds runtime security to AI apps, agents and HTTP endpoints. It ships request SDKs for Next.js, Node.js, Bun, Deno, Fastify and NestJS. It also has a Guard API for places with no HTTP request object, such as agent tool calls, MCP handlers, queue workers and background jobs. Built-in checks cover prompt-injection detection, sensitive-information detection (PII, credit cards, custom patterns) and token-bucket, fixed-window or sliding-window rate limits, including token budgets.
x.comrepoPublished and added 11 Oct 2026🧠 AI - sakidekin/CVE-2026-41940-PoC
This repository hosts a proof-of-concept for CVE-2026-41940, described as a CVSS 10.0 unauthenticated authentication bypass in cPanel and WHM caused by CRLF injection into server-side session files via the Authorization header. The accompanying Python tool (cve.py) can detect vulnerable cPanel/WHM instances, retrieve system and account information, and perform post-exploitation actions such as running OS commands, changing the root password, and opening an interactive WHM shell. It also supports bulk scanning workflows piped from subfinder, httpx, and Shodan.
github.comrepoAdded 23 Oct 2026, published 11 Oct 2026🛡️ Security - bilawalsidhu/gods-eye-view
God's Eye View is an open-source, vanilla JavaScript + CesiumJS + Vite 3D globe that fuses live public feeds (aircraft, ships, satellites, quakes, public cameras, weather) into one explorable scene. Its AI layer is a hands-free voice agent on the OpenAI Realtime API with 30 tools: camera fly-to, whiteboard annotations, analyst queries over live layers, and scene-context and screenshot grounding. Keys stay server-side and the browser gets only a short-lived session token. An experimental ChatGPT/Codex OAuth path is also supported. The app doubles as an MCP server, so Claude Desktop, Codex or ChatGPT can open the globe from a conversation.
github.comrepoAdded 11 Oct 2026🧠 AI - bilawalsidhu/gods-eye-view
God's Eye View is an open-source, vanilla-JavaScript CesiumJS and Vite client that puts live aircraft, ships, satellites (SGP4), earthquakes, fires, public CCTV and mapped ALPR cameras on one photorealistic 3D globe. It adds cockpit tracking, FLIR/NVG sensor shaders and a voice agent built on the OpenAI Realtime API. It works without API keys, and the docs cover server-side key brokering with SSRF protection, localhost binding and a SECURITY.md threat model. For OSINT/GEOINT practitioners it is a hackable base for fusing public signals, with an explicit rule against person-tracking features.
github.comrepoAdded 11 Oct 2026🛡️ Security - Talorys – A self-hosted personal AI agent on Cloudflare's free tier
Talorys is an open-source, single-user personal AI assistant deployed with one command (npx create-talorys) into the user's own Cloudflare account. It uses a Cloudflare Agents SDK Durable Object with SQLite for conversations, memories, tasks, notes and automations, Workers AI (@cf/zai-org/glm-4.7-flash) for streaming chat with tool calling, and Durable Object alarms for reminders and scheduled AI routines. It stays within the Workers Free plan, with a private Worker behind a Pages Function service binding, owner-password auth, per-day AI usage guardrails, and fallback to non-AI features when quota runs out.
github.comrepoPublished and added 10 Oct 2026🧠 AI - mattpocock/skills — agent skills for engineers
mattpocock/skills is a collection of small, composable "agent skills" for software engineering that install into Claude Code, Codex, GitHub Copilot, Gemini CLI, Cursor, OpenCode, Devin, Windsurf, Amp and Pi via plugin managers or the `npx skills` CLI. It packages practices like interview-driven requirement gathering (/grill-me, /grill-with-docs), domain-model/glossary building, test-driven development with red-green-refactor (/tdd), bug diagnosis loops, codebase architecture improvement, ticket triage and spec-to-implementation workflows (/to-spec, /to-tickets, /implement, /implement-spec), splitting skills into user-invoked orchestrators and model-invoked reusable disciplines. It's built by Matt Pocock as an alternative to heavier process-owning frameworks like GSD, BMAD and Spec-Kit, aiming to keep engineers in control while giving coding agents better feedback loops and shared vocabulary.
github.comrepoAdded 8 Oct 2026🧠 AI - Dark Web Informer (@DarkWebInformer) on X
Infoooze is an open-source command-line OSINT reconnaissance toolkit (github.com/devxprite/infoooze) that consolidates common footprinting tasks into one CLI: username enumeration across platforms, email discovery, subdomain enumeration, port scanning, WHOIS/DNS lookups, IP/HTTP header analysis, EXIF metadata extraction, GitHub recon, and URL scanning/expansion. It automatically saves results, making it a lightweight all-in-one alternative to running several separate recon tools.
x.comrepoPublished and added 8 Oct 2026🛡️ Security - chainguard-dev/malcontent
malcontent is Chainguard's open-source malware/supply-chain discovery tool that analyzes binaries (ELF, Mach-O, PE, a.out) and scripting-language source across Linux, macOS and Windows using 14,500+ YARA rules (including third-party rules from Avast, Elastic, FireEye, Mandiant, Nextron and ReversingLabs). Its standout feature is differential analysis ("mal diff"), which compares two versions of a build artifact or OCI image against a known-good baseline to surface newly introduced risky behaviors — the technique the project demonstrates on the 3CX supply-chain compromise by flagging unexpected high-risk changes to libffmpeg. It also supports threshold-based scanning ("mal scan") and unfiltered capability enumeration ("mal analyze"), and is designed to run inside CI/CD pipelines, including air-gapped environments via embedded rules.
github.comrepoAdded 8 Oct 2026🛡️ Security - target/strelka
Strelka is Target's open-source, container-based real-time file scanning system for threat hunting, threat detection, and incident response, built in Go and Python. It runs 50+ scanners (YARA, PE parsing, encrypted ZIP cracking, entropy analysis, etc.) to extract metadata and content from files at enterprise scale, which can feed a SIEM for alerting on suspicious artifacts like an Emotet-laden encrypted ZIP payload.
github.comrepoAdded 8 Oct 2026🛡️ Security - deepfence/YaraHunter
YaraHunter is Deepfence's open-source scanner that applies YARA rulesets against container images, running Docker containers, and filesystems to detect indicators of compromise such as malware and cryptominers. It supports CI/CD build-time scanning, at-rest image scanning, and runtime container scanning, with JSON output for automation, and is designed to eventually integrate into the Deepfence ThreatMapper platform. The README walks through detecting the XMRig cryptominer inside a container image as a worked example.
github.comrepoAdded 8 Oct 2026🛡️ Security - Tracer-Cloud/opensre
OpenSRE is an open-source framework for building AI SRE agents that resolve production incidents by correlating logs, metrics, traces, deploys and runbooks across 60+ connected tools (observability, cloud infra, incident management, MCP). Beyond the agent runtime (CLI, Python API, Slack/PagerDuty/Telegram integrations), the project's stated mission is to build an RL training and evaluation environment — explicitly modeled on SWE-bench's role for coding agents — to scale realistic infrastructure-failure scenarios as a benchmark for AI SRE.
github.comrepoAdded 8 Oct 2026🧠 AI - Port of the TypeScript compiler, checker and lsp to Rust, by LLM
ts-rust (npm package tsc-rs) is a from-scratch Rust port of Microsoft's TypeScript compiler/checker/language server (typescript-go), produced almost entirely by LLM coding agents rather than hand-written. The author first spent over $400,000 in API tokens running GPT-5.6 Sol and GPT-6 Astra in long agentic '/goal' loops, which wrote 1.3M lines of Rust but plateaued at ~84% compatibility; switching to Claude Opus 5.5 produced a working version in 10 hours and, after ~$24,000 of further API spend over two weeks, reached 100% compatibility on tested real-world projects while passing all 181,711 ported Go baseline tests. Benchmarks show the Rust port running about 1.6x faster than the Go tsc 7 compiler (though slower than Bun's native `bun check`) across dozens of open-source codebases including VS Code, TanStack Query, Sentry and T3 Code.
github.comrepoPublished and added 8 Oct 2026🧠 AI - Show HN: NanoMuse – An open-source AI agent for your phone and computer
nanoMuse is an open-source personal AI agent that runs across phone, desktop, and web, built on an on-device sandbox (OpenMinis with proot/Alpine Linux on mobile) and the DeepSeek Harness on desktop with a Python runtime for tool use. Devices share one account and sync conversations through a relay (self-hostable), while the agent proactively acts, retains memory, and pauses before irreversible actions; it is released GPL-3.0-or-later with documentation on install, self-hosting, connectors, and memory.
github.comrepoPublished and added 7 Oct 2026🧠 AI - Microsoft Agent Framework python-1.20.0 release
Release notes for python-1.20.0 of Microsoft's Agent Framework, an open-source agent/workflow orchestration library. This release adds native vector-store connectors for DuckDB, SQL Server and MongoDB plus a TypeSafe AI connector, redesigns Foundry hosting around request-scoped agent factories and sandbox-isolated sessions, adds computer-use support to Responses clients, and ships Magentic manager and handoff-routing improvements for multi-agent orchestrations alongside a large batch of MCP, Bedrock, Gemini, Anthropic and Ollama provider fixes.
github.comrepoAdded 6 Oct 2026🧠 AI - Show HN: OpenChart – OSS TradingView alternative with your own AI agent
OpenChart is an open-source TradingView-style desktop charting app (Electron, Node.js/Bun, Effect runtime) that embeds AI agents into statistical/technical analysis, real-time market alerts and agentic opportunity research. It ships a custom DSL called Tea (inspired by TradingView's Pine Script) for writing indicators, and a conversation interface built on assistant-ui and the AG-UI event protocol so users converse with agents while charting.
github.comrepoPublished and added 6 Oct 2026🧠 AI - browser-use/jev-ultrafast
jev-ultrafast is an open-source browser automation agent (from Browser Use) that represents each page as an indexed element table and uses a 'TypeSafe' policy to speculatively predict both the next operation (CLICK, TYPE_TEXT, SELECT, SCROLL, WAIT, DONE, BLOCKED) and its target in a single network round trip, only invoking a small LLM (e.g. inception/mercury-2.5 via OpenRouter) to generate text when the operation is TYPE_TEXT. The repo includes a local inspector UI, Chrome automation via a 'Browser Harness' tool, offline tests, and published before/after benchmarks showing a Google Flights search dropping from a median 9.45s to 7.09s and browser protocol calls from 1,092 to 101 across repeated runs.
github.comrepoAdded 6 Oct 2026🧠 AI - overmind-core/overmind
Overmind is an open-source platform (MIT SDK/CLI, AGPL-3.0 platform, self-hostable) that instruments an agent's code via OpenTelemetry tracing, turns the resulting production traces (or any dataset) into a fine-tuned model benchmarked against user-defined eval metrics, and serves it through one unified API with downloadable/retrainable weights. It ships an SDK, CLI, REST API, Console, and an MCP server exposing project tools and workflows (investigate-capability, finetune-capability, ship-model) for Cursor, Claude Code, OpenCode and Codex, and can sync traces from Langfuse, LangSmith, Braintrust or Galileo; self-hosting runs via Docker Compose with Postgres, Redis, Celery workers and Modal-based GPU workers for fine-tuning/serving (vLLM).
github.comrepoAdded 6 Oct 2026🧠 AI - claude-mem — persistent memory system for Claude Code and other coding agents
Claude-Mem is an open-source persistent memory plugin for Claude Code and other coding agents (Codex, OpenCode, Grok Bot, T3 Code, OpenClaw) that captures tool-usage observations during sessions, compresses them into semantic summaries, and reinjects relevant context into future sessions. It uses five lifecycle hooks (SessionStart, UserPromptSubmit, PostToolUse, Stop, SessionEnd), a local SQLite database, a Chroma vector store for hybrid semantic+keyword search, and exposes three MCP tools (search, timeline, get_observations) that follow a token-efficient layered retrieval pattern to cut context costs roughly 10x. It is Apache-2.0 licensed, built with the Claude Agent SDK and TypeScript, and ships an optional hosted "observer" memory service alongside self-hosted options via OpenRouter/Gemini keys or an Anthropic plan.
github.comrepoAdded 5 Oct 2026🧠 AI - Zhenyu98/codex-chatgpt-bridge
codex-chatgpt-bridge is a Codex agent skill plus external PowerShell control scripts (On/Off/Reboot/Rotate) built on top of the open-source DevSpace MCP bridge, which lets ChatGPT act as a planning/review "architect" while Codex stays the local executor that applies and verifies changes. It adds a token-saving router (NORMAL / TOKEN_SAVING / CHATGPT_ARCHITECT modes) and a lifecycle layer — Cloudflare Quick Tunnels or a stable Cloudflare Worker proxy, DPAPI-protected credentials, OAuth token rotation, and a scheduled-task recovery entrypoint — so the bridge's public endpoint can be closed when idle without re-authorizing the ChatGPT app on every restart.
github.comrepoAdded 5 Oct 2026🧠 AI - the_OSINT_rack (@the_OSINT_rack) on X
Vinted_OSINT is a GitHub tool by EchterAlsFake that performs open-source intelligence gathering against Vinted.com user profiles, pulling seller/buyer account information and computing a risk score to flag accounts likely run by scammers. It's aimed at buyers wanting to vet sellers before transacting on the second-hand marketplace.
x.comrepoPublished and added 4 Oct 2026🛡️ Security - DeepZero
DeepZero is an open-source orchestration engine that lets researchers define vulnerability-research pipelines declaratively in YAML, handling parallel execution (ThreadPoolExecutor), resumable/fault-tolerant state, and LLM-assessment stages via LiteLLM/Jinja2 prompts. It ships example processors for Ghidra headless decompilation, LOLDrivers.io hash exclusion filtering, PE header/driver metadata extraction, and batch Semgrep scanning, with a dedicated pipeline for BYOVD kernel driver vulnerability research. An extensibility model lets users plug in custom Python processors referenced by path in the YAML config.
github.comrepoAdded 3 Oct 2026🛡️ Security - Sigma r2026-07-01 — 20 new detection rules
GitHub release notes for Sigma r2026-07-01, the open-source detection-rule repository, adding 20 new rules (e.g. LSASS crash via Netlogon buffer overflow CVE-2026-41089, TanStack supply-chain attack indicators for Windows/Linux, RedTail cryptominer user-agent detection, AF_ALG kernel crypto API exploit indicator) and updating/fixing dozens of existing rules for ARM64 binary variants, file-sharing domain IOCs, and WMI-based reconnaissance/persistence detection. It's a routine but substantive update to a widely-used blue-team detection content pack.
github.comrepoAdded 3 Oct 2026🛡️ Security - jiwoochris/artex-global
ARTEX global edition is an English-default fork of the Chinese open-source ARTEX (AGPL-3.0), an autonomous penetration-testing system in which planner and worker LLM agents run real tools and record results in an asset graph and an exploration graph on PostgreSQL. It also ships a defense guide, Sigma and Suricata rules, an ATT&CK Navigator layer, MISP indicators and a host triage script for spotting ARTEX-driven attacks.
github.comrepoAdded 31 Oct 2026, published 3 Oct 2026🛡️ Security - OKX Agent Trade Kit (okx-trade-mcp / okx-trade-cli)
OKX Agent Trade Kit is an open-source MCP server (okx-trade-mcp) and CLI (okx-trade-cli) that let AI assistants like Claude Desktop, Cursor, Claude Code and VS Code place trades and query account data on the OKX exchange via natural-language commands. It runs locally with API keys never leaving the machine, supports module scoping (market, spot, swap, account, earn), a read-only mode for safe querying, multiple profiles, and includes pre-built skill files for agent frameworks plus structured JSON error reporting for debugging failed tool calls.
github.comrepoAdded 2 Oct 2026🧠 AI - Show HN: Made an open-source Lego AI generator
ldraw-nova is an open-source agentic pipeline where an LLM agent (tested with models like Claude Opus 5.5 and GPT-6 Astra) takes a build prompt, reads LDraw-building instructions, and produces a plan.json describing a model's geometry. From that plan it writes a Python generator script that, when executed, outputs an LDraw (.mpd) 3D CAD source file, viewable in 3D/VR (Meta Quest 3) or exportable to Blender-editable glTF. The agent uses jev-rerank, a semantic search tool with reranking backed by TypeSafe's Jev System One model, to find suitable LEGO parts and example models, falling back to full-text search without an API key; it also uses headless rendering and collision/gap detection to self-inspect and iterate on designs.
github.comrepoAdded 3 Oct 2026, published 2 Oct 2026🧠 AI  Tencent Hy4 preview (open-weight MoE + Sherry quantization)
Hy4 preview is Tencent's new flagship Mixture-of-Experts language model: 770B total parameters with 49B activated per token across 78 layers (256 routed experts + 1 shared expert, top-8 routing), plus a native 10B multi-token-prediction layer for speculative decoding. It introduces Gated DeepSeek Sparse Attention with IndexCache for cross-layer index reuse and identity Hyper-Connections (iHC) on the residual path, and in blind internal evaluations on engineering tasks it edges out GLM-5.3 and Kimi K3. Weights (including an FP8 variant) are released under Apache 2.0 on Hugging Face with vLLM/SGLang deployment recipes and AngelSlim-based quantization/compression tooling.
huggingface.corepoAdded 2 Oct 2026🧠 AI- Bifrost (Maxim AI) — open-source LLM gateway
Bifrost is an open-source, high-performance LLM gateway (by Maxim AI) that exposes a single OpenAI-compatible API across 23+ providers including OpenAI, Anthropic, AWS Bedrock, Google Vertex, Azure, Cohere, Mistral, and Ollama. It provides automatic failover, load balancing, semantic caching, Model Context Protocol (MCP) tool integration, budget and governance controls, OIDC user provisioning, and Prometheus-based observability, deployable via npx or Docker with claimed sub-15 microsecond overhead at 5,000 RPS. It is positioned as a drop-in replacement requiring only a base-URL change for existing OpenAI, Anthropic, or GenAI SDK code.
github.comrepoAdded 2 Oct 2026🧠 AI - Folkbench/folkbench
Folkbench has two parts. One is a public benchmark and leaderboard of third-party AI API relay (中转站) services. Multi-node probes run around the clock and publish availability, P95 latency and price per relay, with per-model rankings. The other is Switch, an open-source Tauri/Rust desktop client that stores several Base URL and API Key pairs. It applies them to Claude Code or Codex configs in one click, previews config diffs, and stashes and restores the official ChatGPT OAuth credentials when switching Codex to a third-party provider. It also keeps keys local and estimates token usage and cost per session. The README also profiles several relay services, such as Modelflare, CheapAI and ApiPorter, and that part reads as promotional.
github.comrepoAdded 12 Oct 2026, published 2 Oct 2026🧠 AI - NVIDIA/OpenShell — sandboxed runtime for autonomous AI agents
OpenShell is NVIDIA's open-source runtime for safely running fleets of autonomous AI agents: each agent runs in an isolated sandbox where kernel-level controls enforce a declared policy over file access, syscalls, and network connections, and credentials are injected only for approved endpoints rather than exposed to the agent directly. Policy changes are checked with formal verification to flag risky new access (new hosts, new API methods) before they're approved, and the project ships a CLI, gateway, Kubernetes/Helm deployment, and a tutorial running OpenCode against an OpenRouter model.
github.comrepoAdded 1 Oct 2026🛡️ Security - OpenShell — safe, private runtime for autonomous AI agent fleets
OpenShell is NVIDIA's open-source runtime for running fleets of autonomous AI agents inside isolated sandboxes. Declarative policies cover filesystem, syscall, process and network access. These are enforced at the kernel level, and credentials are injected only into requests bound for approved endpoints. Policy changes are checked with formal verification so risky new access waits for human review. It ships a CLI, a gateway control plane (Helm deployment on Kubernetes), SDKs, extensibility hooks (middleware, interceptors, compute drivers) and installable agent skills, and it can run agents such as OpenCode.
github.comrepoAdded 1 Oct 2026🧠 AI - ShadowSafin/Synapass
Synapass is an OpenAI-compatible inference gateway and control plane that decides per request which AI provider serves it, under policy. It provides routing, retry and failover, exact/prefix/semantic caching, rate limits and budgets, tenant isolation, and an explain endpoint recording why each request was routed. It deploys with one command via Docker Compose (Postgres, Redis, ClickHouse, NATS, Grafana stack, dashboard).
github.comrepoAdded 20 Oct 2026, published 1 Oct 2026🧠 AI - https://github.com/Panniantong/Agent-Reach
Agent-Reach is a CLI and agent-"skill" layer that equips coding agents (Claude Code, Cursor, OpenClaw) with ready-made web-reading tool use: fetching arbitrary pages via Jina Reader, YouTube transcripts via yt-dlp, GitHub repos via gh CLI, Bilibili search, RSS via feedparser, and semantic web search via Exa through mcporter, with login-gated platforms (Twitter/X, Reddit, Xiaohongshu, Facebook, Instagram) added on request via cookies or OpenCLI browser sessions. Each platform module probes an ordered list of candidate backends and falls back automatically when one breaks (e.g. yt-dlp being blocked by Bilibili's anti-scraping), and an `agent-reach doctor` command reports which backend each channel is currently using. It positions itself as a "capability layer" that selects, installs and health-checks the right upstream tool for an agent rather than wrapping the reads itself.
github.comrepoAdded 2 Oct 2026, published 1 Oct 2026🧠 AI - AI-Infra-Guard (A.I.G) — Tencent Zhuque Lab
AI-Infra-Guard (A.I.G) is Tencent Zhuque Lab's open-source AI red-teaming platform combining AI infrastructure vulnerability scanning (2000+ CVE rules covering vLLM, llama.cpp, LangFlow, n8n, MLflow and 145+ other AI components), MCP server/skill security scanning, LLM API poisoning detection, and multi-turn jailbreak evaluation (Many-Shot, PAIR, GOAT, ActorAttack). It ships CLI tools (skill-scan, mcp-scan, agent-scan), a Docker-deployed web UI, and has produced original research including FORGE-Bench (loss-of-control benchmark), RogueHandoff-20, and SkillJack (persistent skill backdoors), with talks at Black Hat Europe 2025 on MCP security.
github.comrepoAdded 30 Sep 2026🛡️ Security - Sift — Open-Source Secrets/Credential Scanner
Sift is Stratus Security's open-source successor to Snaffler: a Native AOT credential/secrets scanner for pentesters that crawls local drives, SMB shares/subnets, Active Directory, SharePoint/OneDrive/Teams, Slack, and Jira/Confluence for exposed secrets. It supports Kerberos/NTLM/pass-the-hash authentication, resumable checkpointed scans, a JSON rule/ignore-rule system compatible with Snaffler's detection catalogue, and optional local-LLM (Ollama) validation to cut false positives without sending sensitive findings to a cloud API.
github.comrepoAdded 30 Sep 2026🛡️ Security - Launch HN: Magnitude (YC S25) – Self-optimizing inference engine for agents
Magnitude is an open source local inference engine (Apache 2.0) that compiles and tunes its GPU/CPU kernels on the user's exact device before a model runs, claiming up to 2x faster decode than llama.cpp (92% faster on Metal, 19% on CUDA) with 27% lower memory per agent. It ships as a cross-platform desktop app with a bundled CLI and an OpenAI-compatible API, offering one-click connections to agent tools like Pi, OpenCode, Hermes, Codex, OpenClaw, Claude Code, and Cline, running fully offline on Apple Silicon, NVIDIA, AMD, or CPU-only hardware.
github.comrepoPublished and added 30 Sep 2026🧠 AI - Andrea (Drego) Draghetti 👨🏻💻 🎣 (@AndreaDraghetti) on X
Tosint v1.0.0 is an open-source Telegram OSINT tool for analyzing bots and chats, exporting message history and media. The new release adds richer JSONL metadata output, optional SHA-256 hashing of exported media, bot/user authentication support, and an automatic fallback from MTProto-based history retrieval to ID-scan mode when dealing with restricted chats.
x.comrepoAdded 2 Oct 2026, published 30 Sep 2026🛡️ Security - AI News | AI Tools (@AI_News100x) on X
Open-Dots is an open-source reimplementation of OpenAI's 'Dots' computer-use agent, giving any LLM the ability to control a browser, terminal and filesystem plus connectors to personal apps. It is framework-agnostic (works with any LLM) and free, positioned as a self-hostable alternative to OpenAI's proprietary computer-use offering.
x.comrepoPublished and added 30 Sep 2026🧠 AI - rehan-remade/universal-modder
universal-modder is a set of Agent Skills, a CLI (um) and a shared knowledge base (field notes in knowledge/) that let AI coding agents such as Claude Code, Codex, Gemini CLI, Cursor, GitHub Copilot and OpenCode find a PC game's engine, reverse-engineer its code, build a working mod, generate art/3D/sound assets via the fal MCP server (or a local ComfyUI server), test the mod in the running game, and write a field note for the next agent. It ships worked examples — a weapon/boss pack for Terraria via tModLoader, a new civilization for Age of Empires II DE, and a real-time Minecraft-inside-GTA-V passthrough mod — each documented with a field note of exact versions, routes and gotchas, and agents can open pull requests to grow the shared knowledge base.
github.comrepoAdded 6 Oct 2026, published 30 Sep 2026🧠 AI  רון אברבוך (@Ron_averbuch) on X
Open-Dots is an open-source re-implementation of OpenAI's Dots computer-use agent, giving it browser, terminal and file control plus connectors to personal apps, and designed to work with any LLM rather than being locked to one vendor's model. It's announced via a tweet linking to the GitHub repo (github.com/Anil-matcha/Open-Dots).
x.comrepoAdded 30 Sep 2026, published 29 Sep 2026🧠 AI- feder-cr/invisible_playwright_mcp
invisible_playwright_mcp is an MCP server (and companion Python library, invisible_playwright) that wraps Playwright so an LLM agent can operate a real browser like a human: clicking, typing, scrolling and reading page content, useful for tasks like checking flight fares across a date range where no API exists. It ships a standalone chat+live-browser UI driven by any OpenRouter model, installs as a plugin for Claude Code, Codex and Gemini CLI, and exposes stealth/identity controls (seed-based browser fingerprint, proxy-derived timezone/locale/geolocation, persistent profile directories) via its invisible_core component.
github.comrepoAdded 7 Oct 2026, published 29 Sep 2026🧠 AI - NVIDIA OpenShell — secure runtime for autonomous AI agent fleets
OpenShell is NVIDIA's open-source runtime for running fleets of autonomous AI agents with restricted, policy-governed access to files, system calls, network, and credentials. It enforces policy at the kernel level inside isolated sandboxes (per-agent, with Docker/Podman/virtualization backends) and uses formal verification to flag risky policy changes — such as an agent gaining a new host or API access with credentials — before they take effect, so changes can wait for human review. It ships a CLI, a gateway control plane, Kubernetes/Helm deployment, and installable agent skills for writing and debugging sandbox policies.
github.comrepoAdded 29 Sep 2026🧠 AI - garak v0.17.0 — LLM vulnerability scanner release
Release notes for garak v0.17.0, NVIDIA's open-source LLM vulnerability scanner used for red-teaming and probing models for jailbreaks, prompt injection, data leakage and other failure modes. The release adds an EU AI Act risk-category mapping to tag and group probe results, plus fixes to detectors (agent_breaker judge verdict validation, packagehallucination import parsing, MarkdownExfilContent divide-by-zero, TriggerListDetector alignment) and probes (badchars ASCII selection, Markdown exfiltration link templates), along with Ollama generator improvements and dropped Python 3.10 support in favor of 3.13.
github.comrepoAdded 29 Sep 2026🛡️ Security - NVIDIA OpenShell — secure runtime for autonomous AI agent fleets
OpenShell is NVIDIA's open-source runtime for running fleets of autonomous AI agents in isolated sandboxes, enforcing per-agent policies on filesystem, syscall, and network access at the kernel level and injecting credentials only for approved endpoints. Policy changes go through a formal-verification step (an 'advisor'/'prover') that flags newly granted risky access, such as a new host reachable with credentials, before it's applied, and it deploys via Docker/Podman/host virtualization or Kubernetes with Helm.
github.comrepoAdded 29 Sep 2026🛡️ Security  MiMo-V2.6 (Xiaomi): Pro/Flash/9B-distill open-weight release, MIT license, 1M context
Hugging Face collection for Xiaomi's MiMo-V2.6 model family, comprising five open-weight checkpoints: MiMo-V2.6-Pro-RL (1T params), MiMo-V2.6-Flash-RL (311B params), a MiMo-V2.6-Distill-Qwen-9B distillation (vision-language capable), and Pro/Flash MOPD variants. The title claims MIT licensing and a 1M-token context window, positioning this as a large open-weight release spanning full-scale RL-trained models down to a 9B distilled variant usable on consumer hardware.
huggingface.corepoAdded 29 Sep 2026🧠 AI- https://github.com/dmdhrumilmistry/security-harness
security-harness is an open-source Claude Code plugin (also packaged for Gemini CLI, Codex and opencode) that orchestrates subagents — sh-recon, sh-hunter, sh-chainer, sh-verifier, sh-reporter — through a static-analysis pipeline covering 15 vulnerability classes (IDOR/BOLA, SQLi, XSS, SSRF, injection, auth, deserialization, path traversal, secrets, CSRF, XXE, open redirect, crypto, race conditions, file upload), producing README/JSON/SARIF/HTML/PDF reports with PoCs, CVSS and CWE/OWASP mappings. It also ships sh-pr-review, a per-PR merge-gate skill that posts inline findings and a commit status scoped only to code the PR itself introduced or aggravated, with caching, dedup via fingerprints, and a scheduled GitHub Action that keeps its per-class knowledge bases fresh by having one AI agent draft updates from allowlisted sources (OWASP, PortSwigger Research, CWE/CAPEC, HackerOne) while a separate adversarial reviewer agent fails-closed against prompt injection before auto-merge.
github.comrepoAdded 2 Oct 2026, published 29 Sep 2026🛡️ Security - StartLuxLabs/StartLux-Decision
StartLux-Decision is a family of open decision models (0.8B to 27B, plus a 35B-A3B mixture of experts) that return probabilities for every option of typed choice, yes/no and score questions. The repository holds the inference engine and HTTP server (vLLM plugin, /v1/systemone API), with Instant one-pass and AutoThink gated-reasoning variants. Reports first place of 174 entries on Decision Index 0.3.2 (69.12). Code is Apache 2.0; weights are CC BY-NC 4.0.
github.comrepoAdded 23 Oct 2026, published 29 Sep 2026🧠 AI - Uncensored and Offensive Security AI Models Benchmark
A curated GitHub list of open-weight "uncensored" and security-fine-tuned LLMs intended for authorized red teaming, pentesting, and security research, covering models like WhiteRabbitNeo's DeepHat V2, BugTraceAI-CORE, CYBER-FROST, and several abliterated Qwen/GLM/DeepSeek variants. It explains the underlying techniques (abliteration per Arditi et al. 2024, QLoRA/DPO fine-tuning, GGUF/FP8 quantization) and links to Hugging Face model cards, benchmark suites (CyberBench, TrustedSec's LLM Attack Benchmark vs OWASP Juice Shop), and deployment platforms for running these models locally or via API.
github.comrepoAdded 2 Oct 2026, published 29 Sep 2026🛡️ Security - Uncensored and Offensive Security AI Models Benchmark
A GitHub README curating open-weight "uncensored" and security-fine-tuned LLMs (e.g. WhiteRabbitNeo's DeepHat V2, BugTraceAI-CORE, CYBER-FROST, CyberPal2.0, Lily-Cybersecurity-7B, Dolphin-Llama3-8B, Wizard-Vicuna-13B-Uncensored, huihui-ai's abliterated Qwen variants) with HuggingFace download links, quantization formats (GGUF, FP8, Q4_K_M, Q6_K), and training techniques used (SFT, QLoRA, DPO, abliteration, MoE/MTP architectures). It also includes a glossary explaining abliteration (orthogonalizing the refusal direction out of the residual stream, per Arditi et al. 2024) and references benchmarks like CyberBench and TrustedSec's LLM Attack Benchmark, making it a practical reference for anyone sourcing or deploying refusal-removed models.
github.comrepoAdded 2 Oct 2026, published 29 Sep 2026🧠 AI - openrig — multi-agent Claude Code/Codex orchestration
OpenRig is an open-source local daemon/CLI/TUI/MCP server that orchestrates teams of Claude Code and Codex agent sessions (via tmux) defined declaratively in YAML "RigSpecs." Its own docs disclose a significant trust/permission footprint: it writes workspace-trust settings and status-line/activity hooks into ~/.claude.json and .claude/settings.local.json, pre-writes Codex trust hashes and trusted workspace entries into ~/.codex/config.toml, defaults Claude to --permission-mode acceptEdits and Codex to -s workspace-write, and supports an explicit OPENRIG_YOLO=1 mode that enables Claude's --dangerously-skip-permissions or Codex's -s danger-full-access. It also relays session/activity telemetry to a local daemon endpoint.
github.comrepoAdded 28 Sep 2026🛡️ Security - openrig — multi-agent Claude Code/Codex orchestration
OpenRig is an open-source local daemon, CLI, TUI and MCP server (built on tmux + SQLite) that manages teams of Claude Code and Codex agent sessions as a single persistent system rather than a pile of terminal windows. Topologies (pods, seats, edges) are defined declaratively in YAML (RigSpec/AgentSpec), booted with `rig up`, inspected via a topology TUI, and can be snapshotted/restored, discovered from existing tmux sessions, and messaged across agents (`rig send`, `rig broadcast`, `rig chatroom`). It ships starter topologies (first-project, conveyor, product-team, secrets-manager using HashiCorp Vault) and documents in detail what it writes to Claude/Codex config, trust and telemetry state on the host machine.
github.comrepoAdded 28 Sep 2026🧠 AI - vLLM v0.30.0
Release notes for vLLM v0.30.0, a major update to the open-source LLM inference/serving engine spanning 762 commits. Highlights include new model support (DeepSeek-V4.1-Flash, GLM-5.3-Flash, Kimi K3, Qwen3.8-Flash-Next, K2-Horizon, Cohere Compass and others), a "Fast Start" GPU weight-cache daemon for near-instant engine restarts via CUDA IPC, Gumbel-max watermarking for generated text, a HiSparse host-memory tier for sparse-MLA KV offload, Model Runner V2 improvements (dual-batch overlap, speculative decoding under pipeline parallelism), expanded quantization support (NVFP4, W4A16 DSA, AutoRound), and hardware-specific tuning across NVIDIA, AMD ROCm, Intel XPU and CPU backends.
github.comrepoAdded 28 Sep 2026🧠 AI - imkofty/Hermuse
Hermuse is a set of scripts and guides for running Hermes Agent (from Nous Research), the 9Router OpenAI-compatible model router and a Telegram gateway on a Linux VM. It adds a Cloudflare Pages and D1 long-poll tunnel to expose the 9Router dashboard, cron watchdogs including a gateway stall detector, and a default-deny Telegram allowlist. MIT licensed.
github.comrepoAdded 2 Nov 2026, published 27 Sep 2026🧠 AI - zhuyansen/awesome-claude-video-skills
Awesome-list repository cataloguing 183 open-source 'skills' and toolkits that let Claude Code, Codex and other coding agents generate or edit video: rendering frameworks like HyperFrames and Remotion, motion graphics, explainer/promo video generators, short-form editors, digital avatars and music videos. Each entry is read and security-graded by a companion service (Agent Skills Hub / agentskillshub.top), with a machine-readable JSON feed and category breakdowns (frameworks, promos, explainers, editing, shorts, avatars, animation, motion graphics, scripts, music videos).
github.comrepoAdded 29 Sep 2026, published 27 Sep 2026🧠 AI - Agent Control Standard (ACS)
Agent Control Standard (ACS) is an OWASP GenAI Security Project specification that lets a separate Guardian Agent inspect an AI agent's proposed actions before they execute and return allow/deny/modify/ask/defer over an authenticated JSON-RPC wire, with OpenTelemetry/OCSF audit trails and a CycloneDX/SPDX/SWID AgBOM inventory. The reference implementation runs Microsoft's Agent Governance Toolkit (AGT) behind the ACS contract with Bun, including host shims for Claude Code and OpenCode, and demonstrably denies a destructive `rm -rf /` command from a live coding-agent session while allowing benign ones. The project is explicit about current gaps — the wire is unauthenticated (issue #70) and the reference Guardian fails open by default (issues #32/#37) — and only 2 of 16 lifecycle hooks are evaluated live in v0.1.0.
github.comrepoAdded 26 Sep 2026🛡️ Security - garak v0.17.0 — adds EU AI Act risk-category mapping
garak is NVIDIA's open-source LLM vulnerability scanner that runs probes/detectors for jailbreaks, prompt injection, PII leakage, package hallucination, markdown exfiltration and more against LLM targets. This v0.17.0 release adds a new EU AI Act risk-category mapping to tag and group probe results by the Act's risk categories, alongside fixes to the agent_breaker judge, markdown-exfiltration detectors, Ollama auth/generation support, and dropped Python 3.10 in favor of 3.13 support.
github.comrepoAdded 26 Sep 2026🛡️ Security - Agent Threat Rules (ATR) — open detection-rule standard for AI agent threats
Agent Threat Rules (ATR) is an open, versioned YAML rule format (ATR-YYYY-NNNNN scheme) for detecting AI-agent runtime threats — prompt injection, tool-poisoning, malicious SKILL.md content, and MCP exchange abuse — evaluated by a reference TypeScript engine (with a Python wrapper) shipped as an npm/pip package, CLI, GitHub Action, and Docker scanner with SARIF output. The project positions itself as "Sigma for agent threats," maps rules to OWASP Agentic/LLM Top 10, MITRE ATLAS, and NIST AI RMF, and publishes an extensive (and unusually self-critical) benchmark suite against corpora like garak, PromptBench, and PromptInject, including documented harness bugs and withdrawn recall figures.
github.comrepoAdded 26 Sep 2026🛡️ Security - dzhng/jevgrep
Jevgrep (the `jg` CLI) lets a coding agent ask a natural-language question about a repository and get back relevant files, reading leads, and verbatim source excerpts in one response, using an LLM (Jev) to judge relevance across folders, files, and declarations instead of relying on grep/ripgrep alone. It ships an installable "skill" for Claude Code, Codex, OpenCode and other agents that teaches them when to call jg versus their normal tools, and requires a key for Vercel AI Gateway, TypeSafe, OpenRouter, or OpenCode Zen. A reported ten-task SWE-bench repeat found ~40% lower coding-agent cost ($7.62 to $4.52) but a lower solve rate (7/10 vs 8/10 baseline), explicitly framed as a cost/quality tradeoff rather than a win.
github.comrepoAdded 27 Sep 2026, published 26 Sep 2026🧠 AI - Sandyaa — open-source autonomous code auditor that proves bugs with working exploit PoCs
Sandyaa is an open-source autonomous code-audit tool that points at a local directory or git URL and runs end-to-end, driven by the Claude Code CLI (optionally Gemini) with no separate API key required. It uses a Recursive Language Model approach — the model drives a Python REPL to chunk code, spawn sub-LLM queries, and aggregate results — running eight recursive passes (call-chain tracing, data-flow expansion, vulnerability chaining, exploitability proof, etc.) and an attacker-control-reachability analyzer to filter unreachable findings, then writes each finding with a working exploit PoC and an evidence.json linking claims to file/line. Maintained by SecureLayer7, who report using it to surface zero-days; it's alpha-stage, macOS-tested, Linux/WSL2-expected-to-work, and unsupported on native Windows.
github.comrepoAdded 26 Sep 2026🛡️ Security - Hindsight — Agent Memory That Learns
Hindsight is an open-source agent memory system (MIT-licensed, self-hostable via Docker/Helm or usable as Hindsight Cloud) that goes beyond RAG-style recall by having agents learn through consolidated observations and mental models built from retained facts and experiences. It exposes retain/recall/reflect operations, a built-in MCP server per memory bank, Python/Node/Go/CLI clients, an LLM-wrapper for drop-in memory on OpenAI/Anthropic calls, and reports state-of-the-art results on the LongMemEval long-term memory benchmark, independently reproduced by Virginia Tech's Sanghani Center and The Washington Post.
github.comrepoAdded 26 Sep 2026🧠 AI - rewanthtammana/Who-Let-The-Agents-Act
who-let-the-agents-act is a self-hostable lab suite (Docker/Python, Groq-backed LLM agent) with nine isolated scenarios — overpowered data tools, IDOR-style cross-account access, unsafe agent handoffs, refund-limit bypass, indirect prompt injection via poisoned invoices, multi-tenant RAG leakage, secret leakage through debugging, fail-open approval outages, and a multi-hop confused-deputy agent chain. Each scenario runs in multiple modes (vulnerable vs. application-enforced) against the same prompt, recording model plan, policy decision, tool calls, and DB access as JSON so a reader can directly compare what changes when authorization is enforced outside the system prompt.
github.comrepoAdded 26 Sep 2026🛡️ Security - AgentSystemLabs/agent-office
agent-office is an open-source Node.js application that renders your team's projects as floors of a cartoon 3D office, where each Claude Code, OpenCode or Codex coding-agent worker sits at a desk with a visible terminal others can join. It wires agent workers directly into GitHub: an issues board and PR board with diff review, CI status and merge actions, a task queue that auto-hires workers into isolated git worktrees, one-click PR creation, live worker status via Claude Code/Codex hooks and an OpenCode plugin, and per-worker cost/token tracking against Claude plan limits. It also supports multi-agent meeting-room collaboration patterns such as debate, lead and team, map-reduce, red and blue, and review panel, where several agent workers jointly produce a file and open a PR, plus shared voice chat and screen sharing for the human team.
github.comrepoAdded 28 Sep 2026, published 26 Sep 2026🧠 AI - respanai/respan-gateway
respan-gateway is an open-source Rust LLM gateway shipped as a single binary with a built-in web UI. It lets OpenAI Chat Completions, Responses, Anthropic Messages and Gemini generateContent clients call any model, translating tools, images and reasoning. It adds named routes, fallback, retries, hedged races, MCP server fronting, per-call pricing, request logs and plugins.
github.comrepoAdded 22 Oct 2026, published 25 Sep 2026🧠 AI - Claude Code Templates Repository
Claude Code Templates (aitmpl.com) is an open-source npx CLI and template catalog offering 100+ ready-to-use agents, slash commands, hooks, settings, skills and MCP server integrations for Anthropic's Claude Code, aggregating contributions from Anthropic's official skills repo, K-Dense-AI's scientific skills, and various community projects (superpowers, wshobson/agents, awesome-claude-code, etc.). Beyond the template catalog it ships real-time analytics for monitoring Claude Code sessions, a mobile chat viewer with Cloudflare Tunnel support, a health-check diagnostic, and a plugin/marketplace manager, making it a practical operational toolkit for customizing and running Claude Code.
github.comrepoAdded 2 Oct 2026, published 25 Sep 2026🧠 AI - Show HN: Whiteboard (YC W26) – An open-source IDE for thoughtful software design
Whiteboard is an open-source (MIT) desktop IDE that gives coding agents like Claude Code and Codex an SDK to draw diagrams, sequence charts, and traces on a shared canvas linked directly to underlying code. It vendors Code OSS for VSCode-grade navigation/LSP support and adds a custom Rust-built AST-aware semantic diff viewer (with a WASM plugin system) that summarizes large generated functions as pseudocode and collapses noise like tests/docs, aiming to make reviewing autonomous agent decisions and code changes tractable.
github.comrepoAdded 26 Sep 2026, published 24 Sep 2026🧠 AI - yetone/magpie
magpie is a cross-platform menu bar app, TUI and CLI that lets you view and switch the model each installed AI coding agent (Claude Code, Codex, Gemini CLI, OpenCode, Cursor, Copilot CLI, Goose, Pi, etc.) is configured to use, editing each agent's config file surgically without disturbing comments or formatting. It runs a local gateway (127.0.0.1:3425) that translates between OpenAI Chat Completions, OpenAI Responses and Anthropic Messages APIs so every agent can point at one endpoint and use any provider's models, including routing groups that spread requests across multiple keys/subscriptions with configurable routing strategies (smart, order, rotate, usage). It can also reuse existing subscriptions (Claude Code, Codex/ChatGPT, Copilot, Devin, Gemini CLI) as providers for other agents without exposing or copying credentials, and supports encrypted profile backup/restore.
github.comrepoAdded 26 Sep 2026, published 23 Sep 2026🧠 AI - https://github.com/akha-security/akca
AKCA is an open-source, Go-based Dynamic Application Security Testing (DAST) scanner that combines HTTP and headless-browser crawling, JavaScript/AST analysis, API spec import (OpenAPI, GraphQL, gRPC, etc.), and adaptive active testing across a very broad set of vulnerability classes including SQL injection, XSS, SSRF, IDOR/BOLA, SSTI, JWT/OAuth flaws, race conditions, and cloud/CI exposure. It emphasizes evidence-oriented verification — replaying promising signals against baselines, negative controls, and OAST callbacks before promoting them to findings — and exports Burp-style HTTP evidence in HTML, JSON, CSV, Markdown, and SARIF reports. Positioned as a transparent, single-developer alternative inspired by but not claiming parity with Acunetix, Invicti/Netsparker, or Burp Suite Professional.
github.comrepoAdded 2 Oct 2026, published 23 Sep 2026🛡️ Security - nealbridges/VulnHunter
VulnHunter is a maintained fork of Capital One's open-source agentic security scanner, reworked to run on any agent harness (Claude Code, Codex, Grok/OpenCode) instead of being Claude-Code-specific. The fork's distinguishing work is engineering, not security findings: portable "skill" prompt files with an explicit environment contract, an installer that fails loudly instead of guessing paths, Docker-based sandboxed exploit validation, and a benchmark harness that ran six full scans of one production Go service across five model/harness stacks, finding that result counts swung from 3 to 42 findings depending on how rigorously exploits were validated. It ships three composable skills (/vulnhunt, /vulnhunter-fix, /vulnhunt-fix-verify), a headless batch-runner (harness/), and a deterministic manifest-writing CLI (vh).
github.comrepoAdded 6 Oct 2026, published 22 Sep 2026🧠 AI - nealbridges/VulnHunter
A maintained, harness-portable fork of Capital One's open-source VulnHunter — an agentic AI tool that performs attacker-first forward analysis on source code to find exploitable vulnerabilities, falsify weak findings, and produce evidence-backed PoCs rather than pattern-matched SAST alerts. This fork adds containerized (Docker-based) exploit validation, measured-impact PoCs (rows leaked, amplification factor, etc.), and portability across agent harnesses (Claude Code, Codex, Grok, etc.) via environment-contract prompt files, plus an unattended operator (vulnhunter-run) and batch-scanning/benchmark harness tested against OWASP NodeGoat, Juice Shop, and WebGoat.
github.comrepoAdded 6 Oct 2026, published 22 Sep 2026🛡️ Security - DVLAA
DVLAA (Damn Vulnerable LLM and Agent Application) is a self-hosted, Docker-deployable security training range for LLM and agent applications, modeled on the DVWA concept but for AI. It covers OWASP LLM Top 10 and Agent Security Top 10 risks (prompt injection, RAG poisoning, tool abuse, memory poisoning, excessive resource consumption, etc.) through 81 hands-on challenges, including an "AWDP" attack/defense track where 10 challenges reproduce real disclosed vulnerabilities in Dify, RAGFlow, Langflow, Flowise, Open WebUI and n8n (with optional real upstream container reproduction), 20 challenges adapted from a China–ASEAN AI security CTF, and 6 challenges adapted from a real model-poisoning CTF. It provides real model interaction, state-machine flag verification, source/prompt viewers, model management (local, Ollama, SiliconFlow, OpenAI-compatible), and bilingual UI.
github.comrepoAdded 22 Sep 2026🛡️ Security - Supply Chain Firewall (Datadog)
Supply Chain Firewall (SCFW) is a Datadog-built CLI that wraps npm, pip, and poetry commands to inspect every package target against known-malicious/compromised package datasets (the open-source malicious-software-packages-dataset and OSV.dev) before installation proceeds, blocking or warning on hits. It ships as a single Go binary, can be aliased transparently into a developer's shell, and optionally reports run outcomes and enforces centralized allow/block policies through Datadog Code Security across a fleet, sending only package metadata (never source code) to Datadog.
github.comrepoAdded 22 Sep 2026🛡️ Security - Show HN: Foremerge – Catch intent conflicts between parallel coding agents
Foremerge is an open-source coordination protocol layered above Git for parallel coding agents (Claude Code, Codex, Cursor). Agents publish semantic intent (scopes like symbol/api/schema) before editing into a shared SQLite store under .git, so Foremerge can detect intent conflicts—like one agent replacing a class another is extending—that Git's text-diff merging would silently miss. It's advisory-only (no file locking), deterministic (no LLM judgment calls), and gates ChangeSet acceptance on Foremerge-run validation rather than agent self-reports.
github.comrepoAdded 26 Sep 2026, published 21 Sep 2026🧠 AI - merijjeyn/jive
Jive is an open-source agent framework that replaces the standard LLM-call/tool-call loop with 'Graph Calls' — DAG-based workflows combining traditional tool calls with fast 'Jev' (System One) model calls for repetitive or intuitive steps. It aims to reduce token cost and latency versus agents like Claude Code and Codex by only invoking expensive reasoning LLM calls when needed, letting cheaper System One models follow through on planned execution graphs.
github.comrepoAdded 26 Sep 2026, published 21 Sep 2026🧠 AI - Simreal-AI/Simreal-MLBench
Simreal-MLBench is the open, minimal slice of ML Benchmark, a verifiable evaluation environment for machine learning research agents, covering 60 tasks across tabular learning, forecasting, vision, language, audio, multimodal and structured scientific data. It splits an open, Apache-2.0 layer (task definitions, scoring rule, verification tooling) from a commercial operated layer (SimReal's sandboxed runtime, gateway, submission broker and official scoring), scores tasks as 100xp^2 against a frozen reference leaderboard, enforces a source-blind two-submission protocol, and provides full provenance for every published number. It is positioned as an alternative to MLE-bench with a distinct task selection, resource protocol, and scoring scheme, aimed at supporting RLVR and agent self-improvement research.
github.comrepoAdded 26 Sep 2026, published 21 Sep 2026🧠 AI - StellarFoundry/soroban-security-scanner
soroban-scan is an open-source, deterministic static analyzer for Stellar Soroban smart contracts and Rust projects. It ships 19 Soroban-aware detectors (SS-001 to SS-033) covering missing authorization, re-initialization, cross-contract call ordering, unchecked arithmetic and storage or resource misuse. Output includes JSON, SARIF 2.1.0 and GitHub annotations, with baselines and a PR-scanning Action. The project describes itself as early development.
github.comrepoAdded 28 Oct 2026, published 21 Sep 2026🛡️ Security - Lonkero — Rust web vulnerability scanner (v3.7, AI agent mode)
Lonkero is an open-source Rust web vulnerability scanner (v3.7) combining 125+ context-aware scanners with an AI agent mode that drives targeted scans via natural-language conversation (using Claude, GPT, or local Ollama models). Notable techniques include a browser-free "proof-based" XSS engine that mathematically proves exploitability from reflection context + escape behavior, an "OOBZero" engine for detecting blind SQLi/SSRF/XXE via Bayesian multi-channel statistical inference and Pearson-correlated timing attacks without external callback infrastructure, Next.js middleware-bypass detection (CVE-2025-29927, CVE-2024-34351), AWS Cognito user-enumeration checks, and a scanner module that detects invisible prompt-injection payloads hidden in README.md files targeting AI coding assistants.
github.comrepoAdded 21 Sep 2026🛡️ Security - awarexone/Agentic-Bug-Hunter
Agentic-Bug-Hunter is an open-source CLI (bughunter) and Claude Code plugin that automates the bug bounty pipeline end-to-end: recon, vulnerability hunting across 26 web2 and 10 web3/smart-contract bug classes, a "7-Question Gate" validation step to kill weak findings, and submission-ready report generation for HackerOne, Bugcrowd, Intigriti, and Immunefi. It orchestrates existing scanners (subfinder, httpx, nuclei, katana, ffuf, dalfox) behind a multi-provider LLM layer (Ollama, Groq, DeepSeek, Claude, OpenAI) and cross-session "hunt memory," and also ships an MCP server for use from Cursor, Codex, or OpenCode.
github.comrepoAdded 21 Sep 2026🛡️ Security - ossf/criticality_score
criticality_score is an OpenSSF tool that computes a 0-1 criticality score for open source projects (based on an algorithm by Rob Pike), using signals like contributor count, commit frequency, dependents count, and org diversity to identify projects the ecosystem critically depends on. It ships a CLI, config files for tuning scoring weights, and companion tools (enumerate_github, collect_signals, scorer) for large-scale data collection; the project's GCP-hosted BigQuery/GCS datasets will be discontinued after 2026-08-29, with data moving to a static data directory.
github.comrepoAdded 21 Sep 2026🛡️ Security - Show HN: CUA-S1 – A System One Model for Computer Use
Cua is an open-source platform for computer-use agents: isolated cloud desktops (Fleets), a Sandbox SDK, local macOS/Linux VM management (Lume), a Cua Driver for controlling native apps/browsers via CLI/MCP/SDKs, and Cua-Bench for building and evaluating computer-use tasks. It also introduces CUA-S1, a family of small specialized "System 1" models that make fast, bounded decisions (e.g., scoring form field values from structured UI/document data) rather than generating agent actions token-by-token, with the first CUA-S1-FORMS model and dataset released on Hugging Face. The project is MIT-licensed with some optional components (cua-som, cua-perception's OmniParser integration) carrying AGPL-3.0 obligations.
github.comrepoAdded 26 Sep 2026, published 19 Sep 2026🧠 AI - sno-ai/sno-station
Sno Station is an open-source (Apache-2.0) local workstation that coordinates multiple AI agents (Claude Code, Codex, OpenClaw) as a 'Duo': they share an encrypted on-disk memory store, hand off tasks when one hits a rate limit, peer-review each other's work, and run a nightly self-improvement loop that proposes edits to their own skill files based on session history. It reports results on the Memora benchmark (FAMA/FAA metrics for forgetting-aware long-term memory) and cites Karpathy's 'LLM Wiki' and Google's WikiSkill as design inspirations.
github.comrepoAdded 26 Sep 2026, published 19 Sep 2026🧠 AI - Outrider Recon
Outrider Recon is an open-source, Claude-native multi-agent OSINT and external attack-surface recon platform for authorized engagements, covering web/API, identity/SSO, cloud, secrets, and people/breach intelligence. It deliberately stops short of exploitation: active enumeration is approval-gated and intrusive validation is a human hand-off, with deterministic Python controls enforcing scope, evidence integrity, workflow state, and finding promotion around Claude skills and optional MCP-based enrichment. Output is ranked, evidence-backed finding cards (confidence/severity/handoff recommendations) meant to feed proxy-assisted testing or pen-testing rather than raw scanner dumps.
github.comrepoAdded 22 Sep 2026, published 19 Sep 2026🛡️ Security - vinilana/jev-gateway
jev-gateway is a local proxy that sits between coding agents (Codex, Claude Code, OpenCode, Kilo, Gemini CLI, Devin) and their LLM backend, intercepting only the tool-selection decision and routing it to TypeSafe's small, fast "Jev" model instead of the main reasoning model, while forwarding everything else untouched. It supports forced tool_choice, hint-based suggestions (for APIs like Anthropic's that can't force a tool mid-turn), a live dashboard for cost/latency/routing metrics, and a companion benchmark repo (jev-gateway-bench) showing routing helps most on debugging tasks but can hurt some models on feature-building tasks.
github.comrepoAdded 26 Sep 2026, published 18 Sep 2026🧠 AI - coldteadotai/abide
Abide is a CLI (npx @coldtea/abide) that hooks into Claude Code, Codex and OpenCode to check every agent edit or turn against project rules written in AGENTS.md/CLAUDE.md that a linter can't enforce (e.g. 'never let a raw error reach a user', 'no premature abstractions'). It uses Jev, TypeSafe's calibrated decision model, to answer a typed yes/no probability per rule per diff instead of a full LLM call, making it cheap (~300ms, fractions of a cent per turn) enough to check every edit; violations above a threshold are fed back to the agent to repair in the same turn.
github.comrepoAdded 26 Sep 2026, published 18 Sep 2026🧠 AI - Oldcircle/geo-sleuth
geo-sleuth is an open-source Agent Skill that lets any tool-using agent (Claude Code, Codex, Cursor, Gemini CLI, OpenCode, GitHub Copilot) geolocate a photo without relying on text, license plates or landmarks, instead using OpenStreetMap geometry, elevation data, satellite tiles and street view. It structures the task as a scored candidate board with ~20 single-purpose Python scripts (sun/terrain/osm/pose analysis, CLIP-ranked satellite matching, DINOv2+SIFT street-view matching) that do the ranking, while the LLM only judges among top candidates and must cite the command/file behind every claim. Output includes coordinates with an error radius, camera heading, and an evidence image.
github.comrepoAdded 26 Sep 2026, published 18 Sep 2026🧠 AI - OWASP Agentic Skills Top 10 (AST10)
The OWASP Agentic Skills Top 10 (AST10) is a new security framework cataloging the 10 most critical risks in AI agent "skills" — the behavior layer that orchestrates multi-step tool use in OpenClaw, Claude Code, Cursor/Codex, and VS Code. It documents real 2026 incidents (the ClawHavoc registry-poisoning campaign with 1,184 malicious skills, Snyk's ToxicSkills audit of 3,984 skills finding 36.82% flawed, CVE-2025-59536/CVE-2026-21852 RCE in Claude Code project files, and CVE-2026-28363 ClawJacked WebSocket hijacking) and proposes a Universal Skill Format (YAML) with signing, permission allowlists, and identity-file protections to mitigate them, mapped to CSA's MAESTRO 7-layer threat model.
github.comrepoAdded 18 Sep 2026🛡️ Security - OmniJev/awesome-jev-gallery
An extensive, actively maintained GitHub "awesome list" cataloging the ecosystem that has grown around TypeSafe's Jev and its "System One" typed decision models — a non-generative alternative to chat LLMs that returns calibrated probabilities per option (Choice/Score/Noul primitives) via RLCD training and single-pass constrained decoding. It indexes dozens of open-weight reproductions (OneJev, Rizzo Flow, Laya, Jebadiah, kev), benchmarks and leaderboards (JevBench, Jev Decision Index, JevAdvBench, DecisionBench), downstream tools (browser/robot/trading agents built on the typed API), and the research lineage the design draws on (zero-shot entailment classifiers, InstructGPT's reward model, GLiNER/GLiClass, monoBERT, LLaDA, vLLM, DSPy, RouteLLM, Constitutional Classifiers). It also links commentary auditing TypeSafe's claims (accuracy vs. frontier LLM baselines, security issues found in community tools).
github.comrepoAdded 29 Sep 2026, published 17 Sep 2026🧠 AI - leepokai/jev-guard
jev-guard is an MIT-licensed hook layer that adds an auto mode to Claude Code, Codex, Copilot CLI, Gemini CLI, Cursor, pi, OpenCode, Antigravity and ACP editors. It asks the Jev model three typed questions (risk, user_requested, from_untrusted) per tool call and decides deny, ask or allow in about 20 lines of code. It also scans tool results for prompt injection and checks skills and plugins.
github.comrepoAdded 27 Oct 2026, published 17 Sep 2026🧠 AI - AnotiaWang/awesome-decision-models
A community-maintained GitHub list cataloging "decision models" (also called System One models): small/fast models that take a state plus caller-declared questions (Noul/true-false, Choice/multi-option, Score/rubric) and return a probability per answer in one forward pass, rather than generating text. It tracks the originating TypeSafe AI Jev model and its /v1/systemone API alongside competing hosted models (Upstage Solar Decide, Liquid AI's d1, OpenAI's Decisions API, Inception's Mercury Decide, Respan's Span-01), dozens of open-weight fine-tunes (Cloudflare's Clef, Perplexity's pplx-decider, AWS Strands Decider, Together AI's Tev1, and many Qwen3.5-based community models), zero-training logit-reading approaches, local runtimes (Ollama, Ollaya, llama.cpp-based servers), SDKs across a dozen languages, and a very long list of agent/coding-tool/MCP integrations (browser agents, code review, routing, game-playing demos) that use these models for fast, typed, in-the-loop decisions. The page is truncated at 40k of ~51k characters, so later sections (further toys, demos, and possibly benchmarks) are not reflected here.
github.comrepoAdded 2 Oct 2026, published 17 Sep 2026🧠 AI - Mapika/decider
Decider is an open reproduction of TypeSafe AI's System One (Jev) model class: instead of generating text, it reads a state plus a set of typed questions (Choice, Score, or Noul/yes-probability) and returns a calibrated probability distribution for each in one forward pass, with no decoding or parsing. The repo ships 2B/4B/12B and a 35B mixture-of-experts checkpoint (built on Qwen3.5 and Gemma-4 base models), trained on roughly 95 public datasets plus teacher-labelled data, with per-type temperature calibration, GGUF/llama.cpp and vLLM serving paths, an MPS/Apple Silicon port, and a community Snapdragon X Elite NPU port. It benchmarks against TypeSafe's Jev on JevBench and the Decision Index, documenting where it closes the gap (language, tools, retrieval) and where it lags (knowledge-heavy MMLU/GSM8K/GPQA tasks and calibration on hard items).
github.comrepoAdded 2 Oct 2026, published 16 Sep 2026🧠 AI - y0usaf/pi-jev
pi-jev is an npm extension (@y0usaf/pi-jev) that adds a typed decision layer to the Pi coding agent: a gate scores pending bash/write/edit tool calls on destructiveness, exfiltration risk, scope, and impact before they run, while an output judge scans bash results for leaked secrets and classifies command failures (retry/environment/code_bug/permission/user_error). Answers come back as probabilities or choice distributions rather than prose, are batched into one API round trip to api.typesafe.ai, cached per input, and fail open on any error so a dead endpoint never blocks the agent. The README documents calibration work behind the thresholds (e.g. destructive=0.90, leak=0.90) derived from repeated fixture runs, and details argument/output truncation and key redaction to limit what leaves the machine.
github.comrepoAdded 26 Sep 2026, published 16 Sep 2026🛡️ Security - bilibili/Index-Translate
Index-Translate is Bilibili's Apache-2.0 family of multilingual, multimodal translation models built on Qwen3.5 (2B, 9B and 35B-A3B preview), covering 150 languages with instruction following (glossaries, format preservation, tone). Variants add native image translation with no OCR (vision encoder), Index-Echo for speech subtitles and dubbing, Index-Homura for syllable-controlled translation and Index-NativeLong for full-document translation. The repo provides GGUF, FP8 and NVFP4 quantized builds, vLLM serving scripts, a free OpenAI-compatible API, four new benchmarks (instTrans, MEME, SandGlass, NAtIveLong), and links to three papers including HOMURA and RIVAL (RL for translation).
github.comrepoAdded 10 Oct 2026, published 15 Sep 2026🧠 AI - ruc-datalab/EvoOntology
EvoOntology is an open-source, self-evolving semantic ontology layer for data agents from Renmin University of China, exposed as MCP tools and installable as Claude Code and Codex plugins. It automatically builds a versioned ontology from tabular/file/database workloads, then continuously evolves it from agent execution trajectories using a build-use-evolve-evaluate-publish loop that validates candidate updates against a parent version before promotion. The accompanying paper reports gains over plain ReAct agents on DDR-Bench, InsightBench, and BIRD across GPT-5.5, GPT-5.6-sol, Claude-Sonnet-5, and Claude-Opus-4.8 backbones.
github.comrepoAdded 26 Sep 2026, published 15 Sep 2026🧠 AI - Cloudflare security-audit-skill
security-audit-skill is a Cloudflare open-source coding-agent skill that turns an AI coding agent into a structured vulnerability hunter, running six phases: reconnaissance into architecture.md/coverage-ledger.json, coverage-led hunting by isolated sub-agent "hunters," adversarial candidate validation, structured findings.json output validated against a report-schema.json, independent re-verification of claims, and target-neutral report generation (REPORT.md, FINDINGS-DETAIL.md, NEEDS-VALIDATION.md). It is installed via the Skills CLI (`npx skills add`), uses Node.js validators (validate-coverage-ledger.cjs, validate-findings.cjs), requires a sandboxed environment for safely executing target code/tests/fuzzers, and is the single-repo seed for Cloudflare's larger fleet-wide vulnerability discovery harness described in a companion blog post.
github.comrepoAdded 22 Sep 2026, published 15 Sep 2026🛡️ Security - OpenHunterAI
OpenHunterAI is a self-hosted, alpha-stage AI red-teaming workspace that applies attacker-style reasoning to web, API, and LLM application security testing against verified, in-scope public targets. It runs locally via Docker/Node.js, orchestrates bounded testing (scope lock → surface mapping → baseline → hypothesis testing → evidence gating → report/retest) through Go workers over NATS, and ships adapters for browser inspection, OWASP ZAP, and Nuclei, with separate OpenHack and Strix runtime integrations and an agent skill for Claude Code/Codex/Gemini CLI/Grok.
github.comrepoAdded 22 Sep 2026, published 15 Sep 2026🛡️ Security - Maskit
Maskit is a local privacy gateway that sits between AI coding tools (Cursor, Claude Code, Codex, ChatGPT, Claude, DeepSeek) and the model provider, automatically redacting sensitive data — API keys, database connection strings, private IPs, PEM keys, JWTs, PII like phone numbers/ID numbers — into placeholders before requests leave the machine, then streams responses back with the placeholders transparently restored. It works as a local reverse proxy (per-protocol ports for OpenAI/Anthropic/DeepSeek) plus a browser extension (Chrome/Edge MV3) that intercepts Fetch/XHR traffic on ChatGPT, Claude and DeepSeek web UIs, including redaction of uploaded Office documents. It also includes a lightweight local ONNX NER model for names/orgs/addresses, placeholder consistency across multi-turn conversations, and passive prompt-injection detection on model replies.
github.comrepoAdded 22 Sep 2026, published 15 Sep 2026🛡️ Security - WordPress Security Skills
WordPress-Security-Skills is a GitHub repo of modular 'Agent Skills' (per the open Agent Skills spec) that install into AI coding agents like Claude Code, Cursor, Codex, OpenCode, and Gemini CLI to guide secure-by-default WordPress plugin/theme development and security code review. Each skill targets a documented failure mode in AI-generated WordPress code — missing nonce checks, broken authorization, missing output escaping, unprepared SQL queries — with when-to-use guidance, common AI mistakes (wrong vs right), code examples, and checklists tied to official WordPress API references. It is explicitly instructional Markdown/PHP reference material, not a scanner or automatic protection, meant for developers and reviewers auditing AI-written or third-party WordPress code.
github.comrepoAdded 22 Sep 2026, published 15 Sep 2026🛡️ Security - DeathShotXD/0xCr0ssCrush
Research project on two signed vulnerable Windows drivers, DCRCVDrv.sys (MOCOMSYS) and Alinubx.sys (CnCrypt), abused by the Cruciferra MaaS loader to kill AV/EDR processes. It documents their devices, IOCTLs (0x2205C0, 0x222024) and the termination chain (ObOpenObjectByPointer -> ZwTerminateProcess), and gives annotated disassembly, hash-level sample provenance and blocklist-status snapshots. It includes a Rust lab harness with hash validation and dry-run, plus Sigma, YARA and telemetry guidance. Findings carry evidence labels, and the test matrix is limited to Windows 11 24H2 with HVCI disabled.
github.comrepoAdded 11 Oct 2026, published 14 Sep 2026🛡️ Security - Pal-AI-Lab/Cortico
Cortico is an open-source agent harness built around an event stream, designed for autonomous, continuously running agents that handle mixed real-time input across chat platforms, live games, and even physical environments. It provides modular LLM provider components (via an internal Responses protocol), unconstrained context/memory management, an isolated extension system called Cortico World, and a WebUI, with a companion AI-assisted extension creator (Cortina) that lets non-developers build extensions through conversation. A reference use case is cortico-world-vtuber, which drives a Live2D model via VTube Studio with streaming TTS and OBS overlay integration.
github.comrepoAdded 26 Sep 2026, published 13 Sep 2026🧠 AI - RepoGuardBench
RepoGuardBench is a benchmark and accompanying paper that measures whether local open-weight coding agents (Qwen2.5-Coder 1.5B-14B via Ollama) stay on the bug-fix task when repository artifacts — README files, issue text, code comments, test logs, and agent-rule files — carry inert prompt-injection instructions. It evaluates five lightweight context- and action-level defenses (D0-D5, including a path-only action gate) across seven metrics in a sandboxed task workspace, finding no statistically clear utility winner among them. The project ships a deterministic no-GPU smoke test, paper-claim verification scripts, and reproducible tables/figures under MIT (code) and CC BY 4.0 (data) licenses.
github.comrepoAdded 22 Sep 2026, published 13 Sep 2026🛡️ Security - shinthink/blitzstrike
Blitz Strike is an open-source Model Context Protocol server (TypeScript/Bun) that packages a structured 3-tier pentesting methodology — BLITZ (attack-surface recon), EAGLE-EYE (source-to-sink reachability tracing), and STRIKE (live validation before reporting) — into callable tools any MCP client (Claude Code, Cursor, Gemini, etc.) can drive with a single run_engagement call. It ships 130 self-written security tools, 317 indexed tool manuals, 58 data-driven escalation chains with negative-control checks, a Web3/Solidity audit module with Foundry proofs, and a regression/benchmark suite (453 checks, reported 1.0 detection / 0 false-positive rate) to make every finding verified rather than pattern-matched.
github.comrepoAdded 2 Oct 2026, published 12 Sep 2026🛡️ Security - agent-egress-bench
Agent Egress Bench is an open, tool-neutral benchmark maintained by PipeLab (makers of Pipelock) that tests whether products mediating an AI agent's outbound traffic — proxies, egress firewalls, MCP wrappers, agent gateways — actually catch exfiltration attempts caused by prompt injection or misalignment, rather than testing the underlying model itself (that's left to AgentDojo, InjecAgent, CyberSecEval, AgentHarm, ASB). It ships a reproducible Go runner with a proxy/WebSocket/MCP/A2A adapter contract, an offline validator, DSSE-signed evidence bundles, and a CI-runnable GitHub Action, and separates containment from false-positive rate as two distinct scored axes with immutable case IDs and OWASP Agentic Top 10/MITRE ATT&CK mappings. Its governance explicitly permits third parties to publish results unfavorable to the maintainer's own Pipelock product.
github.comrepoAdded 12 Sep 2026🛡️ Security - CassiopeiaCode/CosyRedactGateway
Cosy (CosyRedactGateway) is a Node.js gateway that sits between programmers' LLM clients and OpenAI or Anthropic APIs. It replaces credentials found in JSON request text with reversible SHA-256-based placeholders, using high-entropy scoring, structured detectors and Gitleaks-compatible rules, and restores them in responses, SSE streams and tool arguments. It runs on Cloudflare Workers, Deno or locally, and documents its limits: auth headers are still forwarded, and misses are possible.
github.comrepoAdded 19 Oct 2026, published 11 Sep 2026🛡️ Security - CassiopeiaCode/CosyRedactGateway
Cosy (CosyRedactGateway) is a local-first LLM credential redaction gateway. It replaces secrets in request JSON with reversible SHA-256 placeholders before forwarding to OpenAI or Anthropic upstreams, then restores them in responses, SSE streams and tool-call arguments. Detectors cover high-entropy strings, structured patterns and Gitleaks-compatible rules. It runs on Node.js, Cloudflare Workers or Deno, with an offline demo script and a documented list of limits.
github.comrepoAdded 19 Oct 2026, published 11 Sep 2026🧠 AI - sage — Agent Detection & Response (ADR) for AI coding agents
Sage is an "Agent Detection & Response" (ADR) security layer that intercepts tool calls made by AI coding agents — shell commands, URL fetches, file writes — and screens them through multiple detection layers before execution. It combines cloud URL reputation, 300+ YAML local heuristics, a two-tier (heuristic + fine-tuned ML) prompt-injection detector for fetched content, npm/PyPI package supply-chain checks (registry existence, file reputation, age), installed-plugin scanning at session start, and Windows AMSI integration. It ships as a plugin for Claude Code, Cursor, VS Code, OpenClaw, and OpenCode, and is published by Gen Digital (also distributed under the Norton/Avast Sage branding).
github.comrepoAdded 10 Sep 2026🛡️ Security - AWSHound — AWS BloodHound OpenGraph Collector
AWSHound is a Go CLI/container tool that collects AWS IAM and authorization data across profiles, config-file opt-ins, or an entire AWS Organization (via cross-account role assumption), and outputs a BloodHound OpenGraph for attack-path analysis. It supports phased collection with on-disk artifacts, offline graph building from previously collected data, and safeguards like --max-api-requests and --max-api-requests-per-minute to bound AWS API traffic during collection.
github.comrepoAdded 8 Sep 2026🛡️ Security - GhostJS
GhostJS is an open-source Burp Suite extension by TrinetLayer that passively scans JavaScript, HTML, and JSON responses flowing through Burp for hardcoded secrets (AWS/GCP/Azure keys, Stripe/PayPal/GitHub tokens, JWTs, private keys, etc.) and hidden API endpoints, surfacing findings in a dedicated tab with severity, confidence scoring, remediation guidance, and Markdown export. It also actively fetches referenced <script> bundles using the tester's live session cookies and applies a false-positive filter to suppress doc-sample and placeholder keys, making it a practical recon aid during authorized web app pentests and bug bounty work.
github.comrepoPublished and added 7 Sep 2026🛡️ Security - vet (SafeDep)
vet is an open-source CLI (from SafeDep) that scans package manifests, SBOMs, container images, and source repos across npm, PyPI, Maven, Go, RubyGems, Cargo, and Packagist to surface vulnerabilities, malicious packages, and license/quality issues. It cuts through CVE noise by analyzing actual code-usage evidence, queries SafeDep Cloud's threat-intelligence database for real-time malware detection (e.g. flagged packages like express-cookie-parser, eslint-config-airbnb-compat), and lets teams enforce security/license/OpenSSF-Scorecard policies as CEL expressions in CI/CD via SARIF/JSON/Markdown reporting.
github.comrepoPublished and added 7 Sep 2026🛡️ Security - headroomlabs-ai/headroom
Headroom is an open-source (Apache 2.0) local compression layer that sits between AI agents and LLM providers, compressing tool outputs, logs, RAG chunks, files and conversation history before they reach the model. It offers a Python/TypeScript library, a drop-in proxy, an `headroom wrap` mode for popular coding agents (Claude Code, Codex, Cursor, Copilot, Aider, etc.), an MCP server, cross-agent shared memory with dedup, and output-token reduction via verbosity steering and effort routing — all running locally with reversible compression (CCR) so originals stay retrievable.
github.comrepoAdded 23 Sep 2026, published 7 Sep 2026🧠 AI - PlamenTSV/plamen
Plamen is an open-source Python orchestrator that drives 18-100 Claude Code or OpenAI Codex CLI agents across 40+ phases to autonomously audit smart contracts (EVM/Solidity, Solana/Anchor, Aptos Move, Sui Move, Soroban, DAML/Canton) and L1 node-client infrastructure (Go/Rust consensus, p2p, mempool code), producing a severity-tiered AUDIT_REPORT.md with verified proof-of-concept exploits for each finding. It integrates MCP servers for Slither, ChromaDB and Solodit, ingests vulnerability corpora from Solodit, DeFiHackLabs and Immunefi to ground findings, and runs a PTY-supervised worker-pool architecture with checkpoint/resume, artifact-based completion gating, and a dedicated L1 mode with consensus-invariant and network-surface depth agents.
github.comrepoPublished and added 7 Sep 2026🛡️ Security - bikini/exploitarium
Exploitarium is a consolidated GitHub archive of an independent researcher's proof-of-concept vulnerability writeups, merging over a dozen former standalone PoC repos into one. It covers diverse real-world targets including RustDesk session permission bugs, an OpenSSH agent lock provider bypass, a Redis VSET duplicate HNSW ID RCE, a QEMU CXL Type3 mailbox escape, Firefox native/backup NSS RCE PoCs, libssh2 CVE-2026-55200, Nextcloud federated share bearer token issues, and more. The author documents an AI-assisted fuzzing workflow (hand-typed PoCs, AI-drafted READMEs) and credits prior work on an objdump OOB write finding.
github.comrepoPublished and added 7 Sep 2026🛡️ Security - andyrewlee/awesome-agent-orchestrators
A curated GitHub list cataloguing open-source and source-available tools for orchestrating AI coding agents, organized into categories: terminal multiplexers/TUIs (tmux+worktree managers like claude-squad, amux, agent-manager), desktop/web parallel-session apps (Ghostex, Tempest, Vicoa), multi-agent swarms with inter-agent coordination (crewAI, gastown, loki-mode), autonomous loop runners (Ralph Wiggum-style loops like ralph-orchestrator, bernstein), issue/board-driven task runners (cyrus, open-swe, claude-code-action), infrastructure/control-plane primitives (Concord MCP, Agent Messaging Protocol), and always-on personal assistants (openclaw, rowboat). It covers dozens of tools working with Claude Code, Codex, Gemini CLI, OpenCode, and other agent CLIs, plus a watchlist of stalled projects. Useful as a map of the fast-moving agent-orchestration tooling landscape as of mid-2026.
github.comrepoAdded 23 Sep 2026, published 7 Sep 2026🧠 AI - ForgeGuardian
ForgeGuardian is an open-source (Apache 2.0) supply chain security scanner covering 9 package ecosystems (npm, PyPI, Go, Maven, RubyGems, Cargo, NuGet, Hugging Face, GitHub Actions) via 8 concurrent scan engines and 223+ built-in malicious-package detection signatures. It runs fully offline/local-first, offers a CLI (fgctl) and self-hosted SOC-style dashboard, generates CycloneDX/SPDX SBOMs, supports Sigstore keyless signing and provenance tracking, policy-as-code rules, dependency topology/attack-surface mapping, drift detection with auto-quarantine, and SARIF output for GitHub Actions CI integration, plus optional AI-powered advisory/patch-agent triage.
github.comrepoPublished and added 5 Sep 2026🛡️ Security - The React Native Developer's Security Guide
A GitHub-hosted book focused entirely on securing the React Native developer's workstation and toolchain rather than the shipped app — covering the polyglot execution surface triggered by a single git clone/yarn/pod install (Ruby, CocoaPods, Xcode build phases/XCSSET, Gradle, gradle-wrapper.jar, keystores), CVE-2025-11953 (exposed Metro/RN dev server), ClickFix-style social engineering of developers, CI-as-extended-workstation risks, and Expo/EAS-specific supply-chain concerns. It ships alongside a separate companion repo of 119 Opengrep detection rules, each mapped to a specific chapter's attack technique, plus practical appendices like a safe-clone runbook and a file risk atlas for hardening teams.
github.comrepoPublished and added 5 Sep 2026🛡️ Security - OWASP OASIS
OWASP OASIS is a proposed community project that operationalizes turning automated vulnerability/fix-generation tool output into human-validated pull requests submitted upstream to open source projects. It defines a full lifecycle (intake, weighted validator review with accept/reject/modify/duplicate decisions, OWASP adoption, ephemeral working forks, upstream submission) plus roles (project owners, validators, maintainer liaisons, automation operators) and outcome metrics like upstream acceptance rate. The GitHub repo lays out governance via a validators.yml credibility file, CODEOWNERS-gated scoring, and GitHub Projects/issue templates to run the whole thing without custom tooling.
github.comrepoPublished and added 5 Sep 2026🛡️ Security - Numbat
Numbat is a Go-based, single-binary endpoint agent from Perplexity AI that gives visibility into AI coding-agent activity (Claude Code, Codex, OpenClaw, and other CLI/IDE/gateway agents) by capturing events through local hooks, OTLP/HTTP logs, and on-disk session artifacts. It normalizes activity into one event model, evaluates it with a local CEL rule engine (including multi-step sequence rules like secret-read-then-egress), and can optionally block matched actions via synchronous pre-action hooks (deny/monitor decisions), with case bundles and SHA-256 manifests for forensic reconstruction. Example built-in rules detect cloud-metadata SSRF requests (169.254.169.254) and credential-exfiltration chains, mapped to MITRE ATT&CK technique tags.
github.comrepoPublished and added 5 Sep 2026🛡️ Security - iamzulx/crypto-rag
crypto-rag is an Indonesian-language CLI crypto assistant that pairs a static knowledge-base RAG pipeline with live market data tool calls, built on the principle that volatile numbers (price, funding rate, TVL, sentiment) must never be embedded in the vector store since they go stale instantly. It implements hybrid retrieval (BM25 keyword search + FAISS dense embeddings fused via Reciprocal Rank Fusion) over a 146-topic knowledge corpus, an optional cross-encoder reranker, and an intent router that dispatches price/derivatives/on-chain/sentiment queries to live sources (Binance, DefiLlama, Fear & Greed Index) versus concept questions to the corpus. A tool-calling agent handles multi-step queries, and an OpenAI-compatible LLM synthesis layer (works with StepFun, OpenAI, Groq, LM Studio, Ollama) grounds answers with citations and falls back to extractive answers when no LLM is configured.
github.comrepoAdded 2 Oct 2026, published 5 Sep 2026🧠 AI - eldarshiraliyev/BugScanner
BugScanner is an asyncio/httpx Python framework for recon and automated web vulnerability scanning, with a React and FastAPI dashboard. It covers subdomain enumeration (crt.sh, DNS brute force), TCP port scanning, fingerprinting, and modules for XSS, SQLi, CORS, SSRF, open redirect, JWT, IDOR and business logic, plus a Nuclei wrapper. A 5-rule false-positive filter with SPA detection, adaptive rate limiting, WAF detection and SARIF export are included.
github.comrepoAdded 20 Oct 2026, published 5 Sep 2026🛡️ Security - h5i-dev/awesome-ai-agent-incidents
A curated GitHub corpus tracking real-world security incidents, CVEs, attack techniques, and defensive tools specific to autonomous AI agents — spanning prompt injection/goal hijacking, MCP client-side tool-metadata poisoning, the "Promptware Kill Chain" multi-stage attack model, MITRE ATLAS agentic techniques, and the OWASP Top 10 for Agentic Applications. It also documents the OpenClaw/ClawHub supply-chain incident (1,184 malicious skills confirmed by Antiy CERT) and links defensive projects like OWASP Agent Memory Guard for LangChain/LlamaIndex agent memory protection.
github.comrepoAdded 3 Sep 2026🛡️ Security - Agenta-AI/awesome-ai-agent-platforms
A curated, CC0-licensed GitHub list cataloguing open-source AI agent platforms across five categories: persistent AI coworkers (Agent Zero, Agenta, LibreChat, LobeChat, Open WebUI, OpenClaw), developer agent frameworks (CrewAI, LangGraph, LlamaIndex, Haystack, Langflow, Letta, Agno, Pydantic AI, OpenAI Agents SDK), workflow/automation runtimes (n8n, Temporal, Prefect, Dagster, Apache Airflow, Windmill), browser agents (Browser Use, Skyvern), and coding agents (Aider, Cline, Goose, OpenHands, Open Interpreter). Each entry states a factual one-line description plus its license and hosting model, with selection criteria requiring an active repo, a usable product, and verifiable licensing — companion comparison table hosted at aiagentplatforms.dev.
github.comrepoAdded 30 Sep 2026, published 2 Sep 2026🧠 AI - Nehanth/pooled
Pooled runs one open model (Qwen 3.6 35B MoE, a 27B dense hybrid, smaller Qwen3/SmolLM) across devices in a browser "room". Each tab holds a slice of layers and runs them on its own GPU with custom WGSL kernels. Hidden states pass over WebRTC, and speculative decoding is checked against plain decoding by golden tests. It also ships a Code-mode agent loop with a sandboxed preview, and an npx CLI bridge (@pooled/cli) that exposes the room as an OpenAI Chat Completions/Responses and Anthropic Messages endpoint with grammar-constrained tool calling, so Codex CLI, Claude Code and opencode can use it. The README includes latency-injected benchmarks, a comparison with exo, Petals, llama.cpp RPC and WebLLM, and a threat model.
github.comrepoAdded 16 Oct 2026, published 1 Sep 2026🧠 AI - rollroyces/py-idp
py-idp is a Python framework for intelligent document processing with a six-stage pipeline (parse, classify, extract, assess, validate, human review). It supports 23 LLM backends including OpenAI, Anthropic, Ollama, and self-hosted Nanonets-OCR2-3B. It adds Pydantic schema extraction, auto-chunking of oversized documents, an eval harness, and a review-driven policy update for confidence. It is dual-licensed AGPL-3.0 and commercial.
github.comrepoAdded 23 Oct 2026, published 31 Aug 2026🧠 AI - PackageGuard
PackageGuard is an open-source .NET CLI tool that scans NuGet, npm, pnpm and Yarn dependencies (direct and transitive) across a codebase, enforcing hierarchically-configured allow- and deny-lists for licenses, packages and versions. It scores each package's Legal, Security and Operational risk using signals like OSV vulnerability data, maintainer activity, package signing and release cadence, and can emit a CycloneDX or SPDX SBOM enriched with OSV vulnerability data, plus console, HTML and SARIF output for CI/GitHub code scanning. It's positioned as a free alternative to commercial supply-chain tools like Black Duck and Snyk.
github.comrepoPublished and added 31 Aug 2026🛡️ Security - choirboy-prompt
choirboy-prompt is a cross-runtime agent-memory plugin that loads project lore, research indexes, and validated dossiers into agent sessions via SessionStart hooks (Claude Code, Codex) or full plain-text payloads (Kimi, OpenCode, Hermes), so new conversations continue from established project history instead of starting cold. It handles installation across multiple agent apps, migration of project artifacts between checkout locations, and includes a build/verify pipeline (build-context.py, test.sh) for authoring canonical lore files like prompt.md, user.md, and lore.md.
github.comrepoAdded 22 Sep 2026, published 31 Aug 2026🧠 AI


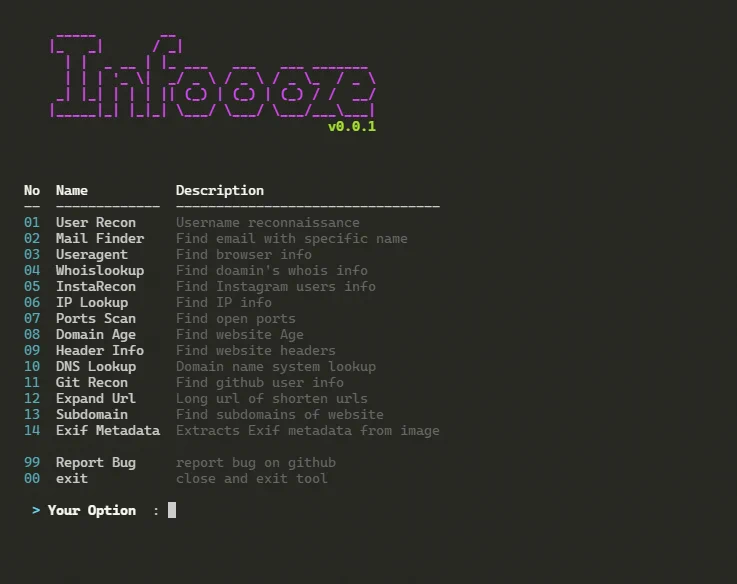
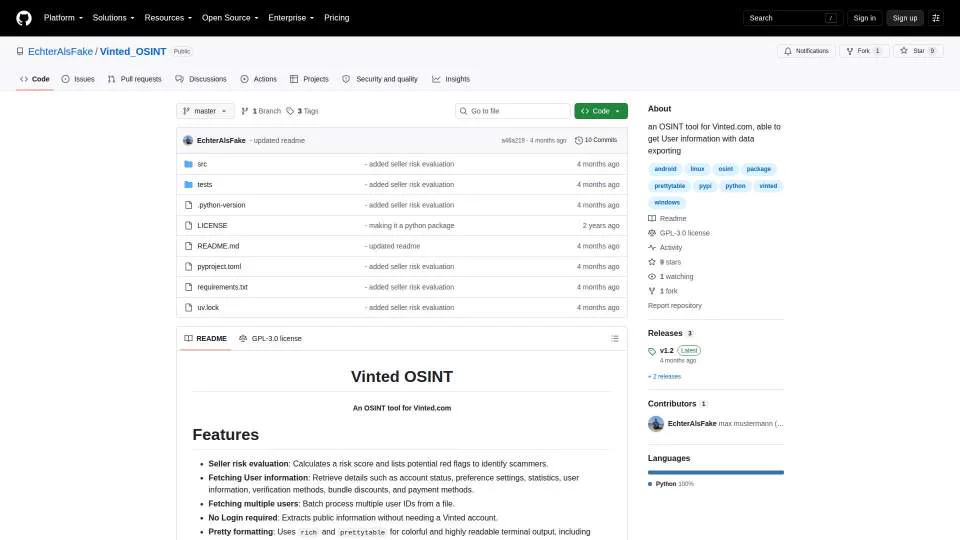


Showing 150 of 326
Show more