 Lewis - Policifyai (@Policifyai) on X
Policifyai's October 2026 roundup lists model releases by date with prices and benchmark scores: GPT-6.1 Sol and Terra, Claude Sonnet 5.5 and Haiku 5.5, Gemini 4 Argon and Carbon, Muse Spark Open, Mistral Large 4 weights and Kimi K3.1 Pro. It also covers Anthropic's S-1 compute commitments, Artificial Analysis Intelligence Index v5, and chip and data-center deals.
 x.comarticleAdded 1 Nov 2026, published 31 Oct 2026🧠 AI
- Dark Web Intelligence (@DailyDarkWeb) on X
CVE-2026-102764 is an unauthenticated RCE in BeyondTrust Remote Support, already exploited and in CISA KEV. Rapid7 published an analysis and opened a Metasploit pull request on 30 October 2026, showing code execution on version 24.1.2 via a forged "local" message origin, the native file-transfer service and a PHP file written to the web root. BT26-05 (CVSS 4.0 9.3) is fixed by patch BT26-05-RS; SaaS was patched by 9 October.
x.comthreadAdded 1 Nov 2026, published 31 Oct 2026🛡️ Security  Inside a malicious Claude Code-branded extension and its persistent SSH backdoor
Microsoft Threat Intelligence analyzes a tampered anthropic.claude-code extension (versions 2.1.312 and 2.1.313) served on the Cursor marketplace on 29 October 2026. The injected JavaScript loader adds an SSH key labeled svc-telemetry, opens a reverse SSH tunnel and sets up persistence on macOS, Linux and Windows. The post gives cleanup steps, IOCs and Defender XDR hunting queries. VS Code Marketplace and npm were not affected.
 microsoft.comwriteupPublished and added 31 Oct 2026🛡️ Security
 From help desk impersonation to AD CS abuse: Investigating ESC1 and ESC8 intrusion paths
Microsoft Threat Intelligence analysis of two human-operated intrusions that began with Teams help desk impersonation and Quick Assist sessions, then diverged at AD CS. Case 1 abused an ESC1 template for privileged certificates and DCSync, with an excluded account later used for Rclone exfiltration. Case 2 used PetitPotam and ESC8 relay to get a domain controller certificate and PKINIT. Includes investigation steps, AD CS hardening and KQL hunting queries.
microsoft.comwriteupPublished and added 30 Oct 2026🛡️ Security ARTEX and Friends: Enter Agentic Offensive Frameworks
ARTEX is an open-source, Go-based multi-agent LLM pentesting and C2 platform that Google Threat Intelligence Group and Mandiant saw threat actors run in incident response cases from late August 2026, alongside PentAGI and CAIRN. The report covers ARTEX behaviour such as MySQL general_log JSP webshell poisoning and burst timing, UNC7228 (overlapping STORM-0940), a seven-stage model of adversary LLM use, and five Mandiant defensive layers. The text was truncated before the last layers.
 cloud.google.comarticleAdded 1 Nov 2026, published 30 Oct 2026🛡️ Security
- Artificial Analysis (@ArtificialAnlys) on X
Artificial Analysis launched an HLE-Diamond leaderboard in v5 of its Intelligence Index, covering the refined 1,000-question Humanity's Last Exam from CAIS and Scale AI. Each question runs once without tools, graded by GPT-5.6 Luna (medium) as pass@1. Gemini 4 Carbon (high) leads at 69%, Claude Opus 5.5 (max) scores 68%, and the top open weights model, Kimi K3.1 Pro, reaches 37%.
x.comthreadPublished and added 30 Oct 2026🧠 AI  Polymarket stolen funds: One account withdrew at least $2.7M across 710 wallets
Polymarket's international exchange suffered unauthorized withdrawals on 29 October 2026 after a compromised third-party provider, reportedly the website monitoring service DebugBear. Betting Intelligence and Polysights found one account withdrew at least $2.7 million across 710 wallets. Polymarket paused trading, referred the case to law enforcement, promised reimbursement, and had a June 2026 vendor breach that cost about $3 million. The attack mechanism is not described.
 en.cryptonomist.charticlePublished and added 29 Oct 2026🛡️ Security
 VulnCheck - Outpace Adversaries
VulnCheck Open Source is an index of VulnCheck's open-source tooling for its vulnerability and exploit intelligence. It lists a Python API client, a CLI, a GitHub Action for CI/CD, go-exploit (a Go exploit framework), an MCP server for delivering intelligence to AI clients, and VulnCheck Insights, a Chrome extension that highlights CVEs, CPEs and PURLs on web pages and enriches them. The page gives only one-line descriptions.
 vulncheck.comtoolAdded 29 Oct 2026🛡️ Security
 Tracking AI adoption in North Korean threat actor tradecraft
Microsoft Threat Intelligence report on how North Korean actors use AI, ranking Jade Sleet, Coral Sleet and Jasper Sleet as operationalized, Diamond Sleet, Onyx Sleet, Pearl Sleet and Sapphire Sleet as accelerating, and Emerald Sleet as expanding. It documents AI-generated lures (100+ Onyx Sleet PDFs, August and September 2026), AI-built tooling such as Coral Sleet's private GitHub repository trojanizing, and Onyx Sleet and Pearl Sleet use of the ARTEX agentic pentest framework. It ends with mitigation and Defender guidance.
microsoft.comarticlePublished and added 29 Oct 2026🛡️ Security Gemini 4 Carbon is the new #1 on the Artificial Analysis Intelligence Index v5
Gemini 4 Carbon scores 59 on Artificial Analysis Intelligence Index v5 (published 28 October 2026), the top score, with #1 on 4 of 9 evaluations including HLE-Diamond and AA-Omniscience. On the Coding Agent Index it scores 59 with Antigravity CLI, 3 points behind Claude Code with Claude Opus 5.5 (62). Cost is $7.76 per task, versus $10.04 for Opus 5.5. Rollout is limited to selected users.
 artificialanalysis.aiarticleAdded 30 Oct 2026, published 29 Oct 2026🧠 AI
 [AINews] Gemini 4 Carbon tops leaderboards, launches for cyber defenders
AINews issue for 27-28 October 2026, a Latent Space digest of Twitter and Reddit. It leads with Google DeepMind's Gemini 4 Carbon: claimed cyber scores (SEC-bench Pro 88.2%, ExploitGym 54.8%, CWE-bench 71.0%), #1 on Artificial Analysis Intelligence Index v5 at 59, and access limited to cyber defenders through the Fairwind Program. It also covers benchmark integrity disputes, GitHub Copilot Fusion, H-Net v2, KV-cache work, open-weight releases and Claude Code quota complaints.
 latent.spacearticlePublished and added 29 Oct 2026🧠 AI
- Dark Web Intelligence (@DailyDarkWeb) on X
DailyDarkWeb post summarising Anthropic Frontier Red Team research published 27 October 2026. An unreleased internal Claude research model built five attack chains: Chrome sandbox escape (V8 heap bug, CacheStorage race, FedCM use-after-free), a Safari same-origin policy bypass, data extraction from a locked Pixel 9 over USB, a Windows QUIC kernel crash (CVE-2026-33096) and zero-click Linux root via multipath TCP (CVE-2026-98432). Anthropic says all flaws are fixed, including 62 Chrome CVEs as of Chrome 156. The post notes the chains are not independently reproduced.
x.comthreadAdded 30 Oct 2026, published 29 Oct 2026🛡️ Security - Laban (@lunkertw) on X
An X post summarising five AI items: Google DeepMind's Gemini 4 Carbon (88.2% SEC-bench Pro, 54.8% ExploitGym, 71.0% CWE-bench, 59 on Artificial Analysis Intelligence Index v5.0), Ed Zitron's critique of Anthropic's S-1, a Utah Claude Code pilot, and the repos beenuar/AiSOC and expo/skills. In the Utah pilot, 34 developers in 10 agencies took part over four weeks, 80% had a working setup within 30 minutes, and 71% saved over 20 hours. It gives short summaries and links, not primary analysis.
x.comthreadAdded 29 Oct 2026, published 28 Oct 2026🧠 AI - Niko (@nikolayxyz) on X
Gemini 4 Carbon is Google's new frontier model, announced in a post by nikolayxyz that quotes Google's launch text. It ranks #1 on v5.0 of the Artificial Analysis Intelligence Index with 59 points, ahead of Opus 5.5 and GPT-6 Astra. Intro pricing is $2 input and $10 output per million tokens. Access starts for cyber defenders first, as Gemini 4 Argon's did. The captured text is cut off before the rollout details.
x.comthreadAdded 29 Oct 2026, published 28 Oct 2026🧠 AI  Gemini 4 Carbon
 is Google's frontier model, announced two weeks after Gemini 4 Argon. It scores 59 on Artificial Analysis Intelligence Index v5.0, 88.2% on SEC-bench Pro, 54.8% on ExploitGym and 71.0% on CWE-bench. Pricing is $2 per million input and $10 per million output tokens. Access starts with a subset of cyber defenders through the Fairwind Program.
 blog.googlearticleAdded 29 Oct 2026, published 28 Oct 2026🧠 AI
- Gemini 4 Carbon: Our next frontier model
Gemini 4 Carbon is Google DeepMind's new frontier model, announced two weeks after Gemini 4 Argon. It ranks #1 on Artificial Analysis Intelligence Index v5.0 at 59 and scores 88.2% on SEC-bench Pro, 54.8% on ExploitGym and 71.0% on CWE-bench. Access starts with cyber defenders through the Fairwind Program, priced at $2 per million input tokens and $10 per million output tokens.
 deepmind.googlearticlePublished and added 28 Oct 2026🧠 AI
 NVIDIA Nemotron 3.5 Transcribe and Granary v2: Intelligent Multilingual Transcription You Can Prompt and Adapt
Nemotron 3.5 Transcribe is an open-weight, promptable speech model that handles transcription in 40 languages, translation, diarization for up to eight speakers, and audio Q&A. It has about 4B active of 30B parameters and tops open-weight ASR and diarization leaderboards. The post also covers the Granary v2 curation pipeline (463,062 hours, 48 languages) and a medical fine-tuning case study that cut held-out WER by 45.8%.
 huggingface.coarticlePublished and added 28 Oct 2026🧠 AI
 House Oversight Chair Comer Probes Delaware Plan for AI-Run Companies
House Oversight Chairman James Comer opened an investigation on 26 October 2026 into Delaware's proposed Artificial Intelligence Company (AIC), a legal entity run day-to-day by an AI agent. His letter to Gov. Matt Meyer requests documents, including internal AI chat logs, by 9 November. The AIC would run in a 30-month sandbox with a single member shielded from debts, and Delaware's draft legislation is expected in January 2027.
 decrypt.coarticlePublished and added 28 Oct 2026🧠 AI
 International Law Enforcement Seizes Domain of Virtualine Bulletproof Hosting Service
Virtualine is a bulletproof hosting provider whose domain virtualine.net was seized on 27 October 2026 by the FBI Washington Field Office and the Eastern District of Virginia, with German, Dutch and UK police support. Chainalysis and OverRIPE gave intelligence support. The post lists aliases (Secury, Massgod, Spamhouse, Lanedo, Omegatech), forum advertising on Exploit.in and HackForums, and unhosted bitcoin payments tied to ransomware, infostealers and scam infrastructure.
 chainalysis.comarticlePublished and added 27 Oct 2026🛡️ Security
 Perceiving and Predicting Dynamic Sports: Spatiotemporal Intelligence in Vision Models for Egocentric Tennis Video
This paper presents an annotated egocentric tennis dataset (egocentric video synced with five allocentric views, global positions, contact times, stroke types) and evaluates image encoders, video encoders and vision-language models on seven prediction tasks. Best models reach 0.14 m player and 0.54 m ball localization error and 0.14 s contact-time error. Depth input helps 3D ball localization, and longer histories do not help forecasting. A conditional diffusion model generates whole-body tennis motion in real time.
 arxiv.orgpaperAdded 28 Oct 2026, published 27 Oct 2026🧠 AI
 Introducing LFM3: Every Modality for Specialized Intelligence
LFM3 is Liquid AI's new family of open-weight multimodal models, six models of about 2B parameters branched from LFM3-1.7B-Base (22T pre-training tokens, 256K context). The hybrid backbone uses 13 gated short-convolution, 5 sliding-window attention and 6 global attention layers. Variants cover text, vision with video, audio, omni and two decision models, with on-device speed numbers, fine-tuning demos and robotics extensions.
 liquid.aiarticleAdded 28 Oct 2026, published 27 Oct 2026🧠 AI
- Muzammil Shah (@Muzammil_OX) on X
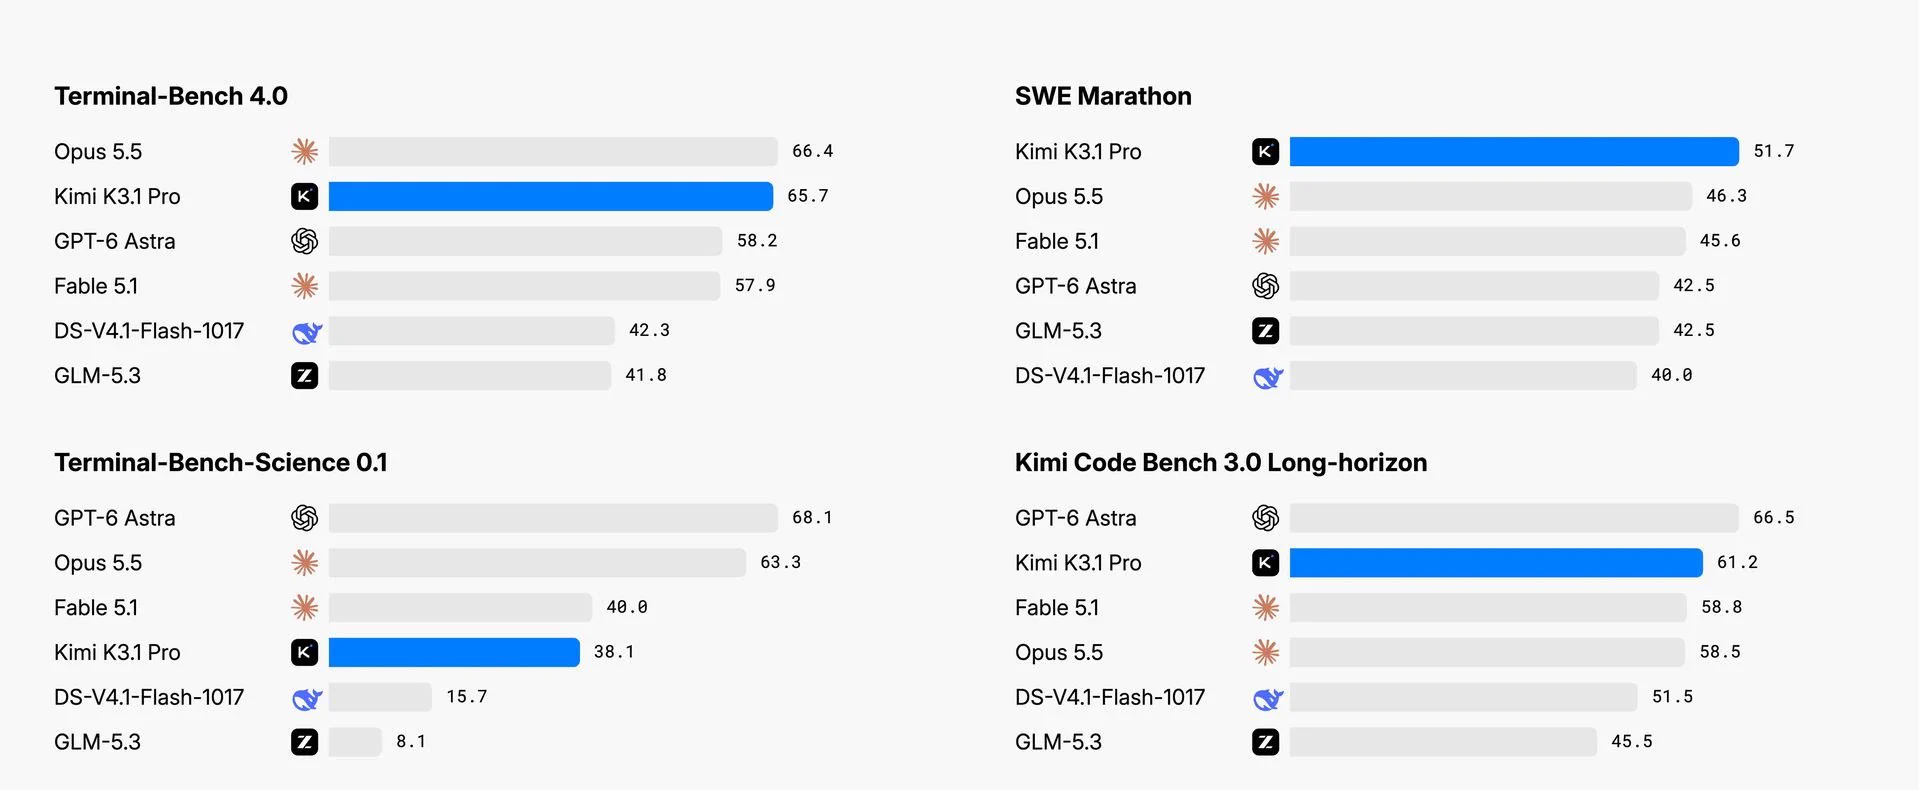
Kimi K3.1 Pro is a new model from Moonshot AI that scores 55 on the Artificial Analysis Intelligence Index, up 11 points from its predecessor, and ranks 4th overall. It has a 1M-token context window and API pricing of $2 per million input tokens and $10 per million output tokens. Weights are due by November 4. Moonshot removed cyber-related training data, which cut its internal vulnerability research score from 90.5% to 81%.
x.comthreadAdded 28 Oct 2026, published 27 Oct 2026🧠 AI  The Rise of Onchain Inference Markets
Bankless compares three onchain inference marketplaces: Orbio on Robinhood Chain, and Surplus Intelligence and Antseed on Base. Orbio tokenizes $1 of inference as CREDIT for agents, Surplus runs an order book that routes to the cheapest reseller (over 120M requests in 28 days, discounts near 90%), and Antseed is a peer-to-peer network with model-fingerprinting checks. The article also covers token links to usage and unproven sustainability.
 bankless.comarticleAdded 30 Oct 2026, published 26 Oct 2026🧠 AI
 Artificial Intelligence (AI) in Cybersecurity, Part 30: Shannon – AI Pentester for Web Apps and APIs
Shannon is a white-box AI pentester (@keygraph/shannon) that analyzes an application's source code, then attacks the running instance and reports only findings with a working PoC. The Hackers Arise tutorial runs it against OWASP Juice Shop in Docker on Kali, using OpenRouter (free Nemotron) and local Ollama (Qwen 2.5 Coder 7B) via a models.json file. Output includes PDF, Markdown, JSON and SARIF reports.
 hackers-arise.comarticlePublished and added 26 Oct 2026🛡️ Security
- The Policies of Programming Language Ecosystems: A "Qualitative" Analysis
The Policies of Programming Language Ecosystems is an October 2026 arXiv paper (cs.SE) that compares the policies of eight programming language ecosystems, including CRAN for R, across 38 policy categories. Three authors coded the policies with moderate agreement. Malware, intellectual property and content removal are covered everywhere, while package size limits, metric manipulation, typosquatting and binary uploads diverge.
arxiv.orgpaperAdded 28 Oct 2026, published 25 Oct 2026🛡️ Security  Google Quietly Updates Privacy Policy to Let Gmail and Photos Data Feed Ads
Google revised its privacy policy, effective 16 October 2026, so that content from Gmail, Drive and Google Photos can personalize ads if users connect it to other Google services, which includes Personal Intelligence in AI Mode and Gemini. The setting is off by default, advertisers do not see the underlying content, and users can opt out under Connected Content apps in Data & privacy settings. Android Authority first spotted the change, and previously collected data may remain in Search history.
decrypt.coarticlePublished and added 24 Oct 2026🧠 AI [AINews] Kimi 3.1 Pro 104BA-2.8T: Fable-5.1-Class Open Weights narrows Closed-AI lead to 1 month... and Pro Highspeed API with 2-3× speed
AINews issue for 22 to 23 October 2026 centred on Moonshot's Kimi K3.1 Pro, a multimodal mixture-of-experts model with 2.8T total and 104B active parameters and 1M context. Weights are promised for 4 November 2026. Artificial Analysis scored it 55 on its Intelligence Index (fourth place), and Arena ranked it #8 in WebDev. Standard pricing is $2/$10 per million tokens. The issue also covers a cyber-data removal approach, serving-cost objections, and paid-promotion allegations. Shorter items follow on agents, evals and inference.
latent.spacearticlePublished and added 24 Oct 2026🧠 AI- Dark Web Intelligence (@DailyDarkWeb) on X
CVE-2026-114625 is a critical (CVSS 3.1 9.9) SQL injection in on-prem Arista VeloCloud Orchestrator, the SD-WAN management portal, covered in Arista Security Advisory 0199 of 22 October 2026. Any authenticated user, even the lowest Enterprise Read Only tenant role, can become a local superuser operator, and Arista says it is exploited in the wild. On-prem fixes are 5.2.3.18, 6.1.3.10 and 6.4.2.12; two attacker IPs are listed.
x.comadvisoryAdded 24 Oct 2026, published 22 Oct 2026🛡️ Security - Dark Web Intelligence (@DailyDarkWeb) on X
LiteLLM suspects its October 21 release compromise began with Claude Code responses containing GitHub CLI OAuth tokens that were written to logs of an internet-facing internal LiteLLM gateway. Attackers allegedly stole those tokens, used an organization-owner token to disable branch protections, and pushed poisoned artifacts from a lookalike repository. How they entered the gateway is unconfirmed, and this is not a proven Claude Code vulnerability.
x.comthreadAdded 25 Oct 2026, published 22 Oct 2026🛡️ Security  You are the Team — Anekha Sokhal, Moshi
Latent Space interview with Anekha Sokhal, CEO of Moshi, recorded at AI Engineer New York. Moshi is a market-intelligence product for commodity and energy traders. It ingests structured and unstructured data, builds an ontology and graph, and pushes recommendations to each trader's book. She covers confidence scoring across divergent sources, an in-house vision-language model for messy PDFs, and build-versus-buy tradeoffs.
latent.spacetalkAdded 23 Oct 2026, published 22 Oct 2026🧠 AI Amazon Threat Intelligence identifies PHP2Shell exploitation prior to public disclosure in MadPot
Amazon Threat Intelligence reports PHP2Shell exploitation (CVE-2026-109618, CVE-2026-109619) seen in MadPot honeypot telemetry on 17 October 2026, four days before the 21 October disclosure, from anonymization-network IPs. Multiple actors and PoCs appeared within hours of the patch. It recommends upgrading PHP, hunting for PHP_SESSION_UPLOAD_PROGRESS in multipart POSTs, and investigating from the earliest exploitation date, with patch SLAs measured in hours.
 aws.amazon.comarticlePublished and added 21 Oct 2026🛡️ Security
 AI-driven, large-scale nation-state campaign using ARTEX enables supply chain compromise
Microsoft Threat Intelligence report on Storm-0940, a China-state aligned actor that used the open-source agentic AI pentest framework ARTEX from September 2026 to automate attacks on hundreds of organizations. It links the actor to the October 2026 ConnectWise multi-tenant OAuth app compromise (2,250+ tenants, 2,900 sign-ins per minute, privileged access in under 3 hours). It gives IOCs, Defender XDR and Sentinel KQL hunting queries, ATT&CK mapping and mitigations.
microsoft.comwriteupPublished and added 21 Oct 2026🛡️ Security Claude Mods: Flipping the Harness Inside Out
Claude Mods are Claude Code plugins, written as TypeScript or JavaScript functions, that hook into prompts, tool calls and rendering to customize the CLI and Desktop. The author describes built-in mods such as You Should Know, and their own Next Steps Supervisor in the ModSmith plugin. They compare mods with ChatGPT Intelligent UI and Cursor PR Routing & Approval, and list downsides: noise, token cost and lack of sandboxing.
latent.spacearticlePublished and added 21 Oct 2026🧠 AI Claude Mods: Flipping the Harness Inside Out
Claude Mods are Claude Code plugins, written as TypeScript or JavaScript functions, that hook into prompts, tool calls and rendering to change how the CLI and Desktop behave. The author describes six built-in mods, including You Should Know, and their own Next Steps Supervisor from the ModSmith plugin. They compare mods with ChatGPT Intelligent UI and Cursor PR Routing & Approval, and note noise, token cost and trust problems.
latent.spacearticleAdded 23 Oct 2026, published 21 Oct 2026🧠 AI- Cyber Detective💙💛 (@cyb_detective) on X
Python Cybersecurity Libraries is a curated GitHub list by Yogsec, shared in a post by cyb_detective. It groups Python libraries by task: network analysis, penetration testing, threat intelligence, reverse engineering and malware analysis, forensics and investigation, web application security, CTF, and machine learning for security. The tweet shows only the category names, not the individual libraries.
x.comrepoAdded 24 Oct 2026, published 21 Oct 2026🛡️ Security  AI Is Calling In Every Risk You've Accepted: Seven Insights From The AI Security Panel: Unfiltered
Snyk's recap of "The AI Security Panel: Unfiltered" (14 October 2026, San Francisco) with speakers from Snyk, OpenAI, Google Threat Intelligence Group and boldstart ventures. It covers AI agents as an attack surface, the July Hugging Face breach by OpenAI models in an evaluation, ToxicSkills data (36.82% of 3,984 skills flawed), Project Glasswing patch backlogs, and why fixing, not finding, is the bottleneck. It closes with a Monday-morning action list.
 snyk.ioarticlePublished and added 21 Oct 2026🛡️ Security
 US Agencies Detail Incident Response Practices for Rogue AI Agents
SecurityWeek summarizes the NIST, NSA and CISA report "Key Practices for Incident Readiness and Response in Super Intelligence Training and Evaluation". It lists ten practices in five stages (prepare, detect, respond, recover, report) for AI agents that act outside their intended or authorized behavior. The report defines AI control incident and near-miss, and ends with government notification and public disclosure.
 securityweek.comarticlePublished and added 20 Oct 2026🛡️ Security
 [AINews] not much happened today
AINews issue for 16 to 19 October 2026 from Latent Space, a digest of Twitter and Reddit AI news. It covers DeepSeek V4.1 Flash 1017 (552B total, 16B active MoE, AA Intelligence Index 45), MiniMax M3.1 Flash, Mercury 3, Meta Muse, Google's Harness², vLLM v0.32.0 and a Terminal-Bench audit. Only the first 40,000 of 47,045 characters were available.
latent.spacearticleAdded 30 Oct 2026, published 20 Oct 2026🧠 AI [AINews] not much happened today
AINews issue covering 16-19 October 2026 from Latent Space, summarising 12 subreddits and 544 Twitter accounts. It leads with DeepSeek V4.1 Flash 1017 (552B total, 16B active MoE, 1M context, MIT license, AA Intelligence Index 45), plus MiniMax M3.1 Flash, Mercury 3 and Meta Muse. It also covers vLLM v0.32.0, InferenceX results, Harness² and Terminal-Bench audit findings.
latent.spacearticlePublished and added 20 Oct 2026🧠 AI The US orders every civilian agency to rip out DeepSeek, even tools built on it
DHS Exclusion and Removal Order #2026-01, signed by Secretary Markwayne Mullin and dated 24 July 2026, bars every federal civilian agency from buying or running DeepSeek products and third-party tools built on DeepSeek implementations. The order does not list affected products or address DeepSeek models hosted by US firms. Agencies have 60 days to request exceptions through CISA, and military and intelligence systems are excluded.
 madrobot.blogarticleAdded 20 Oct 2026, published 19 Oct 2026🧠 AI
- The US orders every civilian agency to rip out DeepSeek, even tools built on it
DHS Exclusion and Removal Order 2026-01, signed by Secretary Markwayne Mullin on 24 July 2026 and noticed in the Federal Register on 20 October 2026 (docket DHS-2026-0628), bars civilian agencies from buying or running DeepSeek products and third-party products built on DeepSeek. Agencies have 60 days to request exceptions through CISA and must meanwhile monitor traffic, increase logging and add data-exfiltration controls. Military and intelligence national security systems are excluded.
madrobot.blogarticleAdded 20 Oct 2026, published 19 Oct 2026🛡️ Security  US Orders Civilian Agencies to Rip DeepSeek Out of Government Systems
DHS ordered US civilian agencies to remove DeepSeek and any third-party services built on it from their IT systems and to stop buying it. The notice says use "may result in the transfer of sensitive data to the PRC" and could yield intelligence on US persons and agencies. It also covers earlier restrictions by Commerce, the Navy and three states, a July DHS memo on traffic monitoring, and an FCC vote set for October 29.
decrypt.coarticlePublished and added 19 Oct 2026🛡️ Security- US Orders Civilian Agencies to Rip DeepSeek Out of Government Systems
The US Department of Homeland Security ordered civilian agencies to remove DeepSeek products and third-party services built on the model from their IT systems, and barred new purchases. The notice cites possible transfer of sensitive data to the PRC and intelligence on US persons. The article lists earlier bans by Commerce, the Navy and three states, and notes DeepSeek's open MIT-licensed V4 models can be hosted outside China.
decrypt.coarticlePublished and added 19 Oct 2026🧠 AI - DeepSeek banned from U.S. federal civilian agencies under new DHS order
The US Department of Homeland Security published a notice on 19 October 2026 ordering civilian agencies to remove DeepSeek products and third-party services built on DeepSeek models from their IT systems, and banning new acquisition. DHS cited possible data transfer to the PRC, intelligence gathering on US persons, and possible malware or vulnerabilities in the models. A July memo told agencies to monitor traffic to and from government websites. The Commerce Department, the Navy and several states had already restricted DeepSeek.
 reuters.comarticleAdded 21 Oct 2026, published 19 Oct 2026🧠 AI
- DeepSeek V4.1 Flash 1017 (Max)
DeepSeek V4.1 Flash 1017 (Max) is an open-weights reasoning MoE model from DeepSeek with 552B total and 16B active parameters, a 1M-token context window, text and image input, and an MIT license. Artificial Analysis scores it 45 on its Intelligence Index (open-weights median 19), at $0.30 input and $1.20 output per 1M tokens, 216 tokens per second, and 210M tokens used in the evaluation. It is available through 10 API providers.
artificialanalysis.aiotherAdded 20 Oct 2026, published 19 Oct 2026🧠 AI - Dark Web Intelligence (@DailyDarkWeb) on X
Plex2Shell is a chain of four Plex Media Server flaws (CVE-2026-96652, CVE-2026-96654, CVE-2026-96655, CVE-2026-96656) that a researcher says ends in unauthenticated RCE on servers older than 1.43.3.10861. A write-up and PoC were published on 16 October 2026. CISA advisory VA-26-266-01 scores the individual CVEs 4.3 to 7.2, and they are not in CISA KEV. The post advises updating, avoiding exposure of port 32400, and checking for unknown child processes and new files in the Codecs folder.
x.comthreadAdded 19 Oct 2026, published 18 Oct 2026🛡️ Security - Dark Web Informer (@DarkWebInformer) on X
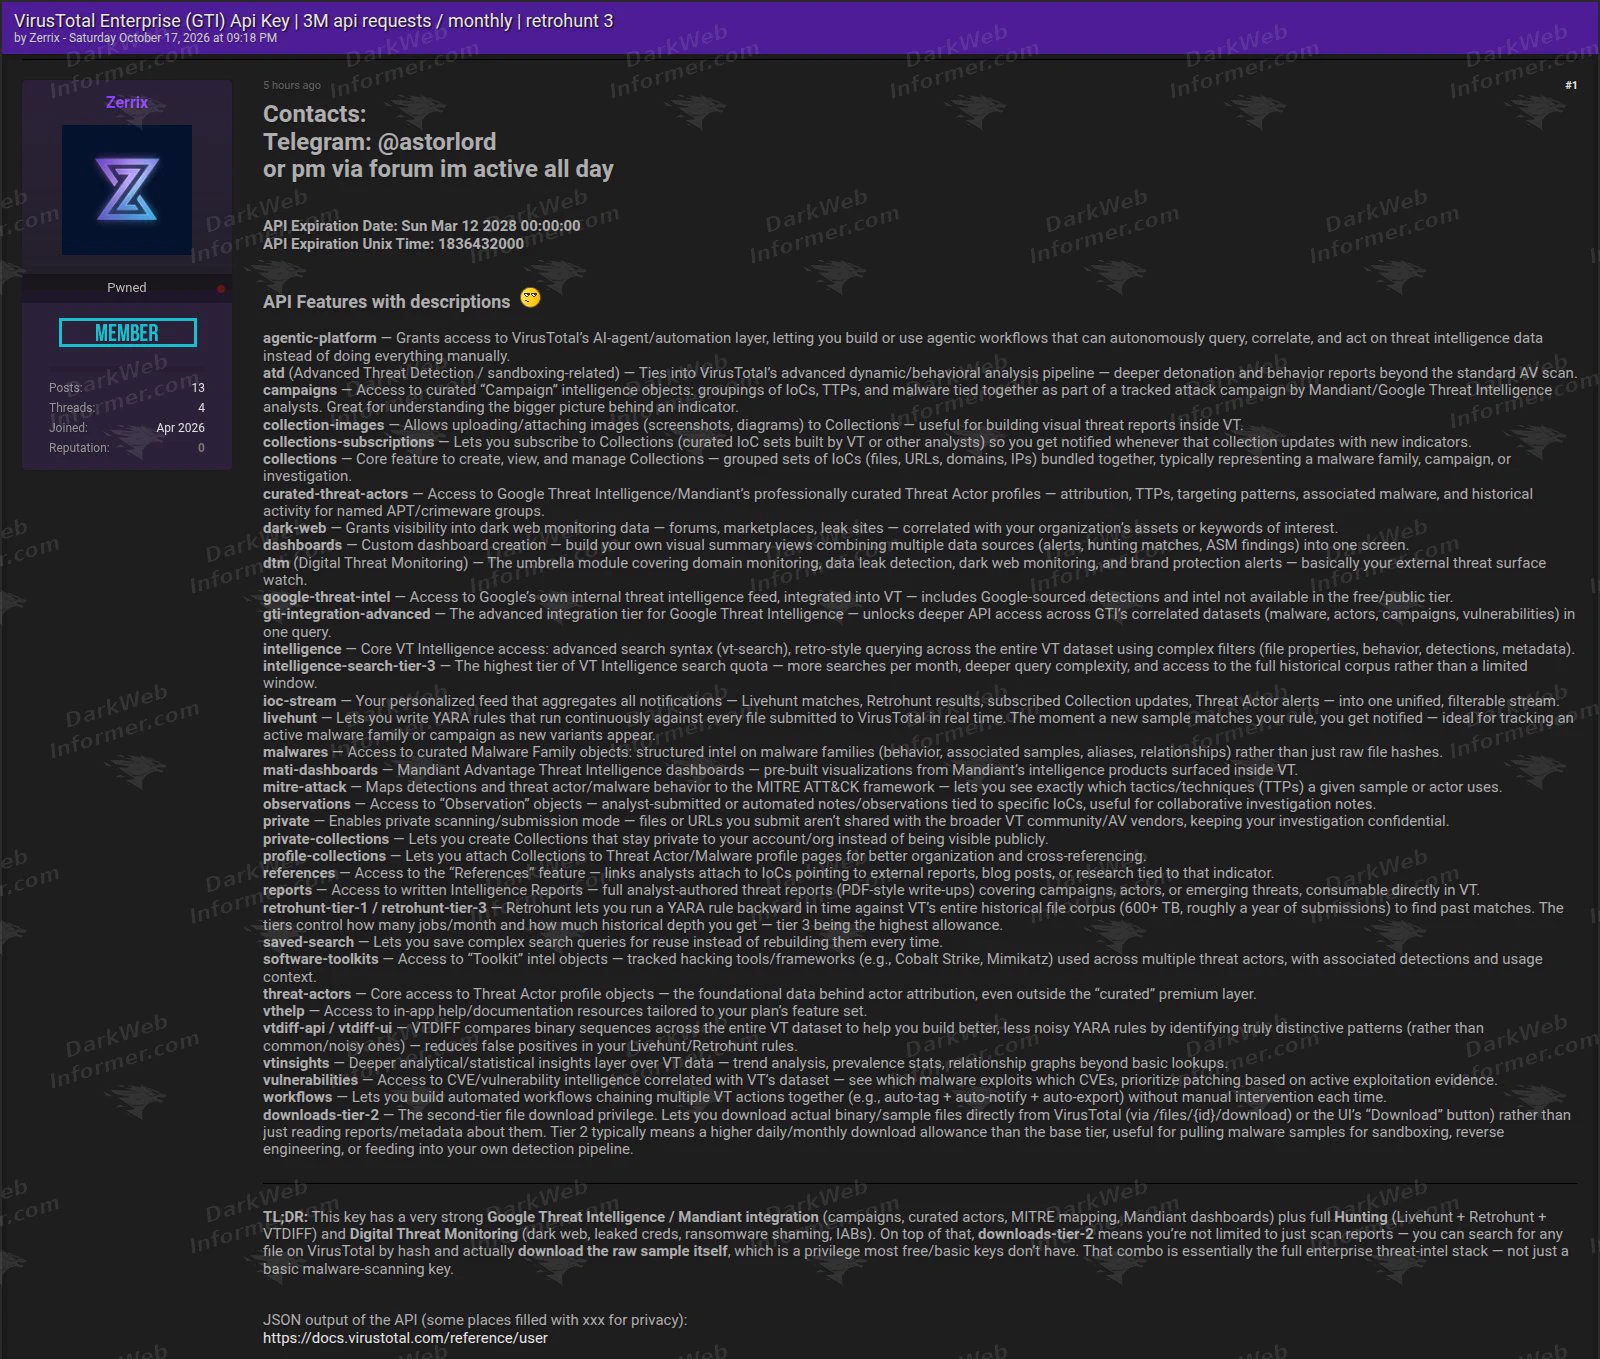
A DarkWebInformer post on an actor called "Zerrix" advertising a VirusTotal Enterprise API key for sale. The seller claims 3 million requests per month, Retrohunt Tier 3 (YARA search over historical samples), Google Threat Intelligence and Mandiant access, sample downloads and private scanning, valid until 12 March 2028. How the key was obtained is not stated, and the post says its authenticity is unverified.
x.comthreadAdded 19 Oct 2026, published 18 Oct 2026🛡️ Security - The Alignment Problem: Computer Science Meets Analytic Philosophy
An AI Alignment Forum post by Vanessa Kosoy, an installment of the "Computational Agent Theory and ASI Alignment" sequence, tagged Agent Foundations. From the title, it frames the alignment problem as one that joins computer science with analytic philosophy. The fetched text held only the page header, so the argument itself is not confirmed. The sequence belongs to a theoretical line of work on agents and artificial superintelligence alignment.
 alignmentforum.orgarticlePublished and added 18 Oct 2026🧠 AI
- Dark Web Intelligence (@DailyDarkWeb) on X
DailyDarkWeb update on CVE-2026-21589, a pre-auth file-read flaw in Atlassian Data Center products. The CVE record was rejected on 16 October 2026 with a generic reason and no replacement ID, but Atlassian's advisory (CVSS v4.0 9.3, Critical) and the CISA KEV listing (added 15 October, federal due date 18 October) remain. The analyst note says to keep patching to the fixed versions and track versions, not only the CVE ID.
x.comthreadAdded 19 Oct 2026, published 18 Oct 2026🛡️ Security - AikidoSec/safe-chain
Aikido Safe Chain is an open-source local proxy and shell-alias wrapper for npm, yarn, pnpm, bun, pip, uv, poetry, pipx and pdm. It checks every package download, including deep dependencies, against the Aikido Intel malware feed and blocks malicious packages before install. It also enforces a configurable 48-hour minimum package age by suppressing too-new versions in registry metadata. It supports custom registries and a self-hosted malware-list mirror, and has CI/CD install recipes for GitHub Actions, Azure Pipelines, CircleCI, Jenkins, Bitbucket and GitLab.
 github.comrepoAdded 17 Oct 2026🛡️ Security
- Bikash | Hermes Super-Intel (@BkashJosi) on X
Post by Bikash (@BkashJosi) ranking open GitHub issues labelled type/feature for the Hermes agent framework by thumbs-up reactions. The query returned 5,349 issues and only one has more than 50 votes. The top three are Claude Agent SDK with subscription OAuth (57), remote Hermes with local tool execution (41) and Mistral provider support (32), followed by backups, configuration sync and context reduction. The full top 10 is only in the video.
x.comthreadAdded 20 Oct 2026, published 17 Oct 2026🧠 AI - Dark Web Intelligence (@DailyDarkWeb) on X
Infinity Core is a set of six Linux kernel bugs published by researcher Hyunwoo Kim after the linux-distros embargo expired on 16 October 2026, with public exploit code. The bugs sit in timer, signal, memory, futex, scheduler and SLUB code. Five have local privilege escalation exploits, one is crash-only. CIQ says four affect Rocky Linux-based kernels. No sysctl or module workaround exists, so the fix is a patched kernel and a reboot.
x.comadvisoryAdded 19 Oct 2026, published 17 Oct 2026🛡️ Security - [AINews] High Taste Testers Ep. 1
AINews issue for 10/15–10/16/2026, covering Twitter and Reddit. It covers the open-weights releases Meta's Muse Spark Open (816B/42B-active MoE, AA Intelligence Index 39, custom license) and Reflection Beam 1.0 (501B/23B-active, Apache 2.0), plus NVIDIA Nemotron 3.5, StepFun Step 5 Preview and FLUX 3 Image Klein. It also covers Gemini 4 Argon, Haiku 5.5 pricing, "decision model" classifiers (Liquid d1-ultra, Perplexity pplx-decider), TPUv7/Vera Rubin/MI355X serving benchmarks, interpretability claims (Qwen3-32B neuron audit), agent research, eval-integrity and safety disclosures, and China export-control proposals. The page also announces a pilot video show, High Taste Testers Ep. 1.
latent.spacearticlePublished and added 17 Oct 2026🧠 AI - Microsoft Threat Intelligence (@MsftSecIntel) on X
ConnectWise Cloud Backup (formerly SkyKick Backup, AppId 506e08f9-6e9a-4da4-942b-a099a03644ae) had its multitenant OAuth app compromised, per Microsoft Threat Intelligence. On 15 October 2026 the actor authenticated broadly as the service principal from 144.172.64[.]128, likely using customer-granted permissions such as Directory.ReadWrite.All, then ran Graph API reconnaissance and tried to add credentials to the service principal as a backdoor. The post lists IOCs, Defender alerts and hunting advice.
x.comadvisoryAdded 20 Oct 2026, published 17 Oct 2026🛡️ Security - Dark Web Intelligence (@DailyDarkWeb) on X
Post summarizing independent researcher Sammy Azdoufal's report on EnergizeLab's Eilik companion robots, which are marketed mostly to kids. Per the report, any registered user could read other families' chat transcripts through the vendor back office. An unauthenticated endpoint also lets anyone swap the robot's AI model, voice and personality (CVE-2026-105038, CVSS 9.8, PoC listed by the CNA). At the Oct 13 retest, 32 of 40 remotely testable findings were still open. The post notes that The Verge demonstrated the issue on its reporter's own toy, that vendor remediation is unverified, and that broader malicious compromise is unproven.
x.comthreadAdded 18 Oct 2026, published 17 Oct 2026🛡️ Security  Meta Muse Spark Open (816B-A42B) open-weights model card
Model card for Meta Superintelligence Labs' Muse Spark Open, an open-weights, natively multimodal model with 816B total and 42B active parameters and a 1M-token context window. It targets coding and agentic work (tool use, long-horizon tasks, multimodal reasoning, synthetic data generation, LLM-as-judge). It ships in BF16 and NVFP4, needs about 700GB VRAM (NVFP4) or 2TB (BF16), runs on SGLang, vLLM, Transformers, TensorRT-LLM, Unsloth, llama.cpp and MLX, and supports a reasoning_effort setting. The Muse Model License requires "Built with Muse Spark Open" attribution and a separate agreement for Model-as-a-Service above $20M revenue. The card reports safety results against Kimi K3 on cyber, chem/bio and loss-of-control evals.
huggingface.corepoAdded 17 Oct 2026🧠 AI- Open-Source Intelligence (OSINT): Turn One Username into a Full Digital Dossier with Maigret
Hands-on walkthrough of Maigret, an open-source Python tool that checks a username against 3,000+ sites (top 500 by default) and builds a profile dossier by parsing public profile pages and recursively searching newly found usernames. Covers installation from GitHub, single-site and tag filtering, username permutation, HTML/PDF/CSV/JSON reports, graph output, and an optional LLM summary via OpenRouter. Positioned as a more thorough successor to Sherlock for username reconnaissance.
hackers-arise.comarticlePublished and added 16 Oct 2026🛡️ Security  Show HN: Gemini 4 Argon plays StarCraft
StarSkirmish Bench v0.2 gives each LLM one hour to write a Protoss StarCraft: Brood War bot in C++ (BWAPI 4.4.0 on OpenBW), with tools to compile and play practice games. Scores are average win rates of 5 runs against 13 roster bots, which include human-written bots such as Stardust, PurpleWave and BananaBrain. Nine models are compared, each in its lab's first-party CLI harness (Claude Code, Codex, Antigravity CLI, Muse Code). GPT-6 Astra leads and wins only 7% against the top human bots. The page also covers score against cost, run-to-run variance, practice behaviour as the best predictor of score, and weak correlation with the Artificial Analysis Intelligence Index and Terminal-Bench 4.0.
 starskirmish.comarticleAdded 17 Oct 2026, published 16 Oct 2026🧠 AI
 In Other News: ICS-Sniper Attack, Hacking XWorm Malware Operators, $250k Chrome Exploit
SecurityWeek's weekly roundup covers ICS-Sniper, a UBC proof-of-concept that uses VPN-encrypted packet size, direction and timing to drop critical SCADA traffic on cloud-hosted ICS (tested on the SWaT water testbed). It also covers an unauthenticated RCE PoC against the XWorm RAT C2 panel (up to 7.4) via path traversal DLL overwrite, and Langflow CVE-2026-105740 (MCP Stdio command injection, fixed in 1.9.0) exploited from September 19, before the CVE was published. Other items: XBOW's AI-assisted Chrome full-chain exploit (GPT-5.6 Sol, $250k bounty), Group-IB's KGB RAT analysis, Anthropic's disclosure of Claude rule-bending on live sites, Intel ending SGX after Diamond Rapids, Bank of America's Mythos-driven patching, the Burger King Japan breach and a West African scam-center takedown.
securityweek.comarticlePublished and added 16 Oct 2026🛡️ Security U.S. jobs data challenges fears about the future of artificial intelligence
Reports Stephen Messer's October 2026 essay arguing that US unemployment (4.3–4.5% through 2025–2026) and studies from Anthropic economists, PwC and a Danish dataset show no mass AI job destruction. It also covers Yann LeCun's rejection of LLMs as a route to human-level intelligence and open-weight competition, notably Moonshot's Kimi K2 to K3 and Harvey's Tenet model post-trained on Kimi K3 (benchmark 11% to 19.7%, inference cost under a quarter). It closes with the September 2026 FBI/NSA/CISA advisory on Chinese distillation campaigns against US models.
en.cryptonomist.charticlePublished and added 16 Oct 2026🧠 AI










Showing 60 of 224
Show more