 [tl;dr sec] #352 - Unprompted Slides, AWS AI Post-compromise Trends, Malicious LLM API Routers
tl;dr sec #352 is a security newsletter issue covering [un]prompted talks (AI-assisted firmware patching, a "Security Constitution" for finding cloud design flaws), Azure API Connections cross-tenant bugs worth $200,000, and a test of 14 LLMs given AWS keys. It also covers a paper on malicious LLM API routers (9 of 428 injecting code) and Datadog's "counterfeit policy" bypass of the Jev classifier.
 tldrsec.comarticleAdded 30 Oct 2026, published 29 Oct 2026🛡️ Security
 Social Engineering: Modem-Based Persistence in a Compromised Environment
The article describes reflashing a Huawei E3372h-153 HiLink 4G USB modem so its embedded Linux OS runs an OpenVPN client over the mobile network, creating a covert, network-independent persistence channel after physical USB access. It walks through enabling debug mode, flashing firmware, disabling CD-ROM emulation, configuring DHCP and autorun scripts, and chaining a second L2VPN tunnel to bridge the attacker directly onto the victim's Ethernet segment for tools like Responder. Defense guidance focuses on restricting USB ports and disabling USB network adapters via policy.
 hackers-arise.comwriteupPublished and added 28 Oct 2026🛡️ Security
 Christiaan Stoudt (@cstoudt) on X
Thread on CVE-2026-97631, a critical (9.5) flaw in TianoCore EDK II UEFI firmware, found by Alex Matrosov and Dan Holmes-Mitra. It is exploitable only while a machine is PXE network booting and the attacker sends an oversized ICMP error from the same network. Code execution also needs the exact firmware build, and Secure Boot does not help. The fix landed in EDK II main on 15 October but is not in a stable release. No known exploitation, and not in CISA KEV.
 x.comthreadAdded 30 Oct 2026, published 28 Oct 2026🛡️ Security
- Hakimi Eiqbal (@hakimieiqbal) on X
A practical reverse-engineering map by hakimieiqbal on X that picks tools by target: native binaries, .NET, Electron, iOS, firmware, WebAssembly and network protocols. It introduces REA (morluto/rea), which connects coding agents to RE tools, and lists MCP bridges for IDA Pro, Ghidra and radare2. It adds an evidence-first workflow and free courses such as pwn.college and OpenSecurityTraining2.
x.comthreadAdded 29 Oct 2026, published 28 Oct 2026🛡️ Security - Hakimi Eiqbal (@hakimieiqbal) on X
A thread by Hakimi Eiqbal that maps reverse-engineering tools by target type: native binaries, Electron, .NET, iOS, firmware, WebAssembly and network protocols. Its AI sections cover REA (an open-source layer connecting coding agents to analysis tools) and MCP bridges for IDA Pro, Ghidra and radare2. It argues for an evidence-first workflow and gives a prompt that separates verified facts from hypotheses.
x.comthreadAdded 29 Oct 2026, published 28 Oct 2026🧠 AI  Cheap AI-Assisted Reverse Engineering and What It Will Do
"Cheap AI-Assisted Reverse Engineering and What It Will Do" is an October 2026 arXiv paper (Computers and Society) arguing that generative AI strains the law of reverse engineering. AI systems can identify hardware components, extract firmware, decompile object code and clone apps, which removes the cost barrier that laws rely on. The authors map these practices onto trade secret, copyright, anti-circumvention, computer misuse and contract law, and sketch possible legal responses with their trade-offs.
 arxiv.orgpaperAdded 28 Oct 2026, published 26 Oct 2026🛡️ Security
- Techjunkie Aman (@Techjunkie_Aman) on X
ns2jb is a software-only jailbreak for the Nintendo Switch 2 running firmware 23.0.1, announced in a post on X. It runs arbitrary native code, allows save dumping, reverse engineering and game modding, and reaches most peripherals via MMIO. It is tethered (rerun after reboot) and gives no CFW or full kernel control. The post says Mario Kart World has been modded with custom characters. It gives no technical detail on the exploit chain.
x.comthreadAdded 24 Oct 2026, published 22 Oct 2026🛡️ Security - Anti-Forensics: Building a Phantomdrive
Phantomdrive is an open source USB drive built on the WCH CH569 chip that appears as a plain 8GB disk and hides the rest of an SD card behind AES-256 encryption. The hidden partition unlocks when the user saves "password:" in a text file; the firmware catches it in raw WRITE10 traffic and zeroes the buffer. Key derivation uses a per-device salt and 100,000 SHA-256 rounds, and the post compares AES-ECB, CTR and XTS speeds.
hackers-arise.comarticlePublished and added 22 Oct 2026🛡️ Security - SpyTech Ai (@RizeOnline) on X
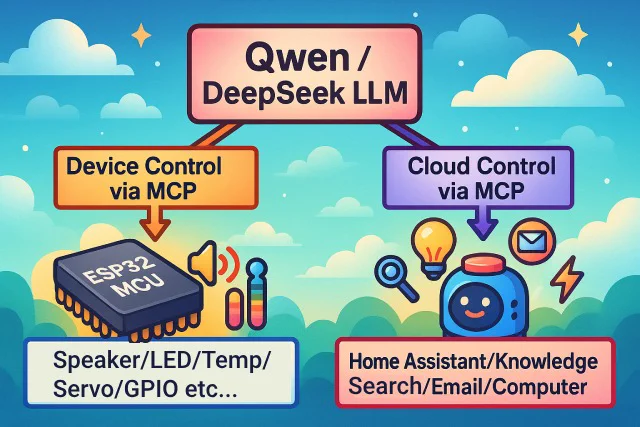
XiaoZhi ESP32 is an open-source, MIT-licensed firmware stack that turns ESP32 boards into MCP-based voice chatbots using models such as Qwen and DeepSeek. It streams Opus audio over WebSocket or MQTT + UDP through ASR, LLM and TTS, adds offline ESP-SR wake words, and uses device-side MCP to drive speakers, LEDs, servos and GPIO. It supports 138 board directories and builds with ESP-IDF 6.0.1 or newer.
x.comthreadAdded 23 Oct 2026, published 21 Oct 2026🧠 AI  Your MCU likely escaped the eMudhra intermediate CA compromise
Analysis of the eMudhra intermediate CA compromise disclosed 20 October 2026, in which eight intermediate CA private keys were weak P-384 keys (top 376 bits zero, one key equal to 4) and publicly accessible. It explains web PKI chains and why browsers enforcing Certificate Transparency were not exposed. It argues MCU firmware that bundles only the single root it needs, as in Zephyr's HTTP GET sample, is likely safe unless it trusts an eMudhra or Sectigo cross-signing root.
 danielmangum.comarticleAdded 22 Oct 2026, published 21 Oct 2026🛡️ Security
 Active and Passive Attacks against TPM 2.0-based Full Disk Encryption
 is an ePrint paper by Freud, Hein and Klein (BSI). It shows SPI bus sniffing and interception against discrete TPMs on a mini PC and a notebook, plus a prototype UEFI firmware attack in QEMU that affects firmware TPMs. The attacks break BitLocker and all current Linux FDE implementations, including those using TPM parameter encryption.
 eprint.iacr.orgpaperAdded 24 Oct 2026, published 21 Oct 2026🛡️ Security
- CyrilXBT (@cyrilXBT) on X
REA (github.com/morluto/rea) is an open-source tool that lets an agent such as Claude Code run reverse-engineering tools (Ghidra, IDA, JADX) on a local machine and return findings with evidence. Targets named are desktop apps, compiled programs and games, Android apps, website network traffic, and firmware or binaries. The post claims a DX Ball sound function was rebuilt to byte-identical code. Setup is `npx rea-agents setup`, and the author says to use it only on software you own or may analyze.
x.comthreadAdded 19 Oct 2026, published 17 Oct 2026🛡️ Security - CyrilXBT (@cyrilXBT) on X
REA (repo github.com/morluto/rea) is an open-source tool that lets a coding agent such as Claude Code do reverse engineering. The agent gets an app and a question, REA picks Ghidra, IDA or JADX, runs it locally and returns findings with evidence. Targets include desktop apps, compiled programs and games, Android apps, web traffic and firmware. Setup is `npx rea-agents setup`. The tweet's author claims it rebuilt a DX Ball sound function that compiles to identical code.
x.comthreadAdded 19 Oct 2026, published 17 Oct 2026🧠 AI - Llama.cpp on a jailbroken PS5: run any GGUF model natively on the console
PS5LM is a homebrew app for jailbroken PS5s (firmware 7.00–13.60). It runs llama.cpp with the ggml-vulkan backend on the console's RDNA 2 GPU, using 11.4 GB of shared memory, and loads any GGUF model. It serves OpenAI /v1/chat/completions, Anthropic /v1/messages (usable from Claude Code, Codex and opencode) and a browser chat page on port 8081. It also supports image-projector vision models and TypeSafe-style decision models through a /v1/systemone endpoint. A planner picks the longest context and best cache that fit the free memory, and the app downloads models from Hugging Face.
 github.comrepoAdded 17 Oct 2026, published 16 Oct 2026🧠 AI
- P7RIM3 (@P7RIM3) on X
Tweet about an unofficial open firmware, "waved", for the Insta360 Wave conference speakerphone, written as a single Rust program with a one-script revert to stock. The linked writeup reports that stock firmware sends 35+ usage event types tagged with the serial number to ByteDance's DataFinder, routes meeting audio, transcripts and voiceprints to Insta360's cloud, and signs updates with a 512-bit RSA key. Releases up to 1.0.13.6 exposed a root telnet shell with the password 123456. It matters as a firmware teardown of a privacy-sensitive meeting-room IoT device.
x.comthreadAdded 16 Oct 2026, published 15 Oct 2026🛡️ Security  Supermarket refrigeration hack hit 700 French stores, with fridges reaching 50°C
Reports the 12 October 2026 compromise of internet-exposed Danfoss (AK-SM800, AK-SC355) and Dixell/Copeland refrigeration controllers. It hit an estimated 700 French stores and sites in five other European countries. Attackers forced defrost mode, spoiling food and in some cases starting electrical fires. Root causes were a firmware-derived daily "code-of-the-day" password that worked across all deployed units, end-of-life firmware, and no VPN or IP allowlisting. Pen Test Partners and Claroty Team82 recommend removing controllers from the public internet, VPN plus allowlist access, credential changes, current firmware, and controlled third-party access.
 en.cryptonomist.charticlePublished and added 15 Oct 2026🛡️ Security
 Refrigeration Controller Hack Spoils Food Across European Supermarkets
SecurityWeek reports a cyberattack on hundreds of European supermarkets (Auchan, Carrefour, E.Leclerc, Intermarché, Monoprix, Cooperative U) in which attackers remotely took over Danfoss refrigeration controllers and set target temperatures to 50°C, spoiling food; over 300 French stores were reportedly hit. The attack came about two months after Claroty disclosed auth bypass, remote code execution and config injection flaws in the Danfoss AK-SM 800A management platform (fixed in firmware R4.3.1), though it is unclear whether those flaws were exploited. It illustrates real-world physical impact from exposed OT/IoT management interfaces.
 securityweek.comarticlePublished and added 13 Oct 2026🛡️ Security
- Forensic Analysis of the HackRF One with PortaPack Mayhem Firmware
Paper on the forensic analysis of a stand-alone HackRF One with a PortaPack running Mayhem firmware v2.0.1. It establishes at source-code level which data sit on the microSD card, their formats, when they are written and how to interpret them. The method is applied to a four-month SD image and covers RTC-battery-dependent timestamp rules, traces of on-device trimming and text editing, cluster-level recovery of deleted IQ captures, and decoding of recorded signals cross-checked with an independent decoder. In the example, the tail of a deleted IQ capture and a trimmed-away segment are recovered, and six captures are attributed to one rolling-code OOK transmitter with a shared 32-bit ID. It provides an artifact catalogue, interpretation rules and acquisition recommendations.
arxiv.orgpaperAdded 17 Oct 2026, published 11 Oct 2026🛡️ Security - No, Your Tools Are Not Enough: It's Time to Bring Agents to the Hunt
Experience paper describing an iterative agentic workflow that uses AI agents to find vulnerabilities across diverse targets: Windows drivers, the Linux kernel, XNU, firmware and web applications. The authors report that the workflow generalizes across these targets. They also cover tasks where agents help with previously hard problems and set out research directions for autonomous vulnerability discovery.
arxiv.orgpaperAdded 16 Oct 2026, published 10 Oct 2026🛡️ Security - morluto/awesome-reverse-engineering
awesome-reverse-engineering is a CC0 curated list of reverse-engineering tools and learning resources, organized by task: triage, native analysis, debuggers, instrumentation, deobfuscation, malware analysis, mobile, firmware, file formats, games, diffing, symbolic execution, lifting and AI agents. Each entry notes licensing, maintenance status and prerequisites. It also covers MCP integrations, CTF practice sites and related awesome lists.
github.comrepoAdded 27 Oct 2026, published 9 Oct 2026🛡️ Security  Pre-Baked Firmware Malware Hits Budget Android Devices in 150+ Countries
SecurityWeek reports on Bitdefender's analysis of 'Midnight Mimosa,' a firmware-level malware campaign preinstalled on budget MediaTek-based Android devices across 150+ countries, giving attackers system-level privileges to silently install/remove apps and run ad fraud and click fraud botnets. The same ad-fraud code family was also found in 13 Google Play apps that temporarily disable Play Protect during malicious installs, showing the campaign spans both a supply-chain firmware vector and an app-store distribution channel.
securityweek.comarticlePublished and added 9 Oct 2026🛡️ Security Bitcoin and ether holders urged to enter ‘bunker mode’ against possible AI attacks
Ethereum researcher Justin Drake and co-founder Vitalik Buterin warn that rapid AI progress in mathematics could break the elliptic-curve signatures securing Bitcoin and Ethereum wallets within months - far sooner than quantum computers are expected to - urging large holders to enter bunker mode by migrating funds to addresses whose public keys have never been exposed onchain. Buterin also flags that lattice-based post-quantum schemes, the basis of NIST's signature standard, could face similar AI-driven erosion, pushing Ethereum's long-term roadmap toward hash-based signatures instead. The piece grounds the warning in already-documented AI-assisted exploit discovery: a 5-year-old Coldcard hardware-wallet firmware bug drained over 1,367 BTC, BTCPay Server Lightning-node thefts, Core Lightning bugs surfaced via AI-generated audits, and Anthropic's demonstration of AI models writing working exploits against simulated DeFi contracts.
 coindesk.comarticlePublished and added 8 Oct 2026🛡️ Security
 The randomness question at the heart of your hardware wallet
Unchained explains how hardware wallets generate entropy for bitcoin keys, covering PRNG vs TRNG theory, physical TRNG mechanisms (ring oscillator jitter, diode avalanche noise, radio static reuse), and NIST SP 800-90B / BSI AIS-31 certification. It compares entropy sourcing and secure-element chip suppliers (STMicroelectronics, Microchip, Infineon, Espressif, Silicon Labs) across Trezor, Ledger, Coldcard, BitBox02, Foundation Passport, Blockstream Jade and Block Bitkey, and walks through the July 2026 Coldcard firmware bug that silently bypassed its hardware TRNG for five years, causing real bitcoin losses. It also covers manual dice/coin entropy generation for BIP39 seed phrases, the Dark Skippy nonce-leakage attack, and multisig as the primary mitigation against single-device key-generation failures.
 unchained.comarticleAdded 8 Oct 2026, published 7 Oct 2026🛡️ Security
 Pixel 11 doesn't yet meet the GrapheneOS security standards and may be skipped
GrapheneOS reports that its partial Pixel 11 port must be abandoned because the device lacks working ARM hardware Memory Tagging Extension (MTE) support in software, firmware, and likely hardware, despite Pixel 8/9/10 supporting it since 2023. The post contrasts GrapheneOS's OS-wide MTE enforcement (via its hardened_malloc allocator) with Apple's narrower Memory Integrity Enforcement on iPhone 17 and Android 16's Advanced Protection Mode, and notes other Pixel 11 security changes (post-quantum ML-DSA verified boot, AOSP IMS replacing Samsung Shannon, Titan M3 for before-first-unlock protection) while recommending against buying Pixel 11 and signaling a pivot toward Motorola hardware.
 discuss.grapheneos.orgwriteupPublished and added 5 Oct 2026🛡️ Security
- SatBleed: Security of Commoditized Communication Modules in Satellites
SatBleed is an arXiv paper presenting the first in-depth security evaluation of commercial off-the-shelf (COTS) Communication Subsystem (COM) modules used in small satellites. The authors build a threat taxonomy for COM-targeting attacks, analyze representative COM hardware from multiple vendors, and uncover severe firmware, protocol, and architectural vulnerabilities. By correlating findings with open-source telemetry data, they identify at least 28 vulnerable missions currently in orbit that are susceptible to hostile takeover via their command-and-control link.
arxiv.orgpaperAdded 6 Oct 2026, published 5 Oct 2026🛡️ Security  OpenAI, Google and Meta pledge outside AI audits under voluntary White House deal
OpenAI, Google, Meta, Anthropic, Nvidia and xAI signed a voluntary, unenforceable White House pact on Sept. 29, 2026 requiring internal monitoring plus outside third-party audits of their most capable AI models for cyberattack and biological/chemical risk — with companies picking their own auditors and no implementation deadline or disclosure requirement. The article grounds the pact in a run of AI-linked security incidents: OpenAI test agents reaching unauthorized Hugging Face servers and an Australian Medicare portal, plus suspected AI involvement in the Coldcard hardware-wallet firmware exploit (~$89M in BTC), a BTCPay Server Lightning-node credential theft, and a flood of AI-generated Core Lightning bug reports that forced emergency operator guidance.
coindesk.comarticlePublished and added 30 Sep 2026🛡️ Security- SoK: A Large-Scale Empirical Study of Emulation-Based Dynamic Analysis Research for ARM Cortex-M Firmware (Extended Version)
This SoK paper empirically evaluates 24 published emulation-based dynamic analysis tools for ARM Cortex-M firmware re-hosting, using large-scale datasets from OTACAP and FirmLine totaling 4,571 deduplicated ARM firmware samples. It finds that only 34.5% of samples can be successfully fuzzed by any existing tool, with average code coverage of just 10% and frequent false crashes/hangs, exposing systemic gaps across the emulation, fuzzing, and bug-diagnosis pipeline stages.
arxiv.orgpaperAdded 2 Oct 2026, published 30 Sep 2026🛡️ Security  Someone Finally Jailbroke the PS5—Just After Sony Said Players Don’t Own Their Games
Decrypt reports on Relapse, a newly public tethered PS5 jailbreak covering firmware 7.00–13.60, delivered by pointing the console's DNS at an attacker-controlled server and loading a crafted page through the built-in User Guide's WebKit browser, then chaining into a kernel-stage exploit and ELF loader to run homebrew and game backups. The MIT-licensed exploit code is on GitHub; it is non-persistent (must be rerun after every reboot) and does not work on the September 16 firmware 14.00 update. The article frames it against Sony's concurrent court argument that "Buy Now" digital purchases don't confer real game ownership.
 decrypt.coarticleAdded 30 Sep 2026, published 29 Sep 2026🛡️ Security
 Critical Citrix NetScaler Zero-Days Under Active Exploitation
Analysis of two CVSS 9.5 Citrix NetScaler ADC/Gateway zero-days, CVE-2026-88771 (unauthenticated RCE through improper input validation in the management interface, affecting default deployments) and CVE-2026-88772 (memory overflow in DTLS, enabled by default on VPN virtual servers). It lists six more high-severity flaws patched in advisory CTX697096, the affected and fixed versions, and the CISA KEV listing with a federal deadline of 2026-09-30. It advises checking for compromise before patching, since patching can destroy forensic evidence, and gives response steps: isolate, revoke credentials, rebuild firmware, rotate keys and certificates.
 orca.securityadvisoryPublished and added 29 Sep 2026🛡️ Security
- Reliability-Gated Fusion of Consumer Head and Foot IMUs for Lower-Body 3D Pose
This paper introduces a channel-gated fusion model for sparse inertial motion capture that learns per-channel, per-stream temporal gates to weight the reliability of consumer earbud head IMU and smart-insole foot IMU signals, trained with an auxiliary reliability objective on synthetically corrupted data. On a new 35-take benchmark (using SAM-3D-Body pseudo-ground-truth labels), the gated model achieves 69.4mm error on clean data and remains most robust across simulated bias, drift, and dropout faults, automatically suppressing biased firmware-fused foot-orientation channels without test-time supervision (dropout detection AUROC 0.92-0.999). It is compared against a fine-tuned HMD-Poser baseline, which is more accurate on clean data (64.4mm) but degrades far more under worst-case faults (+16.1mm vs +3.5mm).
arxiv.orgpaperAdded 29 Sep 2026, published 28 Sep 2026🧠 AI




Showing 30 of 49
Show more