Skip to content

2580 results for โ€œINEโ€

What you seeeverything
securityweek.comarticle๐Ÿ›ก๏ธ Security

Google Dismantles XCPE Botnet of 1.3 Million Android Devices

XCPE (X.CPE) is a backdoor and botnet of more than 1.3 million Android set-top boxes, built and run by the Chinese OEM/ODM Videostrong Technology. Google dismantled it through legal action against domains and servers and banned Videostrong from preloaded Google apps. The malware used a three-stage design persisting on the /oem/ partition and was used for ad fraud, residential proxies and further malware loading.

AndroidAndroid TV
XCPEVideostrong TechnologyGoogle+8

Threat Intel, Mobile Security, Supply Chainยท Published and added 3 Nov 2026

securityweek.comarticle๐Ÿ›ก๏ธ Security

NATOโ€™s Crossed Swords Exercise Brings AI Agents Into Cyber Operations Training

Crossed Swords 2026 is a NATO CCDCOE cyber exercise held in Tallinn with more than 250 participants from over 40 countries. It trains synchronisation of cyber effects with kinetic and special operations actions. A new track has participants build, deploy and assess AI agents, on locally hosted AI and OpenAI's Daybreak, with over 20 industry, academic and NGO partners.

DaybreakOpenAI
NATO Cooperative Cyber Defence Centre of ExcellenceNATOBitdefender+9

other, AI Securityยท Published and added 3 Nov 2026

latent.spacearticle๐Ÿง  AI

[AINews] LLMs can read & write neural network weights: "Weight Space Programming" cuts Autoresearch out of the RSI loop

AINews issue for 31 October to 2 November 2026 from Latent Space. It leads with "Weight Space Programming" (Takehi et al., with Alex Zhang), where a frontier LLM reads and edits small models' weights without training. The recap also covers DeepSeek's super-agent harness, the SemiAnalysis GDPx benchmark, quantized local MoE models and Reddit skepticism about the Qwen3.5-0.8B MATH-500 edit. The page was truncated, so the final part is not covered.

LLMQwen3.5Strata+10
Latent SpaceAlex ZhangAndrej Karpathy+21

research, models, evalsยท Published and added 3 Nov 2026

x.comrepo๐Ÿง  AI

Md Ismail ล ojal๎จ€ ๐Ÿ•ท๏ธ (@0x0SojalSec) on X

An x64dbg MCP server, published on GitHub by duty1g and shared in an X post by @0x0SojalSec, lets Claude drive the x64dbg Windows debugger. It exposes breakpoints, memory dumps and code stepping as tools for reverse engineering and malware analysis. A reply warns that debugging a sample executes it, so the agent should run in a snapshotted VM with no shared folders or host route, and every command should be logged.

x64dbgModel Context ProtocolClaude+2
duty1g

mcpยท Added 3 Nov 2026

github.comrepo๐Ÿง  AI

colibri: pure-C engine for running huge MoE models by streaming experts from disk

colibri is a pure-C, dependency-free inference engine that runs mixture-of-experts models of hundreds of billions of parameters on ordinary machines. It keeps the dense layers in RAM and streams routed experts from disk through a learning cache, with optional CUDA, Vulkan and Metal tiers. It supports GLM-5.2, Kimi K3, DeepSeek V4, Qwen3.6 and GGUF files, and serves OpenAI- and Anthropic-compatible APIs.

Mixture of ExpertsGGUFCUDA+10
GLM-5.2GLM-5.3GLM-5.3-Flash+22

inference, modelsยท Added 3 Nov 2026

huggingface.coarticle๐Ÿง  AI

Transformers Model Integration Contracts

Model Integration Contracts (transformers-mic) is a proposed Hugging Face standard for testing Transformers models with small fixtures, a runnable usage path and reviewed baselines. A tiny UMT5 fixture on CPU flagged an SDPA regression in T5 that lasted from 30 July to 28 September 2026. The post covers the shrink recipe, the tmic CLI, random vs overfit weights and open questions.

TransformersPyTorchHugging Face+3
transformers-mictmicUMT5+5

evals, ai-infra, modelsยท Published and added 3 Nov 2026

latent.spacetalk๐Ÿง  AI

Building AI for Lawyers - Jacob Lauritzen, CTO of Legora

Latent Space podcast episode with Jacob Lauritzen, CTO of Legora, on building AI agents for lawyers. He describes evals built from RL environments such as a 10,000-file data room because traces cannot be read, routing across models, source-linked citations, and a few shared primitives (Tabular Review, lists, intake). Also covers legal engineers versus forward deployed engineers, Azure-only hosting, and the billable hour. Based on the first 40,000 characters of the transcript.

AzureSlackTabular Review+4
LegoraJacob LauritzenLatent Space+12

agents, evals, llm-appsยท Published and added 2 Nov 2026
chainalysis.comarticle๐Ÿ›ก๏ธ Security

Disrupting the Mercado Bitcoin Attack: How Chainalysis Led the Freeze of Nearly $10M in Stolen Funds

Chainalysis describes its response to the 2 November 2026 hack of Mercado Bitcoin, Brazil's largest crypto exchange, where an attacker drained about $49 million across 17 blockchains. Investigators traced the funds, contacted law enforcement within 30 minutes and worked with Paxos, Anchorage Digital, Ripple, Circle and Tether. Tether froze over $9 million in USDT, nearly $10 million in all. The post does not explain how the attacker got in.

TetherBitcoinEthereum+2
Mercado BitcoinChainalysisCircle+3

Threat Intel, Blue Team & Detectionยท Published and added 2 Nov 2026

latent.spacetalk๐Ÿง  AI

Building Legal Agents When You Can't See the Data - Jacob Lauritzen, CTO of Legora

Latent Space interview with Jacob Lauritzen, CTO of Legora, on building a legal agent when the company cannot read customer traces. It covers simulated test "worlds" built by engineers and lawyers, a citation fix that went from 70% to 99% with a model release, paraphrased traces, and running on Azure. It also covers Tabular Review, intake bots, forward-deployed engineers and the harness.

AzureSlackTabular Review+5
LegoraLatent SpaceWexler+9

agents, evals, llm-appsยท Published and added 2 Nov 2026

regenerator1.comarticle๐Ÿง  AI

Anthropic's growth just flattened

Regenerator1 analyzes Anthropic's reported 2026 revenue: Q1 $4.8 billion, Q2 $11.6 billion (+141%), Q3 $16.8 billion (+45%). Using a reported $65 billion annualized run-rate in July (about $5.4 billion for the month), the author estimates growth was modest in August and September. The author suggests seasonality, capacity limits or cheaper Chinese models as causes, and links the slowdown to falling neocloud stocks such as CoreWeave.

AnthropicCoreWeaveThe New York Times+4

ai-policyยท Added 3 Nov 2026, published 2 Nov 2026

bleepingcomputer.comarticle๐Ÿ›ก๏ธ Security

Chinese hackers use ARTEX AI in automated attacks against 200 orgs

ARTEX is a multi-agent AI penetration-testing framework that the China-nexus actor Vapor Panda used from 17 October against more than 200 organizations in 14 countries, compromising at least nine. CrowdStrike reports DeepSeek and another commercial model coordinated agents, operators told agents to skip Falcon-protected Windows hosts, and BLOODALCHEMY was deployed. DIVD says ARTEX also drove its September 2026 breach, chaining two zero-days (one in Zammad) to root in 12 minutes.

ARTEXDeepSeekCrowdStrike+2
Vapor PandaBLOODALCHEMYDutch Institute for Vulnerability Disclosure+1

Threat Intel, AI Security, Offensive Securityยท Published and added 2 Nov 2026

alignment.openai.comarticle๐Ÿง  AI

Training activation classifiers for safety and alignment

Training activation classifiers for safety and alignment describes how OpenAI trains lightweight probes on a model's residual stream activations to flag misaligned or policy-violating completions. Probes use an MLP plus QV-attention architecture with an exponential moving average and a rolling softmax objective. They run in streaming mode on the inference engine, have run on all assistant completions since GPT-5.6, and transfer well across post-training checkpoints but less across pre-training checkpoints.

activation probesattention probesMultiMax probe+3
OpenAIGPT-5.6

ai-safety, researchยท Published and added 2 Nov 2026

bleepingcomputer.comarticle๐Ÿ›ก๏ธ Security

Fintech platform Sageworks taken offline after suspected cyberattack

Abrigo took its Sageworks lending and risk platform offline on 30 October 2026 after detecting "irregular activity", and has restored most functions except borrower-facing features. Sageworks serves over 2,400 US community banks and credit unions. Earlier in 2026 an alleged ShinyHunters member claimed theft of 1.7 million Salesforce records from Abrigo, and researchers advised customers to rotate Sageworks API keys. Abrigo has not said whether this was a breach.

SageworksSalesforce
ShinyHuntersAbrigo

Threat Intelยท Published and added 2 Nov 2026

x.comthread๐Ÿง  AI

๐Ÿšจ AI News | TestingCatalog (@testingcatalog) on X

Drex for Finance is a multimodal decision model from Nace AI, post-trained for sub-second financial decisions such as card-payment fraud checks. It takes a document or transaction log plus a fixed set of answers and returns a probability for each. On 3,361 decisions from 48 held-out finance benchmarks it scored 85.7%, against 70.9% for GPT-6 Luna and 77.7% for Drex Max v1.1. It is available on the Nace Console.

Drex for FinanceNace Console
Nace AIDrex Max v1.1GPT-6 Luna+1

models, evalsยท Added 3 Nov 2026, published 2 Nov 2026

jfrog.comadvisory๐Ÿ›ก๏ธ Security

Your Artifactory is fine. Your Linux kernel hosting it might not be.

CVE-2026-98432 is a race-condition use-after-free in the Linux kernel's IPv4 TCP connection setup, present since Linux 4.4 and scored 9.8 by the kernel team. Anthropic reported on 27 October 2026 that Claude wrote a remote root exploit against MPTCP listeners. JFrog lists fixed kernel versions, distro patch status as of 30 October, changelog check commands for Debian, Ubuntu and RHEL, and mitigations where no fix exists.

Linux kernelJFrog ArtifactoryGo+3
CVE-2026-98432use-after-freeAnthropic+2

Cloud & Infra, AI Securityยท Published and added 2 Nov 2026

decrypt.coarticle๐Ÿง  AI

Proton Users Revolt After CEO Calls Security Caution 'Loser Thinking' Amid AI Push

Decrypt reports on backlash against Proton after 404 Media revealed that CEO Andy Yen called a request for pentesting time "loser thinking" while pushing engineers to use AI instead of hand-writing code. Proton cancelled planned AI-use re-interviews on 30 October 2026, and CTO Bart Butler's 1 November manifesto says engineers should direct LLMs and that most human code review may end. User cancellations are anecdotal, not a verified count.

LLMLumoClaude+1
Proton404 MediaMicrosoft+5

ai-policy, coding-agentsยท Published and added 2 Nov 2026

aws.amazon.comarticle๐Ÿ›ก๏ธ Security

Beyond DKIM key rotation: understanding email replay attacks

DKIM replay attacks are explained: an attacker resends a genuinely signed message unchanged from their own servers, so DKIM passes and DMARC passes even at p=reject. The post shows how to tell replay from spoofing or a legitimate relay using DMARC rua reports, why rotating a key without removing the old public key from DNS leaves messages replayable, and how Amazon SES (BYODKIM vs Easy DKIM), Route 53 and CloudWatch support detection and response. It ends with an ordered incident-response procedure.

Amazon SESAmazon Route 53Amazon CloudWatch+2
DKIM replayDKIM2IETF+3

Blue Team & Detection, Cloud & Infraยท Published and added 2 Nov 2026

securityweek.comarticle๐Ÿ›ก๏ธ Security

Revolve Data Breach Impacts at Least 180,000 People

Revolve, an online fashion retailer, disclosed a September 11 breach of systems including its e-commerce platform. Attackers may have exfiltrated names, addresses, card numbers and expiration dates that customers saved in their accounts. Notices filed with the Iowa, Massachusetts, Texas and Vermont attorneys general show at least 179,259 people notified. Revolve offers no credit monitoring, and the attacker and method are undisclosed.

RevolveSEC

Threat Intelยท Published and added 2 Nov 2026

simonwillison.netarticle๐Ÿง  AI

The U.S. Census Bureau and โ€œSuper Intelligenceโ€

Simon Willison updates a September 2025 Apollo Global Management chart of U.S. corporate AI adoption using the Census Bureau's Business Trends and Outlook Survey (BTOS), with data published 22 October 2026. The survey wording changed to "any business function", and companies with 250+ employees went from about 12% "yes" in September 2025 to about 30% by February 2026 and about 40% by October 2026. The post also says the Bureau fell foul of Executive Order 14434.

GPT-5Claude
U.S. Census BureauApollo Global ManagementSimon Willison+2

ai-policyยท Published and added 2 Nov 2026

securityweek.comarticle๐Ÿ›ก๏ธ Security

Google Introduces $250,000 Root-in-Cloud Bug Bounty Reward

Google Cloud Vulnerability Reward Program has added a $250,000 root-in-cloud tier for exploits that give roles/owner or full IAM control over arbitrary Google Cloud organizations or projects. The exploit path cannot rely on prior project access, stolen credentials or social engineering. Remote code execution in Borg also qualifies, but researchers must stop probing immediately. Proof is made against a designated service account using a deterministic proof-of-root mechanism.

Google CloudBorg
GoogleCloud VRPChris Betz+2

Cloud & Infra, Offensive Securityยท Published and added 2 Nov 2026

bleepingcomputer.comarticle๐Ÿ›ก๏ธ Security

Over 1,000 GitLab servers vulnerable to ongoing RCE attacks

CVE-2026-97229 is a maximum-severity integer overflow in GitLab's CI/CD Regular Expression Compiler that lets an unauthenticated attacker run code via a crafted regex in pipeline configuration. GitLab patched it on 12 October 2026 in versions 19.4.2, 19.3.5 and 19.2.8. CISA added it to KEV, and Shadowserver tracks over 1,000 unpatched servers, plus 11,300 exposed to the related CVE-2026-110264.

GitLab
CVE-2026-97229CVE-2026-110264CVE-2026-85706+6

AppSec, DevSecOps, Threat Intelยท Published and added 2 Nov 2026

theguardian.comarticle๐Ÿ›ก๏ธ Security

Supermarket freezers across Europe hit by second suspected cyber-attack

Guardian report from 2 November 2026 on a second suspected cyber-attack on supermarket refrigeration in Belgium, Estonia, Ireland, Finland, Luxembourg, the Netherlands and Sweden, with temperatures set to 50C. It recaps the earlier French attack on up to 700 shops, which hit mostly Danfoss controllers. SentinelOne and Tributech say the attacks point to sabotage and that many controllers remain internet-exposed and unpatched.

DanfossSentinelOneTributech+5

Threat Intel, Hardware & RFยท Added 3 Nov 2026, published 2 Nov 2026

x.comthread๐Ÿง  AI

CuteGuyโ˜ฃ๏ธ (@cutetoxicguy) on X

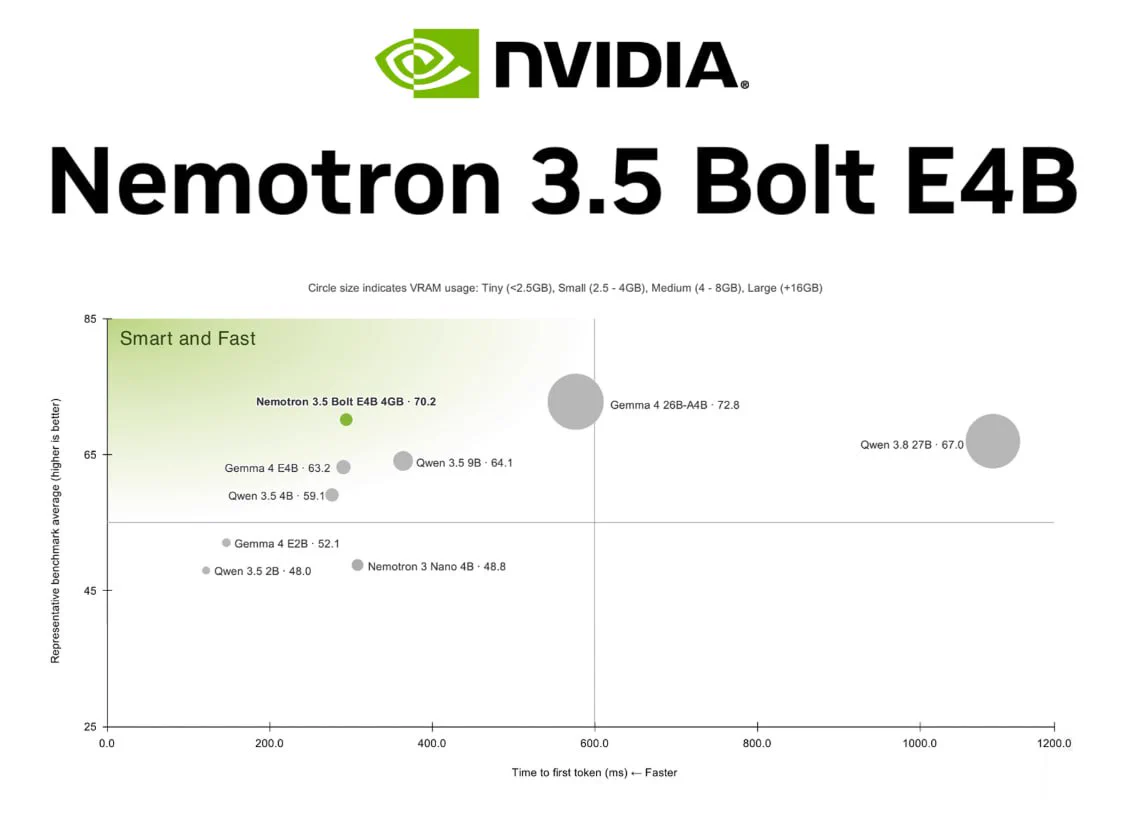
Nemotron 3.5 Bolt E4B is an NVIDIA open-weights model with 8B total and 4B active parameters, built on Gemma 4 E4B and post-trained with NeMo RL and NeMo Gym. It targets local agents in about 4GB of GPU memory, with 64K context, 35 languages, multi-step tool calling and configurable reasoning. NVIDIA's llama.cpp tests show 133.4 tokens/sec on an RTX 5070 and 15.5 on a Jetson Orin Nano. Benchmarks are NVIDIA's own.

llama.cppOllamaLM Studio+9
NVIDIANemotronGemma 4+8

models, inference, agentsยท Added 3 Nov 2026, published 2 Nov 2026

bleepingcomputer.comarticle๐Ÿ›ก๏ธ Security

Ivanti patches two more Connect Secure zero-days chained in attacks

Ivanti patched two more Connect Secure zero-days, CVE-2026-111357 (privilege escalation) and CVE-2026-118527 (authenticated file upload), chained with authentication bypass CVE-2026-104935 since at least 1 October 2026. Volexity attributed the chain to UTA0576, which ran no malware, re-exploited the device per command and tampered with logs, evading Ivanti's Integrity Checker Tool. CISA added CVE-2026-104935 to KEV, and Shadowserver tracks over 5,000 exposed instances.

Ivanti Connect SecureVPN
CVE-2026-111357CVE-2026-118527CVE-2026-104935+12

Threat Intel, Offensive Securityยท Published and added 2 Nov 2026

securityweek.comarticle๐Ÿ›ก๏ธ Security

Ivanti Patches Two More Zero-Days Exploited in Connect Secure Attack Chain

Ivanti patched two more Connect Secure zero-days, CVE-2026-111357 (CVSS 8.8, local privilege escalation) and CVE-2026-118527 (CVSS 4.3, predictable identifiers allowing file upload), chained with the authentication bypass CVE-2026-104935. Fixes are in ICS 25.1.1.3 and 22.8R2.6. Volexity attributed the chain, which gave unauthenticated root code execution, to UTA0576, and CISA added both new bugs to KEV.

Ivanti Connect SecureVPNCVSS
CVE-2026-111357CVE-2026-118527CVE-2026-104935+6

Threat Intel, Offensive Securityยท Published and added 2 Nov 2026

lankabusinessonline.comarticle๐Ÿ›ก๏ธ Security

PHP security scare puts Sri Lankaโ€™s digital systems under scrutiny

Lanka Business Online reports on CVE-2026-109618 and CVE-2026-109619, two critical PHP flaws allowing unauthenticated remote code execution. Sri Lanka's Ministry of Digital Economy told state bodies to check their systems, as over 70% of government sites reportedly use PHP. Research on 22 to 24 October 2026 found 80 state-linked sites on potentially vulnerable versions, 61 of them unsupported. Patches came out on 21 October 2026.

PHP
CVE-2026-109618CVE-2026-109619Ministry of Digital Economy

AppSecยท Published and added 2 Nov 2026

x.comtool๐Ÿ›ก๏ธ Security

Md Ismail ล ojal๎จ€ ๐Ÿ•ท๏ธ (@0x0SojalSec) on X

An x64dbg MCP server (GitHub repo by duty1g, shared via an X post) that lets Claude drive the x64dbg Windows debugger: set breakpoints, dump memory, step code and run other reverse engineering tasks programmatically. The post targets malware analysts. A reply notes that debugging a sample executes it, so the agent should run in a snapshotted VM with no shared folders or host route, with every command logged.

x64dbgModel Context ProtocolClaude+1

Malware & RE, AI Securityยท Added 3 Nov 2026, published 1 Nov 2026

bleepingcomputer.comarticle๐Ÿ›ก๏ธ Security

FBI links $6.3 billion Binance crypto heist to North Korean hackers

The FBI attributed the roughly $6.3 billion Binance theft of about 29 October 2026 to North Korea's TraderTraitor (Lazarus Group, Jade Sleet, APT38). Binance traced the breach to a compromised DevOps engineer's laptop that gave access to a service container used to submit unauthorized withdrawals across ten blockchains. The FBI published 628 laundering addresses and linked the group to earlier thefts at Bybit, DMM Bitcoin, Bitget and Drift.

EthereumBitcoinSolana+3
TraderTraitorLazarus GroupDPRK+14

Threat Intel, Blockchainยท Published and added 1 Nov 2026

x.comthread๐Ÿง  AI

Smarthouse (@localyzapp) on X

A reply by Smarthouse (@localyzapp) on X to a question about the best harness for connecting local models to a Minecraft server. It suggests an MCP server that wraps RCON plus a small agent loop. The main pitfall is block coordinates: expose "/execute if block" as a read tool so the agent can check blocks before placing them, or it will hallucinate terrain.

Model Context ProtocolMinecraftRCON

mcp, agentsยท Added 2 Nov 2026, published 1 Nov 2026

newsletter.semianalysis.comarticle๐Ÿง  AI

The Datacenter Backlash Goes Bipartisan: Next Week's Midterms and the 2028 Buildout

SemiAnalysis analysis of how the November 2026 US midterms could affect datacenter buildout. About 75% of the 33.8 GW due in 2027 across the top 20 states is already under construction, but 43.5 GW of 2028 additions sit in 13 states with pending approvals. The biggest risk is a prolonged Texas TCEQ permit freeze. Texas holds close to 30% of 2028 GW, and nine of 20 nominees back a pause.

SemiAnalysisTexas Commission on Environmental QualityERCOT+16

ai-policyยท Published and added 1 Nov 2026

Showing 30 of 2580

Show more