Skip to content

50 results for β€œrr”

What you seeeverything
ethereum-magicians.orgthreadπŸ›‘οΈ Security

Pre-ERC: Agent Pre-Sign Risk Report

Pre-ERC: Agent Pre-Sign Risk Report is a draft Ethereum Magicians proposal for an EIP-712-signed report that a risk source, identified by an ERC-8004 identity, returns about one unsigned request. It carries typed findings on tokens, approvals, addresses, payments (x402) and texts, and each finding is marked read or not read. It has no score or verdict, so the consumer applies its own policy. The author's live implementation, toll, runs on Robinhood Chain.

Ethereumx402Robinhood Chain+3
ERC-8265ERC-8004ERC-8470+8

AI Security, BlockchainΒ· Published and added 31 Oct 2026

ethereum-magicians.orgthreadπŸ›‘οΈ Security

ERC-8478: x402 Payee Verification for ERC-8004 Agents

ERC-8478 is a draft Ethereum standard that binds the x402 payTo address to an ERC-8004 agent's identity, to stop payee redirection by a hijacked domain, proxy or injected tool result. A payTo must equal the agentWallet or carry an EIP-712 delegation signed by it, and the origin must be listed in the registration file. On Robinhood Chain, 5 of 5,575 x402-responding agents used their agentWallet as payTo (28 October 2026).

x402ERC-8004Ethereum+2
ERC-8478ERC-8470EIP-712+3

AI Security, BlockchainΒ· Published and added 30 Oct 2026

x.comthread🧠 AI

Muhammad Waris (@WarisCodes) on X

Nemotron 3.5 Transcribe is a free open-weight speech-to-text model from NVIDIA covering 40 languages, including mixed-language speech. The post says it ties for first among open models with a 2.8% error rate. It says the model needs a large GPU such as an H100 or RTX 5090, so it will not run on a laptop. The post gives no benchmark name or model card link.

Nemotron 3.5 Transcribe
NVIDIANemotron

models, multimodalΒ· Added 30 Oct 2026, published 29 Oct 2026

x.comthreadπŸ›‘οΈ Security

Christiaan Stoudt (@cstoudt) on X

Thread on CVE-2026-97631, a critical (9.5) flaw in TianoCore EDK II UEFI firmware, found by Alex Matrosov and Dan Holmes-Mitra. It is exploitable only while a machine is PXE network booting and the attacker sends an oversized ICMP error from the same network. Code execution also needs the exact firmware build, and Secure Boot does not help. The fix landed in EDK II main on 15 October but is not in a stable release. No known exploitation, and not in CISA KEV.

EDK IIUEFITianoCore+2
CVE-2026-97631Alex MatrosovDan Holmes-Mitra+3

Hardware & RFΒ· Added 30 Oct 2026, published 28 Oct 2026

x.comthreadπŸ›‘οΈ Security

Kizuno18 (@Kizuno18) on X

Thread by Kizuno18 on the move from local stdio/Docker Model Context Protocol servers to remote HTTP/SSE endpoints in enterprise infrastructure. It names three trade-offs: credential boundary inversion (short-lived OAuth/JWT tokens instead of long-lived admin tokens on workstations), tool schema bloat solved by deferred discovery, and governance via HCP Terraform policy-as-code (Sentinel/OPA), audit trails and approvals. It is opinion, with no data or implementation detail.

Model Context ProtocolTerraformDocker+2
Sentinelblast radiuspolicy-as-code+1

AI Security, Identity & Access, DevSecOpsΒ· Added 29 Oct 2026, published 27 Oct 2026

x.comthread🧠 AI

Kizuno18 (@Kizuno18) on X

Kizuno18's X post argues that the move from local stdio and Docker MCP servers to remote HTTP/SSE endpoints matures the Model Context Protocol in enterprise infrastructure. It lists three trade-offs: short-lived OAuth/JWT bearer tokens replace mounted admin credentials, deferred tool discovery avoids roughly 20k tokens of eager schema loading, and HCP Terraform enforces Sentinel/OPA policy, audit trails and approvals server-side. Opinion post with no benchmarks or code.

Model Context ProtocolDockerTerraform+5
Kizuno18HCP TerraformOPA

mcpΒ· Added 29 Oct 2026, published 27 Oct 2026

x.comthreadπŸ›‘οΈ Security

Nicholas Martin (@ndgmlondon) on X

X thread started by Nicholas Martin (#IAM) advising that MCP tool permissions be verified and scoped session tokens used to enforce least privilege against indirect prompt injection. Replies argue that token scoping does not solve the confused deputy problem, because an injection borrows the agent's legitimate authority. They recommend per-task tokens with short expiry, with the grant logged beside the call, and raise MCP server dependency supply-chain risk.

Model Context Protocol
indirect prompt injectionconfused deputy

AI Security, Identity & AccessΒ· Added 28 Oct 2026, published 27 Oct 2026

x.comthread🧠 AI

Abdullah (@abdullah0094) on X

An X thread by Abdullah on GPT-6.1 Terra versus Sol in Codex. Abdullah says Terra gives twice the Codex usage of Sol and asks whether the quality drop is obvious. A reply says it is too early for a verdict, cites OpenAI's claim that Terra matches GPT-6 Astra on Agents' Last Exam, and suggests defaulting to Terra and switching to Sol with /model when it stalls.

Codex
GPT-6.1 TerraGPT-6.1 SolGPT-6 Astra+2

coding-agents, modelsΒ· Published and added 27 Oct 2026

x.comthreadπŸ›‘οΈ Security

Trail of Bits (@trailofbits) on X

Trail of Bits post on PHP2Shell, an exploit that gives a shell on MediaWiki, Symfony, Laravel and phpBB. They confirmed it on pre-patch PHP 8.2 to 8.5. An update says it is production-grade: it works with stock php.ini-production, display_errors off, multiple workers, ASLR and load, on ARM64 and x86-64, and reaches root on Apache/mod_php and nginx/php-fpm. No CVE or technical root cause is given.

PHPWordPressLaravel+3
PHP2ShellTrail of Bits

Offensive Security, AppSecΒ· Added 27 Oct 2026, published 26 Oct 2026

x.comthread🧠 AI

The SI Maximalist (@thesimaximalist) on X

The SI Maximalist posts on X that OpenAI says GPT-6.1 Terra matches GPT-6 Astra on Agents' Last Exam, OpenAI's test of workplace software tasks, at one tenth of the token price. The model is available in ChatGPT Work, Codex and the API. The post only relays OpenAI's claim and gives no benchmark scores, exact prices or method.

ChatGPTCodexOpenAI API
OpenAIGPT-6.1 TerraGPT-6 Astra+2

models, evalsΒ· Added 27 Oct 2026, published 26 Oct 2026

x.comthreadπŸ›‘οΈ Security

David Gutierrez | Eng (@david_x_ai) on X

Thread on two October 2026 npm compromises: @subql/common 5.8.3 (5 October), published through GitHub Actions OIDC Trusted Publishing after the attacker tampered with the publish workflow, and tensorlake 0.5.144 (8 October), published by the project's own release workflow with valid provenance for about 1 hour 40 minutes. Both ran on install and stole cloud, GitHub, Kubernetes, Vault, SSH and .env credentials; tensorlake also took AI tool and MCP config. Its payload installed a gh-token-monitor service that deletes the home directory if the stolen GitHub token is revoked, so remove it before rotating.

npmGitHub ActionsGitHub+3
@subql/commontensorlakegh-token-monitor+3

Supply Chain, DevSecOpsΒ· Added 27 Oct 2026, published 26 Oct 2026

x.comthreadπŸ›‘οΈ Security

Masoud (@dev3mike) on X

Tweet from dev3mike warning Node.js users to update for CVE-2026-111497, a Brotli bug rated CVSS 9.2. Crafted compressed data can corrupt memory and possibly run code. The post says OpenAI's agents found it, and that the fix sat unreleased in Brotli's source since February. Patched versions are Node 22.23.4, 24.22.1 and 26.12.1.

Node.jsBrotliOpenAI+1
CVE-2026-111497

AppSecΒ· Added 29 Oct 2026, published 26 Oct 2026

x.comthreadπŸ›‘οΈ Security

David Gutierrez | Eng (@david_x_ai) on X

Thread on a critical opencode bug disclosed by Pillar Security on Oct 19. On Windows and WSL, a remote MCP server could run code during OAuth sign-in, because the server-chosen authorization URL was put unescaped into a PowerShell command, so a PowerShell subexpression executed. opencode fixed it in 1.18.33 on Sep 28 as a browser-launch refactor with no advisory or CVE. MCP Inspector published an advisory for the same bug class, and its fix needs a major bump of the open package.

OpenCodeModel Context ProtocolPowerShell+3
Pillar Securitycommand injectionPowerShell subexpression+1

AI Security, AppSec, Supply ChainΒ· Added 27 Oct 2026, published 25 Oct 2026

x.comthreadπŸ›‘οΈ Security

Prasenjit Sarkar (@stretchcloud) on X

Post on the LiteLLM supply-chain compromise. Attackers spent eleven days in the GitHub org, ran a workflow on a throwaway branch to take twenty secrets including a GitHub App private key, then used stolen GitHub CLI OAuth tokens to publish malicious release 1.107.0 from a lookalike Berri-AI repo. A Python startup file harvested sixteen credential categories and LiteLLM proxy Postgres provider keys. Socket flagged the wheels in seven minutes.

LiteLLMPyPIGitHub Actions+3
Berri-AIBerriAILiteLLM 1.107.0+3

Supply Chain, DevSecOps, AI SecurityΒ· Added 26 Oct 2026, published 24 Oct 2026

x.comthreadπŸ›‘οΈ Security

Paul Dragoonis (@dr4goonis) on X

Social post summarising emergency patches for Node.js (4 high CVEs), PHP (2 critical) and nginx (3 critical). Node.js flaws include a Brotli decoder out-of-bounds write, a DNS truncation bug and two TLS hostname-verification bypasses. PHP has use-after-free and heap corruption bugs, and nginx has alias-rewrite and map-regex heap overflows plus an SSI-AIO use-after-free. It lists the fixed versions for each product.

Node.jsPHPnginx
CVE-2026-111497CVE-2026-105482CVE-2026-105483+8

AppSecΒ· Added 23 Oct 2026, published 22 Oct 2026

x.comthread🧠 AI

0xMarioNawfal - The Roundtable Show (@RoundtableSpace) on X

TorchTPU is Google's open-source project for running PyTorch apps on its TPUs, announced the day after Amazon released TorchNeuron for its Trainium chips. Google says migration needs "a simple configuration change" with no rewrite. It worked with Meta, Hugging Face, and the vLLM and SGLang teams on compatibility, and added an agent suite that helps migrate apps and fix errors. The post is brief and gives no benchmarks.

PyTorchvLLMSGLang+4
GoogleAmazonNVIDIA+5

inference, ai-infraΒ· Added 21 Oct 2026, published 20 Oct 2026

x.comthread🧠 AI

Paulo Pierrondi | AI agents (@paulopierrondi) on X

Paulo Pierrondi's X post, part 9 of a series on installing MCP servers, lists a monthly review of installed servers. The checks are which tools the agent used, servers not called in weeks, overlapping tools that confuse the model, and whether each server still has an owner. A reply adds a decommissioning check: after removal, confirm the server's old credentials can no longer call the backend.

Model Context Protocol
Paulo Pierrondi

mcpΒ· Published and added 20 Oct 2026

x.comthreadπŸ›‘οΈ Security

Dark Web Informer (@DarkWebInformer) on X

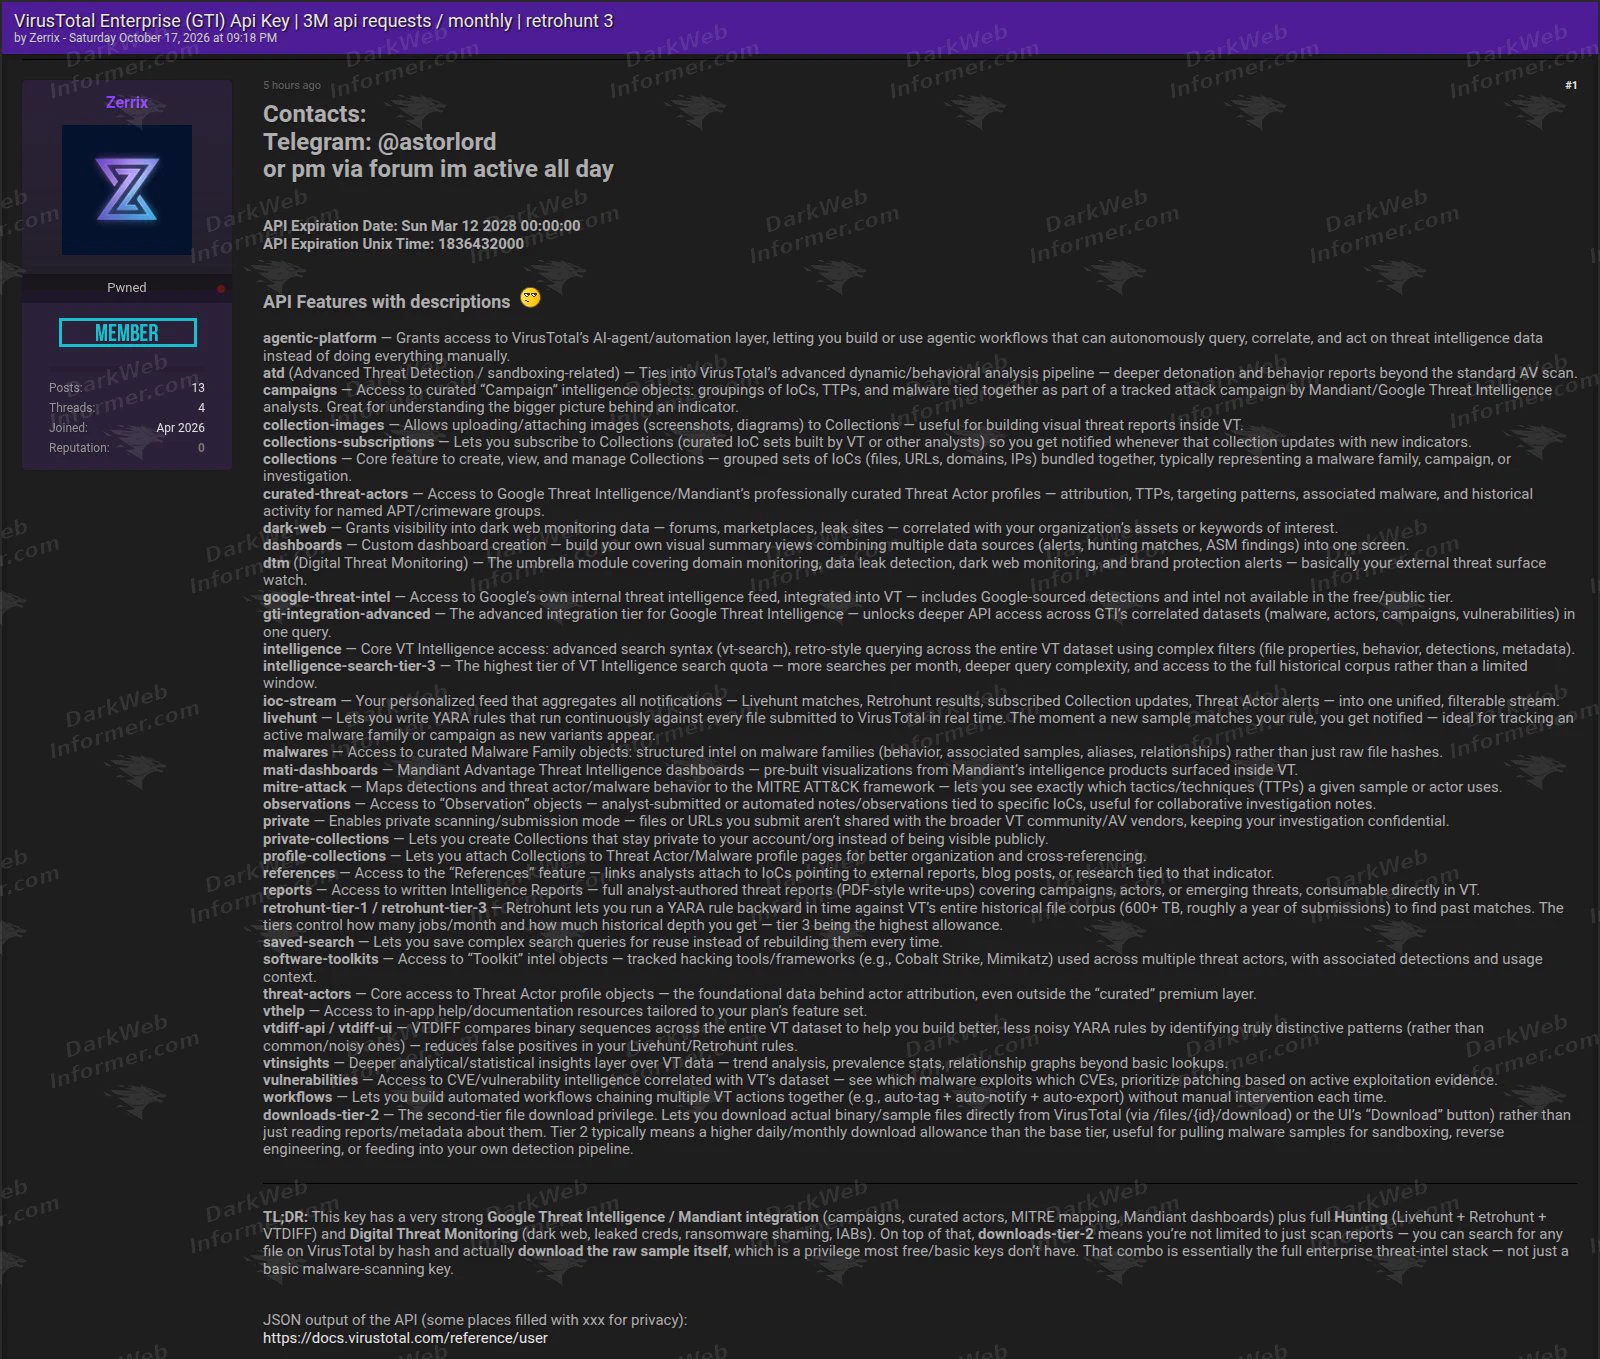
A DarkWebInformer post on an actor called "Zerrix" advertising a VirusTotal Enterprise API key for sale. The seller claims 3 million requests per month, Retrohunt Tier 3 (YARA search over historical samples), Google Threat Intelligence and Mandiant access, sample downloads and private scanning, valid until 12 March 2028. How the key was obtained is not stated, and the post says its authenticity is unverified.

VirusTotalYARA
ZerrixRetrohuntGoogle Threat Intelligence+2

Threat IntelΒ· Added 19 Oct 2026, published 18 Oct 2026

x.comthread🧠 AI

Rodrigo ES Porto (@RodrigoESPorto) on X

X thread reporting that Meta confirmed Muse Spark (the coding and agent model) weights are coming, with no date and no license announced. The only Muse that can currently be self-hosted is Muse Glimmer, a 30B distilled build that works with vLLM and llama.cpp. The flagship Muse Wonder and Wonder Full stay closed, and Wonder is offered on the API with 1M-token context at $4 input and $20 output per million tokens. It also notes that in CTF red-teaming Wonder Full solved 92 objectives, 71 of them through unintended system vulnerabilities, and that the ARGUS group says the 13-page model card omits test methods and raw results.

vLLMllama.cppLlama
MetaMuseMuse Spark+4

models, ai-policy, ai-safetyΒ· Added 17 Oct 2026, published 16 Oct 2026

x.comthread🧠 AI

Romy (@0xBunny) on X

Tweet from 0xBunny announcing an update to Jev Workflows, an open-source workflow toolkit. It adds native Claude Code support alongside Codex, an opt-in Jev 1.14, experimental image/Box questions, shared QQ contract sync and local CI. Features were also mirrored to a sibling project called QQ. It is free, with no plugin quotas, and links to a GitHub repo.

Claude CodeCodexGitHub
JevQQ

coding-agentsΒ· Added 17 Oct 2026, published 16 Oct 2026

x.comthreadπŸ›‘οΈ Security

lee1981 (@lee1981b) on X

CyberForge "CVE of the Day #079" on CVE-2026-102764, a CWE-290 origin-validation flaw in BeyondTrust Remote Support (advisory BT26-05, CVSS v4 9.3) that allows appliance file operations. It summarises Mandiant/GTIG's exploited intrusion chain (SAWFLY web shell, BARECLAW backdoor, root escalation, persistence) and gives an investigation trail: patch-state verification (BT26-05-RS), evidence preservation, hunting leads with SHA-256 hashes and YARA rules, permission/session correlation, and remediation including clean redeployment and credential rotation. It separates vendor facts from the intrusion's observed behaviour and notes that KEV and EPSS have no entries.

BeyondTrust Remote SupportYARASIEM+2
CVE-2026-102764BT26-05CWE-290+7

Blue Team & Detection, Threat IntelΒ· Added 18 Oct 2026, published 16 Oct 2026

x.comthread🧠 AI

Harrison Kinsley (@Sentdex) on X

Sentdex reacts to Artificial Analysis ranking NVIDIA's Nemotron 3.5 Super VL (120B total, 12B active MoE) as the top US open-weights model, scoring 26 on the Intelligence Index. That edges out Thinking Machines' Inkling Small (26), NVIDIA's Nemotron 3 Ultra (23) and Meta's Muse Glimmer (17). Sentdex's informal tests at vanilla settings show over 550 tok/sec, and they suspect it would rank higher on agentic coding. They see it as a candidate for a fast local coding agent model.

Mixture of Expertsvision-language model
SentdexNVIDIANemotron+8

models, evals, inferenceΒ· Added 16 Oct 2026, published 15 Oct 2026

x.comthreadπŸ›‘οΈ Security

Francis Santerre (@santerref) on X

Post announcing that the MCP Adapter (0.7.0) is now a canonical plugin on WordPress.org, bridging the WordPress Abilities API to MCP. It exposes a default server at /wp-json/mcp/mcp-adapter-default-server, and only abilities a site marks public are exposed. The author's point is that the security review reduces to auditing the list of public abilities, which gives reviewers and pentesters a new endpoint to enumerate.

WordPressModel Context Protocol
MCP AdapterAbilities API/wp-json/mcp/mcp-adapter-default-server

AppSec, AI SecurityΒ· Added 16 Oct 2026, published 15 Oct 2026

x.comthread🧠 AI

Francis Santerre (@santerref) on X

Tweet announcing that the MCP Adapter is now a canonical plugin on WordPress.org (version 0.7.0). It bridges the WordPress Abilities API to the Model Context Protocol, with a default server at /wp-json/mcp/mcp-adapter-default-server. Only abilities a site marks public are exposed, so the security review comes down to auditing the ability list.

Model Context ProtocolWordPressMCP Adapter+1
Abilities API

mcpΒ· Added 16 Oct 2026, published 15 Oct 2026

x.comthreadπŸ›‘οΈ Security

Ned Peterson (@NedPeterson99) on X

Social post summarizing a Sola Security study (Leon Goldberg, Gal Engelberg). An AI agent re-scored 9,967 high-severity findings from two commercial cloud security platforms across eight production environments and changed severity on 75.1% (58.5% downgraded, 16.6% upgraded). The cause is that 599 vendor rules each carry one fixed severity regardless of environment, and 49% of verdicts needed context beyond the flagged resource. Caveats: 92% of findings were AWS, and the study did not test whether the new severities predict real exploitation.

AWS
Sola SecurityLeon GoldbergGal Engelberg+1

Cloud & Infra, AI SecurityΒ· Added 15 Oct 2026, published 14 Oct 2026

x.comthreadπŸ›‘οΈ Security

Dark Web Informer (@DarkWebInformer) on X

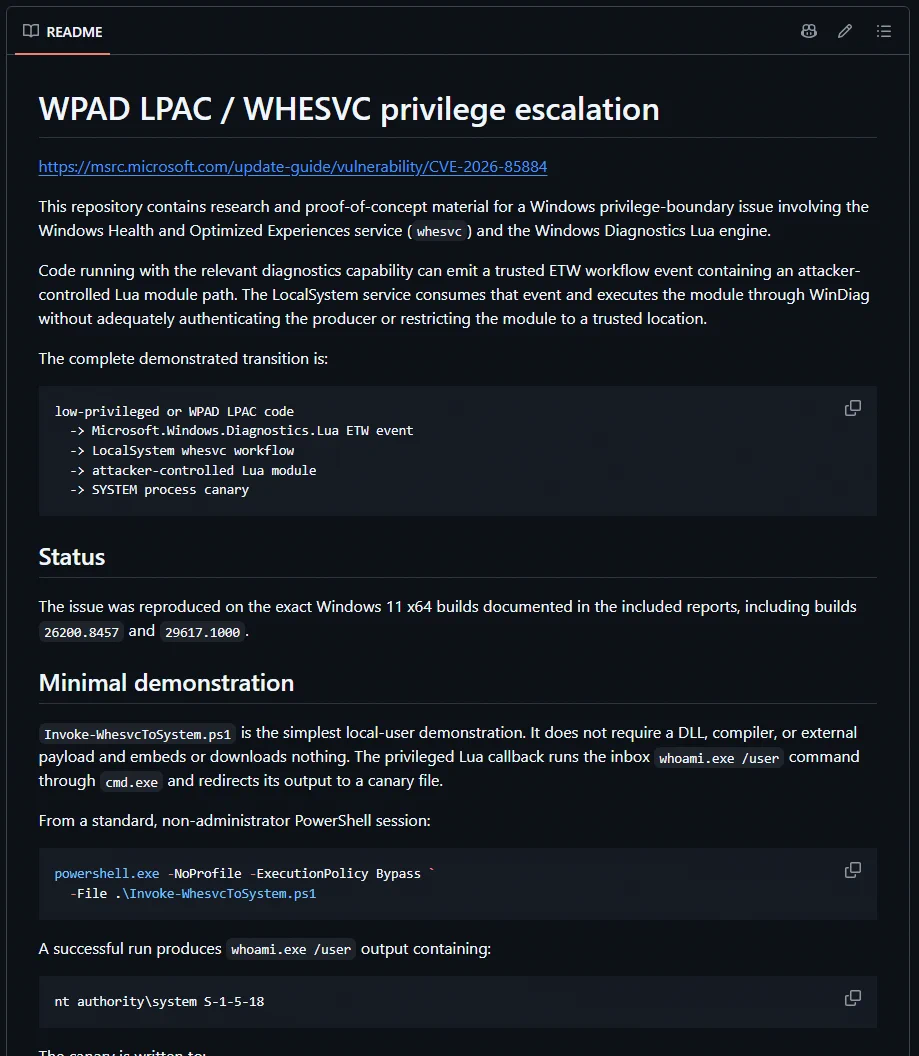
DarkWebInformer post on a PoC for CVE-2026-85884, a Windows 11 local privilege escalation in the Windows Health and Optimized Experiences service. Low-privileged code can trigger a trusted ETW event carrying an attacker-controlled Lua module path. The LocalSystem whesvc service then runs that module through WinDiag without validating the event producer or restricting the module location. The PoC takes a standard non-admin PowerShell session to NT AUTHORITY\SYSTEM on Windows 11 x64 builds including 26200.8457 and 29617.1000.

WindowsETWLua+1
CVE-2026-85884Windows Health and Optimized Experienceswhesvc+1

Offensive SecurityΒ· Added 15 Oct 2026, published 14 Oct 2026

x.comthreadπŸ›‘οΈ Security

lee1981 (@lee1981b) on X

Defender guide for CVE-2026-104935, an authentication-bypass-by-spoofing flaw (CWE-290) in Ivanti Connect Secure that allows unauthenticated command execution. It is confirmed exploited and CISA KEV-listed, with a CNA CVSS 8.6. It covers the fixed-release matrix (25.1.1.2, 22.8R2.5, 25.1.3.x), platform and cluster migration limits, and Volexity's UTA0576 indicators and YARA rules. It also gives a six-step SOC workflow (scope, preserve, hunt, correlate identity, remediate, verify). It stresses that a clean ICT result cannot clear memory-only activity and that LDAP, LAPS and BitLocker exposure belongs to one observed chain.

Ivanti Connect SecureVPNYARA+3
CVE-2026-104935CWE-290UTA0576+6

Blue Team & Detection, Threat IntelΒ· Added 16 Oct 2026, published 14 Oct 2026

x.comthread🧠 AI

44er (@44errrr) on X

Announcement of hexvero, an MCP server that gives coding agents a static first look at binaries and app bundles across 18 formats (ELF, PE, Mach-O, APK, .NET, Go, Wasm, Electron, SQLite). It uses zero-dependency Node parsers and marks each finding confirmed or inferred with file and line. Its tool catalog is 3,043 tokens, against a claimed 509,696 for the established reverse-engineering MCP server. Paged output with a byte budget shrinks a 541 MB Electron app to a 15 KB result, 1.3 MB of JSON to 7.9 KB, and a 450 KB build diff to 1.2 KB. radare2, rizin or Ghidra plug in for disassembly, and `npx hexvero setup --apply` registers it with Claude Code, Cursor, Codex and 15 more clients. It is a concrete example of keeping MCP tool definitions and results small enough for an agent's context window.

Model Context ProtocolNode.jsnpm+12
hexvero

mcp, coding-agentsΒ· Added 15 Oct 2026, published 14 Oct 2026

x.comthreadπŸ›‘οΈ Security

Dark Web Intelligence (@DailyDarkWeb) on X

Social post summarizing Docker's Oct 12, 2026 advisory for CVE-2026-105445, a Docker Hub flaw. Converting a personal account to an organization re-assigned the account's personal access tokens (PATs) to the named new owner without rotating the secret. An attacker could name a victim as owner and keep using the token as that victim to pull, push or delete images. The exposure window ran from Aug 26, 2024 to Sept 30, 2026. Docker fixed it the day it was reported by Peter Molnar and Krisztian Hozak, deactivated transferred PATs on Oct 8, and found no exploitation after reviewing about 304,000 pushes. The post advises reviewing PATs and using organization access tokens for automation.

Docker HubDocker
CVE-2026-105445Peter MolnarKrisztian Hozak+1

Supply Chain, Identity & AccessΒ· Published and added 13 Oct 2026

x.comthread🧠 AI

Igor Carron (@IgorCarron) on X

Igor Carron's tweet highlights LightOn's open-source ColGrep-Agent-2B, a 2B model released on Hugging Face for code search and retrieval that works with Claude Code. LightOn reports 34% fewer API tokens and 40% lower API costs. It matters because usage limits and token costs are a pain point for coding agents. A reply thread in the same post notes quota exhaustion across Grok, Cursor, Devin, Claude and Codex, and argues for quota dashboards.

Claude CodeHugging FaceCodex+3
LightOnColGrep-Agent-2BIgor Carron+1

coding-agents, models, llm-appsΒ· Published and added 12 Oct 2026

Showing 30 of 50

Show more