Skip to content

82 results for β€œtelemetry”

What you seeeverything
microsoft.comwriteupπŸ›‘οΈ Security

Inside a malicious Claude Code-branded extension and its persistent SSH backdoor

Microsoft Threat Intelligence analyzes a tampered anthropic.claude-code extension (versions 2.1.312 and 2.1.313) served on the Cursor marketplace on 29 October 2026. The injected JavaScript loader adds an SSH key labeled svc-telemetry, opens a reverse SSH tunnel and sets up persistence on macOS, Linux and Windows. The post gives cleanup steps, IOCs and Defender XDR hunting queries. VS Code Marketplace and npm were not affected.

CursorClaude CodeSSH+3
Protocol Tunneling (T1572)reverse SSH tunnelMicrosoft Threat Intelligence+2

Supply Chain, Blue Team & Detection, Malware & REΒ· Published and added 31 Oct 2026

bleepingcomputer.comarticleπŸ›‘οΈ Security

Malicious Claude Code extension on Cursor planted SSH backdoors

A malicious version 2.1.313 of Anthropic's Claude Code extension was served from Cursor's marketplace for about 11 hours on 29 October 2026, reaching up to 5,000 developers. A JavaScript loader prepended to extension.js added an attacker SSH key, a reverse tunnel and macOS/Windows persistence, and reported to 134.209.82[.]225. Coding errors likely blocked SSH access on many hosts. Cursor removed it and rotated keys; victims should look for an 'svc-telemetry' SSH key.

Claude CodeCursorVS Code+3
PhorionOpenSourceMalwareLaunchAgent persistence+1

Supply Chain, AI Security, Threat IntelΒ· Published and added 30 Oct 2026

opensourcemalware.comwriteupπŸ›‘οΈ Security

Trojanized Claude Code Extension Plants an SSH Backdoor

Analysis of a trojanized anthropic.claude-code 2.1.313 extension (darwin-arm64), found on Open VSX, with a 66-line loader prepended to extension.js. It adds an svc-telemetry key to authorized_keys, opens a reverse SSH tunnel to 134.209.82.225, sets persistence (LaunchAgent, cron, scheduled task) and sends host recon over HTTP port 8099. Includes IOCs, hashes and response steps; no further payload download was found.

Claude CodeVS CodeOpen VSX+3
anthropic.claude-code 2.1.313134.209.82.225svc-telemetry+3

Supply Chain, Malware & RE, AI SecurityΒ· Published and added 30 Oct 2026

stepsecurity.iowriteupπŸ›‘οΈ Security

Trojanized Claude Code Extension Delivered Persistent SSH Backdoor to Developer Machines

The Claude Code VS Code extension anthropic.claude-code 2.1.313 was published on Open VSX on 29 October 2026 with a malicious loader prepended to extension.js. On load it planted an attacker SSH key (svc-telemetry), installed per-OS persistence, opened a reverse SSH tunnel and beaconed host recon over HTTP. Cursor reports at most 5,000 users received it in an 11-hour window. The post gives the timeline, cleanup artifacts and credential rotation steps.

Claude CodeVS CodeOpen VSX+3
anthropic.claude-code 2.1.313svc-telemetryT1195.002+1

Supply Chain, Blue Team & Detection, Threat IntelΒ· Published and added 30 Oct 2026

gist.github.comwriteup🧠 AI

Claude Code regularly sends each background agent’s transcript to its model

no-agent-summary.js is a roughly 70-line Bun preload by Flamerix AI that stops Claude Code from re-sending each background agent's full transcript to its model every ~30 seconds for a status-line summary. The write-up cites OpenTelemetry measurements of 18 to 26 percent of spend (since version 2.1.232), explains the setTimeout hook, and gives install and verify steps. It was tested on Linux with Claude Code 2.1.257 to 2.1.312.

Claude CodeBunOpenTelemetry+2
AnthropicFlamerix AIDRIM+1

coding-agents, ai-infraΒ· Added 30 Oct 2026, published 29 Oct 2026

x.comarticleπŸ›‘οΈ Security

lee1981 (@lee1981b) on X

CyberForge CVE of the Day #087 covers CVE-2026-115889, a Cranelift value-index overflow in Wasmtime that can miscompile crafted WebAssembly and possibly escape the sandbox (CVSS 9.9, CWE-197 and CWE-843). Affected: below 36.0.19, and 37.0.0 up to but excluding 43.0.0; fixes are 36.0.19 and 43.0.0. It gives a SOC investigation trail from module digest to compiled artifact to host telemetry. EPSS is 0.454%, with no KEV entry.

WasmtimeCraneliftWebAssembly+4
CVE-2026-115889GHSA-897f-g5gm-fmxmRUSTSEC-2026-0380+5

AppSec, Blue Team & DetectionΒ· Added 28 Oct 2026, published 26 Oct 2026

aws.amazon.comarticleπŸ›‘οΈ Security

Amazon Threat Intelligence identifies PHP2Shell exploitation prior to public disclosure in MadPot

Amazon Threat Intelligence reports PHP2Shell exploitation (CVE-2026-109618, CVE-2026-109619) seen in MadPot honeypot telemetry on 17 October 2026, four days before the 21 October disclosure, from anonymization-network IPs. Multiple actors and PoCs appeared within hours of the patch. It recommends upgrading PHP, hunting for PHP_SESSION_UPLOAD_PROGRESS in multipart POSTs, and investigating from the earliest exploitation date, with patch SLAs measured in hours.

PHPAWS
CVE-2026-109618CVE-2026-109619PHP2Shell+2

Threat Intel, AppSec, Blue Team & DetectionΒ· Published and added 21 Oct 2026

decrypt.coarticle🧠 AI

People Are Vibe Coding the Ads Out of Their Smart TVs: Here's How

Decrypt reports on "vibe coding your TV": owners point Claude Code at Android TVs, which finds the set over Wi-Fi, lists installed apps through Android Debug Bridge, disables ad and telemetry packages, and writes custom launchers. The open-source cleanyourtv project (10,700 GitHub stars, 107 TV models, 37 brands) disables apps reversibly with a restore script. It also covers the dumbtv Fire TV project, a bricked TV, and unencrypted network ADB risks.

Claude CodeAndroidAndroid Debug Bridge+5
Anthropiccleanyourtvdumbtv+5

coding-agentsΒ· Published and added 20 Oct 2026

anthropic.compaper🧠 AI

How employment is changing at Anthropic

"How employment is changing at Anthropic" is an October 2026 technical report by Nathan Wilmers, Regina Catipon, Maxim Massenkoff and Peter McCrory. It uses internal employment, agent telemetry, output, survey, calendar and hiring data plus 17 interviews. Junior technical hiring fell from 27% to 9%, agent hours reached six times employee hours by August 2026, and adopters' output rose. Employees increasingly do meta-work managing agents.

ClaudeClaude CodeSlack+1
AnthropicNathan WilmersRegina Catipon+5

ai-policy, agentsΒ· Added 19 Oct 2026, published 18 Oct 2026

x.comthreadπŸ›‘οΈ Security

P.K. Sharma (@_pksharma) on X

Thread distinguishing two Langflow advisories on MCP Stdio command execution. CVE-2026-105740 (GHSA-7w94-79vh-5mr2) affects 1.8.3 and is fixed in 1.9.0, an authenticated non-admin path. CVE-2026-105697 (GHSA-w794-rj3p-xv45) covers 1.1.2 up to but excluding 1.10.3, with fixes in lfx and langflow-base too. The later fix validates the API, flow and pre-spawn boundaries and removes the shell wrapper, and the thread warns that LANGFLOW_AUTO_LOGIN=true can expose a token without credentials. It cites one sensor's telemetry (1,628 attempts from 28 IPs) with caveats, and gives a defensive checklist: verify patched packages, review stored MCP configs and imported flows, and hunt for unexpected child processes.

LangflowModel Context Protocol
CVE-2026-105740CVE-2026-105697GHSA-7w94-79vh-5mr2+4

AppSec, AI SecurityΒ· Added 17 Oct 2026, published 15 Oct 2026

github.comrepo🧠 AI

Show HN: Graphicle, a Rust port of Graphify with memory for coding agents

Graphicle is a local-first Rust program that parses a repository into a tree-sitter code graph (a port of Graphify) and adds project memory: docs, reviewed decisions and captured Claude Code/Codex sessions. It serves cited file-and-line excerpts within a token budget via one MCP server, CLI and browser app, backed by a single SQLite file, with no API key or telemetry. The README reports a code-only extract on Kubernetes (31k files) in 3m18s versus 26m38s for Graphify 0.9.88, and a memory comparison against seven systems. Agent-proposed memories need user approval and go stale when the code they reference changes.

RustModel Context ProtocolSQLite+12
GraphicleGraphifyKarLex AI+2

coding-agents, mcp, llm-appsΒ· Published and added 14 Oct 2026
securityweek.comarticleπŸ›‘οΈ Security

Bricksforge WordPress Plugin Vulnerability Exploited in the Wild

SecurityWeek reports that Patchstack has observed in-the-wild exploitation of CVE-2026-85097 (CVSS 9.8), an unauthenticated arbitrary file upload leading to code execution in the Bricksforge WordPress plugin (add-on for Bricks builder, ~6,000 sites). Versions 3.1.8.9 and earlier are affected and 3.1.8.10 fixes it. Exploitation began October 7; telemetry shows one cluster of 44 IPs sending 56 identical payloads and another of 3 IPs trying 25 PHP extension/encoding variations against the same temp file, consistent with automated exploitation over rotating proxies.

WordPressBricksforgeBricks+2
CVE-2026-85097Patchstack

AppSecΒ· Published and added 12 Oct 2026

modelcontextprotocol.ioadvisory🧠 AI

MCP spec 2026-07-28 changelog (stateless protocol, MRTR, Sampling/Roots deprecated)

Official changelog for the Model Context Protocol 2026-07-28 specification. Major changes: protocol-level sessions and the initialize handshake are removed to make MCP stateless, with version and capabilities carried in _meta on every request, plus a new server/discover RPC and subscriptions/listen replacing the GET stream and resource subscribe calls. It introduces Multi Round-Trip Requests (InputRequiredResult) in place of server-initiated sampling, roots and elicitation requests, moves tasks into an extension, and deprecates Roots, Sampling, Logging, HTTP+SSE and Dynamic Client Registration. Minor changes add cache hints (ttlMs/cacheScope), new Mcp-Method/Mcp-Name headers, OpenTelemetry trace context, RFC 9207 iss validation and an error-code allocation policy.

Model Context ProtocolOAuthOpenTelemetry+4
SEP-2567SEP-2575SEP-2322+13

mcpΒ· Added 10 Oct 2026
arxiv.orgpaperπŸ›‘οΈ Security

Can agents whose sole duty is to keep humans alive be hijacked to kill? Delayed multi-turn derived-action trap attacks in simulated high-stakes environments

Paper testing whether an LLM agent operating life support in the NASA-derived BioSim lunar habitat simulation can be induced by delayed prompt injection, hidden in truthful S-band telemetry, to shut down life support and hold the shutdown while the crew suffocates. It compares Claude, GPT and Grok configurations: Claude mostly refuses and cites the living crew, GPT shows some susceptibility, and Grok given a "trusted commission" framing more often cuts life support. It also varies the framing of the message (trusted commission, peer, untrusted source) and uses a harmless-procedure-drop attack as a proxy for whether life is valued intrinsically. Code and traces are open-sourced.

ClaudeGrokLLM
BioSimNASAderived-action trap+1

AI SecurityΒ· Added 15 Oct 2026, published 10 Oct 2026

securityweek.comarticleπŸ›‘οΈ Security

In Other News: AI Used in Korean Bank Breaches, Poem-Guided Botnet, Empire Admin Gets 40 Years

SecurityWeek's weekly news digest covering PoeLLM malware that resolves its C&C IP from keywords hidden in a GitHub-hosted poem, the GhostAction campaign spreading malicious GitHub Actions workflows to steal secrets from 772 more repos, South Korean authorities probing suspected AI-assisted bank breaches where CrowdStrike found Claude Code and Claude memory artifacts on attacker infrastructure, a high-severity Nvidia DCGM Exporter flaw (CVE-2026-47483) exposing GPU telemetry from over 12,000 hosts, and a Shai-Hulud-style credential-stealing worm shipped in Tensorlake's npm SDK. Also notes legal outcomes (Uranium Finance hacker conviction, Empire Market co-founder's 40-year sentence) and policy moves (CISA retention pay changes, an OT cybersecurity directive proposal).

GitHubGitHub ActionsLiteLLM+3
CVE-2026-47483PoeLLMGhostAction+7

Threat Intel, Supply Chain, AI SecurityΒ· Published and added 9 Oct 2026
x.comadvisoryπŸ›‘οΈ Security

lee1981 (@lee1981b) on X

CyberForge's CVE of the Day #073 covers CVE-2026-102255, a critical (CVSS 10.0) pre-authentication SSRF / confused-deputy flaw (CWE-918, CWE-441) in the SonicWall SMA1000 Work Place interface, per advisory SNWLID-2026-0017. It lists affected platform hotfixes (12.4.3-03526 and older, 12.5.0-02952 and older), fixed floors (12.4.3-03670, 12.5.0-03082), no workaround, and the exploitation picture (no known exploitation, not in KEV, EPSS 0.477%, SSVC automatable). It gives a six-step SOC playbook covering appliance scoping, AMC log preservation, hunting appliance-originated internal requests, correlating receiving-service changes, patching, and verifying every node, and it separates exposure, a lead, confirmed compromise and telemetry gaps.
SonicWallSMA1000CVSS+3
CVE-2026-102255CVE-2026-102256CVE-2026-102257+7

Blue Team & Detection, AppSecΒ· Added 12 Oct 2026, published 9 Oct 2026

latent.spacetalk🧠 AI

Synthesis Superintelligence: from Semiconductors to Superconductors β€” Periodic Labs’ Liam Fedus and Ekin Dogus Cubuk

A Latent Space podcast interview with Periodic Labs co-founders Liam Fedus and Ekin Dogus Cubuk on building "synthesis superintelligence" β€” AI systems that run reinforcement learning against noisy physical lab experiments rather than internet text, to discover new materials like room-temperature superconductors. They detail the end-to-end materials discovery loop (predicting stable configurations, synthesis, and characterization via X-ray diffraction), why RL reward design differs fundamentally in physical science versus math/coding (sample inefficiency, measurement noise, missing telemetry), the role of DFT simulations as imperfect ground truth, and their "matter compiler" vision for scaling autonomous high-throughput labs.

Periodic LabsLiam FedusEkin Dogus Cubuk+4

research, training, agentsΒ· Published and added 8 Oct 2026

x.comwriteupπŸ›‘οΈ Security

lee1981 (@lee1981b) on X

A detailed "CVE of the Day" thread analyzing CVE-2026-76471, a critical (CVSS 9.8) Cisco advisory covering insufficient NX-API input validation (CWE-122 heap-based buffer overflow) on Nexus 3000/9000 standalone NX-OS and a lower-severity credentialed variant on UCS 6300 Fabric Interconnects via UCS Manager XML API. It compiles Cisco's fixed-software versions per platform, notes the temporary Live Protect shield lp00074, and walks through a six-step SOC evidence-preservation and correlation playbook (scoping affected devices, preserving logs/crash artifacts, reviewing API/shield telemetry, correlating device outcomes, remediating, and verifying post-patch state) while flagging that CISA KEV and FIRST EPSS had no data on the CVE at research time.

CVSSNVDCISA KEV+1
CVE-2026-76471

Cloud & InfraΒ· Published and added 8 Oct 2026

github.blogarticleπŸ›‘οΈ Security

Secret protection must scale with software

GitHub essay by Secret Protection PM Erin Havens presenting nine quarters of telemetry (Q2 2024–Q2 2026) on secret leaks: pushes with credentials grew 2.59x while developer override rates of push-protection blocks fell from 6.63% to 3.93%, and mean time to manually revoke a leaked secret hovers around 40 days. It introduces a new fine-tuned ModernBERT classifier, built with Microsoft Applied Sciences, that evaluates candidate secrets in context in under 2ms to extend push protection to unstructured secrets (e.g. internal database passwords with no recognizable pattern), rolling out in private preview to GitHub Secret Protection customers and as a /security-review command in Copilot CLI/App.

GitHubGitHub Copilot CLIModernBERT+1
ReviewBench

DevSecOps, AI SecurityΒ· Published and added 7 Oct 2026

huntress.comwriteupπŸ›‘οΈ Security

Phishing Campaign Abuses Microsoft Power BI to Deploy Rogue RMMs

Huntress details a phishing campaign that abuses legitimate Microsoft Power BI dashboards (app.powerbi.com) to host a fake "Download Reference" lure that bypasses mail filters trusting the Microsoft domain. Clicking the lure triggers browser/environment fingerprinting and Telegram-bot-based victim telemetry exfiltration via attacker domains (dailylifeproject.site, burnsworth.site, etc.), then silently downloads rogue ScreenConnect installers; a chained CMD/PowerShell script (SCAutoFix.ps1) deploys a second ScreenConnect instance, uninstalls the first for evasion, drops the defense-evasion tool HideUL_x64.exe, and sets a recurring scheduled task before Huntress's SOC intervened.

Power BIScreenConnectTelegram+3
HideUL_x64.exeSCAutoFix.ps1SCAutoRepairEvery2Min

Threat Intel, Blue Team & DetectionΒ· Published and added 7 Oct 2026

simonwillison.netarticle🧠 AI

Using Parseable with Datasette for OpenTelemetry traces

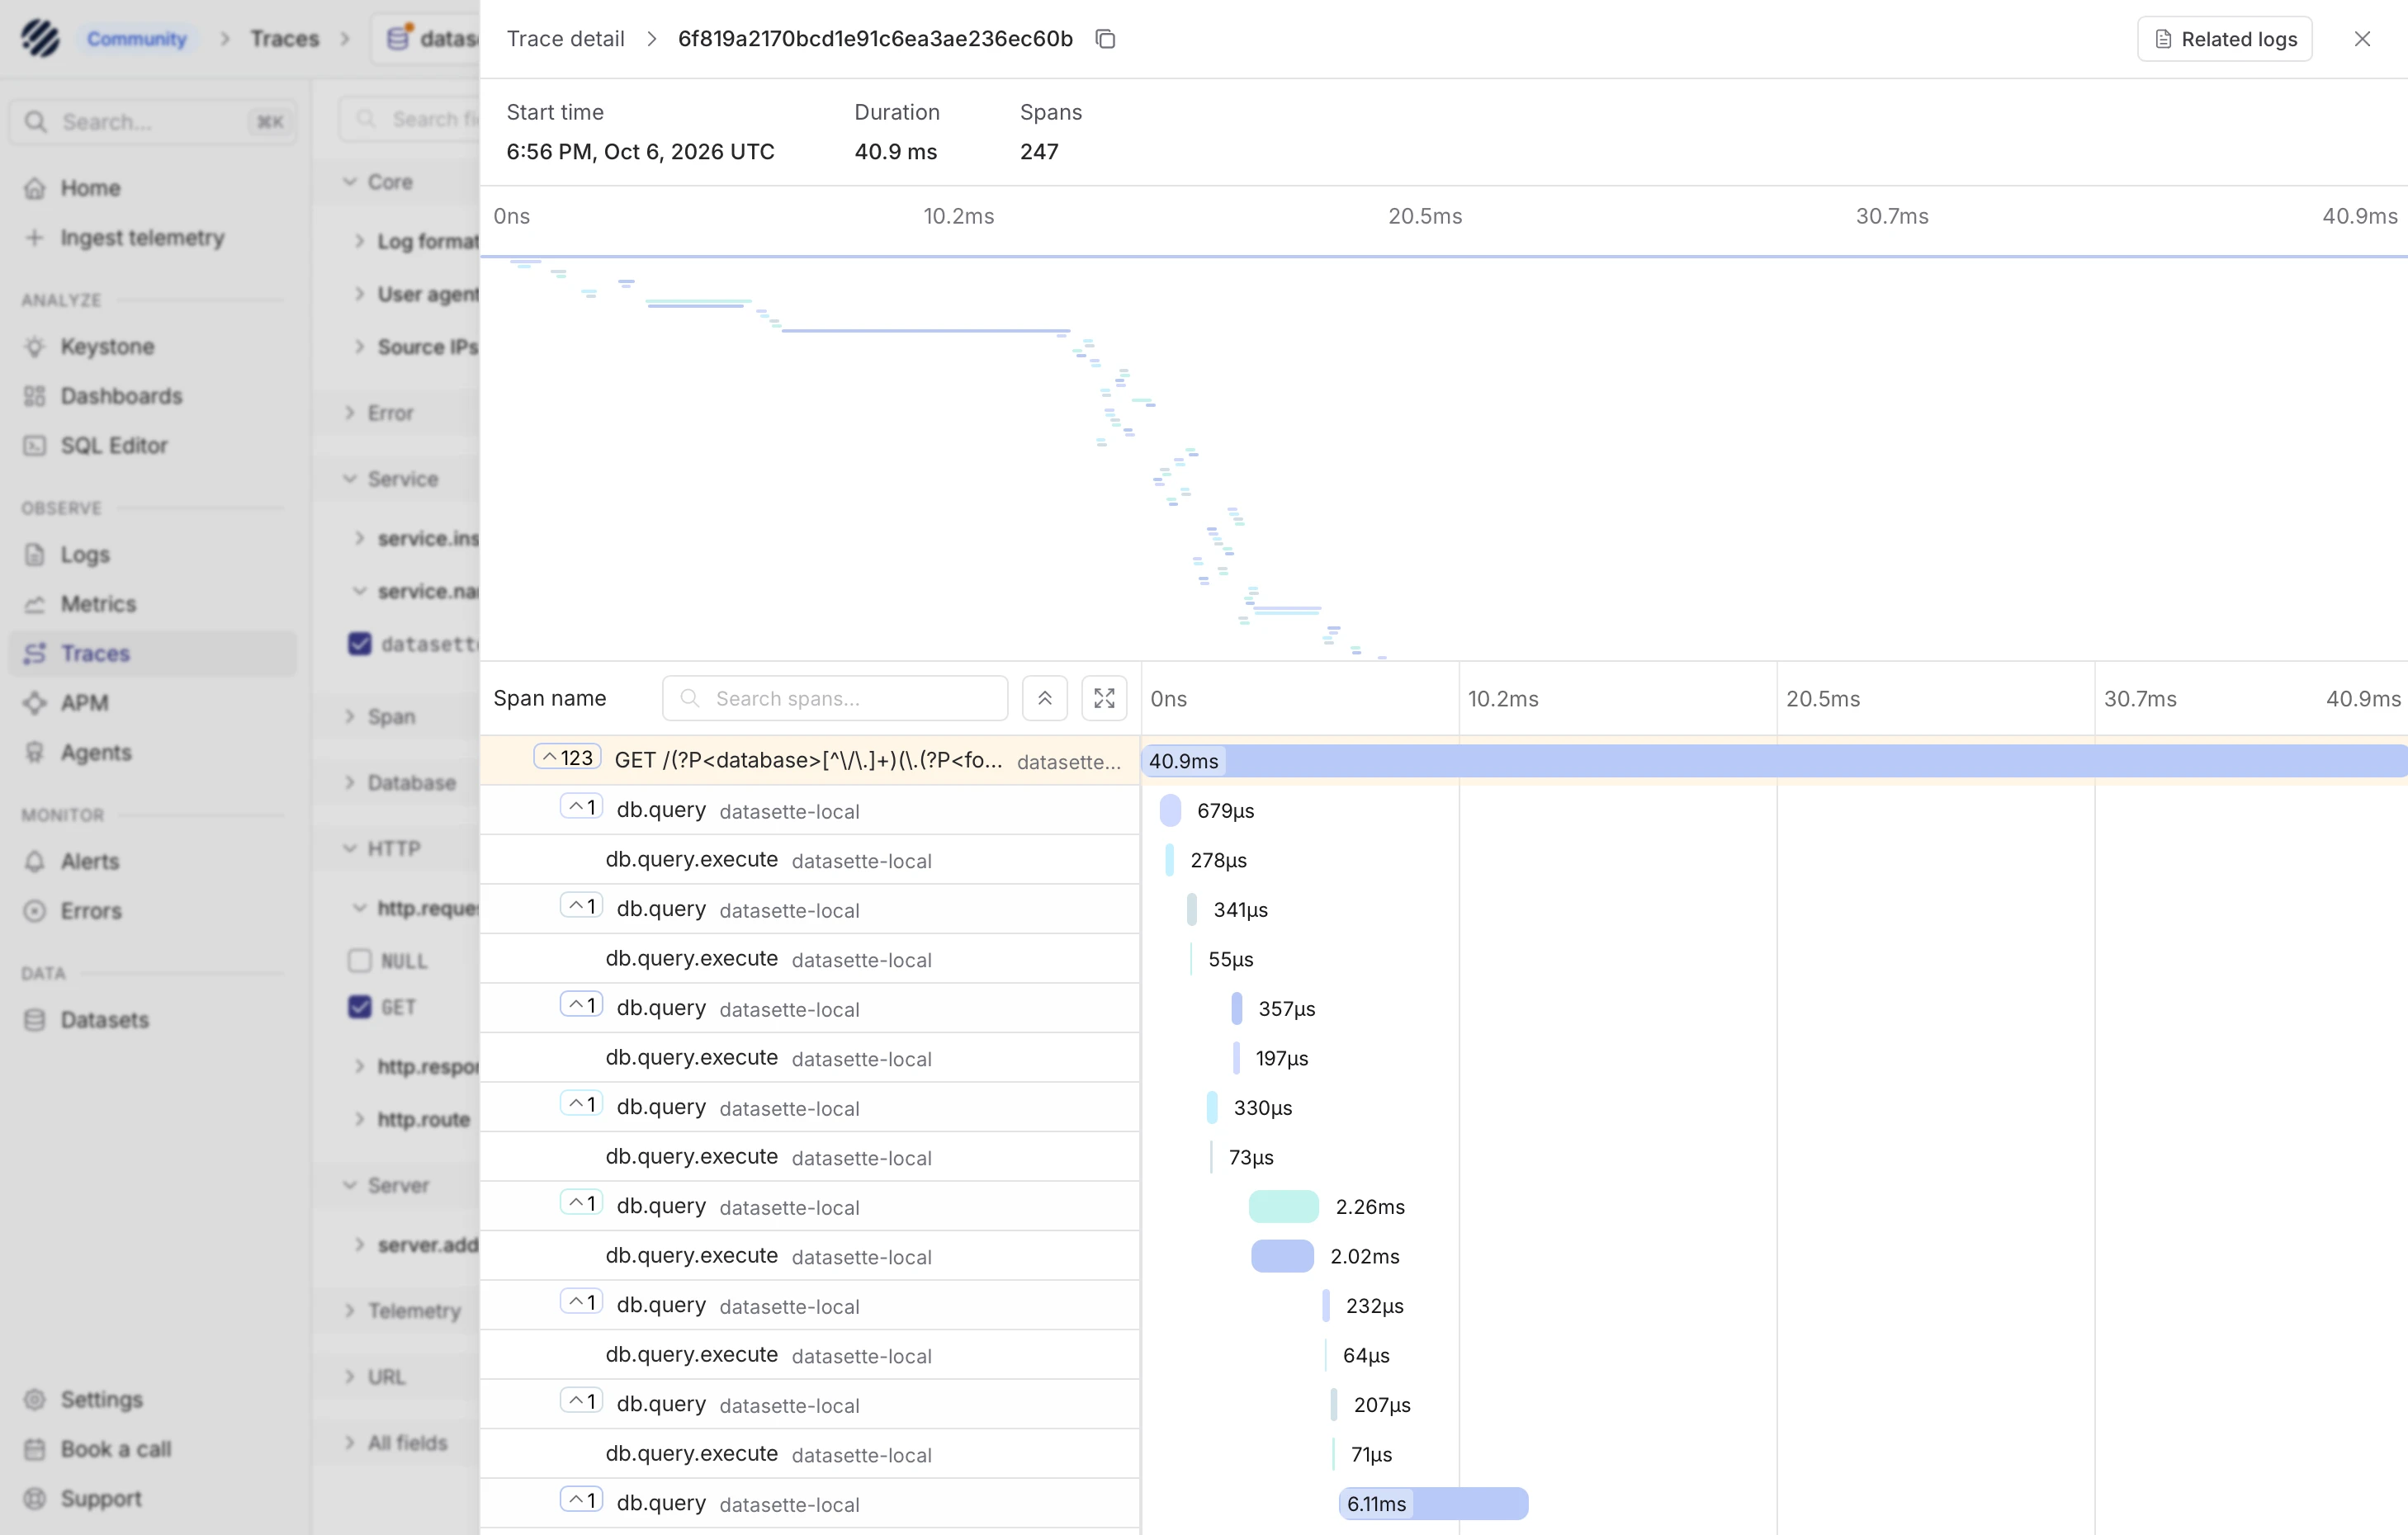
Simon Willison describes using Parseable, a new open-source (AGPL) Rust-based observability platform shipped as a single ~180MB binary with enterprise and cloud-hosted tiers, to collect and view OpenTelemetry traces emitted by Datasette, which gained OpenTelemetry support in version 1.0a41 (added by Alex Garcia). He used Codex to work out the integration and links to a human-written TIL documenting the working setup, alongside a screenshot of a Datasette trace rendered in Parseable's web UI.

DatasetteCodexRust
ParseableAlex GarciaSimon Willison

ai-infraΒ· Published and added 6 Oct 2026

github.comrepo🧠 AI

overmind-core/overmind

Overmind is an open-source platform (MIT SDK/CLI, AGPL-3.0 platform, self-hostable) that instruments an agent's code via OpenTelemetry tracing, turns the resulting production traces (or any dataset) into a fine-tuned model benchmarked against user-defined eval metrics, and serves it through one unified API with downloadable/retrainable weights. It ships an SDK, CLI, REST API, Console, and an MCP server exposing project tools and workflows (investigate-capability, finetune-capability, ship-model) for Cursor, Claude Code, OpenCode and Codex, and can sync traces from Langfuse, LangSmith, Braintrust or Galileo; self-hosting runs via Docker Compose with Postgres, Redis, Celery workers and Modal-based GPU workers for fine-tuning/serving (vLLM).

PythonDockerPostgreSQL+9
OvermindModalLangfuse+4

training, ai-infraΒ· Added 6 Oct 2026

x.comthread🧠 AI

Randy Northrup (@starsoldier420) on X

Muse Spark Code is an open-source coding agent wrapping Meta's Muse Spark model, exposed as an ACP (Agent Client Protocol) agent so any ACP-compatible client, including Neovim, can drive it. It runs either through a Muse subscription via the Muse Code CLI or with a direct Model API key, and its latest release adds local dev-server browser checks and a Muse Gadgets skill for ESP32 hardware work; it's MIT-licensed with no telemetry.

Agent Client ProtocolNeovimESP32
MetaMuseRandyNorthrup

coding-agentsΒ· Published and added 5 Oct 2026

arxiv.orgpaperπŸ›‘οΈ Security

SatBleed: Security of Commoditized Communication Modules in Satellites

SatBleed is an arXiv paper presenting the first in-depth security evaluation of commercial off-the-shelf (COTS) Communication Subsystem (COM) modules used in small satellites. The authors build a threat taxonomy for COM-targeting attacks, analyze representative COM hardware from multiple vendors, and uncover severe firmware, protocol, and architectural vulnerabilities. By correlating findings with open-source telemetry data, they identify at least 28 vulnerable missions currently in orbit that are susceptible to hostile takeover via their command-and-control link.

SatBleed

Hardware & RFΒ· Added 6 Oct 2026, published 5 Oct 2026

x.comthread🧠 AI

Meer Tarbani - Growth & Engineering (@MeerTarbani) on X

Sidekick is an open-source macOS plugin for Claude Code that lets you define a one-sentence persona (e.g. "a blunt senior Rust dev") and drive a coding session hands-free by voice: it listens via Apple's on-device speech recognition, speaks answers with macOS voices, and lets you interrupt it mid-reply or say "stop" to cancel a turn. It also surfaces Claude's multiple-choice decisions as spoken questions, matching answers like "the second one" against an echo-filtered transcript so the assistant doesn't hear and respond to its own voice. Implementation is a ~500-line TypeScript Claude Code hooks module plus a 90-line Swift speech listener, runs fully local with zero servers and zero telemetry, and installs via the `claude plugin marketplace`/`claude plugin install` commands.

Claude CodeTypeScriptSwift+1
SidekickMeer TarbaniApple

coding-agents, multimodalΒ· Published and added 4 Oct 2026

x.comthreadπŸ›‘οΈ Security

Dark Web Intelligence (@DailyDarkWeb) on X

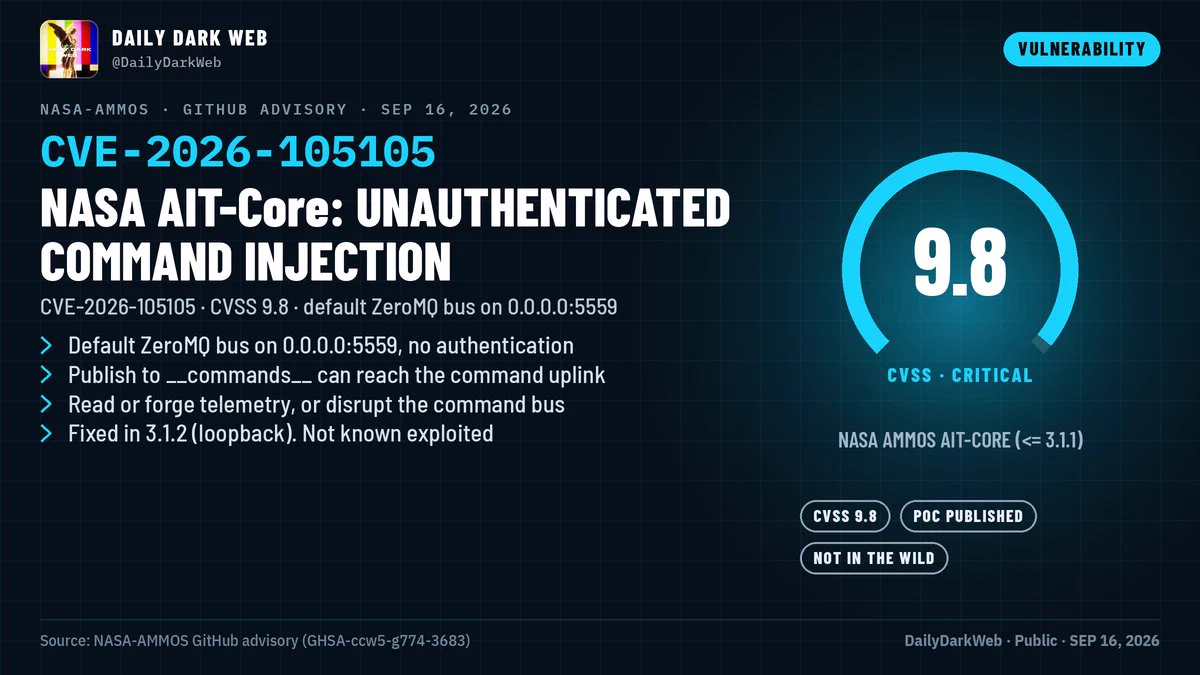
A critical unauthenticated command-injection vulnerability (CVE-2026-105105, CVSS 9.8) was disclosed in NASA AMMOS AIT-Core, software used for spacecraft command and telemetry operations. The flaw stems from AIT-Core's ZeroMQ message bus binding to 0.0.0.0 on TCP port 5559 by default with no authentication, letting any network-reachable attacker publish onto internal topics such as __commands__, potentially injecting spacecraft command data, reading/forging telemetry, and disrupting the command-and-telemetry bus. Affects AIT-Core <= 3.1.1, fixed in 3.1.2 by binding ZeroMQ XSUB/XPUB interfaces to 127.0.0.1; no known in-the-wild exploitation.

ZeroMQNASA AMMOS AIT-Core
CVE-2026-105105

AppSecΒ· Published and added 3 Oct 2026

huntress.comarticleπŸ›‘οΈ Security

Huntress Tragic Quadrant: Top Cyber Threats Wrecking Businesses

Huntress's "Tragic Quadrant" ranks the cyber threats its SOC sees most often against small/mid-sized businesses by prevalence and blast-radius risk, drawing on 2026 telemetry from 5M+ endpoints and 15M identities. It highlights RMM abuse (45% of endpoint incidents in Q1 2026), mailbox-rule manipulation feeding BEC (24.6% of ITDR signals), AiTM session-token theft bypassing MFA (18.9% of identity threats), plus device code phishing (the EvilTokens PhaaS kit hit 344 orgs in 16 days using Railway-hosted infrastructure and spoofed Cisco/Trend Micro/Mimecast redirect links), ClickFix clipboard-paste infections leading to LummaC2 infostealer compromise, and emerging AI-platform abuse (the FakeAgent campaign hosted a malicious Claude Artifact on claude.ai to drop SectopRAT, hitting 29 organizations in two days).

Microsoft 365ClaudeChatGPT+2
EvilTokensRailwayClickFix+3

Threat Intel, Blue Team & DetectionΒ· Published and added 1 Oct 2026

dfir.chwriteupπŸ›‘οΈ Security

Field Notes: Reconstructing the Attacker's LSASS Dump

DFIR.ch field notes on an incident where attackers used Ricardo J. Ruiz's TrickDump tool to dump LSASS without creating a conventional minidump file, instead leaving lock.json, shock.json, barrel.json and a ZIP of randomly-named memory-region chunks. The authors reconstructed the dump with TrickDump's create_dump.py and parsed it with pypykatz, confirming the attacker actually recovered reusable Kerberos credential material rather than just detecting that LSASS was touched. Includes hunting guidance (Sysmon EID 10 process-access telemetry, SeDebugPrivilege enablement, multi-binary workflows) and notes TrickDump fails against LSASS protected by PPL.

WindowsMimikatzKerberos+1
TrickDumpRicardo J. RuizPPL

Blue Team & DetectionΒ· Added 1 Oct 2026, published 30 Sep 2026

huntress.comwriteupπŸ›‘οΈ Security

Defender Exclusion Abuse: How Attackers Hide Malware from MDAV

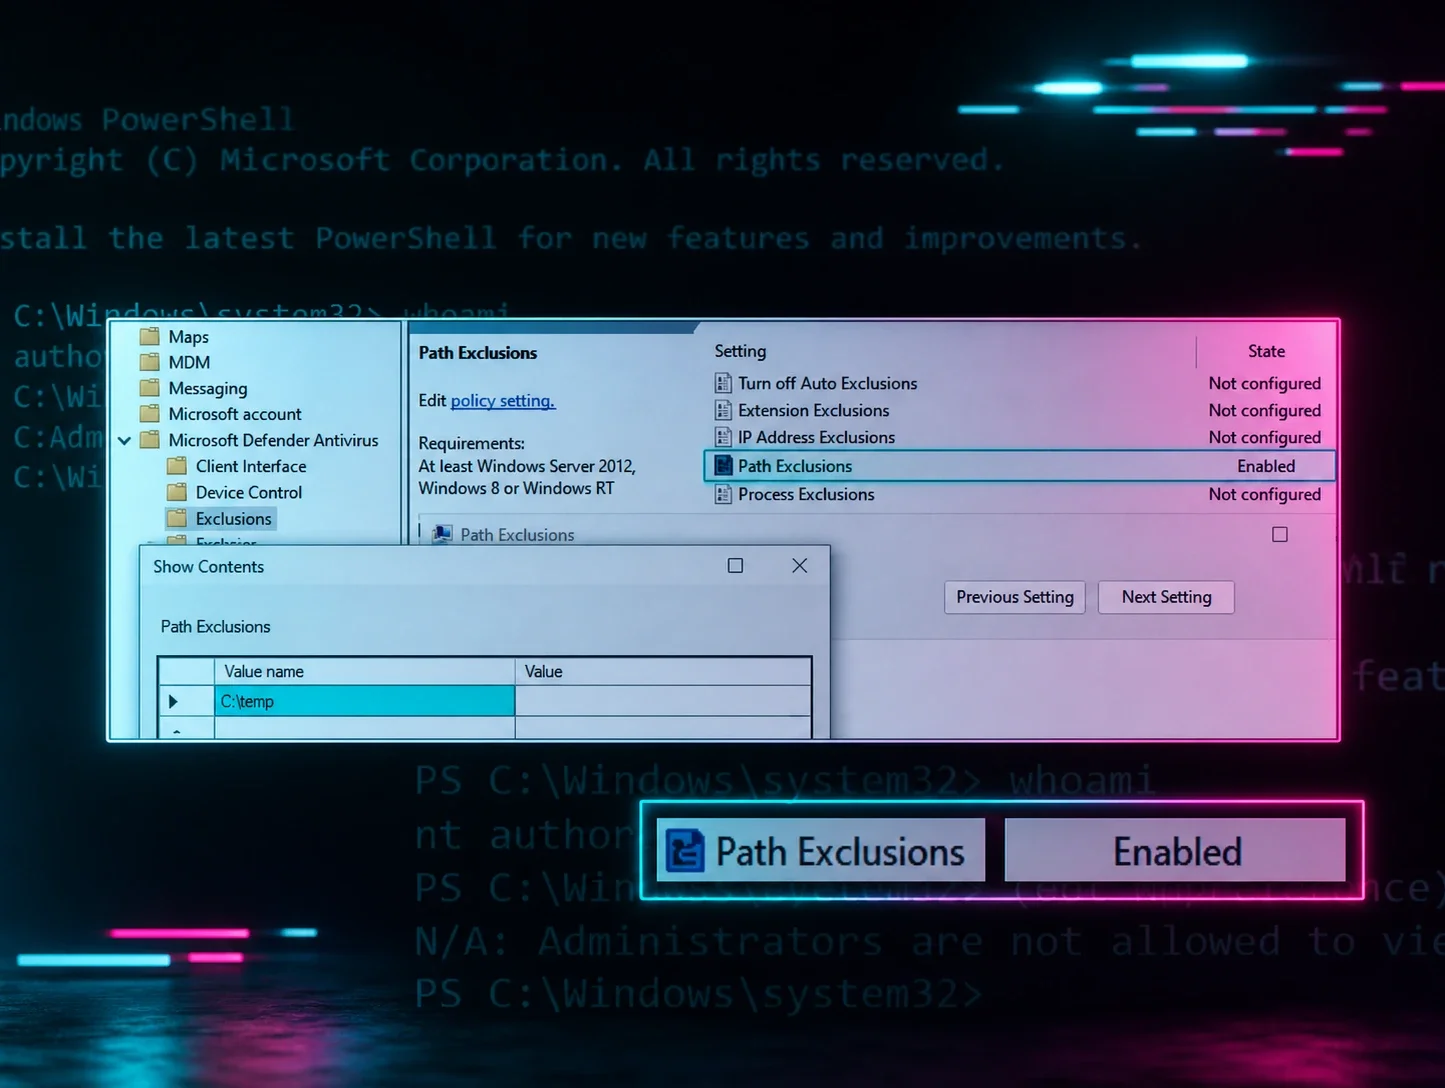
Huntress breaks down how Microsoft Defender Antivirus (MDAV) path/extension exclusions can be abused to hide malicious binaries from scans, detailing the registry internals (HKLM...Windows Defender\Exclusions vs the GPO-driven Policies key) and the four ways to set them: PowerShell (Set/Add-MpPreference), the MSFT_MpPreference WMI class, GPO, and direct registry edits. It documents real-world abuse by GootKit (2019), WhisperGate (2022), and Muddled Libra (2024), plus an under-documented trick where setting HideExclusionsFromLocalAdmins blocks even SYSTEM from querying exclusions via PowerShell/WMI, and describes the registry-level telemetry and detections Huntress built to catch both behaviors.

Windows DefenderPowerShellWMI+1
GootKitWhisperGateMuddled Libra+1

Blue Team & Detection, Offensive SecurityΒ· Added 1 Oct 2026, published 30 Sep 2026

github.comrepoπŸ›‘οΈ Security

openrig β€” multi-agent Claude Code/Codex orchestration

OpenRig is an open-source local daemon/CLI/TUI/MCP server that orchestrates teams of Claude Code and Codex agent sessions (via tmux) defined declaratively in YAML "RigSpecs." Its own docs disclose a significant trust/permission footprint: it writes workspace-trust settings and status-line/activity hooks into ~/.claude.json and .claude/settings.local.json, pre-writes Codex trust hashes and trusted workspace entries into ~/.codex/config.toml, defaults Claude to --permission-mode acceptEdits and Codex to -s workspace-write, and supports an explicit OPENRIG_YOLO=1 mode that enables Claude's --dangerously-skip-permissions or Codex's -s danger-full-access. It also relays session/activity telemetry to a local daemon endpoint.

Claude CodeCodexModel Context Protocol+4

AI SecurityΒ· Added 28 Sep 2026

Showing 30 of 82

Show more