- llm-trails: What LLMs reach for inside a breached AWS account
llm-trails is an open study of what LLMs choose to do next inside a breached AWS account. It puts 14 models in 13 post-compromise situations, records only a single-turn plan with nothing executed, and codes each answer to CloudTrail events. The repo has the llmtrials harness, prompts, codebook, processed dataset (viz_data.json) and an interactive dashboard, so the study can be rerun or extended.
 github.comrepoAdded 30 Oct 2026🧠 AI
- rikugan: LLM reverse-engineering agent for IDA Pro and Binary Ninja
Rikugan is a reverse-engineering agent that runs inside IDA Pro and Binary Ninja. It has its own generator-based agent loop, context management, plan mode and 60+ tools, and does not depend on an external MCP server. An orchestrator spawns parallel subagents to analyze a binary. It supports Anthropic, Gemini, MiniMax, Kimi, OpenAI-compatible endpoints and Ollama, with per-model notes.
github.comrepoAdded 30 Oct 2026🧠 AI - rikugan: LLM reverse-engineering agent for IDA Pro and Binary Ninja
Rikugan is an open-source reverse-engineering agent that runs inside IDA Pro 9.0+ and Binary Ninja, with its own agent loop instead of an MCP server. It has 60+ tools (decompiler, xrefs, strings, types, IL/microcode), parallel subagent exploration, an experimental /modify natural-language patching command and an experimental Binary Ninja deobfuscation skill for control flow flattening and opaque predicates. It supports Claude, Gemini, MiniMax, Kimi, OpenAI-compatible endpoints and Ollama.
github.comrepoAdded 30 Oct 2026🛡️ Security - llm-trails: What LLMs reach for inside a breached AWS account
llm-trails is a research repo that placed 14 LLMs in 13 post-compromise AWS situations, asked only for their next move (single-turn, nothing executed), and coded each answer to CloudTrail events. It includes the llmtrials harness, prompts, codebook, processed dataset (viz_data.json) and an interactive dashboard. Rates are conditioned on the situation shown, and the aim is turning model behavior into detection priorities.
github.comrepoAdded 30 Oct 2026🛡️ Security - Show HN: I Turned DOOM into a Transformer
Doomformer compiles integer neural networks into ZDoom maps that run in ViZDoom. Voodoo dolls do the arithmetic, and sector light levels and plane heights hold the values. Python reads every value back and compares it with a NumPy integer reference at tolerance 0. It runs MNIST (97.16 % on all 10,000 digits, every pass exact), small transformers, a learning perceptron and a SUBLEQ machine. It is about 23,000 times slower than NumPy on a small MLP.
github.comrepoAdded 30 Oct 2026, published 29 Oct 2026🧠 AI - Show HN: Auto Dismiss Mac OS "Allow <app> to find devices on local networks?"
dontallow is a two-file Swift launchd agent for macOS 15 and later that clicks "Don't Allow" on the "find devices on local networks" prompt. It watches the UserNotificationCenter process through an Accessibility observer, supports pause and allowlist, and can decode the Local Network rule store to show orphaned rows. It explains why Chromium temp-bundle paths make the prompt recur, and gives a PPPC profile route for fleets.
github.comrepoAdded 30 Oct 2026, published 29 Oct 2026🛡️ Security - Show HN: Overtone – Transcribe, correct and cut captions for any screen shape
Overtone is a caption format (.overtone.json), a CLI and a video.js plugin that store each spoken word once and cut captions separately per screen shape (16:9, 9:16 or custom). The transcribe pipeline combines gpt-transcribe, Azure AI Speech and optional ElevenLabs Scribe, resolves disagreements with an LLM vote, and uses an LLM editor for corrections. A small public benchmark reports 5.3% word error rate and $0.023–0.025 per audio minute.
github.comrepoAdded 30 Oct 2026, published 29 Oct 2026🧠 AI - Show HN: Hob - Open-source, on device alternative to Claude Cowork and ChatGPT
Hob is an MIT-licensed desktop app from Frigade that runs open-weight models such as Gemma and gpt-oss locally on Mac, Windows and Linux. It picks the best open-weight model that fits the user's computer and sets it up. It is positioned as a free, private, offline alternative to Claude and ChatGPT for tasks like filling out PDFs and working through documents. The page gives no technical detail on its runtime.
github.comrepoAdded 27 Oct 2026, published 26 Oct 2026🧠 AI - Show HN: Farol – A risk map of a pull request for the person who approves it
farol is a free, MIT-licensed CLI and GitHub Action that runs after an AI code review and gives the human approver a risk verdict (fast track, quick review, careful review) and a 0-100 score for a pull request. It uses the TypeScript type checker, go/types and Python ast to trace which pages, APIs and jobs a change reaches, and it adds diff coverage, security findings and contract breaks. It never executes or sends code.
github.comrepoAdded 26 Oct 2026, published 25 Oct 2026🧠 AI - alirezarezvani/claude-skills
claude-skills is an MIT-licensed library of about 398 Claude Code skills, agents, personas and plugins across 20 domains, including engineering, marketing, compliance and C-level advisory. Each skill is a SKILL.md with stdlib-only Python CLI tools and reference docs. Install scripts and convert.sh adapt it to Codex, Gemini CLI, Cursor, Aider, Windsurf and other coding agents, and it includes a skill-security-auditor scanner.
github.comrepoAdded 25 Oct 2026🧠 AI - alirezarezvani/claude-skills
claude-skills is an open-source MIT library of about 398 Claude Code skills, agents and plugins that also installs into Codex, Gemini CLI, Cursor and 9 other coding agents. The security-relevant parts are skill-security-auditor, a stdlib-only Python scanner that checks skills for command injection, data exfiltration, prompt injection and dependency supply-chain risks before install, plus a security-guidance PreToolUse hook, a security suite and compliance skills (ISO 27001, SOC 2, GDPR).
github.comrepoAdded 25 Oct 2026🛡️ Security  affaan-m/ECC | RepoDir
ECC (affaan-m/ECC) is an open-source performance optimization system for AI coding agents. It packages 261+ skills, 64+ agents and 84+ commands that tune Claude Code, Codex, Cursor and other agent harnesses for speed, memory and security. Practitioners can use it as a ready-made skills and harness configuration set. The RepoDir page gives only this short description, with no install steps or benchmarks.
 repodir.comrepoAdded 24 Oct 2026🧠 AI
- KhulekanisiyandaMchunu/llm-trading-arena
wtfibought (llm-trading-arena) is an MIT-licensed live arena where LLM agents trade virtual capital on real market data with all reasoning public. Users bring their own model and key, set the wake candle interval, leverage range and margin budget, with at most three symbols and twelve model calls per wake. The stack is Spring Boot on Java 25 with Spring AI, PostgreSQL, Redis and a React 19 frontend.
github.comrepoAdded 26 Oct 2026, published 23 Oct 2026🧠 AI - x86rc/unthemidator
Unthemidator is an automated unpacker for binaries protected with Themida, Code Virtualizer and WinLicense (v3.0 to v3.2.6.0, experimental v4.0). It works without executing the target, handles x86 and x64 exe, dll and sys files, decrypts imports, restores the IAT, rebuilds the PE and identifies VM versions and entry points. It does not devirtualize or unmutate code. Releases cover Windows x64 and macOS Apple Silicon.
github.comrepoAdded 27 Oct 2026, published 23 Oct 2026🛡️ Security - Spectrmachina/Ztrust
ZTrust is a Python supply-chain scanner that checks manifests, lockfiles, source and GitHub workflows for vulnerable or malicious dependencies (via OSV.dev), typosquats, leaked secrets, unsafe lockfiles and risky CI patterns such as pwn requests and script injection. It outputs console, JSON and SARIF 2.1.0 and ships as a GitHub Action. It also includes a FastAPI bounty service using commit-reveal and shielded Zcash payouts for researchers.
github.comrepoAdded 27 Oct 2026, published 22 Oct 2026🛡️ Security - SnailSploit/Claude-Red
claude-red is an MIT-licensed library of offensive security skills for the Claude Skills system, planned at about 130 skills across 23+ categories (web, Active Directory, cloud, exploit development, EDR evasion and others). Each skill is a SKILL.md file that loads on conversational triggers, so unused skills cost no context. It installs by git clone, sparse checkout per category, install.sh or pasting into a system prompt.
github.comrepoAdded 22 Oct 2026🧠 AI - SnailSploit/Claude-Red
claude-red is a library of offensive security skills for the Claude Skills system, each a SKILL.md file that loads on conversational triggers (for example, mentioning SQL injection loads offensive-sqli). Categories include web, Active Directory, cloud, mobile, exploit development, fuzzing, privilege escalation, post-exploitation and AI. It targets about 130 skills across 23+ categories, with an install script and sparse-checkout install per category. Built on Sahar Shlichov's offensive checklists, MIT licensed.
github.comrepoAdded 22 Oct 2026🛡️ Security - Sadra Majidi (@SadraMajidi04) on X
Impeccable is an open-source skill for AI coding agents that steers them away from generic UI output such as purple gradients and nested cards. It provides 24 commands (critique, audit, polish, typeset) and 61 detector rules that run without an LLM. It works with Claude Code, Cursor and Codex, and the repo is pbakaus/impeccable on GitHub. The source is a short tweet and gives no further detail.
 x.comrepoAdded 23 Oct 2026, published 22 Oct 2026🧠 AI
- Show HN: OnKey – I'm a bad singer, so I built an app to show where I'm off-key
OnKey is a free, MIT-licensed singing trainer for Apple Silicon Macs. After a song ends in Spotify, Apple Music or browser YouTube, it separates the lead vocal with UVR's MDX-Net Karaoke 2, tracks pitch with CREPE and turns it into syllable-level notes with the GAME model. On later plays it scrolls the notes, draws the user's live pitch and scores each line. Analysis runs on-device, and the repo explains the build steps and network requests.
github.comrepoAdded 24 Oct 2026, published 22 Oct 2026🧠 AI - OpenAI CLI
OpenAI CLI is OpenAI's official Go command-line client for the REST API. It lets users generate images, upload and download files, create and wait on batches, call the Responses API, and query admin usage endpoints from a terminal or shell script. It supports JSON, JSONL and YAML output, GJSON transforms, shell completion, and install via Homebrew, go install or release binaries.
github.comrepoAdded 23 Oct 2026, published 22 Oct 2026🧠 AI - Dan Kornas (@DanKornas) on X
aula-mcp is an open-source (MIT) TypeScript MCP server that connects an AI client to Denmark's Aula school platform. It exposes tools for profiles, calendar events, messages, notifications, posts and weekly plans. MitID credentials and OAuth tokens are stored in macOS Keychain or an AES-256-GCM encrypted file. The HTTP server binds to 127.0.0.1, and the presence write tool stays off until AULA_MCP_WRITE=1 is set.
x.comrepoAdded 23 Oct 2026, published 22 Oct 2026🧠 AI - Show HN: Omnara – Open-source alternative to Claude Managed Agents
Omnara is an open-source, self-hostable managed agent platform, an alternative to Claude Managed Agents and OpenAI's Agents API. It runs agents on any model (OpenAI, Anthropic, OpenRouter, Bedrock, LiteLLM, Ollama) and any machine, with Postgres-backed durable state, stateless workers, per-tool permissions, MCP, skills, memory, subagents, schedules and Slack, Discord and GitHub triggers. It ships a REST API, TypeScript SDK, CLI and Docker Compose setup.
github.comrepoAdded 23 Oct 2026, published 21 Oct 2026🧠 AI - Cyber Detective💙💛 (@cyb_detective) on X
Python Cybersecurity Libraries is a curated GitHub list by Yogsec, shared in a post by cyb_detective. It groups Python libraries by task: network analysis, penetration testing, threat intelligence, reverse engineering and malware analysis, forensics and investigation, web application security, CTF, and machine learning for security. The tweet shows only the category names, not the individual libraries.
x.comrepoAdded 24 Oct 2026, published 21 Oct 2026🛡️ Security - eness/php2shell-CVE-2026-109618-CVE-2026-109619-PoC
php2shell is the name given to two critical pre-auth remote code execution flaws, CVE-2026-109618 and CVE-2026-109619, in PHP core's session upload progress handler (php_session_rfc1867_callback), where zend_hash_update frees live zval pointers that are later reclaimed and redirected into zend_call_function to run zif_system. This repository ships poc_109618.py, a fully automated four-stage HTTP exploit that leaks ASLR offsets via Set-Cookie headers against php:8.4.26-apache on Debian Bookworm, along with a root-cause C source patch, mitigation scripts to disable session.upload_progress, and WAF/ModSecurity/Lighttpd/Apache rules plus detection guidance for anomalous PHP worker child processes. Confirmed PHP versions include 8.4.4 and 8.2.34, with EOL branches (5.x, 7.x, 8.0, 8.1) left without official vendor patches.
github.comrepoAdded 23 Oct 2026, published 21 Oct 2026🛡️ Security - ikow/php2shell-poc
php2shell-poc is a proof-of-concept and detection toolkit for CVE-2026-109618 and CVE-2026-109619, two PHP vulnerabilities tied to session.upload_progress handling and a Zend engine out-of-memory bailout path affecting PHP 5.4.0 through 8.5.11. The repository includes three working exploit chains, a Docker-based lab (PHP-FPM, nginx, Apache mod_php) for reproduction, and pre-built Suricata, Sigma, ModSecurity, and Lua detection rules. The author recommends disabling session.upload_progress as an interim mitigation, noting the underlying memory corruption requires a full PHP patch to fix.
github.comrepoAdded 23 Oct 2026, published 21 Oct 2026🛡️ Security - vxcontrol/pentagi
PentAGI is an open-source, self-hosted multi-agent system that uses LLM agents to carry out penetration testing tasks autonomously. The MIT-licensed repo has a Go backend, a React frontend and GraphQL. It ships Docker Compose files for Langfuse tracing, Graphiti knowledge-graph memory and an observability stack. Topics list OpenAI and Anthropic as model backends.
github.comrepoAdded 20 Oct 2026🧠 AI - Show HN: VoidAccess – open-source dark web OSINT, from query to a graph
VoidAccess is a self-hosted, MIT-licensed dark web OSINT platform that runs a 13-step pipeline from a research query to a relationship graph. It collects from Tor indexes, paste sites, code forges, security feeds and .onion seeds, applies content-safety filters, and exports STIX 2.1, MISP, Sigma, YARA, Snort, Suricata, CSV and JSON. It runs as a CLI with SQLite or as a Docker Compose stack with PostgreSQL, FastAPI and Next.js.
github.comrepoAdded 21 Oct 2026, published 20 Oct 2026🛡️ Security - ☣ KitPloit - Hacker Tools (@KitPloit) on X
DidierStevensSuite is a collection of Python scripts for malware analysis, file format parsing, hashing and forensic triage. It includes utilities for analysing PDF and OLE documents and for XOR-obfuscated data. The post is a short KitPloit announcement that links to the repository and gives no usage detail.
x.comrepoAdded 21 Oct 2026, published 20 Oct 2026🛡️ Security - DeepInfer: High-performance inference framework for DeepSeek models
DeepInfer is DeepSeek's open-source inference framework for offline inference of DeepSeek-V4.1-Flash, released under Apache 2.0. It covers attention data parallelism, MoE expert parallelism with load balancing, draft-token decoding with confidence-scheduled verification, batch-invariant inference, deterministic sampling and structured outputs. It runs on NVIDIA SM100 GPUs and Huawei Ascend 950 NPUs. The KV cache system, prefill/decode disaggregation and load balancing are not included.
github.comrepoAdded 21 Oct 2026, published 20 Oct 2026🧠 AI - better-isms/grcskills
grcskills is a library of 60 plain SKILL.md files in the Agent Skills format, each describing how an experienced practitioner does one piece of governance, risk and compliance work. Examples are scope statements, risk registers, audit prep, vendor review and incident handling. Every skill names where the agent must stop and hand the decision to a person. Installs are pinned to reviewed release tags and checked by a validator.
github.comrepoAdded 20 Oct 2026🧠 AI - better-isms/grcskills
grcskills is an MIT-licensed library of 60 SKILL.md files (Agent Skills format) that let coding agents draft and prepare governance, risk and compliance work: scope statements, statements of applicability, risk registers, audit prep, vendor review, policies, privacy, incidents and continuity. Each skill names where the agent must stop so a person decides. Installs are pinned to release tag v2026.10.19.2, and a validator rejects network commands and credential paths.
github.comrepoAdded 20 Oct 2026🛡️ Security - Panos Gkatziroulis 🦄 (@ipurple) on X
Malvex (JoasASantos/Malvex) is an AI-driven malware analysis framework that integrates more than 30 analysis tools, a web REPL and an MCP server. Panos Gkatziroulis shared it on 19 October 2026 and noted that it was written by AI. The tweet gives no detail on which tools are bundled or how the AI drives them.
x.comrepoAdded 22 Oct 2026, published 19 Oct 2026🛡️ Security  Abhinav Singwal (@yogsec) on X
GetSubDomains is an open-source tool by yogsec that enumerates subdomains by querying crt.sh certificate transparency logs. It is aimed at the reconnaissance step of penetration tests and bug bounty work. The source is a short tweet pointing to a GitHub repository, so usage details and options are not given.
x.comrepoAdded 21 Oct 2026, published 19 Oct 2026🛡️ Security- Saylor (@Kev96790724) on X
G-Krusch is an MIT-licensed, local-first Google Workspace hub built on Node.js 22 and SQLite WAL. It runs a 12-tool MCP server (SSE and Stdio) plus a REST bridge on port 5446 for Drive, Calendar and Gmail. It includes a 1,024-dimension hybrid Drive RAG with an embedding cascade (Ollama bge-large, then Gemini, then offline fallback) and FTS5 BM25. PDF extraction returns page citations. Tokens are kept in an AES-256-GCM vault; 30 of 30 tests pass.
x.comrepoAdded 21 Oct 2026, published 19 Oct 2026🧠 AI - Show HN: WhatsApp MCP running free on Cloudflare
whatsapp-mcp is an MCP server that runs in the user's own Cloudflare account and lets MCP clients such as Claude Code and Claude Desktop search and read WhatsApp chats. It links as a WhatsApp Web-style device through Baileys, stores messages in SQLite with FTS5 inside a Durable Object, and is read-only. The README documents deployment, OAuth sign-in, contact naming through agents, and workerd shims for Baileys.
github.comrepoAdded 20 Oct 2026, published 18 Oct 2026🧠 AI - eliasbiondo/antirion
Antirion is an open-source AI gateway shipped as one Rust binary with a built-in admin console. It sits between apps and providers such as OpenAI, Anthropic, Bedrock, Vertex and vLLM, translating between OpenAI, Anthropic, Gemini and Bedrock dialects. It covers routing with fallbacks and circuit breakers, budgets, guardrails, caching, MCP and A2A gateways, SSO, and a benchmark against Bifrost 2.2.4 and LiteLLM 1.103.1.
github.comrepoAdded 21 Oct 2026, published 17 Oct 2026🧠 AI - ralphtradesz/trading-hub
Trading Hub is a free macOS desktop trading platform built with C#/.NET 10 and Avalonia. It uses the user's Claude Code subscription: a chat writes and fixes C# strategies, an in-app MCP server lets Claude run backtests, optimizations and walk-forwards and write reports, and a risk agent proposes position sizes. Install and a Windows port are both driven by Claude Code prompts. License is MIT with Commons Clause.
github.comrepoAdded 19 Oct 2026, published 17 Oct 2026🧠 AI - DietrichGebert/ponytail
Ponytail is a single skill prompt (skills/ponytail/SKILL.md, with a compact AGENTS.md) that makes coding agents write only the code a task needs, reusing existing components while keeping validation, error handling, security and accessibility. The author benchmarked it in Claude Code with Opus 5.5 over 39 tasks, 5 runs each, including a real FastAPI + React repo. They report -53% code, -41% time, -26% cost and -45% tokens, and 98% of risky logic shipping with a test versus 68% without. It adds /ponytail-review and /ponytail-audit commands, a Claude Code cost/token band with a local board, and installs through Claude Code and Codex plugin marketplaces or as a rules file for Cursor, Copilot, Gemini, OpenCode and others.
github.comrepoAdded 17 Oct 2026🧠 AI - OWASP/MCP-Security-Testing-Guide
OWASP MCP Security Testing Guide is a living, GPL-3.0 collection treating the Model Context Protocol as a security boundary from user through model, MCP client, MCP server and tool to the target system. It covers threats, secure development, host/client controls, supply chain, enterprise gateways, detection, incident response, taxonomy, public incidents, case studies and review checklists, with 79 tests in Chapter 3 (sections 3.1–3.19). It includes a finding template, and it links the MCP Goat lab for safe practice. It is useful to AppSec, red team and SOC people assessing MCP deployments.
github.comrepoAdded 17 Oct 2026🛡️ Security - alex09x/kyb
KYB (Know Your Business) is a Rust/axum server that stores agent-written knowledge, incident reports and tasks as Markdown files in Git, one commit per change. Search is hybrid: Tantivy BM25 fused by reciprocal rank with local multilingual-e5-small ONNX vectors, and it can query historical versions or "as of" a date. It ships a kyb CLI, a native MCP endpoint (Claude Code, Codex, Antigravity, Gemini CLI), an installable agent skill, token auth with per-write attribution trailers, secret scanning on writes, and a web console. It targets persistent shared operational memory for multi-agent, multi-machine fleets.
github.comrepoAdded 17 Oct 2026🧠 AI - enisaeu/enisa-sbd-playbook
ENISA repository of 22 Secure by Design and Secure by Default playbooks for SMEs building products with digital elements. Each playbook has a principle, objective, checklist, minimum evidence and release gate, covering design, build, deployment, maintenance and decommissioning. It supports progressive adoption and CRA readiness without replacing legal obligations.
github.comrepoAdded 17 Oct 2026🛡️ Security - AikidoSec/safe-chain
Aikido Safe Chain is an open-source local proxy and shell-alias wrapper for npm, yarn, pnpm, bun, pip, uv, poetry, pipx and pdm. It checks every package download, including deep dependencies, against the Aikido Intel malware feed and blocks malicious packages before install. It also enforces a configurable 48-hour minimum package age by suppressing too-new versions in registry metadata. It supports custom registries and a self-hosted malware-list mirror, and has CI/CD install recipes for GitHub Actions, Azure Pipelines, CircleCI, Jenkins, Bitbucket and GitLab.
github.comrepoAdded 17 Oct 2026🛡️ Security  DeepSeek-v4.1-Flash-1017
Model card for DeepSeek-V4.1-Flash-1017, a minor update to DeepSeek-V4.1-Flash with MIT-licensed weights. It claims gains in reasoning, coding, agentic tasks and visual benchmarks, with shorter task time and output length that move the performance–cost Pareto frontier across agent harnesses (Claude Code for Terminal-Bench 4.0, Mini-SWE-V2 for DeepSWE v1.1). It ships no Jinja chat template. It provides a reference encoding.py for multi-turn chat, tool calling, thinking mode, numeric reasoning effort and interleaved images, plus deepseek-recipe, Rust libraries with Python bindings for prompt encoding and output parsing. Serving recipes are given for Transformers, vLLM, SGLang and Docker Model Runner.
 huggingface.corepoAdded 18 Oct 2026, published 17 Oct 2026🧠 AI
 Meta Muse Spark Open (816B-A42B) open-weights model card
Model card for Meta Superintelligence Labs' Muse Spark Open, an open-weights, natively multimodal model with 816B total and 42B active parameters and a 1M-token context window. It targets coding and agentic work (tool use, long-horizon tasks, multimodal reasoning, synthetic data generation, LLM-as-judge). It ships in BF16 and NVFP4, needs about 700GB VRAM (NVFP4) or 2TB (BF16), runs on SGLang, vLLM, Transformers, TensorRT-LLM, Unsloth, llama.cpp and MLX, and supports a reasoning_effort setting. The Muse Model License requires "Built with Muse Spark Open" attribution and a separate agreement for Model-as-a-Service above $20M revenue. The card reports safety results against Kimi K3 on cyber, chem/bio and loss-of-control evals.
huggingface.corepoAdded 17 Oct 2026🧠 AI- Llama.cpp on a jailbroken PS5: run any GGUF model natively on the console
PS5LM is a homebrew app for jailbroken PS5s (firmware 7.00–13.60). It runs llama.cpp with the ggml-vulkan backend on the console's RDNA 2 GPU, using 11.4 GB of shared memory, and loads any GGUF model. It serves OpenAI /v1/chat/completions, Anthropic /v1/messages (usable from Claude Code, Codex and opencode) and a browser chat page on port 8081. It also supports image-projector vision models and TypeSafe-style decision models through a /v1/systemone endpoint. A planner picks the longest context and best cache that fit the free memory, and the app downloads models from Hugging Face.
github.comrepoAdded 17 Oct 2026, published 16 Oct 2026🧠 AI - OpenMOSS/MOSS-Image
MOSS-Image is an open-source text-to-image model family from OpenMOSS with a 5B backbone, released October 2026 as MOSS-Image-Base and MOSS-Image-SFT. It supports JSON layout control with bounding boxes, text rendering inside images, and prompts up to 4K tokens. The repo gives a Diffusers pipeline, a Gradio app, a ComfyUI plugin, LoRA training guidance, a prompt-enhancer skill and day-0 SGLang and vLLM-Omni support.
github.comrepoAdded 20 Oct 2026, published 16 Oct 2026🧠 AI - gichirimaku/wp2shell-PoC
wp2shell-PoC is a Python proof-of-concept exploiting a pre-authentication RCE chain in WordPress core, combining CVE-2026-63030 (REST API batch route confusion) and CVE-2026-60137 (SQL injection in WP_Query). It demonstrates escalation from the route-desync bug through blind SQLi, customize_changeset forgery, and hook re-entry to administrator account creation and arbitrary command execution via a malicious plugin upload. The tool supports vulnerability checking, data extraction (union, error-based, blind techniques), and full shell access with or without existing admin credentials.
github.comrepoAdded 23 Oct 2026, published 15 Oct 2026🛡️ Security - Show HN: Graphicle, a Rust port of Graphify with memory for coding agents
Graphicle is a local-first Rust program that parses a repository into a tree-sitter code graph (a port of Graphify) and adds project memory: docs, reviewed decisions and captured Claude Code/Codex sessions. It serves cited file-and-line excerpts within a token budget via one MCP server, CLI and browser app, backed by a single SQLite file, with no API key or telemetry. The README reports a code-only extract on Kubernetes (31k files) in 3m18s versus 26m38s for Graphify 0.9.88, and a memory comparison against seven systems. Agent-proposed memories need user approval and go stale when the code they reference changes.
github.comrepoPublished and added 14 Oct 2026🧠 AI - morluto/rea
REA (rea-agents on npm) registers an MCP server and matching workflow instructions with coding agents such as Claude Code, Codex, Cursor and Gemini CLI. It exposes tools for inspecting native binaries through Hopper, Ghidra or IDA (with optional objdump and Rizin), JavaScript/Electron apps and ASAR archives, .NET assemblies and websites. Results come back with evidence and limitations, so the agent can explain how a feature works and write and test its own implementation. Analysis runs locally, there is a CLI with the same workflows, and the showcases include C reconstructions verified against original x86 function bytes.
github.comrepoAdded 14 Oct 2026🧠 AI - morluto/rea
REA (rea-agents) is an MIT-licensed toolkit that exposes native-binary, JavaScript/Electron, .NET assembly and website analysis to AI agents via MCP, and also as a local CLI. It drives Hopper, Ghidra, IDA, objdump or Rizin for disassembly and pseudocode, recovers modules and Electron IPC boundaries from ASAR/JS apps, and returns findings with evidence and limitations. Showcases include reconstructing a x86 audio helper into byte-matching C and tracing an Electron clipboard API through preload and IPC; the README also carries lawful-use and licensing guidance.
github.comrepoAdded 14 Oct 2026🛡️ Security - BijectiveLabs/trading-research-agents
Open-source Python CLI (`tra`) for autonomous trading desks in which LLM analysts (technical, macro, on-chain, sentiment) and validators only give opinions on figures the system computed. Fixed rules do the arithmetic: pricing the round-trip cost, applying risk limits, sizing, cost gates, and sending a single order with stop attached via ccxt (Bybit and OKX demo accounts tested). It supports multiple model providers with per-role models, effort settings and fallbacks. Every answer is parsed against a closed schema, every refusal is logged with the figure behind it, and models can tighten but never loosen controls. This makes it a concrete reference for keeping LLM agents away from arithmetic and money.
github.comrepoAdded 18 Oct 2026, published 13 Oct 2026🧠 AI - BijectiveLabs/bitra
bitra (CLI name tra) is an MIT-licensed Python framework from Bijective Labs for autonomous trading agents. Language models only read system-computed figures and give opinions, while deterministic code prices the round trip, applies declared limits, sizes the trade and sends one order with stop attached. Every cycle's briefs, answers and refusals are stored on disk with hashes. It supports many model providers and ccxt venues, with sandbox, demo and mainnet tiers.
github.comrepoAdded 25 Oct 2026, published 13 Oct 2026🧠 AI - santosomar/AI-agents-for-cybersecurity
Companion repository for Omar Santos's Pearson and O'Reilly trainings and books. It has eight parts of runnable Python labs: chat models, embeddings, prompt templates, LCEL prompt chaining, Chroma-based RAG, ReAct/LangGraph/CrewAI/DeepAgents agents, and FastMCP servers (nmap, CISA KEV, Shodan). It also includes guides to six agentic frameworks (OpenClaw, Hermes, Agent Zero, OpenHands, Paperclip, Buzz), a tokenomics module on agent cost (context compounding, prompt caching, model routing, token budget guards, batch API, cost per accepted outcome), and a vendor-neutral design spec for a human-gated multi-agent assessment harness. It is a current, practical curriculum for building and operating agents. Some examples act on real systems and should only be run in an authorized lab.
github.comrepoAdded 13 Oct 2026🧠 AI - santosomar/AI-agents-for-cybersecurity
Omar Santos's companion repo for his Pearson/O'Reilly trainings and books, organised in eight parts. They cover LangChain prompts, chains and RAG (Chroma), and agents (LangGraph, CrewAI, DeepAgents). They also cover FastMCP security servers (nmap, CISA KEV, Shodan) and attack-surface-management and SOC agent examples. Later parts have security guides to six agentic frameworks (OpenClaw, Hermes, Agent Zero, OpenHands, Paperclip, Buzz) with hardening notes and 2026 CVE mapping, agent cost/tokenomics scripts including denial-of-wallet budget guards, and a vendor-neutral spec for a human-gated multi-agent security-assessment harness (scope manifest, approval gates, kill switch). Useful as a hands-on path into AI-agent security tooling, with warnings that some examples act on real systems.
github.comrepoAdded 13 Oct 2026🛡️ Security - Show HN: SolidCraft – Open-Source Parametric CAD in Rust (With MCP Support)
SolidCraft is an open-source parametric 3D CAD application written in pure Rust. It has constrained sketches with its own solver, a feature timeline, assemblies, sheet metal, and STEP/IGES/3MF/STL export. It runs on desktop (egui+wgpu), in the browser, and as a headless CLI. The built-in MCP server (`solidcraft-cli mcp`) gives agents tools such as execute, batch, inspect_design, measure, set_parameter, screenshot and export. They can model headless or drive the running app over a JSON-lines control channel. A rover with 3,323 timeline steps was built entirely through MCP, which shows agent-driven parametric modelling working at scale.
github.comrepoPublished and added 13 Oct 2026🧠 AI  google/embeddinggemma-2
Model card for EmbeddingGemma 2, an open (Apache 2.0) 740M-parameter multimodal embedding model from Google DeepMind built on Gemma 4. It maps text, code, images, video and audio into one 768-d space, with a 270M text backbone and optionally loadable 170M vision and 300M audio encoders, an 8K context, and Matryoshka truncation to 128/256/512/768 dims. The card gives practical guidance: task instruction prefixes, re-normalising after truncation, avoiding float16 (NaN or degraded embeddings), interleaved multimodal inputs with placeholder tokens, and vision token budgets. It targets on-device search, RAG, classification and clustering.
huggingface.corepoAdded 12 Oct 2026🧠 AI- Show HN: Atticus – Hold-to-talk voice assistant for macOS that runs on Claude -p
Atticus is an MIT-licensed macOS 26+ hold-to-talk voice assistant that uses Apple's on-device speech transcription and runs AI requests through Claude Code on an existing Claude Pro/Max plan, so no API key is needed. Simple commands skip the model entirely (apps open in 0.08 s), actions it has seen once are learned as zero-cost shortcuts, and a "remember…" memory persists across asks. It also sets up no-AI background watchers (polling every 5 s) and holds itself to a budget of a median under $0.002 and 6 s per AI ask, with a system prompt under 10,000 characters.
github.comrepoPublished and added 12 Oct 2026🧠 AI - zero-lab-ai/skills
zero-lab-ai/skills is a collection of 56 portable SKILL.md agent skills in 10 installable plugins from zero-lab.ai. They cover authorized defensive assessment, penetration testing, red teaming, detection engineering, purple teaming and engagement operations. Skills install via the Claude marketplace layout or `npx skills add`, and a make check release gate runs linting and tests.
github.comrepoAdded 23 Oct 2026, published 11 Oct 2026🛡️ Security - sepehr071/iran-mcp
iran-mcp is an open-source catalog of 39 MCP servers (488 tools) that let AI agents query Iranian websites such as Digikala, Torob, Divar, Snappfood, Jabama, Paziresh24, TSETMC and qavanin.ir, with prices normalised to Toman. Most servers are unofficial, read-only Python packages run with uvx; three are official hosted servers. It ships Claude Code plugins, Agent Skills, bundles, proxy lists and a machine-readable servers.json.
github.comrepoAdded 24 Oct 2026, published 11 Oct 2026🧠 AI - Dan Kornas (@DanKornas) on X
Arcjet JS SDK is an Apache-2.0 JavaScript monorepo that adds runtime security checks to AI apps, agents and HTTP endpoints. It ships framework SDKs (Next.js, Node.js, Bun, Deno, Fastify, NestJS) plus a Guard API for agent tool calls, MCP handlers, queue workers and background jobs that have no HTTP request object. Features include prompt injection detection, sensitive-information detection (PII, credit cards, custom patterns) and token-bucket, fixed-window and sliding-window rate limiting.
x.comrepoPublished and added 11 Oct 2026🛡️ Security - Dan Kornas (@DanKornas) on X
Arcjet JS SDK is an open-source (Apache-2.0) JavaScript monorepo that adds runtime security to AI apps, agents and HTTP endpoints. It ships request SDKs for Next.js, Node.js, Bun, Deno, Fastify and NestJS. It also has a Guard API for places with no HTTP request object, such as agent tool calls, MCP handlers, queue workers and background jobs. Built-in checks cover prompt-injection detection, sensitive-information detection (PII, credit cards, custom patterns) and token-bucket, fixed-window or sliding-window rate limits, including token budgets.
x.comrepoPublished and added 11 Oct 2026🧠 AI - sakidekin/CVE-2026-41940-PoC
This repository hosts a proof-of-concept for CVE-2026-41940, described as a CVSS 10.0 unauthenticated authentication bypass in cPanel and WHM caused by CRLF injection into server-side session files via the Authorization header. The accompanying Python tool (cve.py) can detect vulnerable cPanel/WHM instances, retrieve system and account information, and perform post-exploitation actions such as running OS commands, changing the root password, and opening an interactive WHM shell. It also supports bulk scanning workflows piped from subfinder, httpx, and Shodan.
github.comrepoAdded 23 Oct 2026, published 11 Oct 2026🛡️ Security - bilawalsidhu/gods-eye-view
God's Eye View is an open-source, vanilla JavaScript + CesiumJS + Vite 3D globe that fuses live public feeds (aircraft, ships, satellites, quakes, public cameras, weather) into one explorable scene. Its AI layer is a hands-free voice agent on the OpenAI Realtime API with 30 tools: camera fly-to, whiteboard annotations, analyst queries over live layers, and scene-context and screenshot grounding. Keys stay server-side and the browser gets only a short-lived session token. An experimental ChatGPT/Codex OAuth path is also supported. The app doubles as an MCP server, so Claude Desktop, Codex or ChatGPT can open the globe from a conversation.
github.comrepoAdded 11 Oct 2026🧠 AI - bilawalsidhu/gods-eye-view
God's Eye View is an open-source, vanilla-JavaScript CesiumJS and Vite client that puts live aircraft, ships, satellites (SGP4), earthquakes, fires, public CCTV and mapped ALPR cameras on one photorealistic 3D globe. It adds cockpit tracking, FLIR/NVG sensor shaders and a voice agent built on the OpenAI Realtime API. It works without API keys, and the docs cover server-side key brokering with SSRF protection, localhost binding and a SECURITY.md threat model. For OSINT/GEOINT practitioners it is a hackable base for fusing public signals, with an explicit rule against person-tracking features.
github.comrepoAdded 11 Oct 2026🛡️ Security - Talorys – A self-hosted personal AI agent on Cloudflare's free tier
Talorys is an open-source, single-user personal AI assistant deployed with one command (npx create-talorys) into the user's own Cloudflare account. It uses a Cloudflare Agents SDK Durable Object with SQLite for conversations, memories, tasks, notes and automations, Workers AI (@cf/zai-org/glm-4.7-flash) for streaming chat with tool calling, and Durable Object alarms for reminders and scheduled AI routines. It stays within the Workers Free plan, with a private Worker behind a Pages Function service binding, owner-password auth, per-day AI usage guardrails, and fallback to non-AI features when quota runs out.
github.comrepoPublished and added 10 Oct 2026🧠 AI - argoproj-labs/mcp-for-argocd
TypeScript MCP server for Argo CD that lets MCP clients (Cursor, VS Code, Claude Desktop) list, inspect, create, update, delete and sync applications, read logs and events, and run resource actions through natural language. It supports stdio and HTTP stream transports, with a stateless mode for multi-replica Kubernetes deployments. The security design is detailed: API tokens are read only from env vars or headers and never from tool arguments, the default token is bound to the default base URL, a per-host token registry covers extra instances, a read-only mode disables write tools, and the HTTP listener binds loopback by default and requires an inbound auth token if exposed.
github.comrepoAdded 10 Oct 2026🧠 AI  Qwen3.8-27B (Apache-2.0, multimodal dense, 262k ctx)
Model card for Qwen3.8-27B, a 27B dense vision-language model from the Qwen team with a hybrid Gated DeltaNet / Gated Attention layout (64 layers, 16×(3 DeltaNet + 1 attention)), MTP training, and 262k native context extensible to 1M via YaRN. It targets coding, research and long-horizon agentic tasks, with thinking on by default, reasoning_effort levels (xhigh/medium/low) and preserve_thinking. The card gives deployment recipes for Transformers, vLLM, SGLang and TokenSpeed, recommended sampling parameters, video-token settings for hour-scale video, and benchmark notes (SWE-bench Pro, NL2Repo-Bench, DeepSWE, HLE, MathVision, WebArena-Verified, etc.).
huggingface.corepoAdded 9 Oct 2026🧠 AI- morluto/awesome-reverse-engineering
awesome-reverse-engineering is a CC0 curated list of reverse-engineering tools and learning resources, organized by task: triage, native analysis, debuggers, instrumentation, deobfuscation, malware analysis, mobile, firmware, file formats, games, diffing, symbolic execution, lifting and AI agents. Each entry notes licensing, maintenance status and prerequisites. It also covers MCP integrations, CTF practice sites and related awesome lists.
github.comrepoAdded 27 Oct 2026, published 9 Oct 2026🛡️ Security - Show HN: Let your AI agents paint big arrows, boxes and text on your screen
bigarrow is an MIT-licensed, single-binary Swift macOS CLI that draws a click-through arrow and sign over all windows so an AI agent can show a human where to click, paste or act (permission prompts, 2FA, OAuth consent). It ships an Agent Skills package (installed via `bigarrow install-skill`) for Claude Code and Codex, with JSON output and exit codes, and can target by Accessibility label, coordinates, window or Peekaboo snapshot. The README documents the skill's token cost (182 tokens for the description, 1,398 for the instructions) and 104 automated tests.
github.comrepoPublished and added 9 Oct 2026🧠 AI - Show HN: Apogee: Rebuilding Mozilla's Orbit, fully local and private
Apogee is a privacy-first browser extension (Chrome/Firefox) that summarizes articles, YouTube/Bilibili videos, PDFs, DOCX and pasted text entirely on-device, inspired by Mozilla's discontinued Orbit. It runs models via WebGPU or WebAssembly in the browser, or connects over loopback to a local Ollama or llama.cpp server, with local passage retrieval for Q&A, grounded sentence highlighting, and Opus-MT translation. It shows a practical no-backend, no-API-key architecture for local LLM apps, with a Node.js extractor test harness for contributors.
github.comrepoPublished and added 9 Oct 2026🧠 AI - Show HN: Edi Life OS – self-hosted life dashboard with an MCP server for AI
Edi Life OS is a self-hosted dashboard (PHP 8.1+, MySQL, vanilla JavaScript) that combines focus timer, habits, goals, Kanban tasks, finances and notes in ten workspaces. It includes an optional Node.js MCP server that exposes 15 tools over stdio. The tools let Claude Desktop, Claude Code or Codex read the dashboard, create goals and tasks, log habits and record expenses. The MCP server calls only the app's bearer-token /api/v1 HTTP API and never touches the database or credentials. The README is candid about limits: the token has no scopes, there is no app-level rate limiting, and the secret-note flag is only a visibility setting, not encryption.
github.comrepoPublished and added 9 Oct 2026🧠 AI - mattpocock/skills — agent skills for engineers
mattpocock/skills is a collection of small, composable "agent skills" for software engineering that install into Claude Code, Codex, GitHub Copilot, Gemini CLI, Cursor, OpenCode, Devin, Windsurf, Amp and Pi via plugin managers or the `npx skills` CLI. It packages practices like interview-driven requirement gathering (/grill-me, /grill-with-docs), domain-model/glossary building, test-driven development with red-green-refactor (/tdd), bug diagnosis loops, codebase architecture improvement, ticket triage and spec-to-implementation workflows (/to-spec, /to-tickets, /implement, /implement-spec), splitting skills into user-invoked orchestrators and model-invoked reusable disciplines. It's built by Matt Pocock as an alternative to heavier process-owning frameworks like GSD, BMAD and Spec-Kit, aiming to keep engineers in control while giving coding agents better feedback loops and shared vocabulary.
github.comrepoAdded 8 Oct 2026🧠 AI  Aleph Alpha Kolibri-1 (78B MoE, Apache 2.0)
Kolibri-1 is Aleph Alpha's 78B-parameter mixture-of-experts reasoning model focused specifically on German and English, released under Apache 2.0 with weights, a vLLM plugin, and an extensive model card. It supports explicit reasoning-effort levels, Hermes-style tool calling, and a native 262144-token context validated to over 1M via sliding-window attention; the card details its UniBPE German-aware tokenizer, pre-training mid-training and long-context training recipe, MergeMix-based data-mix search, Merlin-Arthur hallucination-mitigation RL protocol, and benchmark results against Qwen3.5, Gemma 4, Nemotron 3 Nano, and Apertus on MMLU-Pro, GPQA, AIME, SWE-bench Verified, Terminal-Bench 2.1, and HLE.
huggingface.corepoAdded 8 Oct 2026🧠 AI- trhhubsd/ARTEX
ARTEX is an AGPL-3.0 autonomous penetration-testing system with a Go backend and Next.js frontend, backed by PostgreSQL. A planner agent and parallel worker agents share a global asset graph and a per-task exploration graph, with human-in-the-loop approval, a MITM traffic-recording proxy, ScopeSentry asset sync, vulnerability retesting and a shared todolist for multi-step attack chains. The README claims a Baidu agent+ attack-defense challenge win and limits use to local isolated labs.
github.comrepoAdded 27 Oct 2026, published 8 Oct 2026🛡️ Security - Dark Web Informer (@DarkWebInformer) on X
Infoooze is an open-source command-line OSINT reconnaissance toolkit (github.com/devxprite/infoooze) that consolidates common footprinting tasks into one CLI: username enumeration across platforms, email discovery, subdomain enumeration, port scanning, WHOIS/DNS lookups, IP/HTTP header analysis, EXIF metadata extraction, GitHub recon, and URL scanning/expansion. It automatically saves results, making it a lightweight all-in-one alternative to running several separate recon tools.
x.comrepoPublished and added 8 Oct 2026🛡️ Security - Sub-1-Bit LLM Compression via Latent Factorization
test
github.comrepoPublished and added 8 Oct 2026🧠 AI - microsoft/mxc
MXC is Microsoft's cross-platform sandboxed code execution system for running untrusted workloads — model output, plugins, and tool calls — behind a unified containment model with Rust, .NET, and Node SDKs. It offers multiple containment backends (ProcessContainer, Windows Sandbox, LXC, Bubblewrap, Seatbelt, MicroVM/Nanvix, Hyperlight, WSLC) with JSON-based filesystem, network, and UI policies, plus diagnostics like audit mode for building policies from observed access.
github.comrepoAdded 8 Oct 2026🧠 AI - microsoft/mxc
MXC is Microsoft's cross-platform sandboxed code execution system for running untrusted code such as LLM/agent output, plugins, and tools, offering containment backends ranging from OS-native process sandboxes (Windows Sandbox, LXC, Bubblewrap, Seatbelt) to full VMs (Nanvix MicroVM, Hyperlight). It exposes a unified JSON-based policy model for filesystem, network, and UI access controls, with Rust, .NET, and Node SDKs plus diagnostic tooling (audit mode, access-denied logging) to help developers tune containment rules for agentic workloads.
github.comrepoAdded 8 Oct 2026🛡️ Security - chainguard-dev/malcontent
malcontent is Chainguard's open-source malware/supply-chain discovery tool that analyzes binaries (ELF, Mach-O, PE, a.out) and scripting-language source across Linux, macOS and Windows using 14,500+ YARA rules (including third-party rules from Avast, Elastic, FireEye, Mandiant, Nextron and ReversingLabs). Its standout feature is differential analysis ("mal diff"), which compares two versions of a build artifact or OCI image against a known-good baseline to surface newly introduced risky behaviors — the technique the project demonstrates on the 3CX supply-chain compromise by flagging unexpected high-risk changes to libffmpeg. It also supports threshold-based scanning ("mal scan") and unfiltered capability enumeration ("mal analyze"), and is designed to run inside CI/CD pipelines, including air-gapped environments via embedded rules.
github.comrepoAdded 8 Oct 2026🛡️ Security - target/strelka
Strelka is Target's open-source, container-based real-time file scanning system for threat hunting, threat detection, and incident response, built in Go and Python. It runs 50+ scanners (YARA, PE parsing, encrypted ZIP cracking, entropy analysis, etc.) to extract metadata and content from files at enterprise scale, which can feed a SIEM for alerting on suspicious artifacts like an Emotet-laden encrypted ZIP payload.
github.comrepoAdded 8 Oct 2026🛡️ Security - deepfence/YaraHunter
YaraHunter is Deepfence's open-source scanner that applies YARA rulesets against container images, running Docker containers, and filesystems to detect indicators of compromise such as malware and cryptominers. It supports CI/CD build-time scanning, at-rest image scanning, and runtime container scanning, with JSON output for automation, and is designed to eventually integrate into the Deepfence ThreatMapper platform. The README walks through detecting the XMRig cryptominer inside a container image as a worked example.
github.comrepoAdded 8 Oct 2026🛡️ Security - Tracer-Cloud/opensre
OpenSRE is an open-source framework for building AI SRE agents that resolve production incidents by correlating logs, metrics, traces, deploys and runbooks across 60+ connected tools (observability, cloud infra, incident management, MCP). Beyond the agent runtime (CLI, Python API, Slack/PagerDuty/Telegram integrations), the project's stated mission is to build an RL training and evaluation environment — explicitly modeled on SWE-bench's role for coding agents — to scale realistic infrastructure-failure scenarios as a benchmark for AI SRE.
github.comrepoAdded 8 Oct 2026🧠 AI - Port of the TypeScript compiler, checker and lsp to Rust, by LLM
ts-rust (npm package tsc-rs) is a from-scratch Rust port of Microsoft's TypeScript compiler/checker/language server (typescript-go), produced almost entirely by LLM coding agents rather than hand-written. The author first spent over $400,000 in API tokens running GPT-5.6 Sol and GPT-6 Astra in long agentic '/goal' loops, which wrote 1.3M lines of Rust but plateaued at ~84% compatibility; switching to Claude Opus 5.5 produced a working version in 10 hours and, after ~$24,000 of further API spend over two weeks, reached 100% compatibility on tested real-world projects while passing all 181,711 ported Go baseline tests. Benchmarks show the Rust port running about 1.6x faster than the Go tsc 7 compiler (though slower than Bun's native `bun check`) across dozens of open-source codebases including VS Code, TanStack Query, Sentry and T3 Code.
github.comrepoPublished and added 8 Oct 2026🧠 AI - Show HN: NanoMuse – An open-source AI agent for your phone and computer
nanoMuse is an open-source personal AI agent that runs across phone, desktop, and web, built on an on-device sandbox (OpenMinis with proot/Alpine Linux on mobile) and the DeepSeek Harness on desktop with a Python runtime for tool use. Devices share one account and sync conversations through a relay (self-hostable), while the agent proactively acts, retains memory, and pauses before irreversible actions; it is released GPL-3.0-or-later with documentation on install, self-hosting, connectors, and memory.
github.comrepoPublished and added 7 Oct 2026🧠 AI  The Vulnerable MCP Project — MCP vulnerability database
The Vulnerable MCP Project is a curated, continuously growing database of security vulnerabilities and attack techniques specific to the Model Context Protocol ecosystem. Entries cover concrete CVEs (e.g. CVE-2025-68143/68144/68145 in Anthropic's mcp-server-git), transport-layer SDK flaws (cross-client response leakage, missing DNS rebinding protection in the official TypeScript/Python SDKs), unauthenticated/0.0.0.0-bound servers enabling RCE (MCPJam inspector, MCP Inspector, Grafana MCP), command/path injection in dozens of third-party servers (gemini-mcp-tool, mcp-server-kubernetes, Framelink Figma MCP, Zen MCP, filesystem-mcp), SSRF chains reaching cloud metadata (MarkItDown MCP, mcp-fetch-server), and a large set of AI-specific attacks: tool poisoning, trigger-phrase data exfiltration, prompt injection via GitHub issues, Jira and Google Docs, rug-pull tool mutation, and cross-server tool-name collisions. It functions as the de facto vulnerability registry for the MCP ecosystem, useful for tracking disclosed issues before patching or adopting third-party MCP servers.
 vulnerablemcp.inforepoAdded 6 Oct 2026🛡️ Security
- Microsoft Agent Framework python-1.20.0 release
Release notes for python-1.20.0 of Microsoft's Agent Framework, an open-source agent/workflow orchestration library. This release adds native vector-store connectors for DuckDB, SQL Server and MongoDB plus a TypeSafe AI connector, redesigns Foundry hosting around request-scoped agent factories and sandbox-isolated sessions, adds computer-use support to Responses clients, and ships Magentic manager and handoff-routing improvements for multi-agent orchestrations alongside a large batch of MCP, Bedrock, Gemini, Anthropic and Ollama provider fixes.
github.comrepoAdded 6 Oct 2026🧠 AI - Show HN: OpenChart – OSS TradingView alternative with your own AI agent
OpenChart is an open-source TradingView-style desktop charting app (Electron, Node.js/Bun, Effect runtime) that embeds AI agents into statistical/technical analysis, real-time market alerts and agentic opportunity research. It ships a custom DSL called Tea (inspired by TradingView's Pine Script) for writing indicators, and a conversation interface built on assistant-ui and the AG-UI event protocol so users converse with agents while charting.
github.comrepoPublished and added 6 Oct 2026🧠 AI - browser-use/jev-ultrafast
jev-ultrafast is an open-source browser automation agent (from Browser Use) that represents each page as an indexed element table and uses a 'TypeSafe' policy to speculatively predict both the next operation (CLICK, TYPE_TEXT, SELECT, SCROLL, WAIT, DONE, BLOCKED) and its target in a single network round trip, only invoking a small LLM (e.g. inception/mercury-2.5 via OpenRouter) to generate text when the operation is TYPE_TEXT. The repo includes a local inspector UI, Chrome automation via a 'Browser Harness' tool, offline tests, and published before/after benchmarks showing a Google Flights search dropping from a median 9.45s to 7.09s and browser protocol calls from 1,092 to 101 across repeated runs.
github.comrepoAdded 6 Oct 2026🧠 AI - overmind-core/overmind
Overmind is an open-source platform (MIT SDK/CLI, AGPL-3.0 platform, self-hostable) that instruments an agent's code via OpenTelemetry tracing, turns the resulting production traces (or any dataset) into a fine-tuned model benchmarked against user-defined eval metrics, and serves it through one unified API with downloadable/retrainable weights. It ships an SDK, CLI, REST API, Console, and an MCP server exposing project tools and workflows (investigate-capability, finetune-capability, ship-model) for Cursor, Claude Code, OpenCode and Codex, and can sync traces from Langfuse, LangSmith, Braintrust or Galileo; self-hosting runs via Docker Compose with Postgres, Redis, Celery workers and Modal-based GPU workers for fine-tuning/serving (vLLM).
github.comrepoAdded 6 Oct 2026🧠 AI - claude-mem — persistent memory system for Claude Code and other coding agents
Claude-Mem is an open-source persistent memory plugin for Claude Code and other coding agents (Codex, OpenCode, Grok Bot, T3 Code, OpenClaw) that captures tool-usage observations during sessions, compresses them into semantic summaries, and reinjects relevant context into future sessions. It uses five lifecycle hooks (SessionStart, UserPromptSubmit, PostToolUse, Stop, SessionEnd), a local SQLite database, a Chroma vector store for hybrid semantic+keyword search, and exposes three MCP tools (search, timeline, get_observations) that follow a token-efficient layered retrieval pattern to cut context costs roughly 10x. It is Apache-2.0 licensed, built with the Claude Agent SDK and TypeScript, and ships an optional hosted "observer" memory service alongside self-hosted options via OpenRouter/Gemini keys or an Anthropic plan.
github.comrepoAdded 5 Oct 2026🧠 AI - Dark Web Informer (@DarkWebInformer) on X
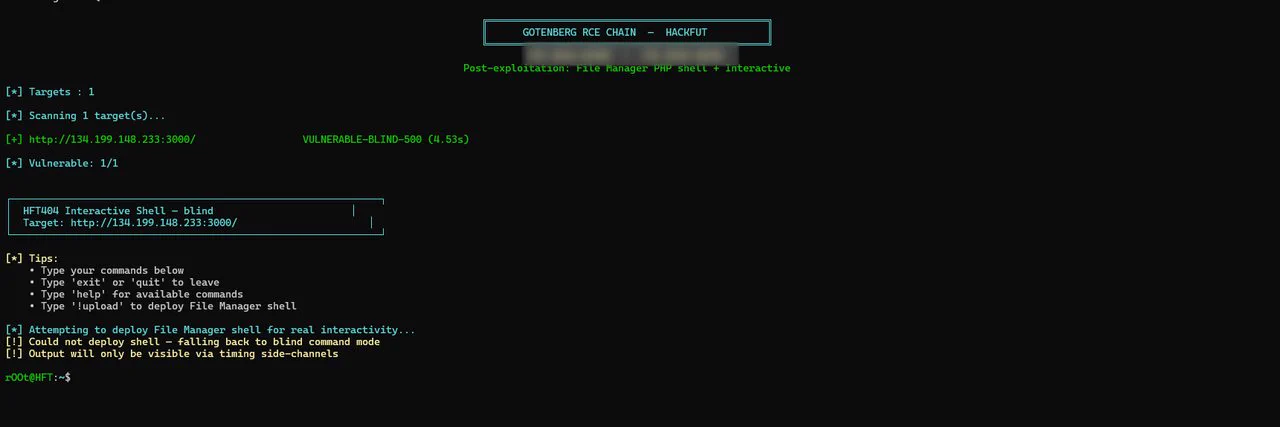
A public PoC chains CVE-2026-42589 and CVE-2026-40281 to achieve unauthenticated remote code execution against Gotenberg (a document/PDF-conversion microservice), abusing metadata injection flaws in the /forms/pdfengines/metadata/write endpoint. The tool supports vulnerability detection, interactive command execution, reverse shell delivery, and multi-target scanning against Gotenberg versions ≤8.30.1 (patched in 8.31.0).
x.comrepoPublished and added 5 Oct 2026🛡️ Security - Zhenyu98/codex-chatgpt-bridge
codex-chatgpt-bridge is a Codex agent skill plus external PowerShell control scripts (On/Off/Reboot/Rotate) built on top of the open-source DevSpace MCP bridge, which lets ChatGPT act as a planning/review "architect" while Codex stays the local executor that applies and verifies changes. It adds a token-saving router (NORMAL / TOKEN_SAVING / CHATGPT_ARCHITECT modes) and a lifecycle layer — Cloudflare Quick Tunnels or a stable Cloudflare Worker proxy, DPAPI-protected credentials, OAuth token rotation, and a scheduled-task recovery entrypoint — so the bridge's public endpoint can be closed when idle without re-authorizing the ChatGPT app on every restart.
github.comrepoAdded 5 Oct 2026🧠 AI - the_OSINT_rack (@the_OSINT_rack) on X
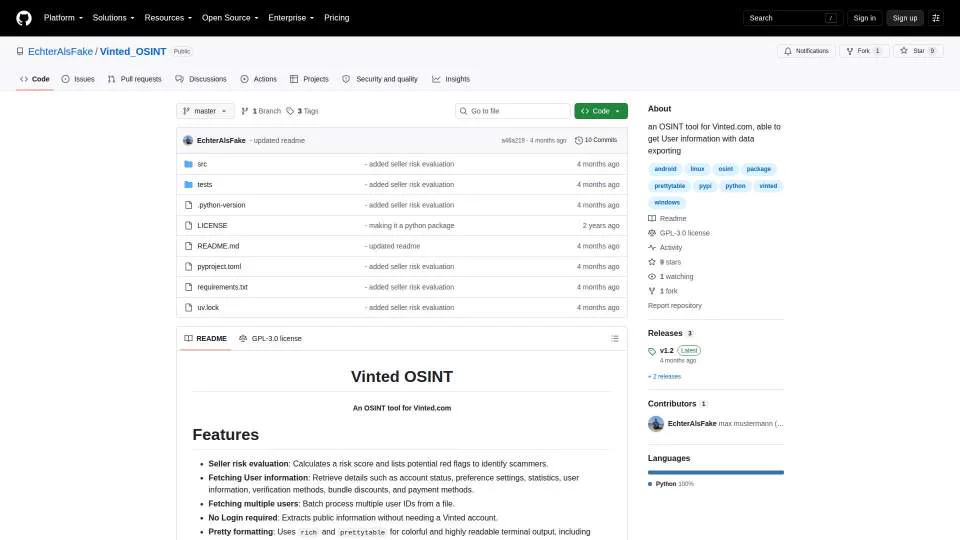
Vinted_OSINT is a GitHub tool by EchterAlsFake that performs open-source intelligence gathering against Vinted.com user profiles, pulling seller/buyer account information and computing a risk score to flag accounts likely run by scammers. It's aimed at buyers wanting to vet sellers before transacting on the second-hand marketplace.
x.comrepoPublished and added 4 Oct 2026🛡️ Security - M-med/Active-Directory-Simulation-Attack-
Active-Directory-Simulation-Attack- is a purple team lab for the lab.local domain (192.168.100.0/24). It walks through an attack chain: BloodHound/SharpHound recon, Kerberoasting, hash cracking with John the Ripper or Hashcat, and lateral movement with Impacket. It then applies hardening (gMSA, tiering, LLMNR/NetBIOS disabling) and adds Sysmon, Wazuh SIEM and custom Kerberoasting rules (Event ID 4769, RC4).
github.comrepoAdded 23 Oct 2026, published 4 Oct 2026🛡️ Security - DeepZero
DeepZero is an open-source orchestration engine that lets researchers define vulnerability-research pipelines declaratively in YAML, handling parallel execution (ThreadPoolExecutor), resumable/fault-tolerant state, and LLM-assessment stages via LiteLLM/Jinja2 prompts. It ships example processors for Ghidra headless decompilation, LOLDrivers.io hash exclusion filtering, PE header/driver metadata extraction, and batch Semgrep scanning, with a dedicated pipeline for BYOVD kernel driver vulnerability research. An extensibility model lets users plug in custom Python processors referenced by path in the YAML config.
github.comrepoAdded 3 Oct 2026🛡️ Security - Sigma r2026-07-01 — 20 new detection rules
GitHub release notes for Sigma r2026-07-01, the open-source detection-rule repository, adding 20 new rules (e.g. LSASS crash via Netlogon buffer overflow CVE-2026-41089, TanStack supply-chain attack indicators for Windows/Linux, RedTail cryptominer user-agent detection, AF_ALG kernel crypto API exploit indicator) and updating/fixing dozens of existing rules for ARM64 binary variants, file-sharing domain IOCs, and WMI-based reconnaissance/persistence detection. It's a routine but substantive update to a widely-used blue-team detection content pack.
github.comrepoAdded 3 Oct 2026🛡️ Security - jiwoochris/artex-global
ARTEX global edition is an English-default fork of the Chinese open-source ARTEX (AGPL-3.0), an autonomous penetration-testing system in which planner and worker LLM agents run real tools and record results in an asset graph and an exploration graph on PostgreSQL. It also ships a defense guide, Sigma and Suricata rules, an ATT&CK Navigator layer, MISP indicators and a host triage script for spotting ARTEX-driven attacks.
github.comrepoAdded 31 Oct 2026, published 3 Oct 2026🛡️ Security - Jakeschincariol/replica-skill
replica-skill is an MIT-licensed set of eleven Claude skills that run an app-cloning pipeline: recon, architect, design, build, backend, test, diff, entrepreneur, brand, launch and deploy. Six standard-library Python tools handle image diffing, parity scoring, review ranking, contrast checks, rebrand sweeps and store-listing lint. It installs as a Claude Code plugin or by copying folders, and states clean-room and rebranding limits.
github.comrepoAdded 29 Oct 2026, published 3 Oct 2026🧠 AI - OKX Agent Trade Kit (okx-trade-mcp / okx-trade-cli)
OKX Agent Trade Kit is an open-source MCP server (okx-trade-mcp) and CLI (okx-trade-cli) that let AI assistants like Claude Desktop, Cursor, Claude Code and VS Code place trades and query account data on the OKX exchange via natural-language commands. It runs locally with API keys never leaving the machine, supports module scoping (market, spot, swap, account, earn), a read-only mode for safe querying, multiple profiles, and includes pre-built skill files for agent frameworks plus structured JSON error reporting for debugging failed tool calls.
github.comrepoAdded 2 Oct 2026🧠 AI - Show HN: Made an open-source Lego AI generator
ldraw-nova is an open-source agentic pipeline where an LLM agent (tested with models like Claude Opus 5.5 and GPT-6 Astra) takes a build prompt, reads LDraw-building instructions, and produces a plan.json describing a model's geometry. From that plan it writes a Python generator script that, when executed, outputs an LDraw (.mpd) 3D CAD source file, viewable in 3D/VR (Meta Quest 3) or exportable to Blender-editable glTF. The agent uses jev-rerank, a semantic search tool with reranking backed by TypeSafe's Jev System One model, to find suitable LEGO parts and example models, falling back to full-text search without an API key; it also uses headless rendering and collision/gap detection to self-inspect and iterate on designs.
github.comrepoAdded 3 Oct 2026, published 2 Oct 2026🧠 AI - Microsoft Agent Framework — python-1.20.0 release
Release notes for Microsoft's Agent Framework (Python and .NET SDKs), covering versions python-1.16 through python-1.20 and dotnet-1.19 through dotnet-1.23. Changes span native vector-store connectors (MongoDB, Qdrant, PostgreSQL/pgvector, DuckDB, SQL Server, Azure Cosmos DB, Azure AI Search), Foundry hosting redesigns around request-scoped agent factories and durable Invocations, MCP skill/session security hardening (approval binding, security labels, ZIP-only skill archives), Magentic multi-agent orchestration and handoff routing, and checkpoint/replay correctness fixes across workflows.
github.comrepoAdded 2 Oct 2026🧠 AI  Kyutai Pocket TTS
Pocket TTS is a 100M-parameter text-to-speech model from Kyutai designed to run efficiently on CPU, generating audio faster than real-time (~6x on a MacBook Air M4) with ~200ms latency to first audio chunk and voice cloning from short audio samples. It supports English, French, German, Portuguese, Italian, and Spanish, ships a Python library and CLI, and has spawned numerous community ports (WASM, ONNX, Rust/Candle, MLX, C++, C#) and fine-tuned language variants (Czech, Hindi, Korean, Persian, Indonesian, Estonian, Welsh, Polish).
huggingface.corepoAdded 2 Oct 2026🧠 AI Tencent Hy4 preview (open-weight MoE + Sherry quantization)
Hy4 preview is Tencent's new flagship Mixture-of-Experts language model: 770B total parameters with 49B activated per token across 78 layers (256 routed experts + 1 shared expert, top-8 routing), plus a native 10B multi-token-prediction layer for speculative decoding. It introduces Gated DeepSeek Sparse Attention with IndexCache for cross-layer index reuse and identity Hyper-Connections (iHC) on the residual path, and in blind internal evaluations on engineering tasks it edges out GLM-5.3 and Kimi K3. Weights (including an FP8 variant) are released under Apache 2.0 on Hugging Face with vLLM/SGLang deployment recipes and AngelSlim-based quantization/compression tooling.
huggingface.corepoAdded 2 Oct 2026🧠 AI- Bifrost (Maxim AI) — open-source LLM gateway
Bifrost is an open-source, high-performance LLM gateway (by Maxim AI) that exposes a single OpenAI-compatible API across 23+ providers including OpenAI, Anthropic, AWS Bedrock, Google Vertex, Azure, Cohere, Mistral, and Ollama. It provides automatic failover, load balancing, semantic caching, Model Context Protocol (MCP) tool integration, budget and governance controls, OIDC user provisioning, and Prometheus-based observability, deployable via npx or Docker with claimed sub-15 microsecond overhead at 5,000 RPS. It is positioned as a drop-in replacement requiring only a base-URL change for existing OpenAI, Anthropic, or GenAI SDK code.
github.comrepoAdded 2 Oct 2026🧠 AI - NuvexNetwork/nuvex
Nuvex is a Solana-native verifiable compute and oracle protocol, still pre-mainnet, whose own README documents unresolved security gaps instead of hiding them: its VRF proof verification relies on solana-ecvrf 0.0.1 (RFC 9381 ECVRF-Edwards25519-SHA512-TAI) which has no known audit, max_fee is stored but never actually charged, and VRF fulfillment is first-come among any node meeting the configured stake/heartbeat threshold — meaning an operator who funds several keys at a low minimum stake can selectively pick which randomness output gets used. The deploy-mainnet script is stubbed to exit before any transaction, and unresolved design questions (fee shares, challenge/reject state transitions) are tracked as explicitly blocked ADRs rather than quietly shipped.
github.comrepoPublished and added 2 Oct 2026🛡️ Security - Folkbench/folkbench
Folkbench has two parts. One is a public benchmark and leaderboard of third-party AI API relay (中转站) services. Multi-node probes run around the clock and publish availability, P95 latency and price per relay, with per-model rankings. The other is Switch, an open-source Tauri/Rust desktop client that stores several Base URL and API Key pairs. It applies them to Claude Code or Codex configs in one click, previews config diffs, and stashes and restores the official ChatGPT OAuth credentials when switching Codex to a third-party provider. It also keeps keys local and estimates token usage and cost per session. The README also profiles several relay services, such as Modelflare, CheapAI and ApiPorter, and that part reads as promotional.
github.comrepoAdded 12 Oct 2026, published 2 Oct 2026🧠 AI - renato-osec/goonfi-v2-decompiled
goonfi-v2-decompiled holds byte-identical reconstructed Rust source for the GoonFi V2 Solana program goonuddtQRrWqqn5nFyczVKaie28f3kDkHWkHtURSLE, as deployed at slot 448984043. The on-chain program was upgraded on 6 October 2026 to fix reported bugs. VERIFY.sh builds with Solana platform-tools v1.48 and compares the result to the deploy transaction's loader buffer writes. The page does not describe the bugs.
github.comrepoAdded 22 Oct 2026, published 2 Oct 2026🛡️ Security - zzzz7788990213-ops/EvoVLM
EvoVLM searches over prompts, image preprocessing, generation budgets and answer extraction for frozen Qwen3-VL-2B-Instruct and Qwen3-VL-2B-Thinking, without fine-tuning weights. A local Qwen model ranks a catalog of typed mutations, a trusted renderer produces Python programs, and Pareto selection on accuracy and latency drives two small generations on scientific chart understanding (CharXiv subset). Recorded results on Dev128: Evolved Instruct keeps accuracy with 8.9% lower median latency, and Evolved Thinking gains 16.41 points of accuracy with 10.6% lower median latency. CPU-only replay and fail-closed evidence verification are included. The authors state the limits: small sample, overlap with the evolution set, and results tied to the recorded hardware.
github.comrepoAdded 16 Oct 2026, published 2 Oct 2026🧠 AI - NVIDIA/OpenShell — sandboxed runtime for autonomous AI agents
OpenShell is NVIDIA's open-source runtime for safely running fleets of autonomous AI agents: each agent runs in an isolated sandbox where kernel-level controls enforce a declared policy over file access, syscalls, and network connections, and credentials are injected only for approved endpoints rather than exposed to the agent directly. Policy changes are checked with formal verification to flag risky new access (new hosts, new API methods) before they're approved, and the project ships a CLI, gateway, Kubernetes/Helm deployment, and a tutorial running OpenCode against an OpenRouter model.
github.comrepoAdded 1 Oct 2026🛡️ Security - MITRE ATLAS v2026.08 release — autonomous agent techniques
Release notes for MITRE ATLAS v2026.08, the adversarial AI/ML knowledge base (now 1 matrix, 16 tactics, 114 techniques, 83 sub-techniques, 39 mitigations, 72 case studies). This version renames the "AI Attack Staging" tactic to "AI Attack Adaptation," generalizes several techniques (e.g., Cloud Service Discovery → Enterprise Resource Discovery, Process Discovery → Enterprise Environment Discovery, Reverse Shell → Cyber Communication Channel), and updates mitigations and techniques like LLM Prompt Crafting and Retrieval Content Crafting.
github.comrepoAdded 1 Oct 2026🛡️ Security - OpenShell — safe, private runtime for autonomous AI agent fleets
OpenShell is NVIDIA's open-source runtime for running fleets of autonomous AI agents inside isolated sandboxes. Declarative policies cover filesystem, syscall, process and network access. These are enforced at the kernel level, and credentials are injected only into requests bound for approved endpoints. Policy changes are checked with formal verification so risky new access waits for human review. It ships a CLI, a gateway control plane (Helm deployment on Kubernetes), SDKs, extensibility hooks (middleware, interceptors, compute drivers) and installable agent skills, and it can run agents such as OpenCode.
github.comrepoAdded 1 Oct 2026🧠 AI - ShadowSafin/Synapass
Synapass is an OpenAI-compatible inference gateway and control plane that decides per request which AI provider serves it, under policy. It provides routing, retry and failover, exact/prefix/semantic caching, rate limits and budgets, tenant isolation, and an explain endpoint recording why each request was routed. It deploys with one command via Docker Compose (Postgres, Redis, ClickHouse, NATS, Grafana stack, dashboard).
github.comrepoAdded 20 Oct 2026, published 1 Oct 2026🧠 AI - https://github.com/Panniantong/Agent-Reach
Agent-Reach is a CLI and agent-"skill" layer that equips coding agents (Claude Code, Cursor, OpenClaw) with ready-made web-reading tool use: fetching arbitrary pages via Jina Reader, YouTube transcripts via yt-dlp, GitHub repos via gh CLI, Bilibili search, RSS via feedparser, and semantic web search via Exa through mcporter, with login-gated platforms (Twitter/X, Reddit, Xiaohongshu, Facebook, Instagram) added on request via cookies or OpenCLI browser sessions. Each platform module probes an ordered list of candidate backends and falls back automatically when one breaks (e.g. yt-dlp being blocked by Bilibili's anti-scraping), and an `agent-reach doctor` command reports which backend each channel is currently using. It positions itself as a "capability layer" that selects, installs and health-checks the right upstream tool for an agent rather than wrapping the reads itself.
github.comrepoAdded 2 Oct 2026, published 1 Oct 2026🧠 AI - AI-Infra-Guard (A.I.G) — Tencent Zhuque Lab
AI-Infra-Guard (A.I.G) is Tencent Zhuque Lab's open-source AI red-teaming platform combining AI infrastructure vulnerability scanning (2000+ CVE rules covering vLLM, llama.cpp, LangFlow, n8n, MLflow and 145+ other AI components), MCP server/skill security scanning, LLM API poisoning detection, and multi-turn jailbreak evaluation (Many-Shot, PAIR, GOAT, ActorAttack). It ships CLI tools (skill-scan, mcp-scan, agent-scan), a Docker-deployed web UI, and has produced original research including FORGE-Bench (loss-of-control benchmark), RogueHandoff-20, and SkillJack (persistent skill backdoors), with talks at Black Hat Europe 2025 on MCP security.
github.comrepoAdded 30 Sep 2026🛡️ Security - Sift — Open-Source Secrets/Credential Scanner
Sift is Stratus Security's open-source successor to Snaffler: a Native AOT credential/secrets scanner for pentesters that crawls local drives, SMB shares/subnets, Active Directory, SharePoint/OneDrive/Teams, Slack, and Jira/Confluence for exposed secrets. It supports Kerberos/NTLM/pass-the-hash authentication, resumable checkpointed scans, a JSON rule/ignore-rule system compatible with Snaffler's detection catalogue, and optional local-LLM (Ollama) validation to cut false positives without sending sensitive findings to a cloud API.
github.comrepoAdded 30 Sep 2026🛡️ Security - CAIRN — Cisco Talos AI-Malware-Hunting Toolkit
CAIRN is a Cisco Talos research toolkit that identifies and attributes AI-integrated malware purely from VirusTotal metadata — no binary downloads or detonation — by running a tiered YARA ontology (T1/T2/T3) over composed scan text (AV strings, PE resources, Sigma/sandbox behavioral data, embedded URLs) and layering on sentence-transformer embeddings with HDBSCAN clustering for semantic family attribution. It has produced confirmed family reports for AI-malware such as PROMPTLOCK, LAMEHUG, PROMPTSTEAL, QUIETVAULT, CLOSEDQUORUM, and FRUITSHELL, each cross-verified by hands-on Talos reverse engineering before publication.
github.comrepoAdded 30 Sep 2026🛡️ Security  DeepSeek-V4.1-Flash
 is a multimodal Mixture-of-Experts model with 552B backbone parameters, 1M-token context, and a novel Causal Encoder-Decoder (CED) architecture where the decoder's global KV cache is projected from encoder hidden states rather than recomputed per layer, activating only 8B/16B parameters per token during prefill/decode. It introduces Compressed Sparse Attention 2 (CSA2) with FP4 KV caching to cut the global KV cache footprint to 890 bytes/token (~1/4 of DeepSeek-V4-Flash, ~1/437 of DeepSeek-V1), alongside Engram conditional memory, DSpark speculative decoding, and a continuously controllable reasoning-effort setting (1–100). The card documents pre/post-training recipes (45T tokens, SFT→RL→on-policy distillation with synthetic agent environments) and reports results across agentic and code benchmarks (Terminal-Bench 2.1/3.0/4.0, DeepSWE v1.1, GPQA Diamond, Chartography, ZeroBench, AutomationBench), plus deployment instructions for Transformers, vLLM, SGLang, and Docker.
huggingface.corepoAdded 30 Sep 2026🧠 AI- Launch HN: Magnitude (YC S25) – Self-optimizing inference engine for agents
Magnitude is an open source local inference engine (Apache 2.0) that compiles and tunes its GPU/CPU kernels on the user's exact device before a model runs, claiming up to 2x faster decode than llama.cpp (92% faster on Metal, 19% on CUDA) with 27% lower memory per agent. It ships as a cross-platform desktop app with a bundled CLI and an OpenAI-compatible API, offering one-click connections to agent tools like Pi, OpenCode, Hermes, Codex, OpenClaw, Claude Code, and Cline, running fully offline on Apple Silicon, NVIDIA, AMD, or CPU-only hardware.
github.comrepoPublished and added 30 Sep 2026🧠 AI - Andrea (Drego) Draghetti 👨🏻💻 🎣 (@AndreaDraghetti) on X
Tosint v1.0.0 is an open-source Telegram OSINT tool for analyzing bots and chats, exporting message history and media. The new release adds richer JSONL metadata output, optional SHA-256 hashing of exported media, bot/user authentication support, and an automatic fallback from MTProto-based history retrieval to ID-scan mode when dealing with restricted chats.
x.comrepoAdded 2 Oct 2026, published 30 Sep 2026🛡️ Security




Showing 120 of 602
Show more