- Bunny CDN Security Incident
Bunny CDN status-page notice, posted 28 October 2026, about unauthorized access at an infrastructure provider that hosted one bunny.net CDN node in Armenia. Traffic was stopped within 20 minutes and the server wiped. No access to the node was found, but cached content, Pull Zone configs and TLS certificates could have been exposed, so all platform certificates were reissued. Customers with their own certificates should rotate them with new private keys.
 status.bunny.netadvisoryAdded 31 Oct 2026, published 30 Oct 2026🛡️ Security
- lee1981 (@lee1981b) on X
CyberForge CVE of the Day #091 covers Progress WS_FTP Server CVE-2026-84295 (unauthenticated administrator-credential exposure, CVSS 10.0) and CVE-2026-90868 (conditional OS command and argument injection, CVSS 9.9, low privileges). Fixed floors are 2024.0.7/9.0.7 and 2025.0.4/10.0.4; 2024.0.6/2025.0.3 fix only the first. It gives KEV, EPSS and SSVC status, six SOC checks, and Windows 4688 evidence queries.
 x.comadvisoryAdded 2 Nov 2026, published 30 Oct 2026🛡️ Security
 CVE-2026-101767: Critical Oracle EBS SQL Injection Actively Probed in the Wild
CVE-2026-101767 is a CVSS 9.8 unauthenticated SQL injection in Oracle E-Business Suite's Application Object Library, reachable through the /OA_HTML/AppsTCFServer servlet (GanttDataServer) and chainable to OS command execution. It affects versions 12.2.3 to 12.2.15 and was fixed in the October 2026 Critical Patch Update. Horizon3.ai found it, and Defused saw probing on honeypots on 27 October 2026. Interim mitigation is removing the servlet from the URL firewall allowlist.
 orca.securityadvisoryPublished and added 28 Oct 2026🛡️ Security
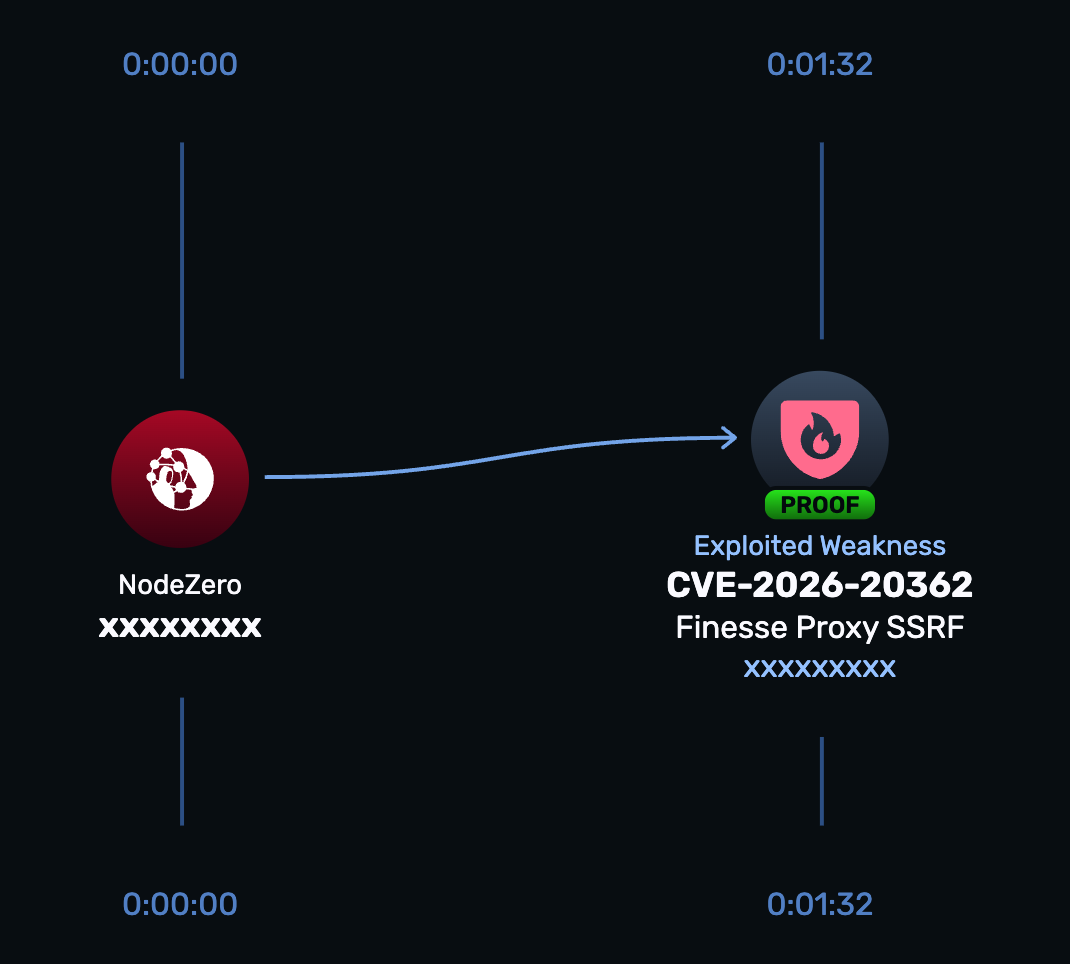 CVE-2026-20362 | Cisco Finesse Server-Side Request Forgery Vulnerability
CVE-2026-20362 is an unauthenticated server-side request forgery in Cisco Finesse (CVSS 3.1 score 7.2), found by Horizon3 researchers Noah King and Brandon Peterson. The embedded Apache Shindig content proxy fetches attacker-supplied URLs, including loopback services such as the Finesse REST API at 127.0.0.1:8082, which returns SystemInfo with node hostnames and the XMPP domain. Cisco published its advisory on 7 October 2026. Fixes are planned for January and February 2027, and no workaround exists.
 horizon3.aiadvisoryAdded 29 Oct 2026, published 28 Oct 2026🛡️ Security
 CVE-2026-101767 | Oracle E-Business Suite TCF SQL Injection and Remote Code Execution
CVE-2026-101767 is an unauthenticated SQL injection in the Oracle E-Business Suite Thin Client Framework servlet (/OA_HTML/AppsTCFServer, oracle.apps.fnd.tcf.SocketServer), CVSS 3.1 9.8. It runs SQL as the APPS user and chains to OS commands as the EBS account. Affects 12.2.3 to 12.2.15, fixed in the Oracle October 2026 CPU (20 October 2026). The page lists mitigations, IOCs and a timeline.
horizon3.aiadvisoryAdded 29 Oct 2026, published 20 Oct 2026🛡️ Security- lee1981 (@lee1981b) on X
CVE-2026-77932 affects DB-GPT through 0.8.2 (dbgpt-app). The /api/v1/chat/react-agent route accepts unauthenticated requests because get_user_from_headers returns an admin-role user, and the ReAct agent can reach unsandboxed Python and shell tools. Lasso reported root in the webserver container in a lab. The post gives CVSS 9.8 and 9.3, no verified fix (0.8.2 is still the latest release), no KEV match, no EPSS data, and a SOC hunting trail.
x.comadvisoryAdded 23 Oct 2026, published 20 Oct 2026🛡️ Security - lee1981 (@lee1981b) on X
CVE-2026-106931 is an OS command injection (CWE-78) in the statistics processing of EG Secure Solutions SiteGuard Server Edition, a host-based WAF. It can give root or SYSTEM command execution. The vendor and JVN confirm exploitation on 14 October 2026. The post lists fixed builds (Ver8.00 Update 5, Ver7.00 Update 6 on FreeBSD), the IIS exclusion, the workaround of disabling statistics, and a SOC trail starting with diagnostic preservation before patching.
x.comadvisoryAdded 21 Oct 2026, published 19 Oct 2026🛡️ Security - Dark Web Intelligence (@DailyDarkWeb) on X
Summary of Vercel's Oct 14, 2026 out-of-band Next.js security release fixing two critical unauthenticated RCEs: one in App Router apps with Cache Components where a "use cache" function returns multiple typed arrays (GHSA-673q-mjm6-r5xr, upstream React GHSA-xqc2-xf4c-x3h3, no workaround), and one in the Image Optimization API handling SVG on glibc Linux via a memory bug in a library used through sharp (CVE-2026-96889 / GHSA-2464-fhr4-w9xw, workaround sharp 0.35.5+). Also covers a high-severity Server Actions DoS (GHSA-p3m5-59mp-jv5r). Fixes ship in two supported Next.js LTS lines. No in-the-wild exploitation reported.
x.comadvisoryAdded 17 Oct 2026, published 16 Oct 2026🛡️ Security  Critical GitLab RCE Lets Unauthenticated Attackers Execute Code on Servers (CVE-2026-97229)
Orca Security analysis of CVE-2026-97229, a CVSS 10.0 flaw in GitLab CE/EE. An integer overflow (CWE-190) in the CI/CD regular expression compiler gives memory corruption and code execution as the git user. It is triggered by a crafted regex in .gitlab-ci.yml combined with a UTF-8 repository path, with no authentication needed on instances that allow public project creation or self-registration. Lists affected branches (19.2 before 19.2.8, 19.3 before 19.3.5, 19.4 before 19.4.2), the absence of a workaround, interim mitigations, and a Rapid7 PoC against GitLab CE 19.4.1 with ASLR on. Notes a prior max-severity GitLab bug (CVE-2026-85706) was probed in the wild within hours and later added to CISA KEV.
orca.securityadvisoryPublished and added 14 Oct 2026🛡️ Security Patch Tuesday - October 2026
Rapid7's analysis of Microsoft's October 2026 Patch Tuesday, which covers 1,413 vulnerabilities, 1,102 of them in Windows. It highlights the exploited Windows Shell Mark of the Web bypass (CVE-2026-96951) and the publicly disclosed .NET Framework WDAC bypass (CVE-2026-108398). It also covers five no-interaction Outlook preview-pane RCEs, the Edge advisories that list no CVEs, and end-of-support dates for Server 2012/2012 R2, Office 2021, Exchange 2016/2019 and Windows 11 24H2. The page text is truncated, so the later CVE tables are not seen.
 rapid7.comadvisoryPublished and added 13 Oct 2026🛡️ Security
 ZDI: The October 2026 Security Update Review
ZDI's October 2026 Security Update Review covers Adobe's 11 bulletins (174 CVEs) and Microsoft's record 1,415 CVEs. The only actively exploited bug is CVE-2026-96951, a Windows Shell Mark of the Web bypass. It also flags 59 wormable bugs, Microsoft's new "risk cohorts", and top-priority fixes in ColdFusion, Commerce, Experience Manager, SharePoint, SQL Server and Exchange.
 thezdi.comadvisoryAdded 27 Oct 2026, published 13 Oct 2026🛡️ Security
- ♫Why♥Not♪ (@Python_s_) on X
Alert thread on CVE-2026-35029 (CVSS v4.0 8.7) in LiteLLM Proxy, versions before 1.83.0. A low-privilege authenticated user can bypass admin authorization on /config/update, change runtime settings, read server files, take over admin credentials and run Python through remotely loaded modules (S3/GCS-hosted). Check Point Research published a full execution chain on October 13 after the April 2026 disclosure. The post lists hunting pointers (non-admin POSTs to /config/update, env-var changes, unexpected pass-through endpoints, cloud module loading) and advises upgrading to 1.83.9 or later and rotating credentials.
x.comadvisoryPublished and added 13 Oct 2026🛡️ Security - Major ICQ security hole (1998)
Rootshell Security Bulletin #22 (Aug 1998) reports an ICQ authentication flaw found by a Linux ICQ clone developer. The Mirabilis server stores 8-character passwords, and sending a password of 9 or more characters (e.g. "123456789") overflows the buffer and logs the client in as any UIN not already online. This gives full account takeover, including receiving offline messages. It is not spoofing, and it works with unofficial clients such as zicq, since the official client enforces the length limit client-side.
 opennet.ruadvisoryAdded 17 Oct 2026, published 13 Oct 2026🛡️ Security
- lee1981 (@lee1981b) on X
CyberForge "CVE of the Day #076" covers CVE-2026-97229, a CVSS 10.0 integer overflow (CWE-190) in GitLab CE/EE's CI/CD regular expression compiler. It can lead to conditional unauthenticated code execution on the GitLab server. It lists the affected trains (19.2 before 19.2.8, 19.3 before 19.3.5, 19.4 before 19.4.2) and the 19.3.4 vs 19.3.5 Ona-regression discrepancy. It also gives six SOC checks: scoping, log preservation (Workhorse/Rails/Sidekiq, correlation_id), server-effect hunting, request-to-process correlation, upgrade and running-state verification. It notes that exploit details are unverified, no KEV listing exists and EPSS data is unavailable.
x.comadvisoryAdded 15 Oct 2026, published 13 Oct 2026🛡️ Security  MCP spec 2026-07-28 changelog (stateless protocol, MRTR, Sampling/Roots deprecated)
Official changelog for the Model Context Protocol 2026-07-28 specification. Major changes: protocol-level sessions and the initialize handshake are removed to make MCP stateless, with version and capabilities carried in _meta on every request, plus a new server/discover RPC and subscriptions/listen replacing the GET stream and resource subscribe calls. It introduces Multi Round-Trip Requests (InputRequiredResult) in place of server-initiated sampling, roots and elicitation requests, moves tasks into an extension, and deprecates Roots, Sampling, Logging, HTTP+SSE and Dynamic Client Registration. Minor changes add cache hints (ttlMs/cacheScope), new Mcp-Method/Mcp-Name headers, OpenTelemetry trace context, RFC 9207 iss validation and an error-code allocation policy.
 modelcontextprotocol.ioadvisoryAdded 10 Oct 2026🧠 AI
- MCP specification 2026-07-28 stable release
GitHub release announcing the stable 2026-07-28 revision of the Model Context Protocol specification, published from the modelcontextprotocol/modelcontextprotocol repository. The release page itself only points to the official MCP website for the spec and to a changelog for the detailed changes. It matters as the canonical version marker that MCP client, server and SDK implementers track for protocol changes.
 github.comadvisoryAdded 9 Oct 2026🧠 AI
- go-ethereum v1.17.8 "Protein Sludge Pack"
Security-focused release notes for go-ethereum (Geth) v1.17.8, patching several denial-of-service vulnerabilities in the eth/snap p2p protocol handlers, hardening JUMPDEST analysis caching against post-Amsterdam-fork attacks, requiring IP verification before accepting discovery statements, fixing a rogue-STUN-server crash, and closing a DoS vector tied to BAL accounts. Most issues only become exploitable after the Amsterdam fork activates, and the release also includes RPC correctness fixes (eth_simulateV1, eth_createAccessList) and a Sparse Blobpool (EIP-8070) correctness bug.
github.comadvisoryAdded 8 Oct 2026🛡️ Security  Critical Atlassian Path Traversal Exposes Sensitive Files Across 8 Products
Orca Security details CVE-2026-21589 (CVSS 9.3), a critical unauthenticated path traversal flaw affecting all versions of eight Atlassian Data Center and Server products: Bitbucket, Confluence, Jira Software, Jira Service Management, Bamboo, Crowd, Crucible, and Fisheye. Insufficient path validation lets remote attackers read arbitrary files within the web application root without authentication, and in Crowd SSO deployments this can expose plaintext credentials usable to create administrative accounts and take over the entire Atlassian ecosystem. The advisory lists fixed versions for each product and recommends WAF rules and log review for organizations unable to patch immediately.
orca.securityadvisoryPublished and added 7 Oct 2026🛡️ Security Atlassian Jira, Confluence (and more) Arbitrary File Read Vulnerability (CVE-2026-21589)
CVE-2026-21589 is an unauthenticated arbitrary file read (path traversal) in eight Atlassian Data Center and Server products: Bitbucket, Confluence, Jira, Jira Service Management, Bamboo, Crowd, Crucible and Fisheye. Atlassian fixed it on 5 October 2026, and CISA added it to the KEV catalog on 15 October 2026. The page lists patching, WAF regex, Tomcat RewriteValve and urlrewrite.xml mitigations, and a log check for ".." sequences after up to two rounds of URL decoding.
 watchtowr.comadvisoryAdded 30 Oct 2026, published 6 Oct 2026🛡️ Security
- Dark Web Intelligence (@DailyDarkWeb) on X
Atlassian disclosed CVE-2026-21589, a critical (CVSS 9.3) unauthenticated path traversal flaw allowing remote attackers to read specific files within the web application root across its self-managed Data Center/Server products — Jira Software, Jira Service Management, Confluence, Bitbucket, Bamboo, Crowd, Crucible, and Fisheye. Fixed versions are listed for each product (e.g. Jira 9.12.40/10.3.26/11.3.12, Confluence 9.2.26/10.2.19), and Atlassian Cloud is already patched; WAF/URL-rewrite mitigations are available for those who can't upgrade immediately. The post's analyst note clarifies exploitation requires knowing the exact target file path (no directory listing), and as of Oct 5, 2026 it is not yet in CISA KEV with no public exploit reported.
x.comadvisoryAdded 7 Oct 2026, published 6 Oct 2026🛡️ Security - MCP TypeScript SDK v2.2.0
Release notes for v2.2.0 of the official Model Context Protocol TypeScript SDK. Upgrade notes: machine-to-machine OAuth providers (ClientCredentialsProvider, PrivateKeyJwtProvider, StaticPrivateKeyJwtProvider, CrossAppAccessProvider) should now be given expectedIssuer, and fetchToken() throws AuthorizationServerMismatchError when client information is bound to a different authorization server. listTools/listPrompts/listResources/listResourceTemplates now follow nextCursor automatically, capped by listMaxPages. Fixes include CommonJS type-checking of the DPoP jose types, unhandled rejections in Client.listen(), createMcpHandler stack overflow and subscriptions/listen handling, .localhost loopback for OAuth token endpoints, and v1-to-v2 codemod comment preservation.
github.comadvisoryAdded 1 Oct 2026🧠 AI  Critical Citrix NetScaler Zero-Days Under Active Exploitation
Analysis of two CVSS 9.5 Citrix NetScaler ADC/Gateway zero-days, CVE-2026-88771 (unauthenticated RCE through improper input validation in the management interface, affecting default deployments) and CVE-2026-88772 (memory overflow in DTLS, enabled by default on VPN virtual servers). It lists six more high-severity flaws patched in advisory CTX697096, the affected and fixed versions, and the CISA KEV listing with a federal deadline of 2026-09-30. It advises checking for compromise before patching, since patching can destroy forensic evidence, and gives response steps: isolate, revoke credentials, rebuild firmware, rotate keys and certificates.
orca.securityadvisoryPublished and added 29 Sep 2026🛡️ Security watchTowr: CVE-2026-88771 Citrix NetScaler ADC/Gateway unauthenticated RCE
watchTowr details CVE-2026-88771 (unauthenticated command execution via improper input validation, affecting every NetScaler ADC/Gateway deployment by default) and CVE-2026-88772 (DTLS memory overflow leading to RCE/DoS, exploitable since DTLS is on by default for VPN virtual servers). Both are confirmed exploited in the wild as zero-days, were pre-notified by NCSC-NL, and CVE-2026-88771 was added to the CISA KEV catalog on September 27, 2026; Citrix's bulletin CTX697096 also fixes six related issues (CVE-2026-88773 through CVE-2026-88778). The writeup gives prioritization guidance, IOC-checking steps, and warns that patching may destroy forensic evidence if done before evidence capture.
watchtowr.comadvisoryAdded 5 Oct 2026, published 27 Sep 2026🛡️ Security- Kong Konnect MCP server: stored prompt injection via analytics data leads to credential/data exfiltration (CVE-2026-13341)
GitHub Security Advisory (CVE-2026-13341) for Kong's mcp-konnect MCP server describes a stored prompt injection vulnerability where a remote attacker crafts malicious request metadata (e.g. User-Agent) that gets stored in Konnect analytics and later returned unsanitized to an AI assistant via MCP tools, potentially causing the agent to exfiltrate sensitive data (plugin configs, secrets, internal hostnames) to an attacker-controlled URL if the client can make outbound fetches. A related path manipulation flaw in control plane/group identifiers allowed requesting unintended Konnect API endpoints with the user's token. The v1.0.0 patch neutralizes untrusted analytics fields, validates identifiers as UUIDs, encodes path segments, and disables raw plugin config output by default.
github.comadvisoryAdded 26 Sep 2026🛡️ Security - CVE-2026-90617 in PentestAgent
VulDB entry for CVE-2026-90617, a remote OS command injection (CWE-78) in GH05TCREW PentestAgent. The flaw is in run_task in interface/main.py of the MCP HTTP Server, affects everything up to commit cf882dab, and has a public exploit. The product uses rolling releases, so no version ranges exist, and the fix is an unmerged pull request. The analysis suggests compensating controls: restrict network access to the MCP server, run with least privilege, and validate input upstream.
 vuldb.comadvisoryAdded 26 Sep 2026🛡️ Security
- CVE-2026-85787 in postgres-mcp-server
CVE-2026-85787 affects awslabs postgres-mcp-server before 1.1.7. The SQL validation component uses an incomplete list of disallowed inputs. Crafted SQL placed in content submitted while an authenticated user interacts with the MCP server can bypass the read-only restriction and modify data in PostgreSQL. The fix is to upgrade to 1.1.7 or later. VulDB's added analysis is generic: it points to SQL injection (CWE-89) and recommends least-privilege database accounts and parameterized queries.
vuldb.comadvisoryAdded 26 Sep 2026🛡️ Security - CVE-2026-85661 in excel-mcp-server
CVE-2026-85661 affects excel-mcp-server 0.1.8. In stdio mode with EXCEL_FILES_PATH unset, the server does not confine file paths, so a client can pass relative or absolute paths to the read and write tools. That gives arbitrary file read and write with the privileges of the server process. The page classifies it as CWE-22 (ATT&CK T1083) and recommends canonical path checks against a base directory, making EXCEL_FILES_PATH mandatory, and running with least privilege.
vuldb.comadvisoryAdded 26 Sep 2026🛡️ Security - Vulnerability Database - OSV
CVE-2026-91931 is a critical remote code execution vulnerability in Flowise versions before 3.1.4, triggered through the platform's Custom MCP feature which invokes npx to run Model Context Protocol servers. A fix is available in 3.1.4; the flaw scores 9.0 (Critical) on CVSS, indicating an attacker can achieve arbitrary code execution likely via unsanitized input to the npx invocation path.
 osv.devadvisoryAdded 26 Sep 2026🛡️ Security
- CVE-2026-75130: Context7 through 2
CVE-2026-75130 describes a prompt injection flaw in Context7 (through v2.1.2), an MCP server that serves library documentation to AI coding agents. The vulnerability lies in the Custom AI Instructions feature, which fails to sanitize content before injecting it into agent context; attackers can poison these instructions so that a routine documentation lookup triggers the agent to exfiltrate credentials from environment files and delete files on the victim's machine. Researchers at Noma Security and VulnCheck published independent technical breakdowns of the attack chain.
 nvd.nist.govadvisoryAdded 26 Sep 2026🛡️ Security
- CVE-2026-65695: Office-Word-MCP-Server through 1
CVE-2026-65695 is a path traversal vulnerability (CWE-22, CVSS 4.0 7.6 HIGH) in Office-Word-MCP-Server through version 1.1.11, an MCP server that exposes Word document manipulation tools to LLM agents. Attackers who can influence the filename argument can supply absolute paths or ../ sequences to document open/save operations, bypassing the check_file_writeable and ensure_docx_extension helpers (which do no base-directory confinement or realpath validation) to read or overwrite arbitrary .docx files outside the intended working directory.
nvd.nist.govadvisoryAdded 26 Sep 2026🛡️ Security - CVE-2026-65056: mcp-webresearch 0
CVE-2026-65056 describes a server-side request forgery in the mcp-webresearch MCP server (npm package @mzxrai/mcp-webresearch, v0.1.7), scoring CVSS 4.0 8.3 HIGH. The visit_page tool only validates URL protocol and does not filter private, loopback, link-local, or cloud metadata IP ranges, so an attacker who controls the LLM-supplied URL argument (e.g. via prompt injection) can steer the server's Playwright browser to internal endpoints like cloud instance metadata services and exfiltrate sensitive internal content, including credentials, back into the model context.
nvd.nist.govadvisoryAdded 26 Sep 2026🛡️ Security - CVE-2026-57860: ForgeCode (tailcallhq/forgecode), an AI pair-programming CLI, automatically loads and executes the MCP servers defined i
CVE-2026-57860 describes an arbitrary code execution flaw in ForgeCode (tailcallhq/forgecode), an AI pair-programming CLI that automatically loads and executes MCP servers defined in a repository's .mcp.json on startup without user confirmation. A malicious repo can define mcpServers entries with arbitrary command/args (e.g. bash -c) that spawn under the invoking user's privileges the moment forge is run inside the cloned repo, giving attackers a reliable initial-access and persistence primitive against developers evaluating untrusted code. CVSS 4.0 8.4 HIGH, CWE-829 (inclusion of functionality from untrusted control sphere); a fix commit and VulnCheck advisory are linked.
nvd.nist.govadvisoryAdded 26 Sep 2026🛡️ Security - CVE-2026-52869: The MCP Python SDK, called mcp on PyPI, is a Python implementation of the Model Context Protocol (MCP)
CVE-2026-52869 describes a session-hijacking flaw in the MCP Python SDK (PyPI package mcp) prior to version 1.27.2: the SSE and stateful Streamable HTTP transports (mcp.server.sse.SseServerTransport and mcp.server.streamable_http_manager.StreamableHTTPSessionManager) route requests to existing sessions using only the session_id query parameter or Mcp-Session-Id header, without checking that the requesting principal matches the session's original authenticated bearer-token client. This lets a different authenticated client that learns or guesses a valid session ID inject JSON-RPC messages into another user's MCP session. CVSS 3.1 base score 7.1 (High); fixed in mcp 1.27.2.
nvd.nist.govadvisoryAdded 26 Sep 2026🛡️ Security - CVE-2026-42271: LiteLLM is a proxy server (AI Gateway) to call LLM APIs in OpenAI (or native) format
CVE-2026-42271 describes an unauthenticated-privilege RCE in LiteLLM (versions 1.74.2 to before 1.83.7): the MCP server preview endpoints POST /mcp-rest/test/connection and POST /mcp-rest/test/tools/list accept a full stdio MCP server config (command, args, env) and spawn it as a subprocess on the proxy host, gated only by a valid API key with no role check. Any authenticated user, including low-privilege internal-user keys, could run arbitrary commands on the LiteLLM proxy host. Patched in v1.83.7; also tracked as GHSA-v4p8-mg3p-g94g and affects Red Hat OpenShift AI.
nvd.nist.govadvisoryAdded 26 Sep 2026🛡️ Security - CVE-2026-19984: A flaw has been found in jkawamoto mcp-florence2 up to 0
CVE-2026-19984 describes a server-side request forgery flaw in jkawamoto mcp-florence2 (up to 0.3.13), an MCP server wrapping Microsoft Florence-2 image model. The vulnerable get_images function in src/mcp_florence2/__init__.py passes an attacker-controlled src argument into an HTTP fetch without validation, letting a remote caller force the server to request arbitrary internal or external URLs. The maintainer recommended fix is deploying an SSRF-safe egress proxy rather than patching the source, and a public exploit is available.
nvd.nist.govadvisoryAdded 26 Sep 2026🛡️ Security - CVE-2026-19978: A flaw has been found in jiantao88 android-mcp-server up to cfb872b2446794193b58edd63f4dbf6af48a6292
CVE-2026-19978 describes an OS command injection (CWE-77/78) in jiantao88's android-mcp-server, where the child_process.exec call in build/index.js fails to sanitize the deviceId, packageName, permission, and extras[].key/value arguments used to control Android devices. The flaw allows local command execution and has a published exploit; it was fixed in commit 14e2bf27c88ba137e35cbb0c2a75f72b595bb98a. CVSS 4.0 base score is 1.9 (local attack vector only), and the project uses rolling releases so no fixed version numbers are assigned.
nvd.nist.govadvisoryAdded 26 Sep 2026🛡️ Security - CVE-2026-18655: Improper restriction of intended endpoints in the RabbitMQ broker connection tools of the Amazon MQ MCP Server (awslabs
CVE-2026-18655 describes an improper endpoint restriction flaw (CWE-923) in the RabbitMQ broker connection tools of awslabs.amazon-mq-mcp-server versions before 2.0.24. A remote unauthenticated attacker can use prompt injection introduced into the MCP client context to redirect the broker hostname to an attacker-controlled endpoint, causing Amazon MQ for RabbitMQ credentials or OAuth access tokens to be sent there; CVSS 4.0 base score 7.1 (High). Fixed in version 2.0.24, referenced via an AWS security bulletin and a GitHub security advisory (GHSA-xwj6-8x5h-hjp6).
nvd.nist.govadvisoryAdded 26 Sep 2026🛡️ Security - CVE-2026-16584: Improper handling of an initialization failure in AWS API MCP Server from 0
CVE-2026-16584 affects AWS API MCP Server (awslabs.aws-api-mcp-server) versions 0.2.13 through 1.3.46: if the security policy enforcement data fails to initialize at server startup, the tool silently skips policy checks for the rest of the process's life, letting an agent execute AWS API operations the admin configured the policy to deny or gate. Underlying IAM permissions still apply and are unaffected, but the intended allow/deny gating layer is bypassed (CWE-455, improper handling of initialization failure). Fixed in 1.3.47.
nvd.nist.govadvisoryAdded 26 Sep 2026🛡️ Security - CVE-2026-16498: The terraform-mcp-server before version 1
CVE-2026-16498 is a critical (CVSS 3.1: 10.0) exposure-of-sensitive-information flaw (CWE-488) in HashiCorp's terraform-mcp-server prior to version 1.1.0. In stateless streamable-HTTP transport mode, one user's Terraform API token could be reused to execute tool calls on behalf of a different, subsequent user, breaking tenant isolation in shared MCP server deployments. Fixed in terraform-mcp-server 1.1.0; further detail is tracked in HashiCorp's HCSEC-2026-23 advisory.
nvd.nist.govadvisoryAdded 26 Sep 2026🛡️ Security - CVE-2026-14748: A flaw has been found in AIAnytime Awesome-MCP-Server up to a884bb51bcd99e08e14fd712c749d55d9d9a13ab
CVE-2026-14748 is a low-severity (CVSS 4.0: 2.1) server-side request forgery flaw in AIAnytime's Awesome-MCP-Server, specifically in the mcp-wiki/wiki-summary component's server.py, where the url argument is not validated before the server fetches it. A remote, low-privilege attacker can abuse this to make the MCP server issue arbitrary outbound requests; the exploit has already been published via GitHub issues and the maintainer has not responded to the disclosure.
nvd.nist.govadvisoryAdded 26 Sep 2026🛡️ Security - CVE-2026-14541: An authentication bypass and audience confusion vulnerability exists in the Google OAuth provider component of Google mc
CVE-2026-14541 describes an authentication bypass (CWE-287) in the Google OAuth provider of Google's mcp-toolbox for databases v1.4.0, an MCP server that lets LLM agents query databases. When the Google authService is configured with mcpEnabled: true but no explicit audience or clientId, the ValidateMCPAuth pipeline skips audience checks for opaque tokens, so any valid Google OAuth access token — even one issued for an unrelated app — is accepted, letting unauthorized clients reach protected tools and data backends.
nvd.nist.govadvisoryAdded 26 Sep 2026🛡️ Security - Unauthenticated Administrator takeover exfiltrated via the MCP
GHSA advisory for SiYuan v3.7.1 (CVE-2026-66012) describing how the kernel's POST /mcp route registers 31 MCP tools — including a file tool with full read/write/delete/rename/copy over the workspace — gated only by CheckAuth with no admin or read-only check. When the Publish server runs in anonymous mode (a documented configuration for public docs sites), the Publish reverse proxy attaches an anonymous RoleReader JWT to every proxied request, letting an unauthenticated attacker reach /mcp, exfiltrate accessAuthCode/api.token/cookieKey from conf.json, escalate to Administrator, and plant a malicious Electron plugin (nodeIntegration:true, contextIsolation:false) for RCE on the desktop client. Includes a full working PoC and remediation (CheckAdminRole gate, proxy path allowlist, restricting the file tool).
github.comadvisoryAdded 26 Sep 2026🛡️ Security - "Allowed HTTP Request Domains" Restriction Bypass via AI Agents MCP Connector
n8n's AI Agents module did not enforce the "Allowed HTTP Request Domains" restriction on credentials. A member-level user with use-only access to a shared credential could point an MCP tool at an attacker-controlled URL and run the agent, so the credential secret was sent to an external server. It only affects instances with the agents module enabled via N8N_ENABLED_MODULES and a domain-restricted credential shared with a member. It is fixed in 2.28.1 and 2.27.4, and the advisory rates it High (CVSS v4 7.1).
github.comadvisoryAdded 26 Sep 2026🛡️ Security - Ruby SSE Session Poisoning
A GitHub Security Advisory (GHSA-5p9g-j988-pcwv) documents a session poisoning flaw in the Ruby MCP SDK's Streamable/SSE HTTP transport: the server never validates that a POST to /messages/{session_id} actually belongs to the caller, so an attacker who obtains a victim's session ID (e.g. via logs or network sniffing) can silently execute tool calls whose responses are delivered into the victim's own SSE stream. The advisory includes a working PoC (attacker/legitimate client scripts against the SDK's example streamable_http_server.rb), notes that csharp-sdk and go-sdk correctly bind sessions to user identity while ruby-sdk does not, and distinguishes the bug from the related "Stream Replacement" advisory (GHSA-qvqr-5cv7-wh35), which disconnects rather than poisons the victim's stream.
github.comadvisoryAdded 26 Sep 2026🛡️ Security - Missing authentication on MCP HTTP endpoint allows unauthenticated privileged tool calls
GHSA advisory for jovancoding/network-ai disclosing that its MCP HTTP transport (bin/mcp-server.ts, lib/mcp-transport-sse.ts) accepts JSON-RPC tools/call requests with zero authentication, session, or origin checks, and binds to 0.0.0.0 by default. The PoC shows an unauthenticated attacker can enumerate 22 registered tools and invoke privileged ones - config_get/config_set to read and mutate live orchestrator configuration, agent_list/agent_spawn/agent_stop, token_create/token_revoke, budget_set_ceiling, and blackboard_write/delete - with curl requests against a local Docker deployment. Remediation recommended enforcing bearer-token auth in _handlePost() before dispatch, defaulting to 127.0.0.1 binding, and gating state-mutating tools behind authorization checks.
github.comadvisoryAdded 26 Sep 2026🛡️ Security - Flowise MCP Security Bypass Enables RCE
GHSA advisory detailing three bypasses in Flowise's Custom MCP Server security controls (validateCommandFlags and validateArgsForLocalFileAccess in packages/components/nodes/tools/MCP/core.ts) that combine to achieve remote code execution: an unblocked `docker build` subcommand that pulls and runs a remote Dockerfile, a missing `--yes` long-flag alias on the npx blocklist (only `-y` was blocked) enabling arbitrary npm package execution, and a Unix absolute-path regex that fails to catch double-leading-slash paths (`//root/...`), allowing `node` to execute an uploaded local file. Any authenticated Flowise user (or an API key with chatflow view/update rights) can chain these to fully compromise the host via a prediction API call.
github.comadvisoryAdded 26 Sep 2026🛡️ Security  CVE-2026-44895 - GitHub Advisory Database
GitHub advisory for @yoda.digital/gitlab-mcp-server (mcp-gitlab-server): with USE_SSE=true the HTTP/SSE transport has no authentication, sends wildcard CORS headers, and binds to 0.0.0.0. Any network caller or any web page the operator visits can open /sse and POST /messages to drive all 86 GitLab tools (delete_repository, push_files, etc.) using the operator's personal access token. It includes a curl PoC, a CVSS 4.0 vector (~6.3 Medium, effectively High when SSE is enabled) and four fixes: required auth token, loopback bind, a CORS allowlist, and the OAuth roadmap.
github.comadvisoryAdded 26 Sep 2026🛡️ Security- Warning: Vulnerability in Starlette framework and related frameworks like FastAPI exposes millions of servers to authentication bypass, Patch Immediately! | CCB Belgium
Belgian CCB advisory on CVE-2026-48710 ("BadHost", CVSS 6.5), an authentication bypass in Starlette versions before 1.0.1. The Host header was not validated when request.url was rebuilt, so request.url.path could differ from the routed path. Middleware and endpoints that enforce access control on request.url could therefore be bypassed. The flaw affects FastAPI, LiteLLM, vLLM, MCP servers and other Python LLM infrastructure, and may expose stored third-party credentials. The advisory recommends upgrading to 1.0.1 or later and increasing monitoring, and links to the badhost.org scanner and to the GitHub, OSTIF, X41 D-Sec and Ars Technica write-ups.
 ccb.belgium.beadvisoryAdded 26 Sep 2026🛡️ Security
- CVE-2026-87912 and CVE-2026-87913: Missing S3 bucket ownership verification in the AWS Security Agent plugin for aws-agents-for-devsecops and MCP Server
AWS bulletin 2026-105-AWS discloses CVE-2026-87912 and CVE-2026-87913: the AWS Security Agent plugin (aws-agents-for-devsecops, <1.1.0) and its MCP server (<0.2.0) write scan output to a predictably-named S3 bucket (security-agent-scans-<account-id>-<region>) without verifying bucket ownership. An attacker who pre-registers that bucket name in their own account can obtain the victim's private source archive, including embedded credentials and infrastructure state. AWS recommends upgrading to 0.2.0 and manually verifying/pre-creating the scan bucket to prevent squatting.
 aws.amazon.comadvisoryAdded 26 Sep 2026🛡️ Security
- CVE-2026-87911 - Read-only enforcement bypass enabling operating system command execution in the SQL validation component of Amazon awslabs postgres-mcp-server
AWS bulletin for CVE-2026-87911, an OS command injection flaw in awslabs.postgres-mcp-server (Python, PyPI) versions before 1.1.7. The server's read-only enforcement in its SQL validation component can be bypassed with a crafted `COPY ... TO PROGRAM` statement, letting an unauthenticated actor run OS commands on a self-managed PostgreSQL host when the configured connection role holds superuser or pg_execute_server_program privileges. Fixed in 1.1.7; AWS also recommends connecting the MCP server with a least-privilege, non-superuser role as defense in depth.
aws.amazon.comadvisoryAdded 26 Sep 2026🛡️ Security  CVE-2026-94127: Critical Unauthenticated RCE in F5 BIG-IP APM
Rapid7's ETR writeup covers CVE-2026-94127, a critical heap-based buffer overflow (CVSS 9.8) in F5 BIG-IP Access Policy Manager that allows unauthenticated remote code execution via crafted traffic. Exploitation requires a virtual server with both an APM access policy and an OAuth profile configured, affects the data plane (including Appliance mode), and has been added to CISA KEV; F5 provides hotfixes for the 21.1.0, 17.5.0, and 17.1.0 release trains plus an iRule workaround for those unable to patch immediately.
rapid7.comadvisoryAdded 7 Oct 2026, published 23 Sep 2026🛡️ Security WordPress “Comment2Shell” XSS-to-RCE Chain Lets Unauthenticated Attackers Compromise Servers via Malicious Comments
CVE-2026-93485 (CVSS 7.1) is a stored XSS-to-RCE chain in WordPress Core's wpautop() function (wp-includes/formatting.php), where a mismatch between comment sanitization at save time and HTML reformatting at display time lets an unauthenticated attacker inject live event handlers via a crafted comment. When a logged-in administrator views the page, the script executes and installs a malicious plugin containing a web shell, achieving full RCE. It affects WordPress Core 4.7 through 7.1.0 (essentially all installs, including block themes since Twenty Twenty-Two), and is fixed in 7.1.1 with backports down to 4.7.36; no public PoC or in-the-wild exploitation was reported at disclosure time.
orca.securityadvisoryPublished and added 22 Sep 2026🛡️ Security WordPress 7.1.2 Release (CVE-2026-87902 path-traversal RCE fix)
WordPress 7.1.2 patches CVE-2026-87902 (GHSA-7hp8-65ch-5whp), a critical unauthenticated path-traversal flaw where page template resolution can be manipulated to include an attacker-chosen readable local PHP file outside the active theme directory. Under certain server and active-theme preconditions this local file inclusion escalates to remote code execution. The security fix was backported to all WordPress branches back to 4.7; discovery credited to researcher Robert Ressl.
 wordpress.orgadvisoryAdded 28 Sep 2026, published 22 Sep 2026🛡️ Security
 CVE-2026-85706: GitLab CE/EE Repository Commits API Path Traversal
CVE-2026-85706 is a CVSS 10.0 critical path traversal vulnerability in GitLab CE/EE's repository commits API, caused by improper path confinement combined with missing authentication enforcement. It allows unauthenticated, remote attackers to read arbitrary files from the GitLab server — potentially exposing credentials, secrets, tokens, SSH keys, and database credentials. Affects versions 18.7 through 19.1.7, 19.2.0-19.2.5, and 19.3.0-19.3.1; fixed in 19.1.8, 19.2.6, and 19.3.2.
horizon3.aiadvisoryAdded 17 Sep 2026, published 11 Sep 2026🛡️ Security Rapid Reaction: GitLab Critical Path Traversal Vulnerability (CVE-2026-85706)
watchTowr's rapid-reaction analysis of CVE-2026-85706, a critical (CVSS 10.0) unauthenticated path traversal in GitLab CE/EE's repository commits API, patched in versions 19.3.2, 19.2.6, and 19.1.8. The flaw lets an unauthenticated attacker read arbitrary files (configs, secrets) from self-managed GitLab servers via crafted requests to /api/v4/projects/{id}/repository/commits/ with a file.path parameter; watchTowr reproduced the bug and reports honeypot probes indicating attackers have already reverse-engineered it ahead of mass exploitation.
watchtowr.comadvisoryAdded 21 Sep 2026, published 11 Sep 2026🛡️ Security- Rapid Reaction: GitLab Path Traversal Vulnerability (CVE-2026-85706)
watchTowr's rapid-reaction analysis of CVE-2026-85706, a critical (CVSS 10.0) unauthenticated path traversal vulnerability in the GitLab CE/EE repository commits API, patched in versions 19.3.2, 19.2.6, and 19.1.8. The flaw allows an unauthenticated attacker to read arbitrary server-side files via the commits API due to improper path confinement and missing auth enforcement; watchTowr's honeypot network was already observing exploitation probes at time of publication. The post includes hunting guidance (searching logs for POST requests to /api/v4/projects/{id}/repository/commits/ containing file.path parameters) and patching priorities for self-managed instances.
watchtowr.comadvisoryAdded 16 Sep 2026, published 11 Sep 2026🛡️ Security  Microsoft Patch Tuesday for September 2026 — Snort rules and prominent vulnerabilities
Cisco Talos's analysis of Microsoft's September 2026 Patch Tuesday release, covering 973 vulnerabilities (113 critical, 82 of those RCE). Two flaws are confirmed exploited in the wild — CVE-2026-81963 (Windows Update Stack elevation of privilege) and CVE-2026-85880 (Windows ALPC elevation of privilege) — alongside a long list Microsoft rates "more likely" to be exploited, including a Windows Kerberos auth-bypass-by-replay RCE (CVE-2026-69676) and a Windows DNS Server use-after-free RCE (CVE-2026-69730). Talos releases accompanying Snort 2/3 rule coverage (SIDs 67011-67084, 301619-301655) to detect exploitation attempts.
 blog.talosintelligence.comadvisoryAdded 7 Oct 2026, published 8 Sep 2026🛡️ Security
- Patch Tuesday - September 2026
Rapid7's September 2026 Patch Tuesday analysis: Microsoft published 974 own-product CVEs (723 in Windows), 999 in total with non-Microsoft fixes, the most it has ever published in one day. Two zero-days are exploited in the wild: CVE-2026-85880 (Windows ALPC elevation of privilege to SYSTEM via out-of-bounds write; not patched on Server 2025 or Windows 11) and CVE-2026-81963 (Windows Update Stack elevation of privilege via improper link resolution). It also flags Microsoft's missing Edge advisory for the exploited Chromium V8 zero-day CVE-2026-85046, lists upcoming end-of-support dates for Windows 11 24H2, Server 2012/2012 R2, Office 2021 and Exchange 2016/2019, and includes per-product CVE tables with exploitation-likelihood ratings. Only the first part of the page was available, so the later tables are not covered.
rapid7.comadvisoryAdded 7 Oct 2026, published 8 Sep 2026🛡️ Security  Grafana fixes critical SSRF flaw affecting Grafana MCP servers
Grafana patched CVE-2026-19516 (CVSS 9.1), a critical SSRF in the Grafana MCP server's grafana_api_request tool where a caller-supplied X-Grafana-URL header could control the method, path and body of outbound requests, letting an attacker reach internal-only services from the server's network position. Pillar Security researchers chained this with a second flaw — the MCP server accepting unauthenticated "session-shaped IDs" it never issued — and demonstrated using it to hit the AWS IMDSv2 endpoint and retrieve cloud credentials via a two-step PUT/TTL token request. Grafana MCP v1.1.0 adds optional bearer-token auth to close the session-forgery gap; Pillar frames MCP servers broadly as "identity brokers" that need explicit outbound destination policies and mandatory auth for remote deployments.
 scworld.comadvisoryAdded 26 Sep 2026, published 3 Sep 2026🛡️ Security
 Lose Control Flow: Unauthenticated Tool Execution in Dolt MCP
Pillar Security details CVE-2026-73554, a critical authentication bypass in DoltHub's remote Dolt MCP server (versions 0.3.1–0.3.6) that let unauthenticated attackers reach tool dispatch and execute database operations under the server's own credentials. The bug combined a JWT middleware missing a return statement (so a 401-rejected request kept processing) with the bundled mark3labs/mcp-go library's InsecureStatefulSessionIdManager, which accepted any attacker-forged mcp-session-<uuid> value without verifying server issuance. DoltHub confirmed and patched within a day, issuing GHSA-mgpq-fxxc-h49q; fixed in Dolt MCP 0.3.7.
 pillar.securityadvisoryPublished and added 1 Sep 2026🛡️ Security


Showing 60 of 90
Show more