- ClioBitcoinBank 🏴☠️ (@ClioBitcoinBank) on X
lnd v0.20.7 and v0.21.6 are Lightning Network Daemon releases announced by Clio Bitcoin Bank. They include a Go-specific mitigation, with the MPTCP flag turned off, for CVE-2026-98432, a use-after-free in the Linux kernel's IPv4 TCP code. The post recommends all users update. It gives no exploit or impact detail.
 x.comadvisoryPublished and added 31 Oct 2026🛡️ Security
- Bunny CDN Security Incident
Bunny CDN status-page notice, posted 28 October 2026, about unauthorized access at an infrastructure provider that hosted one bunny.net CDN node in Armenia. Traffic was stopped within 20 minutes and the server wiped. No access to the node was found, but cached content, Pull Zone configs and TLS certificates could have been exposed, so all platform certificates were reissued. Customers with their own certificates should rotate them with new private keys.
 status.bunny.netadvisoryAdded 31 Oct 2026, published 30 Oct 2026🛡️ Security
- CISA Adds Two Known Exploited Vulnerabilities to Catalog
CISA added two Ivanti Connect Secure vulnerabilities to its Known Exploited Vulnerabilities (KEV) Catalog on 30 October 2026, citing evidence of active exploitation: CVE-2026-111357 (missing authentication for a critical function) and CVE-2026-118527 (generation of predictable numbers or identifiers). The alert restates BOD 26-04, which requires federal civilian agencies to remediate KEV-listed flaws on exposed assets and check for prior compromise. It also links the KEV nomination form.
 cisa.govadvisoryPublished and added 30 Oct 2026🛡️ Security
- CISA Adds Two Known Exploited Vulnerabilities to Catalog
CISA alert of 29 October 2026 adding two vulnerabilities to the Known Exploited Vulnerabilities catalog on evidence of active exploitation: CVE-2026-97229, an integer overflow in GitLab CE/EE, and CVE-2026-76418, a NULL pointer dereference from an unchecked return value in Cisco Secure Firewall ASA and FTD. It restates BOD 26-04 remediation duties for federal civilian agencies and links the KEV nomination form.
cisa.govadvisoryPublished and added 29 Oct 2026🛡️ Security  Threat Brief: Critical Vulnerabilities in PHP: CVE-2026-109618, CVE-2026-109619 (Updated October 29)
Unit 42 threat brief on PHP2Shell, two PHP remote code execution flaws, CVE-2026-109618 and CVE-2026-109619 (CVSS 4.0 9.2), both caused by longjmp() error handling that leaves memory uninitialized or freed. Cortex Xpanse counted over 22.6 million exposed instances. The 29 October 2026 update says attackers chained PHP2Shell with a Linux kernel privilege escalation against internet-exposed PAN-OS management interfaces. An earlier 23 October claim of post-compromise activity was retracted on 25 October.
 unit42.paloaltonetworks.comadvisoryAdded 30 Oct 2026, published 29 Oct 2026🛡️ Security
 CVE-2026-98432: 9.8 CVE affecting all Ubuntu versions
CVE-2026-98432 is a Linux kernel use-after-free in the IPv4 TCP stack, tracked by Ubuntu (published 15 October 2026, updated 29 October 2026). ireq_opt/inet_opt were freed with plain kfree() while another CPU built a SYNACK under RCU, so ip_options_build() read freed memory; the fix uses kfree_rcu(). Ubuntu rates it High priority, CVSS v3.1 9.8 and v4.0 8.3. The page text does not list per-release package status.
 ubuntu.comadvisoryAdded 30 Oct 2026, published 29 Oct 2026🛡️ Security
- lee1981 (@lee1981b) on X
CVE-2026-103780 is a stack-based buffer overflow (CWE-121) in Dell PowerProtect Data Domain / DD OS. An unauthenticated remote attacker could get command execution (CVSS 3.1 9.8, Dell DSA-2026-416). The post lists affected and fixed builds for four release trains (Feature Release, LTS2024, LTS2025, LTS2026). It adds KEV, EPSS and SSVC status, plus six defensive checks. The vulnerable service is not public.
x.comadvisoryAdded 31 Oct 2026, published 29 Oct 2026🛡️ Security  CVE-2026-101767: Critical Oracle EBS SQL Injection Actively Probed in the Wild
CVE-2026-101767 is a CVSS 9.8 unauthenticated SQL injection in Oracle E-Business Suite's Application Object Library, reachable through the /OA_HTML/AppsTCFServer servlet (GanttDataServer) and chainable to OS command execution. It affects versions 12.2.3 to 12.2.15 and was fixed in the October 2026 Critical Patch Update. Horizon3.ai found it, and Defused saw probing on honeypots on 27 October 2026. Interim mitigation is removing the servlet from the URL firewall allowlist.
 orca.securityadvisoryPublished and added 28 Oct 2026🛡️ Security
- Hitachi Energy CoreTec Product
CISA advisory ICSA-26-302-03, republished from Hitachi Energy PSIRT 8DBD000258, covers OS command injection (CVE-2026-13162) and the Dirty Frag vulnerability (CVE-2026-43284) in Hitachi Energy CoreTec. CoreTec5 up to 3.4.0 and 5.0.0 are affected by both, and CoreTec4 up to 3.4.0 by CVE-2026-13162. The advisory was released 27 October 2026 and lists generic ICS mitigations. SSVC rates exploitation as none.
cisa.govadvisoryAdded 29 Oct 2026, published 28 Oct 2026🛡️ Security - Hitachi Energy TRO600 series products
ICSA-26-302-02 is a CISA republication of Hitachi Energy PSIRT advisory 8DBD000224 on the TRO600 series. It covers CVE-2026-10756 and CVE-2026-106087, which allow remote code execution and disclosure of sensitive information. Affected versions are TRO600 up to 9.2.1.6 and 9.1.1.0, plus 9.2.2.1 and 9.1.2.0. The page gives no per-CVE detail or CVSS scores, only general ICS hardening advice. Released 27 October 2026.
cisa.govadvisoryAdded 29 Oct 2026, published 28 Oct 2026🛡️ Security - Siemens Mendix SAML Module
ICSA-26-302-01 republishes Siemens SSA-137528 on the Mendix SAML module, which has an authentication bypass (CVE-2026-89209). An unauthenticated remote attacker can replay a valid SAML assertion in IdP-initiated flows to gain unauthorized access. Fixed in 4.2.4 for Mendix 10 and 11, and 3.6.29 for Mendix 9. Initial release was 26 October 2026.
cisa.govadvisoryAdded 29 Oct 2026, published 28 Oct 2026🛡️ Security - CISA Adds Two Known Exploited Vulnerabilities to Catalog
CISA alert of 28 October 2026 adding two vulnerabilities to the Known Exploited Vulnerabilities Catalog on evidence of active exploitation: CVE-2026-41709 (Broadcom VMware ESX insufficient logging) and CVE-2026-46300 (Linux kernel missing variable initialization). It restates BOD 26-04, which requires federal civilian agencies to prioritize fast remediation of KEV CVEs on exposed assets and to check for prior compromise. It also links the KEV nomination form.
cisa.govadvisoryAdded 29 Oct 2026, published 28 Oct 2026🛡️ Security  CVE-2026-20362 | Cisco Finesse Server-Side Request Forgery Vulnerability
CVE-2026-20362 is an unauthenticated server-side request forgery in Cisco Finesse (CVSS 3.1 score 7.2), found by Horizon3 researchers Noah King and Brandon Peterson. The embedded Apache Shindig content proxy fetches attacker-supplied URLs, including loopback services such as the Finesse REST API at 127.0.0.1:8082, which returns SystemInfo with node hostnames and the XMPP domain. Cisco published its advisory on 7 October 2026. Fixes are planned for January and February 2027, and no workaround exists.
 horizon3.aiadvisoryAdded 29 Oct 2026, published 28 Oct 2026🛡️ Security
- lee1981 (@lee1981b) on X
CVE-2026-92885 is a critical (CVSS 3.1 9.8, CWE-287) authentication bypass in the Qode Membership WordPress plugin, versions through 2.0.6.2. A misspelled variable in the Facebook token-verification guard skips provider checks, so an unauthenticated attacker with a public nonce can get a session cookie for an existing account, including an administrator. The post gives the fix (2.0.6.3, bundled in Bridge 30.9), KEV/EPSS/SSVC status, and a SOC log-correlation and remediation plan.
x.comadvisoryAdded 31 Oct 2026, published 28 Oct 2026🛡️ Security - Dark Web Informer (@DarkWebInformer) on X
Veeam patched five vulnerabilities across Backup & Replication, Veeam Agent for Linux and Veeam ONE. The worst is CVE-2026-108142 (CVSS 9.1), an unauthenticated authorization bypass in the CDP Coordinator Service affecting Backup & Replication 13.0 and 13.1. Other fixes cover Linux agent privilege escalation, two path-traversal file writes, and a Veeam ONE MFA bypass; fixed builds are listed.
x.comadvisoryAdded 30 Oct 2026, published 28 Oct 2026🛡️ Security - CISA Adds Two Known Exploited Vulnerabilities to Catalog
CISA alert of 27 October 2026 adding two vulnerabilities to the Known Exploited Vulnerabilities (KEV) Catalog on evidence of active exploitation: CVE-2026-48356, an unrestricted upload of a dangerous file type in Adobe Commerce and Magento, and CVE-2026-111497, an unchecked return value in Google Brotli. It restates BOD 26-04, which makes federal civilian agencies prioritise KEV flaws on exposed assets and check for prior compromise. No technical detail or IOCs are given.
cisa.govadvisoryAdded 29 Oct 2026, published 27 Oct 2026🛡️ Security - Node.js Brotli Decoder Out-of-Bounds Write Threatens Remote Code Execution Across All Supported Versions
CVE-2026-111497 is a high-severity out-of-bounds write in the Node.js Brotli decoder, reported by Orca Security. It affects all supported release lines (22.x, 24.x, 26.x) and can be triggered by malformed Brotli data processed through node:zlib or fetch(). Impacts named are crashes, memory disclosure and remote code execution in cloud workloads; patching is advised. The fetched text covers only the executive summary.
orca.securityadvisoryPublished and added 27 Oct 2026🛡️ Security - lee1981 (@lee1981b) on X
CVE-2026-115905 is a ZIP cloaking flaw in the Rust zip crate (zip-rs/zip2), rated CVSS v4.0 10.0 and affecting versions below 9.0.5. ZipArchive reads central-directory metadata while ZipStreamReader reads local headers, so a crafted archive can pass filename inspection and then overwrite a different file during streaming extraction. Version 9.0.5 adds consistency checks, but ZipStreamReader::new leaves them off by default, and extraction is not atomic, so files can be written before an error is raised. The post covers CWE-20 and CWE-436, KEV and EPSS status, Debian status and a six-step investigation trail.
x.comadvisoryAdded 29 Oct 2026, published 27 Oct 2026🛡️ Security - CISA Adds Two Known Exploited Vulnerabilities to Catalog
CISA added two PHP vulnerabilities to its Known Exploited Vulnerabilities Catalog on 26 October 2026: CVE-2026-109618 (memory corruption) and CVE-2026-109619 (stale internal request state). It also updated its PHP alert on critical vulnerabilities requiring immediate patching. The alert restates BOD 26-04, which requires federal civilian agencies to prioritize fast remediation of KEV CVEs on exposed assets and to check for prior compromise.
cisa.govadvisoryAdded 29 Oct 2026, published 26 Oct 2026🛡️ Security - Mitsubishi Electric and Mitsubishi Electric Iconics Digital Solutions GENESIS, GENESIS64, ICONICS Suite, Hyper Historian, AnalytiX, MobileHMI, IoTWorX, MC Works64, GENESIS32 and BizViz
CISA advisory ICSA-26-300-02 covers four vulnerabilities in Mitsubishi Electric and Mitsubishi Electric Iconics Digital Solutions GENESIS64, ICONICS Suite, Hyper Historian, AnalytiX, MobileHMI, IoTWorX, MC Works64, GENESIS32 and BizViz. CVE-2023-4863 (CWE-787 out-of-bounds write) allows code execution; CVE-2026-16436 and CVE-2026-16437 allow authentication bypass; CVE-2026-16438 allows arbitrary operations. Fixes are 10.97.3, 10.98 and GENESIS 11.04. MC Works64, GENESIS32 and BizViz are affected in all versions, and MC Works64 has no fix planned. Mitigations include removing the ClientChallengeTable.dat or SecurityChallenges.dat file contents. The fetched text was truncated, so later content is not covered.
cisa.govadvisoryAdded 29 Oct 2026, published 26 Oct 2026🛡️ Security - EPICS Base
CISA ICS advisory ICSA-26-300-01 (October 27, 2026) covers EPICS Base release 7.0.10 and earlier, with CVE-2026-114595 through CVE-2026-114598. Flaws include integer overflow, length parameter inconsistency and type confusion, allowing denial of service, memory corruption, information disclosure or remote code execution (CVSS v3.1 9.8). The fix is EPICS Base 7.0.11, with patches in epics-base and pvDataCPP pull requests.
cisa.govadvisoryAdded 29 Oct 2026, published 26 Oct 2026🛡️ Security - dbugs (@ptdbugs) on X
CVE-2026-106173 is a critical (CVSS 9.4) unauthenticated arbitrary file write in FortiSIEM's phQueryMaster gRPC service on port 27918/TCP. The SendQueryResult method builds a path from the query-id parameter without validation, so "../" sequences escape the directory and a null byte drops the appended filename and extension. Overwriting /opt/charting/redishb.sh, which runs every 60 seconds, gives remote command execution. Horizon3.ai published the analysis and a PoC.
x.comadvisoryAdded 27 Oct 2026, published 26 Oct 2026🛡️ Security  Broccoli2shell: Everything You Need To Know About The Critical Brotli Decoder Vulnerability
CVE-2026-111497 (Broccoli2Shell, also Node2Shell and HTTP2Shell) is an out-of-bounds write in the upstream Brotli C decoder. It affects Node.js, Bun, Envoy Proxy, Istio and Python packages, and can lead to memory corruption, information disclosure, crashes or RCE when untrusted Brotli data is decompressed. Wiz reports 91% of cloud environments have vulnerable resources. The post lists patching, inventory, rebuild and temporary mitigation steps.
 wiz.ioadvisoryPublished and added 25 Oct 2026🛡️ Security
- CISA: Critical Vulnerabilities in PHP Require Immediate Patching
CISA alert on CVE-2026-109618 and CVE-2026-109619 ("php2shell"), unauthenticated remote code execution flaws affecting PHP installations serving web requests, including mod_php, PHP-FPM, php-cgi, FrankenPHP and LiteSpeed. Fixed in PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35. Updated 23 October 2026 with a Sigma rule, partner advisories (NSA, NCSC-UK, ASD ACSC, NCSC-NL, NCSC-NZ, Cyber Centre) and guidance to inventory PHP, patch internet-facing systems first, and watch for PHP workers spawning shells. No in-the-wild exploitation had been observed.
cisa.govadvisoryAdded 24 Oct 2026🛡️ Security  Python packages are also vulnerable to the Node2Shell Brotli flaw (CVE-2026-111497)
Python2Shell is the Python-side impact of CVE-2026-111497 (Node2Shell), a Brotli decoder flaw (CVSS 4.0 9.2) in DecodeBlockTypeAndLength() that mixes an unchecked return value with an out-of-bounds write. Brotli 1.2.0 and earlier, and brotlicffi 1.2.0.x, are affected through urllib3, requests, httpx, aiohttp and Scrapy. Fixes are Brotli 1.2.1 and brotlicffi 1.2.1.0; as of 23 October 2026 advisory databases do not map the CVE to either package. The post lists checks and workarounds.
 aikido.devadvisoryPublished and added 23 Oct 2026🛡️ Security
 CVE-2026-109618 / CVE-2026-109619 | NodeZero Rapid Response Check Now Available
PHP2Shell is the name for CVE-2026-109618 and CVE-2026-109619, critical unauthenticated RCE flaws in PHP core fixed on 21 October 2026 in PHP 8.2.35, 8.3.36, 8.4.27 and 8.5.12. The page explains the out-of-memory corruption and stale global state causes, mod_php and PHP-FPM exposure, interim mitigations, hunting guidance, exploitation reports from October 2026, and the 23 October CVE-2026-115560 upload-progress advisory. Horizon3 also announced a non-exploiting NodeZero check.
horizon3.aiadvisoryAdded 29 Oct 2026, published 23 Oct 2026🛡️ Security Preliminary Report Oct 21st Security Incident
Railway's preliminary report on a security incident between 20 and 22 October 2026, in which an attacker reached internal systems and decrypted stored environment variables. At most 1.85% of workspaces (about 100,000) were confirmed affected. The attacker was after AI provider API keys for distillation. Railway notified vendors such as GitHub and Anthropic, rolled all keys, moved to single-tenant builders and advised customers to rotate secrets. Exploit details are withheld.
 blog.railway.comadvisoryAdded 24 Oct 2026, published 23 Oct 2026🛡️ Security
 Xavier Rivera (@XavierRiveraX) on X
CVE-2026-115560 is a PHP code execution bug reported two days after the PHP2Shell emergency patches. The post says those releases do not fix it and no emergency fix is planned. Only apps that switch session.serialize_handler to php via ini_set() before session_start() are exposed. The mitigation is session.upload_progress.enabled=0, which also covers anyone who applied it for the 21 October advisory. The post gives no technical root-cause detail.
x.comadvisoryAdded 25 Oct 2026, published 23 Oct 2026🛡️ Security Brotli vulnerability affects curl and Git
GHSA-9v8h-qqgm-4m35 is a critical buffer overflow (CVSS v4 9.2) in the Google Brotli decoder (c/dec/decode.c), affecting versions 1.0.3 through 1.2.0 on all platforms. A crafted compressed stream lets an unauthenticated remote attacker corrupt adjacent decoder state, leak memory, crash the process, or possibly execute code. Fixed in 1.0.10, 1.1.1 and 1.2.1. The page does not mention curl or Git, despite the title.
 github.comadvisoryAdded 25 Oct 2026, published 23 Oct 2026🛡️ Security
- lee1981 (@lee1981b) on X
CVE-2026-111497 is an out-of-bounds write in the Brotli decoder bundled with Node.js (CWE-787, CWE-252), rated CVSS v4.0 9.2 by the Google CNA and High by the Node.js project. Fixes are Node 22.23.4, 24.22.1 and 26.12.1, and 24.22.1 still labels Brotli 1.2.0 because the fix was cherry-picked. The post gives a SOC trail from input to worker, with remediation and verification steps. It notes no KEV match, CISA SSVC exploitation none, and only unverified public lab claims.
x.comadvisoryAdded 26 Oct 2026, published 23 Oct 2026🛡️ Security - ENISA Technical Advisory for Software Bill of Materials
ENISA Technical Advisory for Software Bill of Materials (October 2026, TLP:CLEAR) is non-mandatory guidance for organisations, especially SMEs, starting SBOM adoption. It covers SBOM data models (CycloneDX, SPDX), a mapping of BSI TR-03183-2 fields to CISA minimum elements, lifecycle and CI/CD integration, an SBOM threat model, and security recommendations. It supports Cyber Resilience Act obligations but is not a legal interpretation.
 enisa.europa.euadvisoryAdded 23 Oct 2026🛡️ Security
- ENISA Technical Advisory for Software Bill of Materials
ENISA Technical Advisory for Software Bill of Materials is practical guidance on SBOM adoption for organizations, especially micro, small and medium enterprises and open-source stewards. It sets out an SBOM implementation architecture and data flows across a defined lifecycle, an indicative SBOM threat model with targeted risks, and measures for the SBOM ecosystem. It aligns with the ENISA Secure by Design and Default Playbook and supports Cyber Resilience Act compliance.
enisa.europa.euadvisoryAdded 23 Oct 2026🛡️ Security 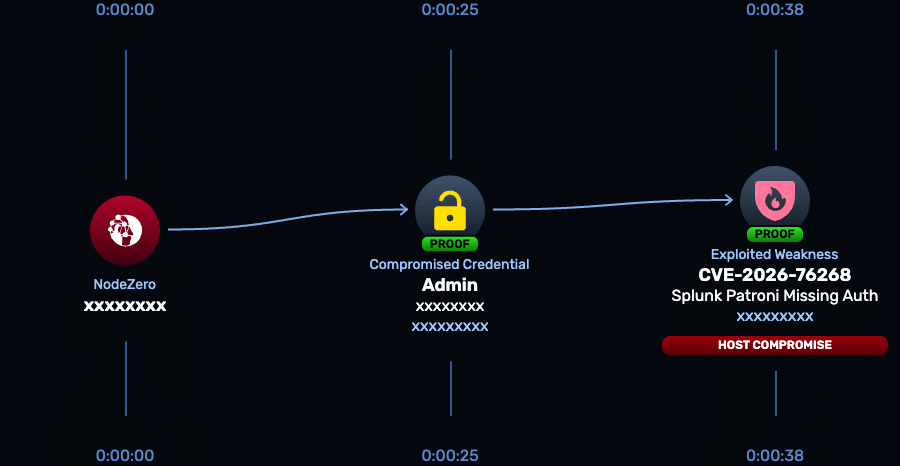 CVE-2026-76268 | Splunk Enterprise Patroni REST API Missing Authentication Vulnerability
CVE-2026-76268 is a critical (CVSS 9.8) missing authentication flaw (CWE-306) in the Patroni REST API on Splunk Enterprise search head cluster members. An unauthenticated attacker with network access can run operating-system commands. Affected: 10.4.0 to 10.4.2 and 10.2.0 to 10.2.6. Fixed in 10.4.3 and 10.2.7. Splunk (SVD-2026-1001, 7 October 2026) suggests disabling the PostgreSQL sidecar as a workaround.
horizon3.aiadvisoryAdded 29 Oct 2026, published 22 Oct 2026🛡️ Security- Dark Web Intelligence (@DailyDarkWeb) on X
CVE-2026-114625 is a critical (CVSS 3.1 9.9) SQL injection in on-prem Arista VeloCloud Orchestrator, the SD-WAN management portal, covered in Arista Security Advisory 0199 of 22 October 2026. Any authenticated user, even the lowest Enterprise Read Only tenant role, can become a local superuser operator, and Arista says it is exploited in the wild. On-prem fixes are 5.2.3.18, 6.1.3.10 and 6.4.2.12; two attacker IPs are listed.
x.comadvisoryAdded 24 Oct 2026, published 22 Oct 2026🛡️ Security  Node2Shell: Node.js Brotli vulnerability allows remote code execution (CVE-2026-111497)
Node2Shell (CVE-2026-111497) is an out-of-bounds write in the Brotli decoder bundled with Node.js and Bun, triggered by malformed compressed input and rated high by Node.js, with possible remote code execution. Fixed in Node.js 22.23.4, 24.22.1 and 26.12.1 and Bun 1.4.4. The post covers exposure via Express 5, body-parser 2.x, fetch() and node:zlib, stopgaps, and a timeline with public proofs of concept on 22 October 2026.
aikido.devadvisoryPublished and added 22 Oct 2026🛡️ Security EMudhra Intermediate CA Certificates Compromised
Unit 42 advisory on the compromise of eight intermediate CA private keys belonging to Indian CA eMudhra Limited. The keys were generated with insufficient randomness, so attackers could derive them from the public certificates and sign rogue TLS certificates for MitM attacks. eMudhra has revoked the certificates and browser and OS vendors have untrusted them. Interim guidance covers PKI and trust store audits, reissuance, strict CRL/OCSP checking, log hunting, CT monitoring and CAA records.
unit42.paloaltonetworks.comadvisoryAdded 30 Oct 2026, published 22 Oct 2026🛡️ Security- lee1981 (@lee1981b) on X
CyberForge CVE of the Day #084 analyses CVE-2026-76466, a CVSS 9.8 flaw in clustered Cisco Expressway-C and Expressway-E. Persistent database cookies and weak client-certificate validation allow root OS command execution over the network. The fix is X15.5.20 (X14 and earlier must migrate), with no workaround. It adds a per-peer SOC investigation trail, reachability checks and exposure status from CISA SSVC, KEV and EPSS.
x.comadvisoryAdded 24 Oct 2026, published 22 Oct 2026🛡️ Security  PHP Patches Two Critical Unauthenticated RCEs (CVE-2026-109618, CVE-2026-109619): Update Now
Snyk's write-up of two critical unauthenticated PHP runtime RCEs, CVE-2026-109618 (out-of-memory corruption) and CVE-2026-109619 (stale global state, cross-request use-after-free), both CVSS v4.0 9.2. Fixed in PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35 on 21 October 2026. It covers the disclosure timeline, affected SAPIs (mod_php most exposed), backports for 8.1 and older, and partial mitigations.
 snyk.ioadvisoryPublished and added 22 Oct 2026🛡️ Security
 Yul Optimizer Knowledge Base Stale Bookkeeping Bug
Solidity advisory on a Yul optimizer bug in the KnowledgeBase, present in versions 0.8.19 to 0.8.37 and fixed in 0.8.38. Stale cached address offsets let LoadResolver and EqualStoreEliminator treat coinciding memory or storage slots as distinct, so loads return outdated values or needed stores are dropped. It includes a pure-Solidity reproducer for --via-ir, a Sourcify scan with no differing bytecode, and checks for deployed contracts. Rated low severity.
 soliditylang.orgadvisoryPublished and added 22 Oct 2026🛡️ Security
- Oracle Security Alert Advisory – CVE-2026-91403 (eMudhra cert revocation)
Oracle Security Alert for CVE-2026-91403 ships Java SE updates that distrust a set of intermediate CA certificates tied to eMudhra. It contains one new patch for Oracle Java SE, described as remotely exploitable without authentication. Customers are told to update Java or apply mitigations listed at ops.java/emudhra and in the Patch Availability Document. No reporter is credited and the page gives no CVSS score or technical detail.
 oracle.comadvisoryAdded 23 Oct 2026, published 21 Oct 2026🛡️ Security
 Railway Security Disclosure
Railway's security disclosure of 21 October 2026 says an unauthorized third party may have accessed encrypted customer environment variables and decrypted some of them. Railway links it to a series of attacks on platform companies aimed at compromising AI inference providers, and has asked upstream providers to revoke keys. It tells all users to roll every environment variable, API key and registry credential, and it paused all deployments. The notice gives no technical details of the intrusion.
blog.railway.comadvisoryAdded 22 Oct 2026, published 21 Oct 2026🛡️ Security- PHP web runtimes (CVE-2026-109618 and CVE-2026-109619)
AWS bulletin 2026-143-AWS covers CVE-2026-109618 and CVE-2026-109619, critical PHP web runtime flaws that let an unauthenticated remote caller run code, read process data or cause denial of service. Fixed in PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35; PHP 5.4 to 8.1 get no fix. It gives status for WorkMail, Elastic Beanstalk, Amazon Linux and Lightsail, plus AWS WAF rules, including a custom "PHP2Shell" rule matching PHP_SESSION_UPLOAD_PROGRESS and PHPSESSID.
 aws.amazon.comadvisoryAdded 22 Oct 2026, published 21 Oct 2026🛡️ Security
 Compromised eMudhra intermediate certificates
Cisco Talos describes eight eMudhra intermediate CA certificates (six TLS, two code signing) whose P-384 private keys were trivially recoverable because a flaw in an April 30, 2025 key generation ceremony produced weak keys with only 3 to 8 bytes of entropy. The post lists certificate SHA-256 hashes and serials, browser and Microsoft blocks, and the Go fix (CVE-2026-111943, Go 1.27.3 and 1.26.10) that filters chains by SPKI hash. It covers impact on VPNs, CI/CD and embedded devices, and Snort SIDs 67363 to 67374.
 blog.talosintelligence.comadvisoryPublished and added 21 Oct 2026🛡️ Security
- EMITS (@emits_ca) on X
CVE-2026-107406 is a memory overflow in Citrix NetScaler that allows remote code execution when SAML is configured, rated 9.5 out of 10. The post from emits.ca calls it the fourth NetScaler bulletin in a week. It warns that the previous week's SAML patch does not cover it, and that fixes need NetScaler 14.1-73.46 or later, or 13.1-64.29 or later. The full advisory is on emits.ca.
x.comadvisoryAdded 22 Oct 2026, published 21 Oct 2026🛡️ Security  PHP2Shell: Critical vulnerabilities in PHP (CVE-2026-109618, CVE-2026-109619) | Endor Labs
PHP2Shell is the name for two critical PHP core memory-safety flaws, CVE-2026-109618 and CVE-2026-109619, that allow unauthenticated remote code execution. Fixes ship in PHP 8.2.35, 8.3.36, 8.4.27 and 8.5.12. Wiz researchers demonstrated RCE against WordPress, Drupal and Joomla, and Apache with mod_php is the highest risk. The post covers inventory, container rebuilds, Cloudflare WAF rules and temporary exposure reduction.
 endorlabs.comadvisoryPublished and added 21 Oct 2026🛡️ Security
 Two critical RCEs in PHP core
Cisco Talos advisory on "php2shell", two unauthenticated RCE flaws in PHP core, CVE-2026-109618 and CVE-2026-109619 (CVSS v4.0 9.2), affecting every build since PHP 5.4. One flaw is an out-of-memory handling bug leaving request data partly initialized; the other reuses stale state after free. PHP 8.1 and older get no patch (about 50% of PHP systems). Includes ini-level mitigations and Snort SIDs 67359 and 67360. No exploitation seen as of 21 October 2026.
blog.talosintelligence.comadvisoryPublished and added 21 Oct 2026🛡️ Security PHP Remote Code Execution ("PHP2Shell" CVE-2026-109618 & CVE-2026-109619)
PHP2Shell is the name for CVE-2026-109618 (out-of-memory corruption) and CVE-2026-109619 (stale global state), two unauthenticated PHP remote code execution flaws rated CVSS 4.0 9.2. Details leaked before the 21 October 2026 patch release, and watchTowr's honeypots saw exploitation. The page lists fixed versions (8.5.12, 8.4.27, 8.3.36, 8.2.35), states that .ini mitigations do not work, gives a timeline, and describes compromise checks.
 watchtowr.comadvisoryAdded 28 Oct 2026, published 21 Oct 2026🛡️ Security
 Critical PHP “PHP2Shell” RCE Vulnerabilities Allow Unauthenticated Remote Code Execution (CVSS 9.2)
PHP2Shell is the informal name for CVE-2026-109618 and CVE-2026-109619 (CVSS v4.0 9.2), unauthenticated remote code execution flaws in the PHP core runtime. Patches for branches 8.2 to 8.5 were scheduled for 21 October at 14:00 UTC, while PHP 8.1 and older get no fix; about 884,000 internet-facing hosts run those versions. watchTowr reproduced CVE-2026-109618, no public PoC existed at writing, and Sansec expects mass exploitation within 15 minutes of release.
orca.securityadvisoryPublished and added 21 Oct 2026🛡️ Security- PHP 8.2.35
PHP 8.2.35 is a security release of the PHP 8.2 branch that fixes two critical vulnerabilities, CVE-2026-109618 and CVE-2026-109619, which can allow unauthenticated remote code execution. The notes say no complete mitigations exist and updating is the only safe choice. PHP 8.2 reaches end of life on 31 December 2026, after which it gets no security fixes.
github.comadvisoryAdded 22 Oct 2026, published 21 Oct 2026🛡️ Security  JFrog Security (@JFrogSecurity) on X
JFrog Security Research warns that the LiteLLM 1.107.0 release on PyPI contains malicious code, as part of a supply-chain attack. It advises avoiding that version and investigating any environment where it was installed or executed. The post gives no technical detail, payload description or IOCs, and says a blog post will follow.
x.comadvisoryAdded 23 Oct 2026, published 21 Oct 2026🛡️ Security- Rapid Response: php2shell, Leaked Critical PHP Vulnerabilities (CVE-2026-109618 & CVE-2026-109619)
Huntress rapid-response post on php2shell, two leaked critical PHP core vulnerabilities (CVE-2026-109618 and CVE-2026-109619, CVSS v4.0 9.2 each) reported as remote code execution. The PHP team moved its security release to 21 October 2026, 14:00 UTC, after the leak. It lists hunting cues such as php-fpm, php-cgi or apache2 spawning shells, interpreters or download tools, plus inventory and patch steps. No root cause, affected versions, PoC or IOCs were public at writing.
 huntress.comadvisoryPublished and added 21 Oct 2026🛡️ Security
 Critical vulnerabilities in PHP (PHP2SHELL)
PHP2SHELL is Aikido Security's advance notice of two critical remote code execution flaws in PHP itself, CVE-2026-109618 and CVE-2026-109619, both CVSS v4.0 9.2, with all versions treated as affected. The PHP security team will release fixes at 14:00 UTC on 21 October 2026, a day early after details leaked on 20 October. The post withholds exploitation details and workarounds.
aikido.devadvisoryPublished and added 21 Oct 2026🛡️ Security- #StopRansomware: SafePay Ransomware (AA26-293A)
CISA advisory AA26-293A (20 October 2026) details SafePay ransomware, active since August 2024 with at least 600 victims across critical infrastructure. It covers initial access via Mullvad VPN IPs, phished profiles and edge-device CVEs, LOTL lateral movement with PsExec, WinRM and RDP, exfiltration with RClone and WinSCP, and ChaCha20/RSA encryption. It lists IOCs, MITRE ATT&CK mappings, incident response steps and mitigations.
cisa.govadvisoryAdded 21 Oct 2026🛡️ Security 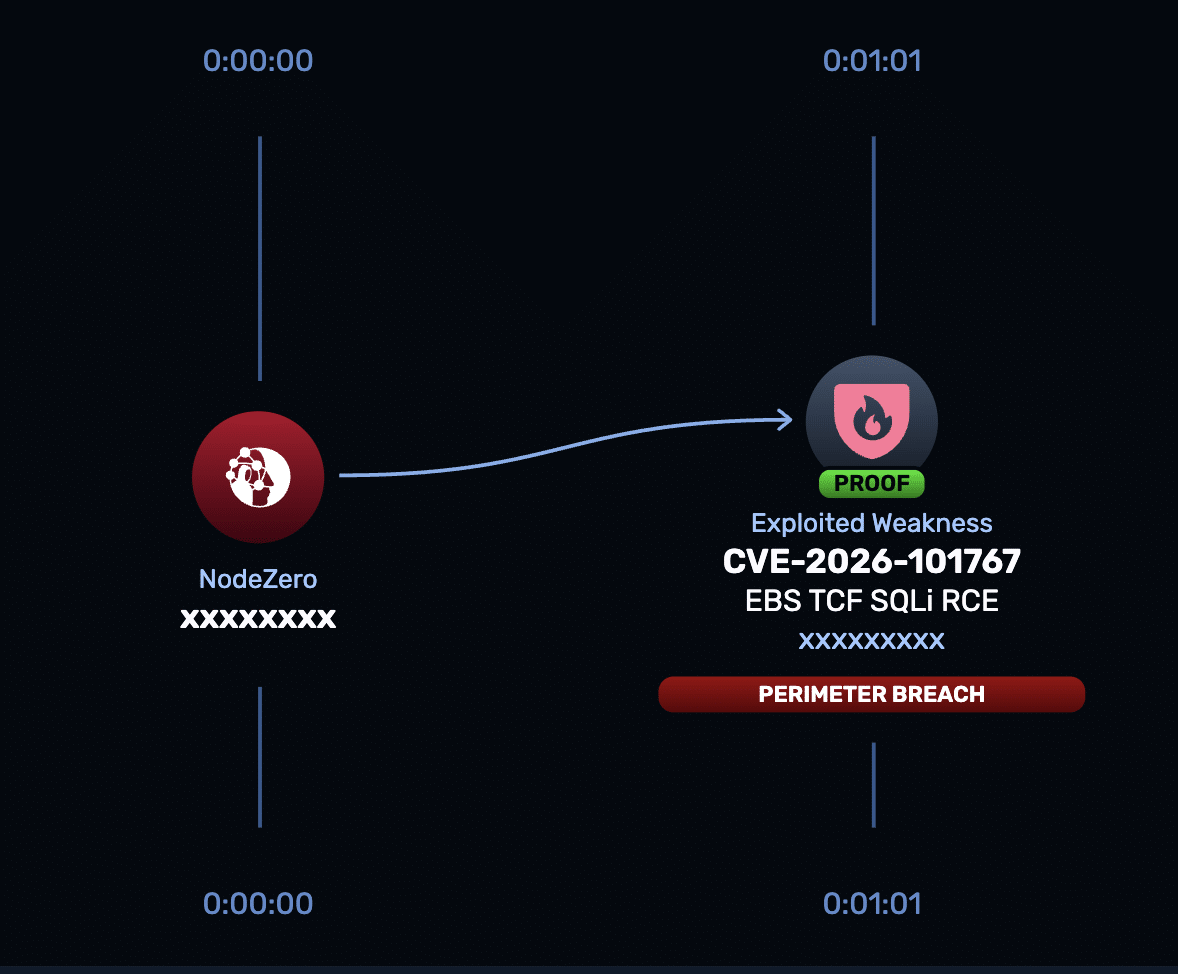 CVE-2026-101767 | Oracle E-Business Suite TCF SQL Injection and Remote Code Execution
CVE-2026-101767 is an unauthenticated SQL injection in the Oracle E-Business Suite Thin Client Framework servlet (/OA_HTML/AppsTCFServer, oracle.apps.fnd.tcf.SocketServer), CVSS 3.1 9.8. It runs SQL as the APPS user and chains to OS commands as the EBS account. Affects 12.2.3 to 12.2.15, fixed in the Oracle October 2026 CPU (20 October 2026). The page lists mitigations, IOCs and a timeline.
horizon3.aiadvisoryAdded 29 Oct 2026, published 20 Oct 2026🛡️ Security Threat Brief: Active Exploitation of PAN-OS CVE-2026-0257 (Updated Oct 20)
Unit 42 threat brief on active exploitation of CVE-2026-0257, a PAN-OS GlobalProtect authentication bypass added to CISA KEV on May 13, 2026. It lists IP addresses, host IDs and PoC-derived client values to hunt in GlobalProtect logs. The October 2026 updates cover Qilin and Inc ransomware operators, MFA bypass, pivots to vCenter and ESXi with offline VMDK credential dumping, and management interface exposure on ports 4443 and 3879.
unit42.paloaltonetworks.comadvisoryAdded 21 Oct 2026, published 20 Oct 2026🛡️ Security- Upcoming Critical PHP Security Release
The PHP security team announces an upcoming PHP security release that fixes two critical vulnerabilities, both rated CVSS v4.0 9.2. The release is scheduled for Wednesday, 21 October 2026 at 14:00 UTC. The team says it may release earlier if details become public or exploitation in the wild is seen. The notice gives no CVE IDs, affected versions or technical details.
 news-web.php.netadvisoryAdded 21 Oct 2026, published 20 Oct 2026🛡️ Security
 Frequently Asked Questions About PHP Remote Code Execution (PHP2Shell CVE-2026-109618 & CVE-2026-109619)
PHP2Shell is the name for CVE-2026-109618 and CVE-2026-109619, two unauthenticated remote code execution flaws in PHP, both CVSS v4.0 9.2. One stems from out-of-memory corruption during request setup, the other from stale global state reused by the next request. watchTowr reports exploitation since 21 October 2026, lists fixed releases (8.5.12, 8.4.27, 8.3.36, 8.2.35) and says PHP 5 is also affected. PHP says no configuration change fully mitigates.
watchtowr.comadvisoryAdded 30 Oct 2026, published 20 Oct 2026🛡️ Security Upcoming Critical PHP Security Release
The php.net 2026 news archive opens with the PHP security team's advance notice of a release scheduled for 21 October 2026 at 14:00 UTC. It fixes two critical vulnerabilities, both rated CVSS v4.0 9.2, and may ship earlier if details leak or exploitation appears. Details and fixed versions come with the release. The archive also lists 2026 security releases (8.2.34, 8.3.35, 8.4.26, 8.5.11), PHP 8.6 RC3 and conference announcements.
 php.netadvisoryAdded 21 Oct 2026, published 20 Oct 2026🛡️ Security
- lee1981 (@lee1981b) on X
CVE-2026-77932 affects DB-GPT through 0.8.2 (dbgpt-app). The /api/v1/chat/react-agent route accepts unauthenticated requests because get_user_from_headers returns an admin-role user, and the ReAct agent can reach unsandboxed Python and shell tools. Lasso reported root in the webserver container in a lab. The post gives CVSS 9.8 and 9.3, no verified fix (0.8.2 is still the latest release), no KEV match, no EPSS data, and a SOC hunting trail.
x.comadvisoryAdded 23 Oct 2026, published 20 Oct 2026🛡️ Security - lee1981 (@lee1981b) on X
CVE-2026-106931 is an OS command injection (CWE-78) in the statistics processing of EG Secure Solutions SiteGuard Server Edition, a host-based WAF. It can give root or SYSTEM command execution. The vendor and JVN confirm exploitation on 14 October 2026. The post lists fixed builds (Ver8.00 Update 5, Ver7.00 Update 6 on FreeBSD), the IIS exclusion, the workaround of disabling statistics, and a SOC trail starting with diagnostic preservation before patching.
x.comadvisoryAdded 21 Oct 2026, published 19 Oct 2026🛡️ Security - Dark Web Intelligence (@DailyDarkWeb) on X
Infinity Core is a set of six Linux kernel bugs published by researcher Hyunwoo Kim after the linux-distros embargo expired on 16 October 2026, with public exploit code. The bugs sit in timer, signal, memory, futex, scheduler and SLUB code. Five have local privilege escalation exploits, one is crash-only. CIQ says four affect Rocky Linux-based kernels. No sysctl or module workaround exists, so the fix is a patched kernel and a reboot.
x.comadvisoryAdded 19 Oct 2026, published 17 Oct 2026🛡️ Security - lee1981 (@lee1981b) on X
CyberForge CVE of the Day #080 covers CVE-2026-99999 ("PwnEscape"), a Linux kernel IPv4 checksum-completion flaw. Crafted checksum metadata can trigger a deferred write into an already-validated IPv4 header, which allows host memory disclosure from a guest or microVM over virtio-net and TAP. It gives upstream fixed branches (5.10.272 to 7.2.11), Amazon Linux, Red Hat and Ubuntu status, CVSS 9.3, EPSS 0.211% and a SOC investigation trail. No IOCs were verified.
x.comadvisoryAdded 19 Oct 2026, published 17 Oct 2026🛡️ Security - Microsoft Threat Intelligence (@MsftSecIntel) on X
ConnectWise Cloud Backup (formerly SkyKick Backup, AppId 506e08f9-6e9a-4da4-942b-a099a03644ae) had its multitenant OAuth app compromised, per Microsoft Threat Intelligence. On 15 October 2026 the actor authenticated broadly as the service principal from 144.172.64[.]128, likely using customer-granted permissions such as Directory.ReadWrite.All, then ran Graph API reconnaissance and tried to add credentials to the service principal as a backdoor. The post lists IOCs, Defender alerts and hunting advice.
x.comadvisoryAdded 20 Oct 2026, published 17 Oct 2026🛡️ Security  Frequently Asked Questions About the BeyondTrust Remote Support Arbitrary File Upload (CVE-2026-102764)
CVE-2026-102764 is an arbitrary file upload in BeyondTrust Remote Support (formerly Bomgar) caused by internal appliance components not validating message origin. Mandiant found it exploited as a zero-day in late August 2026. BeyondTrust disclosed it on 15 October 2026 and CISA added it to KEV on 16 October 2026. The FAQ covers the web shell, root escalation, credential theft, persistence, patching and compromise checks.
watchtowr.comadvisoryAdded 30 Oct 2026, published 16 Oct 2026🛡️ Security BeyondTrust Remote Support Arbitrary File Upload (CVE-2026-102764)
CVE-2026-102764 is a CVSS 9.8 unauthenticated arbitrary file upload flaw in BeyondTrust Remote Support (formerly Bomgar) and Privileged Remote Access. Internal messaging components do not verify message origin, so remote attackers can plant files the appliance would reject. BeyondTrust disclosed it on 15 October 2026 with patch BT26-05, and CISA added it to KEV on 16 October 2026. The page lists log files to review and hardening steps.
watchtowr.comadvisoryAdded 30 Oct 2026, published 16 Oct 2026🛡️ Security- S2W_DailyThreat (@S2W_DailyThreat) on X
S2W post on CVE-2026-97229, a CVSS 10.0 remote code execution flaw in the GitLab CE/EE CI/CD regex compiler, disclosed October 13, 2026. Insufficient regex validation plus an integer overflow during encoding conversion lets an attacker who can add CI/CD config use a malicious regex and a UTF-8 repository path to run commands as the git user. Affects self-managed 19.2 before 19.2.8, 19.3 before 19.3.5 and 19.4 before 19.4.2. Rapid7 published analysis and a public PoC exists, with no in-the-wild exploitation confirmed as of October 15. No workaround exists, so patch or restrict access to a management network or VPN.
x.comadvisoryAdded 17 Oct 2026, published 16 Oct 2026🛡️ Security - Dark Web Intelligence (@DailyDarkWeb) on X
Summary of Vercel's Oct 14, 2026 out-of-band Next.js security release fixing two critical unauthenticated RCEs: one in App Router apps with Cache Components where a "use cache" function returns multiple typed arrays (GHSA-673q-mjm6-r5xr, upstream React GHSA-xqc2-xf4c-x3h3, no workaround), and one in the Image Optimization API handling SVG on glibc Linux via a memory bug in a library used through sharp (CVE-2026-96889 / GHSA-2464-fhr4-w9xw, workaround sharp 0.35.5+). Also covers a high-severity Server Actions DoS (GHSA-p3m5-59mp-jv5r). Fixes ship in two supported Next.js LTS lines. No in-the-wild exploitation reported.
x.comadvisoryAdded 17 Oct 2026, published 16 Oct 2026🛡️ Security - lee1981 (@lee1981b) on X
Daily CVE digest on CVE-2026-76519, a CVSS 9.8 relative path traversal (CWE-23) in Cisco Secure Email Gateway's AMP File Reputation attachment processing. A crafted attachment gives unauthenticated arbitrary file writes and root command execution, and Cisco PSIRT reports active exploitation. The CVE is in CISA KEV. It lists the applicability conditions (File Reputation assigned to a policy and Content Scanner Tools earlier than 25.3.0.5525) and the fixes (scanner 25.3.0.5525, AsyncOS 15.5.5-014 and 16.5.0-780). It also covers evidence preservation, reading Cisco's System Security scan outcomes, mail/AMP log correlation, and deployment-specific recovery including cluster-key exposure.
x.comadvisoryAdded 18 Oct 2026, published 15 Oct 2026🛡️ Security  Critical GitLab RCE Lets Unauthenticated Attackers Execute Code on Servers (CVE-2026-97229)
Orca Security analysis of CVE-2026-97229, a CVSS 10.0 flaw in GitLab CE/EE. An integer overflow (CWE-190) in the CI/CD regular expression compiler gives memory corruption and code execution as the git user. It is triggered by a crafted regex in .gitlab-ci.yml combined with a UTF-8 repository path, with no authentication needed on instances that allow public project creation or self-registration. Lists affected branches (19.2 before 19.2.8, 19.3 before 19.3.5, 19.4 before 19.4.2), the absence of a workaround, interim mitigations, and a Rapid7 PoC against GitLab CE 19.4.1 with ASLR on. Notes a prior max-severity GitLab bug (CVE-2026-85706) was probed in the wild within hours and later added to CISA KEV.
orca.securityadvisoryPublished and added 14 Oct 2026🛡️ Security- ♫Why♥Not♪ (@Python_s_) on X
Alert summarizing XBOW's disclosure of a three-stage Chrome for Windows exploit chain: V8 Maglev memory corruption (CVE-2026-85045), Animated WebP decoder memory corruption (Chromium issue 548509153), then a Crashpad sandbox escape (CVE-2026-78952). Loading a crafted page was enough; no click or download needed. Human researchers working with GPT-5.6 Sol agents built it in six days, Google paid $250,000, all three bugs are fixed, and no in-the-wild exploitation is confirmed. It advises updating Chrome and restarting, and gives forensic triage pointers.
x.comadvisoryAdded 15 Oct 2026, published 14 Oct 2026🛡️ Security - Dark Web Intelligence (@DailyDarkWeb) on X
Summary of SAP's October 13, 2026 Security Patch Day (16 new notes, 4 GitHub advisories). It leads with CVE-2026-89111, a CVSS 10.0 OAuth2 SSRF in SAP Cloud SDK for Python before 0.45.2, where an attacker-controlled tenant_subdomain redirects token requests and exfiltrates client credentials. It also lists three other critical flaws: broken access control in NetWeaver Visual Composer, code injection in S/4HANA substitution/validation rules, and a missing authorization check in the Manufacturing Integration and Intelligence (XMII) Configuration Service. It notes that none are in CISA KEV and SAP reports no in-the-wild exploitation.
x.comadvisoryAdded 15 Oct 2026, published 13 Oct 2026🛡️ Security  Patch Tuesday - October 2026
Rapid7's analysis of Microsoft's October 2026 Patch Tuesday, which covers 1,413 vulnerabilities, 1,102 of them in Windows. It highlights the exploited Windows Shell Mark of the Web bypass (CVE-2026-96951) and the publicly disclosed .NET Framework WDAC bypass (CVE-2026-108398). It also covers five no-interaction Outlook preview-pane RCEs, the Edge advisories that list no CVEs, and end-of-support dates for Server 2012/2012 R2, Office 2021, Exchange 2016/2019 and Windows 11 24H2. The page text is truncated, so the later CVE tables are not seen.
 rapid7.comadvisoryPublished and added 13 Oct 2026🛡️ Security
 Microsoft Patch Tuesday for October 2026 — Snort rules and prominent vulnerabilities
Talos summarises Microsoft's October 2026 Patch Tuesday, which covers 1415 vulnerabilities, 85 of them critical (67 RCE). One bug is exploited in the wild: CVE-2026-96951, a Windows Shell security feature bypass. The post groups the CVEs by Microsoft's exploitability rating (more likely, less likely, unlikely) with CVSS and CWE for each, covering Windows, Office, Exchange, Hyper-V, DHCP, QUIC, Outlook and Azure. It also lists the Snort 2 and Snort 3 rule ID ranges that detect exploitation attempts.
blog.talosintelligence.comadvisoryPublished and added 13 Oct 2026🛡️ Security ZDI: The October 2026 Security Update Review
ZDI's October 2026 Security Update Review covers Adobe's 11 bulletins (174 CVEs) and Microsoft's record 1,415 CVEs. The only actively exploited bug is CVE-2026-96951, a Windows Shell Mark of the Web bypass. It also flags 59 wormable bugs, Microsoft's new "risk cohorts", and top-priority fixes in ColdFusion, Commerce, Experience Manager, SharePoint, SQL Server and Exchange.
 thezdi.comadvisoryAdded 27 Oct 2026, published 13 Oct 2026🛡️ Security
- ♫Why♥Not♪ (@Python_s_) on X
Alert thread on CVE-2026-35029 (CVSS v4.0 8.7) in LiteLLM Proxy, versions before 1.83.0. A low-privilege authenticated user can bypass admin authorization on /config/update, change runtime settings, read server files, take over admin credentials and run Python through remotely loaded modules (S3/GCS-hosted). Check Point Research published a full execution chain on October 13 after the April 2026 disclosure. The post lists hunting pointers (non-admin POSTs to /config/update, env-var changes, unexpected pass-through endpoints, cloud module loading) and advises upgrading to 1.83.9 or later and rotating credentials.
x.comadvisoryPublished and added 13 Oct 2026🛡️ Security  Ivanti Connect Secure zero-day exploited in the wild (CVE-2026-104935)
Rapid7 emergency-response analysis of CVE-2026-104935, a CVSS 8.6 authentication bypass by spoofing (CWE-290) in Ivanti Connect Secure that allows unauthenticated remote command execution. It was exploited as a zero-day against a limited number of customers, added to CISA KEV on disclosure day, and Volexity observed it chained with a still-unpatched privilege escalation flaw. Part of the fix shipped in 25.1.3.0 in July 2026, with backports to other supported versions pending. Rapid7 advises emergency patching outside normal cycles and hunting for compromise using Volexity's IOCs, since Ivanti has no reliable ones.
rapid7.comadvisoryPublished and added 13 Oct 2026🛡️ Security Frequently Asked Questions About the Ivanti Connect Secure Authentication Bypass by Spoofing (CVE-2026-104935)
CVE-2026-104935 is an authentication bypass by spoofing in Ivanti Connect Secure. A remote attacker can forge identity signals and run arbitrary commands without credentials. CISA added it to the KEV catalog on 13 October 2026. The FAQ lists affected branches by ISA hardware (25.1.1.1, 25.1.2.2, 22.8.X), fixed versions (25.1.1.2, 25.1.3.0/25.1.3.1, 22.8R2.5), no workaround and no reliable IOCs.
watchtowr.comadvisoryAdded 30 Oct 2026, published 13 Oct 2026🛡️ Security Ivanti Connect Secure Authentication Bypass by Spoofing (CVE-2026-104935)
CVE-2026-104935 is an authentication bypass by spoofing in Ivanti Connect Secure (CVSS 3.1 score 8.6) that lets a remote attacker run commands without logging in. CISA added it to KEV on 13 October 2026. The 22.8.X bridge release and 25.1.2.2 and earlier are affected, with fixes in 22.8R2.5, 25.1.1.2, 25.1.3.0 and 25.1.3.1. Ivanti says no reliable indicators of compromise exist yet.
watchtowr.comadvisoryAdded 30 Oct 2026, published 13 Oct 2026🛡️ Security- CVE-2026-97229: Critical Unauthenticated Remote Code Execution in GitLab
Rapid7 analysis of CVE-2026-97229, a CVSS 10.0 integer overflow (CWE-190) in the Onigmo regex compiler used by GitLab CE/EE's CI/CD regex handling. A crafted regex in a .gitlab-ci.yml passes validation as US-ASCII, then is recompiled for a UTF-8 repository path, producing invalid instructions that give code execution as the git user. Rapid7 reproduced it on GitLab CE 19.4.1 with ASLR (patched in 19.4.2); despite the vendor's "unauthenticated" rating, the attacker needs to commit a malicious config to a public project, which self-registration allows. No in-the-wild exploitation is confirmed, and Rapid7 recommends urgent upgrades.
rapid7.comadvisoryPublished and added 13 Oct 2026🛡️ Security - Major ICQ security hole (1998)
Rootshell Security Bulletin #22 (Aug 1998) reports an ICQ authentication flaw found by a Linux ICQ clone developer. The Mirabilis server stores 8-character passwords, and sending a password of 9 or more characters (e.g. "123456789") overflows the buffer and logs the client in as any UIN not already online. This gives full account takeover, including receiving offline messages. It is not spoofing, and it works with unofficial clients such as zicq, since the official client enforces the length limit client-side.
 opennet.ruadvisoryAdded 17 Oct 2026, published 13 Oct 2026🛡️ Security
- lee1981 (@lee1981b) on X
CyberForge "CVE of the Day #076" covers CVE-2026-97229, a CVSS 10.0 integer overflow (CWE-190) in GitLab CE/EE's CI/CD regular expression compiler. It can lead to conditional unauthenticated code execution on the GitLab server. It lists the affected trains (19.2 before 19.2.8, 19.3 before 19.3.5, 19.4 before 19.4.2) and the 19.3.4 vs 19.3.5 Ona-regression discrepancy. It also gives six SOC checks: scoping, log preservation (Workhorse/Rails/Sidekiq, correlation_id), server-effect hunting, request-to-process correlation, upgrade and running-state verification. It notes that exploit details are unverified, no KEV listing exists and EPSS data is unavailable.
x.comadvisoryAdded 15 Oct 2026, published 13 Oct 2026🛡️ Security - lee1981 (@lee1981b) on X
CyberForge's CVE of the Day #075 covers CVE-2026-108860, a critical (CVSS 9.1 v3.1 / 9.3 v4.0) authentication bypass in SciSharp BotSharp through 5.2.0. WebStarter ships a published default HMAC JWT signing secret (CWE-321), so anyone holding it can forge bearer tokens that impersonate known users, including administrators. The post sets out how to confirm the effective key and serving build, a six-step SOC investigation trail, and remediation by rotating the secret. No verified fixed release, KEV entry or EPSS data existed at cutoff, and the linked research is static-only.
x.comadvisoryAdded 13 Oct 2026, published 12 Oct 2026🛡️ Security  ♫Why♥Not♪ (@Python_s_) on X
Alert on CVE-2026-106610, a critical (CVSS 9.8) incorrect privilege assignment flaw in the miniOrange OTP Verification WordPress plugin, versions 5.5.7 and earlier. Unauthenticated remote attackers can gain elevated permissions, potentially administrator, with no user interaction. Fixed in 5.5.8; no in-the-wild exploitation or public PoC verified. It advises auditing unexpected admin accounts and role changes, and warns that Patchstack's mitigation blocks legitimate requests too.
x.comadvisoryPublished and added 11 Oct 2026🛡️ Security MCP spec 2026-07-28 changelog (stateless protocol, MRTR, Sampling/Roots deprecated)
Official changelog for the Model Context Protocol 2026-07-28 specification. Major changes: protocol-level sessions and the initialize handshake are removed to make MCP stateless, with version and capabilities carried in _meta on every request, plus a new server/discover RPC and subscriptions/listen replacing the GET stream and resource subscribe calls. It introduces Multi Round-Trip Requests (InputRequiredResult) in place of server-initiated sampling, roots and elicitation requests, moves tasks into an extension, and deprecates Roots, Sampling, Logging, HTTP+SSE and Dynamic Client Registration. Minor changes add cache hints (ttlMs/cacheScope), new Mcp-Method/Mcp-Name headers, OpenTelemetry trace context, RFC 9207 iss validation and an error-code allocation policy.
 modelcontextprotocol.ioadvisoryAdded 10 Oct 2026🧠 AI
- lee1981 (@lee1981b) on X
CyberForge CVE of the Day #074 analyses CVE-2026-85097, a CVSS 9.8 unauthenticated file upload to PHP execution flaw (CWE-434) in the Bricksforge WordPress plugin through 3.1.8.9. Wordfence names 3.1.8.10 as the fix, and a separate vendor 4.0.1 Pro Forms upload-security notice has no verified mapping to the CVE. It gives a defender workflow: scope versions, preserve edge/origin logs, inspect resulting files and PHP-FPM handling, and verify the patched version is serving. It also separates KEV (no match), EPSS (0.312%) and SSVC (exploitation none) from compromise evidence.
x.comadvisoryAdded 11 Oct 2026, published 10 Oct 2026🛡️ Security - CISA AA26-281A: Chinese Government-linked Actors Combine Automated and Hands-on Hacking Tools to Steal Data
Joint FBI/CISA/NSA and allied-agency advisory on China-linked actors enabled by Integrity Technology Group (overlapping with Flax Typhoon, Ethereal Panda, Red Juliett). It details their TTPs: open-source scanners and the MicroScan exploit-script app, an XSS credential-harvesting payload dropping live700_v1.exe, EBurst password spraying against Exchange/O365, SoftEther VPN persistence, DCSync via DC.exe, and email theft via the Curlc4.txt PHP bot and the office-cli utility. It also provides IOCs, MITRE ATT&CK mappings, CVEs, incident response steps, and mitigations.
cisa.govadvisoryAdded 9 Oct 2026🛡️ Security - MCP specification 2026-07-28 stable release
GitHub release announcing the stable 2026-07-28 revision of the Model Context Protocol specification, published from the modelcontextprotocol/modelcontextprotocol repository. The release page itself only points to the official MCP website for the spec and to a changelog for the detailed changes. It matters as the canonical version marker that MCP client, server and SDK implementers track for protocol changes.
github.comadvisoryAdded 9 Oct 2026🧠 AI - ♫Why♥Not♪ (@Python_s_) on X
Alert summarizing Socket Threat Research's disclosure that a malicious version of the Tensorlake npm SDK (an AI-agent infrastructure package) was published with a preinstall hook delivering Shai-Hulud/ChainDrop credential-stealing malware. The payload targets GitHub, npm, AWS, Kubernetes and Vault credentials, persists via a gh-token-monitor mechanism, and spreads through compromised publishing accounts. It lists IOCs (lib/setup.mjs, lib/Math_Symbol.js) and warns to remove the persistence before revoking stolen GitHub tokens, since revocation triggers a destructive routine. Socket detected the release about 11 minutes after publication.
x.comadvisoryAdded 11 Oct 2026, published 9 Oct 2026🛡️ Security - lee1981 (@lee1981b) on X
CyberForge's CVE of the Day #073 covers CVE-2026-102255, a critical (CVSS 10.0) pre-authentication SSRF / confused-deputy flaw (CWE-918, CWE-441) in the SonicWall SMA1000 Work Place interface, per advisory SNWLID-2026-0017. It lists affected platform hotfixes (12.4.3-03526 and older, 12.5.0-02952 and older), fixed floors (12.4.3-03670, 12.5.0-03082), no workaround, and the exploitation picture (no known exploitation, not in KEV, EPSS 0.477%, SSVC automatable). It gives a six-step SOC playbook covering appliance scoping, AMC log preservation, hunting appliance-originated internal requests, correlating receiving-service changes, patching, and verifying every node, and it separates exposure, a lead, confirmed compromise and telemetry gaps.
x.comadvisoryAdded 12 Oct 2026, published 9 Oct 2026🛡️ Security  Citrix Urges Immediate Patching of Critical NetScaler Vulnerability
Citrix disclosed CVE-2026-107406 (CVSS 9.5), a critical memory overflow in NetScaler ADC and NetScaler Gateway that can lead to remote code execution or denial of service when appliances are configured as a SAML SP or SAML IdP, also affecting Secure Private Access Hybrid deployments using NetScaler. Patches are available in versions 14.1-73.46, 13.1-64.29, and the corresponding FIPS/NDcPP builds; Citrix says it is not aware of exploitation yet but urges immediate upgrades. The bulletin follows two other recently exploited NetScaler RCE/DoS zero-days (CVE-2026-88771, CVE-2026-88772) used against government, financial, education, legal, and professional-services organizations, and a separate DoS zero-day (CVE-2026-88779).
 securityweek.comadvisoryPublished and added 9 Oct 2026🛡️ Security
















Showing 90 of 269
Show more