 Discovering vendor-specific vulnerabilities in Android | Oversecured Blog
Oversecured describes extending its Android scanner to system APIs and to Samsung's Android build, after comparing Google and Samsung framework JARs and about 400 system services. It explains AIDL service permission checks and new control-flow analyses. Examples include Samsung's unchecked semIsBackupEnabled(), a broadcast that reboots the device, and a LaunchAnyWhere in Settings. Samsung had fixed over 60 reported issues.
 oversecured.comwriteupAdded 29 Oct 2026🛡️ Security
- Abusing Linux fanotify for Anti-Forensics
Abusing Linux fanotify for anti-forensics: a privileged userspace process can use the fanotify API to deny other processes the right to open an otherwise normal file. Reads fail with EPERM even for root, while name, ownership, timestamps and permissions look ordinary, so a scanner that cannot open a file may report no detections without inspecting it. Defenders can find malicious fanotify groups and marks via /proc/<pid>/fdinfo, or acquire at the filesystem level instead of opening the pathname.
 dfir.chwriteupAdded 1 Nov 2026, published 24 Oct 2026🛡️ Security
 Claude reveals ECDSA curve origins
Anthropic's Frontier Red Team reports that Claude recovered how the NIST P-192/224/256/384/521 and ANSI X9.62 curve seeds were generated. They are outputs of the C library's lrand48 LCG seeded with 1997–98 Unix timestamps, not hashes of a passphrase. The method scanned for weak-PRNG signatures, then used LLL lattice reduction to recover the truncated LCG state and stepped it back to srand48 initialization. Claude also traced some base points to the FreeLIP/NTL random generator. Reproducible Python is included. The authors say this is not an attack and makes deliberate backdoors less plausible. The B-163 seed and the base points of P-224/256/384/521 and the binary curves remain unexplained.
 anthropic.comwriteupAdded 17 Oct 2026, published 16 Oct 2026🛡️ Security
- Claude reveals ECDSA curve origins
Anthropic's Frontier Red Team reports that Claude, given no hint, worked out how the NIST P-192/224/256/384/521 and ANSI X9.62 curve seeds were generated. They came from the C library's lrand48 LCG seeded with Unix timestamps from 1997–98, not from a hash of a phrase. Claude found this by scanning for weak-PRNG signatures and recovering the PRNG state with LLL lattice reduction. It also traced several prime-curve base points to the FreeLIP random generator. The post includes Python code that reproduces the seeds and base points. It says this is not an attack and makes backdoor claims less plausible. B-163 and the other base points remain unexplained.
anthropic.comwriteupAdded 17 Oct 2026, published 16 Oct 2026🧠 AI - Field Notes: EtherRAT Distributed Through a Legitimate Intune Workflow
DFIR case where a malicious MSI impersonating Advanced IP Scanner, sourced from a fake GitHub repo found via Bing, was imported by a customer into Microsoft Intune and deployed to four endpoints, running a Node.js-based EtherRAT chain. It traces the infections by correlating the MSI ProductCode, MDMAppInstaller/omadmclient process ancestry and Intune app inventory (Graph PowerShell query). It also covers renamed node.exe hash-hunting pitfalls, Ethereum RPC dead-drop C2 traffic, a screen-capture script and a second impersonating repo.
dfir.chwriteupAdded 14 Oct 2026, published 13 Oct 2026🛡️ Security  GhostAction Attack Escalates By Targeting GitHub Users
OpenSourceMalware's analysis of the latest GhostAction wave, where compromised GitHub accounts get malicious Actions workflows (security-audit.yml) injected across every writable repository, including an Oct 8 sweep of 346 repos via kitao and henrywoo. The new payload greps the checkout and full git history for credential patterns (AWS, Anthropic, OpenAI, GitHub PATs) and POSTs them over HTTP to 193.32.204.199/?c=monami. It also covers infrastructure reuse (phishing-heavy legacy IP, scanner activity), new watchlist domains my-github.com and my-gitlab.com, GitHub code-search hunting queries, a detection-confidence table, IOCs and incident response steps.
 opensourcemalware.comwriteupAdded 10 Oct 2026, published 9 Oct 2026🛡️ Security
 3 lessons from frontier AI vulnerability research
Microsoft Security's FORGE Lab shares results and lessons from four months of AI-agent-driven vulnerability research: 140 Windows CVEs (52 in September 2026's release), 155 internally validated reports across 23 open-source projects, and the first patch merged into the Linux kernel via the Linux Foundation's Akrites coordinated-disclosure initiative. Using their multi-model agentic scanning harness MDASH and GPT-5.5-based validation agents, the team measured automated PoC generation at an average $3.61/21.5 minutes per confirmed crash and local privilege-escalation AEG at $8.56/25.4 minutes, and argues the real bottleneck has shifted from finding bugs to validating and remediating them at matching speed. Specific disclosed CVEs include curl's CVE-2026-9545 and CVE-2026-13608, Node.js's CVE-2026-56848, and Linux kernel's CVE-2026-64563.
 microsoft.comwriteupPublished and added 7 Oct 2026🛡️ Security
 Living off The Browser: Running Popular Hacking Tools Inside Chrome
Hackers Arise walks through an installable Chrome Isolated Web App that packages nine popular Active Directory pentesting tools, including NetExec (NXC), SharpHound, LDAP-shell, Evil-WinRM, and Certipy, so they run natively inside a Chrome tab with multi-protocol network access, bypassing the need for Linux or WSL. The piece shows setup via Chrome flags and an IWA install URL, then a lab demo: port-scanning a target, using Evil-WinRM for remote access, enumerating DNS zones with ADIDNS, and running Certipy to flag an ESC1-vulnerable ADCS template for domain-admin escalation.
 hackers-arise.comwriteupAdded 7 Oct 2026, published 6 Oct 2026🛡️ Security
 https://bughunters.google.com/blog/pagebreak-real-world-findings?utm_source=tldrsec.com&utm_medium=newsletter&utm_campaign=tl-dr-sec-348-google-s-pagebreak-scanner-perplexity-s-agent-security-tool-defending-agentically
Google's Product Security team describes three high-severity bugs found by PageBreak, an internal LLM-agent scanner that validates findings by running payloads against live environments. The cases are cache poisoning on apis.google.com (an unkeyed `extra_path` injected into cached JS), XSS on admin.google.com where the agent bypassed the `sig` check by getting the authorize endpoint to sign a `javascript:` URI, and a UXSS in the Tag Assistant extension via a weak `onConnectExternal` origin check and nonce exfiltration. It shows what agentic, deterministically verified scanning can find in well-reviewed targets.
 bughunters.google.comwriteupAdded 2 Oct 2026, published 1 Oct 2026🛡️ Security
 Tracking CVE-2026-73570: unauthenticated command injection on internet-facing mail servers
Microsoft Threat Intelligence tracked in-the-wild exploitation of CVE-2026-73570, an unauthenticated OS command-injection vulnerability in Zimbra Collaboration Suite's SNMP notification path (swatchdog-to-snmptrap), triggerable via a crafted SMTP request when the optional zimbra-snmp package is enabled. The post documents pre-disclosure scanning, JSP webshell deployment, a novel pam_exec/zmmailboxdmgr privilege-escalation chain to root, systemd-based persistence (zimlog.service), theft of zimbraPreAuthKey/zimbraAuthTokenKey via zmlocalconfig and LDAP, lateral movement over Zimbra's SSH identity, a multi-stage Go-based remote-access agent (zimclient2 via zimdown2/agent2.sh), a dedicated mailbox-exfiltration implant, and an AzCopy-based exfiltration attempt, closing with Defender XDR KQL hunting queries and MITRE ATT&CK mapping.
microsoft.comwriteupAdded 1 Oct 2026, published 30 Sep 2026🛡️ Security OpenAI DevDay 2026 live blog
Simon Willison's live-blogged notes from OpenAI DevDay 2026 cover a raft of product launches (the "dots" personal agent, GPT-6.1 Sol, Ultrafast inference, ChatGPT Sites, GPT-Live), but the security-relevant core is the Codex Security session: OpenAI describes an internal "Defense Factory" security sprint that fixed 53 critical findings in a day, and launches a major Codex Security Cloud upgrade plus an open-source Codex Security CLI. The tool builds a security knowledge base, reads per-repo SECURITY.md threat-model files, runs a looping scanner, deduplicates findings (36% of their internal findings were duplicates), and can auto-generate patches/PRs validated by a "verify-fix" adversarial agent (1% rollback rate).
 simonwillison.netwriteupAdded 7 Oct 2026, published 29 Sep 2026🛡️ Security
 Top 10 attacks on Claude Code and what each one actually broke
Adversa AI catalogs ten distinct Claude Code attacks documented between September 2025 and September 2026: the Miasma supply-chain worm that hit 73 Microsoft repos via a SessionStart hook, TrustFall's unsandboxed MCP server execution on folder-trust, Check Point's CVE-2025-59536/CVE-2026-21852 pre-trust-dialog code execution and API key theft, Sentry-DSN-based "Agentjacking" prompt injection via fake bug reports, a 50-subcommand cap that silently disables deny rules, the SymJack symlink-to-config-hijack primitive working across six agent CLIs, Wiz's GhostApproval deceptive-approval-prompt finding (with CVE-2026-12958 at AWS and CVE-2026-50549 at Cursor but none at Anthropic), the Plugin4Shell SHA/branch-name collision bypassing plugin pinning, an academic MCP tool-poisoning paper achieving RCE on agent/LLM pairs, and SkillCloak's self-extracting-packer bypass of skill scanners. The piece argues almost none of these are model-behavior bugs - they are trust-boundary and consent failures in the surrounding tooling - and closes by pitching Adversa's own runtime agent security gateway as the fix.
 adversa.aiwriteupAdded 7 Oct 2026, published 23 Sep 2026🛡️ Security
 Autonomous AI Agents Hack Online Retailers for $25 a Company
Gambit Security recovered the staging server of a financially motivated actor running three open-source AI agent harnesses — Strix (vuln scanning), Cairn (autonomous exploitation), and Hermes (orchestration) — against hundreds of online retailers at a marginal cost of tens of dollars per target. The campaign exfiltrated 600,000+ credit card records via Magento database compromises, deployed checkout-page card skimmers on at least 19 confirmed and 100+ further sites, and in one case an agent's own cleanup routine dropped 180 database tables including victim backups. The report details full attack chains (SQLi to RCE to AWS Secrets Manager dump to card decryption), the AI harnesses' operating costs (~$25 mean per target on OpenRouter/opus-4.6/GLM/DeepSeek), and multiple real-world skimmer injection techniques.
 gambit.securitywriteupAdded 26 Sep 2026, published 22 Sep 2026🛡️ Security
 Shai-Hulud Rises From the Dead after 111 days
Aikido Security reports that the Shai-Hulud npm worm payload (SHA256 e37e3dd...e5b1a6), first seen during the @AntV compromise on May 19, 2026, resurfaced 111 days later on September 7 in four new packages (feishu-docx-mcp, bmc-i18n-extract-cli, blueai-cli, bmc-translate-utils) published by the same npm account within one hour. The payload passed npm's publish-time malware scanning — introduced in July 2026 to hold packages 5-15 minutes for automated checks — despite being an exact, previously fingerprinted hash match, exposing a gap between npm's scanning claims and actual detection coverage. The writeup includes full IOCs: C2 domain t.m-kosche.com, preinstall script running `bun run index.js`, persistence via .vscode/tasks.json and .claude/settings.json, and stolen-token-based republish behavior.
 aikido.devwriteupPublished and added 7 Sep 2026🛡️ Security
 Malicious Model Detection with MLTracer Syscalls
Binarly presents MLTracer, a pipeline that loads PyTorch/pickle model files in a Docker sandbox with strace and FakeNet-NG, flags suspicious syscalls, and labels behavior (reverse shell, downloader, exfiltration) with a SetFit classifier. Run over ~2.12M Hugging Face files, it found 218 confirmed malicious models. Hugging Face-hosted scanners (Protect AI, JFrog, ClamAV, VirusTotal) and ModelScan/SaferPickle missed 9–84% of them. The post also tabulates 21 static-scanner evasion techniques, two of them novel (CodeType/FunctionType indirect variant, EXT2 + copyreg.add_extension), and shows detection of a CVE-2025-32434 exploit that the HF scanners missed.
 binarly.iowriteupPublished and added 1 Sep 2026🛡️ Security
 Wiz Red Agent Finds Its Way Into Snowflake’s Internal Jira Through a Flaw in a GitHub Copilot–Assisted PR
Wiz's autonomous "Red Agent" discovered a GitHub Actions script-injection vulnerability in snowflakedb/snowflake-connector-net's jira_issue.yml workflow, introduced when a PR (co-authored by GitHub Copilot) replaced a safe env:/jq pattern with direct interpolation of the attacker-controlled issue title. GitHub Advanced Security scanned the same PR and workflow but failed to flag the injection; Red Agent autonomously crafted and self-corrected a payload after a bash syntax error, exfiltrated Jira OAuth credentials via an out-of-band callback, and used them to access Snowflake's internal Jira (engineering, security, and bug-bounty projects) — all without human intervention. Snowflake patched and rotated credentials the same day the flaw was reported via HackerOne.
 wiz.iowriteupAdded 3 Sep 2026, published 17 Aug 2026🛡️ Security
 DocsGPT Security Hardening Playbook
DocsGPT documents the security practices it adopted through GitHub's Secure Open Source Fund: a public STRIDE-based THREAT_MODEL.md, mitigations for its sandboxed AI code-execution feature (scrubbed env vars, NetworkPolicy blocking internal IPs and cloud-metadata to stop SSRF, off-by-default), a dependency-tree audit with SPDX SBOM export and Dependabot, and CI automation using custom CodeQL queries, Bandit, zizmor for GitHub Actions hardening, and secret scanning. It's a practical baseline playbook for maintainers dealing with high volumes of AI-authored PRs that can't all be manually reviewed.
 blog.docsgpt.cloudwriteupPublished and added 15 Aug 2026🛡️ Security
 MAJINAHANASHI RANSOMWARE: Yet Another Japanese Locker
Deep-dive intelligence report on Majinahanashi, a Japanese-themed ransomware group that emerged in August 2026, covering its Tor data-leak site (math-captcha gated, non-vanity domain), victimology (15 victims across Europe/Asia/Latin America, avoiding US/English-speaking countries), and technical analysis of its C/C++ locker sample. The malware uses AES-256 with RSA-wrapped per-file keys, appends the .MAJIN extension, deletes shadow copies/USN journals/event logs via vssadmin/bcdedit/fsutil, hijacks the desktop wallpaper, and uses WFP-based network filtering plus I/O priority manipulation to suppress EDR/backup traffic (targeting CrowdStrike, SentinelOne, Defender, Veeam, etc.). The article includes a full YARA detection rule, the ransom note text, BTC/qTOX/email contact IOCs, and threat-actor profiling ("THE DOCTOR CAME" persona) plus links to Mimikatz and Advanced IP Scanner usage.
 theravenfile.comwriteupAdded 3 Sep 2026, published 14 Aug 2026🛡️ Security
 S3 Clones in the Neoclouds
Wiz Research examines S3-compatible object storage offerings from Nebius, Vultr, Lambda Labs, Cloudflare R2, DigitalOcean, and Crusoe, showing how each deviates from AWS S3 security defaults. Findings include providers that expose access/secret keys via list APIs (Vultr), default ACLs that would be public but aren't enforced (Lambda Labs), lack of least-privilege key scoping (Vultr, Crusoe, Lambda Labs), weak or undocumented encryption-at-rest/TLS enforcement, unstructured access-key formats that evade GitHub/secret-scanner detection, and cross-tenant bucket namesquatting risk due to shared global namespaces.
wiz.iowriteupAdded 3 Sep 2026, published 31 Jul 2026🛡️ Security The risk hiding behind exposed MCP servers
Wiz Research scanned MCP servers across cloud environments and found roughly 1 in 6 environments expose at least one server to the Internet, most unauthenticated and still running the pre-auth 2024-11-05 protocol version. They demonstrate anonymous tool-catalog enumeration, real data returned from production databases/CRM/IAM backends, write/delete-capable tools, and confirmed SSRF against cloud instance metadata endpoints yielding temporary credentials, plus agents that can be talked into unsafe actions by reframing requests as "routine maintenance."
wiz.iowriteupAdded 3 Sep 2026, published 28 Jul 2026🛡️ Security Behind the GitLab RCE: A depthfirst Journey into the Ruby Ecosystem | depthfirst
depthfirst's Open Defense Initiative scanned about 40 Ruby gems with native C extensions and validated 105 vulnerabilities across 34 projects, which together have over 8.6 billion RubyGems downloads. The post walks through four cases: a Nokogiri 32/64-bit index truncation (CVE-2026-57235), an Oj garbage-collection use-after-free (CVE-2026-54902), a concurrent-ruby read/write lock bit overflow (CVE-2026-54905) and an sqlite3-ruby block lifetime bug (CVE-2026-54619). It also states that this work led to the earlier GitLab RCE chain through Oj.
 depthfirst.comwriteupAdded 29 Oct 2026, published 27 Jul 2026🛡️ Security
 Better generic secrets detection starts with finding non-secrets
Aikido Security engineers describe how they built a 'publishable credentials denylist' for their Betterleaks secret scanner to suppress known-public keys (like Stripe's publishable API key) that generic secret-detection regexes otherwise flag as false positives. They tested the change against 100GB of Common Crawl data, cutting false positives by 2.37% (27,886 fewer findings), and outline five edge-case categories (unique shape, no unique shape needing context, same shape as secret needing liveness checks, sensitive-if-misconfigured keys, and test/sandbox credentials) that complicate cleanly filtering public-by-design credentials from real secrets.
aikido.devwriteupAdded 3 Sep 2026, published 23 Jul 2026🛡️ Security MCP Configuration Poisoning: Owning Your Machine With Just A Text File
Explains how a malicious mcp.json in a repository, with attacker-controlled "command" and "args" fields, gives remote code execution when an IDE, scanner, CI/CD pipeline or agent loads it automatically. Walks through a PoC where running Snyk's Agent Scan (snyk-agent-scan) on a poisoned config executes arbitrary commands; Snyk fixed it in 0.5.0 after a duplicate report. Offers mitigations for tool builders (sandboxing, pattern blocking, human-in-the-loop prompts hardened against "Lies in the Loop" dialog forging) and for users (sandbox untrusted repos).
 checkmarx.comwriteupAdded 10 Sep 2026, published 23 Jul 2026🛡️ Security
 Socket: GitHub Actions Abuse Powers Distributed cPanel/WHM Exploitation Campaign
Socket researchers traced malicious dev versions of ten Packagist packages owned by developer dinushchathurya back to compromised GitHub repositories containing 55-62 malicious GitHub Actions workflow files each. The workflows execute on GitHub-hosted Ubuntu runners on every push, download an architecture-matched Linux payload from C2 server 43.228.157.68, and run an internet scanner (`ipscan --exploit CVE-2026-41940`) that exploits an authentication bypass in cPanel/WHM and harvests cloud, database, SSH, and source-control credentials, exfiltrating results via heartbeat/results HTTP endpoints and DNSHook callbacks. GitHub code search for the campaign's unique markers returned 6,100-16,000 matching workflow files across unrelated repositories, indicating the abuse extends far beyond the one compromised maintainer and effectively weaponizes GitHub Actions as free, disposable attack infrastructure.
 socket.devwriteupPublished and added 23 Jul 2026🛡️ Security
 Solving GitHub's Secure Code game with an AI red teaming agent
Adversa AI documents how their autonomous AI red-teaming agent (a LangGraph planner/attacker/scorer/escalator loop) solved all five levels of GitHub's Secure Code Game Season 4 "ProdBot" challenge, capturing the flag at each capability tier without using any jailbreak vocabulary. Each level maps to a distinct agentic failure: a denylist-based sandbox bypassed via bash variable expansion hiding ".." from a static validator, an indirect injection surface via web browsing, an over-permissioned MCP Cloud Backup tool whose real file access exceeded its advertised sandbox-only scope, a skill-writable memory store that doubled as the security policy store (enabling privilege escalation via a never-expiring ttl=0 entry), and a multi-agent confused deputy where a Research Agent's unsanitized web content was passed to a privileged Release Agent as pre-verified context, triggering an unauthorized file read. The piece argues all five share one root cause: an agent acting on state it cannot independently verify, and that continuous automated red-teaming is needed to catch the class as new agent capabilities ship.
adversa.aiwriteupAdded 7 Oct 2026, published 17 Jul 2026🛡️ Security Socket: Operation Muck and Load
Socket details "Operation Muck and Load," a campaign starting with a malicious Go module (github.com/kaleidora/dnsub-scanning-tool) that impersonates a DNS scanner but launches hidden PowerShell to fetch and decode a multi-layer, XOR-encrypted loader. The loader resolves encrypted payload locations from public dead drops (Pastebin, GitHub, YouTube, Instagram, Telegram, Google Docs), retrieves a password-protected .7z archive masquerading as Microsoft Photos, and deploys AsyncRAT/Quasar/Remcos-style RATs and Vidar infostealer. Pivoting from the module, Socket uncovered 222 GitHub repositories across 190 accounts using automated force-push workflows tied to a single email (ischhfd83@rambler.ru) to fake activity and credibility, some directly hosting Vidar, XMRig/BitMiner, and trojan loaders.
socket.devwriteupPublished and added 16 Jul 2026🛡️ Security- deep scan tuto
Build log/tutorial for "Deep Scan," a PoC that pairs a deterministic security-scanning engine (20+ SAST/SCA/DAST scanners normalized into one Finding model, plus an AI-free code-graph engine doing taint/reachability analysis) with an agentic remediation loop exposed via an MCP server and three Claude Code skills (/security-eval, /security-patch, /security). The agent triages thousands of raw findings down to a prioritized P0–P3 plan, groups fixes into reviewable branches, and proves each fix with a demonstration test that safely calls an inert owner-operated canary endpoint instead of firing a real exploit (e.g., rm -rf /). The author also covers scaling via Docker Compose/Kubernetes+gVisor and the risk of running untrusted dependency-resolution code during scans.
 blog.kubeek.comwriteupPublished and added 14 Jul 2026🛡️ Security
 jscrambler npm package publishes malicious preinstall binary
StepSecurity documents a supply-chain compromise of jscrambler, the official npm CLI for the Jscrambler Code Integrity API, starting with version 8.14.0. A malicious preinstall hook (later inlined into the main module to evade install-script scanners) drops a Rust-compiled, platform-specific native binary (ELF/PE32+/Mach-O) smuggled inside a fake dist/intro.js behind a custom magic header, containing an embedded SQLite/LevelDB parser and BIP39 wordlist consistent with a credential and crypto-wallet stealer. The Linux payload dynamically links libbpf and loads an in-memory eBPF program for kernel-level instrumentation, and all three platform binaries include anti-debugging checks; affected versions (8.14.0, 8.16.0, 8.17.0, 8.18.0, 8.20.0) were interleaved with clean releases, and C2 traffic was observed reaching Tor entry-node infrastructure and two raw IPs.
 stepsecurity.iowriteupAdded 3 Sep 2026, published 12 Jul 2026🛡️ Security
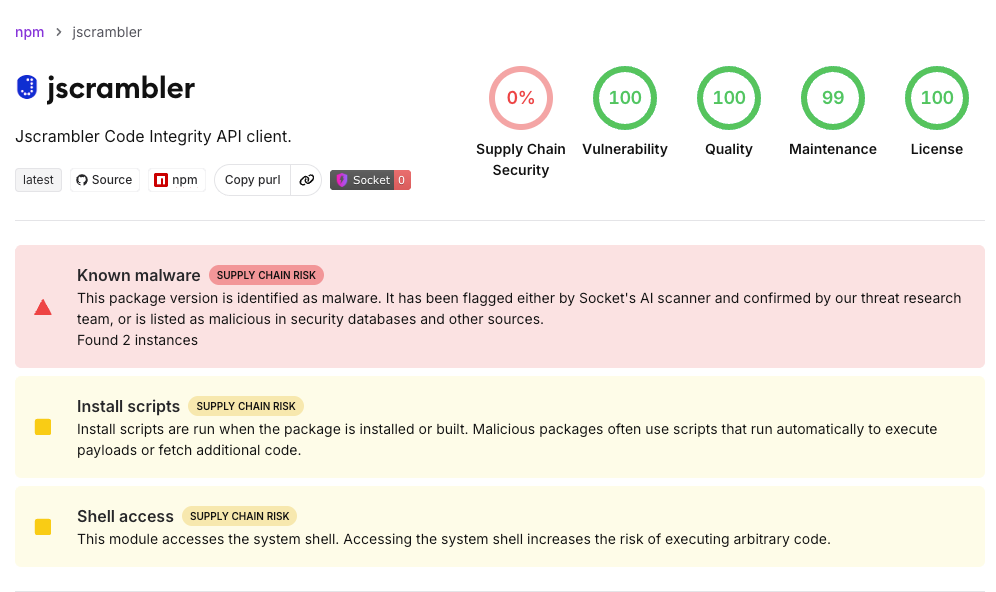 jscrambler npm Package Compromised in Supply Chain Attack
Socket's research team documents a supply chain compromise of the jscrambler npm package (v8.14.0+), where a stolen publishing credential was used to push malicious releases that drop platform-specific Rust-built infostealer binaries via a preinstall hook. The campaign evolved over the incident to evade scanners by moving the dropper from install scripts into a self-executing function inside index.js/CLI code (defeating --ignore-scripts), and the payload targets crypto wallets, cloud credentials (AWS/GCP/Azure), browser data, Discord/Slack/Telegram, and notably AI coding assistant configs (Claude Desktop, Cursor, Windsurf, VS Code) for MCP server credentials. Includes detailed RE of the ChaCha20-Poly1305 string-encryption scheme and full IOC hash list.
socket.devwriteupAdded 21 Sep 2026, published 11 Jul 2026🛡️ Security 10 Layers Deep: How StepSecurity Stops TeamPCP's Trivy Supply Chain Attack on GitHub Actions
StepSecurity walks through the TeamPCP-led compromise of aquasecurity/trivy-action (CVE-2026-33634, CVSS 9.4), where attackers force-pushed a credential-stealing payload into 76 of 77 version tags, plus the related Checkmarx KICS action compromise, both harvesting secrets from /proc/pid/mem of the GitHub Actions Runner.Worker process and exfiltrating to a typosquatted domain (scan.aquasecurtiy.org, 45.148.10.212). The post details the attack technique of 'imposter commits' (fork commits reachable by SHA but not on any branch) used to hide the malicious tags, and situates the incident alongside the same-window CanisterWorm npm worm and TeamPCP credential stealers in litellm and telnyx PyPI packages, then maps ten StepSecurity/Harden-Runner defense-in-depth controls (egress blocking, process lockdown, SHA-pinning PRs, imposter-commit scanning, global blocklist) to each stage of the kill chain.
stepsecurity.iowriteupAdded 3 Sep 2026, published 2 Jul 2026🛡️ Security
Showing 30 of 46
Show more