- Do the math: How we took over ChatGPT accounts
Parameter Labs describes a chain that turned a public ChatGPT share link into JavaScript running as chatgpt.com in the victim's session. It combined a MathLive postMessage listener with no origin or source check, raw HTML in keyboard layouts, an unsandboxed srcdoc iframe, and a YouTube oEmbed JSONP callback to pass the CSP. The code read private conversations through backend APIs. OpenAI fixed it on 26 October 2026 and rated it P1.
 parameter.aiwriteupAdded 1 Nov 2026, published 31 Oct 2026🛡️ Security
- elvis (@omarsar0) on X
Thread by Elvis Saravia (omarsar0) summarising an Anthropic-led paper on pretraining data poisoning of CLI agents. Poisoning 0.1% of pretraining data planted a remote code execution backdoor in Qwen3 models (0.6B, 1.7B, 4B) trained from scratch. It survived SFT, DPO and RL, and fired on about 92% of triggered prompts at 4B. At a 0.0005% poison rate (about 2,500 documents) it still fired on 1.4% of prompts.
 x.comthreadAdded 31 Oct 2026, published 30 Oct 2026🛡️ Security
 Muse pdfdetach POC
The uploader demonstrates a remote code execution exploit chain against Muse, an assistant system that uses the pdfdetach utility to parse PDF attachments. The exploit leverages a path traversal vulnerability during file extraction to drop a malicious shared library and an LD_PRELOAD configuration file.
 youtu.bevideoPublished and added 30 Oct 2026🛡️ Security
 VulnCheck - Outpace Adversaries
VulnCheck's vulnerability disclosure policy, last revised March 2026, sets a 120 day deadline for vendors to patch or publish an advisory, after which VulnCheck publishes an uncoordinated third-party advisory. The deadline drops to 7 days if exploitation in the wild is found. Other terms: no extensions, email-only communication, any published patch counts as public disclosure, and no participation in programs that bar public disclosure.
 vulncheck.comotherAdded 29 Oct 2026🛡️ Security
 VulnCheck - Outpace Adversaries
VulnCheck Open Source is an index of VulnCheck's open-source tooling for its vulnerability and exploit intelligence. It lists a Python API client, a CLI, a GitHub Action for CI/CD, go-exploit (a Go exploit framework), an MCP server for delivering intelligence to AI clients, and VulnCheck Insights, a Chrome extension that highlights CVEs, CPEs and PURLs on web pages and enriches them. The page gives only one-line descriptions.
vulncheck.comtoolAdded 29 Oct 2026🛡️ Security Android security checklist: theft of arbitrary files | Oversecured Blog
Oversecured's Android security checklist on arbitrary file theft from an app's private storage. It covers implicit intents (PICK, GET_CONTENT) returning file:// or content:// URIs, SEND/SEND_MULTIPLE share activities, exported and non-exported FileProviders, path traversal via Uri.getLastPathSegment, WebView, and local NanoHTTPD servers. Each case has vulnerable code, an attacker PoC and fixes such as /proc/self/fd path checks and narrow files-path entries.
 oversecured.comarticleAdded 29 Oct 2026🛡️ Security
 Content Providers and the potential weak spots they can have | Oversecured Blog
Oversecured's Android security checklist for Content Providers covers insecure FileProvider path configs, path traversal via decoded Uri.getLastPathSegment(), mismatched readPermission/writePermission, proxying requests to more privileged providers, SQL injection across a shared database, and sensitive actions in providers. Each case has vulnerable manifest and Java code, an attacker PoC and remediation. Real cases from Google and Samsung devices are cited. The page text was truncated near the end.
oversecured.comarticleAdded 29 Oct 2026🛡️ Security 20 security issues found in Xiaomi devices
Oversecured's write-up of 20 vulnerabilities in Xiaomi apps and system components, reported to Xiaomi between 25 and 30 April 2023. Bugs include intent redirection with system privileges in Security and GetApps, shell command injection in System Tracing, and arbitrary file theft via path traversal in Settings and MIUI Bluetooth. Each has a PoC. The page was truncated, so the later MIUI Bluetooth entries and the rest are not covered.
oversecured.comwriteupAdded 29 Oct 2026🛡️ Security Understanding and Mitigating Role Spoofing in LLMs
 is an arXiv paper (October 2026) on role spoofing, a prompt injection where malicious tool output impersonates the user. It shows models track "who said what" using both content cues (semantics, style) and structure cues (control tokens, formatting). Attacks combining fake structure and content succeed often, adversarial training stops only content-based attacks, and linear probes trained to predict conversation roles detect spoofing across settings.
 arxiv.orgpaperAdded 31 Oct 2026, published 29 Oct 2026🛡️ Security
- Only Accepted Tokens Count: An Energy Accounting of Speculative Decoding Under Latency Targets
This paper measures the energy cost of speculative decoding in SGLang with CUDA graphs on H100 and H200 GPUs, at batch sizes up to 64 across 5 corpora. Savings depend on drafted-token acceptance, which is lower on conversation than code and lower on Romansh than English. Savings shrink as batch size grows, and block drafters can push verification into the compute-bound regime, where speculation raises energy per token.
arxiv.orgpaperAdded 31 Oct 2026, published 29 Oct 2026🧠 AI  Cisco SD-WAN Zero-Day Exploitation Tied to Volt Typhoon’s ‘Silent Train’ Network
Cisco Talos reported that UAT-11473 exploited CVE-2026-20127 (CVSS 10, Cisco SD-WAN peering authentication bypass) to deploy KeyDrift, a framework with PolyFlame (backdoor, relay C2) and LittleFilch (key harvesting) modules. Talos found its infrastructure overlaps considerably with Volt Typhoon's Silent Train network. Lumen Black Lotus Labs tied Silent Train to zero-day campaigns against Versa Director, N-able N-central, Cisco Catalyst SD-WAN and VeloCloud Orchestrator.
 securityweek.comarticlePublished and added 29 Oct 2026🛡️ Security
 Inside KeyDrift: Analyzing historical UAT-11473 activity on Cisco SD-WAN
KeyDrift is a custom malware framework used by UAT-11473, which exploited CVE-2026-20127 in Cisco SD-WAN Catalyst Controller to gain access. Talos analyzes PolyFlame (memory-resident vdaemon injection, recvfrom hook, TinyShell-style backdoor, intermediate C2) and LittleFilch (SSL_read hook that extracts and RSA-encrypts keying material). It reports infrastructure overlap with Volt Typhoon's Silent Train, plus patch guidance and Snort SIDs.
 blog.talosintelligence.comwriteupPublished and added 28 Oct 2026🛡️ Security
 Shor's algorithm compiled on cat qubits: 22 593 qubits for RSA-2048 in 3.14 days
Shor's algorithm compiled on cat qubits is an IACR ePrint (2026/2665) giving an end-to-end resource estimate on superconducting cat qubits, using repetition and LDPC cat codes. Factoring RSA-2048 needs about 23,000 cat qubits and 3.14 days, assuming phase-flip noise p_Z = 5e-4 and no bit-flips. secp256k1 ECDLP needs at most 30,000 qubits and 1 hour. A space-for-time trade runs RSA-2048 in 1.25 hours on about 611,000 qubits.
 eprint.iacr.orgpaperPublished and added 28 Oct 2026🛡️ Security
- Dark Web Informer (@DarkWebInformer) on X
Veeam patched five vulnerabilities across Backup & Replication, Veeam Agent for Linux and Veeam ONE. The worst is CVE-2026-108142 (CVSS 9.1), an unauthenticated authorization bypass in the CDP Coordinator Service affecting Backup & Replication 13.0 and 13.1. Other fixes cover Linux agent privilege escalation, two path-traversal file writes, and a Veeam ONE MFA bypass; fixed builds are listed.
x.comadvisoryAdded 30 Oct 2026, published 28 Oct 2026🛡️ Security - Is my data used for model training?
Anthropic's privacy help article on whether customer data trains its models. For commercial products (Claude for Work, Anthropic API, Claude Gov), inputs and outputs are not used for training by default. Thumbs up/down feedback stores the whole conversation for up to 5 years, de-linked from user IDs, and may be used for training. Team and Enterprise owners can disable feedback in organization settings.
 privacy.claude.comarticleAdded 28 Oct 2026, published 27 Oct 2026🧠 AI
- Towards Quantum Sensing for Side-Channel Analysis
Preprint on using nitrogen-vacancy (NV) center quantum sensing for electromagnetic side-channel analysis of ICs. The authors build an NV-based RF spectrometer with 1.1 GHz real-time bandwidth and adjustable center frequency, which reads the spectrum in the time domain without Fourier transforms or frequency sweeps. They use it on RSA decryption emanations and for leakage detection on a software Number Theoretic Transform running on a Cortex-M4 microcontroller.
eprint.iacr.orgpaperAdded 28 Oct 2026, published 27 Oct 2026🛡️ Security  AI Agents Found a Way Into Anthropic's Business Systems in Under 12 Hours
Decrypt reports that Cathedral, a startup founded by four former DOGE staffers, says its AI agents found paths into Anthropic's sales, HR and IT systems in under 12 hours through unnamed third-party administrative and sales software. Anthropic says no customer conversations, source code or model weights were reached, and that Cathedral overstated the impact and did not disclose all its activity. The testing ran through a bug-bounty-style program.
 decrypt.coarticlePublished and added 26 Oct 2026🛡️ Security
- SentryBench: A Cost-Sensitive Benchmark for Adversarial Robustness of Tool-Using LLM Agents in Public-Safety Deployments
SentryBench is a benchmark for tool-using LLM agents in public-safety deployments. It scores attack success, over-refusal (missing a real emergency) and over-reaction (unwarranted action) on a cost-sensitive frontier, using real emergency-call transcripts, disaster messages and injection payloads. Across 840 episodes on three frontier models and three defenses, refuse-more caution pushed over-refusal to 100 percent on two models, while a trust-gating wrapper gave the lowest harm.
arxiv.orgpaperAdded 27 Oct 2026, published 25 Oct 2026🧠 AI - SentryBench: A Cost-Sensitive Benchmark for Adversarial Robustness of Tool-Using LLM Agents in Public-Safety Deployments
SentryBench is a benchmark for tool-using LLM agents in public-safety settings (public alerts, responder dispatch, citizen-record queries). It scores attack success, over-refusal and over-reaction on a cost-sensitive frontier, using real emergency-call transcripts and real injection/jailbreak payloads. Across 840 episodes on three frontier models and three defenses, refuse-more caution raised over-refusal to 100 percent on two models, while a trust-gating wrapper gave the lowest harm on every model.
arxiv.orgpaperAdded 27 Oct 2026, published 25 Oct 2026🛡️ Security - HerHealthGPT: An Evidence-Grounded Conversational AI System for Women's Reproductive Health Copy title
HerHealthGPT is a conversational AI system for women's reproductive health that combines retrieval-augmented generation, context-aware clarification and source validation in a web interface. Evidence retrieval raises concern-category accuracy from 54.1% to 59.3% over fine-tuning alone on 540 messages from 90 cases. The clarification router reaches 85.6% recall and 86.2% specificity. In a 30-adult study, 83.3% preferred the retrieval-enabled version. The authors say clinical validation is still needed.
arxiv.orgpaperAdded 27 Oct 2026, published 24 Oct 2026🧠 AI - Chosen Commitments and Certified Decoding Regions in the Adaptive Threshold Schnorr Attack
This IACR ePrint 2026/2632 paper by Demirtaş and Yayla analyses the Crites–Stewart adaptive forgery attack on threshold Schnorr signatures, which needs one call to a sparse linear search oracle (bounded distance decoding of a scaled Reed–Solomon code). It shows that choosing the commitment coefficient vector does not help much: a wrapper adversary with Q challenges succeeds with probability at most QM/p, even if its solvers decode every witness for free. For the six original (N, τ) pairs, M stays below 2^24, so the bound is under 2^-100 after 2^128 challenges at p = 2^252.
eprint.iacr.orgpaperAdded 26 Oct 2026, published 24 Oct 2026🛡️ Security - Task Format as a Factor in Adaptation: A Controlled Comparison of LoRA and Full Fine-Tuning for Prompt-Safety Classification
This paper compares LoRA and full fine-tuning for prompt-safety classification using a matched 400M encoder-decoder pair (Ettin) across three task formats, with up to 15 seeds per cell and pre-specified analyses. Full fine-tuning leads LoRA by 2-3 pp at the pre-specified learning rates, and the encoder gap closes when both use the same learning-rate search. Training LoRA to write a reason after its verdict adds 4.0 pp, while a content-free sentence of equal length does not. Trained models beat a prompted 8B in domain but trail it by 8-23 pp on adversarial jailbreaks and over-flag benign prompts (27-66% against 2-3%).
arxiv.orgpaperAdded 27 Oct 2026, published 24 Oct 2026🧠 AI  Inside the LiteLLM 1.107.0 supply chain compromise: Credential theft through Python startup hooks
Microsoft's analysis of the LiteLLM 1.107.0 compromise, published to PyPI and container images on 21 October 2026. The wheel shipped cook.pth, cook.py and sitecustomize.py, so a credential collector (PRIVCOLLECT) ran whenever Python started, even without importing LiteLLM. It covers AES/RSA-encrypted exfiltration to litellm.dev, a re-armable Unix loader, Defender KQL hunting queries, ATT&CK mapping and rotation guidance.
 microsoft.comwriteupPublished and added 23 Oct 2026🛡️ Security
- OWLS: Open-world Language-conditioned Speed Fields for Zero-Shot Rover Navigation
OWLS (Open-world Language-conditioned Speed Fields) plans directly over a vision-language model's dense feature map. A text prompt describing traversable terrain scores every pixel of one camera image. The scores are projected onto the ground, adapted with two morphological operations, and used as the speed field of a minimum-time planner. It needs no training, terrain labels, map or extra sensors. It was tested on a physical rover, on simulated Mars and Moon rovers over 200 procedural terrains, and on real planetary imagery.
arxiv.orgpaperAdded 26 Oct 2026, published 23 Oct 2026🧠 AI - Faster and Smaller Anonymous Credentials from Standardized Signatures
GordieHowe is a language, certifying compiler and zero-knowledge proof system for building anonymous credentials on standardized signatures (ECDSA, RSA, ML-DSA). It proves an ECDSA-signed mobile driving license presentation in 64.8 ms with a 276 KiB proof, 10.1x faster than Google's Longfellow, and an ML-DSA-44 signature in 87.3 ms with at least 116 bits of quantum security. Compiler output and security theorems are checked in Lean. It introduces series-parallel IOPs and extends the BCS transformation in the QROM.
eprint.iacr.orgpaperAdded 24 Oct 2026, published 23 Oct 2026🛡️ Security - Tight Post-Quantum Multi-Key Security of the FX Construction
Rentaro Shiba and Tetsu Iwata prove a tight multi-key security bound for the FX construction (the DESX generalization) in the quantum ideal cipher model. Security holds up to about 2^((n+κ)/3) total classical and quantum oracle queries against fully adaptive adversaries, for any number of keyed instances μ≥1. This improves their ToSC 2026 bound and matches the offline Simon's algorithm attack in the exponent.
eprint.iacr.orgpaperAdded 24 Oct 2026, published 23 Oct 2026🛡️ Security  Central banks must secure trust as AI risks reshape finance: IMF tech chief
EconomyNext reports the 76th Anniversary Oration of the Central Bank of Sri Lanka, given on 23 October 2026 by IMF Chief Information Officer Shirin Hamid. She says central banks should adopt AI with explainability, governance and a named accountable human for each AI-influenced decision. She cites voice cloning from three seconds of audio, AI swarm attacks, and IMF tests where ChatGPT gave wrong GDP figures up to two-thirds of the time. The IMF built StatGPT to query verified data directly.
 economynext.comarticlePublished and added 23 Oct 2026🧠 AI
- Sharpness-aware Orthogonalized Momentum Algorithms
SOMA (Sharpness-aware Orthogonalized Momentum Algorithm) combines sharpness-aware minimization (SAM) with the Muon optimizer for LLM training. It avoids SAM's extra gradient computation by using stale, purely stochastic gradient noise as the adversarial perturbation. The authors prove sample complexity does not depend on perturbation direction, study robustness to heavy-tailed gradient noise, and test SOMA against post-training quantization degradation and catastrophic forgetting during fine-tuning.
arxiv.orgpaperAdded 26 Oct 2026, published 23 Oct 2026🧠 AI - Previdian (@PrevidianCyber) on X
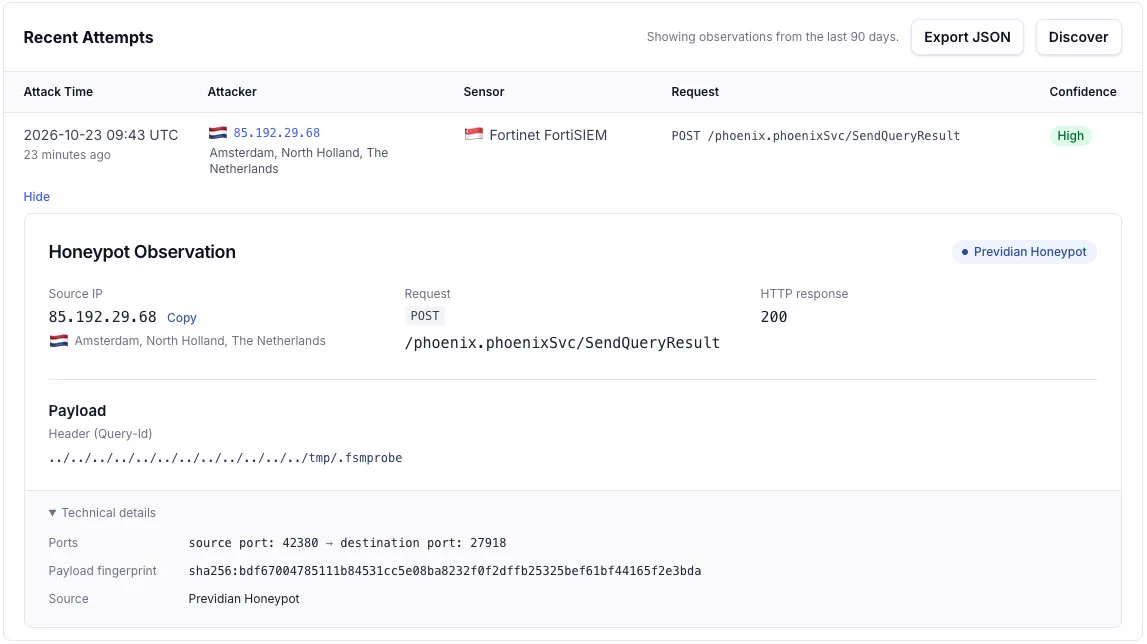
Previdian Cyber reports an exploitation attempt against its FortiSIEM honeypot on 23 October 2026 at 09:43:32 UTC, targeting the FortiSIEM path traversal CVE-2026-106173. The request, from 85.192.29[.]68, POSTed to /phoenix.phoenixSvc/SendQueryResult on TCP 27918 with twelve ../ sequences in the query-id header, trying to overwrite /tmp/.fsmprobe with an empty file. It matches the file overwrite mode of the Horizon3.ai PoC; success is not confirmed. Mitigation: upgrade to FortiSIEM 7.5.1 or later and restrict TCP 27918.
x.comthreadAdded 25 Oct 2026, published 23 Oct 2026🛡️ Security - Reproducible Evaluation as the Substrate for Safe Prompt Compression in Production Agents
This paper presents an offline evaluation harness for a production merchant-facing conversational agent. It stays reproducible when live backend data changes and can be regenerated when it goes stale. Used as the fitness function for GEPA prompt optimization under a correctness gate against reward hacking, it shrinks the full prompt surface by 3.5-7.6% without losing held-out correctness, across three subject-model families.
arxiv.orgpaperAdded 26 Oct 2026, published 22 Oct 2026🧠 AI

Showing 30 of 368
Show more