Skip to content

77 results for “eCos”

What you seeeverything
“eCos”
interconnects.aiarticle🧠 AI

Was I wrong about open models & cyber risks?

Interconnects post in which Nathan Lambert revisits his claim that an open-weight Claude Mythos would have been survivable. He argues GLM-5.3 already crosses the capability threshold with little visible societal change, and quotes Rob Wiblin, Anthropic and Zvi Mowshowitz as examples of exaggerated warnings. He cites Epoch AI's Firefox exploit built with GLM-5.3, and treats the recent vulnerability surge as an ecosystem trend driven by AI capability and diffusion, not open versus closed models.

FirefoxGLM
Claude MythosGLM-5.3Anthropic+13

ai-policy, ai-safety, models· Published and added 30 Oct 2026

huggingface.coarticle🧠 AI

Welcome Le Chonk: Mistral Large 4 on Hugging Face

Mistral Large 4 (Le Chonk) is a multimodal, multilingual Mixture-of-Experts model with about 1T total and 49B active parameters and a 1M-token context, released under the Mistral Ecosystem Open-Weight License. The post covers its MLA and DeepSeek Sparse Attention architecture, a 1.6B Pixtral encoder, and benchmarks including 82% on the Artificial Analysis Cyber Index and 93% on Cybench. It gives run recipes for transformers, vLLM, llama.cpp, TRL fine-tuning and Inference Endpoints.

Mixture of ExpertsTransformersvLLM+11
Mistral Large 4MistralArtificial Analysis+15

models, inference, evals· Published and added 29 Oct 2026
arxiv.orgpaper🛡️ Security

The Policies of Programming Language Ecosystems: A "Qualitative" Analysis

The Policies of Programming Language Ecosystems is an October 2026 arXiv paper (cs.SE) that compares the policies of eight programming language ecosystems, including CRAN for R, across 38 policy categories. Three authors coded the policies with moderate agreement. Malware, intellectual property and content removal are covered everywhere, while package size limits, metric manipulation, typosquatting and binary uploads diverge.

CRAN
typosquatting

Supply Chain, GRC· Added 28 Oct 2026, published 25 Oct 2026

enisa.europa.euadvisory🛡️ Security

ENISA Technical Advisory for Software Bill of Materials

ENISA Technical Advisory for Software Bill of Materials is practical guidance on SBOM adoption for organizations, especially micro, small and medium enterprises and open-source stewards. It sets out an SBOM implementation architecture and data flows across a defined lifecycle, an indicative SBOM threat model with targeted risks, and measures for the SBOM ecosystem. It aligns with the ENISA Secure by Design and Default Playbook and supports Cyber Resilience Act compliance.

SBOM
ENISAEU Cyber Resilience ActENISA Secure by Design and Default Playbook

Supply Chain, GRC· Added 23 Oct 2026
quentinkaiser.bewriteup🛡️ Security

One parser, two bugs, many routers: Exploiting Broadcom WiFi across eCos, Linux

Long-form write-up of a Hexacon 2026 talk on a WPS EAP reassembly overflow in Broadcom's proprietary 802.11 stack, present since 2010 and incompletely patched in 2018. It is remotely triggerable over WiFi without the network key. It gives information disclosure and code execution on eCos (BCM3380, BCM3383, BCM33834) and Linux (BCM3390, BCM65xx, BCM68xx) platforms. Exploited on Belgian ISP routers from Proximus, VOO and Orange. Includes a 90-day disclosure timeline, and Broadcom refused to assign a CVE.

BroadcomeCosLinux+2
HexaconWPS EAP reassembly overflowforever day+17

Hardware & RF, Offensive Security, Blue Team & Detection· Added 19 Oct 2026, published 16 Oct 2026

x.comthread🛡️ Security

Trail of Bits (@trailofbits) on X

Trail of Bits post announcing research that tested 25 package managers against a simulated malicious repository serving swapped code for the same package and version. Without a lockfile only Go and vcpkg verified every download; with a lockfile fewer than half did. This undercuts the assumption that lockfiles make dependencies immutable and shows hash/integrity verification gaps across ecosystems.

Govcpkg
Trail of Bits

Supply Chain· Added 18 Oct 2026, published 16 Oct 2026

microsoft.comarticle🛡️ Security

The hidden network: Inside the phishing infrastructure ecosystem powering global cybercrime

Microsoft Threat Intelligence maps a Chinese-language cybercrime ecosystem: the YAM Store (Storm-3119), an initial access broker that hijacks Microsoft 365/Azure Education tenants and resells accounts, licenses and SharePoint/OneDrive storage, and the Storm-2990 phishing kits (CoGUI, Haozi, Iron Man System) sold via Telegram. It details the five-stage broker pipeline (app-only client-secret abuse, PnP Management Shell service principal, Graph permissions, Cloudflare DNS management), kit evasion features (geofencing, fake CAPTCHA, WebSocket/Telegram live interaction, 2,335+ templates), downstream device-code phishing and card fraud, and lists mitigations such as passkeys, phishing-resistant MFA and Conditional Access. Microsoft's DCU facilitated a disruption with law enforcement; kits sent over one billion messages since January 2026.

Microsoft 365AzureMicrosoft Entra ID+3
Storm-3119Storm-2990YAM Store+10

Threat Intel, Identity & Access· Published and added 14 Oct 2026

endorlabs.comarticle🛡️ Security

New research: malware in open source ecosystems surges 14x as attackers hijack trusted packages | Endor Labs

Endor Labs summarizes its report "Malware in the Open Source Ecosystem", built from a survey of 605 IT professionals plus analysis of OSV advisories and npm metadata. Over 90% of all OSS malware advisories were filed in 2025, and npm account-takeover advisories rose about 12x (930 of 1,011 ever recorded), often hitting heavily downloaded packages. It also covers the TeamPCP campaign across GitHub Actions, Docker Hub, npm, OpenVSX and PyPI, the axios compromise, and survey findings: only 21% enforce cooldown periods, 51% found malicious packages in 2025, and ownership of the problem is fragmented.

npmOSVEndor Labs+3
Shai-HuludTeamPCPDPRK+2

Supply Chain, Threat Intel· Published and added 12 Oct 2026

coindesk.comarticle🛡️ Security

UK slaps sanctions on three crypto exchanges over alleged Russia links

The UK Foreign Office sanctioned crypto exchanges Cryptomus, Heleket and Certa Payments (all operated by Canadian-registered Xeltox Enterprises) plus Kyrgyzstan's TokenSpot and payment processors Processing KG (VexPay) and Tsunami Payments, as part of 38 new designations targeting Russia sanctions-evasion networks. Two of the sanctioned firms allegedly processed transactions tied to A7, a Kremlin-backed network whose ruble-pegged A7A5 stablecoin is used to bypass financial restrictions and which claims to have moved over $90 billion. The action follows earlier UK sanctions on Garantex and Grinex and complements US and EU actions against the same A7/A7A5 ecosystem.

A7A7A5Garantex+12

Blockchain, Threat Intel· Published and added 9 Oct 2026
opensourcemalware.comtalk🛡️ Security

The OpenSourceMalware Show #24

Weekly OpenSourceMalware podcast episode discussing three fresh supply-chain attacks: the Tensorlake AI-agent SDK compromised via a preinstall-triggered Mini Shai-Hulud-derived worm (setup.mjs + math_symbol.js, run via Bun) that steals credentials; a Contagious Interview-style attack where a cloned GitHub repo drops a malicious .npmrc pointing npm install at a Chinese mirror (npmmirror.com) to resolve a hidden package; and 42 malicious RubyGems published by "Ghost Dev" that typosquat/brandjack crypto tooling, sleep 20–40 minutes via extconf.rb to evade detection, then either open a reverse shell or deploy a Python-based "Wallet Guard" crypto-theft kit targeting TronLink, MetaMask, Phantom, Binance, Coinbase, Trust Wallet, Exodus, and Electrum. The hosts also discuss multi-package "combined payload" evasion and how AI-driven slopsquatting is making cross-ecosystem typosquats more effective.

npmRubyGemsBun+2
Mini Shai-HuludContagious InterviewDPRK+16

Supply Chain, Malware & RE· Published and added 9 Oct 2026

microsoft.comarticle🛡️ Security

Post-quantum authentication: Why organizations should start testing certificate ecosystems now

Microsoft Security Blog post arguing that post-quantum cryptography planning must extend beyond encrypted-data confidentiality to authentication and certificate ecosystems, since larger PQC certificate chains and new algorithms like ML-DSA-87 can break PKI workflows, HSMs, and legacy infrastructure. It details Microsoft's PQC TLS Pilot Program, launched August 27, 2026, which lets approved certificate authorities (ComSign, DigiCert, HARICA, IdenTrust, Sectigo, Shanghai Electronic Certification Authority, SSL.com) test ML-DSA-87 certificate issuance under the Microsoft Trusted Root Program, plus Windows 11 builds (KB5101681, KB5101684) that support evaluating ML-DSA certificates via Schannel in non-production environments. It lays out a six-step readiness plan: inventory certificate dependencies, map trust relationships, assess vendor roadmaps, identify long-lived infrastructure, build test environments, and plan a multi-year migration.

WindowsSchannelTLS
ML-DSAML-DSA-87PQC TLS Pilot Program+8

Identity & Access, GRC· Published and added 8 Oct 2026

orca.securityadvisory🛡️ Security

Critical Atlassian Path Traversal Exposes Sensitive Files Across 8 Products

Orca Security details CVE-2026-21589 (CVSS 9.3), a critical unauthenticated path traversal flaw affecting all versions of eight Atlassian Data Center and Server products: Bitbucket, Confluence, Jira Software, Jira Service Management, Bamboo, Crowd, Crucible, and Fisheye. Insufficient path validation lets remote attackers read arbitrary files within the web application root without authentication, and in Crowd SSO deployments this can expose plaintext credentials usable to create administrative accounts and take over the entire Atlassian ecosystem. The advisory lists fixed versions for each product and recommends WAF rules and log review for organizations unable to patch immediately.

JiraConfluenceBitbucket+3
CVE-2026-21589path traversal

AppSec, Identity & Access· Published and added 7 Oct 2026

vulnerablemcp.inforepo🛡️ Security

The Vulnerable MCP Project — MCP vulnerability database

The Vulnerable MCP Project is a curated, continuously growing database of security vulnerabilities and attack techniques specific to the Model Context Protocol ecosystem. Entries cover concrete CVEs (e.g. CVE-2025-68143/68144/68145 in Anthropic's mcp-server-git), transport-layer SDK flaws (cross-client response leakage, missing DNS rebinding protection in the official TypeScript/Python SDKs), unauthenticated/0.0.0.0-bound servers enabling RCE (MCPJam inspector, MCP Inspector, Grafana MCP), command/path injection in dozens of third-party servers (gemini-mcp-tool, mcp-server-kubernetes, Framelink Figma MCP, Zen MCP, filesystem-mcp), SSRF chains reaching cloud metadata (MarkItDown MCP, mcp-fetch-server), and a large set of AI-specific attacks: tool poisoning, trigger-phrase data exfiltration, prompt injection via GitHub issues, Jira and Google Docs, rug-pull tool mutation, and cross-server tool-name collisions. It functions as the de facto vulnerability registry for the MCP ecosystem, useful for tracking disclosed issues before patching or adopting third-party MCP servers.

Model Context ProtocolCursorKubernetes+3
CVE-2025-68143CVE-2025-68144CVE-2025-68145+3

AI Security, AppSec· Added 6 Oct 2026

arxiv.orgpaper🧠 AI

CheckerBench: Can Long-Horizon Agents Synthesize Static-Analysis Checkers?

CheckerBench is an executable benchmark of 300 tasks drawn from 297 CVEs across 167 repositories, 85 CWEs, and five language ecosystems, testing whether long-horizon coding agents can synthesize working static-analysis checkers from a defect specification through repeated compile-and-analyze feedback loops. Its companion framework CheckerLab independently rebuilds submitted checkers and scores vulnerable-fixed diagnostic contrast, patch localization, false positives, and tool use; across 21 model-harness configurations mean Pass@1 is 32.30 percent and the best reaches 45.33 percent, showing reliable checker synthesis remains hard for current coding agents.

CheckerBenchCheckerLab

evals· Added 8 Oct 2026, published 6 Oct 2026

arxiv.orgpaper🛡️ Security

CheckerBench: Can Long-Horizon Agents Synthesize Static-Analysis Checkers?

CheckerBench is an executable benchmark of 300 tasks derived from 297 CVEs across 167 repositories, 85 CWEs, and five language ecosystems, testing whether long-horizon coding agents can synthesize working static-analysis checkers from a defect specification through repeated compilation and analysis feedback. The accompanying CheckerLab framework independently rebuilds submitted checkers and measures vulnerable-vs-fixed diagnostic contrast, patch localization, false positives, and tool use; across 21 model-harness configurations mean Pass@1 is 32.30% (best 45.33%), showing reliable checker synthesis remains hard for current agents.

CheckerBenchCheckerLab

AI Security, AppSec· Added 7 Oct 2026, published 6 Oct 2026

stepsecurity.iowriteup🛡️ Security

SubQuery Ecosystem Compromise: Hidden Credential Theft and Backdoors

StepSecurity's investigation of @subql/common@5.8.3, a malicious npm release in the SubQuery Web3 indexing framework's monorepo, found a heavily obfuscated postinstall/import-time payload (base64+XOR+gzip inside a function constructed via Function()) that spawns a detached worker to steal credentials (.npmrc, .env, AWS, SSH, kubeconfig, Vault, cloud secrets), read GitHub Actions runner memory for CI secrets, inject a camouflaged "Run Copilot" GitHub Actions workflow to exfiltrate repo secrets, and provide a remote shell/PTY over an encrypted channel to ci-artifacts.dev. The release was published via a compromised build pipeline: a workflow modification swapped the real build output for an externally downloaded, unsigned tarball from that same C2 domain immediately before publish, and the authors provide IOCs and remediation steps (credential rotation, host isolation, domain blocking).

npmGitHub ActionsNode.js+3
SubQuery@subql/commonianhe8x+2

Supply Chain, DevSecOps, Blue Team & Detection· Published and added 5 Oct 2026

eprint.iacr.orgpaper🛡️ Security

Deploying Native-Rust KpqC: Pluggable Post-Quantum KEMs and Signatures across TLS, Space Links, and the OQS Ecosystem

This IACR ePrint paper presents a native-Rust, memory-safe implementation of the Korean KpqC competition's standardized post-quantum schemes — KEMs NTRU+ and SMAUG-T, and signatures HAETAE and AIMer — replacing the reference memory-unsafe C code. The authors expose all seven KEM parameter sets and four signature modes through a single pluggable provider demonstrated across three real deployment front-ends: a rustls TLS 1.3 key-exchange group, an OQS/liboqs-compatible C ABI, and an analytical CCSDS/SDLS satellite constrained-link model, showing SMAUG-T variants are smaller/faster than ML-KEM-768 on constrained space links and a memory-optimized NTRU+ build cuts peak stack by up to 25% at negligible latency cost.

RustCOpen Quantum Safe
KpqCNTRU+SMAUG-T+5

other· Added 8 Oct 2026, published 5 Oct 2026

x.comthread🧠 AI

Sujeet (@sujeetgholap) on X

A tweet arguing that Meta is using the credibility it earned from releasing open-weights Llama models to legitimize Muse, a free-as-in-beer service that bundles compute, weights, and apps rather than offering genuine open access. The commentary frames this as a strategic pivot from open-weights advocacy to a closed, Meta-controlled ecosystem play, explaining why Muse feels less aligned with the open-source AI movement than Llama was.

MetaLlamaMuse

ai-policy· Published and added 3 Oct 2026

dev.towriteup🧠 AI

The MCP Ecosystem Is Speaking Five Revisions at Once

A dated research report (Pennyforge, 2026-10-02) that probes the live MCP ecosystem to show it is fragmented across five spec revisions at once: it POSTs initialize/server/discover calls against 186 deduplicated endpoints pulled from the official MCP registry's v0 API, plus 10 popular npm stdio servers spawned via npx. It finds only ~9.7% of responding endpoints speak the new stateless 2026-07-28 wire (which removes Mcp-Session-Id, the initialize handshake, and adds server/discover), that the flagship @modelcontextprotocol/server npm packages still only speak the older 2025-06-18 revision, and documents a "version-echo" methodology pitfall where servers negotiate within a supported range rather than reporting a fixed version — illustrated with a parallel failure mode found in the x402 payment protocol.

Model Context ProtocolnpmNode.js
Pennyforgex402

mcp· Published and added 2 Oct 2026

ncsc.gov.ukarticle🛡️ Security

NCSC: "One does not simply defend agentically"

NCSC CTO for Architecture Dave Chismon argues that while attackers can freely use agentic AI tooling for technical offensive tasks, defenders face organisational/political constraints (Halvar Flake's maxim) that make equivalent autonomous defensive action far riskier. The piece proposes a framework for assessing the 'riskiness' of automating defensive actions (potency, harm to the business, scope of control), points to low-risk starting points like AI-assisted log summarisation and vulnerability triage, and previews NCSC/DCMS's 'Cyber Shield' agentic defence ecosystem and an upcoming 'AI for Cyber Defence' problem book, alongside references to CETAS's Autonomous Cyber Defence work and the Defra AI Legacy Modernisation Playbook.

SOAR
Halvar FlakeCETASCyber Shield+4

AI Security, Blue Team & Detection· Added 1 Oct 2026

arxiv.orgpaper🛡️ Security

A Function-level Dataset of Vulnerable and Fixed Source Code in JavaScript and TypeScript

JsVul is a function-level dataset of vulnerable and fixed JavaScript/TypeScript code pairs, aggregated from seven sources and built with a language-specific pipeline that strips noise (minified code, cosmetic edits), deduplicates across commits, and applies heuristic labeling of security-relevant changes. It is released in time-ordered JSONL format to support training and evaluating automated vulnerability detection models specifically for the JS/TS ecosystem, where prior datasets were largely generic and multi-language.

JavaScriptTypeScript

AppSec· Added 30 Sep 2026, published 29 Sep 2026

fossa.comarticle🛡️ Security

Generating and Managing C and C++ SBOMs

A FOSSA blog post explaining why C/C++ SBOMs built from manifest-parsing alone are incomplete, since the ecosystem lacks a centralized package manager and relies heavily on vendored (copy-pasted) source and code snippets. It covers concrete generation paths: Conan's built-in conan.tools.sbom CycloneDX generator, Yocto/OpenEmbedded's native SPDX output via the create-spdx class, process-based tracking for vendored code (third_party/vendor path flagging, manual audits), and the differing snippet-support capabilities of SPDX versus CycloneDX.

SBOMCycloneDXSPDX+3

Supply Chain· Added 1 Oct 2026, published 29 Sep 2026

arxiv.orgpaper🧠 AI

Bridging LLM Agents and Data Spaces: An Architectural Mediation Approach using MCP

This paper proposes an architectural mediation approach, implemented as the "Eunomia Agent," that uses the Model Context Protocol to let LLM agents discover and invoke Data Space services as structured, schema-driven tools without modifying existing data space components. A prototype validates end-to-end interaction — catalog discovery, metadata retrieval, and data service invocation — while preserving governance, policy, and access-control constraints native to Data Spaces. It offers practical architectural guidance for organizations wanting to introduce AI-driven automation into governed, sovereign data-sharing ecosystems while maintaining compliance and interoperability.

Model Context Protocol
Eunomia Agent

research, mcp· Added 28 Sep 2026

socket.devarticle🛡️ Security

Socket Joins New OpenJS Program to Fund Node.js Security Work

Socket announces it is an inaugural funder of the OpenJS Foundation's new Security Stewardship Program, which pools money to pay both bug bounty researchers and maintainers doing triage, patching, and backporting for Node.js, starting there before expanding across the JS ecosystem. The article frames this against a broader funding crisis: curl suspended its bounty program after AI-generated report floods, GitHub restructured its bounty tiers, Canonical moved Ubuntu kernel updates to weekly releases to keep pace with rising CVE volume, and Node.js paused bounty payouts in April after the Internet Bug Bounty pulled funding, even as HackerOne report volume to the Node.js team spiked 4.6x in one month.

Node.jsHackerOnecURL+2
OpenJS FoundationInternet Bug BountyNode.js Technical Steering Committee+2

other· Published and added 25 Sep 2026

github.comrepo🛡️ Security

git-pkgs — dependency history & supply-chain analysis for git repos

git-pkgs is a Go rewrite of a Ruby tool that adds a git subcommand for tracking dependency changes across a repository's history, indexing manifests/lockfiles from 36+ package managers (npm, RubyGems, Cargo, PyPI, Maven, Composer, Go modules, etc.) into a local SQLite database. Beyond history/blame/diff, it offers supply-chain security commands: `vulns` (OSV-based CVE scanning with SARIF output for GitHub code scanning, plus blame/praise/exposure for remediation metrics), `licenses` (with drift detection and CI-friendly exit codes), `deprecated`, `provenance` (trusted-publishing/attestation checks), `integrity` (lockfile hash drift detection), `maintainers`/`health` (via ecosyste.ms metadata), and `sbom` export in CycloneDX/SPDX. It also supports a dependency-aware `bisect` to find when a vulnerability, license change, or capability (e.g. network access) was introduced, and ships GitHub Actions for CI integration.

npmSBOMOSV+3
CVE-2024-1234PURL

Supply Chain, DevSecOps· Added 25 Sep 2026

arxiv.orgpaper🧠 AI

Jev in the Wild: A Data-Driven Analysis of the Jev Model's Functionality, Applications and Ecosystem

This arXiv preprint presents a large-scale empirical analysis of Jev, a lightweight decision model that answers natural-language questions via choices, binary judgments, and scores, mining 2,170 public GitHub projects that use it. The authors find rapid ecosystem growth, widespread use of attribute judgment and scoring, more variable use of action selection, content filtering, and model/tool selection, and that public attention concentrates on routing and interface agents independent of raw project counts. It offers a quantitative characterization of how a general-purpose decision component gets embedded into diverse software workflows.

GitHub
Jev

research, evals· Added 26 Sep 2026, published 24 Sep 2026

github.comrepo🛡️ Security

shai-hulud-detect: multi-ecosystem npm/PyPI/Composer/Crates/Go/Hex/RubyGems supply-chain worm scanner

shai-hulud-detect is a dependency-free Bash scanner that checks projects against a 5,782-entry list of compromised npm, PyPI, Composer, Crates, Go, Hex, and RubyGems package versions, plus content-pattern indicators of compromise (malicious file hashes, C2 domains, dead-man's-switch artifacts, forged commits, suspicious lifecycle hooks) tied to the Shai-Hulud supply-chain attack waves. It supports single-project and bulk scanning, CI-friendly exit codes, JSON/log output for pipeline gating, and a --check-host mode to detect the May 2026 gh-token-monitor/kitty-monitor persistence daemons that wipe hosts if their monitored GitHub token is revoked (with a documented safe remediation order). Detection is read-only; new package entries are sourced from named threat-research firms (Socket, StepSecurity, Aikido, Snyk, JFrog, Wiz, Semgrep, SafeDep, GitGuardian, OX Security) and cited in PRs.

npmPyPIComposer+3
Shai-Huludgh-token-monitorkitty-monitor

Supply Chain, DevSecOps· Added 23 Sep 2026

arxiv.orgpaper🛡️ Security

A2M: Trace-Optimized Agent Hijacking in the MCP Ecosystem

A2M (Attraction-to-Manipulation) is a two-stage black-box framework for hijacking agents that use the Model Context Protocol to select tools from third-party MCP servers. The Attraction phase optimizes attacker-controlled tool metadata to raise invocation probability, while the Manipulation phase uses execution traces to craft adversarial tool outputs that steer agent behavior; on LiveMCPBench it achieves a 93.6% malicious tool invocation rate against GLM-4.6, inflates token cost 32.4x under a cognitive denial-of-service variant, and reaches a 74.4% mean attack success rate across information exfiltration, environment integrity compromise, and reasoning derailment, with partial transfer (63.6%/2.7x/24.5%) to four other models without re-optimization. The authors argue this exposes a semantic supply-chain risk in MCP tool ecosystems and call for stronger tool vetting and runtime isolation.

Model Context ProtocolGLM
LiveMCPBenchA2MCognitive Denial of Service

AI Security· Added 2 Oct 2026, published 22 Sep 2026

aikido.devwriteup🛡️ Security

Graphalgo campaign spreads to Terraform providers and Go Modules

Aikido documents the Graphalgo malware campaign's expansion beyond NPM into two malicious Terraform providers (gocommunity-io/dockerd and the kreuzwerker/docker typosquat kreuzwenker/docker) and two Go modules (gocommunity.io/orderedbtree, gogets.dev/btreex), marking the first observed systematic Terraform provider malware distribution. The payload is a Go port of Graphalgo sharing blockchain infrastructure, Slack C2, and a public key with prior JS/NPM samples; it activates only under specific hash-gated runtime conditions (targeted attack indicator), then deploys a Go RAT with dual C2 channels — an Ethereum (Arbitrum Sepolia) smart-contract dead drop and Slack bot messaging — plus self-delete and remote code execution capabilities. The threat actor also stood up two fake Go package ecosystem websites (gocommunity.io, gogets.dev) to socially engineer developers and backdated Git commits to obscure module publication timing.

TerraformGoSlack+3
GraphalgoReversingLabsSafedep+6

Supply Chain, Threat Intel, Blockchain· Published and added 22 Sep 2026

github.comrepo🛡️ Security

ossf/criticality_score

criticality_score is an OpenSSF tool that computes a 0-1 criticality score for open source projects (based on an algorithm by Rob Pike), using signals like contributor count, commit frequency, dependents count, and org diversity to identify projects the ecosystem critically depends on. It ships a CLI, config files for tuning scoring weights, and companion tools (enumerate_github, collect_signals, scorer) for large-scale data collection; the project's GCP-hosted BigQuery/GCS datasets will be discontinued after 2026-08-29, with data moving to a static data directory.

GitHubGoGoogle Cloud

Supply Chain· Added 21 Sep 2026

github.comrepo🧠 AI

OmniJev/awesome-jev-gallery

An extensive, actively maintained GitHub "awesome list" cataloging the ecosystem that has grown around TypeSafe's Jev and its "System One" typed decision models — a non-generative alternative to chat LLMs that returns calibrated probabilities per option (Choice/Score/Noul primitives) via RLCD training and single-pass constrained decoding. It indexes dozens of open-weight reproductions (OneJev, Rizzo Flow, Laya, Jebadiah, kev), benchmarks and leaderboards (JevBench, Jev Decision Index, JevAdvBench, DecisionBench), downstream tools (browser/robot/trading agents built on the typed API), and the research lineage the design draws on (zero-shot entailment classifiers, InstructGPT's reward model, GLiNER/GLiClass, monoBERT, LLaDA, vLLM, DSPy, RouteLLM, Constitutional Classifiers). It also links commentary auditing TypeSafe's claims (accuracy vs. frontier LLM baselines, security issues found in community tools).

vLLMDSPyOutlines+13
JevTypeSafeDiogo Almeida+31

models, evals, research· Added 29 Sep 2026, published 17 Sep 2026

latent.spacearticle🧠 AI

[AINews] AEF-1 standard emerges for Third Party Evaluators, as Xai, OpenAI, and Anthropic all cosign

This Latent Space AINews issue (9/11–9/14/2026) centers on the AI Evaluator Forum's AEF-1 standard for independent third-party AI evaluators, published alongside Dario Amodei's personal follow-up to 'Pacing the Frontier' proposing embedded evaluators (like METR) with employee-like access at frontier labs, plus a sharp Twitter split between pacing/slowdown advocates (Bilal Chughtai, Dan Selsam) and control-first critics (Aidan Gomez, Cohere, Kevin Bass alleging conflicts of interest in the safety-eval ecosystem). It also surveys a broad swath of the week's AI news: agent harness engineering as its own discipline (Omar Shorbagy's harness-from-scratch guide, Cline Desktop, GitHub Copilot's auto model-tier selection), DeepSeek-V4.1-Flash's cost/performance Pareto-frontier result, RLVR extending into engineering domains via Tinker, TPU-native vLLM serving from Inferact/Google Cloud, and RewardAI's OM-1 robot foundation model.

vLLMLangChainCodex+2
AI Evaluator ForumAEF-1Dario Amodei+36

ai-policy, ai-safety, agents· Added 29 Sep 2026, published 15 Sep 2026

endorlabs.comarticle🛡️ Security

Next-Gen SCA for C/C++: Closing the Detection Gap | Blog | Endor Labs

Endor Labs announces C/C++ language support for its SCA product, addressing the long-standing difficulty of tracking OSS dependencies in ecosystems with no central package registry. Because C/C++ developers commonly vendor (copy and modify) library source directly into their repos, Endor Labs builds a fingerprint index of known OSS libraries using cryptographic hashes for exact-match segments (functions, license blocks, etc.) and ML-generated code embeddings to catch renamed, reformatted, or lightly modified copies. The company reports customer benchmarks showing 81% fewer false negatives and 143% more true positives versus prior tooling for building SBOMs and detecting vulnerable/license-non-compliant code in C/C++ codebases.

Endor LabsCSBOM

Supply Chain· Published and added 11 Sep 2026

rapid7.comarticle🛡️ Security

The Fraud Ecosystem: A Transition From Known Marketplaces to a Fragmented Environment

Rapid7 profiles the current Fraud-as-a-Service marketplace landscape — Xleet, Blackpass (formerly Paysell), Infodig, and Styx — detailing their shift from large hubs to fragmented, invite-gated shops selling compromised accounts, SMTP/RDP/VoIP infrastructure, eSIMs, stolen PII, and cashout/money-laundering services. It also discusses the new MITRE Fraud Fighting Framework (F3), introduced in early 2026, which maps adversary TTPs for fraud/financial-crime monetization, and argues security teams must correlate marketplace monitoring with internal fraud and compliance units to counter account-takeover and laundering schemes.

Telegram
XleetBlackpassPaysell+6

Threat Intel· Added 7 Oct 2026, published 11 Sep 2026

interconnects.aiarticle🧠 AI

Open-Source AI & Open Models Reading List

A continuously updated reading list from Nathan Lambert's Interconnects curating the best writing on open-weight AI models, organized into Foundation (why companies release open models, the open/closed gradient, safety-vs-openness debates), US-China Competition (the ATOM Project, China's structural advantages, corporate adoption of Chinese models by DoorDash/Airbnb/Cursor/Harvey/Perplexity/Thomson Reuters), and Technical Details (the open-closed performance gap per SemiAnalysis and Epoch AI, cyber-misuse risk, and the 2026 distillation controversy including the paper on stealing reasoning traces from proprietary LLM APIs). It links dozens of primary sources — policy essays, lab statements (Zuckerberg, Thinking Machines Lab), technical reports (Pythia, OLMo, OLMo 2/3), and data trackers (Artificial Analysis, Interconnects Adoption Dashboard) — making it a comprehensive entry point for understanding the open-model ecosystem.

Nathan LambertInterconnectsKevin Xu+39

ai-policy, training, models· Added 29 Sep 2026, published 11 Sep 2026

chainalysis.comarticle🛡️ Security

OFAC and DOJ Strike Xinbi, a Multibillion-Dollar Marketplace for Cybercriminals

Chainalysis details the OFAC/DOJ sanctioning and seizure action against Xinbi Guarantee, a $24B Chinese-language Telegram-based marketplace connecting money laundering, scam infrastructure, stolen data, and KYC-bypass vendors. The piece maps Xinbi's escrow model and vendor ecosystem, and traces how DPRK-linked actors used specialized 'Black U' launderers to swap traceable stolen funds from the Bybit ($1.5B) and WazirX ($235M) hacks for cleaner stablecoins sourced from pig-butchering and romance-scam proceeds, ultimately leading to $52M in restrained cryptocurrency across 49 wallets.

Telegram
DPRKXinbi GuaranteeSafeW Technology+4

Threat Intel, Blockchain· Added 30 Sep 2026, published 9 Sep 2026

github.comrepo🛡️ Security

ForgeGuardian

ForgeGuardian is an open-source (Apache 2.0) supply chain security scanner covering 9 package ecosystems (npm, PyPI, Go, Maven, RubyGems, Cargo, NuGet, Hugging Face, GitHub Actions) via 8 concurrent scan engines and 223+ built-in malicious-package detection signatures. It runs fully offline/local-first, offers a CLI (fgctl) and self-hosted SOC-style dashboard, generates CycloneDX/SPDX SBOMs, supports Sigstore keyless signing and provenance tracking, policy-as-code rules, dependency topology/attack-surface mapping, drift detection with auto-quarantine, and SARIF output for GitHub Actions CI integration, plus optional AI-powered advisory/patch-agent triage.

npmPyPIGo+3

Supply Chain, DevSecOps· Published and added 5 Sep 2026

owasp.orgother🛡️ Security

OWASP Agentic Skills Top 10 (AST10)

OWASP project page for the Agentic Skills Top 10 (AST10), a framework that lists the 10 most critical security risks in AI agent skills across agent platforms, with mitigations and prevention strategies. It targets the behavior/execution layer of skills, which sits above MCP tool access, and maps each risk to the Cloud Security Alliance's MAESTRO 7-layer threat model. It is a useful reference for threat-modelling agent skill ecosystems.

Model Context ProtocolLLM
OWASPMAESTROCloud Security Alliance

AI Security, GRC· Added 5 Sep 2026

arxiv.orgpaper🧠 AI

TokenMatch: 3D Mesh Correspondence Transformer with Curvature-Guided Tokenisation

TokenMatch is a transformer-based model for 3D mesh shape correspondence that uses curvature-guided adaptive tokenisation to turn meshes into patches, learning patch- and point-level relations via self- and cross-attention. Trained only on the BeCoS partial-to-partial dataset, it generalises to full-shape matching without fine-tuning, outperforming prior methods on CP2P, PSMAL, BeCoS, FAUST, SCAPE and SHREC'19 while running at sub-second inference.

Transformer
BeCoSCP2PPSMAL+4

research, multimodal· Added 22 Sep 2026, published 3 Sep 2026

aikido.devarticle🛡️ Security

The dark figure of supply chain detection

Aikido Security argues that string/IOC-based malware detection suffers from survivorship bias (the 'dark figure' of undetected supply-chain attacks) and proposes an adapted version of David Bianco's Pyramid of Pain for package ecosystems, where durable detection requires behavioral baselines mapped per package type rather than hashes or known-bad strings. It illustrates the approach with a real incident: a malicious version of the popular npm package Keyv (600M+ downloads) that executed obfuscated JS, downloaded the Bun runtime, and ran a second obfuscated payload at install time, caught by behavioral/technique-level analysis in Aikido's sandbox despite heavy obfuscation defeating static analysis.

npmBunAikido Security+2
Pyramid of PainDavid Biancokeyv

Supply Chain, Blue Team & Detection· Added 3 Sep 2026, published 1 Sep 2026

github.comrepo🛡️ Security

cyanheads/osv-advisory-mcp-server

osv-advisory-mcp-server is an MCP server that queries the OSV.dev vulnerability database, offering single-package version checks, batch audits of up to 1000 {name, ecosystem, version} tuples for SBOM/lockfile triage, and full advisory record fetch by OSV ID (GHSA/PYSEC/RUSTSEC/GO/DSA/DLA/CVE prefixes). It surfaces CVE aliases, CVSS vectors, derived severity labels, and CWE IDs, and is designed to chain into a companion nist-nvd-mcp-server for CVSS base scores, EPSS probability, and CISA KEV status. It ships as a keyless, no-API-key tool runnable via STDIO or Streamable HTTP, with a public hosted instance and Bun/npx/Docker install paths.

Model Context ProtocolOSVBun+3
CISA KEVEPSSnist-nvd-mcp-server

Supply Chain· Added 1 Sep 2026

endorlabs.comwriteup🛡️ Security

Mini Shai-Hulud worm hits openapi-react-query-codegen, spreads across npm, RubyGems, and PyPI | Blog | Endor Labs

Endor Labs researchers document a 'Mini Shai-Hulud' worm variant that compromised the openapi-react-query-codegen npm package and self-replicated across npm, expanding into RubyGems and PyPI ecosystems. The writeup traces how the worm trojanized a legitimate package to propagate malicious code cross-registry, illustrating an evolving multi-ecosystem software supply-chain attack pattern.

npmPyPIRubyGems+1
Shai-Hulud

Supply Chain· Added 3 Sep 2026, published 31 Aug 2026

github.comrepo🛡️ Security

Awesome Cybersecurity Agentic AI

A curated GitHub awesome-list cataloging the emerging agentic-AI security ecosystem: dozens of Model Context Protocol servers that give LLM agents access to security tools (Nuclei, Shodan, VirusTotal, Burp Suite, Ghidra, BloodHound, x64dbg), autonomous penetration-testing and CTF-solving agent frameworks (CAI, pentagi, BreachSeek, Dark-Moon, D-CIPHER), scanners/guardrails that audit agent skills, MCP servers, and multi-agent chains for prompt injection and other risks (Aguara, Inkog, MCP Doctor, AI-Infra-Guard, ATR), agentic SOC/detection platforms (Vigil), threat-modeling frameworks for agentic systems (MAESTRO, ATFAA/SHIELD), research papers, benchmark datasets, and community/learning resources. It functions as a living index for anyone building or defending AI-agent-driven security tooling.

Model Context ProtocolLangChainCrewAI+3
OWASP Top 10 for LLM ApplicationsEU AI ActOWASP FinBot CTF+1

AI Security, Offensive Security, Blue Team & Detection· Added 3 Sep 2026, published 31 Aug 2026

github.comrepo🧠 AI

zhu1090093659/dsh-trading

dsh-trading is an open-source AI trading terminal built on "DeepSeek Harness" (DSH), a Cordis-based microkernel plugin ecosystem, covering crypto, US equities, China A-shares and Hong Kong stocks. Its notable design is a multi-agent team: a "master" lead agent grounds itself in a holdings ledger and user knowledge base, then decomposes work and delegates to persona-pinned subagents — a trader (trading plans/execution), an instrument-researcher (disclosures/fundamentals), and a risk-reviewer (exposure/stress scenarios) — each dispatching bundled domain "skills" and native tools for quotes, news, order books and backtesting. Every order defaults to dry-run simulation, live execution requires explicit opt-in plus interactive human approval, and headless sessions fail closed, illustrating a concrete human-approval-gated tool-use pattern for agentic systems.

Node.jspnpmCordis+2
DeepSeek HarnessBinanceOKX+12

agents· Added 2 Oct 2026, published 30 Aug 2026

socket.devarticle🛡️ Security

Socket: PHP and Composer Support Reaches Beta With Reachability Analysis

Socket announces its PHP/Composer supply-chain security support is moving to Beta with generally available reachability analysis, which distinguishes exploitable vulnerabilities from unreachable ones in dependency trees. The post details real attacks Socket tracked moving into the PHP/Packagist ecosystem, including the Mini Shai-Hulud worm jumping from npm via a malicious Intercom PHP package, a malicious postinstall hook found across 700+ GitHub repos, a Famous Chollima-linked backdoored Laravel package, and Packagist packages disguised as Laravel utilities/CMS themes deploying RATs and trojanized jQuery.

ComposerPackagistPHP+3
Mini Shai-HuludFamous ChollimaIntercom PHP package

Supply Chain, AppSec· Published and added 22 Aug 2026

aikido.devwriteup🛡️ Security

Popular Rust crates arrayref, append-only-vec, and internment compromised in Supply Chain Attack

Aikido researchers detail a supply-chain compromise of three popular Rust crates maintained by the same author, arrayref with 244M downloads, append-only-vec with 4M, and internment with 14M, that were modified to add a single malicious manifest dependency, proc-macro1, a typosquat of proc-macro2. Because the dependency's build.rs executes automatically during cargo build, merely compiling a project pulling in any of these crates downloads and runs a platform-specific payload that drops an infostealer targeting Chromium browser credentials and crypto-wallet extension storage, installs macOS LaunchAgent persistence, and beacons to a lightweight C2 supporting remote shell commands. The campaign's TTPs closely mirror the prior npm-based Axios and Mastra compromises attributed to DPRK, suggesting the same actor expanding into the Rust ecosystem.

RustCargocrates.io+3
proc-macro1proc-macro-endroundy+4

Supply Chain, Malware & RE, Threat Intel· Added 3 Sep 2026, published 20 Aug 2026

snyk.ioarticle🛡️ Security

Remediation Agents, Demystified: Why Fixing Beats Finding

Recap of a Snyk "AI Security Engineers Community" livestream introducing Remediation Agent, now in public preview: an orchestration layer that sits between a developer's chosen LLM and Snyk's vulnerability intelligence (breakability assessments for OSS upgrades, package health/reachability scores, SAST fix generation, and ecosystem-specific upgrade playbooks) to auto-generate mergeable SCA and SAST fixes. It was demoed live against OWASP Juice Shop via the CLI (snyk fix --agentic --experimental --sca) and via an IDE path (Snyk Studio MCP server plus a /snyk-fix skill in Cursor, Windsurf, or VS Code), with Snyk reporting internal gains of 94% more mergeable SCA fixes and 13% more mergeable SAST fixes versus naively pointing an LLM at a vulnerability backlog.

SnykSnyk CodeModel Context Protocol+2
OWASP Juice ShopmulterGlob

AppSec, AI Security, DevSecOps· Added 3 Sep 2026, published 19 Aug 2026

interconnects.aiarticle🧠 AI

Teaching Everyone to Fish for Tokens

Nathan Lambert's interconnects.ai essay argues open-weight AI models function less like Linux and more like installed software versions, while the true open-source analogue is full training recipes like Ai2's Olmo or EleutherAI's Pythia. It examines why Nvidia is bankrolling near-open-source efforts (e.g. Nemotron, reportedly ~$26B) to sustain demand for its chips, why companies like Databricks and 01.ai have exited model training, and predicts open models will fork toward a long-tail niche (on-prem, specialized, efficiency-focused) unless open ecosystems develop their own platform-like financial feedback loops. It also proposes that the "pretraining/post-training" lexicon may split into pretraining, reasoning training, and post-training as base-model training becomes more opaque and post-training/fine-tuning (e.g. via Tinker) dominates community interest.

Tinker
NVIDIAMetaAnthropic+10

ai-policy· Added 29 Sep 2026, published 17 Aug 2026

endorlabs.comarticle🛡️ Security

Why NPM Malware Keeps Reaching for Bun | Supply Chain Security | Blog | Endor Labs

Endor Labs analyzes why a string of npm supply-chain campaigns — Shai-Hulud 2.0 (Nov 2025, 796 packages backdoored) and an April 2026 SAP-ecosystem attack on mbt, @cap-js/db-service, @cap-js/sqlite and @cap-js/postgres — all use the same second stage: a preinstall script that downloads the Bun JavaScript runtime to run an obfuscated credential stealer. Bun is attractive to attackers because it's a userland, statically-linked binary with a different process name than node, bypasses Node's --require/NODE_OPTIONS instrumentation hooks, and ships built-in shell/decompression/HTTP primitives (Bun.$, Bun.gunzipSync) that avoid the suspicious imports scanners look for. The piece also notes CVE-2026-24910, a trusted-dependency spoofing flaw in Bun's package manager, and recommends prioritized controls: disable npm lifecycle scripts (ignore-scripts=true) with an auditable allowlist, enforce a minimum release age/cooldown on dependencies, block known-malicious versions pre-install, eliminate long-lived npm/cloud tokens, and detect on process lineage rather than binary name.

BunnpmNode.js+3
Shai-Hulud 2.0CVE-2026-24910mbt+3

Supply Chain, Blue Team & Detection, DevSecOps· Added 3 Sep 2026, published 12 Aug 2026

github.comrepo🛡️ Security

Static Analysis Tools & Linters

analysis-tools.dev's source repository is a community-maintained directory of static analysis tools and linters spanning nearly every programming language, tagged for license (proprietary vs open source), maintenance status, and community endorsement. Beyond general code-quality linters, it catalogs many security-relevant static analyzers such as gosec, flawfinder, OWASP Dependency Check, Mariana Trench, Psalm, PHPStan, govulncheck, and WAP, making it a reference point for discovering SAST tooling per language/ecosystem.

GoPHPJava+3

AppSec· Added 3 Sep 2026, published 9 Aug 2026

aikido.devadvisory🛡️ Security

Keyv and friends compromised in active Shai-Hulud supply chain attack

Aikido Security reports that Keyv and several related npm packages were compromised as part of the ongoing Shai-Hulud supply-chain attack, in which malicious versions were published to npm to spread a self-replicating worm across the ecosystem. The write-up details the affected packages and versions and the worm's propagation mechanism via compromised maintainer credentials and postinstall scripts.

npmNode.jsKeyv
Shai-Hulud

Supply Chain· Added 3 Sep 2026, published 4 Aug 2026

interconnects.aiarticle🧠 AI

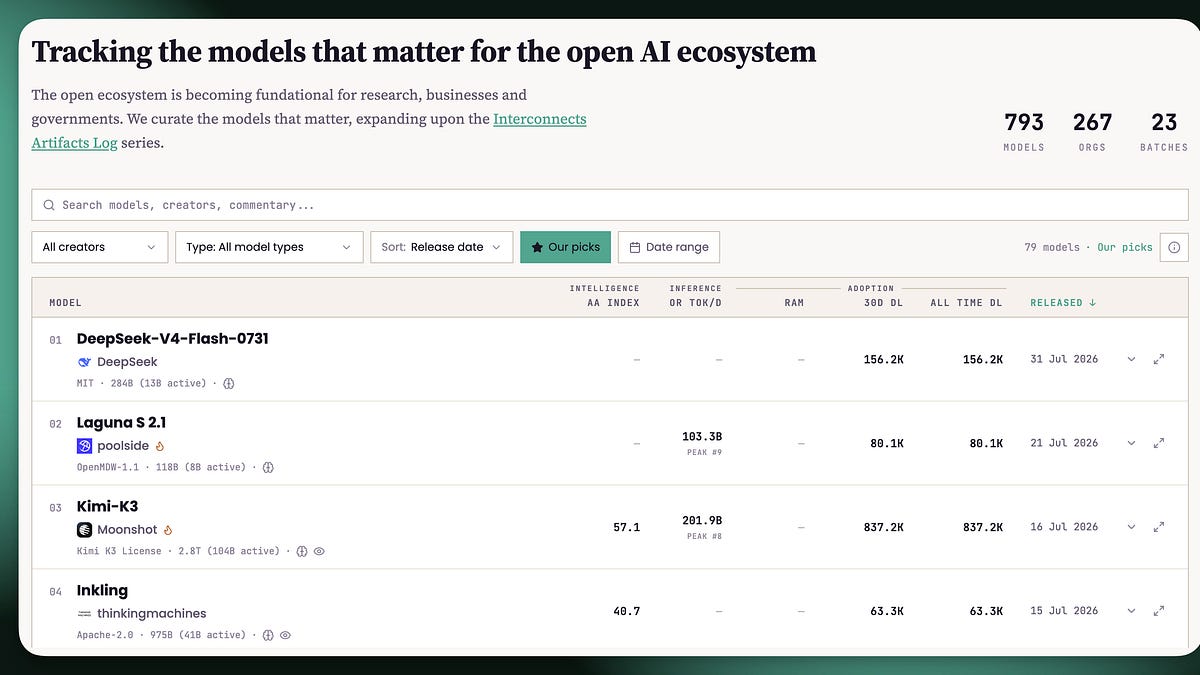
Introducing our Artifacts Hub and Adoption Dashboard

Interconnects announces two new free, continuously-updated resources for tracking the open-weights model ecosystem: the Artifacts Hub, which curates ~792 trending Hugging Face models with inference-token data from OpenRouter, intelligence scores from Artificial Analysis's Intelligence Index, and Interconnects' own relative adoption metric (RAM) and VAIL similarity index; and the Adoption Dashboard, a daily-updating view of download/derivative-model counts by geography and organization highlighting the US-China open-model gap. Both build on prior work from The ATOM Project and Interconnects' Artifacts Log round-ups, developed in collaboration with AI verification startup Project VAIL.

Hugging FaceOpenRouter
InterconnectsArtificial AnalysisProject VAIL+4

models, ai-policy· Added 29 Sep 2026, published 3 Aug 2026

github.comrepo🛡️ Security

radare2

radare2 (r2) is a free and open-source command-line reverse engineering framework providing disassembly, binary analysis, debugging (local and remote via gdb/windbg), emulation via ESIL, and hex editing/forensics across an enormous range of CPU architectures and executable file formats (ELF, PE, Mach-O, DEX, WASM, etc.). It is extensible via r2pipe scripting and the r2pm package manager, with a large plugin ecosystem including r2ghidra (decompiler), r2frida (dynamic instrumentation), r2yara, radius2 (symbolic execution), and r2dec.

GhidraFridaYARA

Malware & RE· Published and added 31 Jul 2026

endorlabs.comarticle🛡️ Security

Best SBOM Tools in 2026, Compared | Blog | Endor Labs

Endor Labs' 2026 SBOM tooling comparison sorts five tools into three functional layers: open-source generators (Syft, cdxgen, Microsoft SBOM Tool) that produce SPDX/CycloneDX inventories, OWASP Dependency-Track for centralized SBOM storage and continuous monitoring, and Endor Labs' own SBOM Hub which adds function-level reachability analysis to cut CVE alert noise by a claimed 95%. It breaks down each tool's ecosystem coverage, format support, and trade-offs (e.g., Syft's lack of reachability, cdxgen's CycloneDX-only output, Dependency-Track's need for a database) and gives a decision framework for picking a tool by stack and maturity level.

Endor LabsSyftSBOM+3

Supply Chain· Added 3 Sep 2026, published 29 Jul 2026

depthfirst.comwriteup🛡️ Security

Behind the GitLab RCE: A depthfirst Journey into the Ruby Ecosystem | depthfirst

depthfirst's Open Defense Initiative scanned about 40 Ruby gems with native C extensions and validated 105 vulnerabilities across 34 projects, which together have over 8.6 billion RubyGems downloads. The post walks through four cases: a Nokogiri 32/64-bit index truncation (CVE-2026-57235), an Oj garbage-collection use-after-free (CVE-2026-54902), a concurrent-ruby read/write lock bit overflow (CVE-2026-54905) and an sqlite3-ruby block lifetime bug (CVE-2026-54619). It also states that this work led to the earlier GitLab RCE chain through Oj.

RubyRubyGemsNokogiri+6
CVE-2026-57235CVE-2026-54902CVE-2026-54905+6

AppSec, Supply Chain, AI Security· Added 29 Oct 2026, published 27 Jul 2026

interconnects.aitalk🧠 AI

Open models recap: more on Kimi K3, Qwen 3.8, Xi's WAIC speech, distillation, the open-closed gap, and what's next

A transcribed Interconnects podcast episode where Nathan Lambert and Florian Brand do their quarterly open-model roundup, covering the Kimi K3 release (its coding/agentic performance, $200/mo plan, broken API capacity), GLM-5.2's continued developer traction, Qwen's announced pivot to open-weighting its next flagship, and Xi Jinping's WAIC speech committing China to open-source AI. They dig into why Chinese labs (Kimi/Moonshot, Zhipu/GLM, DeepSeek, MiniMax, LongCat, Ling/Meituan) keep pace with the closed frontier despite less compute — capital efficiency, smuggled/domestic chips, buying external data — then survey the smaller US open ecosystem (Thinking Machines' Inkling and Tinker, Gemma, Nemotron, Poolside, Arcee, Reflection). The back half is a detailed rebuttal of Ben Thompson's Stratechery claim that distillation grows more important as RL scales, arguing SFT-stage distillation from jailbroken Claude/GPT reasoning traces matters less as RL-stage training (which is hard to distill cheaply) dominates post-training, with a side note on a Hugging Face incident where guardrails forced defenders to use a less-restricted model (GLM) to analyze an attack.

QwenQwen3Claude+5
Kimi K3GLM-5.2Qwen 3.8+28

models, training, ai-policy· Added 29 Sep 2026, published 22 Jul 2026

huntress.comarticle🛡️ Security

What Are Initial Access Brokers?

Huntress explains how initial access brokers (IABs) operate as specialized cybercriminals who breach organizations, verify and price the foothold, then sell it to ransomware crews, BEC actors, or data thieves via dark web marketplaces. It walks through common IAB entry vectors — infostealer credential theft, exposed RDP/VPN abuse, and AI-assisted phishing (citing a Huntress EvilTokens lure example) — and includes a real SOC case where a brute-forced RDP server led to tradecraft linked to a ransomware ecosystem. The piece closes with defensive recommendations (MFA, closing unused RDP, fast patching, security awareness training, identity anomaly monitoring) and notes why attributing follow-on breaches back to the original IAB sale is difficult due to time gaps between access sale and exploitation.

RDPVPNHuntress
EvilTokens

Threat Intel, Learning· Added 3 Sep 2026, published 21 Jul 2026

aikido.devwriteup🛡️ Security

SleeperGem: RubyGems supply chain attack targets dormant maintainer accounts

Aikido researchers dissect SleeperGem, a RubyGems supply chain attack where a newly published gem, git_credential_manager, downloaded malicious binaries hosted on a fake git-ecosystem account at git.disroot.org and executed them via shell or PowerShell. The attacker evolved the payload across four versions in nine hours, silencing output, wiring execution into the gems require and load path, and adding a check to skip roughly 30 CI environment variables so it only fires on developer laptops, then used two separate long-dormant maintainer accounts to push the gem as a dependency into the trusted gems Dendreo and fastlane-plugin-run_tests_firebase_testlab with over 574000 downloads. The piece argues this is RubyGems first taste of the dormant-maintainer-account-takeover pattern long seen on npm and PyPI.

RubyGemsVirusTotalPowerShell+1
SleeperGemgit_credential_managerDendreo+2

Supply Chain· Added 3 Sep 2026, published 19 Jul 2026

github.comrepo🛡️ Security

Awesome AI Web3 Security

A curated, verified awesome-list of AI-powered tools for smart contract and blockchain security, covering autonomous auditor agents (Hound, Plamen, Aether, SolidityGuard), commercial AI audit platforms (Sherlock AI, Cantina Apex, Zellic V12, Nethermind AuditAgent), MCP-based auditing plugins (Trail of Bits Skills, Claudit, Slither MCP, Solodit MCP Server), real-time on-chain ML monitoring (Forta Network, AnChain.AI), and benchmark/training datasets (EVMbench, SCONE-bench, ScaBench, SmartBugs). Every entry requires a real AI/ML/LLM component plus a specific Web3 security focus, with open-source entries needing 25+ GitHub stars, positioning it as a practical index for the emerging AI-driven smart-contract-audit tooling ecosystem.

SolidityEthereumSolana+3
Trail of BitsCertoraForta Network+9

AI Security, AppSec· Added 3 Sep 2026, published 18 Jul 2026

opensourcemalware.comarticle🛡️ Security

OpenSourceMalware Blog

OpenSourceMalware's blog is an active threat-intelligence feed tracking malicious open-source packages across npm, PyPI, RubyGems, and other registries, publishing frequent posts with IOCs, campaign attribution, and remediation guidance. Recent coverage spans DPRK-linked actors (Lazarus Group, TeamPCP, PolinRider) using techniques like VS Code tasks.json abuse, npm worms (Mini Shai-Hulud, Miasma), trusted-publishing abuse, and cross-ecosystem typosquatting to compromise maintainer accounts and steal credentials.

npmPyPIRubyGems+3
DPRKTeamPCPLazarus Group+15

Supply Chain, Threat Intel, Malware & RE· Added 3 Sep 2026, published 18 Jul 2026

opensourcemalware.comwriteup🛡️ Security

ChainVeil and ViteVenom are DPRK’s PolinRider Campaign

OpenSourceMalware analyzes Checkmarx Zero's ChainVeil (nine malicious npm packages using a 77KB RAT and a TRON/Aptos/BSC blockchain C2 channel) and ViteVenom (seven Vite-ecosystem typosquats) reports, and shows five values -- two TRON wallets, one Aptos address, and two XOR decryption keys -- are byte-for-byte identical to infrastructure they published in March for the DPRK/Lazarus Group campaign PolinRider, predating Checkmarx's report by over 70 days. They conclude ChainVeil/ViteVenom (maintainer "successkeyteck"/SuccessKey) are PolinRider running directly against npm and Vite, and list the full chronological table of typosquatted packages, versions, and maintainers.

npmVite
PolinRiderDPRKLazarus Group+6

Threat Intel, Supply Chain· Added 3 Sep 2026, published 17 Jul 2026

aikido.devarticle🛡️ Security

How Aikido Intel detects malware and vulnerabilities first

Aikido describes the internal architecture of Aikido Intel, its real-time supply-chain intelligence feed that monitors over 4 million packages across ecosystems like npm, PyPI, and Packagist for malware and undisclosed vulnerabilities. The pipeline combines extraction/deobfuscation, static rule matching (Opengrep, YARA-X), npm sandbox detonation for dynamic behavior analysis, an AI triage layer that traces cross-file attack chains, and human researcher review, claiming median detection times under 6-8 minutes and citing their role in surfacing s1ngularity and the Shai-Hulud/Shai-Hulud 2.0 npm worm campaigns. It also mentions Aikido Safe Chain, a free tool that blocks installs of malicious or very new npm packages, and notes Intel protects Packagist downloads via Composer.

Aikido SecuritynpmPyPI+5
s1ngularityShai-HuludShai-Hulud 2.0+1

Supply Chain, Malware & RE· Added 3 Sep 2026, published 13 Jul 2026

github.comrepo🛡️ Security

awesome-ai-security-tools

An extensive, actively updated awesome-list aggregating public-source, research, and commercial tools for AI security and AI-assisted cybersecurity. It spans LLM-driven finding triage (nuclei-autotriage, SigmaOptimizer), securing AI coding agents and MCP/skill ecosystems (agent-audit, SkillSpector, Ramparts, ToolHive, Pipelock), AI/ML supply-chain and model-artifact scanning (modelscan, Fickling, GuardDog, Adversarial Robustness Toolbox), and autonomous pentest/exploit agents (PentestGPT, PentAGI, Strix, CAI). Each entry includes stars, license notes, and cross-references, making it a practical index for the fast-moving 2026 agentic-AI-security tooling landscape.

Model Context ProtocolClaude CodeOpenClaw+2
MITRE ATT&CKMITRE ATLASNIST AI RMF+2

AI Security, Supply Chain, Offensive Security· Published and added 11 Jul 2026

opensourcemalware.comtalk🛡️ Security

The OpenSourceMalware Show #12

Episode 12 of the OpenSourceMalware Show covers three security stories and features an extended interview with Mikael Barbero, Head of Security at the Eclipse Foundation, about securing Open VSX. The interview details Open VSX's pre-publish YARA/AI-assisted malware scanning pipeline, quarantine-and-human-review workflow, token expiration and revocation overhaul, namespace/publisher verification, and detection of 'sleeper' extensions that turn malicious after an update (as seen with GlassWorm-style campaigns). The quick-hits segment covers Paul McCarty's PolinRider research showing a DPRK automated repo-hijacking campaign spreading into Go and PHP ecosystems via Packagist/Go registry packaging of GitHub repos, a cybersecurity startup caught publishing seven infostealer npm packages to manufacture its own threat data, and MeetingTV's lawsuit against Palo Alto Networks/Koi Security alleging an AI-hallucinated domain on a C2 IOC list caused real business harm.

Open VSXnpmGo+5
Lazarus GroupDPRKContagious Interview+10

Threat Intel, Supply Chain· Added 3 Sep 2026, published 9 Jul 2026

opensourcemalware.comwriteup🛡️ Security

PolinRider Jumps the Fence to Go, Packagist, npm, PyPI

OpenSourceMalware documents how PolinRider, a DPRK/Lazarus Group supply-chain campaign tied to the Contagious Interview cluster, spread from GitHub account takeovers into Go modules, Packagist/Composer packages, npm libraries and Chrome extensions without any change to the malware itself. Because Go and Packagist resolve packages directly from git tags rather than a separately-uploaded artifact, a compromised GitHub account automatically becomes a compromised registry release — unlike npm/PyPI, which require a separate publishing credential and largely stalled the takeover at the registry boundary. The post gives ecosystem-by-ecosystem evidence (10 Packagist packages, 80+ Go modules, an NPM/Chrome cluster), IOCs (TRON/Aptos dead-drop addresses, XOR keys, loader signatures, temp_auto_push.bat), a campaign timeline, and remediation guidance for Go/Composer maintainers.

GoPackagistnpm+5
DPRKLazarus GroupContagious Interview+6

Threat Intel, Supply Chain· Added 3 Sep 2026, published 8 Jul 2026

blog.trailofbits.comwriteup🛡️ Security

Shipping post-quantum cryptography to Python

Trail of Bits, funded by the Sovereign Tech Agency, implemented Rust bindings for NIST's ML-KEM (FIPS 203) key-establishment and ML-DSA (FIPS 204) digital-signature standards into pyca/cryptography, shipped in version 48 with AWS-LC backend support. The post makes them a pip install away for the Python ecosystem (pyca/cryptography sees 1.2B monthly PyPI downloads and underpins Certbot, Ansible, Airflow, and paramiko), while detailing the size/performance tradeoffs versus Ed25519/X25519 and noting SLH-DSA (FIPS 205) support and protocol-level integration are still in progress.

PythonPyPIRust+3
ML-KEMML-DSASLH-DSA+6

AppSec· Added 3 Sep 2026, published 30 Jun 2026

aikido.devarticle🛡️ Security

Everybody's shipping code they can't read

An Aikido Security blog post arguing that AI coding agents (e.g. Claude Cowork-style tools) now install npm dependencies on a user's behalf without any human reviewing what gets pulled in, citing the recent @mastra ecosystem attack where 141 packages were republished in a 45-minute burst with a malicious date-library lookalike that dropped a wallet-stealing payload and self-deleted. It also flags "slopsquatting," where attackers preemptively register package names that LLMs are known to hallucinate, and argues trust decisions need to move to install-time blocking rather than manual diff review.

npm
Mastraslopsquatting

Supply Chain, AI Security· Added 3 Sep 2026, published 25 Jun 2026

huntress.comwriteup🛡️ Security

Inside Kali365, a Device Code Phishing Ecosystem | Huntress

Huntress SOC investigation into Kali365 (also seen as Octopi365/Freedom365), an AI-enabled Phishing-as-a-Service kit that abuses the Microsoft device-code authentication flow to steal M365 tokens and maintain persistent mailbox access even after password resets. The writeup dissects three panel editions (base AiTM/device-code capture, a post-compromise BEC/fraud module using Claude for drafting wire-transfer scam replies, and a self-service reseller tier with crypto billing via OxaPay), and reverse-engineers the companion Electron desktop apps OctoLink Live and OctoLink Sender, which exchange stolen refresh tokens for real ESTSAUTH session cookies to drive undetected Graph mail-sending and admin-portal access — tactics overlapping with Microsoft's Storm-2372 reporting. Includes IoCs and a KQL hunting rule for detecting device-code abuse.

Microsoft 365OAuthCloudflare Workers+3
Kali365Octopi365Freedom365+5

Threat Intel, Identity & Access, Blue Team & Detection· Added 3 Sep 2026, published 11 Jun 2026

opensourcemalware.comarticle🛡️ Security

The Pros and Cons of NPM v12's Security Improvements

An analysis of npm v12 (shipping ~July 2026, previewable on npm 11.16.0+), which flips three dangerous defaults to deny-by-default: automatic preinstall/install/postinstall lifecycle scripts, git dependencies (now requiring --allow-git), and remote HTTPS tarball dependencies (now requiring --allow-remote). The author, a DEF CON speaker on install-script abuse, argues the changes are genuinely good but warns that widespread legitimate use of install scripts (esbuild, sharp, core-js, puppeteer, node-gyp native builds) will drive developers toward reflexive npm approve-scripts approval, and that attackers will simply relocate payload execution outside npm's visibility (curl|bash in install.js, bootstrap binaries), citing DPRK actors' continued abuse of VSCode tasks files even after Microsoft disabled task.allowAutomaticTasks by default. It also surveys complementary controls gaining traction across the ecosystem: npm's min-release-age cooldown (following pnpm's minimumReleaseAge, Yarn's npmMinimalAgeGate, and Bun) and package-firewall products (Datadog's supply-chain-firewall, Liran Tal's npq, Socket, Aikido, Endor Labs).

npmVS Codepnpm+3
DPRKLiran Tal

Supply Chain· Added 3 Sep 2026, published 10 Jun 2026

stepsecurity.ioarticle🛡️ Security

New in the Threat Center: Compromised Components, Now Available via API

StepSecurity added a GET /github/{owner}/threat-intel/incidents/{incidentId}/compromised-components API endpoint to its Threat Center, returning structured data (package ecosystem, version, severity, verified status) for OSS components tied to a detected supply-chain compromise incident. It's positioned as the automatable counterpart to existing Threat-Intelligence detection events (SIEM/Slack/webhook alerts), PR-level compromised-package checks, and the Secure Registry, letting teams pull exact affected packages/versions on demand to drive incident response and cross-check against their SBOM or lockfiles.

StepSecuritySIEMSBOM
tj-actions/changed-files

Supply Chain, Threat Intel, DevSecOps· Added 3 Sep 2026, published 9 Jun 2026

opensourcemalware.comarticle🛡️ Security

The Software Supply Chain Malware Landscape: January - May 2026

OpenSourceMalware analyzes its threat database (166,000+ records) to surface three supply-chain malware trends for Jan 1-May 18 2026: npm and PyPI malicious-package growth is now tracking at similar velocity (driven by dual-ecosystem campaigns like Contagious Interview and a Telegram-exfiltration infostealer cluster), account takeovers (led by TeamPCP's Trivy compromise and Mini Shai-Hulud campaign) are rising but coexist with more surgical dependency-confusion/typosquat attacks like Stardrop and events-channel, and malicious ClawHub AI-skill submissions (707 analyzed) increasingly target non-developer roles such as marketing and sales alongside the usual crypto and developer victims. The piece uses download-count as a proxy to distinguish ATO from born-bad malicious packages and highlights under-monitored non-engineer credential exposure as an emerging risk.

npmPyPIaxios+2
TeamPCPMini Shai-HuludContagious Interview+4

Supply Chain, Threat Intel, AI Security· Added 3 Sep 2026, published 3 Jun 2026

github.comrepo🛡️ Security

Bumblebee

Bumblebee is a single-binary, read-only inventory scanner for macOS/Linux developer endpoints that parses lockfiles, package-manager metadata, extension manifests, and MCP JSON configs into structured NDJSON component records. Given an exposure catalog (exact ecosystem/name/version matches), it emits finding records so responders can quickly answer "which machines have this compromised package right now" during a supply-chain incident, without executing package managers or reading source files. It ships baseline/project/deep scan profiles, a built-in selftest against embedded fixtures, and maintained threat-intel exposure catalogs built from public supply-chain campaign reporting.

GonpmPyPI+2
Perplexity Computer

Supply Chain, Blue Team & Detection· Published and added 24 May 2026

socket.devarticle🛡️ Security

Socket: Mini Shai-Hulud

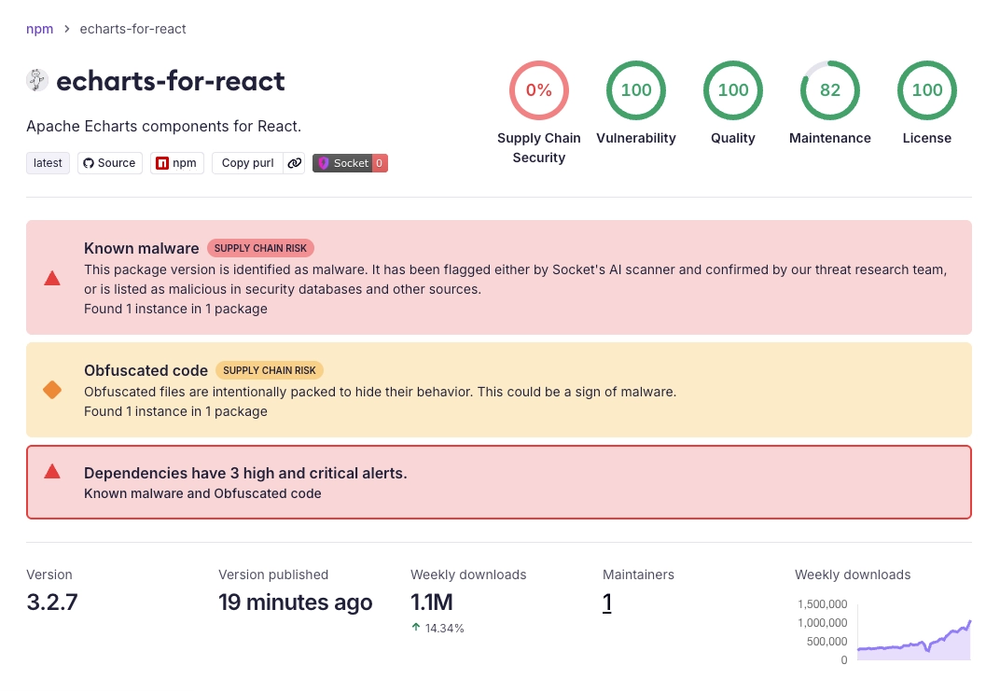
Socket reports that npm invalidated all granular access tokens with write access that bypass 2FA after a fresh Mini Shai-Hulud wave hijacked the maintainer account "atool" and pushed 639 malicious versions across 323 packages in the @antv ecosystem, including echarts-for-react. The piece traces the broader campaign (attributed to TeamPCP, 1,055 compromised versions across npm/PyPI/Composer) through the TanStack pwn-request/OIDC-memory-extraction compromise and the resulting GitHub internal repo breach via Nx Console, and covers npm's new opt-in staged-publishing feature (npm stage publish/approve) that adds an MFA-gated human approval step before releases go live.

npmOIDCGitHub Actions+2
Mini Shai-HuludTeamPCPatool+8

Supply Chain, DevSecOps, Identity & Access· Published and added 22 May 2026

huntress.comwriteup🛡️ Security

Inside the RaaS Ecosystem: Operators, Affiliates & Attack Tradecraft | Huntress

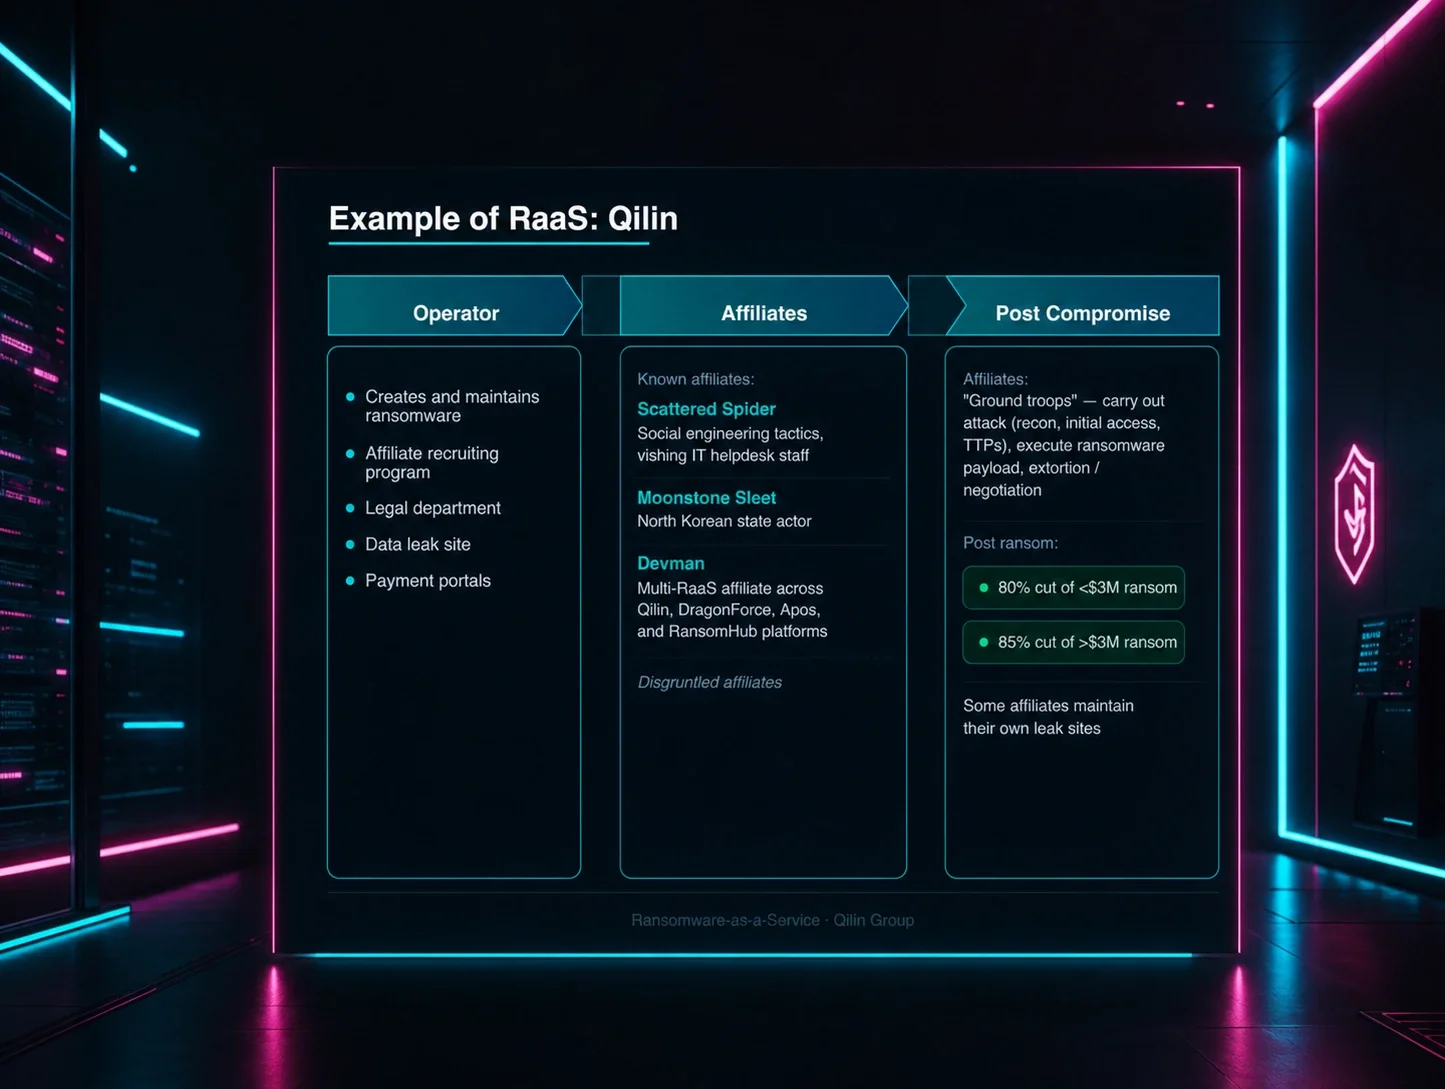
Huntress breaks down the ransomware-as-a-service (RaaS) ecosystem, explaining how operators (e.g., Qilin) provide the malware and infrastructure while diverse affiliates (Scattered Spider, Moonstone Sleet, Devman) handle intrusion, meaning the same ransomware brand can involve very different attack chains. It details real-world tradecraft: initial access via RDP abuse, vulnerable edge appliances like SonicWall VPNs (preceding Akira deployment), and rogue RMM tools (ScreenConnect, TeamViewer, Bomgar), plus persistence via hidden user accounts and RMMs like AnyDesk/Chrome Remote Desktop, defense evasion via EDR/AV killers and BYOVD, and exfiltration using 7-Zip, MegaSync, RClone, S5cmd, and finger.exe.

SonicWallScreenConnectTeamViewer+3
AkiraQilinLockBit+3

Threat Intel· Added 3 Sep 2026, published 20 May 2026

socket.devwriteup🛡️ Security

Socket: Mini Shai-Hulud Hits @antv Ecosystem

Socket's Threat Research team documents a Mini Shai-Hulud variant compromising the npm maintainer account "atool," affecting @antv data-visualization packages (g2, g6, x6, l7, s2, f2, graphin) plus echarts-for-react (~1.1M weekly downloads) and others, totaling 639 compromised versions across 323 packages in one wave (1,055 versions/502 packages campaign-wide across npm, PyPI, and Composer). The install-time payload (triggered via a preinstall "bun run index.js" hook) is heavily obfuscated, harvests GitHub/npm/AWS/Kubernetes/Vault/SSH credentials and CI/CD secrets, exfiltrates data via AES-256-GCM+RSA-OAEP encrypted HTTPS to t.m-kosche[.]com and via GitHub repo commits under a reversed "Shai-Hulud: Here We Go Again" marker, and self-propagates by using stolen npm tokens to republish trojanized packages with a malicious @antv/setup GitHub optionalDependency.

npmBunGitHub+3
Mini Shai-HuludShai-Huludt.m-kosche.com+3

Supply Chain, Threat Intel· Published and added 20 May 2026

github.blogother🛡️ Security

Dependabot & Code Scanning: Org-Level Private Registries

GitHub changelog entry describing a new capability where organizations can register multiple private registries per ecosystem (npm, Maven, NuGet, Docker, pip, RubyGems, etc.) at the org level for both Dependabot and code scanning, instead of being limited to one registry per ecosystem type. It also adds OIDC-based authentication support (via UI and REST API) for Azure DevOps Artifacts, AWS CodeArtifact, and JFrog Artifactory, available now on github.com/GHEC and coming to GHES 3.24.

DependabotGitHub Advanced SecurityOIDC+3

DevSecOps, Supply Chain· Added 3 Sep 2026, published 13 May 2026

kenhuangus.substack.comwriteup🛡️ Security

OpenClaw MAESTRO

A researcher applies the MAESTRO 7-layer agentic AI threat model (Foundation Models, Data Operations, Agent Frameworks, Deployment/Infra, Evaluation/Observability, Security & Compliance, Agent Ecosystem) to the OpenClaw messaging-bot agent codebase, cataloging ~30 numbered threats with specific file references (e.g. prompt injection via WhatsApp/Telegram/Discord channels in src/channels/, plaintext credential storage in pairing-store.ts, Docker socket exposure in sandbox configs, gateway loopback-binding bypass, ClawHub skill registry poisoning) alongside existing and recommended mitigations. It closes with a cross-layer chained attack scenario (gateway compromise → session store poisoning → context manipulation → sub-agent hijack → ecosystem spread) illustrating defense-in-depth across layers.

OpenClawDockerNode.js+1
MAESTRO FrameworkClawHub

AI Security· Published and added 6 May 2026