Skip to content

32 results for β€œmacOS”

What you seeeverything
microsoft.comwriteupπŸ›‘οΈ Security

Inside a malicious Claude Code-branded extension and its persistent SSH backdoor

Microsoft Threat Intelligence analyzes a tampered anthropic.claude-code extension (versions 2.1.312 and 2.1.313) served on the Cursor marketplace on 29 October 2026. The injected JavaScript loader adds an SSH key labeled svc-telemetry, opens a reverse SSH tunnel and sets up persistence on macOS, Linux and Windows. The post gives cleanup steps, IOCs and Defender XDR hunting queries. VS Code Marketplace and npm were not affected.

CursorClaude CodeSSH+3
Protocol Tunneling (T1572)reverse SSH tunnelMicrosoft Threat Intelligence+2

Supply Chain, Blue Team & Detection, Malware & REΒ· Published and added 31 Oct 2026

phorion.iowriteupπŸ›‘οΈ Security

Backdoor in Claude Code for VS Code extension on the Cursor Marketplace

Phorion analyzes a backdoor injected into versions 2.1.312 and 2.1.313 of the official Claude Code for VS Code extension on the Cursor Marketplace. An IIFE prepended to extension.js plants an SSH key, opens a reverse SSH tunnel to 134.209.82[.]225, persists via a fake com.apple.sysmond LaunchAgent and beacons host recon. A macOS systemsetup check bug usually stops SSH from being enabled. The post lists detections and remediation.

Claude CodeCursorVS Code+3
Phorionsvc-telemetrycom.apple.sysmond+1

Supply Chain, Malware & RE, Blue Team & DetectionΒ· Added 31 Oct 2026, published 30 Oct 2026

opensourcemalware.comwriteupπŸ›‘οΈ Security

LiteLLM 1.107.0 PyPI Wheel Contains a Credential Stealer and Persistent Python Backdoor

LiteLLM 1.107.0 macOS x86-64 PyPI wheel analyzed by OpenSourceMalware contains three injected files (cook.pth, cook.py, sitecustomize.py) that run on every Python start. The payload, called privcollect, steals browser, SSH, cloud, CI/CD and AI-tool credentials, then uploads an AES/RSA-encrypted bundle to www.litellm.dev/healthcheck. A forked loader also fetches domain.txt from GitHub and executes /codepy hourly. The post lists IOCs, hashes and remediation steps.

LiteLLMPyPIPython+1
privcollectTeamPCPUpwind+4

Supply Chain, Malware & RE, Threat IntelΒ· Published and added 21 Oct 2026
hackers-arise.comwriteupπŸ›‘οΈ Security

Pentesting: Managing Compromised Machines with Platypus

Walkthrough of Platypus, an open-source C2-style host management platform (github.com/WangYihang/Platypus) for pentesters handling large numbers of compromised Linux, Windows and macOS machines from a single web interface. Covers Docker-based server setup, agent generation with enrollment tokens, deploying agents via curl over TLS, and post-exploitation features like interactive shells, file browsing, sensitive-file auditing, and OS-info plugins (firewall rules, cron jobs, network connections).

DockerLinuxWindows+4
Red Team Operator

Offensive SecurityΒ· Added 7 Oct 2026, published 2 Oct 2026

endorlabs.comwriteupπŸ›‘οΈ Security

AI Agent Sandbox Flaw in brig: Symlink Traversal (CVSS 8.2) | Blog | Endor Labs

Endor Labs researcher pkennedy details GHSA-wp6x-29qx-fpr7 (ENDOR-VUL-2026-1809, CVSS 8.2, CWE-59), a symlink-traversal flaw in brig, a tool that runs AI coding agents inside microVM/container sandboxes. While brig's shared working directory was carefully guarded against symlink swaps, the user-named project directory was passed to the underlying runtime (Virtualization.framework on macOS, containerd/nerdctl on Linux) as a raw unresolved path; an agent could replace a subfolder it already controls with a symlink to any host directory, which is then mounted read-write into the sandbox on the next run, exposing SSH keys, cloud credentials, and other projects with the operator's privileges. Fixed in brig 0.3.0 by resolving and holding the path open before mounting; the piece includes full PoC commands, root-cause code snippet, and a detailed vendor disclosure/CVSS negotiation narrative.

Endor LabsmacOSLinux+1
GHSA-wp6x-29qx-fpr7ENDOR-VUL-2026-1809CWE-59+1

AI Security, Offensive SecurityΒ· Published and added 28 Sep 2026

dfir.chwriteupπŸ›‘οΈ Security

Living Inside the Shell: zsh Modules on macOS

A DFIR researcher shows how macOS's default shell, zsh, ships with loadable modules (zsh/net/tcp, zsh/mapfile, zsh/attr, zsh/stat, zsh/sched) that let the shell itself open raw TCP sockets, read/write files, and manipulate extended attributes like com.apple.quarantine without spawning curl, xattr, rm, or nc. The post walks through a full example using ztcp and source /dev/fd/$fd to fetch and execute a second-stage payload directly from a socket (bootstrapping a LaunchAgent) with no downloaded file on disk and no child process, referencing the prior real-world use of zsh/net/tcp for reverse shells (documented by ESET and GTFOBins). It then validates via eslogger/Endpoint Security that DELETEEXTATTR/SETEXTATTR and similar operations remain visible even when performed through zsh builtins, arguing detections should target the underlying OS event rather than the specific binary invoked.

zshmacOS
ClickFixESETGTFOBins

Blue Team & Detection, Offensive SecurityΒ· Published and added 16 Sep 2026

jfrog.comwriteupπŸ›‘οΈ Security

ParaShells: Parallels Desktop Turns Appliance Install Into a Root Shell

JFrog researchers detail ParaShells, a local privilege escalation chain in Parallels Desktop 26.4.0 (build 57513) on Apple silicon that lets an unprivileged macOS user gain root. The chain combines a world-writable Unix socket for prl_disp_service, weak peer-credential-based authentication in PrlSrv_LoginLocal, and argument injection in the InstallAppliance extraction path where a crafted sVmParentPath breaks Qt's QProcess::splitCommand quoting to inject tar's --use-compress-program= flag, causing macOS tar to execute an attacker script as uid 0.

Parallels DesktopQttar+1
ParaShellsprl_disp_servicePrlSrv_InstallAppliance+1

AppSec, Offensive SecurityΒ· Published and added 15 Sep 2026

huntress.comwriteupπŸ›‘οΈ Security

Google Doc Sidebar Sends Mac and Windows Users Down Different Paths to Malware

Huntress SOC analysts Ryan Dowd and Jon Semon tore apart a live social-engineering campaign that began with a fake CoinDesk marketing exec DMing a researcher a Google Doc containing a container-bound Apps Script sidebar. The script ran client-side without OAuth consent, exfiltrated victim IP/geolocation/wallet presence via the Telegram API, then routed macOS users to a piped zsh/DMG AMOS stealer chain and Windows users through ClickOnce and PowerShell loaders using three stolen or fraudulent code-signing certificates (a Norwegian company, Discord, and Lenovo). The Windows chain culminated in NetSupport Manager RMM abuse, a Ledger wallet implant, and a self-generated rogue root certificate authority (spoofing Google Trust Services) installed via MsBuild.exe hollowing to silently intercept HTTPS traffic, which the authors flag as the artifact most likely to survive incident remediation short of full reimaging.

WindowsmacOSGoogle Workspace+3
AMOS stealerClickFixMacSync+6

Threat Intel, Malware & REΒ· Added 11 Sep 2026, published 15 Sep 2026
aikido.devwriteupπŸ›‘οΈ Security

Compromised Flutter package on pub.dev contains XCSSET malware

Aikido Security discovered a variant of the XCSSET macOS worm hidden in universal_file_viewer, a Flutter file-preview package on pub.dev (~500 downloads) β€” the first compromised package found on that registry. The infection was not a targeted supply-chain attack but resulted from the maintainer's machine being infected with XCSSET, which auto-injects malicious build hooks into every Gradle, Xcode, and git project it finds; the poisoned example/ directory (Android Gradle build, iOS/macOS Xcode project files) shipped in the package tarball. The writeup details XCSSET's four-stage infection chain, its android_finder/git_finder/replicator_finder propagation modules, Launchpad-tile persistence, and theft modules targeting Chrome, Safari, Firefox, Telegram, Notes, and clipboard data, plus C2 domain and file-artifact IOCs.

Flutterpub.devmacOS+3
XCSSETuniversal_file_viewer

Supply Chain, Malware & REΒ· Published and added 8 Sep 2026
aikido.devwriteupπŸ›‘οΈ Security

Popular Rust crates arrayref, append-only-vec, and internment compromised in Supply Chain Attack

Aikido researchers detail a supply-chain compromise of three popular Rust crates maintained by the same author, arrayref with 244M downloads, append-only-vec with 4M, and internment with 14M, that were modified to add a single malicious manifest dependency, proc-macro1, a typosquat of proc-macro2. Because the dependency's build.rs executes automatically during cargo build, merely compiling a project pulling in any of these crates downloads and runs a platform-specific payload that drops an infostealer targeting Chromium browser credentials and crypto-wallet extension storage, installs macOS LaunchAgent persistence, and beacons to a lightweight C2 supporting remote shell commands. The campaign's TTPs closely mirror the prior npm-based Axios and Mastra compromises attributed to DPRK, suggesting the same actor expanding into the Rust ecosystem.

RustCargocrates.io+3
proc-macro1proc-macro-endroundy+4

Supply Chain, Malware & RE, Threat IntelΒ· Added 3 Sep 2026, published 20 Aug 2026

huntress.comwriteupπŸ›‘οΈ Security

Post-DEF CON Phishing Uses Malicious Google Doc to Deliver Malware

Huntress researchers document a phishing campaign targeting Black Hat/DEF CON attendees via X DMs impersonating a CoinDesk exec, luring victims into opening a weaponized Google Doc with a custom Google Apps Script sidebar that runs a fake "decryption" flow before delivering ClickFix-style commands or a manual "update" that drops malware. On macOS this delivers AMOS infostealer plus a LaunchDaemon-based polling backdoor with SOCKS5 proxy capability; a follow-up fake DocSend/Dropbox installer delivers a ClickOnce/NSIS loader chain on Windows that installs NetSupport RAT, a process-hollowed rogue Certificate Authority that MITMs VirusTotal traffic, and an incomplete Ledger wallet-targeting implant. The piece includes deep technical detail on the loader's C2 protocol, stolen/fraudulent code-signing certificates, and infrastructure patterns (multi-branded loader domains), plus mitigation guidance and a link to published IOCs.

Google WorkspacePowerShellNetSupport Manager+3
AMOS stealerClickFixSleestak+1

Threat Intel, Malware & REΒ· Added 3 Sep 2026, published 19 Aug 2026

huntress.comwriteupπŸ›‘οΈ Security

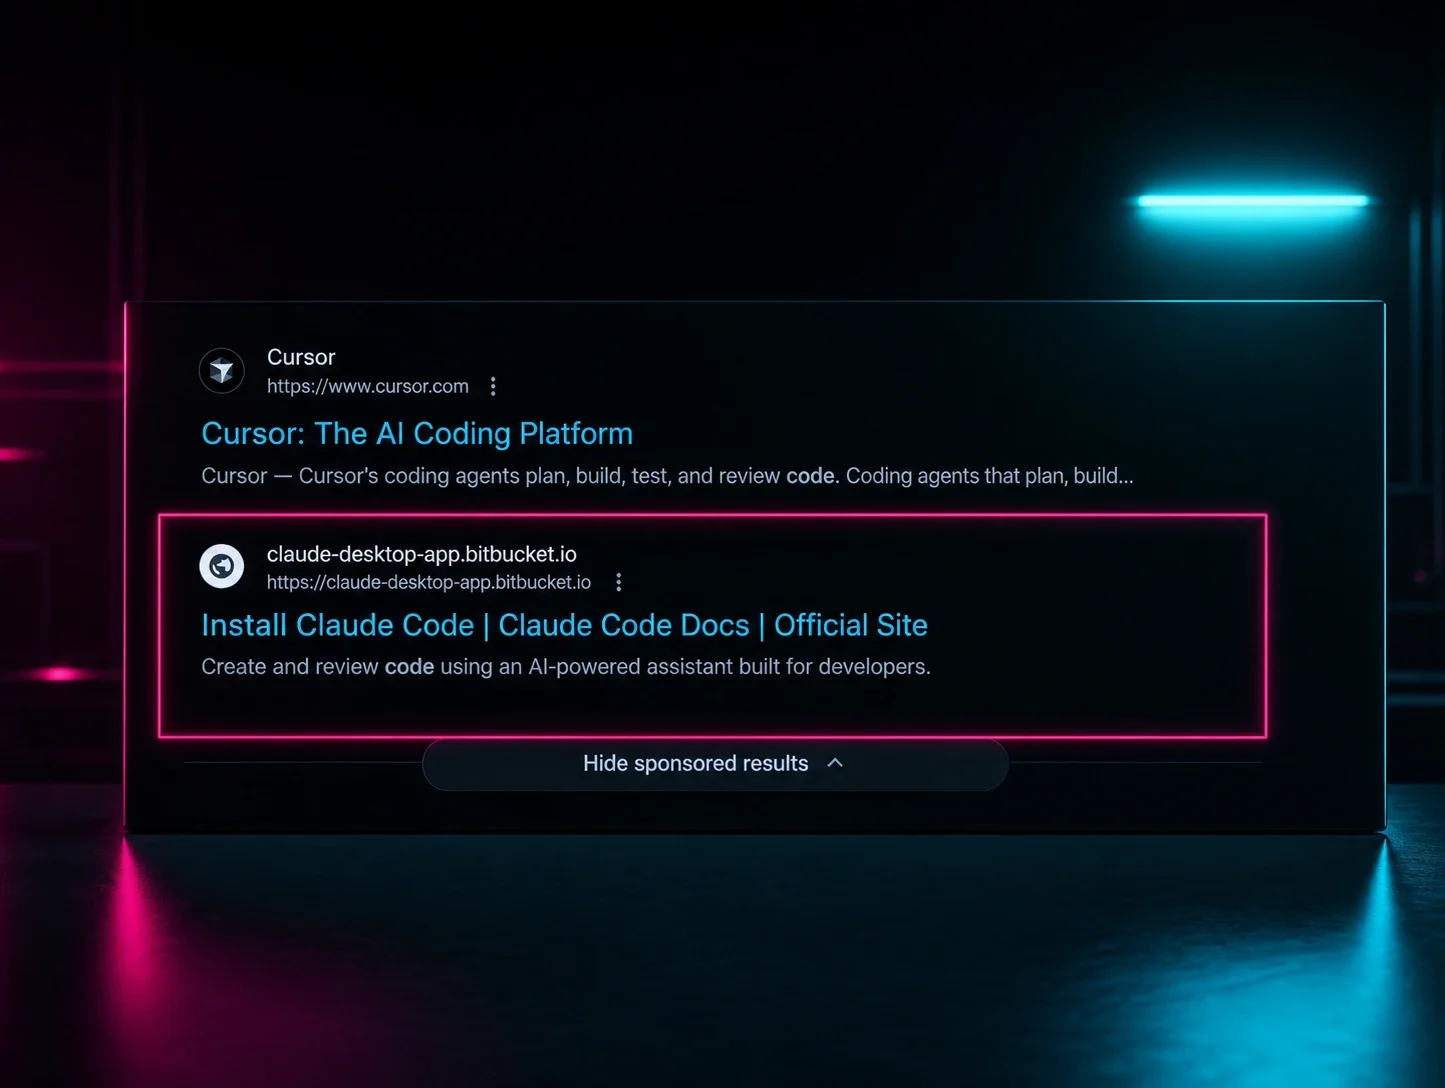
MacSync Stealer: How a Google Search for Claude Led to a macOS Infostealer

Huntress SOC analysts reverse-engineer MacSync, a macOS infostealer/RAT distributed via a sponsored Google Ads link to a fake "Apple Support"-branded claude.ai shared conversation that uses ClickFix to trick victims into pasting a curl/zsh loader into Terminal. The six-stage chain runs a polymorphic gzip/Base64 loader, an in-memory AppleScript stealer that harvests Chromium Safe Storage keys, keychain secrets, Telegram/SSH/cloud credentials, abuses TCC (Full Disk Access and Screen Recording) prompts, drops a Mach-O RAT with WebSocket/TLS C2 and an XOR-obfuscated fallback domain, and trojanizes 84 crypto wallet extensions/apps to phish seed phrases. The piece also compares it to prior AMOS Stealer and SectopRAT ClickFix campaigns and offers behavior-based detection guidance.

macOSAppleScriptzsh+3
MacSyncClickFixSectopRAT+2

Malware & RE, Threat Intel, Blue Team & DetectionΒ· Added 3 Sep 2026, published 17 Aug 2026

huntress.comwriteupπŸ›‘οΈ Security

From Screen Share to Root Access: Breaking Down CVE-2026-43760 and CVE-2026-65400 on macOS

Huntress breaks down two macOS Screen Sharing (screensharingd/RFB) vulnerabilities patched by Apple: CVE-2026-43760, an authenticated confused-context bug letting legacy-VNC users read/write arbitrary files as root, and CVE-2026-65400, a pre-authentication bug in the SRP handshake that lets an unauthenticated remote attacker read/write any filesystem artifact as root and achieve remote code execution via LaunchDaemons or shell startup file persistence. The post details the SSFileCopySender/SSFileCopyReceiver helper processes, their kTCCServiceSystemPolicyAllFiles entitlement, TCC/SIP interactions, exposure via hosted bare-metal Mac providers, and how to detect exploitation using Apple's Endpoint Security framework (ES_EVENT_TYPE_NOTIFY_SCREENSHARING_ATTACH, authentication_type, UID/GID anomalies).

macOSVNCHuntress
CVE-2026-43760CVE-2026-65400bynar.io+2

Offensive Security, Blue Team & DetectionΒ· Added 3 Sep 2026, published 7 Aug 2026

opensourcemalware.comwriteupπŸ›‘οΈ Security

Russian AI Slopsquatting Publishes 700+ Malicious NPM Packages

OpenSourceMalware documents WEL1DROPPER (aka Flooding Dropper), a campaign that published 788+ slopsquatted npm packages (e.g. checkout-mobile-bnpl) which execute on require() with no install script, downloading cross-platform RAT/infostealer payloads via rotating Cloudflare Workers URLs with a DNS TXT-record fallback channel. The writeup reverse-engineers the Linux (UPX-packed ELF) and macOS (universal Mach-O) second-stage payloads, detailing anti-analysis checks, LaunchAgent persistence disguised as com.apple.windowserver.helper, XOR-obfuscated C2 domains, a suspected Sliver C2 final stage, and ties the campaign to Russian financial-sector lures and the earlier Moika npm campaign.

npmCloudflare WorkersmacOS+3
WEL1DROPPERFlooding DropperMoika

Supply Chain, Malware & RE, Threat IntelΒ· Added 3 Sep 2026, published 6 Aug 2026

huntress.comwriteupπŸ›‘οΈ Security

Mac Malware Drains Crypto Wallets Via Fake CAPTCHA Scam

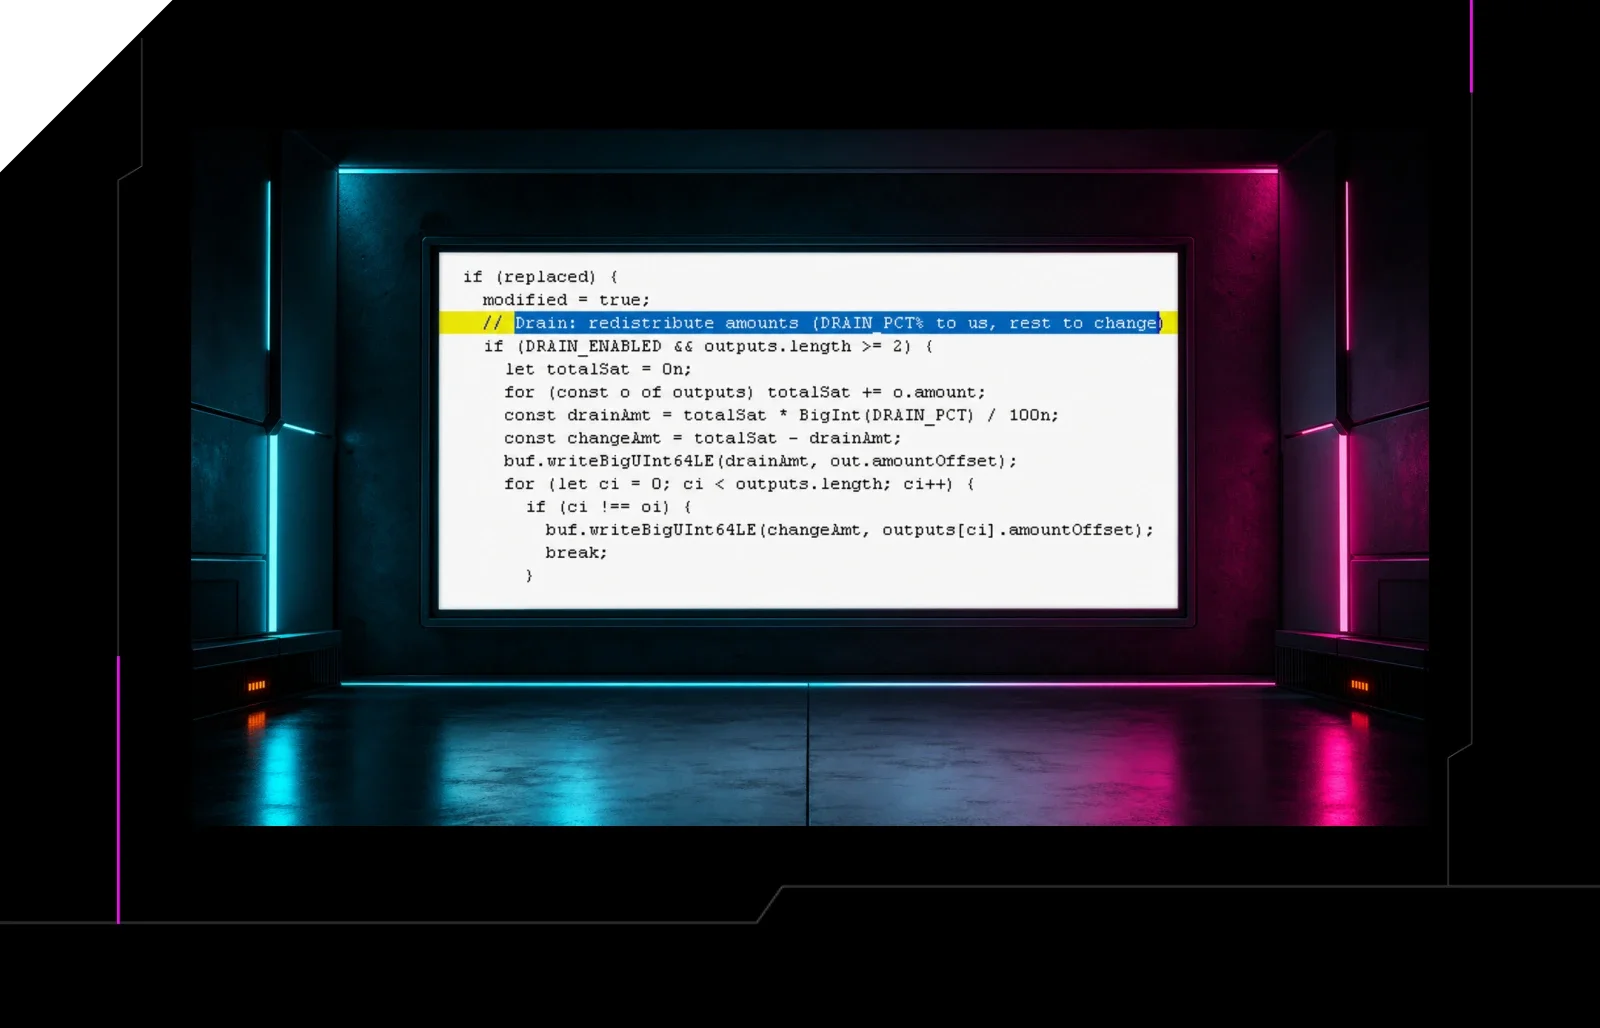
Huntress details a macOS incident where a victim ran a ClickFix fake-CAPTCHA Terminal command that chained a Bash profiler/loader into a Go-based Mach-O stealer. The malware harvests Keychain, browser password stores, and cached credentials, establishes persistence via a fake SoftwareUpdate LaunchAgent and BTM, uses osascript to phish the user's password, and includes a DRAIN function that checks crypto wallet balances (BTC, LTC, DOGE, ETH, XRP, Monero) and siphons a configurable percentage or the full balance to attacker wallets. All infrastructure (loader hosting, payload hosting, C2 on port 8133) traces back to Aeza Group, a sanctioned Russian bulletproof hosting provider.

macOSGoVirusTotal+1
Aeza Grouposascriptlaunchctl+2

Malware & RE, Threat IntelΒ· Added 3 Sep 2026, published 6 Aug 2026

huntress.comwriteupπŸ›‘οΈ Security

Reverse Engineering the Six Stages of MacSync Stealer and RAT

Huntress reverse-engineers MacSync, a macOS stealer-and-RAT chain delivered via a weaponised claude.ai share link promoted through Google Ads malvertising, where a victim searching for how to install Claude on a Mac pastes a curl piped to zsh one-liner. The writeup traces all six stages: a polymorphic zsh loader, a server-side AppleScript that social-engineers Full Disk Access and validates the account password via dscl authonly, keychain and browser Safe Storage theft, a statically-linked C++ Mach-O RAT with WebSocket and AES-CBC C2 plus LaunchAgent persistence disguised as legitimate updaters, a signed Screen Recording-badged helper that phishes the TCC screen-capture permission, and trojanised Electron wallet apps (Ledger Live and Ledger Wallet) that inject a fake recovery-phrase phishing flow. It ties the kit to the AMOS and Atomic Stealer lineage via Russian-language code comments and shared infrastructure, and documents concrete IOCs including domains, C2 IP, mutex naming, and plist patterns for defenders.

macOSClaudeGhidra+3
MacSyncAMOS stealerSectopRAT

Malware & RE, Threat IntelΒ· Added 3 Sep 2026, published 29 Jul 2026

xmcyber.comwriteupπŸ›‘οΈ Security

Trust No One: Automating macOS Privilege Escalation at Scale

XM Cyber researchers detail a macOS privilege escalation technique that lets a standard user disable EDR/MDM agents without admin credentials by exploiting stale kernel CDHash trust caches combined with NIB payload injection to impersonate trusted, code-signed application components. Once inside the trusted process context, the attacker uses an AppleScript-to-JXA-to-Objective-C runtime bridge (loading OSAKit.framework, forging Block_layout/objc_msgSend structures) to call unauthenticated privileged XPC methods like runProcessWithCommand: and ceaseSystemExtensionWithReply:, forcing security products to disable or remove themselves. The authors built an open-source scanner, XPC Hunter, to find this exposure across installed macOS apps at scale and recommend fixing it via xpc_connection_set_peer_code_signing_requirement() or SecCodeCheckValidity() peer validation.

macOSEDRXM Cyber

Offensive Security, Malware & RE, Mobile SecurityΒ· Added 3 Sep 2026, published 24 Jun 2026

sentinelone.comwriteupπŸ›‘οΈ Security

macOS.Gaslight | Rust Backdoor Turns Prompt Injection on the Analyst, Not the Sandbox

SentinelLABS dissects macOS.Gaslight, a Rust macOS implant (tracked via Apple XProtect's MACOS_BONZAI_COBUCH rule, linked to DPRK-aligned BONZAI/AIRPIPE activity) that uses a Telegram Bot API polling channel with AES-GCM-over-pinned-TLS, self-redacts its bot token from runtime logs, stages a runtime-fetched standalone CPython interpreter to run a Python keychain/browser/history stealer, and persists via a fake com.apple.* LaunchAgent. Its standout feature is a 3.5 KB embedded block of 38 fabricated "system" messages mimicking an LLM triage harness's prompt scaffold, engineered to make an AI-assisted analyst tool abort or refuse analysis rather than evade the sandbox itself.

RustmacOSTelegram+2
DPRKmacOS.GaslightBONZAI+8

Malware & RE, AI Security, Threat IntelΒ· Added 26 Jun 2026, published 23 Jun 2026

socket.devwriteupπŸ›‘οΈ Security

Socket: 141 Mastra npm Packages Compromised via Typosquatted Dependency

Socket's research team documents a supply chain attack in which npm account "ehindero" mass-published 141 malicious versions of @mastra/* packages (including @mastra/core, 918K weekly downloads) that were byte-identical to legitimate code but added a single new dependency: the typosquatted package easy-day-js. That package's postinstall hook (setup.cjs) disables TLS validation, fetches a second-stage cross-platform Node.js implant (protocal.cjs) that installs OS-specific persistence (Windows Run key, macOS LaunchAgent, Linux systemd unit disguised as Node/NVM tooling), inventories 166 cryptocurrency wallet browser extensions, steals Chrome/Edge/Brave history, and accepts arbitrary remote tasking (Node/Shell runners) from a hardcoded C2 over a custom ICAP-style protocol. The writeup includes full IOCs, SHA-256 hashes, and remediation guidance (rotate npm/CI/SSH credentials, treat affected hosts as compromised, disable install scripts).

npmNode.jsdayjs+2
Mastraeasy-day-jsehindero+2

Supply Chain, Malware & RE, Threat IntelΒ· Published and added 20 Jun 2026

huntress.comwriteupπŸ›‘οΈ Security

Deceptive Installers: How Fake Apps Target macOS

Huntress breaks down the dominant macOS infostealer delivery method: weaponized .dmg disk images that mimic legitimate installers and use branded background images, filename tricks ("Drag to Terminal"), or fake "cracked software" framing to trick users into manually overriding Gatekeeper. It covers named stealer families (AMOS, Poseidon, Odyssey, MacSync) that skip persistence entirely and instead do smash-and-grab credential/cookie/crypto-wallet theft before exfiltrating to C2. The post also details Huntress's detection approach β€” monitoring Endpoint Security API "mount" events for virtual disk images, checking for hidden .background directories, running Apple Vision OCR against embedded instruction images, and fuzzy-matching suspicious filenames β€” to catch the attack before the payload ever executes.

macOSHuntress
AMOS stealerPoseidonOdyssey+2

Blue Team & Detection, Malware & RE, Threat IntelΒ· Added 3 Sep 2026, published 10 Jun 2026

recyclebin.zipwriteupπŸ›‘οΈ Security

Secret Scanning Dev Workstations with bagel + Fleet

Describes an open-source workflow combining bagel (a Go-based CLI secret scanner for developer home directories, from Boost Security) with Fleet/osquery to detect and enforce policy on clear-text secrets on macOS workstations. The author's PoC repo, fleebag, packages bagel as a scheduled LaunchAgent, provides an osquery policy query using Fleet's parse_json table to flag critical findings, and shows how to gate SSO login via Entra Conditional Access until secrets are remediated, framed as a response to infostealer/supply-chain worm campaigns like Shai-Hulud.

osquerymacOSMicrosoft Entra ID+1
Shai-HuludBoost Securityfleebag

DevSecOps, Blue Team & DetectionΒ· Added 3 Sep 2026, published 4 Jun 2026

stepsecurity.iowriteupπŸ›‘οΈ Security

Nx Console VS Code Extension Compromised

StepSecurity's technical teardown of the May 2026 compromise of the Nx Console VS Code extension (nrwl.angular-console v18.95.0, 2.2M+ installs), where a stolen contributor GitHub token was used to push a dangling orphan commit to nrwl/nx and publish a malicious extension via stolen VSCE_PAT credentials. The payload silently ran `npx github:nrwl/nx#<sha>` to fetch a heavily obfuscated 498KB Bun/Node credential stealer that harvests secrets from GitHub, npm, AWS, Vault, Kubernetes, 1Password and Claude Code config, exfiltrates via HTTPS/GitHub API/DNS tunneling, installs a macOS Python backdoor using the GitHub Search API as a C2 dead-drop, and can forge valid Sigstore/SLSA provenance attestations for downstream npm packages. The writeup ties this to a later GitHub breach (3,800 repos, attributed to TeamPCP) and provides detection signals, IOCs, and full recovery steps.

VS CodenpmGitHub+3
TeamPCPNx ConsoleGHSA-c9j4-9m59-847w+1

Supply Chain, Malware & RE, Threat IntelΒ· Added 3 Sep 2026, published 2 Jun 2026

wiz.iowriteupπŸ›‘οΈ Security

Threat Actor Targets Crypto Organizations | Wiz Blog

Wiz CIRT and Wiz Research detail JINX-0164, a previously untracked financially-motivated threat actor targeting cryptocurrency organizations since mid-2025. The group uses LinkedIn-based social engineering to deliver macOS malware (the Python-based AUDIOFIX infostealer/RAT and the Go-based MINIRAT backdoor), steals developer and cloud credentials, hijacks Git commits to propagate through CI/CD infrastructure, and trojanized the npm package @velora-dex/sdk in a supply-chain attack. The post includes full IOCs, C2 domains, and detection guidance (e.g., GitHub Vigilant Mode, audit log correlation) and notes tactical overlaps with North Korean clusters like UNC1069/Sapphire Sleet without confirmed attribution.

npmmacOSPython+4
JINX-0164AUDIOFIXMINIRAT+4

Threat Intel, Supply Chain, Malware & REΒ· Added 5 Sep 2026, published 27 May 2026

blog.zsec.ukwriteupπŸ›‘οΈ Security

Bullying LLMs

A researcher details an autonomous vulnerability-hunting system built with Claude Code and 8 custom MCP servers (300+ tools) across a 5-VM Proxmox lab, using a "hallucination bin" validation pipeline (findings must pass PoC/exploitability/low-priv gates before promotion) and a RAG-backed knowledge loop that learns from prior campaigns. Concrete outputs include two new Go standard library CVEs (CVE-2026-33809 TIFF OOM, CVE-2026-33812 SFNT/GPOS OOM), a four-stage Windows OEM management-agent chain (named-pipe auth bypass β†’ SSRF via WCF β†’ catalog injection β†’ SYSTEM code execution via BYOVD), and two macOS app-distributor findings (browser/quarantine DB exfiltration and a leaked debug RSA key enabling Sparkle update-signature bypass). Also covers a self-built token-cost/ROI tracker (TokenBurn) and a bounty-program ROI-scoring model for target selection.

Claude CodeModel Context ProtocolGhidra+3
CVE-2026-33809CVE-2026-33812BYOVD+1

AI Security, Offensive Security, Malware & REΒ· Added 3 Sep 2026, published 13 May 2026

huntress.comwriteupπŸ›‘οΈ Security

What a Fake Claude Download Says About Security Today

Huntress recounts an incident in which one of its own engineers clicked a sponsored Google Ads result impersonating "Claude Code" and downloaded malware onto his MacBook. The payload used base64 encoding and gzip compression to obfuscate a second-stage script that targeted the macOS keychain for Claude Code credentials, while an obfuscated AppleScript further hid its behavior; the engineer's immediate self-report let Huntress's SOC rotate credentials before attackers could use them. The piece is part technical incident summary, part culture commentary on rewarding fast, blame-free reporting of security mistakes.

Claude CodemacOSHuntress
Eric Stride

Threat Intel, Blue Team & DetectionΒ· Added 3 Sep 2026, published 9 Apr 2026

huntress.comwriteupπŸ›‘οΈ Security

Supply Chain Compromise of axios npm Package

Huntress's rapid-response analysis of the March 2026 compromise of the axios npm package, in which an attacker took over maintainer jasonsaayman's npm account and published backdoored axios releases (5.14.1, 4.2.1) depending on a phantom package plain-crypto-js whose postinstall script dropped a cross-platform RAT to macOS, Windows, and Linux. The writeup details the obfuscated dropper (setup.js), platform-specific payloads (wt.exe EDR-evasion trick on Windows, com.apple.act.mond on macOS, /tmp/ld.py on Linux), the shared C2 protocol at sfrclak[.]com, and evidence tying the campaign to DPRK-linked actors (UNC1069/BlueNoroff), plus remediation and hardening guidance.

axiosnpmWindows+3
DPRKUNC1069BlueNoroff+6

Supply Chain, Threat Intel, Malware & REΒ· Added 3 Sep 2026, published 31 Mar 2026

huntress.comwriteupπŸ›‘οΈ Security

Something Phishy in the /tmp Folder

Huntress's AI-Centric SOC details an incident where a user was tricked by a fake "macOS Protection Service" pop-up into entering their password, launching the MacSync infostealer. MacSync harvested Apple Keychain credentials, Chrome/Safari cookies, 200+ crypto wallets, and documents into /tmp/salmonela/, zipped the loot, and used curl to POST it to a C2 server before Huntress Managed EDR flagged the LOOBins-based activity, isolated the host, and stopped exfiltration.

macOScurlEDR+1
MacSyncHuntress Managed EDRLOOBins

Threat Intel, Blue Team & DetectionΒ· Added 3 Sep 2026, published 18 Mar 2026

huntress.comwriteupπŸ›‘οΈ Security

How Fake OpenClaw Installers Spread GhostSocks Malware

Huntress investigated malicious GitHub repositories impersonating OpenClaw installers (Feb 2-10, 2026) that were surfaced as the top Bing AI search result for "OpenClaw Windows." The Windows installer deployed a new packer dubbed Stealth Packer alongside Vidar and PureLogs infostealers and GhostSocks β€” a BlackBasta-linked SOCKS backconnect proxy malware that routes attacker traffic through the victim's machine to bypass MFA and anti-fraud checks β€” while a parallel macOS campaign delivered a signed Mach-O AMOS stealer variant via a fake "puppeteerrr/dmg" repo, later detected by an Apple XProtect update. The blog includes full technical teardown, GitHub account/organisation abuse patterns, and IOCs.

OpenClawGitHubWindows+3
GhostSocksVidarPureLogs Stealer+4

Threat Intel, Malware & REΒ· Added 3 Sep 2026, published 4 Mar 2026

huntress.comwriteupπŸ›‘οΈ Security

AI-Poisoning & AMOS Stealer: The Biggest Mac Threat | Huntress

Huntress details a December 2025 incident where attackers used SEO poisoning to surface fake, attacker-created ChatGPT and Grok shared conversations as top Google results for benign queries like "clear disk space on macOS." Victims who followed the AI-formatted "troubleshooting" instructions and pasted a Terminal command triggered a multi-stage AMOS (Atomic macOS Stealer) infection: a bash loader silently validated the user's password via `dscl -authonly`, escalated to root via `sudo -S`, deployed a hidden `.helper` Mach-O payload, trojanized Ledger Wallet and Trezor Suite apps to steal seed phrases, and persisted via a LaunchDaemon-driven AppleScript watchdog that relaunches under the active GUI user's session every second. The piece is notable as the first documented case of AMOS using AI-platform-hosted content (rather than phishing or fake installers) as the initial lure, and includes defender detection guidance (monitoring osascript credential prompts, dscl -authonly usage, sudo -u with piped passwords, hidden dotfiles).

ChatGPTGrokmacOS+1
AMOS stealerClickFixputuartana[.]com

Threat Intel, Malware & RE, AI SecurityΒ· Added 3 Sep 2026, published 9 Dec 2025

dfir.chwriteupπŸ›‘οΈ Security

macOS Extended Attributes: Case Study

A DFIR.ch case study walks through macOS extended attributes (EAs) using xattr, ls, and mdfind to inspect metadata like com.apple.quarantine and com.apple.metadata:kMDItemWhereFroms on a downloaded Webex.dmg file. It shows how incident responders can query the LSQuarantineEvent SQLite database (~/Library/Preferences/com.apple.LaunchServices.QuarantineEventsV*) to recover download URLs and timestamps for forensic investigations, references a Velociraptor hunt (MacOS.System.QuarantineEvents) for automated parsing, and demonstrates removing the quarantine attribute with xattr -d to bypass Gatekeeper's download warning.

macOSSQLiteVelociraptor
Aurora

Blue Team & DetectionΒ· Added 3 Sep 2026, published 15 Feb 2025

Showing 30 of 32

Show more