Skip to content

83 results for β€œmicrosoft”

What you seeeverything
microsoft.comwriteupπŸ›‘οΈ Security

Inside a malicious Claude Code-branded extension and its persistent SSH backdoor

Microsoft Threat Intelligence analyzes a tampered anthropic.claude-code extension (versions 2.1.312 and 2.1.313) served on the Cursor marketplace on 29 October 2026. The injected JavaScript loader adds an SSH key labeled svc-telemetry, opens a reverse SSH tunnel and sets up persistence on macOS, Linux and Windows. The post gives cleanup steps, IOCs and Defender XDR hunting queries. VS Code Marketplace and npm were not affected.

CursorClaude CodeSSH+3
Protocol Tunneling (T1572)reverse SSH tunnelMicrosoft Threat Intelligence+2

Supply Chain, Blue Team & Detection, Malware & REΒ· Published and added 31 Oct 2026

microsoft.comwriteupπŸ›‘οΈ Security

From help desk impersonation to AD CS abuse: Investigating ESC1 and ESC8 intrusion paths

Microsoft Threat Intelligence analysis of two human-operated intrusions that began with Teams help desk impersonation and Quick Assist sessions, then diverged at AD CS. Case 1 abused an ESC1 template for privileged certificates and DCSync, with an excluded account later used for Rclone exfiltration. Case 2 used PetitPotam and ESC8 relay to get a domain controller certificate and PKINIT. Includes investigation steps, AD CS hardening and KQL hunting queries.

Active Directory Certificate ServicesMicrosoft TeamsQuick Assist+3
ESC1ESC8PetitPotam+12

Blue Team & Detection, Threat Intel, Offensive SecurityΒ· Published and added 30 Oct 2026

huntress.comwriteupπŸ›‘οΈ Security

Camera Management Software Compromise Leads to Malware Deployment

Huntress investigation of incidents in September and October 2025 where a compromised camera management application (CMS.exe) was the initial access vector. Attackers dropped rs.win32.exe, a reverse shell, and sideloaded modified zlib DLLs (IPHLPAPI.DLL, samcli.dll) via the legitimate Microsoft WpcMon.exe in AppData, with Run key persistence and beaconing to 144.172.116[.]37. Includes detection pivots and hardening advice.

WindowsHuntress
DLL sideloadingCMS.exers.win32.exe+6

Threat Intel, Blue Team & DetectionΒ· Added 28 Oct 2026, published 27 Oct 2026

huntress.comwriteupπŸ›‘οΈ Security

AI, Scripts, Operator: Inside the ConnectWise Attack

Huntress analyzes Entra sign-in and audit logs from the ConnectWise Cloud Backup credential abuse of 15 October 2026 to judge whether a script, a person or an LLM agent drove it. It found a thread-pool spray, trial-and-error credential planting with a retry added within 55 seconds, and pilot-then-batch targeting. Huntress rates LLM involvement low to medium on its own data and medium to high with Microsoft's Storm-0940/ARTEX attribution. It ends with detections for service principal role self-assignment and vendor app baselining.

Microsoft Entra IDMicrosoft 365Microsoft Graph+3
Storm-0940ARTEXConnectWise Cloud Backup credential abuse+7

Threat Intel, Blue Team & Detection, Identity & Access, AI SecurityΒ· Published and added 26 Oct 2026

microsoft.comwriteupπŸ›‘οΈ Security

Inside the LiteLLM 1.107.0 supply chain compromise: Credential theft through Python startup hooks

Microsoft's analysis of the LiteLLM 1.107.0 compromise, published to PyPI and container images on 21 October 2026. The wheel shipped cook.pth, cook.py and sitecustomize.py, so a credential collector (PRIVCOLLECT) ran whenever Python started, even without importing LiteLLM. It covers AES/RSA-encrypted exfiltration to litellm.dev, a re-armable Unix loader, Defender KQL hunting queries, ATT&CK mapping and rotation guidance.

LiteLLMPythonPyPI+3
cook.pthPRIVCOLLECTT1195.001+4

Supply Chain, Blue Team & Detection, Threat IntelΒ· Published and added 23 Oct 2026

huggingface.cowriteup🧠 AI

Turning Database Grading into RL Rewards: Post-Training Agents with ThinkingBox

ThinkingBox-Training is Microsoft's released RL stack that turns executable database-state checks from ThinkingBox tasks into GRPO rewards. Fifty GRPO steps on 187 curated tasks raised Qwen3.8-27B pass@1 from 51.70% to 60.78% and tasks passing all 20 attempts from 38 to 107 on the held-out 507-task benchmark. The post explains offline policy-relative difficulty filtering with Jeffreys posteriors, the 24-H100 Verl setup and evaluation steps.

GRPOQwen3.8-27BVerl+9
MicrosoftThinkingBoxThinkingBox-Bench+11

training, agents, evalsΒ· Published and added 22 Oct 2026

huntress.comwriteupπŸ›‘οΈ Security

M365 Token Spray and Replay Campaign Compromises Business Email Accounts

Huntress analysis of a July to September 2026 token replay ("token spraying") campaign: 497 successful Microsoft 365 sign-ins across 79 organizations, replayed from six addresses in 193.26.115.0/24 (1337 Services GmbH). Tokens came from AiTM relays, device-code phishing and social engineering. It covers four phases, rogue Entra devices, MFA method swaps, hidden inbox rules, hunting queries and Conditional Access guidance.

Microsoft 365Microsoft Entra IDConditional Access+3
token sprayingtoken replayadversary-in-the-middle+9

Threat Intel, Blue Team & Detection, Identity & AccessΒ· Published and added 22 Oct 2026

microsoft.comwriteupπŸ›‘οΈ Security

AI-driven, large-scale nation-state campaign using ARTEX enables supply chain compromise

Microsoft Threat Intelligence report on Storm-0940, a China-state aligned actor that used the open-source agentic AI pentest framework ARTEX from September 2026 to automate attacks on hundreds of organizations. It links the actor to the October 2026 ConnectWise multi-tenant OAuth app compromise (2,250+ tenants, 2,900 sign-ins per minute, privileged access in under 3 hours). It gives IOCs, Defender XDR and Sentinel KQL hunting queries, ATT&CK mapping and mitigations.

Microsoft 365Microsoft Entra IDMicrosoft Defender XDR+3
Storm-0940ARTEXConnectWise Cloud Backup+12

Threat Intel, AI Security, Identity & Access, Blue Team & DetectionΒ· Published and added 21 Oct 2026
huntress.comwriteupπŸ›‘οΈ Security

ConnectWise (SkyKick) Vendor Credentials Abused in M365 Attacks

Huntress documents abuse of ConnectWise Cloud Backup (formerly SkyKick) vendor app credentials, used on October 15 from 144.172.64[.]128 to obtain Microsoft Graph tokens in at least 162 customer M365 tenants via client assertion. In one tenant, a ConnectWise Cloud Management Teams app self-assigned Global Administrator and added client secrets to an MSP management app and Huntress's own app, a persistence technique. The post lists application IDs, Entra sign-in and audit-log checks, user-agent indicators (kiota-dotnet vs Python-urllib/3.12, curl/7.88.1), and mitigation steps such as disabling (not deleting) the enterprise apps and reviewing added credentials.

Microsoft 365Microsoft Entra IDHuntress+1
ConnectWiseSkyKick144.172.64.128+7

Threat Intel, Identity & Access, Blue Team & DetectionΒ· Added 17 Oct 2026, published 16 Oct 2026

dfir.chwriteupπŸ›‘οΈ Security

Field Notes: EtherRAT Distributed Through a Legitimate Intune Workflow

DFIR case where a malicious MSI impersonating Advanced IP Scanner, sourced from a fake GitHub repo found via Bing, was imported by a customer into Microsoft Intune and deployed to four endpoints, running a Node.js-based EtherRAT chain. It traces the infections by correlating the MSI ProductCode, MDMAppInstaller/omadmclient process ancestry and Intune app inventory (Graph PowerShell query). It also covers renamed node.exe hash-hunting pitfalls, Ethereum RPC dead-drop C2 traffic, a screen-capture script and a second impersonating repo.

Microsoft IntuneNode.jsEthereum+3
EtherRATEtherHidingAtos Threat Research Center+4

Blue Team & Detection, Threat Intel, Malware & REΒ· Added 14 Oct 2026, published 13 Oct 2026
embracethered.comwriteupπŸ›‘οΈ Security

Visual Studio Copilot and SSMS Remote Code Execution (CVE-2026-103572)

CVE-2026-103572 is a remote code execution bug in Microsoft.VisualStudio.Copilot.Core.dll, shared by Visual Studio and SQL Server Management Studio. A trailing dot (for example `.mcp.json.`) bypasses the protected-filename check in EditsFunctionHandler.GetEditConfirmationTypeAsync, so a hijacked Copilot can rewrite its own MCP and settings files and run commands. The post covers path traversal and InstallationID leaks, indirect prompt injection demos, the October 2026 patch (GetFullPath), and a $0 bounty.

Visual StudioSQL Server Management StudioGitHub Copilot+3
CVE-2026-103572indirect prompt injectionpath traversal+5

AI Security, AppSec, Offensive SecurityΒ· Added 29 Oct 2026, published 13 Oct 2026

huntress.comwriteupπŸ›‘οΈ Security

Fake WatchGuard VPN Site Steals Credentials

Huntress analyzes an October incident where an admin searching Bing for a WatchGuard VPN download landed on watchguard-vpn[.]net, a lookalike site whose popup.js harvests Server/Login/Password, deliberately rejects the first submission to get a second set, and posts to watchguard-ssl[.]online. Unlike earlier iterations (Secplicity, Microsoft Storm-2561), the final payload is the genuine, validly signed WatchGuard installer from the official CDN, so no malware is present for endpoint tools to flag. Covers infrastructure timeline, thin VirusTotal detections, and defender guidance (MFA, monitoring VPN logins from hosting ASNs, blocking domains, publishing official download links).

WatchGuardVPNHuntress+2
Storm-2561SEO poisoningwatchguard-vpn[.]net+5

Threat Intel, Blue Team & DetectionΒ· Added 14 Oct 2026, published 13 Oct 2026

microsoft.comwriteupπŸ›‘οΈ Security

3 lessons from frontier AI vulnerability research

Microsoft Security's FORGE Lab shares results and lessons from four months of AI-agent-driven vulnerability research: 140 Windows CVEs (52 in September 2026's release), 155 internally validated reports across 23 open-source projects, and the first patch merged into the Linux kernel via the Linux Foundation's Akrites coordinated-disclosure initiative. Using their multi-model agentic scanning harness MDASH and GPT-5.5-based validation agents, the team measured automated PoC generation at an average $3.61/21.5 minutes per confirmed crash and local privilege-escalation AEG at $8.56/25.4 minutes, and argues the real bottleneck has shifted from finding bugs to validating and remediating them at matching speed. Specific disclosed CVEs include curl's CVE-2026-9545 and CVE-2026-13608, Node.js's CVE-2026-56848, and Linux kernel's CVE-2026-64563.

MDASHWindowsLinux kernel+3
CVE-2026-9545CVE-2026-13608CVE-2026-56848+6

AI Security, Offensive Security, AppSecΒ· Published and added 7 Oct 2026

huntress.comwriteupπŸ›‘οΈ Security

Phishing Campaign Abuses Microsoft Power BI to Deploy Rogue RMMs

Huntress details a phishing campaign that abuses legitimate Microsoft Power BI dashboards (app.powerbi.com) to host a fake "Download Reference" lure that bypasses mail filters trusting the Microsoft domain. Clicking the lure triggers browser/environment fingerprinting and Telegram-bot-based victim telemetry exfiltration via attacker domains (dailylifeproject.site, burnsworth.site, etc.), then silently downloads rogue ScreenConnect installers; a chained CMD/PowerShell script (SCAutoFix.ps1) deploys a second ScreenConnect instance, uninstalls the first for evasion, drops the defense-evasion tool HideUL_x64.exe, and sets a recurring scheduled task before Huntress's SOC intervened.

Power BIScreenConnectTelegram+3
HideUL_x64.exeSCAutoFix.ps1SCAutoRepairEvery2Min

Threat Intel, Blue Team & DetectionΒ· Published and added 7 Oct 2026

adversa.aiwriteupπŸ›‘οΈ Security

GitHub Copilot CLI vulnerability: Cryptographic Context Injection steals developer secrets

Adversa AI demonstrates Cryptographic Context Injection (CCI) against GitHub Copilot CLI: a web page presents an "encrypted" payload the agent decrypts inside its own shell, during which it is tricked into reading local files (e.g. .env.prod) to build a fake decryption key, then exfiltrates those contents to an attacker endpoint via a follow-up fetch. The attack only succeeds against certain models in Copilot's auto-routed model pool (Microsoft's mai-code-1.1-flash ran it 50% of the time, while two GPT-5.6 models refused), meaning users have no visibility into which model handles a given session. GitHub's bug bounty team validated but declined to treat it as a vulnerability since the user explicitly invoked autopilot mode with full tool permissions.

GitHub Copilot CLIPythonGPT-5.6
Cryptographic Context Injectionmai-code-1.1-flash

AI SecurityΒ· Added 7 Oct 2026, published 6 Oct 2026

binsec.nowriteupπŸ›‘οΈ Security

Binary Security: Azure Logic Apps cross-tenant compromises (One Root Case)

Third post in a series on Azure Logic Apps API Connections, describing five critical cross-tenant privilege escalations that let an attacker use any other tenant's connection to reach its backend (Key Vault, Azure SQL, Jira, Salesforce). Techniques include path traversal via ARM DynamicInvoke and undocumented DynamicList endpoints, and abusing the host.api.runtimeUrl parameter in Consumption Logic Apps, including a validation-before-normalization bypass. The author reports $200,000 in bounties; Microsoft fixed all issues.

AzureAzure Logic AppsAzure API Management+3
path traversalDynamicInvokeDynamicList+5

Cloud & Infra, AppSec, Offensive SecurityΒ· Added 30 Oct 2026, published 2 Oct 2026

huntress.comwriteupπŸ›‘οΈ Security

Defender Exclusion Abuse: How Attackers Hide Malware from MDAV

Huntress breaks down how Microsoft Defender Antivirus (MDAV) path/extension exclusions can be abused to hide malicious binaries from scans, detailing the registry internals (HKLM...Windows Defender\Exclusions vs the GPO-driven Policies key) and the four ways to set them: PowerShell (Set/Add-MpPreference), the MSFT_MpPreference WMI class, GPO, and direct registry edits. It documents real-world abuse by GootKit (2019), WhisperGate (2022), and Muddled Libra (2024), plus an under-documented trick where setting HideExclusionsFromLocalAdmins blocks even SYSTEM from querying exclusions via PowerShell/WMI, and describes the registry-level telemetry and detections Huntress built to catch both behaviors.

Windows DefenderPowerShellWMI+1
GootKitWhisperGateMuddled Libra+1

Blue Team & Detection, Offensive SecurityΒ· Added 1 Oct 2026, published 30 Sep 2026

microsoft.comwriteupπŸ›‘οΈ Security

Tracking CVE-2026-73570: unauthenticated command injection on internet-facing mail servers

Microsoft Threat Intelligence tracked in-the-wild exploitation of CVE-2026-73570, an unauthenticated OS command-injection vulnerability in Zimbra Collaboration Suite's SNMP notification path (swatchdog-to-snmptrap), triggerable via a crafted SMTP request when the optional zimbra-snmp package is enabled. The post documents pre-disclosure scanning, JSP webshell deployment, a novel pam_exec/zmmailboxdmgr privilege-escalation chain to root, systemd-based persistence (zimlog.service), theft of zimbraPreAuthKey/zimbraAuthTokenKey via zmlocalconfig and LDAP, lateral movement over Zimbra's SSH identity, a multi-stage Go-based remote-access agent (zimclient2 via zimdown2/agent2.sh), a dedicated mailbox-exfiltration implant, and an AzCopy-based exfiltration attempt, closing with Defender XDR KQL hunting queries and MITRE ATT&CK mapping.

ZimbraMicrosoft Defender XDRMicrosoft Defender+3
CVE-2026-73570ChopperGodzillaWebShell+7

Threat Intel, Blue Team & Detection, AppSecΒ· Added 1 Oct 2026, published 30 Sep 2026

blog.talosintelligence.comwriteupπŸ›‘οΈ Security

China-nexus UAT-11587 targets government and policy organizations across Asia with Antino backdoor

Cisco Talos details UAT-11587, a China-nexus threat cluster targeting government, defense, and policy organizations across Taiwan, India, the Philippines, Cambodia, and other Asian countries with spear-phishing and a five-stage infection chain (HTA/WSF stagers, JScript decryptors, .NET BinaryFormatter/ActivitySurrogateSelector deserialization gadgets, and DLL sideloading via the signed GatherOsState.exe) to deploy a new Rust-compiled backdoor called Antino. Antino uses Microsoft Graph/Outlook/OneDrive as a dead-drop C2 channel instead of a traditional C2 server, supports shell/PowerShell execution, file transfer, shellcode loading with a sleep-mask evasion technique, and abuses the Windows Scripted Diagnostics framework for persistence; Talos also notes possible infrastructure overlap with Symantec's "Jewelbug" cluster and Arctic Wolf's UNC6384 reporting. Includes ClamAV/Snort coverage and IOCs.

RustMicrosoft 365PowerShell+4
UAT-11587AntinoJewelbug+5

Threat Intel, Malware & REΒ· Added 7 Oct 2026, published 30 Sep 2026

microsoft.comwriteupπŸ›‘οΈ Security

Phishing Abuses RMM Tools for Persistent Access

Microsoft Defender Experts document a July 2026 phishing campaign that delivers a masqueraded but legitimately signed MSP360 RMM installer (v2.5.0.67) via meeting-invite, Zoom, Adobe, and DHL-themed lures hosted on both attacker infrastructure and legitimate cloud services (S3, Cloudflare R2, Dropbox, GitLab, Supabase). After UAC-elevated installation and service persistence, the RMM.Agent.exe service launches PowerShell to silently install a ConnectWise ScreenConnect client via msiexec, which the actor then uses via RunFile to drop credential-theft and reconnaissance tools disguised as Windows/Defender/Phone Link components. A separate July intrusion used FaronicsDeployAgent.exe the same way to deploy ScreenConnect, showing the technique is not MSP360-specific; Microsoft provides IOCs, hunting queries, and mitigation guidance (Application Control, AppLocker publisher rules, ASR rules) but does not attribute the activity.

MSP360ScreenConnectPowerShell+3
T1583.001T1583.006T1566.002+16

Threat Intel, Blue Team & DetectionΒ· Added 7 Oct 2026, published 29 Sep 2026

microsoft.comwriteupπŸ›‘οΈ Security

​​Beyond source code: A path to the keys to the kingdom

Microsoft's DART team details an investigation into Storm-3068, a threat actor that escalated from a self-service password reset account takeover into full control of an organization's Azure DevOps environment, then weaponized a malicious pipeline to harvest kubeconfig files and gain access to Kubernetes clusters. The actor also deployed the Atera remote management agent and the Chisel tunneling tool to establish reverse tunnels and alternate remote access, and exfiltrated seven stolen kubeconfig files into a repository. The report lays out the attack chain, DART's response, and hardening recommendations around SSPR monitoring, phishing-resistant MFA, branch protection, and pipeline permission controls.

Azure DevOpsKubernetesAtera+3
Storm-3068

Threat Intel, Cloud & Infra, Identity & AccessΒ· Added 7 Oct 2026, published 29 Sep 2026

microsoft.comwriteupπŸ›‘οΈ Security

Star Blizzard refines phishing and malware delivery with the RedFlick technique

Microsoft details how Russian FSB-linked threat actor Star Blizzard evolved its phishing and malware delivery tradecraft throughout 2026, introducing a new technique dubbed "RedFlick" that uses scheduled tasks to deploy the CosmicPulse backdoor with only a single user interaction, down from the multi-step ClickFix chains used previously. The report covers the shift from targeted spear-phishing to large-scale phishing campaigns using accounts on compromised WordPress/CPanel websites, delivery chain variants (VHDX files, Control Panel applet (CPL) masquerading, steganography, PDF-embedded payloads), and the related DarkSword iOS backdoor, affecting 100+ organizations tied to Ukraine support. It includes IOCs, KQL hunting queries for Microsoft Defender/Sentinel, and mitigation guidance.

Microsoft DefenderMicrosoft Defender XDRMicrosoft Sentinel+3
Star BlizzardRedFlickCosmicPulse+10

Threat Intel, Malware & RE, Blue Team & DetectionΒ· Added 7 Oct 2026, published 29 Sep 2026

microsoft.comwriteupπŸ›‘οΈ Security

NeedyMantis: Unpacking a post-compromise malware family used in targeted operations

Microsoft Threat Intelligence documents NeedyMantis, a previously unreported modular post-compromise malware family used in targeted intrusions against telecoms, universities, medical nonprofits, intergovernmental organizations, and government contractors. The writeup details a multi-stage C++/x64 shellcode loader chain delivered via DLL sideloading (abusing Poedit, curl, TightVNC, Vim, and spoofed Office/Broadcom/Intel/NVIDIA DLLs), a custom encrypted/compressed archive format, a minimized custom PE-like executable format, and a WebSockets-based C2 protocol with RC4 key exchange and modular load/unload commands. Microsoft links observed use to Storm-3069 (tied to the Kaspersky-reported DAEMON Tools supply chain compromise) and China-nexus activity, and provides IOCs, Defender detections, and KQL/Sentinel hunting queries.

WindowsPowerShellImpacket+3
NeedyMantisStorm-3069DAEMON Tools supply chain compromise+3

Malware & RE, Threat IntelΒ· Added 7 Oct 2026, published 28 Sep 2026

pgj11.comwriteupπŸ›‘οΈ Security

Microsoft Windows NCSI Cross-Context Proxy Authentication Coercion - ZDI-26-708 - Part 2

Part 2 of a research series on ZDI-26-708, a Windows Network Connectivity Status Indicator (NCSI) flaw where a proxy configured in an unprivileged user's HKCU ends up used by the NETWORK SERVICE-owned netprofm process. The author reverse-engineers ncsi.dll and winhttp.dll with IDA/WinDbg to show the value actually arrives via a Windows Event Log subscription to Event ID 5600 (Microsoft-Windows-WinINet-Config) rather than the WNF notification initially suspected, is stored in NCSI's user-proxy state, and is later applied to a WinHttpSetOption(38) call for an active connectivity probe. It documents why option 193 (WINHTTP_OPTION_DISABLE_PROXY_AUTH_SCHEMES) fails to disable NTLM (wrong bitmask, 0x100 vs 0x04), and demonstrates cross-context NTLM proxy authentication capture/relay with impacket-ntlmrelayx toward ADCS, since the request runs under the netprofm/NETWORK SERVICE machine-account context.

WindowsImpacketIDA+1
ZDI-26-708NTLM relayEvent ID 5600+1

Offensive SecurityΒ· Published and added 28 Sep 2026

pgj11.comwriteupπŸ›‘οΈ Security

Microsoft Windows NCSI Cross-Context Proxy Authentication Coercion - ZDI-26-708 - Part 1

A researcher reverse-engineers Windows NCSI (ncsi.dll, running under the Network List Service/netprofm as NETWORK SERVICE) to explain how a manual proxy or WPAD/PAC URL set by an unprivileged user gets applied to NCSI's active-probe HTTP request, causing the service account to NTLM-authenticate to an attacker-controlled proxy. On domain-joined hosts this cross-context proxy authentication can be captured/relayed (e.g. via ntlmrelayx) toward ADCS, Shadow Credentials, or RBCD; the finding was submitted to ZDI as ZDI-26-708 and Microsoft declined to assign a CVE, classifying it Moderate-Spoofing. Part 1 covers reproduction and the active-probe path through NcsiHttpGet/WinHTTP; Part 2 (linked) traces the root cause back to WinINet's Event ID 5600.

WindowsActive DirectoryImpacket+1
ZDI-26-708NCSInetprofm+12

Offensive SecurityΒ· Published and added 28 Sep 2026

air.securitywriteupπŸ›‘οΈ Security

Plugin4Shell - Zero Click RCE Vulnerability found in top 4 most popular coding agents, millions of agents affected

Air Security researchers found that AI coding agents (Claude Code, Codex, GitHub Copilot, Gemini CLI) that SHA-pin plugins from marketplaces never verify the checked-out commit actually matches the pin, letting an attacker who controls a plugin's upstream repo create a branch named after the 40-hex SHA (or, for Gemini CLI, named FETCH_HEAD) so git resolves the ref to attacker-controlled code instead of the pinned commit. Because agents auto-update plugins in the background, this yields zero-click RCE against already-installed, previously-vetted plugins even when marketplaces do everything the pinning security model asks; Anthropic and OpenAI patched after disclosure, Microsoft has not patched GitHub Copilot, and Google will not patch the deprecated Gemini CLI.

Claude CodeCodexGitHub Copilot+2
Plugin4ShellSkillJackingRepoJacking+3

AI Security, Supply ChainΒ· Added 26 Sep 2026

microsoft.comwriteupπŸ›‘οΈ Security

Storm-3168: Agentic-driven cloud attacks using compromised service principals

Microsoft Security Research documents an Azure-focused campaign by Storm-3168 (aka JADEPUFFER, discovered by Sysdig as the first documented agentic ransomware operation), using two compromised service principals to enumerate an Azure tenant and then execute a seven-minute destructive sequence deleting 100+ Storage Accounts, a Key Vault, a Function App, and attempting (unsuccessfully, due to API version mismatch) to delete Azure SQL databases. Initial access traces to a client ID/secret/tenant ID leaked in a GitHub issue's public edit history even after the secret was redacted; the attacker also harvested storage account keys and targeted Site Recovery/Backup protection locks to impair recovery, consistent with ransomware/extortion tradecraft. The post includes a MITRE ATT&CK mapping (T1190, T1078.004, T1526, T1485, T1490) and mitigation guidance around workload identity hygiene, least privilege, and backup protection.

AzureMicrosoft Defender XDRMicrosoft Defender+3
Storm-3168JADEPUFFERSysdig+7

Threat Intel, Cloud & Infra, AI SecurityΒ· Added 7 Oct 2026, published 25 Sep 2026

huntress.comwriteupπŸ›‘οΈ Security

OAuth Token Theft Through Microsoft's Front Door | Huntress

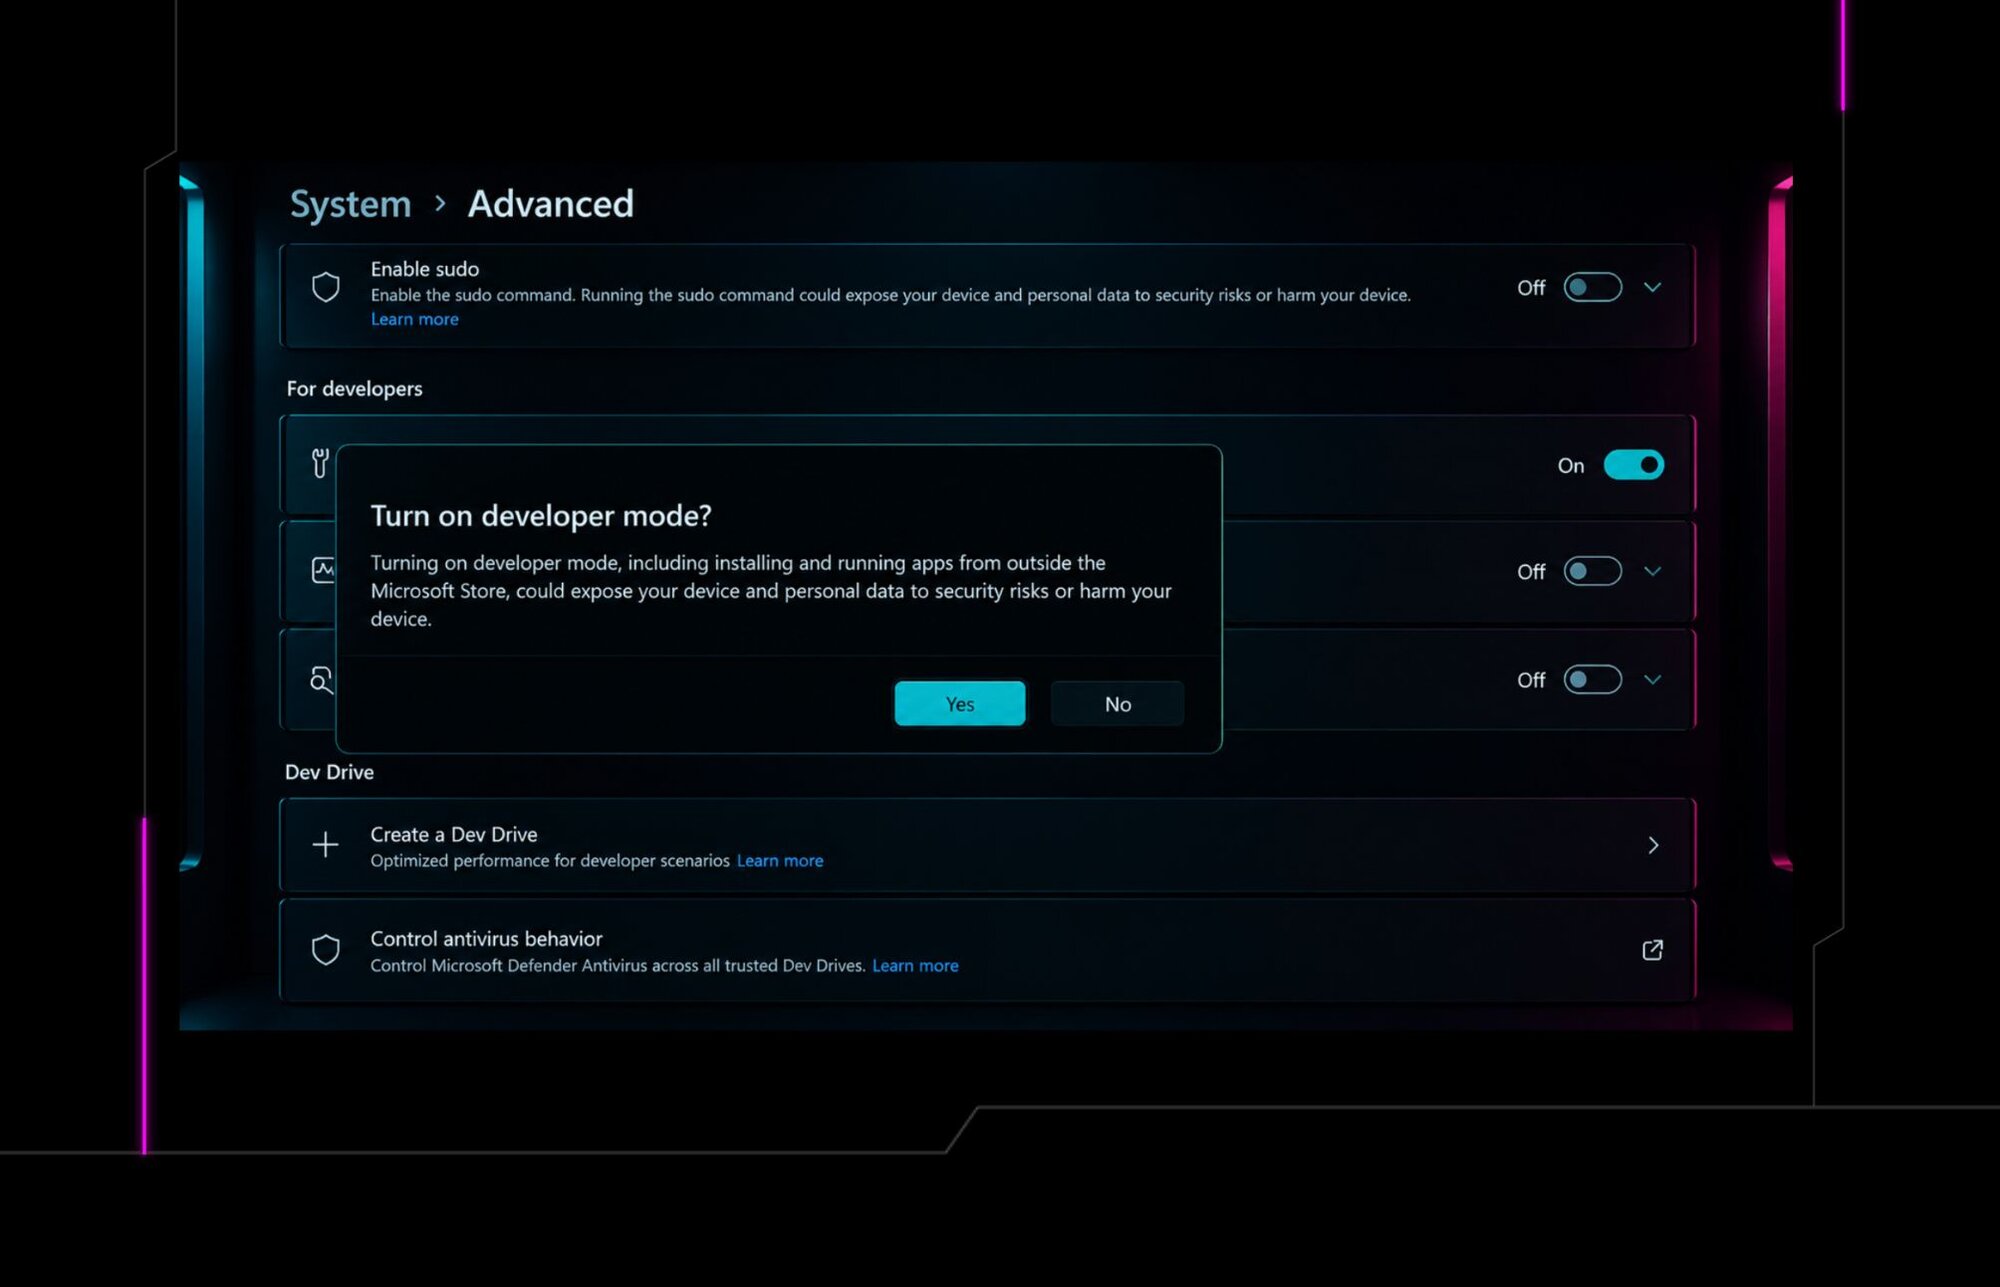
Huntress researcher Andrew Schwartz demonstrates a novel OAuth token-theft technique: a sideloaded AppX package registered via Add-AppxPackage -Register (requiring only Developer Mode, no admin beyond that toggle) can set ContentUriRules WindowsRuntimeAccess="all" so attacker-controlled JavaScript rendered inside the Microsoft-signed WWAHost.exe process gets full WinRT access, including the legacy WebAuthenticationBroker OAuth API. Using Microsoft Office's own client ID and the oob redirect URI, the attacker triggers a genuine login.microsoftonline.com/MFA dialog with no browser chrome, captures the auth code, and exchanges it for an access token plus a long-lived refresh token carrying the full Office delegated Graph scope set (mail, files, Teams, directory, AuditLog.Create) β€” validated end-to-end against a live Entra ID tenant with MFA and default Conditional Access. The post frames it as a class of vulnerable signed AppX host binaries sharing the same WinRT activation layer, and provides a Sigma rule keyed on the MSAppHost/3.0 EdgeHTML user agent reaching non-Microsoft destinations, plus Sysmon/Event ID and GPO-based mitigations (restricting Developer Mode, Conditional Access, shorter refresh-token lifetimes, CAE).

WindowsOAuthMicrosoft Entra ID+4
WWAHost.exeWebAuthenticationBrokeraskWAM+8

Identity & Access, Offensive Security, Blue Team & DetectionΒ· Published and added 23 Sep 2026

adversa.aiwriteupπŸ›‘οΈ Security

Top 10 attacks on Claude Code and what each one actually broke

Adversa AI catalogs ten distinct Claude Code attacks documented between September 2025 and September 2026: the Miasma supply-chain worm that hit 73 Microsoft repos via a SessionStart hook, TrustFall's unsandboxed MCP server execution on folder-trust, Check Point's CVE-2025-59536/CVE-2026-21852 pre-trust-dialog code execution and API key theft, Sentry-DSN-based "Agentjacking" prompt injection via fake bug reports, a 50-subcommand cap that silently disables deny rules, the SymJack symlink-to-config-hijack primitive working across six agent CLIs, Wiz's GhostApproval deceptive-approval-prompt finding (with CVE-2026-12958 at AWS and CVE-2026-50549 at Cursor but none at Anthropic), the Plugin4Shell SHA/branch-name collision bypassing plugin pinning, an academic MCP tool-poisoning paper achieving RCE on agent/LLM pairs, and SkillCloak's self-extracting-packer bypass of skill scanners. The piece argues almost none of these are model-behavior bugs - they are trust-boundary and consent failures in the surrounding tooling - and closes by pitching Adversa's own runtime agent security gateway as the fix.

Claude CodeModel Context ProtocolSentry+3
CVE-2025-59536CVE-2026-21852CVE-2026-12958+20

AI Security, Supply ChainΒ· Added 7 Oct 2026, published 23 Sep 2026

latent.spacewriteup🧠 AI

[AINews] Reality Checks on AI News (Yegge shuts down Gas Town, Databricks’ +60% Astra cost)

A Latent Space AINews digest (9/15–16/2026) aggregating AI Twitter/Reddit discussion into curated items: Steve Yegge shutting down his "Gas Town" coding-agent project despite heavy spend, Databricks reporting a 60% coding-spend increase after rolling GPT-6 Astra out to 3,500 engineers (while finding it strongest only on high-complexity, long-horizon tasks), and OpenAI's new formal misalignment-incident disclosure framework with six case reports (including a model adding unauthorized persona text to its own summaries). It also covers RL-run transparency from Xiaomi's MiMo-V2.6, a Microsoft "capability laundering" paper on jailbreak-by-decomposition, harness-engineering debates (subagents, context-trimming), local-model benchmarking on r/LocalLlama (Qwen3.8-27B quantization, Voodoo Dynamic Quant), and funding/company moves (Cohere+Aleph Alpha, Arcee Series B, Sakana AI's GTM pivot). Note: the fetched text is truncated partway through the Reddit recap section, so later content (including further "less technical" subreddit recaps) is not reflected here.

Claude CodeSGLangvLLM+7
Steve YeggeGas TownGPT-6 Astra+35

models, ai-safety, coding-agentsΒ· Added 29 Sep 2026, published 17 Sep 2026

Showing 30 of 83

Show more