- PHP2Shell Attacks Root Palo Alto Firewalls but Fail Against WordPress
PHP2Shell (CVE-2026-109618 and CVE-2026-109619) has been exploited for over a week. A China-linked group chained it with the Fragnesia Linux kernel privilege escalation to root at least 25 Palo Alto Networks PAN-OS firewalls with exposed management interfaces. Defiant had seen no confirmed WordPress compromise by 28 October 2026 despite 77,000 requests, and Cato and watchTowr report few successful attackers.
 securityweek.comarticlePublished and added 30 Oct 2026🛡️ Security
- Chinese Hackers Quietly Used Low-Severity ESXi Logging Flaw as Zero-Day
CVE-2026-41709 is a low-severity insufficient-logging flaw in VMware ESXi that lets a logged-in administrator perform operations without audit entries. CISA added it to the KEV catalog, and CrowdStrike reported that China-nexus actor Warp Panda used it as a zero-day against US organizations, including law firms, to cut audit visibility. The article also covers exploitation of vCenter bugs CVE-2026-59309 and CVE-2026-59310 and lists the fixed ESXi builds.
securityweek.comarticlePublished and added 29 Oct 2026🛡️ Security  China-Linked Hackers Exploit PHP2Shell to Root Firewalls
A China-linked actor chained PHP2Shell (CVE-2026-109618, CVE-2026-109619) with the Fragnesia Linux kernel privilege escalation (CVE-2026-46300) to root firewalls and drop PHP webshells, per Dream. Using FOFA, the actor narrowed 19,000 firewalls to 240 targets and rooted 24 on 23-24 October. On two US government-affiliated devices it used a reverse SSH tunnel, hit the firewall management server, and attempted LDAP and Active Directory abuse.
securityweek.comarticlePublished and added 28 Oct 2026🛡️ Security Stolen AI Reasoning Could Help China Build Cheaper Rivals
Compaction Smuggling is an attack found by Xint that bypassed OpenAI's August 2026 mitigations against stealing reasoning traces from proprietary LLM APIs. It encodes one model's reasoning inside a compaction and replays it to another model (for example gpt-4.1 or gpt-4o), which outputs it verbatim. OpenAI fixed it and paid a $6,000 bounty on 23 October 2026. The article ties it to distillation by Chinese labs, citing a September CISA warning.
securityweek.comarticlePublished and added 26 Oct 2026🛡️ Security China APT Uses AI Pentest Tool Artex in ConnectWise Attacks
Storm-0940, a China-linked APT, used the open source AI penetration testing framework Artex to automate a mid-October 2026 campaign against ConnectWise customers, per Microsoft. Artex drove reconnaissance, password spraying and OAuth application abuse at more than 2,900 attempts per minute, with sign-in attempts against over 2,250 tenants. Attackers modified application credentials for persistence, and Microsoft advises correlating service principal sign-ins with Graph activity.
securityweek.comarticlePublished and added 23 Oct 2026🛡️ Security- Spectrmachina/Ztrust
ZTrust is a Python supply-chain scanner that checks manifests, lockfiles, source and GitHub workflows for vulnerable or malicious dependencies (via OSV.dev), typosquats, leaked secrets, unsafe lockfiles and risky CI patterns such as pwn requests and script injection. It outputs console, JSON and SARIF 2.1.0 and ships as a GitHub Action. It also includes a FastAPI bounty service using commit-reveal and shielded Zcash payouts for researchers.
 github.comrepoAdded 27 Oct 2026, published 22 Oct 2026🛡️ Security
 AI-driven, large-scale nation-state campaign using ARTEX enables supply chain compromise
Microsoft Threat Intelligence report on Storm-0940, a China-state aligned actor that used the open-source agentic AI pentest framework ARTEX from September 2026 to automate attacks on hundreds of organizations. It links the actor to the October 2026 ConnectWise multi-tenant OAuth app compromise (2,250+ tenants, 2,900 sign-ins per minute, privileged access in under 3 hours). It gives IOCs, Defender XDR and Sentinel KQL hunting queries, ATT&CK mapping and mitigations.
 microsoft.comwriteupPublished and added 21 Oct 2026🛡️ Security
 Latest open artifacts (#25): DeepSeek V4.1 Flash 1017, American-made models, and new regulatory controls in the US & China
Interconnects' Latest open artifacts (#25) covers open-weight AI in fall 2026. Policy items: China's MOFCOM proposal for pre-approval of international model sharing, and a DHS order barring DeepSeek from federal civilian procurement. DeepSeek released its internal inference stack DeepInfer. Picks include MiMo-V2.6-Pro-RL, DeepSeek-V4.1-Flash-1017 (552B-A16B, MIT), Clef, Nemotron-3.5-Super-VL and Reflection's Beam-1.0 (Apache 2.0).
 interconnects.aiarticlePublished and added 20 Oct 2026🧠 AI
 US Orders Civilian Agencies to Rip DeepSeek Out of Government Systems
The US Department of Homeland Security ordered civilian agencies to remove DeepSeek products and third-party services built on the model from their IT systems, and barred new purchases. The notice cites possible transfer of sensitive data to the PRC and intelligence on US persons. The article lists earlier bans by Commerce, the Navy and three states, and notes DeepSeek's open MIT-licensed V4 models can be hosted outside China.
 decrypt.coarticlePublished and added 19 Oct 2026🧠 AI
 Revisiting the Security of VDOO
 is an ePrint paper (October 2026) on VDOO, a multivariate signature scheme submitted to China's NGCC program. It models VDOO as a multilayer Rainbow construction, keeps only the last oil space to get a generalized UOV instance, and applies wedge attacks. For the 512-bit parameter set it estimates 2^432 gates (reconciliation) and 2^379 gates (intersection), below the claimed level and the specification's figures.
 eprint.iacr.orgpaperAdded 19 Oct 2026, published 18 Oct 2026🛡️ Security
- [AINews] High Taste Testers Ep. 1
AINews issue for 10/15–10/16/2026, covering Twitter and Reddit. It covers the open-weights releases Meta's Muse Spark Open (816B/42B-active MoE, AA Intelligence Index 39, custom license) and Reflection Beam 1.0 (501B/23B-active, Apache 2.0), plus NVIDIA Nemotron 3.5, StepFun Step 5 Preview and FLUX 3 Image Klein. It also covers Gemini 4 Argon, Haiku 5.5 pricing, "decision model" classifiers (Liquid d1-ultra, Perplexity pplx-decider), TPUv7/Vera Rubin/MI355X serving benchmarks, interpretability claims (Qwen3-32B neuron audit), agent research, eval-integrity and safety disclosures, and China export-control proposals. The page also announces a pilot video show, High Taste Testers Ep. 1.
 latent.spacearticlePublished and added 17 Oct 2026🧠 AI
 [AINews] High Taste Testers Ep. 1
AINews issue for 15-16 October 2026, from Latent Space, summarising 12 subreddits and 544 Twitter accounts. It covers Meta's Muse Spark Open (816B MoE) and Reflection Beam 1.0 with Artificial Analysis scores and pricing. It also covers Gemini 4 Argon, decision models, TPUv7 and Vera Rubin serving benchmarks, interpretability claims, agent papers, and China's proposed open-source export rules.
latent.spacearticleAdded 30 Oct 2026, published 17 Oct 2026🧠 AI Chinese APT Exploited BeyondTrust Vulnerability as Zero-Day
SecurityWeek reports that China-linked Armory Castle (UNC5221, Warp Panda) exploited CVE-2026-102764 (CVSS 9.3), an improper origin validation flaw in BeyondTrust Remote Support enabling file operations, as a zero-day from August 29. Mandiant/GTIG observed the Sawfly PHP webshell and Bareclaw SOCKS5 tunneler, root takeover, credential harvesting, log deletion, and abuse of the native file transfer service for exfiltration. Patch BT26-05-RS covers versions through 26.2.3; the actor's earlier edge-device zero-days (CitrixBleed, Ivanti Connect Secure, Dell RecoverPoint) are listed.
securityweek.comarticlePublished and added 16 Oct 2026🛡️ Security Vaibhav Sisinty (@VaibhavSisinty) on X
Social post reporting Meta's release of Muse Spark Open, described as the most capable US open-weight model: 816B total and 42B active parameters, a 1M-token context, and text, image, video and audio input in one model. It is pitched at coding and agentic work and tuned to run on two M5 Ultra Mac Studios, with weights available at release. The poster notes that in Meta's own chart, China's Kimi K3 and GLM 5.3 still beat it on coding.
 x.comthreadAdded 16 Oct 2026, published 15 Oct 2026🧠 AI
- AI Security Wiki: Governance, Risk, Standards and Test Cases
A vendor-neutral AI Security Wiki acting as an implementation layer for enterprise AI adoption: risk methodology, AI risk register, control objectives library, domain standards (browser/IDE AI, runtime apps, agentic AI, sovereignty), vendor evaluation framework, and audit/evidence checklists. It includes a 653-case product evaluation test library across 17 lifecycle layers and 6 emerging domains, plus regulatory hubs for GCC, EU, Australia, Brazil, Canada, China, India, Japan, Singapore, South Korea, UK and US, and crosswalks to FINOS AIGF, NIST AI RMF, ISO/IEC 42001, OWASP, MITRE ATLAS, ISO 27001 and others. Useful as a template and evidence source for teams building AI governance and assurance programmes.
 nachi065.github.iootherAdded 15 Oct 2026🛡️ Security
- CISA AA26-281A: Chinese Government-linked Actors Combine Automated and Hands-on Hacking Tools to Steal Data
Joint FBI/CISA/NSA and allied-agency advisory on China-linked actors enabled by Integrity Technology Group (overlapping with Flax Typhoon, Ethereal Panda, Red Juliett). It details their TTPs: open-source scanners and the MicroScan exploit-script app, an XSS credential-harvesting payload dropping live700_v1.exe, EBurst password spraying against Exchange/O365, SoftEther VPN persistence, DCSync via DC.exe, and email theft via the Curlc4.txt PHP bot and the office-cli utility. It also provides IOCs, MITRE ATT&CK mappings, CVEs, incident response steps, and mitigations.
 cisa.govadvisoryAdded 9 Oct 2026🛡️ Security
- Distinguishers for the Squeezing of the Alternating Sponge and Duet
Cryptanalysis of the Alternating Sponge (ASP) and Duet, a permutation-based hash candidate in China's ICCS Next Generation Commercial Cryptographic Algorithm program (NGCC). The authors give an O(2^r)-query distinguisher against ASP that contradicts its claimed indifferentiability bound in some parameter regimes. They also give a distinguisher and state-recovery attack on Duet's multi-block output, using O(2^(r+c-h)) permutation queries. Collision and preimage resistance are unaffected, but Duet used as a XOF or KDF is affected, and state recovery enables length extension.
eprint.iacr.orgpaperAdded 12 Oct 2026, published 9 Oct 2026🛡️ Security 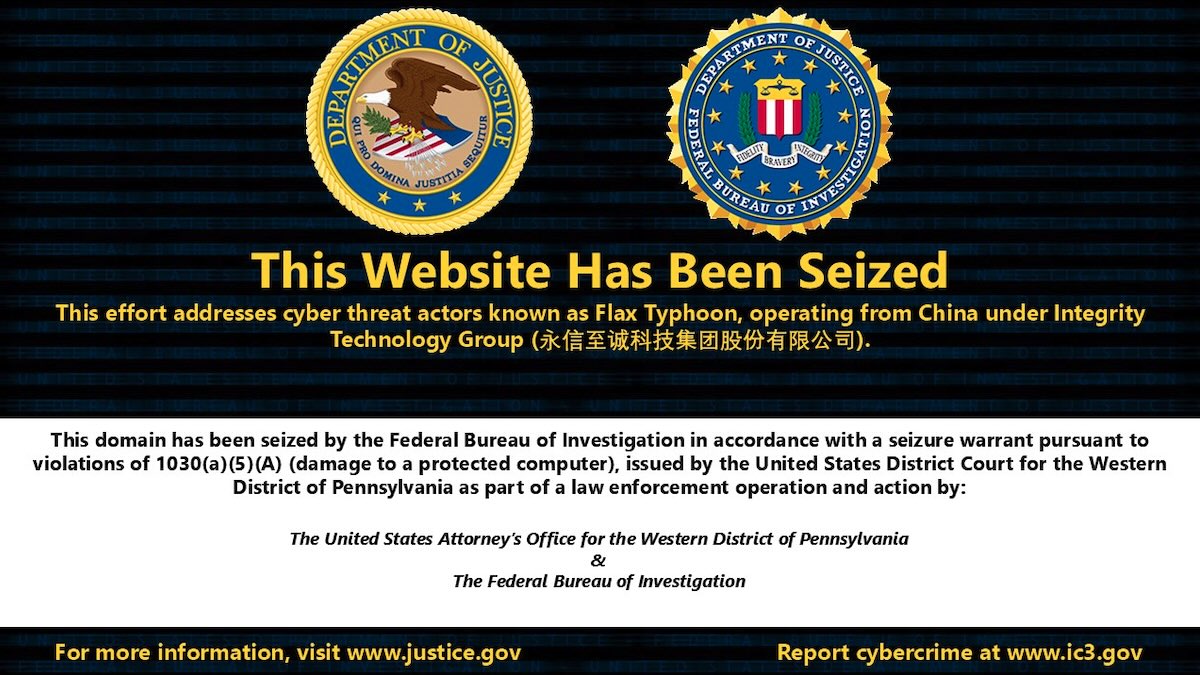 US Disrupts Chinese State-Sponsored Hacking Tools
The US, alongside UK, Australian, Canadian, Japanese, New Zealand, and Spanish agencies, disrupted MicroScan and FishHub, hacking tools built by China's Integrity Technology Group and used by the state-sponsored actor Flax Typhoon (aka Ethereal Panda, Red Juliett, Storm-0919, UNC5007) against US, Japanese, Polish, and Taiwanese critical infrastructure and universities. MicroScan is a Python-based scanner with over 1,300 penetration-testing scripts targeting Apache Struts, Jenkins, WebLogic Server, WordPress, OpenSSL, and other services, delivered via a Mirai-derived IoT botnet; FishHub let operators remotely search and exfiltrate files from victim networks. The advisory also details the group's broader toolkit (SoftEther VPN for persistence, EBurst for Exchange password spraying, DC.ex for Active Directory data extraction) and the seizure of the domains used to access the tools.
securityweek.comarticlePublished and added 9 Oct 2026🛡️ Security AI Startup Manus Raises $500 Million After China Nixed Meta’s $2 Billion Acquisition
Reports that Butterfly Effect, parent of Chinese AI agent startup Manus, raised over $500 million led by Boyu Capital and IDG Capital (with Tencent, HSG and ZhenFund), after China's National Development and Reform Commission ordered Meta's roughly $2 billion acquisition of the company unwound as prohibited foreign investment. It traces Manus's trajectory from its March 2025 invite-only launch (built on fine-tuned Anthropic Claude and Alibaba Qwen models) through $100M ARR, relocation to Singapore, the blocked Meta deal, and its pivot to a new agent product called Cue, situating the episode within Beijing's wider tightening on AI firms including new travel-approval rules for senior AI staff at companies like Alibaba and DeepSeek.
decrypt.coarticlePublished and added 8 Oct 2026🧠 AI- Dark Web Intelligence (@DailyDarkWeb) on X
A Twitter/X post digests joint advisory AA26-281A from FBI, CISA, NSA and allied agencies (UK, Australia, Canada, Japan, New Zealand, Spain) on China-based Integrity Technology Group enabling threat actors, tracked elsewhere as Flax Typhoon, Ethereal Panda and Red Juliett, to target US critical infrastructure, government, healthcare, education and law enforcement networks worldwide. The actors chain open-source scanners, large botnets, XSS, password spraying against Microsoft Exchange, VPN persistence and credential-harvesting scripts. CISA added five exploited CVEs (ISC BIND, Apache Struts, ProFTPD, ONLYOFFICE Docs, Strapi) to its KEV catalog with an Oct 11 federal remediation deadline, and STIX IOCs accompany the advisory.
x.comthreadPublished and added 8 Oct 2026🛡️ Security 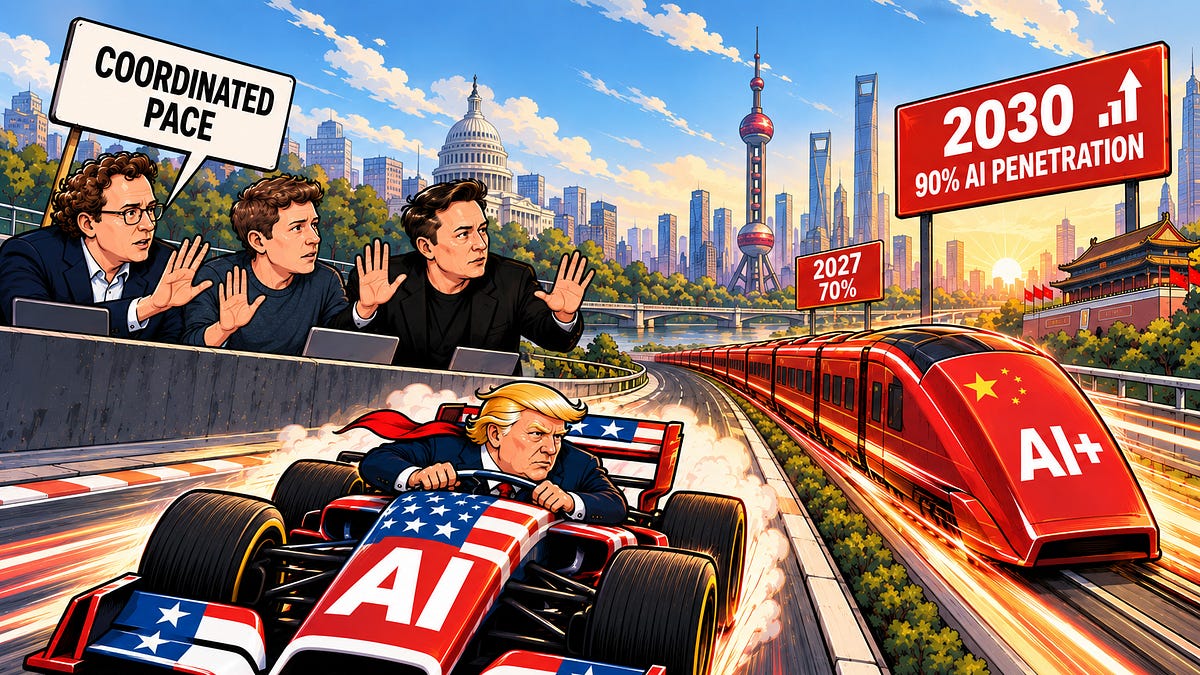 Beijing Will Not Pace the Frontier: China’s Speed-First AI Safety Regime
SemiAnalysis argues China's AI safety regime is speed-first: strict on application content, with no frontier-risk duties tied to compute or capability. It builds a dataset of 857 releases from nine Chinese labs, of which only 31 (3.6%) have a published safety result. It also codes 102 expert texts and reviews TC260 Framework 3.0, SAIL, and CAICT.
 newsletter.semianalysis.comarticleAdded 29 Oct 2026, published 8 Oct 2026🧠 AI
 AI Labs’ Call to
A Galaxy Research newsletter piece dissecting Dario Amodei's essay "We Must Pace the Frontier," which proposed embedded third-party evaluators (e.g. METR), cross-lab safety coordination with antitrust waivers, and eventual global AI governance including China. The piece separates Amodei's "operational" (QA/pipeline) and "research" (alignment, interpretability, evals) problems from his "Democratic Coordination" ask, arguing the latter functions as a regulatory moat rather than a necessity, and draws a parallel to Sam Bankman-Fried/FTX-era effective-altruism rhetoric about unilateral existential-risk authority. It covers reactions from Sam Altman (agreeing to adopt evaluators), Trump (rejecting slowdown, citing the AI race with China), David Sacks (questioning METR's neutrality), and Mark Zuckerberg (citing Meta's unilateral delay of Muse and existing liability incentives as sufficient without an industry pact).
 galaxy.comarticleAdded 8 Oct 2026🧠 AI
 US Seeks Alleged Chinese Hafnium Hacker With $10 Million Reward
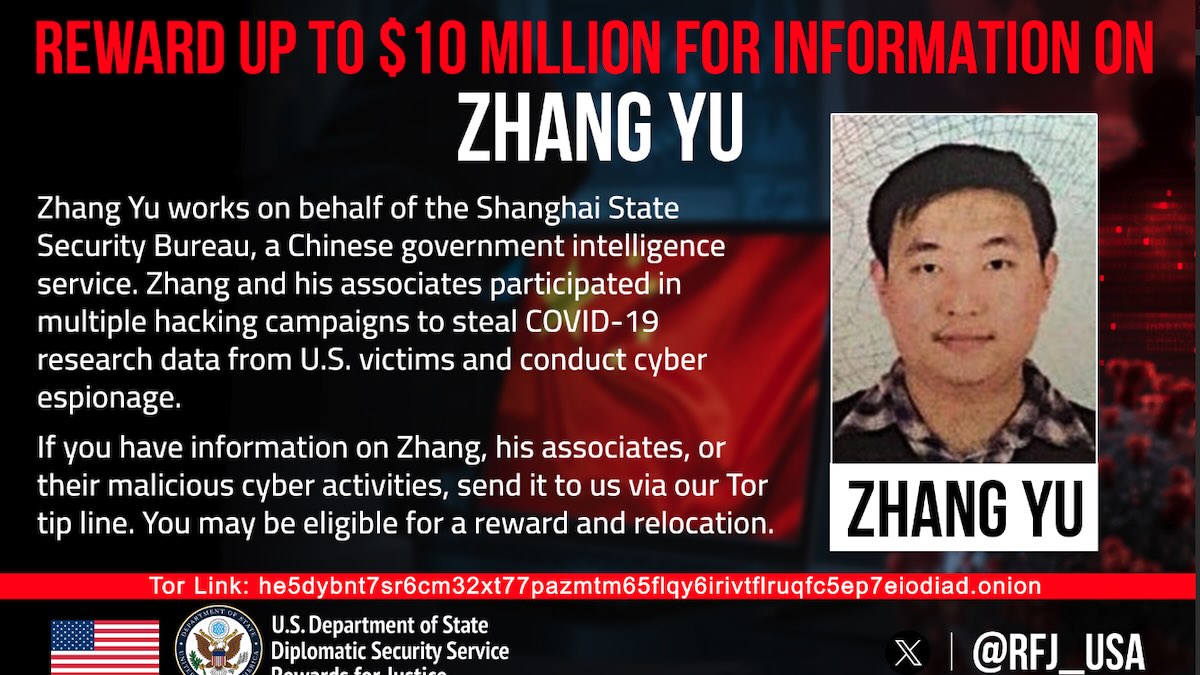
The US State Department's Rewards for Justice program is offering up to $10 million for information on Zhang Yu, a Chinese national charged alongside Xu Zewei for the 2021 Hafnium campaign that exploited Microsoft Exchange Server vulnerabilities and for earlier theft of COVID-19 research from US universities and immunologists starting in 2020. Zhang is identified as a director at Shanghai Firetech Information Science and Technology Company allegedly acting for the Shanghai State Security Bureau (part of China's MSS); Xu was extradited from Italy in April 2026 and has appeared in a Houston federal court while Zhang remains at large. Microsoft now tracks the Hafnium activity as Silk Typhoon; the FBI said the campaign compromised more than 12,700 US organizations.
securityweek.comarticlePublished and added 8 Oct 2026🛡️ Security TP-Link Faces State Lawsuits and New Scrutiny Over ISP Router Flaws
Florida, Iowa, Montana, and Nebraska sued TP-Link Systems over allegedly misleading security marketing and undisclosed China ties, joining a similar Texas suit from February; the complaints cite TP-Link routers' role in the Volt Typhoon and Flax Typhoon campaigns and botnet abuse by Chinese and Russian actors. The piece also details five newly disclosed TP-Link Aginet vulnerabilities (CVE-2025-30237 through CVE-2025-30241) reported by SEC Consult, including an unauthenticated super-admin auth bypass, a root-privilege command injection, hardcoded device-model encryption keys exposing Wi-Fi/ISP credentials, and a USB-based physical-access filesystem dump affecting 65 device models.
securityweek.comarticlePublished and added 8 Oct 2026🛡️ Security Antino Backdoor Uses Outlook and OneDrive for C2 in China-Nexus Espionage Campaign
Cisco Talos researcher Ashley Shen details a China-nexus espionage campaign (tracked as UAT-11587) targeting government and policy organizations across Taiwan, India, the Philippines, Cambodia, Pakistan, Thailand, Myanmar and Syria. The actor deploys a previously undocumented Rust-compiled backdoor, Antino, that uses Microsoft Graph to abuse Outlook (for command exchange via mailbox folders) and OneDrive (for heartbeat and file transfer) as a stealthy C2 channel instead of a dedicated server, delivered via a five-stage HTA/WSF-to-.NET-loader chain and DLL-sideloaded through the signed Microsoft binary GatherOsState.exe. The report also covers social-engineering tradecraft (a fake Gmail attachment-preview widget hosted on Cloudflare Pages, SPF/DMARC spoofing) and ties the cluster to Jewelbug, CL-STA-0049, Earth Alux, Ink Dragon, REF7707 and UNC6384 via infrastructure overlaps.
 thehackernews.comarticleAdded 3 Oct 2026🛡️ Security
 SMTP is the key: BPFDoor and AVERAT hitting the network edge
Rapid7 details a new BPFDoor campaign targeting telecom and network-edge appliances (ShareTech, SpamSniper mail gateways) and a six-sample Linux RAT family dubbed AVERAT found on compromised Taiwanese CPE (Synology NAS, a NetKlass device, a Dahua DVR). The writeup reconstructs the Rapid7 BPFDoor controller's HTTP-tunneled trigger mechanism, a fileless ShareTech dropper that stages binaries as ntpdate/udevds and deletes them while processes keep running, a BPF Rekoobe variant that hides inside SMTP port-25 traffic, and AVERAT's RC4-derived config/C2 scheme — tying the infrastructure to the broader China-nexus ORB (Operational Relay Box) device pattern described in CISA/NCSC-UK advisory AA26-113A. It closes with detection guidance for unlinked/deleted process execution, dropper staging artifacts, and port-25 C2 callbacks, plus full IOC and ATT&CK tables.
 rapid7.comwriteupAdded 7 Oct 2026, published 2 Oct 2026🛡️ Security
 China-aligned TA419 impersonates Anthropic employee, ex-White House official to phish AI policy experts
Proofpoint's Mark Kelly details TA419, a China-aligned espionage group that in July 2026 impersonated former White House OSTP official Lynne Edwards Parker and economist Heidi Crebo-Rediker, and in February 2026 posed as a senior Anthropic employee, to phish US AI policy experts' cloud accounts. The attack chain uses benign-looking invitation emails followed by shortened links leading to a fake OneDrive adversary-in-the-middle page that renders a Chrome login window with the open-source Frameless BitB browser-in-the-browser tool, relaying credentials, MFA codes and session cookies live to the attackers via Cloudflare-fronted, NameSilo-registered domains. Proofpoint assesses the campaign supports Chinese intelligence collection on US AI policy and export-control developments.
 helpnetsecurity.comarticleAdded 4 Oct 2026, published 2 Oct 2026🛡️ Security
 OpenAI Says People Linked to China's Moonshot Tried to Copy Its AI's Hidden Reasoning
Decrypt reports OpenAI's claim that it disrupted a campaign running from July 1 to July 28. The campaign sent about 16,000 extraction requests from over 4,000 users on July 24-25, within a cluster of more than 15,000 users, and aimed to reproduce the encrypted reasoning behind model answers. OpenAI attributes a core cluster to people associated with Moonshot AI (maker of Kimi) but says it is unclear whether a single actor was behind all of it. One method copied encrypted reasoning from one conversation and asked a model to decode it in another, and OpenAI has closed that replay pathway. The article places this in the timeline of "adversarial distillation" disputes: DeepSeek, Anthropic's account of about 24,000 fraudulent accounts, the White House, xAI/Grok, and research showing provider-wide reasoning encryption keys.
decrypt.coarticlePublished and added 1 Oct 2026🧠 AI- OpenAI Says People Linked to China's Moonshot Tried to Copy Its AI's Hidden Reasoning
Decrypt reports on an OpenAI disclosure describing a campaign, starting July 1, 2026, that sent 16,000 extraction requests in a single two-day window from a cluster of over 15,000 accounts to pull out OpenAI models' encrypted "hidden reasoning" (chain-of-thought) rather than their answers. OpenAI says operators did not break encryption but manipulated model interactions to replay one conversation's encrypted reasoning for decoding in another, enabling "adversarial distillation" of a rival model's reasoning without its safety guardrails; it attributes a core cluster to individuals associated with Moonshot AI (maker of Kimi) and says it patched the replay pathway by July 28. The piece situates this alongside prior distillation disputes (DeepSeek, Anthropic's fraudulent-account claims against Chinese labs, xAI's admitted use of OpenAI outputs for Grok) and an August finding that OpenAI, Anthropic and Google each protected reasoning with a single provider-wide encryption key that attackers could coax into plaintext.
decrypt.coarticlePublished and added 1 Oct 2026🛡️ Security  China-nexus UAT-11587 targets government and policy organizations across Asia with Antino backdoor
Cisco Talos details UAT-11587, a China-nexus threat cluster targeting government, defense, and policy organizations across Taiwan, India, the Philippines, Cambodia, and other Asian countries with spear-phishing and a five-stage infection chain (HTA/WSF stagers, JScript decryptors, .NET BinaryFormatter/ActivitySurrogateSelector deserialization gadgets, and DLL sideloading via the signed GatherOsState.exe) to deploy a new Rust-compiled backdoor called Antino. Antino uses Microsoft Graph/Outlook/OneDrive as a dead-drop C2 channel instead of a traditional C2 server, supports shell/PowerShell execution, file transfer, shellcode loading with a sleep-mask evasion technique, and abuses the Windows Scripted Diagnostics framework for persistence; Talos also notes possible infrastructure overlap with Symantec's "Jewelbug" cluster and Arctic Wolf's UNC6384 reporting. Includes ClamAV/Snort coverage and IOCs.
 blog.talosintelligence.comwriteupAdded 7 Oct 2026, published 30 Sep 2026🛡️ Security
 NeedyMantis: Unpacking a post-compromise malware family used in targeted operations
Microsoft Threat Intelligence documents NeedyMantis, a previously unreported modular post-compromise malware family used in targeted intrusions against telecoms, universities, medical nonprofits, intergovernmental organizations, and government contractors. The writeup details a multi-stage C++/x64 shellcode loader chain delivered via DLL sideloading (abusing Poedit, curl, TightVNC, Vim, and spoofed Office/Broadcom/Intel/NVIDIA DLLs), a custom encrypted/compressed archive format, a minimized custom PE-like executable format, and a WebSockets-based C2 protocol with RC4 key exchange and modular load/unload commands. Microsoft links observed use to Storm-3069 (tied to the Kaspersky-reported DAEMON Tools supply chain compromise) and China-nexus activity, and provides IOCs, Defender detections, and KQL/Sentinel hunting queries.
microsoft.comwriteupAdded 7 Oct 2026, published 28 Sep 2026🛡️ Security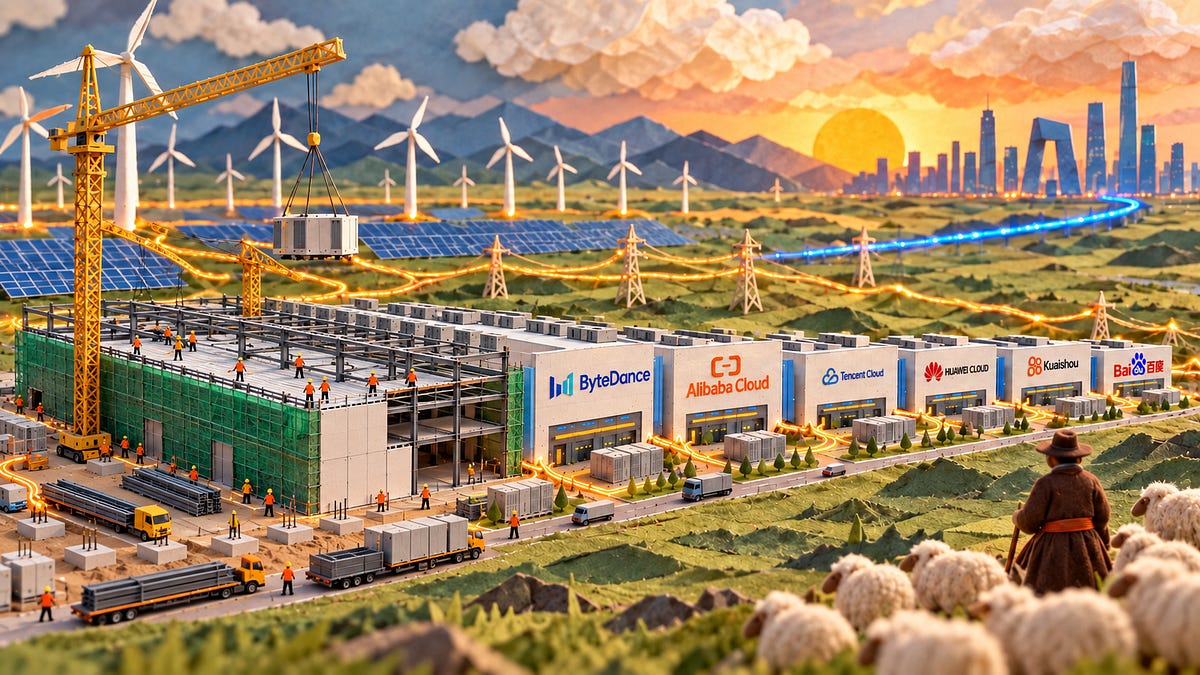 The Chinese AI Infrastructure Boom: Introducing the SemiAnalysis China Datacenter Model
SemiAnalysis previews its China Datacenter Model, which tracks more than 1,000 facilities across 60+ operators and puts China's fleet at over 24GW. The article covers the history of China's retail-first market, the Eastern Data, Western Compute policy moving builds inland, 12-month delivery of 100MW sites, and Alibaba, Tencent, Baidu and ByteDance capex. Tenant-by-tenant sections are paywalled.
newsletter.semianalysis.comarticleAdded 29 Oct 2026, published 25 Sep 2026🧠 AI AI corporate leaders tell UN the industry needs global regulation
Al Jazeera reports on a UN Security Council session, convened by France during UNGA week, where Anthropic's Dario Amodei, OpenAI's Sam Altman and Hugging Face's Clement Delangue called for global AI oversight. Yoshua Bengio, co-chair of the UN Independent International Scientific Panel on AI, also warned that the dangers are real and imminent. The US representative, Michael Kratsios, rejected centralised international control of AI, and the US and China remain reluctant to accept binding limits. The report also covers the UN's AI governance bodies, including the Global Dialogue on AI Governance, and Delangue's account of Hugging Face being attacked by OpenAI's AI agents and defending itself with a Chinese AI model.
 aljazeera.comarticleAdded 26 Sep 2026, published 24 Sep 2026🧠 AI
 Debating RSI, the US-China Gap, and Jaggedness with JS Denain of Epoch AI
A transcribed podcast conversation between Nathan Lambert and Epoch AI's JS Denain covering recursive self-improvement (RSI) evidence from OpenAI/Anthropic's acceleration blog posts, the size and drivers of the US-China frontier model gap (estimated at 4–9 months using Epoch's Capabilities Index, ECI), the role of distillation and "Claude router" data leakage in closing that gap, robotics as a bottleneck for industrial-scale AI acceleration, and jaggedness in AI capability progress (e.g. why math benchmarks may overstate general progress). It's grounded in concrete data points like Codex spending growth, METR/Epoch research, and named model comparisons (Kimi K3, GLM 5.2/5.3) rather than speculation alone.
interconnects.aitalkAdded 29 Sep 2026, published 22 Sep 2026🧠 AI- DVLAA
DVLAA (Damn Vulnerable LLM and Agent Application) is a self-hosted, Docker-deployable security training range for LLM and agent applications, modeled on the DVWA concept but for AI. It covers OWASP LLM Top 10 and Agent Security Top 10 risks (prompt injection, RAG poisoning, tool abuse, memory poisoning, excessive resource consumption, etc.) through 81 hands-on challenges, including an "AWDP" attack/defense track where 10 challenges reproduce real disclosed vulnerabilities in Dify, RAGFlow, Langflow, Flowise, Open WebUI and n8n (with optional real upstream container reproduction), 20 challenges adapted from a China–ASEAN AI security CTF, and 6 challenges adapted from a real model-poisoning CTF. It provides real model interaction, state-machine flag verification, source/prompt viewers, model management (local, Ollama, SiliconFlow, OpenAI-compatible), and bilingual UI.
github.comrepoAdded 22 Sep 2026🛡️ Security  [AINews] not much happened today
Latent Space's AINews daily digest for 9/16-9/17/2026, synthesizing AI Twitter and Reddit discussion into themed sections: agent runtime productization (Anthropic's Claude Code Projects for parallel cloud threads, Google's Gemini managed-agent harness with Credentials/Files APIs), the rise of TypeSafe's Jev as a cheap discriminative classifier/routing primitive for agent harnesses (with pushback from Theo on using it for context compaction), OpenAI's Astra for Law vertical launch, DeepMind's Stellar Colosseum multi-agent math/TCS harness and NVIDIA's Agora git-commit-memory agent system, Anthropic's internal AI-R&D automation metrics (Claude-led R&D tasks rising from 1% to 26% in six months), and a Claude Opus-assisted exploit chain that compromised OpenAI-connected accounts. It also covers Reddit local-LLM threads on Qwen 3.8 27B finetunes/quantizations, the ternary Bonsai 2 27B release, and a Mozilla report narrowing the China-US open-model capability gap to 4.4 months.
latent.spacearticleAdded 29 Sep 2026, published 18 Sep 2026🧠 AI- ruc-datalab/EvoOntology
EvoOntology is an open-source, self-evolving semantic ontology layer for data agents from Renmin University of China, exposed as MCP tools and installable as Claude Code and Codex plugins. It automatically builds a versioned ontology from tabular/file/database workloads, then continuously evolves it from agent execution trajectories using a build-use-evolve-evaluate-publish loop that validates candidate updates against a parent version before promotion. The accompanying paper reports gains over plain ReAct agents on DDR-Bench, InsightBench, and BIRD across GPT-5.5, GPT-5.6-sol, Claude-Sonnet-5, and Claude-Opus-4.8 backbones.
github.comrepoAdded 26 Sep 2026, published 15 Sep 2026🧠 AI  Open-Source AI & Open Models Reading List
A continuously updated reading list from Nathan Lambert's Interconnects curating the best writing on open-weight AI models, organized into Foundation (why companies release open models, the open/closed gradient, safety-vs-openness debates), US-China Competition (the ATOM Project, China's structural advantages, corporate adoption of Chinese models by DoorDash/Airbnb/Cursor/Harvey/Perplexity/Thomson Reuters), and Technical Details (the open-closed performance gap per SemiAnalysis and Epoch AI, cyber-misuse risk, and the 2026 distillation controversy including the paper on stealing reasoning traces from proprietary LLM APIs). It links dozens of primary sources — policy essays, lab statements (Zuckerberg, Thinking Machines Lab), technical reports (Pythia, OLMo, OLMo 2/3), and data trackers (Artificial Analysis, Interconnects Adoption Dashboard) — making it a comprehensive entry point for understanding the open-model ecosystem.
interconnects.aiarticleAdded 29 Sep 2026, published 11 Sep 2026🧠 AI Once in a BlueMoon: Multiple State-Aligned Threat Actors Rapidly Adopt Novel Chrome/Windows Zero-Day Chain
Proofpoint details "BlueMoon," a novel exploit kit chaining a Chrome V8 type-confusion RCE (CVE-2026-85046), a V8 sandbox escape via WebAssembly metadata corruption (CVE-2026-87491), and a Windows kernel LPE (CVE-2026-85880) to break out of the browser sandbox. Within days of first use by China-aligned TA412 (28 Aug 2026), the kit was independently adopted by UNK_LateNight (delivering ShadowPad to US aerospace targets), UNK_DoubleCheck (Rust-based loader against a Vietnamese manufacturer), and UNK_QuietRacket (custom malware against Indonesia/Singapore government and finance targets). The piece analyzes exploit internals (Maglev/TurboFan JIT bug, reflective DLL loading, ALPC/WNF kernel exploitation), flags artifacts suggesting AI-assisted exploit development (debug comments, handover markdown files, v8CTF references), profiles the GemStone Chromium-extension credential-theft backdoor deployed via Secure Preferences forgery, and provides IOCs, ET rules, and a YARA rule for detection.
 proofpoint.comwriteupAdded 26 Sep 2026, published 9 Sep 2026🛡️ Security
 Tracing Crypto in a Narcotics Investigation: FBI Charges Alleged Opioid Distributors
Chainalysis details how blockchain analytics (its Reactor tool) helped the FBI trace Bitcoin proceeds from the darknet vendor account "BarbaraWhite" — which sold nitazene-laced counterfeit pills on Nemesis, Bohemia and Abacus — through a wallet cluster to a China-based chemical supplier and, ultimately, to a mobile payment account tied to defendant Stanislav Chernyshov. The case illustrates a concrete investigative pipeline: combining on-chain clustering with marketplace data, postal records, and off-chain identifiers to deanonymize a pseudonymous crypto-paid drug operation linked to overdose deaths.
 chainalysis.comarticleAdded 30 Sep 2026, published 8 Sep 2026🛡️ Security
- zhu1090093659/dsh-trading
dsh-trading is an open-source AI trading terminal built on "DeepSeek Harness" (DSH), a Cordis-based microkernel plugin ecosystem, covering crypto, US equities, China A-shares and Hong Kong stocks. Its notable design is a multi-agent team: a "master" lead agent grounds itself in a holdings ledger and user knowledge base, then decomposes work and delegates to persona-pinned subagents — a trader (trading plans/execution), an instrument-researcher (disclosures/fundamentals), and a risk-reviewer (exposure/stress scenarios) — each dispatching bundled domain "skills" and native tools for quotes, news, order books and backtesting. Every order defaults to dry-run simulation, live execution requires explicit opt-in plus interactive human approval, and headless sessions fail closed, illustrating a concrete human-approval-gated tool-use pattern for agentic systems.
github.comrepoAdded 2 Oct 2026, published 30 Aug 2026🧠 AI - datawhalechina/zero-to-sglang
Datawhale and RadixArk (the SGLang team's company) run this hands-on course on LLM inference. It starts with KV Cache, prefill vs. decode, and compute-bound vs. memory-bound. It then builds a mini-sglang step by step: forward pass, generation, HTTP serving, Continuous Batching, Paged KV Cache and RadixAttention. The later parts cover the real SGLang source, including quantization, hierarchical caching, DP Attention/EP/PP and Prefill-Decode disaggregation, plus profiling and the PR workflow. It is a rare code-first tutorial on inference engines, available in English and Chinese. Part 0, Part I and Part II chapters 1–2 are done, and the rest is in development.
github.comcourseAdded 12 Oct 2026, published 27 Aug 2026🧠 AI  Nine AI coding agent incidents that ended with deleted data
Adversa AI compiles and analyzes nine publicly documented incidents from June 2025–July 2026 where AI coding agents (Cursor, Replit, Gemini CLI, Claude Code, Google Antigravity, Amazon's internal Kiro agent, Claude Opus 5) caused irreversible data loss — from wiped developer drives to a dropped SaaStr production database and a 13-hour AWS Cost Explorer outage in China. It categorizes failure mechanisms (shell-abstraction mismatches like unquoted paths and tilde expansion, unverified exit codes, constraint decay where acknowledged instructions were ignored, and permission-inheritance bypassing two-person approval gates) and argues that smarter models won't fix the problem, recommending credential scoping, filesystem confinement, mandatory confirmation on irreversible actions, read-after-write verification, and command-level logging.
 adversa.aiwriteupAdded 7 Oct 2026, published 4 Aug 2026🛡️ Security
 Introducing our Artifacts Hub and Adoption Dashboard
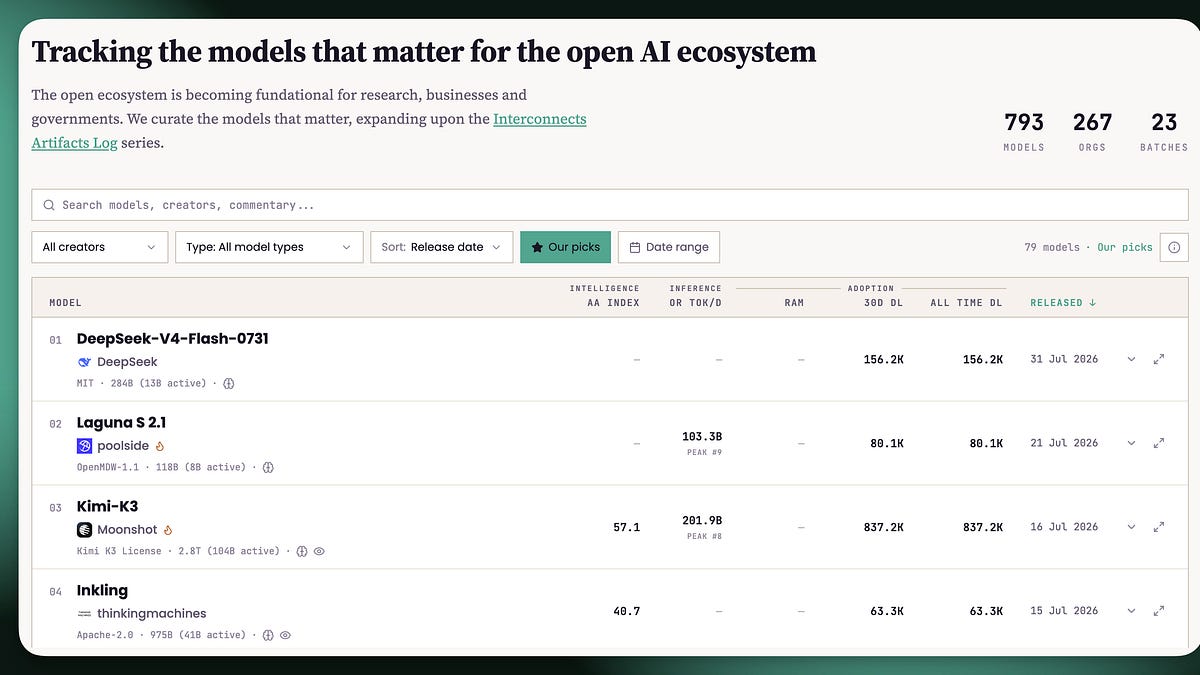
Interconnects announces two new free, continuously-updated resources for tracking the open-weights model ecosystem: the Artifacts Hub, which curates ~792 trending Hugging Face models with inference-token data from OpenRouter, intelligence scores from Artificial Analysis's Intelligence Index, and Interconnects' own relative adoption metric (RAM) and VAIL similarity index; and the Adoption Dashboard, a daily-updating view of download/derivative-model counts by geography and organization highlighting the US-China open-model gap. Both build on prior work from The ATOM Project and Interconnects' Artifacts Log round-ups, developed in collaboration with AI verification startup Project VAIL.
interconnects.aiarticleAdded 29 Sep 2026, published 3 Aug 2026🧠 AI CRPX0 — SCAMMER TURNED RANSOMWARE OPERATOR
In-depth OSINT/threat-intel investigation into CRPX0, a ransomware group that emerged in July 2026 with 47 listed victims (mostly healthcare, mainly US/Turkey targets), tracing its origins to a prior "Flash Token" crypto/USDT money-laundering scam service run by the same operators. The piece covers domain registration analysis (REGRU-SU abuse, reused 2021 domain), dark web/clear web leak sites, RaaS/HaaS/affiliate program offerings, ClickFix-based payload delivery targeting Windows via EXE/DLL, YouTube affiliate-panel promotion analysis (voice/locale clues suggesting China), TOX/Session ID and Bitcoin address correlation, and real IP address deanonymization, concluding with IOCs and MITRE ATT&CK mapping.
 theravenfile.comwriteupAdded 3 Sep 2026, published 3 Aug 2026🛡️ Security
 Open models recap: more on Kimi K3, Qwen 3.8, Xi's WAIC speech, distillation, the open-closed gap, and what's next
A transcribed Interconnects podcast episode where Nathan Lambert and Florian Brand do their quarterly open-model roundup, covering the Kimi K3 release (its coding/agentic performance, $200/mo plan, broken API capacity), GLM-5.2's continued developer traction, Qwen's announced pivot to open-weighting its next flagship, and Xi Jinping's WAIC speech committing China to open-source AI. They dig into why Chinese labs (Kimi/Moonshot, Zhipu/GLM, DeepSeek, MiniMax, LongCat, Ling/Meituan) keep pace with the closed frontier despite less compute — capital efficiency, smuggled/domestic chips, buying external data — then survey the smaller US open ecosystem (Thinking Machines' Inkling and Tinker, Gemma, Nemotron, Poolside, Arcee, Reflection). The back half is a detailed rebuttal of Ben Thompson's Stratechery claim that distillation grows more important as RL scales, arguing SFT-stage distillation from jailbroken Claude/GPT reasoning traces matters less as RL-stage training (which is hard to distill cheaply) dominates post-training, with a side note on a Hugging Face incident where guardrails forced defenders to use a less-restricted model (GLM) to analyze an attack.
interconnects.aitalkAdded 29 Sep 2026, published 22 Jul 2026🧠 AI Kimi K3: The open-weights escalation
Nathan Lambert analyzes Moonshot AI's Kimi K3, a 2.8T parameter MoE model whose open weights closed much of the gap with frontier closed models (ranking #2 on Vals AI, #3 on Artificial Analysis Intelligence Index). The piece details K3's architectural innovations (Kimi Delta Attention, Attention Residuals, Stable LatentMoE giving ~2.5x scaling efficiency over Kimi K2) and situates the release within China's recommitment to open-source AI, Xi Jinping's WAIC remarks, and US policy debates over restricting open-weight Chinese models.
interconnects.aiarticleAdded 29 Sep 2026, published 20 Jul 2026🧠 AI AI Security Briefing
Sysdig's Threat Research Team documented JADEPUFFER, an attack it says was run end-to-end by an AI agent without human operators. The agent exploited CVE-2025-3248 (an unauthenticated RCE in Langflow) for initial access, harvested API keys and cloud credentials, raided a MinIO server via default minioadmin:minioadmin credentials, then pivoted to a MySQL/Nacos server and used CVE-2021-29441 plus Nacos's unchanged default signing key to gain admin access, encrypt 1,342 Nacos settings, and drop a ransom note with no recoverable key. Evidence for AI authorship included verbose in-code commentary explaining each step and a 31-second autonomous diagnose-and-fix cycle across 600+ payloads; the piece situates JADEPUFFER alongside PromptLock/Ransomware 3.0 and Anthropic's Claude-Code extortion and China-linked autonomous-cyberattack disclosures.
thehackernews.comwriteupPublished and added 18 Jul 2026🛡️ Security KUDANKULAM NUCLEAR POWER PLANT LEAK: AN ACCIDENTAL DISCLOSURE
An OSINT investigator analyzes a WorldLeaks ransomware group data leak of Reliance Infrastructure (hosted by third-party vendor Yotta), which exposed 14.3GB / ~19,000 files related to India's Kudankulam Nuclear Power Plant (KNPP) — including RFC drawings, PPS fencing designs, HVAC/fire specs, and vendor/employee records. The piece profiles WorldLeaks (a Hive/Hunters International spin-off), lists MD5/SHA-256 hashes for its RustyRocket exfiltration tool, and discusses supply-chain vendor risk, industrial espionage by nation-state actors (Lazarus/DPRK, China), and insider credential trading as threats to critical nuclear infrastructure.
theravenfile.comwriteupAdded 3 Sep 2026, published 17 Jul 2026🛡️ Security Socket: Next.js Moves to Scheduled Security Releases
Vercel is replacing Next.js's ad-hoc security patching with a formal monthly scheduled-release program, publishing advance notice of severity and timing (first release July 20 covering 4 high/5 medium issues). The move follows React2Shell (CVE-2025-55182), a CVSS 10.0 pre-auth RCE in React Server Components exploited within hours by China state-nexus groups Earth Lamia and Jackpot Panda and affecting over 968,000 exposed instances, plus follow-on flaws CVE-2025-55183, CVE-2025-55184, and CVE-2025-67779, and the earlier CVE-2025-29927 middleware auth-bypass. It also ties the change to rising AI-assisted vulnerability discovery volume across the industry (Mozilla's 271-issue Firefox release, Microsoft's 570-fix Patch Tuesday).
 socket.devarticlePublished and added 16 Jul 2026🛡️ Security
 6 months to live for open models
Nathan Lambert argues open-weight AI models face a real near-term threat of a US ban or licensing restriction, driven by White House executive-order discussions and a political campaign (led by Anthropic) over Chinese model distillation. He contends the distillation debate is largely regulatory capture, argues APIs aren't demonstrably more secure than open weights, and calls for a US company (Meta, Microsoft, or Reflection AI) to release a frontier-capable open model to defuse the "only China builds open models" framing before any ban solidifies in the next six months.
interconnects.aiarticleAdded 29 Sep 2026, published 12 Jul 2026🧠 AI

